Share
Embed
Transcript
51 slides
-
Android & Me • I’m a first-year graduate student. •
I developed my first Android APP——BloGeo two years ago. • I’ve been an Android user for two years. • Now I’ve just started to learn Android security. -
Outline • Introduction to Android – Brief history – Architecture
• Android Development – Environment – Programming framework – Building and running process – Case Study • Overview of Android Security Feature • Android Security Lab (by Security Compass) • My Future Study -
Brief History • Written by Andy Rubin(founder of Android Inc.)
• Acquired by Google in 2005 • Android 1.0 released in 2007 • Android 4.0 released in 2011 • 52.5% of global mobile users -
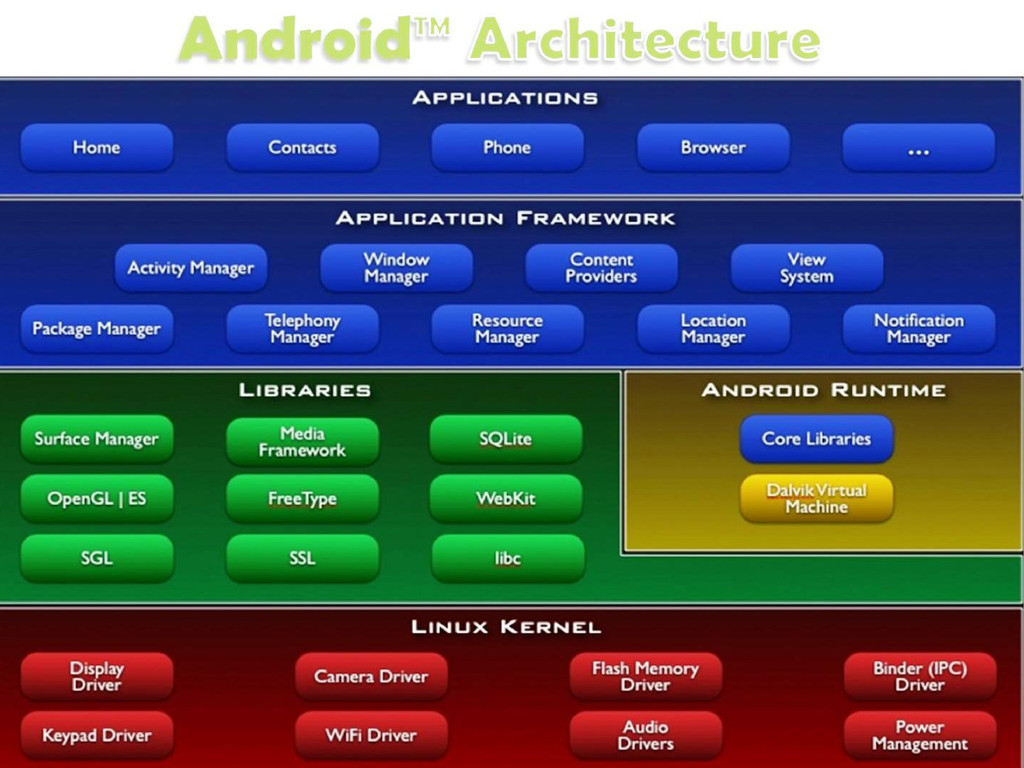
Brief Introduction • First complete, open and free mobile platform
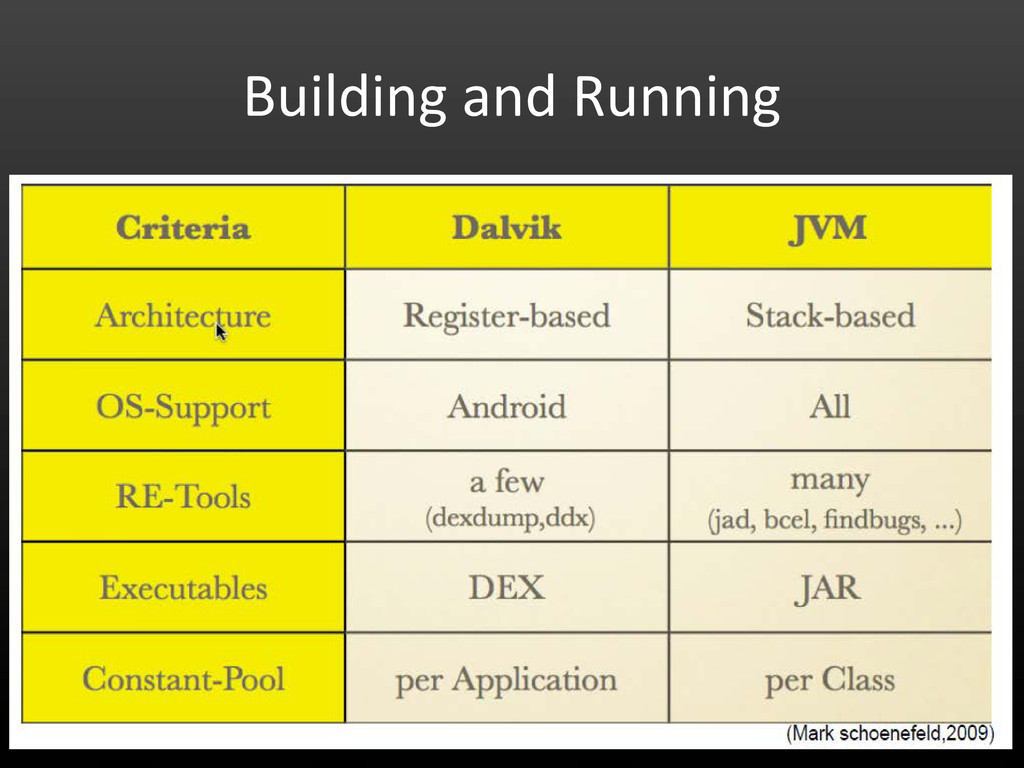
• Operating System – Mobile device optimized Linux kernel 2.6 • Application framework – Mainly Java-based – Running on Dalvik virtual machine featuring JIT compilation • Key applications – Gmail, Maps, Contacts, Market and etc. -
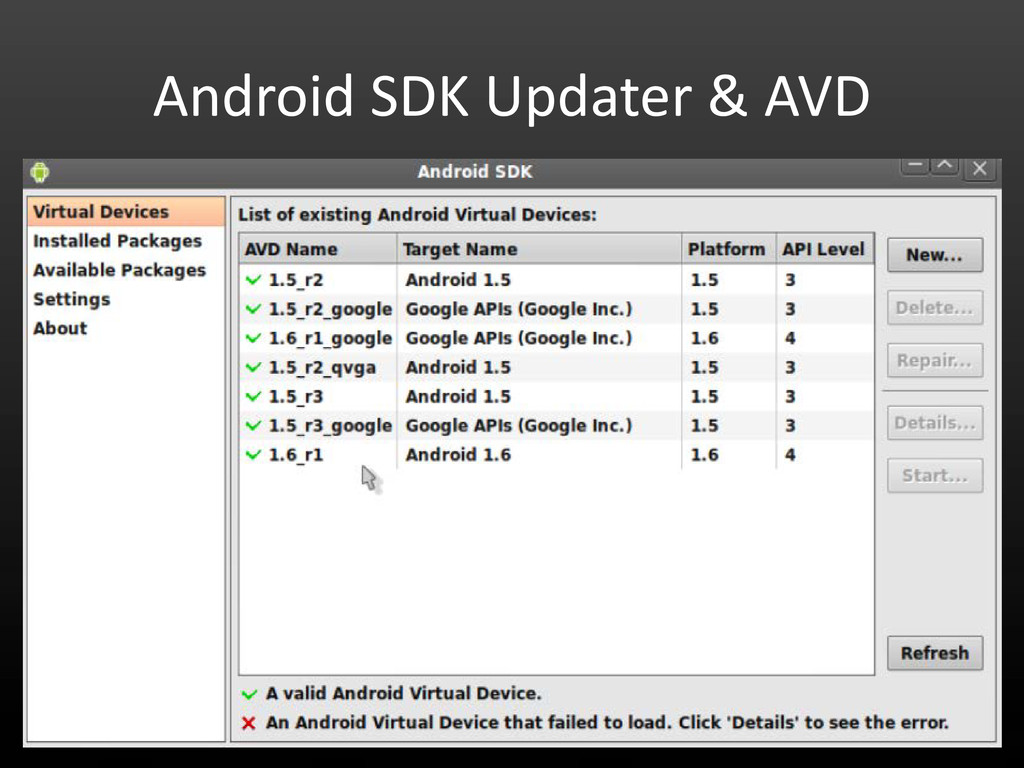
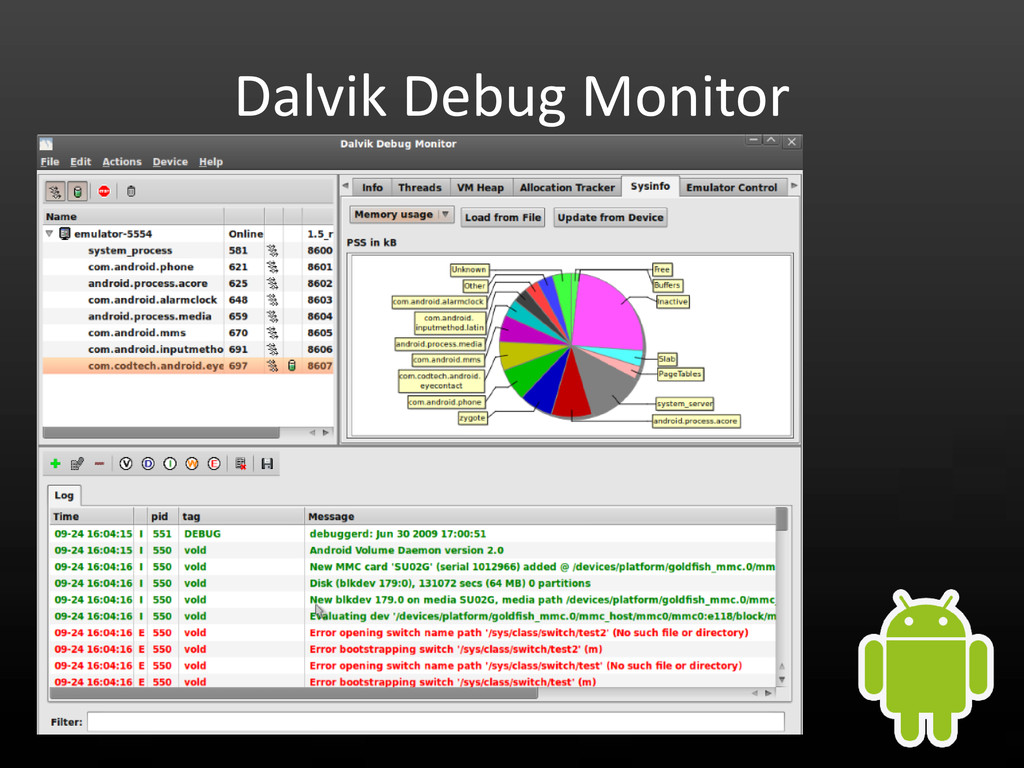
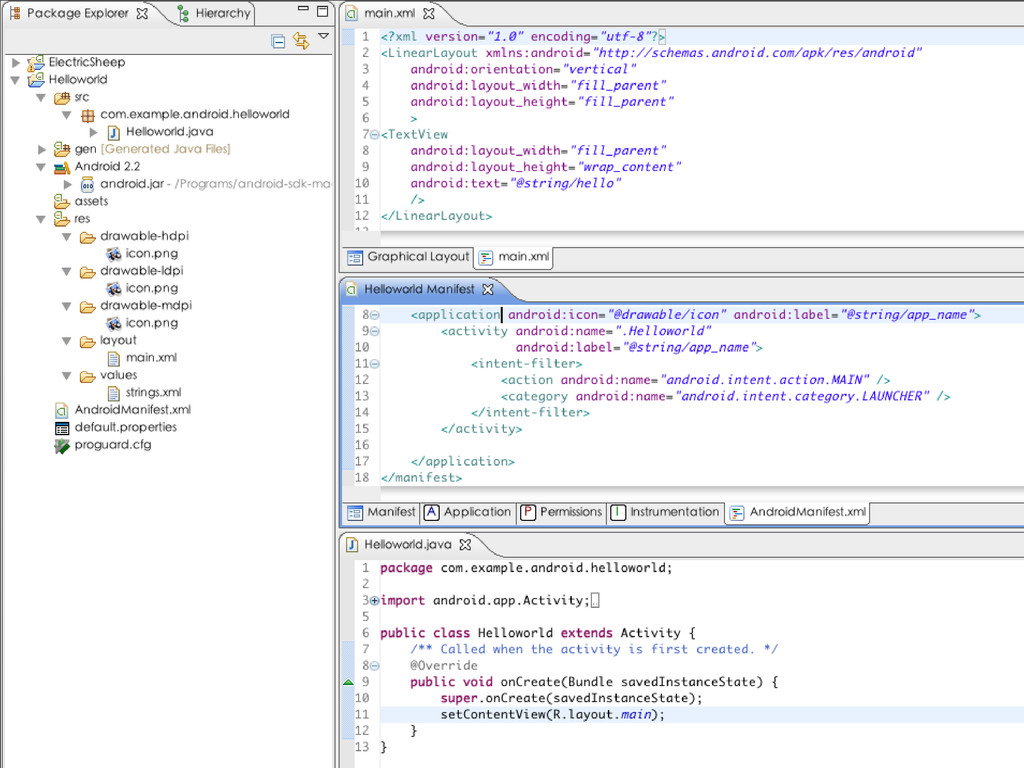
Developing Environment • Totally free-of-charge – Open source – Eclipse
with ADT plugin – SDK tools with an emulator – Android market • Dev guide – http://developer.android.com -
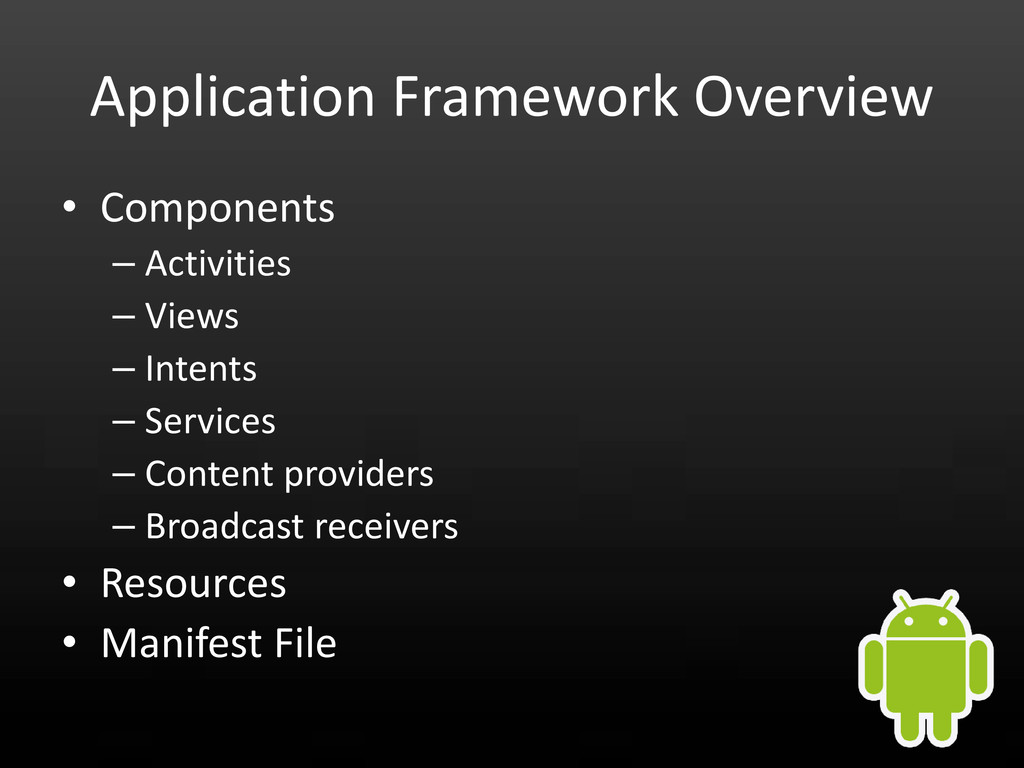
Application Framework Overview • Components – Activities – Views –
Intents – Services – Content providers – Broadcast receivers • Resources • Manifest File -
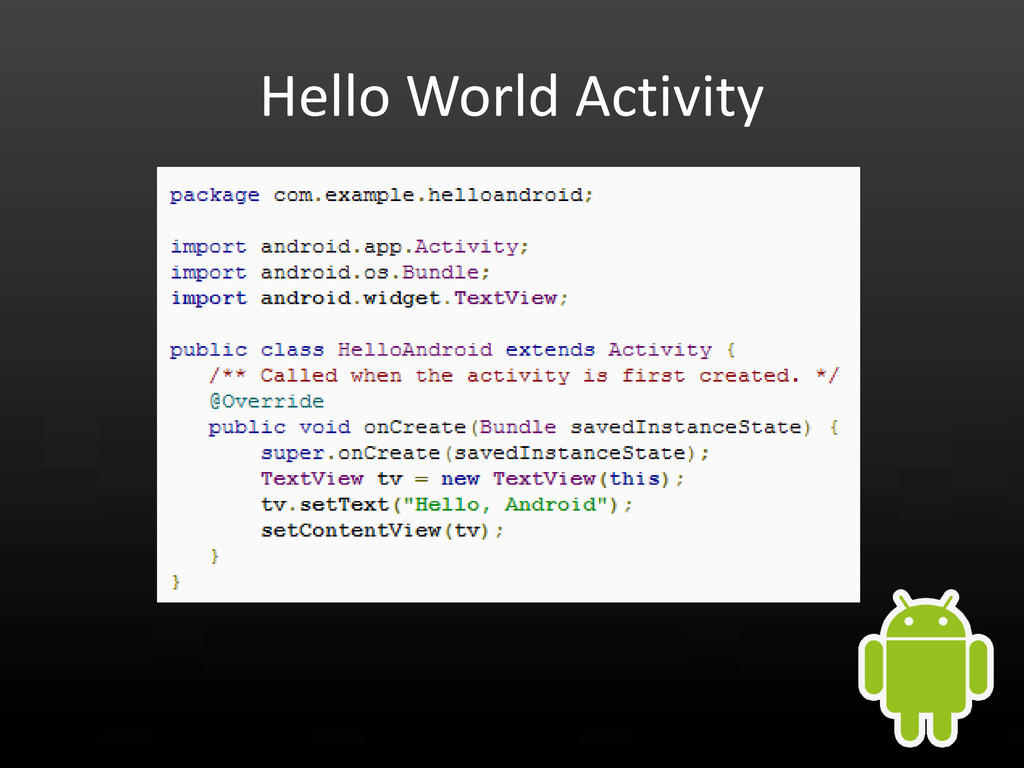
Activities • An activity is a single, focused thing that
the user can do • Typically correspond to one UI screen • Activities are stacked like a deck of cards • Active activity is placed on top -
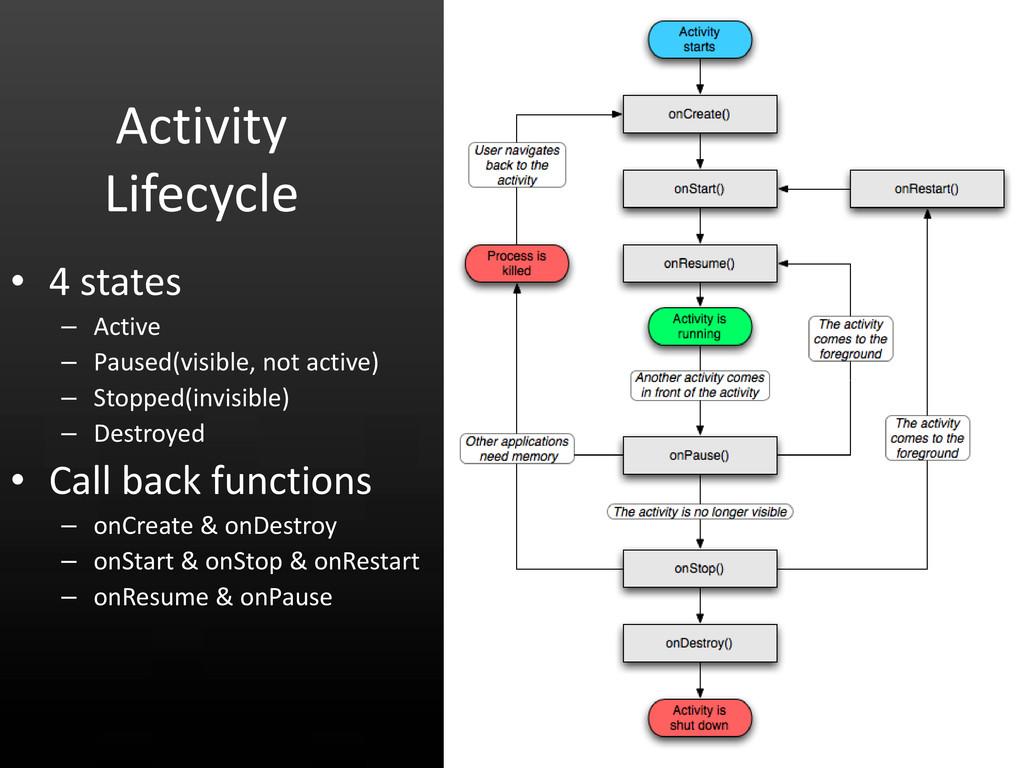
Activity Lifecycle • 4 states – Active – Paused(visible, not
active) – Stopped(invisible) – Destroyed • Call back functions – onCreate & onDestroy – onStart & onStop & onRestart – onResume & onPause -
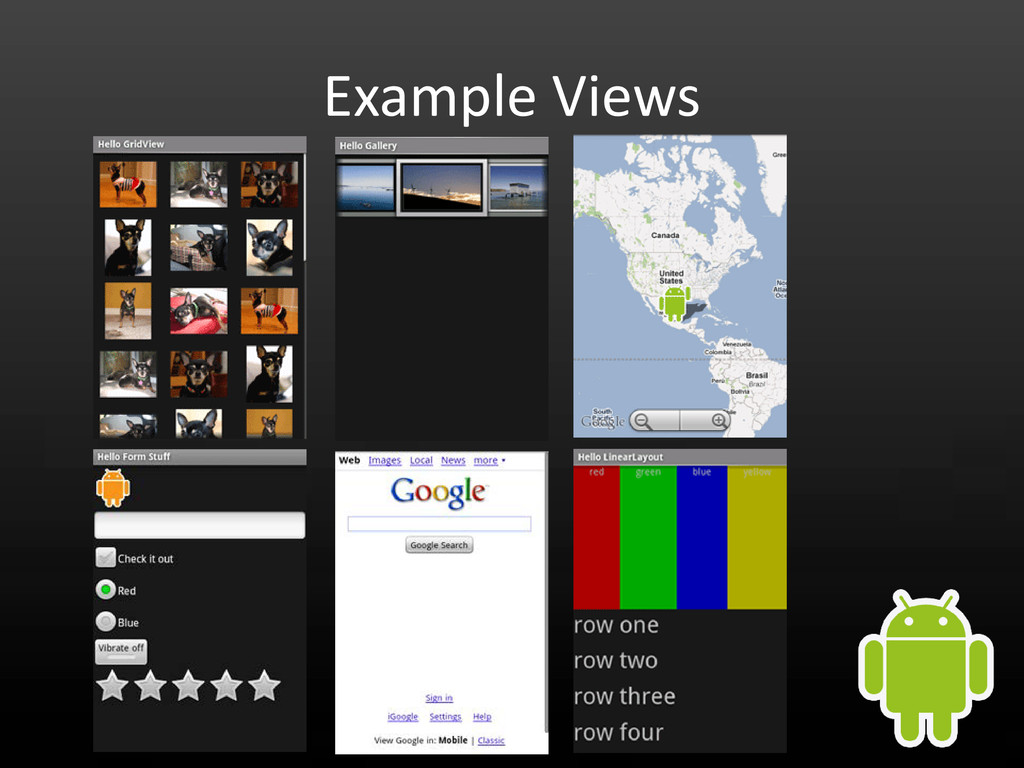
Views • Views are GUI controls(E.g. TextView, EditText, Button) •
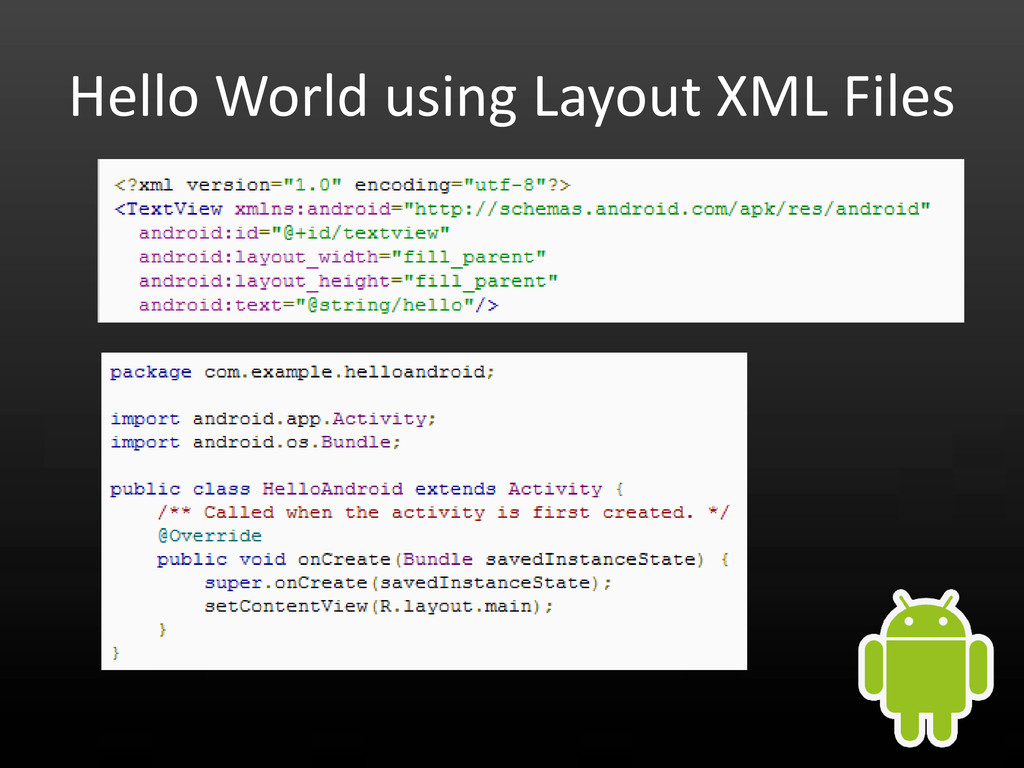
Activity windows consist of views and viewgroups • Organized as trees to build up GUIs • Operations we can perform on views – Set properties: Use function or define in the XML layout files to load. – Set focus – Set up listener – Set visibility – Draw anything we like • We can use Layout to help place views – E.g. LinearLayout, TableLayout, AbsoluteLayout – Use function or define in the XML layout files -
Intents • Intents are used to exchange data between Activities
or Applications • Think of Intents as a verb and object; a description of what you want done – E.g. VIEW, CALL, PLAY etc.. • Describes what the application wants • Provides late runtime binding -
Services • Services run in the background • Don’t interact
with the user • Run on the main thread of the process -
Content Providers • Content providers store and retrieve data and
make it accessible to all applications • It is the only way to share data across packages • The backend is SQLite • They are linked to clients • Data exposed as a unique URI -
Resources • Resources are images , strings and etc. •
Externalize resources from application code • SDK will generate codes to map a resource to an id, we can use static class R to get resources • Layout xml files are also resources -
Manifest File • Control file that tells the system what
to do and how the top-level components are related • It’s the “glue” that actually specifies which intents your activities receive • Specifies permissions -
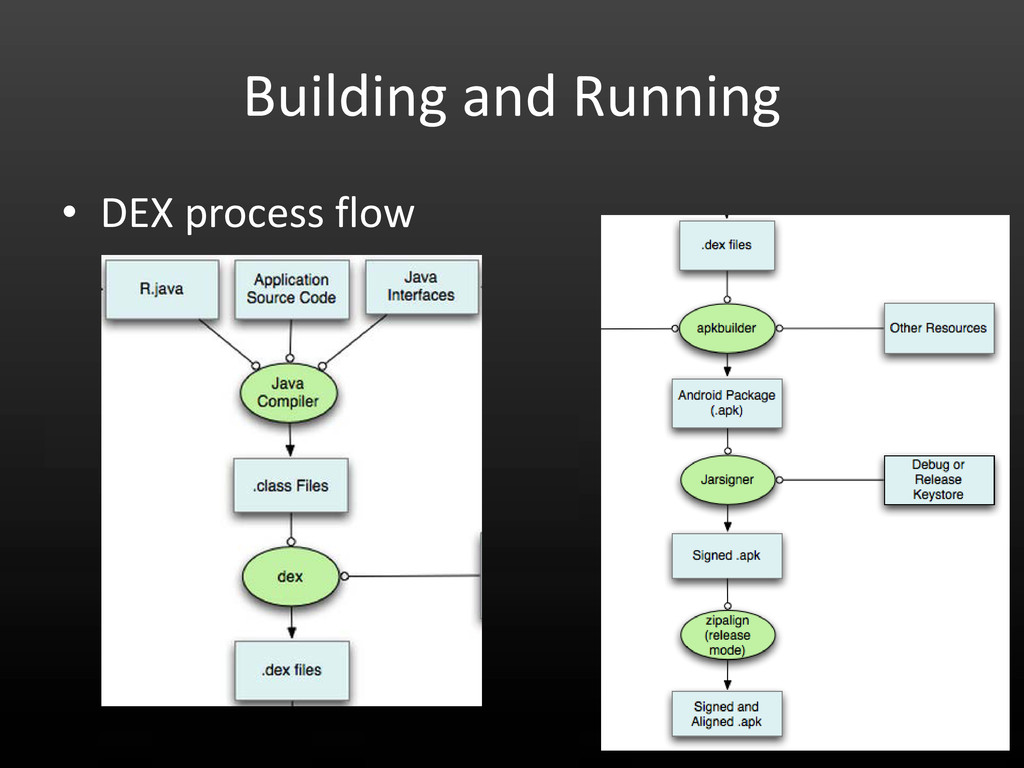
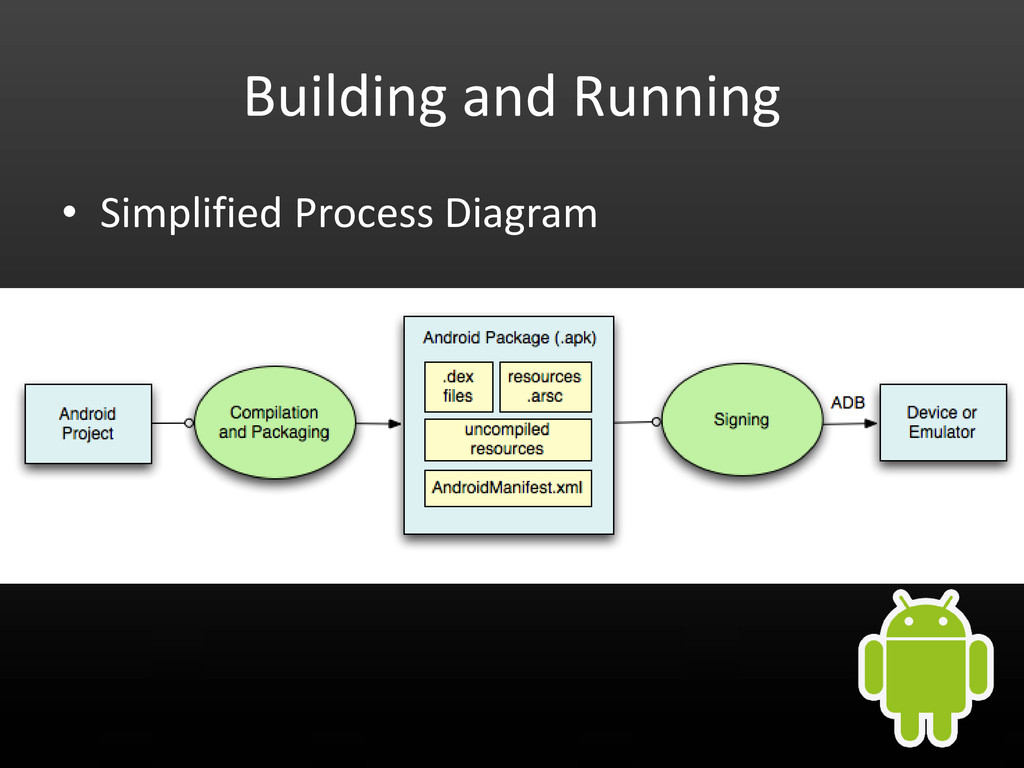
Building and Running • Android package format – Bundle a
few files into a file(.apk) – Just a zip file – Classes.dex is core file – compiled java classes – Use ‘DX’ tool to convert Java *.class to Dalvik bytecode *.dex -
Developing Process • Create your own android project • Design
the UI • Externalize resources • React to events • Run the application -
Android Security Overview • Goals – Protect user data –
Protect system resources (including the network) – Provide application isolation • Android security features provided – Robust security at the OS level through the Linux kernel – Mandatory application sandbox for all applications – Secure interprocess communication – Application signing – Application-defined and user-granted permissions -
Android Security Overview(cont.) • Application Sandbox: Kernel Level – Each
Application has a user ID(UID) to run • Interprocess Communication – Binder • A lightweight capability-based remote procedure call mechanism designed for high performance when performing in-process and cross-process calls. – Intents – ContentProviders • Application signing -
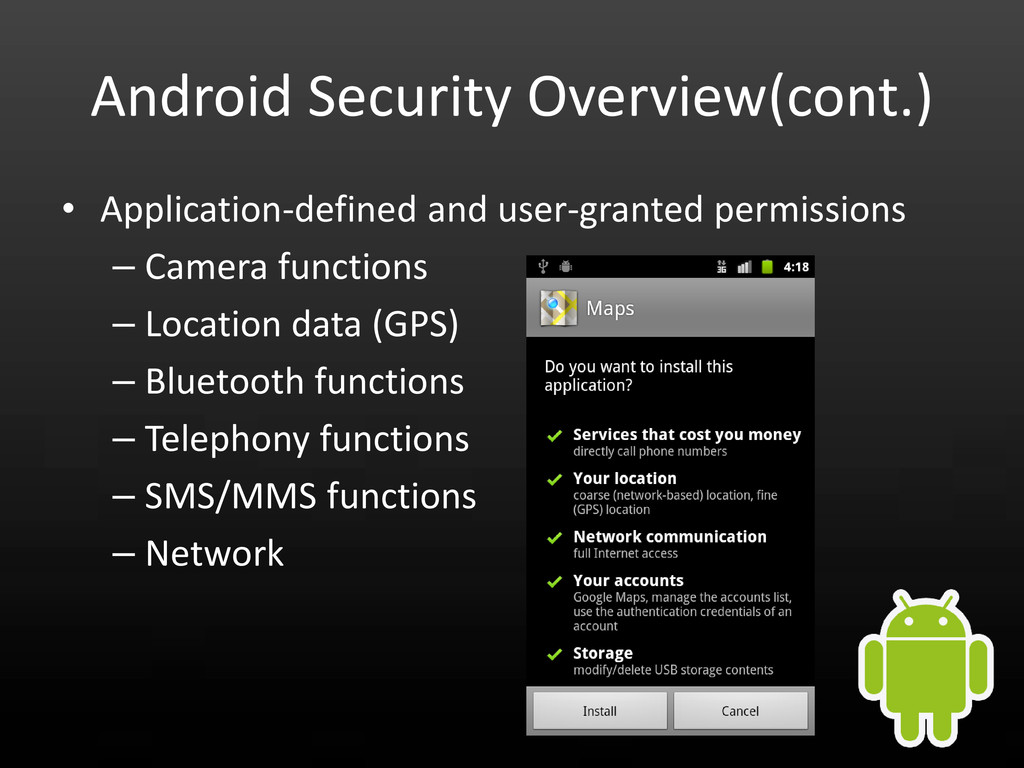
Android Security Overview(cont.) • Application-defined and user-granted permissions – Camera
functions – Location data (GPS) – Bluetooth functions – Telephony functions – SMS/MMS functions – Network -
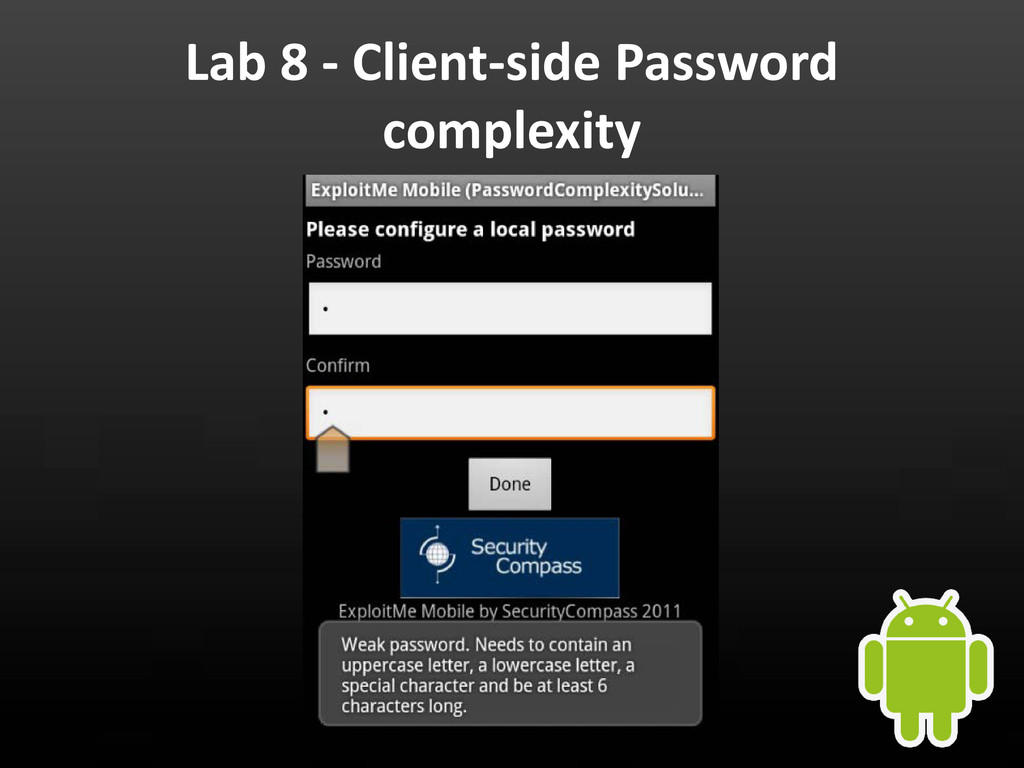
ExploitMe Mobile Android Labs • By Security Compass – information
security consulting firm – specializing in secure software development and training • An open source project demonstrating Android mobile hacking • A bank transfer mobile client • Server written in python(http/https) • 8 Labs -
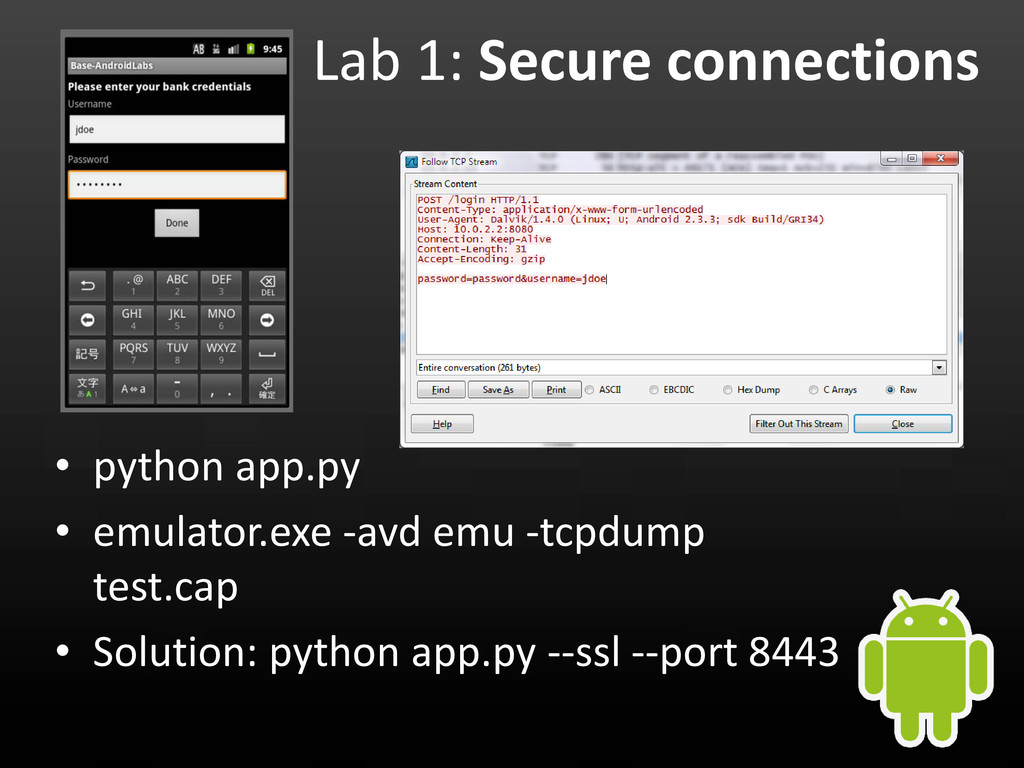
Lab 1: Secure connections • python app.py • emulator.exe -avd
emu -tcpdump test.cap • Solution: python app.py --ssl --port 8443 -
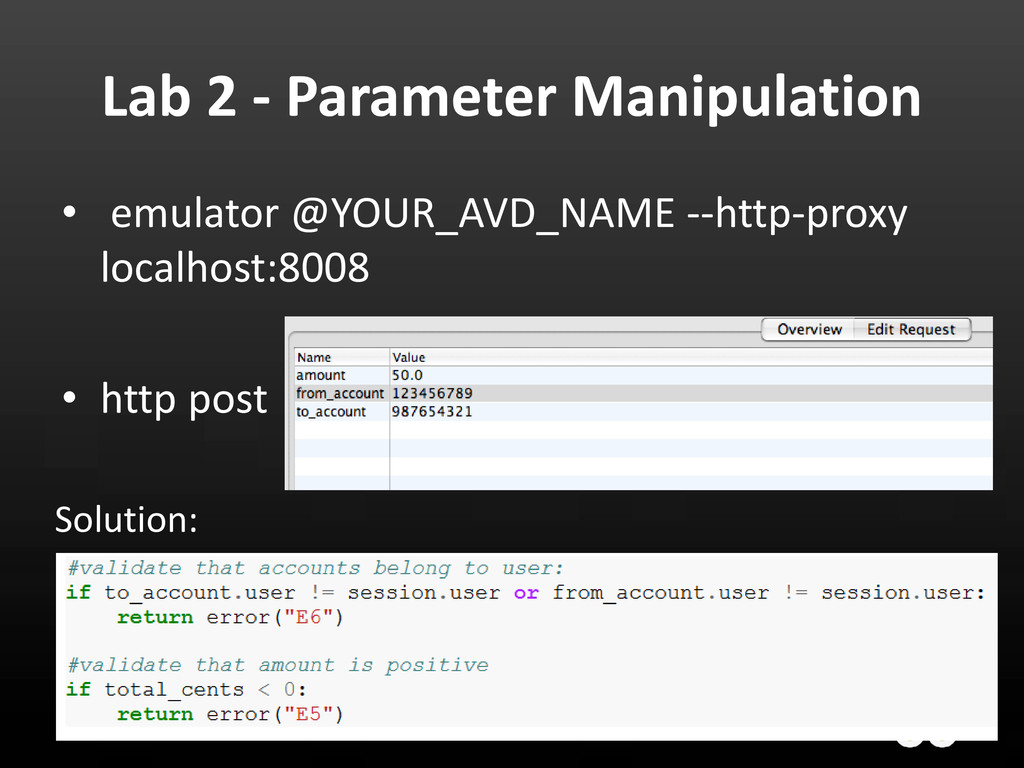
Lab 2 - Parameter Manipulation • emulator @YOUR_AVD_NAME --http-proxy localhost:8008
• http post Solution: -
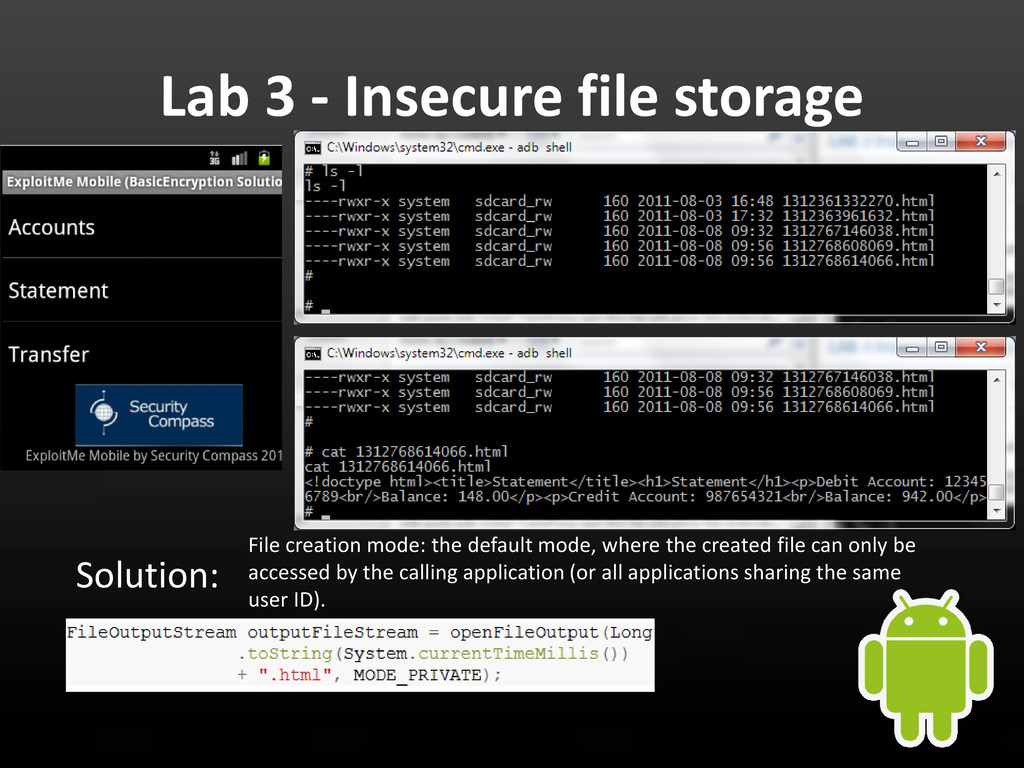
Lab 3 - Insecure file storage Solution: File creation mode:
the default mode, where the created file can only be accessed by the calling application (or all applications sharing the same user ID). -
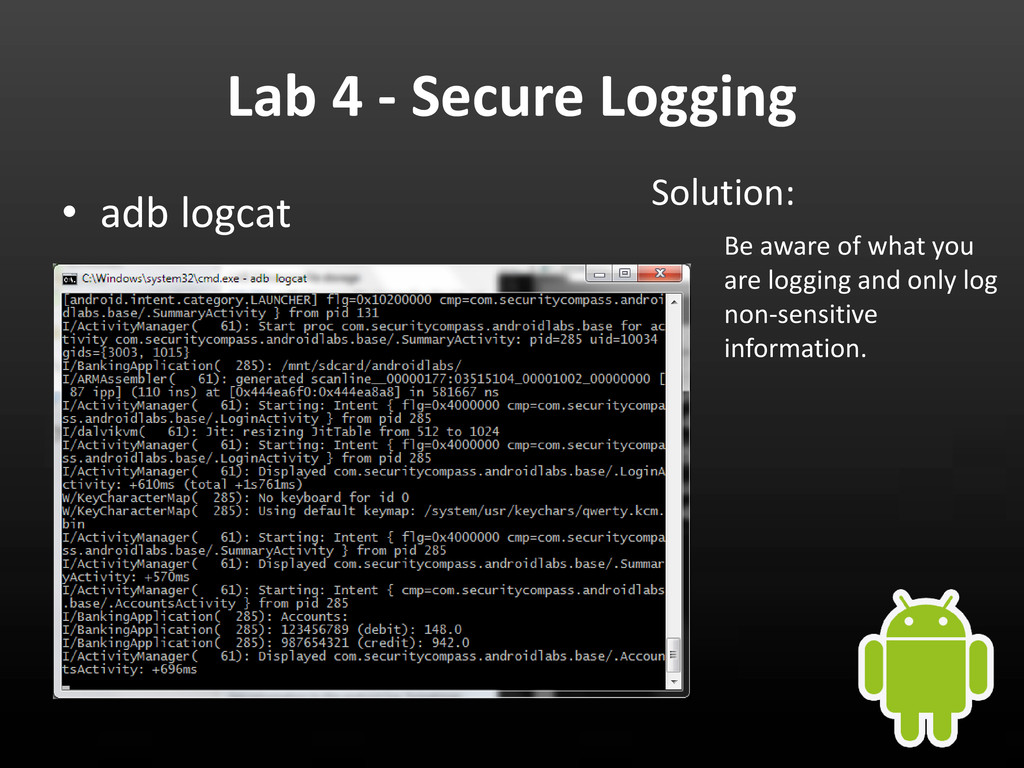
Lab 4 - Secure Logging • adb logcat Be aware
of what you are logging and only log non-sensitive information. Solution: -
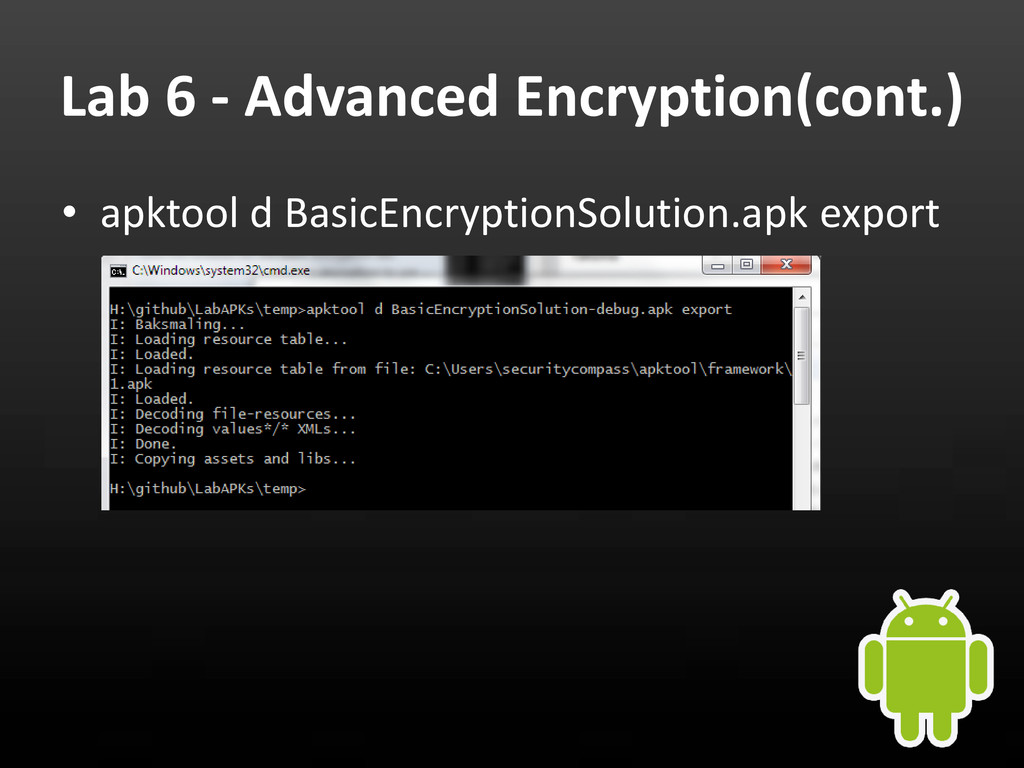
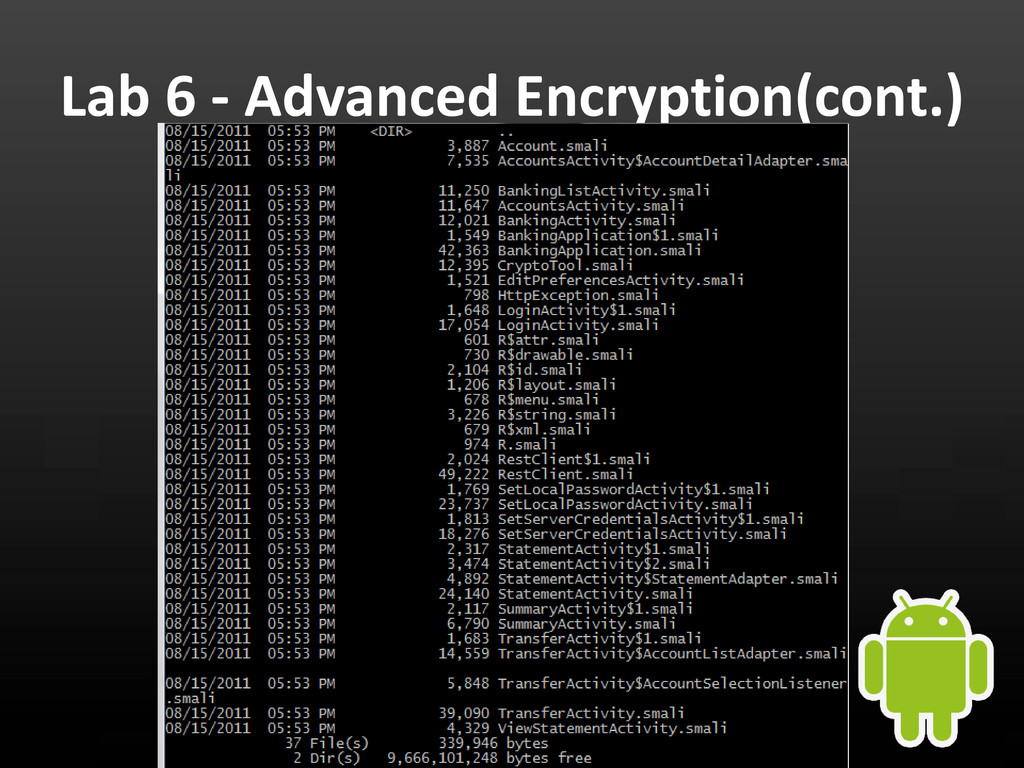
Lab 6 - Advanced Encryption • apktool – It is
a tool for reengineering 3rd party, closed, binary Android apps. – It can decode resources to nearly original form and rebuild them after making some modifications. -
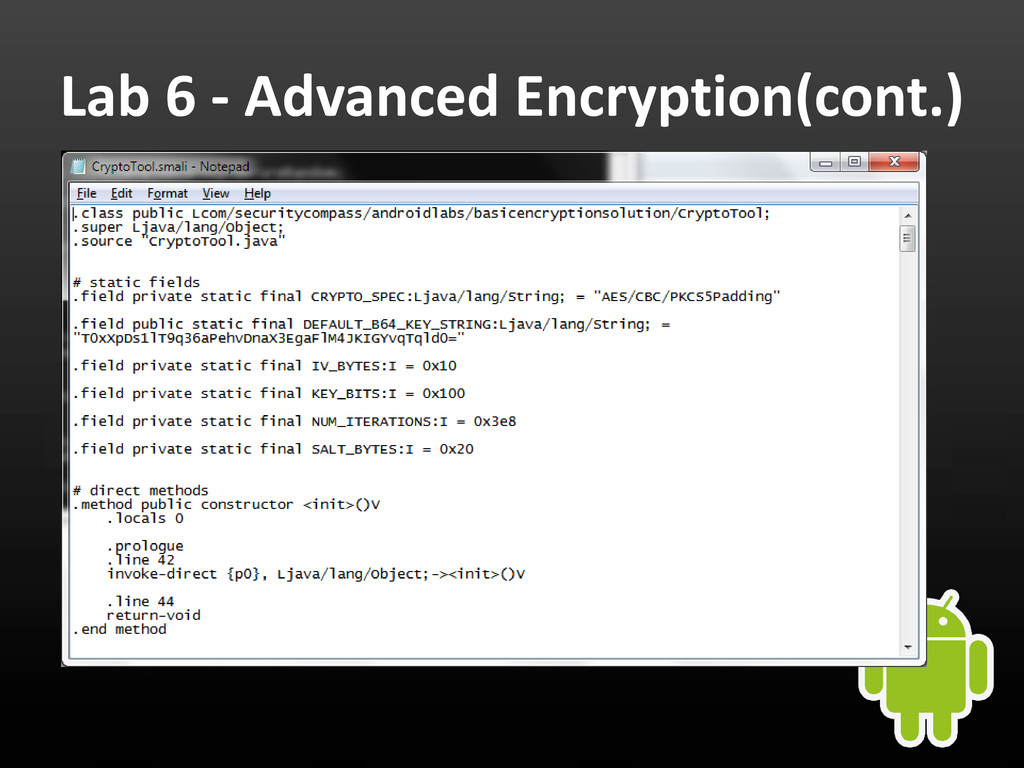
Lab 6 - Advanced Encryption(cont.) • Smali – Smali is
an assembler for the dex format used by dalvik -
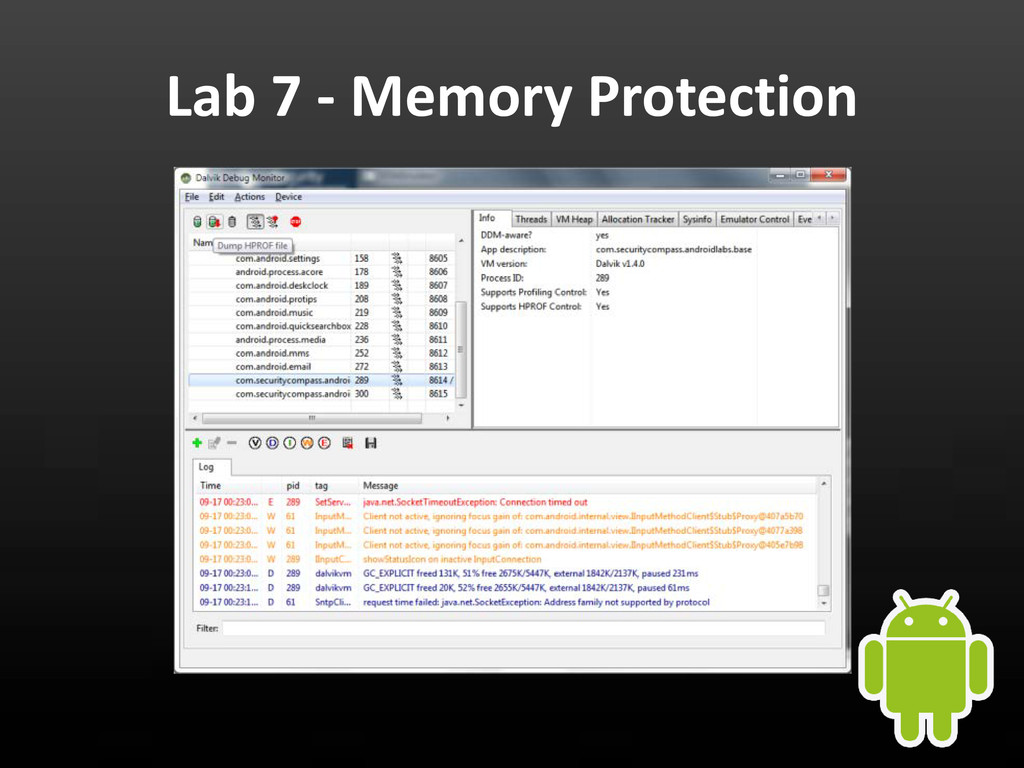
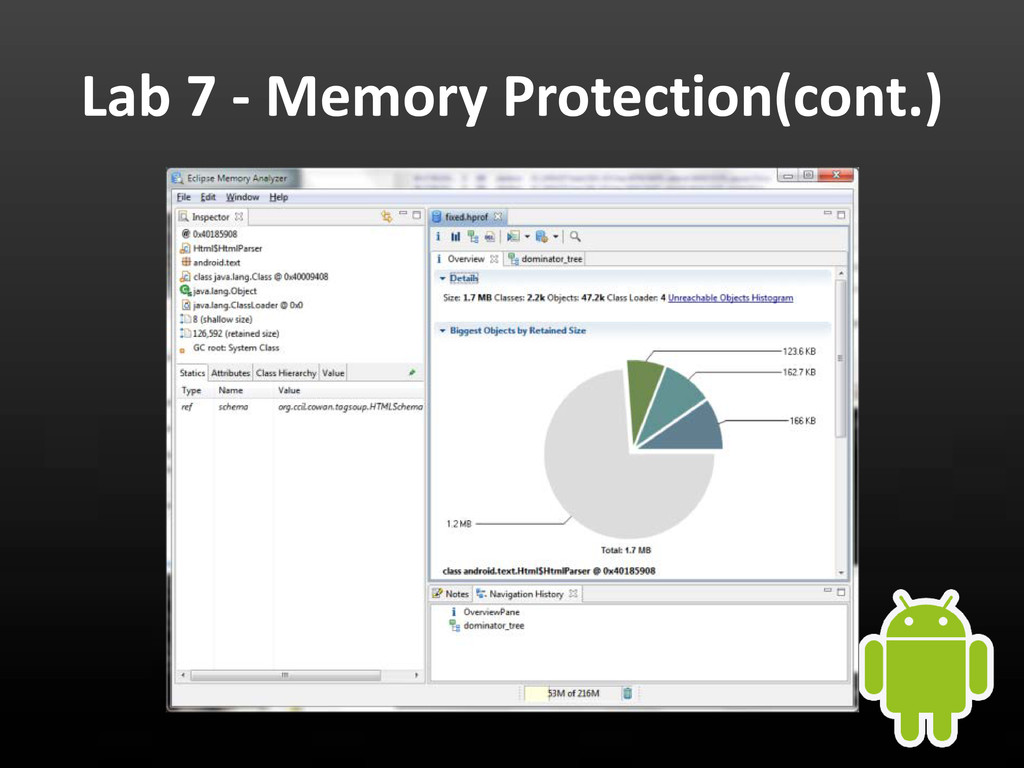
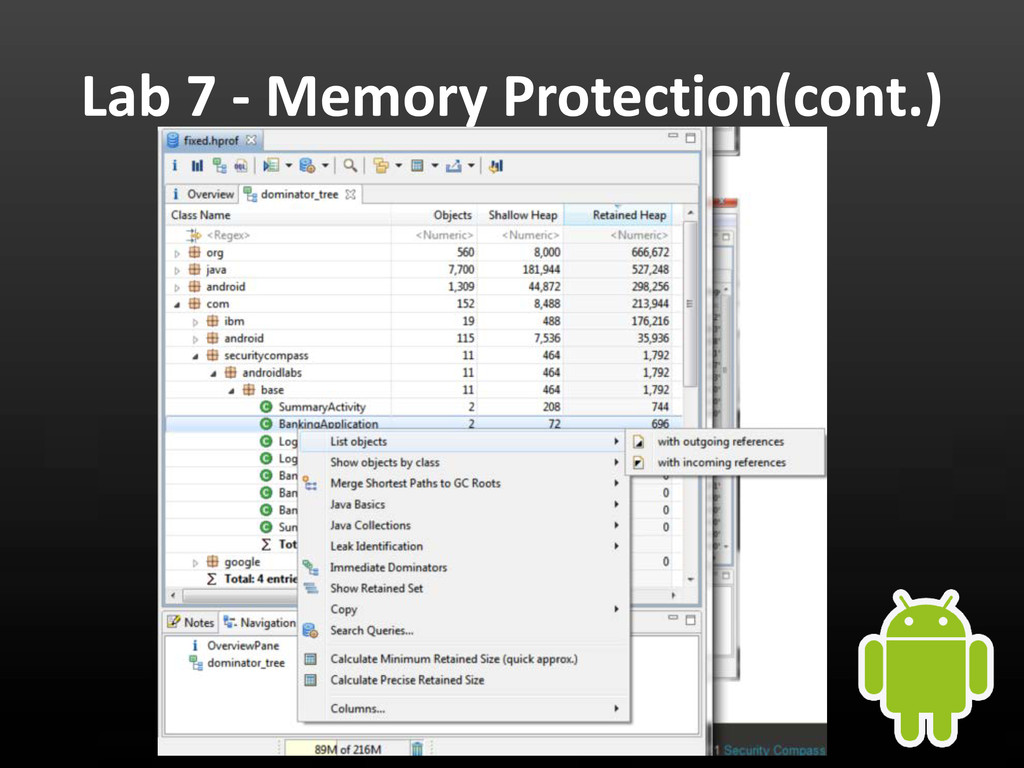
Lab 7 - Memory Protection • hprof-conv source dest –
Convert dex memory dump format to Java format • Use MAT(memory analyzer tool) to browse it -
Future Study I hope I can show you some more
hacking examples next time. Android Reverse Engineering!