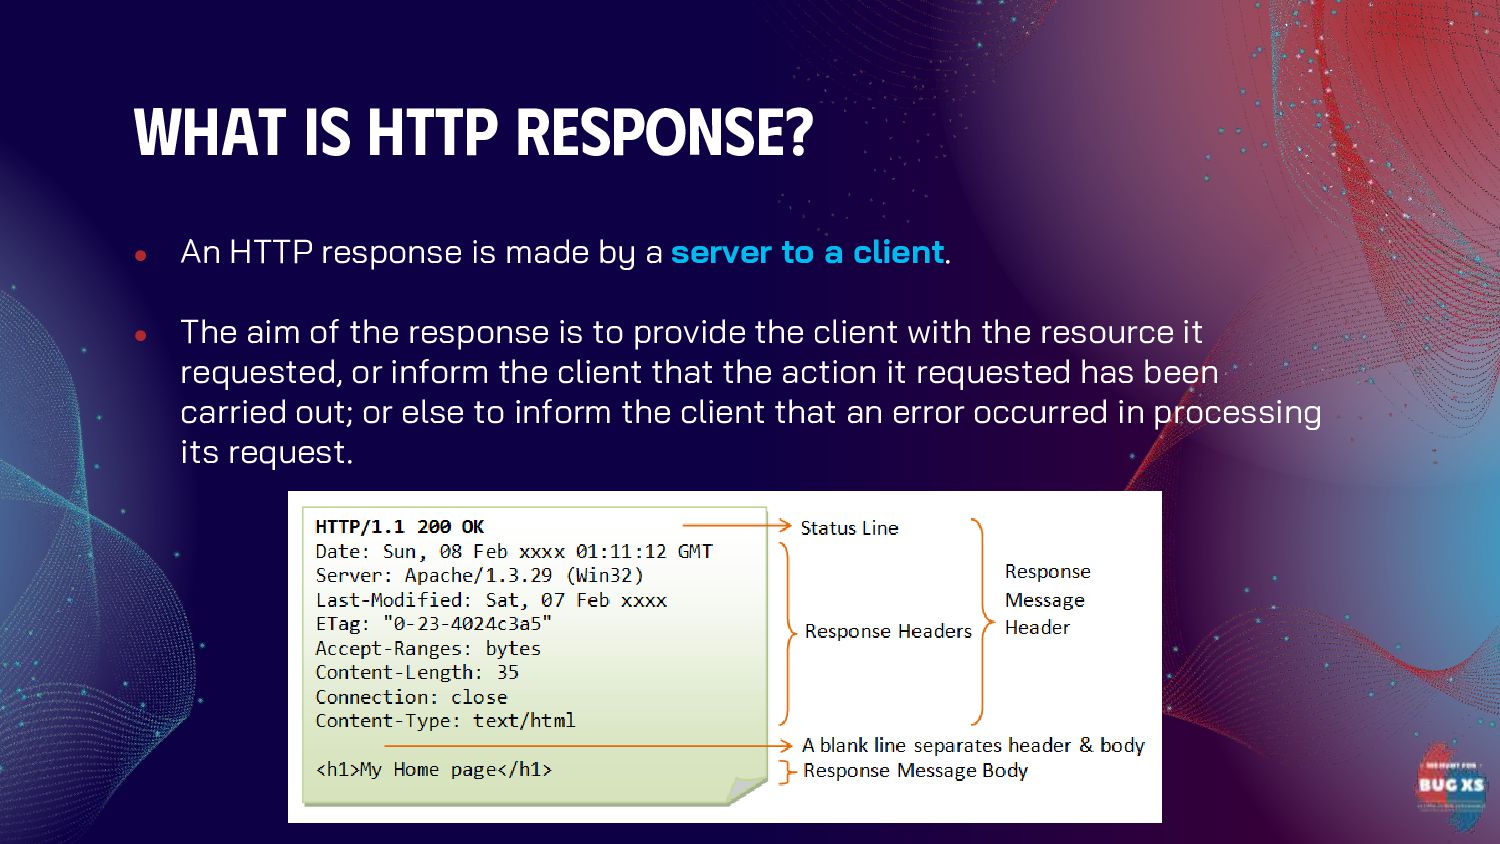
a client. • The aim of the response is to provide the client with the resource it requested, or inform the client that the action it requested has been carried out; or else to inform the client that an error occurred in processing its request. What is HTTP Response?
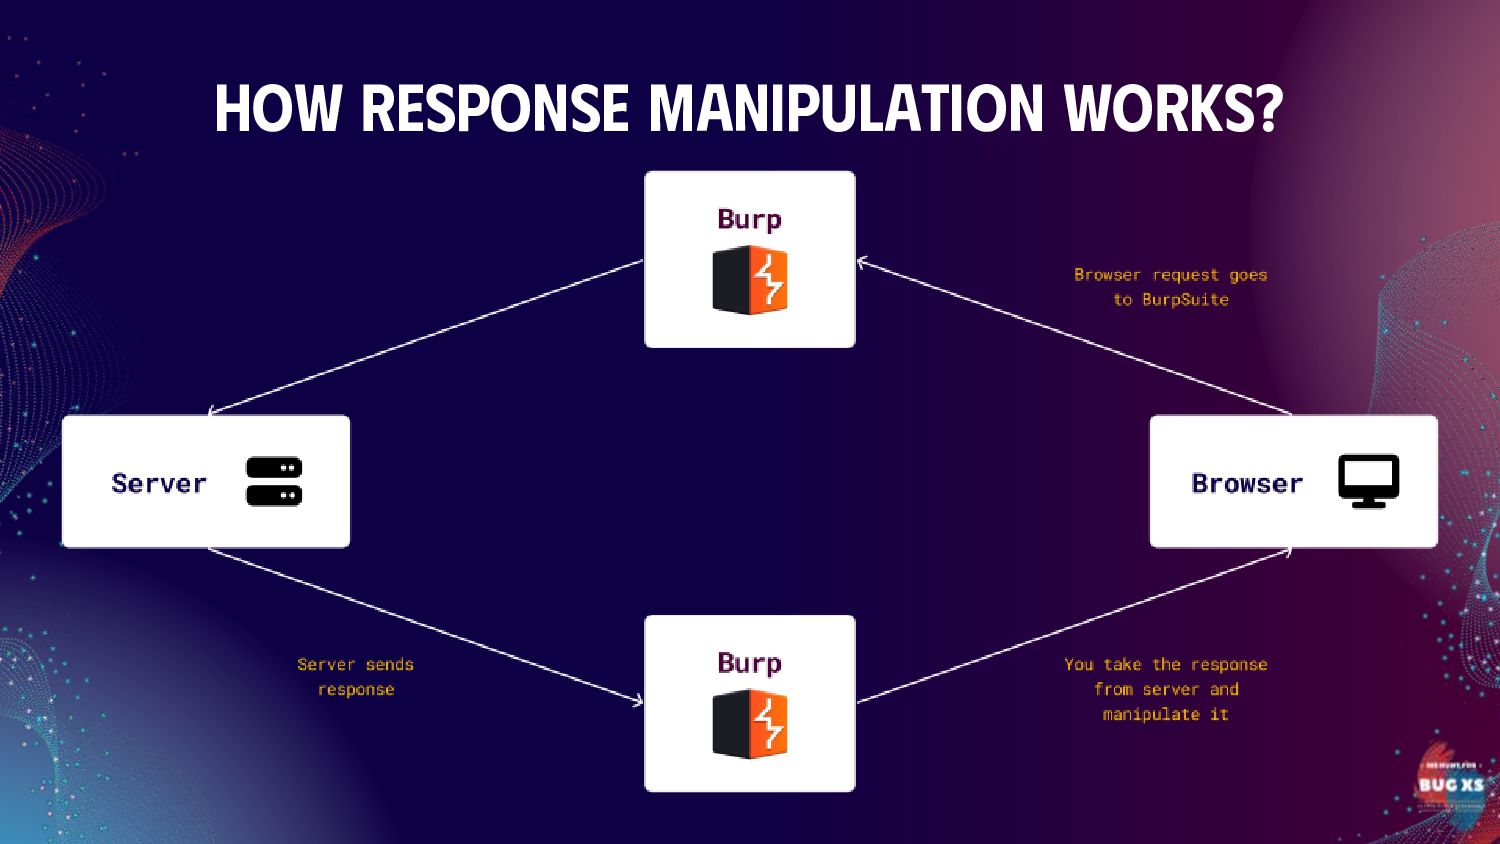
or altering the responses sent by a web server in the Hypertext Transfer Protocol (HTTP) communication. • This method is very helpful in finding multiple critical vulnerabilities including business logic issues. What is HTTP Response Manipulation?
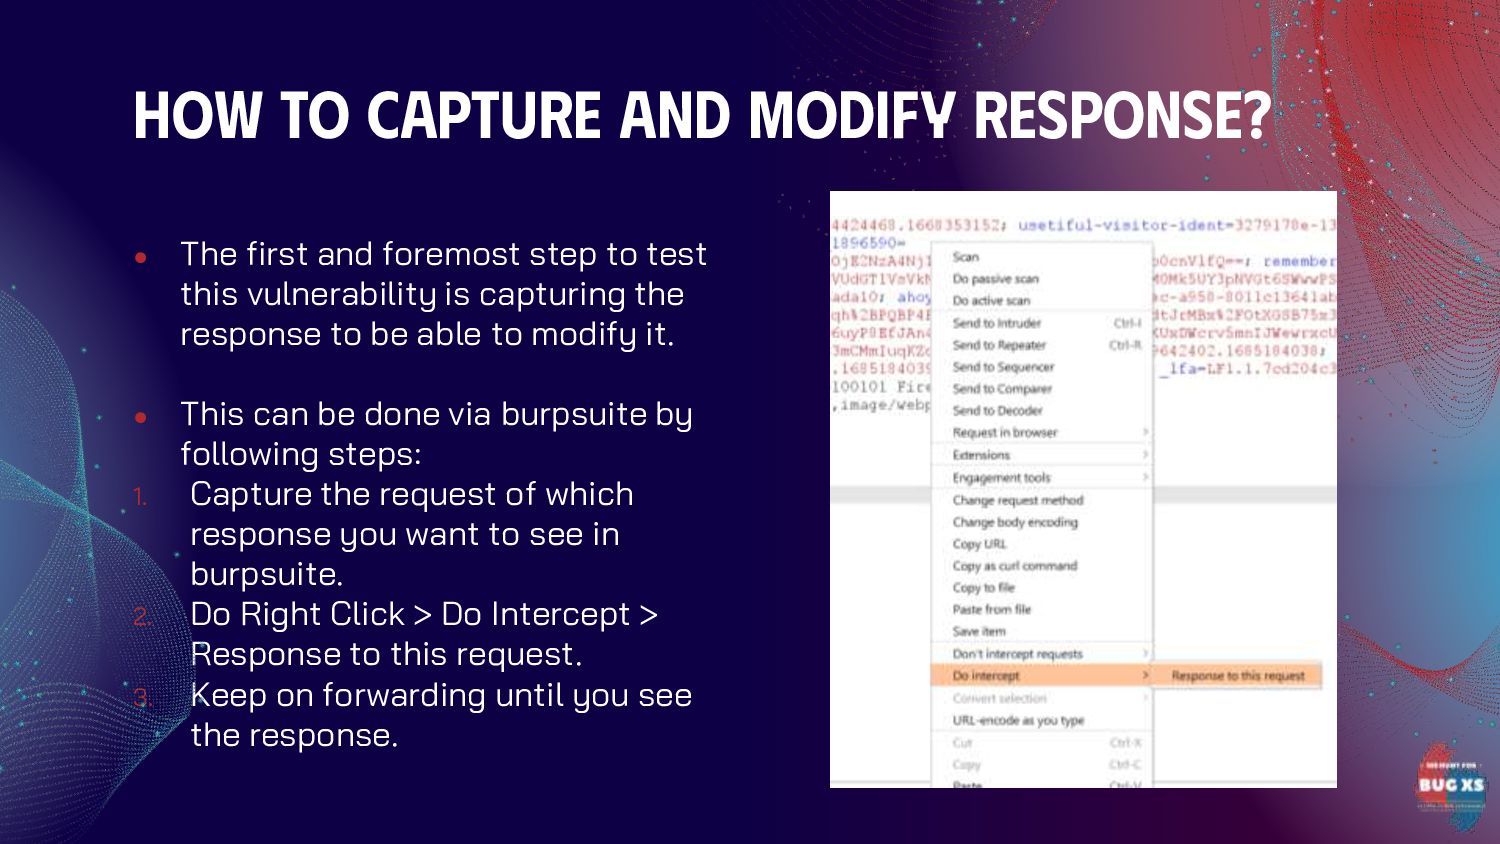
is capturing the response to be able to modify it. • This can be done via burpsuite by following steps: 1. Capture the request of which response you want to see in burpsuite. 2. Do Right Click > Do Intercept > Response to this request. 3. Keep on forwarding until you see the response. How to capture and modify response?
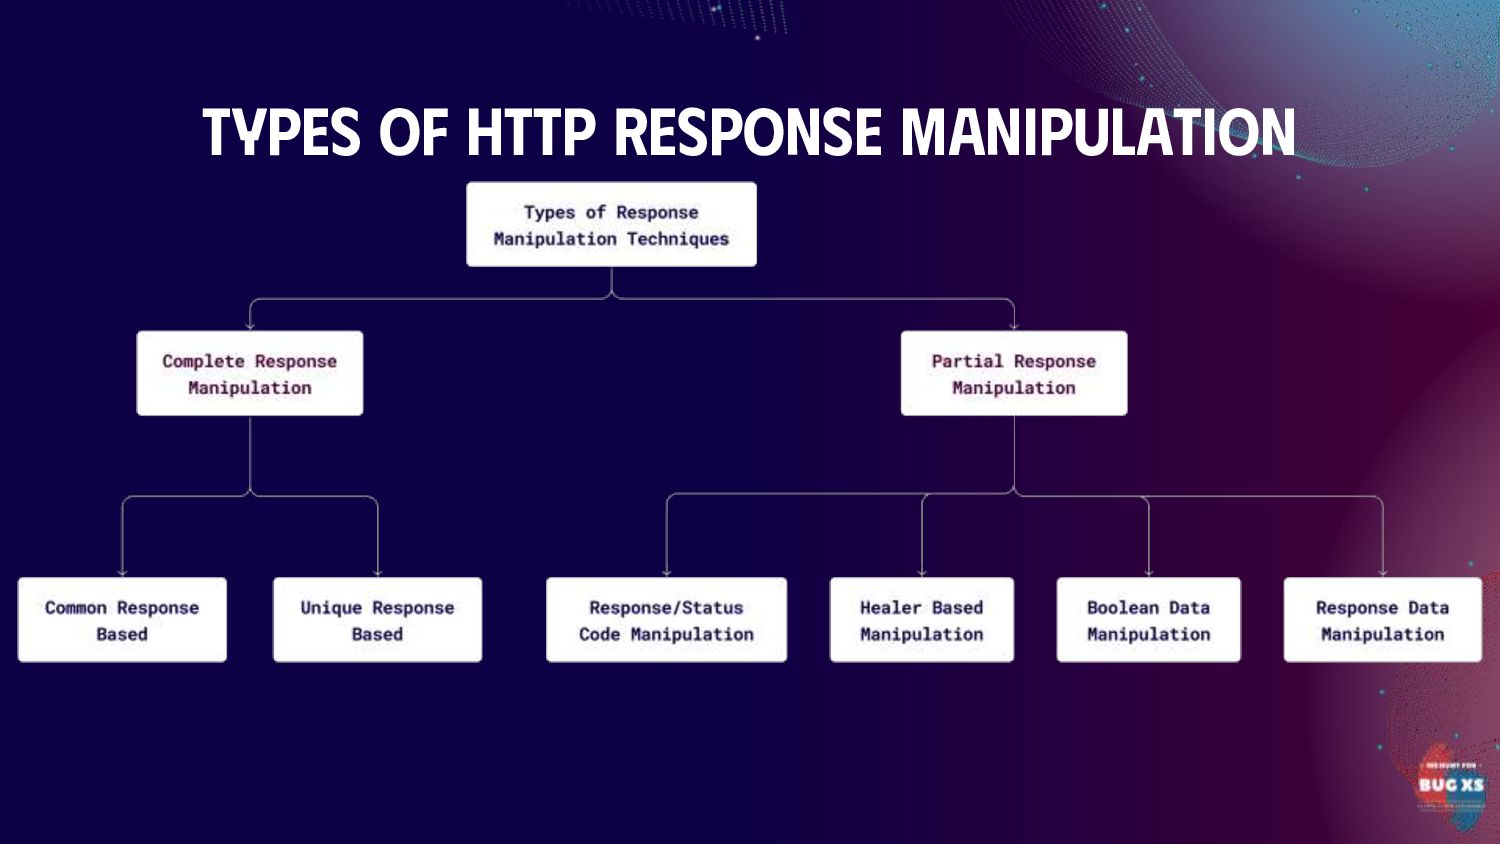
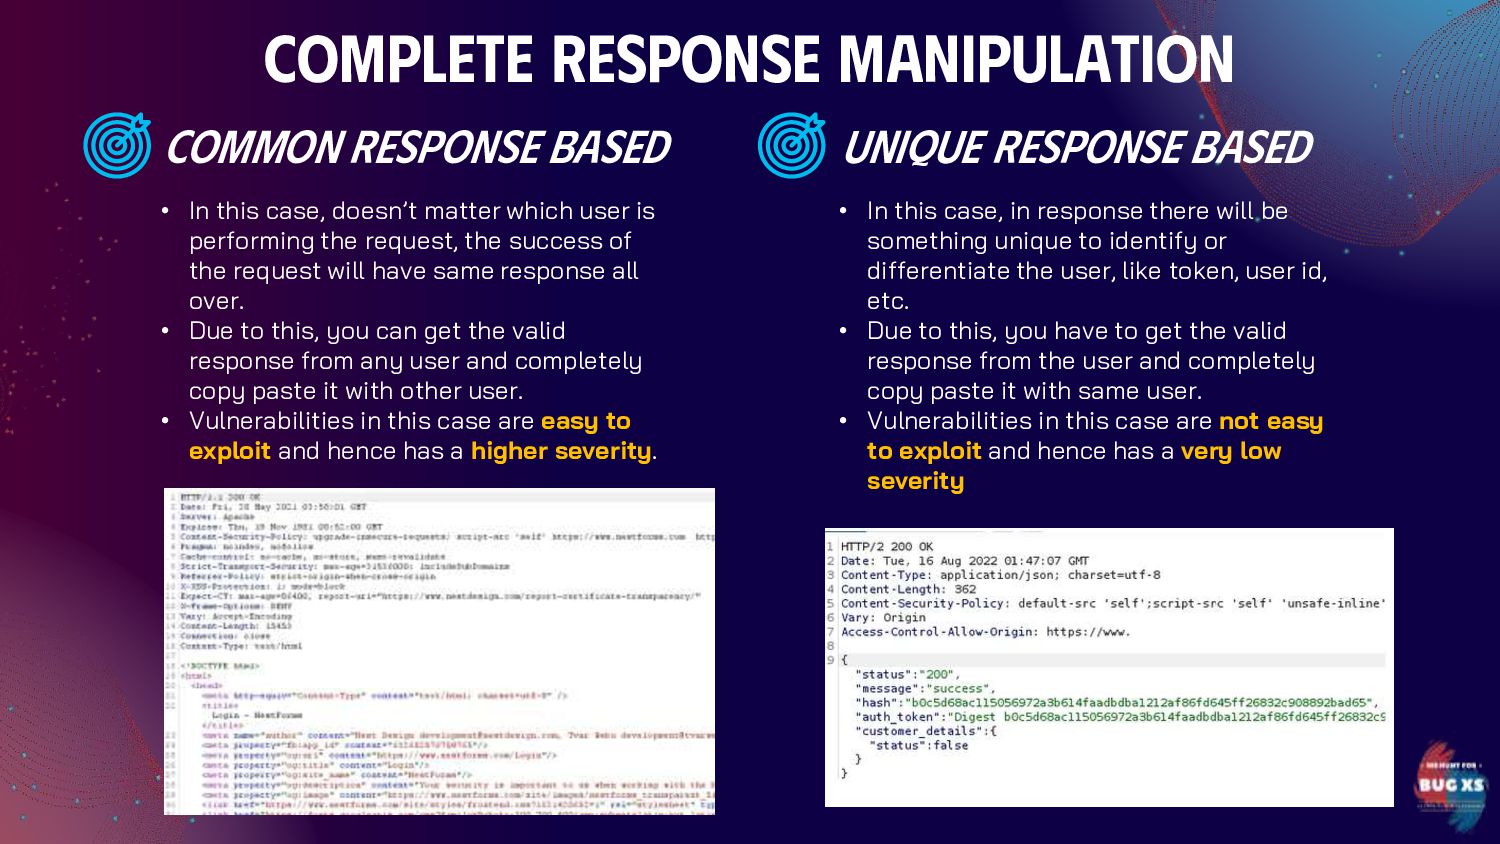
the request, the success of the request will have same response all over. • Due to this, you can get the valid response from any user and completely copy paste it with other user. • Vulnerabilities in this case are easy to exploit and hence has a higher severity. • In this case, in response there will be something unique to identify or differentiate the user, like token, user id, etc. • Due to this, you have to get the valid response from the user and completely copy paste it with same user. • Vulnerabilities in this case are not easy to exploit and hence has a very low severity UNIQUE RESPONSe BASED Common Response Based Complete Response Manipulation
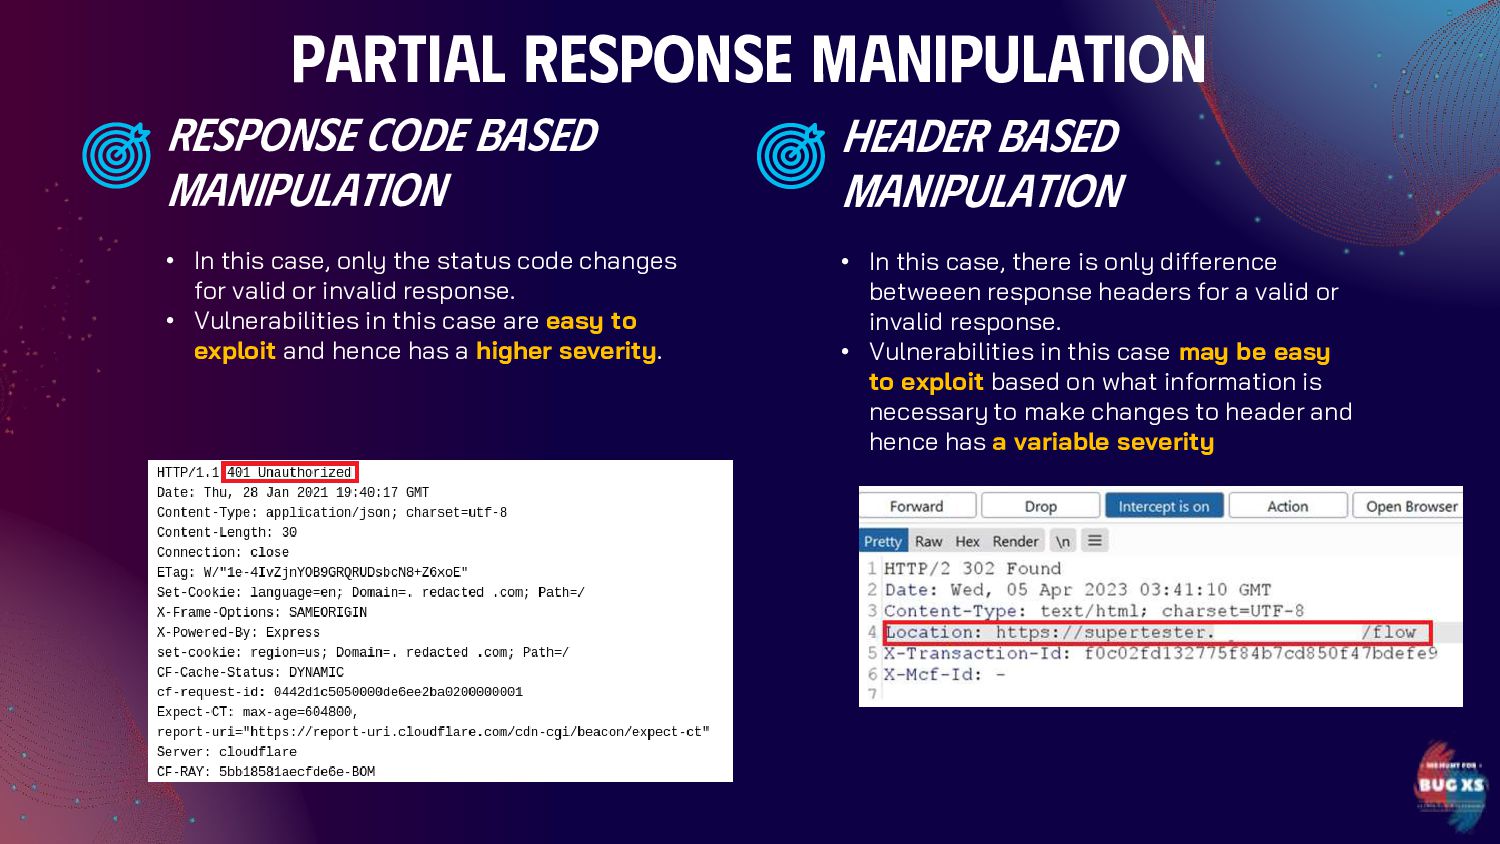
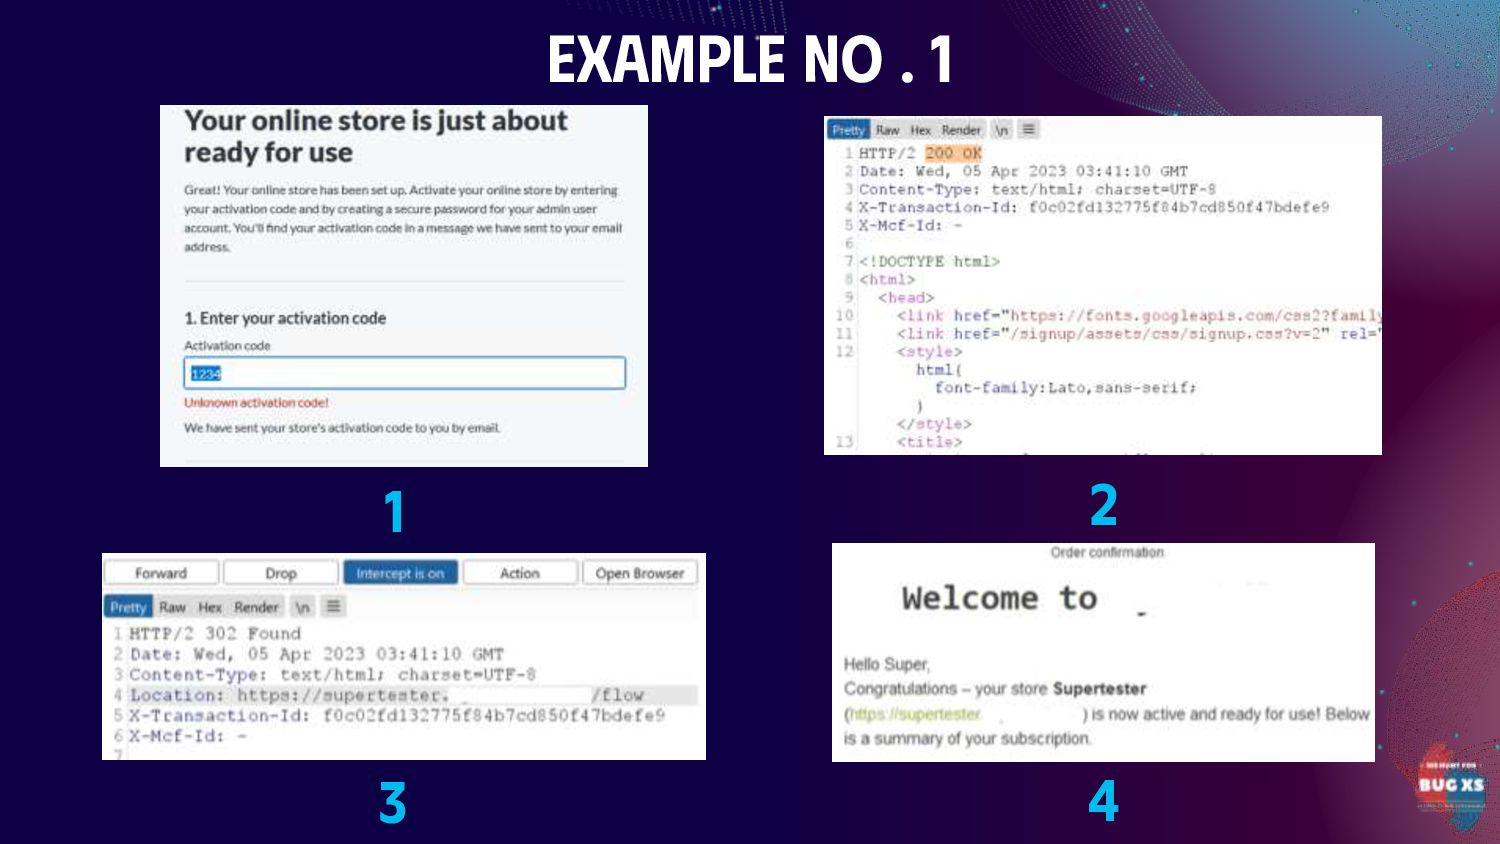
valid or invalid response. • Vulnerabilities in this case are easy to exploit and hence has a higher severity. • In this case, there is only difference betweeen response headers for a valid or invalid response. • Vulnerabilities in this case may be easy to exploit based on what information is necessary to make changes to header and hence has a variable severity HEADER BASED Manipulation Response Code Based MANIPULATION Partial Response Manipulation
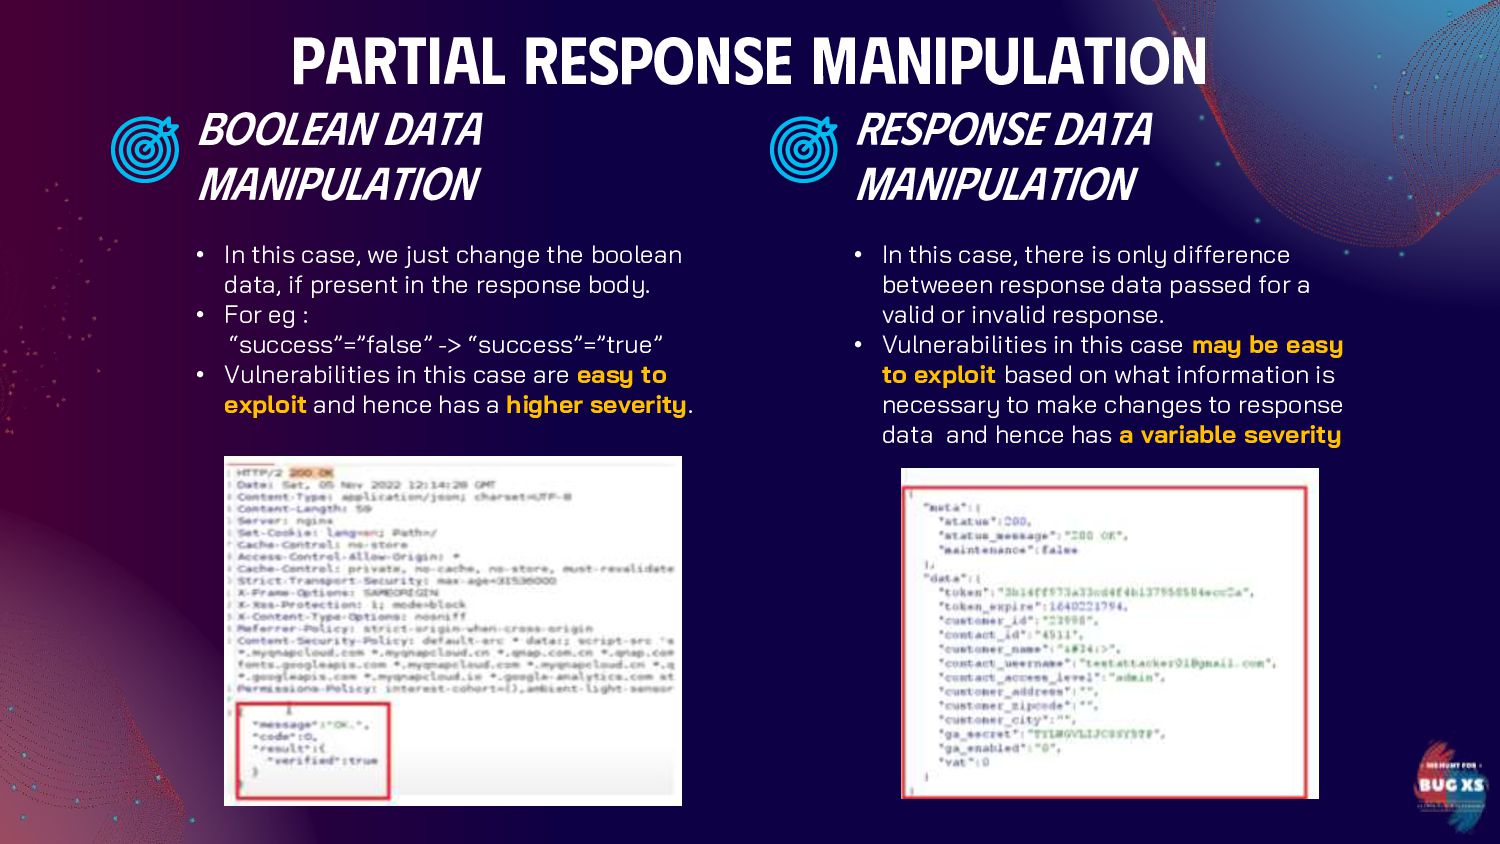
if present in the response body. • For eg : “success”=”false” -> “success”=”true” • Vulnerabilities in this case are easy to exploit and hence has a higher severity. • In this case, there is only difference betweeen response data passed for a valid or invalid response. • Vulnerabilities in this case may be easy to exploit based on what information is necessary to make changes to response data and hence has a variable severity Response data manipulation Boolean Data manipulation Partial Response Manipulation
Response Manipulation methods. • Keep in mind the ease of exploitability / real world exploitation scenario for the case that you have found and mention in your reports as well. • Different techniques can be used at a same time for exploitation. • Less user Interaction leads to ease of exploitation ,which leads to higher severity. • Mentioning the above points will make your reports more convincing to the trigger. Takeaways


 sapt
 skipperchong
 axbom
 swwweet
 marketingsoph
 danielanewman
 mfonobong
 kneath
 retrage
 notwaldorf
 tonyrice
 holman
 ianozsvald