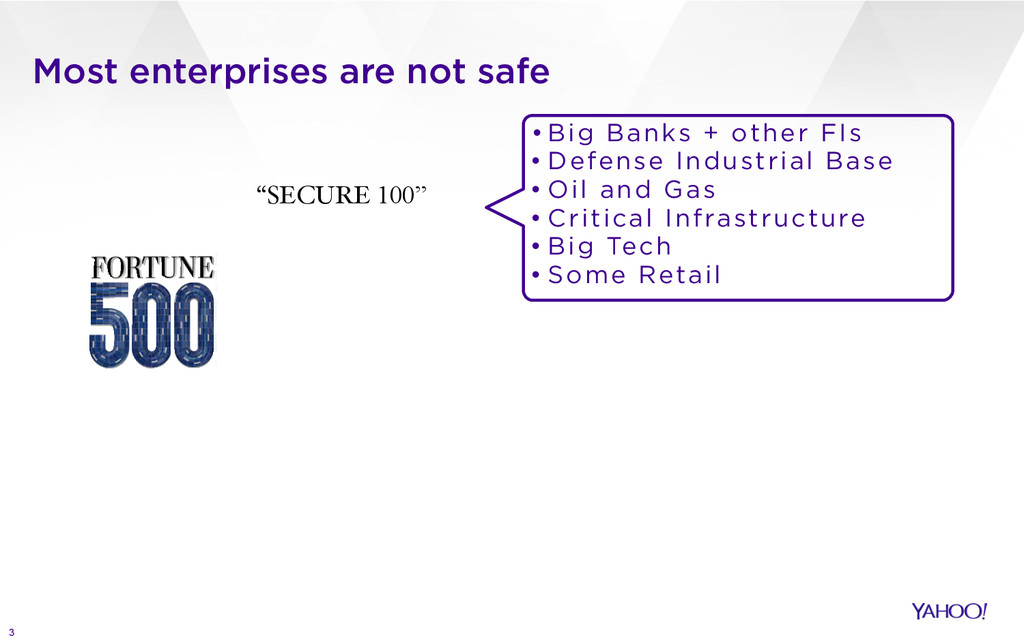
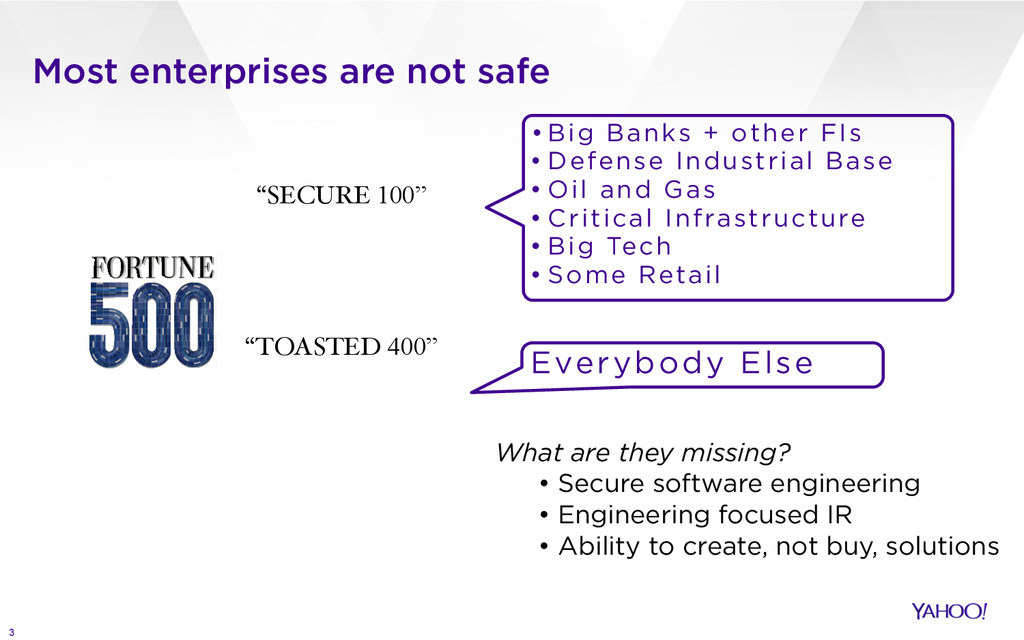
other FIs • Defense Industrial Base • Oil and Gas • Critical Infrastructure • Big Tech • Some Retail Everybody Else “SECURE 100” What are they missing? • Secure software engineering • Engineering focused IR • Ability to create, not buy, solutions “TOASTED 400”
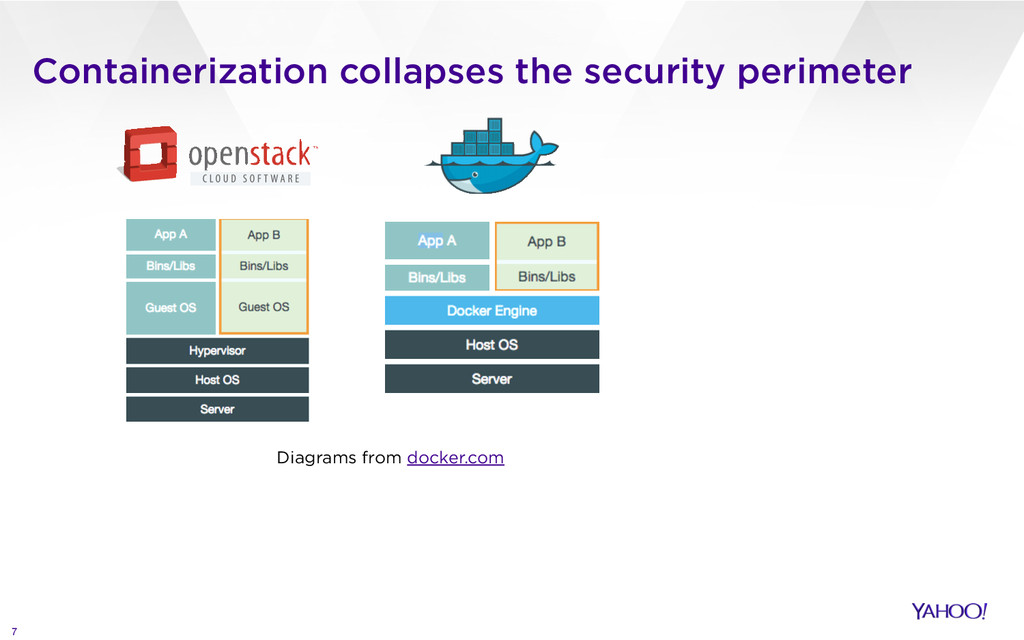
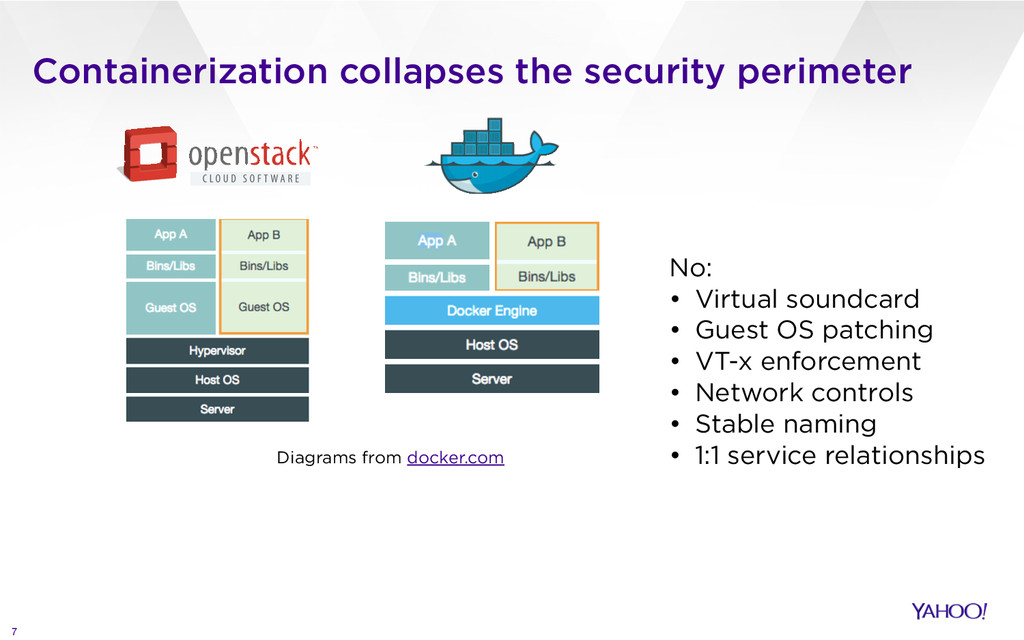
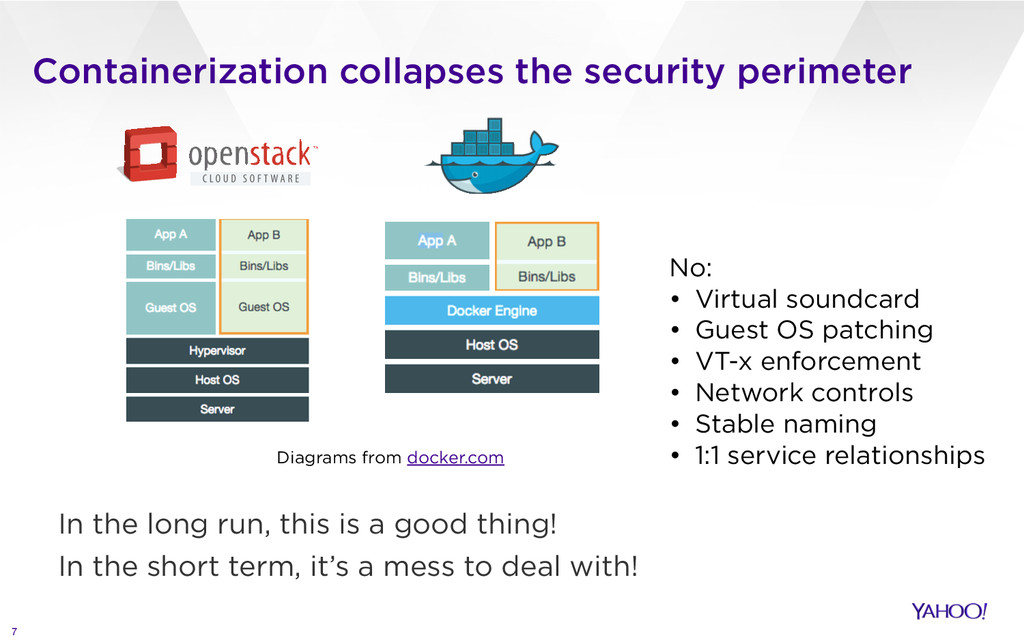
this is a good thing! In the short term, it’s a mess to deal with! No: • Virtual soundcard • Guest OS patching • VT-x enforcement • Network controls • Stable naming • 1:1 service relationships Diagrams from docker.com
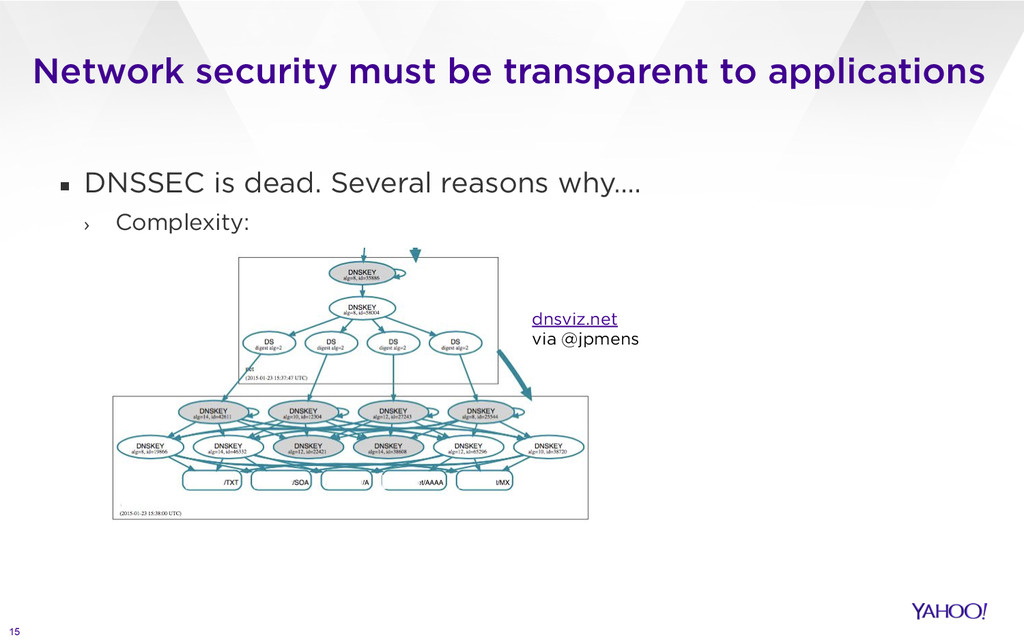
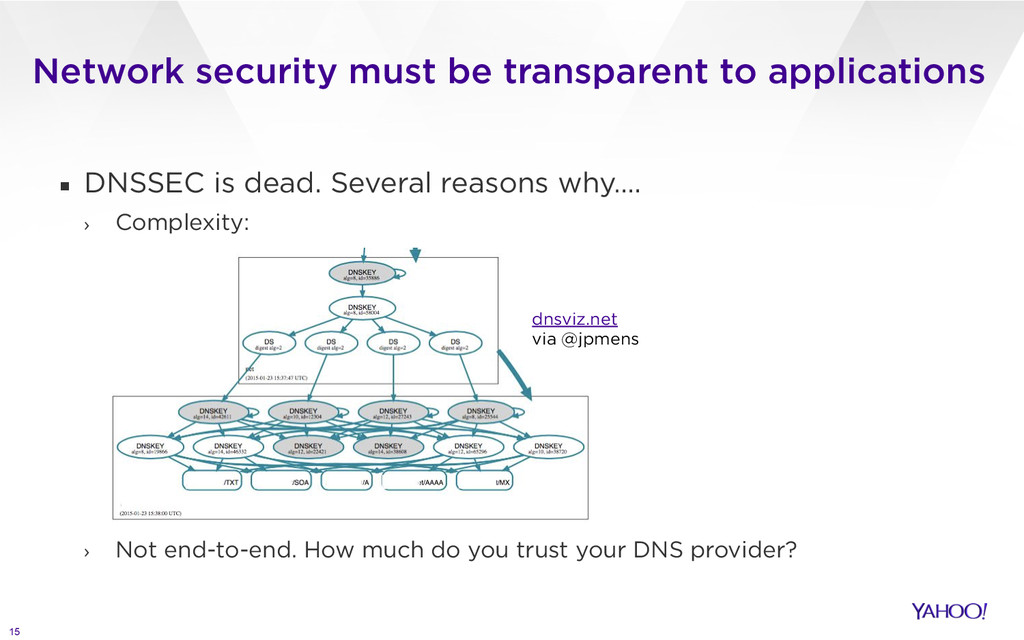
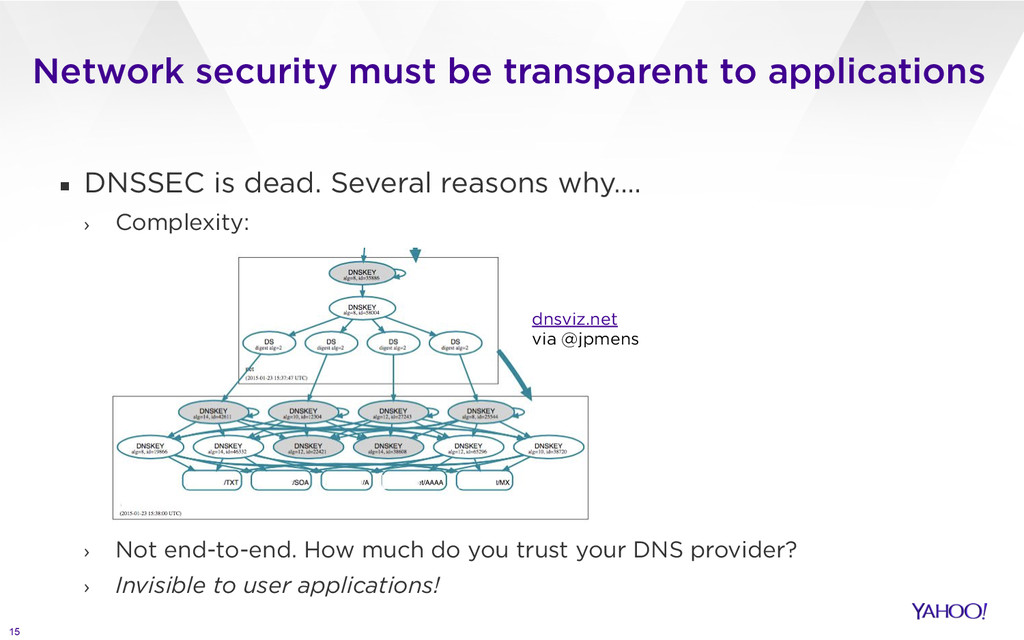
is dead. Several reasons why…. › Complexity: › Not end-to-end. How much do you trust your DNS provider? › Invisible to user applications! dnsviz.net via @jpmens
the default ▪ Automatically fixes itself ▪ Fails gracefully instead of failing insecurely and immediately ▪ Including client-side failures ▪ Recognizes the difficulties it’s users face
the default ▪ Automatically fixes itself ▪ Fails gracefully instead of failing insecurely and immediately ▪ Including client-side failures ▪ Recognizes the difficulties it’s users face ▪ Takes into account the entire lifecycle of the user
the default ▪ Automatically fixes itself ▪ Fails gracefully instead of failing insecurely and immediately ▪ Including client-side failures ▪ Recognizes the difficulties it’s users face ▪ Takes into account the entire lifecycle of the user Yes, I’m a security paternalist
matches ▪ SMS › Lowest common denominator › Surprisingly expensive › Unreliable › Insecure in many countries ▪ TOTP › Bad user experience › Many apps means no control over seeds
matches ▪ SMS › Lowest common denominator › Surprisingly expensive › Unreliable › Insecure in many countries ▪ Push notifications › Much more secure › Require more user interaction ▪ TOTP › Bad user experience › Many apps means no control over seeds
matches ▪ SMS › Lowest common denominator › Surprisingly expensive › Unreliable › Insecure in many countries ▪ Push notifications › Much more secure › Require more user interaction ▪ TOTP › Bad user experience › Many apps means no control over seeds None solve the account lifecycle management problem This is the #1 issue for user safety
work to do to: • Build apps with no L3 protections • Patch in our CI/CD pipelines • Provide end-to-end and transformable encryption • Make browsers more trustworthy than the OS
work to do to: • Build apps with no L3 protections • Patch in our CI/CD pipelines • Provide end-to-end and transformable encryption • Make browsers more trustworthy than the OS • More work for AppSec, less for the rest of security • Can we solve some of these problems without selling product
all users to be safe using any of our products from any country on any platform. I’m currently looking for a Director of Product Security to reinvent how we build safe products and meet this goal for 1.3B users


 appseccalifornia
 afnizarnur
 nikkihalliwell
 aleyda
 akashhashmi
 marketingsoph
 katarinadahlin
 gurzu
 davidcarrasco
 szymonslowik
 popppiees
 deanohume