Share
Embed
Transcript
33 slides
-
OSINT for AppSec:! Recon-ng and Beyond Tim Tomes! @lanmaster53! [email protected]
OSINT for AppSec: Recon-ng and Beyond - Tim Tomes 2015 ! 1! -
Managing Consultant @nVisium. Hacker looking out for users by training
______. Write code. Love Jesus. Drive fast. OSINT for AppSec: Recon-ng and Beyond - Tim Tomes 2015 ! 2! -
Disclaimer CAUTION: Live demos ahead. Offensive material is possible. While
I don’t condone it, preventing it wouldn’t be much fun. OSINT for AppSec: Recon-ng and Beyond - Tim Tomes 2015 ! 3! -
Credits Brian Fehrman – @fullmetalcache Micah Hoffman – @webbreacher Quentin
Kaiser – @qkaiser Offensive Security – @offsectraining John Poulin – @forced_request Mauro Soria – github.com/maurosoria OSINT for AppSec: Recon-ng and Beyond - Tim Tomes 2015 ! 4! -
What good is OSINT for an AppSec assessment when you
have source code? OSINT for AppSec: Recon-ng and Beyond - Tim Tomes 2015 ! 5! -
The “darker” the assessment, the more critical the need for
OSINT. OSINT for AppSec: Recon-ng and Beyond - Tim Tomes 2015 ! 6! -
Impact is the key to making risk decisions. OSINT for
AppSec: Recon-ng and Beyond - Tim Tomes 2015 ! 7! -
How can OSINT help me show risk from AppSec perspective?
OSINT for AppSec: Recon-ng and Beyond - Tim Tomes 2015 ! 8! -
Contacts What • usernames & email addresses Why • user
enumeration + no anti-automation + weak password policy = win • user enumeration + account lockout = win OSINT for AppSec: Recon-ng and Beyond - Tim Tomes 2015 ! 10! -
Contacts How • [recon-ng] > search -contacts – recon/domains-contacts/salesmaple – recon/contacts-contacts/mailtester •
scrape metadata from files. • tools vary • recon/domains-contacts/metacrawler OSINT for AppSec: Recon-ng and Beyond - Tim Tomes 2015 ! 11! #DEMO -
Profiles What • social media profiles, public or private Why
• user enumeration + no anti-automation + in- band password reset = win • LOW to PWNED, AppSec style. OSINT for AppSec: Recon-ng and Beyond - Tim Tomes 2015 ! 13! -
Profiles How • [recon-ng] > search -profiles – recon/companies-profiles/bing_linkedin – recon/profiles-profiles/linkedin_crawl – *recon/profiles-contacts/linkedin
– recon/profiles-profiles/profiler – recon/contacts-profiles/facebook_directory OSINT for AppSec: Recon-ng and Beyond - Tim Tomes 2015 ! 14! #DEMO -
Breaches What • username and password sets • breach details
Why • password reuse • pattern analysis • areas of weakness OSINT for AppSec: Recon-ng and Beyond - Tim Tomes 2015 ! 16! -
Breaches How • [recon-ng] > search -credentials – recon/domains-credentials/pwnedlist* – recon/contacts-credentials/hibp_breach – recon/contacts-credentials/hibp_paste
• https://www.privacyrights.org/data-breach – /data-breach-asc?title=<company> • https://zeltser.com/was-company-hacked/ • search OSINT for AppSec: Recon-ng and Beyond - Tim Tomes 2015 ! 17! -
Technologies What • client and server-side technologies • outdated software
Why • facilitates other attack vectors • direct exploitation of the infrastructure OSINT for AppSec: Recon-ng and Beyond - Tim Tomes 2015 ! 19! -
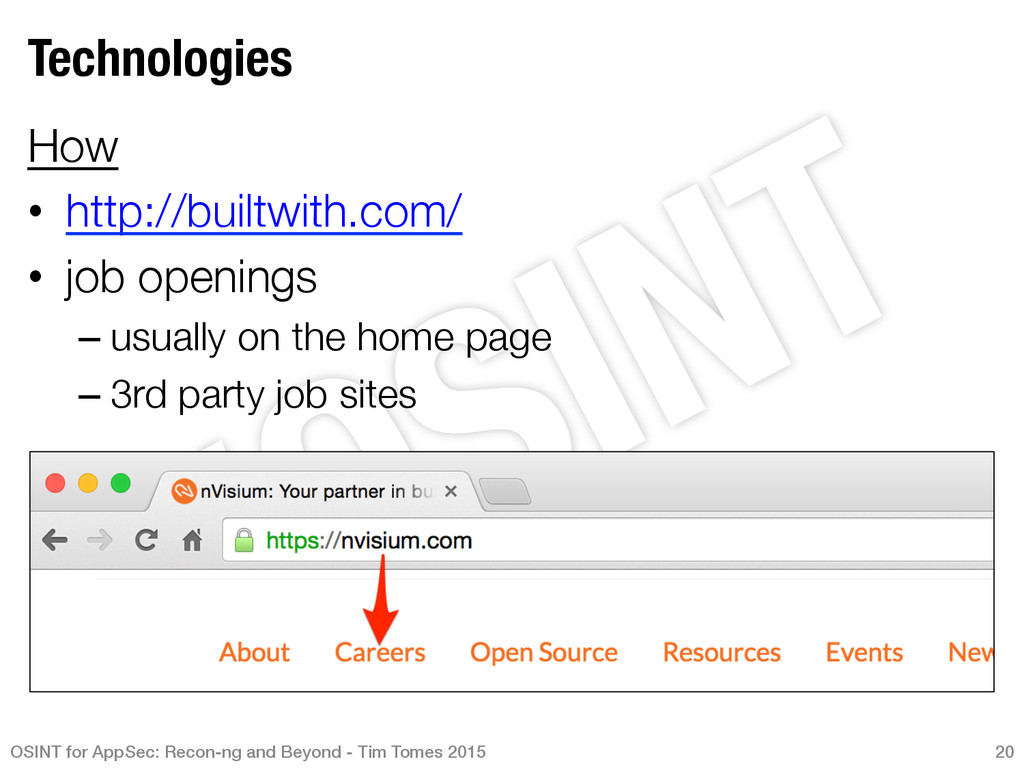
Technologies How • http://builtwith.com/ • job openings – usually on the
home page – 3rd party job sites OSINT for AppSec: Recon-ng and Beyond - Tim Tomes 2015 ! 20! -
Vulnerabilities What • exploitable vulnerabilities • source code leaks in
news groups, forums, etc. • searchable bugs Why • no/low effort vulnerability discovery • quick wins OSINT for AppSec: Recon-ng and Beyond - Tim Tomes 2015 ! 22! -
Dynamic Vulnerabilities How • online vulnerability scanners – PunkSPIDER -
https://www.punkspider.org/ – ASafaWeb - https://asafaweb.com/ • vulnerability disclosure sites – XSSposed - https://www.xssposed.org/ – Zone-H - http://zone-h.org/ • [recon-ng] > search -vulnerabilities – recon/domains-vulnerabilities/punkspider – recon/domains-vulnerabilities/xssposed • Target App must be public facing! OSINT for AppSec: Recon-ng and Beyond - Tim Tomes 2015 ! 23! -
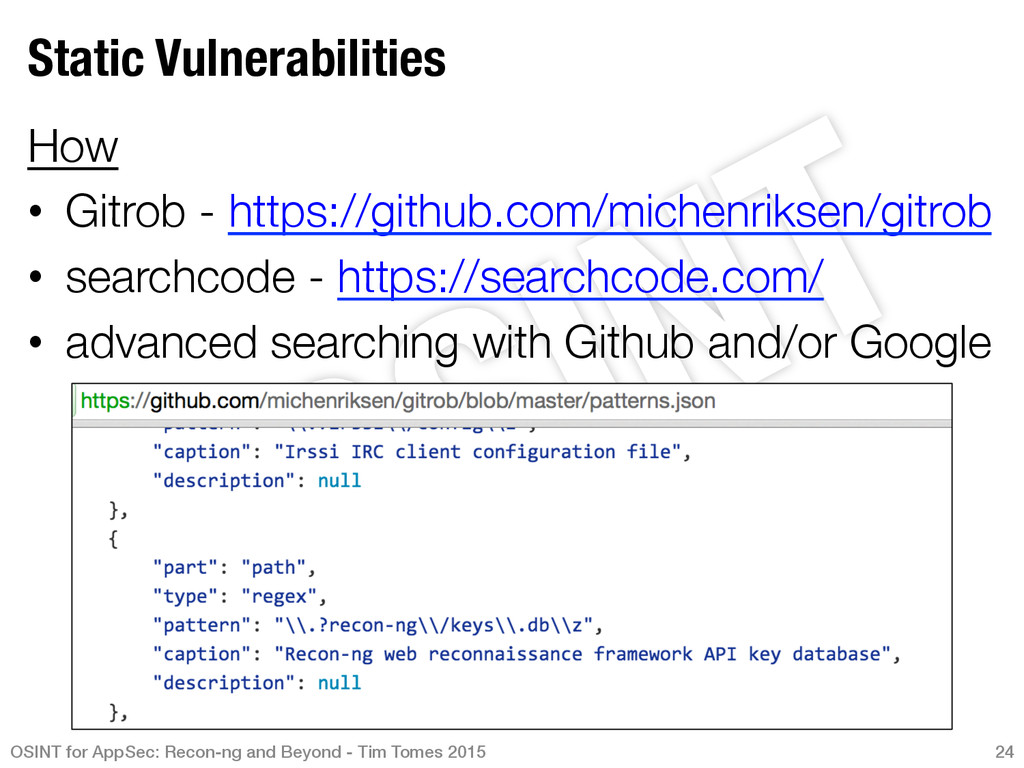
Static Vulnerabilities How • Gitrob - https://github.com/michenriksen/gitrob • searchcode -
https://searchcode.com/ • advanced searching with Github and/or Google OSINT for AppSec: Recon-ng and Beyond - Tim Tomes 2015 ! 24! -
Github Dorking • 2 approaches – use Github advanced search – use
Google with site:github.com • Github search forces you to include keywords. – path:.ssh/id_rsa BEGIN • Google “site” makes it harder to focus on a target. – inurl:secret_token filetype:rb site:github.com – inurl:secret_token filetype:rb site:github.com inurl:lockitron/selfstarter OSINT for AppSec: Recon-ng and Beyond - Tim Tomes 2015 ! 25! -
Github Dorking • “Goo-git” Dorks – Allows for searching more than
just Github. Bitbucket, etc. – Results not as reliable as searching directly. • [recon-ng] > search github – recon/companies-multi/github_miner – recon/profiles-repositories/github_repos – recon/repositories-vulnerabilities/github_dorks OSINT for AppSec: Recon-ng and Beyond - Tim Tomes 2015 ! 26! -
SENSITIVE INFORMATION OSINT for AppSec: Recon-ng and Beyond - Tim
Tomes 2015 ! 27! -
Sensitive Information What • debugging information • development notes •
out-of-band configuration storage Why • learn about apps in private repos • credentials & secret keys OSINT for AppSec: Recon-ng and Beyond - Tim Tomes 2015 ! 28! -
Sensitive Information How • Pastes • Gists – Devs treat them
like pastes. – Github doesn’t currently allow organizational Gists. – Grab the Gists of the organization’s developers. – Search for keywords, or just browse. • [recon-ng] > search gist – recon/repositories-vulnerabilities/gists_search OSINT for AppSec: Recon-ng and Beyond - Tim Tomes 2015 ! 29! -
GOOGLE HACKING DATABASE OSINT for AppSec: Recon-ng and Beyond -
Tim Tomes 2015 ! 30! -
Google Dorking • leads to credentials, source code snippets, contact
info, vulnerabilities, files, etc. • lots of dork sources – GHDB – Anonymous SQLi Google dorks – Goo-git dorks – custom dorks (appsec specific) • also, BHDB – http://www.bishopfox.com/download/876/ • [recon-ng] > search ghdb – recon/domains-vulnerabilities/ghdb OSINT for AppSec: Recon-ng and Beyond - Tim Tomes 2015 ! 31! #DEMO -
Final Thoughts • Nothing shown today requires pay-for API access.
It’s all free. • Please help me build out the lists of dorks and keywords. • Shout out to the guys at Offensive Security for maintaining and providing access to the GHDB. • Recon-ng as a Service (RAAS) • #PWAPT | 5-6 November, 2015 | Charlotte, NC http://appsec.rocks OSINT for AppSec: Recon-ng and Beyond - Tim Tomes 2015 ! 32! -
Tim Tomes @lanmaster53 [email protected] http://www.lanmaster53.com https://nvisium.com OSINT for AppSec: Recon-ng
and Beyond - Tim Tomes 2015 ! 33!