Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
最適なAWS環境を作るために~AWS Well-Architected Framework活用...
Search
Oshima
March 26, 2024
22
0
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
最適なAWS環境を作るために~AWS Well-Architected Framework活用のポイントと具体的行動~
Oshima
March 26, 2024
More Decks by Oshima
See All by Oshima
JAWS Days2024 B-5 AWS ConfigとAWS Organizationsを使ってセキュリティを強化しよう
oshima0306
0
230
Featured
See All Featured
Exploring the relationship between traditional SERPs and Gen AI search
raygrieselhuber
PRO
4
4.4k
Producing Creativity
orderedlist
PRO
348
41k
Efficient Content Optimization with Google Search Console & Apps Script
katarinadahlin
PRO
1
930
How STYLIGHT went responsive
nonsquared
100
6.3k
The Pragmatic Product Professional
lauravandoore
37
7.5k
Lessons Learnt from Crawling 1000+ Websites
charlesmeaden
PRO
1
1.6k
Data-driven link building: lessons from a $708K investment (BrightonSEO talk)
szymonslowik
1
1.4k
Distributed Sagas: A Protocol for Coordinating Microservices
caitiem20
333
23k
Reflections from 52 weeks, 52 projects
jeffersonlam
356
22k
Documentation Writing (for coders)
carmenintech
77
5.6k
How GitHub (no longer) Works
holman
316
150k
Making Projects Easy
brettharned
120
6.8k
Transcript
Copyright © IDS Co., LTD. All rights reserved. 1 Confidential
第2部 ログ記録
Copyright © IDS Co., LTD. All rights reserved. 2 Confidential
2 自己紹介 ログ記録 名前: 大島雪乃 経歴: 株式会社アイディーエス サニークラウド事業部 好きなもの: 猫とビール 好きなAWSサービス: AWS Organizations
Copyright © IDS Co., LTD. All rights reserved. 3 Confidential
3 Agenda 01. アンチパターン 02. アンチパターンに対しての解決策 03. 具体的な設定例のご紹介 ログ記録
Copyright © IDS Co., LTD. All rights reserved. 4 Confidential
ログ記録 アンチパターン • 必要な場合に備えて、あらゆるタイプのログを保存する。 • ログが永久に保存される、またはすぐに削除される。 • 誰でもログにアクセスできる。 • 必要な場合にのみログ整合性をチェックする。 • ログガバナンスと使用について、手動プロセスのみに依存する。
Copyright © IDS Co., LTD. All rights reserved. 7 Confidential
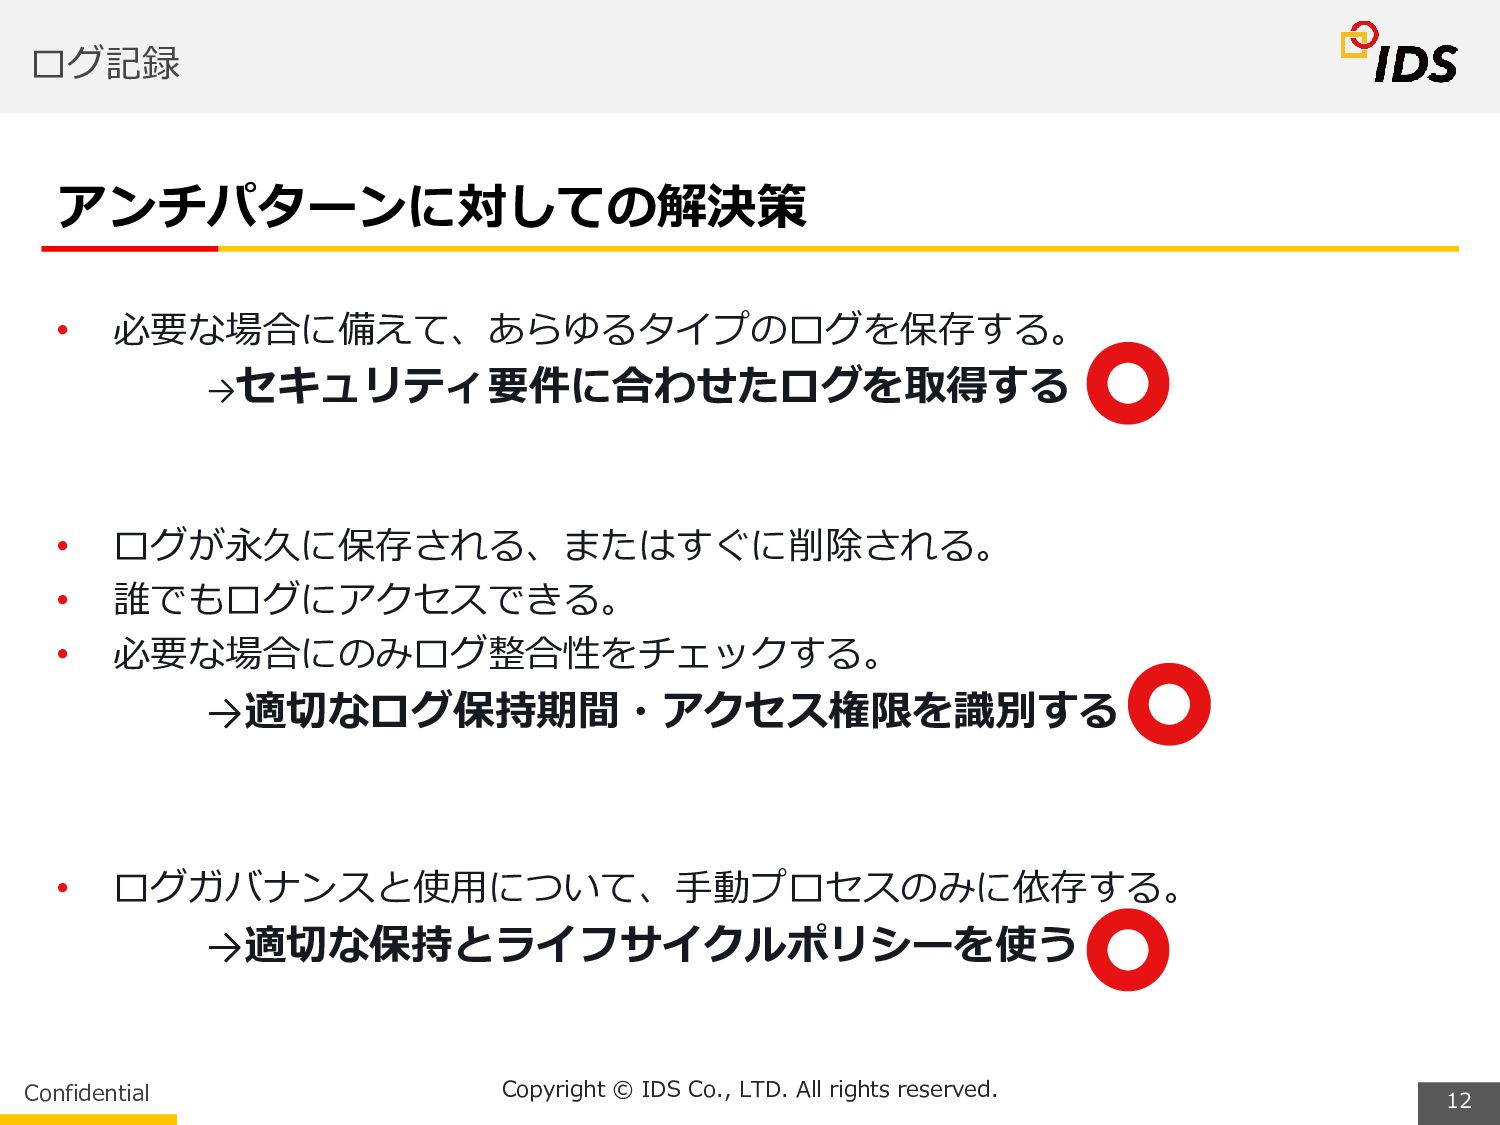
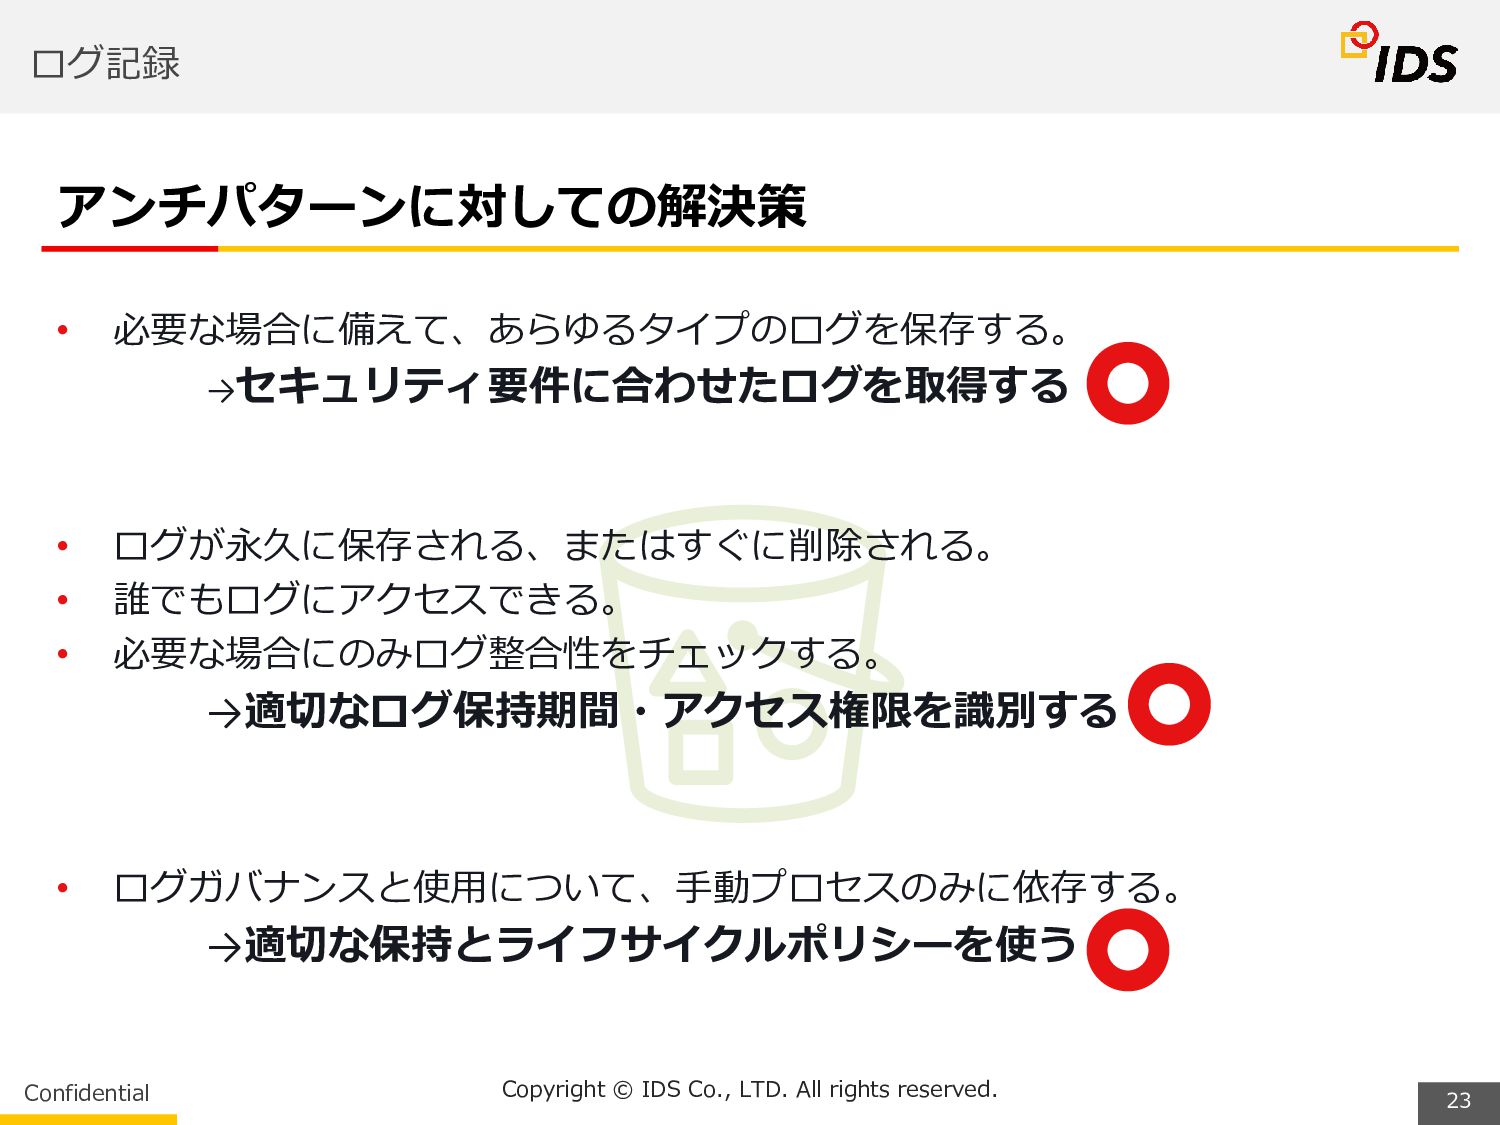
ログ記録 アンチパターンに対しての解決策 • 必要な場合に備えて、あらゆるタイプのログを保存する。 →セキュリティ要件に合わせたログを取得する • ログが永久に保存される、またはすぐに削除される。 • 誰でもログにアクセスできる。 • 必要な場合にのみログ整合性をチェックする。 →適切なログ保持期間・アクセス権限を識別する • ログガバナンスと使用について、手動プロセスのみに依存する。 →適切な保持とライフサイクルポリシーを使う
Copyright © IDS Co., LTD. All rights reserved. 8 Confidential
ログ記録 –アンチパターンに対しての解決策- セキュリティ要件に合わせたログを取得する AWSのサービスのログ 環境に合わせたログ 取得するログの種類 ログ名 CloudTrailログ(AWS) VPCフローログ(AWS) ALBアクセスログ(AWS) /var/log/message(OS) /var/log/secure(OS) 監査ログ(アプリ) アクセスログ(アプリ)
Copyright © IDS Co., LTD. All rights reserved. 9 Confidential
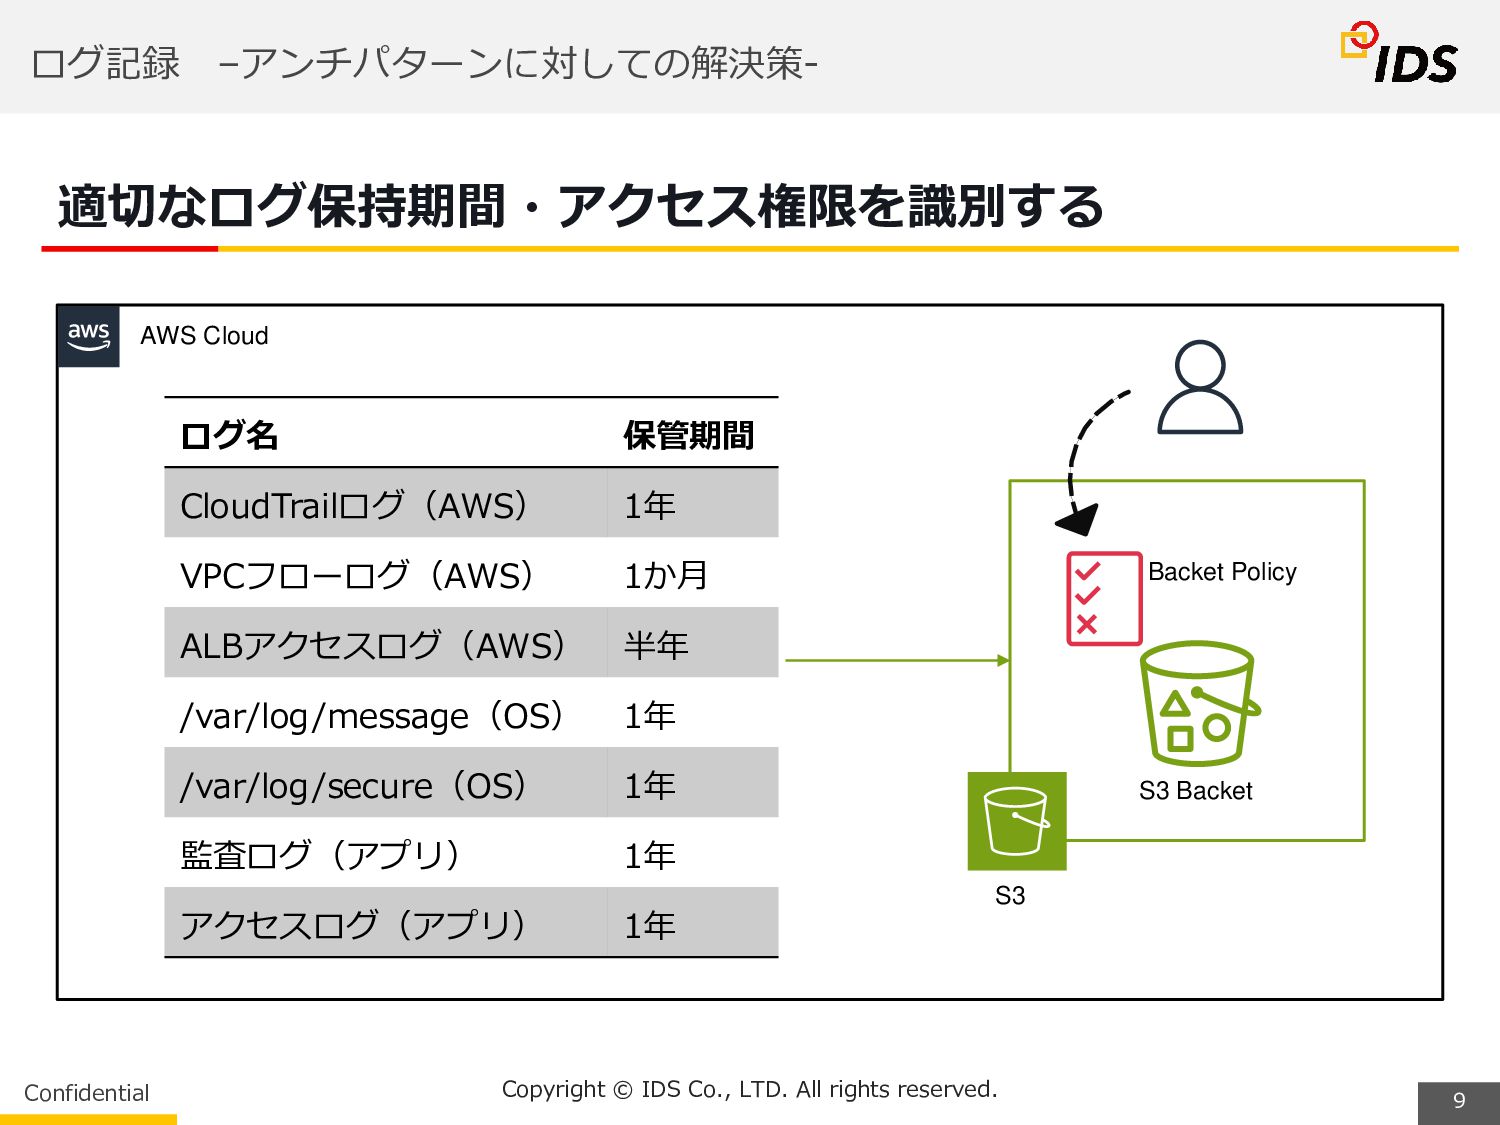
適切なログ保持期間・アクセス権限を識別する ログ名 保管期間 CloudTrailログ(AWS) 1年 VPCフローログ(AWS) 1か月 ALBアクセスログ(AWS) 半年 /var/log/message(OS) 1年 /var/log/secure(OS) 1年 監査ログ(アプリ) 1年 アクセスログ(アプリ) 1年 AWS Cloud S3 S3 Backet Backet Policy ログ記録 –アンチパターンに対しての解決策-
Copyright © IDS Co., LTD. All rights reserved. 11 Confidential
適切な保持とライフサイクルポリシーを使う S3 Standard S3 標準-IA ログファイルA アップロード 0日 90日 180日 365日 ログファイルA の削除 アクセス頻度の高い ファイル向け アクセス頻度が低いが すぐに取り出す必要 があるファイル向け アクセスがほぼなく、 即時取り出しを必要 としないファイル向け S3 Glacier Flexible Retrieval ログ記録 –アンチパターンに対しての解決策-
Copyright © IDS Co., LTD. All rights reserved. 12 Confidential
ログ記録 アンチパターンに対しての解決策 • 必要な場合に備えて、あらゆるタイプのログを保存する。 →セキュリティ要件に合わせたログを取得する • ログが永久に保存される、またはすぐに削除される。 • 誰でもログにアクセスできる。 • 必要な場合にのみログ整合性をチェックする。 →適切なログ保持期間・アクセス権限を識別する • ログガバナンスと使用について、手動プロセスのみに依存する。 →適切な保持とライフサイクルポリシーを使う
Copyright © IDS Co., LTD. All rights reserved. 13 Confidential
ログ記録 設定例のご紹介
Copyright © IDS Co., LTD. All rights reserved. 14 Confidential
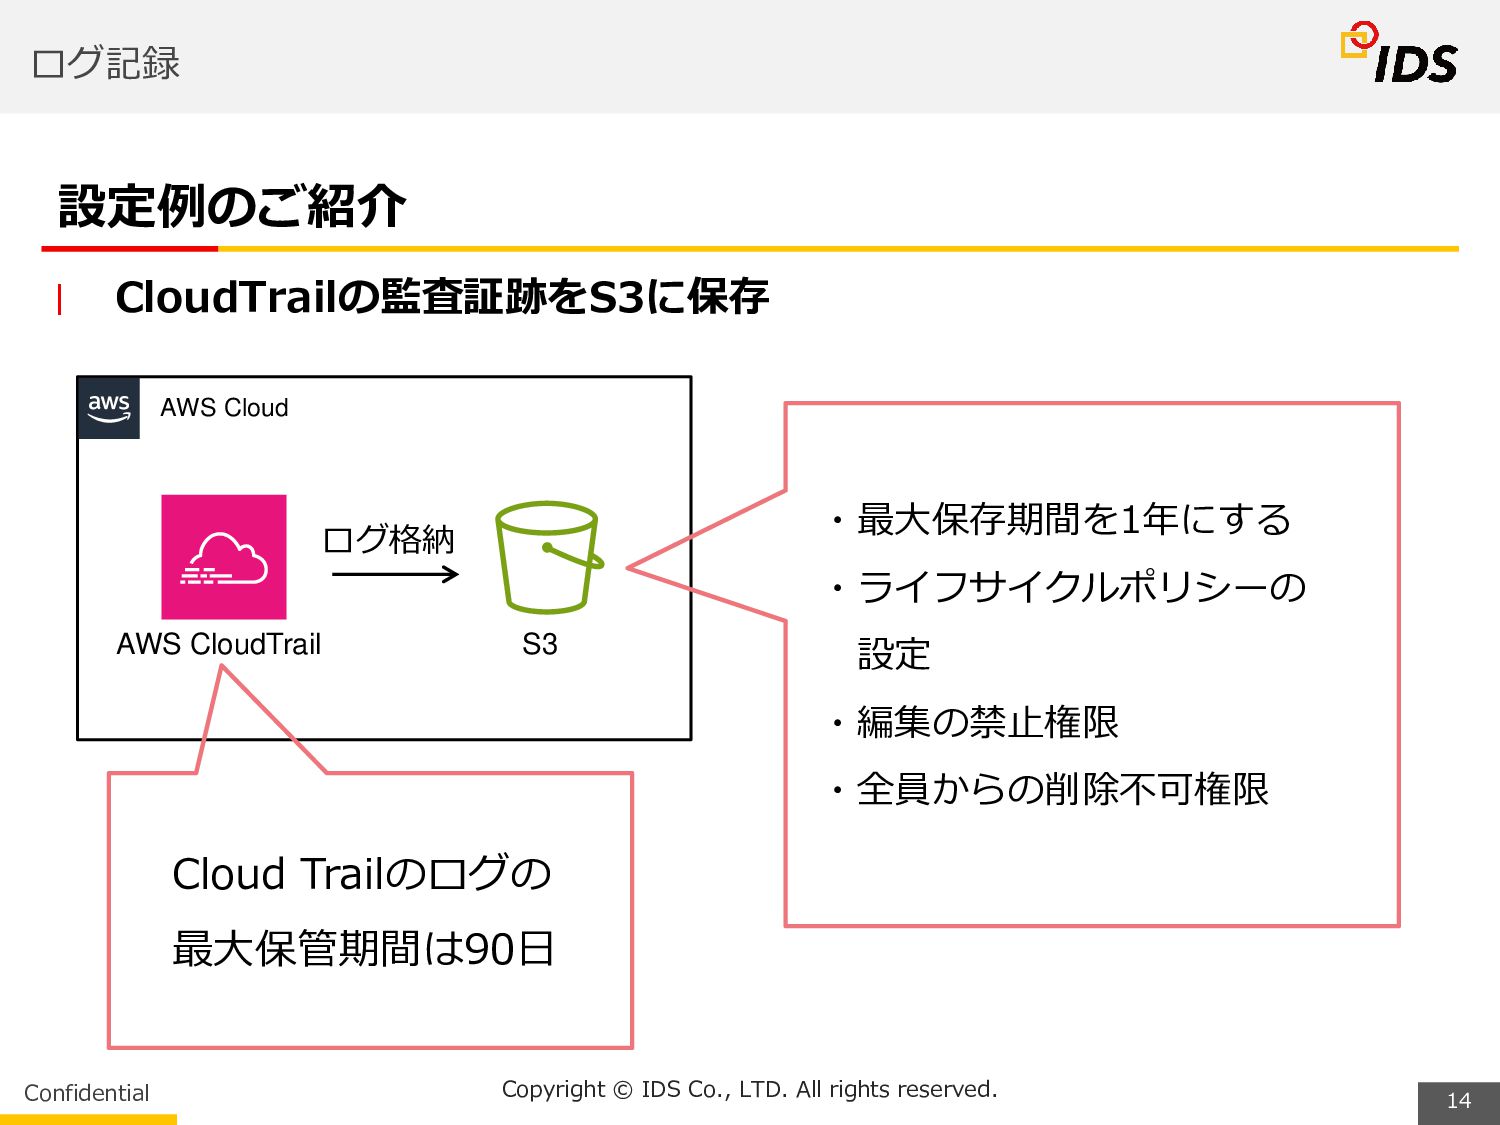
ログ記録 設定例のご紹介 CloudTrailの監査証跡をS3に保存 AWS Cloud AWS CloudTrail S3 Cloud Trailのログの 最大保管期間は90日 ・最大保存期間を1年にする ・ライフサイクルポリシーの 設定 ・編集の禁止権限 ・全員からの削除不可権限 ログ格納
Copyright © IDS Co., LTD. All rights reserved. 15 Confidential
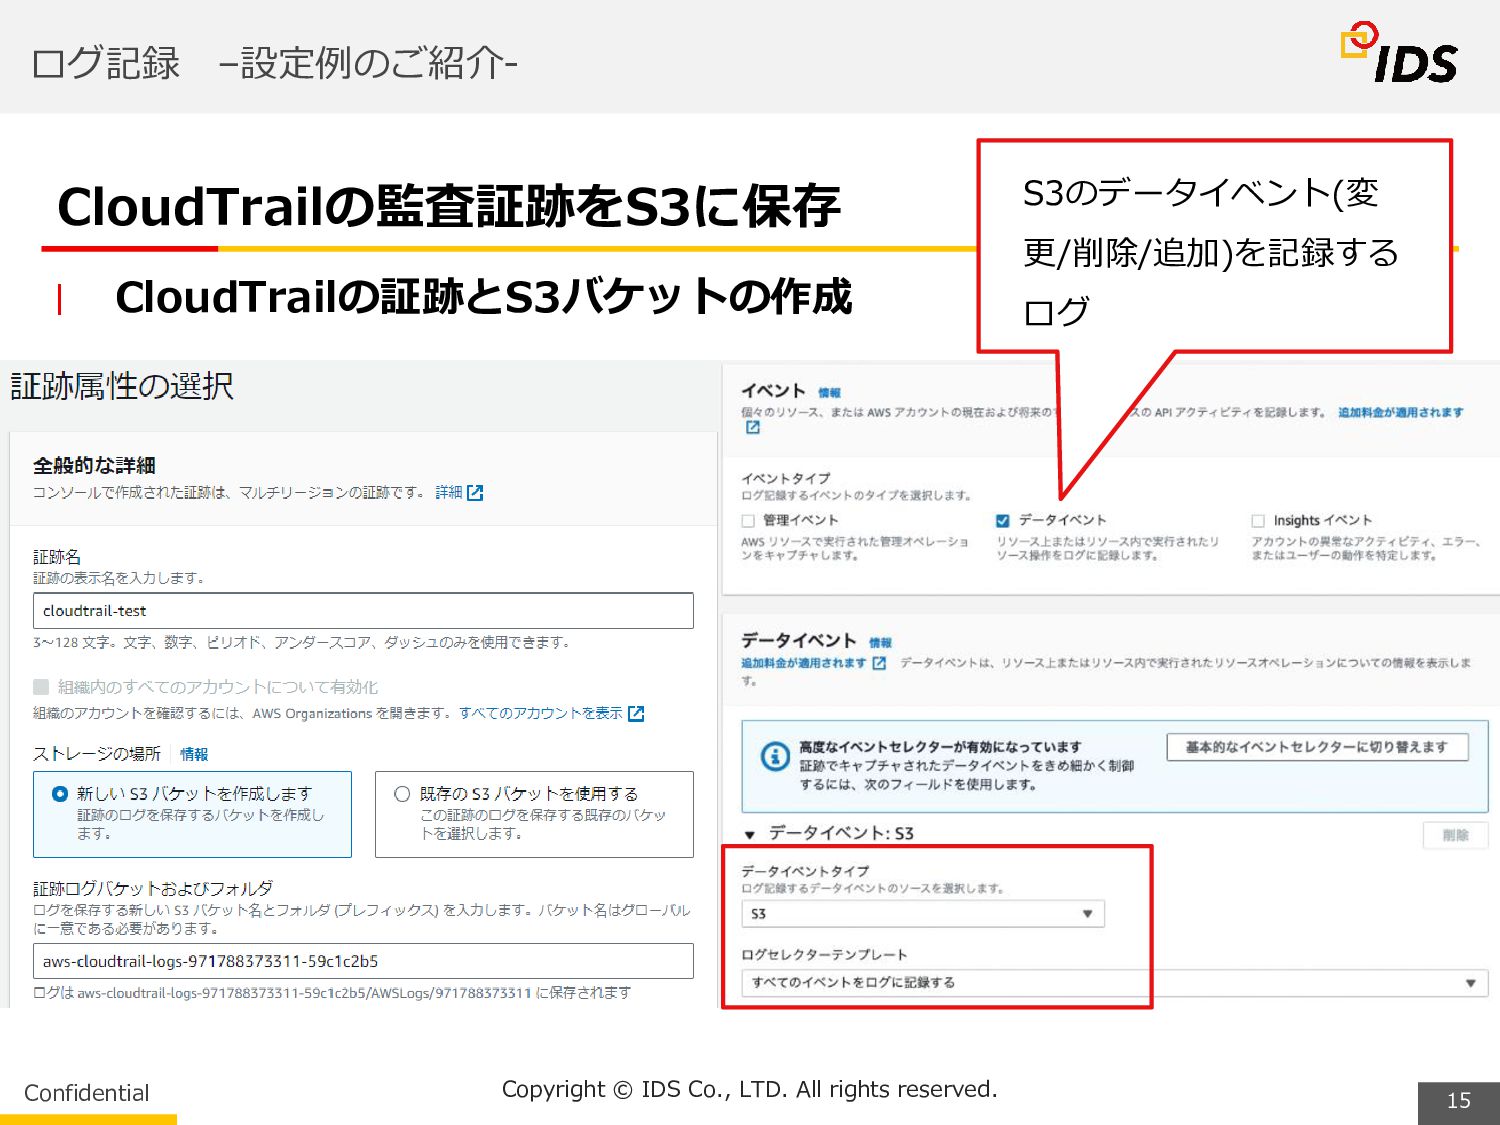
ログ記録 –設定例のご紹介- CloudTrailの監査証跡をS3に保存 CloudTrailの証跡とS3バケットの作成 S3のデータイベント(変 更/削除/追加)を記録する ログ
Copyright © IDS Co., LTD. All rights reserved. 16 Confidential
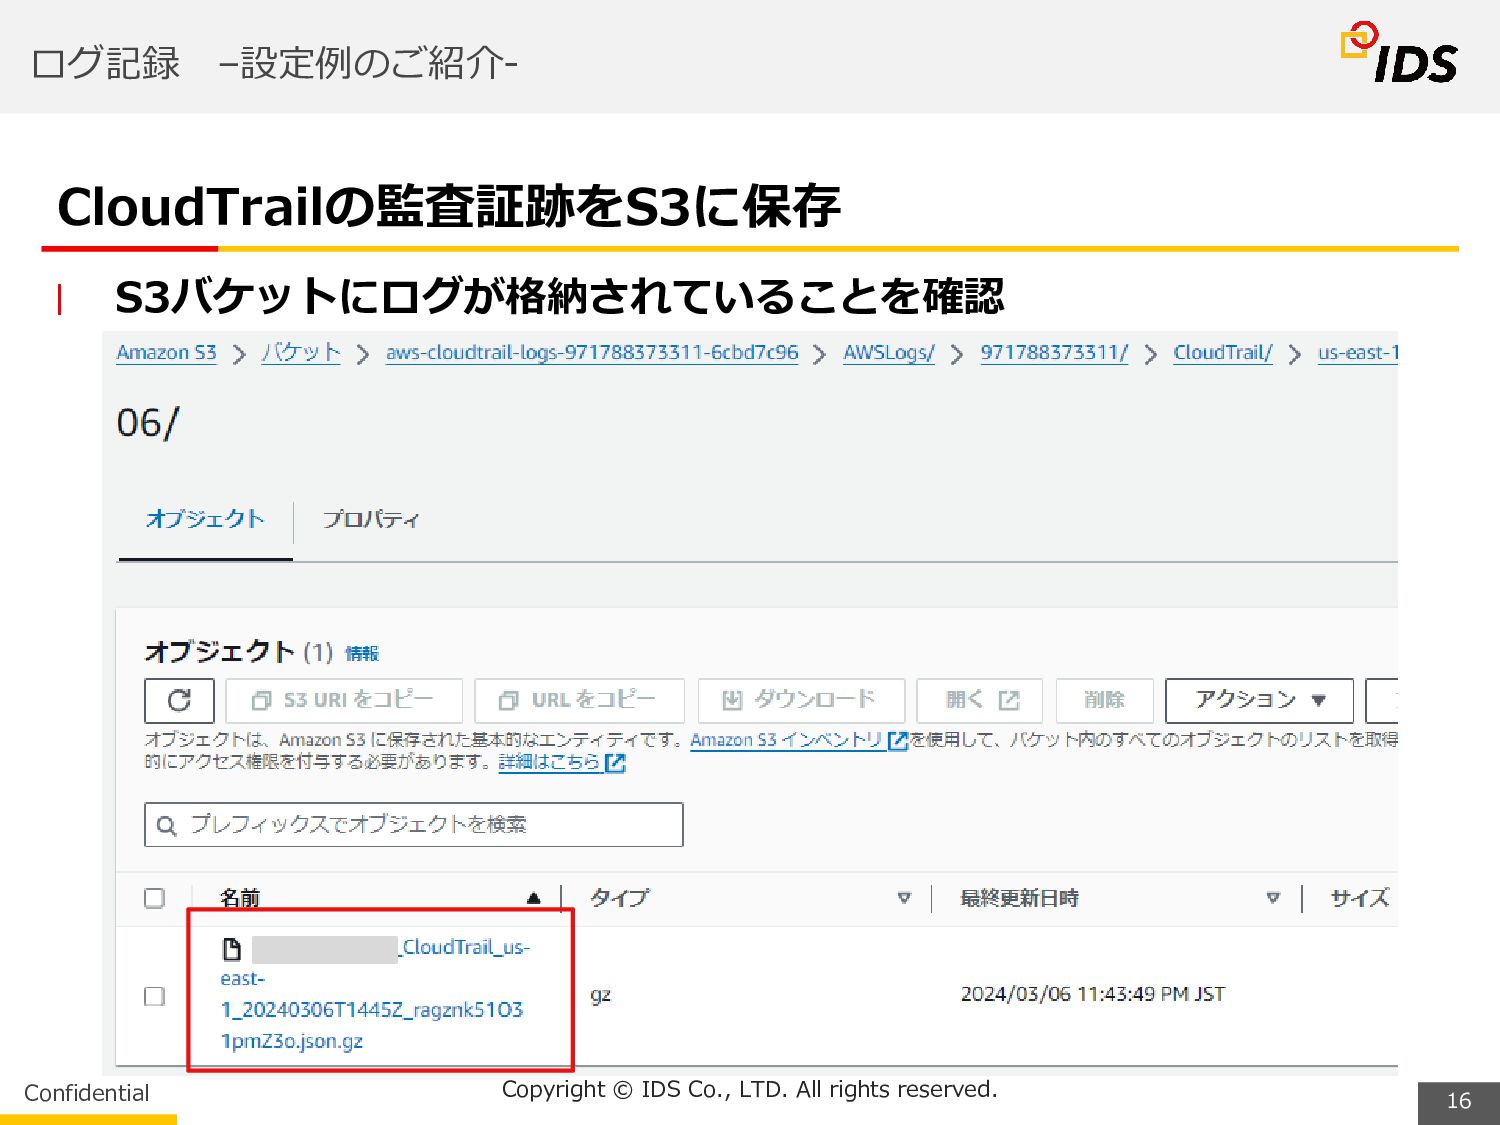
CloudTrailの監査証跡をS3に保存 S3バケットにログが格納されていることを確認 ログ記録 –設定例のご紹介-
Copyright © IDS Co., LTD. All rights reserved. 17 Confidential
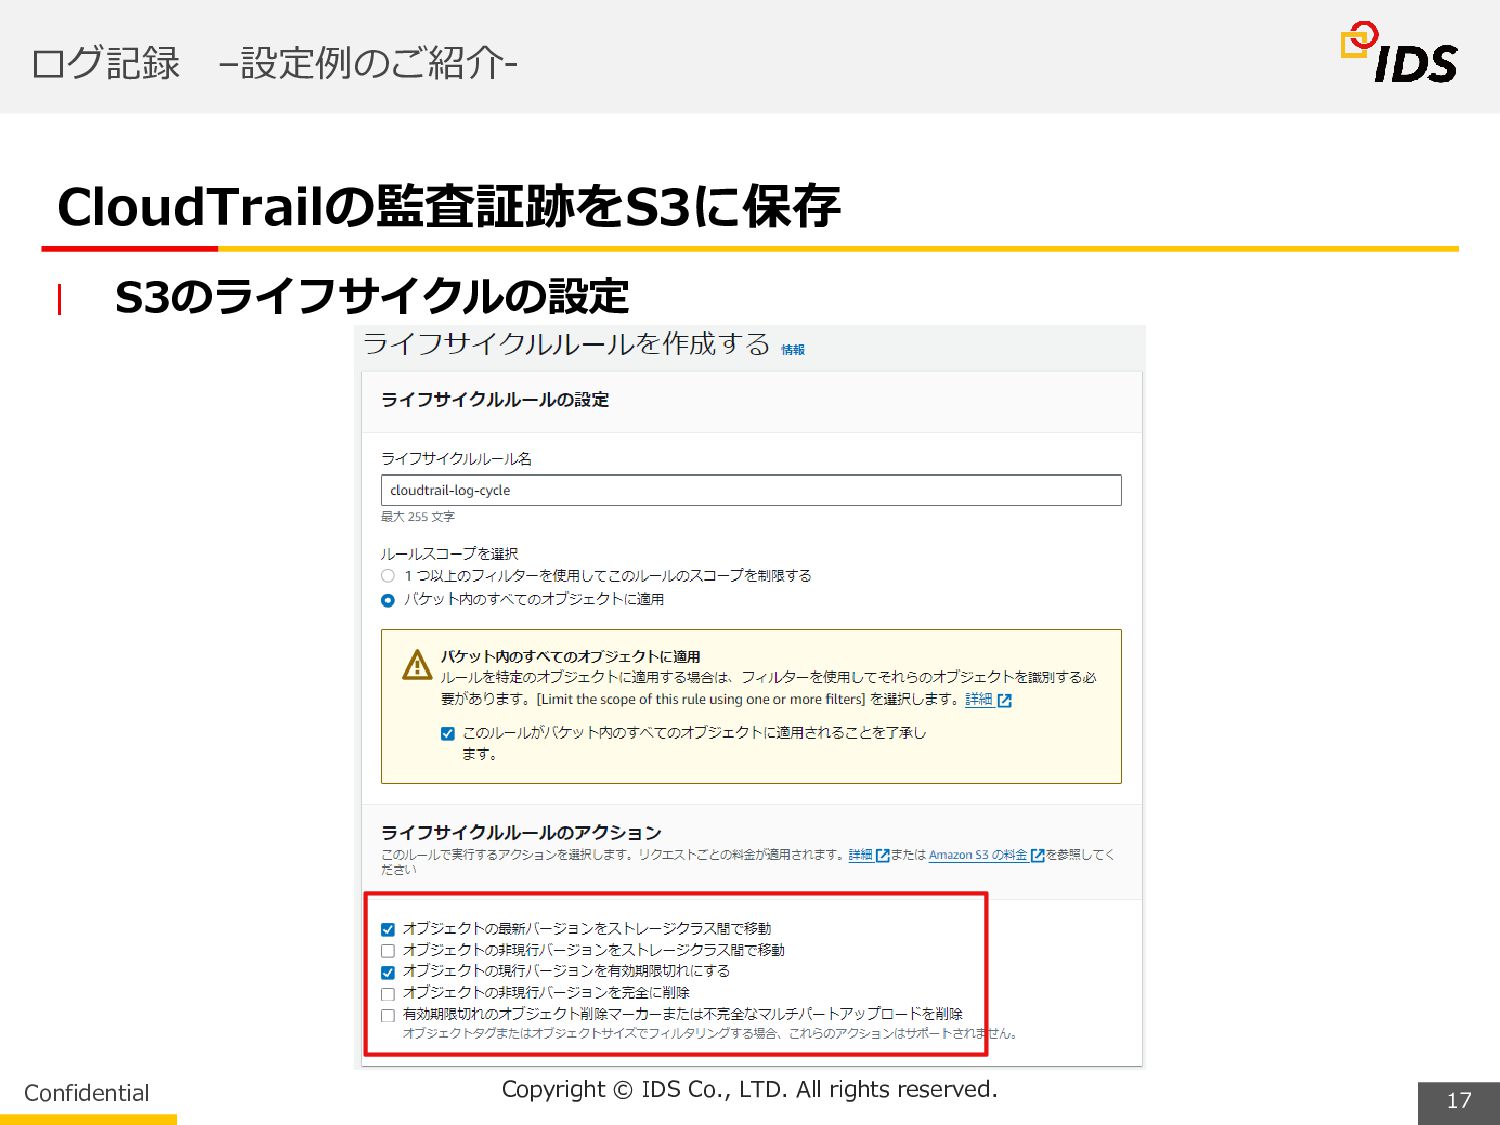
ログ記録 –設定例のご紹介- CloudTrailの監査証跡をS3に保存 S3のライフサイクルの設定
Copyright © IDS Co., LTD. All rights reserved. 18 Confidential
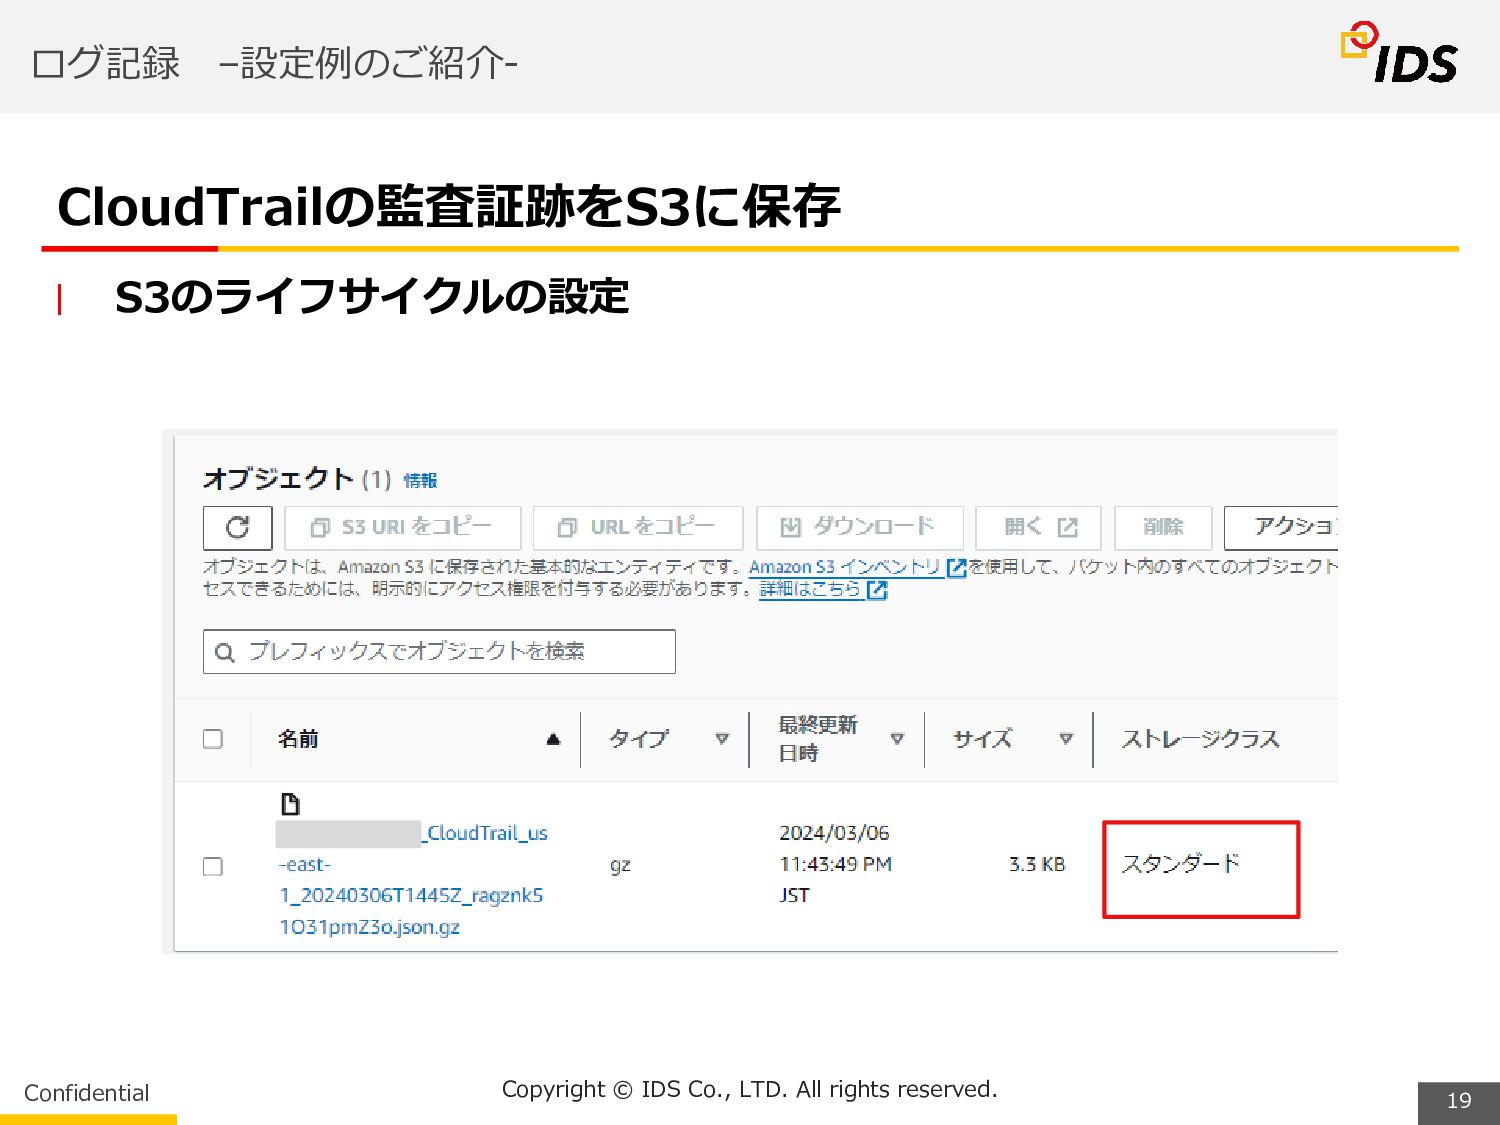
ログ記録 –設定例のご紹介- CloudTrailの監査証跡をS3に保存 S3のライフサイクルの設定 S3 Standard 0日 90日 S3 Glacier Flexible Retrieval 365日 削除
Copyright © IDS Co., LTD. All rights reserved. 19 Confidential
ログ記録 –設定例のご紹介- CloudTrailの監査証跡をS3に保存 S3のライフサイクルの設定
Copyright © IDS Co., LTD. All rights reserved. 20 Confidential
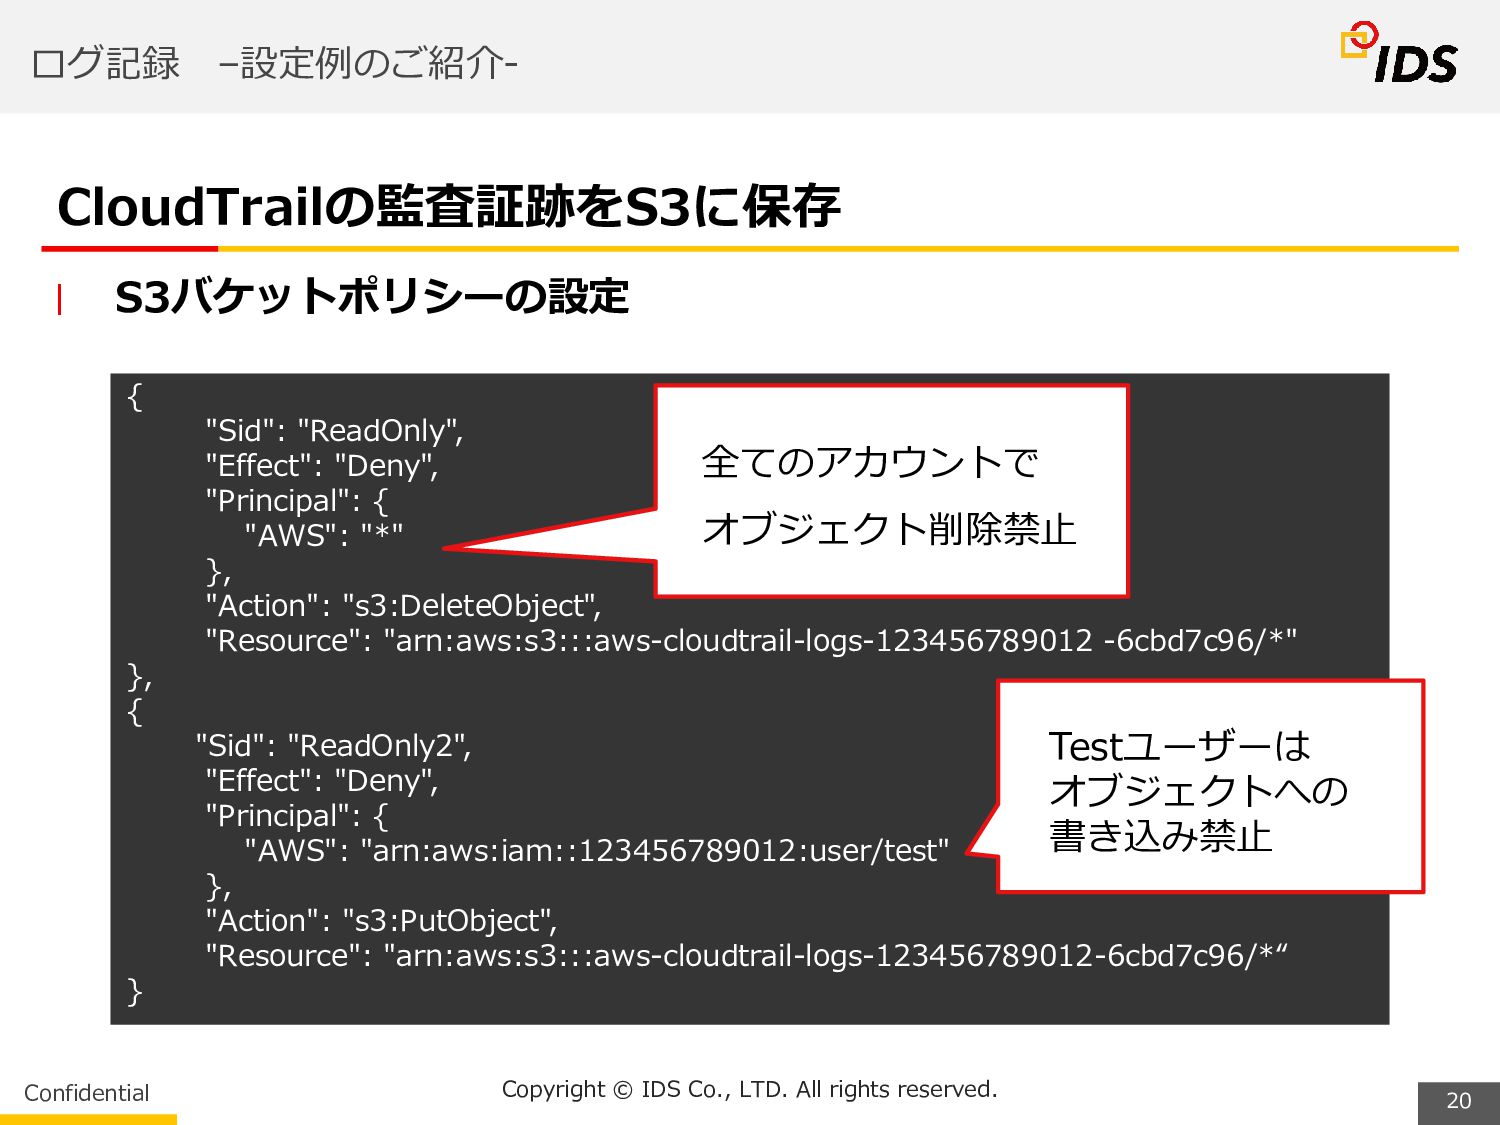
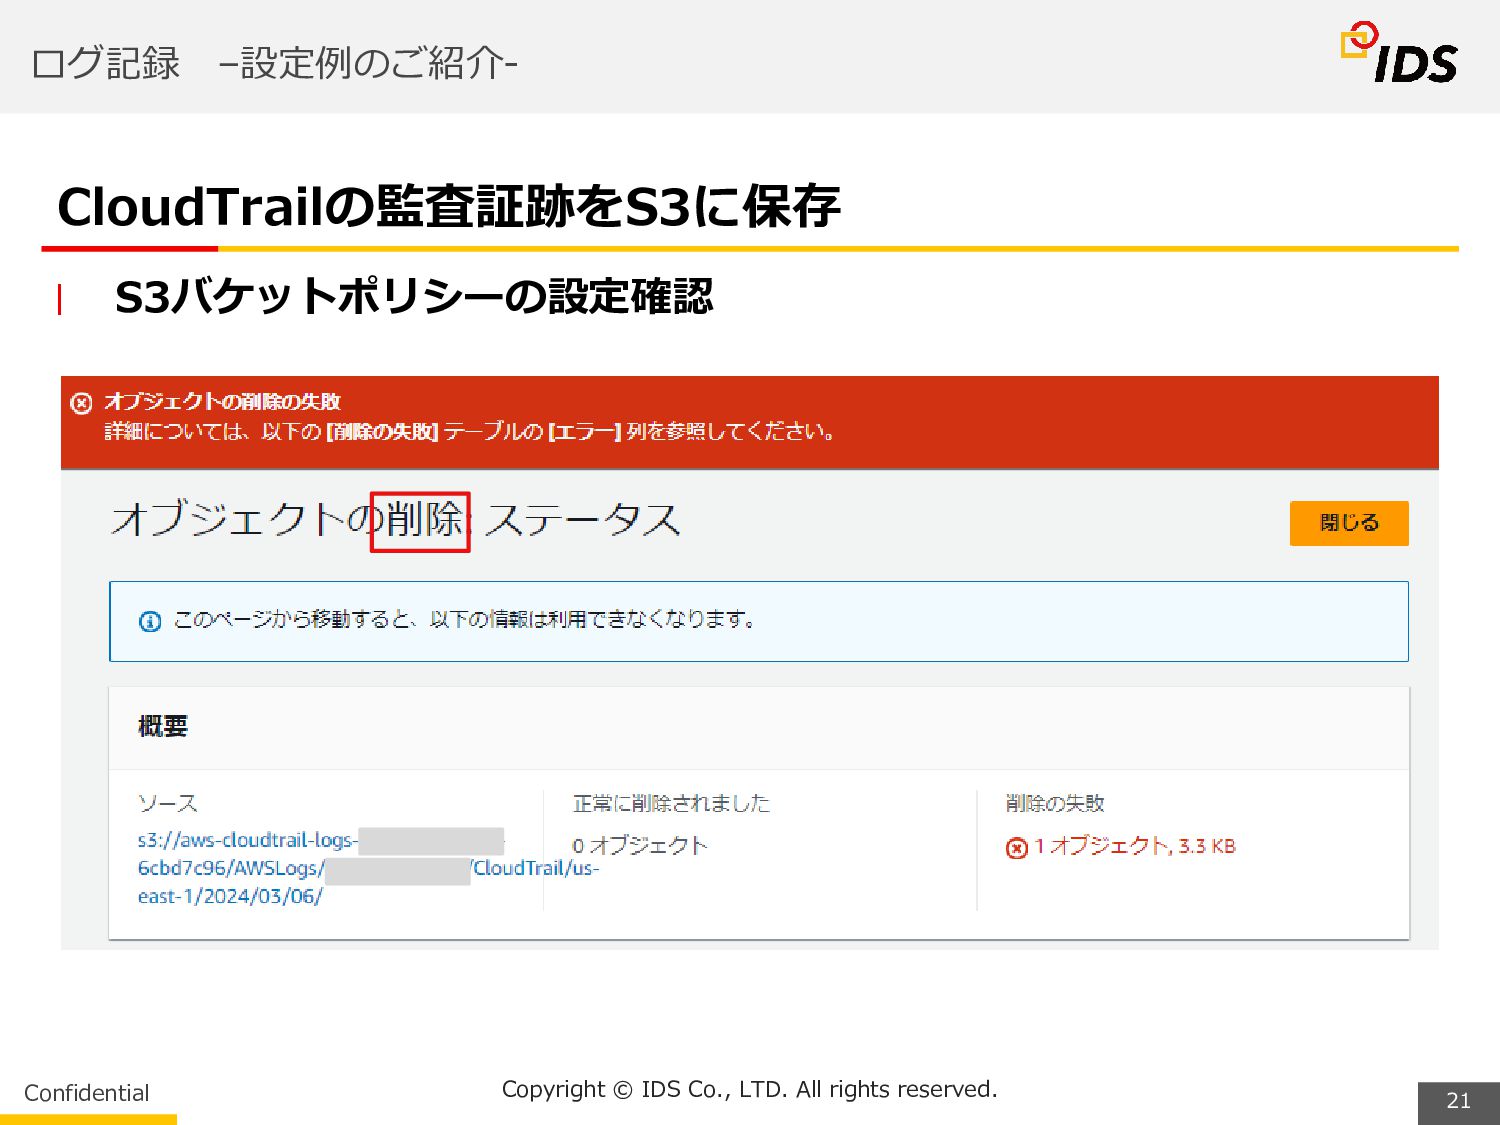
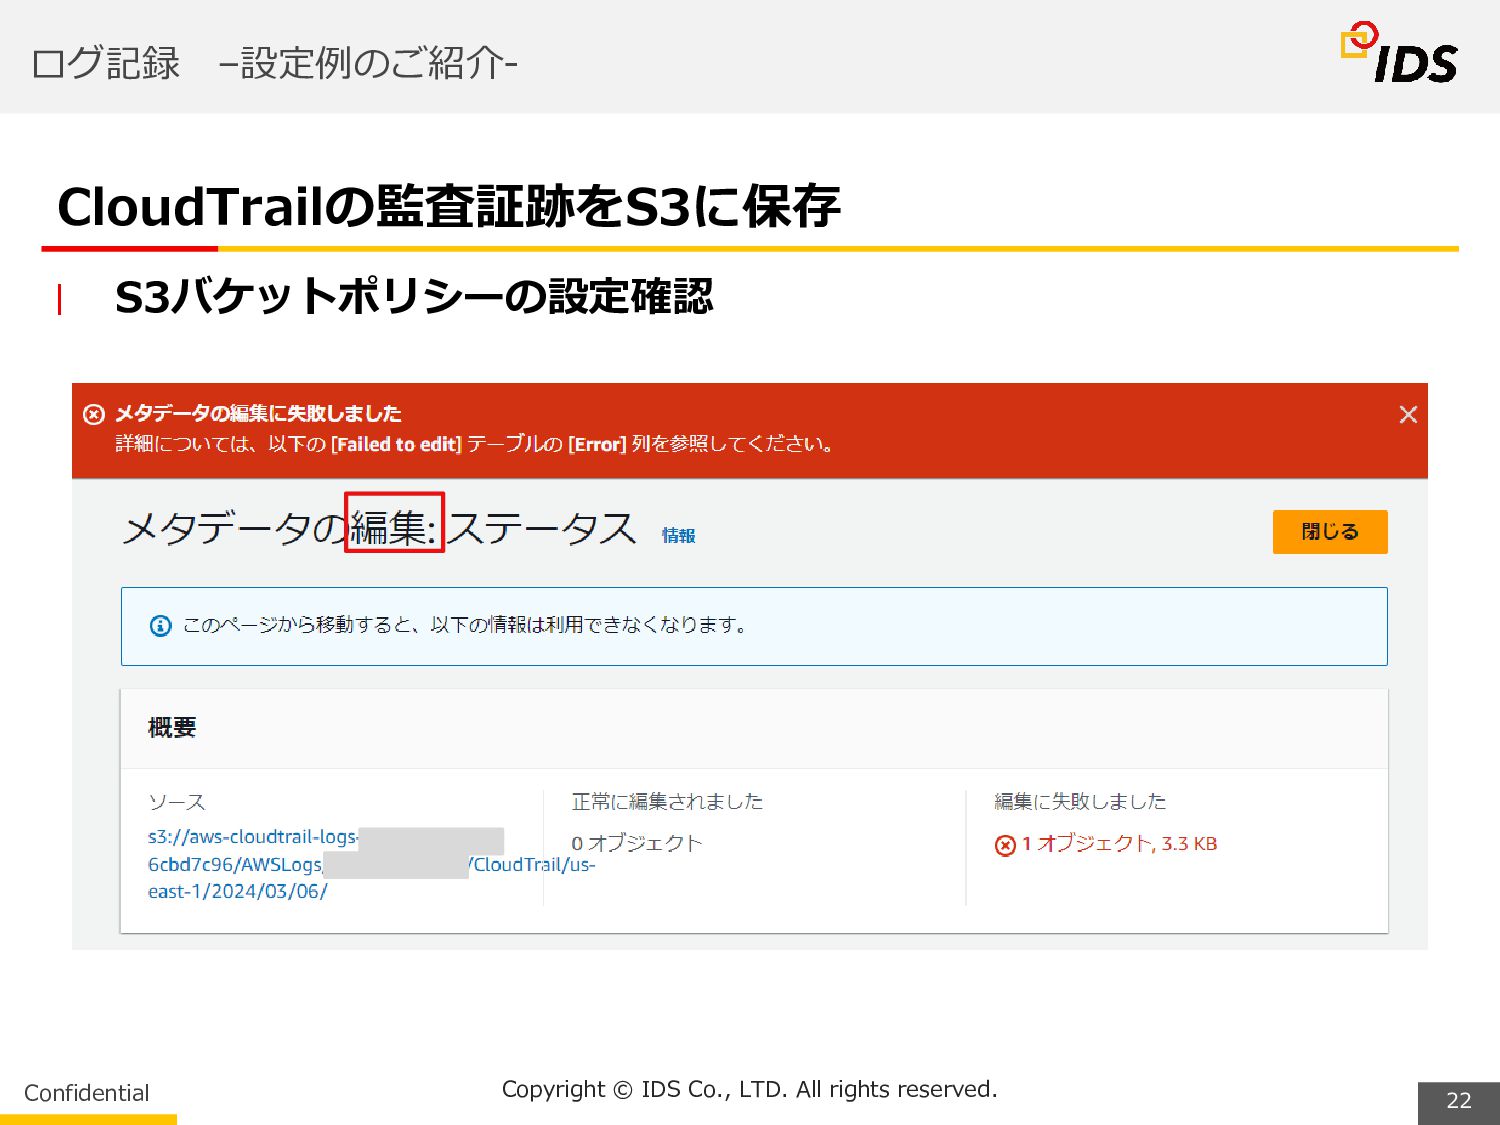
ログ記録 –設定例のご紹介- CloudTrailの監査証跡をS3に保存 S3バケットポリシーの設定 { "Sid": "ReadOnly", "Effect": "Deny", "Principal": { "AWS": "*" }, "Action": "s3:DeleteObject", "Resource": "arn:aws:s3:::aws-cloudtrail-logs-123456789012 -6cbd7c96/*" }, { "Sid": "ReadOnly2", "Effect": "Deny", "Principal": { "AWS": "arn:aws:iam::123456789012:user/test" }, "Action": "s3:PutObject", "Resource": "arn:aws:s3:::aws-cloudtrail-logs-123456789012-6cbd7c96/*“ } 全てのアカウントで オブジェクト削除禁止 Testユーザーは オブジェクトへの 書き込み禁止
Copyright © IDS Co., LTD. All rights reserved. 21 Confidential
ログ記録 –設定例のご紹介- CloudTrailの監査証跡をS3に保存 S3バケットポリシーの設定確認
Copyright © IDS Co., LTD. All rights reserved. 22 Confidential
ログ記録 –設定例のご紹介- CloudTrailの監査証跡をS3に保存 S3バケットポリシーの設定確認
Copyright © IDS Co., LTD. All rights reserved. 23 Confidential
ログ記録 アンチパターンに対しての解決策 • 必要な場合に備えて、あらゆるタイプのログを保存する。 →セキュリティ要件に合わせたログを取得する • ログが永久に保存される、またはすぐに削除される。 • 誰でもログにアクセスできる。 • 必要な場合にのみログ整合性をチェックする。 →適切なログ保持期間・アクセス権限を識別する • ログガバナンスと使用について、手動プロセスのみに依存する。 →適切な保持とライフサイクルポリシーを使う
Copyright © IDS Co., LTD. All rights reserved. 24 Confidential
Q&A


 oshima0306
 raygrieselhuber
 orderedlist
 katarinadahlin
 nonsquared
 lauravandoore
 charlesmeaden
 szymonslowik
 caitiem20
 jeffersonlam
 carmenintech
 holman
 brettharned