Share
Embed
Mantis - Asset Discovery at Scale
Presented at BlackHat Europe Arsenal 2023
Bharath
December 14, 2023
Transcript
25 slides
-
ABOUT US OUR TEAM DEVELOPER EXPERT DESIGN Praveen Kanniah
Loves Application Security. Breaks “Complexity Bias” Prateek Thakare Loves coding. Breaks business logics. Bharath Kumar “Charts the Uncharted” Loves Attack Surface Management -
Automated Asset Discovery, Recon and Scanning Framework Mantis is a
command-line tool with dashboard support, streamlining the entire work fl ow by automating the process of asset discovery, reconnaissance, and vulnerability scanning on the identi fi ed assets. Its capabilities also extends to supporting distributed scanning IS A MANTIS -
Tailored for Product security teams Scalability and Ef fi ciency
Not just a tool collection framework Existing frameworks are designed to cater bug bounty professionals mostly While existing frameworks are feature rich, there are very less or no options out there to distribute scans Mantis is crafted to facilitate the development of new tools, based on the gathered information PURPOSE MANTIS -
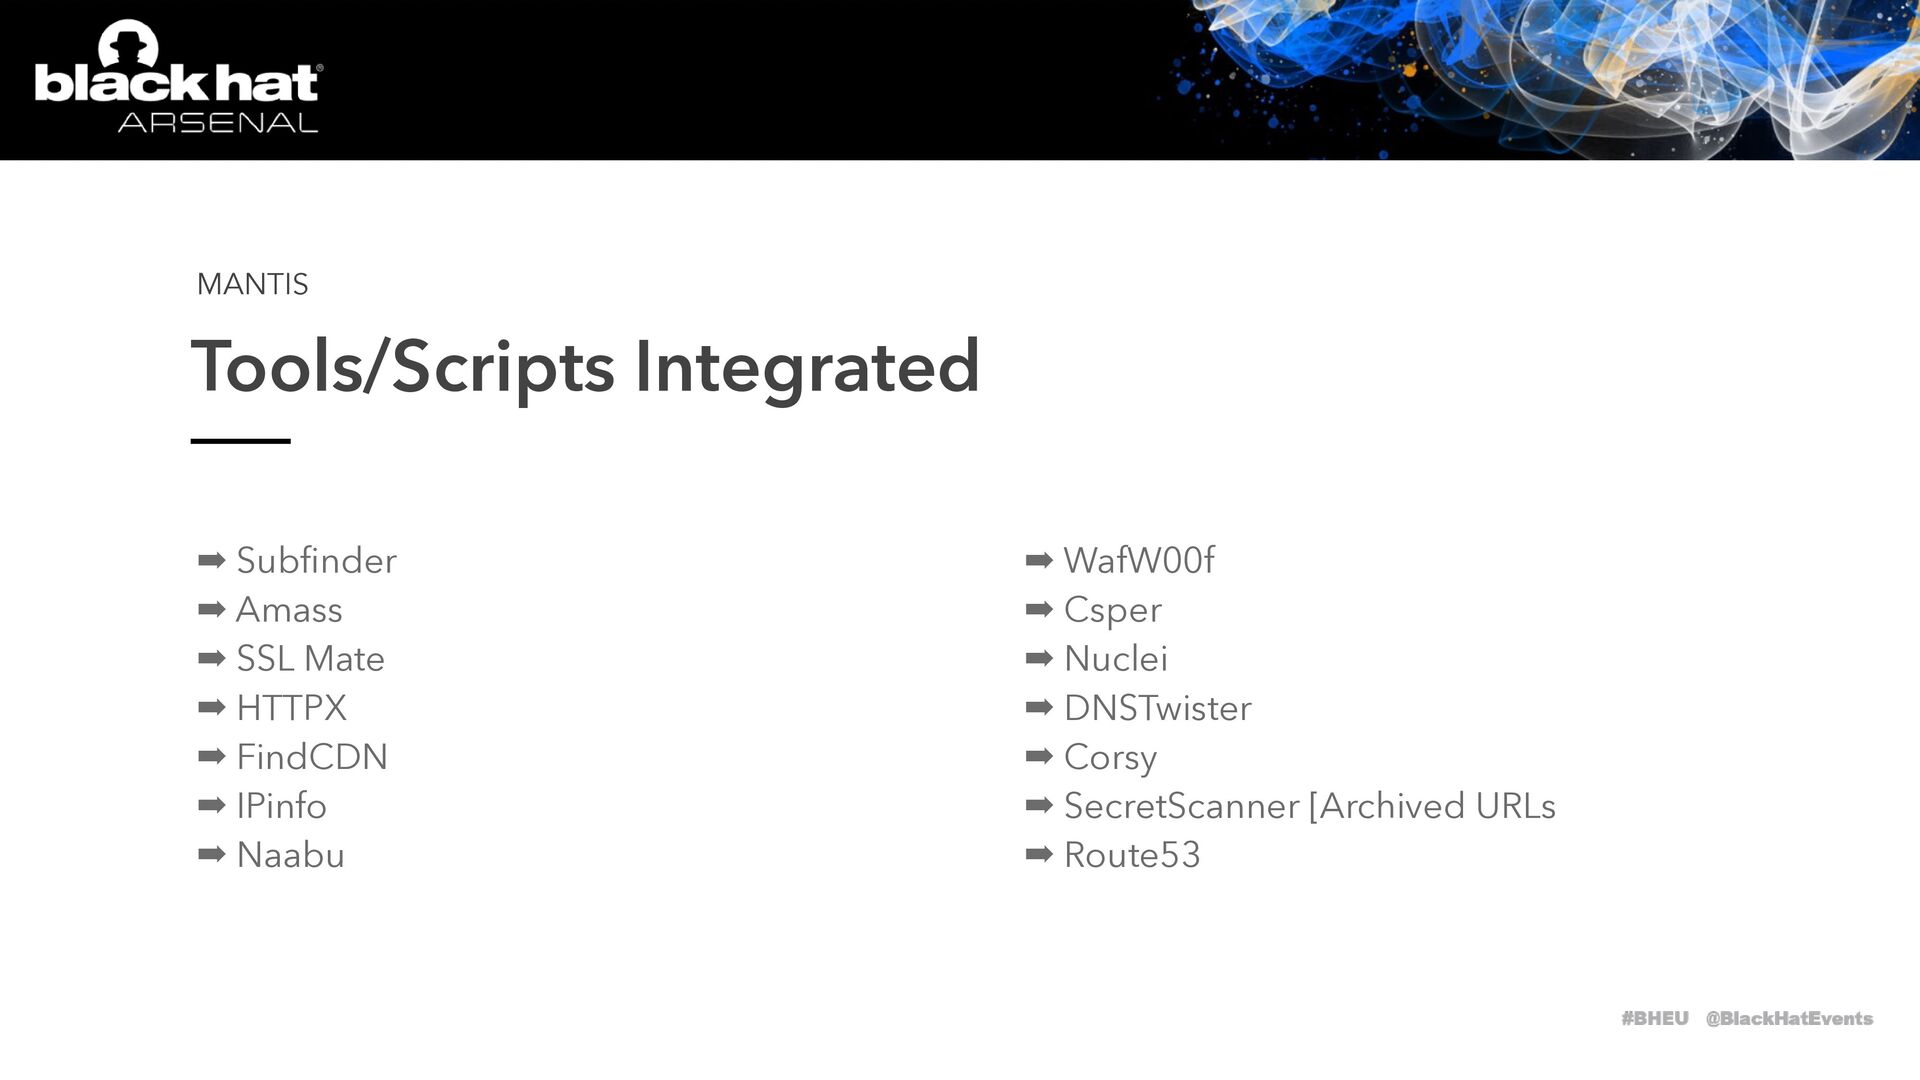
Tools/Scripts Integrated MANTIS ➡ Sub fi nder ➡ Amass ➡
SSL Mate ➡ HTTPX ➡ FindCDN ➡ IPinfo ➡ Naabu ➡ WafW00f ➡ Csper ➡ Nuclei ➡ DNSTwister ➡ Corsy ➡ SecretScanner [Archived URLs ➡ Route53 -
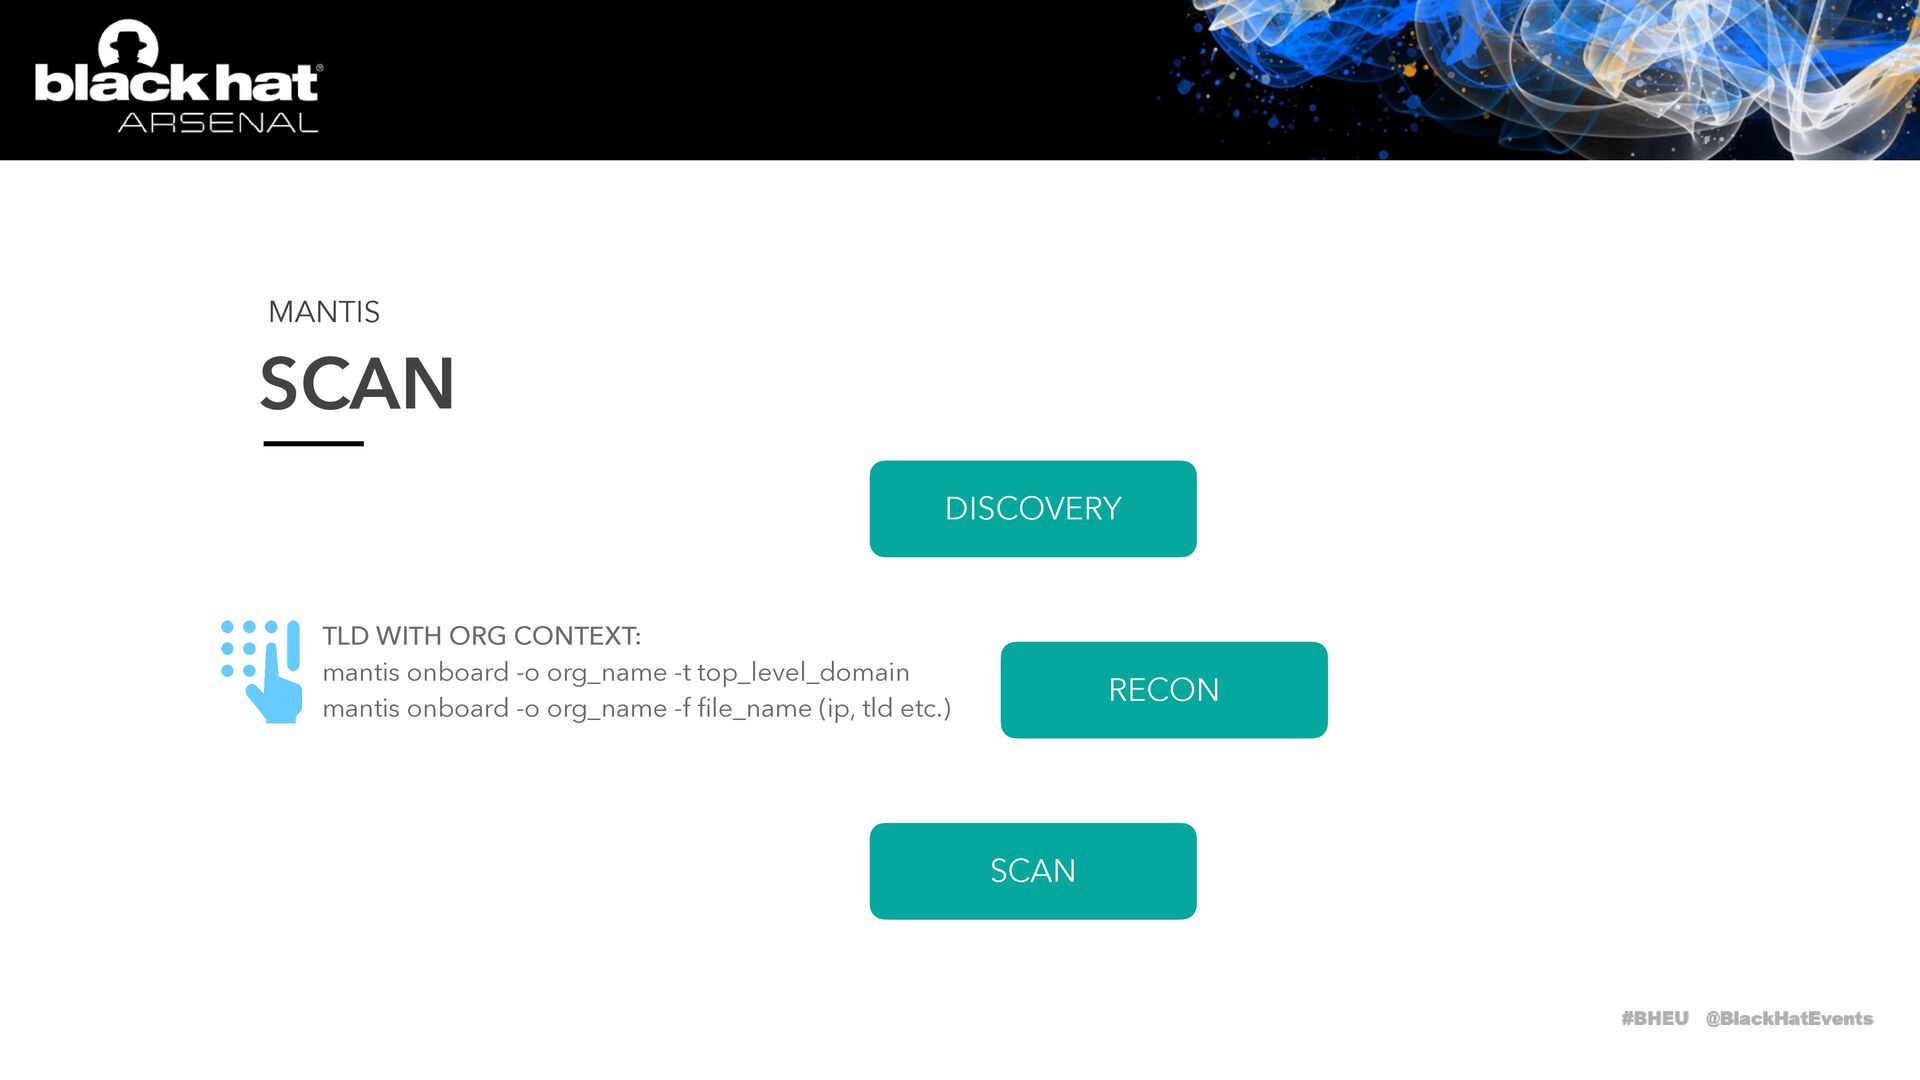
SCAN MANTIS DISCOVERY RECON SCAN TLD WITH ORG CONTEXT: mantis
onboard -o org_name -t top_level_domain mantis onboard -o org_name -f fi le_name (ip, tld etc.) -
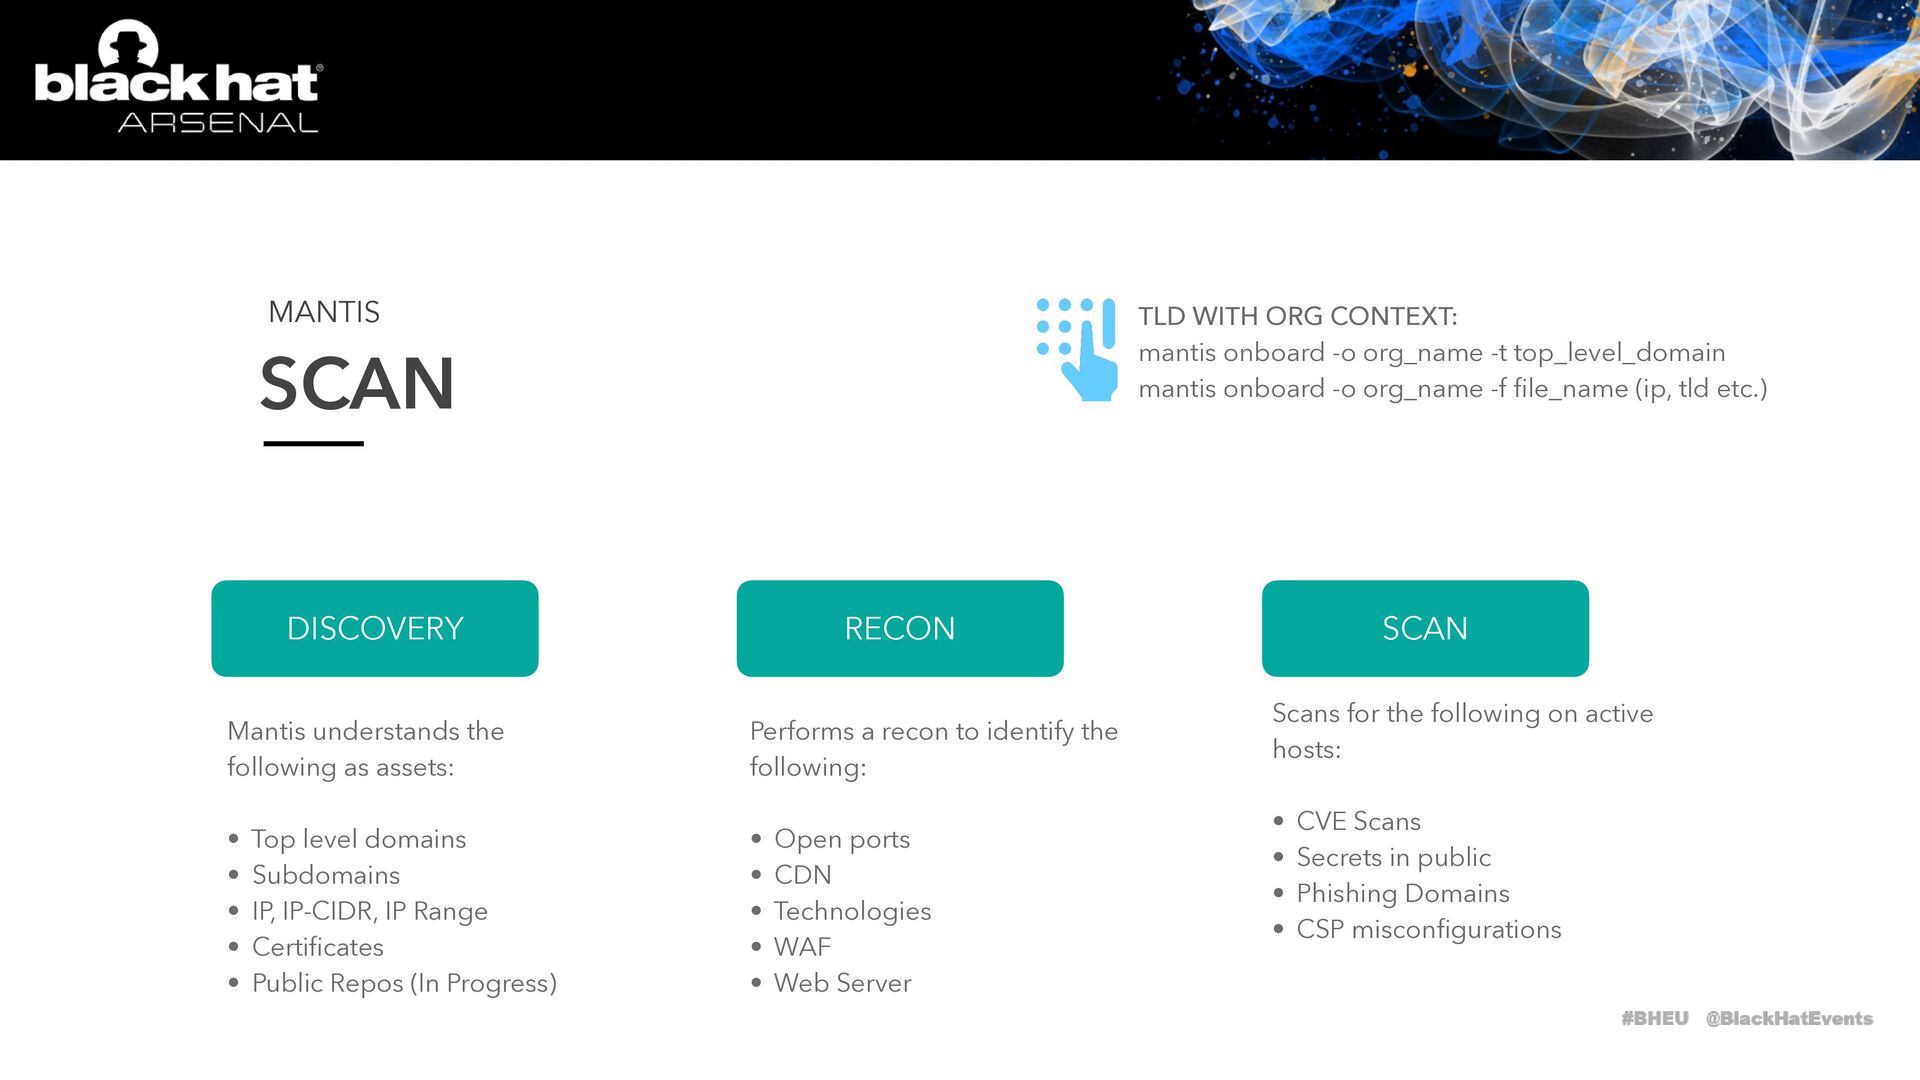
SCAN MANTIS DISCOVERY RECON SCAN Mantis understands the following as
assets: • Top level domains • Subdomains • IP, IP-CIDR, IP Range • Certi fi cates • Public Repos (In Progress) Performs a recon to identify the following: • Open ports • CDN • Technologies • WAF • Web Server Scans for the following on active hosts: • CVE Scans • Secrets in public • Phishing Domains • CSP miscon fi gurations TLD WITH ORG CONTEXT: mantis onboard -o org_name -t top_level_domain mantis onboard -o org_name -f fi le_name (ip, tld etc.) -
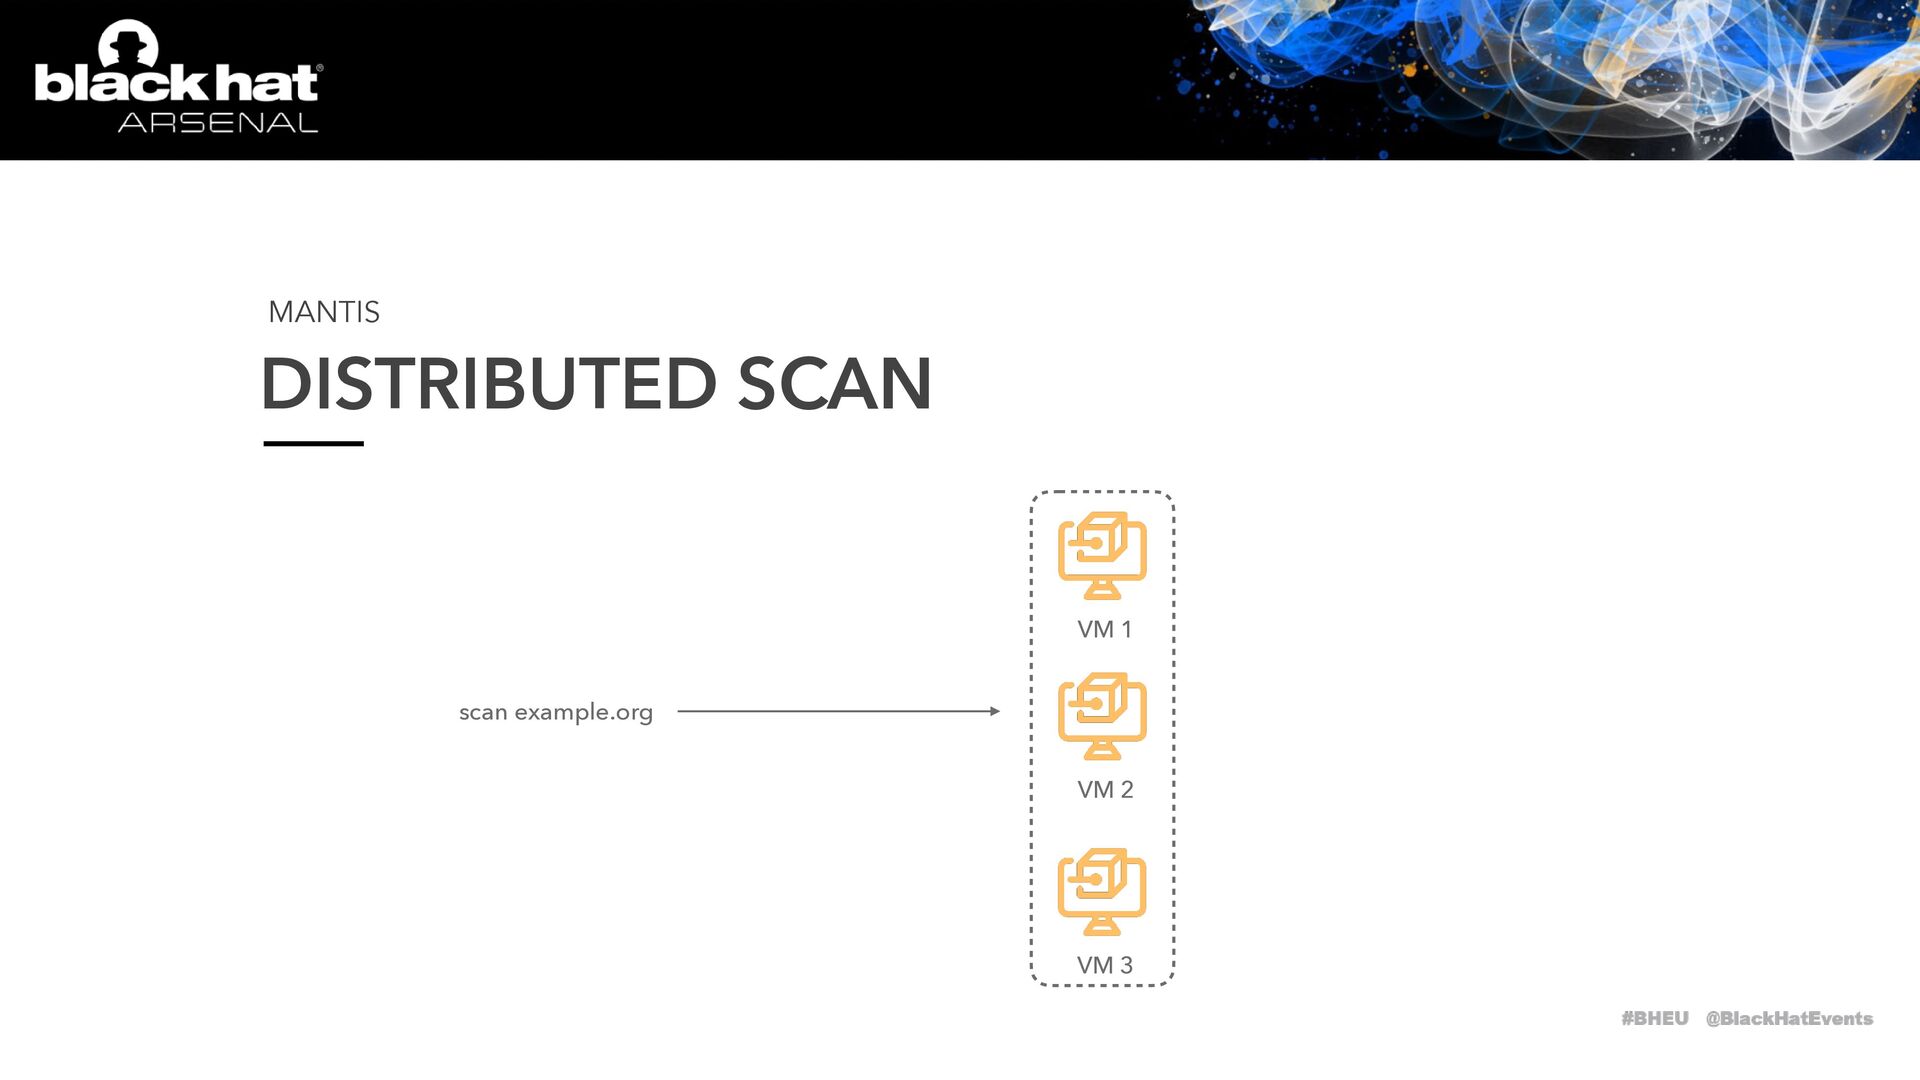
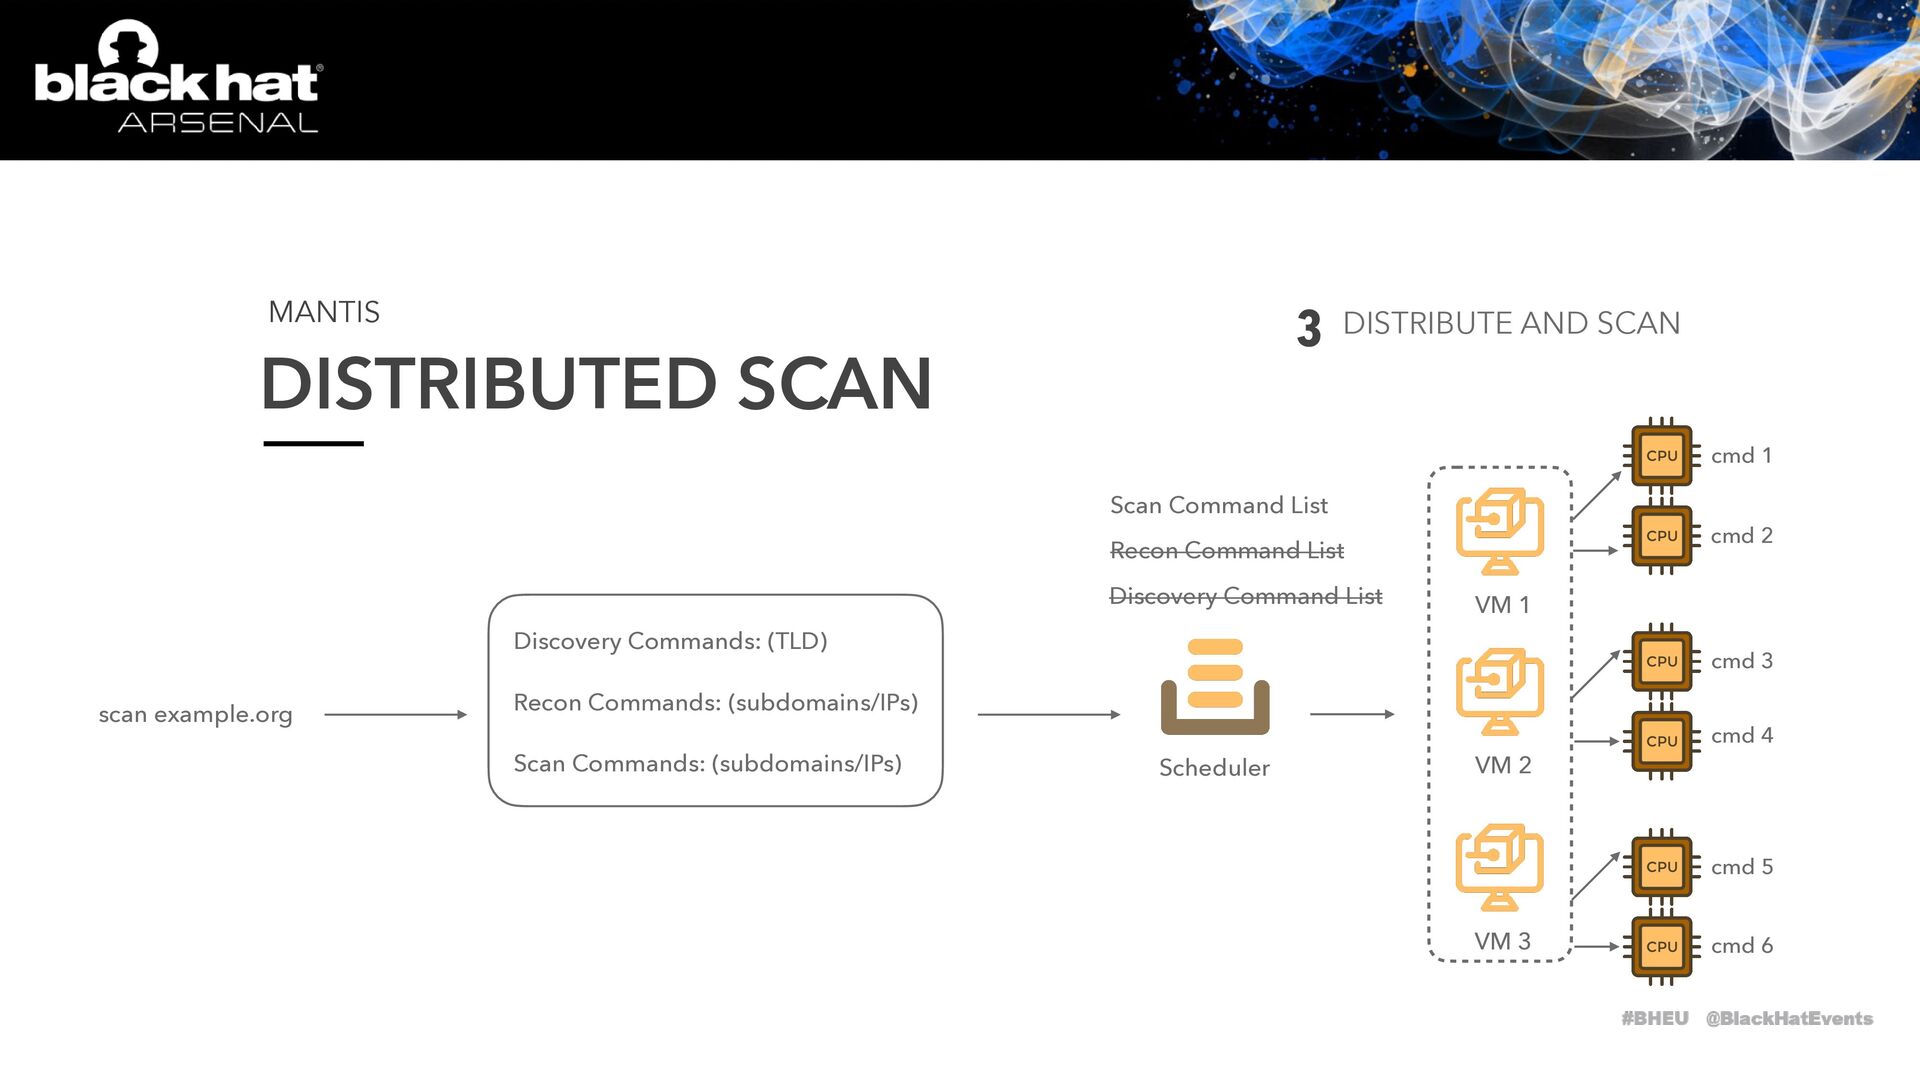
DISTRIBUTED SCAN MANTIS VM 1 VM 2 VM 3 scan
example.org -
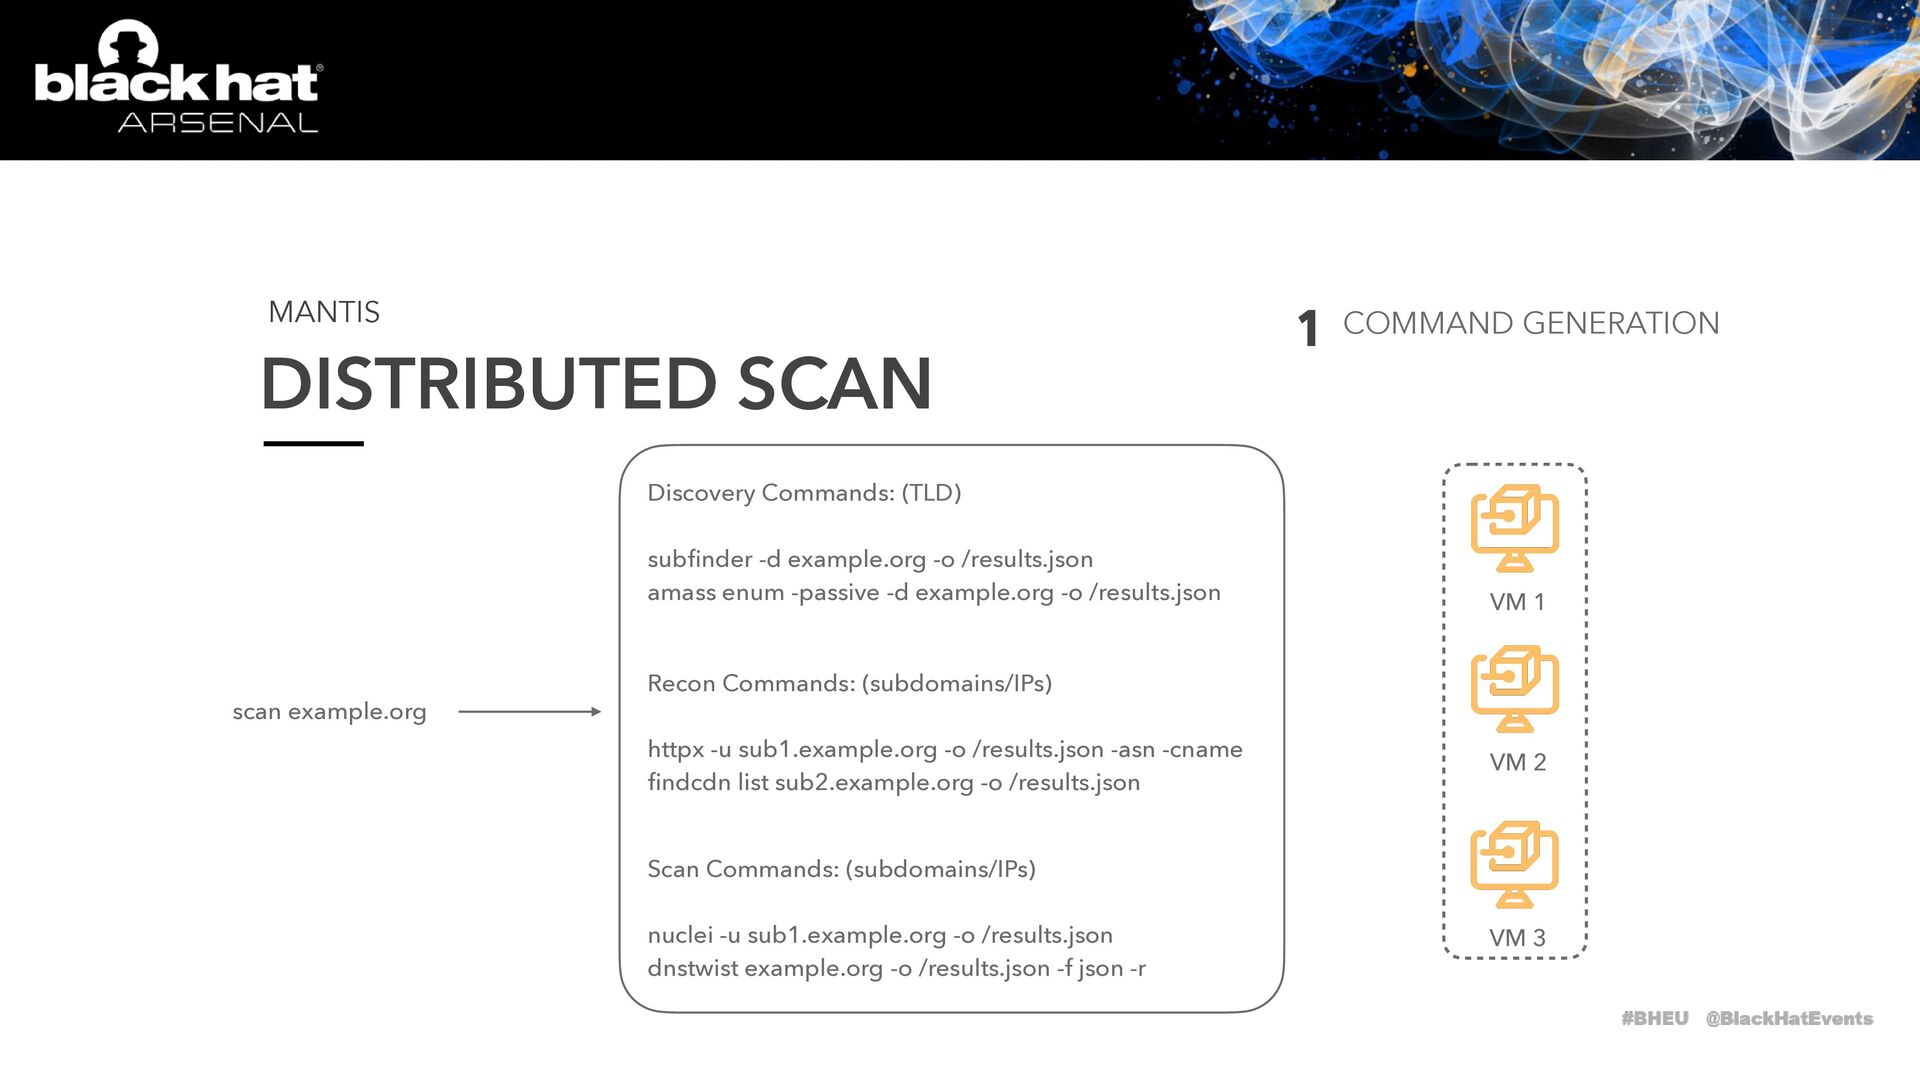
DISTRIBUTED SCAN MANTIS VM 1 VM 2 VM 3 scan
example.org Discovery Commands: (TLD) sub fi nder -d example.org -o /results.json amass enum -passive -d example.org -o /results.json Recon Commands: (subdomains/IPs) httpx -u sub1.example.org -o /results.json -asn -cname fi ndcdn list sub2.example.org -o /results.json Scan Commands: (subdomains/IPs) nuclei -u sub1.example.org -o /results.json dnstwist example.org -o /results.json -f json -r COMMAND GENERATION 1 -
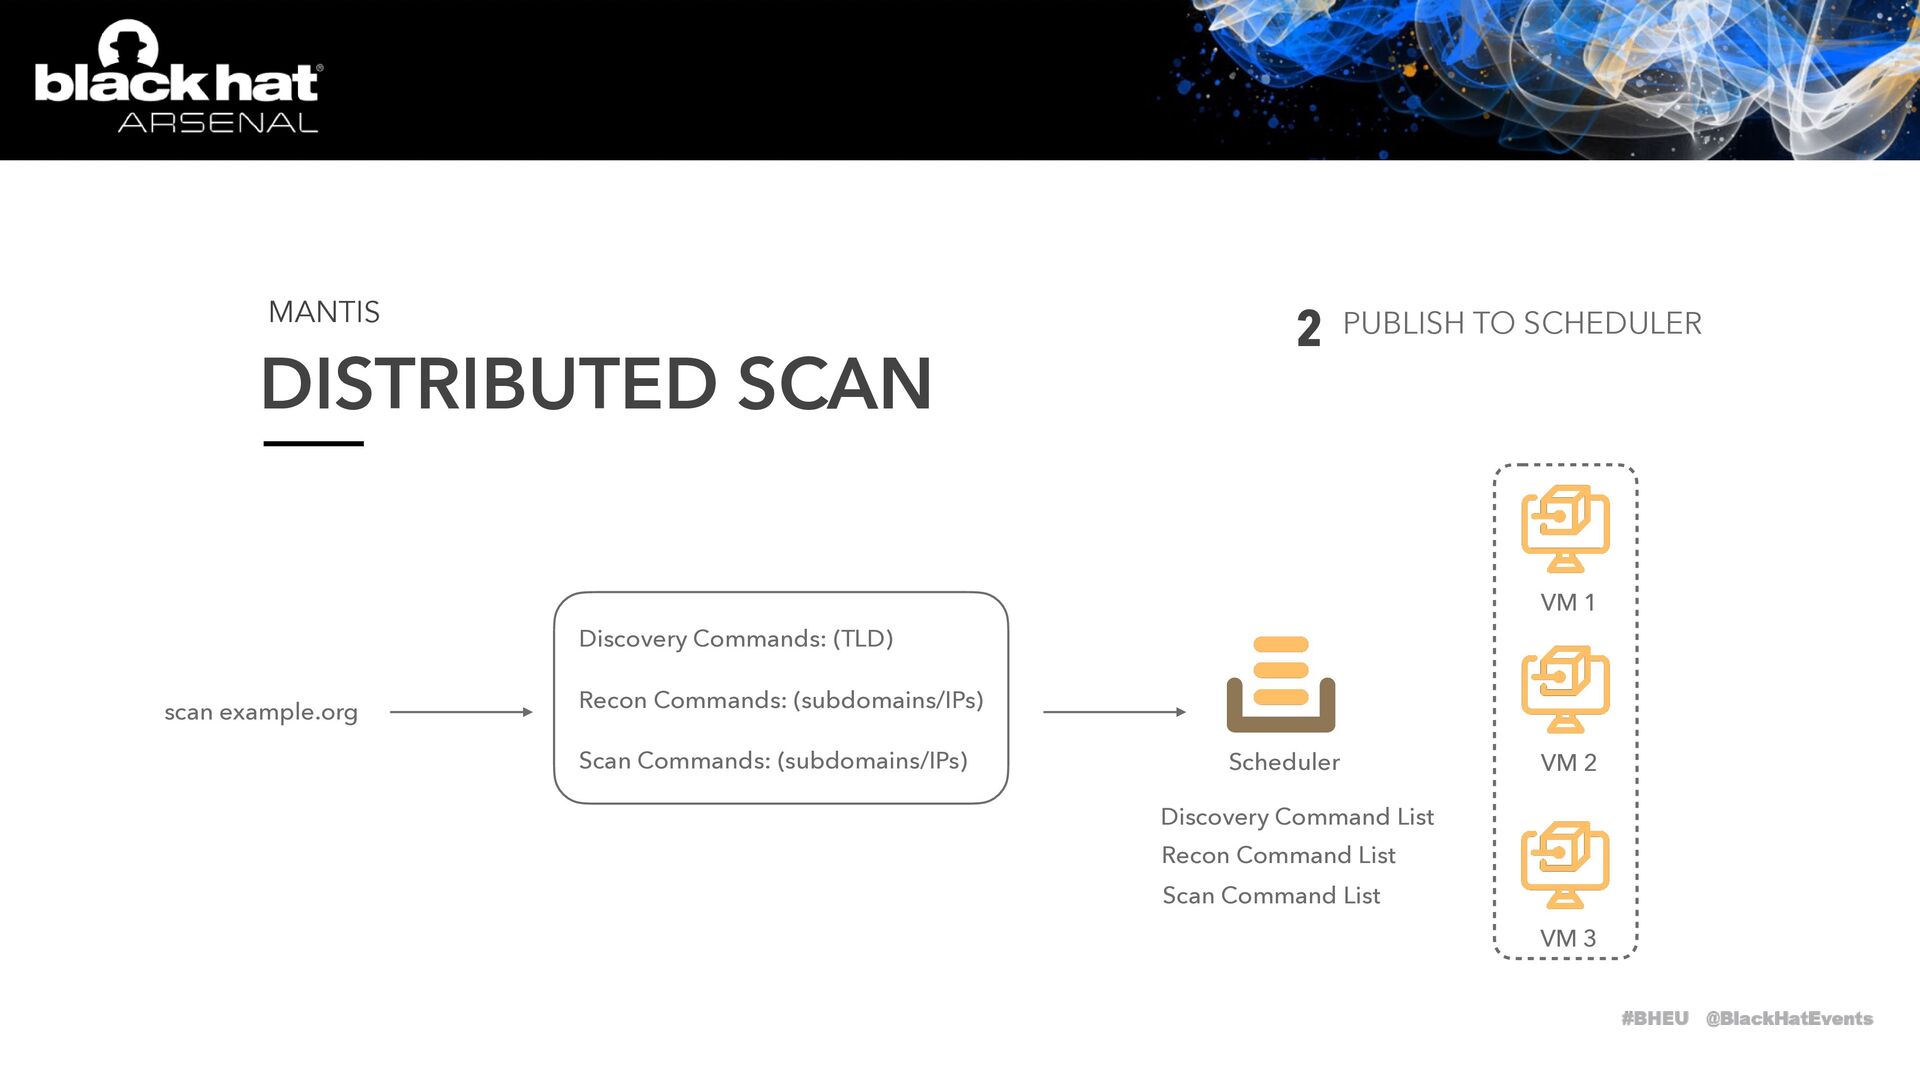
DISTRIBUTED SCAN MANTIS VM 1 VM 2 VM 3 scan
example.org Discovery Commands: (TLD) Recon Commands: (subdomains/IPs) Scan Commands: (subdomains/IPs) PUBLISH TO SCHEDULER 2 Scheduler Discovery Command List Recon Command List Scan Command List -
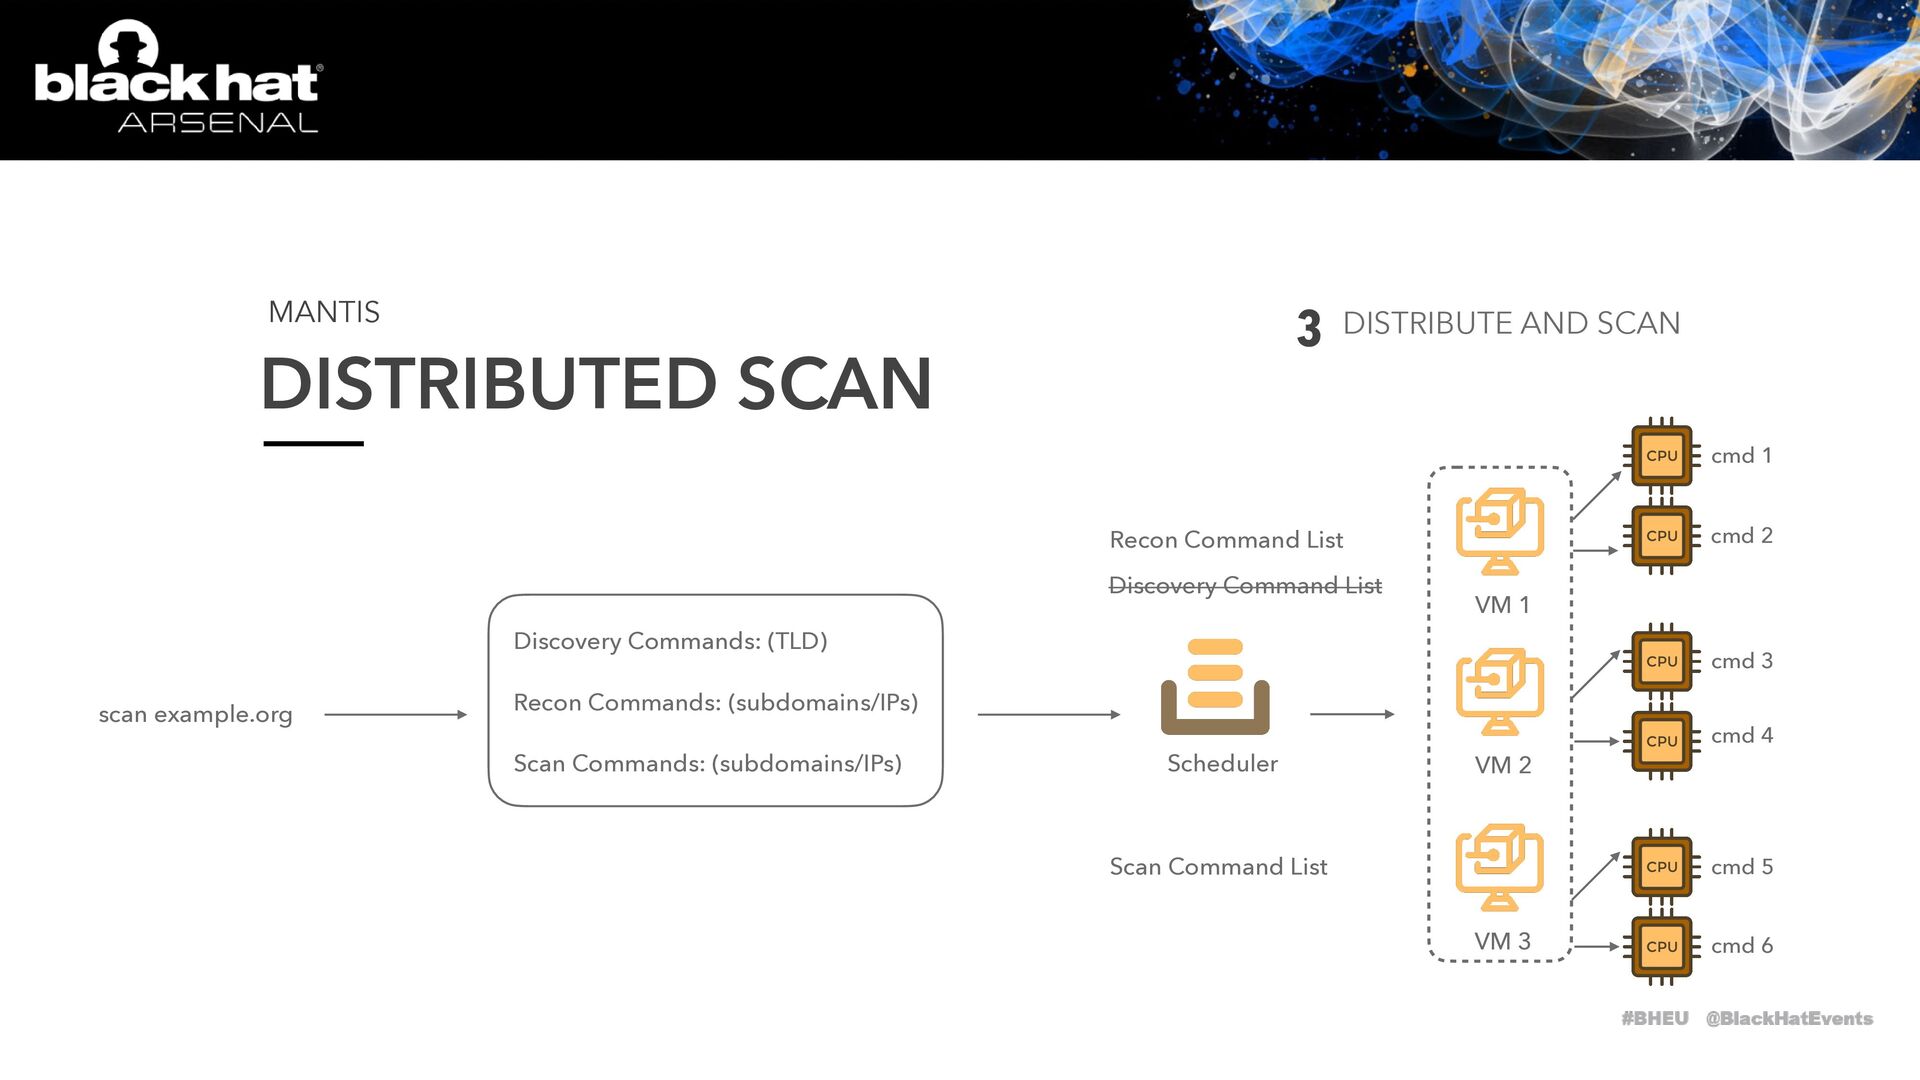
DISTRIBUTED SCAN MANTIS VM 1 VM 2 VM 3 scan
example.org Discovery Commands: (TLD) Recon Commands: (subdomains/IPs) Scan Commands: (subdomains/IPs) DISTRIBUTE AND SCAN 3 Scheduler cmd 1 cmd 2 cmd 3 cmd 4 cmd 5 cmd 6 Discovery Command List Recon Command List Scan Command List -
DISTRIBUTED SCAN MANTIS VM 1 VM 2 VM 3 scan
example.org Discovery Commands: (TLD) Recon Commands: (subdomains/IPs) Scan Commands: (subdomains/IPs) DISTRIBUTE AND SCAN 3 Scheduler cmd 1 cmd 2 cmd 3 cmd 4 cmd 5 cmd 6 Recon Command List Discovery Command List Scan Command List -
DISTRIBUTED SCAN MANTIS VM 1 VM 2 VM 3 scan
example.org Discovery Commands: (TLD) Recon Commands: (subdomains/IPs) Scan Commands: (subdomains/IPs) DISTRIBUTE AND SCAN 3 Scheduler cmd 1 cmd 2 cmd 3 cmd 4 cmd 5 cmd 6 Scan Command List Recon Command List Discovery Command List -
DISCOVER EXISTING ASSETS A mature product security team is typically
established only 4 to 5 years after the product's launch. REQUIREMENTS PRODUCT SECURITY TEAM 1 STAY VIGILANT REGARDING NEW ASSETS Multiple coordination efforts with different teams, including Infrastructure, are necessary to understand newly launched assets. 2 CONTINOUS SCANNING Implementing automation for continuous discovery of assets and vulnerabilities 3 SCANNING LARGE NO. OF ASSETS To achieve continuous scanning, there is a necessity to scale a single scan across multiple instances 5 VULNERABILITY MANAGEMENT Assets should be mapped to teams or applications to facilitate swift noti fi cations and responses 4 -
ONBOARDING MANTIS "As a product security team, you want to
install Mantis for your organisation straight out of the box" -
ADDING INTERNAL CONTEXT MANTIS "As a product security team, you
just don't want rely on tools to discover your assets and want to add internal context" -
SCHEDULING MANTIS "As a product security team, you would want
to schedule continuous scans on your assets" -
DASHBOARD AND ALERTING MANTIS "As a product security team, you
will want to visualise your entire assets and vulnerabilities at one place and be alerted on new discovery and fi ndings" -
VULNERABILITY MANAGEMENT MANTIS "As a product security team, you will
want to track the open/closed status of your vulnerabilities" -
DISTRIBUTING YOUR SCAN MANTIS As a product security team, you'll
aim to enhance your infrastructure and anticipate Mantis to ef fi ciently distribute your single scan" -
NEW TOOL INTEGRATIONS MANTIS As a product security team, you
will want to add a new open source tool or write a new tool based on the gathered information" -
WHAT WE WANT TO DO MANTIS Improvise Distributed Scanning Secrets
Scanning Phishing Detection Accuracy Calculator Use of open-AI to reduce false positives Encourage open-source contributions Horizontal Subdomain Enumeration