Share
Embed
Intro to Browser security policies/features
Slides from the talk Intro to Browser security policies/features.
The talk covers:
- Understand Same Origin Policy(SOP)
- Limitations of Same Origin Policy(SOP)
- Mechanisms to work around Same Origin Policy(SOP)
- postMessage
- CORS
Bharath
November 17, 2018
Transcript
44 slides
-
ABOUT ME ABOUT ME Bharath Kumar Security Engineer @ Offensive
Security Certified Professional(OSCP) Appsecco -
THE PLAN THE PLAN Understand Same Origin Policy(SOP) Limitations of
Same Origin Policy(SOP) Mechanisms to work around Same Origin Policy(SOP) -
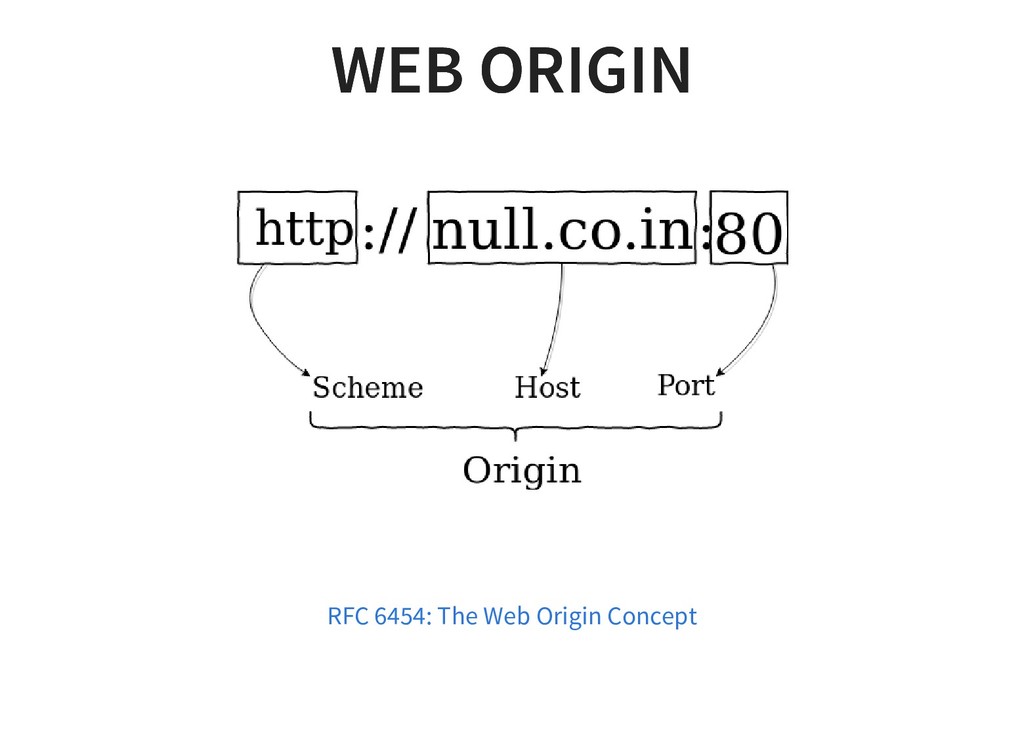
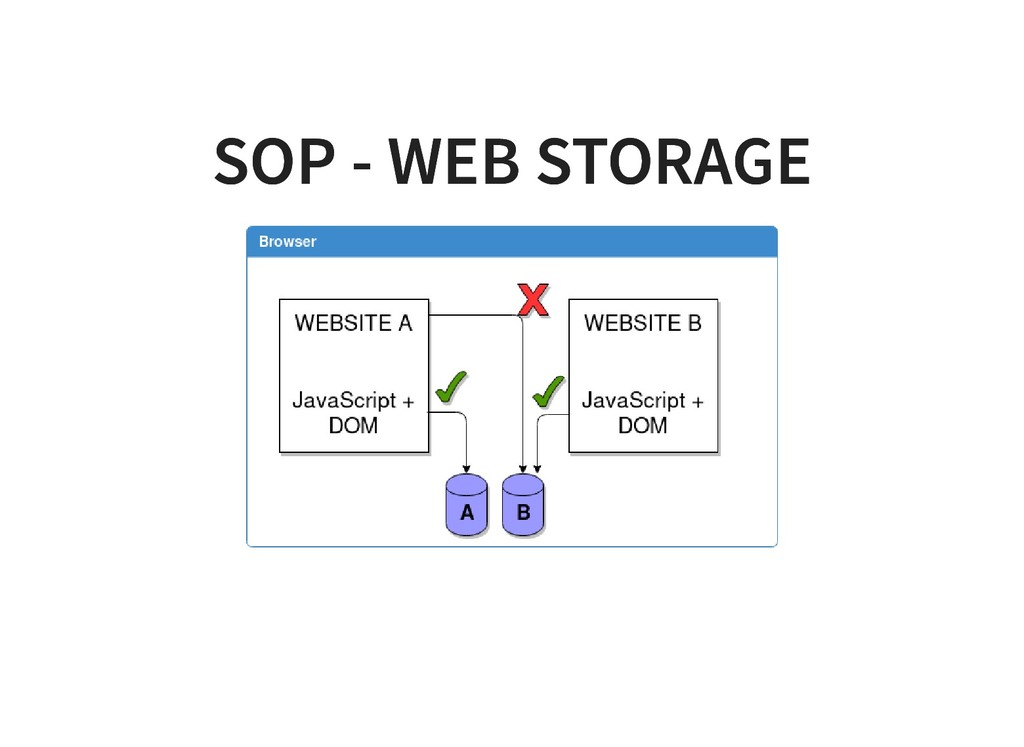
SAME ORIGIN POLICY SAME ORIGIN POLICY The same-origin policy is
a critical (browser) security mechanism that restricts how a document or script loaded from one origin can interact with a resource from another origin. It helps isolate potentially malicious documents, reducing possible attack vectors. https://developer.mozilla.org/en-US/docs/Web/Security/Same-origin_policy -
SUBSETS OF SAME ORIGIN SUBSETS OF SAME ORIGIN POLICY RULES
POLICY RULES Document Object Model(DOM) XMLHttpRequest (XHR) Web Storage API HTTP cookies Pseudo protocols Flash/PDF/Silverlight ... -
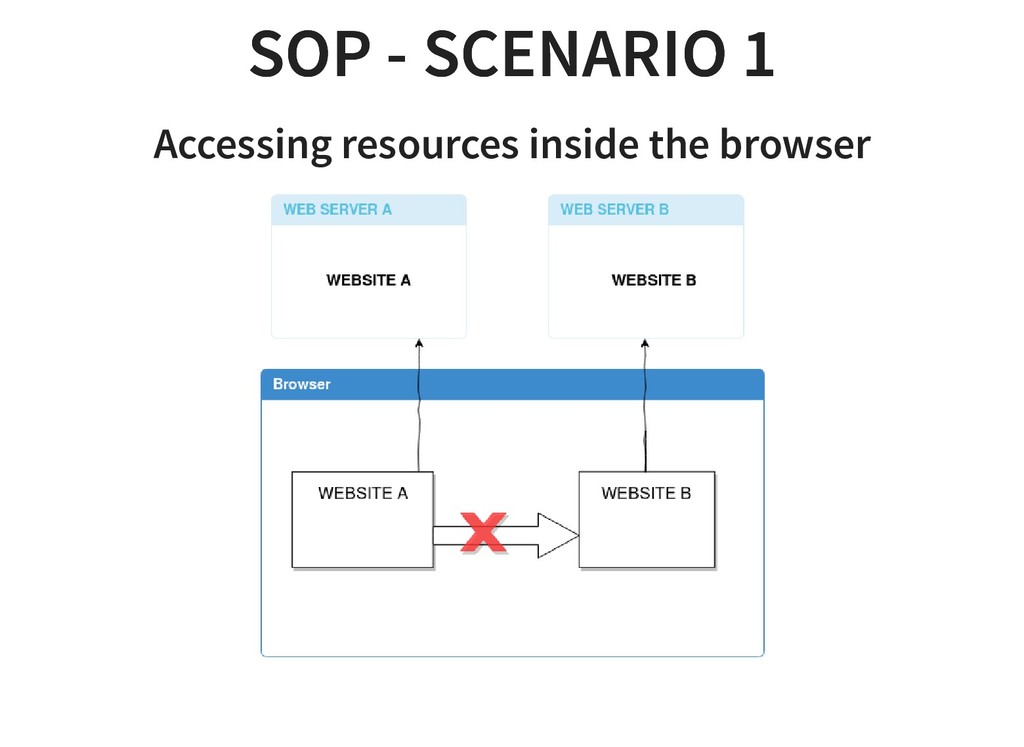
SOP - SCENARIO 1 SOP - SCENARIO 1 Accessing resources
inside the browser -
SOP - SCENARIO 2 SOP - SCENARIO 2 Accessing resources
over the network -
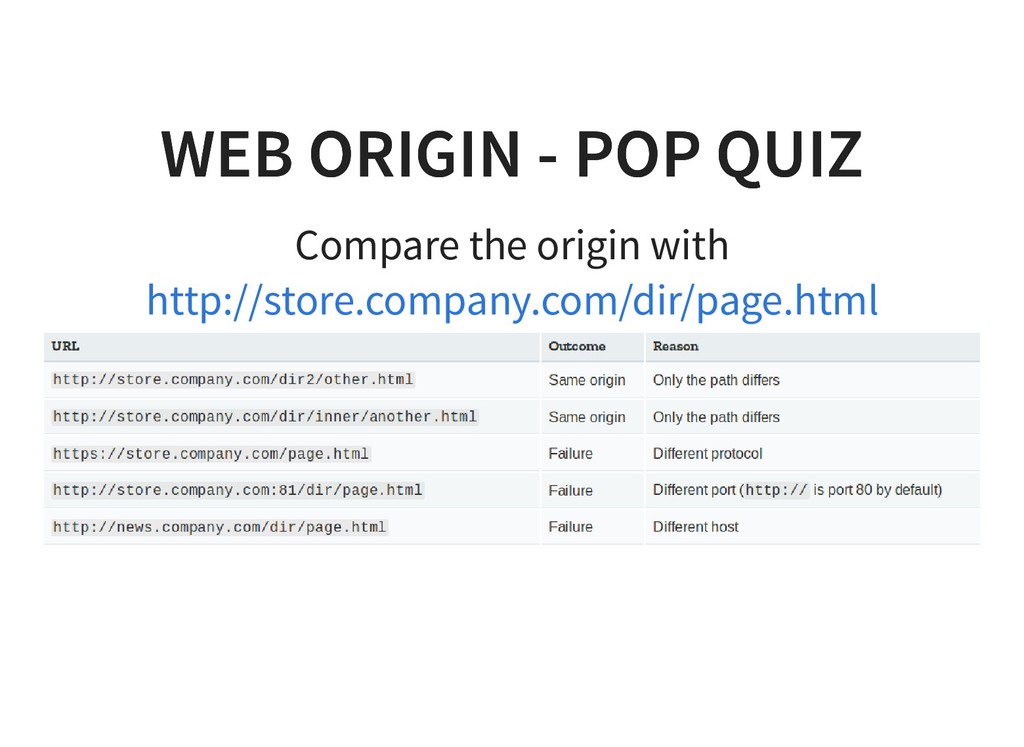
WEB ORIGIN - POP QUIZ WEB ORIGIN - POP QUIZ
Compare the origin with http://store.company.com/dir/page.html -
WEB ORIGIN - POP QUIZ WEB ORIGIN - POP QUIZ
Compare the origin with http://store.company.com/dir/page.html -
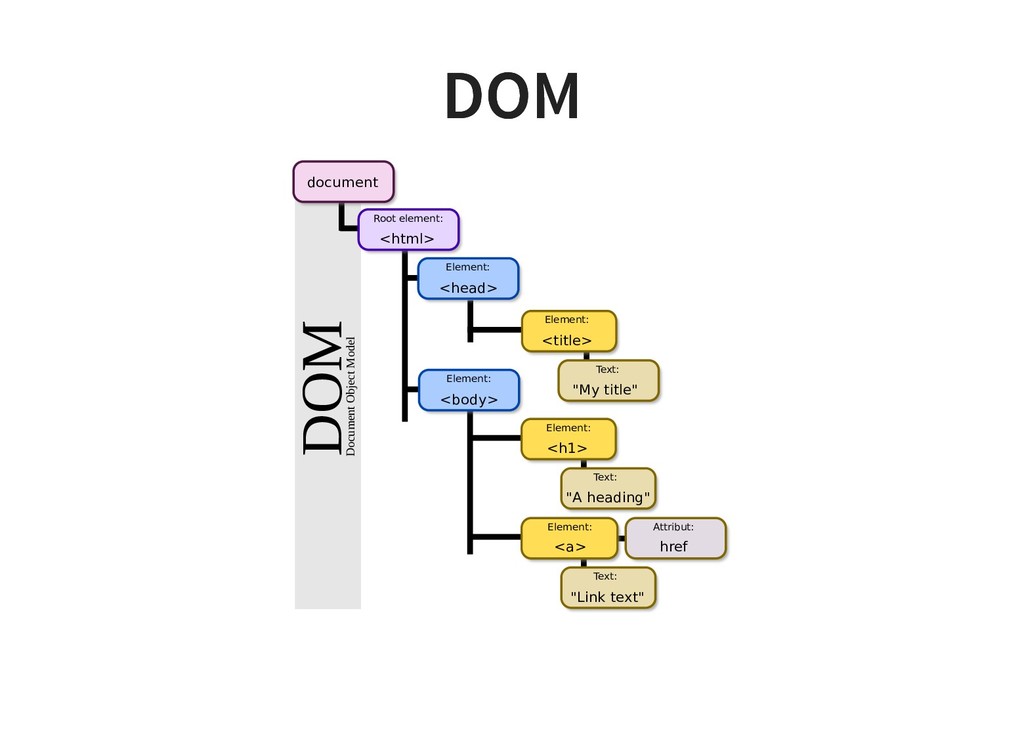
DOCUMENT OBJECT DOCUMENT OBJECT MODEL(DOM) MODEL(DOM) DOM connects web pages
to scripts or programming languages DOM is a programming interface for HTML and XML documents DOM represents the page so that programs can change the document structure, style, and content https://developer.mozilla.org/en-US/docs/Web/API/Document_Object_Model -
DOM DOM Element: <head> Element: <body> Element: <title> Text: "My
title" Element: <h1> Text: "A heading" Element: <a> Text: "Link text" DOM Document Object Model document Attribut: href Root element: <html> -
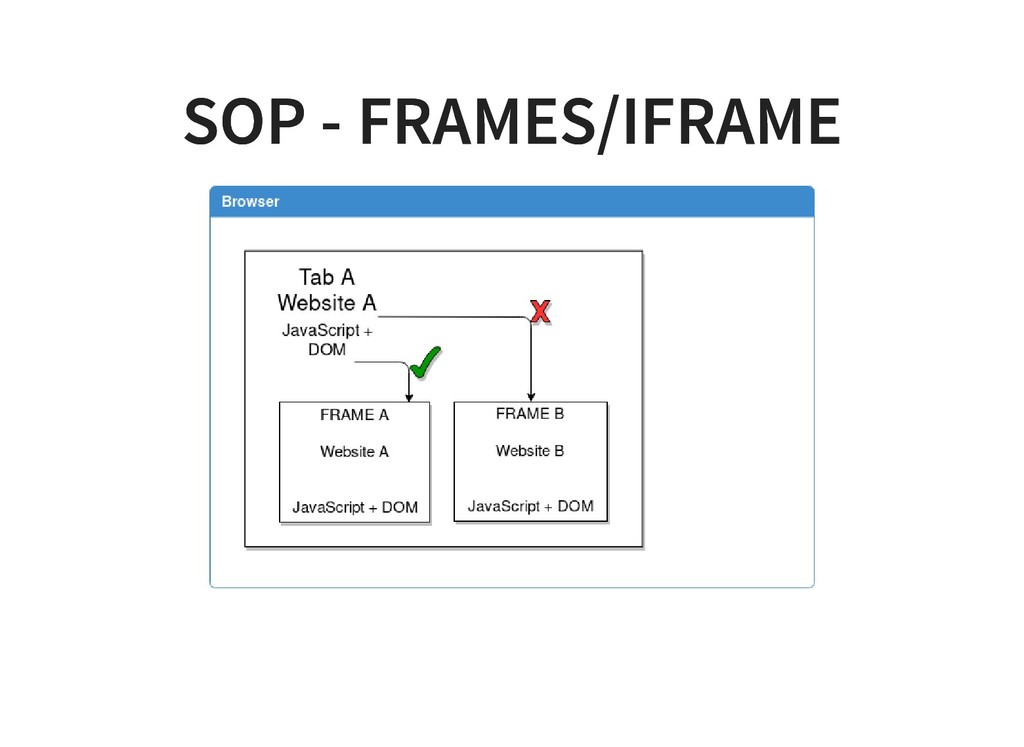
SOP - FRAMES/IFRAME SOP - FRAMES/IFRAME Each frame/Iframe is isolated
and gets a seperate JavaScript execution context Frames/Iframes can manipulate the parent location using window.parent.location even if the parent has different origin -
XMLHTTPREQUEST XMLHTTPREQUEST XMLHttpRequest (XHR) objects allow JavaScript to interact with
servers Using XHR you can retrieve data from a URL without having to do a full page refresh XHR can be used to retrieve any type of data, not just XML, and it supports protocols other than HTTP XHR requests can be made with cookies and custom HTTP headers https://developer.mozilla.org/en-US/docs/Web/API/XMLHttpRequest -
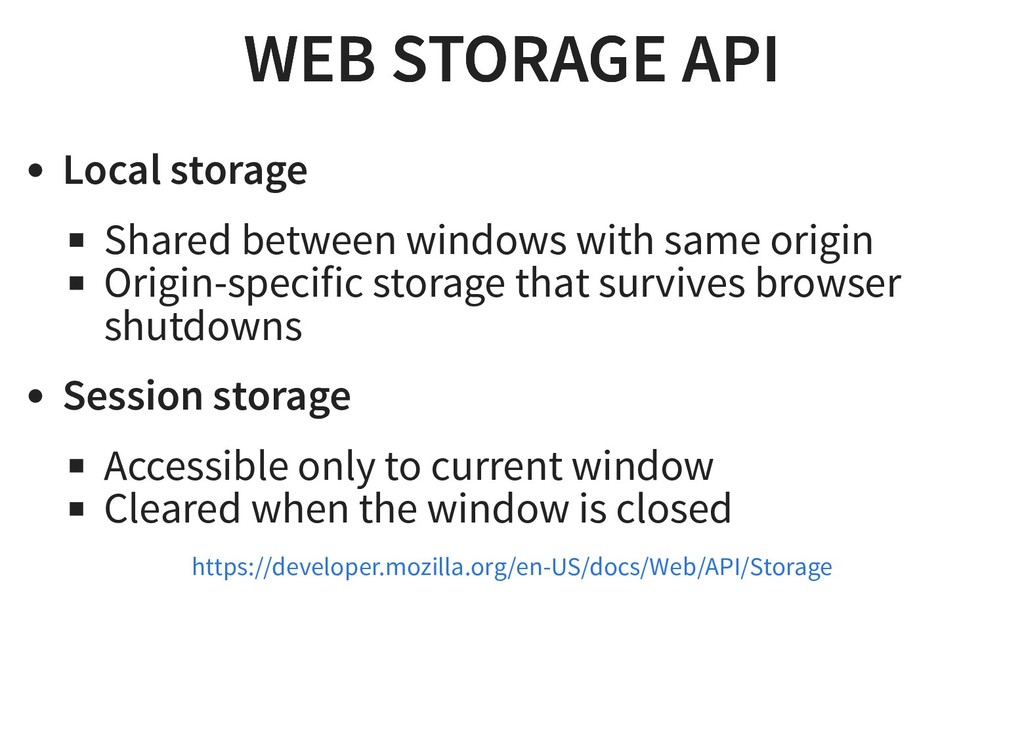
WEB STORAGE API WEB STORAGE API Local storage Shared between
windows with same origin Origin-specific storage that survives browser shutdowns Session storage Accessible only to current window Cleared when the window is closed https://developer.mozilla.org/en-US/docs/Web/API/Storage -
DEMO - SOP - WEB STORAGE DEMO - SOP -
WEB STORAGE -
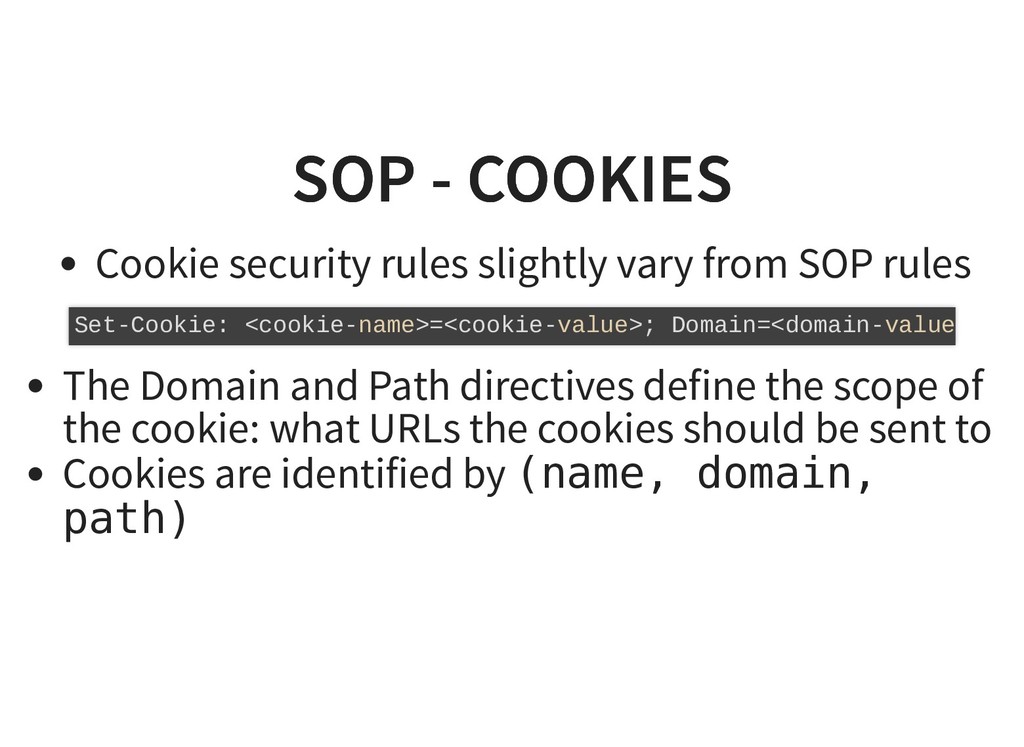
SOP - COOKIES SOP - COOKIES Cookie security rules slightly
vary from SOP rules The Domain and Path directives define the scope of the cookie: what URLs the cookies should be sent to Cookies are identified by (name, domain, path) Set-Cookie: <cookie-name>=<cookie-value>; Domain=<domain-value -
LIMITATIONS OF SOP 1 LIMITATIONS OF SOP 1 SOP is
too broad to isolate between path based resources such as home pages or profiles https://null.co.in/profile/1 https://null.co.in/profile/352 -
SPECIFICATIONS/FEATURES SPECIFICATIONS/FEATURES THAT EXTEND ORIGIN THAT EXTEND ORIGIN Content Security
Policy(CSP) ... Suborigins First Party Isolation -
LIMITATIONS OF SOP 2 LIMITATIONS OF SOP 2 SOP makes
it difficult for legitimately cooperating sites to exchange data store.wikimedia.org payment.wikimedia.org -
SPECS/FEATURES TO ENABLE SPECS/FEATURES TO ENABLE CROSS-DOMAIN INTERACTIONS CROSS-DOMAIN INTERACTIONS
document.domain (Applies to SOP DOM) postMessage (Applies to SOP DOM) Cross Origin Resource Sharing (Applies to SOP XMLHttpRequest) -
DOCUMENT.DOMAIN DOCUMENT.DOMAIN The domain property of the Document interface gets/sets
the domain portion of the origin of the current document This property can be used by two cooperating websites that share a common top-level domain to agree that for the purpose of future same-origin checks they want to be viewed as same origin This feature although looks simple, it is a security tarpit -
DEMO - DOCUMENT.DOMAIN FOR DEMO - DOCUMENT.DOMAIN FOR CROSS-DOMAIN INTERACTIONS
CROSS-DOMAIN INTERACTIONS -
POSTMESSAGE POSTMESSAGE postMessage() API is an HTML5 extension that permits
cross window communications between non-same- origin sites The window.postMessage() method safely enables cross-origin communication between Window objects; e.g., between a page and a pop-up that it spawned, or between a page and an iframe embedded within it -
CROSS ORIGIN RESOURCE CROSS ORIGIN RESOURCE SHARING(CORS) SHARING(CORS) CORS is
a mechanism that uses additional HTTP headers to tell a browser to let a web application running at one origin (domain) have permission to access selected resources from a server at a different origin. https://developer.mozilla.org/en-US/docs/Web/HTTP/CORS -
CORS - SIMPLE REQUEST CORS - SIMPLE REQUEST A simple
CORS request doesn't trigger pre-flight request Browser makes a GET/POST/HEAD request and the server responds with Access-Control-Allow- Origin headers Access-Control-Allow-Origin let's the server determine which origins are allowed to read the responses -
REQUESTS WITH CREDENTIALS REQUESTS WITH CREDENTIALS The most interesting capability
exposed by both XMLHttpRequest or Fetch and CORS is the ability to make "credentialed" requests that are aware of HTTP cookies and HTTP Authentication information -
REQUESTS WITH CREDENTIALS REQUESTS WITH CREDENTIALS On the browser side,
the XMLHttpRequest request made has to set withCredentials to true in order to make the invocation with Cookies On the server side, the server has to send Access- Control-Allow-Credentials: true header to let the browser know that the server agrees to share response of a request made with credentials -
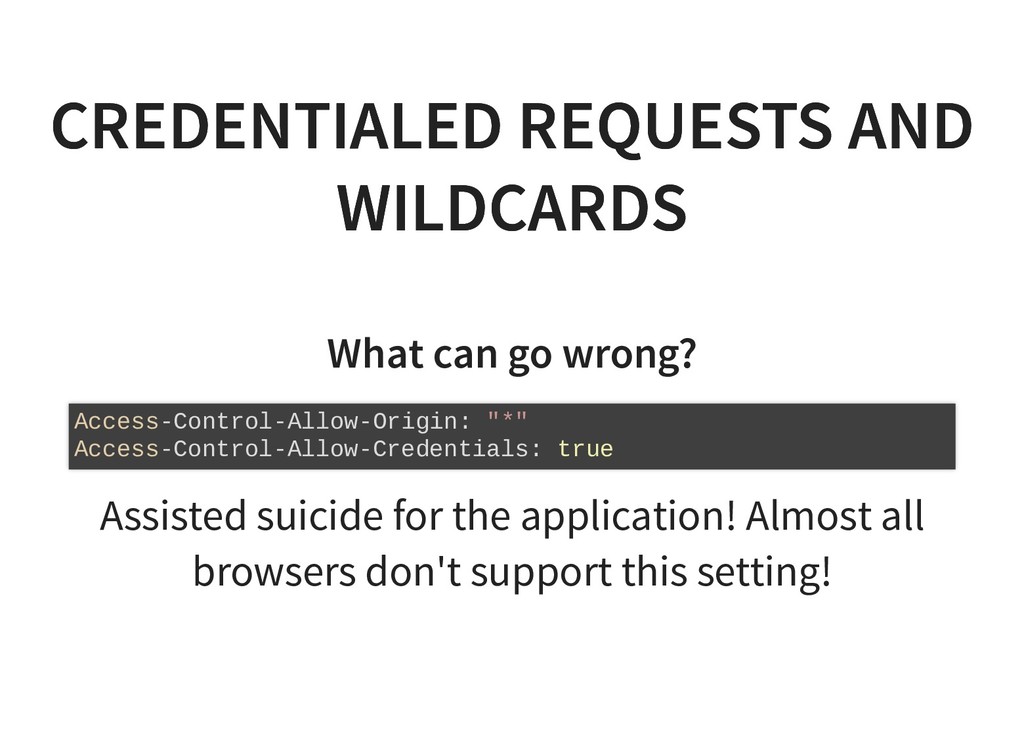
CREDENTIALED REQUESTS AND CREDENTIALED REQUESTS AND WILDCARDS WILDCARDS What can
go wrong? Assisted suicide for the application! Almost all browsers don't support this setting! Access-Control-Allow-Origin: "*" Access-Control-Allow-Credentials: true -
CORS WITH REFLECTED ORIGIN CORS WITH REFLECTED ORIGIN Each time
the browser makes a cross- domain request (a request to another domain) it adds an origin header. That header has the value of the domain the request originates from, almost like the referer header. https://blog.detectify.com/2018/04/26/cors-misconfigurations-explained/ -
REFERENCES REFERENCES [Free book] [Video] Browser Security Handbook The Tangled
Web: A Guide to Securing Modern Web Applications Same-origin policy: The core of web security by Kirk Jackson Same-Origin Policy: Evaluation in Modern Browsers, USENIX Security 2017 Learn SOP while modeling with Alloy The Browser Hacker's Handbook https://portswigger.net/blog/exploiting-cors-misconfigurations-for-bitcoins-and- bounties