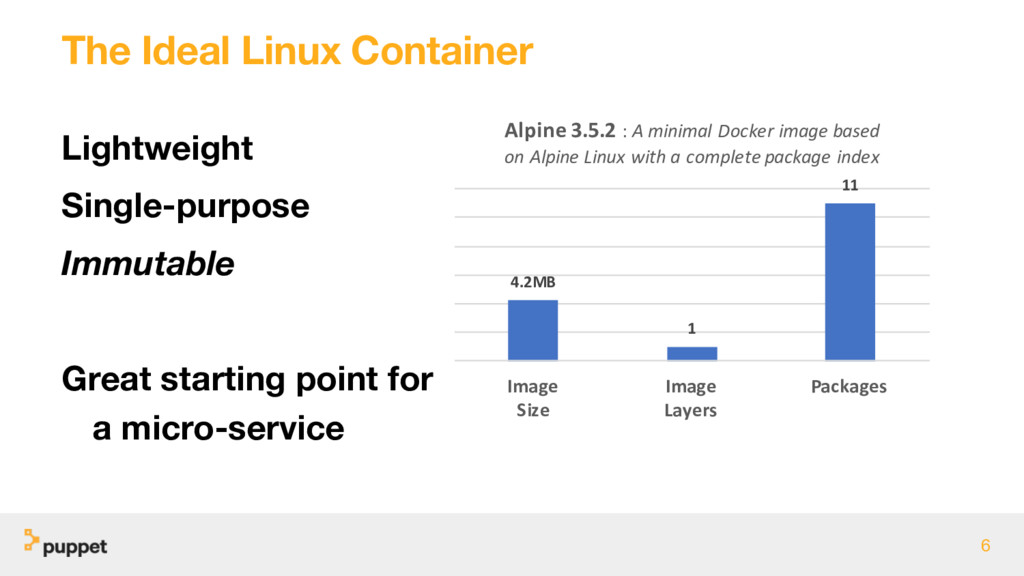
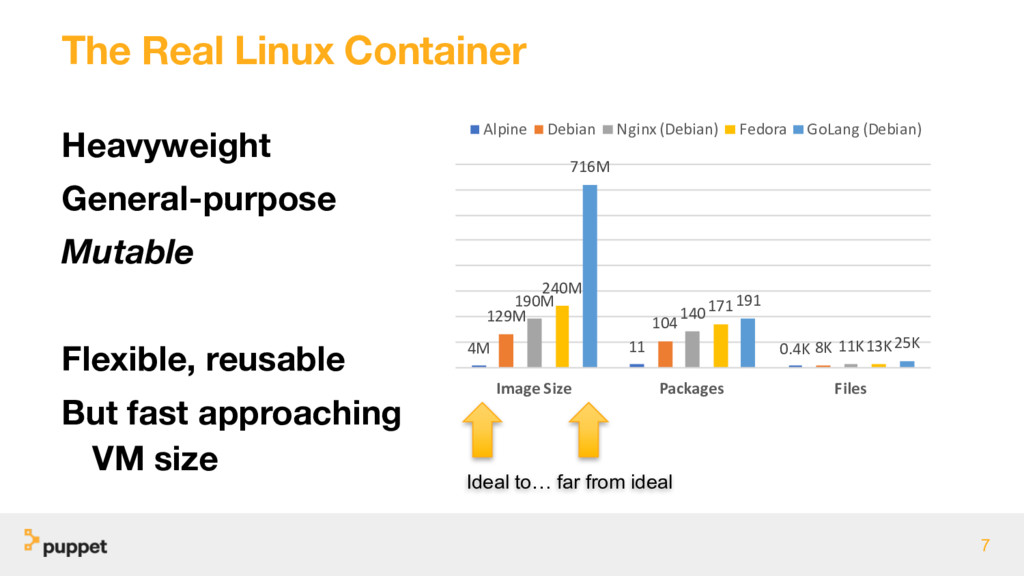
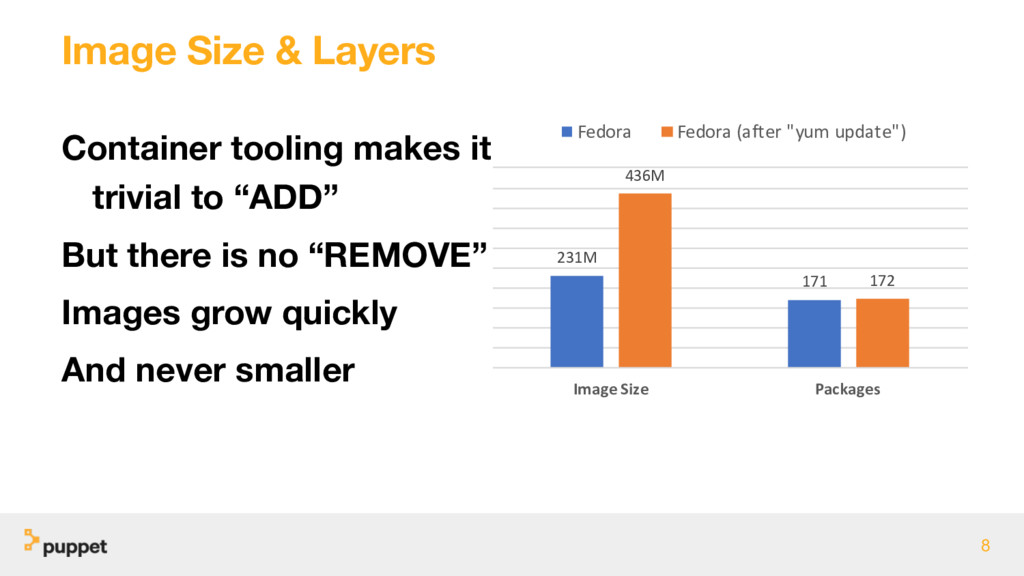
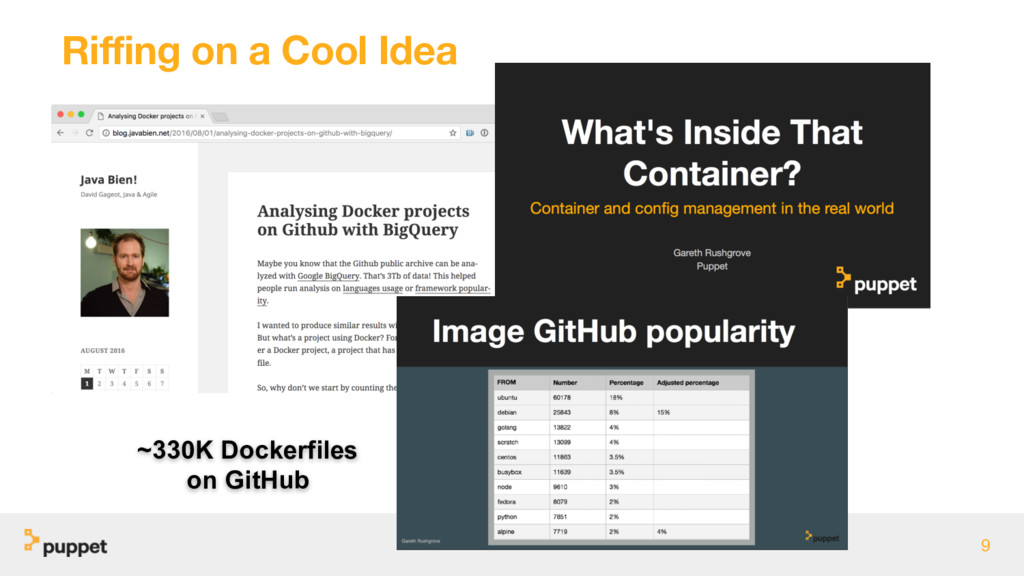
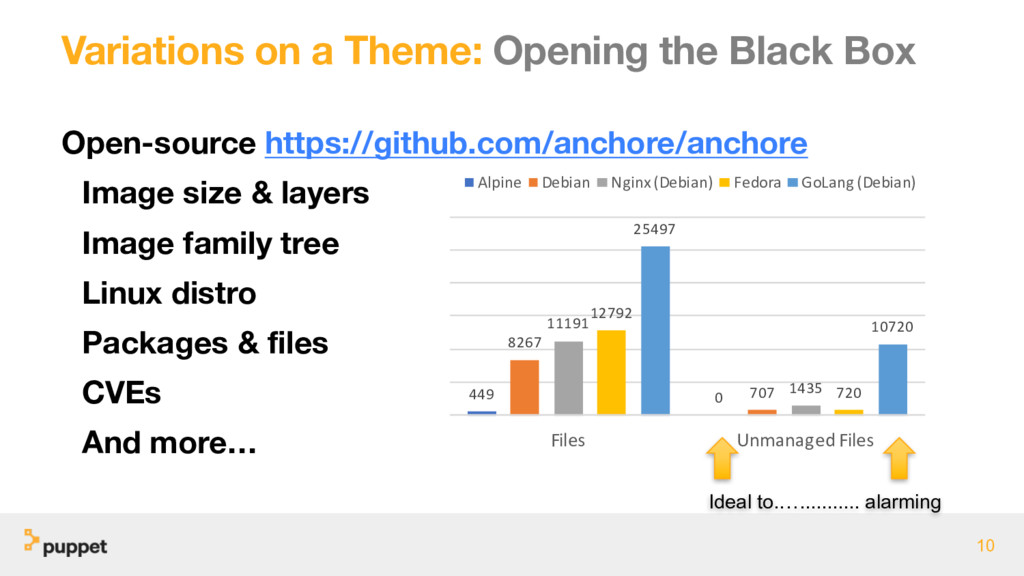
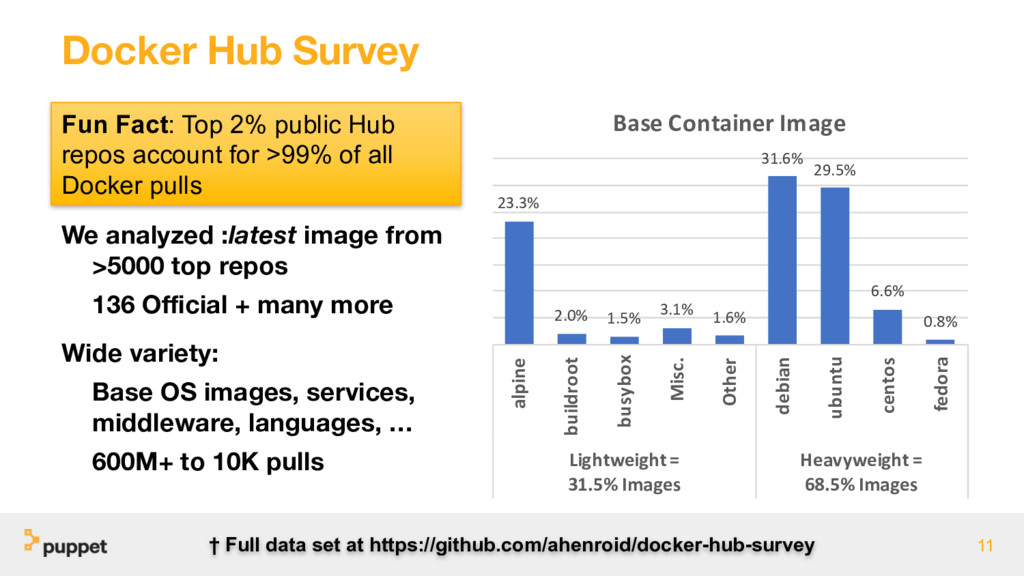
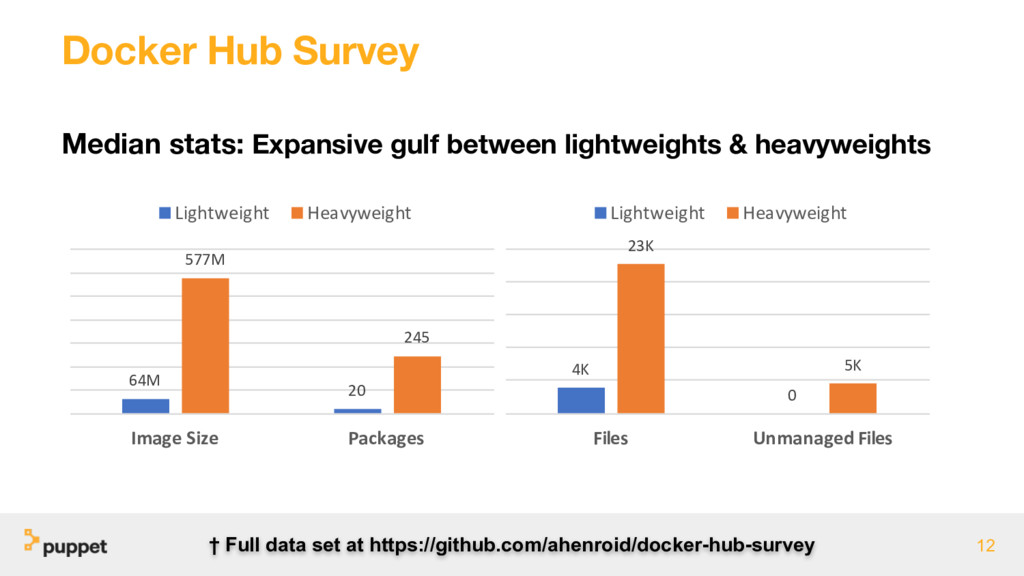
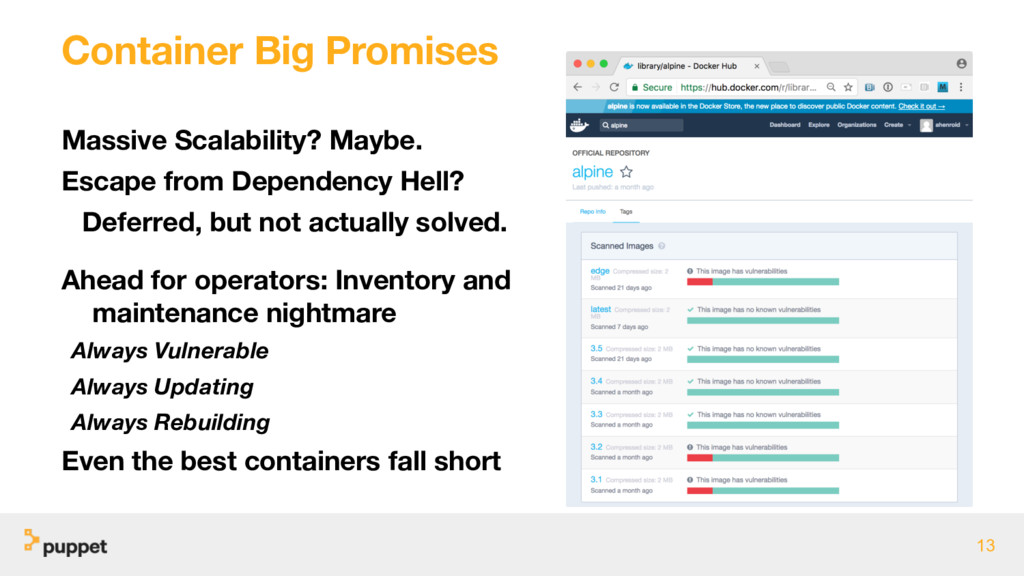
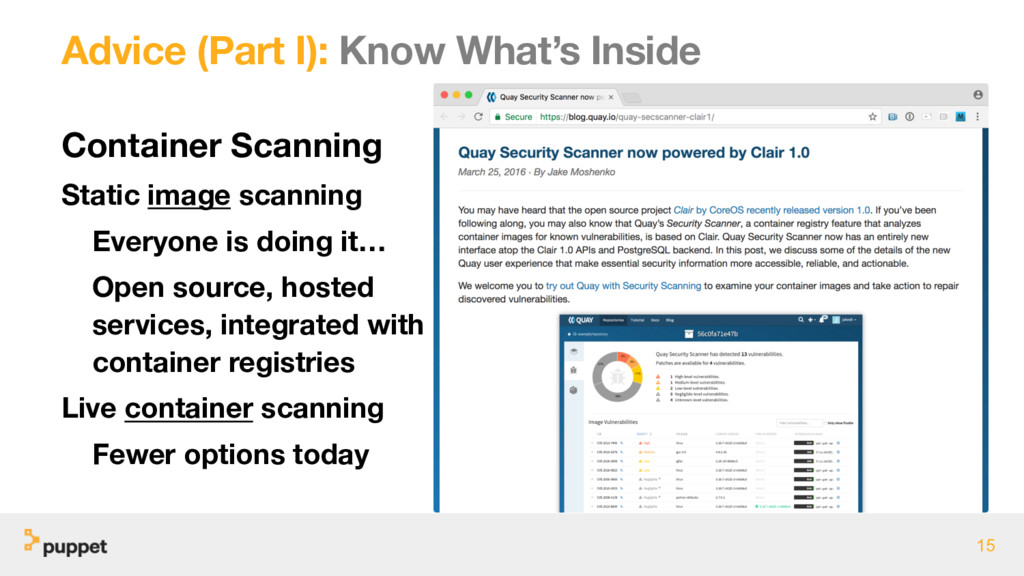
Today’s best practices for building and deploying Linux containers do not always align with the messy realities of containers used in production. In the wild, the vast majority of containers include entire OS filesystems, applications with complex and often poorly understood dependencies, and a plethora of libraries, with all of their attendant security vulnerability and maintenance concerns.
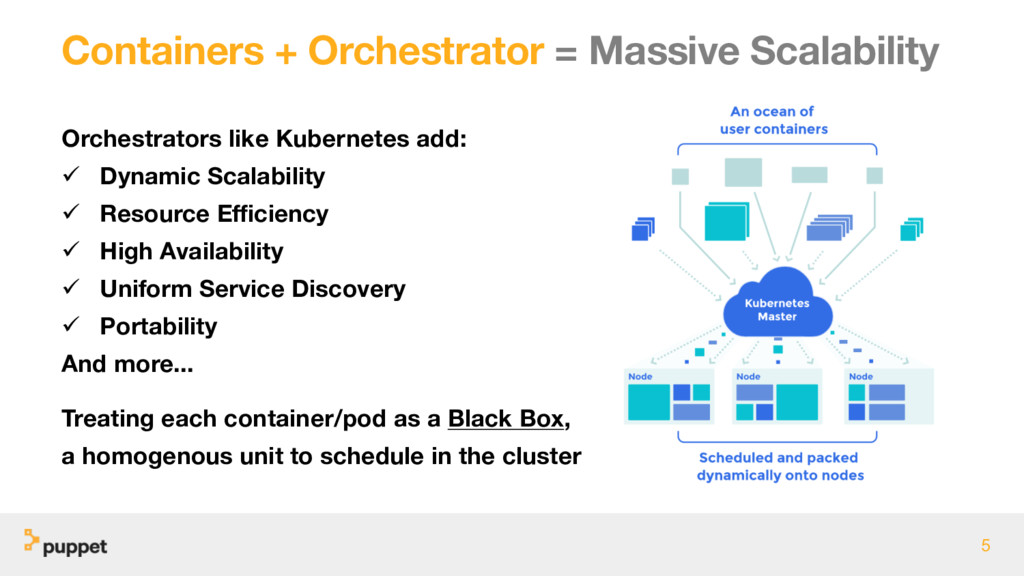
Container orchestration systems like Kubernetes encourage us to treat containers as immutable black boxes. From these building blocks, developers can assemble, integrate, and scale distributed applications with relative ease. Containers as black boxes, is that a brilliant idea or, considering what might be lurking inside, a terrible idea? The answer is both, and after this talk, you will understand why.


 tetsuya28
 puhitaku
 nealle
 masakiokuda
 ymotongpoo
 willnet
 namiki64
 takuroabe
 riyaamemiya
 recruitengineers
 shuta13
 oikon48
 destraynor
 speakerdeck
 katarinadahlin
 andyhume
 schlessera
 lara
 csswizardry
 tenderlove
 inesmontani
 dugsong
 palkan
 techseoconnect