Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
インフラ構築の自動化・量産化
Search
AkimitsuHamaguchi
July 11, 2014
Programming
1k
3
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
インフラ構築の自動化・量産化
AkimitsuHamaguchi
July 11, 2014
Other Decks in Programming
See All in Programming
ジョジョの世界をXRで再現する
mofurune
0
170
エージェントを使い続けるためのメタワーク / Meta-work for keeping using the agent
rkaga
1
190
現場と育てるRailsモデリング 〜Spreadsheetから始めたモデル設計〜
siroemk
2
630
AI主導のプログラミング学習アプリを作ってみた
econanringo
0
180
Apple Intelligence を用いた個人情報誤送信防止、及びユーザーリクエスト体験の改善について
yukiny
0
350
[JA] Domain Modeling with Vanilla Rails: 「操作」から再考するRailsの設計論
yasaichi
3
440
PumaからFalconに移行したRailsアプリケーションでの実践
falcon8823
0
180
【加筆修正版】Laravel のアプリケーションをどこにデプロイするか #phpcon_ehime
akase244
0
150
S3 TablesのIcebergデータに、AIエージェントからアクセスしてみた / 20261016developersio2026joetsu-accessing-iceberg-in-s3tables-via-agent
kasacchiful
PRO
0
170
R8 の設定見直しでアプリサイズ削減
andpad
0
220
UPDATE をやめる — EF Core でマスタをバージョン管理する
panda728
PRO
0
1.2k
phperだってパンチカードでコーディングしたい
o0h
PRO
0
350
Featured
See All Featured
The Anti-SEO Checklist Checklist. Pubcon Cyber Week
ryanjones
0
270
Distributed Sagas: A Protocol for Coordinating Microservices
caitiem20
333
23k
We Analyzed 250 Million AI Search Results: Here's What I Found
joshbly
2
2k
Future Trends and Review - Lecture 12 - Web Technologies (1019888BNR)
signer
PRO
0
3.8k
Keith and Marios Guide to Fast Websites
keithpitt
413
23k
Product Roadmaps are Hard
iamctodd
55
13k
How to make the Groovebox
asonas
2
2.5k
Jamie Indigo - Trashchat’s Guide to Black Boxes: Technical SEO Tactics for LLMs
techseoconnect
PRO
0
710
DBのスキルで生き残る技術 - AI時代におけるテーブル設計の勘所
soudai
PRO
68
58k
Refactoring Trust on Your Teams (GOTO; Chicago 2020)
rmw
35
3.8k
Data-driven link building: lessons from a $708K investment (BrightonSEO talk)
szymonslowik
1
1.4k
A Soul's Torment
seathinner
8
3.8k
Transcript
インフラ構築の自動化・量産化 ~Chefによる運用管理~
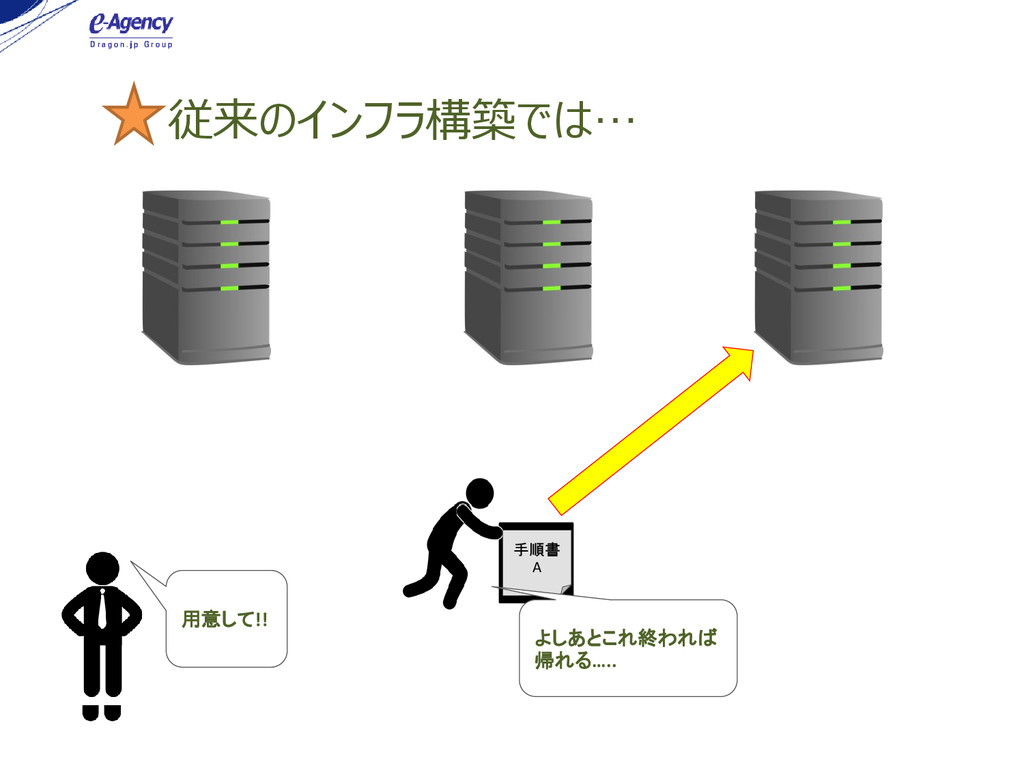
従来のインフラ構築では…
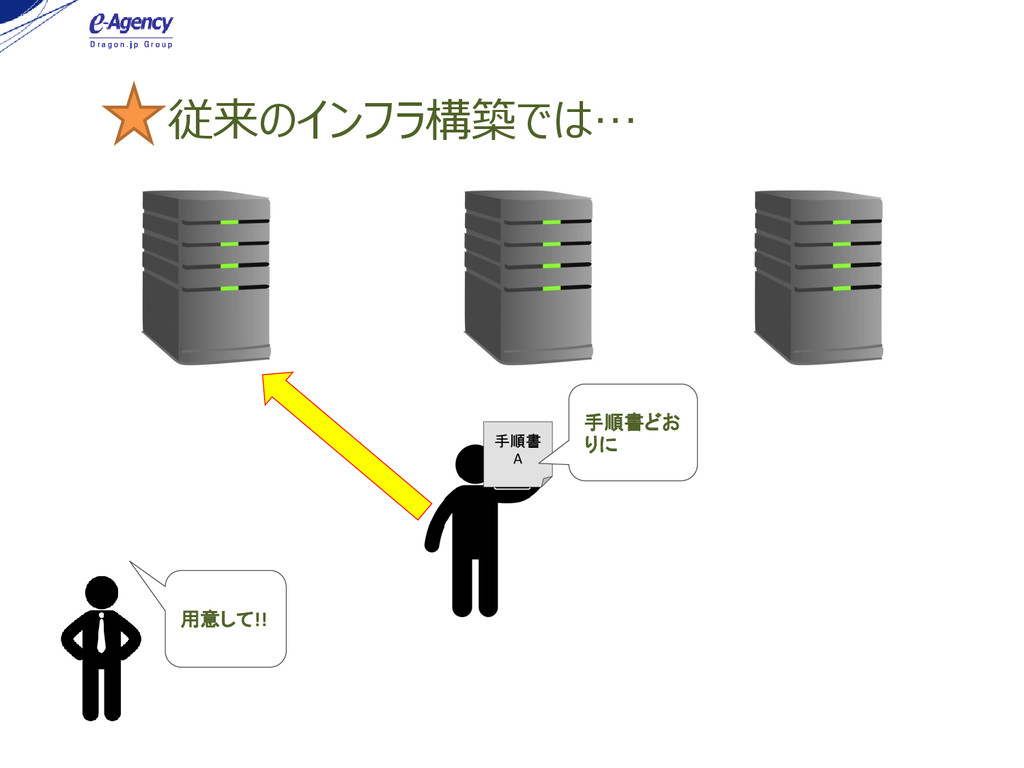
従来のインフラ構築では… 手順書 A 手順書どお りに 用意して!!
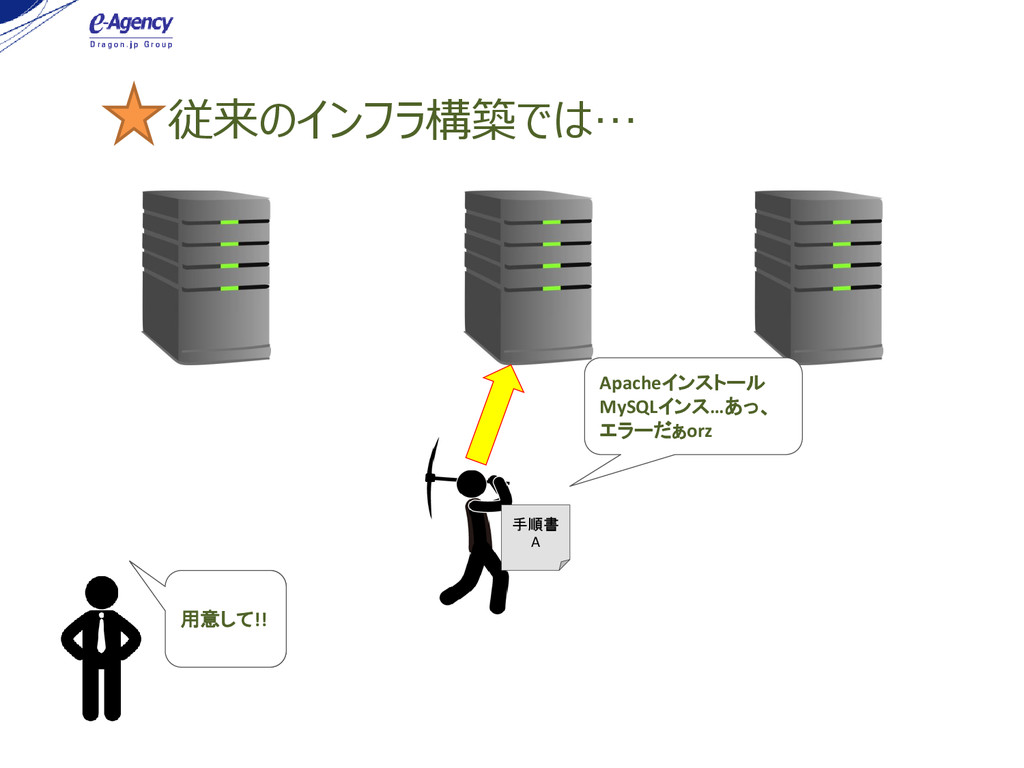
従来のインフラ構築では… 手順書 A Apacheインストール MySQLインス…あっ、 エラーだぁorz 用意して!! 用意して!!
従来のインフラ構築では… 手順書 A よしあとこれ終われば 帰れる….. 用意して!! 用意して!! 用意して!!
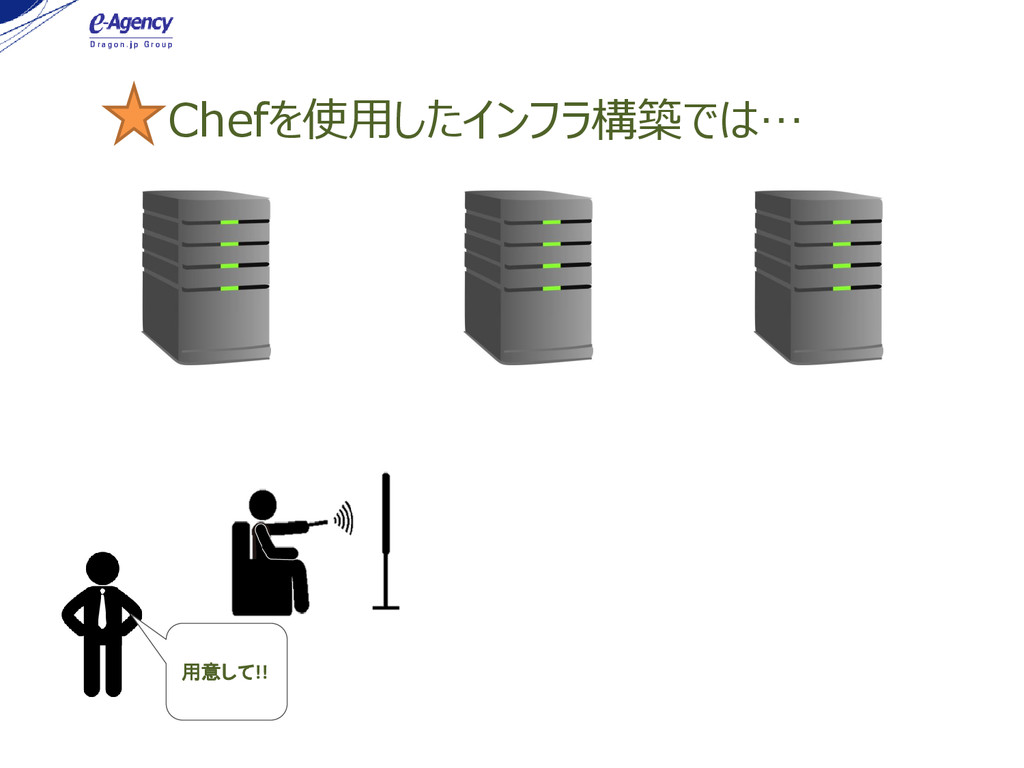
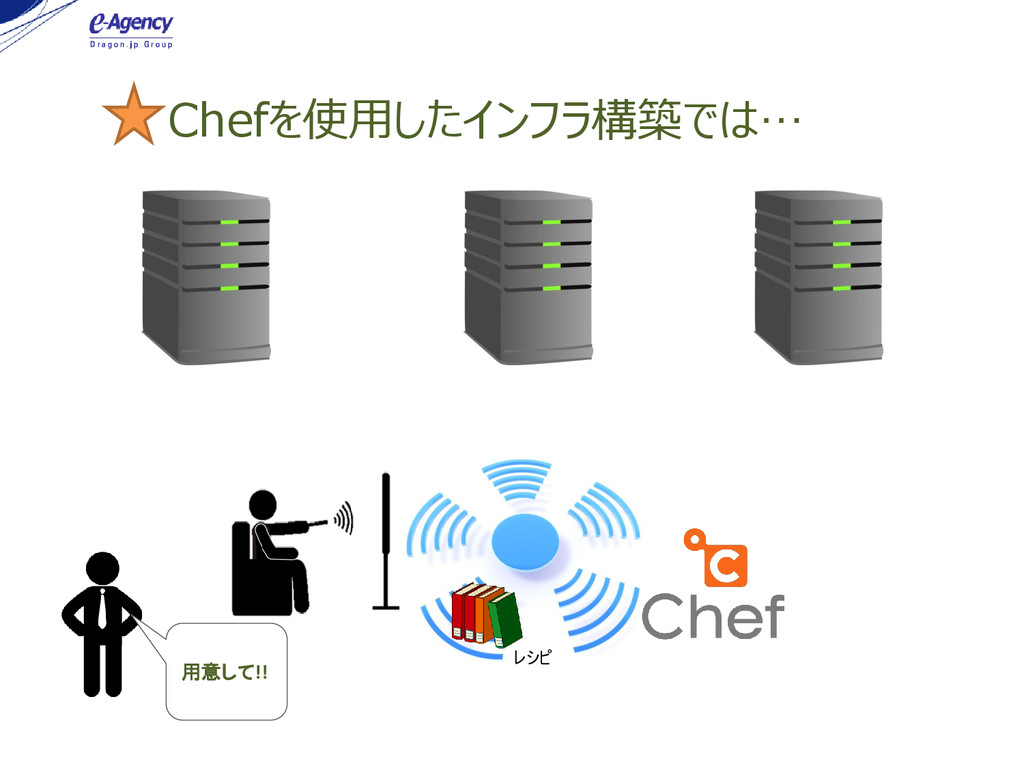
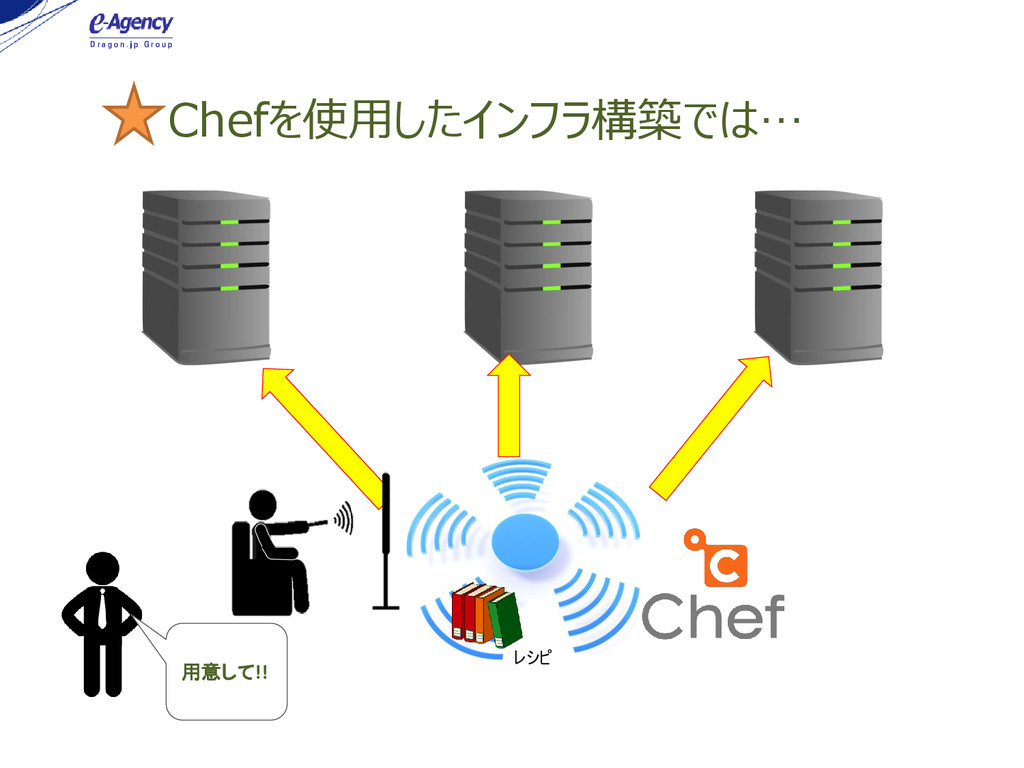
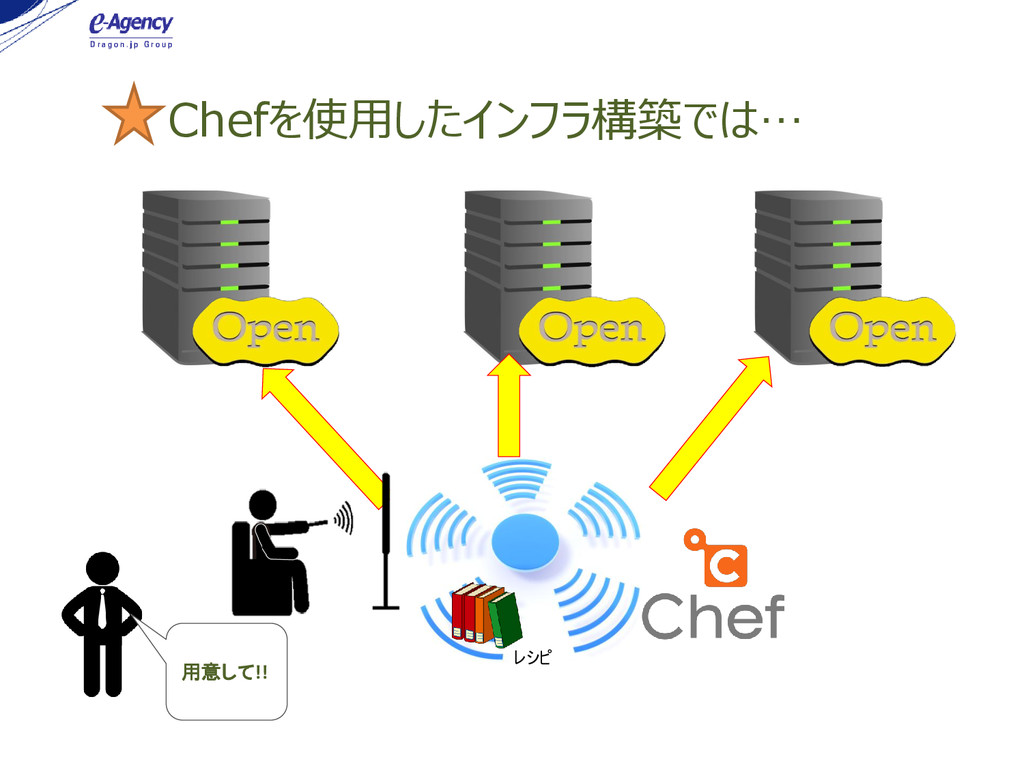
Chefを使用したインフラ構築では…
Chefを使用したインフラ構築では… 用意して!!
レシピ Chefを使用したインフラ構築では… 用意して!!
レシピ Chefを使用したインフラ構築では… 用意して!!
レシピ Chefを使用したインフラ構築では… 用意して!!
Chefとは
Chefとは サーバの自動構築のためのフレームワーク
Chefとは サーバの自動構築のためのフレームワーク あたかもRubyでプログラミングをするように インフラの構成管理をコードによって行える
Chefとは サーバの自動構築のためのフレームワーク あたかもRubyでプログラミングをするように インフラの構成管理をコードによって行える 設定+確認作業をミス無く実施(もしくは 間違いが発生しても複数台に即修正を 反映)できる
Chefの理念
Chefの理念 ~Infrastructure as CODE~ インフラをプログラミングしてコード化
Chefの理念 ~Infrastructure as CODE~ インフラをプログラミングしてコード化 Idempotence サーバのあるべき状態に管理 する「冪等性(べきとうせい) 」
Chefの理念 ~Infrastructure as CODE~ インフラをプログラミングしてコード化 Idempotence サーバのあるべき状態に管理 する「冪等性(べきとうせい) 」 手順ではなく状態を定義
サーバの状態をコードという外部表 現で管理
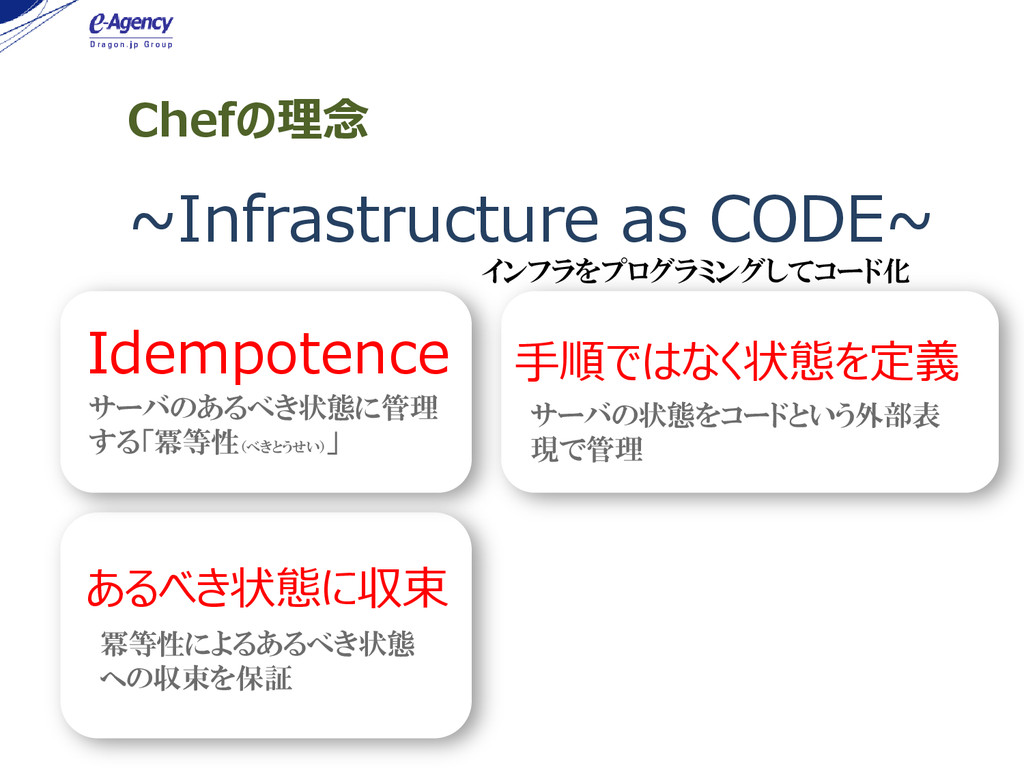
Chefの理念 ~Infrastructure as CODE~ インフラをプログラミングしてコード化 Idempotence サーバのあるべき状態に管理 する「冪等性(べきとうせい) 」 手順ではなく状態を定義
サーバの状態をコードという外部表 現で管理 あるべき状態に収束 冪等性によるあるべき状態 への収束を保証
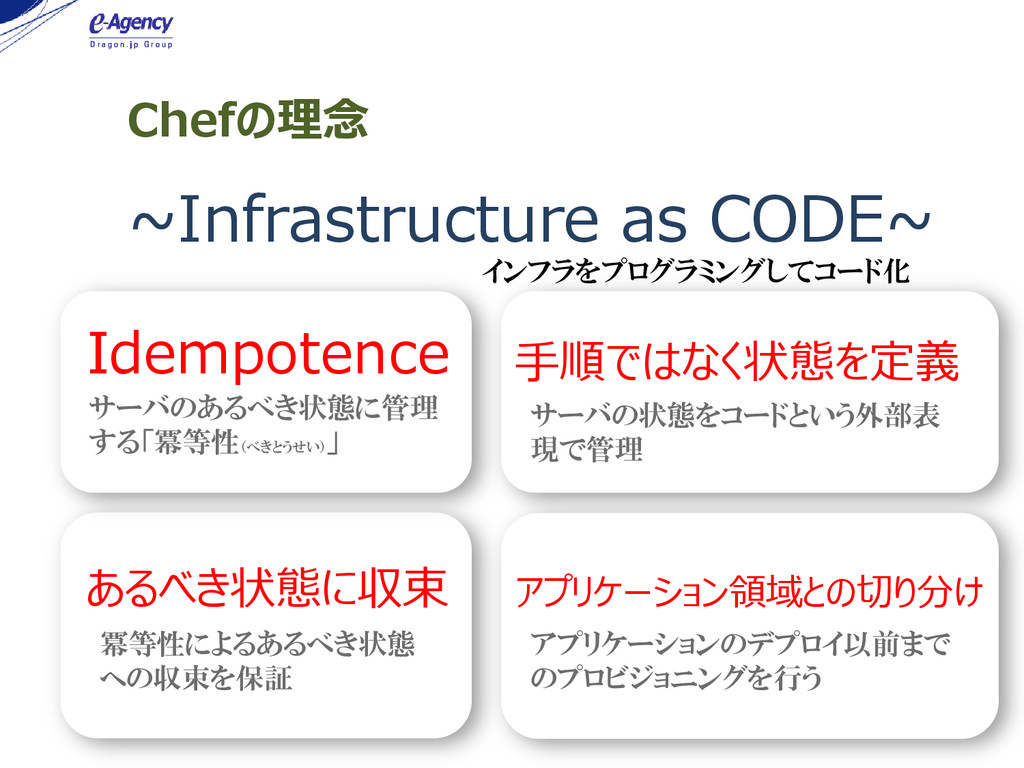
Chefの理念 ~Infrastructure as CODE~ インフラをプログラミングしてコード化 Idempotence サーバのあるべき状態に管理 する「冪等性(べきとうせい) 」 手順ではなく状態を定義
サーバの状態をコードという外部表 現で管理 あるべき状態に収束 冪等性によるあるべき状態 への収束を保証 アプリケーション領域との切り分け アプリケーションのデプロイ以前まで のプロビジョニングを行う
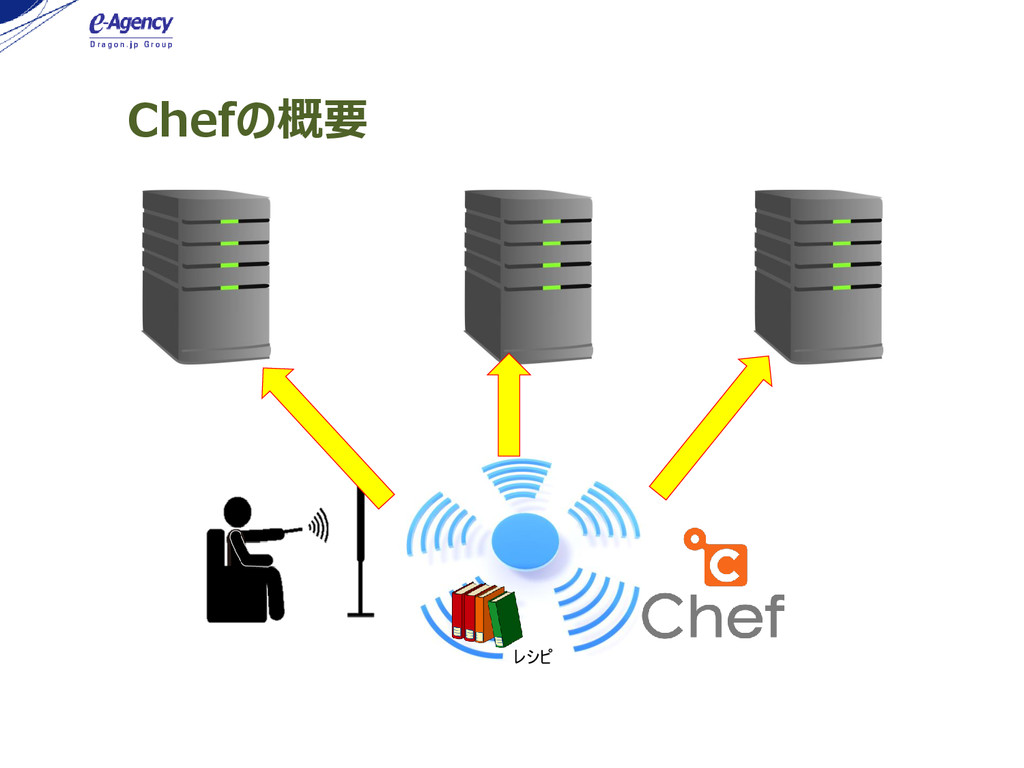
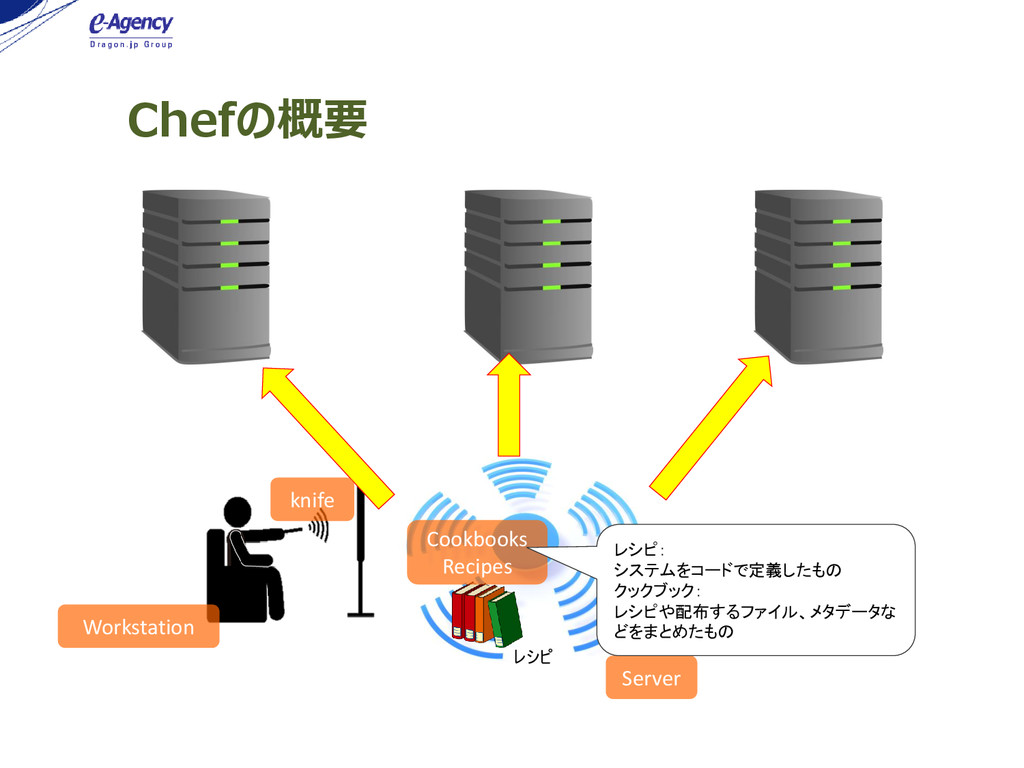
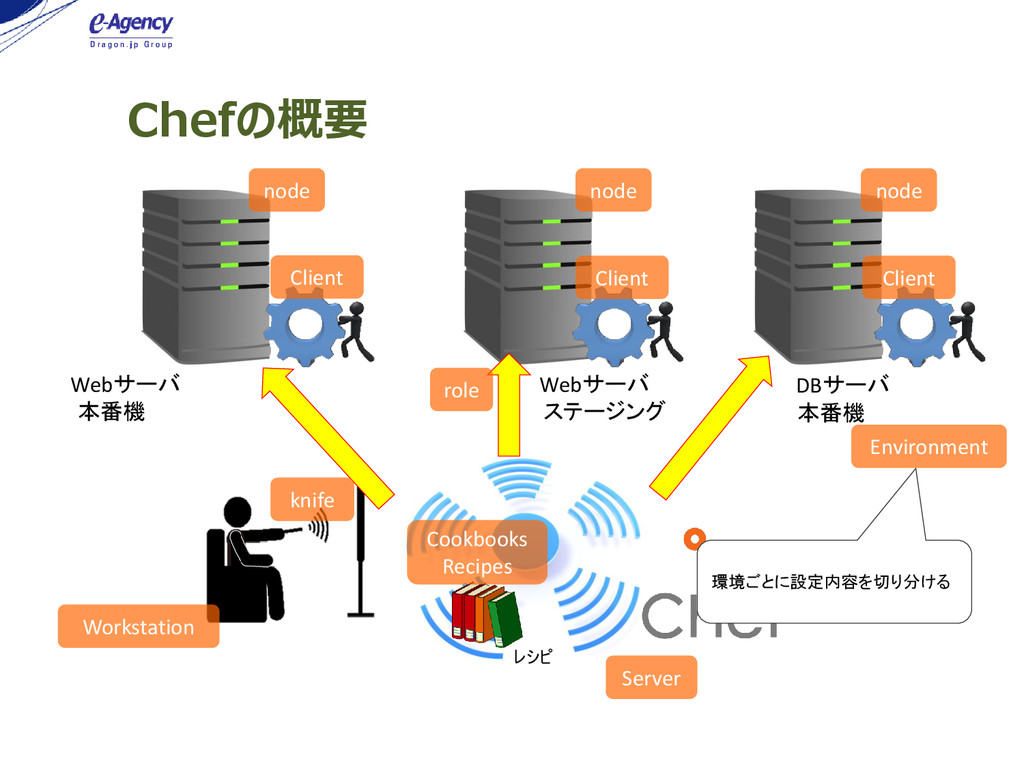
Chefの概要 レシピ
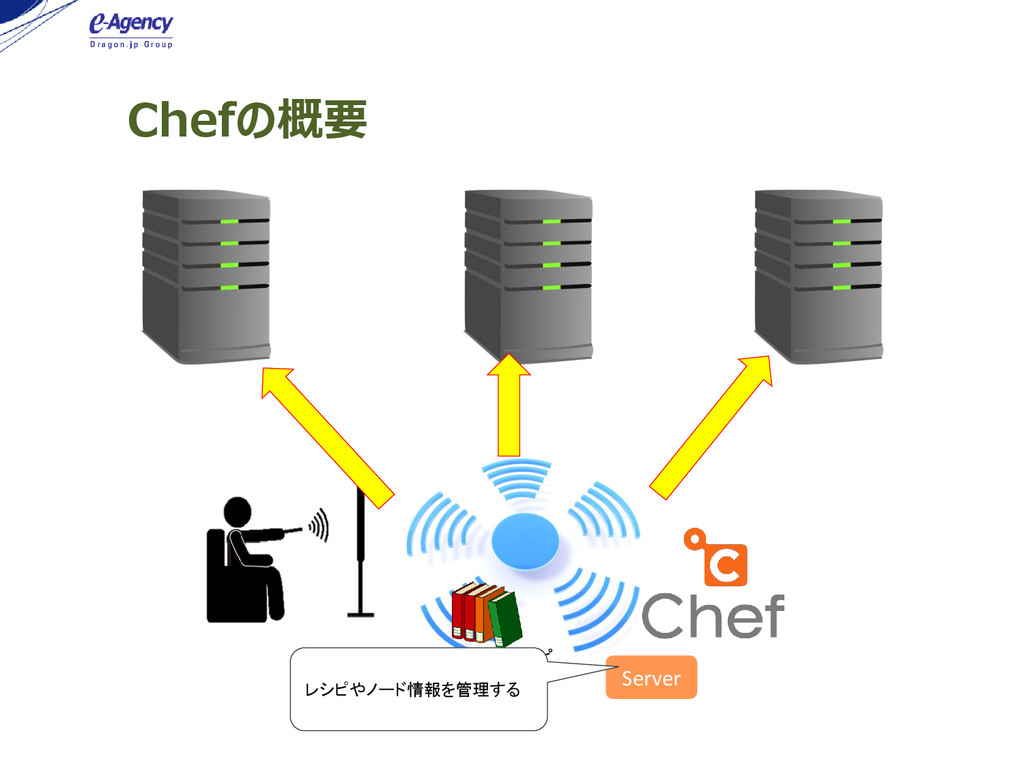
Chefの概要 レシピ Server レシピやノード情報を管理する
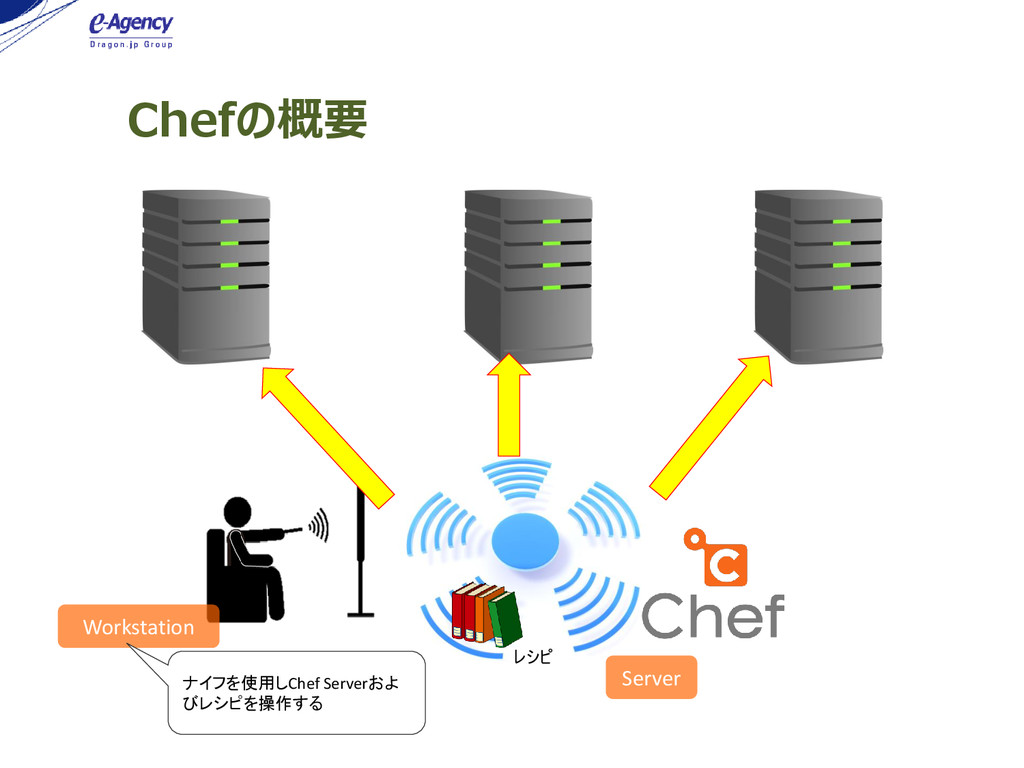
Chefの概要 レシピ Workstation Server ナイフを使用しChef Serverおよ びレシピを操作する
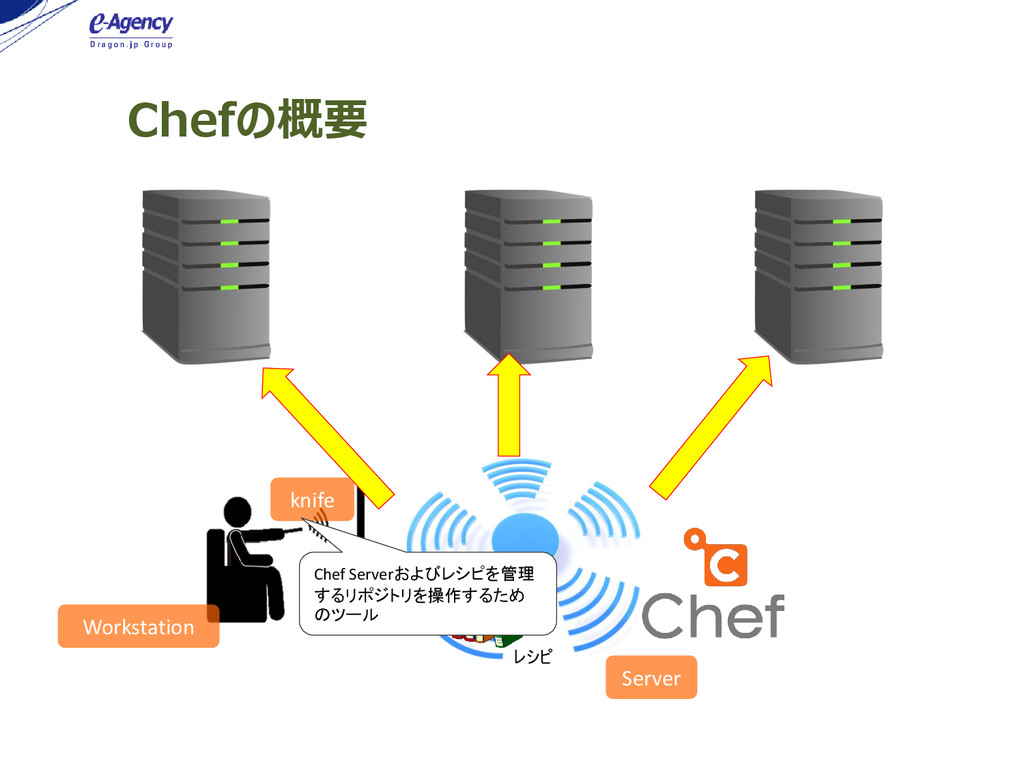
Chefの概要 レシピ Workstation Server knife Chef Serverおよびレシピを管理 するリポジトリを操作するため のツール
Chefの概要 レシピ Workstation Server knife Cookbooks Recipes レシピ: システムをコードで定義したもの クックブック:
レシピや配布するファイル、メタデータな どをまとめたもの
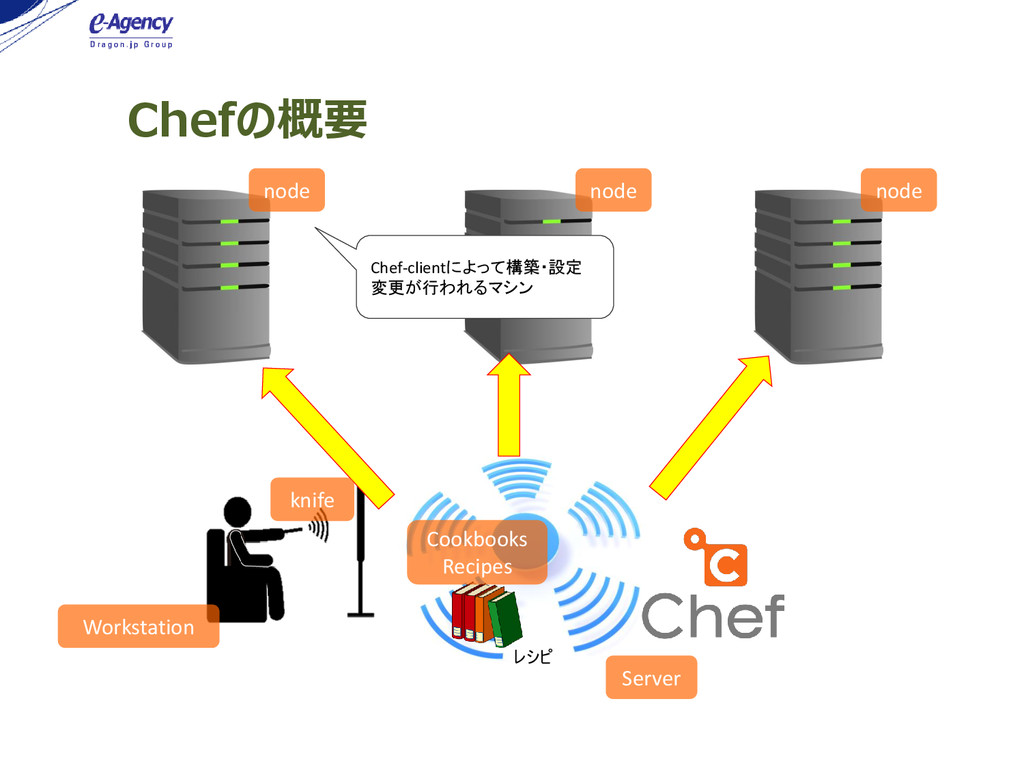
Chefの概要 レシピ Workstation Server node node node knife Cookbooks Recipes
Chef-clientによって構築・設定 変更が行われるマシン
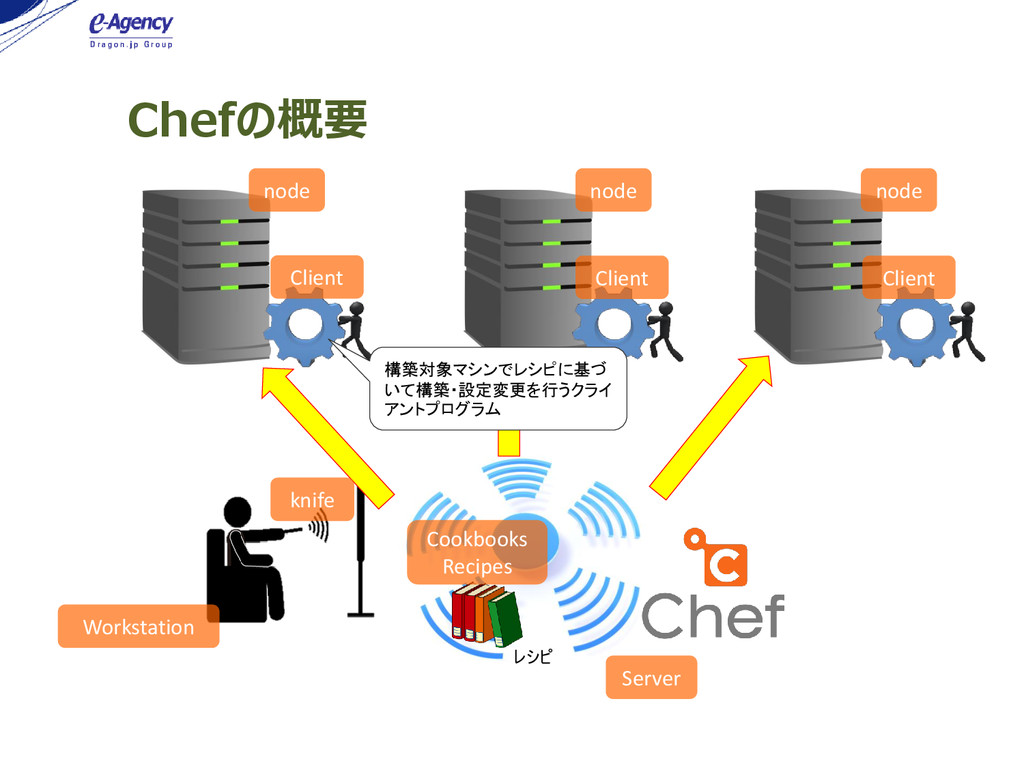
Chefの概要 レシピ Workstation Server node node node Client Client Client
knife Cookbooks Recipes 構築対象マシンでレシピに基づ いて構築・設定変更を行うクライ アントプログラム
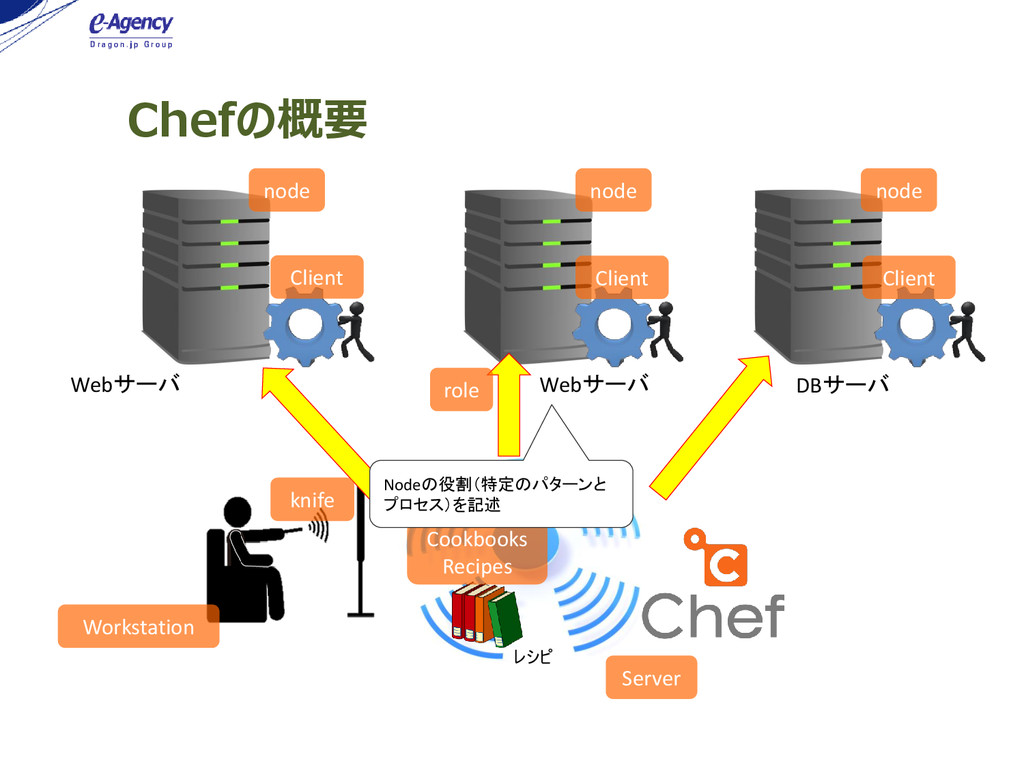
Chefの概要 レシピ Workstation Server node node node Client Client Client
role Webサーバ DBサーバ Webサーバ knife Cookbooks Recipes Nodeの役割(特定のパターンと プロセス)を記述
Chefの概要 レシピ Workstation Server node node node Client Client Client
role Environment Webサーバ DBサーバ 本番機 Webサーバ ステージング 本番機 knife Cookbooks Recipes 環境ごとに設定内容を切り分ける
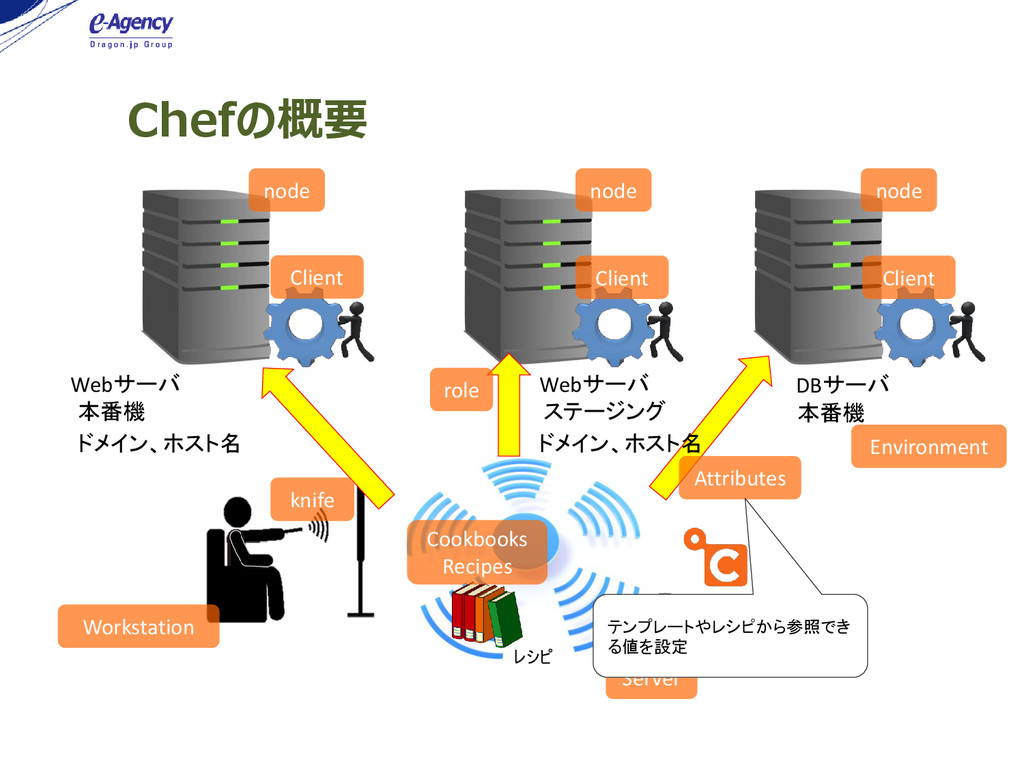
Chefの概要 レシピ Workstation Server node node node Client Client Client
role Environment Webサーバ DBサーバ 本番機 Webサーバ ステージング 本番機 ドメイン、ホスト名 knife Cookbooks Recipes Attributes ドメイン、ホスト名 テンプレートやレシピから参照でき る値を設定
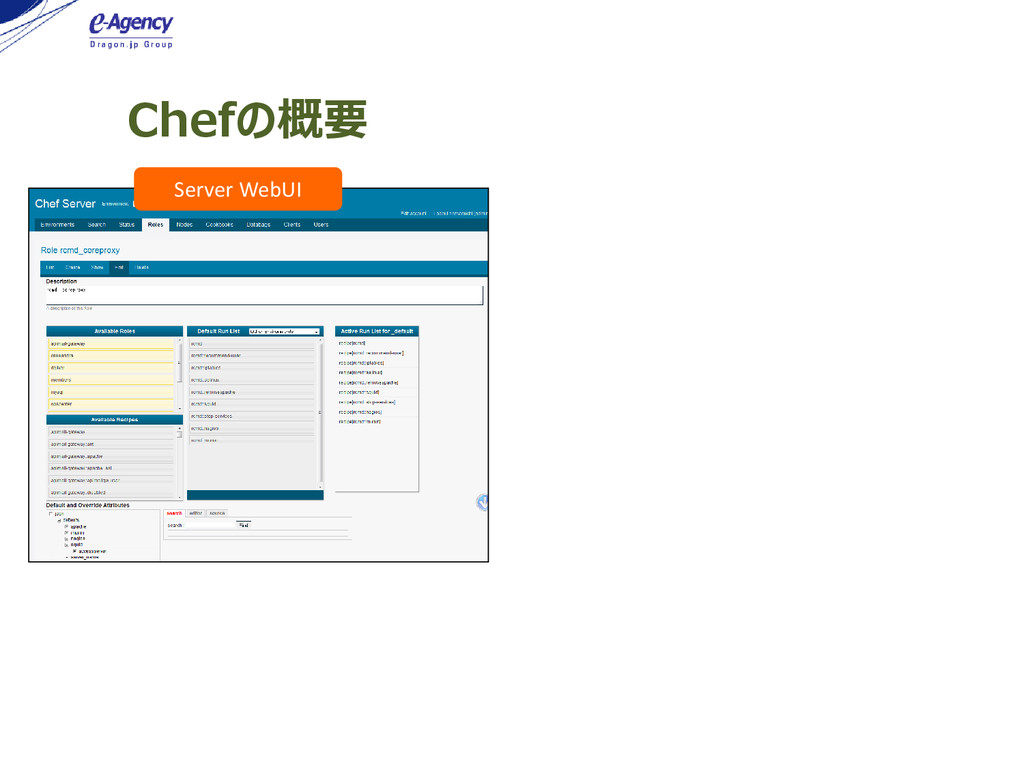
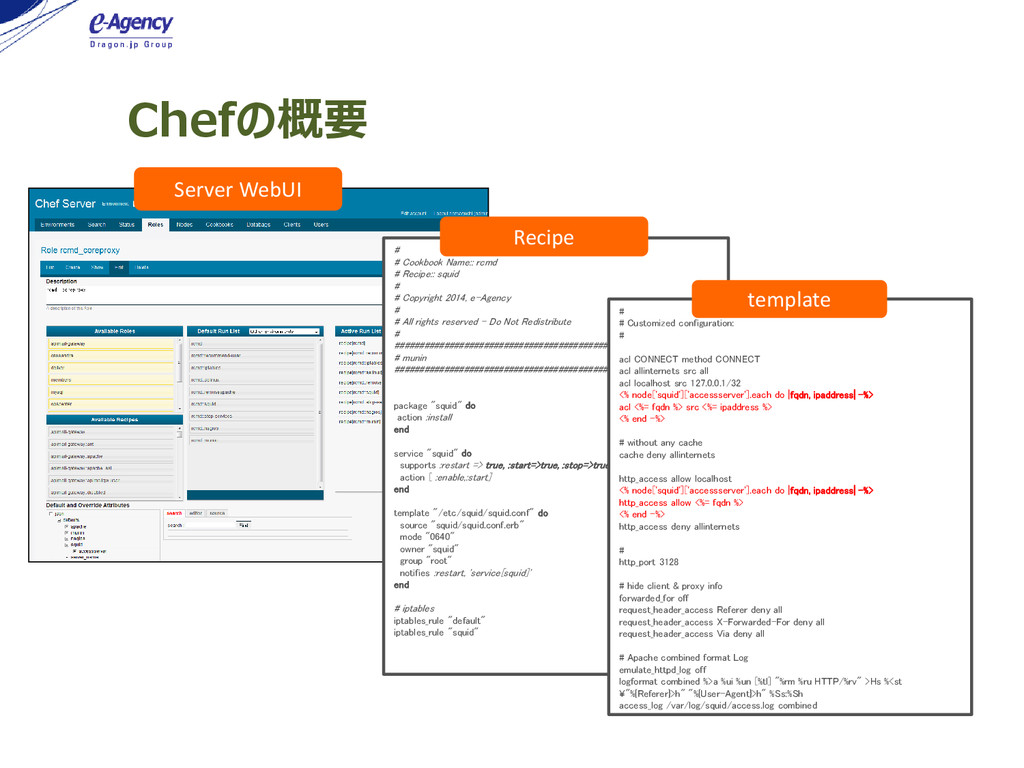
Chefの概要 Server WebUI
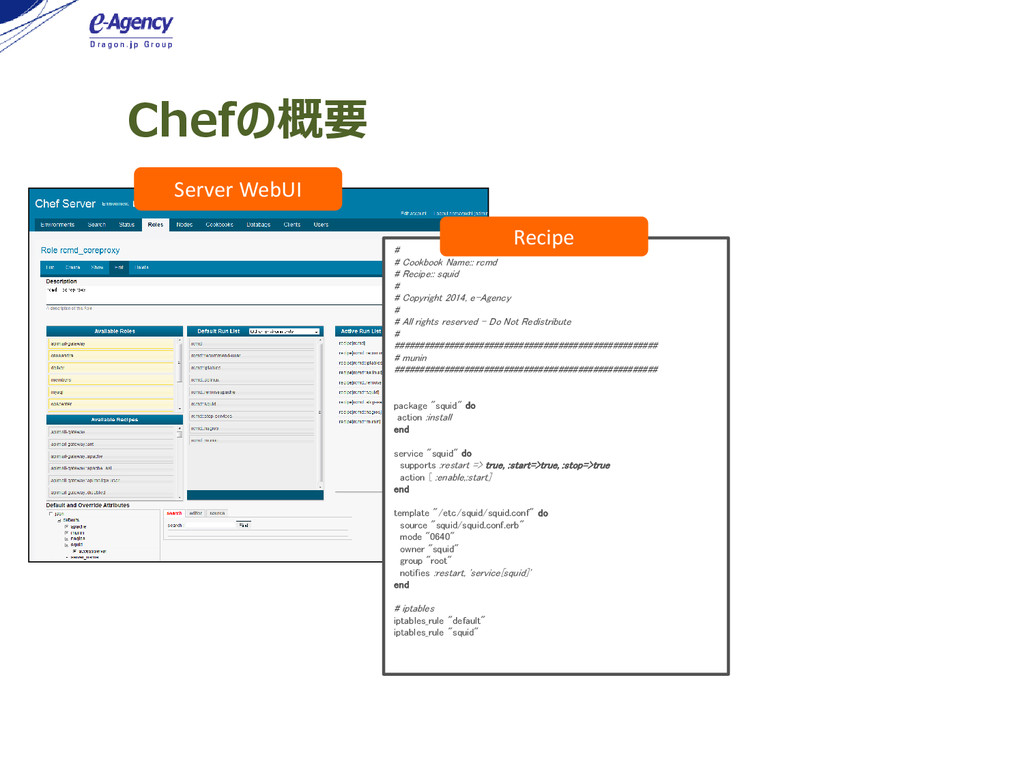
Chefの概要 Server WebUI # # Cookbook Name:: rcmd # Recipe::
squid # # Copyright 2014, e-Agency # # All rights reserved - Do Not Redistribute # ##################################################### # munin ##################################################### package "squid" do action :install end service "squid" do supports :restart => true, :start=>true, :stop=>true action [ :enable,:start] end template "/etc/squid/squid.conf" do source "squid/squid.conf.erb" mode "0640" owner "squid" group "root" notifies :restart, 'service[squid]' end # iptables iptables_rule "default" iptables_rule "squid" Recipe
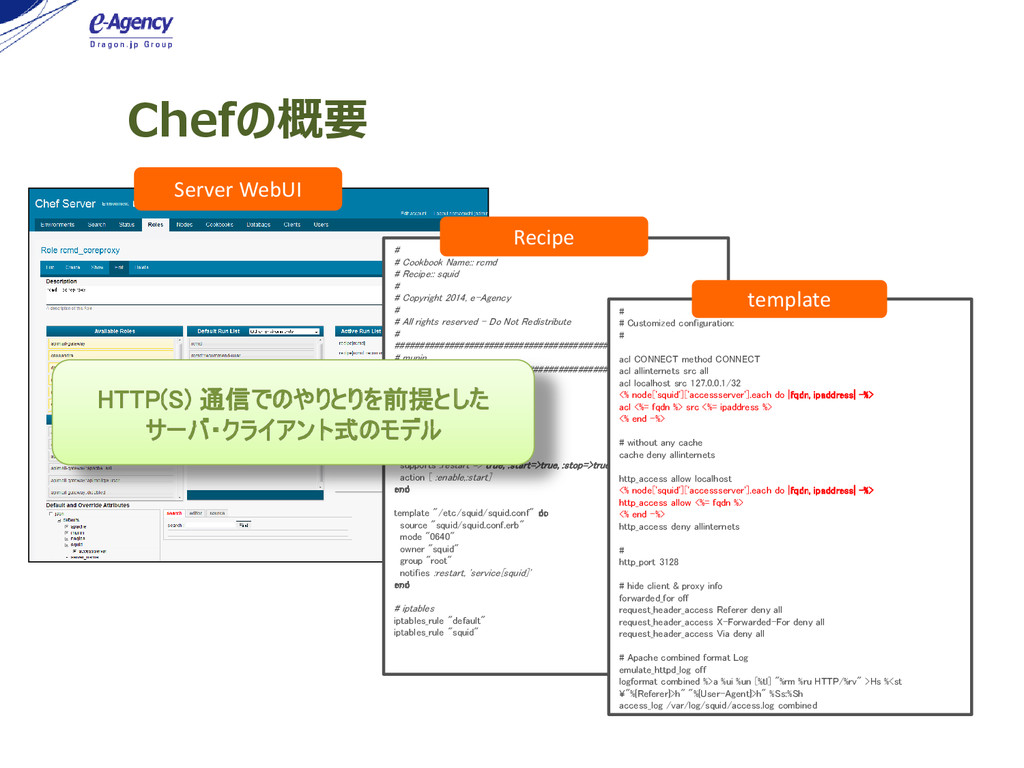
Chefの概要 Server WebUI # # Cookbook Name:: rcmd # Recipe::
squid # # Copyright 2014, e-Agency # # All rights reserved - Do Not Redistribute # ##################################################### # munin ##################################################### package "squid" do action :install end service "squid" do supports :restart => true, :start=>true, :stop=>true action [ :enable,:start] end template "/etc/squid/squid.conf" do source "squid/squid.conf.erb" mode "0640" owner "squid" group "root" notifies :restart, 'service[squid]' end # iptables iptables_rule "default" iptables_rule "squid" Recipe # # Customized configuration: # acl CONNECT method CONNECT acl allinternets src all acl localhost src 127.0.0.1/32 <% node['squid']['accessserver'].each do |fqdn, ipaddress| -%> acl <%= fqdn %> src <%= ipaddress %> <% end -%> # without any cache cache deny allinternets http_access allow localhost <% node['squid']['accessserver'].each do |fqdn, ipaddress| -%> http_access allow <%= fqdn %> <% end -%> http_access deny allinternets # http_port 3128 # hide client & proxy info forwarded_for off request_header_access Referer deny all request_header_access X-Forwarded-For deny all request_header_access Via deny all # Apache combined format Log emulate_httpd_log off logformat combined %>a %ui %un [%tl] "%rm %ru HTTP/%rv" >Hs %<st ¥"%{Referer}>h" "%{User-Agent}>h" %Ss:%Sh access_log /var/log/squid/access.log combined template
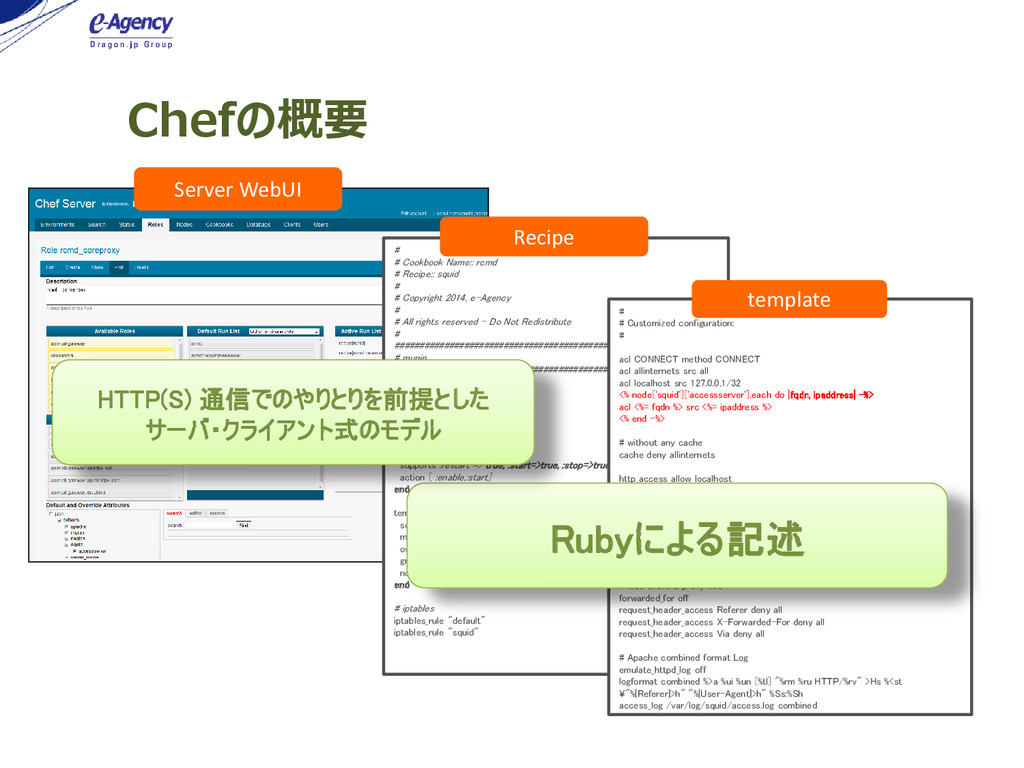
Chefの概要 Server WebUI # # Cookbook Name:: rcmd # Recipe::
squid # # Copyright 2014, e-Agency # # All rights reserved - Do Not Redistribute # ##################################################### # munin ##################################################### package "squid" do action :install end service "squid" do supports :restart => true, :start=>true, :stop=>true action [ :enable,:start] end template "/etc/squid/squid.conf" do source "squid/squid.conf.erb" mode "0640" owner "squid" group "root" notifies :restart, 'service[squid]' end # iptables iptables_rule "default" iptables_rule "squid" Recipe # # Customized configuration: # acl CONNECT method CONNECT acl allinternets src all acl localhost src 127.0.0.1/32 <% node['squid']['accessserver'].each do |fqdn, ipaddress| -%> acl <%= fqdn %> src <%= ipaddress %> <% end -%> # without any cache cache deny allinternets http_access allow localhost <% node['squid']['accessserver'].each do |fqdn, ipaddress| -%> http_access allow <%= fqdn %> <% end -%> http_access deny allinternets # http_port 3128 # hide client & proxy info forwarded_for off request_header_access Referer deny all request_header_access X-Forwarded-For deny all request_header_access Via deny all # Apache combined format Log emulate_httpd_log off logformat combined %>a %ui %un [%tl] "%rm %ru HTTP/%rv" >Hs %<st ¥"%{Referer}>h" "%{User-Agent}>h" %Ss:%Sh access_log /var/log/squid/access.log combined template HTTP(S) 通信でのやりとりを前提とした サーバ・クライアント式のモデル
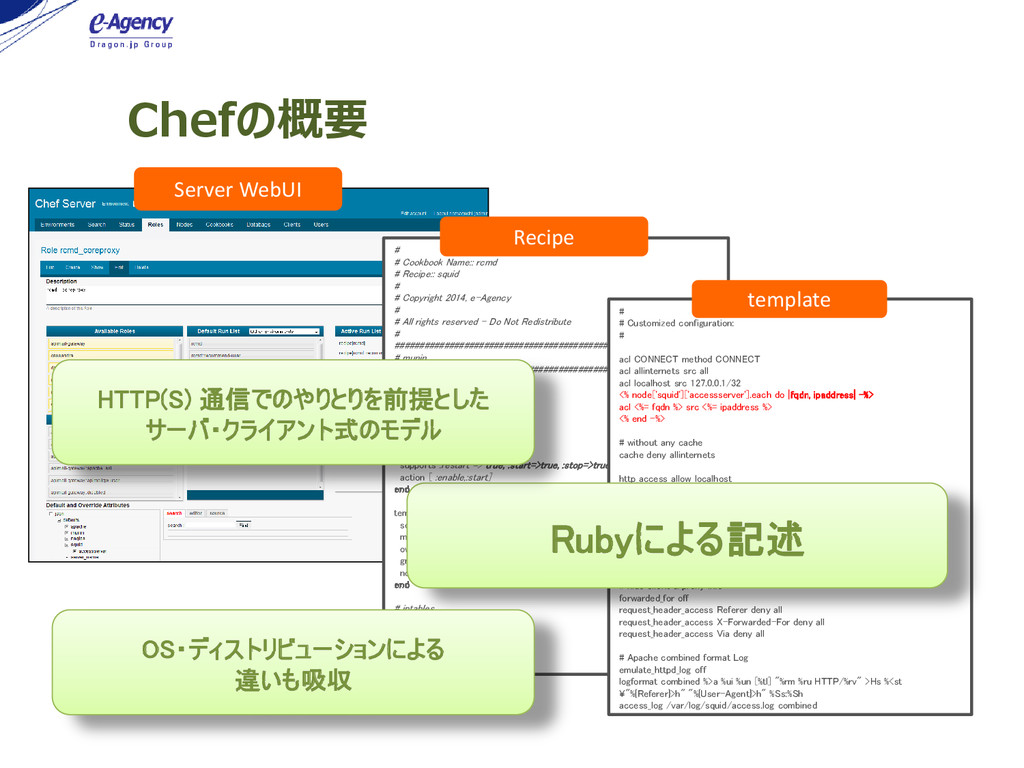
Chefの概要 Server WebUI # # Cookbook Name:: rcmd # Recipe::
squid # # Copyright 2014, e-Agency # # All rights reserved - Do Not Redistribute # ##################################################### # munin ##################################################### package "squid" do action :install end service "squid" do supports :restart => true, :start=>true, :stop=>true action [ :enable,:start] end template "/etc/squid/squid.conf" do source "squid/squid.conf.erb" mode "0640" owner "squid" group "root" notifies :restart, 'service[squid]' end # iptables iptables_rule "default" iptables_rule "squid" Recipe # # Customized configuration: # acl CONNECT method CONNECT acl allinternets src all acl localhost src 127.0.0.1/32 <% node['squid']['accessserver'].each do |fqdn, ipaddress| -%> acl <%= fqdn %> src <%= ipaddress %> <% end -%> # without any cache cache deny allinternets http_access allow localhost <% node['squid']['accessserver'].each do |fqdn, ipaddress| -%> http_access allow <%= fqdn %> <% end -%> http_access deny allinternets # http_port 3128 # hide client & proxy info forwarded_for off request_header_access Referer deny all request_header_access X-Forwarded-For deny all request_header_access Via deny all # Apache combined format Log emulate_httpd_log off logformat combined %>a %ui %un [%tl] "%rm %ru HTTP/%rv" >Hs %<st ¥"%{Referer}>h" "%{User-Agent}>h" %Ss:%Sh access_log /var/log/squid/access.log combined template Rubyによる記述 HTTP(S) 通信でのやりとりを前提とした サーバ・クライアント式のモデル
Chefの概要 Server WebUI # # Cookbook Name:: rcmd # Recipe::
squid # # Copyright 2014, e-Agency # # All rights reserved - Do Not Redistribute # ##################################################### # munin ##################################################### package "squid" do action :install end service "squid" do supports :restart => true, :start=>true, :stop=>true action [ :enable,:start] end template "/etc/squid/squid.conf" do source "squid/squid.conf.erb" mode "0640" owner "squid" group "root" notifies :restart, 'service[squid]' end # iptables iptables_rule "default" iptables_rule "squid" Recipe # # Customized configuration: # acl CONNECT method CONNECT acl allinternets src all acl localhost src 127.0.0.1/32 <% node['squid']['accessserver'].each do |fqdn, ipaddress| -%> acl <%= fqdn %> src <%= ipaddress %> <% end -%> # without any cache cache deny allinternets http_access allow localhost <% node['squid']['accessserver'].each do |fqdn, ipaddress| -%> http_access allow <%= fqdn %> <% end -%> http_access deny allinternets # http_port 3128 # hide client & proxy info forwarded_for off request_header_access Referer deny all request_header_access X-Forwarded-For deny all request_header_access Via deny all # Apache combined format Log emulate_httpd_log off logformat combined %>a %ui %un [%tl] "%rm %ru HTTP/%rv" >Hs %<st ¥"%{Referer}>h" "%{User-Agent}>h" %Ss:%Sh access_log /var/log/squid/access.log combined template Rubyによる記述 HTTP(S) 通信でのやりとりを前提とした サーバ・クライアント式のモデル OS・ディストリビューションによる 違いも吸収
e-Agencyにおける導入 ~クラウドプロダクト部における事例~
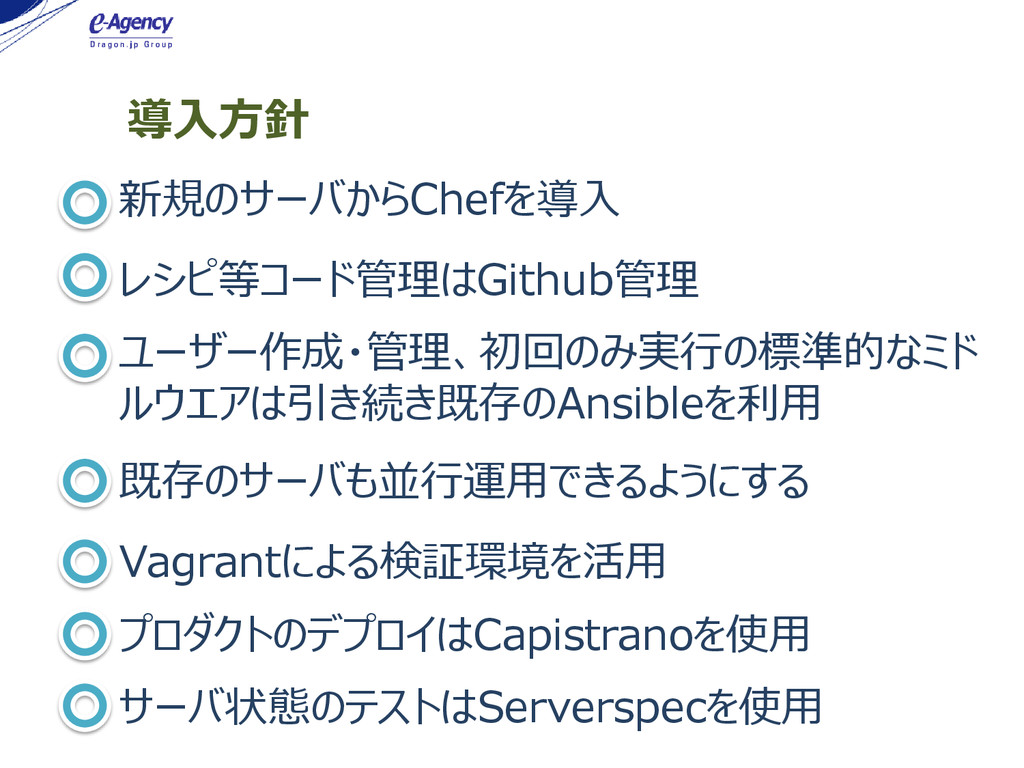
導入方針
導入方針 新規のサーバからChefを導入
導入方針 新規のサーバからChefを導入 レシピ等コード管理はGithub管理
導入方針 新規のサーバからChefを導入 レシピ等コード管理はGithub管理 ユーザー作成・管理、初回のみ実行の標準的なミド ルウエアは引き続き既存のAnsibleを利用
導入方針 新規のサーバからChefを導入 レシピ等コード管理はGithub管理 ユーザー作成・管理、初回のみ実行の標準的なミド ルウエアは引き続き既存のAnsibleを利用 既存のサーバも並行運用できるようにする
導入方針 新規のサーバからChefを導入 レシピ等コード管理はGithub管理 ユーザー作成・管理、初回のみ実行の標準的なミド ルウエアは引き続き既存のAnsibleを利用 既存のサーバも並行運用できるようにする Vagrantによる検証環境を活用
導入方針 新規のサーバからChefを導入 レシピ等コード管理はGithub管理 ユーザー作成・管理、初回のみ実行の標準的なミド ルウエアは引き続き既存のAnsibleを利用 既存のサーバも並行運用できるようにする Vagrantによる検証環境を活用 プロダクトのデプロイはCapistranoを使用
導入方針 新規のサーバからChefを導入 レシピ等コード管理はGithub管理 ユーザー作成・管理、初回のみ実行の標準的なミド ルウエアは引き続き既存のAnsibleを利用 既存のサーバも並行運用できるようにする Vagrantによる検証環境を活用 プロダクトのデプロイはCapistranoを使用 サーバ状態のテストはServerspecを使用
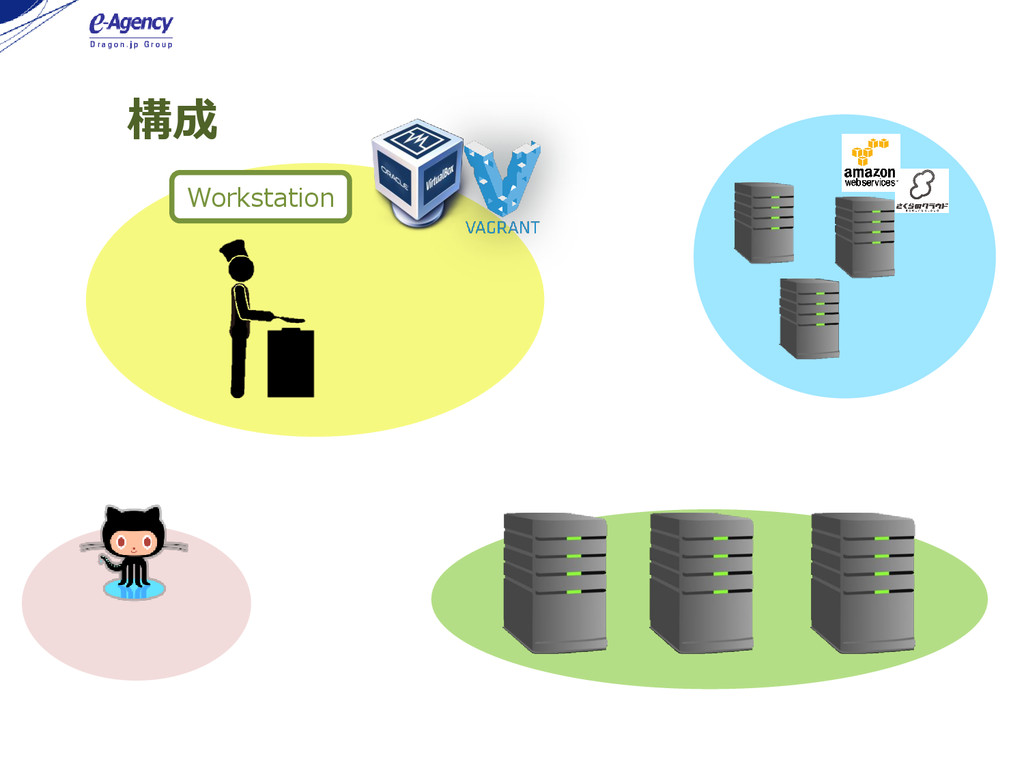
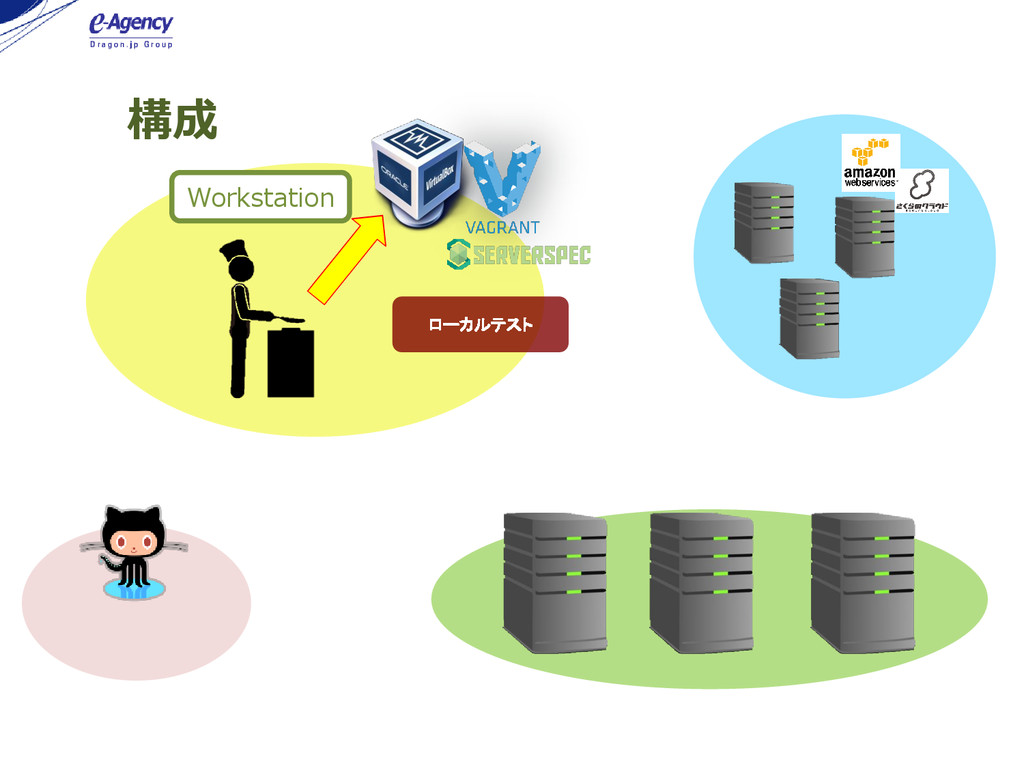
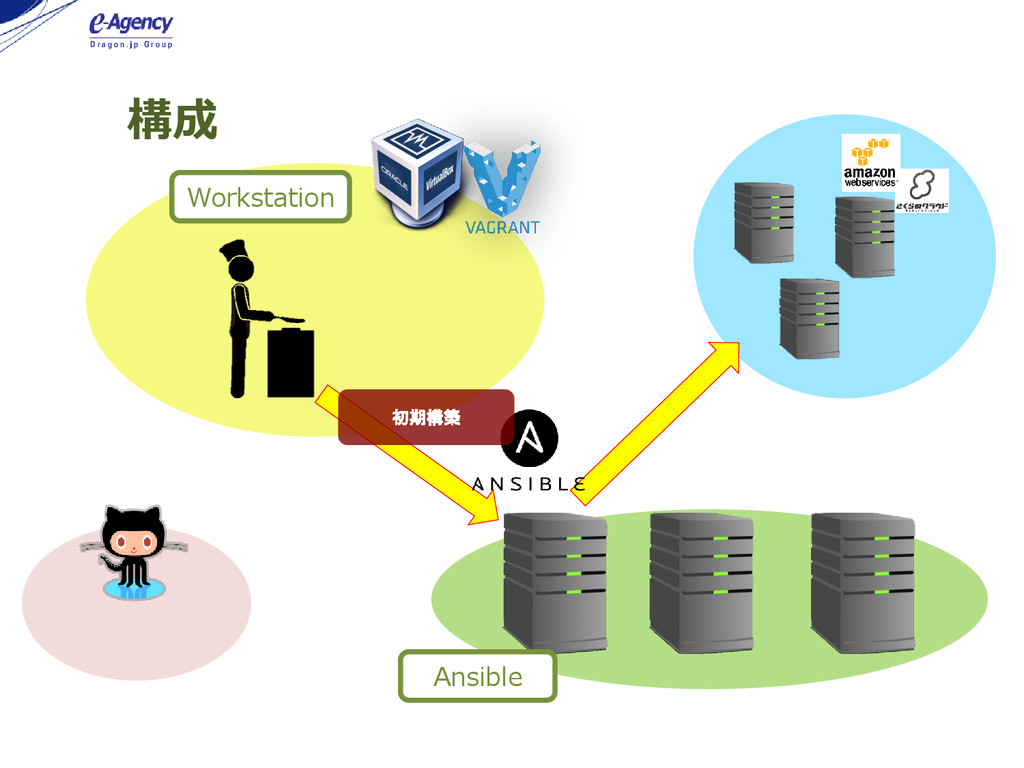
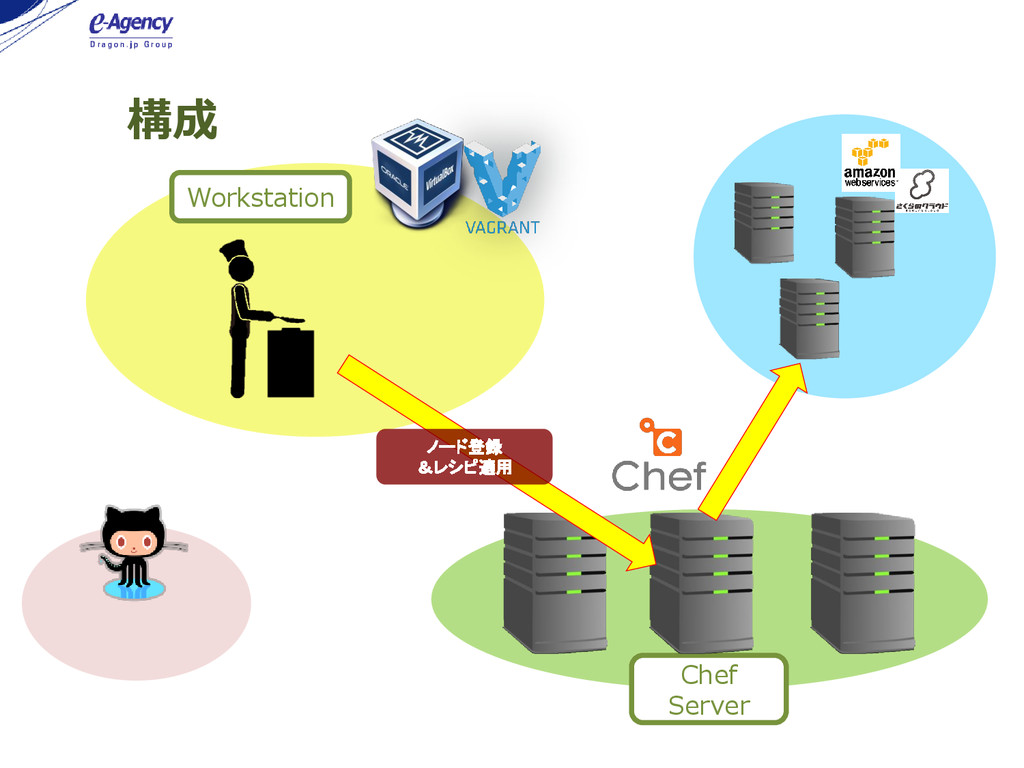
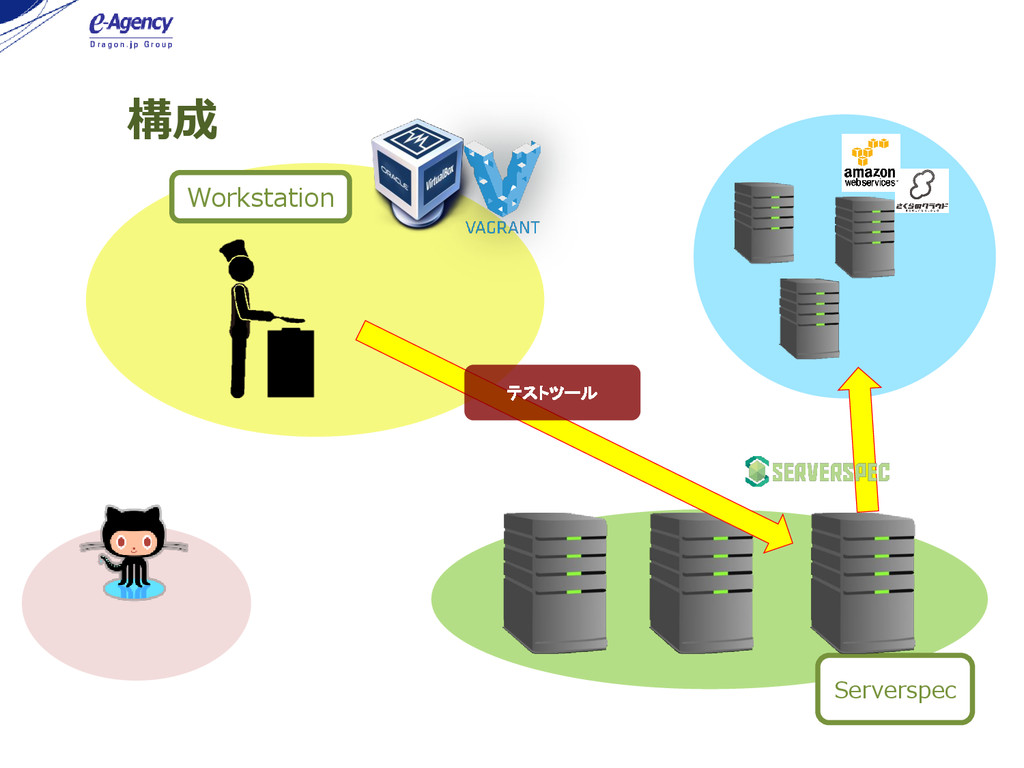
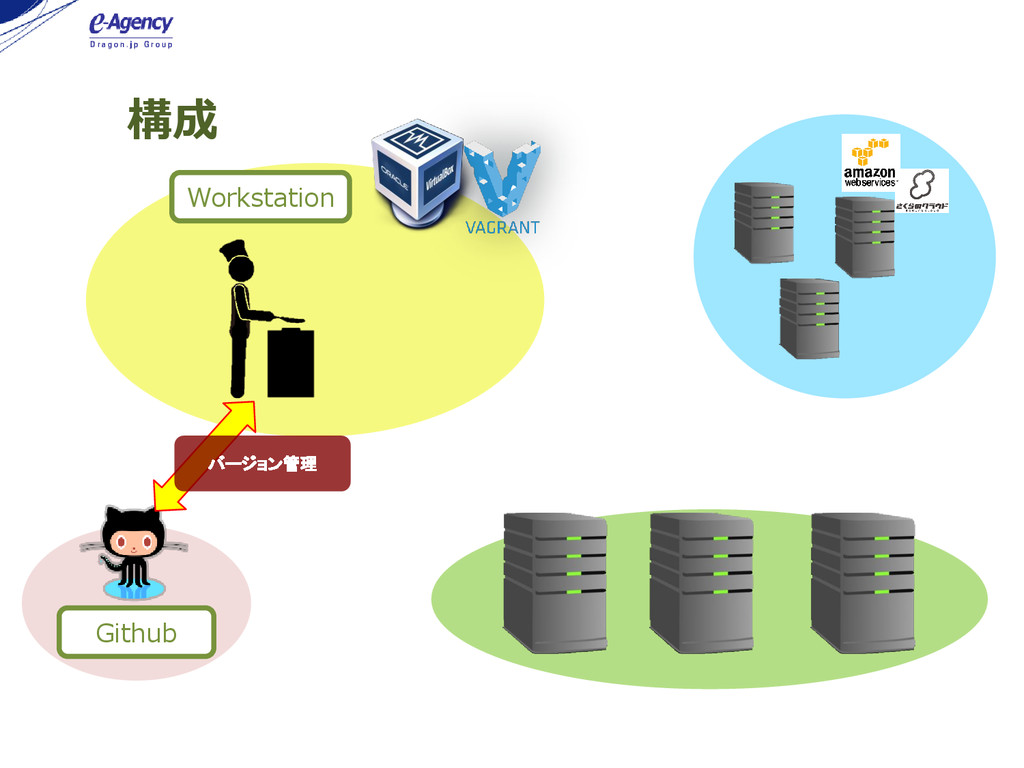
構成 Workstation
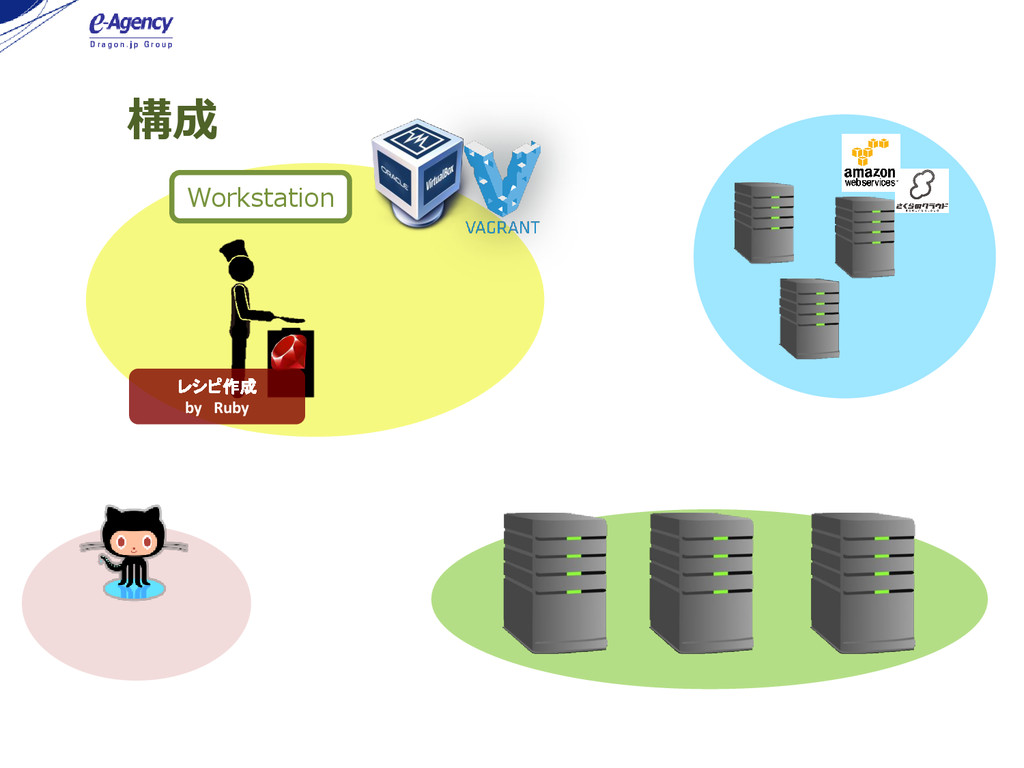
構成 Workstation レシピ作成 by Ruby
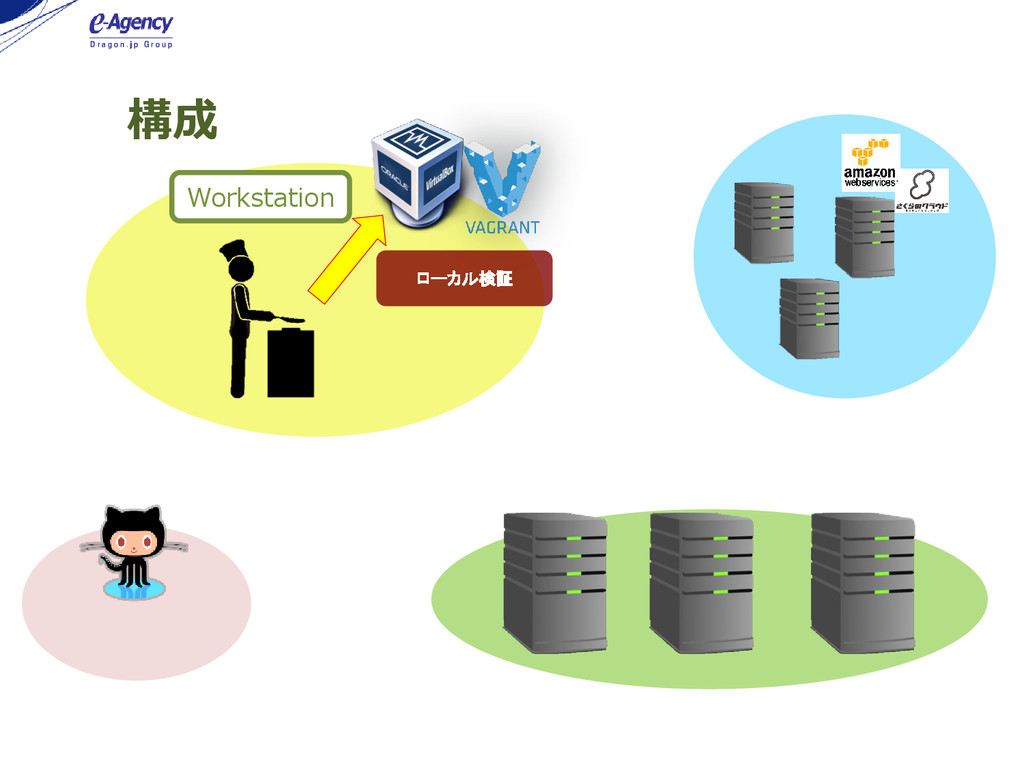
構成 Workstation ローカル検証
構成 Workstation ローカルテスト
構成 Workstation Ansible 初期構築
構成 Workstation Chef Server ノード登録 &レシピ適用
構成 Workstation Serverspec テストツール
構成 Workstation Github バージョン管理
今後の展望
今後の展望 API使用によるさくらのクラウド・AWSでのスケール アップ・スケールアウトの一括管理
今後の展望 API使用によるさくらのクラウド・AWSでのスケール アップ・スケールアウトの一括管理 LDAP等のユーザー一括管理ツールとの併用 (Ansibleの置き換えを視野にいれて)
今後の展望 API使用によるさくらのクラウド・AWSでのスケール アップ・スケールアウトの一括管理 LDAP等のユーザー一括管理ツールとの併用 (Ansibleの置き換えを視野にいれて) レシピの再利用性・共通化を進めて、社内インフ ラの見通しを良くする
今後の展望 API使用によるさくらのクラウド・AWSでのスケール アップ・スケールアウトの一括管理 LDAP等のユーザー一括管理ツールとの併用 (Ansibleの置き換えを視野にいれて) レシピの再利用性・共通化を進めて、社内インフ ラの見通しを良くする JenkinsによるレシピのGithubコミット→テスト→ サーバ構築・適用までの統合管理化
今後の展望 API使用によるさくらのクラウド・AWSでのスケール アップ・スケールアウトの一括管理 LDAP等のユーザー一括管理ツールとの併用 (Ansibleの置き換えを視野にいれて) レシピの再利用性・共通化を進めて、社内インフ ラの見通しを良くする JenkinsによるレシピのGithubコミット→テスト→ サーバ構築・適用までの統合管理化 Dockerを利用した開発環境のアプリの実行環
境管理(Immutable Infrastructure 不変なサーバ基盤 の実装)
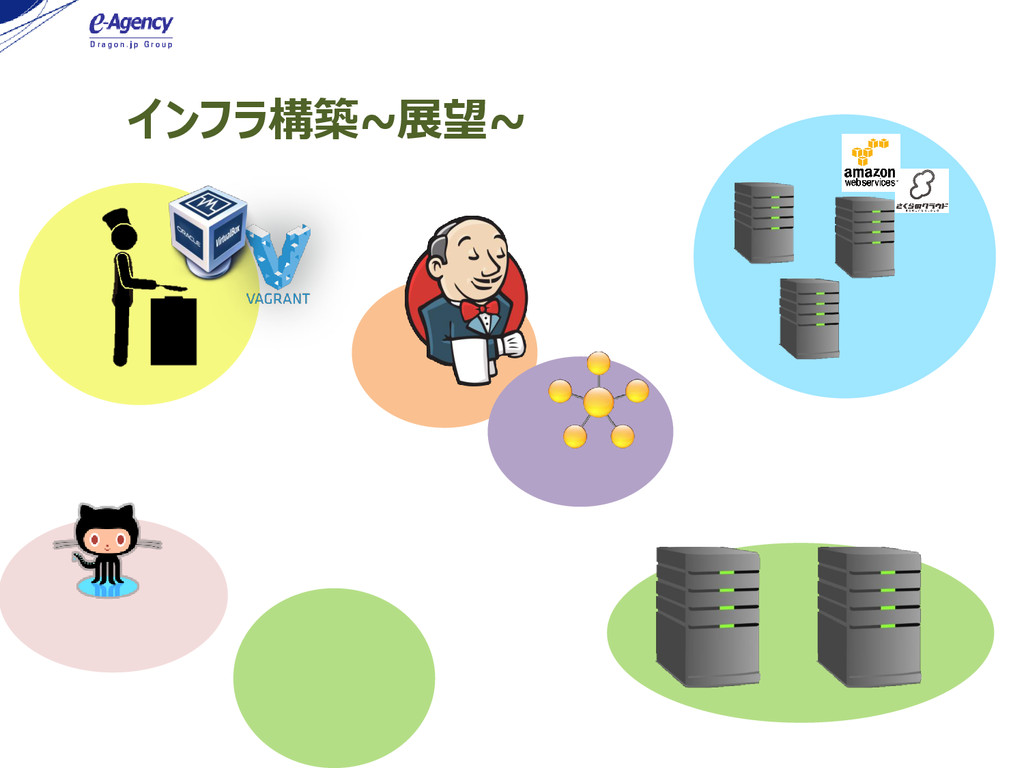
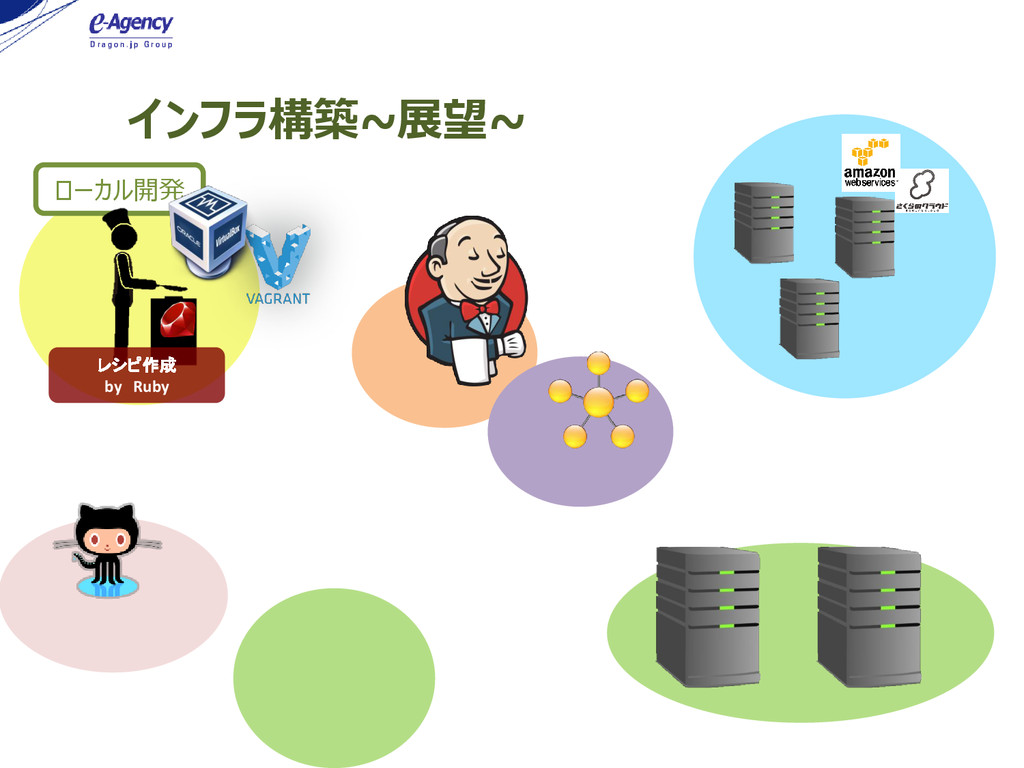
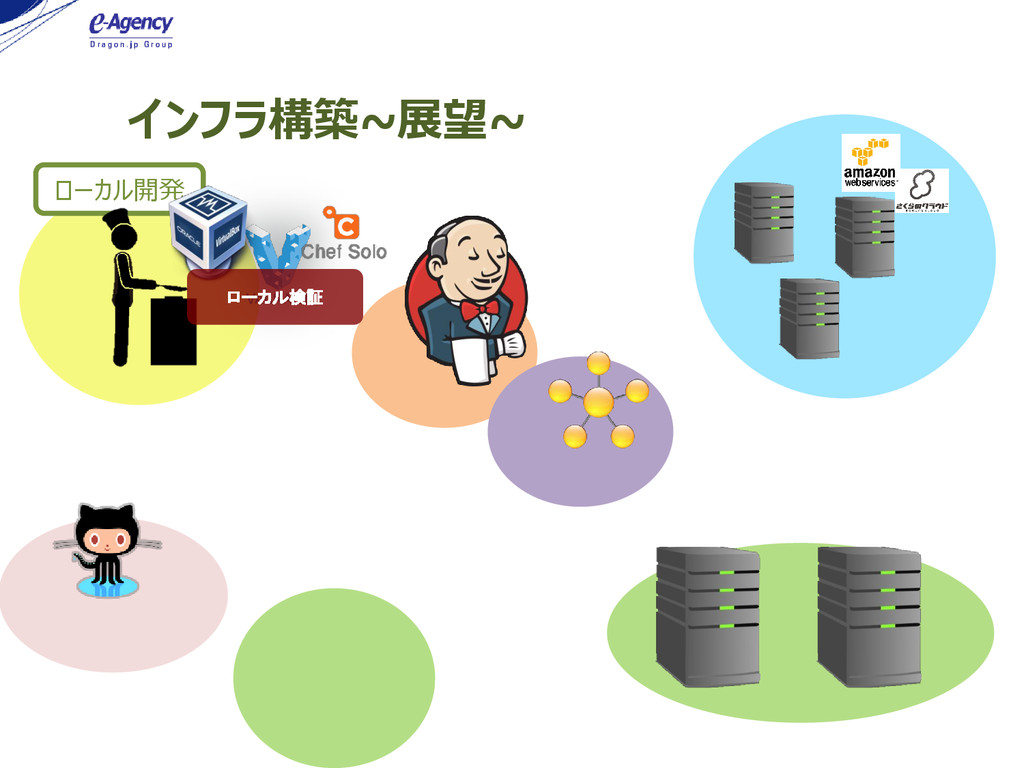
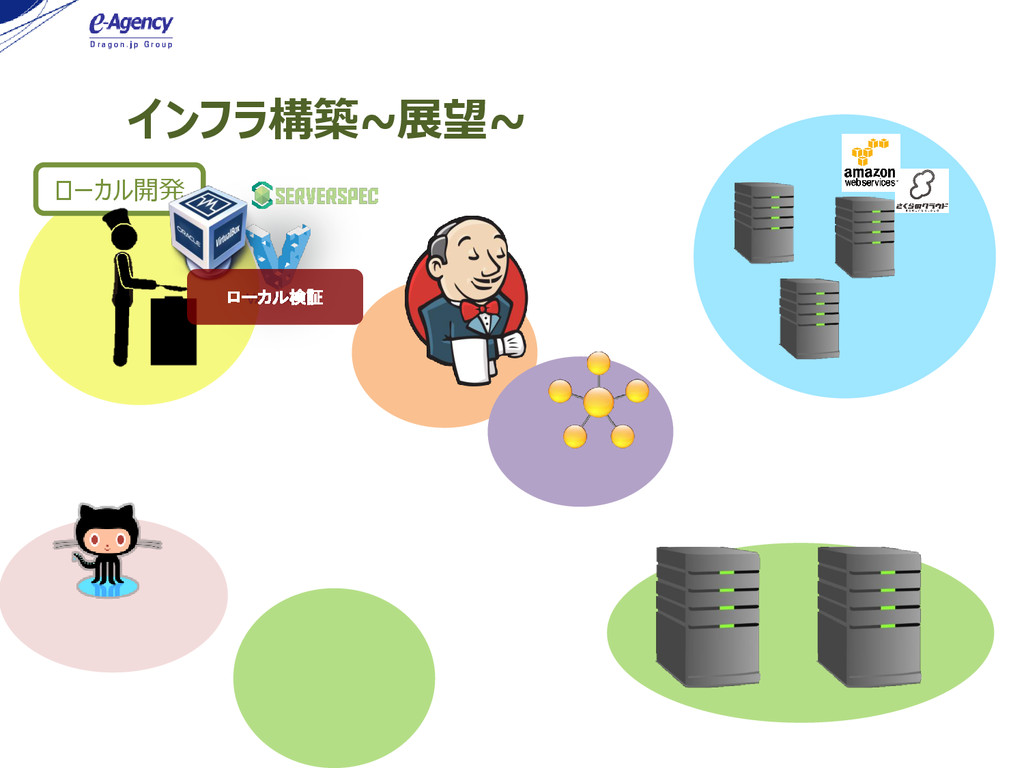
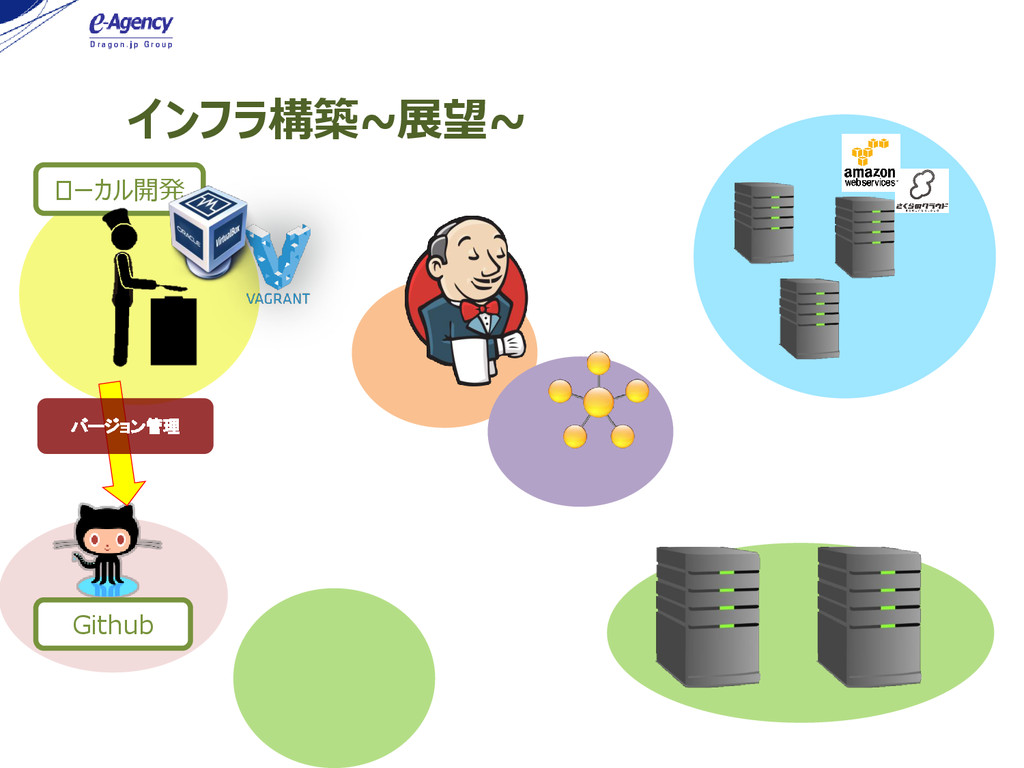
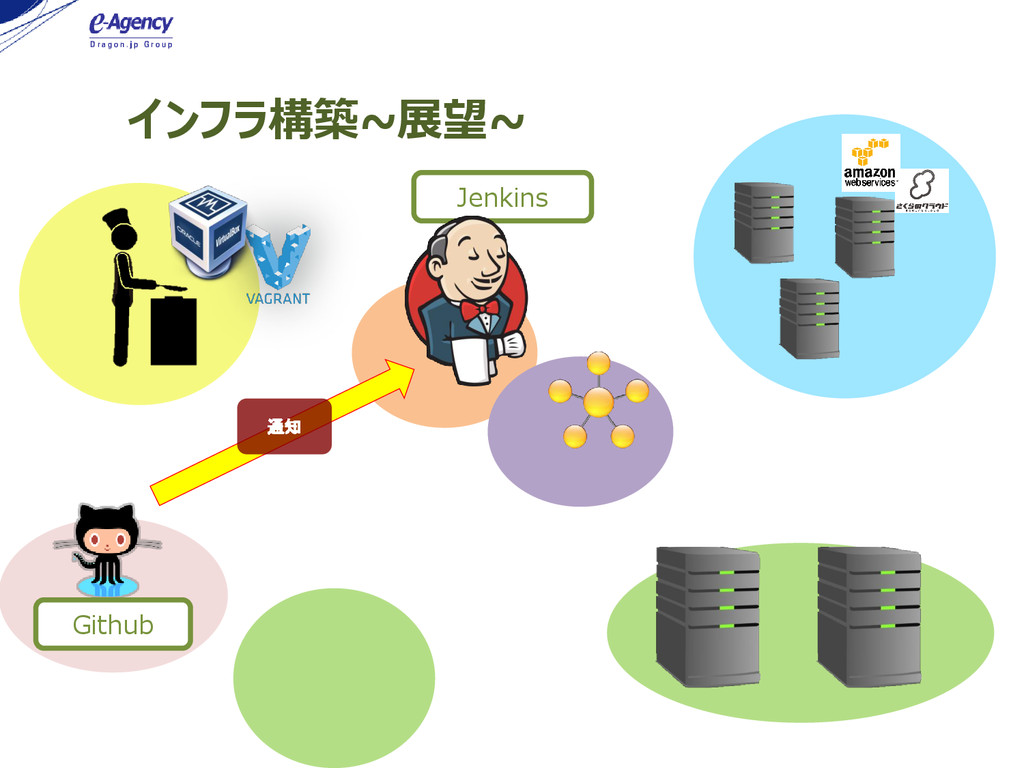
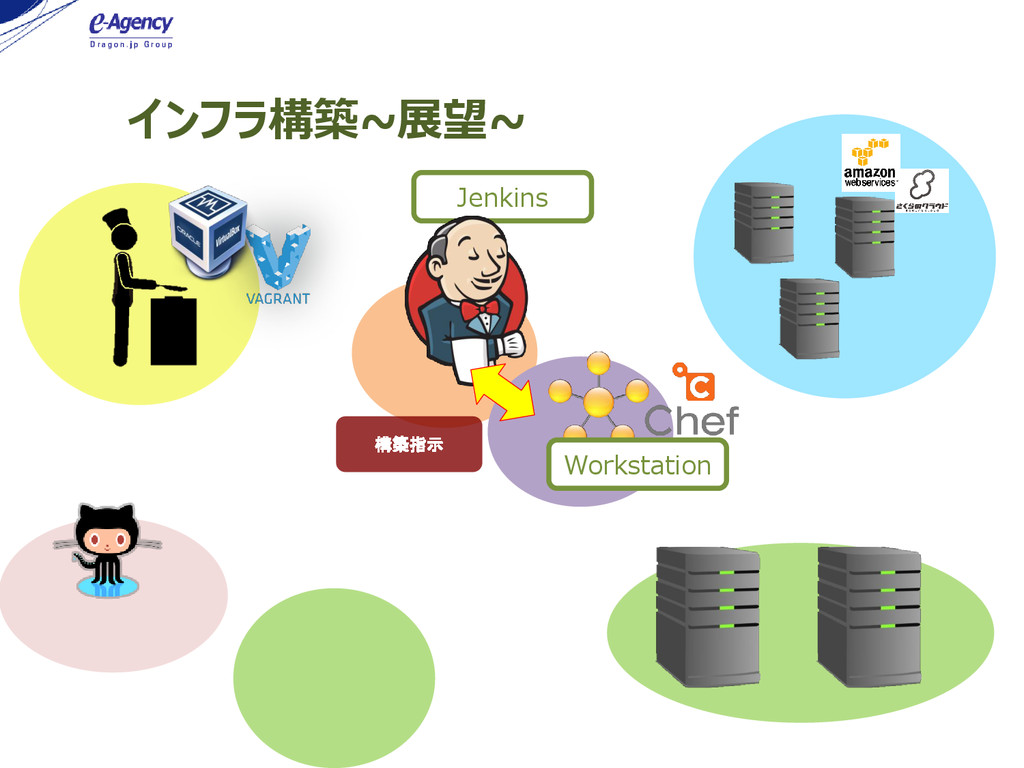
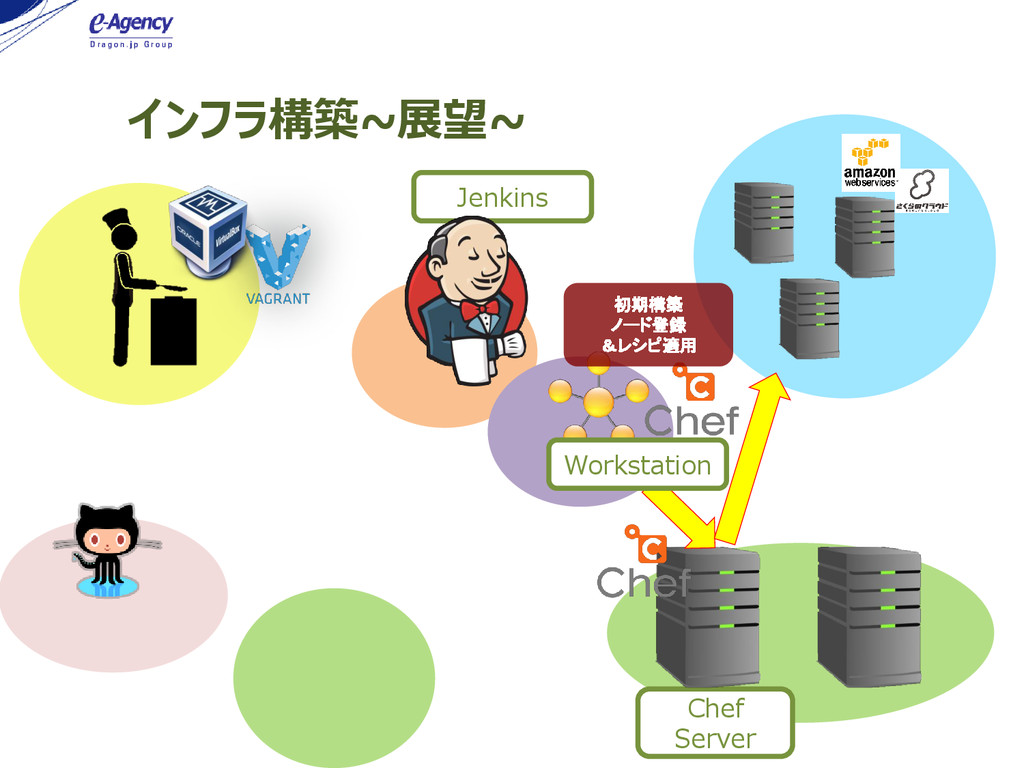
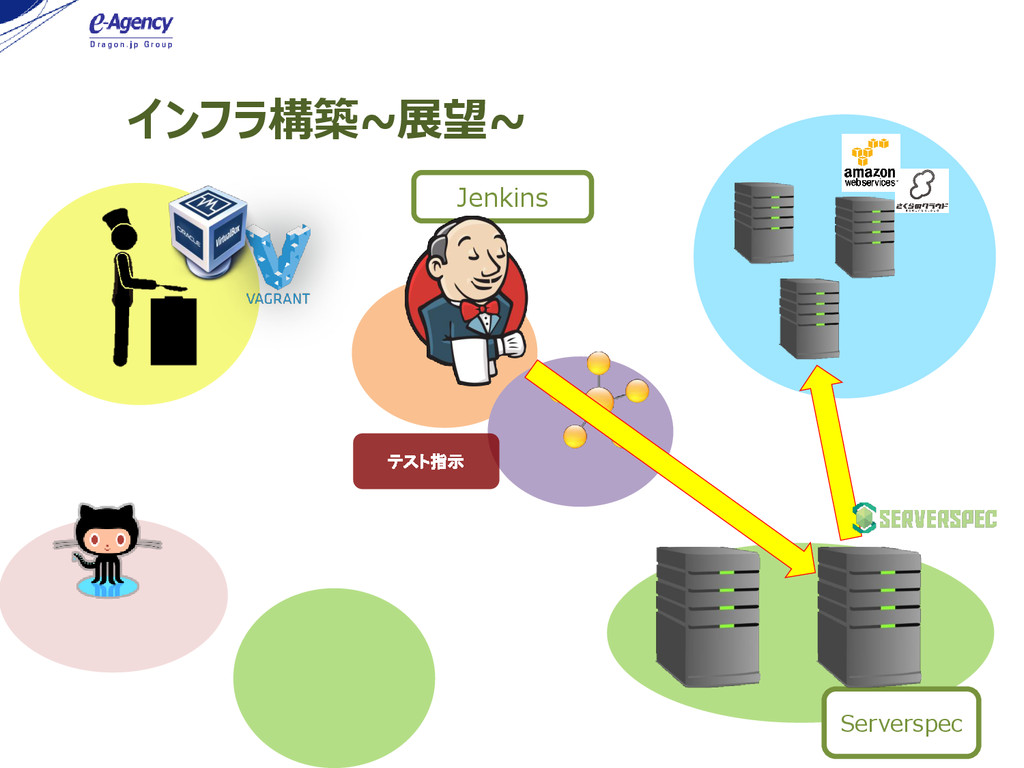
インフラ構築~展望~
ローカル開発 インフラ構築~展望~ レシピ作成 by Ruby
ローカル開発 インフラ構築~展望~ ローカル検証
ローカル開発 インフラ構築~展望~ ローカル検証
ローカル開発 インフラ構築~展望~ Github バージョン管理
インフラ構築~展望~ Github Jenkins 通知
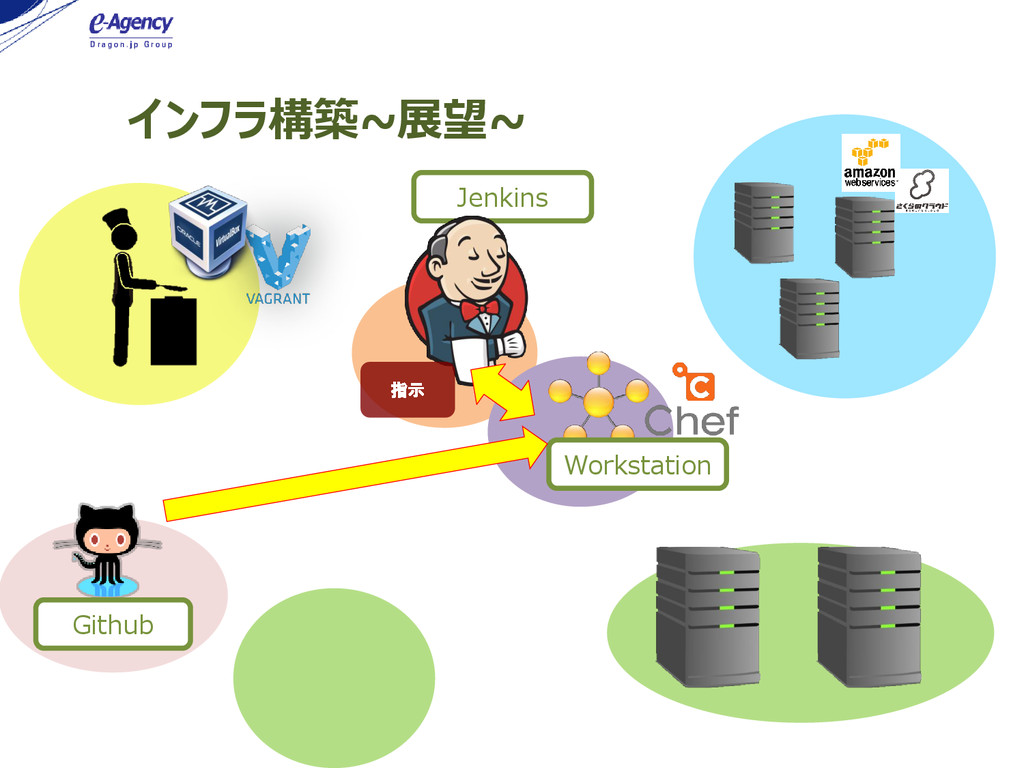
インフラ構築~展望~ Github Jenkins Workstation 指示
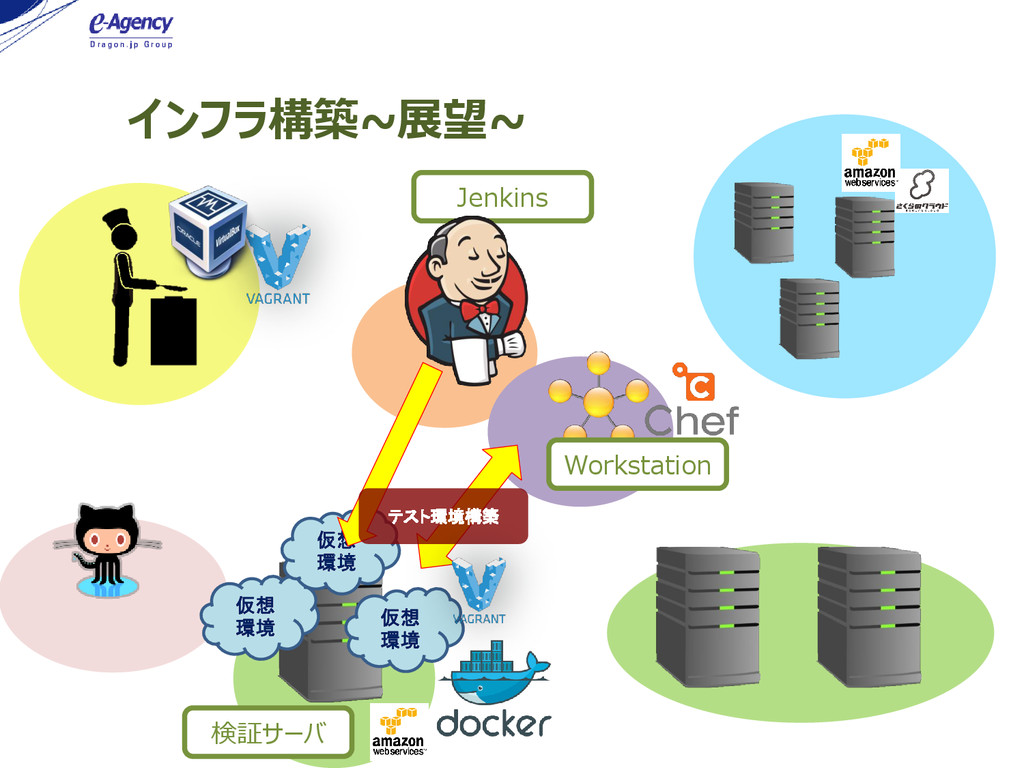
インフラ構築~展望~ Jenkins 仮想 環境 仮想 環境 仮想 環境 検証サーバ Workstation
テスト環境構築
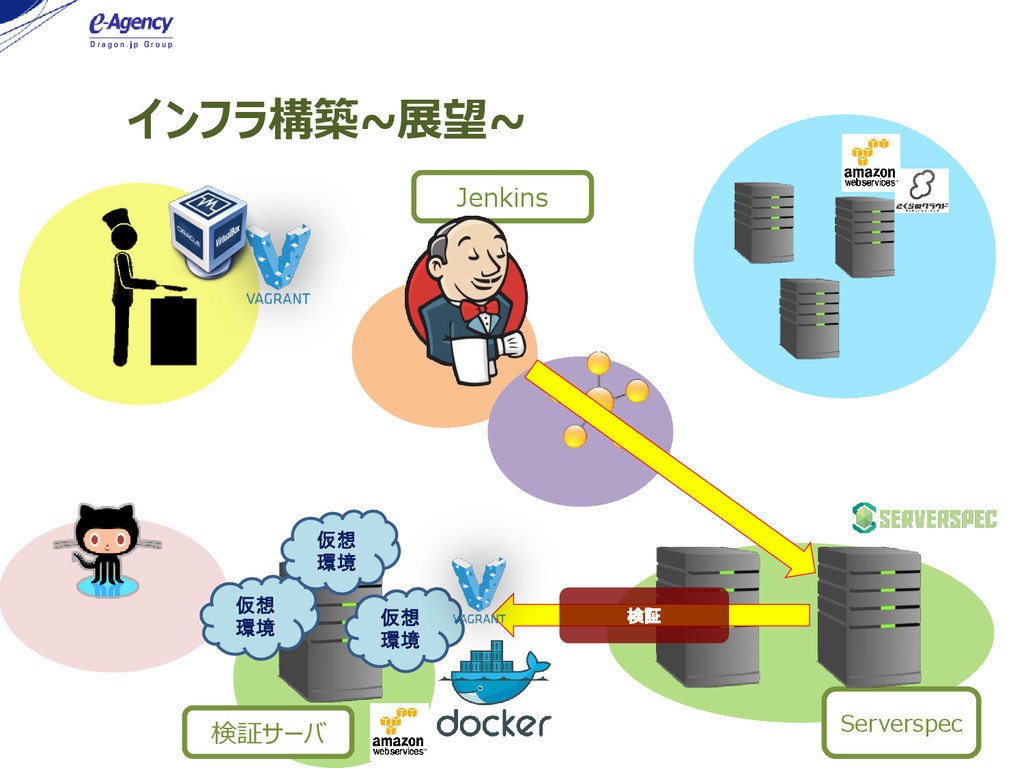
インフラ構築~展望~ Jenkins 仮想 環境 仮想 環境 仮想 環境 Serverspec 検証サーバ
検証
インフラ構築~展望~ Jenkins Workstation 構築指示
インフラ構築~展望~ Jenkins Chef Server Workstation 初期構築 ノード登録 &レシピ適用
インフラ構築~展望~ Jenkins Serverspec テスト指示
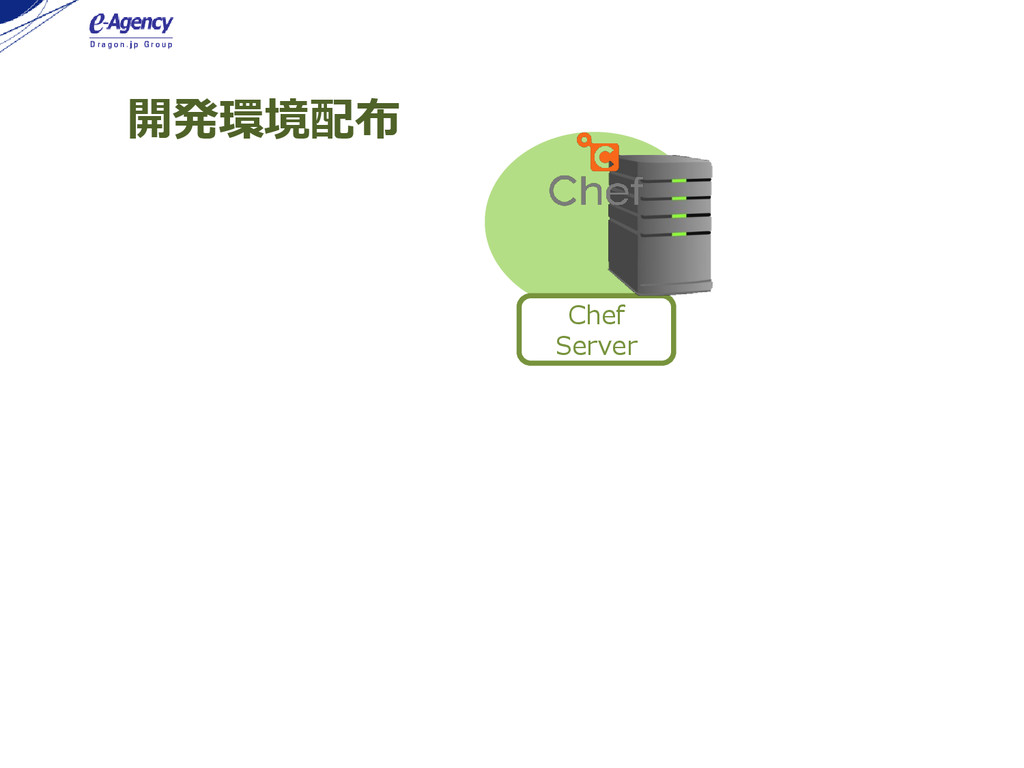
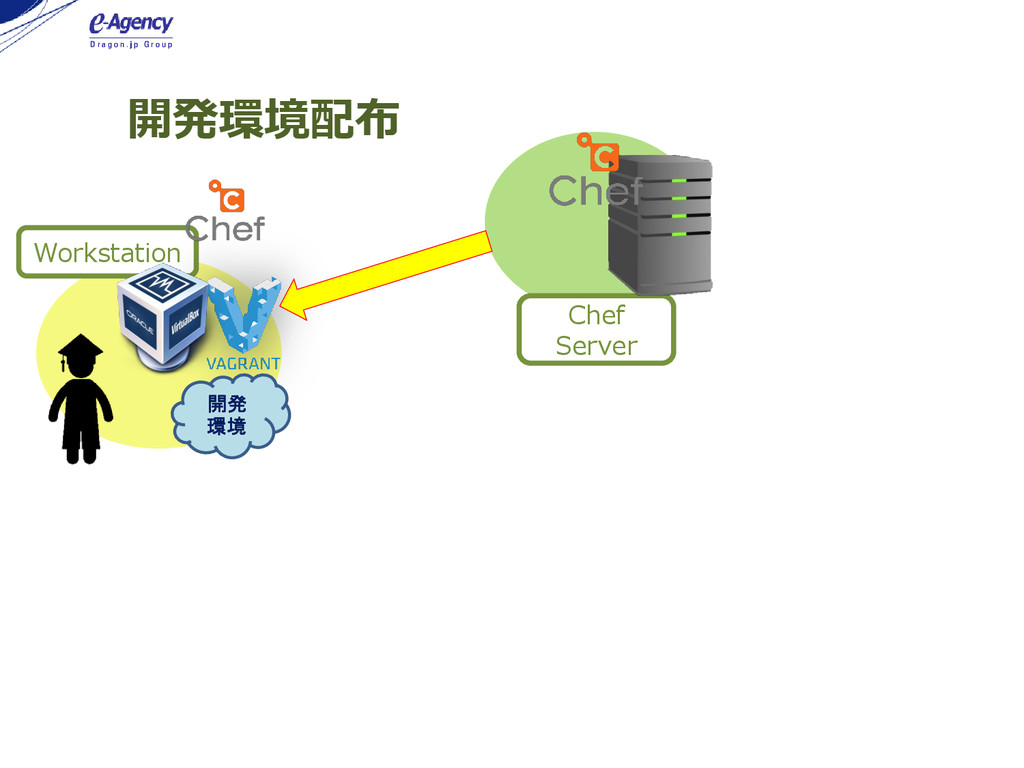
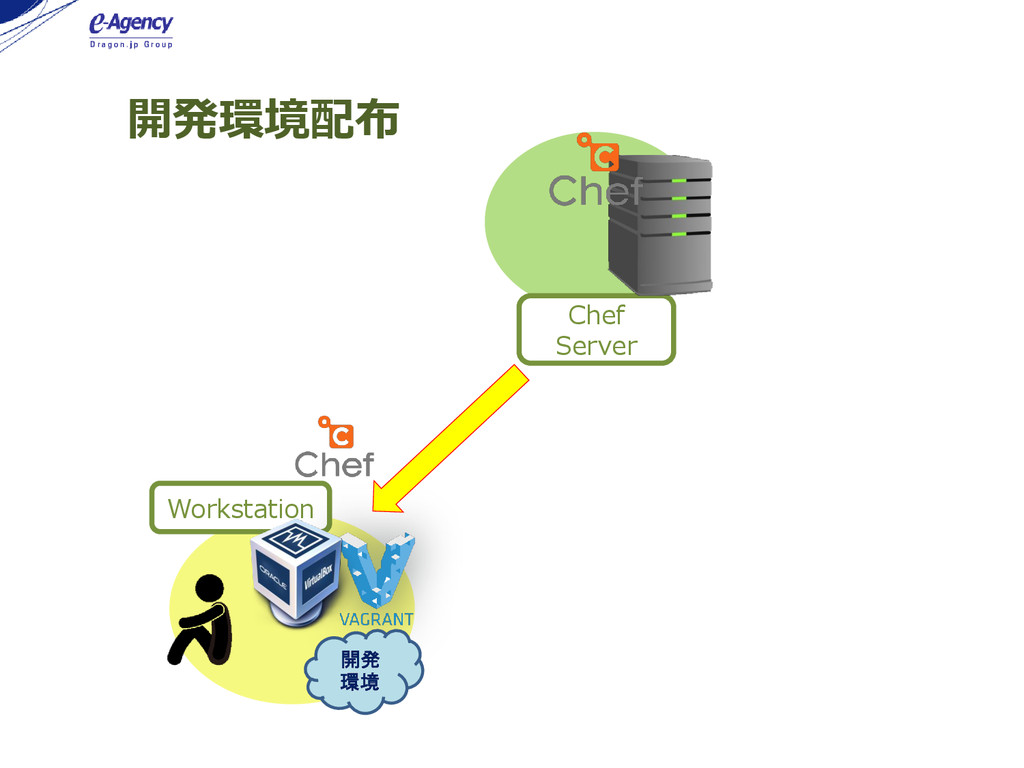
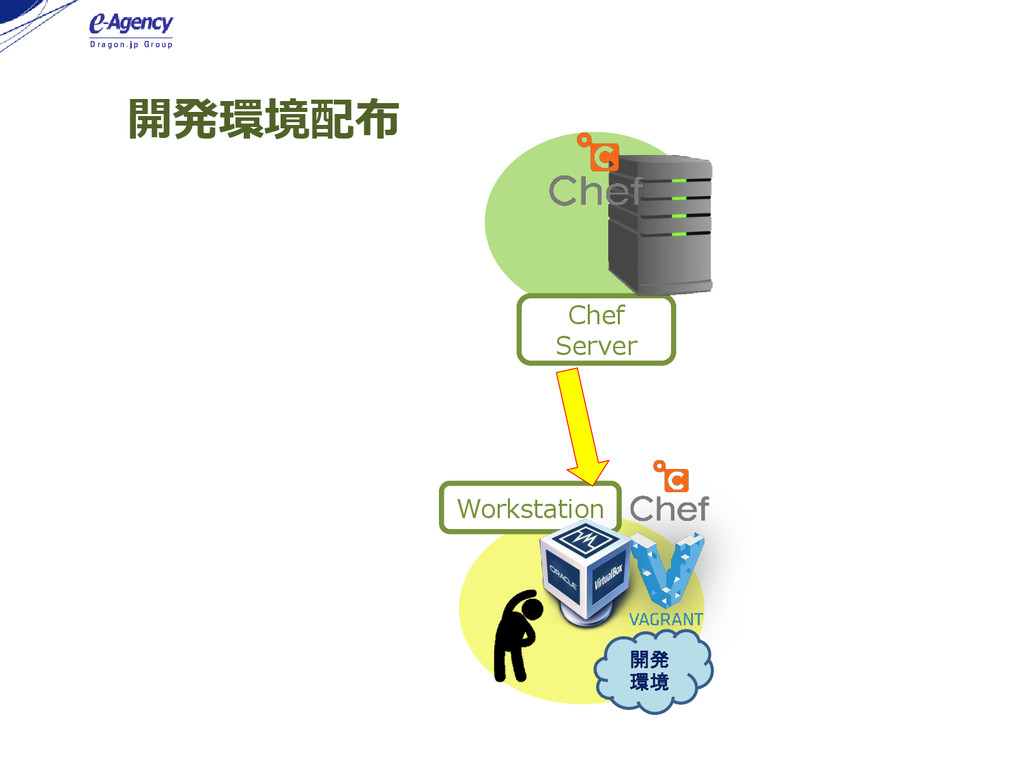
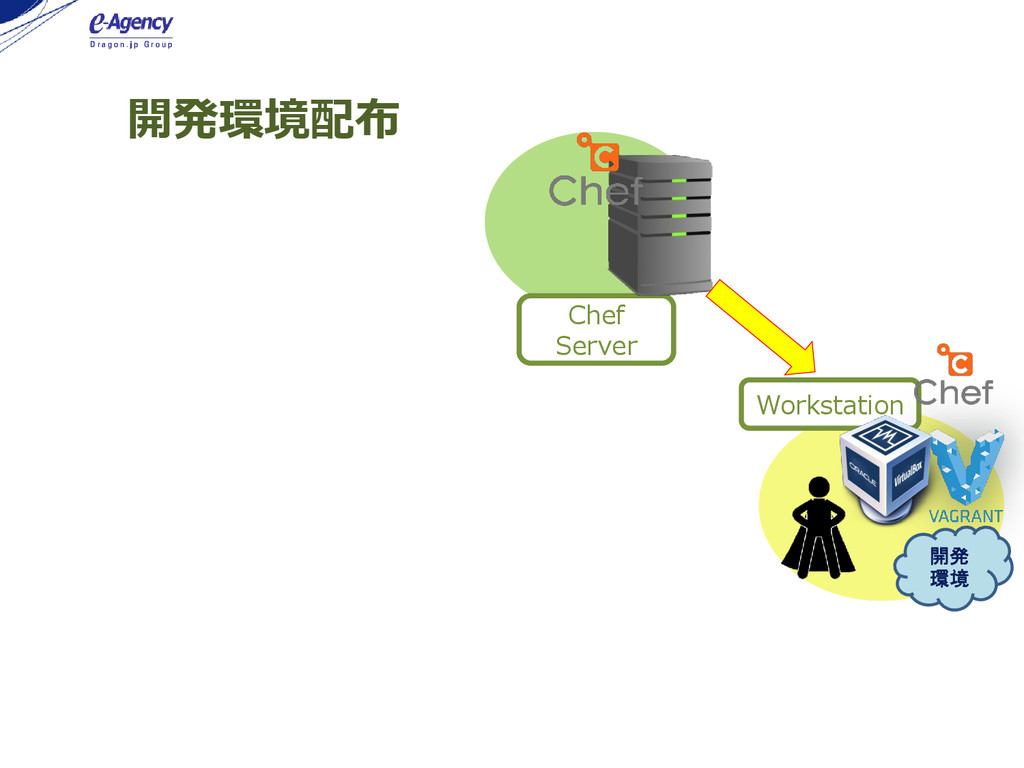
開発環境配布 Chef Server
開発環境配布 Chef Server Workstation 開発 環境
開発環境配布 Chef Server Workstation 開発 環境
開発環境配布 Chef Server Workstation 開発 環境
開発環境配布 Chef Server Workstation 開発 環境
Infrastructure as CODEがもたらすもの
Infrastructure as CODEがもたらすもの 作業手順が全部コードになる。
Infrastructure as CODEがもたらすもの 作業手順が全部コードになる。 インフラもコードレビュー。チーム全体で共有。
Infrastructure as CODEがもたらすもの 作業手順が全部コードになる。 インフラもコードレビュー。チーム全体で共有。 インフラの継続的インテグレーション。頻繫なテ スト、品質チェックによる問題の早期発見。
Infrastructure as CODEがもたらすもの 作業手順が全部コードになる。 インフラもコードレビュー。チーム全体で共有。 インフラの継続的インテグレーション。頻繫なテ スト、品質チェックによる問題の早期発見。 アプリケーション開発で行われてきたいろいろな "ワークフロー" をインフラ作業の世界にも導入
以上 https://github.com/AkimitsuHamaguchi https://github.com/croud-product https://github.com/hrix Members


 mofurune
 rkaga
 siroemk
 econanringo
 yukiny
 yasaichi
 falcon8823
 akase244
 kasacchiful
 andpad
 panda728
 o0h
 ryanjones
 caitiem20
 joshbly
 signer
 keithpitt
 iamctodd
 asonas
 techseoconnect
 soudai
 rmw
 szymonslowik
 seathinner