Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
XSS&CSRF
Search
ar7z1
November 17, 2015
140
0
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
XSS&CSRF
Внутренний курс по безопасности для разработчиков
ar7z1
November 17, 2015
Transcript
45 slides
XSS CSRF
[email protected]
TOOLS
http://bit.ly/ 1tMrggU
http://bit.ly/ 1jKA1UJ
XSS
Reflected
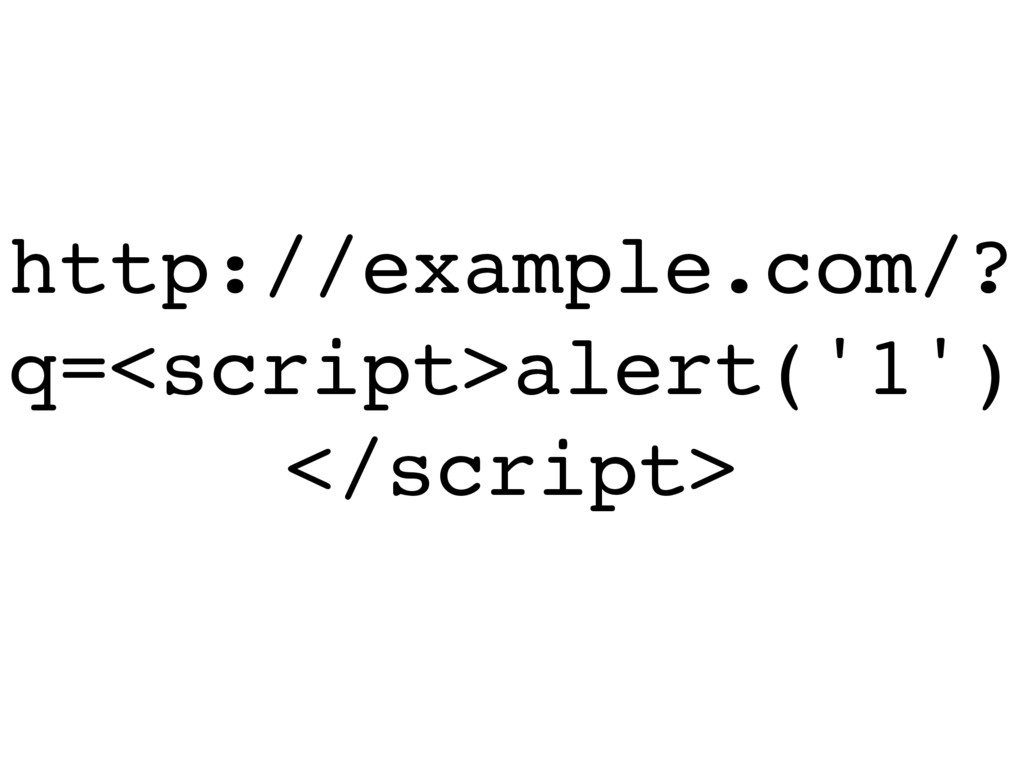
http://example.com/? q=<script>alert('1') </script>
Stored
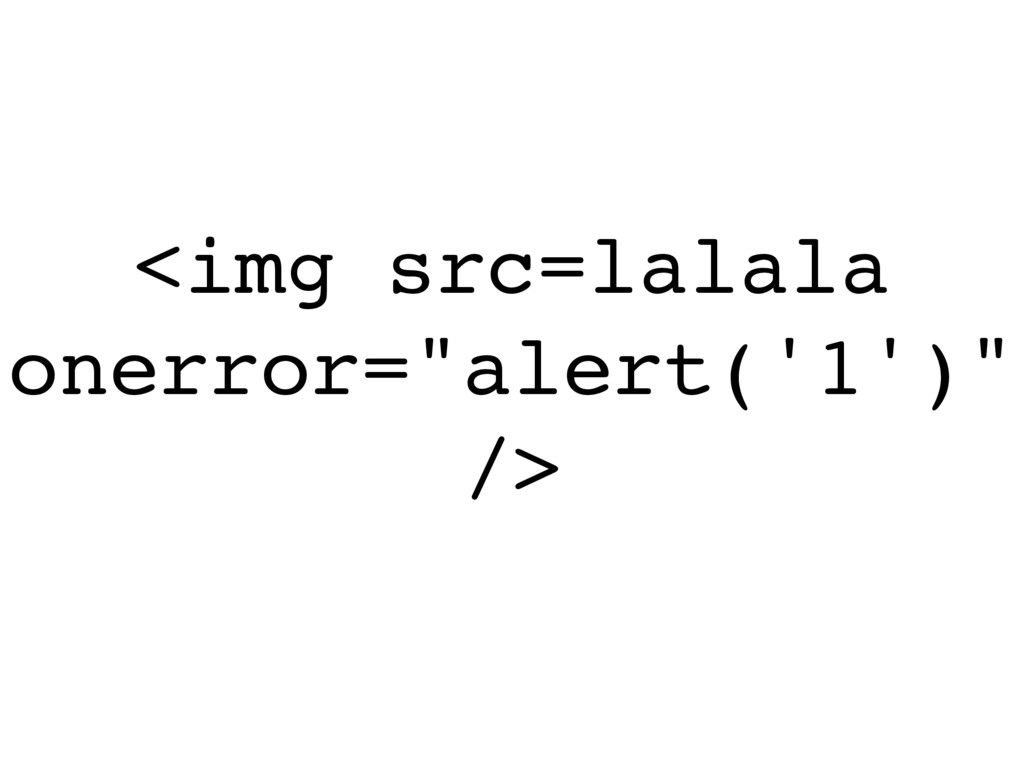
<img src=lalala onerror="alert('1')" />
DOM-based
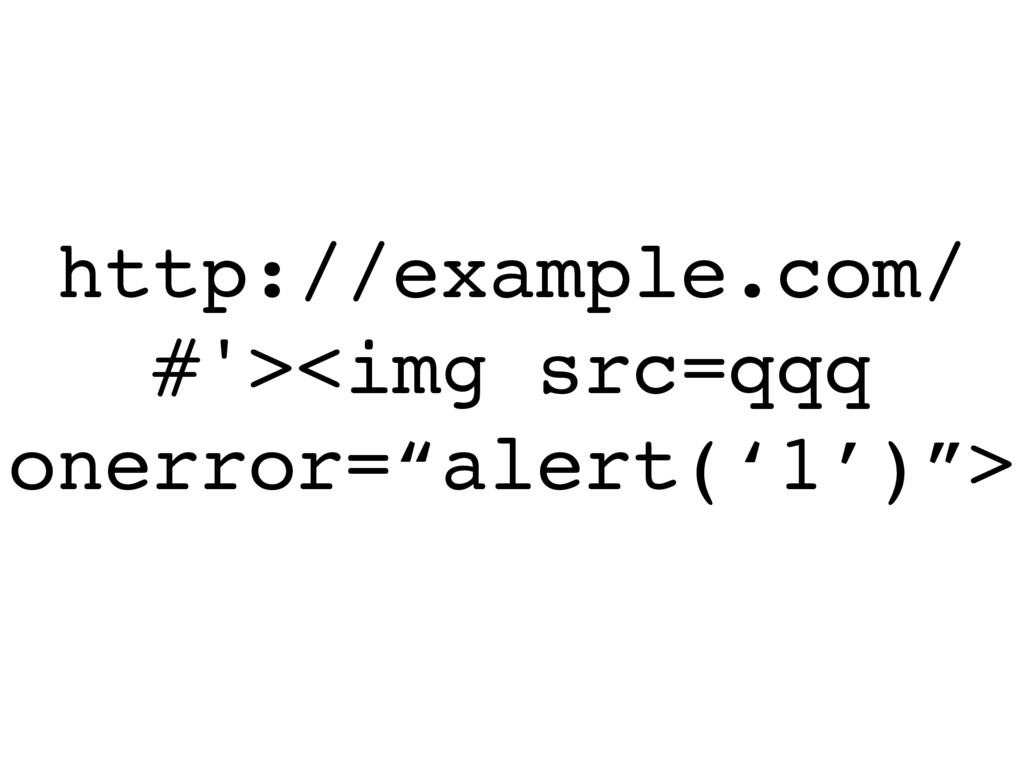
http://example.com/ #'><img src=qqq onerror=“alert(‘1’)”>
https://xss- game.appspot .com/
None
None
jsfuck.com
HtmlEncode
innerHTML document.write eval @Html.Raw
X-XSS-Protection
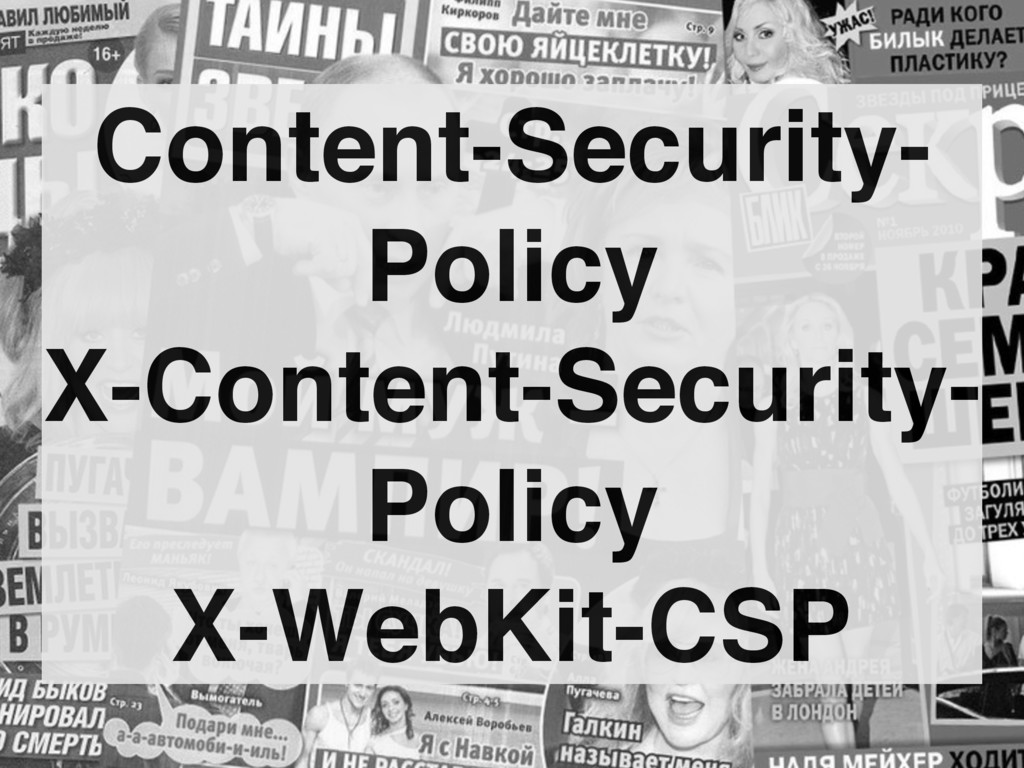
Content-Security- Policy X-Content-Security- Policy X-WebKit-CSP
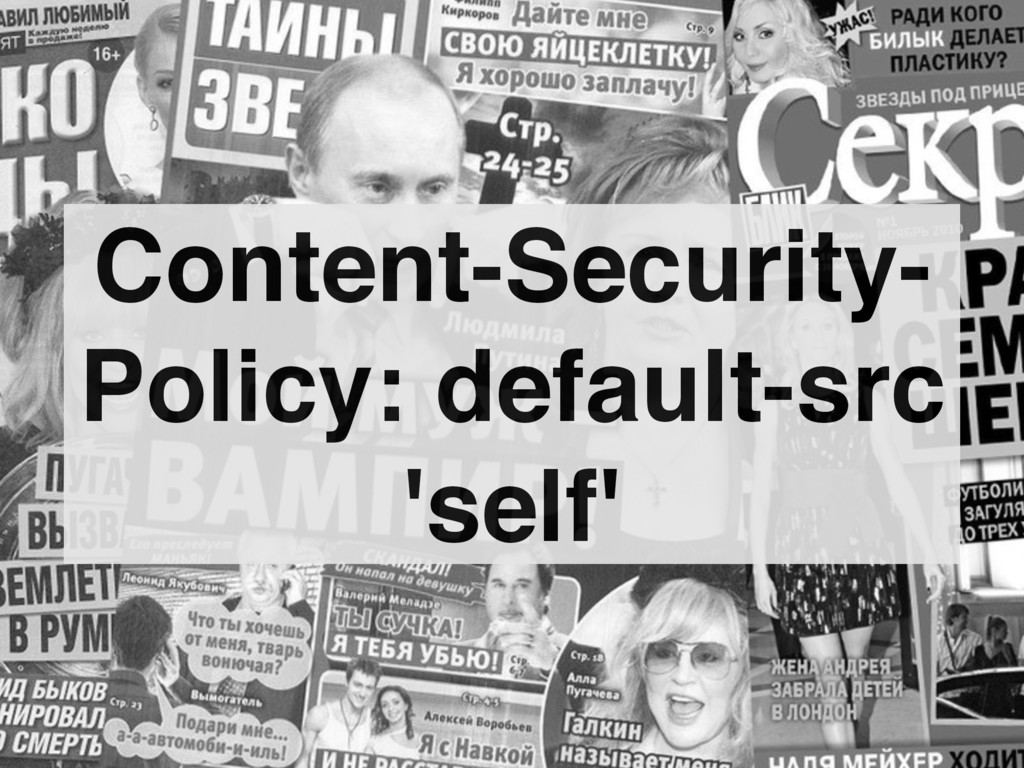
Content-Security- Policy: default-src 'self'
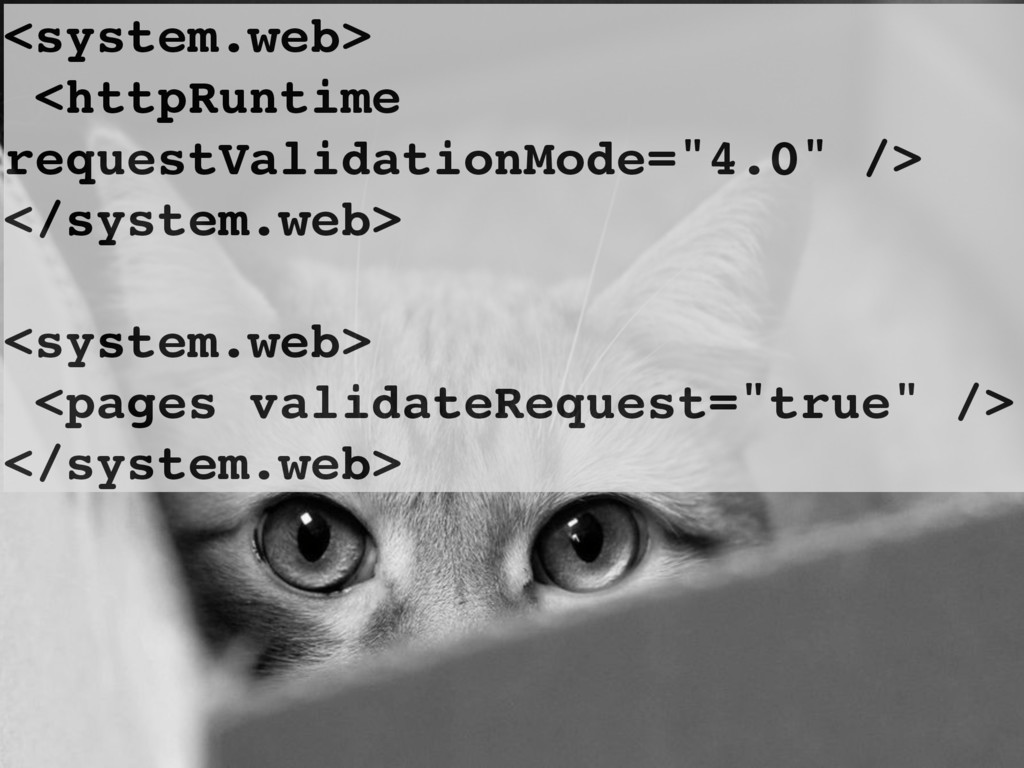
<system.web> <httpRuntime requestValidationMode="4.0" /> </system.web> <system.web> <pages validateRequest="true" /> </system.web>
CSRF
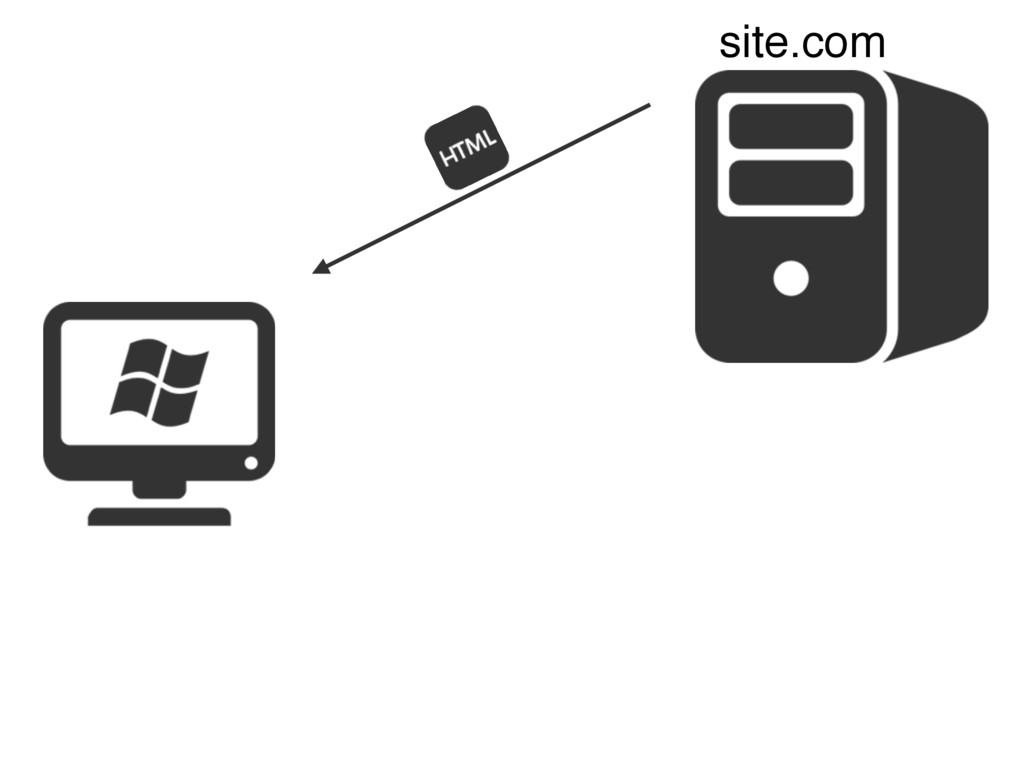
site.com
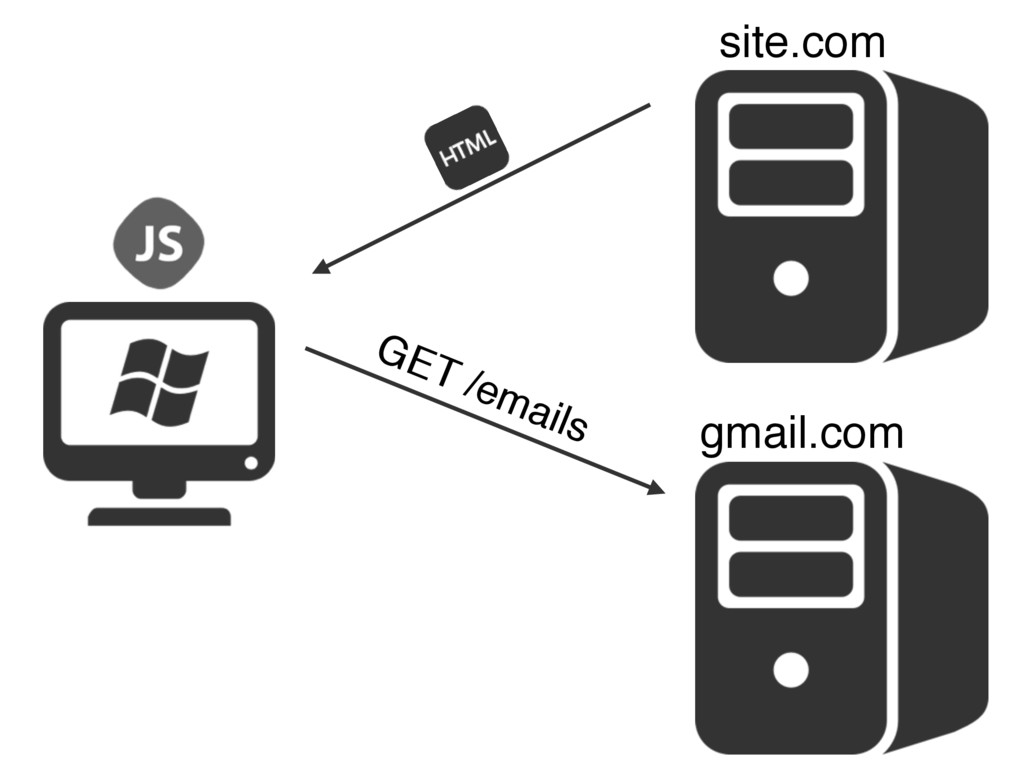
site.com GET /emails gmail.com
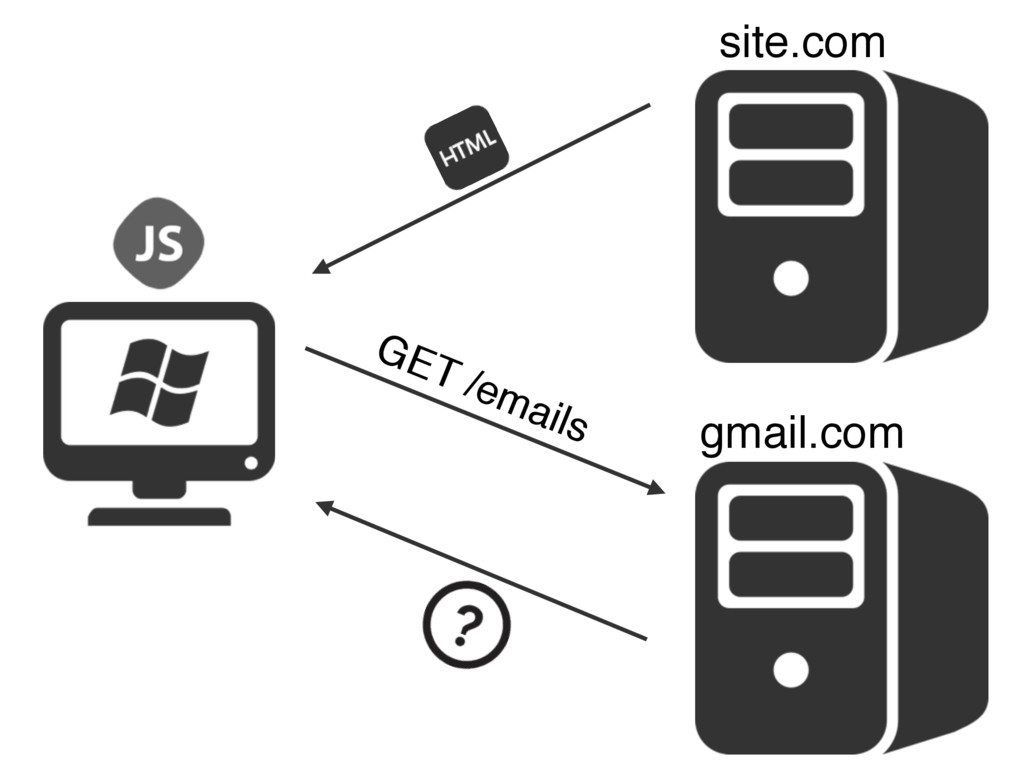
site.com GET /emails gmail.com
Same Origin Policy
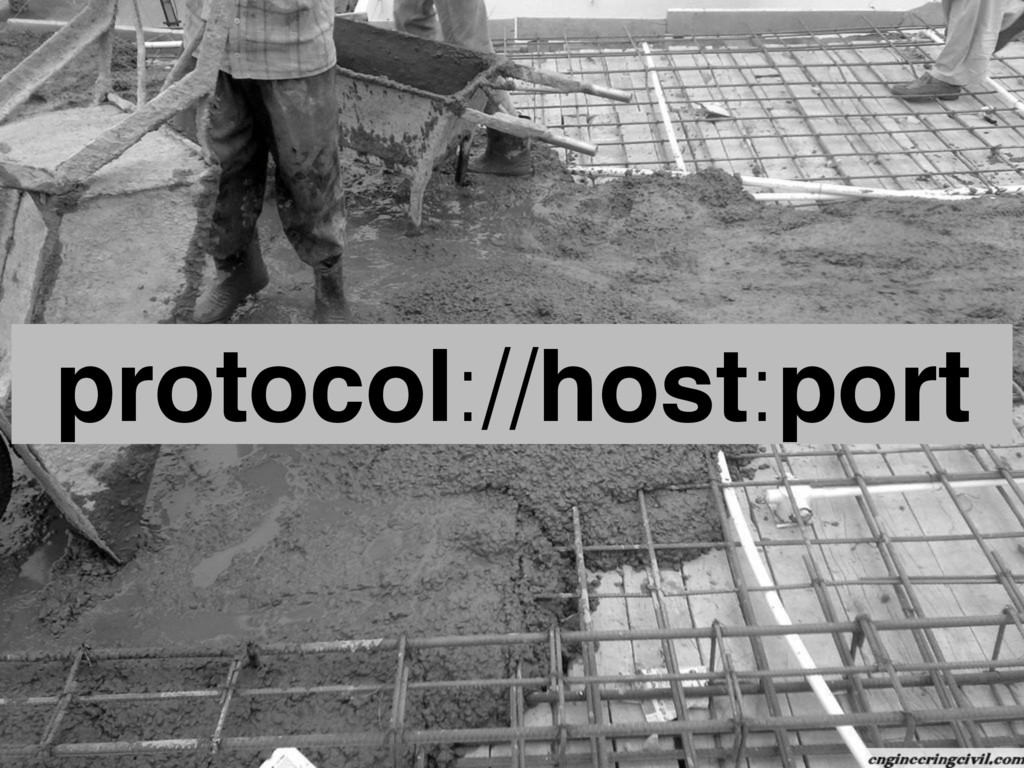
protocol://host:port
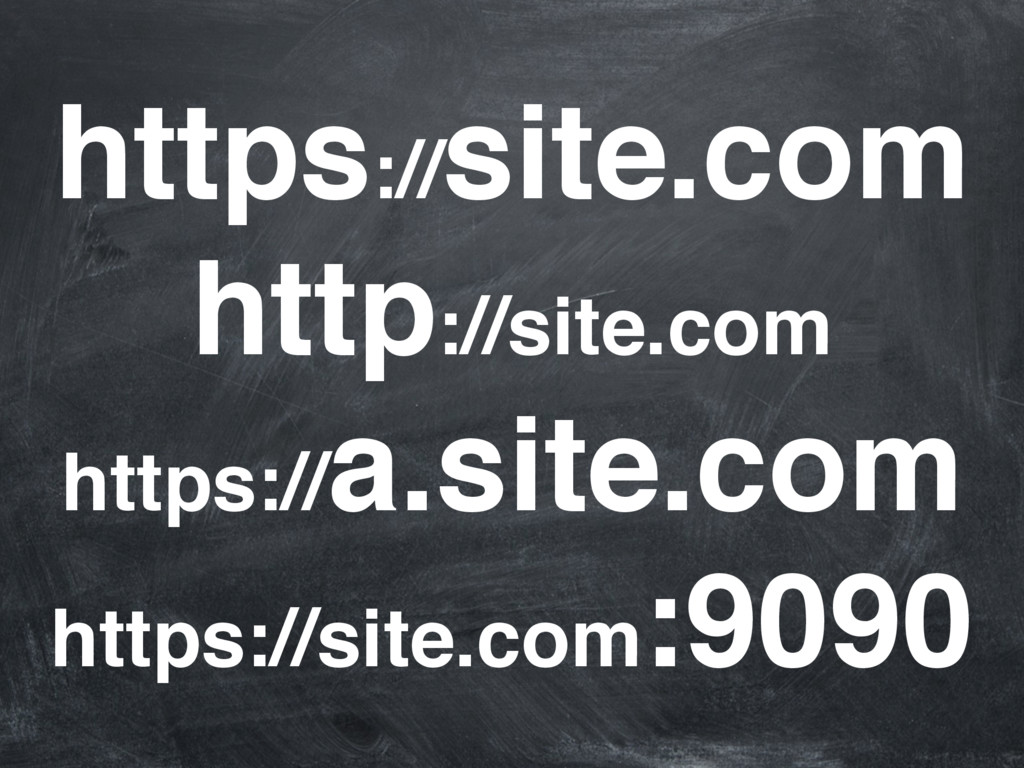
https://site.com http://site.com https://a.site.com https://site.com:9090
None
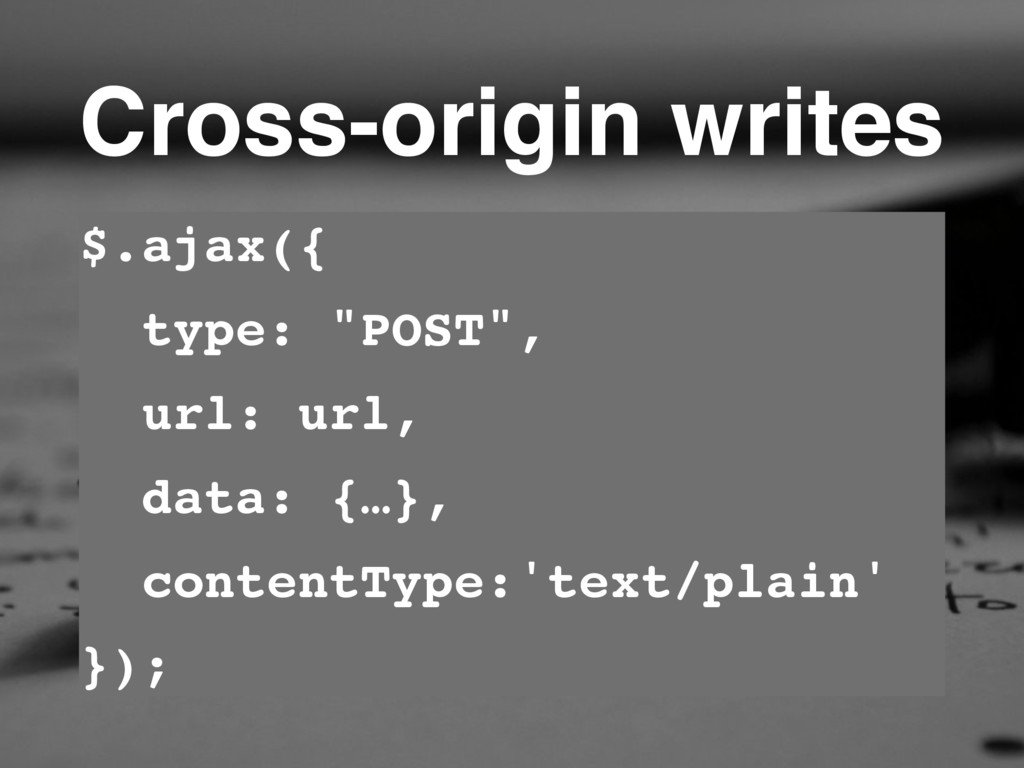
Cross-origin writes $.ajax({ type: "POST", url: url, data: {…}, contentType:'text/plain'
});
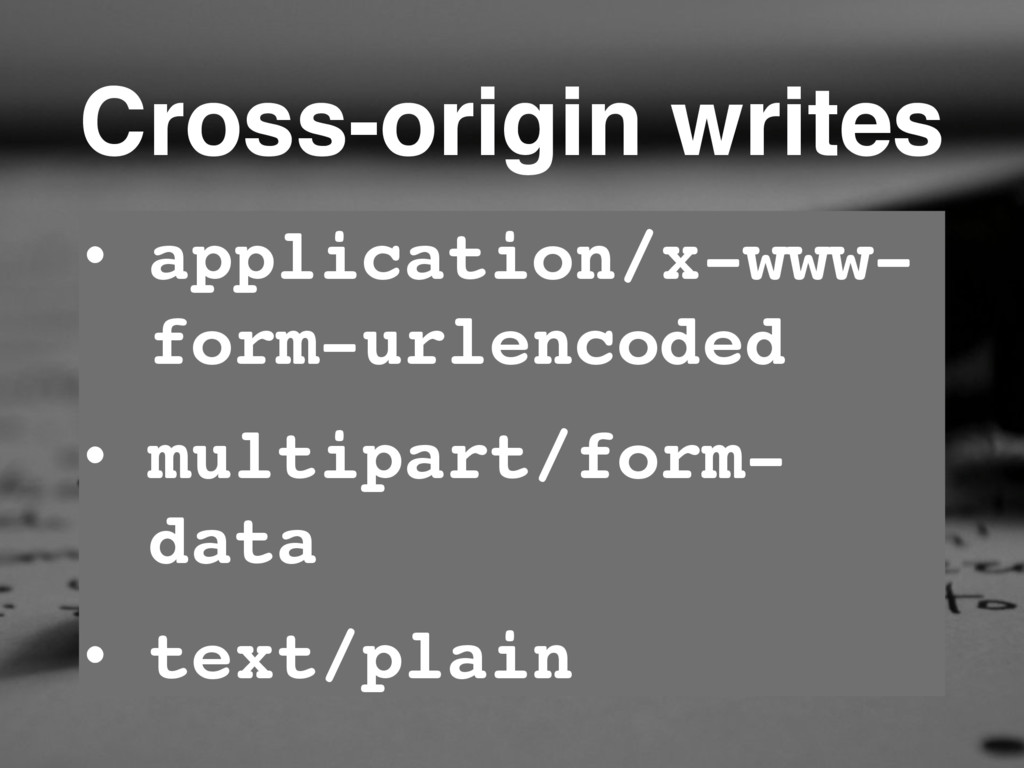
Cross-origin writes • application/x-www- form-urlencoded • multipart/form- data • text/plain
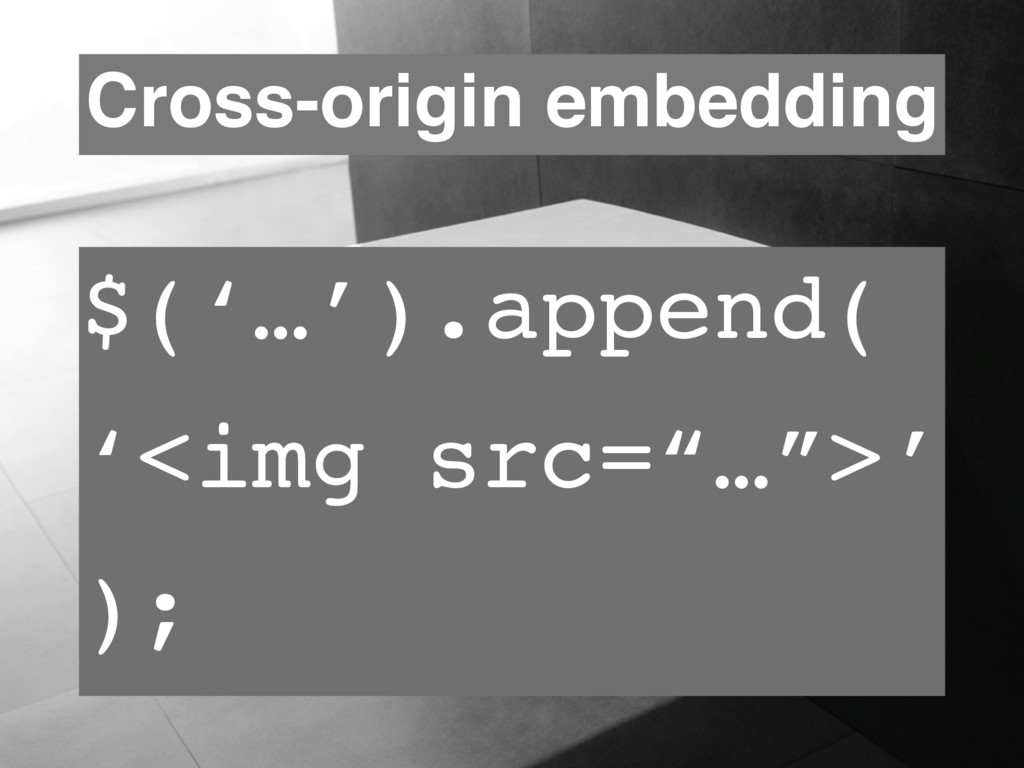
Cross-origin embedding $(‘…’).append( ‘<img src=“…”>’ );
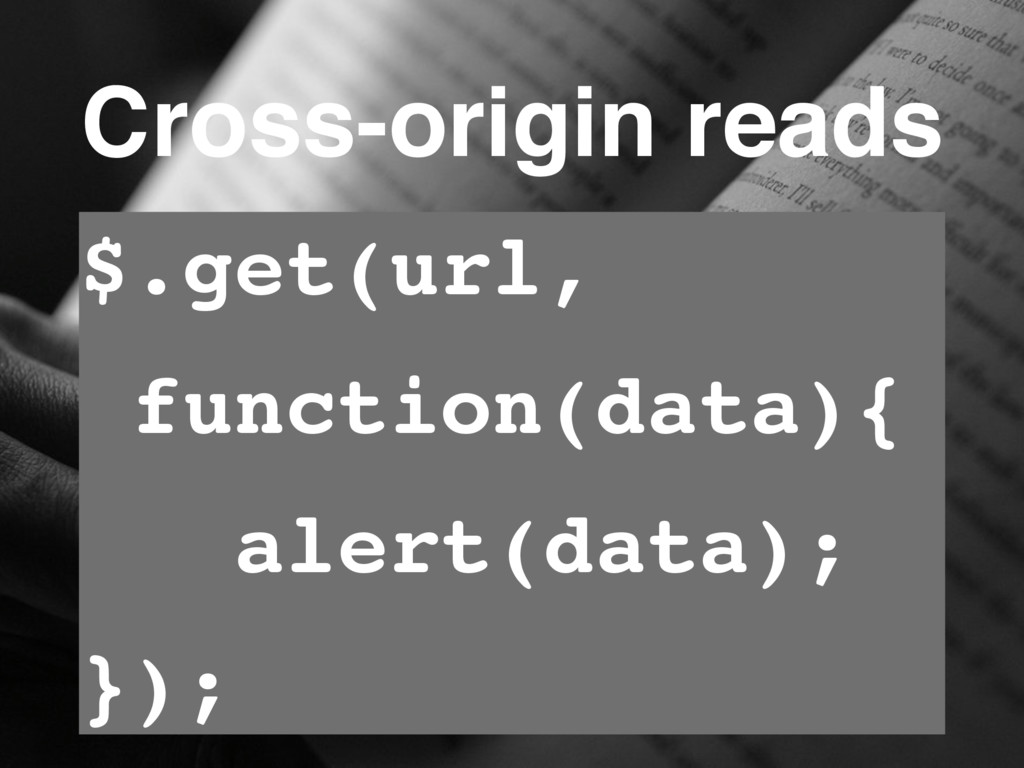
Cross-origin reads $.get(url, function(data){ alert(data); });
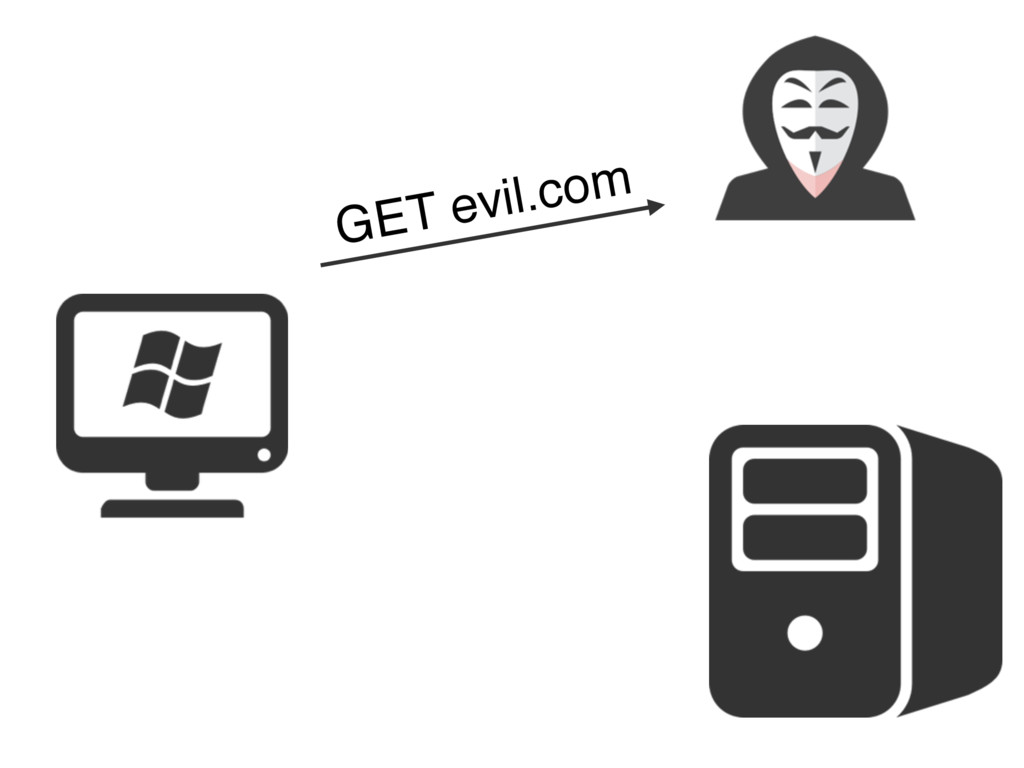
GET evil.com
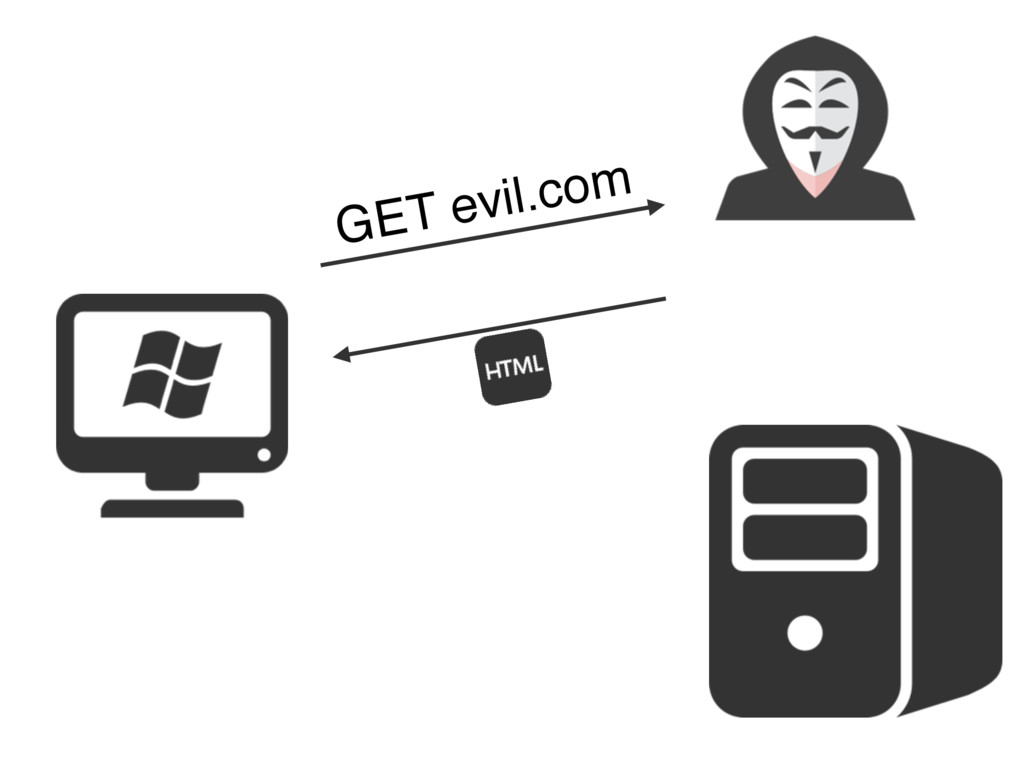
GET evil.com
<form method=“POST” action=“https://…/ SaveEmail”> <input type=“hidden” name=“email” value=“
[email protected]
” /> </form>
<form method=“POST” action=“https://…/SaveEmail”> <input type=“hidden” name=“email” value=“
[email protected]
” /> </form>
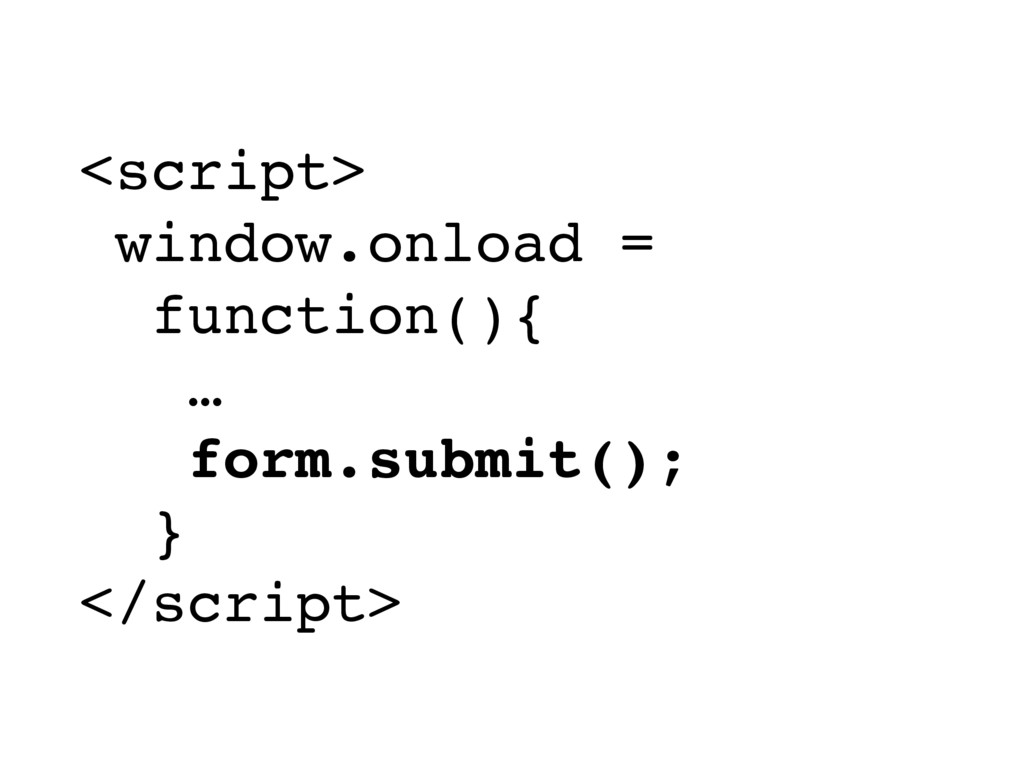
<script> window.onload = function(){ … form.submit(); } </script>
POST /SaveEmail
[email protected]
GET evil.com
candy- csrf.apphb.com
None
@troyhunt
webgoat. github.io
https://ctftime.org
@ar7z1
[email protected]
More Decks by ar7z1
See All by ar7z1
Шпора.Безопасность
ar7z1
1
81
XSS & CSRF 2.0
ar7z1
0
120
HappyDev 2015
ar7z1
0
110
Featured
See All Featured
The browser strikes back
jonoalderson
0
2k
The Anti-SEO Checklist Checklist. Pubcon Cyber Week
ryanjones
0
310
Noah Learner - AI + Me: how we built a GSC Bulk Export data pipeline
techseoconnect
PRO
0
500
Art, The Web, and Tiny UX
lynnandtonic
304
22k
Scaling GitHub
holman
464
140k
Statistics for Hackers
jakevdp
799
230k
技術選定の審美眼(2025年版) / Understanding the Spiral of Technologies 2025 edition
twada
PRO
121
130k
Lightning talk: Run Django tests with GitHub Actions
sabderemane
0
330
The Mindset for Success: Future Career Progression
greggifford
PRO
0
570
Winning Ecommerce Organic Search in an AI Era - #searchnstuff2025
aleyda
2
2.2k
The Hidden Cost of Media on the Web [PixelPalooza 2025]
tammyeverts
2
580
Ethics towards AI in product and experience design
skipperchong
2
470


 ar7z1
 jonoalderson
 ryanjones
 techseoconnect
 lynnandtonic
 holman
 jakevdp
 twada
 sabderemane
 greggifford
 aleyda
 tammyeverts
 skipperchong