Upgrade to Pro — share decks privately, control downloads, hide ads and more …

Getting_OAuth_Into_Your_Dev_Toolbox.pdf

 Getting_OAuth_Into_Your_Dev_Toolbox.pdf

Avatar for Brett Berliner

Brett Berliner

May 31, 2017

More Decks by Brett Berliner

Other Decks in Technology

Transcript

  1. OAuth Issues • Too permissive • Endpoint discovery impossible •

    Authentication is NOT the “Auth” • Security is an afterthought
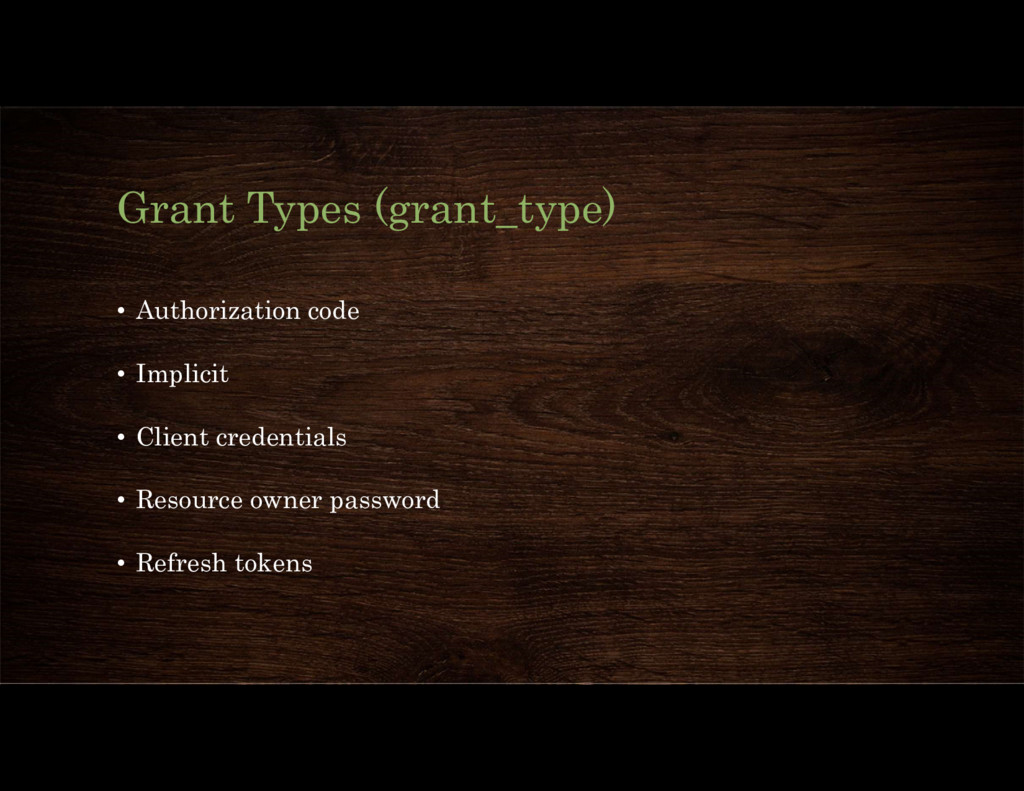
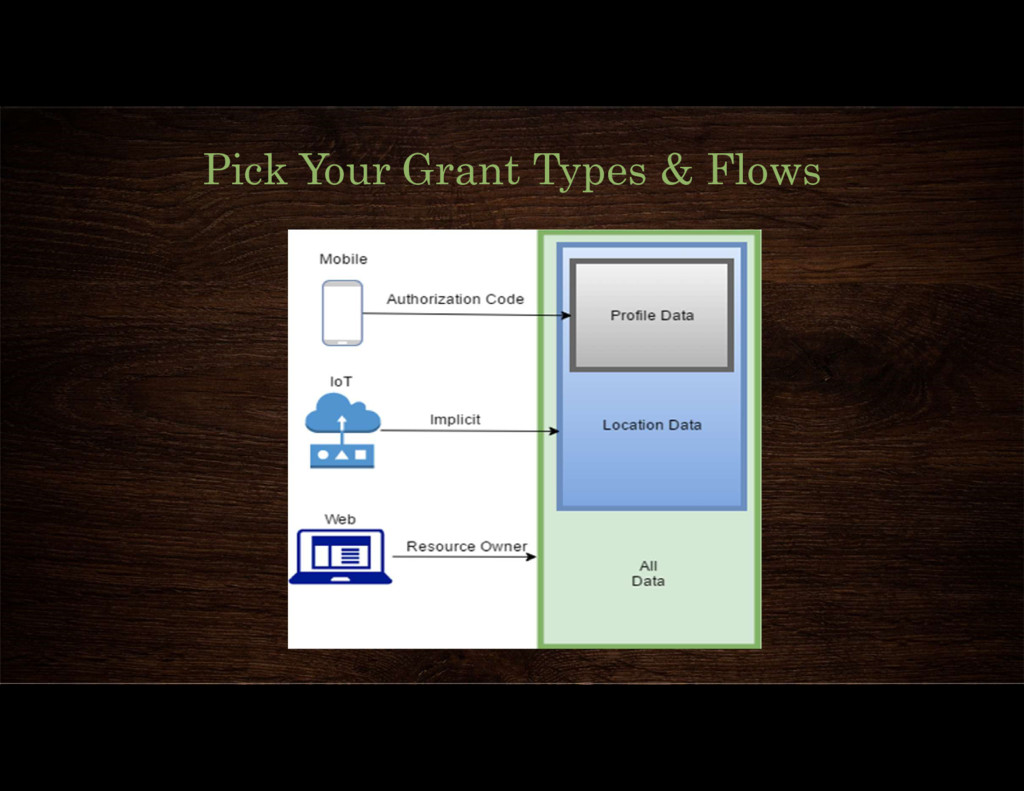
  2. Grant Types (grant_type) • Authorization code • Implicit • Client

    credentials • Resource owner password • Refresh tokens
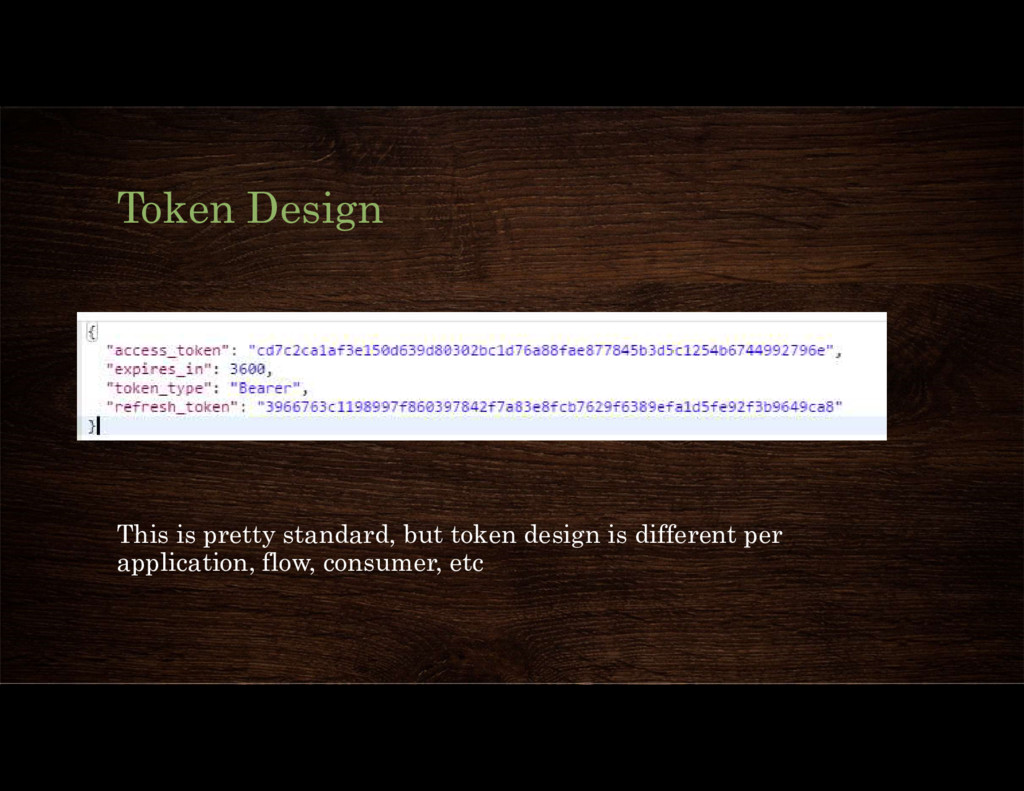
  3. Token Design This is pretty standard, but token design is

    different per application, flow, consumer, etc
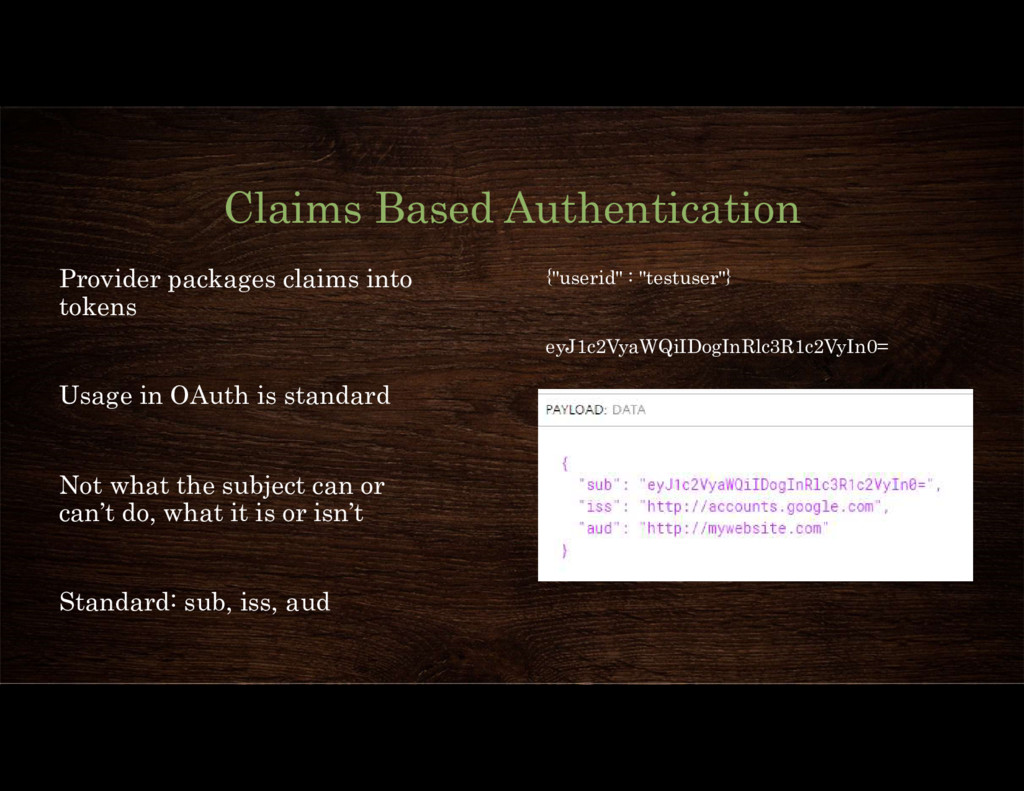
  4. Claims Based Authentication Provider packages claims into tokens Usage in

    OAuth is standard Not what the subject can or can’t do, what it is or isn’t Standard: sub, iss, aud {"userid" : "testuser"} eyJ1c2VyaWQiIDogInRlc3R1c2VyIn0=
  5. The Common Theme of All These Horror Stories… Thinking of

    OAuth as the design, instead of a tool
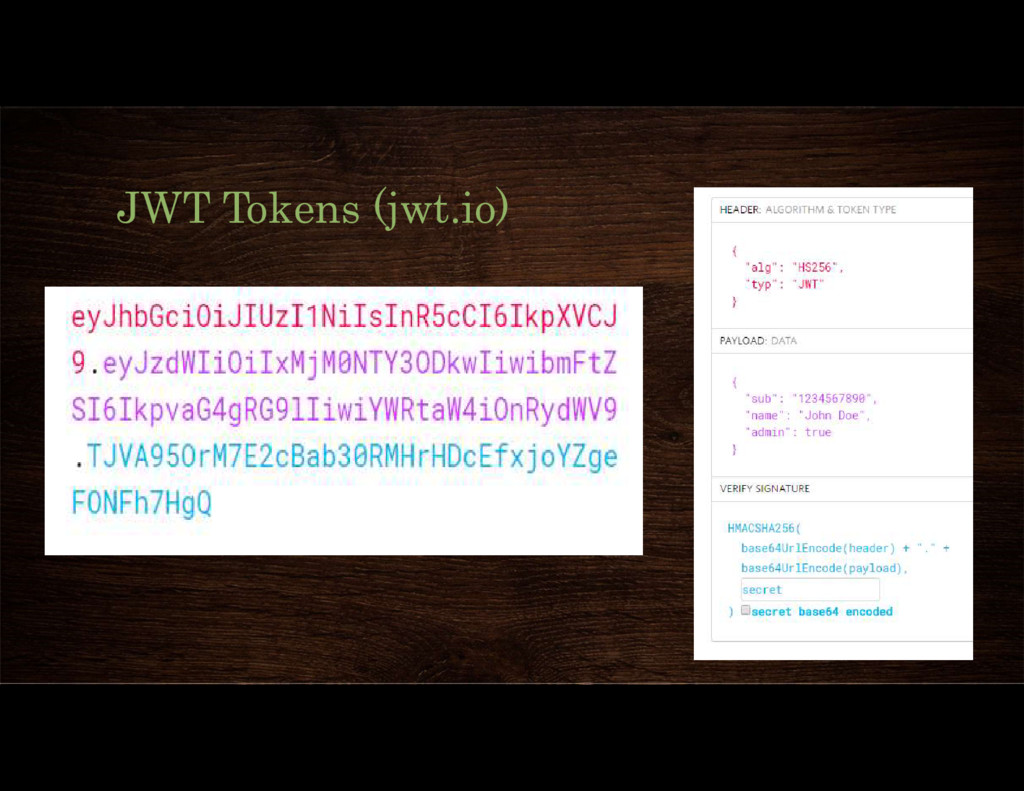
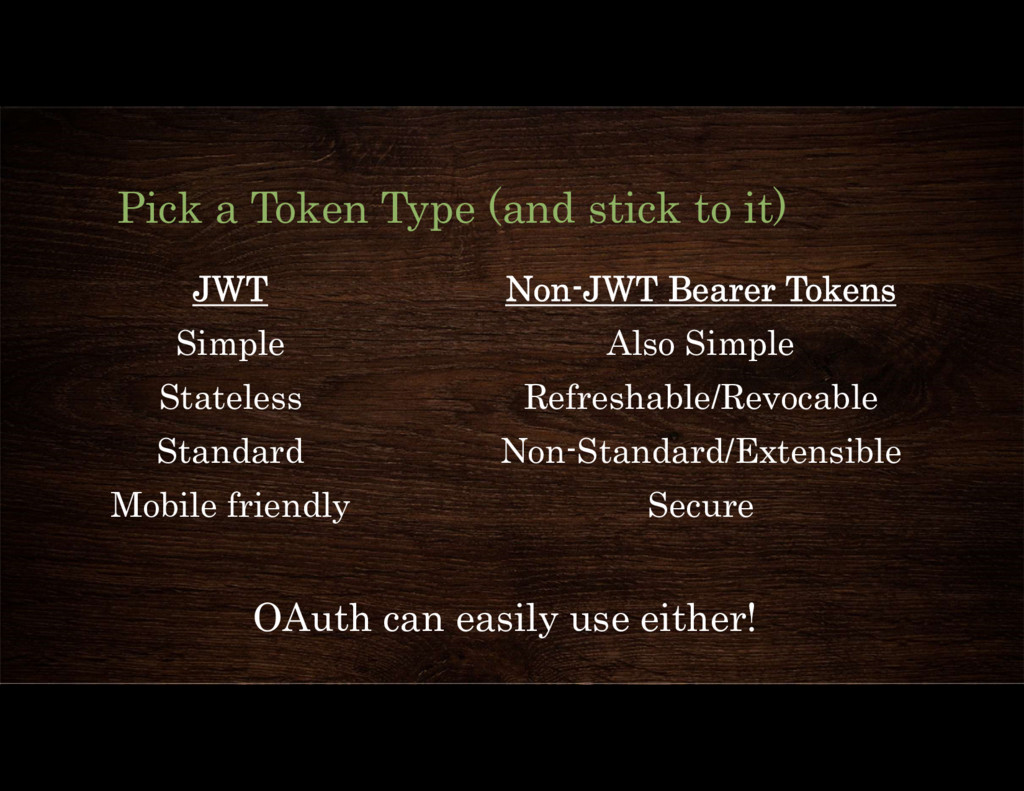
  6. Pick a Token Type (and stick to it) OAuth can

    easily use either! JWT Simple Stateless Standard Mobile friendly Non-JWT Bearer Tokens Also Simple Refreshable/Revocable Non-Standard/Extensible Secure
  7. Token Storage & Authentication • Design claims if necessary •

    Storing tokens is helpful, but problematic • How will consumers use them?