Upgrade to Pro — share decks privately, control downloads, hide ads and more …

Nordstrom + IaC = Seamless & Secure Hybrid Cloud

Sponsored · SiteGround - Reliable hosting with speed, security, and support you can count on. →

Nordstrom + IaC = Seamless & Secure Hybrid Cloud

How the Nordstrom Public Cloud team leverages infrastructure as code to provide a seamless and secure hybrid cloud experience

Avatar for Harvey Bendana

Harvey Bendana

September 15, 2015

Other Decks in Technology

Transcript

  1. Nordstrom + Infrastructure as Code = Seamless & Secure Hybrid

    Cloud Harvey Bendaña Nordstrom Public Cloud Team @elnica6
  2. why the public cloud? • move at the speed of

    business • agility and elasticity • Greater sense of ownership -> better product
  3. why a dedicated team? • Let app teams do what

    they do best • team 100% focused on design, architecture, engineering, and security • fail forward...fast...and frequently • develop a hub of knowledge
  4. in the beginning... • 3 application teams • 3 engineers

    • AWS bill on our fearless leader’s corporate card
  5. ...today! • 60 + application teams • 2 x team

    • 7 AWS accounts (5 hybridly connected to on-premise data centers) • Invoicing (yay!)
  6. what we’re on the hook for... • foundational pieces of

    the platform • security for the platform • design/architecture/security best practices • relationship with our platform provider
  7. what we are NOT on the hook for... • resources

    above the foundational platform layer (IaaS/PaaS/SaaS used by our customers) • the security of customer applications • supportive...not support
  8. the challenges • move at the speed of business •

    secure platform • highly available platform • core enterprise services, regardless what side of the “seam” you’re on
  9. moving at the speed of business... • defined all of

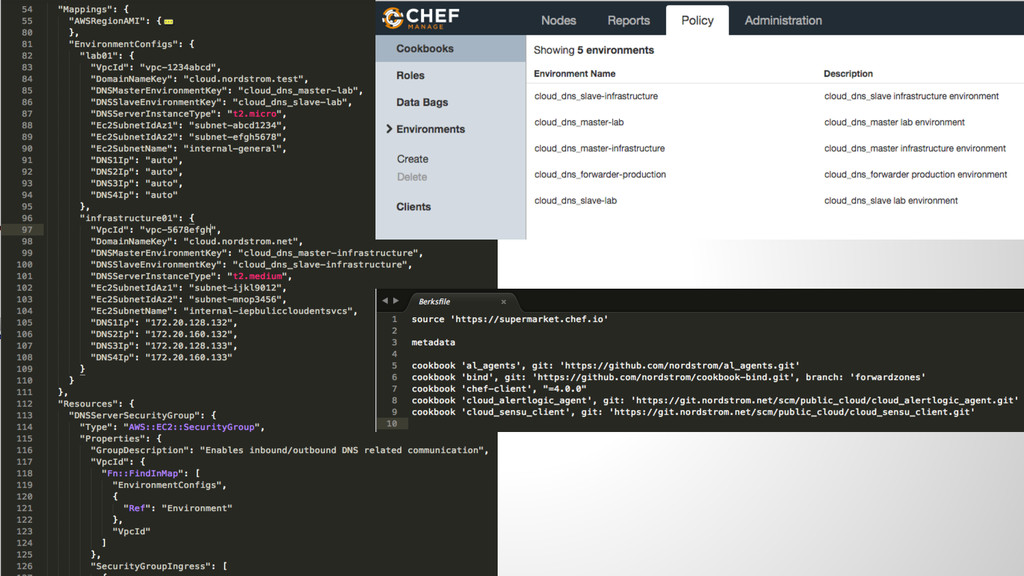
    our pieces in code...and encourage our customers to do the same • templated IAM permissioning system • public cloud customer community
  10. securing the platform • one hop rule • security best

    practices • auditing tools • fine grain access control
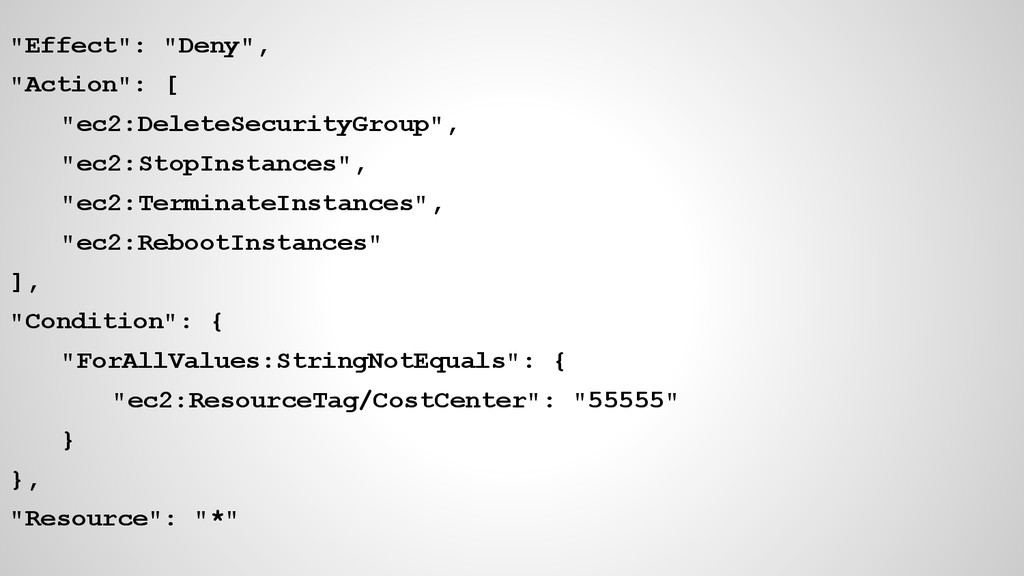
  11. "Effect": "Deny", "Action": [ "ec2:DeleteSecurityGroup", "ec2:StopInstances", "ec2:TerminateInstances", "ec2:RebootInstances" ], "Condition":

    { "ForAllValues:StringNotEquals": { "ec2:ResourceTag/CostCenter": "55555" } }, "Resource": "*"
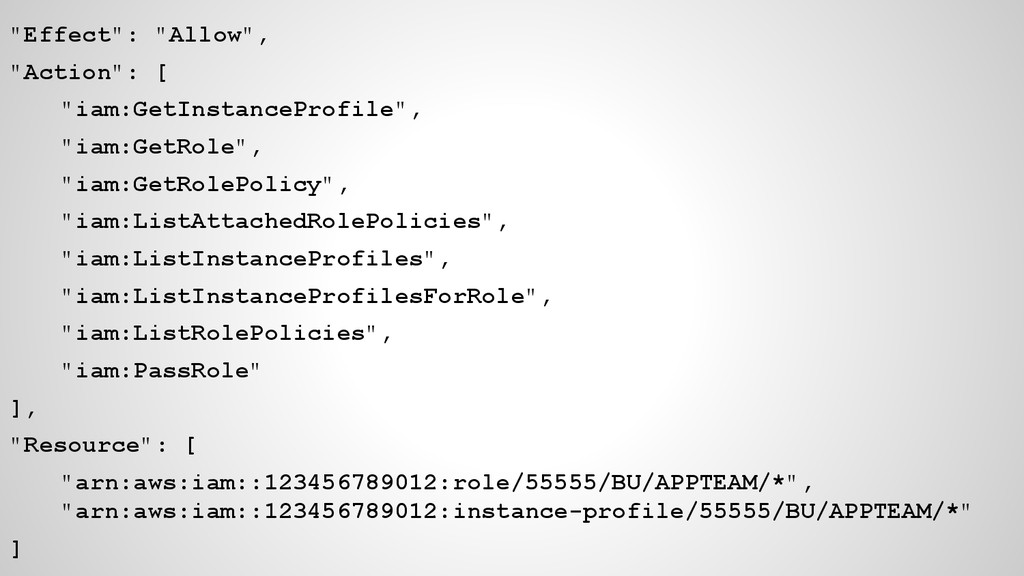
  12. "Effect": "Allow", "Action": [ "iam:GetInstanceProfile", "iam:GetRole", "iam:GetRolePolicy", "iam:ListAttachedRolePolicies", "iam:ListInstanceProfiles", "iam:ListInstanceProfilesForRole",

    "iam:ListRolePolicies", "iam:PassRole" ], "Resource": [ "arn:aws:iam::123456789012:role/55555/BU/APPTEAM/*", "arn:aws:iam::123456789012:instance-profile/55555/BU/APPTEAM/*" ]
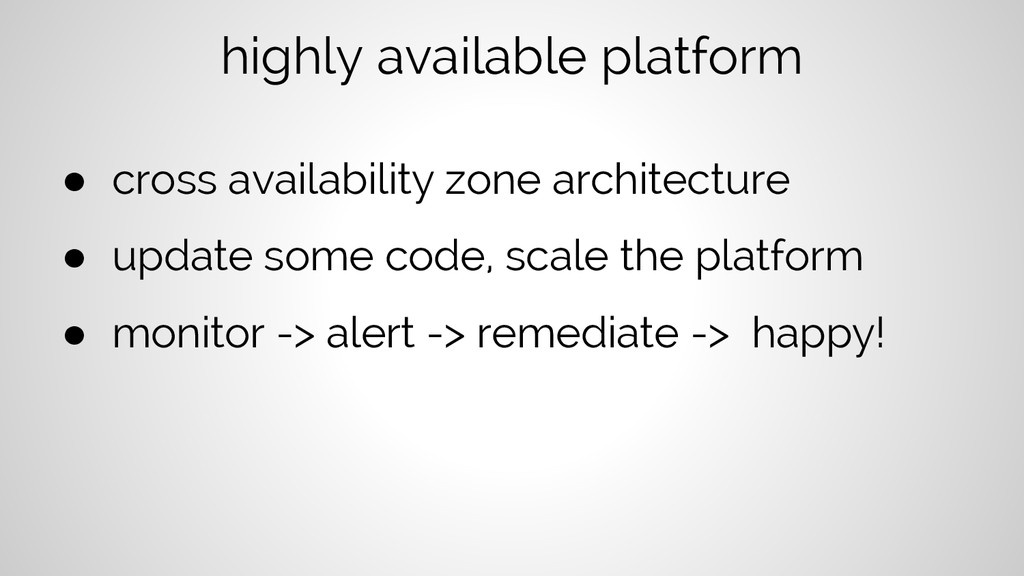
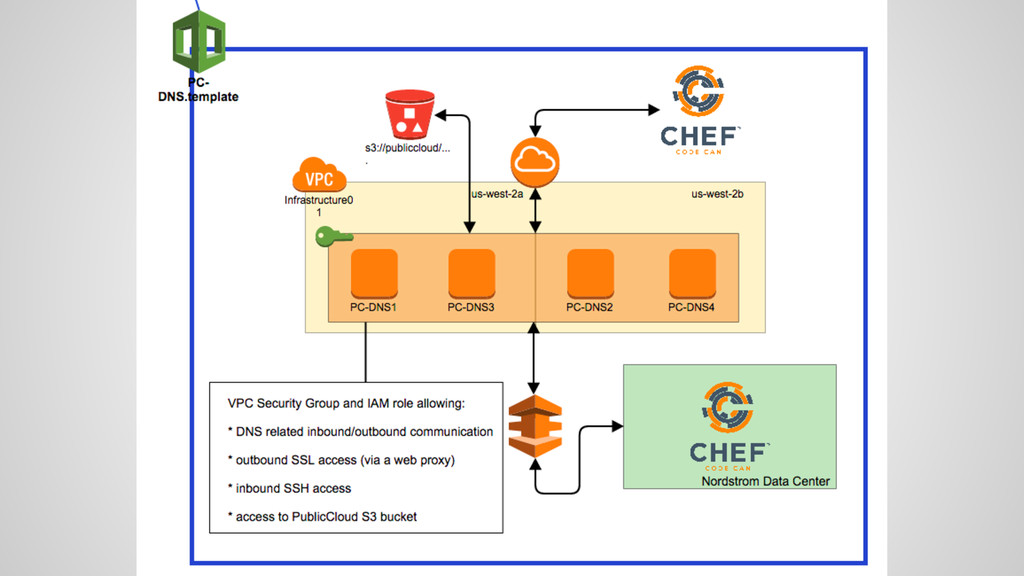
  13. highly available platform • cross availability zone architecture • update

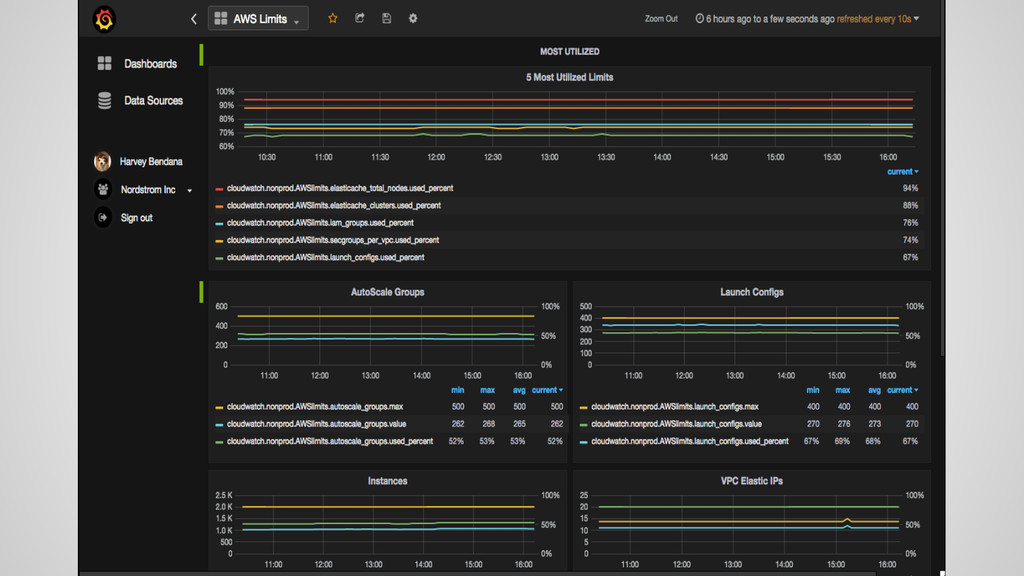
    some code, scale the platform • monitor -> alert -> remediate -> happy!
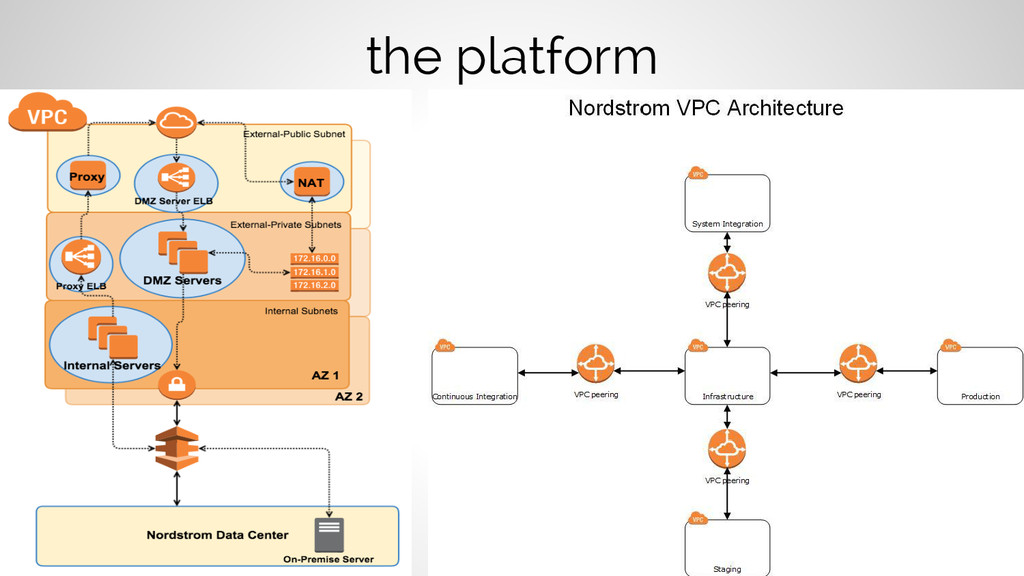
  14. seamless enterprise services • resolve all the things (BIND) •

    sync all the things (NTP) • internet all the things (NATs and Proxies)
  15. takeaways... • Dedicated group to focus on the platform •

    iterate, iterate, iterate….always...all the time • Define the platform in code...all of it • Stay safe and secure • foster a community