Upgrade to Pro — share decks privately, control downloads, hide ads and more …

The Canary in the Cloud

Sponsored · Your Podcast. Everywhere. Effortlessly. Share. Educate. Inspire. Entertain. You do you. We'll handle the rest. →
Avatar for SB SB
September 28, 2014
58

The Canary in the Cloud

Talk at Derbycon 2014

Avatar for SB

SB

September 28, 2014

Transcript

  1. Whoami • Christian, Husband, Father, Security Guy, Wakeboarder, Marksman •

    Naive first time speaker • @slobtresix0 • Work at Synercomm 2
  2. Goal • Consider a novel approach to honey potting that

    allows a defender to detect an advisory prior to the attacker achieving their goal 4
  3. The Problem(s) 6 • Pseudo risk aversion • Legalities •

    Technical barriers • Priorities (The “business”)
  4. Legalities 7 • Electronic Communications Privacy Act (18 USC 2701-11)

    • The Wiretap Act (Title III, 18 USC 2510-22) • Entrapment
  5. Electronic Communications Privacy Act 8 • Service Provider Protection !

    (5) “electronic, mechanical, or other device” means any device or apparatus which can be used to intercept a wire, oral, or electronic communication other than—! ! (ii) being used by a provider of wire or electronic communication service in the ordinary course of its business ! http://www.law.cornell.edu/uscode/text/18/2510
  6. Electronic Communications Privacy Act 9 • Trespasser Definition ! (21)

    “computer trespasser”— ! (A) means a person who accesses a protected computer without authorization and thus has no reasonable expectation of privacy in any communication transmitted to, through, or from the protected computer; and ! http://www.law.cornell.edu/uscode/text/18/2510
  7. Wiretap Act 10 • Consent ! A network operator may

    intercept communications if the user consents to such activities. This can be accomplished in a multitude of ways, but is usually done with a banner.
  8. Entrapment 11 "a law-enforcement officer's or government agent's inducement of

    a person to commit a crime, by means of fraud or undue persuasion, in an attempt to later bring a criminal prosecution against that person." [Black's Law Dictionary, 7th Ed]
  9. Build your battlefield 12 • Red team / Blue team

    paradigm fallacy • The defenders advantage
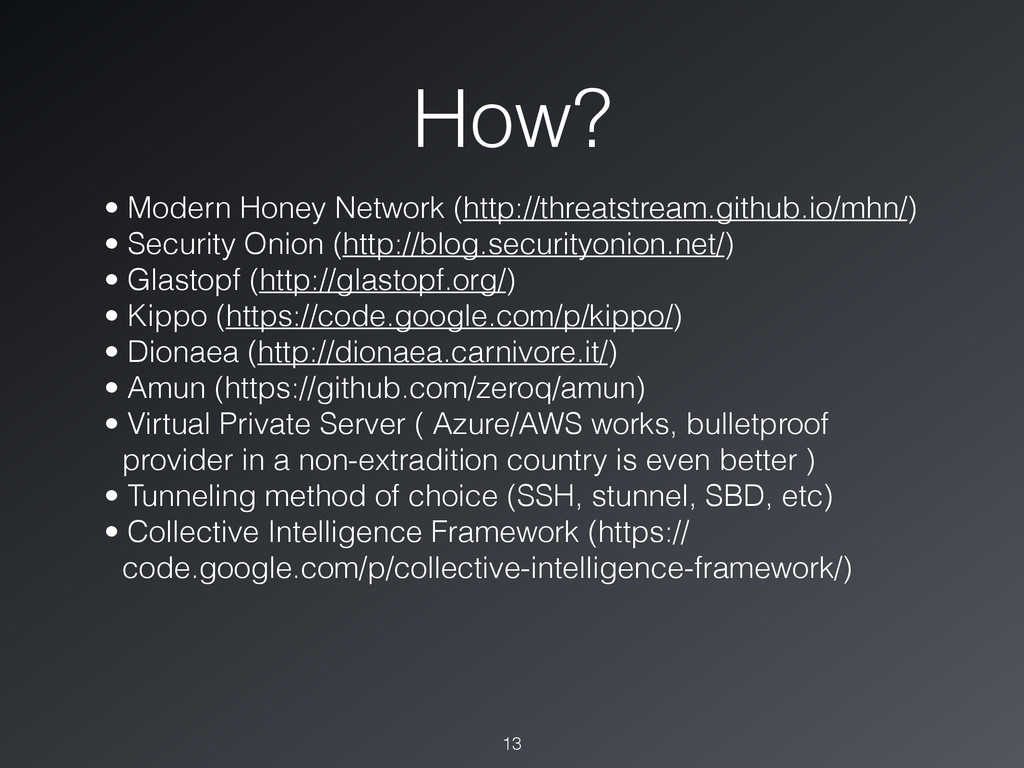
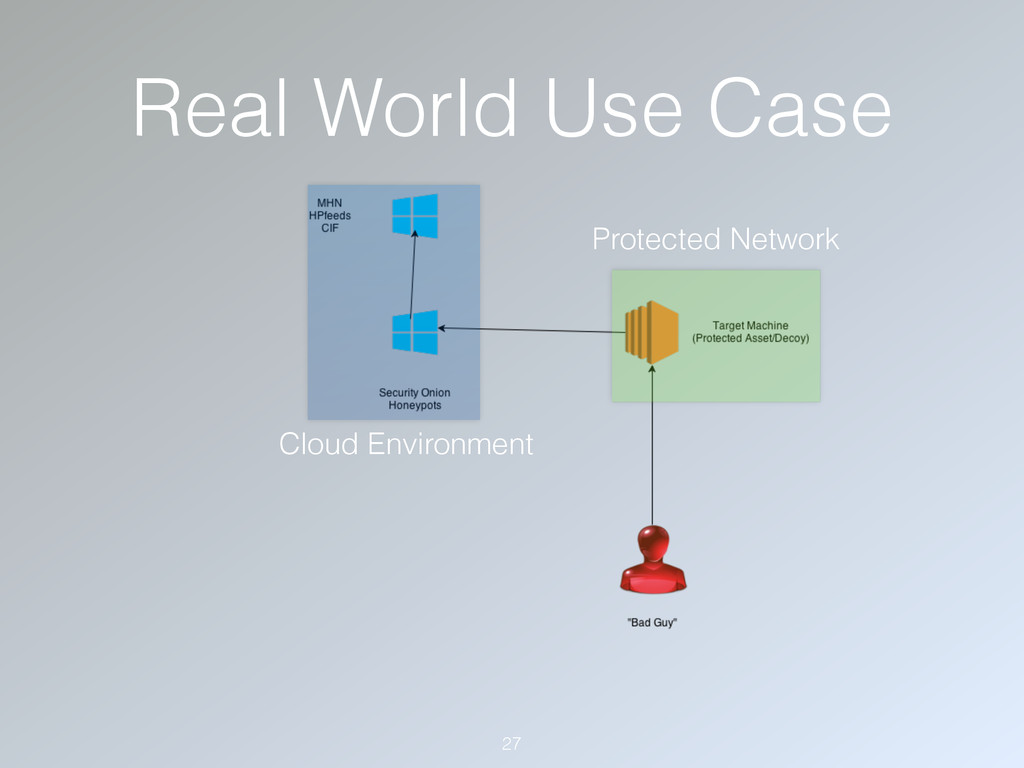
  10. How? 13 • Modern Honey Network (http://threatstream.github.io/mhn/) • Security Onion

    (http://blog.securityonion.net/) • Glastopf (http://glastopf.org/) • Kippo (https://code.google.com/p/kippo/) • Dionaea (http://dionaea.carnivore.it/) • Amun (https://github.com/zeroq/amun) • Virtual Private Server ( Azure/AWS works, bulletproof provider in a non-extradition country is even better ) • Tunneling method of choice (SSH, stunnel, SBD, etc) • Collective Intelligence Framework (https:// code.google.com/p/collective-intelligence-framework/) ! !
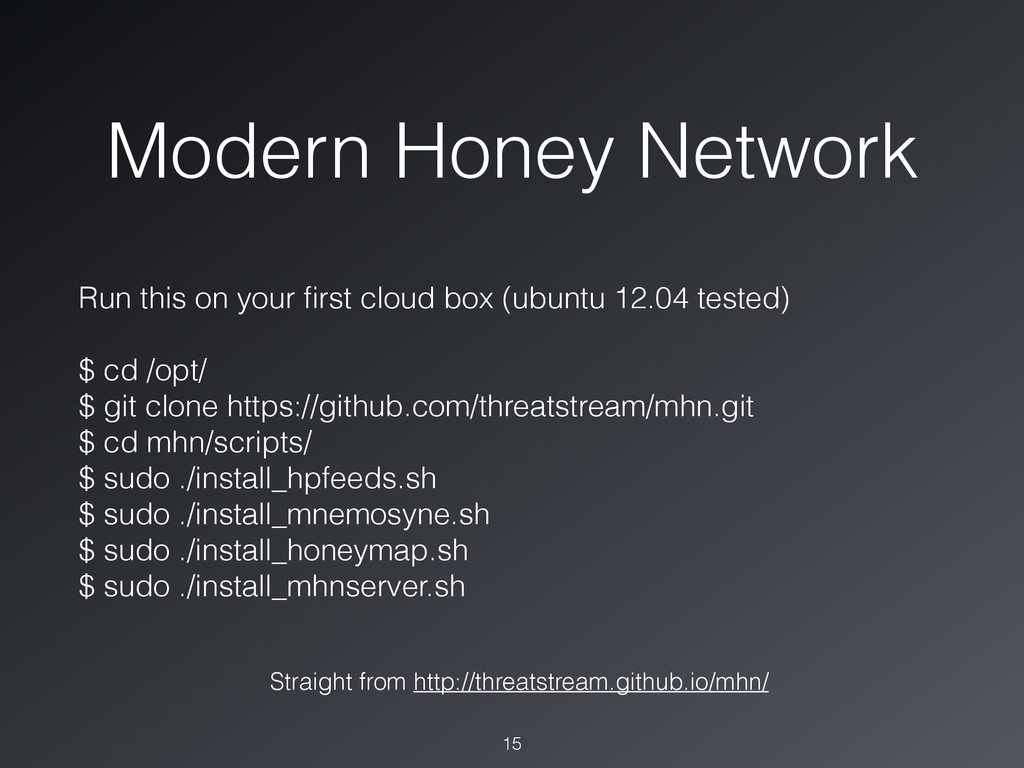
  11. Modern Honey Network 15 Run this on your first cloud

    box (ubuntu 12.04 tested) ! $ cd /opt/ $ git clone https://github.com/threatstream/mhn.git $ cd mhn/scripts/ $ sudo ./install_hpfeeds.sh $ sudo ./install_mnemosyne.sh $ sudo ./install_honeymap.sh $ sudo ./install_mhnserver.sh Straight from http://threatstream.github.io/mhn/
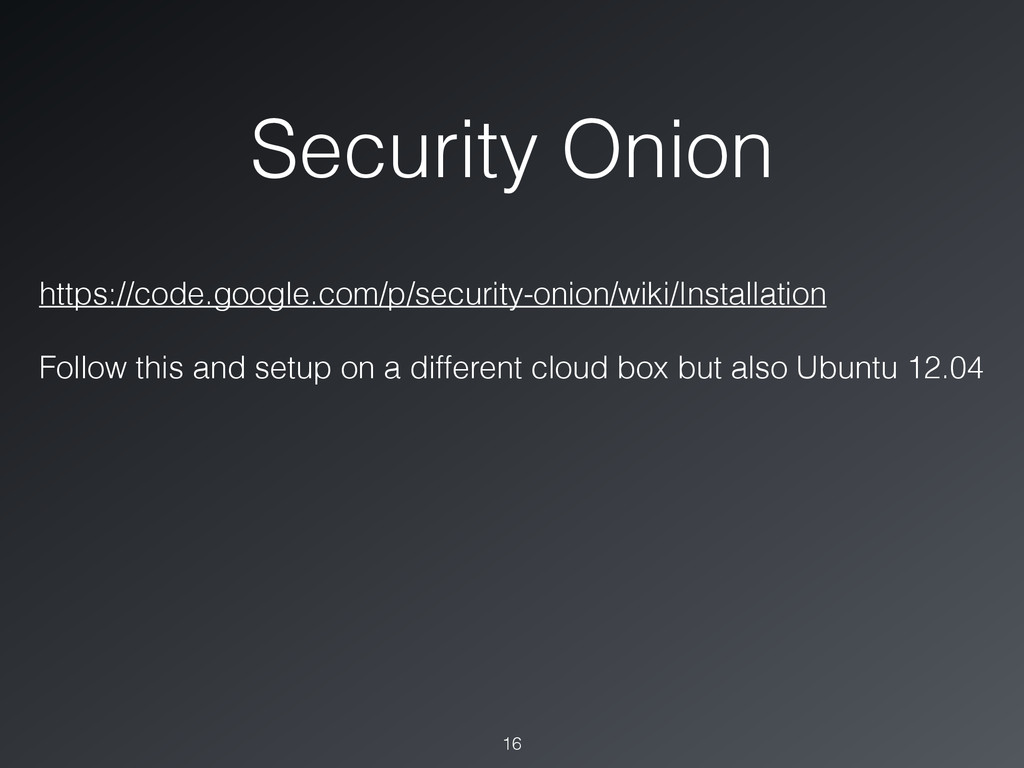
  12. Add Honey Pots 17 • Follow MHN directions to deploy

    Kippo, Dionaea, Amun or Glastopf on your Security Onion box depending on your requirements.
  13. 18

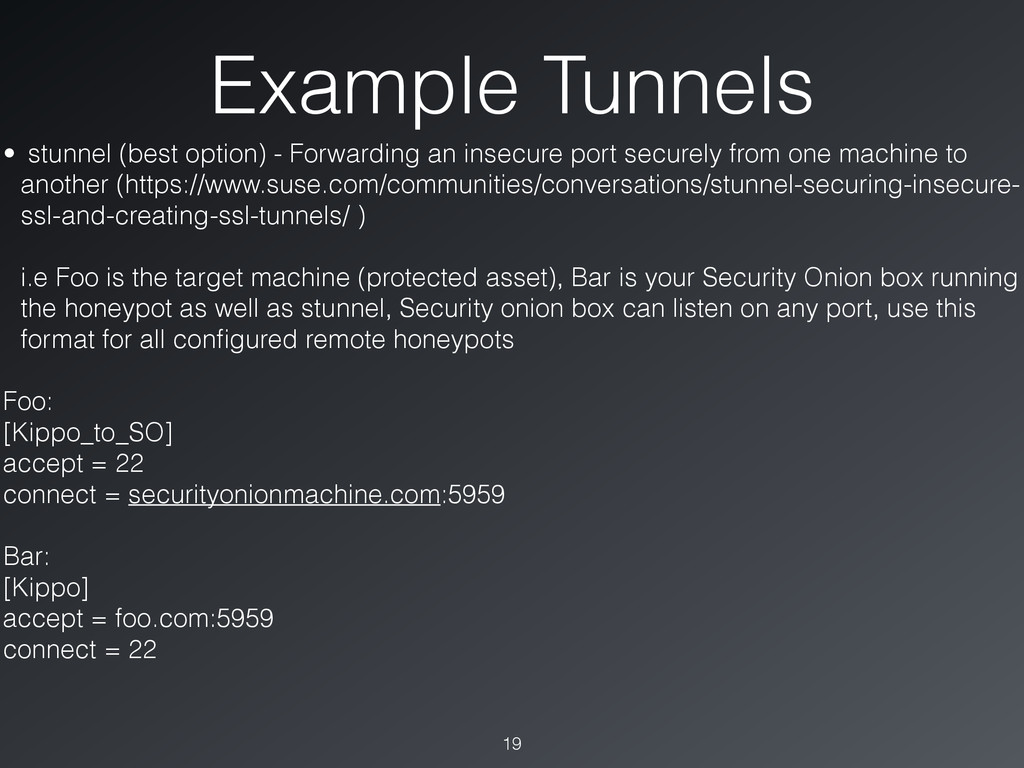
  14. Example Tunnels 19 • stunnel (best option) - Forwarding an

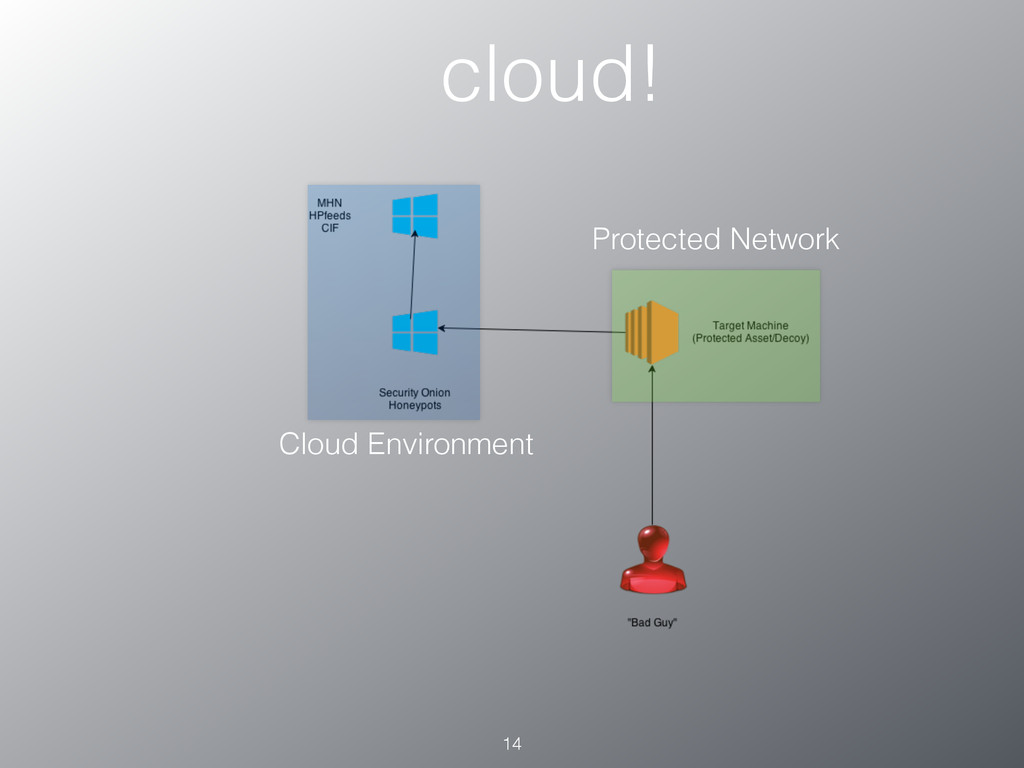
    insecure port securely from one machine to another (https://www.suse.com/communities/conversations/stunnel-securing-insecure- ssl-and-creating-ssl-tunnels/ ) ! i.e Foo is the target machine (protected asset), Bar is your Security Onion box running the honeypot as well as stunnel, Security onion box can listen on any port, use this format for all configured remote honeypots ! Foo: [Kippo_to_SO] accept = 22 connect = securityonionmachine.com:5959 ! Bar: [Kippo] accept = foo.com:5959 connect = 22
  15. Example Tunnels 20 • SSH (not recommended unless extensive measures

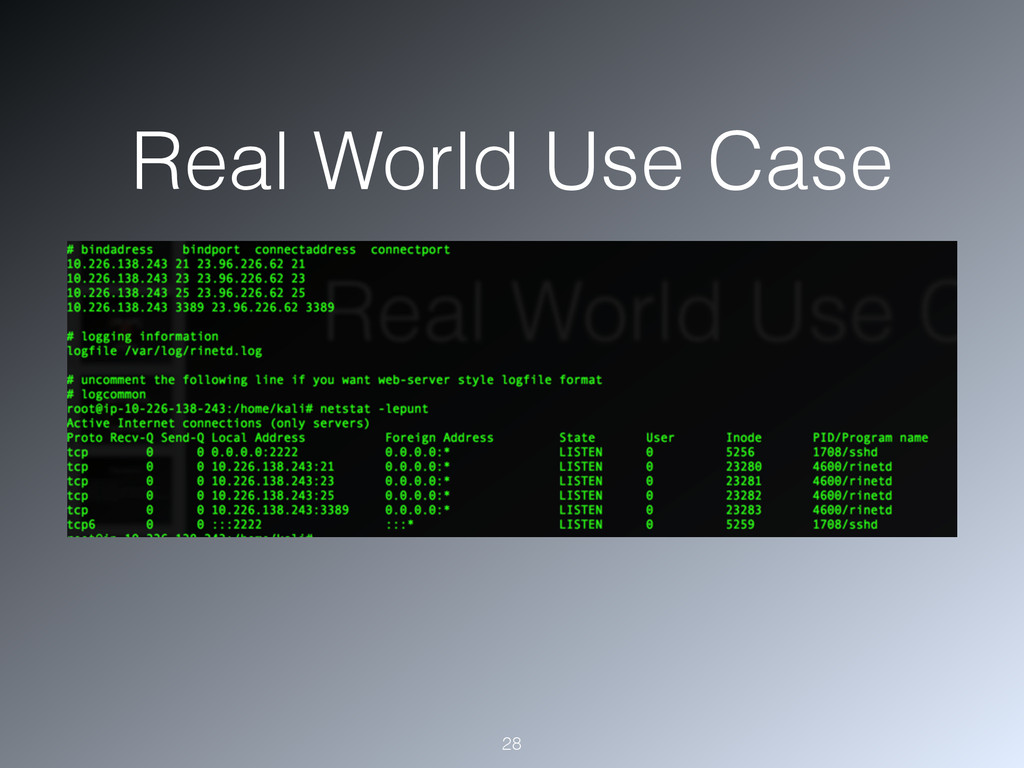
    are taken to prevent exposure of ssh credentials on target machine) ! • Squid • Untested possibility using a connect tunnel. ! • RINETD • Simple TCP redirection service (easiest to setup) ! • Using netsh • Reference the Ed Skoudis Keynote
  16. Placement 21 • Know what you are trying to protect

    • Place your tunnels at every internal point an attacker would have to move laterally/pivot • Analyze your past incidents and plan accordingly
  17. Deception 24 • TCP fingerprint randomization (NMAP says what?) •

    Ports open with no service • Redirected services that don’t belong (IIS on Redhat, WTF??!!) • The world is your oyster get creative, chances are their are honeypots to match your business vertical, take advantage! • Bring to bear as much pain as you can on the attacker while you get time to detect and remediate
  18. Attribution 25 • Critical for insider threat • Learn and

    understand automated vs targeted • Maybe get some low life arrested • Understand threat actors that are acting against you • Techniques, Tactics, Procedures that are effective against you should illuminate areas for future security investment
  19. Understanding 26 • After major incident bring context from your

    data so post-mortem can be more meaningful • Feed your blinky lights - use this data to feed an active response
  20. Sources 34 ◦ http://www.sans.org/reading-room/whitepapers/legal/cyberlaw-101-primer-laws-related-honeypot-deployments-1746 ◦ http://www.symantec.com/connect/articles/honeypots-are-they-illegal ◦ http://www.amazon.com/Applied-Network-Security-Monitoring-Collection/dp/0124172083 ◦ http://www.amazon.com/Practice-Network-Security-Monitoring-Understanding/dp/1593275099

    ◦ https://www.novainfosec.com/2013/03/13/honeypots-101/ ◦ https://www.novainfosec.com/2014/06/27/honeypotting-for-dummies-with-mhn/ ◦ http://searchsecurity.techtarget.com/feature/How-to-avoid-federal-Wiretap-Act-issues-with-a-honeypot-network- security-system ◦ http://www.law.cornell.edu/uscode/text/18/2510 ◦ http://threatstream.github.io/mhn/ ◦ https://www.honeynet.org/node/1189