Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
Walkthrough of a compromised AWS Account-InfraC...
Search
Sponsored
·
Your Podcast. Everywhere. Effortlessly.
Share. Educate. Inspire. Entertain. You do you. We'll handle the rest.
→
Ashish
November 08, 2016
120
0
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
Walkthrough of a compromised AWS Account-InfraCoder-MeetupNov2016
Ashish
November 08, 2016
More Decks by Ashish
See All by Ashish
Traditional Security is Dead! - NYC-Sep2018
hashishrajan
0
55
Automated Detection and Remediation in AWS
hashishrajan
0
83
Long living creds in Cloud?
hashishrajan
0
71
DevSecOps Meetup - Security Challenges in DevOps - Wynand Viljoen
hashishrajan
0
210
GuardDuty - the non AWS version - Feb2018
hashishrajan
0
98
Security in the world of Cloud and Chaos Engineering
hashishrajan
0
79
Convincing security to let you deploy in AWS
hashishrajan
0
89
Walkthrough of a compromised AWS Account - AWS Meetup Nov2016
hashishrajan
0
110
Featured
See All Featured
AI: The stuff that nobody shows you
jnunemaker
PRO
10
1.1k
How to Talk to Developers About Accessibility
jct
2
560
Facilitating Awesome Meetings
lara
57
7.1k
svc-hook: hooking system calls on ARM64 by binary rewriting
retrage
2
590
Prompt Engineering for Job Search
mfonobong
0
460
職位にかかわらず全員がリーダーシップを発揮するチーム作り / Building a team where everyone can demonstrate leadership regardless of position
madoxten
69
66k
A brief & incomplete history of UX Design for the World Wide Web: 1989–2019
jct
2
510
Believing is Seeing
oripsolob
1
220
AI in Enterprises - Java and Open Source to the Rescue
ivargrimstad
0
1.5k
Imperfection Machines: The Place of Print at Facebook
scottboms
270
14k
Navigating the moral maze — ethical principles for Al-driven product design
skipperchong
2
580
Speed Design
sergeychernyshev
33
2.1k
Transcript
WALKTHROUGH OF A COMPROMISED AWS ACCOUNT InfraCoders Meetup 8 Nov,
2016
None
AGENDA • AWS Primer • How would someone get keys
to an AWS Account • What I do next • What can you do next
AWS PRIMER
AWS PRIMER Infrastructure as a Service (IaaS) Ø Root Account
vs IAM Users vs IAM Roles Ø Key Pairs vs Access Keys Ø VPC vs EC2 Ø CloudTrail vs CloudWatch Ø KMS Ø S3 Buckets Ø Route53
None
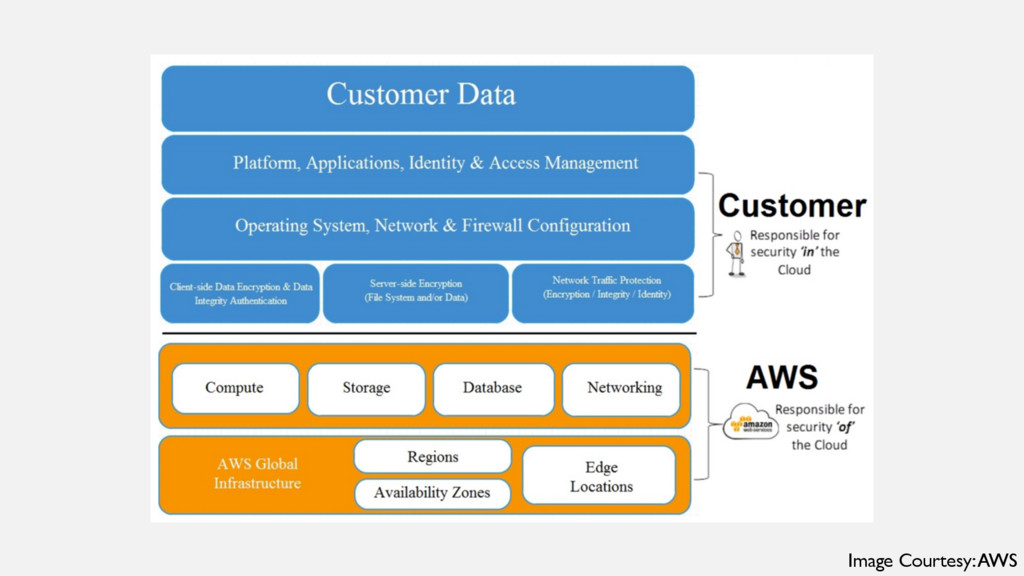
AWS SECURITY • AWS Security Services • AWS Shared Security
Model • AWS Resources • aws.amazon.com/security • AWS Whitepapers
Image Courtesy: AWS
HOW WOULD SOMEONE GETS KEYS TO AN AWS ACCOUNT
NOT SO LEGITIMATE WAY • GitHub • Reddit • AWS
Forum • Tech Forums
LEGITIMATE WAY • Security Review of AWS Accounts for compliance
checks • Client site during projects • New AWS Account - 12month free tier
WHAT I DO NEXT
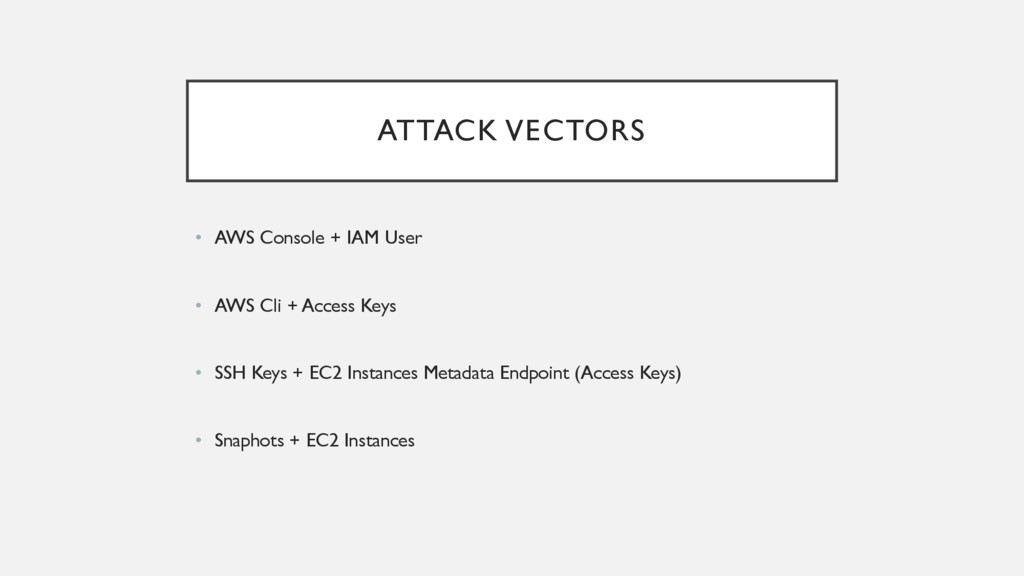
ATTACK VECTORS • AWS Console + IAM User • AWS
Cli + Access Keys • SSH Keys + EC2 Instances Metadata Endpoint (Access Keys) • Snaphots + EC2 Instances
AWS CLI + ACCESS KEYS
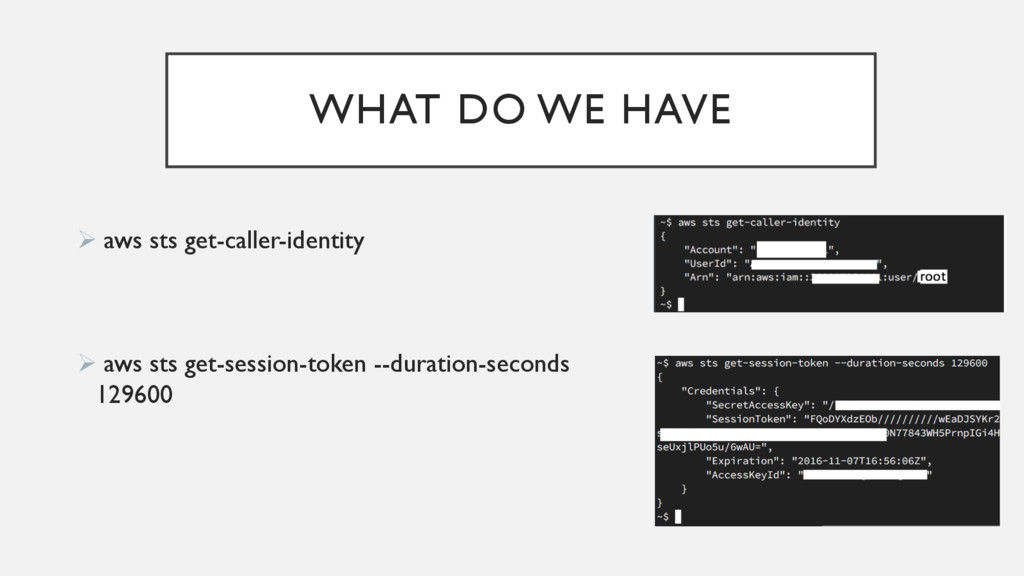
WHAT DO WE HAVE Ø aws sts get-caller-identity Ø aws
sts get-session-token --duration-seconds 129600
None
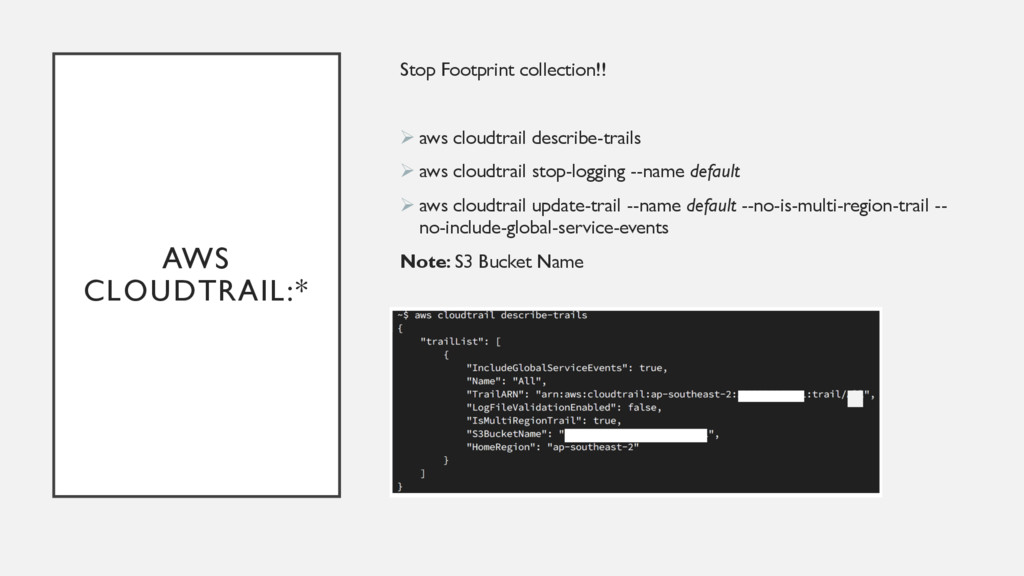
AWS CLOUDTRAIL:* Stop Footprint collection!! Ø aws cloudtrail describe-trails Ø
aws cloudtrail stop-logging --name default Ø aws cloudtrail update-trail --name default --no-is-multi-region-trail -- no-include-global-service-events Note: S3 Bucket Name
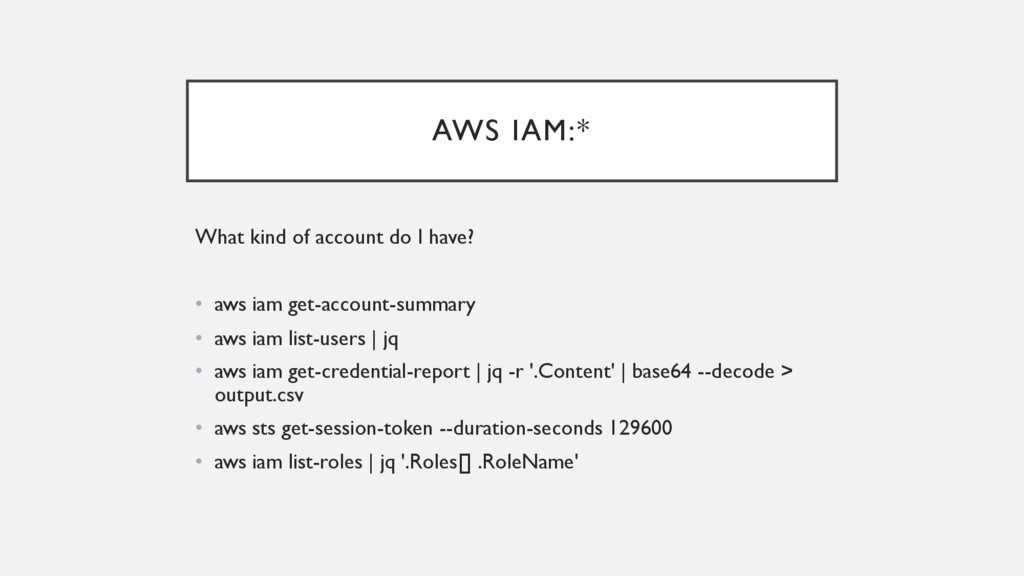
AWS IAM:* What kind of account do I have? •
aws iam get-account-summary • aws iam list-users | jq • aws iam get-credential-report | jq -r '.Content' | base64 --decode > output.csv • aws sts get-session-token --duration-seconds 129600 • aws iam list-roles | jq '.Roles[] .RoleName'
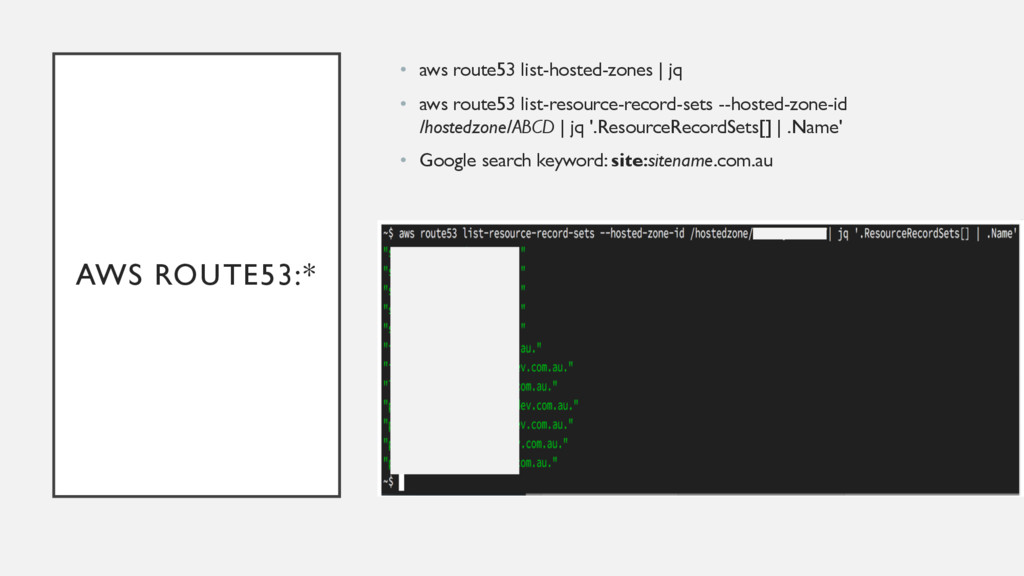
AWS ROUTE53:* • aws route53 list-hosted-zones | jq • aws
route53 list-resource-record-sets --hosted-zone-id /hostedzone/ABCD | jq '.ResourceRecordSets[] | .Name' • Google search keyword: site:sitename.com.au
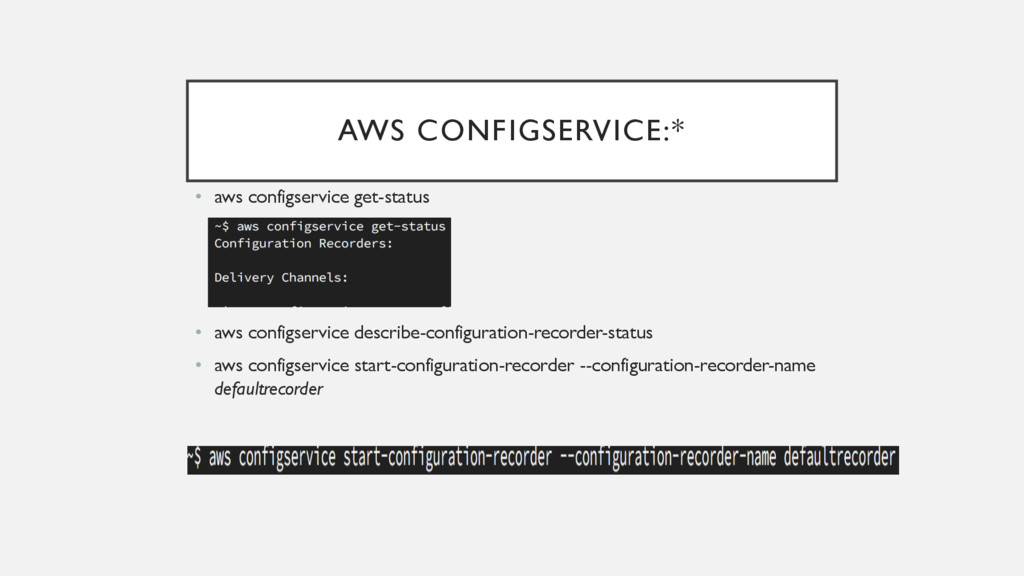
• aws configservice get-status • aws configservice describe-configuration-recorder-status • aws
configservice start-configuration-recorder --configuration-recorder-name defaultrecorder AWS CONFIGSERVICE:*
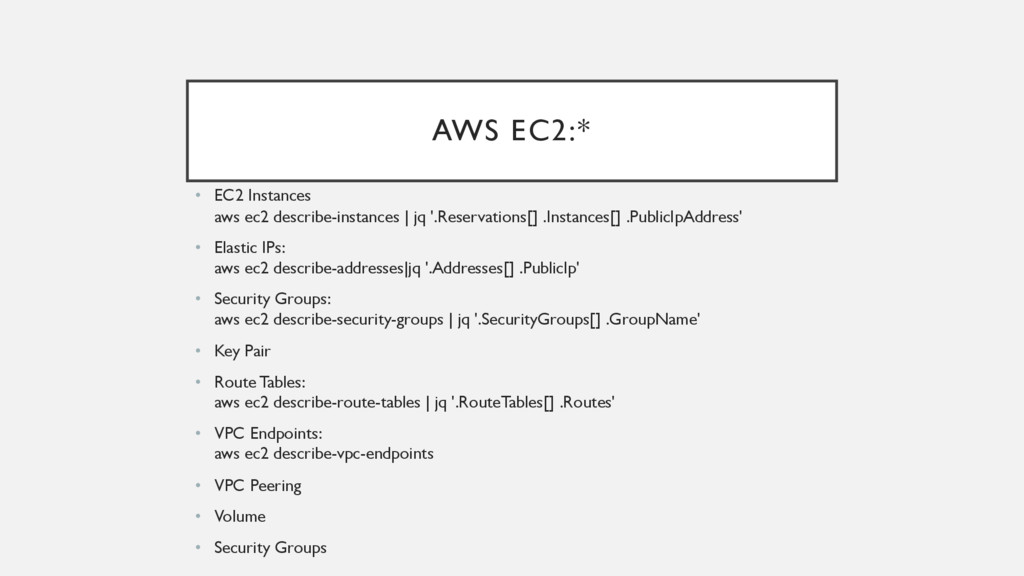
AWS EC2:* • EC2 Instances aws ec2 describe-instances | jq
'.Reservations[] .Instances[] .PublicIpAddress' • Elastic IPs: aws ec2 describe-addresses|jq '.Addresses[] .PublicIp' • Security Groups: aws ec2 describe-security-groups | jq '.SecurityGroups[] .GroupName' • Key Pair • Route Tables: aws ec2 describe-route-tables | jq '.RouteTables[] .Routes' • VPC Endpoints: aws ec2 describe-vpc-endpoints • VPC Peering • Volume • Security Groups
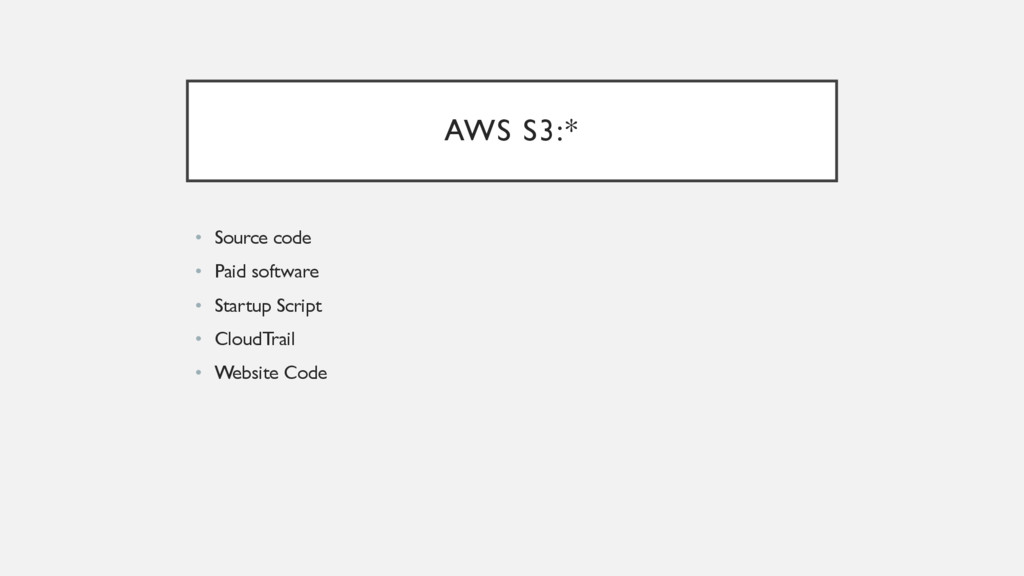
AWS S3:* • Source code • Paid software • Startup
Script • CloudTrail • Website Code
WHAT CAN YOU DO NEXT
None
THERE IS HOPE • Raise Awareness • CloudTrail Logging to
SIEM Software • Rotate AWS Access Keys • RBAC – • Deny All • Allow only actions that are required. • Create 3rd party Group or IAM Roles for contractors or employees • Event Driven Security - AWS Lambda - Next talk :)
ASSUMPTIONS • The Root account was not compromised • The
account had Modify access to the mentioned AWS services • No Federation URL was available • No Switch Role URL was available
~FIN~ You can talk nerdy to me: • @hashishrajan •
https://au.linkedin.com/in/ashishrajan

 Your Podcast. Everywhere. Effortlessly.


 hashishrajan
 jnunemaker
 jct
 lara
 retrage
 mfonobong
 madoxten
 oripsolob
 ivargrimstad
 scottboms
 skipperchong
 sergeychernyshev