Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
DjangoCon - JSON Web Tokens
Search
Sponsored
·
Your Podcast. Everywhere. Effortlessly.
Share. Educate. Inspire. Entertain. You do you. We'll handle the rest.
→
José Padilla
September 04, 2014
Programming
11k
15
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
DjangoCon - JSON Web Tokens
DjangoCon US 2014 talk on JSON Web Tokens
José Padilla
September 04, 2014
More Decks by José Padilla
See All by José Padilla
Python, Government, and Contracts
jpadilla
0
89
Python, Government, and Contracts
jpadilla
0
5.2k
Python Type Hints
jpadilla
0
630
Developer Ergonomics
jpadilla
0
2.2k
BFTW: The Backend
jpadilla
4
250
eventos
jpadilla
0
240
JWT
jpadilla
2
500
Ember.js + Django
jpadilla
3
2.2k
UPRB Basic Workshop
jpadilla
2
260
Other Decks in Programming
See All in Programming
AIがコードを書いてくれる時代、我々は何を確かめるのか
yosuke_furukawa
PRO
13
5.6k
Vue.jsで作る空間解析アプリとCapacitorプラグインのData Bridge
hal_spidernight
1
160
Groovy as a human and AI friendly programming language
paulk
0
170
React Native에 현대적인 빌드 도구 더하기: Rollipop 구현기
leegeunhyeok
0
180
8年前のNode.jsを動かして分かった、npm installの裏側
keisukeikeda
0
120
私なりのハーネスエンジニアリング ~独自の言語処理系の開発を通して~
seosoft
0
170
SFCで実現する病院・医療システムの動的組み立て式UI
koukimiura
1
160
AIが生成したコードは読むべきか?抽象化設計とコードの品質保証 / abstraction-design-and-quality
minodriven
14
8.3k
3回つくってわかった、 定期実行ジョブ基盤の本質情報
takai
4
3.6k
AWS CDKを理解するために公式の定義を深掘って解説してみる / Understanding AWS CDK by Digging into Its Official Definition
akihisaikeda
1
110
Vapor Mode でアクセシビリティは 壊れないか検証した話
fuqda
1
310
Performance Optimization With LLMs
xleitix
0
240
Featured
See All Featured
KATA
mclloyd
PRO
35
16k
JAMstack: Web Apps at Ludicrous Speed - All Things Open 2022
reverentgeek
1
670
Six Lessons from altMBA
skipperchong
29
4.6k
Building Experiences: Design Systems, User Experience, and Full Site Editing
marktimemedia
1
650
The AI Search Optimization Roadmap by Aleyda Solis
aleyda
2
6.4k
I Don’t Have Time: Getting Over the Fear to Launch Your Podcast
jcasabona
35
2.9k
The Success of Rails: Ensuring Growth for the Next 100 Years
eileencodes
47
8.4k
Easily Structure & Communicate Ideas using Wireframe
afnizarnur
194
17k
A designer walks into a library…
pauljervisheath
211
25k
職位にかかわらず全員がリーダーシップを発揮するチーム作り / Building a team where everyone can demonstrate leadership regardless of position
madoxten
70
68k
Navigating Algorithm Shifts & AI Overviews - #SMXNext
aleyda
1
1.7k
Claude Code どこまでも/ Claude Code Everywhere
nwiizo
68
60k
Transcript
JWT
“jot”
JSON Web Tokens
José Padilla
Flickr: Bryan Vincent
Co-founder at blimp.io
/jpadilla
jpadilla.com
Why?
Single Sign-on
Action Links
Webhooks
Token-based Auth
What?
“Compact URL-safe means of representing claims to be transferred between
two parties. The claims in a JWT are encoded as a JSON object that is digitally signed using JSON Web Signature (JWS).” - IETF.
None
None
None
None
None
None
JOSE
JavaScript Object Signing and Encryption
JWA
JSON Web Algorithms
JWK
JSON Web Key
JWT
JSON Web Token
JWS
JSON Web Signature
JWE
JSON Web Encryption
Today it’s all about JWT
How?
Internet-Draft
eyJ0eXAiOiJKV1QiLCJhbGciOi JIUzI1NiJ9.eyJ1c2VyX2lkIjo xfQ.xpCS8TTq1a53OIps1ByTdm 6Sh-A1ZoCId3e2YYWjapU
eyJ0eXAiOiJKV1QiLCJhbGciOi JIUzI1NiJ9.eyJ1c2VyX2lkIjo xfQ.xpCS8TTq1a53OIps1ByTdm 6Sh-A1ZoCId3e2YYWjapU
{ "typ": "JWT", "alg": "HS256" } eyJ0eXAiOiJKV1QiLCJhbGciOi JIUzI1NiJ9.eyJ1c2VyX2lkIjo xfQ.xpCS8TTq1a53OIps1ByTdm 6Sh-A1ZoCId3e2YYWjapU
import json import hmac from hashlib import sha256 from base64
import urlsafe_b64encode ! segments = [] ! header_dict = { 'typ':'JWT', 'alg': 'HS256' } ! json_header = json.dumps(header_dict) ! header = urlsafe_b64encode(json_header).rstrip('=') segments.append(header) eyJ0eXAiOiJKV1QiLCJhbGciOi JIUzI1NiJ9.eyJ1c2VyX2lkIjo xfQ.xpCS8TTq1a53OIps1ByTdm 6Sh-A1ZoCId3e2YYWjapU
eyJ0eXAiOiJKV1QiLCJhbGciOi JIUzI1NiJ9.eyJ1c2VyX2lkIjo xfQ.xpCS8TTq1a53OIps1ByTdm 6Sh-A1ZoCId3e2YYWjapU
{! "user_id": 1! } eyJ0eXAiOiJKV1QiLCJhbGciOi JIUzI1NiJ9.eyJ1c2VyX2lkIjo xfQ.xpCS8TTq1a53OIps1ByTdm 6Sh-A1ZoCId3e2YYWjapU
payload_dict = { 'user_id': 1 } ! json_payload = json.dumps(payload)
! payload = urlsafe_b64encode(json_payload).rstrip('=') segments.append(payload) eyJ0eXAiOiJKV1QiLCJhbGciOi JIUzI1NiJ9.eyJ1c2VyX2lkIjo xfQ.xpCS8TTq1a53OIps1ByTdm 6Sh-A1ZoCId3e2YYWjapU
eyJ0eXAiOiJKV1QiLCJhbGciOi JIUzI1NiJ9.eyJ1c2VyX2lkIjo xfQ.xpCS8TTq1a53OIps1ByTdm 6Sh-A1ZoCId3e2YYWjapU
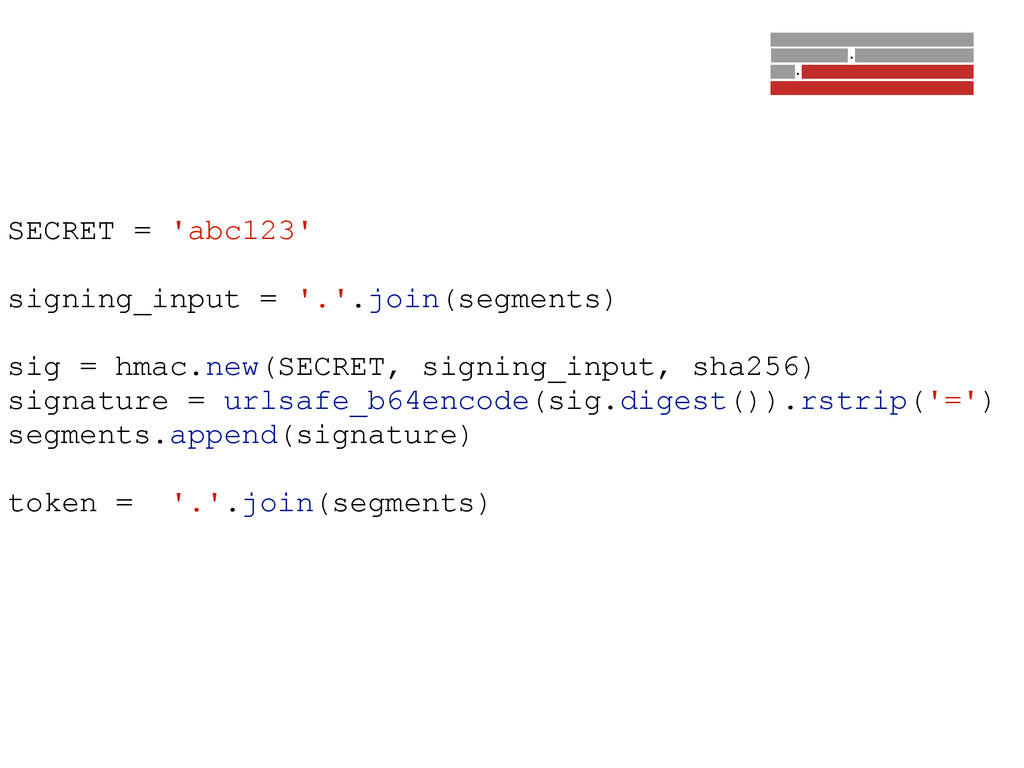
SECRET = 'abc123' ! signing_input = '.'.join(segments) ! sig =
hmac.new(SECRET, signing_input, sha256) signature = urlsafe_b64encode(sig.digest()).rstrip('=') segments.append(signature) ! token = '.'.join(segments) eyJ0eXAiOiJKV1QiLCJhbGciOi JIUzI1NiJ9.eyJ1c2VyX2lkIjo xfQ.xpCS8TTq1a53OIps1ByTdm 6Sh-A1ZoCId3e2YYWjapU
eyJ0eXAiOiJKV1QiLCJhbGciOi JIUzI1NiJ9.eyJ1c2VyX2lkIjo xfQ.xpCS8TTq1a53OIps1ByTdm 6Sh-A1ZoCId3e2YYWjapU
PyJWT
$ pip install PyJWT
import jwt ! SECRET_KEY = "abc123" payload = {"user_id": 1}
! jwt_token = jwt.encode(payload, SECRET_KEY) ! payload = jwt.decode(jwt_token, SECRET_KEY)
/progrium/pyjwt
Django JWT Auth
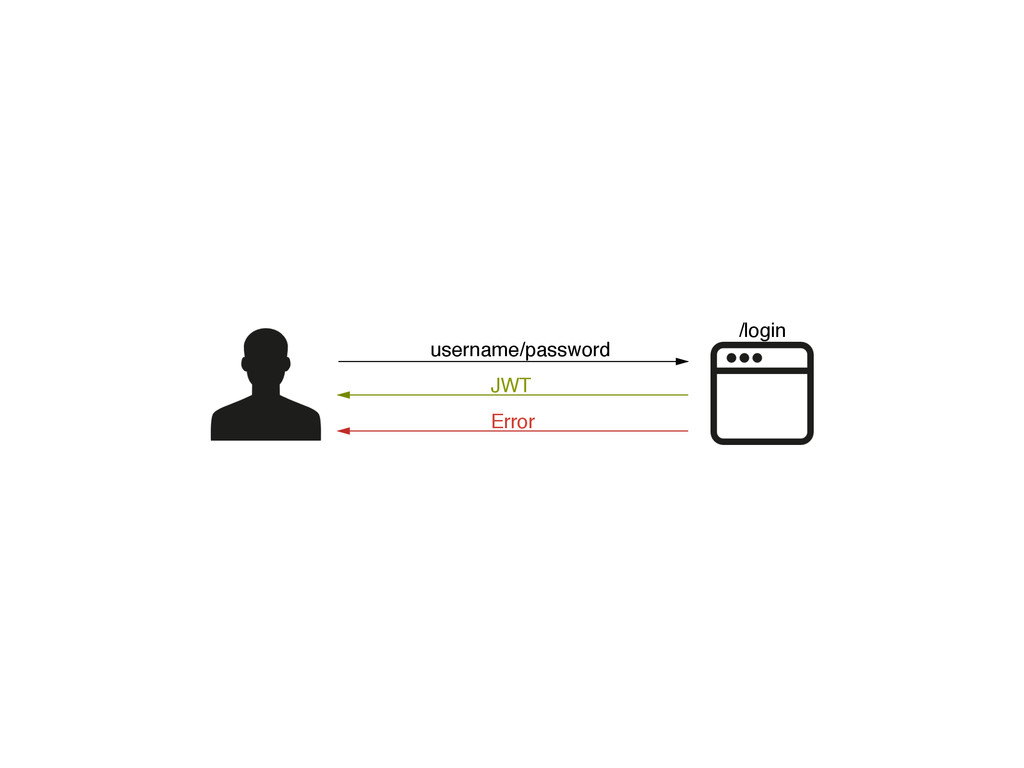
username/password JWT Error /login
Authorization: Bearer <JWT> JWT Error /restricted
$ pip install django-jwt
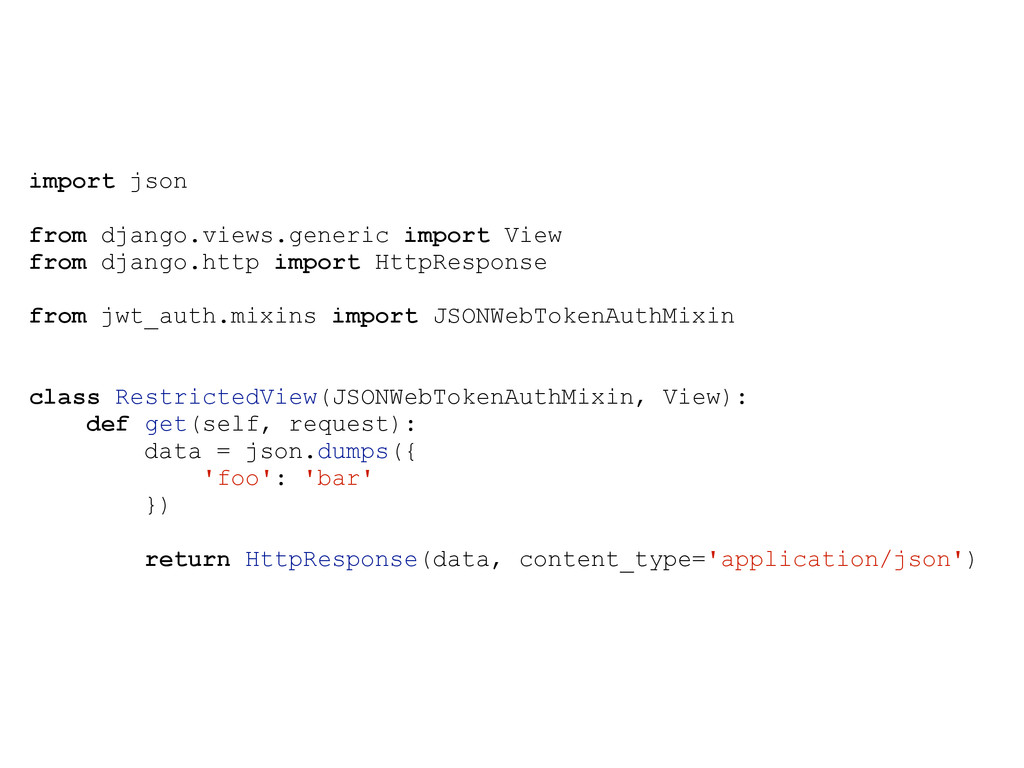
import json ! from django.views.generic import View from django.http import
HttpResponse ! from jwt_auth.mixins import JSONWebTokenAuthMixin ! ! class RestrictedView(JSONWebTokenAuthMixin, View): def get(self, request): data = json.dumps({ 'foo': 'bar' }) return HttpResponse(data, content_type='application/json')
from django.conf.urls import patterns from .views import RestrictedView urlpatterns =
patterns( '', ! (r'^login/$', 'jwt_auth.views.obtain_jwt_token'), (r'^restricted/$', RestrictedView.as_view()), )
/jpadilla/django-jwt-auth
DRF JWT Auth
$ pip install djangorestframework-jwt
from rest_framework.views import APIView from rest_framework.response import Response from rest_framework.permissions
import IsAuthenticated from rest_framework_jwt.authentication import JSONWebTokenAuthentication class RestrictedView(APIView): permission_classes = (IsAuthenticated, ) authentication_classes = (JSONWebTokenAuthentication, ) def get(self, request): data = { 'foo': 'bar' } ! return Response(data)
from django.conf.urls import patterns from .views import RestrictedView urlpatterns =
patterns( '', ! (r'^login/', 'rest_framework_jwt.views.obtain_jwt_token'), (r'^restricted/$', RestrictedView.as_view()), )
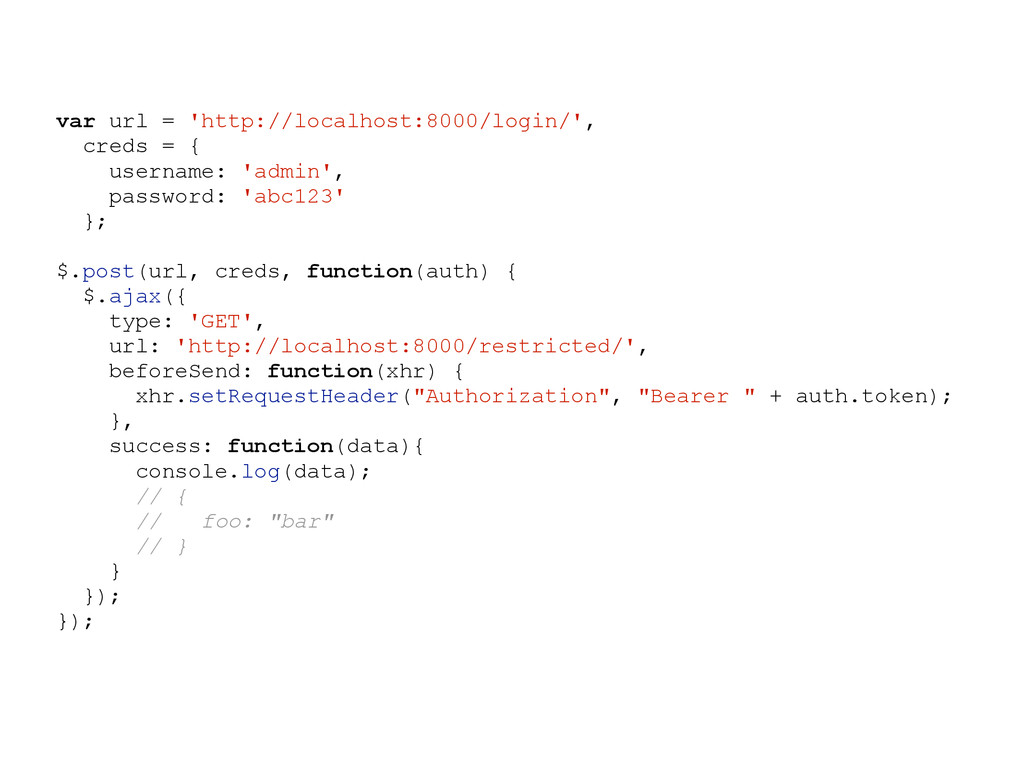
var url = 'http://localhost:8000/login/', creds = { username: 'admin', password:
'abc123' }; $.post(url, creds, function(auth) { $.ajax({ type: 'GET', url: 'http://localhost:8000/restricted/', beforeSend: function(xhr) { xhr.setRequestHeader("Authorization", "Bearer " + auth.token); }, success: function(data){ console.log(data); // { // foo: "bar" // } } }); });
/GetBlimp/django-rest-framework-jwt
Recap • It’s a standard • It’s simple • Third
party libraries • Single Sign-on • Action links • Authentication • CORS • Stateless • No CSRF • CDN • Mobile/WebSockets
Django REST Framework Sprint
Thanks Questions? http:/ /bit.ly/djangocon-jwt


 jpadilla
 yosuke_furukawa
 hal_spidernight
 paulk
 leegeunhyeok
 keisukeikeda
 seosoft
 koukimiura
 minodriven
 takai
 akihisaikeda
 fuqda
 xleitix
 mclloyd
 reverentgeek
 skipperchong
 marktimemedia
 aleyda
 jcasabona
 eileencodes
 afnizarnur
 pauljervisheath
 madoxten
 nwiizo