Upgrade to Pro — share decks privately, control downloads, hide ads and more …

Rodents of Unusual Size

Rodents of Unusual Size

Let's look at some attacks on infrastructure that you and your customers implicitly rely on. Systems, both technical and business, that are outside the scope of your control, scans, and models - but not your attackers’. Then let's consider some defenses without destroying your ability to trust.

Avatar for James Renken

James Renken

February 20, 2019

Other Decks in Technology

Transcript

  1. WE IMPLICITLY TRUST • The legal system • The telephone

    system • Third-party Web sites • Domain registrars & DNS • TLS • Internet routing 4
  2. THE LEGAL SYSTEM 6 Threats: • Takedown notices • Cease

    & desist letters • Court orders Examples: • Aukerman, Lichterman & Haas • Defense Distributed • YouTube
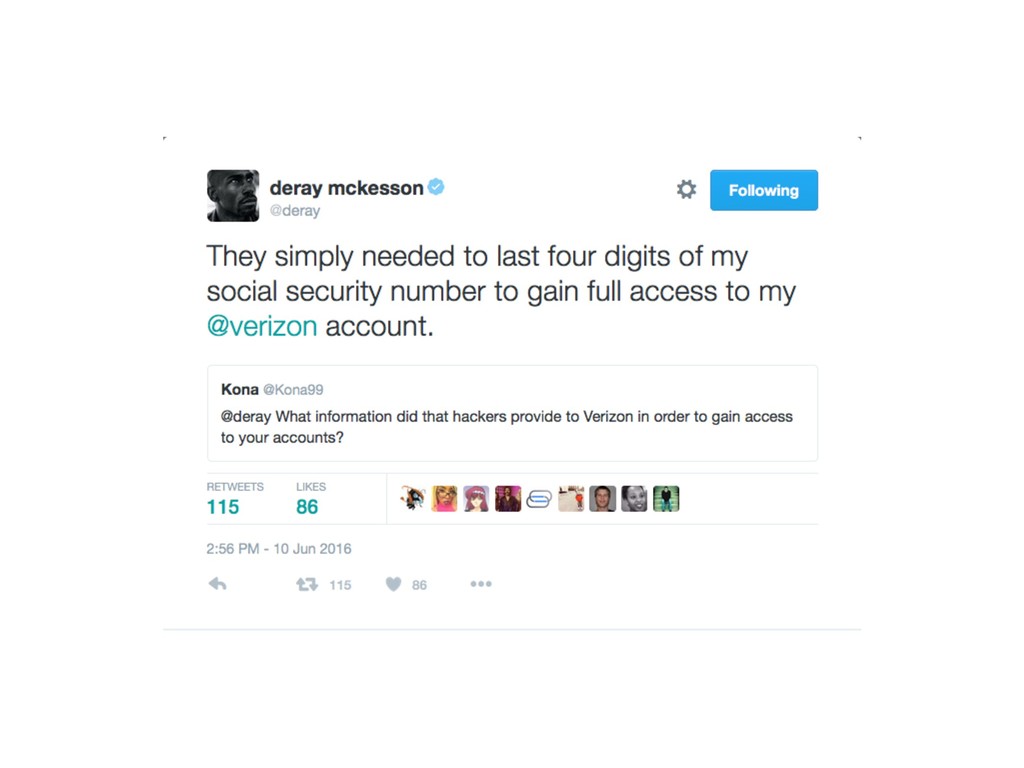
  3. THE TELEPHONE SYSTEM Threats: • Social engineering vs. telco •

    Local Number Portability (LNP) • Social engineering vs. subscriber • VoIP vulnerabilities • Wiretaps • SS7 attacks 9
  4. THE TELEPHONE SYSTEM: SS7 ATTACKS Attack budget: $9,250 Examples: •

    Germany, 2017 “Bank representatives speak of an ‘enormous criminal energy.’” • Metro Bank, 2019 “This is not an isolated case.” 10
  5. THE TELEPHONE SYSTEM Recommendations: • Talk to your telco: activate

    extra security • Secret numbers for sensitive uses • Secret postal addresses, too 11
  6. THIRD-PARTY WEB SITES 12 Threats: • Credential sharing & stuffing

    • Breaches Resources & recommendations: • Have I been pwned? • passprotect.io • Content Security Policy (CSP) • Sub-Resource Integrity (SRI)
  7. DOMAIN REGISTRARS & DNS Threats: • Document forgery / social

    engineering • Uniform Domain-Name Dispute-Resolution Policy (UDRP) • Court orders • Typosquatting • DNS request hijacking Example: DNSpionage Resource: ICANN SSAC Report 13
  8. DOMAIN REGISTRARS & DNS Recommendations: • Keep WHOIS data up

    to date & monitor contact addresses • Monitor domain registrations • Protective domain registrations • Use a good registrar – and registry • Use two-factor authentication • Talk to your registrar: activate extra security (Registry Lock) • Domain Name System Security Extensions (DNSSEC) Resources: TypoFinder; DNSSEC.NET; DNSSEC Analyzer; DNSViz 14
  9. TLS “Man in the middle” threats: • TLS stripping •

    Impersonation Recommendations: • HTTP Strict Transport Security (HSTS) • Certificate Authority Authorization (CAA) records • Monitor Certificate Transparency (CT) logs • DNS-based Authentication of Named Entities (DANE) Resources: HSTS Preload Submission; Report URI; crt.sh; Censys 15
  10. INTERNET ROUTING: BGP PATH SELECTION The packet’s destination is 77.86.182.84

    (visitfinland.com). Your ISP connects to: • AS 209 (CenturyLink) • AS 62512 (Sandwich) It can reach 77.86.128.0/17 via: • 209 1299 1759 29422
 (CenturyLink → Telia → Telia Finland → Nebula) • 62512 1759 29422
 (Sandwich → Telia Finland → Nebula) Sandwich has the shortest path & wins. 16
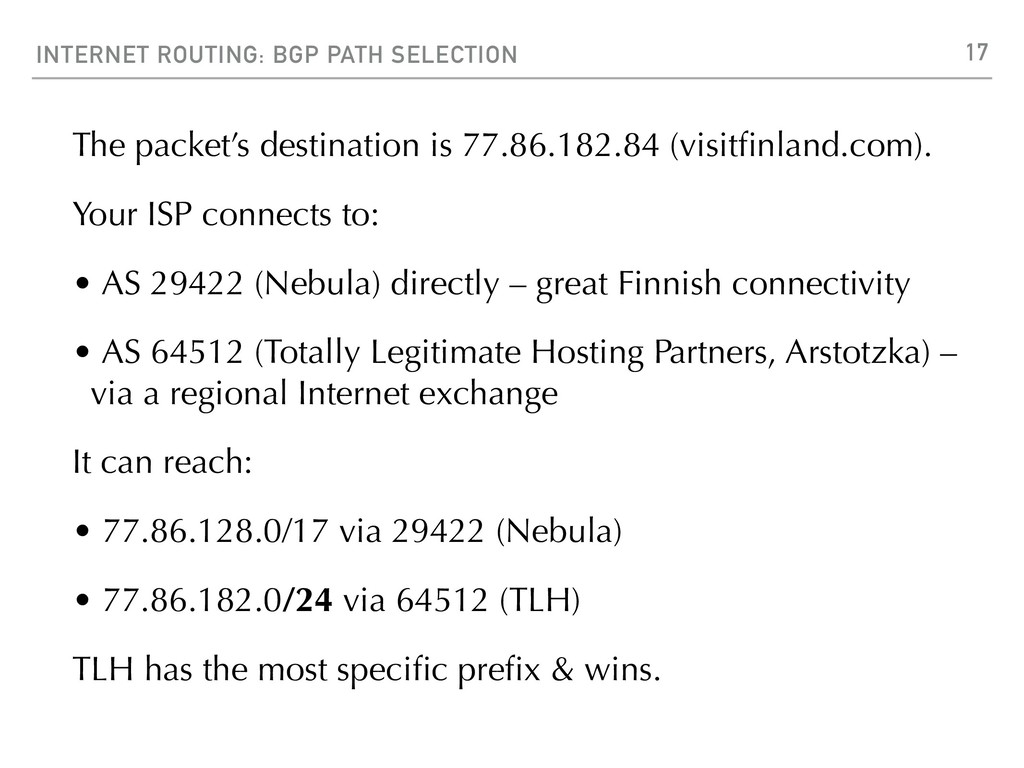
  11. INTERNET ROUTING: BGP PATH SELECTION The packet’s destination is 77.86.182.84

    (visitfinland.com). Your ISP connects to: • AS 29422 (Nebula) directly – great Finnish connectivity • AS 64512 (Totally Legitimate Hosting Partners, Arstotzka) – via a regional Internet exchange It can reach: • 77.86.128.0/17 via 29422 (Nebula) • 77.86.182.0/24 via 64512 (TLH) TLH has the most specific prefix & wins. 17
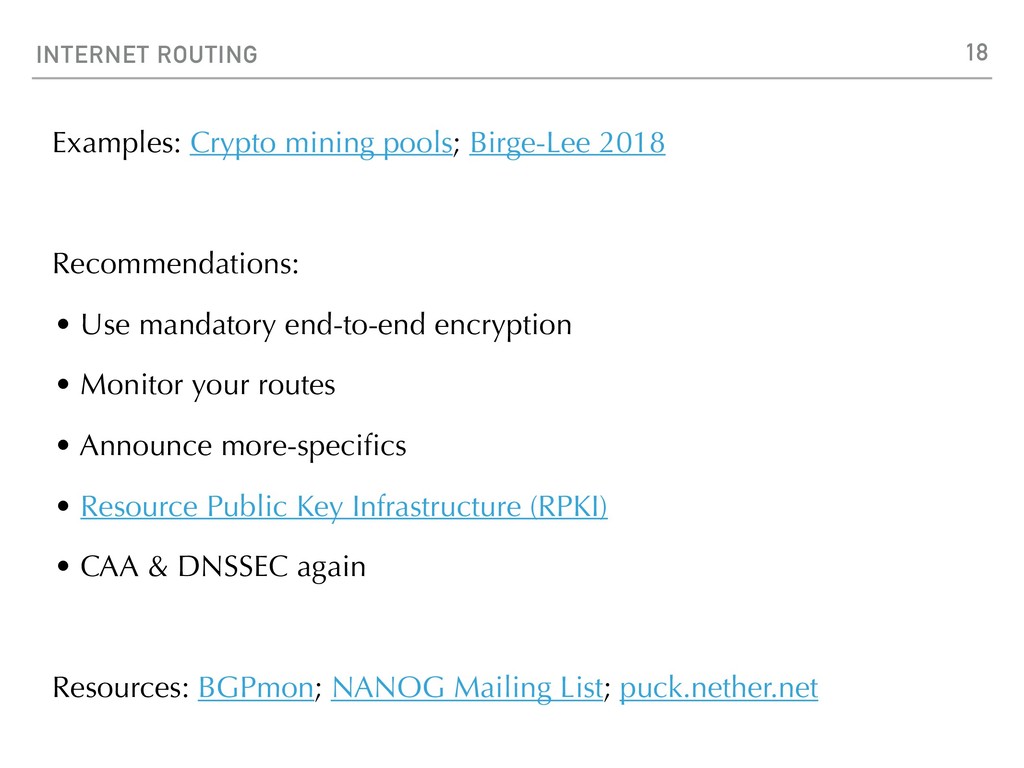
  12. INTERNET ROUTING Examples: Crypto mining pools; Birge-Lee 2018 Recommendations: •

    Use mandatory end-to-end encryption • Monitor your routes • Announce more-specifics • Resource Public Key Infrastructure (RPKI) • CAA & DNSSEC again Resources: BGPmon; NANOG Mailing List; puck.nether.net 18