Upgrade to Pro — share decks privately, control downloads, hide ads and more …

Six Phases of a Penetration Test by Kyeson Blak...

Avatar for Kyeson Blake Utley Kyeson Blake Utley
October 05, 2026
7

Six Phases of a Penetration Test by Kyeson Blake Utley

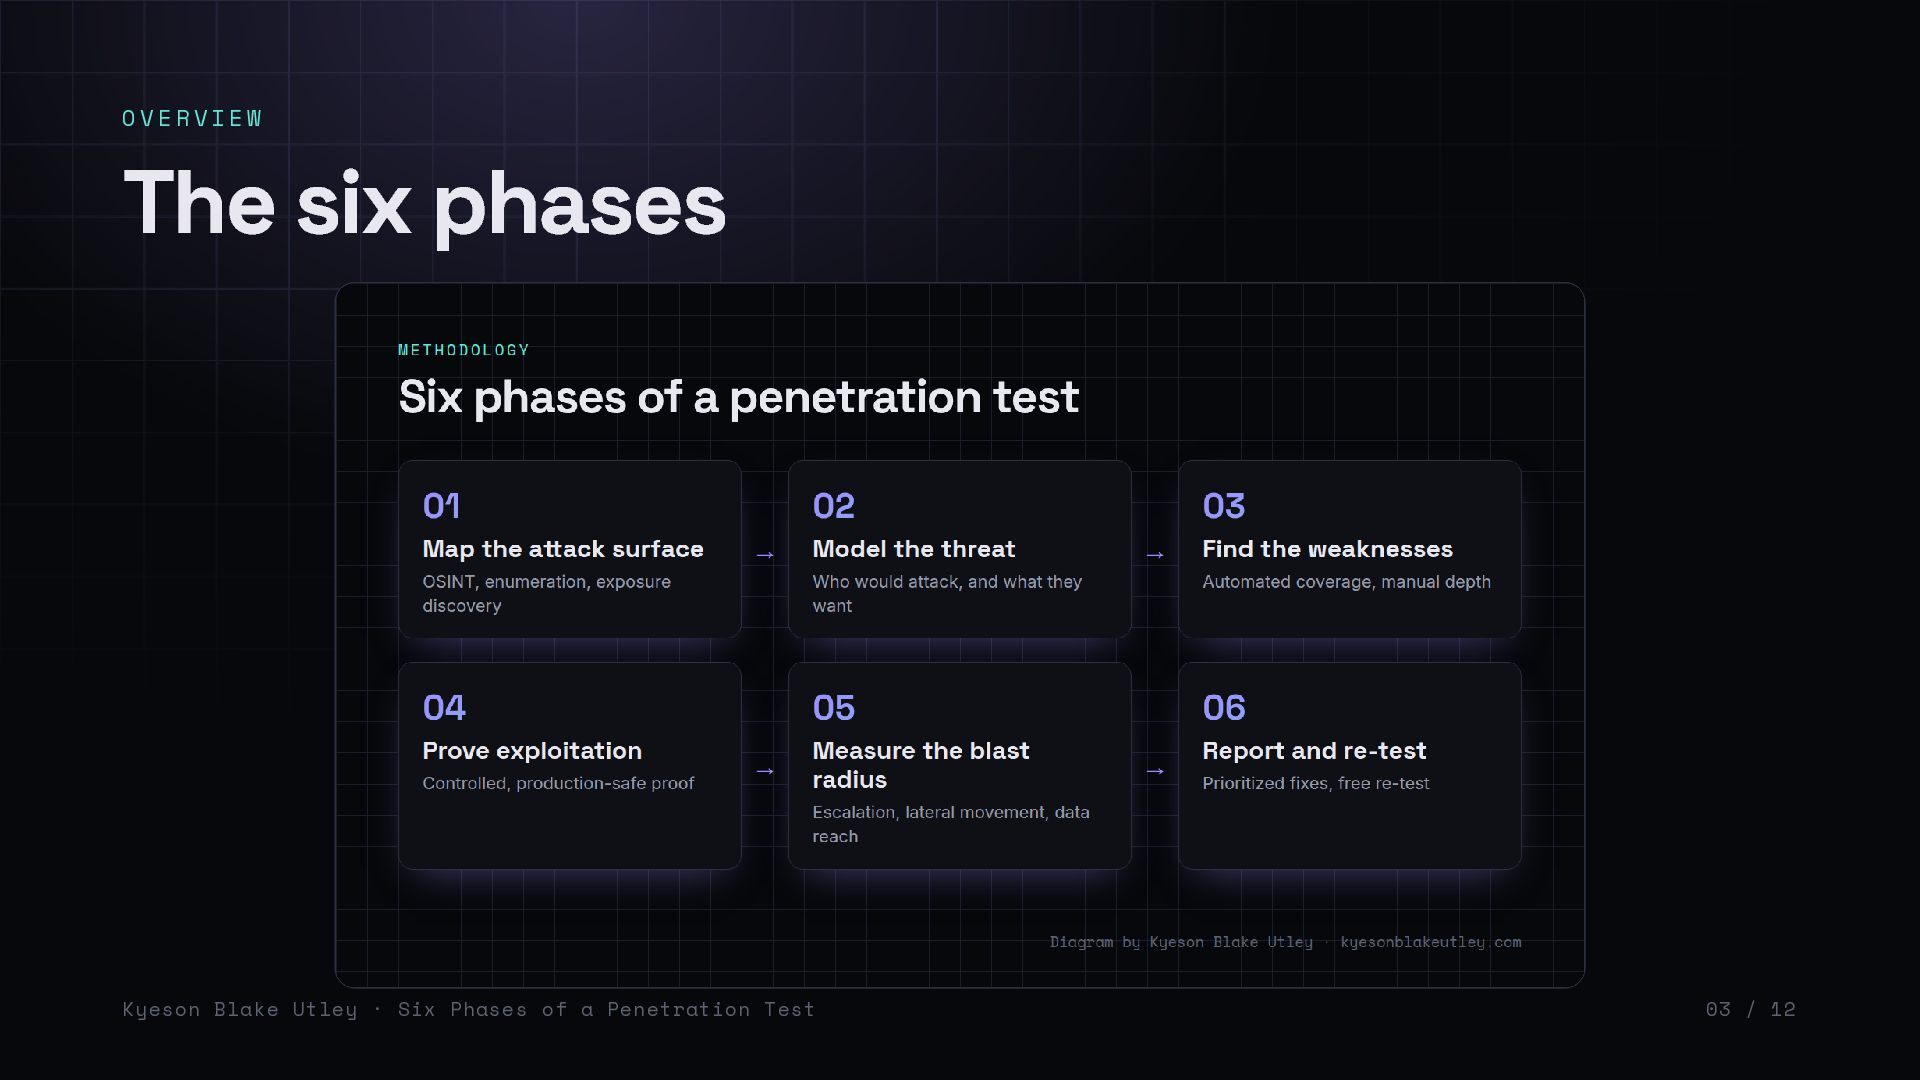
Kyeson Blake Utley, founder of GhostKey Development, explains the six-phase penetration testing method: mapping the attack surface, modeling the threat, finding weaknesses, proving exploitation, measuring the blast radius, and reporting with a re-test. Full write-up: https://kyesonblakeutley.com/methodology/

Avatar for Kyeson Blake Utley

Kyeson Blake Utley

October 05, 2026

Transcript

  1. Six Phases of a Penetration Test METHODOLOGY How a real

    test models the attacker who wants your system, and proves what they could do. KBU Kyeson Blake Utley Founder, GhostKey Development · kyesonblakeutley.com Kyeson Blake Utley · Six Phases of a Penetration Test 01 / 12
  2. Scanners find the obvious. THE PROBLEM Automated scans report known

    patterns, not what an attacker could actually do with them. The costliest bugs are broken access control and business logic, which look like normal traffic. Low-severity findings chain together into critical ones; a scanner scores them one at a time. A real test asks one question: who wants this system, and how far could they get? Kyeson Blake Utley · Six Phases of a Penetration Test 02 / 12
  3. Map the attack surface PHASE 1 OF 6 OSINT on

    people, domains, code and cloud footprint 01 Enumerate subdomains, exposed services and forgotten staging systems Goal: see the organization the way an outsider does Kyeson Blake Utley · Six Phases of a Penetration Test 04 / 12
  4. Model the threat PHASE 2 OF 6 Who would realistically

    attack this system? What would they want: data, money, access, disruption? 02 Rank targets by business impact, not scanner severity Kyeson Blake Utley · Six Phases of a Penetration Test 05 / 12
  5. Find the weaknesses PHASE 3 OF 6 Automated tools for

    breadth and coverage 03 Manual testing for depth: access control, business logic, chained bugs Logic flaws never appear in a scan report Kyeson Blake Utley · Six Phases of a Penetration Test 06 / 12
  6. Prove exploitation PHASE 4 OF 6 Every finding is demonstrated,

    not described Controlled, production-safe proof of impact 04 “Potentially vulnerable” is not a finding Kyeson Blake Utley · Six Phases of a Penetration Test 07 / 12
  7. Measure the blast radius PHASE 5 OF 6 05 From

    one foothold: privilege escalation and lateral movement How much data and which systems are actually reachable? Stop before anything is harmed Kyeson Blake Utley · Six Phases of a Penetration Test 08 / 12
  8. Report and re-test PHASE 6 OF 6 Plain-language summary for

    leadership 06 CVSS-scored findings with reproduction steps and a prioritized fix list Free re-test once fixes are in, with an attestation of the result Kyeson Blake Utley · Six Phases of a Penetration Test 09 / 12
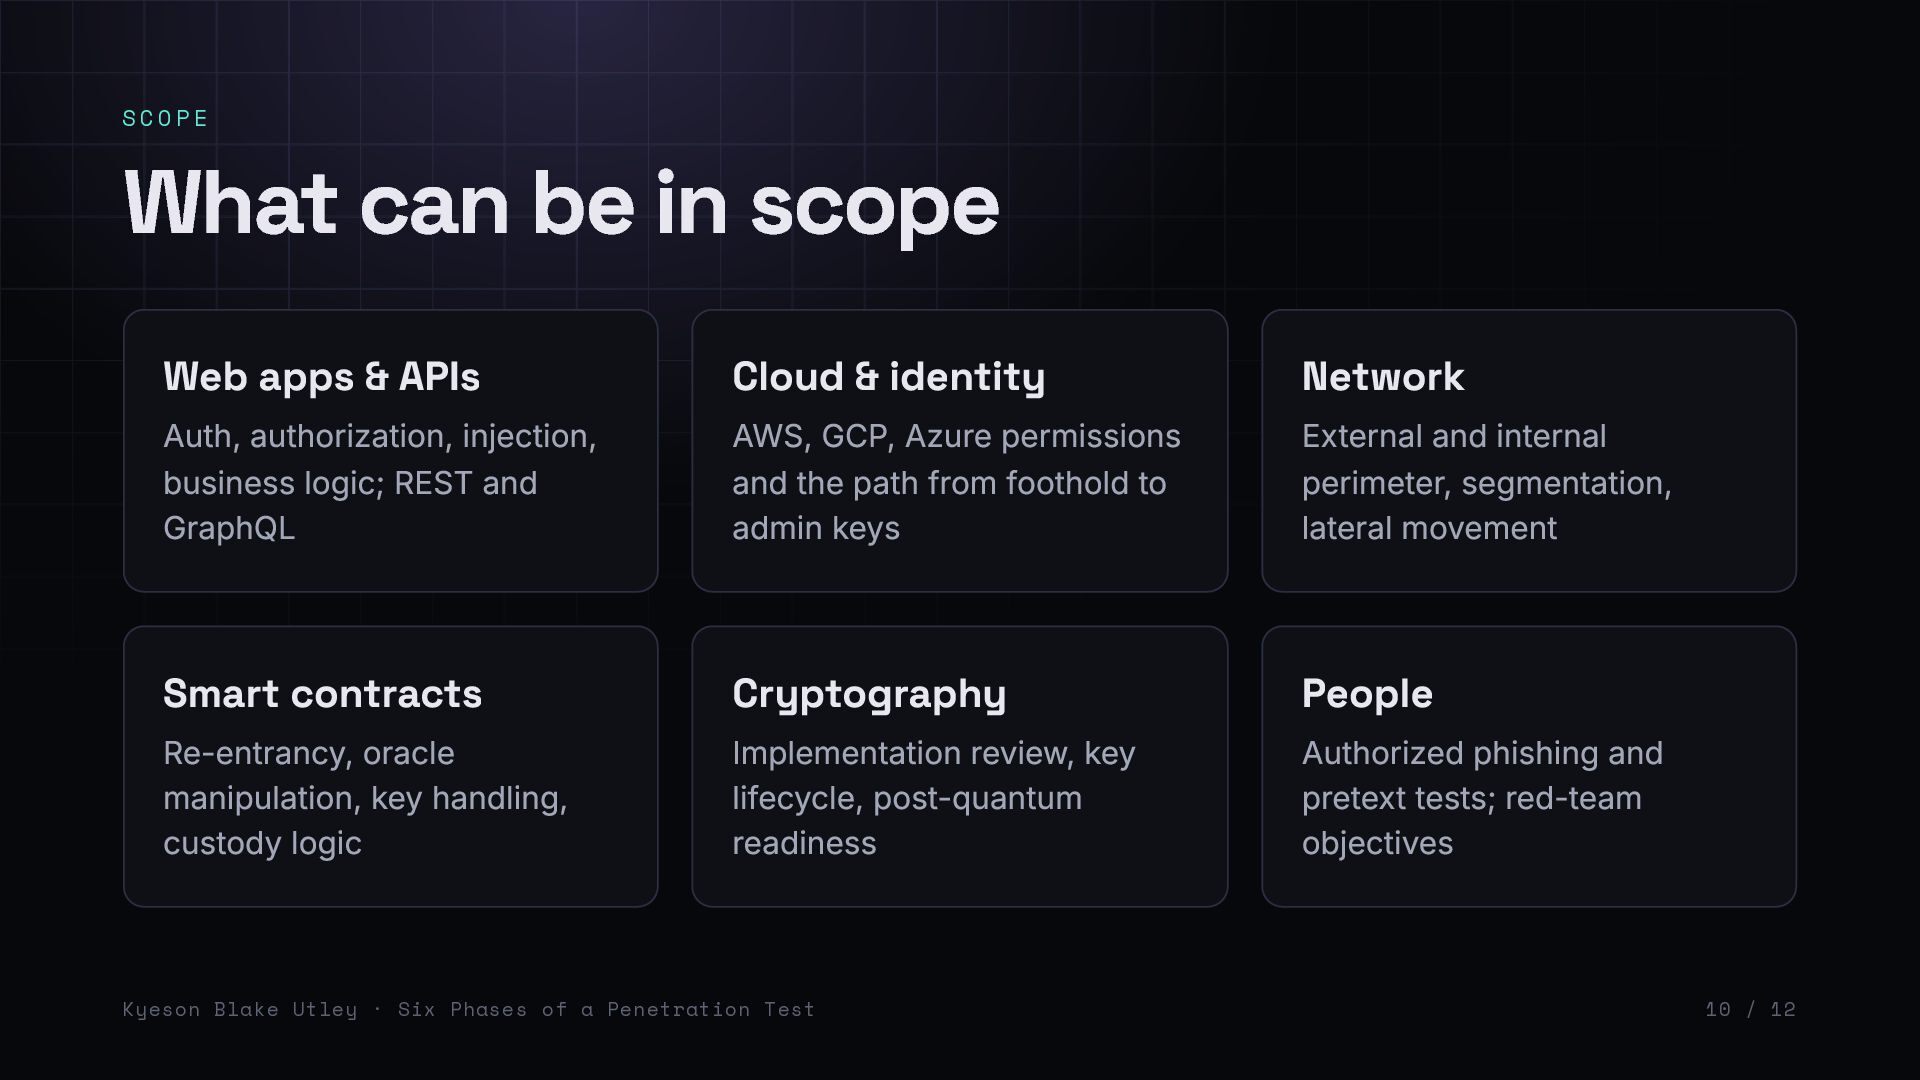
  9. What can be in scope SCOPE Web apps & APIs

    Cloud & identity Network Smart contracts Cryptography People Auth, authorization, injection, business logic; REST and GraphQL Re-entrancy, oracle manipulation, key handling, custody logic AWS, GCP, Azure permissions and the path from foothold to admin keys Implementation review, key lifecycle, post-quantum readiness Kyeson Blake Utley · Six Phases of a Penetration Test External and internal perimeter, segmentation, lateral movement Authorized phishing and pretext tests; red-team objectives 10 / 12
  10. Offense, under discipline RULES OF ENGAGEMENT Written authorization and an

    agreed scope before any testing starts. Agreed testing windows and emergency contacts; productionimpacting techniques need explicit sign-off. Findings and data stay confidential and are destroyed on an agreed schedule. Aligned to PTES, OWASP WSTG, MITRE ATT&CK and NIST SP 800-115, so results map to frameworks auditors already use. Kyeson Blake Utley · Six Phases of a Penetration Test 11 / 12
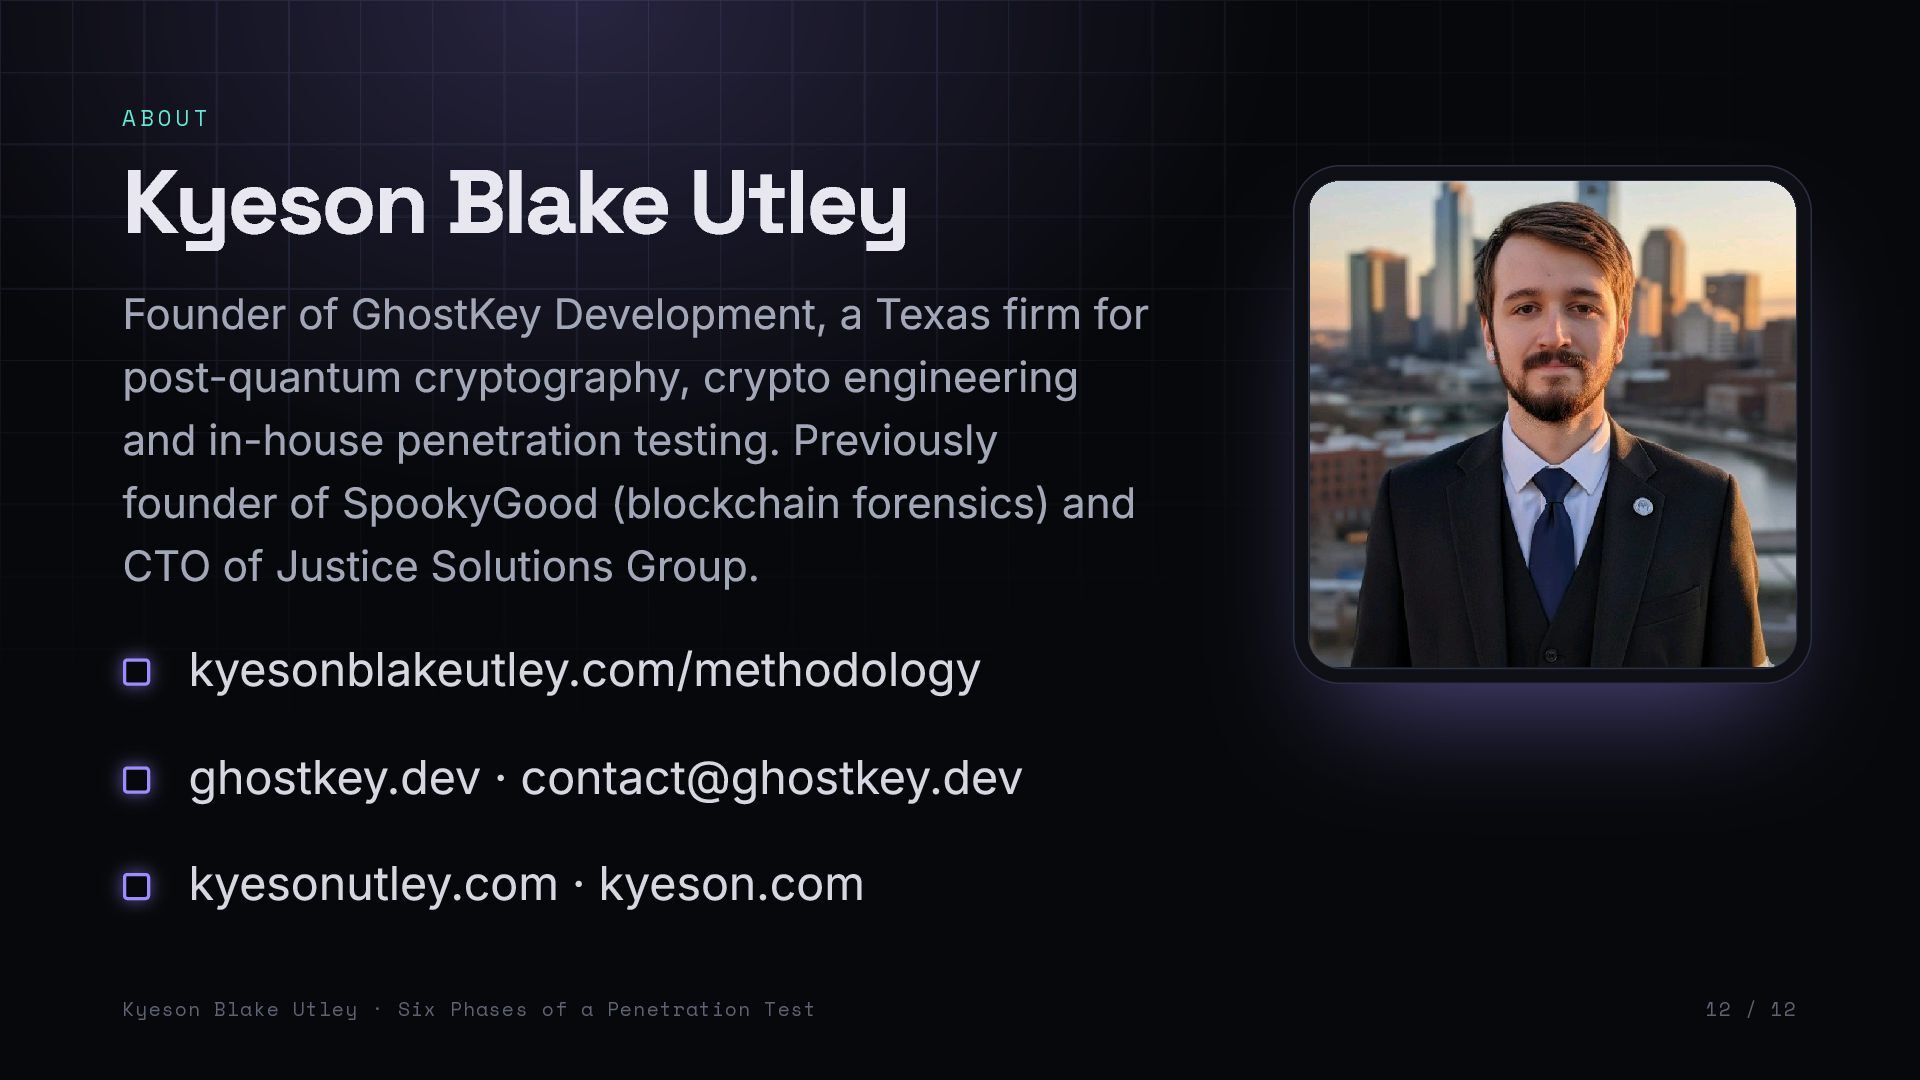
  11. Kyeson Blake Utley ABOUT Founder of GhostKey Development, a Texas

    firm for post-quantum cryptography, crypto engineering and in-house penetration testing. Previously founder of SpookyGood (blockchain forensics) and CTO of Justice Solutions Group. kyesonblakeutley.com/methodology ghostkey.dev · [email protected] kyesonutley.com · kyeson.com Kyeson Blake Utley · Six Phases of a Penetration Test 12 / 12