Upgrade to Pro — share decks privately, control downloads, hide ads and more …

Harvest Now, Decrypt Later: A Post-Quantum Migr...

Avatar for Kyeson Blake Utley Kyeson Blake Utley
October 05, 2026
8

Harvest Now, Decrypt Later: A Post-Quantum Migration Playbook by Kyeson Blake Utley

Why harvest-now-decrypt-later makes post-quantum migration urgent, what NIST's FIPS 203/204/205 standards change, the 2030 and 2035 deadlines, and a four-step migration method. By Kyeson Blake Utley, founder of GhostKey Development. White paper: https://doi.org/10.5281/zenodo.23177774

Avatar for Kyeson Blake Utley

Kyeson Blake Utley

October 05, 2026

Transcript

  1. Harvest Now, Decrypt Later P O S T- Q U

    A N T U M P L AY B O O K A practical migration playbook for engineering teams. KU Kyeson Blake Utley Founder, GhostKey Development · kyesonutley.com Kyeson Blake Utley · Harvest Now, Decrypt Later 01 / 13
  2. The attack has already started. T H E T H

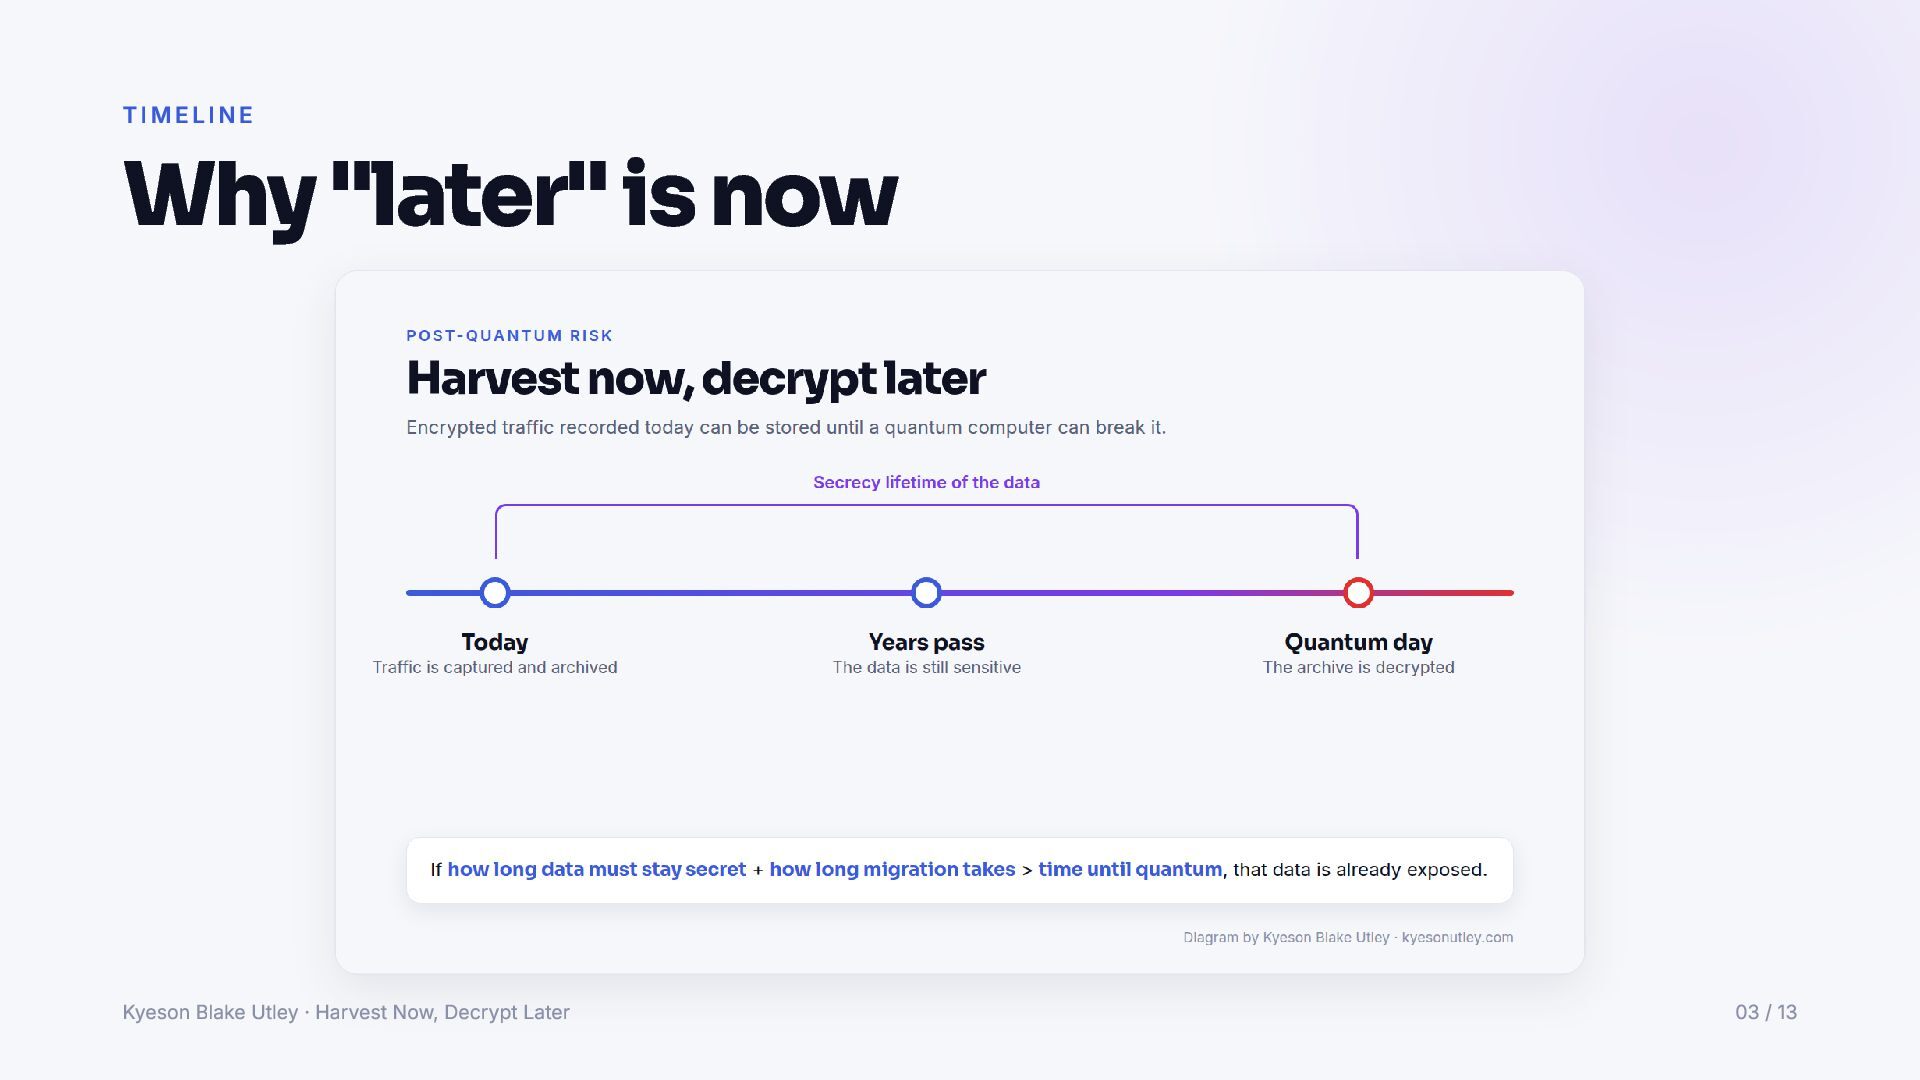
    R E AT Adversaries can record encrypted traffic today and store it. Once a cryptographically relevant quantum computer exists, RSA and elliptic-curve key exchange fall to Shor's algorithm. Anything captured before migration is decryptable later, no matter how strong it looked at the time. Kyeson Blake Utley · Harvest Now, Decrypt Later 02 / 13
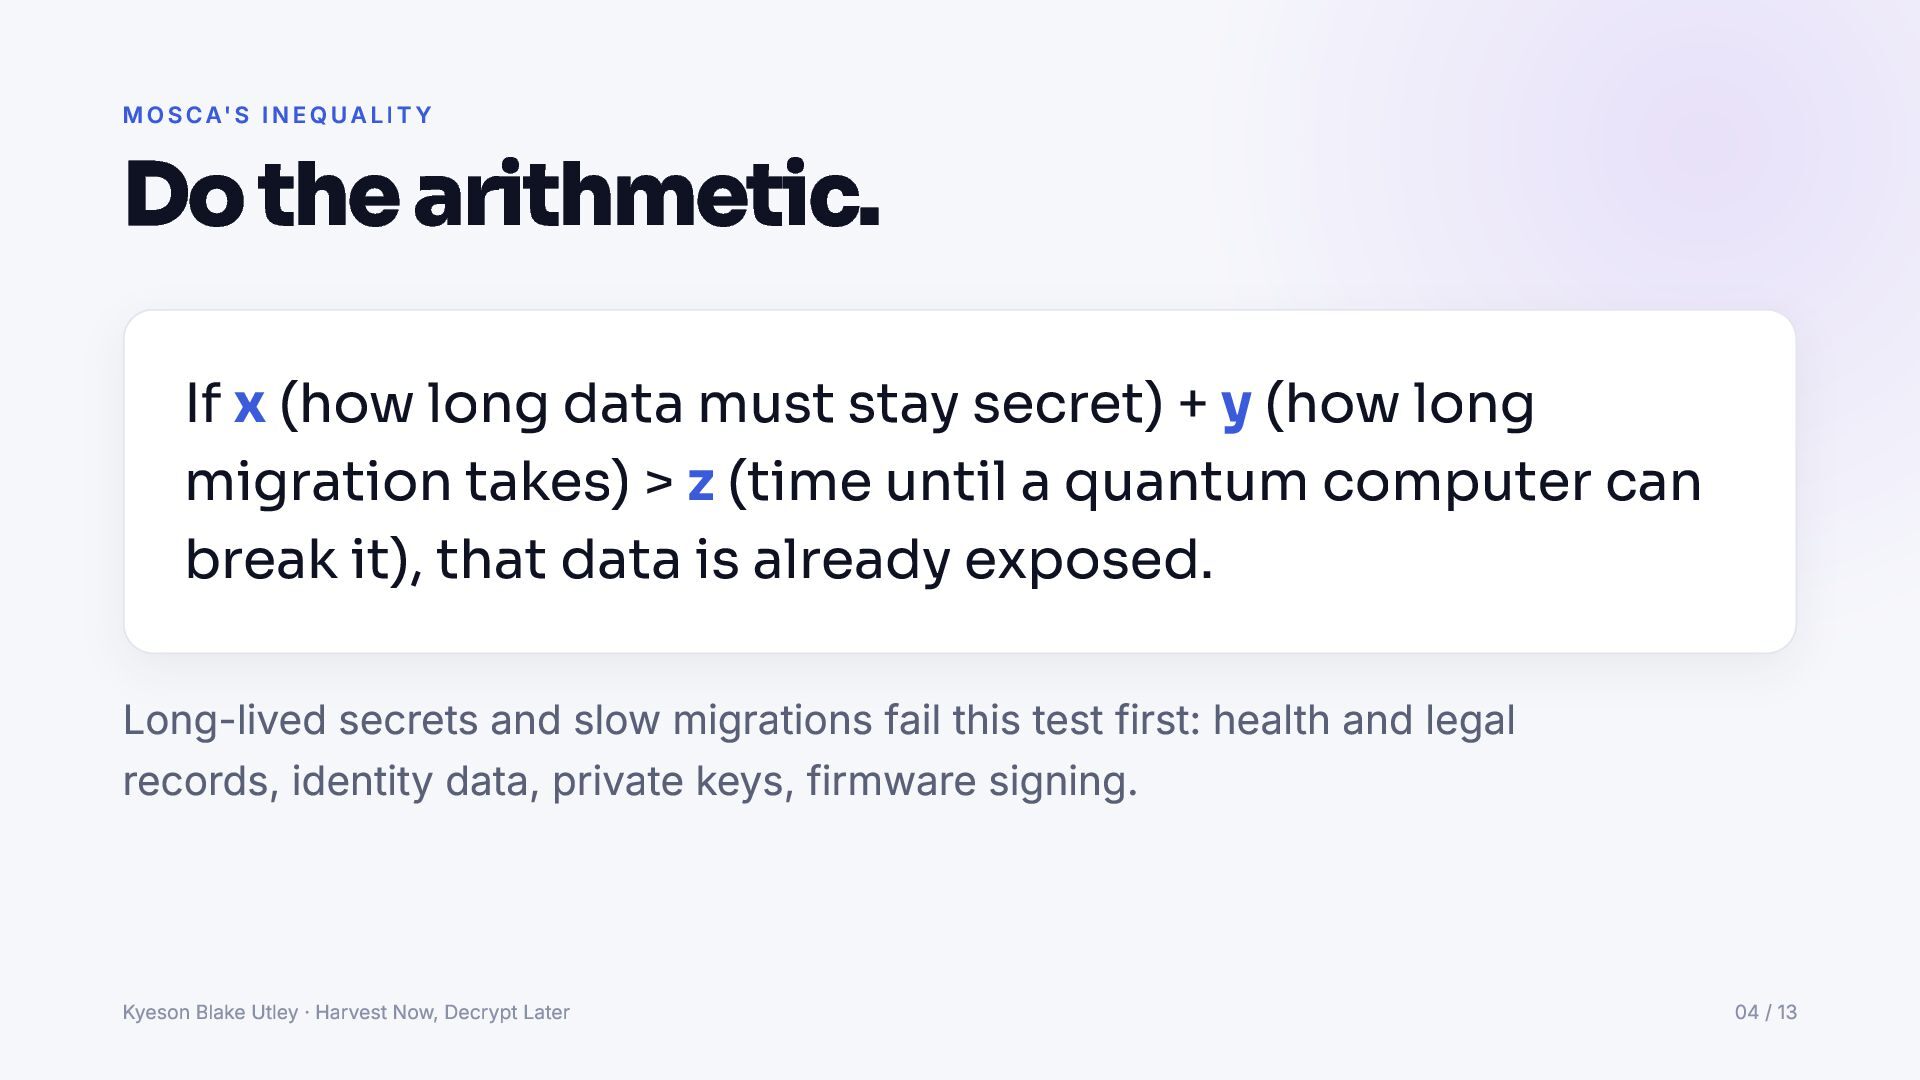
  3. Do the arithmetic. M O S C A' S I

    N E Q U A L I T Y If x (how long data must stay secret) + y (how long migration takes) > z (time until a quantum computer can break it), that data is already exposed. Long-lived secrets and slow migrations fail this test first: health and legal records, identity data, private keys, firmware signing. Kyeson Blake Utley · Harvest Now, Decrypt Later 04 / 13
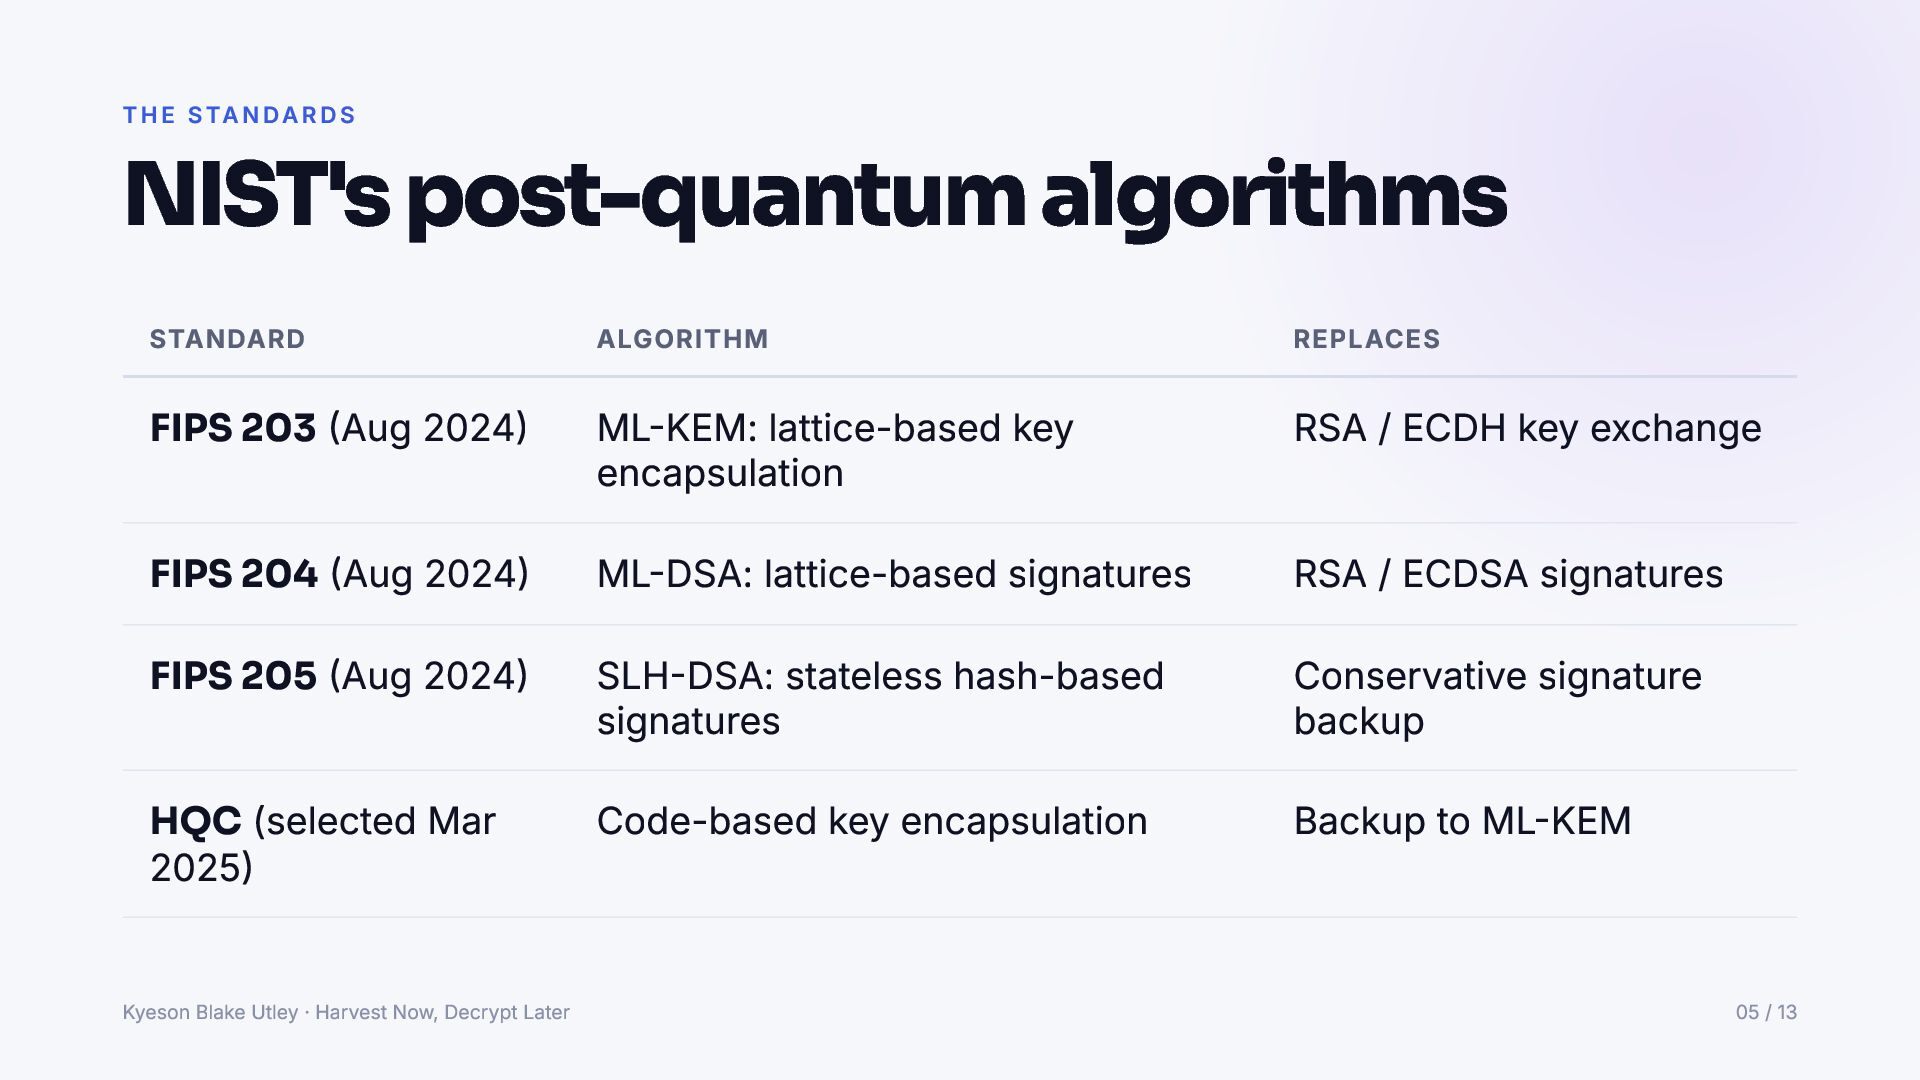
  4. NIST's post-quantum algorithms T H E S TA N DA

    R D S STANDARD ALGORITHM REPLACES FIPS 203 (Aug 2024) ML-KEM: lattice-based key encapsulation RSA / ECDH key exchange FIPS 204 (Aug 2024) ML-DSA: lattice-based signatures RSA / ECDSA signatures FIPS 205 (Aug 2024) SLH-DSA: stateless hash-based signatures Conservative signature backup HQC (selected Mar Code-based key encapsulation Backup to ML-KEM 2025) Kyeson Blake Utley · Harvest Now, Decrypt Later 05 / 13
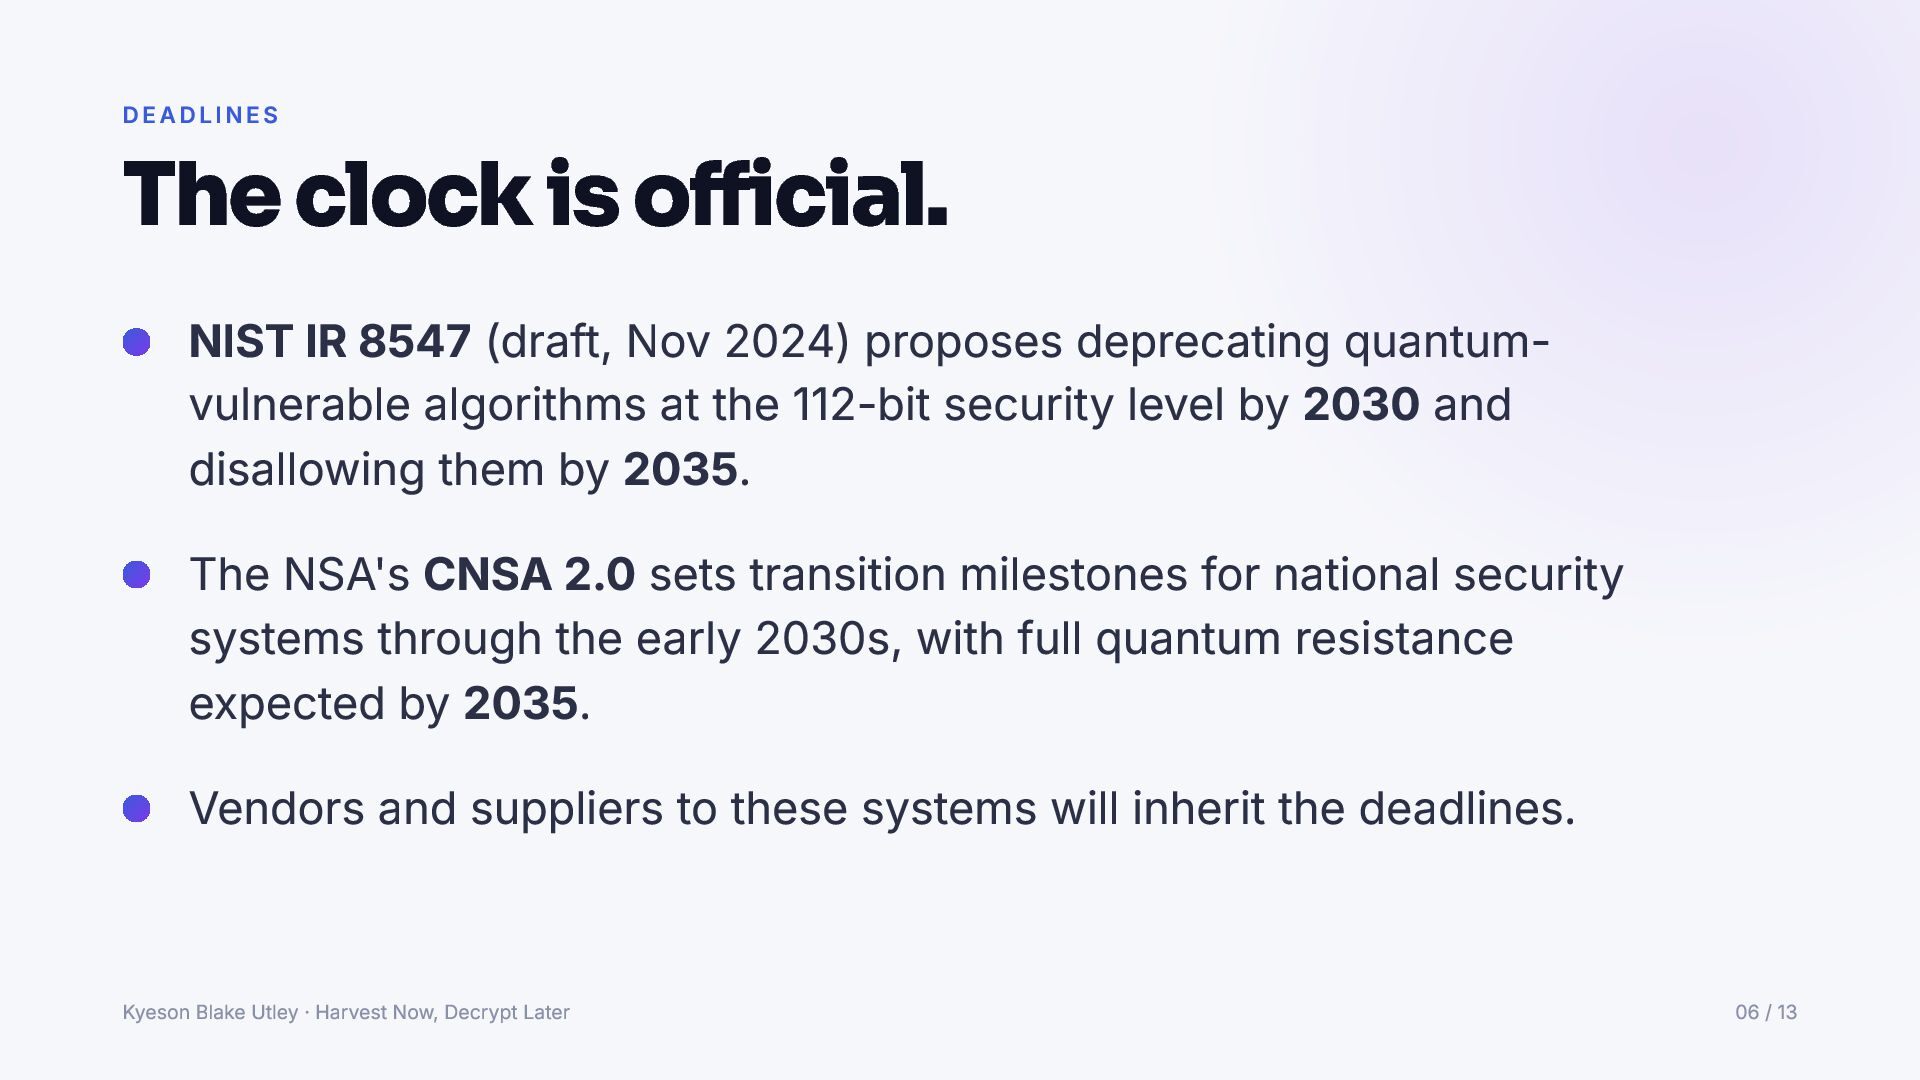
  5. The clock is official. DEADLINES NIST IR 8547 (draft, Nov

    2024) proposes deprecating quantumvulnerable algorithms at the 112-bit security level by 2030 and disallowing them by 2035. The NSA's CNSA 2.0 sets transition milestones for national security systems through the early 2030s, with full quantum resistance expected by 2035. Vendors and suppliers to these systems will inherit the deadlines. Kyeson Blake Utley · Harvest Now, Decrypt Later 06 / 13
  6. 1. Inventory M I G R AT I O N

    S T E P Find every use of key exchange and signatures: TLS terminators, VPNs, SSH, code signing, wallet software, service meshes, HSMs. You can't migrate what you haven't found. Kyeson Blake Utley · Harvest Now, Decrypt Later 07 / 13
  7. 2. Prioritize by secrecy lifetime M I G R AT

    I O N S T E P Rank systems by how long their data must stay secret, not by how important they feel. A quiet archive link can matter more than a busy API. Kyeson Blake Utley · Harvest Now, Decrypt Later 08 / 13
  8. 3. Go hybrid M I G R AT I O

    N S T E P Pair a classical algorithm with ML-KEM (for example X25519 + ML-KEM-768 in TLS 1.3). You stay safe if either one is broken. Major browsers and messaging apps already ship this. Kyeson Blake Utley · Harvest Now, Decrypt Later 09 / 13
  9. 4. Build crypto-agility M I G R AT I O

    N S T E P Isolate cryptography behind interfaces and configuration. The algorithms will change again; hard-coded primitives mean paying for migration twice. Kyeson Blake Utley · Harvest Now, Decrypt Later 10 / 13
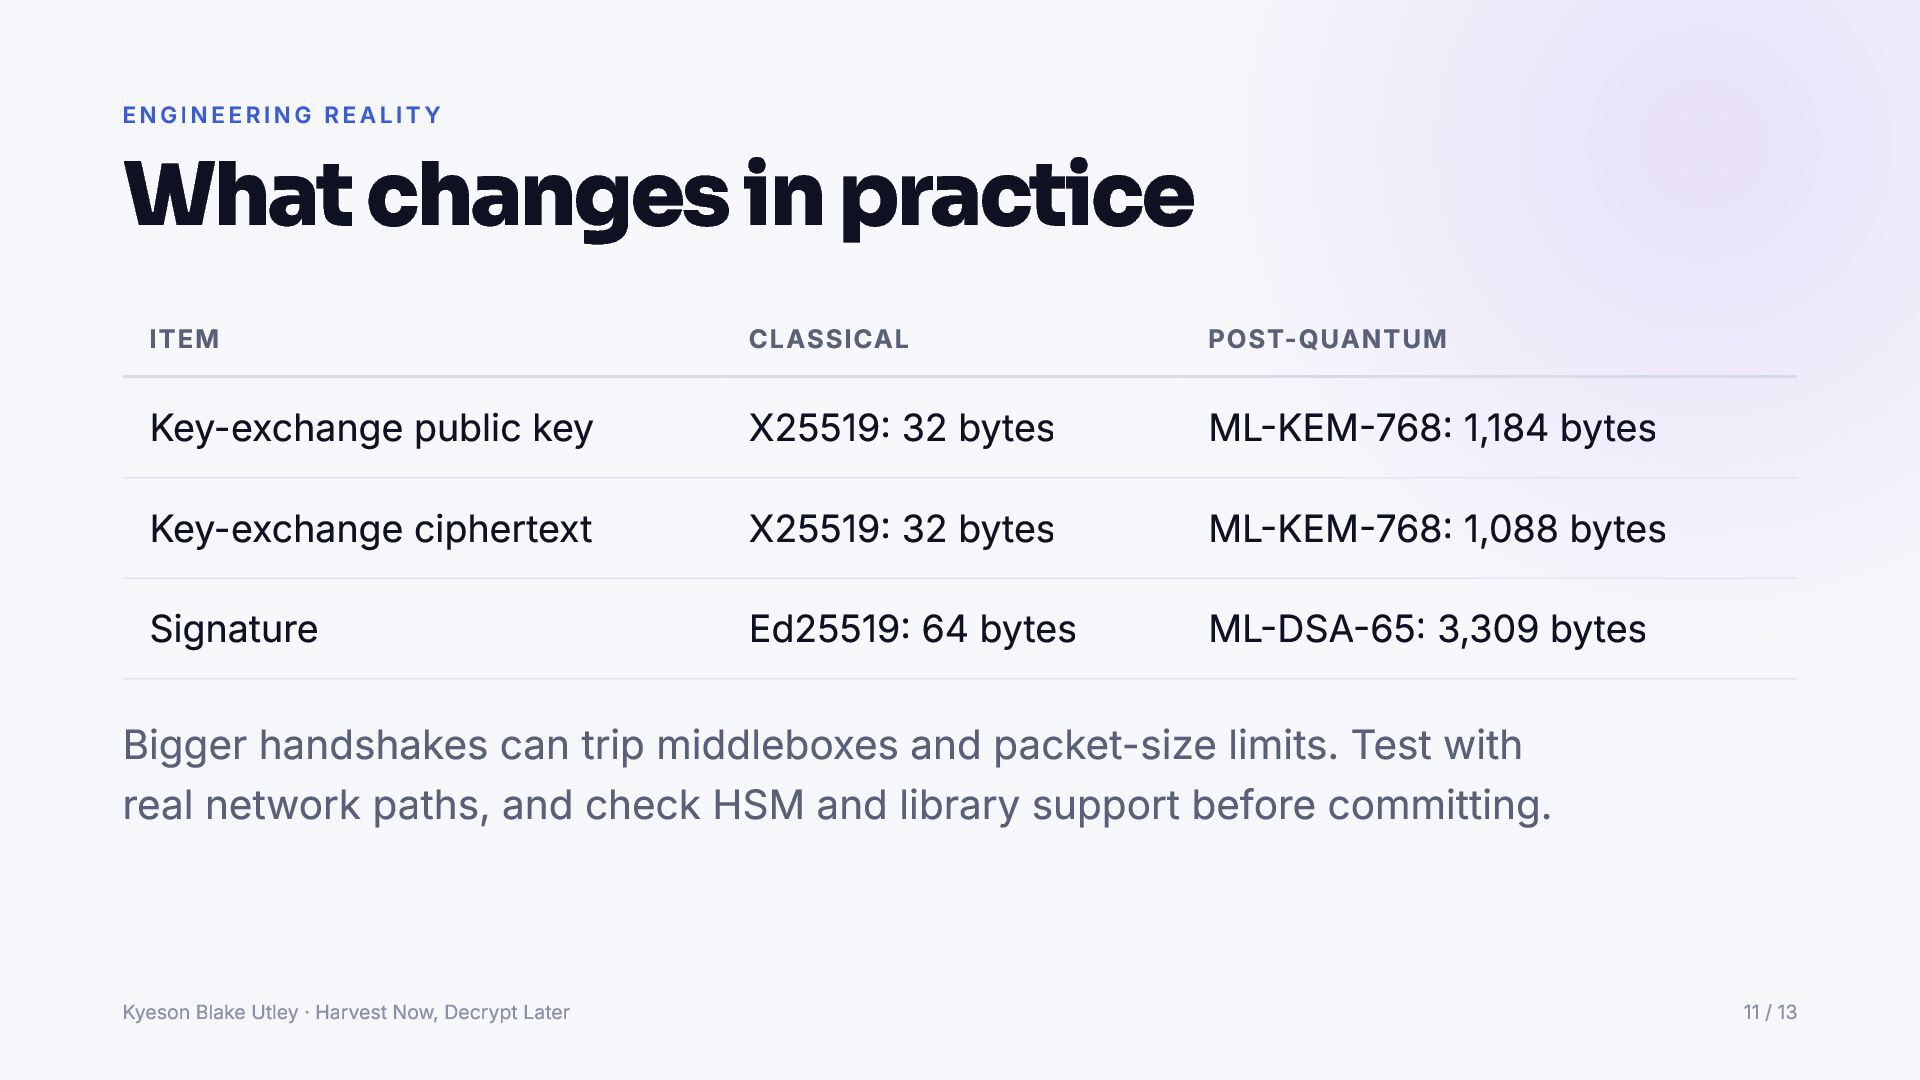
  10. What changes in practice ENGINEERING REALITY ITEM CLASSICAL POST-QUANTUM Key-exchange

    public key X25519: 32 bytes ML-KEM-768: 1,184 bytes Key-exchange ciphertext X25519: 32 bytes ML-KEM-768: 1,088 bytes Signature Ed25519: 64 bytes ML-DSA-65: 3,309 bytes Bigger handshakes can trip middleboxes and packet-size limits. Test with real network paths, and check HSM and library support before committing. Kyeson Blake Utley · Harvest Now, Decrypt Later 11 / 13
  11. Implementation fails, not math. THE REAL RISK New code means

    new side channels: verify constant-time behavior in the compiled binary, not the source. Use well-maintained libraries (for example OpenSSL 3.5+, which ships ML-KEM, ML-DSA and SLH-DSA) instead of writing your own. Audit the integration: key handling, downgrade paths and fallback logic are where migrations break. Kyeson Blake Utley · Harvest Now, Decrypt Later 12 / 13
  12. Kyeson Blake Utley ABOUT Founder of GhostKey Development, a Texas

    engineering firm for post-quantum cryptography, cryptocurrency engineering and in-house penetration testing. Read the full white paper at kyesonutley.com ghostkey.dev · [email protected] kyesonblakeutley.com · kyeson.com Kyeson Blake Utley · Harvest Now, Decrypt Later 13 / 13