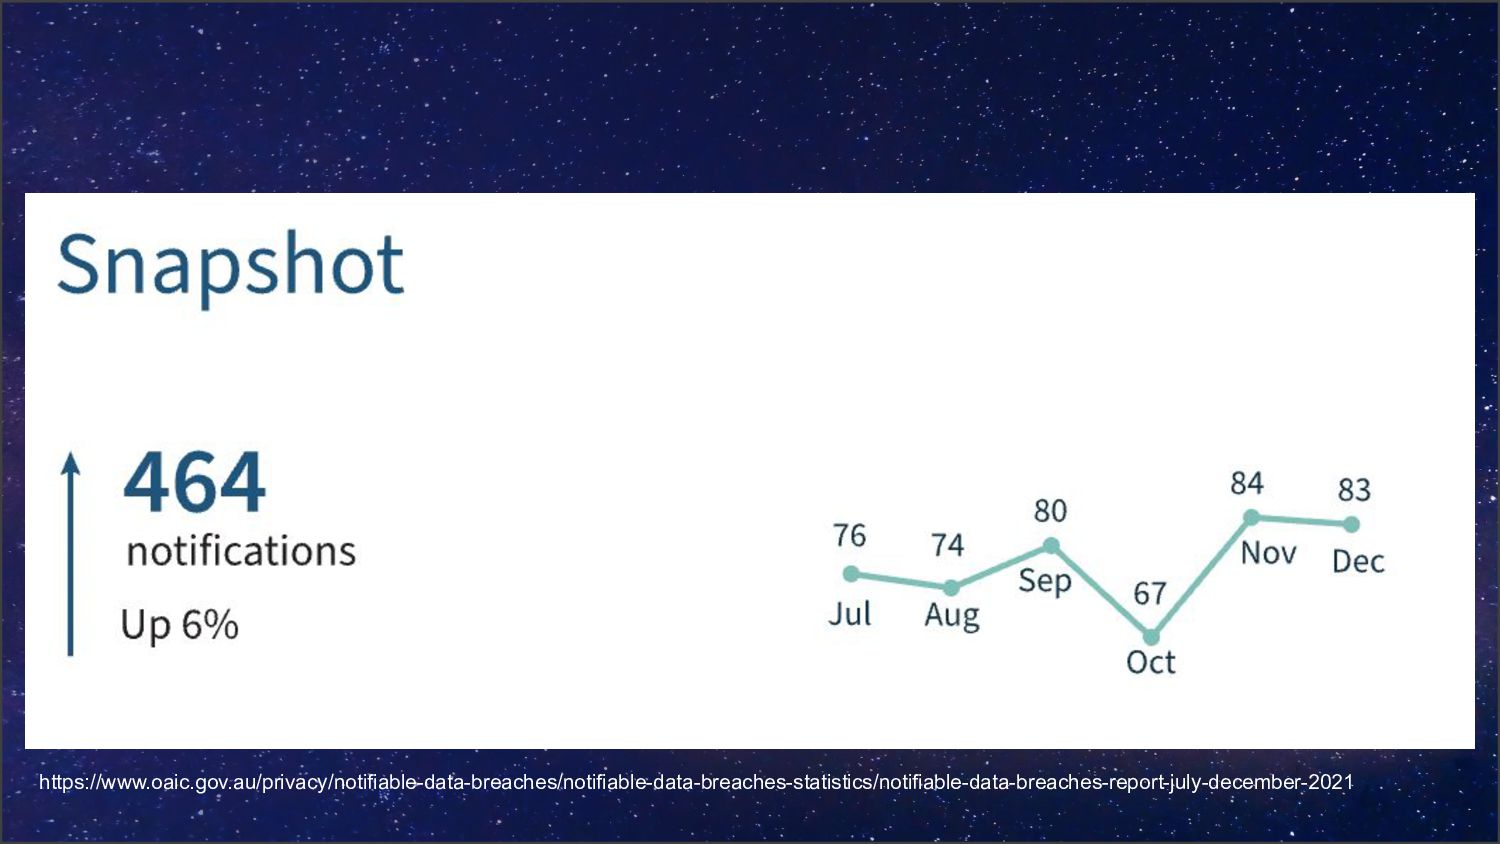
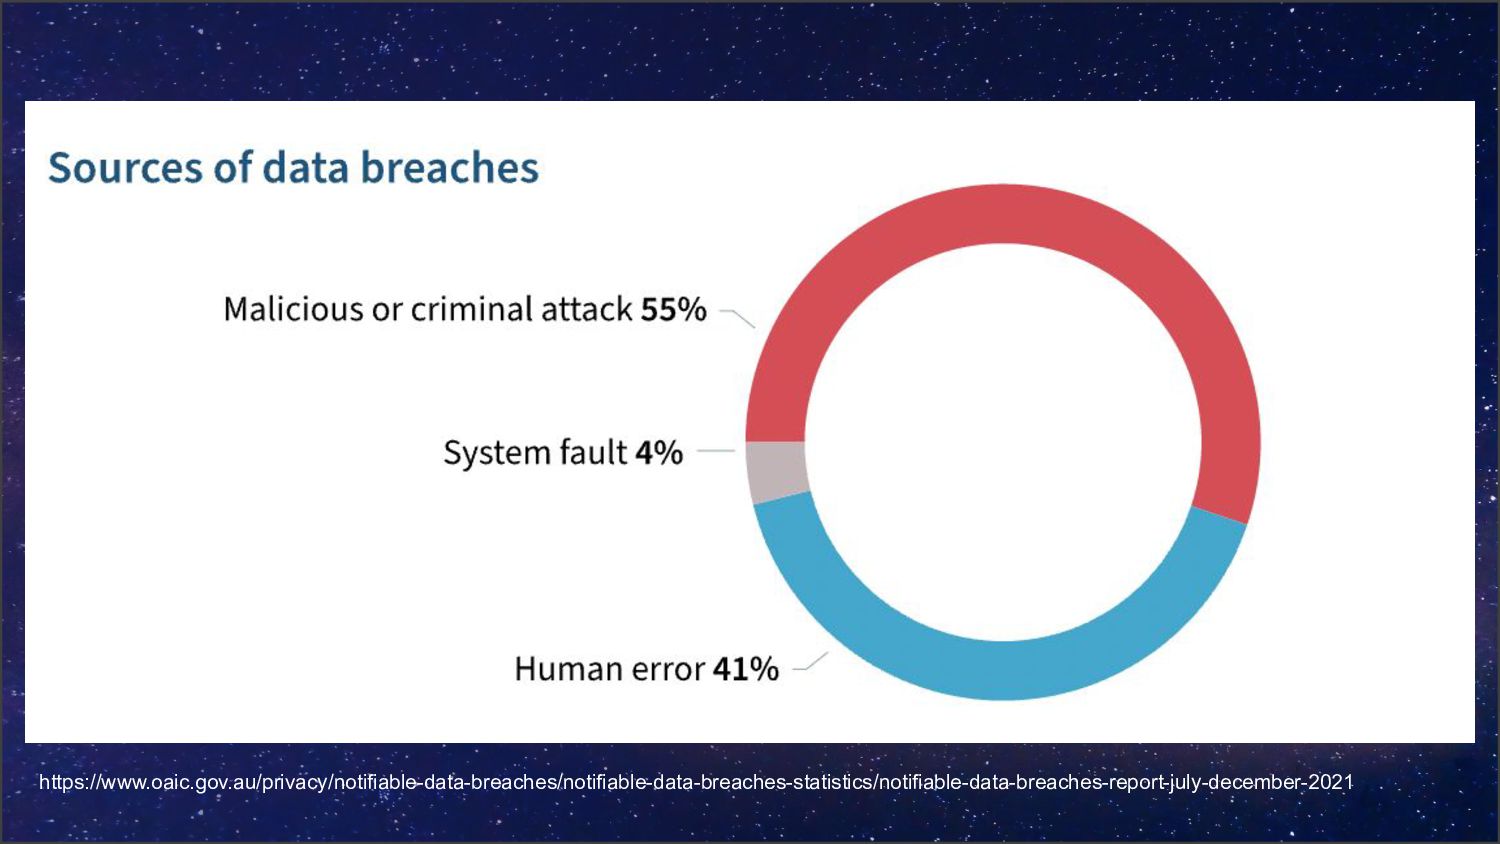
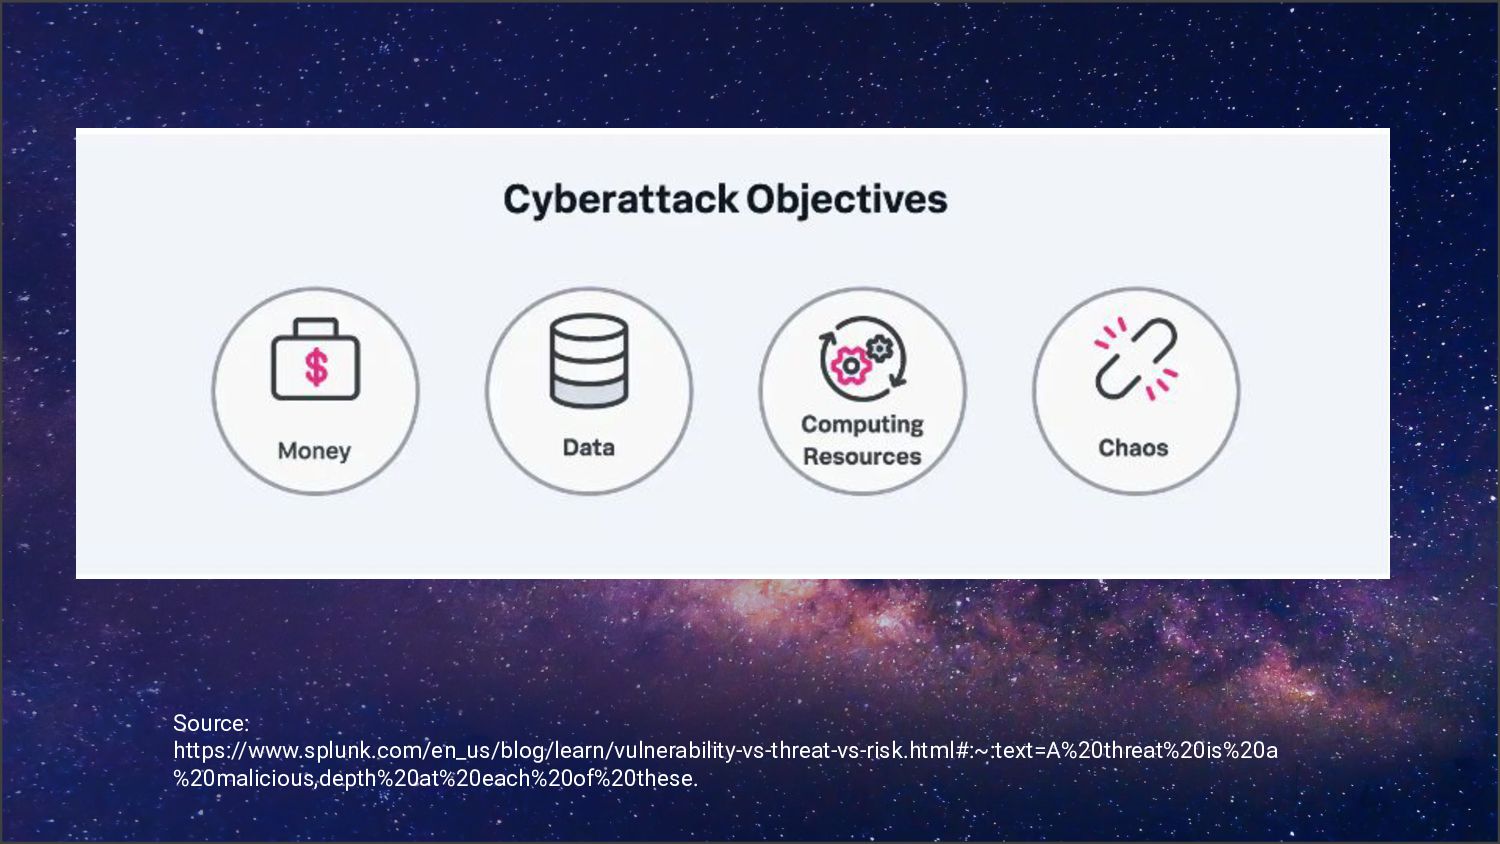
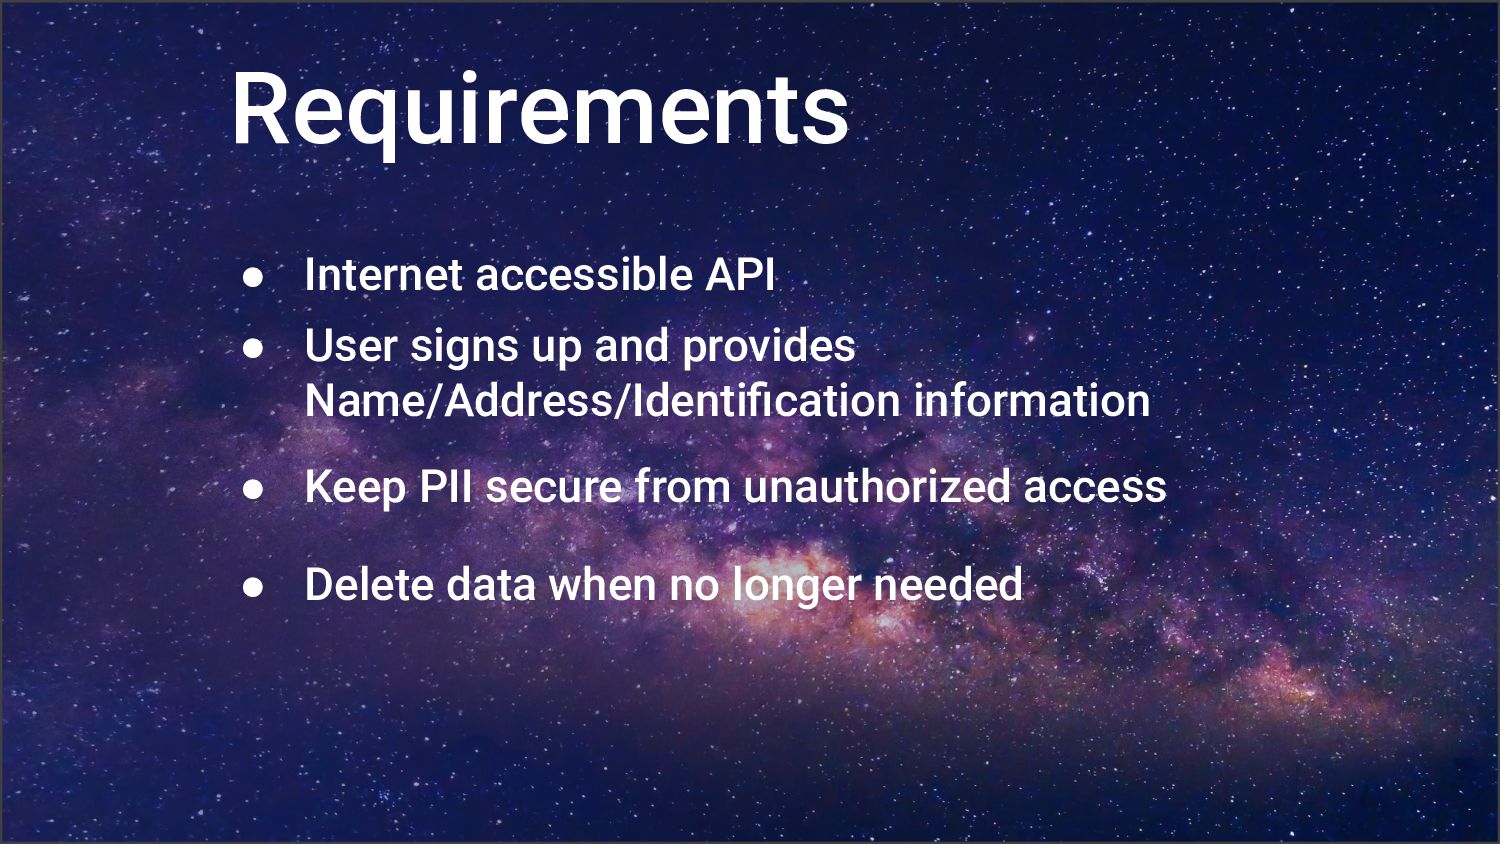
Current events have put the unauthorised access of customer personal information in the spotlight like never before. A lot of these breaches should never have happened if basic security best practices are implemented.
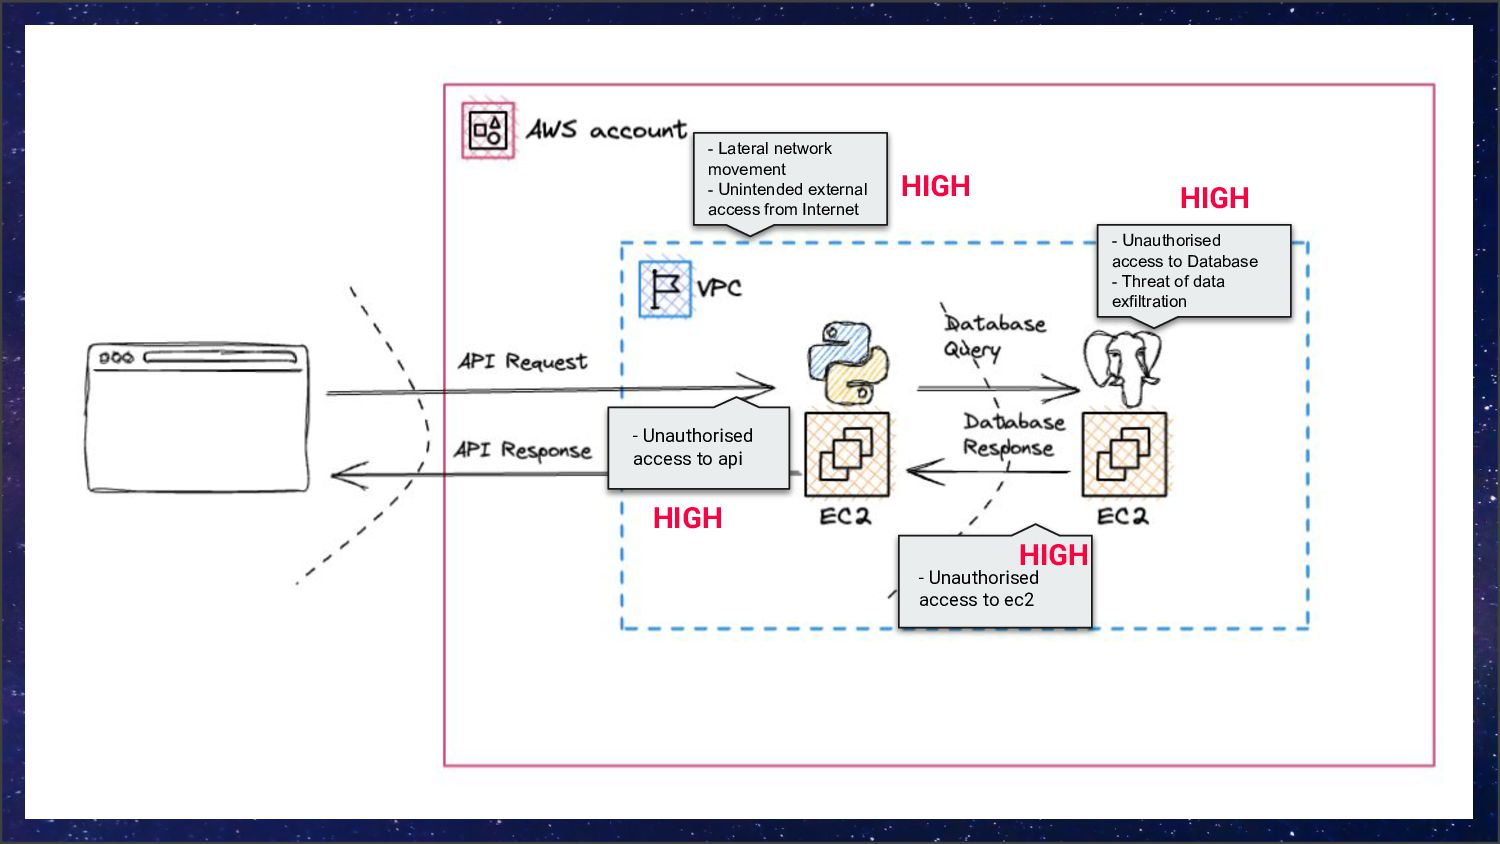
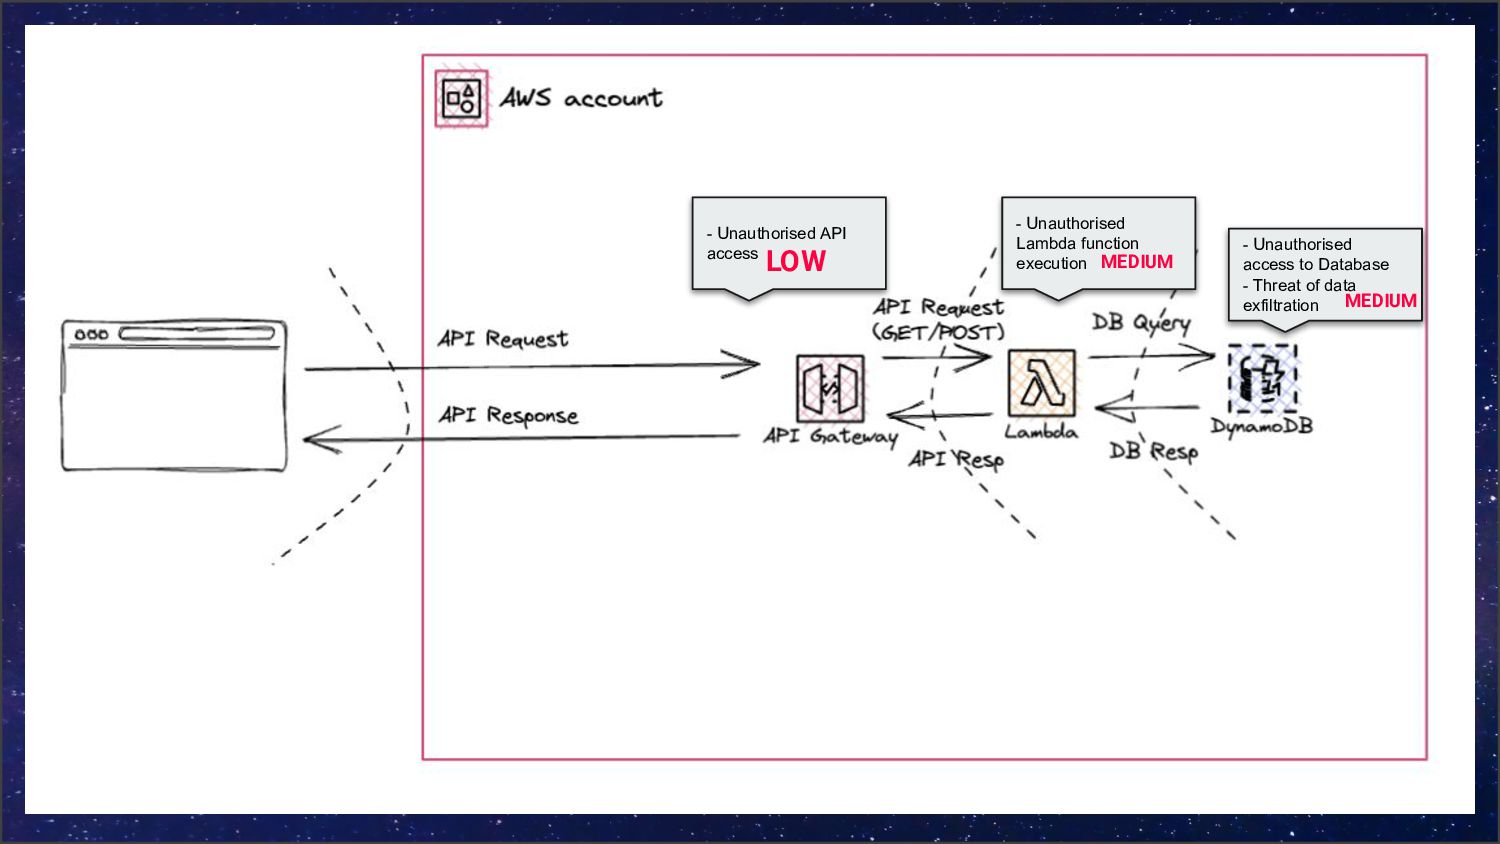
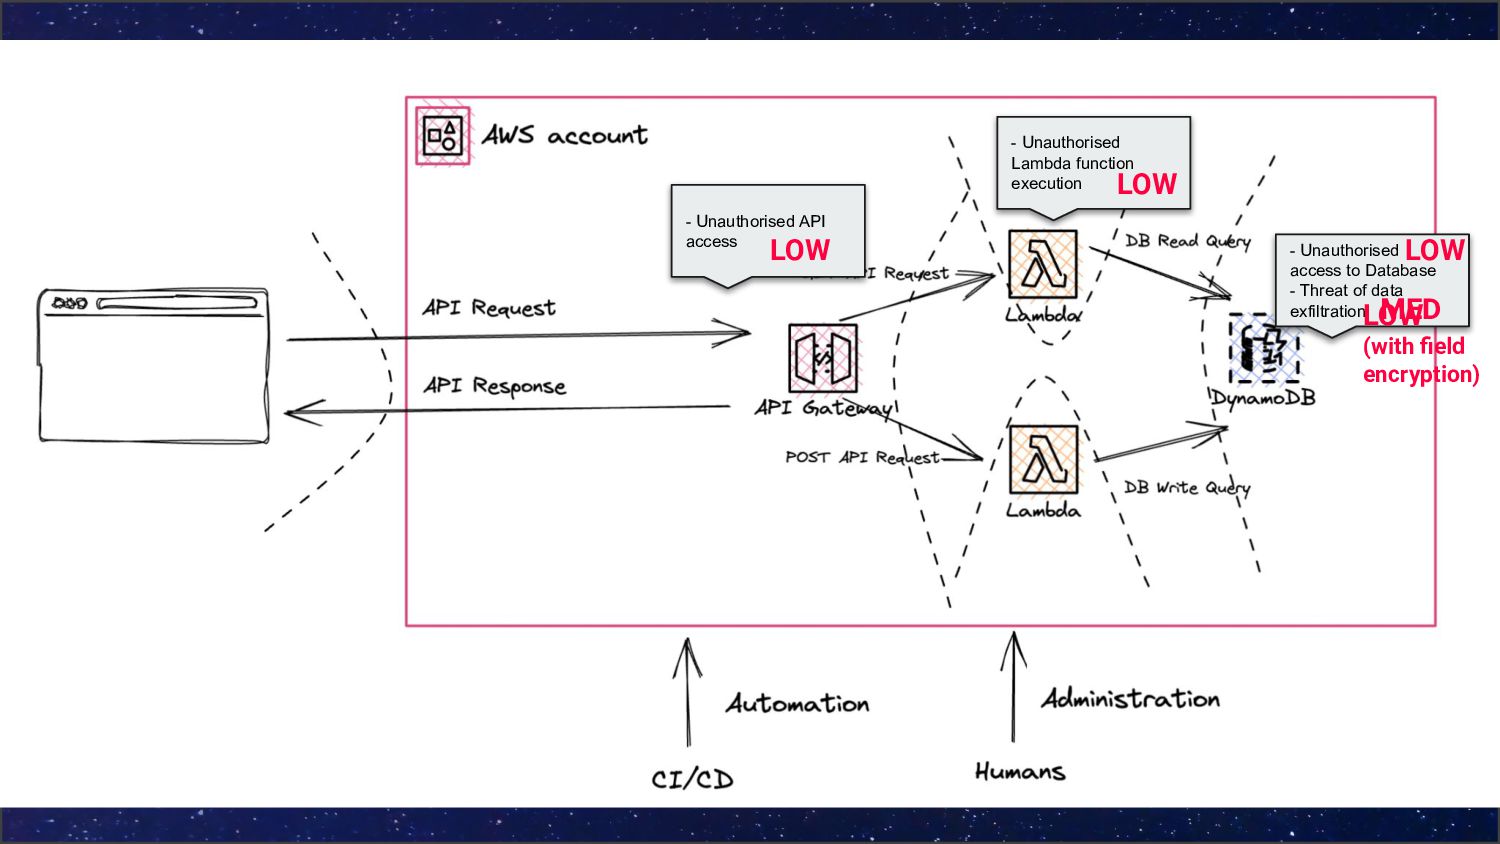
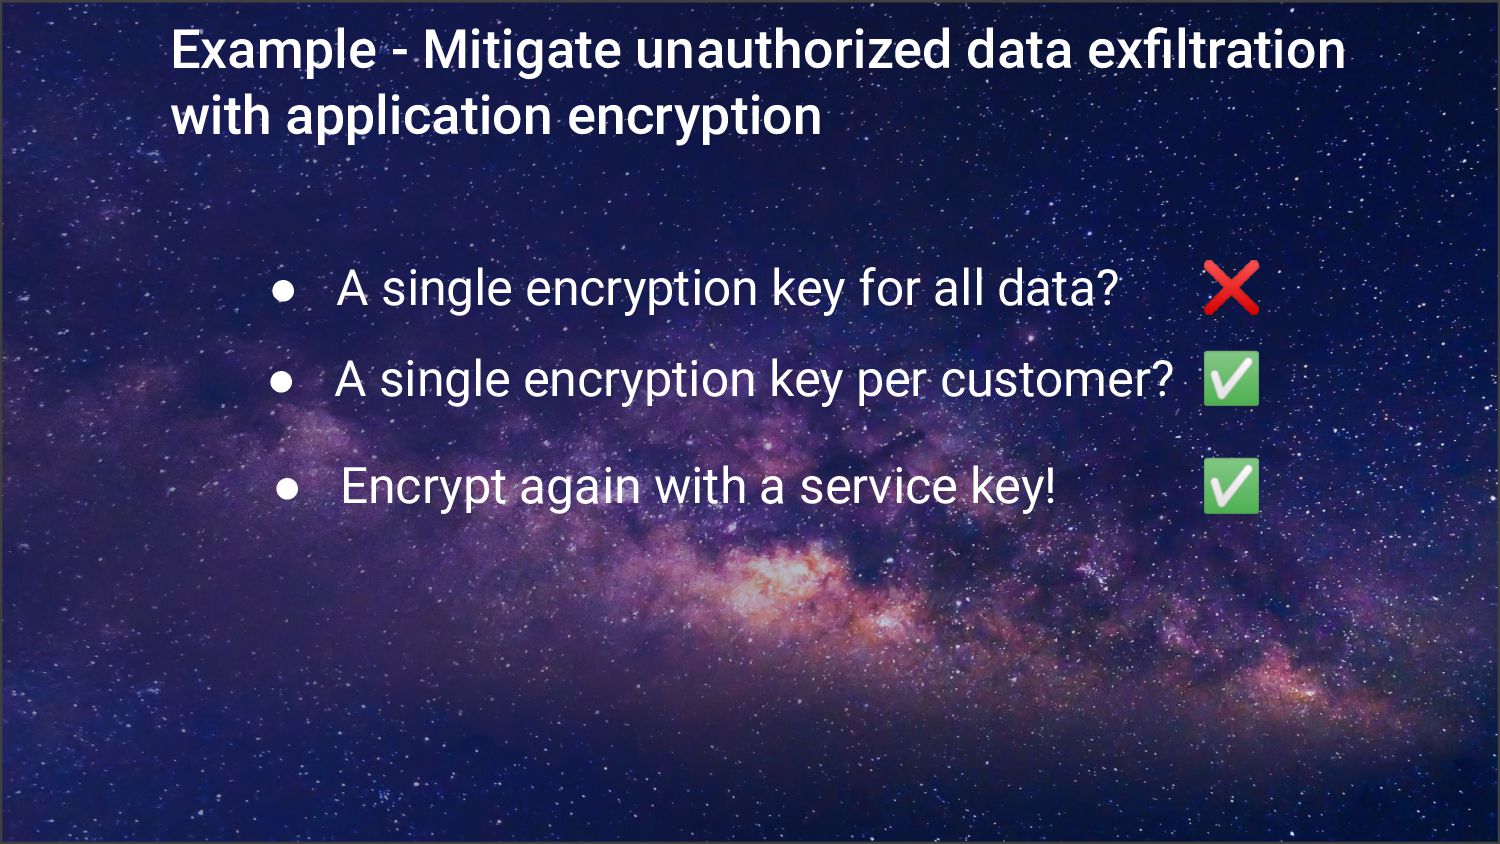
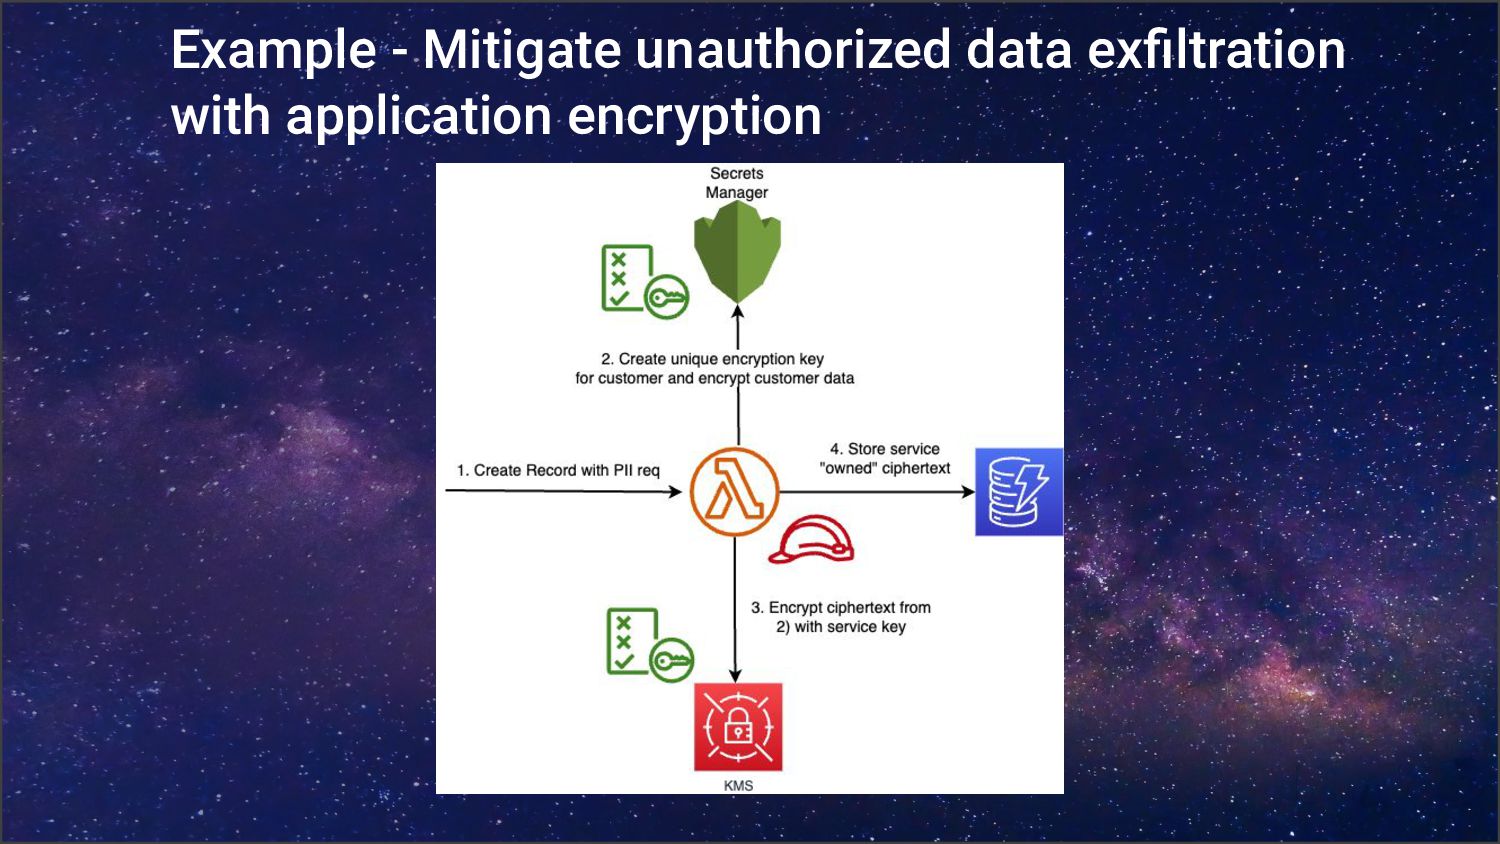
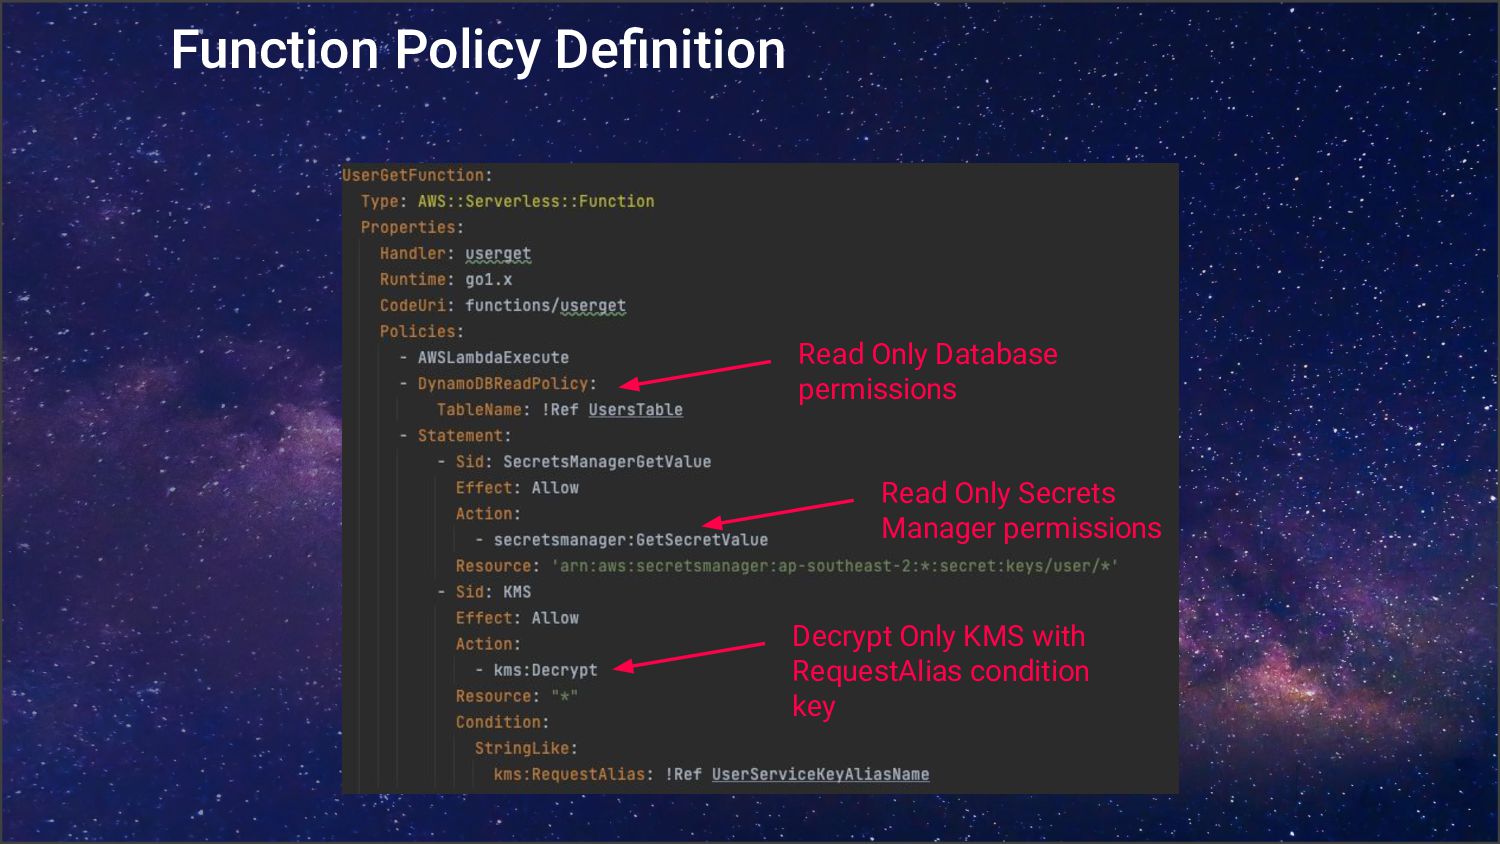
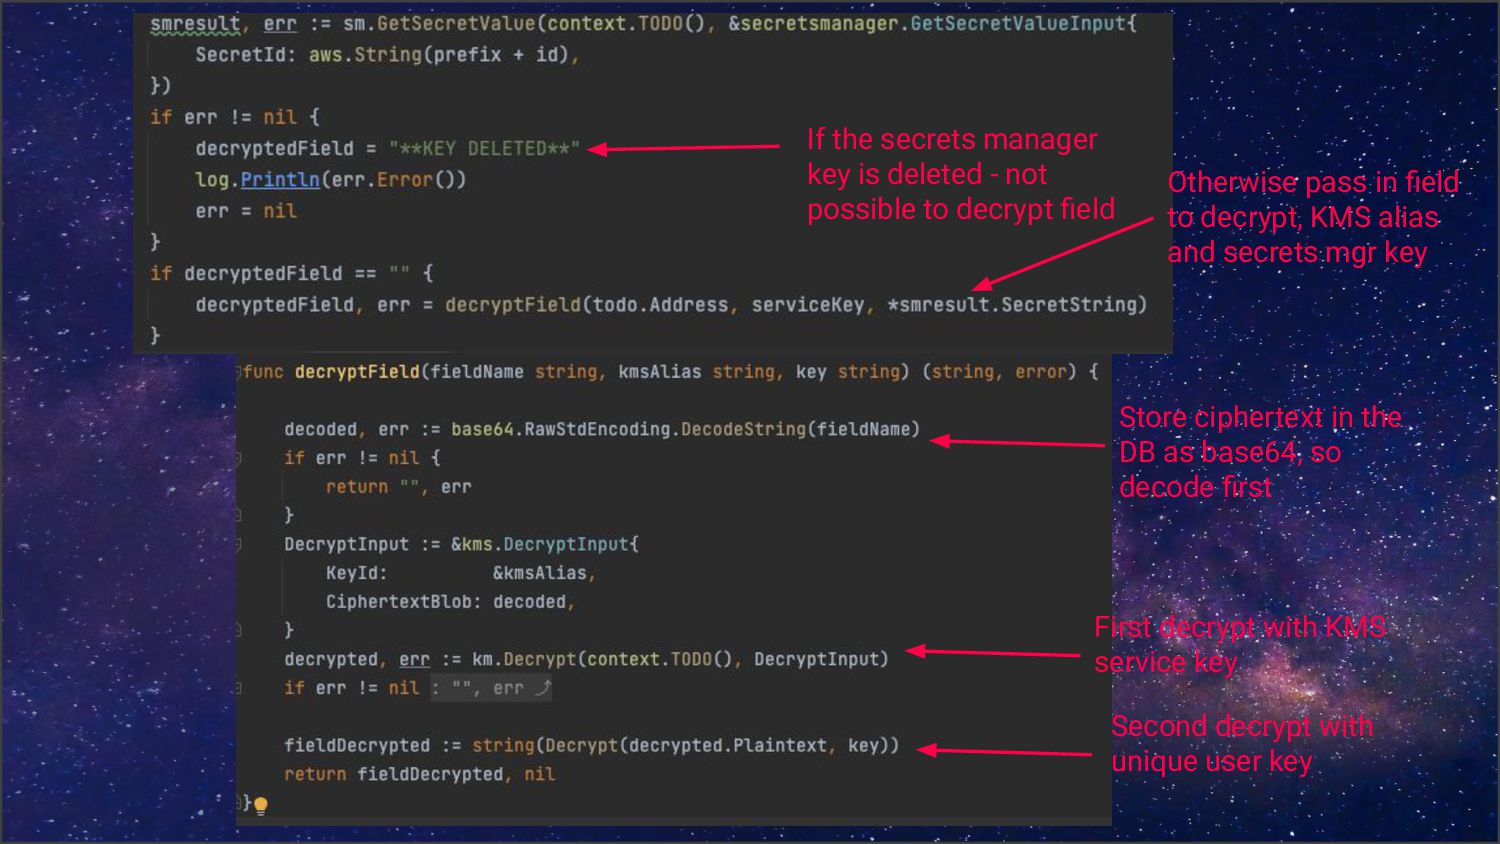
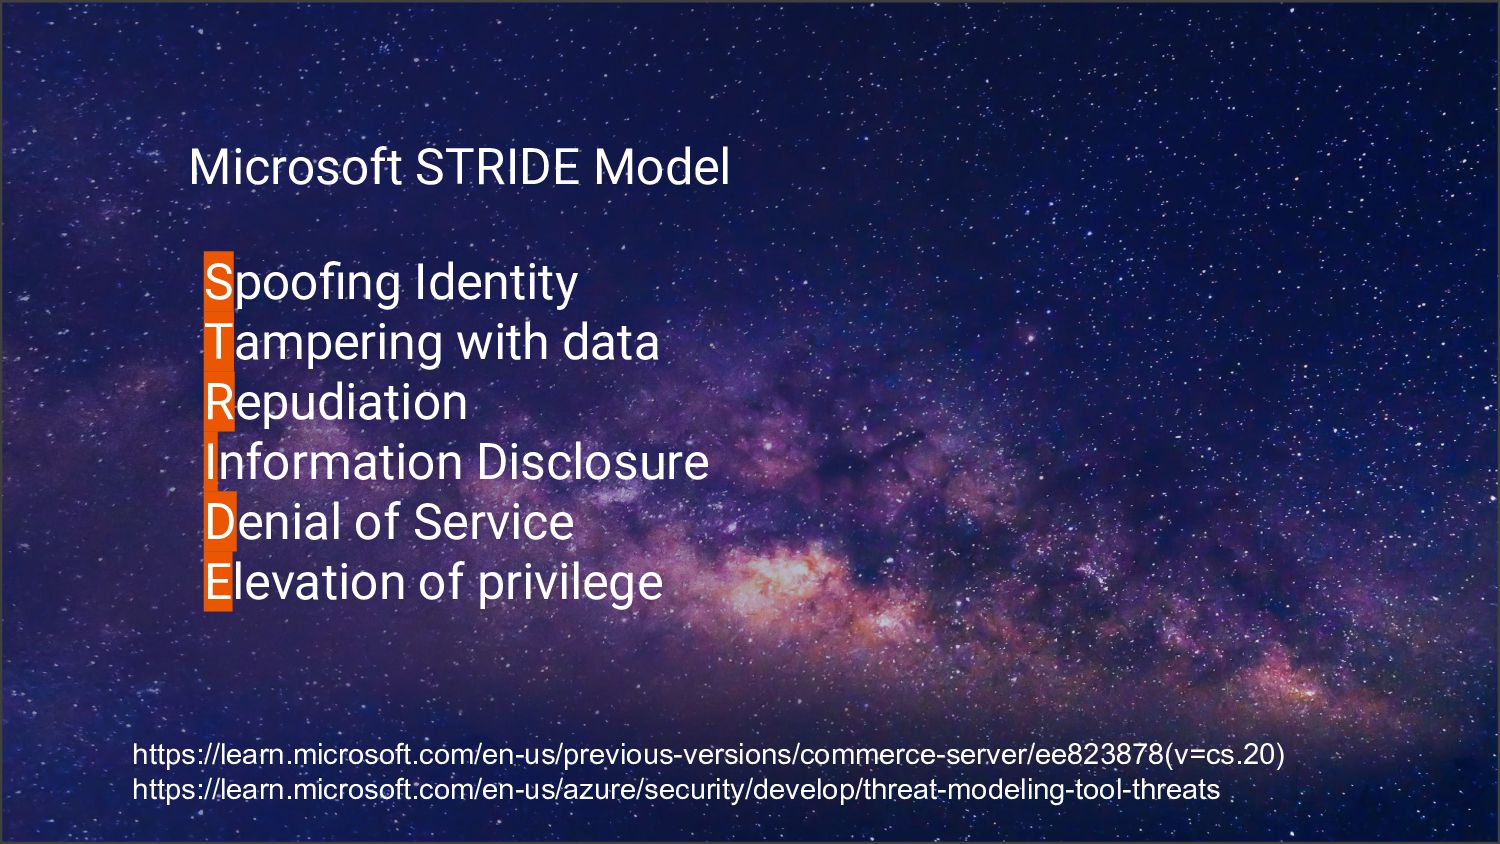
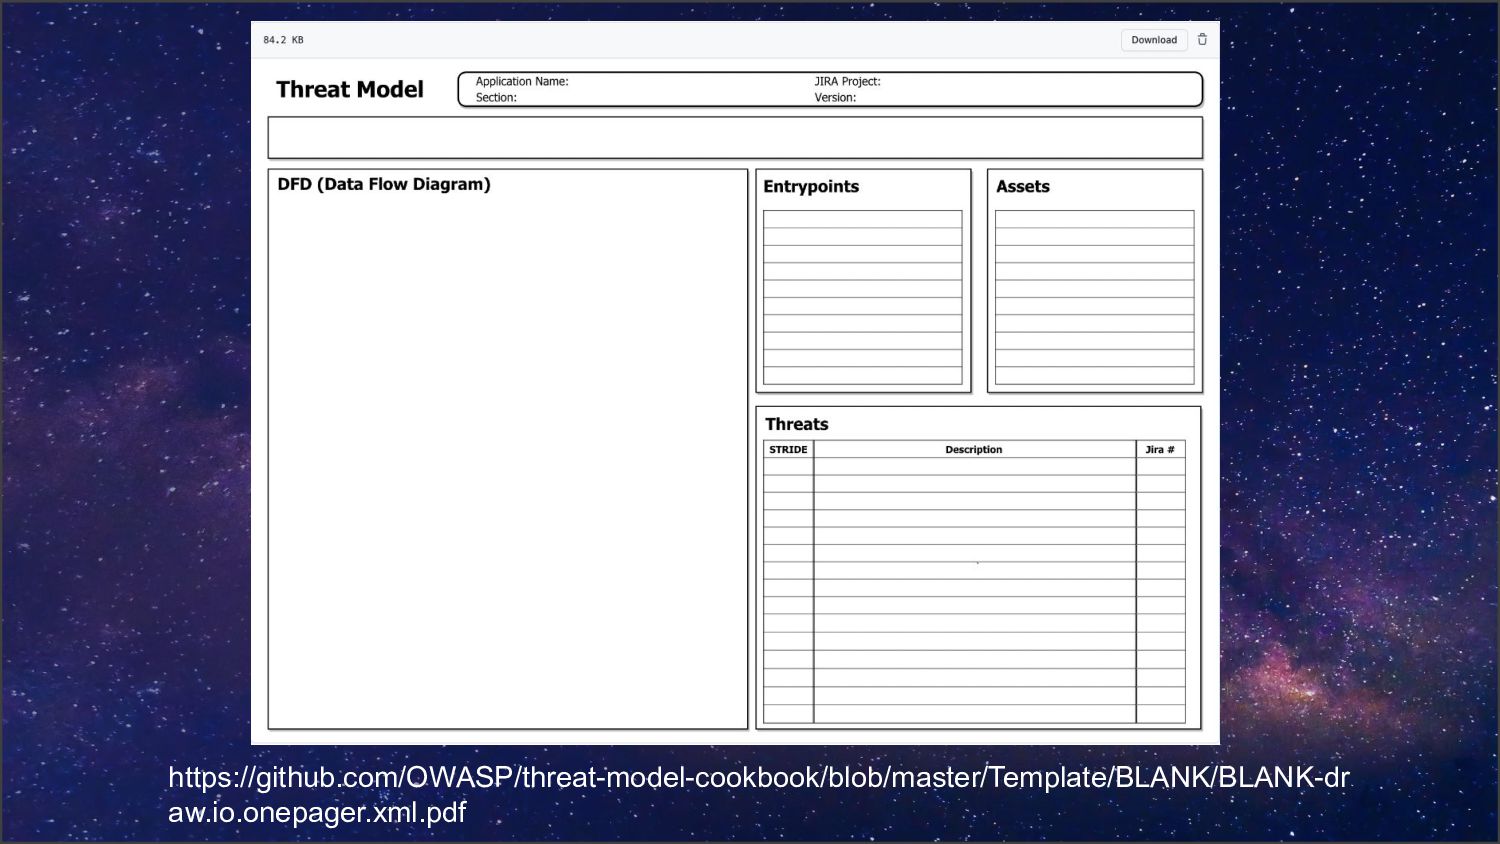
In this session we will run through an overview of how to threat model a fictitious organisations API and describe ways to mitigate risk to stop unintentional access by third parties. While the title mentions Serverless, the techniques apply for Serverful architectures as well. The talk will use AWS as the cloud of choice, but the choice of cloud is just an implementation detail.


 samlambert
 tammielis
 emna__ayadi
 tmiket
 jcasabona
 vanstee
 colly
 reverentgeek
 thekraken
 addyosmani
 jonoalderson
 iamctodd