Upgrade to Pro — share decks privately, control downloads, hide ads and more …

Mobile Security Standards for the new decade

Avatar for MobiTalk MobiTalk
February 13, 2020

Mobile Security Standards for the new decade

Mobile computing has changed the game, the world is moving towards a Mobile-first approach. Smart devices are often used for sensitive business applications, such as on-the-go business connectivity, and sensitive personal applications, such as email, mobile banking, and social media. But unfortunately, most of the mobile app developers have the least focus on security and privacy. As we step into the new decade with ever more focus on Mobile solutions, we must understand what our mobile apps are really doing to avoid opening up new doors for malicious interference. In this talk, we will go through the common security flaws in mobile applications in both Android & iOS platforms and shed some light on the mechanisms to guard against them.

Avatar for MobiTalk

MobiTalk

February 13, 2020

More Decks by MobiTalk

Other Decks in Technology

Transcript

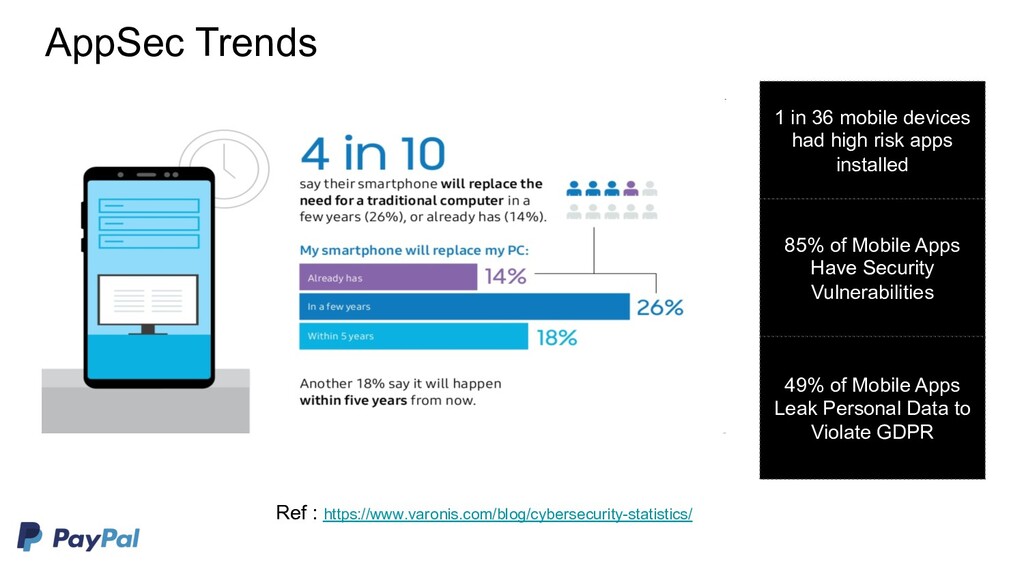
  1. AppSec Trends Ref : https://www.varonis.com/blog/cybersecurity-statistics/ 1 in 36 mobile devices

    had high risk apps installed 85% of Mobile Apps Have Security Vulnerabilities 49% of Mobile Apps Leak Personal Data to Violate GDPR
  2. • How to provide requirements for software architects and developers

    seeking to develop secure mobile applications? • Are there any specific recommendations as to what level of security is recommended for different use-cases? • Are there any industry standard that can be tested against in mobile app security reviews? Security In Development Lifecycle?
  3. • The Open Web Application Security Project (OWASP) is a

    nonprofit foundation that works to improve the security of software • Popular for “Top 10 Application Security Risks” lists ◦ https://wiki.owasp.org/index.php/Category:OWASP_Top_Ten_Project • Flagship projects ◦ https://wiki.owasp.org/index.php/Category:OWASP_Project#tab=Project_Inventory OWASP To The Rescue!
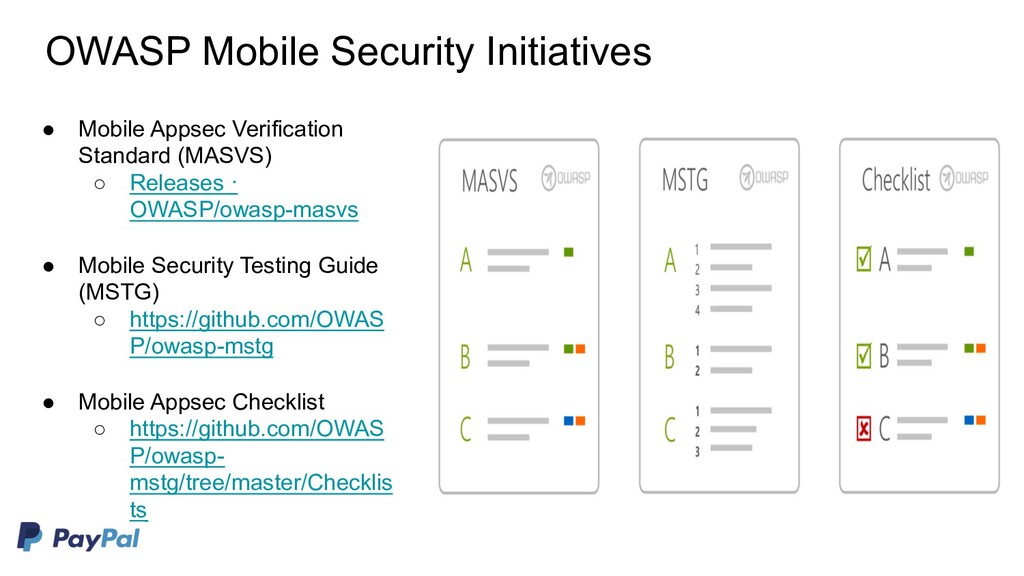
  4. • Mobile Appsec Verification Standard (MASVS) ◦ Releases · OWASP/owasp-masvs

    • Mobile Security Testing Guide (MSTG) ◦ https://github.com/OWAS P/owasp-mstg • Mobile Appsec Checklist ◦ https://github.com/OWAS P/owasp- mstg/tree/master/Checklis ts OWASP Mobile Security Initiatives
  5. • Standardized Baseline ◦ Standard Security ◦ Defence in Depth

    ◦ RE Resilience • Mapping to Domains ◦ Breaks the requirements into 8 domains • Plan of attack ◦ Implemented checklists OWASP MASVS - Intro
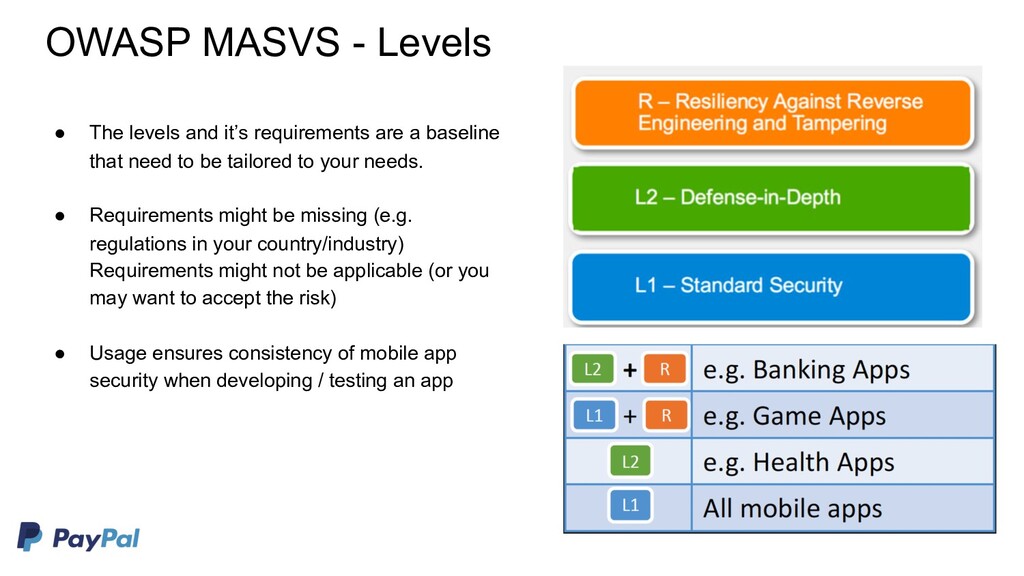
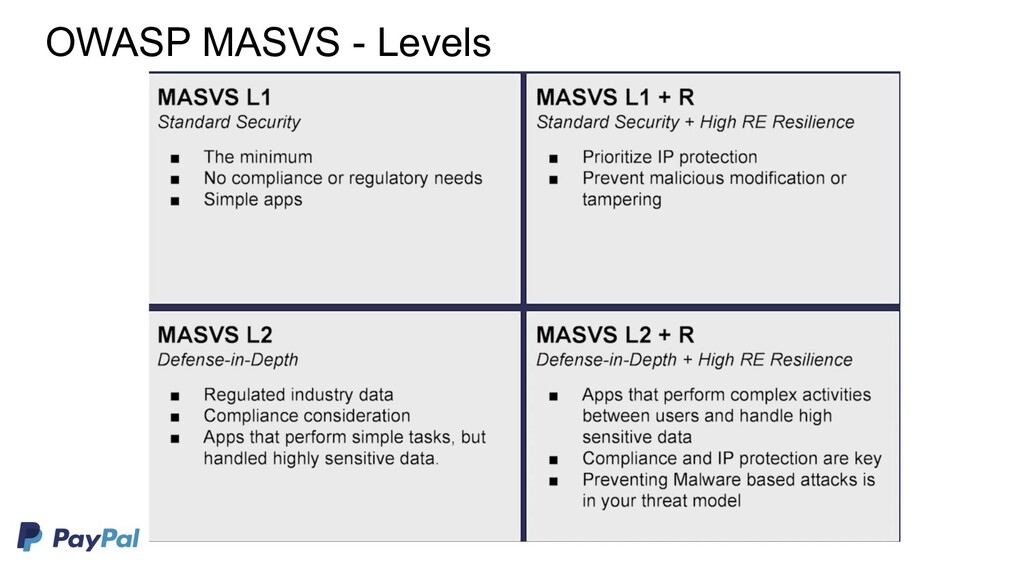
  6. • The levels and it’s requirements are a baseline that

    need to be tailored to your needs. • Requirements might be missing (e.g. regulations in your country/industry) Requirements might not be applicable (or you may want to accept the risk) • Usage ensures consistency of mobile app security when developing / testing an app OWASP MASVS - Levels
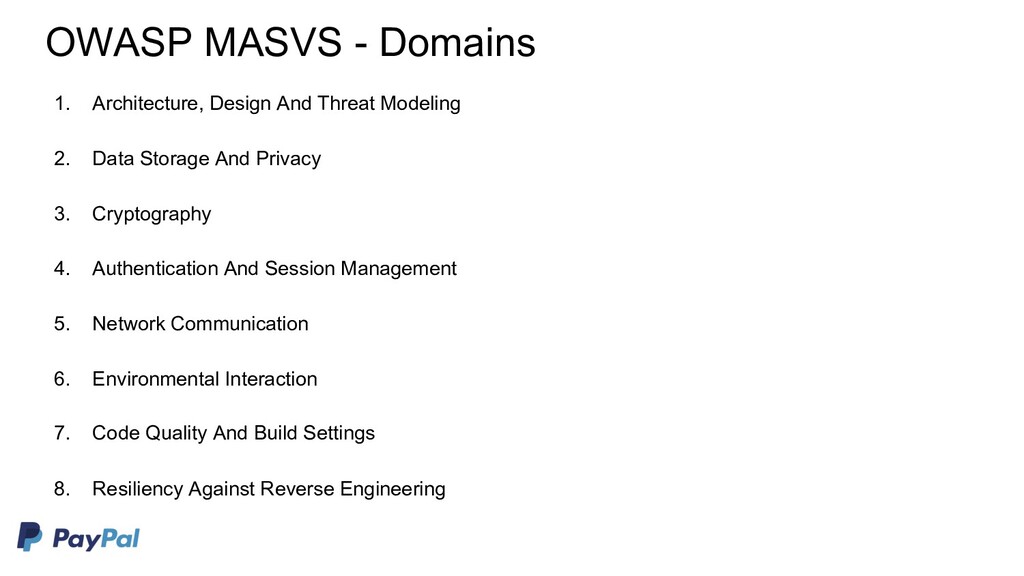
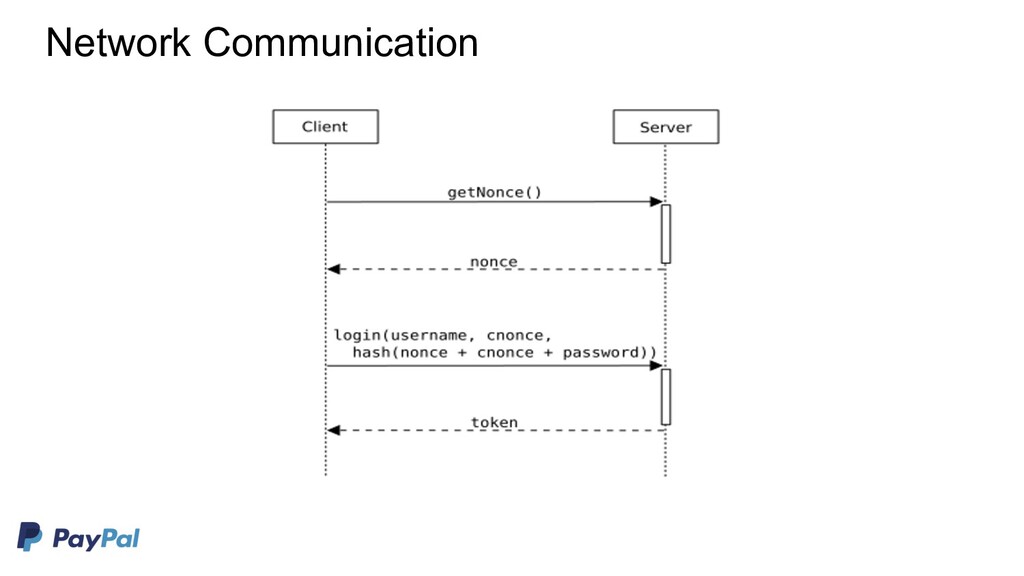
  7. 1. Architecture, Design And Threat Modeling 2. Data Storage And

    Privacy 3. Cryptography 4. Authentication And Session Management 5. Network Communication 6. Environmental Interaction 7. Code Quality And Build Settings 8. Resiliency Against Reverse Engineering OWASP MASVS - Domains
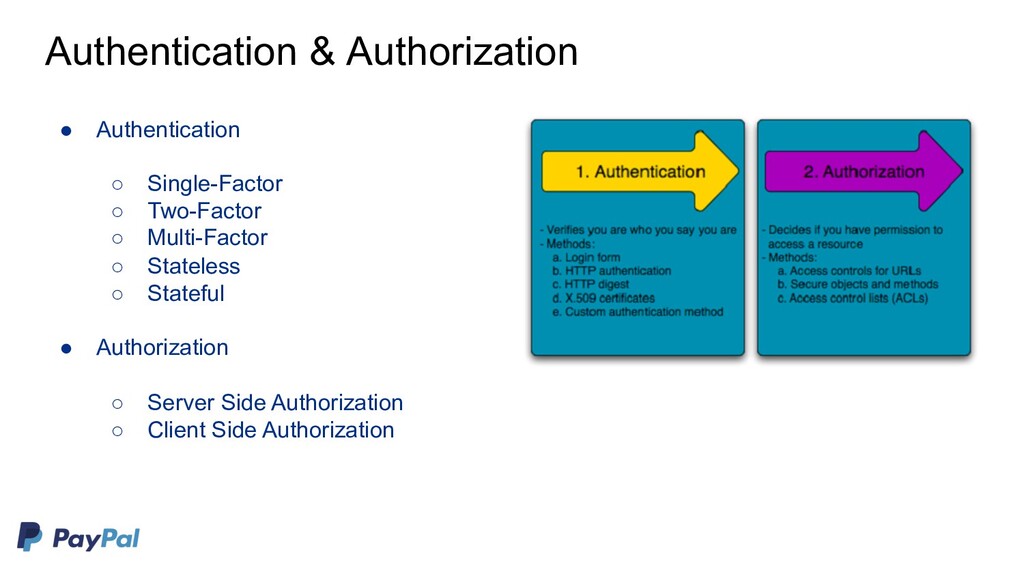
  8. • Authentication ◦ Single-Factor ◦ Two-Factor ◦ Multi-Factor ◦ Stateless

    ◦ Stateful • Authorization ◦ Server Side Authorization ◦ Client Side Authorization Authentication & Authorization
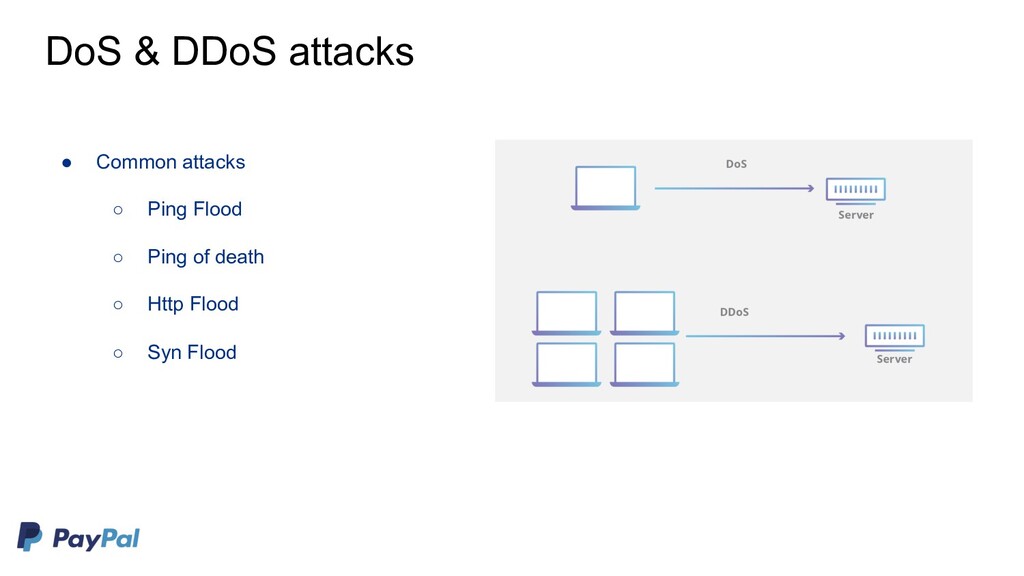
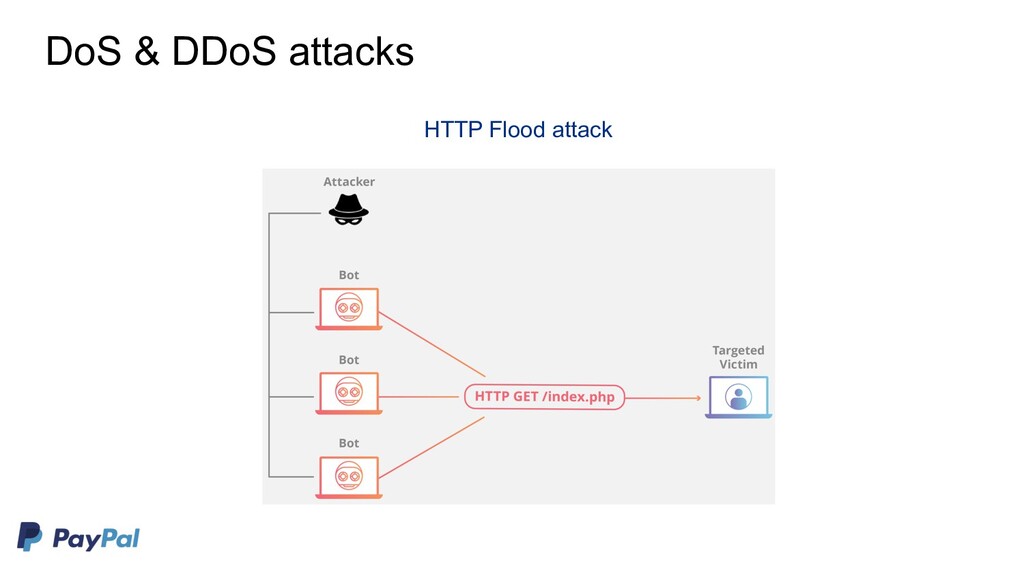
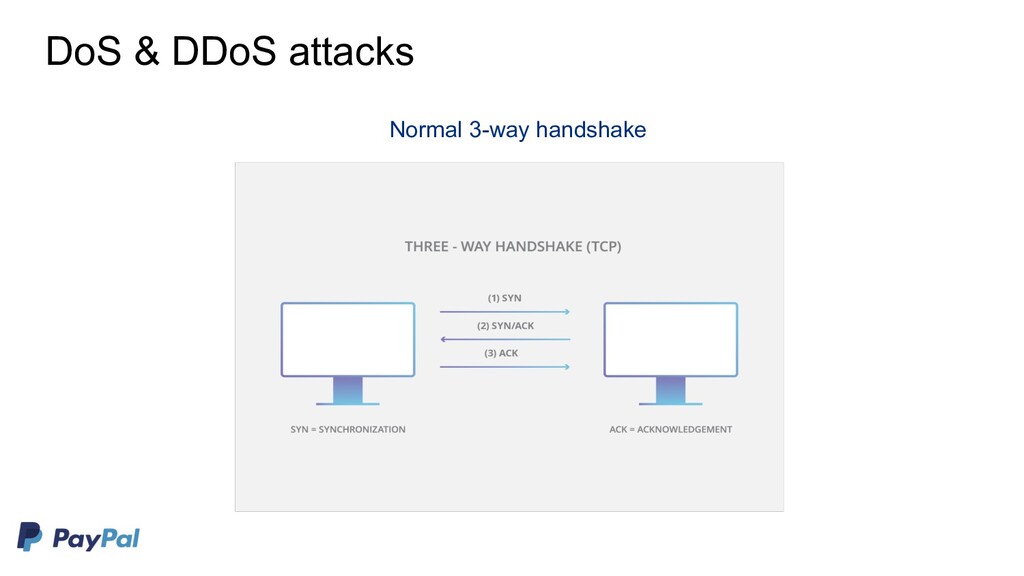
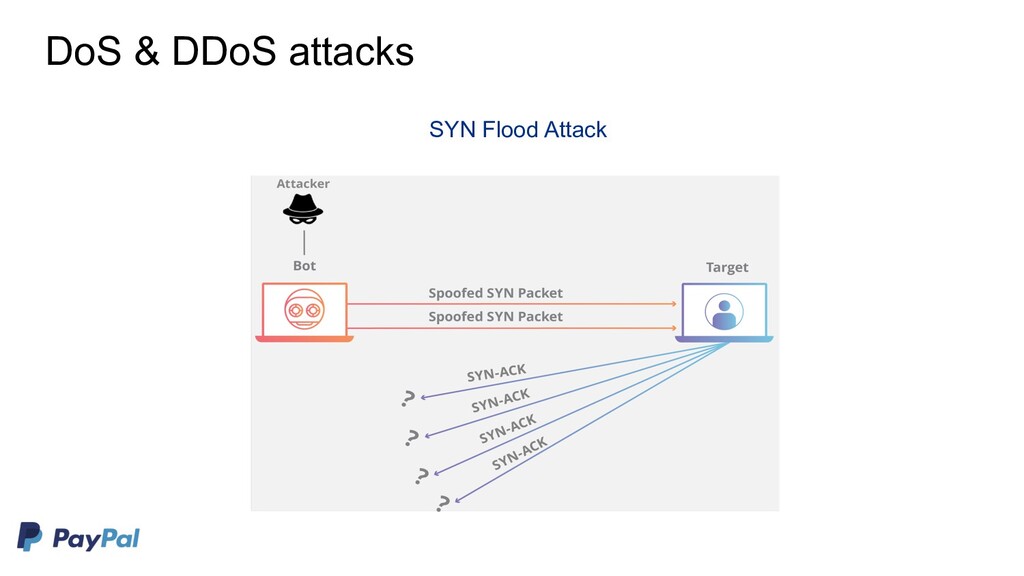
  9. • Common attacks ◦ Ping Flood ◦ Ping of death

    ◦ Http Flood ◦ Syn Flood DoS & DDoS attacks
  10. Prevention: ◦ 2 way certificate pinning ◦ Blackhole routing ◦

    Rate Limiting ◦ Increasing the Backlog queue ◦ Recycling the oldest pending connection ◦ Introducing Web Application Firewall as middleware ◦ SYN Cookies ◦ Blacklisting ◦ Whitelisting DoS & DDoS attacks
  11. • Using Permissions which are absolutely mandatory for the app

    • Be aware of Permissions inherited from libraries included • Transparency in Permissions • Inform user about the system access explicitly • Scoped Storage Permission Handling
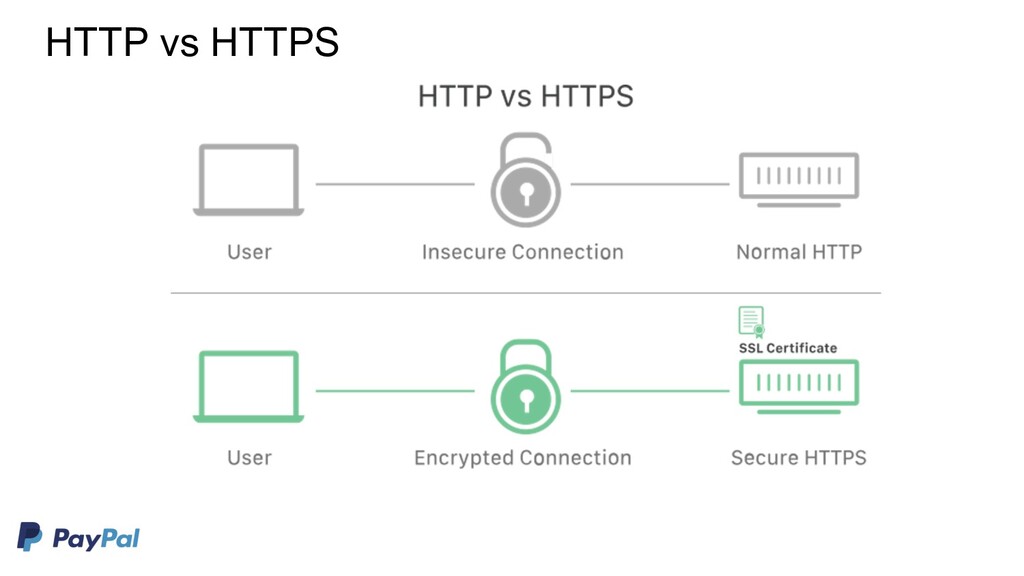
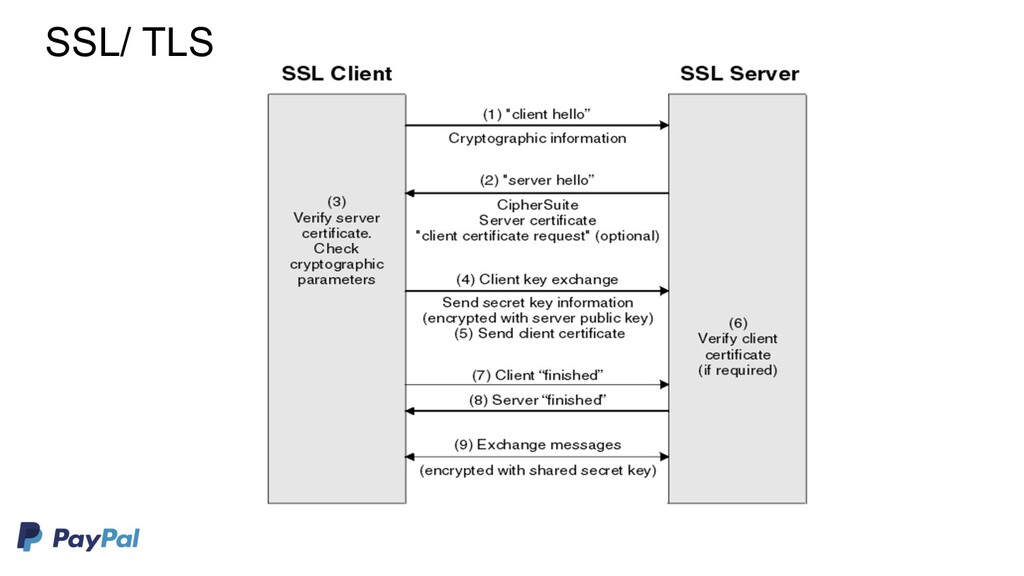
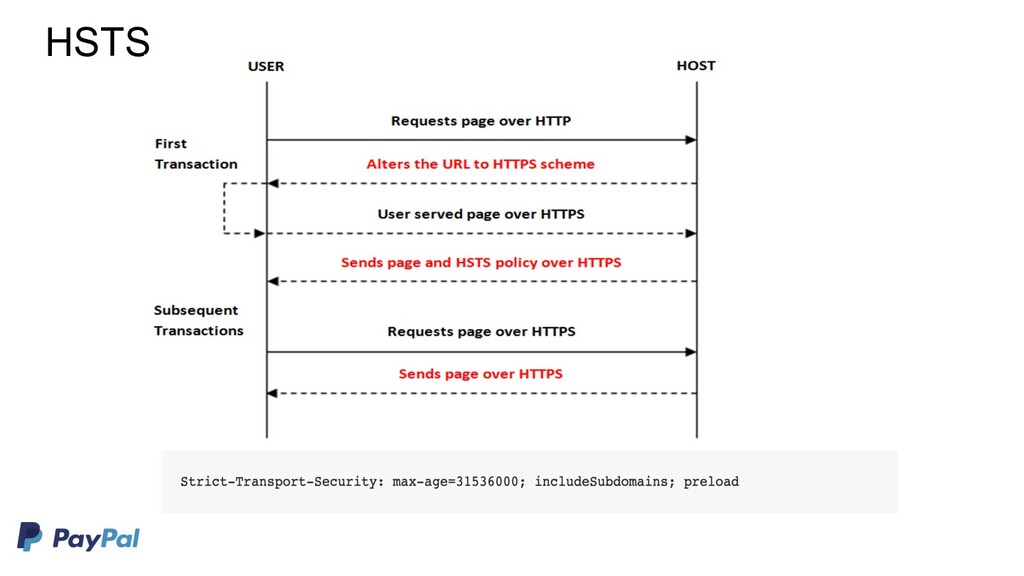
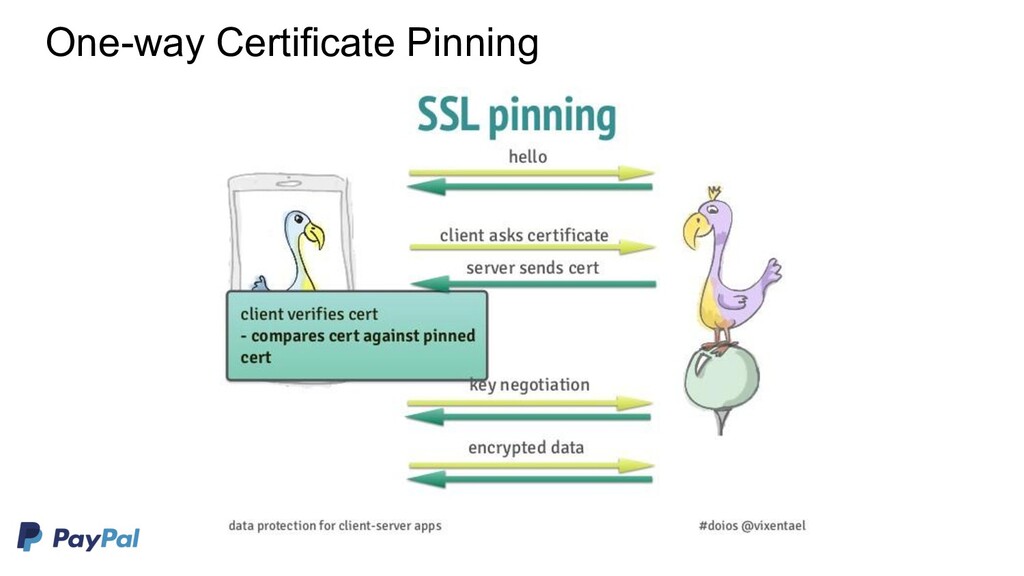
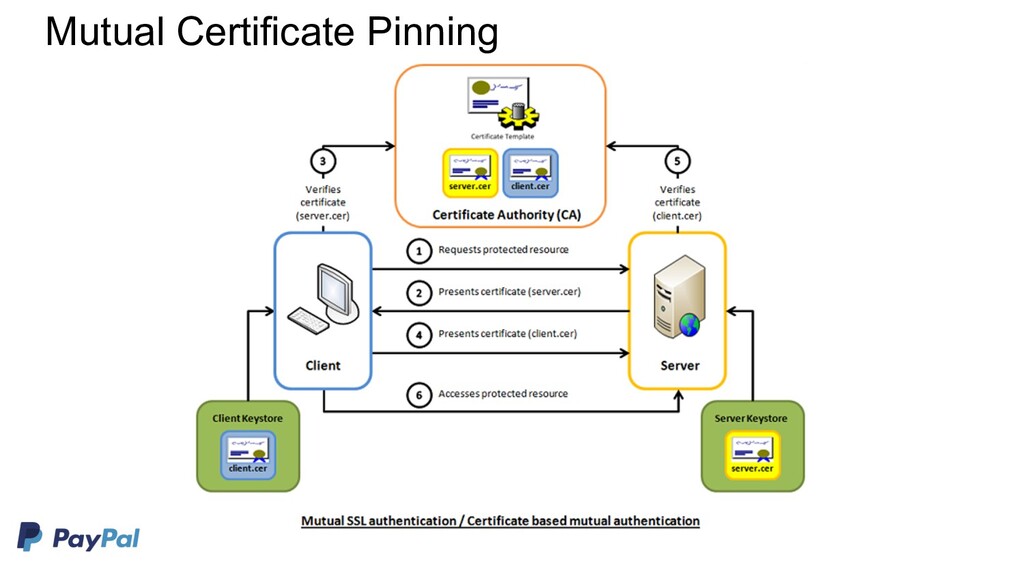
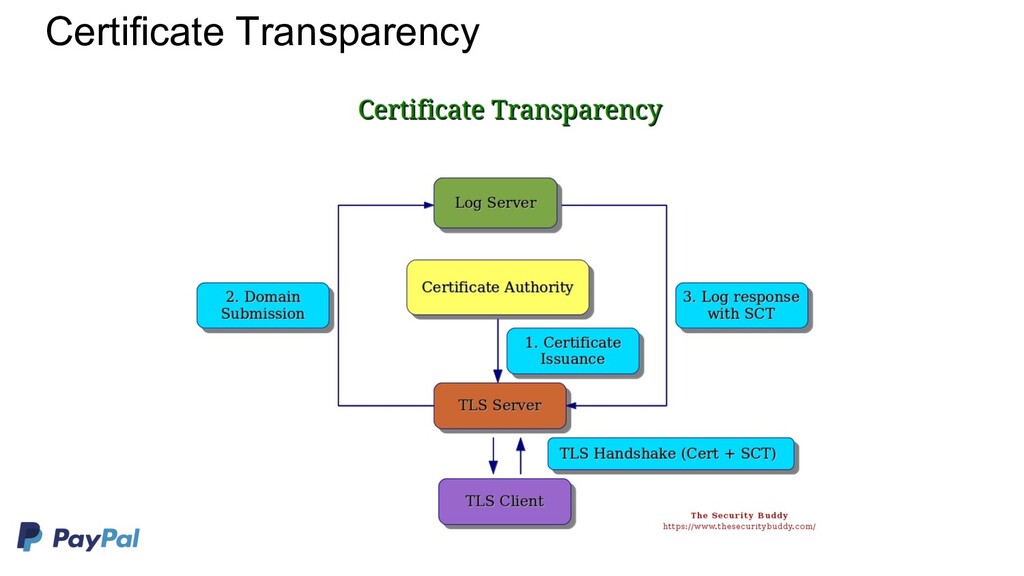
  12. • Using HTTPS with strong encryption • Using HSTS •

    One-way certificate pinning • Mutual certificate pinning • Certificate transparency Network security
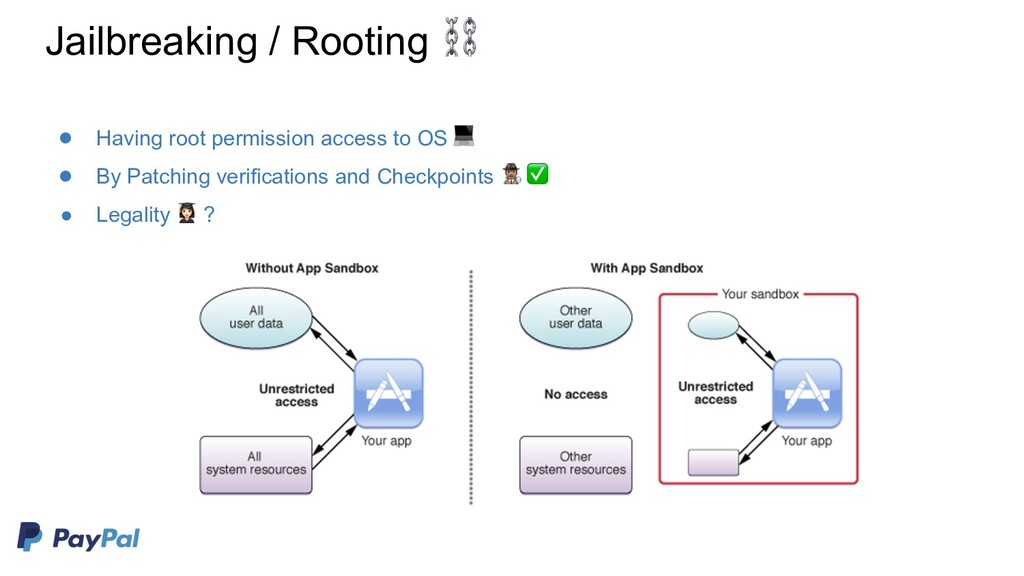
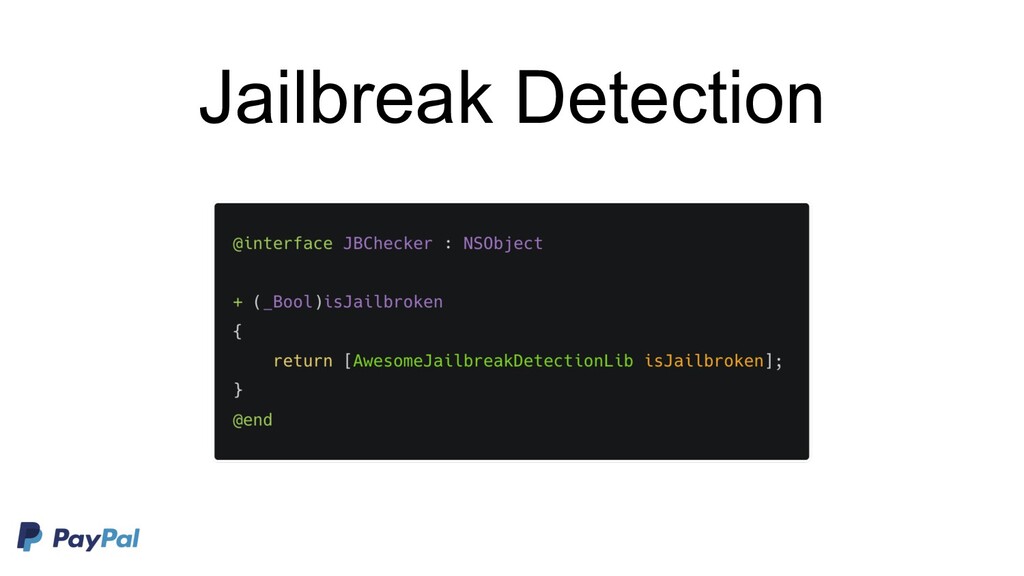
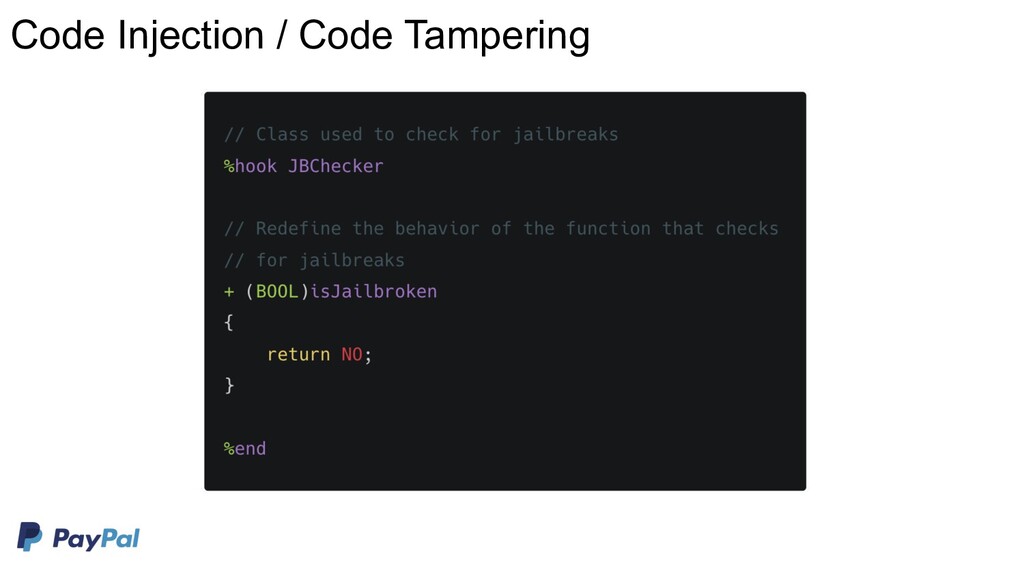
  13. • Having root permission access to OS • By Patching

    verifications and Checkpoints $ ✅ • Legality & ? Jailbreaking / Rooting ⛓
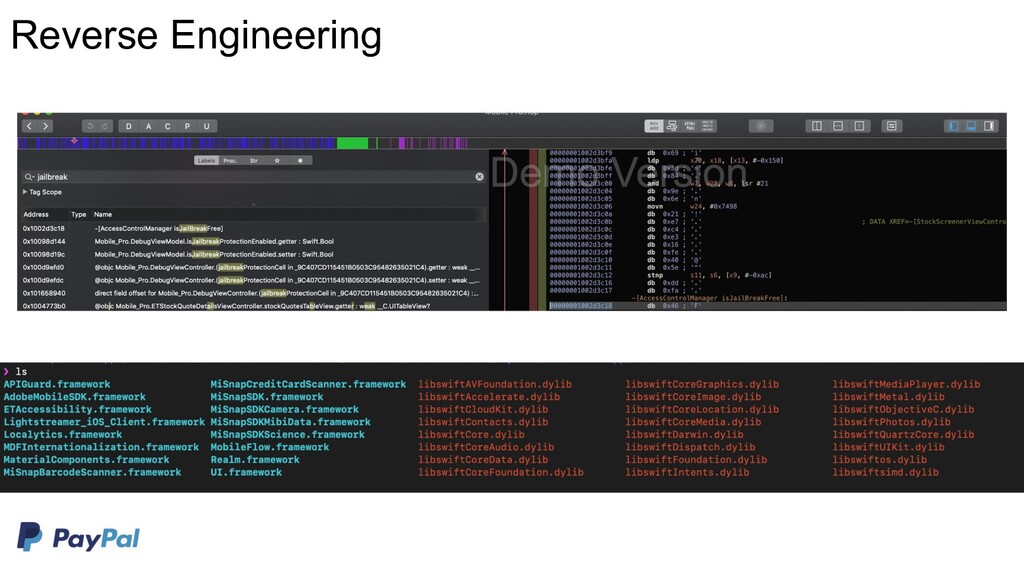
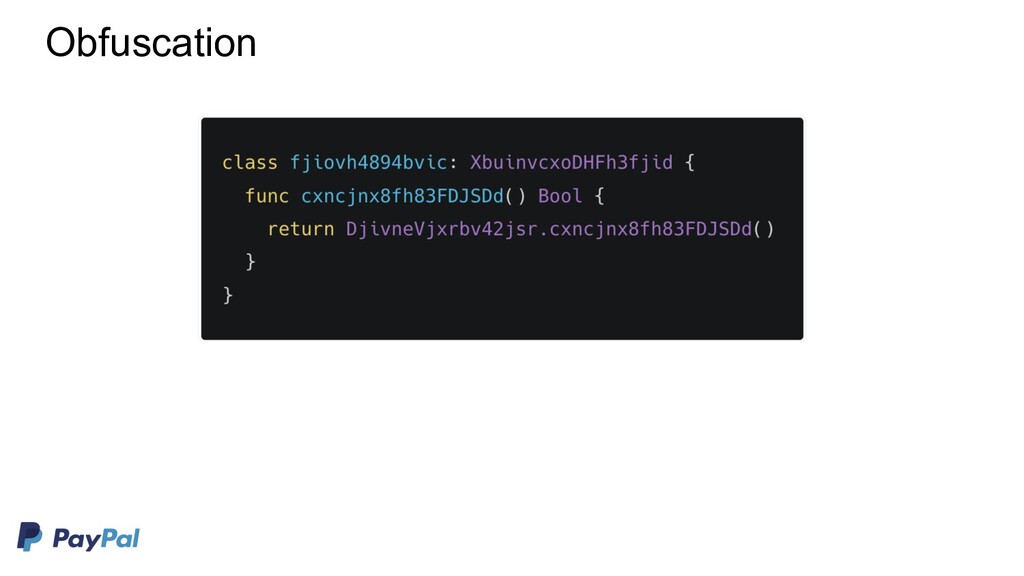
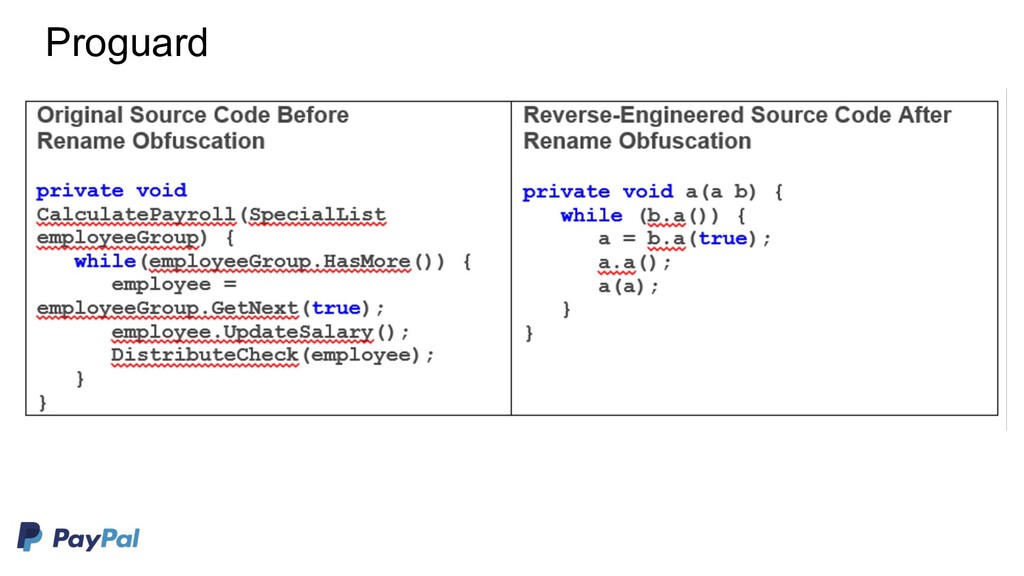
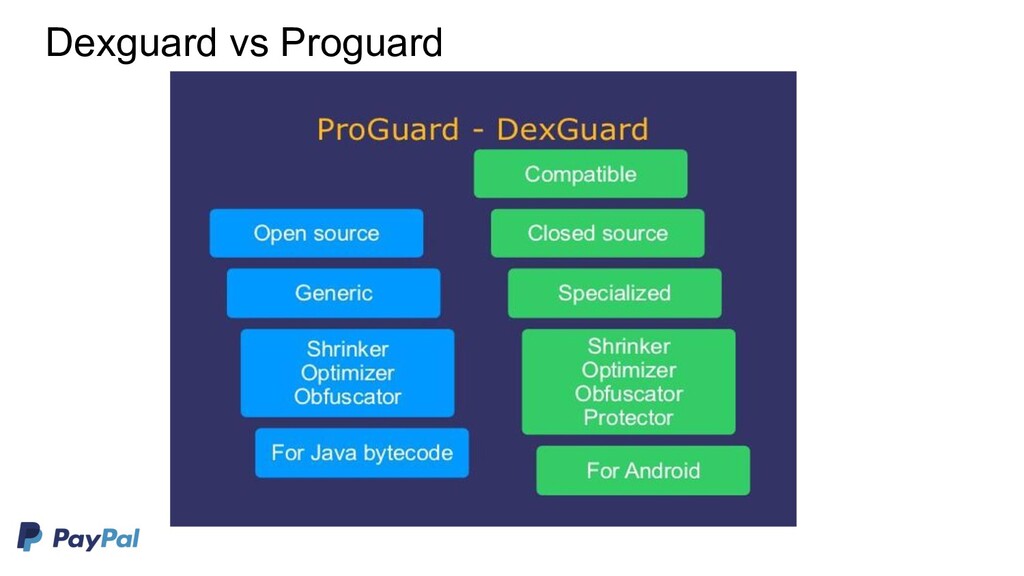
  14. • Analyze software in order to identify and understand the

    parts it is composed of. Like sniffing sensitive code and data. • Disassemble the ipa/apk • As a developer we had to be resilient for reverse Engineering Reverse Engineering
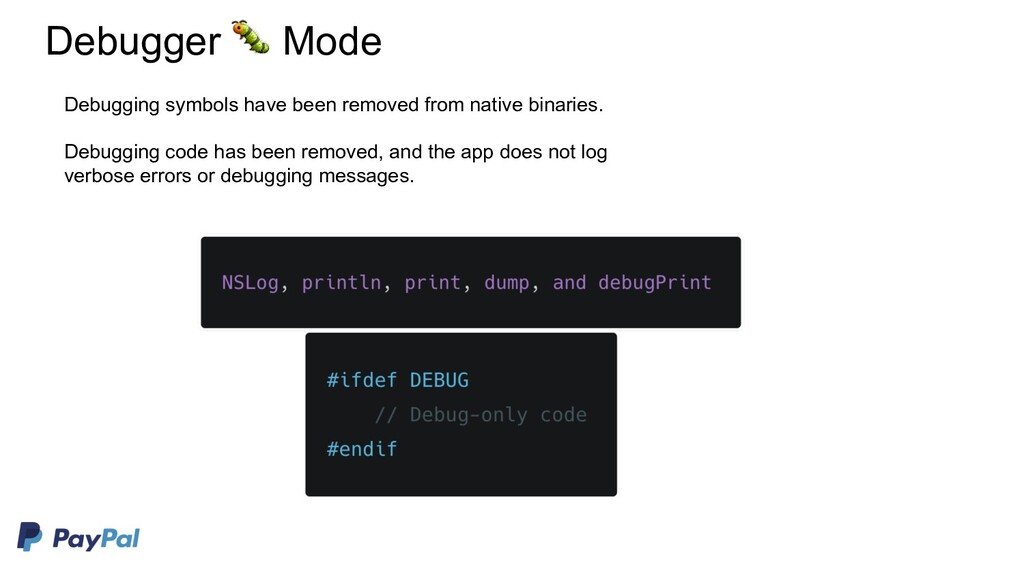
  15. Debugger Mode Debugging symbols have been removed from native binaries.

    Debugging code has been removed, and the app does not log verbose errors or debugging messages.
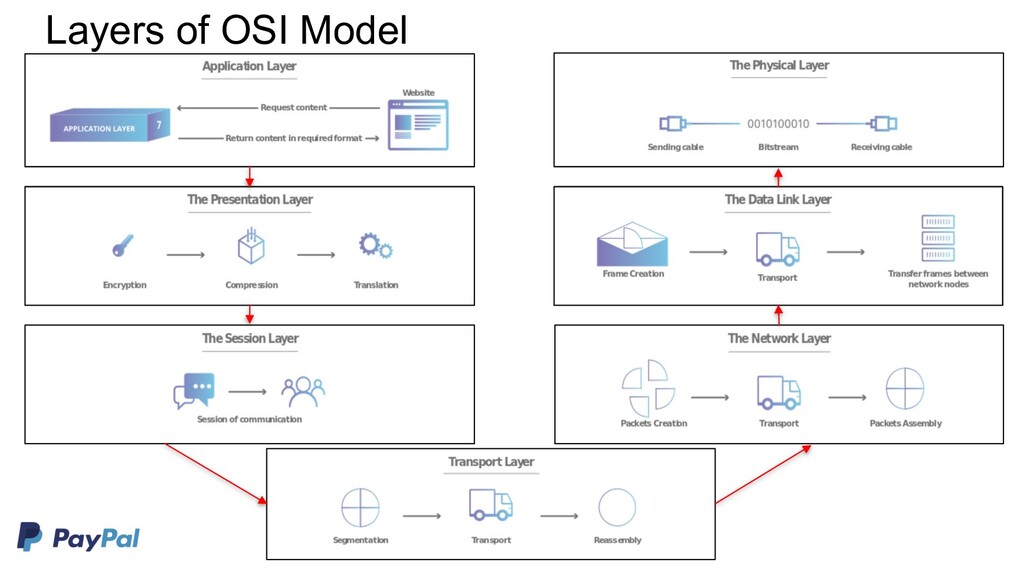
  16. • https://www.geeksforgeeks.org/layers-of-osi-model/ • https://www.javatpoint.com/osi-model • https://www.cloudflare.com/learning/ddos/glossary/open-systems-interconnection- model-osi/ • https://www.cloudflare.com/en-in/learning/ddos/what-is-a-ddos-attack/ •

    https://www.cloudflare.com/learning/ddos/syn-flood-ddos-attack/ • https://www.cloudflare.com/learning/ddos/glossary/ddos-blackhole-routing/ • https://medium.com/datadriveninvestor/authentication-vs-authorization-716fea914d55 • https://developer.android.com/training/permissions/usage-notes • http://www.differencebetween.info/difference-between-encryption-encoding-and- hashing Bibliography
  17. • http://ithare.com/advocating-obscurity-part-iii-code-obfuscation-basics/ • https://medium.com/bugbountywriteup/how-to-bypass-certificate-validation-ssl-pinning- ef8af8b15c40 • https://www.codeproject.com/Articles/326574/An-Introduction-to-Mutual-SSL- Authentication • https://medium.com/babylon-engineering/android-security-certificate-transparency-

    601c18157c44 • https://www.certificate-transparency.org/ • https://www.thesecuritybuddy.com/data-breaches-prevention/what-is-certificate- transparency/ • https://www.globalsign.com/en/blog/what-is-certificate-transparency • https://www.cloudflare.com/learning/ssl/why-is-http-not-secure/ Bibliography