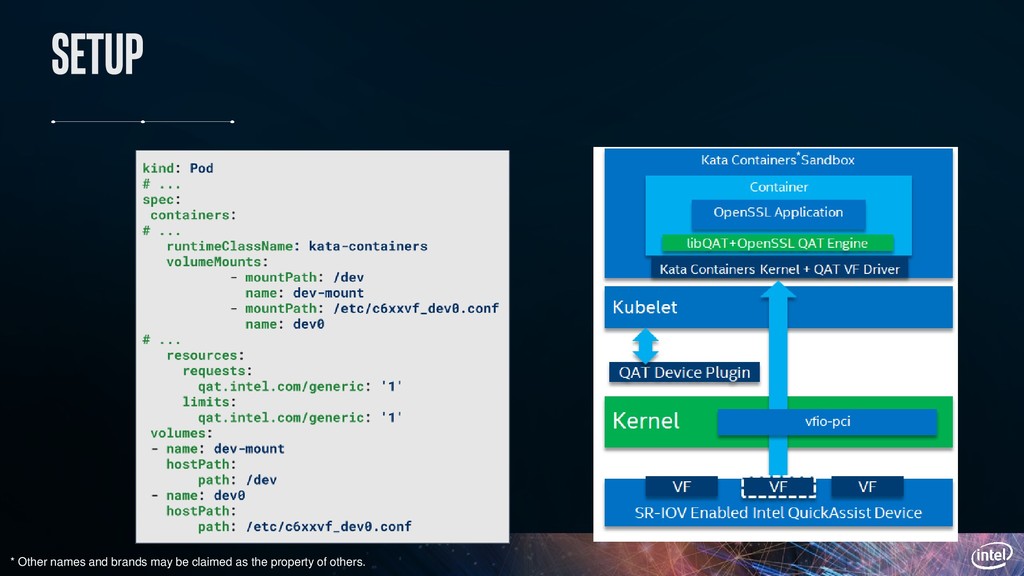
Kubernetes* • Kubernetes Device Plugins • Pods, Sandboxing, RuntimeClass • Kata Containers* • Demo: HW Accelerated OpenSSL* Crypto * Other names and brands may be claimed as the property of others.
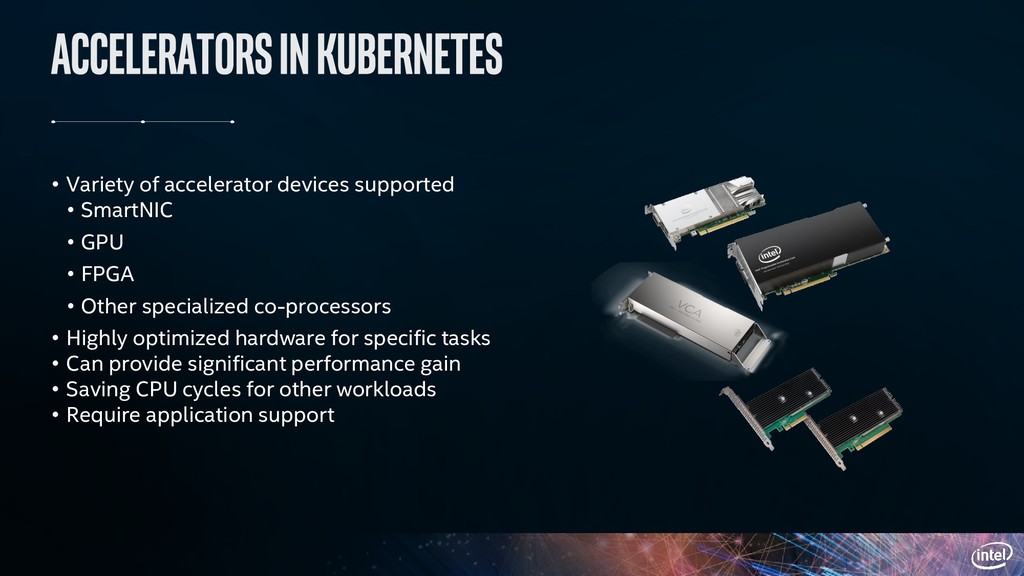
• FPGA • Other specialized co-processors • Highly optimized hardware for specific tasks • Can provide significant performance gain • Saving CPU cycles for other workloads • Require application support
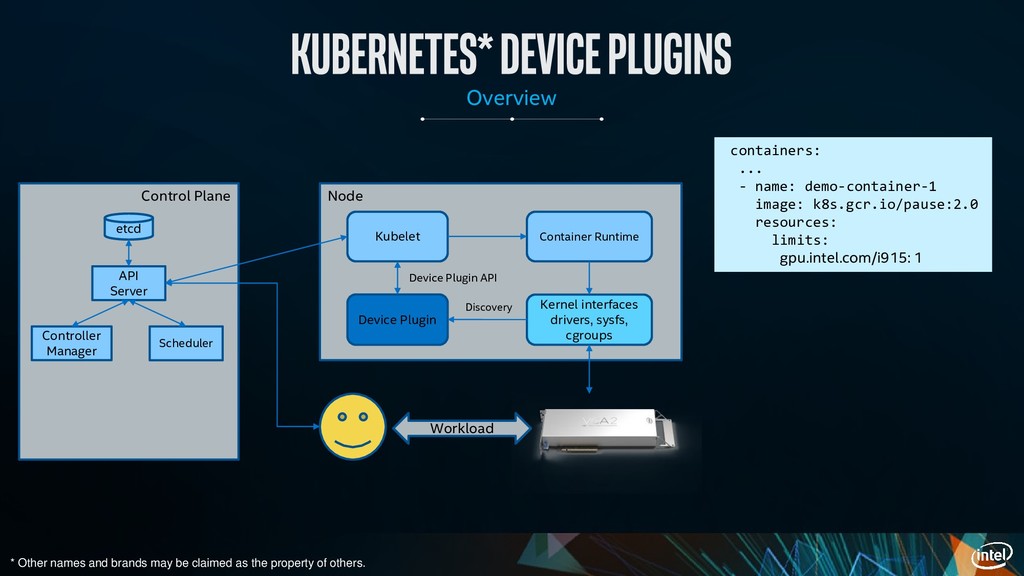
sysfs, cgroups Device Plugin etcd Scheduler API Server Controller Manager Workload Discovery Device Plugin API containers: ... - name: demo-container-1 image: k8s.gcr.io/pause:2.0 resources: limits: gpu.intel.com/i915: 1 * Other names and brands may be claimed as the property of others.
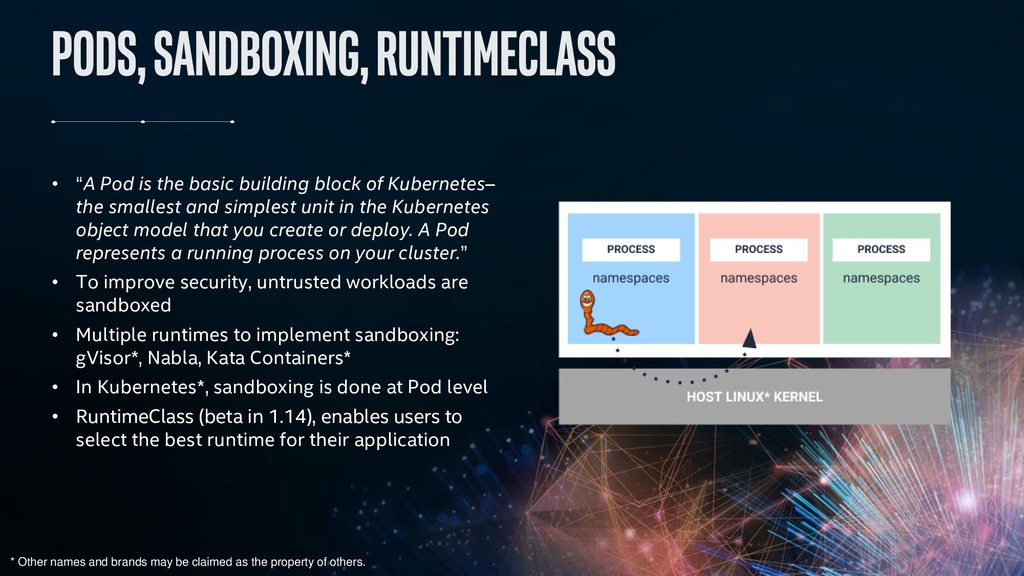
the smallest and simplest unit in the Kubernetes object model that you create or deploy. A Pod represents a running process on your cluster.” • To improve security, untrusted workloads are sandboxed • Multiple runtimes to implement sandboxing: gVisor*, Nabla, Kata Containers* • In Kubernetes*, sandboxing is done at Pod level • RuntimeClass (beta in 1.14), enables users to select the best runtime for their application * Other names and brands may be claimed as the property of others.
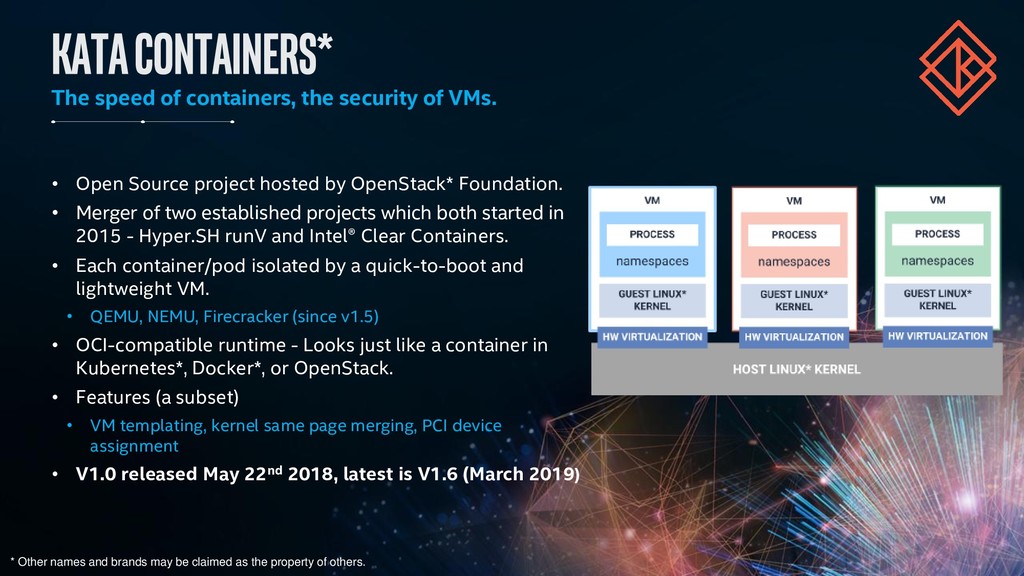
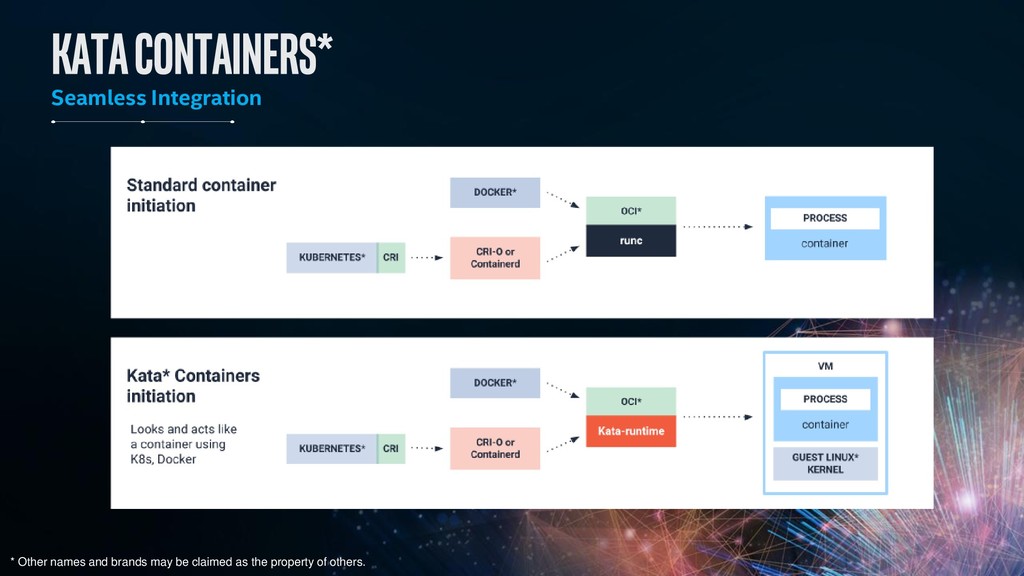
Source project hosted by OpenStack* Foundation. • Merger of two established projects which both started in 2015 - Hyper.SH runV and Intel® Clear Containers. • Each container/pod isolated by a quick-to-boot and lightweight VM. • QEMU, NEMU, Firecracker (since v1.5) • OCI-compatible runtime - Looks just like a container in Kubernetes*, Docker*, or OpenStack. • Features (a subset) • VM templating, kernel same page merging, PCI device assignment • V1.0 released May 22nd 2018, latest is V1.6 (March 2019) * Other names and brands may be claimed as the property of others.
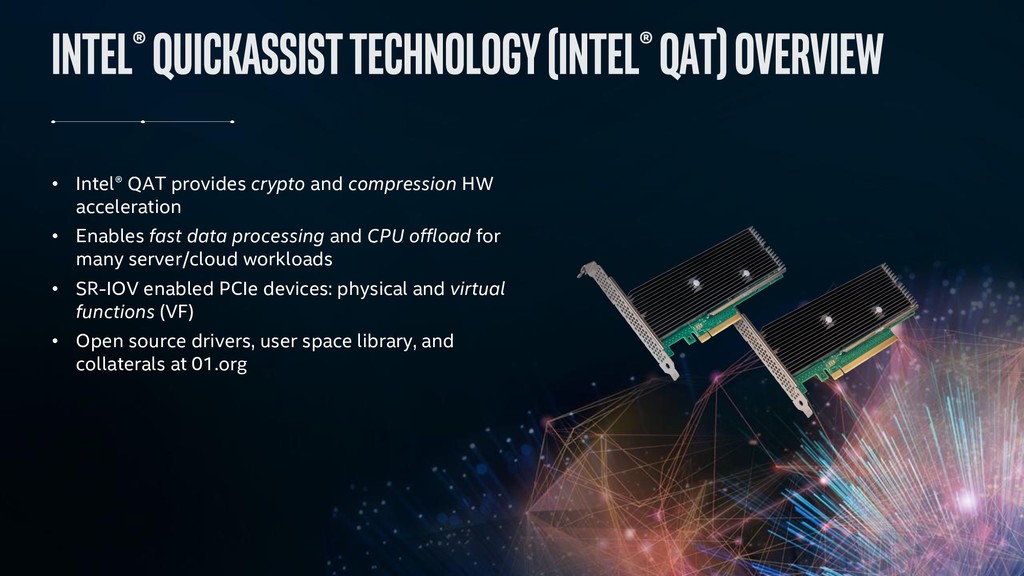
Enables fast data processing and CPU offload for many server/cloud workloads • SR-IOV enabled PCIe devices: physical and virtual functions (VF) • Open source drivers, user space library, and collaterals at 01.org


 genda
 shuta13
 pfn
 takanorip
 codatum
 kentarofujii
 kenichiodo
 ludicmind
 ivry_presentationmaterials
 yamanoku
 sudoakiy
 csswizardry
 ammeep
 lauravandoore
 wayneb77
 62gerente
 thoeni
 davidcarrasco
 techseoconnect
 mfonobong
 colly
 wjessup
 chikuwait