Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
Stop the security theater!
Search
Pratul Kalia
October 07, 2017
Programming
330
0
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
Stop the security theater!
Pratul Kalia
October 07, 2017
More Decks by Pratul Kalia
See All by Pratul Kalia
The special case of Mobile DevOps
pratul
2
54
Reldex: measuring the effectiveness of your app release process
pratul
0
48
Simplifying Software Estimation
pratul
1
300
Effective and efficient mobile engineering
pratul
0
220
Designing future-proof Android applications
pratul
0
230
Android - an introduction for developers
pratul
3
280
Semantic Content Repositories
pratul
1
200
How To Become A Hacker
pratul
3
340
Other Decks in Programming
See All in Programming
dotNET_vulnclicker_intro.pdf
deka_morita
0
140
Workers Cache を知る
syumai
0
370
Next.js: The final boss of Web Performance
guaca
0
260
AWSに止められる覚悟してますか?
morizo_1984
2
540
Herb in Rails 8.2: Your ERB views, now HTML-aware @ Rails World 2026, Austin, Texas
marcoroth
0
220
コードで差別化できない時代の ソフトウェアエンジニアリング / Software Engineering in an Era Where Code Doesn’t Differentiate
kishida
2
180
IBM Bob Dojo #1 仕様駆動開発入門
oniak3ibm
PRO
0
390
Simple Storage Service(S3) is not simple
iwatsukayura
0
290
Agents on Rails - Rails at Scale 2026
irinanazarova
0
560
パスワード再設定メールのURLについて知っておこう
uyuki234
0
160
Optunaを作ったときにやりたかったこと、その後 (2026/10/16, Optuna Meetup #3)
iwiwi
1
440
自サークルのIdPからログアウトできるようになるまで
taiseiue
1
140
Featured
See All Featured
Product Roadmaps are Hard
iamctodd
55
13k
Skip the Path - Find Your Career Trail
mkilby
1
260
New Earth Scene 8
popppiees
4
2.7k
Raft: Consensus for Rubyists
vanstee
142
7.8k
JavaScript: Past, Present, and Future - NDC Porto 2020
reverentgeek
52
6.1k
Pawsitive SEO: Lessons from My Dog (and Many Mistakes) on Thriving as a Consultant in the Age of AI
davidcarrasco
0
260
Introduction to Domain-Driven Design and Collaborative software design
baasie
1
1k
Chasing Engaging Ingredients in Design
codingconduct
0
360
Writing Fast Ruby
sferik
630
63k
Building the Perfect Custom Keyboard
takai
2
910
sira's awesome portfolio website redesign presentation
elsirapls
0
460
Max Prin - Stacking Signals: How International SEO Comes Together (And Falls Apart)
techseoconnect
PRO
0
490
Transcript
Stop the security theater! pratul kalia @prxtl uncommon.is
“the practice of investing in countermeasures intended to provide the
feeling of improved security while doing little or nothing to achieve it.”
None
Cost-benefit analysis • Imperative to all security discussions • Security
of personal app vs business-critical app
Password rules are pointless • You’re not using a modern
password-hashing algorithm • Only length matters!
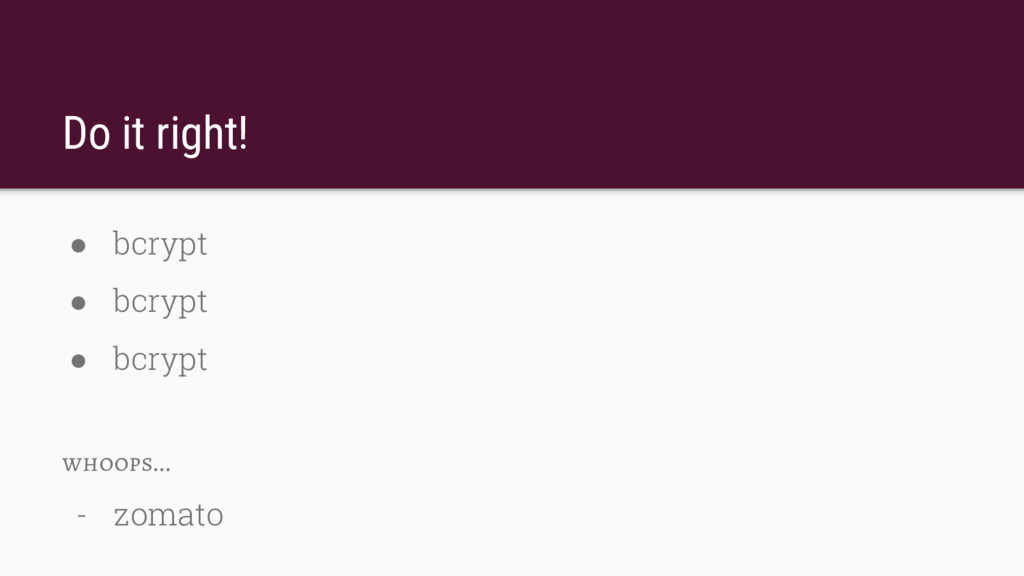
Do it right! • bcrypt • bcrypt • bcrypt whoops...
- zomato
Stop “inventing” your own security practices • Security is very,
very hard to get right • You’re not that smart! • It is easier to do the known right thing... than to know what you’re doing wrong
Don’t try to “save” your API endpoints • Your backend
should not get affected by a rogue client • MITM all the way • Certificate pinning does not solve this! whoops... - “Basic HTTP auth over TLS”
Stop client-side encryption • Don’t place your key under the
doormat • Security by obscurity is weak whoops... - “Double encryption!”
Anything part of your APK can be read • This
includes all API keys • … access tokens • … anything else hard-coded
Auth token in SharedPreferences • No problems! • Other apps
on the system cannot read your app’s data
Data you don’t have, cannot be stolen • Store user
data with utmost caution • You’re a user too! example... - “Who else in my Contacts uses this app?”
What about rooted devices? • All. • bets. • are.
• off.
Remember alternate attack vectors • Bribe a security guard? •
Bribe an employee?
Time for something real.
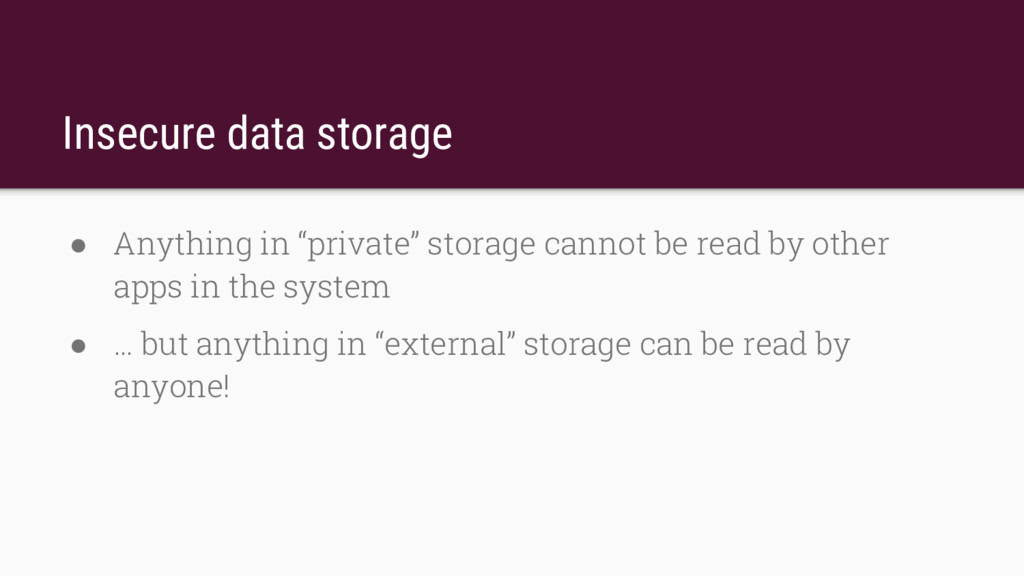
Insecure data storage • Anything in “private” storage cannot be
read by other apps in the system • … but anything in “external” storage can be read by anyone!
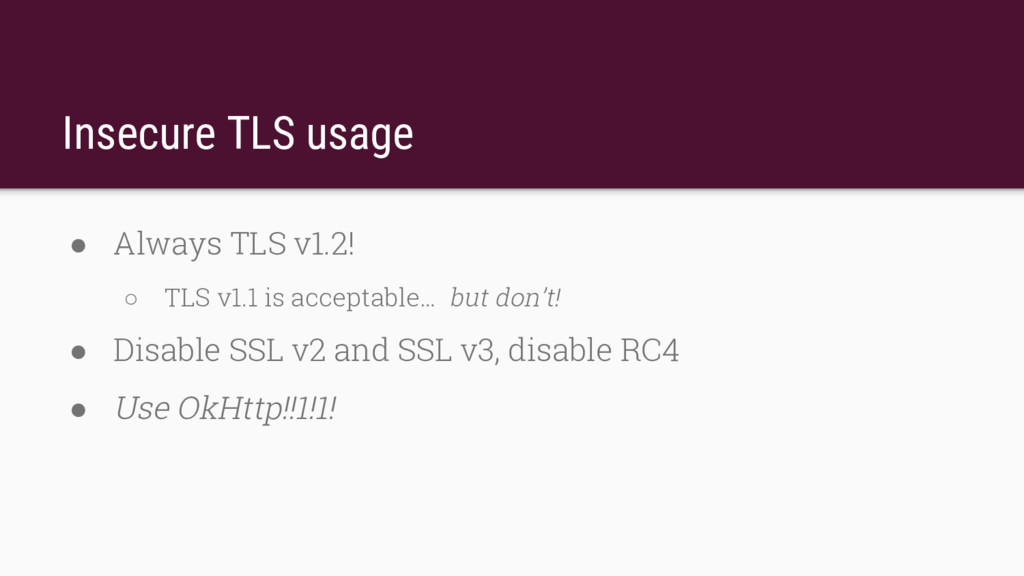
Insecure TLS usage • Always TLS v1.2! ◦ TLS v1.1
is acceptable… but don’t! • Disable SSL v2 and SSL v3, disable RC4 • Use OkHttp!!1!1!
Please break your own systems • Please! • Pay for
it!
fin


 pratul
 deka_morita
 syumai
 guaca
 morizo_1984
 marcoroth
 kishida
 oniak3ibm
 iwatsukayura
 irinanazarova
 uyuki234
 iwiwi
 taiseiue
 iamctodd
 mkilby
 popppiees
 vanstee
 reverentgeek
 davidcarrasco
 baasie
 codingconduct
 sferik
 takai
 elsirapls
 techseoconnect