Upgrade to Pro — share decks privately, control downloads, hide ads and more …

Side channel

Side channel

Avatar for Riccardo Scandariato

Riccardo Scandariato

October 15, 2019

Other Decks in Education

Transcript

  1. Learning objectives [knowledge] Understand the nature of this class of

    attacks [skills] Avoid one (simple) type of timing attack 2
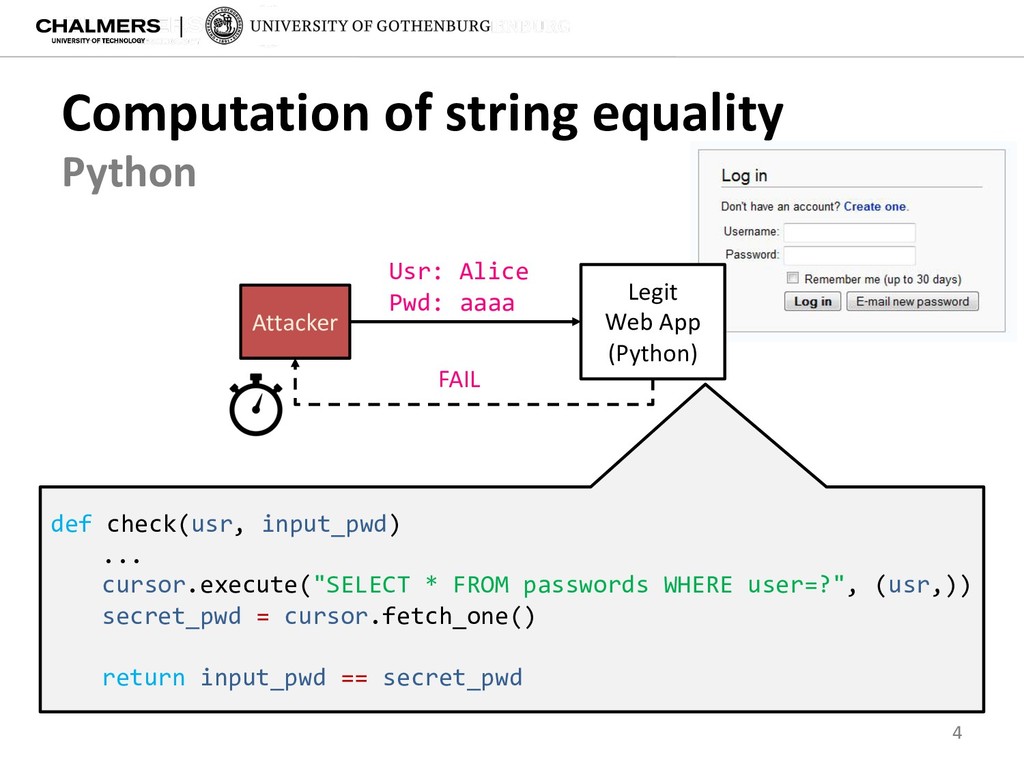
  2. Computation of string equality 4 Python Attacker Legit Web App

    (Python) Usr: Alice Pwd: aaaa def check(usr, input_pwd) ... cursor.execute("SELECT * FROM passwords WHERE user=?", (usr,)) secret_pwd = cursor.fetch_one() return input_pwd == secret_pwd FAIL
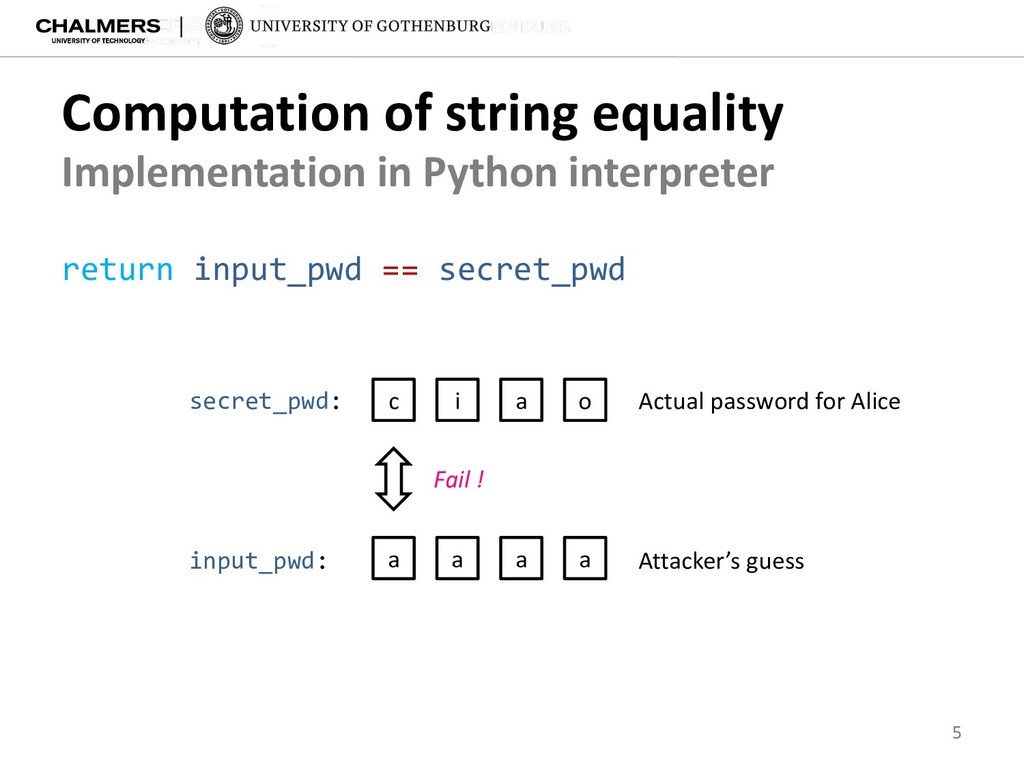
  3. Computation of string equality 5 Implementation in Python interpreter return

    input_pwd == secret_pwd a a a a c i a o input_pwd: secret_pwd: Actual password for Alice Attacker’s guess Fail !
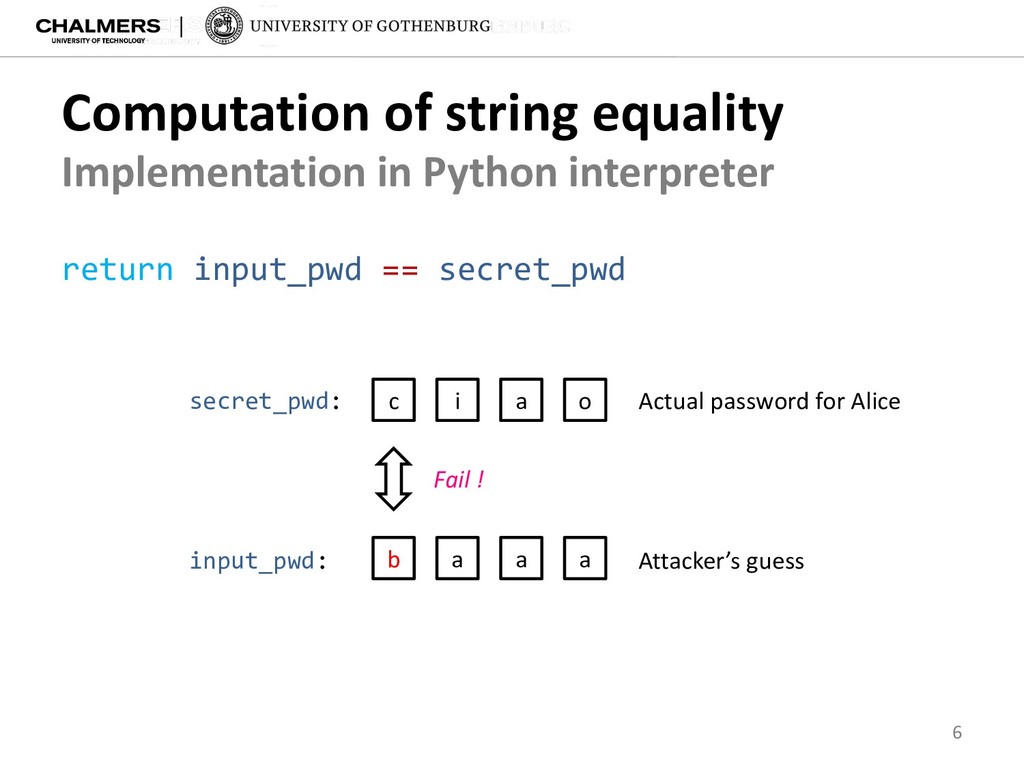
  4. Computation of string equality 6 Implementation in Python interpreter b

    a a a c i a o Actual password for Alice Fail ! Attacker’s guess return input_pwd == secret_pwd input_pwd: secret_pwd:
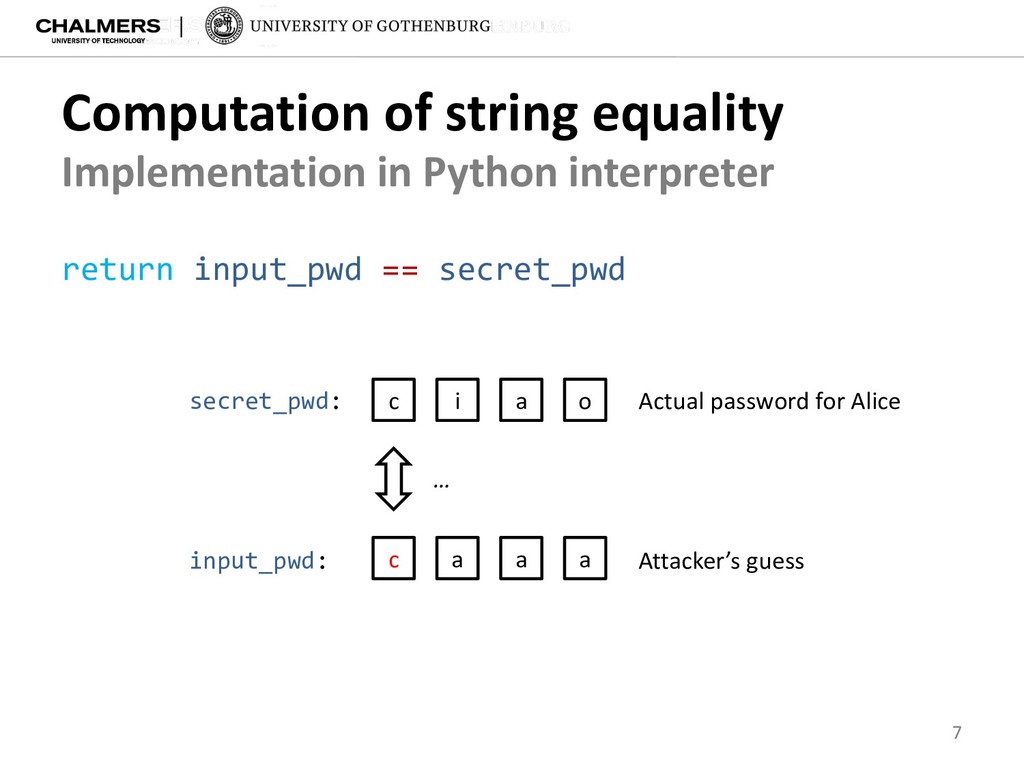
  5. Computation of string equality 7 Implementation in Python interpreter c

    a a a c i a o Actual password for Alice Attacker’s guess return input_pwd == secret_pwd input_pwd: secret_pwd: …
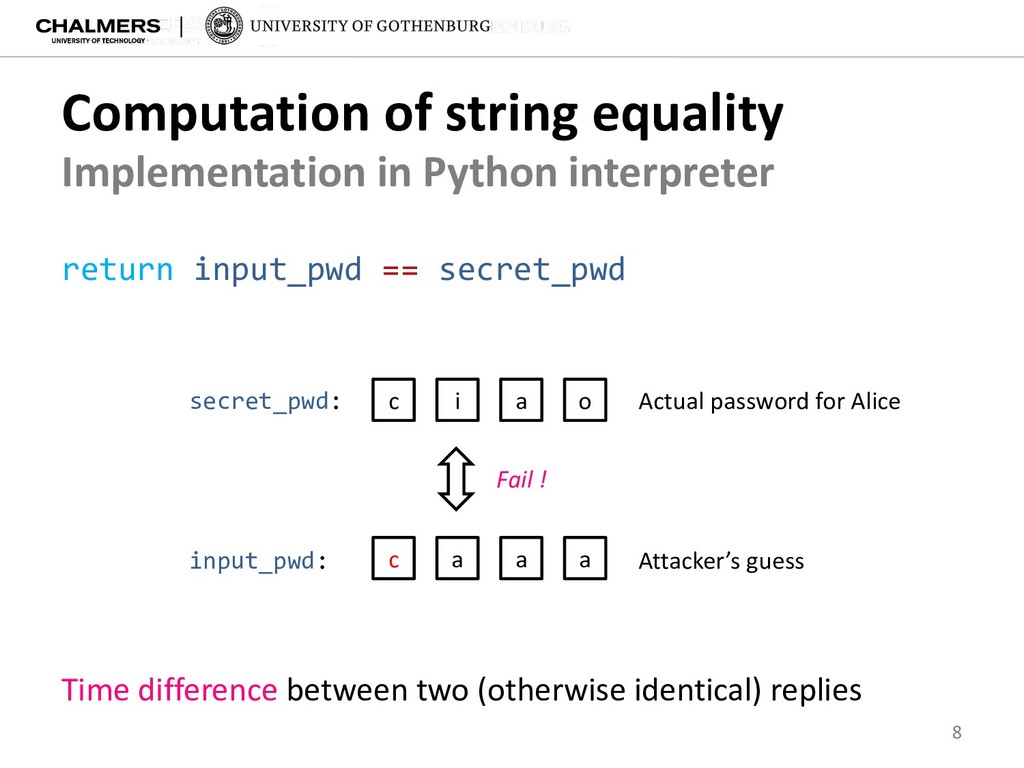
  6. Computation of string equality 8 Implementation in Python interpreter c

    a a a c i a o Actual password for Alice Fail ! Time difference between two (otherwise identical) replies Attacker’s guess return input_pwd == secret_pwd input_pwd: secret_pwd:
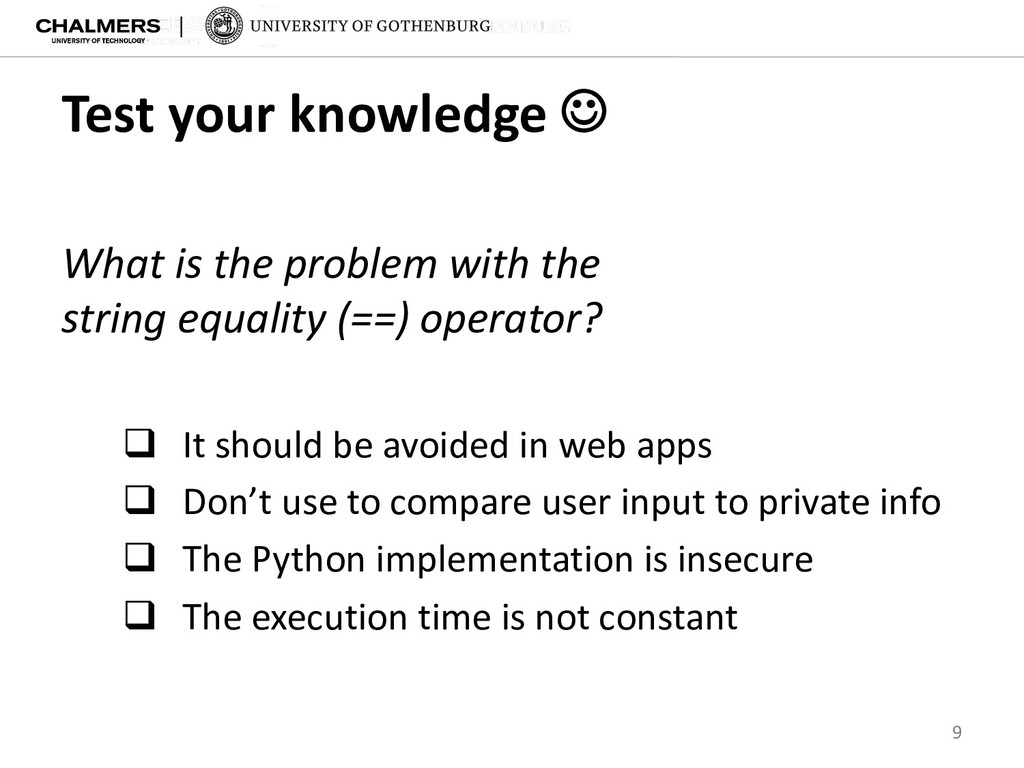
  7. Test your knowledge J What is the problem with the

    string equality (==) operator? q It should be avoided in web apps q Don’t use to compare user input to private info q The Python implementation is insecure q The execution time is not constant 9
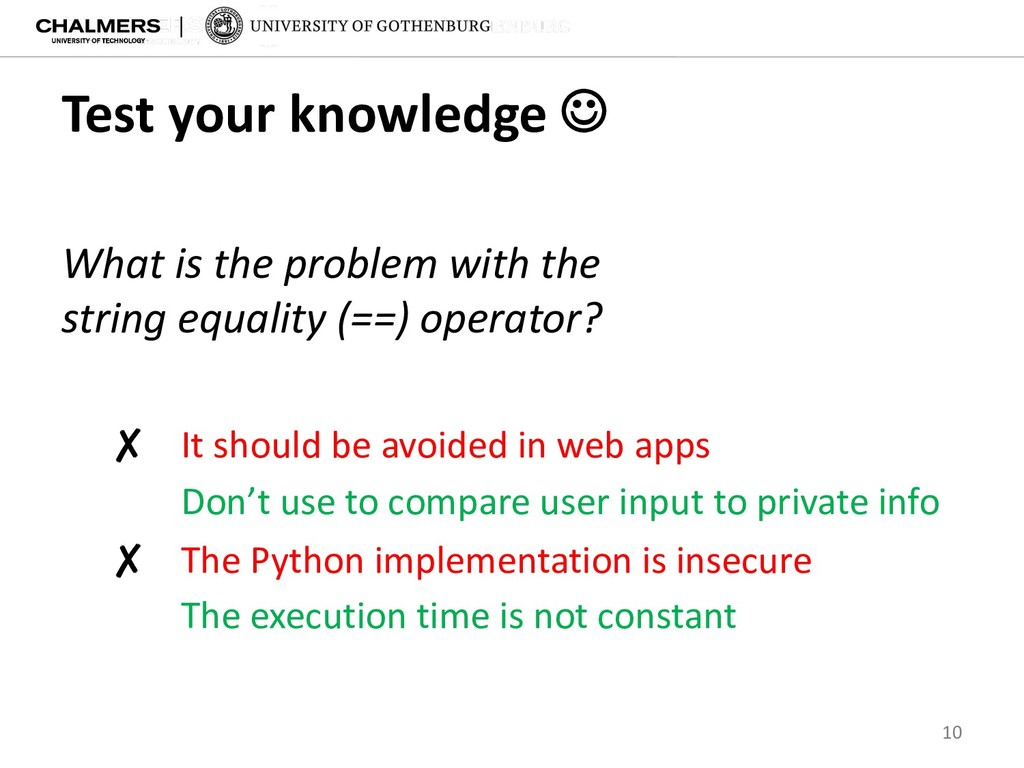
  8. Test your knowledge J What is the problem with the

    string equality (==) operator? ✘ It should be avoided in web apps Don’t use to compare user input to private info ✘ The Python implementation is insecure The execution time is not constant 10
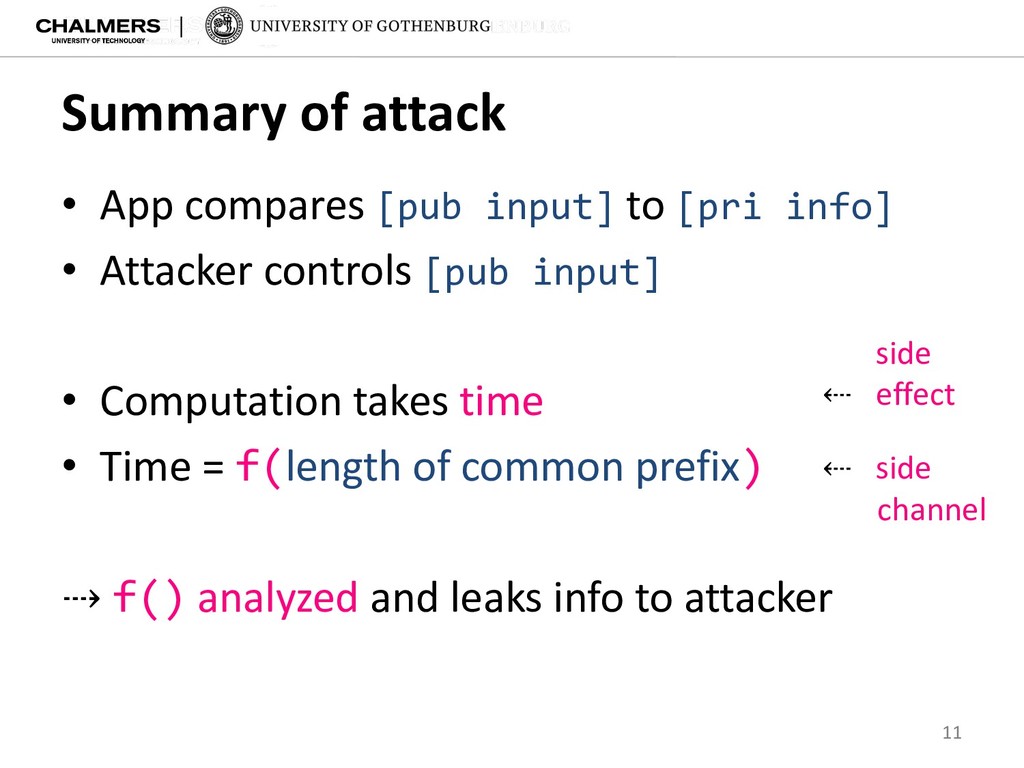
  9. Summary of attack • App compares [pub input] to [pri

    info] • Attacker controls [pub input] • Computation takes time • Time = f(length of common prefix) ⇢ f() analyzed and leaks info to attacker 11 ⇠ side channel side ⇠ effect
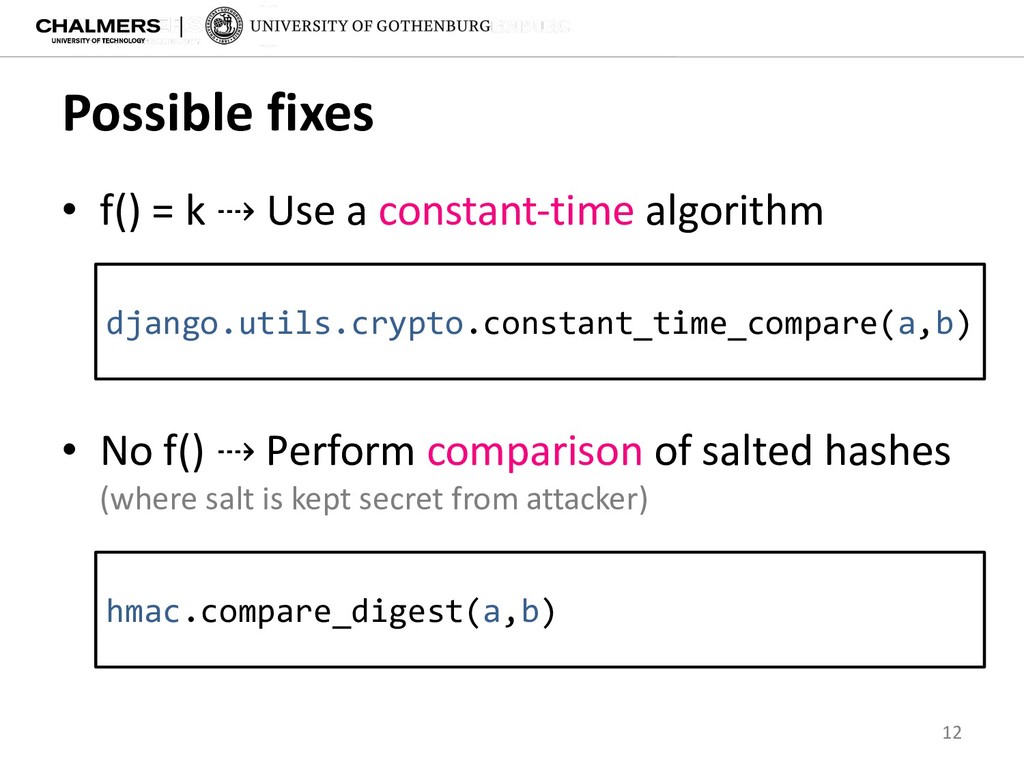
  10. Possible fixes • No f() ⇢ Perform comparison of salted

    hashes (where salt is kept secret from attacker) 12 hmac.compare_digest(a,b) • f() = k ⇢ Use a constant-time algorithm django.utils.crypto.constant_time_compare(a,b)
  11. Challenges for the attacker Measuring such small quantities (!sec) over

    the internet might not be realistic* 13 * S. Crosby, D. Wallach, R. Riedi, Opportunities and Limits of Remote Timing Attacks, TISSEC 12(3), 2009
  12. Further reading • Timing attacks in web apps ⇢ A.

    Bortz, D. Boneh, P. Nandy, Exposing Private Information by Timing Web Applications, WWW 2007 • What can be measured on an inet connection ⇢ S. Crosby, D. Wallach, R. Riedi, Opportunities and Limits of Remote Timing Attacks, TISSEC 12(3), 2009 14