Upgrade to Pro — share decks privately, control downloads, hide ads and more …

Continuous Delivery Techniques for Managing AWS...

Sponsored · SiteGround - Reliable hosting with speed, security, and support you can count on. →

Continuous Delivery Techniques for Managing AWS Accounts

Avatar for rob.godfrey@gmail.com

[email protected]

July 25, 2018

Other Decks in Technology

Transcript

  1. Usage of AWS at the FT • Started pilots in

    2013 • Began migration of workloads in early 2014 • Today 600+ workloads are running in 50+ accounts @robgodfr
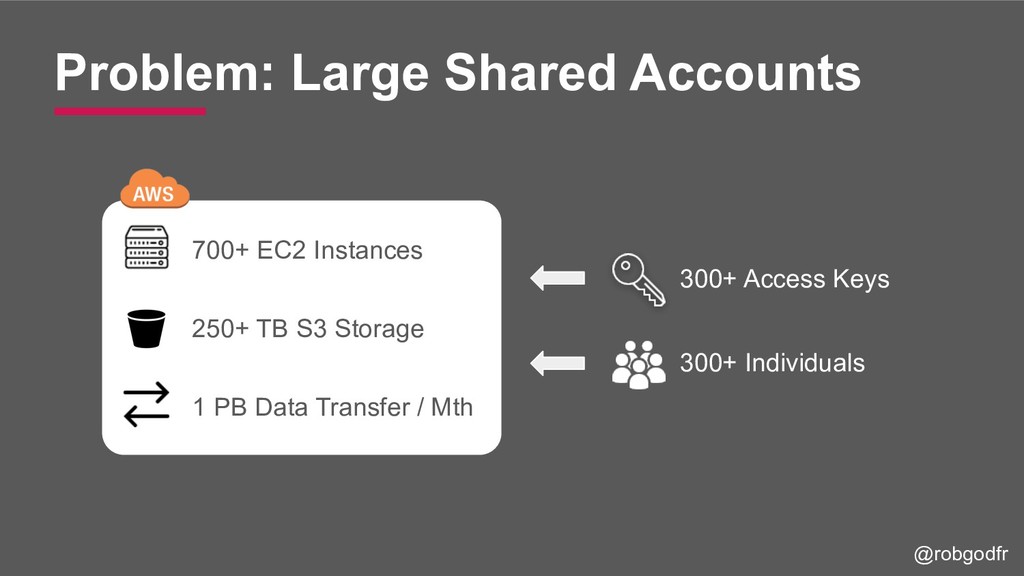
  2. Problem: Large Shared Accounts 700+ EC2 Instances 250+ TB S3

    Storage 1 PB Data Transfer / Mth 300+ Access Keys 300+ Individuals @robgodfr
  3. Motivations for Multiple Accounts • Least privilege access to data

    and resources • Reduced blast radius in event of a security breach • Clearer resource ownership, better cost attribution and improved housekeeping @robgodfr
  4. Challenges • Manual processes for provisioning & updating accounts •

    Significant inconsistencies across accounts • Limited investment in automation or testing 
 @robgodfr
  5. Guiding Principles @robgodfr • Keep everything in version control •

    Create a repeatable, reliable process for releasing software • Automate almost everything • Build quality in
  6. Where are we today? @robgodfr • All baseline infrastructure managed

    in source control • Resource definitions packaged into reusable modules • Consistent infrastructure across accounts • Automated pipelines for release and deployment • Infrastructure tests ensure a low deployment failure rate
  7. @robgodfr 1. Reusable Modules for Infrastructure 2. Building Accounts using

    Modules 3. Management of many AWS Accounts What will we cover?
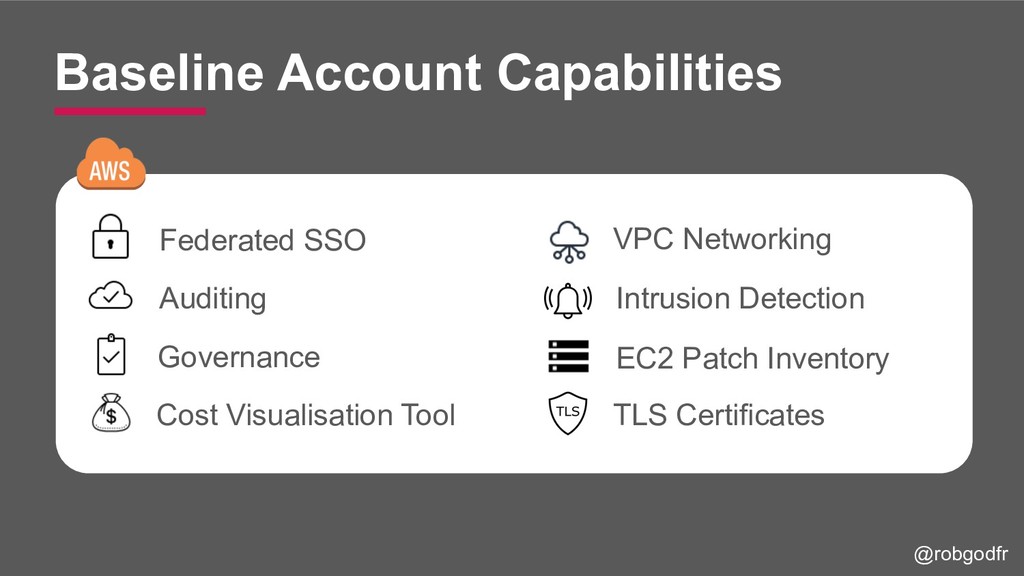
  8. Baseline Account Capabilities @robgodfr Federated SSO Auditing Cost Visualisation Tool

    VPC Networking TLS Certificates Intrusion Detection EC2 Patch Inventory Governance
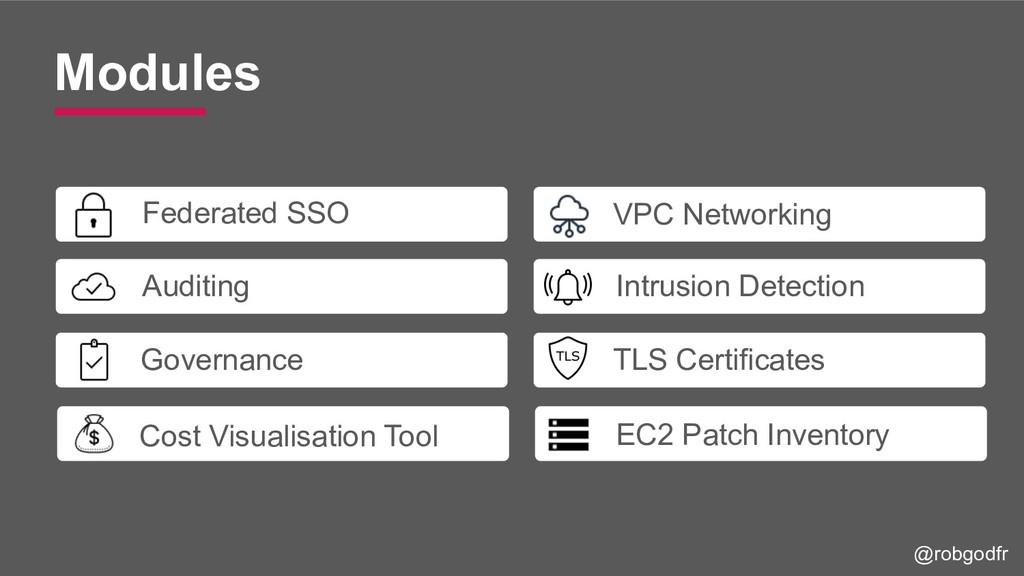
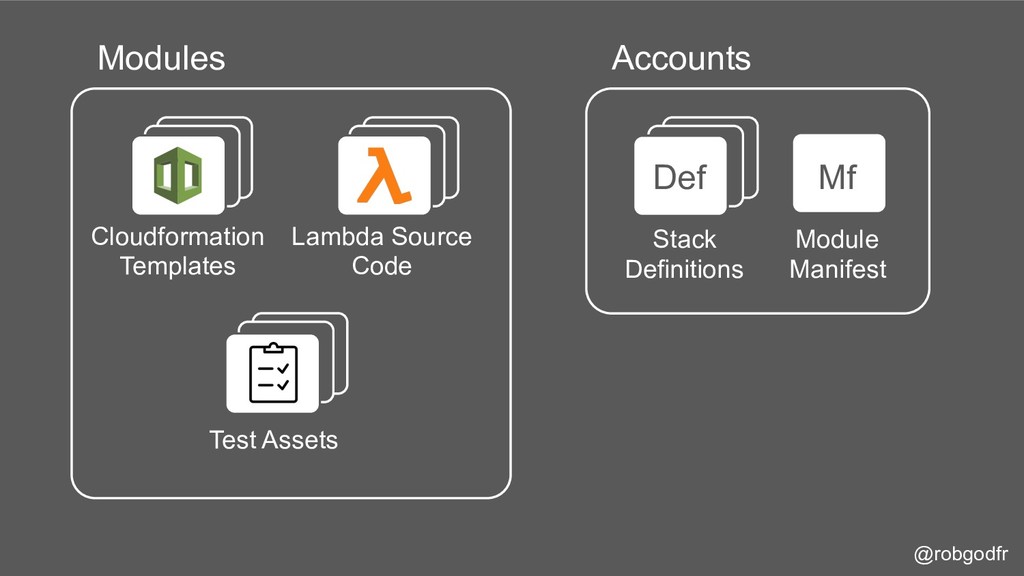
  9. Modules @robgodfr Federated SSO Auditing Cost Visualisation Tool VPC Networking

    TLS Certificates Intrusion Detection EC2 Patch Inventory Governance
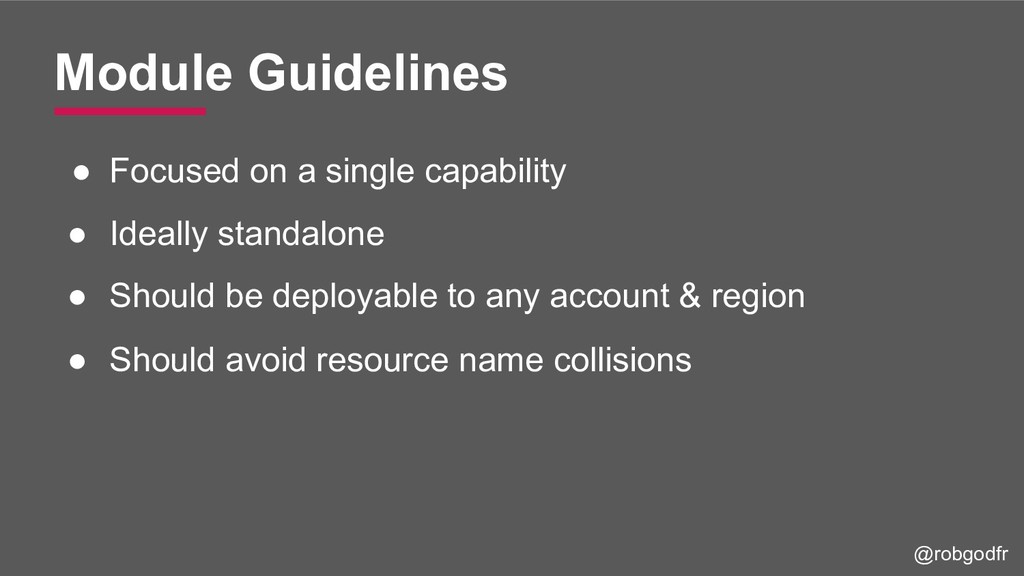
  10. Module Guidelines @robgodfr • Focused on a single capability •

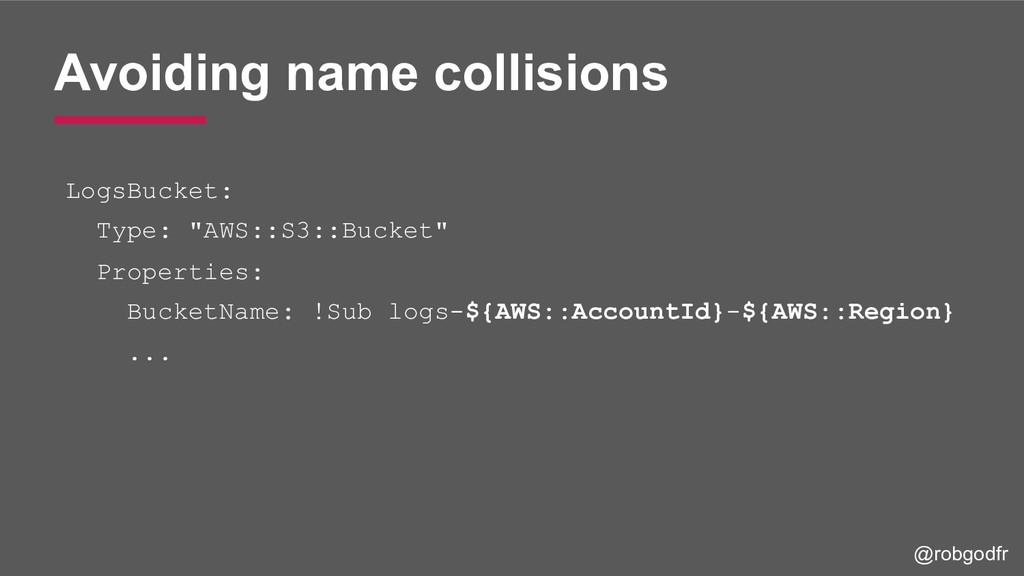
    Ideally standalone • Should be deployable to any account & region • Should avoid resource name collisions
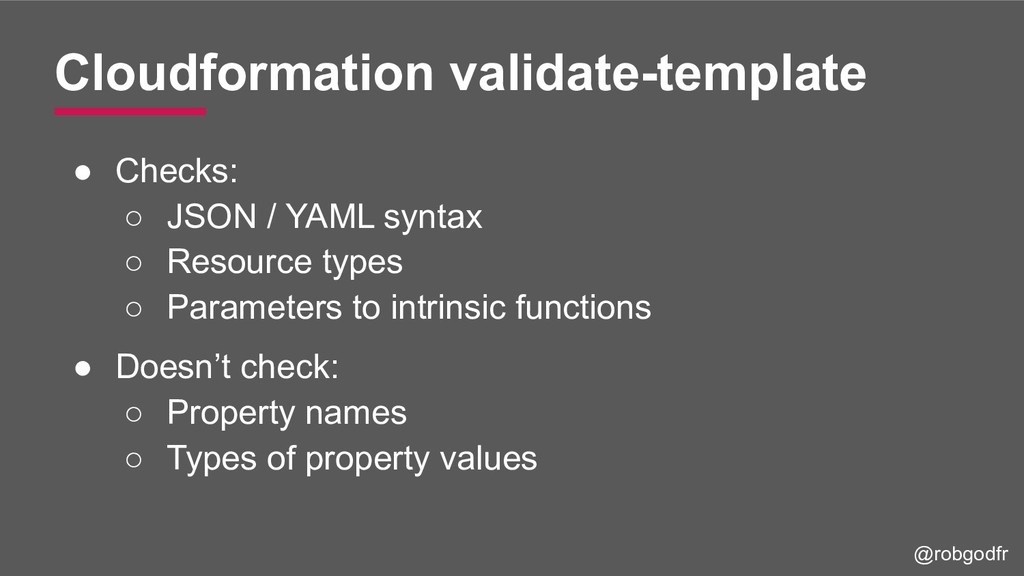
  11. Cloudformation validate-template @robgodfr • Checks: ◦ JSON / YAML syntax

    ◦ Resource types ◦ Parameters to intrinsic functions • Doesn’t check: ◦ Property names ◦ Types of property values
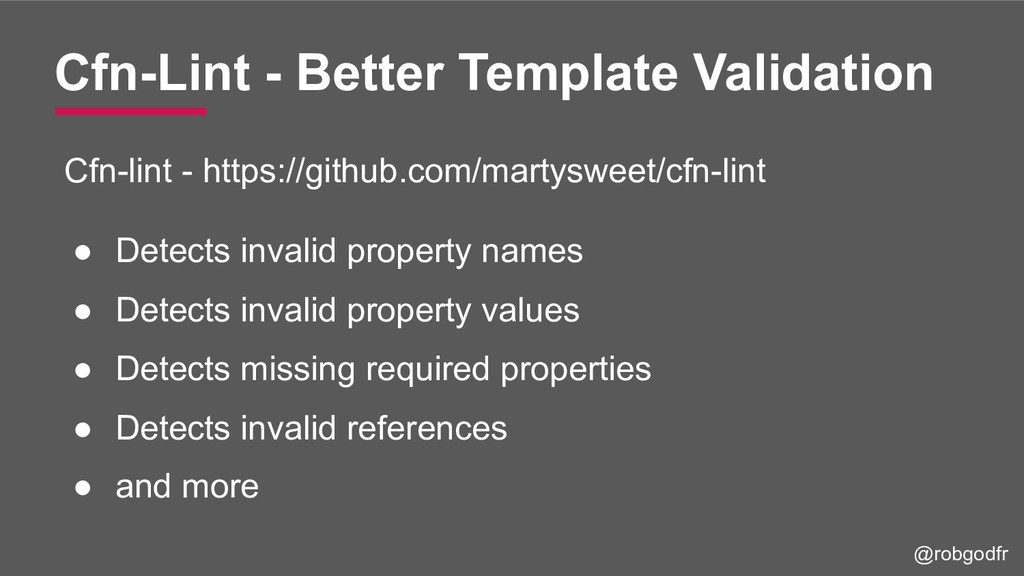
  12. Cfn-Lint - Better Template Validation @robgodfr Cfn-lint - https://github.com/martysweet/cfn-lint •

    Detects invalid property names • Detects invalid property values • Detects missing required properties • Detects invalid references • and more
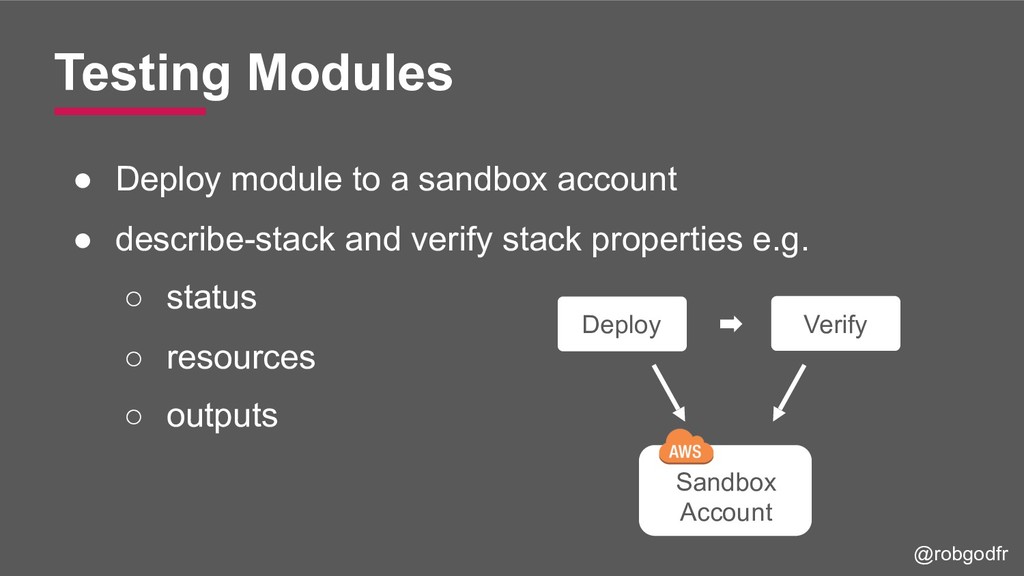
  13. Testing Modules @robgodfr • Deploy module to a sandbox account

    • describe-stack and verify stack properties e.g. ◦ status ◦ resources ◦ outputs Sandbox Account Deploy Verify
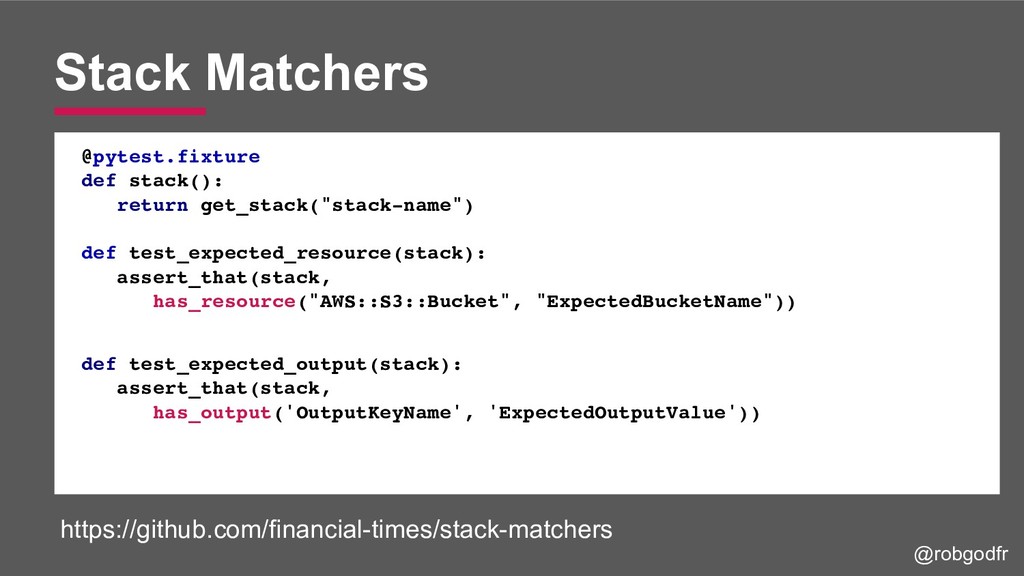
  14. Stack Matchers @robgodfr @pytest.fixture def stack(): return get_stack("stack-name") def test_expected_resource(stack):

    assert_that(stack, has_resource("AWS::S3::Bucket", "ExpectedBucketName")) def test_expected_output(stack): assert_that(stack, has_output('OutputKeyName', 'ExpectedOutputValue')) https://github.com/financial-times/stack-matchers
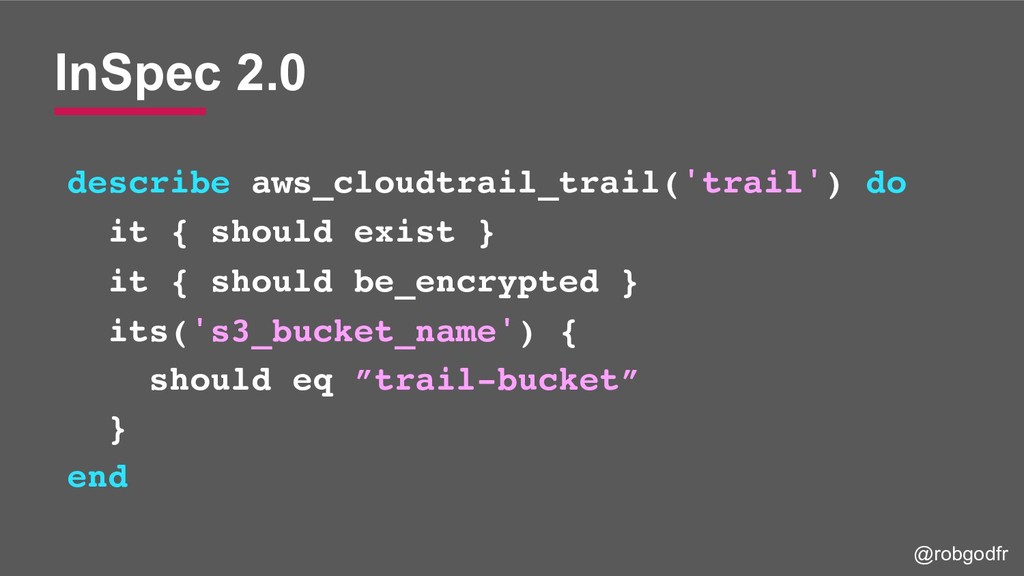
  15. InSpec 2.0 @robgodfr describe aws_cloudtrail_trail('trail') do
 it { should exist

    }
 it { should be_encrypted }
 its('s3_bucket_name') { should eq ”trail-bucket” }
 end
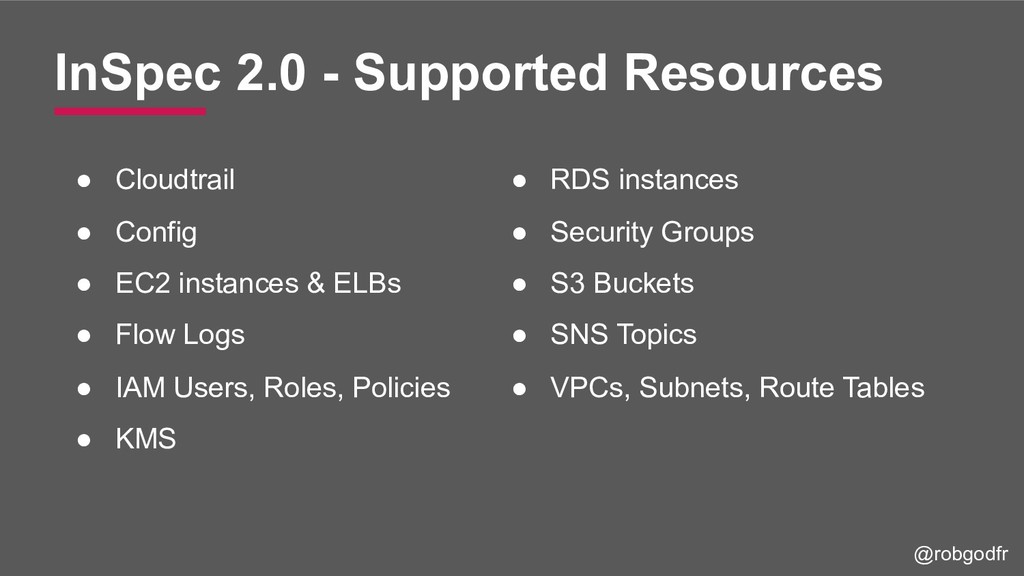
  16. InSpec 2.0 - Supported Resources @robgodfr • Cloudtrail • Config

    • EC2 instances & ELBs • Flow Logs • IAM Users, Roles, Policies • KMS • RDS instances • Security Groups • S3 Buckets • SNS Topics • VPCs, Subnets, Route Tables
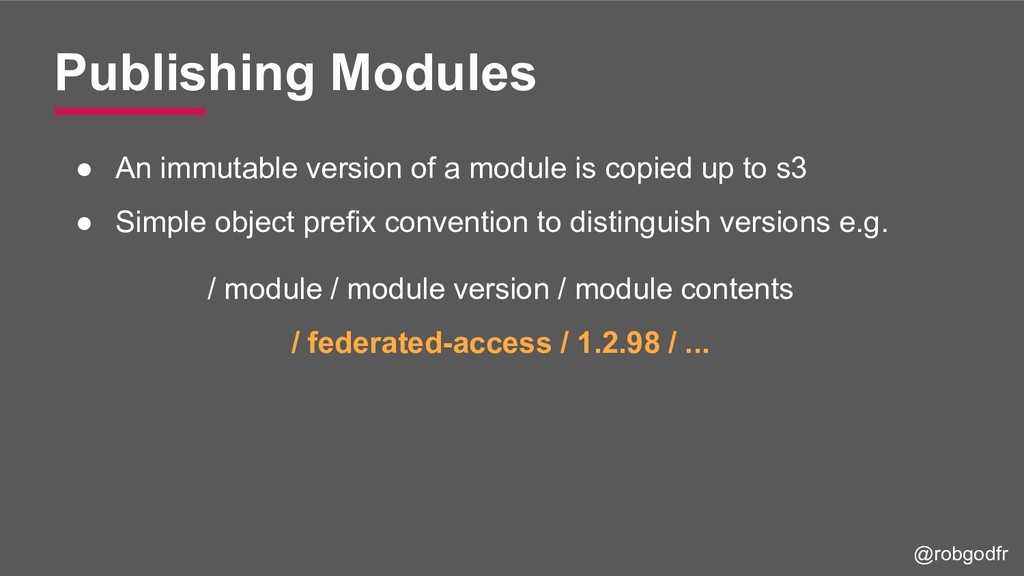
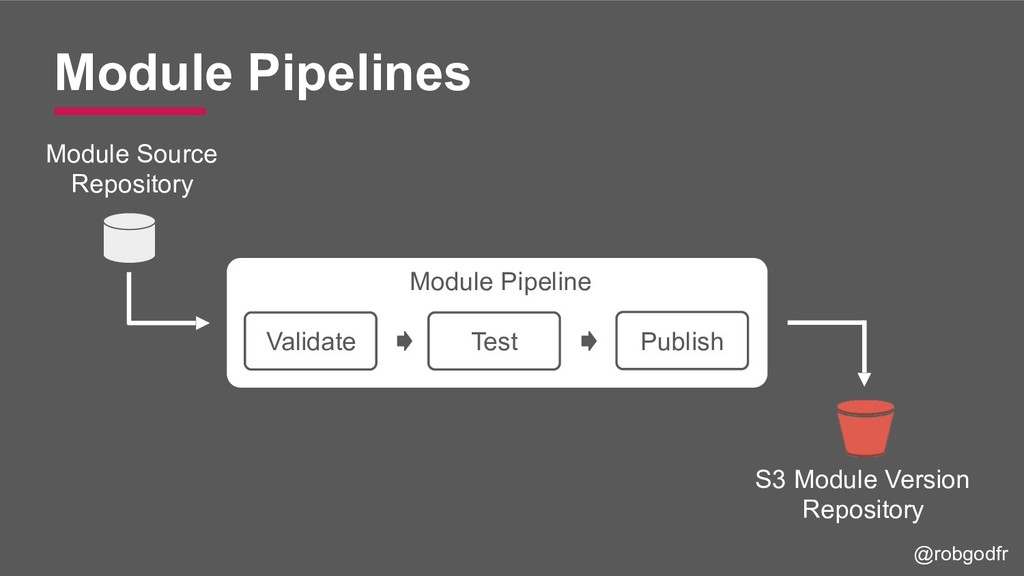
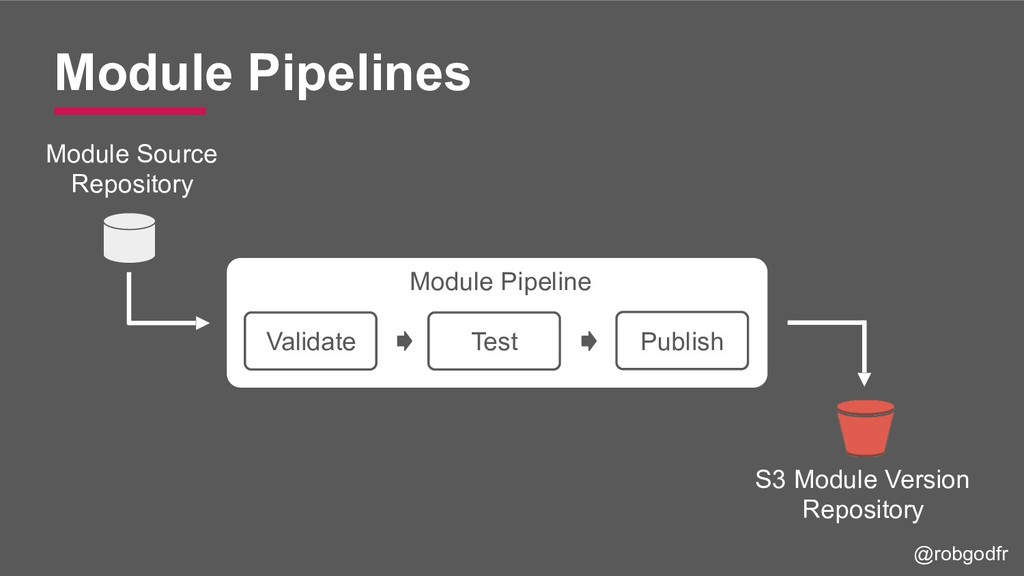
  17. Publishing Modules @robgodfr • An immutable version of a module

    is copied up to s3 • Simple object prefix convention to distinguish versions e.g. / module / module version / module contents / federated-access / 1.2.98 / ...
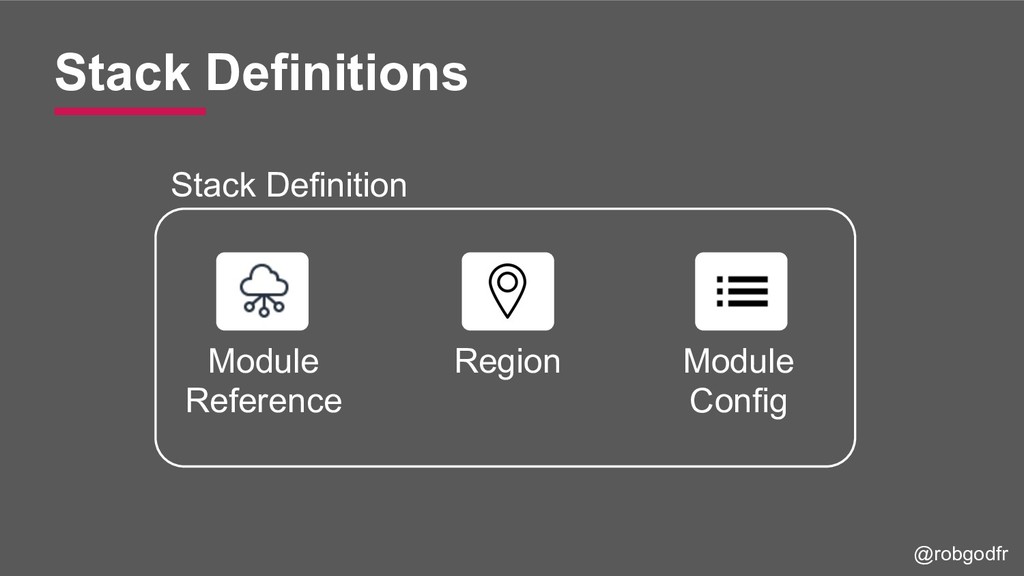
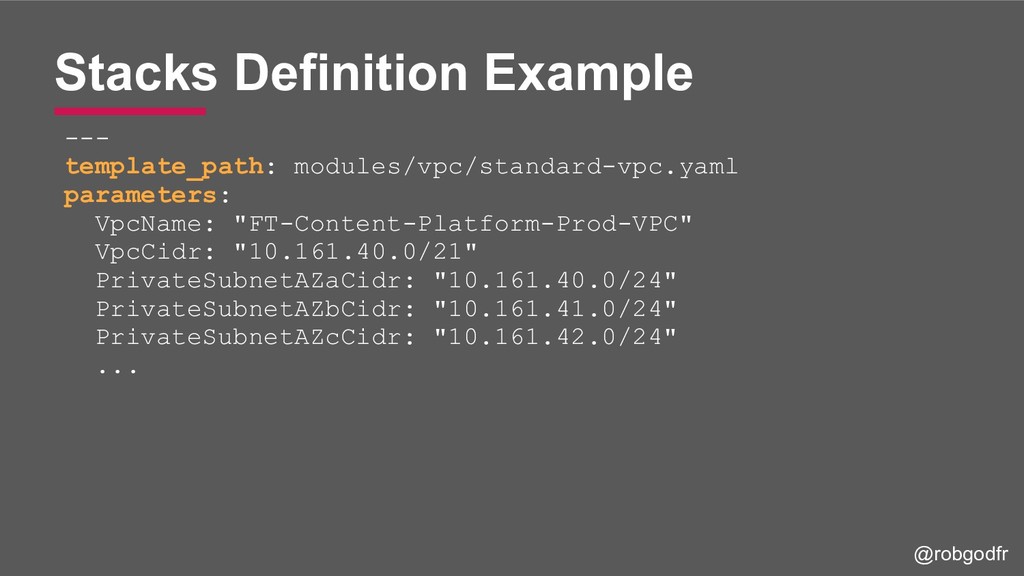
  18. Stacks Definition Example --- template_path: modules/vpc/standard-vpc.yaml parameters: VpcName: "FT-Content-Platform-Prod-VPC" VpcCidr:

    "10.161.40.0/21" PrivateSubnetAZaCidr: "10.161.40.0/24" PrivateSubnetAZbCidr: "10.161.41.0/24" PrivateSubnetAZcCidr: "10.161.42.0/24" ... @robgodfr
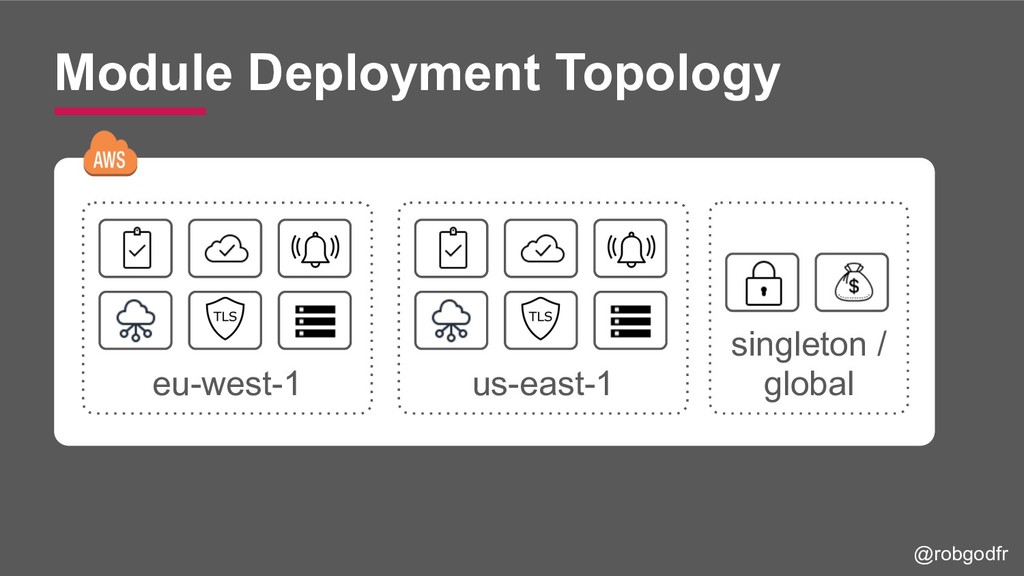
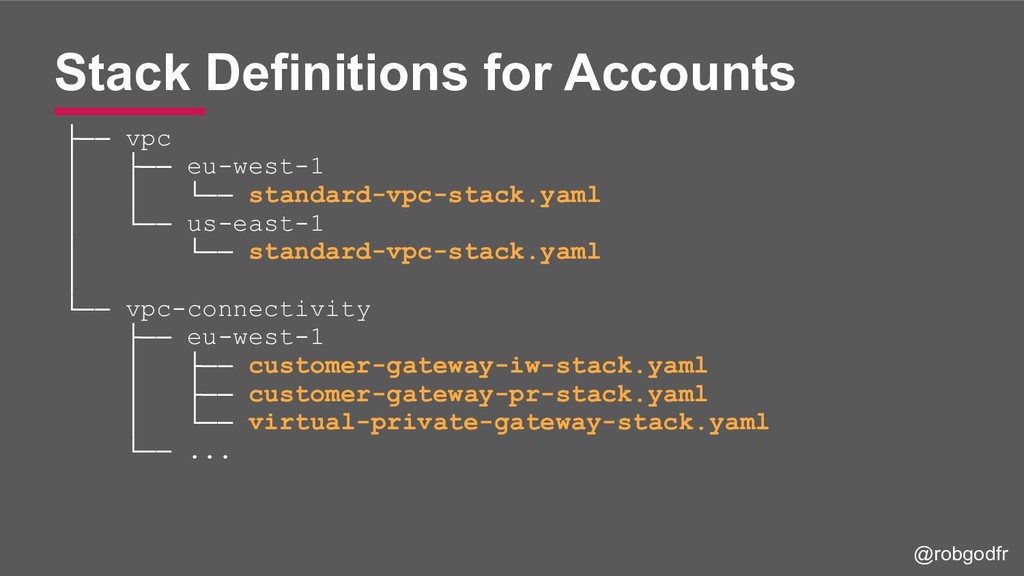
  19. Stack Definitions for Accounts ├── vpc │ ├── eu-west-1 │

    │ └── standard-vpc-stack.yaml │ └── us-east-1 │ └── standard-vpc-stack.yaml │ └── vpc-connectivity ├── eu-west-1 │ ├── customer-gateway-iw-stack.yaml │ ├── customer-gateway-pr-stack.yaml │ └── virtual-private-gateway-stack.yaml └── ... @robgodfr
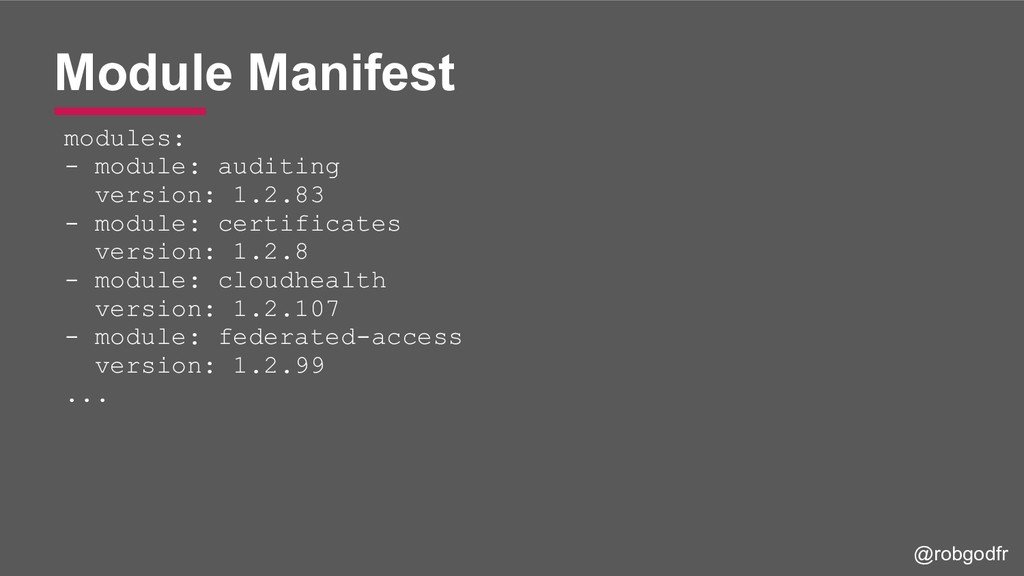
  20. Module Manifest modules: - module: auditing version: 1.2.83 - module:

    certificates version: 1.2.8 - module: cloudhealth version: 1.2.107 - module: federated-access version: 1.2.99 ... @robgodfr
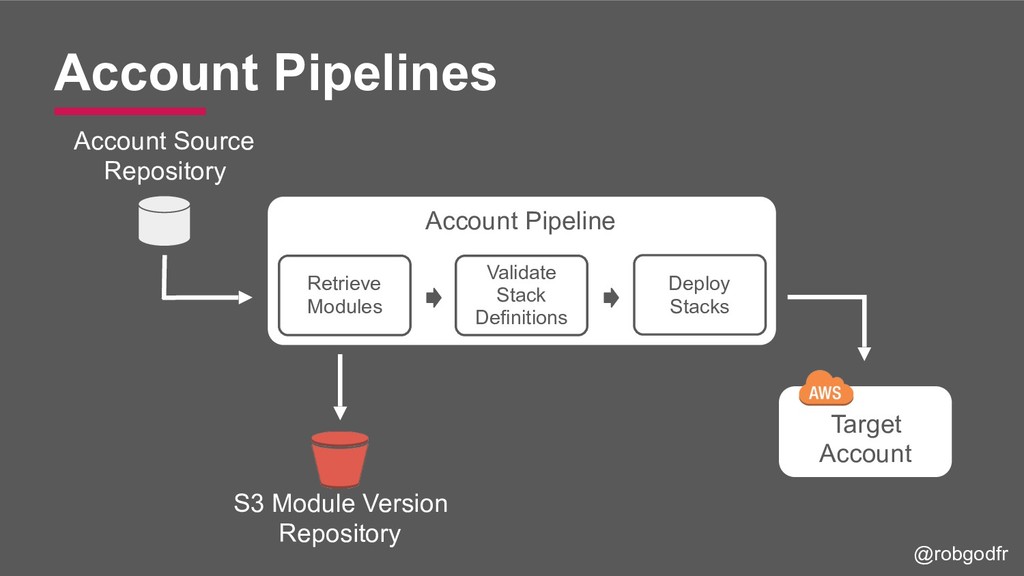
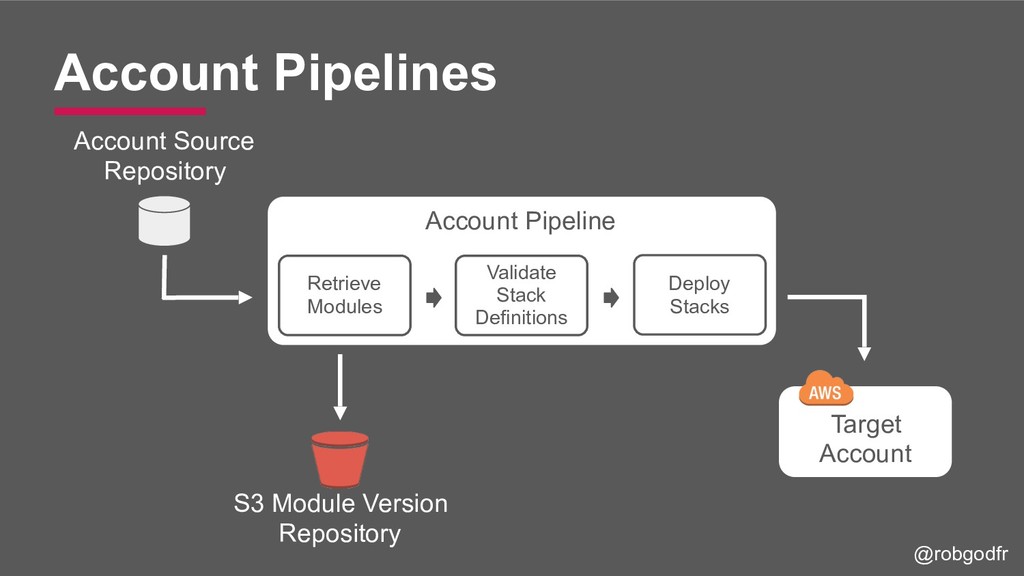
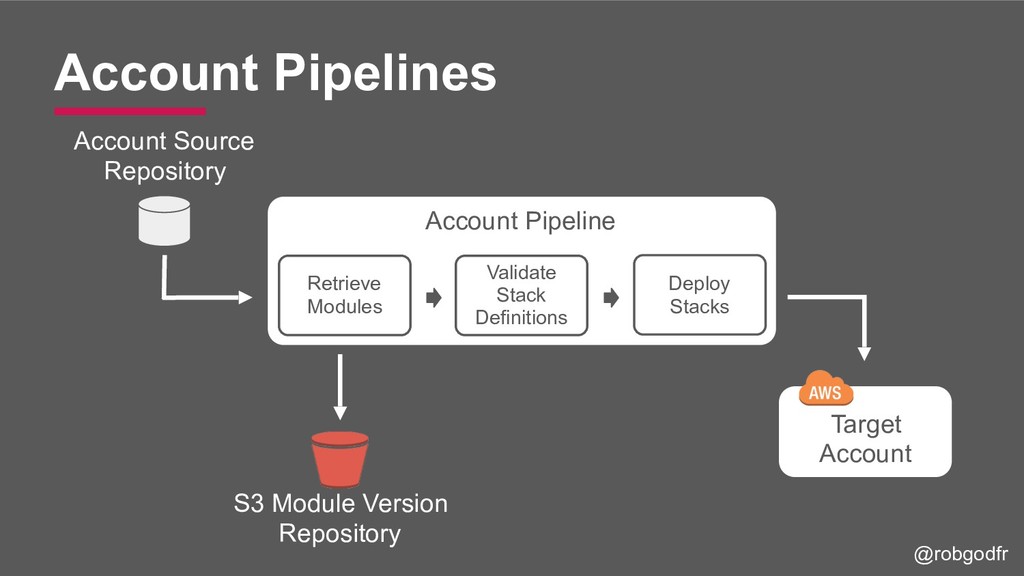
  21. Account Pipelines Retrieve Modules @robgodfr Validate Stack Definitions Deploy Stacks

    S3 Module Version Repository Target Account Account Pipeline Account Source Repository
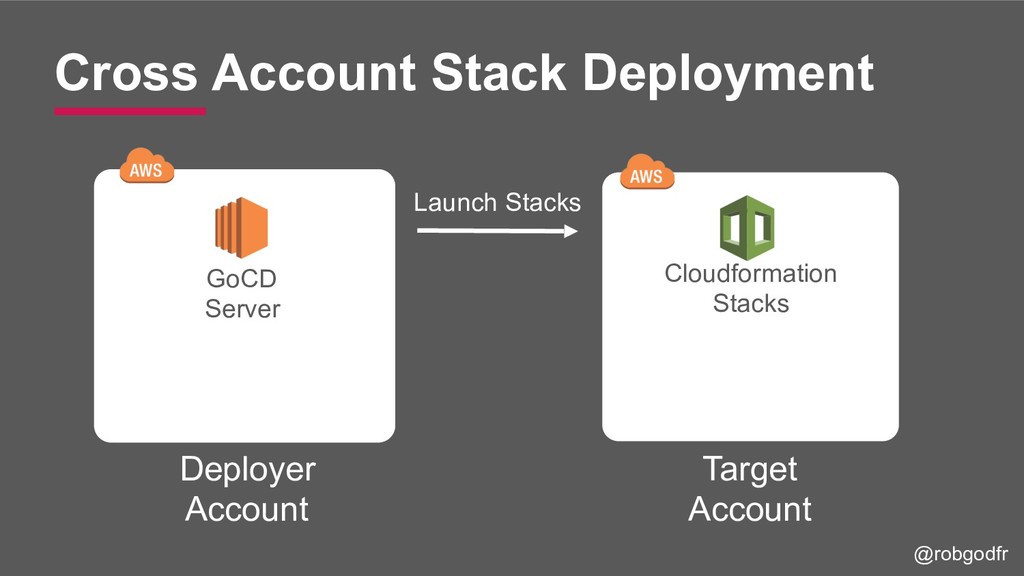
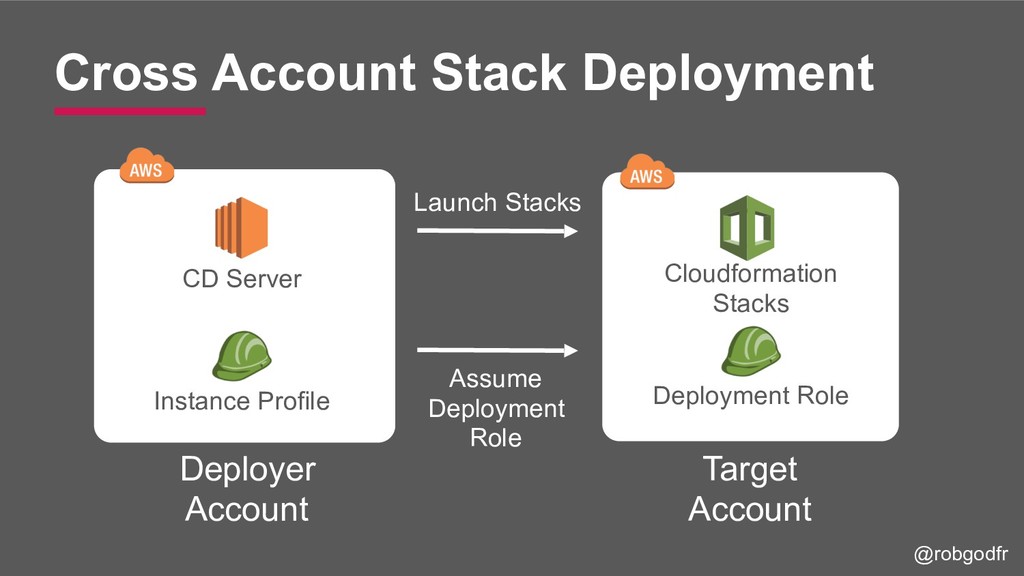
  22. Cross Account Stack Deployment @robgodfr CD Server Deployment Role Instance

    Profile Launch Stacks Cloudformation Stacks Assume Deployment Role Target Account Deployer Account
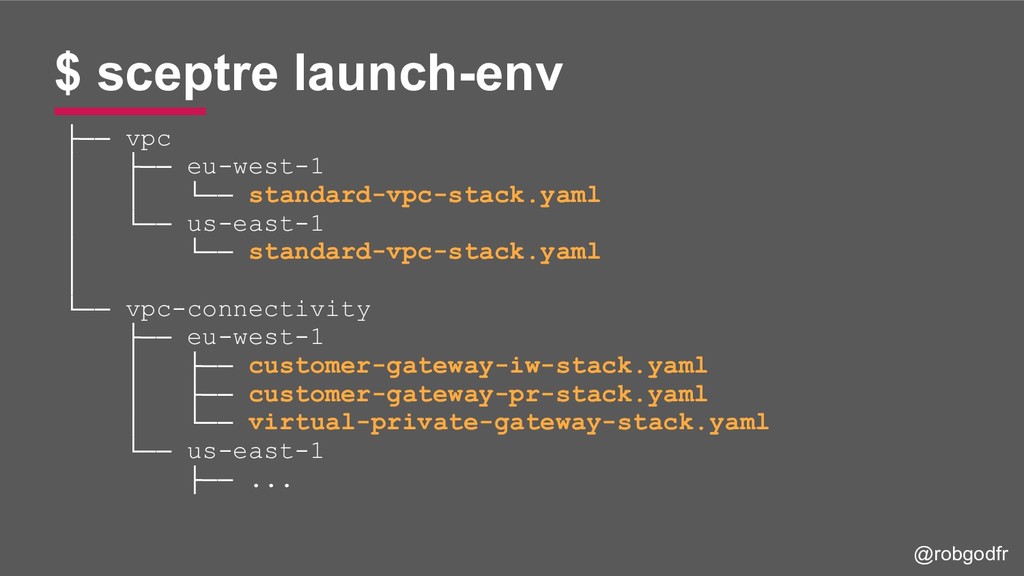
  23. $ sceptre launch-env ├── vpc │ ├── eu-west-1 │ │

    └── standard-vpc-stack.yaml │ └── us-east-1 │ └── standard-vpc-stack.yaml │ └── vpc-connectivity ├── eu-west-1 │ ├── customer-gateway-iw-stack.yaml │ ├── customer-gateway-pr-stack.yaml │ └── virtual-private-gateway-stack.yaml └── us-east-1 ├── ... @robgodfr
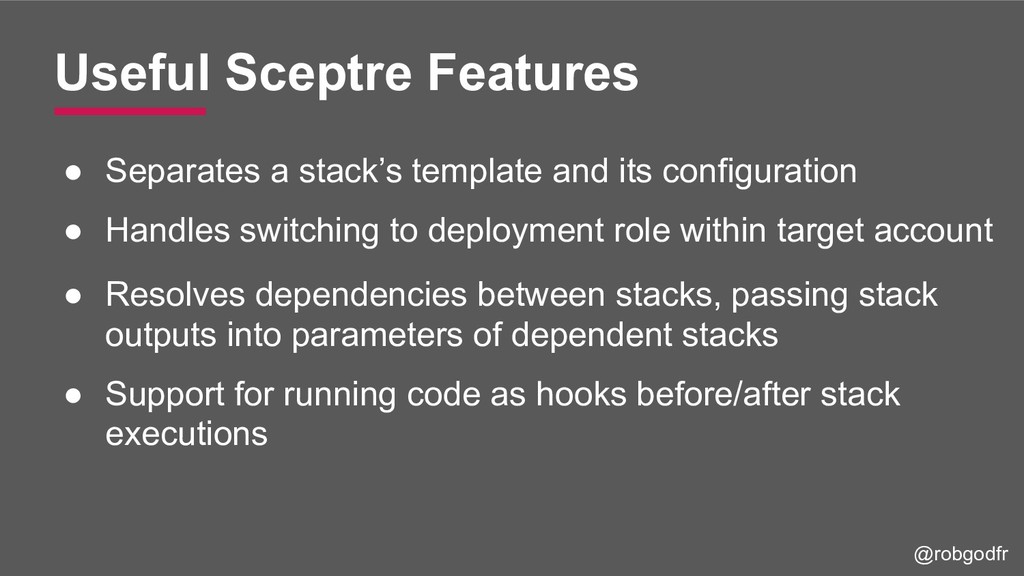
  24. Useful Sceptre Features • Separates a stack’s template and its

    configuration • Handles switching to deployment role within target account • Resolves dependencies between stacks, passing stack outputs into parameters of dependent stacks • Support for running code as hooks before/after stack executions @robgodfr
  25. Account Pipelines Retrieve Modules @robgodfr Validate Stack Definitions Deploy Stacks

    S3 Module Version Repository Target Account Account Pipeline Account Source Repository
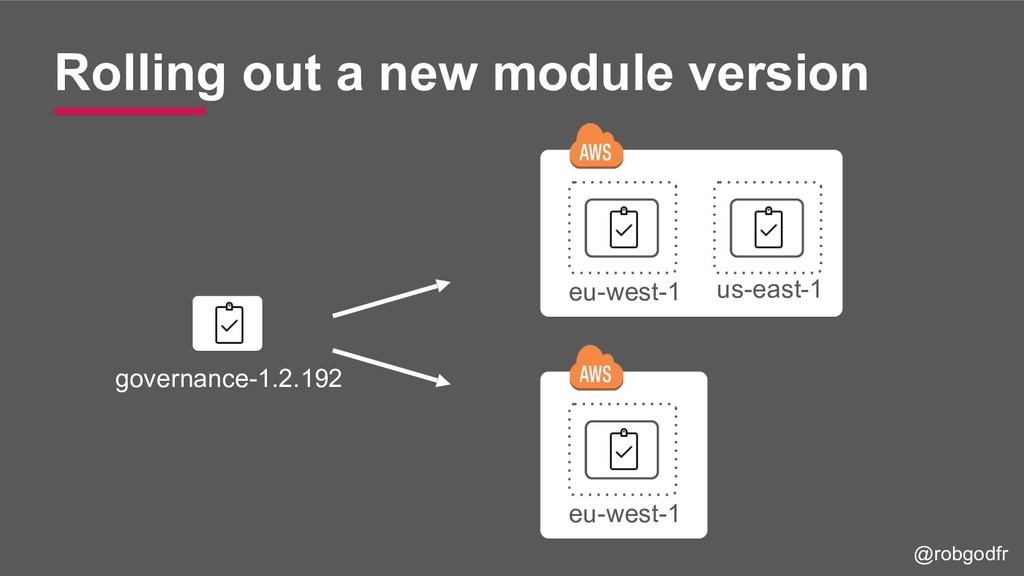
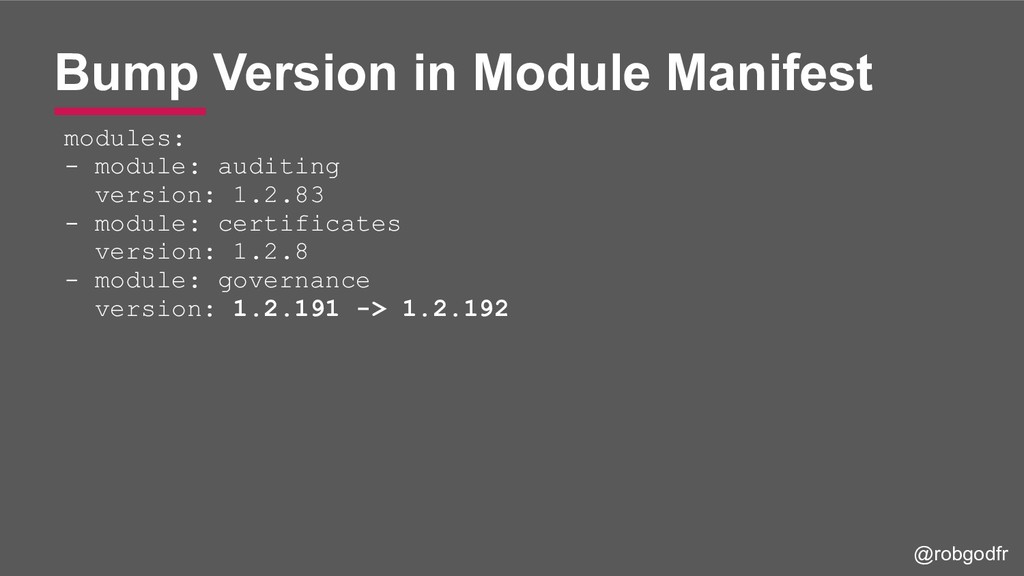
  26. Bump Version in Module Manifest modules: - module: auditing version:

    1.2.83 - module: certificates version: 1.2.8 - module: governance version: 1.2.191 -> 1.2.192 @robgodfr
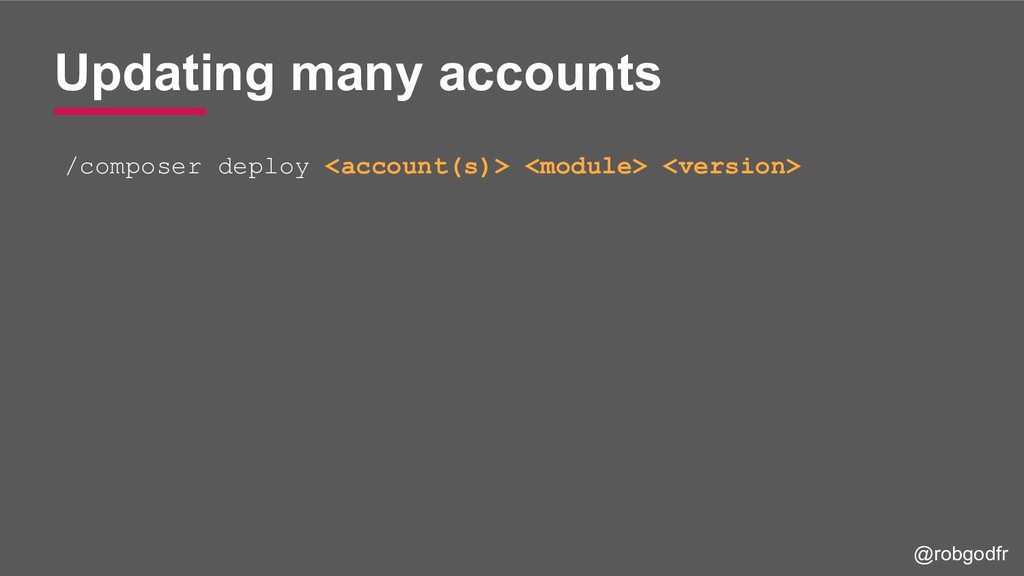
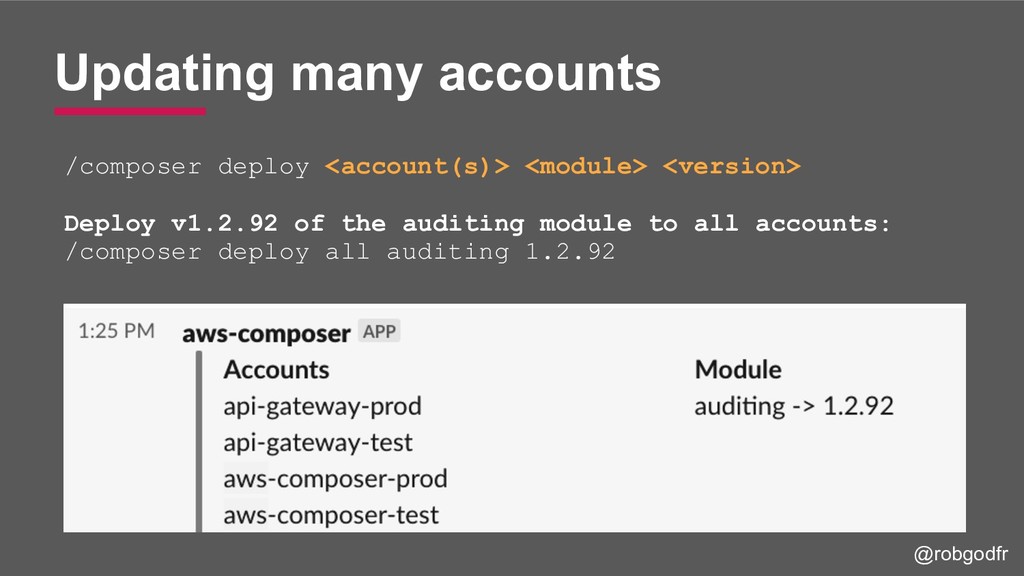
  27. Updating many accounts /composer deploy <account(s)> <module> <version> Deploy v1.2.92
    of the auditing module to all accounts: /composer deploy all auditing 1.2.92 @robgodfr
  28. Account Pipelines Retrieve Modules @robgodfr Validate Stack Definitions Deploy Stacks

    S3 Module Version Repository Target Account Account Pipeline Account Source Repository