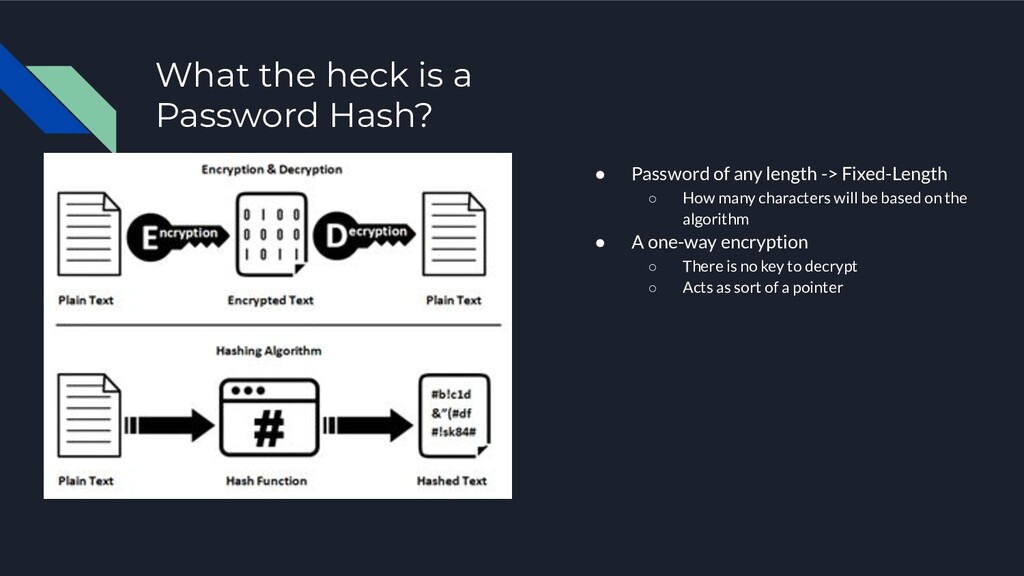
any length -> Fixed-Length ◦ How many characters will be based on the algorithm • A one-way encryption ◦ There is no key to decrypt ◦ Acts as sort of a pointer
calculate ▪ But not TOO easy for password hashes; otherwise brute force attacks become too easy ◦ Be infeasible to reverse ▪ Hashes should be one-way functions ▪ Otherwise, someone could determine passwords from hashes ◦ Be sensitive to changes - avalanche effect ◦ Be deterministic ◦ Have minimal collisions ▪ Ideally, two distinct pieces of data should not result in the same hash ◦ Not reveal anything about the data
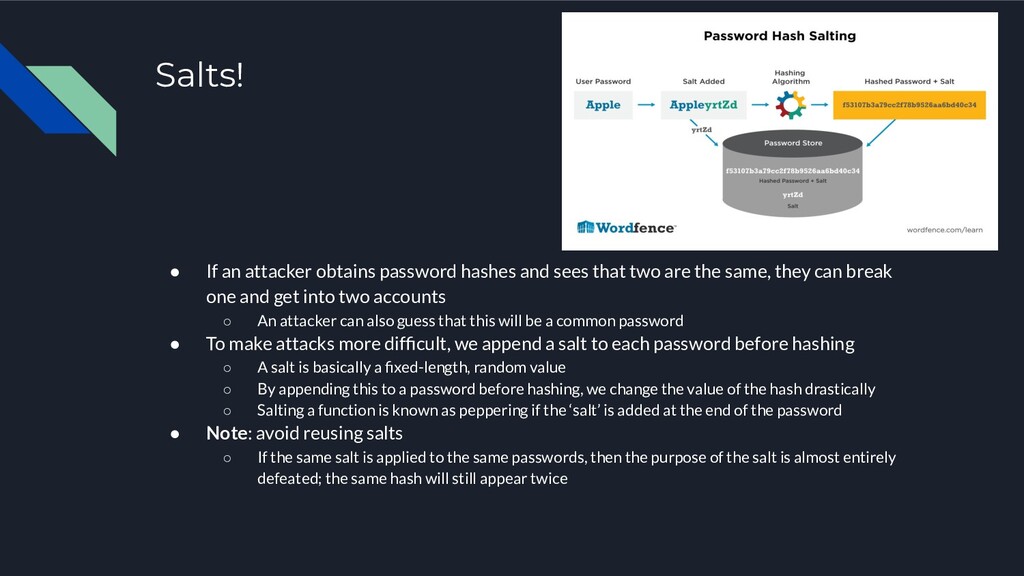
that two are the same, they can break one and get into two accounts ◦ An attacker can also guess that this will be a common password • To make attacks more difficult, we append a salt to each password before hashing ◦ A salt is basically a fixed-length, random value ◦ By appending this to a password before hashing, we change the value of the hash drastically ◦ Salting a function is known as peppering if the ‘salt’ is added at the end of the password • Note: avoid reusing salts ◦ If the same salt is applied to the same passwords, then the purpose of the salt is almost entirely defeated; the same hash will still appear twice
you enter your password, gets sent to some server somewhere ◦ How does the server check if the entered password is correct? ▪ Storing password in plaintext == BAD • If When a hacker gets onto the system, they can get passwords easily • Malicious employees can also easily obtain passwords • Plaintext Offenders • How good is your password? ▪ Encrypting passwords is better, but not great • Encryption is designed to be undone; we don’t want that with passwords ▪ Hashing is the single best option • By hashing your entered password and comparing that to a database of password hashes, we reduce the chance of anyone finding out your password • Some companies will hash, encrypt, and then hash again, adding extra layers of protection
you have downloaded some file or someone has sent you some file ◦ How do you know you received the right file? ▪ What if someone intercepted the traffic and changed the file? ◦ Hashes allow us to verify file integrity • These are the main applications, although others do exist in the world of cheese
the same hash ◦ Because there are infinite possibilities for passwords, and there exists only a finite mathematical mapping for hashes, there is bound to be a repeat ▪ As a general rule of thumb, the more bits that that an encryption algorithm outputs, the better
of password hashes. What’s the worst case scenario? • Brute force attacks are always an option ◦ An attacker can generate every possible password, hash that, and see if that matches the target hash ◦ Brute force attacks take a while, but quickly-calculated hashes make it easier • Dictionary Attacks ◦ The idea of tools like hydra and hashcat ◦ Feed in a word list, and try the passwords from the list ◦ One of the most common PW list, rockyou.txt • Rainbow tables make things even easier ◦ A rainbow table is a list of pre-computed hashes and their inputs ◦ By comparing a target hash against a rainbow table, an attacker can potentially crack a hash much sooner
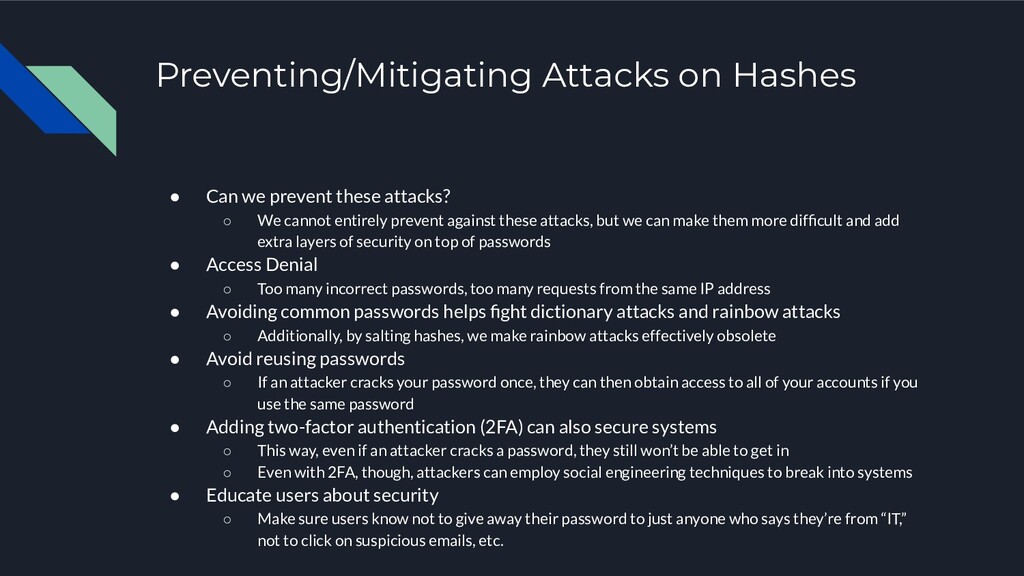
◦ We cannot entirely prevent against these attacks, but we can make them more difficult and add extra layers of security on top of passwords • Access Denial ◦ Too many incorrect passwords, too many requests from the same IP address • Avoiding common passwords helps fight dictionary attacks and rainbow attacks ◦ Additionally, by salting hashes, we make rainbow attacks effectively obsolete • Avoid reusing passwords ◦ If an attacker cracks your password once, they can then obtain access to all of your accounts if you use the same password • Adding two-factor authentication (2FA) can also secure systems ◦ This way, even if an attacker cracks a password, they still won’t be able to get in ◦ Even with 2FA, though, attackers can employ social engineering techniques to break into systems • Educate users about security ◦ Make sure users know not to give away their password to just anyone who says they’re from “IT,” not to click on suspicious emails, etc.


 unt_csc
 mfonobong
 erikaheidi
 rabernat
 lindahogenes
 aleyda
 baasie
 jct
 cassininazir
 axbom
 auna
 keathley
 inesmontani