Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
jsconf.uy - Death to Cookies Long Live Tokens
Search
Matias Woloski
March 15, 2014
Technology
45
0
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
jsconf.uy - Death to Cookies Long Live Tokens
Matias Woloski
March 15, 2014
More Decks by Matias Woloski
See All by Matias Woloski
Death to Cookies, Long Live JSON Web Tokens
woloski
2
270
Death to Cookies Long Live Tokens - Gluecon 2014
woloski
0
180
Death to Cookies, Long Live Tokens
woloski
5
690
Other Decks in Technology
See All in Technology
Active Record Connection Adaptersにおける長年の課題に再び取り組む
yahonda
0
250
会社紹介資料 / Sansan Company Profile
sansan33
PRO
31
430k
スキマバイトという雇用形態は存在しないので、雇用期間1日のアルバイト契約を事業者とワーカーが結ぶ手続きを支えるのがタイミーなんです
akitoshiga
0
210
AIがコードを書く時代に、エンジニアは何で自分の価値を証明するのか / In an era where AI writes code how do engineers prove their value
carta_engineering
3
1.1k
Gemini Intelligence 入門 ― AppFunctions と Gemini Nano
takuroabe
0
310
会社説明資料
persolserverworks
0
9.8k
AI コーディングと人間の認知スループット / CTO Night & Day 2026 Morning Session / AI Coding and Human Cognitive Throughput
prog893
5
1.3k
事業成長とデータ活用を止めないためのマネジメントへ挑戦
hiracky16
0
410
USB PDを使ってスマホを労わりたい
raspython3
0
180
ソフトウェア ファクトリー - 再現性のあるソフトウェアの工場づくり / Software factory
iktakahiro
7
5.1k
Temporal 最高!でも改めて「日付」について調べたら人類の負債すぎる件
riyaamemiya
0
190
初海外で注意すべきこと12選!!!安全快適なre:invent生活にするために
yuuuuuuu168
1
180
Featured
See All Featured
No one is an island. Learnings from fostering a developers community.
thoeni
21
3.9k
JavaScript: Past, Present, and Future - NDC Porto 2020
reverentgeek
52
6.1k
職位にかかわらず全員がリーダーシップを発揮するチーム作り / Building a team where everyone can demonstrate leadership regardless of position
madoxten
69
67k
State of Search Keynote: SEO is Dead Long Live SEO
ryanjones
0
320
Designing for humans not robots
tammielis
254
26k
Fight the Zombie Pattern Library - RWD Summit 2016
marcelosomers
234
18k
Conquering PDFs: document understanding beyond plain text
inesmontani
PRO
4
3.2k
What does AI have to do with Human Rights?
axbom
PRO
1
2.5k
A better future with KSS
kneath
240
18k
Being A Developer After 40
akosma
92
590k
The Impact of AI in SEO - AI Overviews June 2024 Edition
aleyda
6
1.2k
Exploring the Power of Turbo Streams & Action Cable | RailsConf2023
kevinliebholz
37
6.6k
Transcript
Death to Cookies Long Live Tokens @woloski @jfroma
None
None
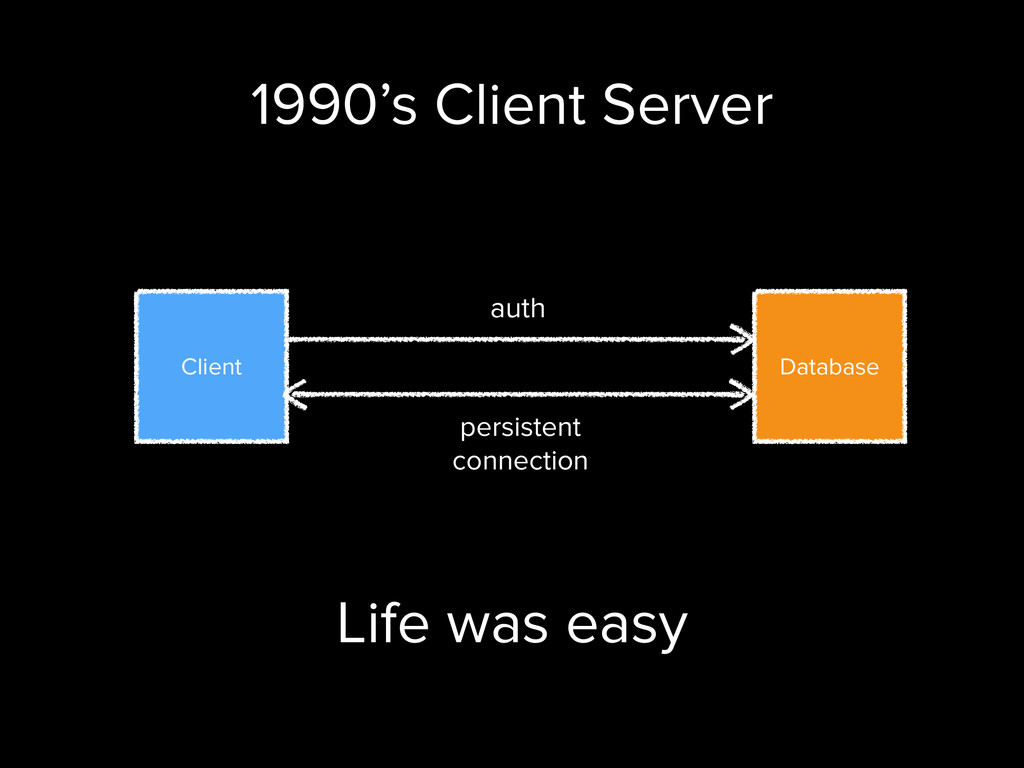
Client Database auth persistent connection 1990’s Client Server Life was
easy
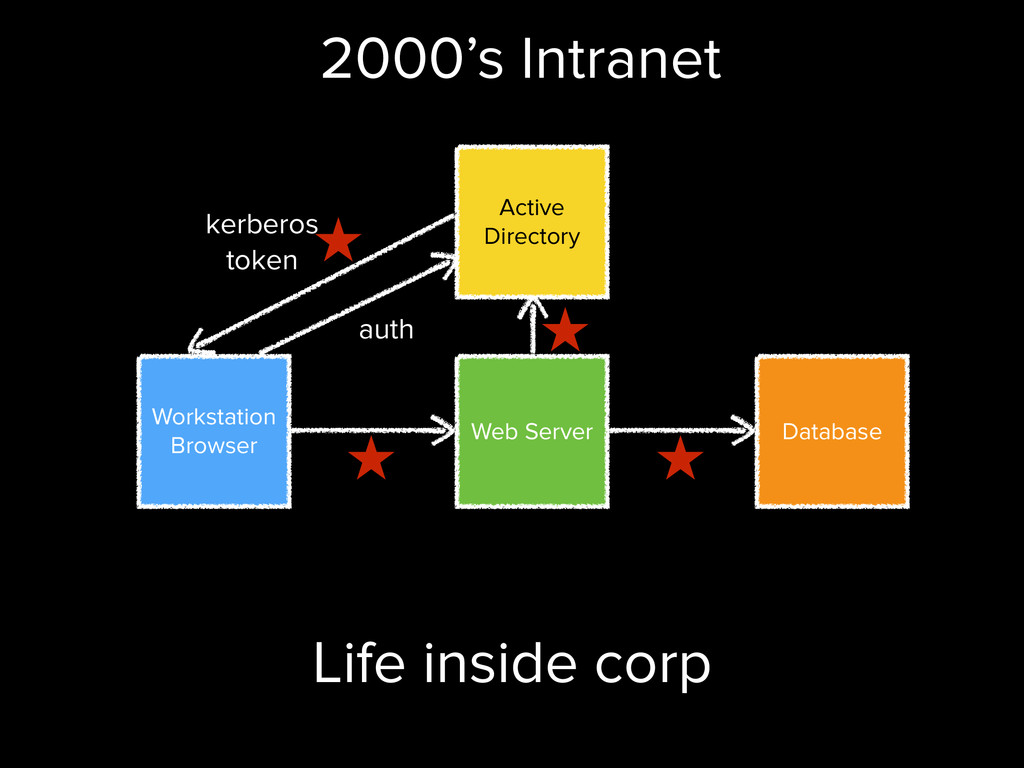
Workstation Browser Database auth 2000’s Intranet Web Server Active Directory
kerberos token Life inside corp
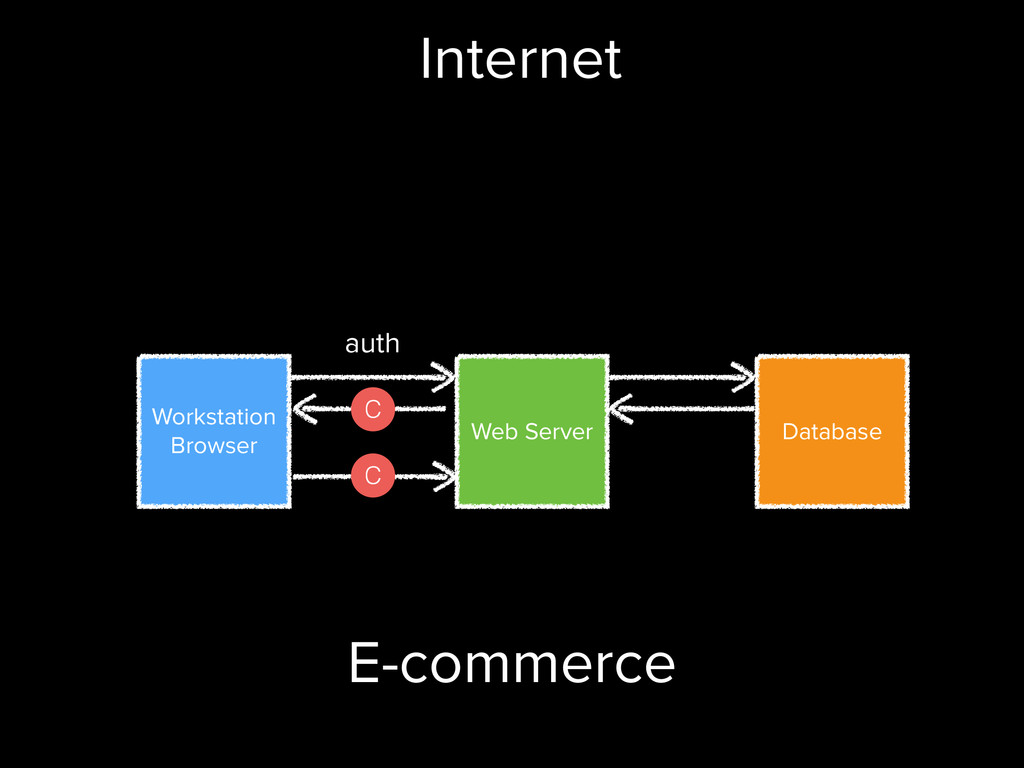
Workstation Browser Database Internet Web Server auth C C E-commerce
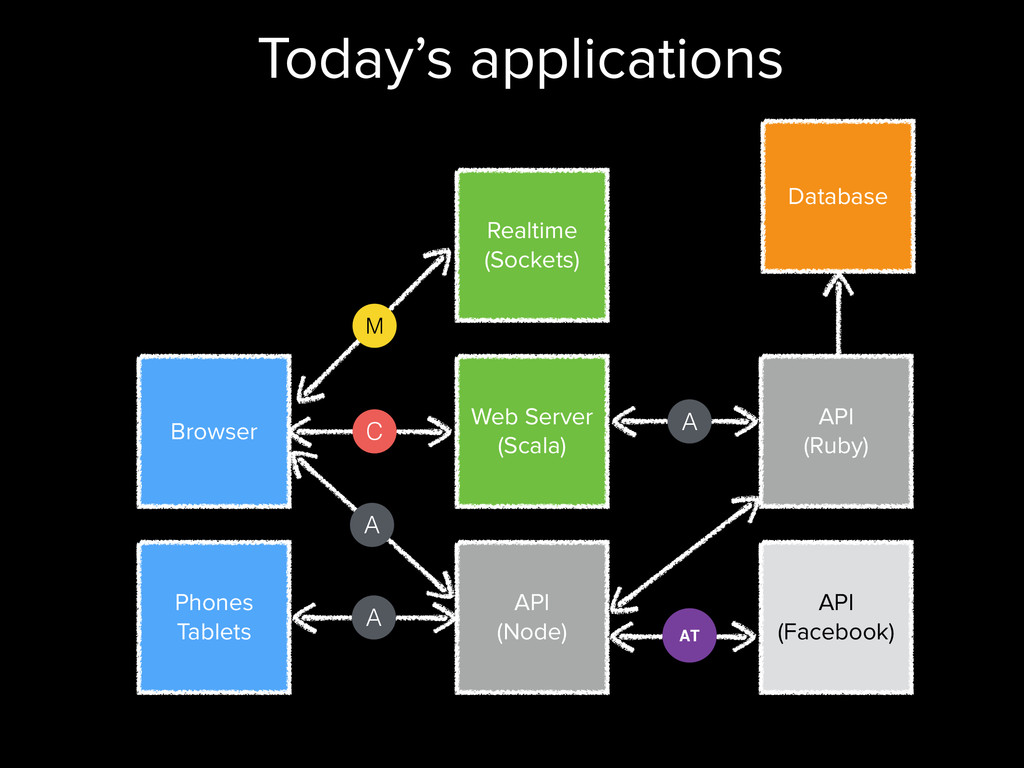
Browser Database Today’s applications Web Server (Scala) API (Ruby) API
(Node) Phones Tablets Realtime (Sockets) API (Facebook) C M A A A AT
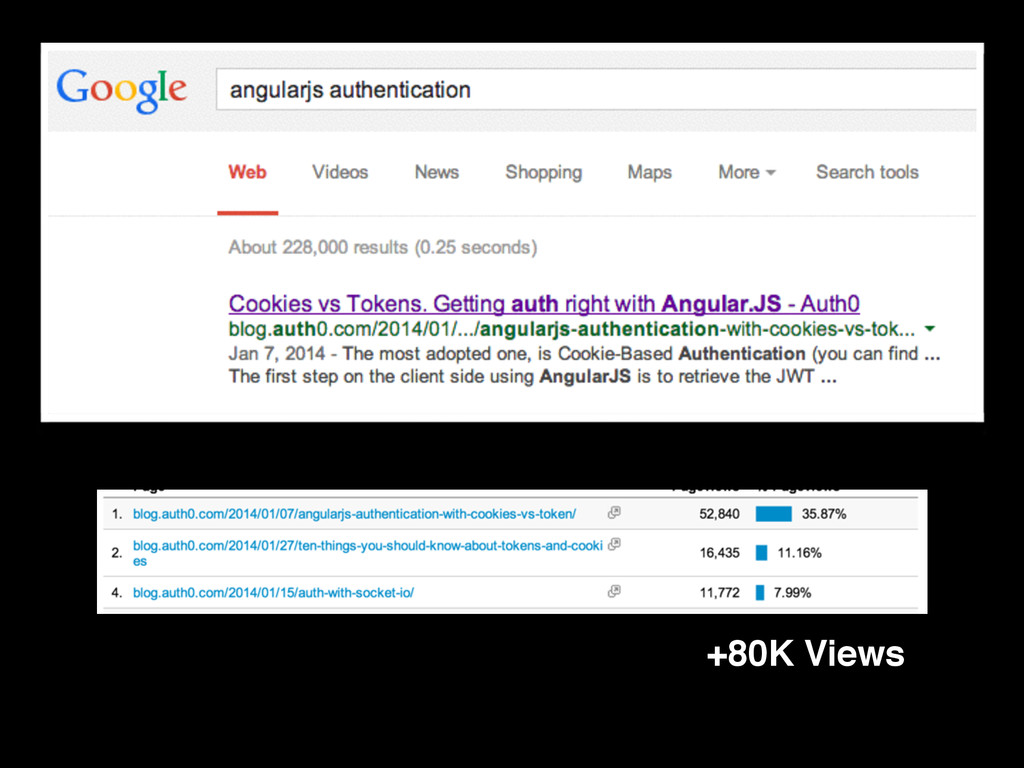
+80K Views
None
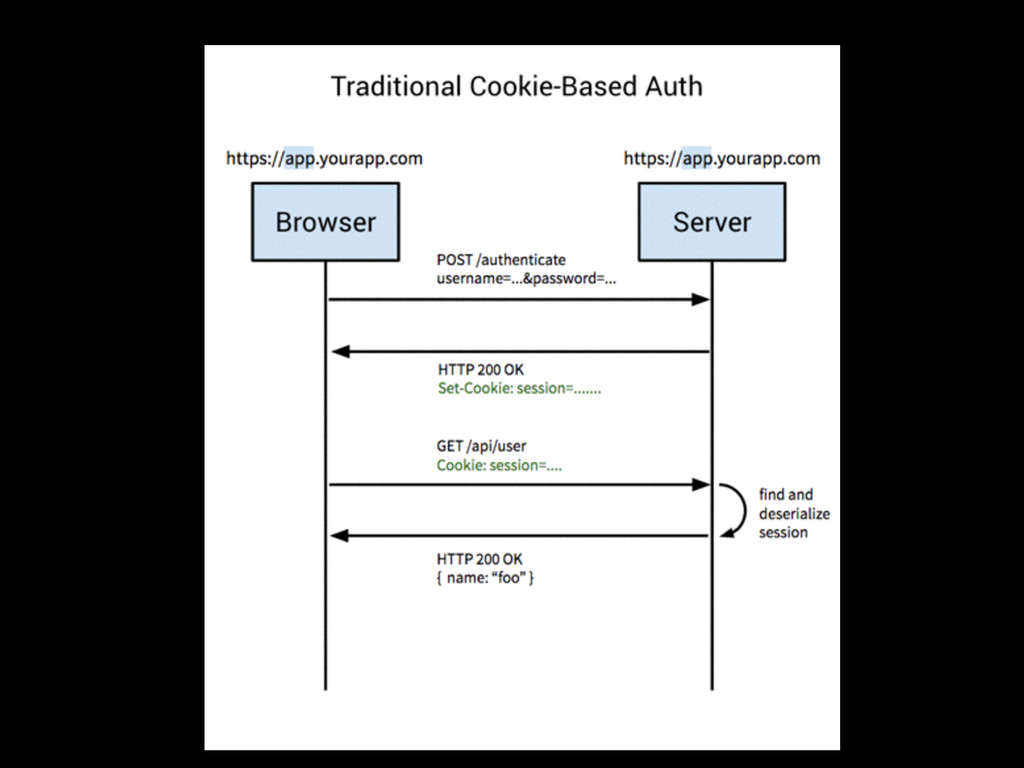
Cookie-based auth is a sub- optimal solution for today’s systems
Set-Cookie + CORS = doesn’t play well 1
Cookies are coupled to the web framework ! If you
try to reuse a cookie issued by Java in Node, not easy 2
APIs don’t use cookies, native apps either 3
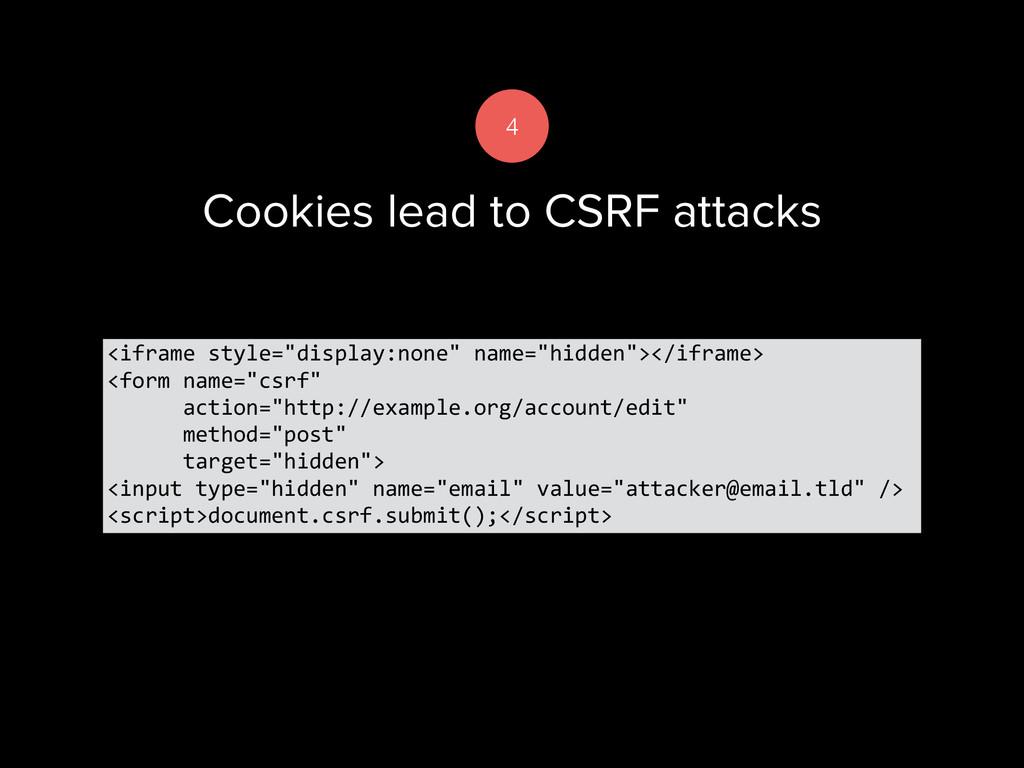
Cookies lead to CSRF attacks <iframe style="display:none" name="hidden"></iframe> <form
name="csrf" action="http://example.org/account/edit" method="post" target="hidden"> <input type="hidden" name="email" value="
[email protected]
" /> <script>document.csrf.submit();</script> 4
http://tools.ietf.org/html/draft-ietf-oauth-json-web-token
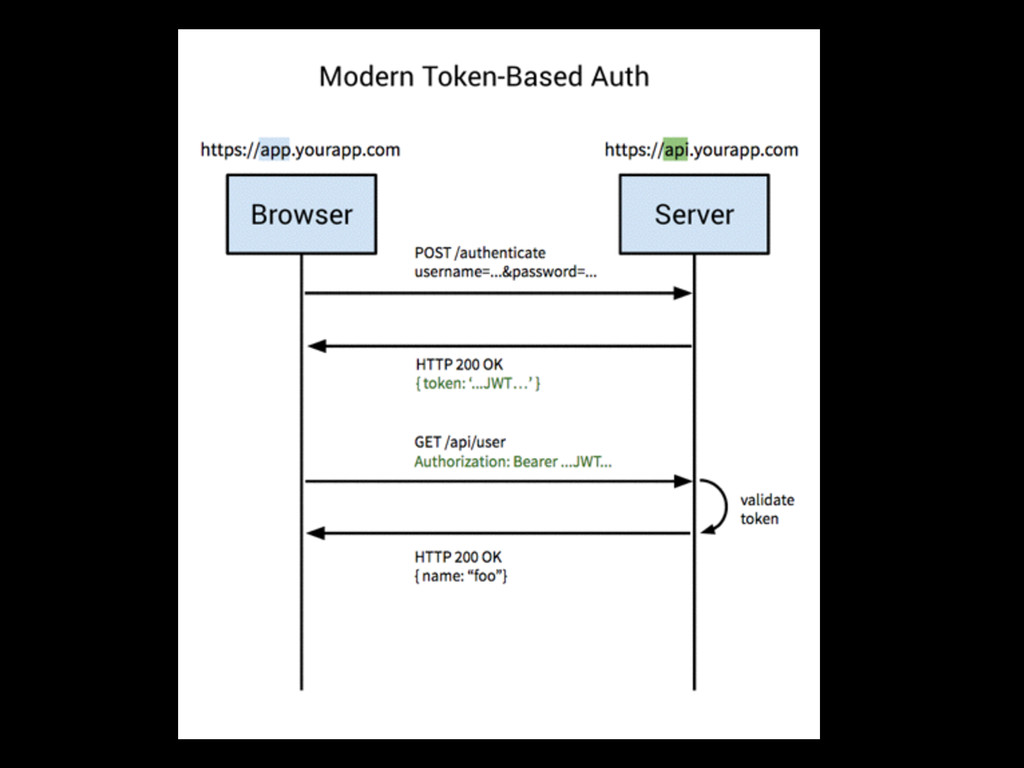
How it works?
Not everything is pink color
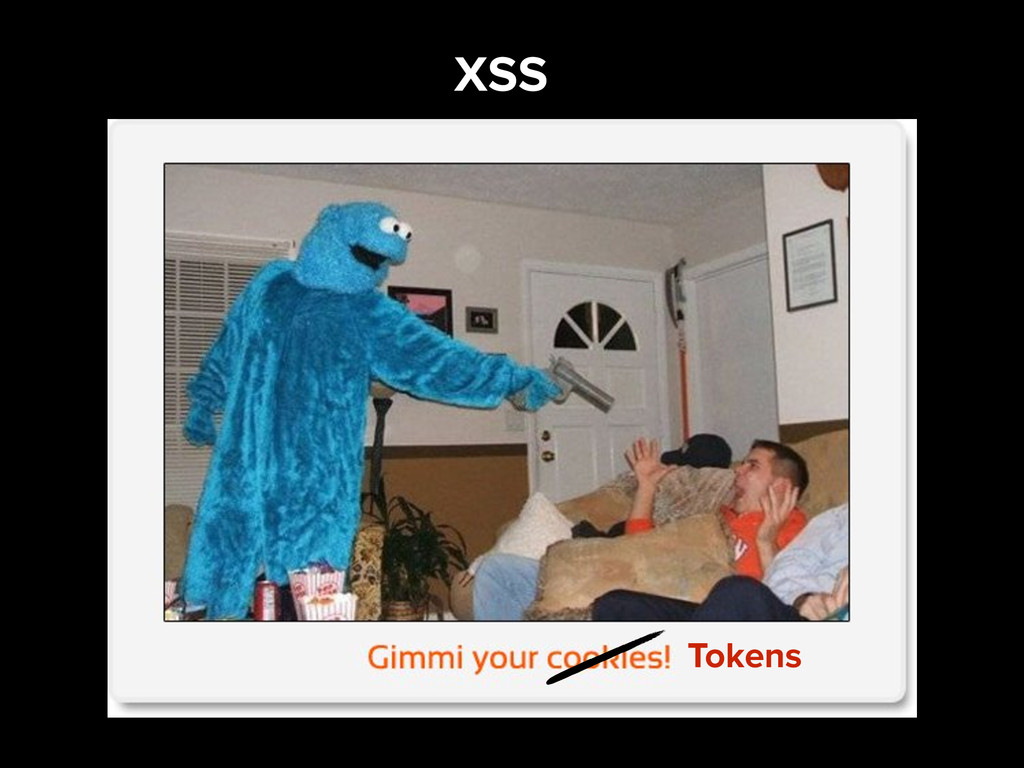
art: http://abeon-hosting.com/security-blog/xss-attack-in-action-cookie-stealer/ Tokens XSS
Sanitize and encode everything ! Google Caja https://developers.google.com/caja/
Try token-based authentication in your next project
TOOOOOOOOKEEEENS
Thanks! @woloski @jfroma blog.auth0.com jwt.io
Appendix
None
None
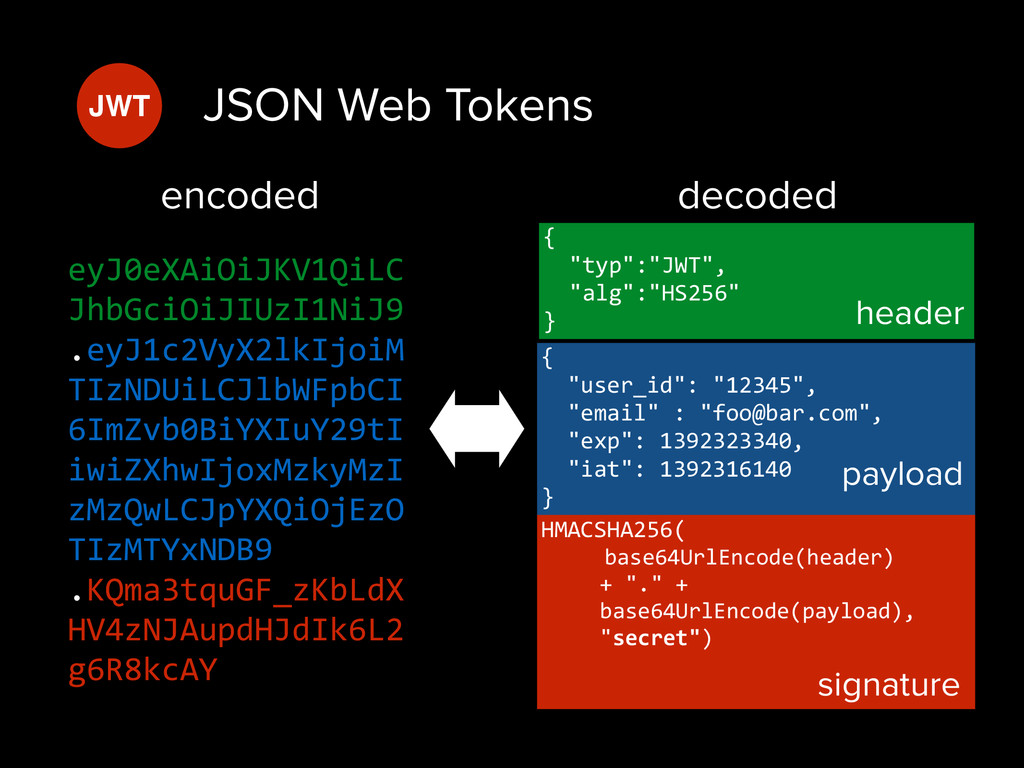
JWT JSON Web Tokens eyJ0eXAiOiJKV1QiLC JhbGciOiJIUzI1NiJ9 .eyJ1c2VyX2lkIjoiM TIzNDUiLCJlbWFpbCI 6ImZvb0BiYXIuY29tI
iwiZXhwIjoxMzkyMzI zMzQwLCJpYXQiOjEzO TIzMTYxNDB9 .KQma3tquGF_zKbLdX HV4zNJAupdHJdIk6L2 g6R8kcAY ! ! { "typ":"JWT", "alg":"HS256" } { "user_id": "12345", "email" : "
[email protected]
", "exp": 1392323340, "iat": 1392316140 } HMACSHA256( base64UrlEncode(header) + "." + base64UrlEncode(payload), "secret") ! header payload signature encoded decoded
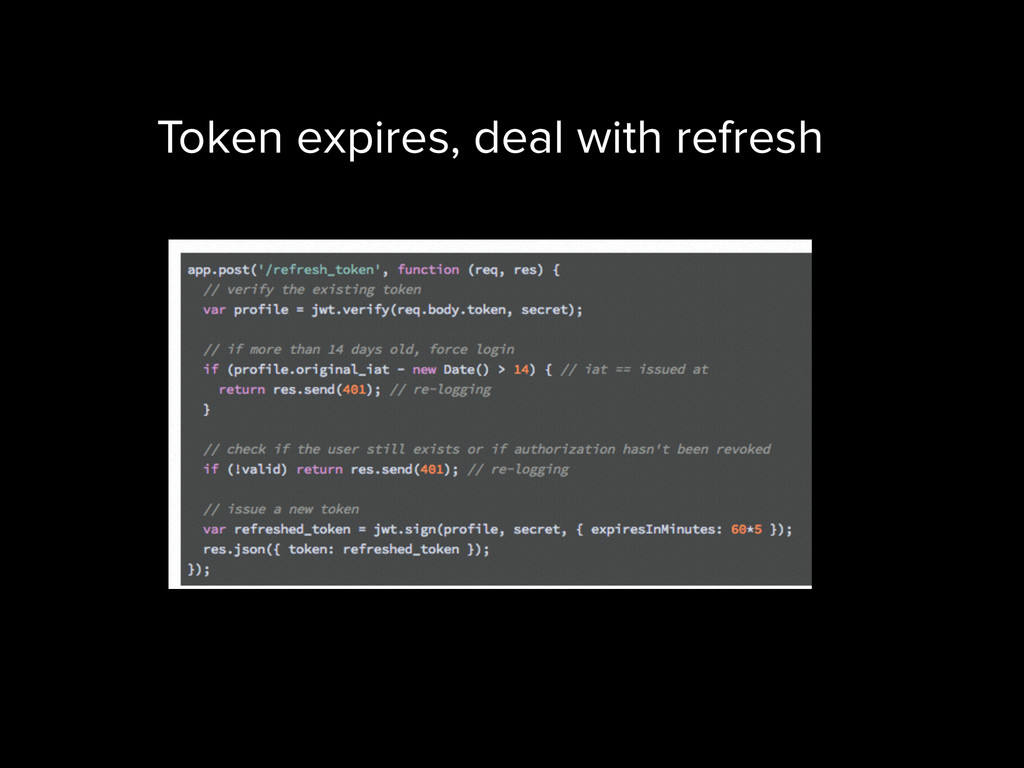
Token expires, deal with refresh
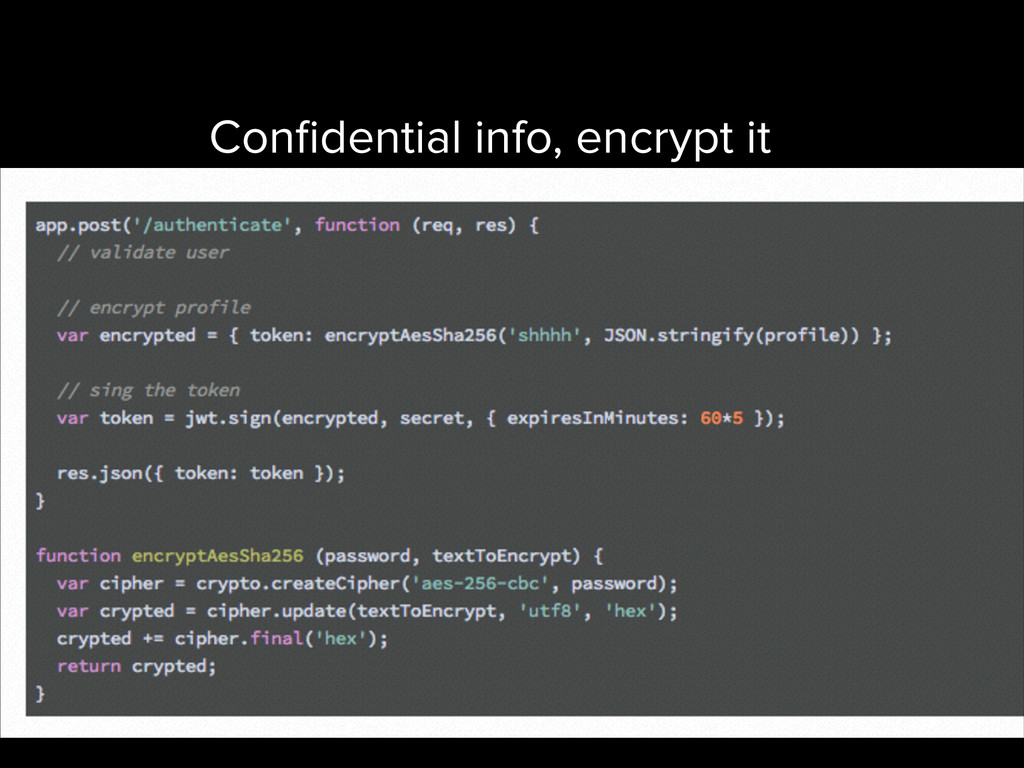
Confidential info, encrypt it
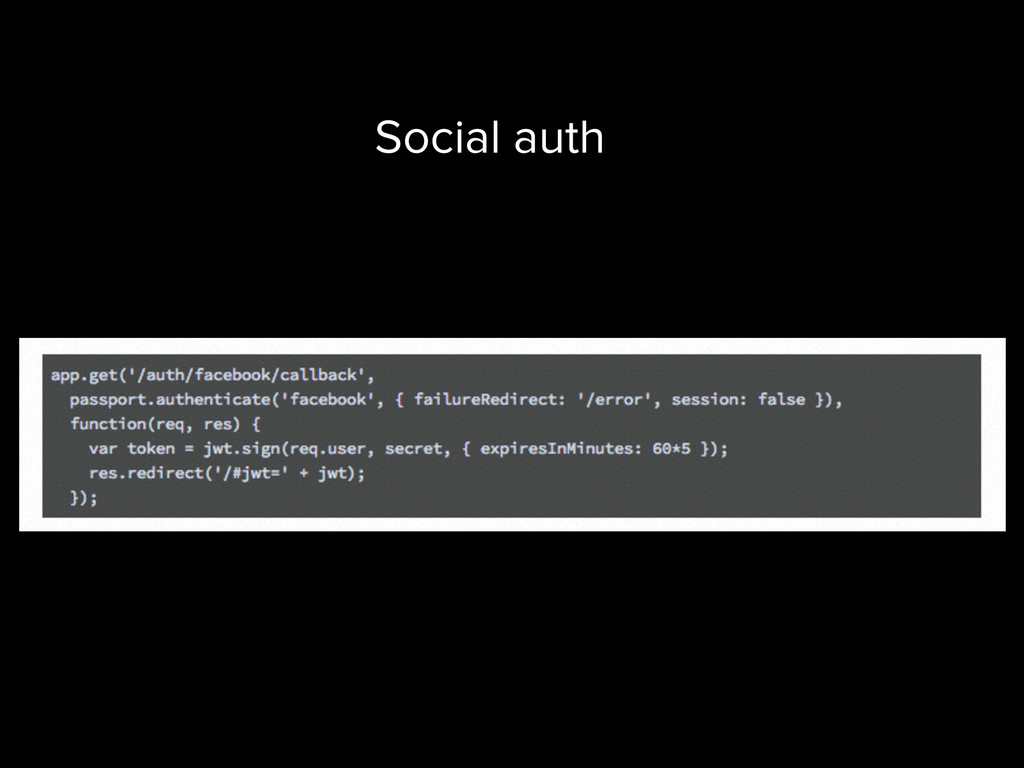
Social auth
Tokens can get big Don’t over engineer Don’t do fine
grained permissions Define scopes
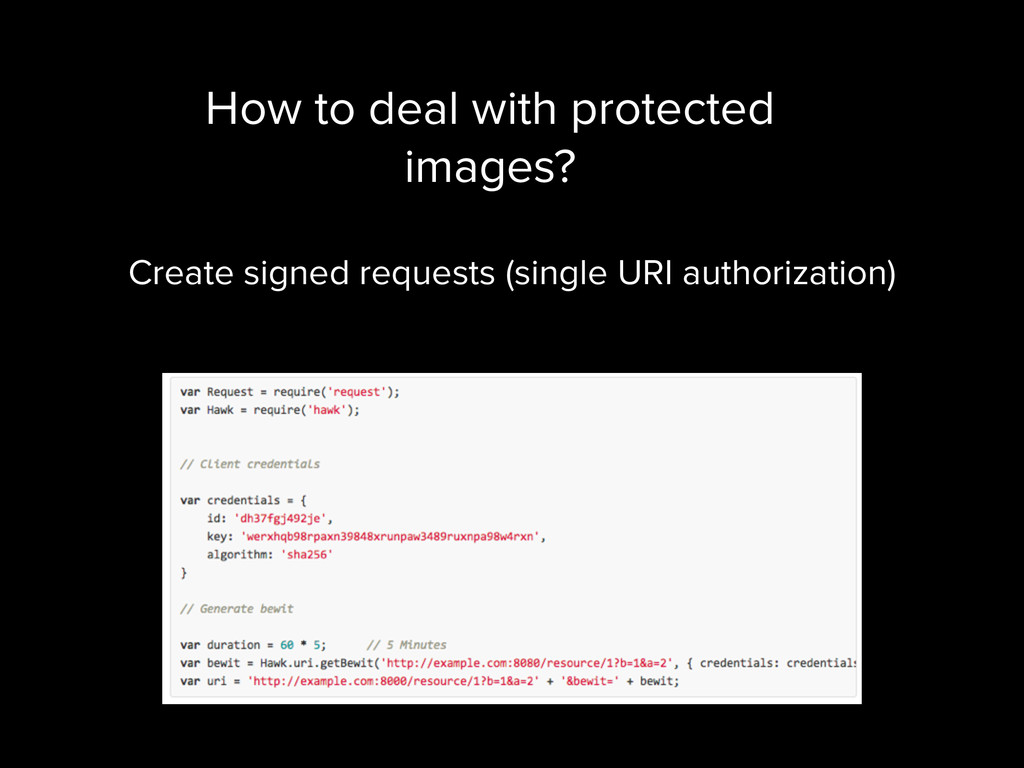
How to deal with protected images? https://github.com/hueniverse/hawk#single-uri-authorization Create signed requests
(single URI authorization)


 woloski
 yahonda
 sansan33
 akitoshiga
 carta_engineering
 takuroabe
 persolserverworks
 prog893
 hiracky16
 raspython3
 iktakahiro
 riyaamemiya
 yuuuuuuu168
 thoeni
 reverentgeek
 madoxten
 ryanjones
 tammielis
 marcelosomers
 inesmontani
 axbom
 kneath
 akosma
 aleyda
 kevinliebholz