agencies years agency Transitioned international clicks-and-mortar fashion retailer to in-house development Led migration to Magento 2 Lead software engineer responsible for platform integrations at AI Search and Personalisation provider years in-house years vendor side 7 3 5
about bad code 2. A lot of bad code does what it claims 3. Bad code presents tangible risks 4. Stakeholders can be quick to point the finger and slow to make connections
about bad code 2. A lot of bad code does what it claims 3. Bad code presents tangible risks 4. Stakeholders can be quick to point the finger and slow to make connections 5. People are stubborn
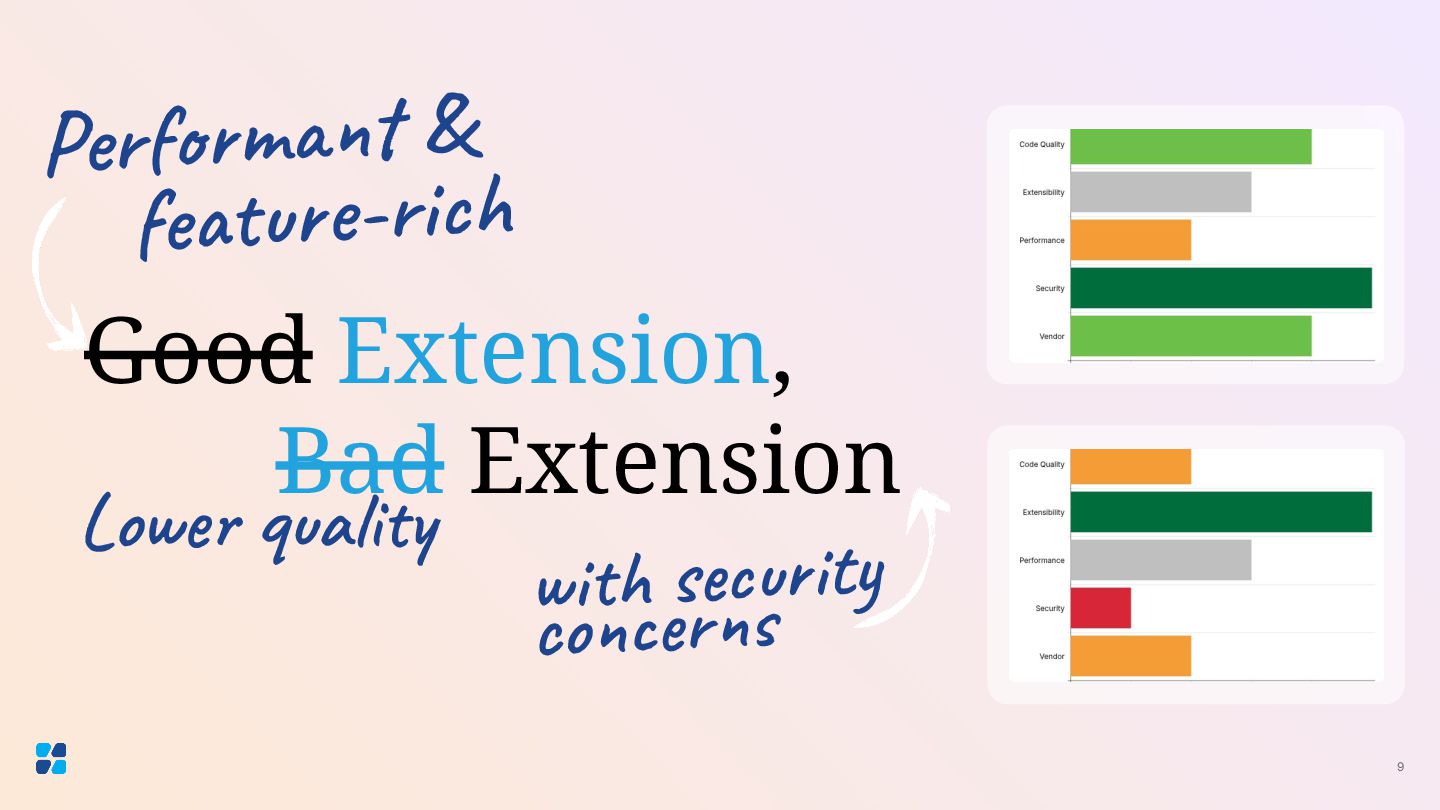
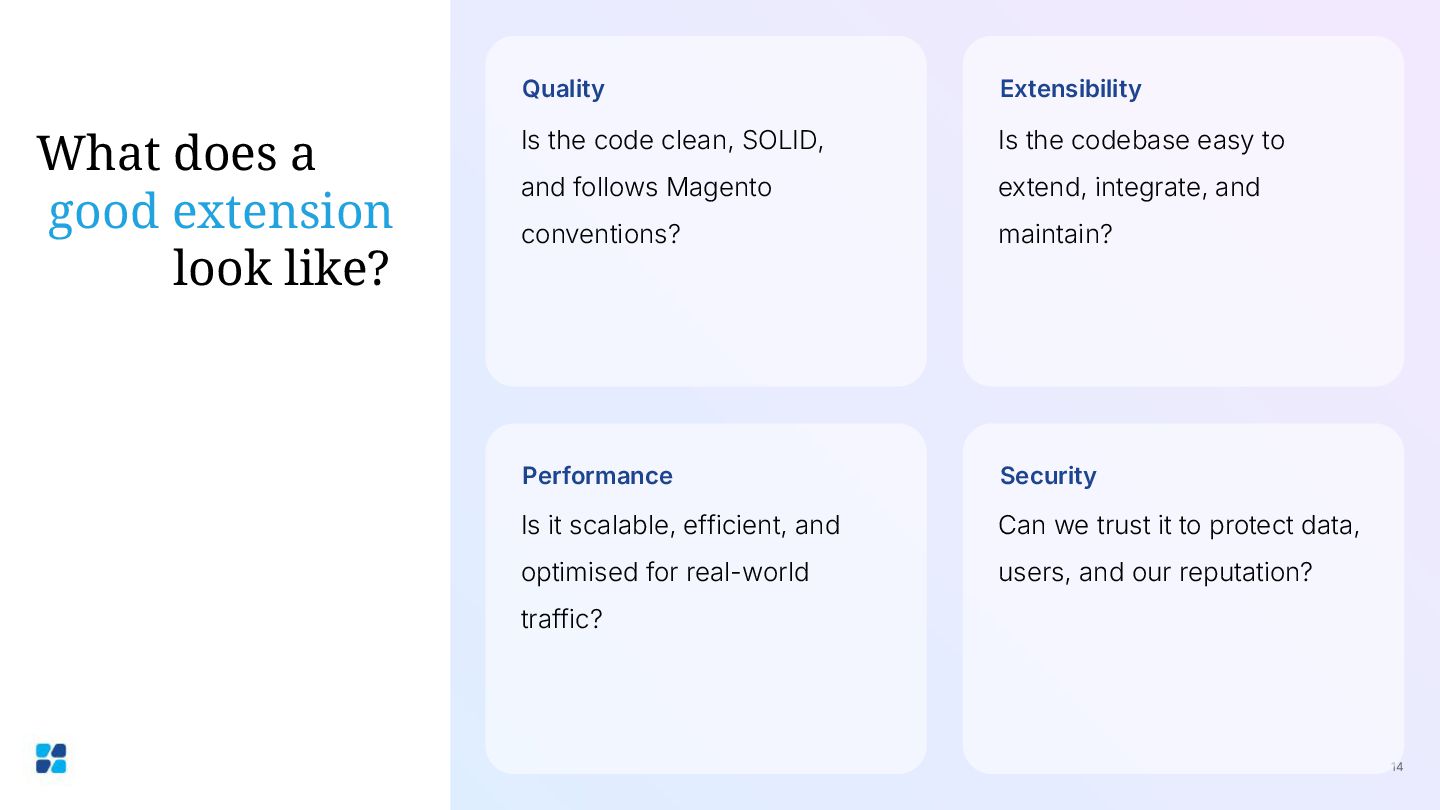
Performance Security Is the code clean, SOLID, and follows Magento conventions? Is the codebase easy to extend, integrate, and maintain? Is it scalable, efficient, and optimised for real-world traffic? Can we trust it to protect data, users, and our reputation?
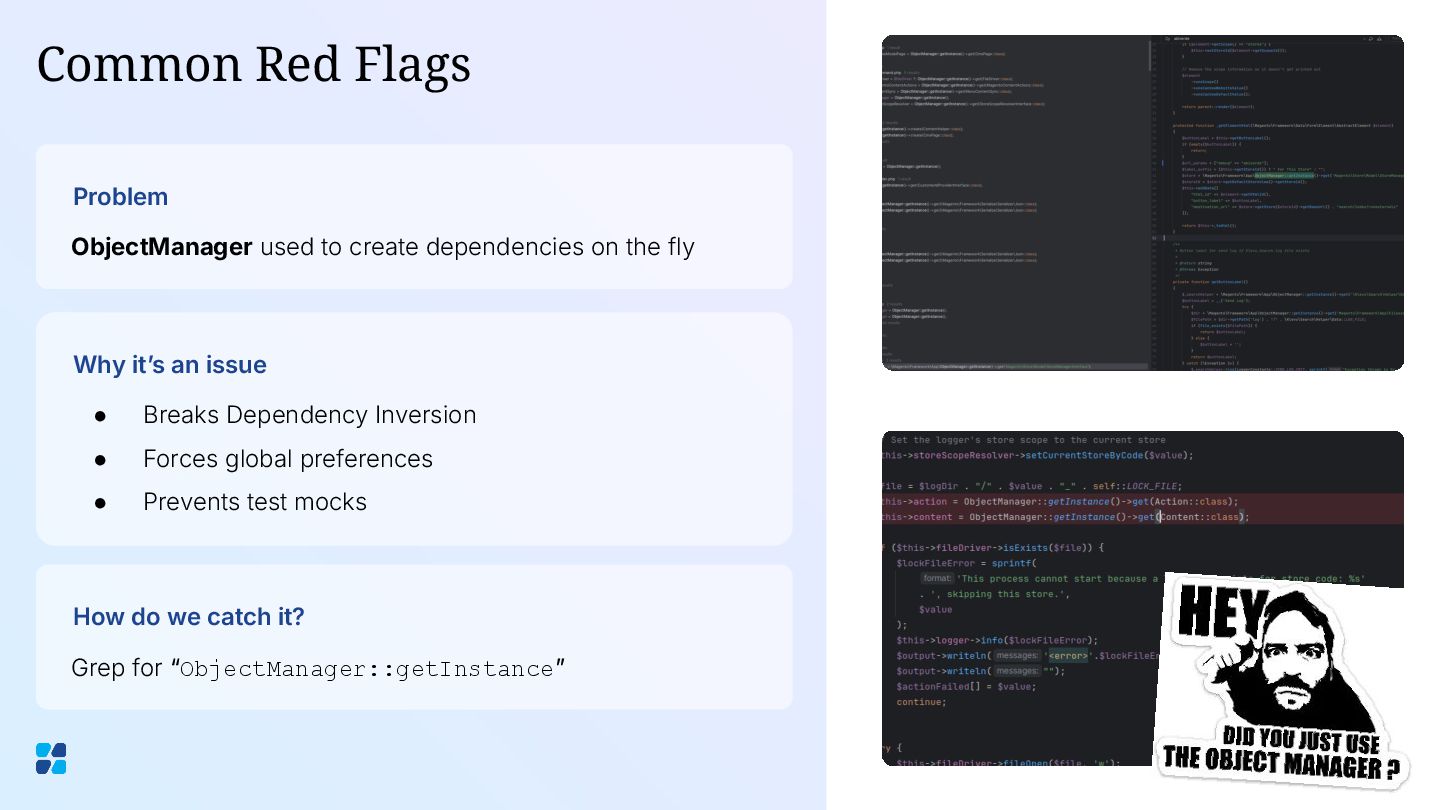
on the fly Why itʼs an issue • Breaks Dependency Inversion • Forces global preferences • Prevents test mocks How do we catch it? Grep for “ObjectManager::getInstanceˮ
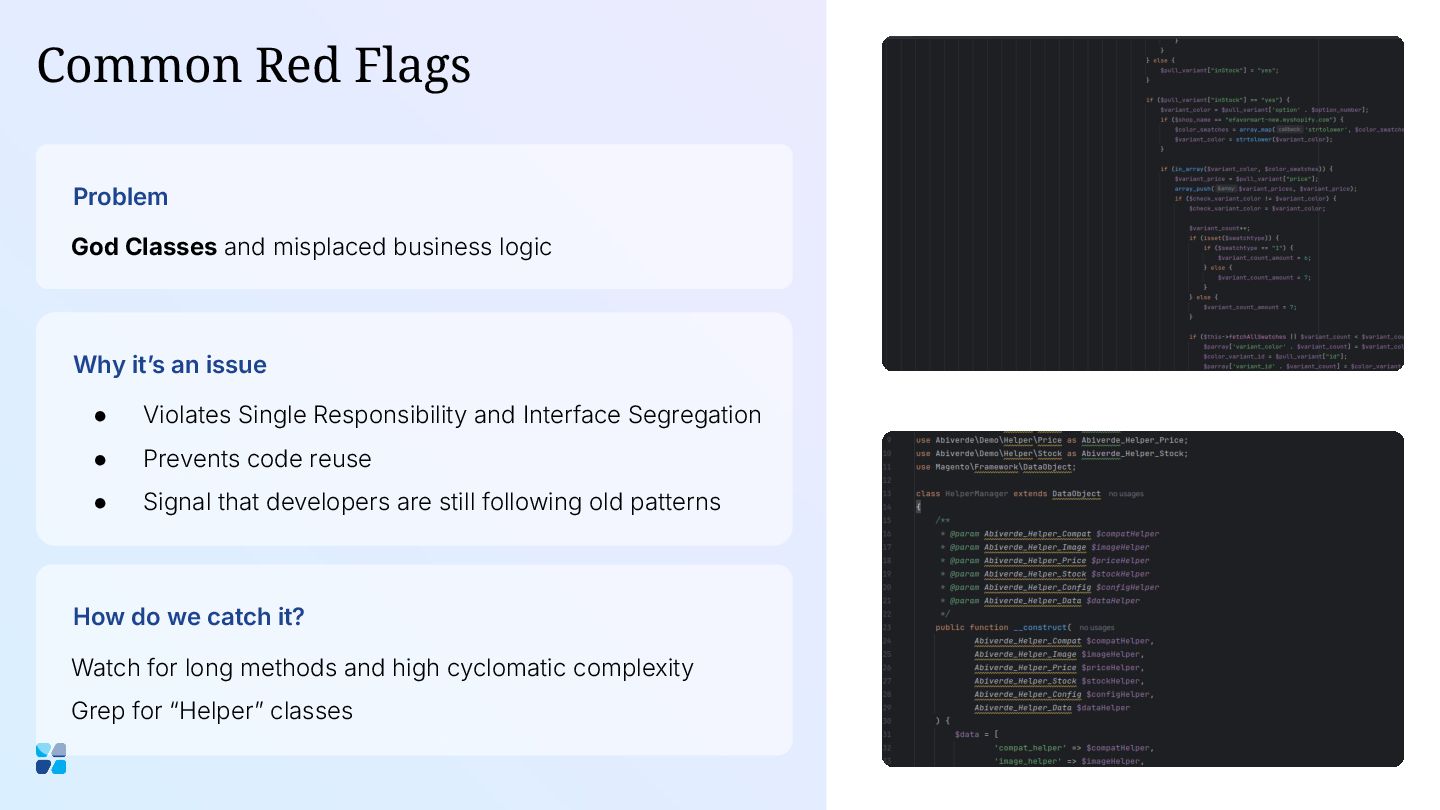
logic Why itʼs an issue • Violates Single Responsibility and Interface Segregation • Prevents code reuse • Signal that developers are still following old patterns How do we catch it? Watch for long methods and high cyclomatic complexity Grep for “Helperˮ classes
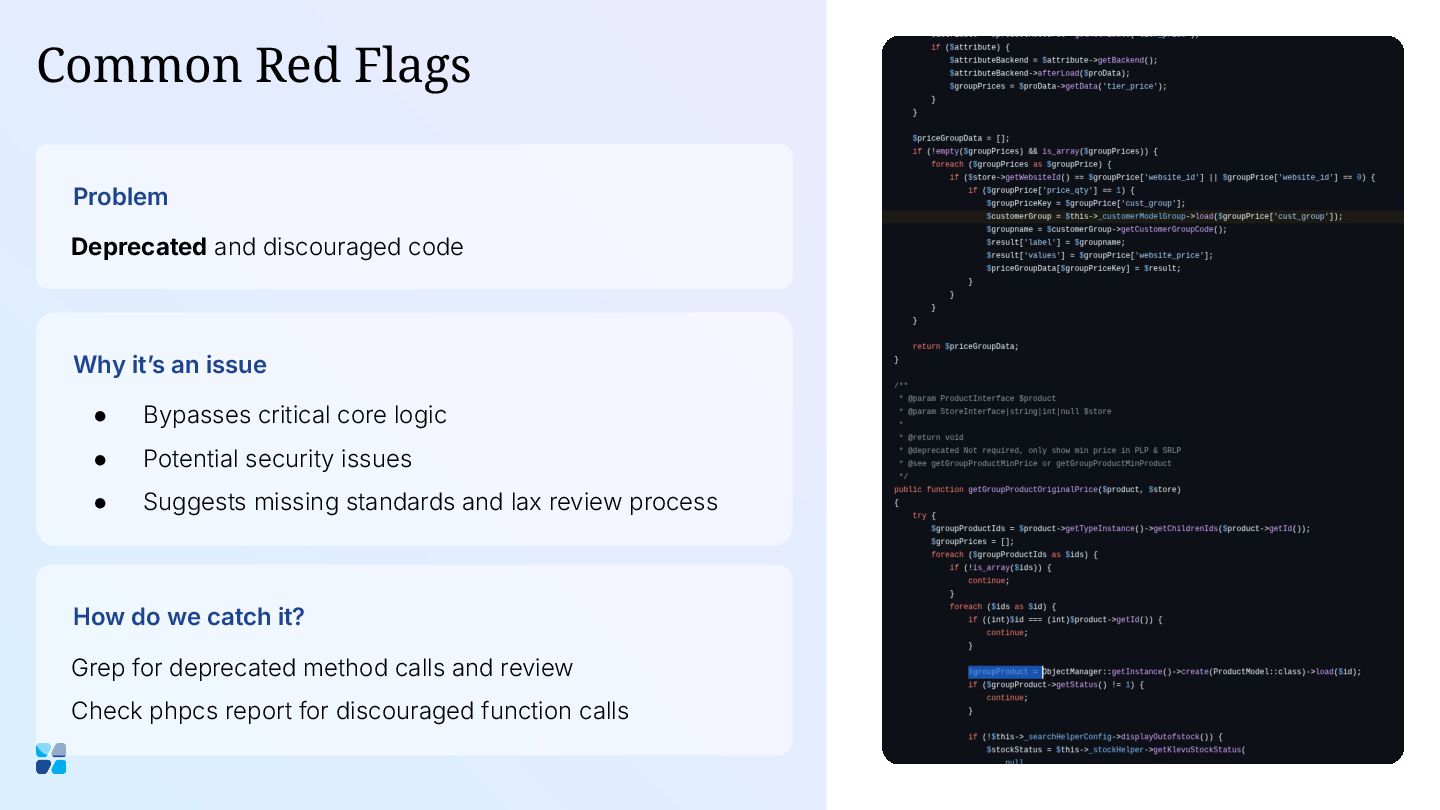
itʼs an issue • Bypasses critical core logic • Potential security issues • Suggests missing standards and lax review process How do we catch it? Grep for deprecated method calls and review Check phpcs report for discouraged function calls
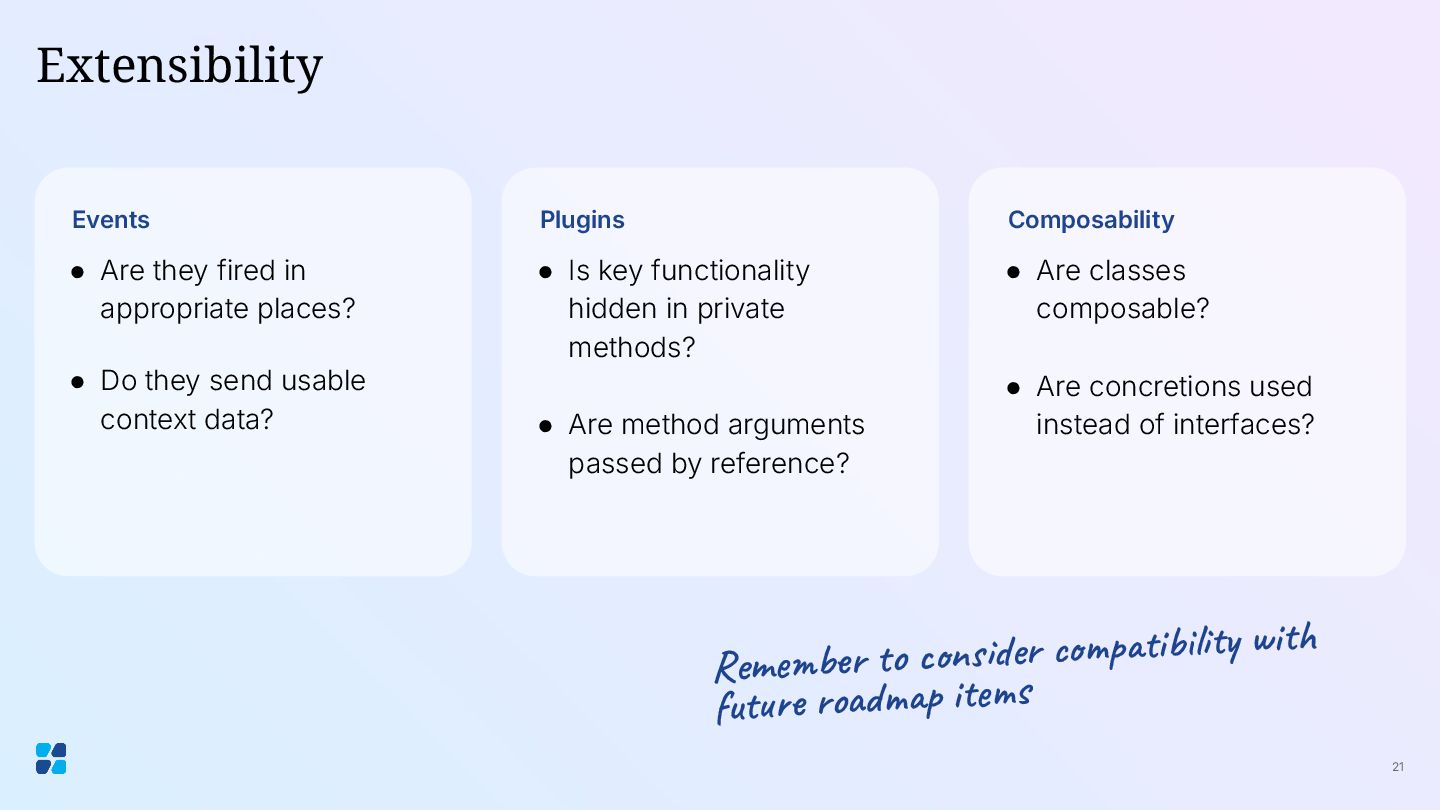
• Are they fired in appropriate places? • Do they send usable context data? Events • Is key functionality hidden in private methods? • Are method arguments passed by reference? Plugins • Are classes composable? • Are concretions used instead of interfaces? Composability
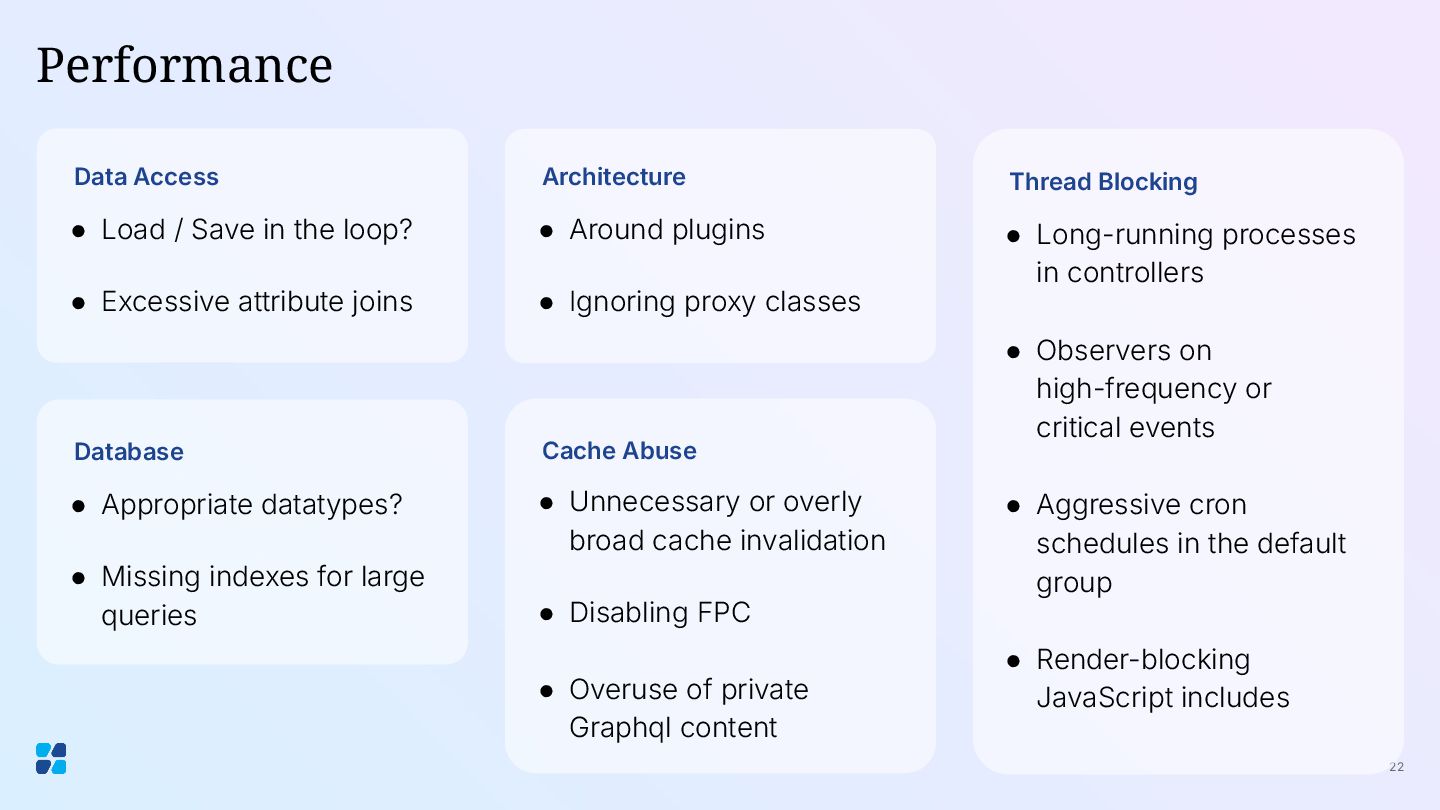
/ Save in the loop? • Excessive attribute joins • Long-running processes in controllers • Observers on high-frequency or critical events • Aggressive cron schedules in the default group • Render-blocking JavaScript includes • Unnecessary or overly broad cache invalidation • Disabling FPC • Overuse of private Graphql content Database • Appropriate datatypes? • Missing indexes for large queries Architecture • Around plugins • Ignoring proxy classes
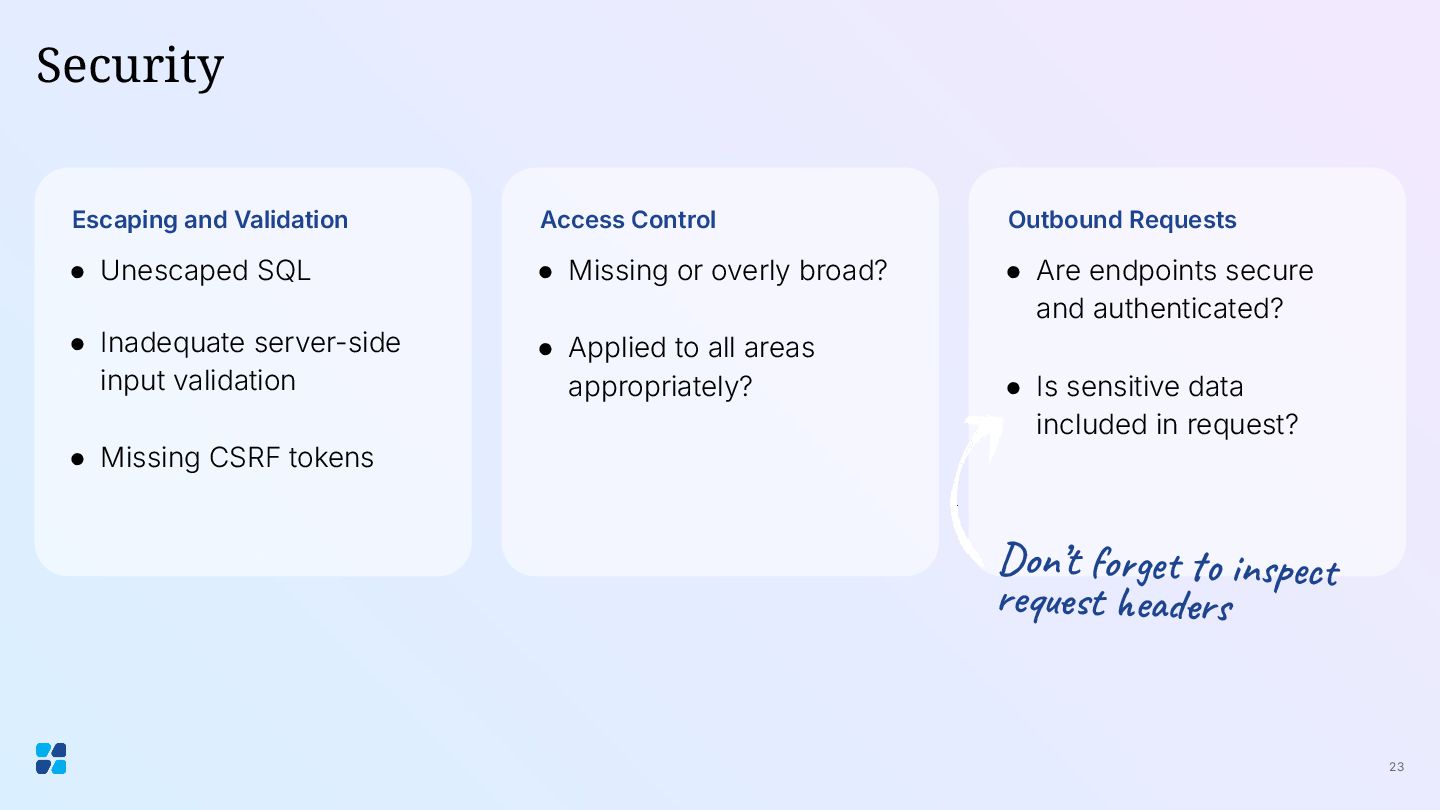
• Missing CSRF tokens Escaping and Validation • Missing or overly broad? • Applied to all areas appropriately? Access Control • Are endpoints secure and authenticated? • Is sensitive data included in request? Outbound Requests Don’t forget to inspect request headers
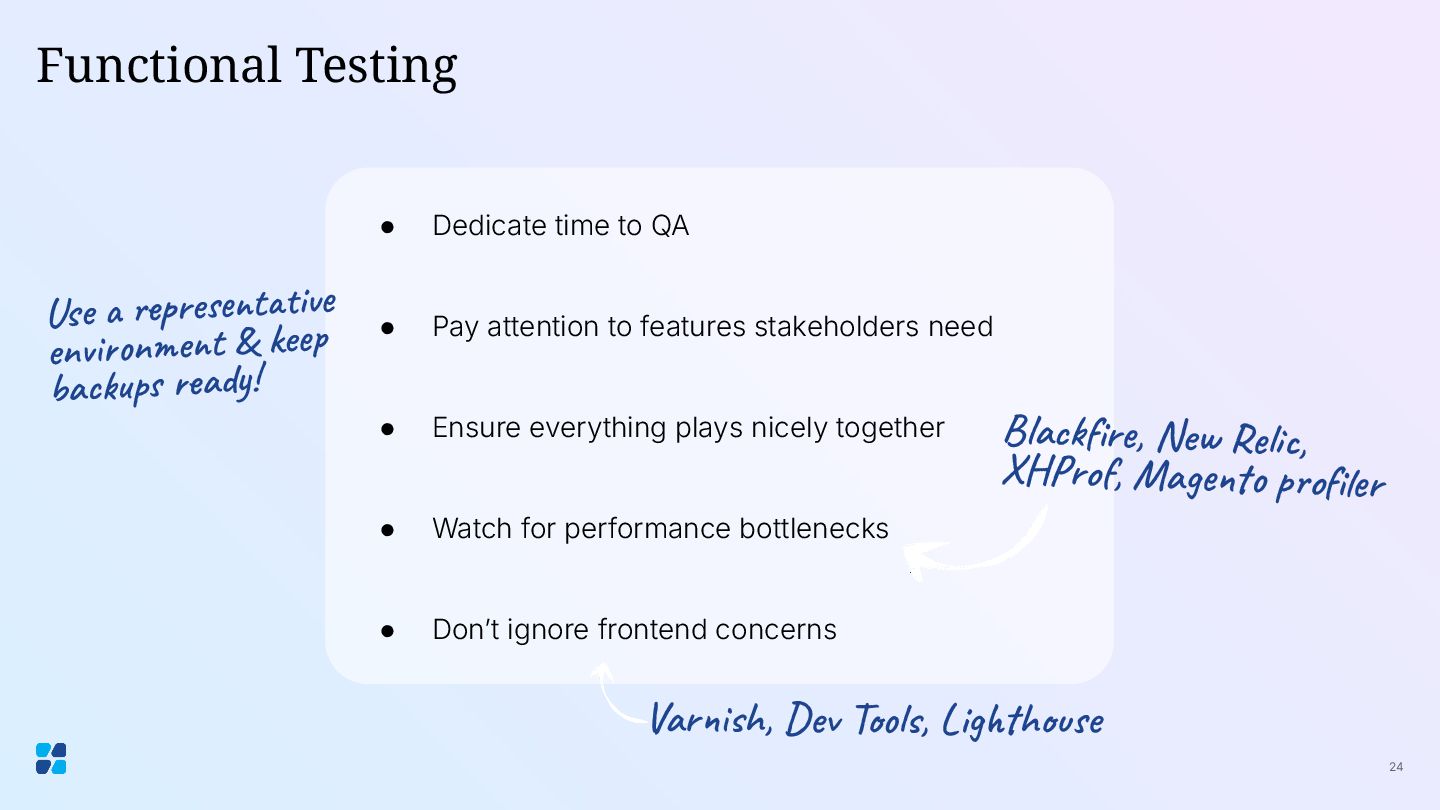
attention to features stakeholders need • Ensure everything plays nicely together • Watch for performance bottlenecks • Donʼt ignore frontend concerns Blackfire, New Relic, XHProf, Magento profiler Varnish, Dev Tools, Lighthouse Use a representative environment & keep backups ready!
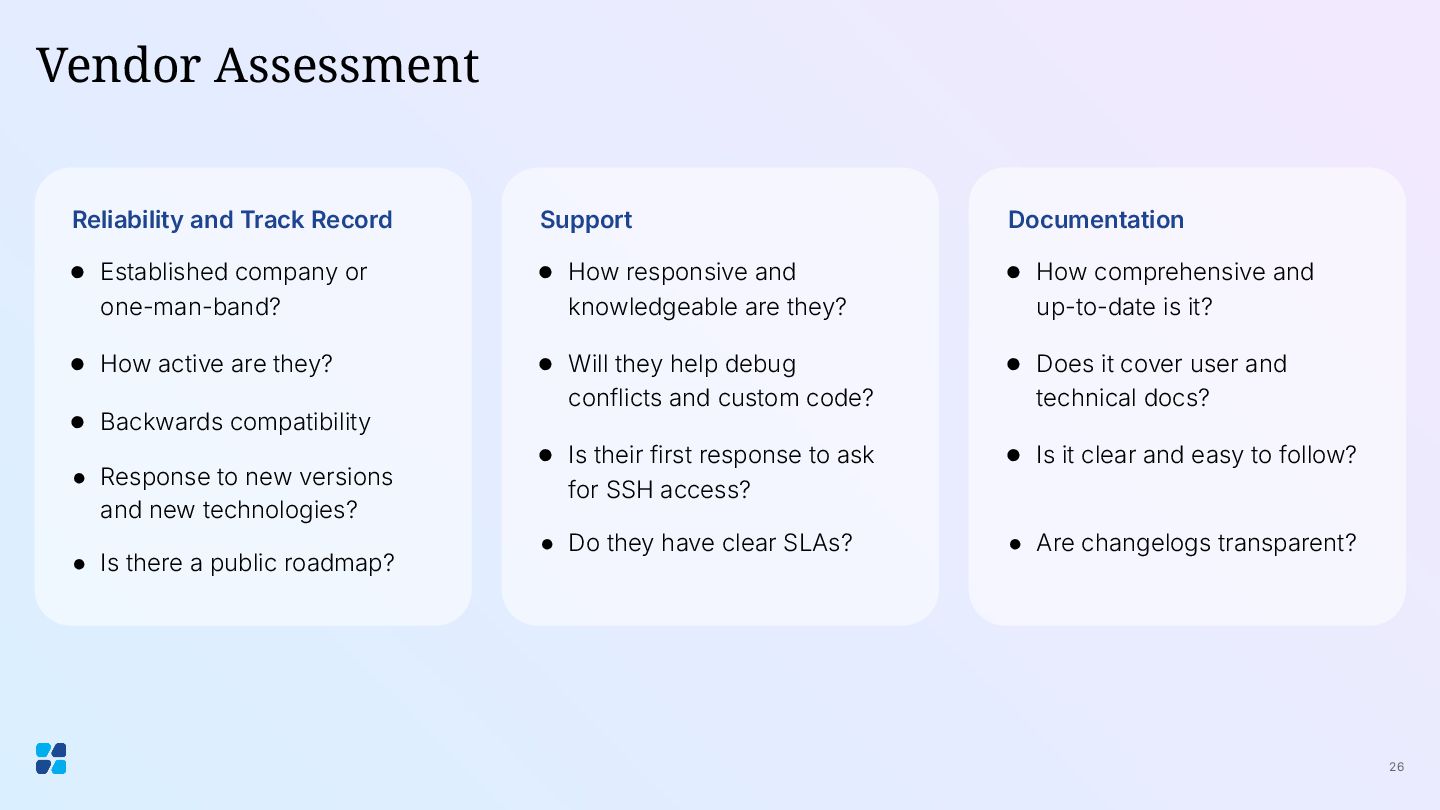
active are they? • Backwards compatibility • Response to new versions and new technologies? • Is there a public roadmap? Reliability and Track Record Support Documentation • How responsive and knowledgeable are they? • Will they help debug conflicts and custom code? • Is their first response to ask for SSH access? • Do they have clear SLAs? • How comprehensive and up-to-date is it? • Does it cover user and technical docs? • Is it clear and easy to follow? • Are changelogs transparent?
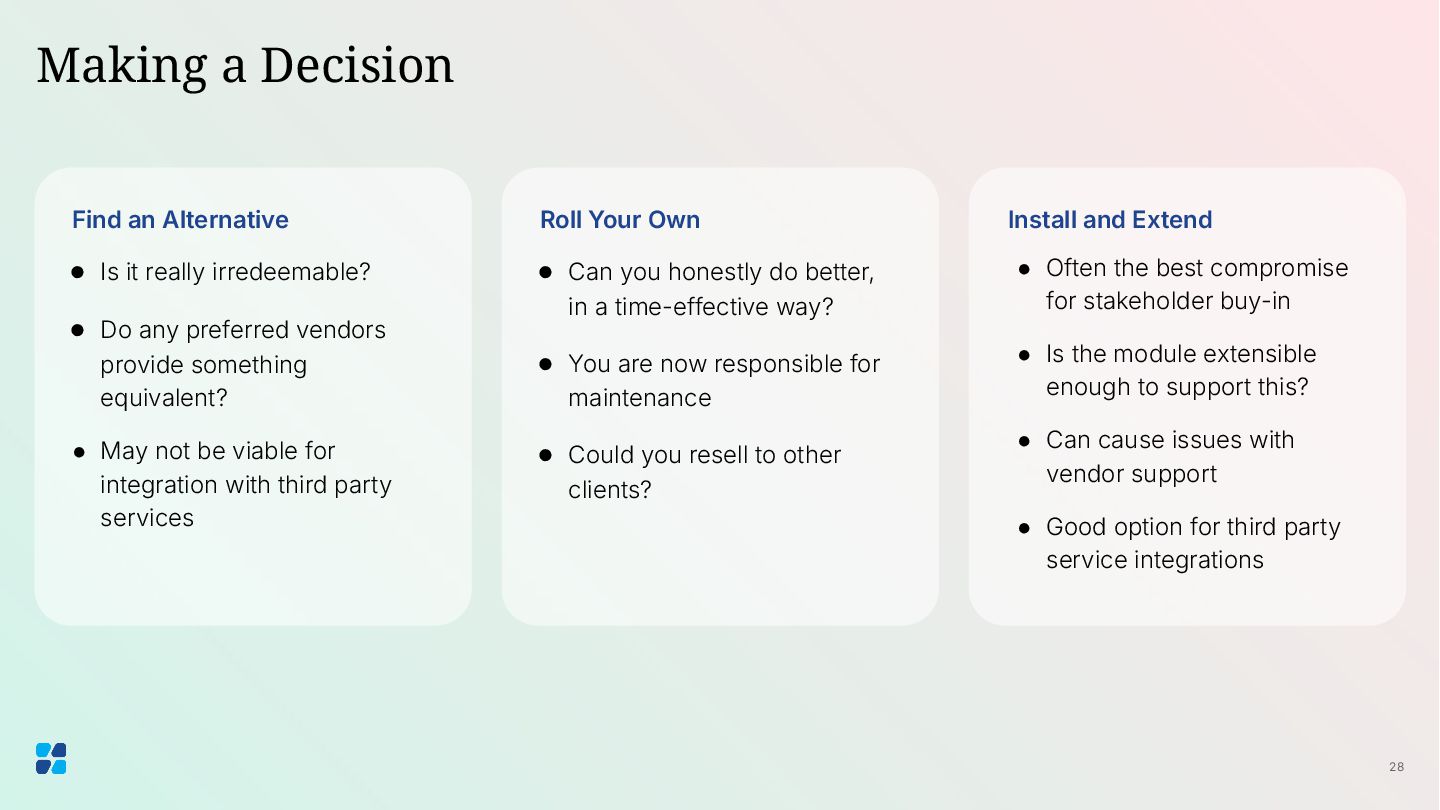
Do any preferred vendors provide something equivalent? • May not be viable for integration with third party services Find an Alternative Roll Your Own Install and Extend • Can you honestly do better, in a time-effective way? • You are now responsible for maintenance • Could you resell to other clients? • Often the best compromise for stakeholder buy-in • Is the module extensible enough to support this? • Can cause issues with vendor support • Good option for third party service integrations
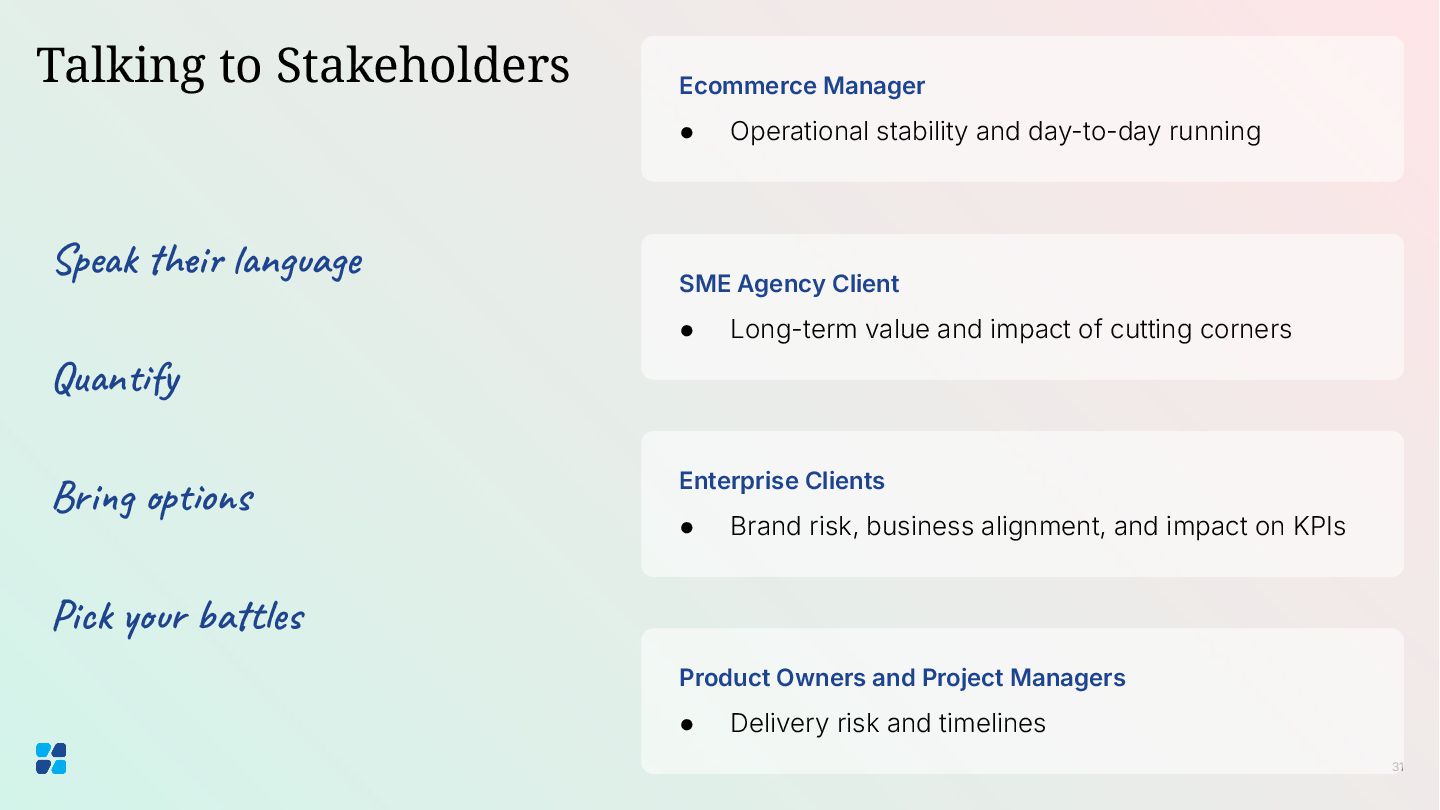
Pick your battles • Operational stability and day-to-day running Ecommerce Manager • Delivery risk and timelines Product Owners and Project Managers • Long-term value and impact of cutting corners SME Agency Client • Brand risk, business alignment, and impact on KPIs Enterprise Clients
to Security Walk Away Compromise Nuclear option if you can afford to lose the relationship Bring options and find a middle ground Ensure any risks are documented before moving forwards Disagree but Commit
to Security Walk Away Compromise Nuclear option if you can afford to lose the relationship Bring options and find a middle ground Ensure any risks are documented before moving forwards Disagree but Commit Let It Go Save yourself for issues that matter more
the people behind it Validate your approach Be pragmatic and base decisions on evidence, not ego Speak your stakeholdersʼ language Honesty and clarity build trust - technobabble doesnʼt! In Summary
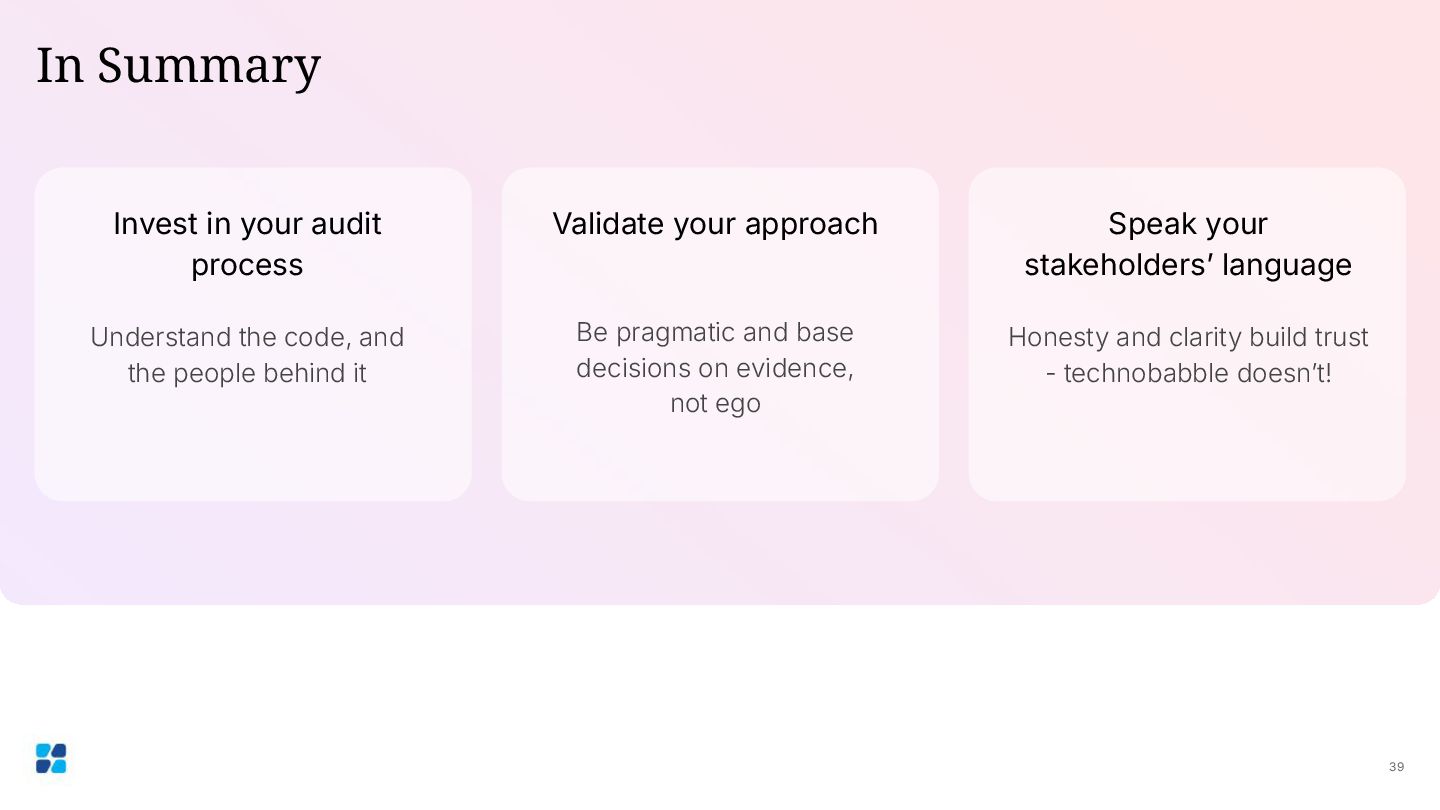
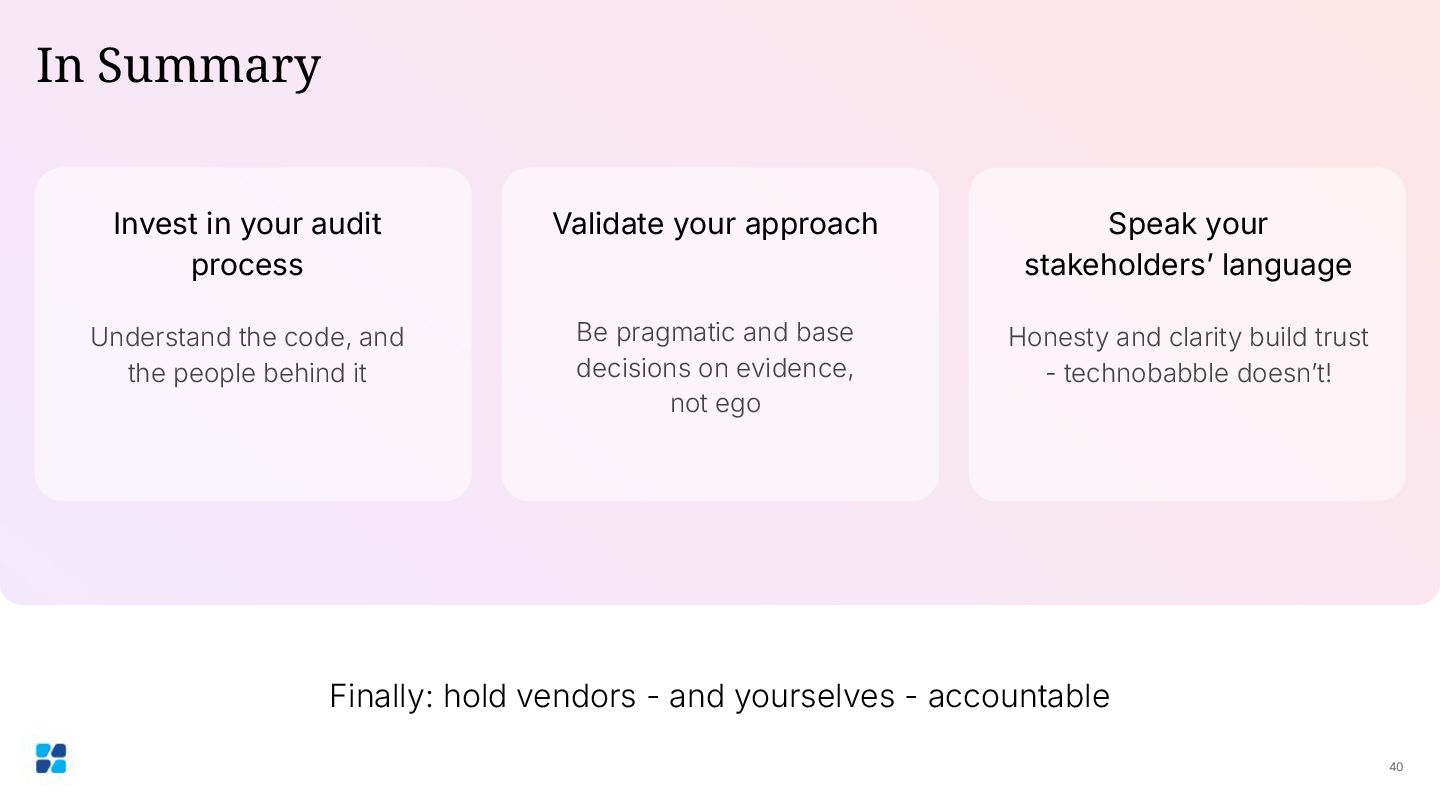
in your audit process Understand the code, and the people behind it Validate your approach Be pragmatic and base decisions on evidence, not ego Speak your stakeholdersʼ language Honesty and clarity build trust - technobabble doesnʼt! In Summary


 abiverde
 rkaga
 o0h
 lynnswap
 tosite
 optim
 kasacchiful
 ryu1013
 prota
 panda728
 yukiny
 drumath2237
 yutobara
 minecr
 eileencodes
 tmiket
 thoeni
 kimpetersen
 inesmontani
 aleyda
 tammyeverts
 vanstee
 katarinadahlin