Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
Dockerize Java Securely: SBOMs + Attestations +...
Search
Sponsored
·
Your Podcast. Everywhere. Effortlessly.
Share. Educate. Inspire. Entertain. You do you. We'll handle the rest.
→
Mohammad-Ali A'râbi
October 15, 2026
20
0
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
Dockerize Java Securely: SBOMs + Attestations + Cosign
Mohammad-Ali A'râbi
October 15, 2026
Transcript
58 slides
None
Whose Day is It?
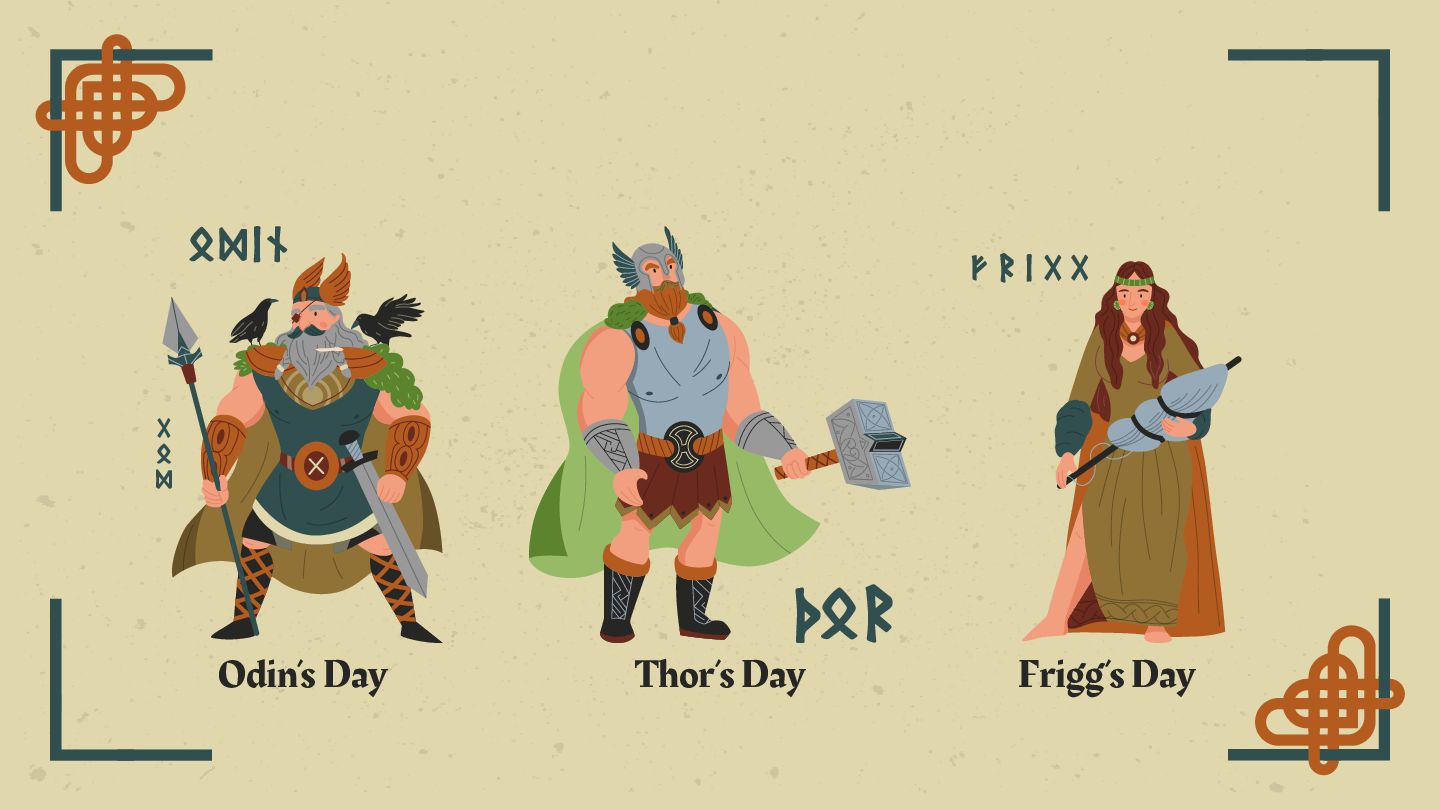
Odin’s Day Thor’s Day Frigg’s Day
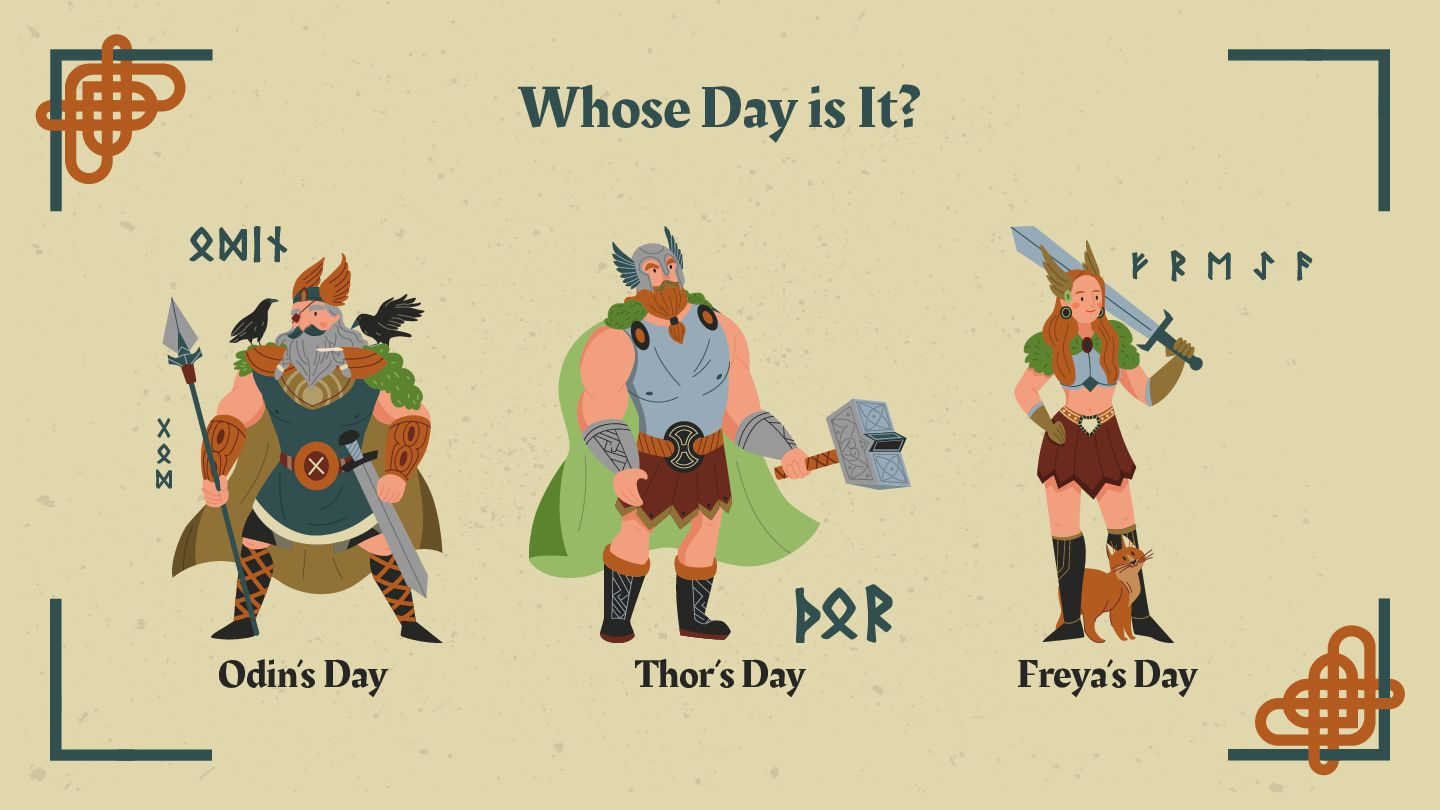
Whose Day is It? Odin’s Day Thor’s Day Freya’s Day
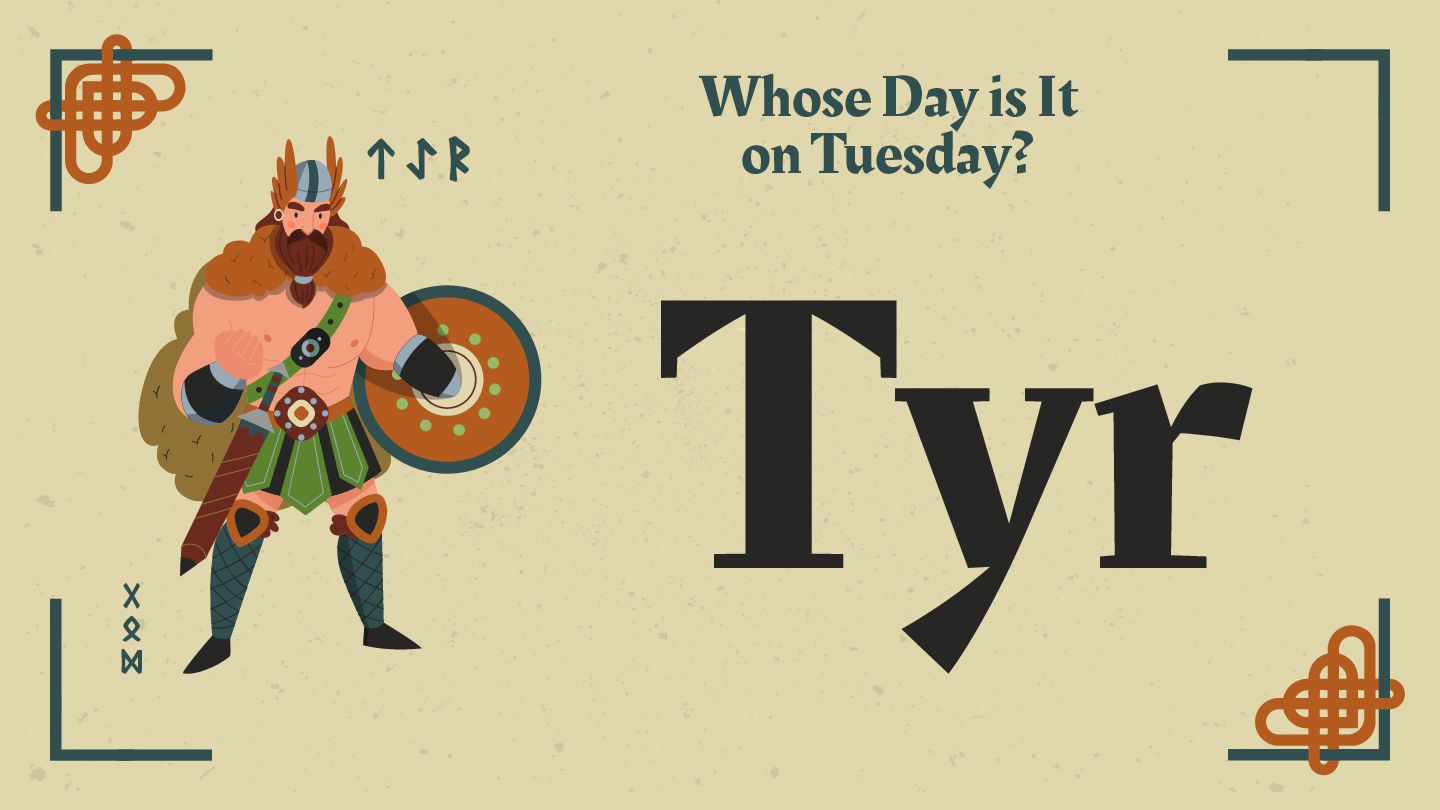
Whose Day is It on Tuesday?
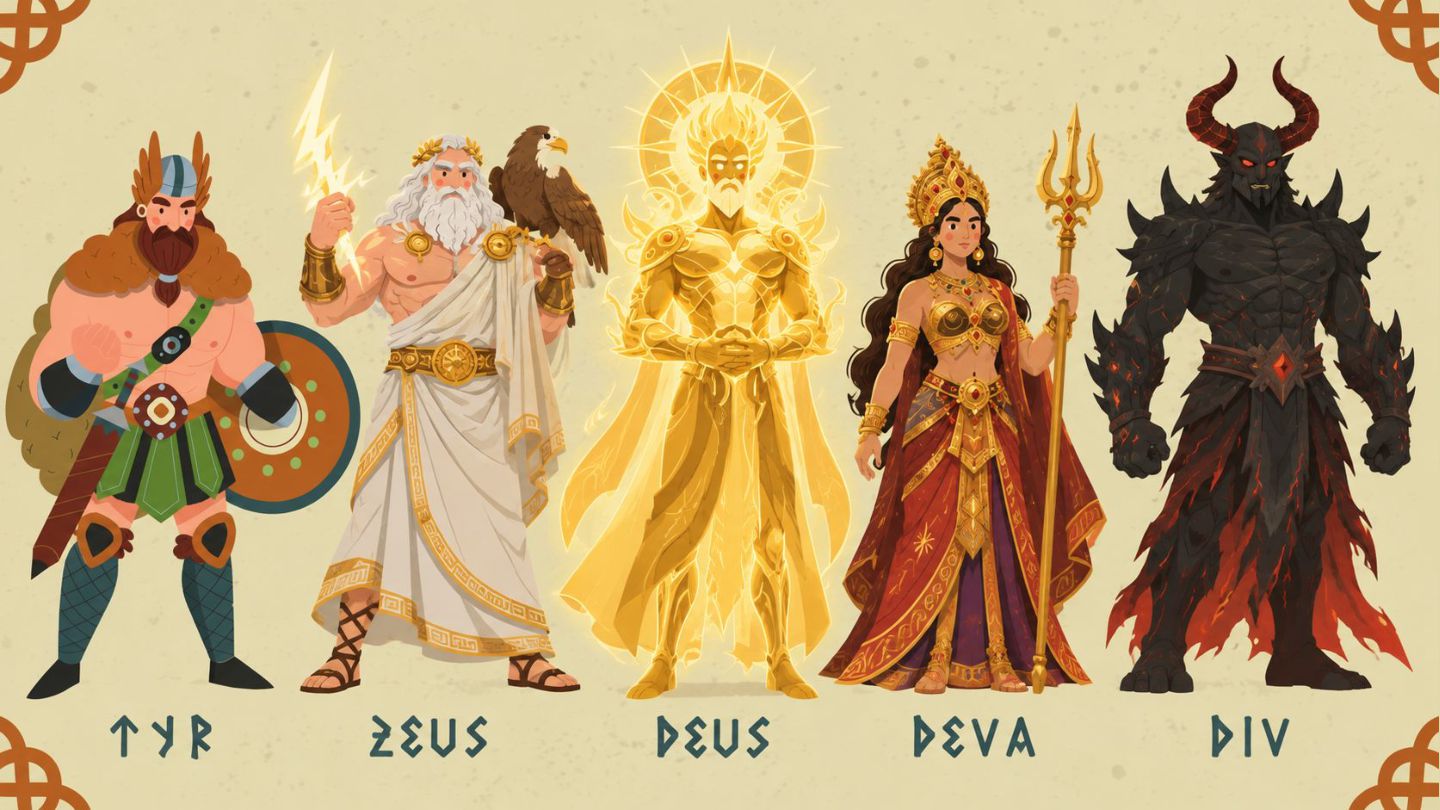
Whose Day is It on Tuesday? Tyr
None
None
None
None
Dockerize Securely v2.0.0-halloween-edition Mohammad-Ali A’râbi BaselOne, Basel, BS, Switzerland
Mohammad-Ali A’râbi Software Engineer @ JobRad Docker Captain Author of
“Docker and Kubernetes Security” Books: ContainerSecurity.dev LinkedIn, Twitter, Medium: @aerabi BlueSky, website: aerabi.com
Let’s fight CVEs together
CVE Common Vulnerabilities and Exposures They lurk in the shadows,
awaiting an opportunity to attack! Which CVEs do you know?
CVE Common Vulnerabilities and Exposures They lurk in the shadows,
awaiting an opportunity to attack! Meet: - React2Shell CVE-2025-55182 - Log4Shell CVE-2021-44228
Log4Shell Log4Shell was a zero-day vulnerability discovered in November 2021.
In early 2022, everyone was talking about SBOMs .
SBOM Software Bill of Materials is a list of all
of the packages on a Docker image. It became more popular after the Log4Shell incident. SBOMs help identify affected dependencies quickly.
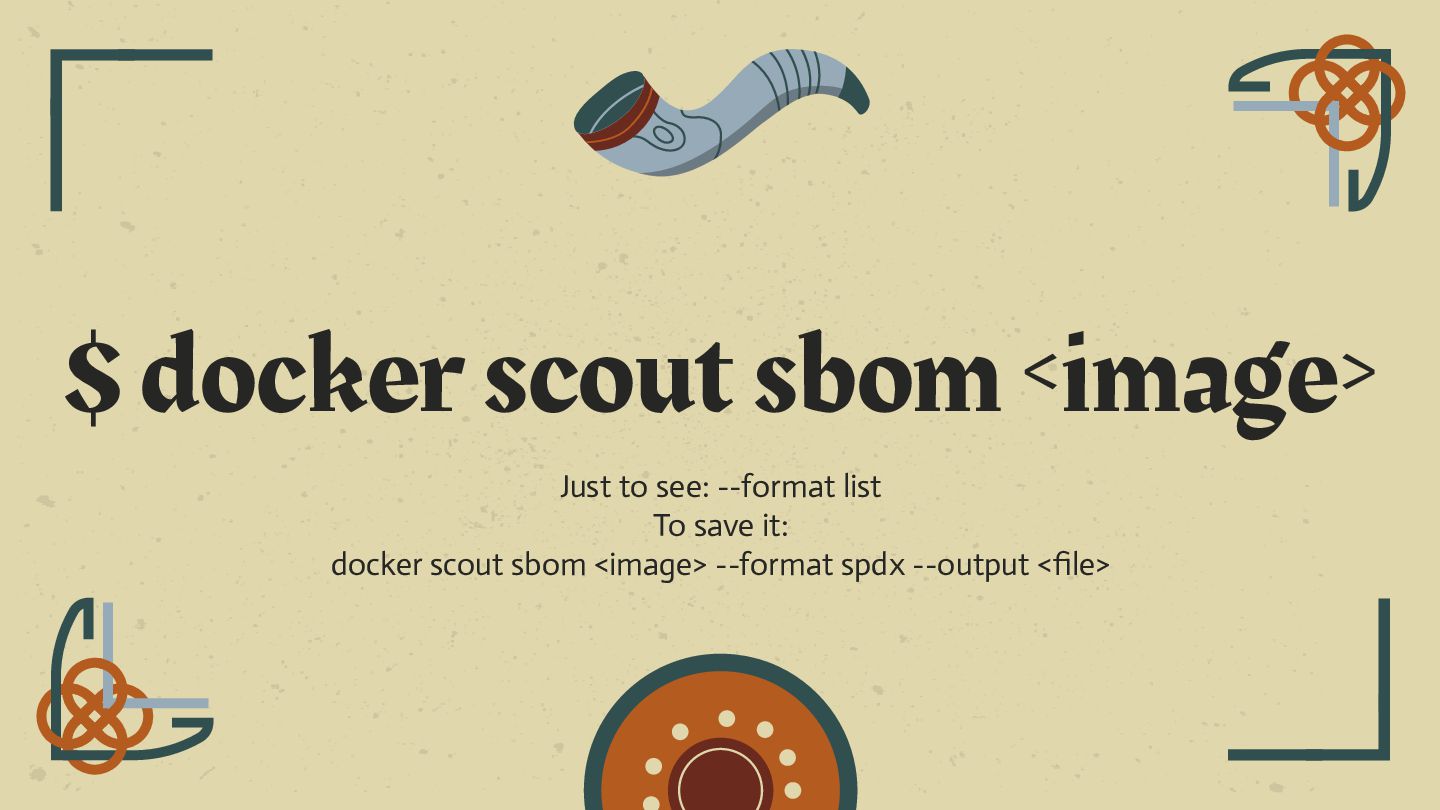
$ docker scout sbom <image> Just to see: --format list
To save it: docker scout sbom <image> --format spdx --output <file>
None
None
Jack Cryptojack Jack the Buur Jack-o’-Lantern 1 Docker Scout Jack-o’-Lantern
is coming to illuminate the night
None
$ docker scout cves <image> Checks the Docker image for
CVEs. Will use SBOM attestations if available.
$ trivy image <image> Scans OS and application dependencies for
known CVEs. Use --severity HIGH,CRITICAL to prioritize.
2 Hardened Images How hard can it be?
None
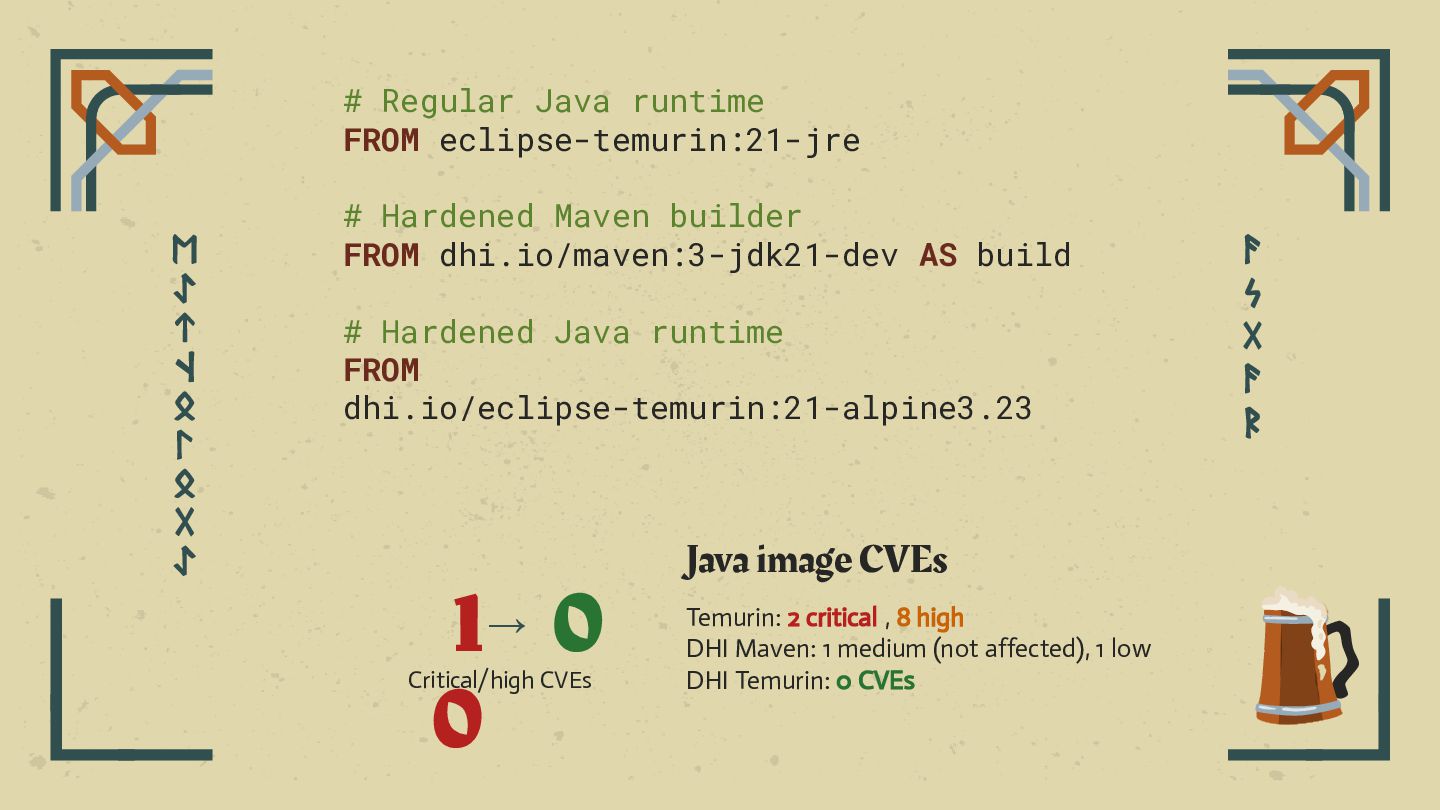
DHI Docker Hardened Images are minimal images designed to reduce
attack surface and known vulnerabilities. Use -dev variants for build stages and minimal runtime variants in production.
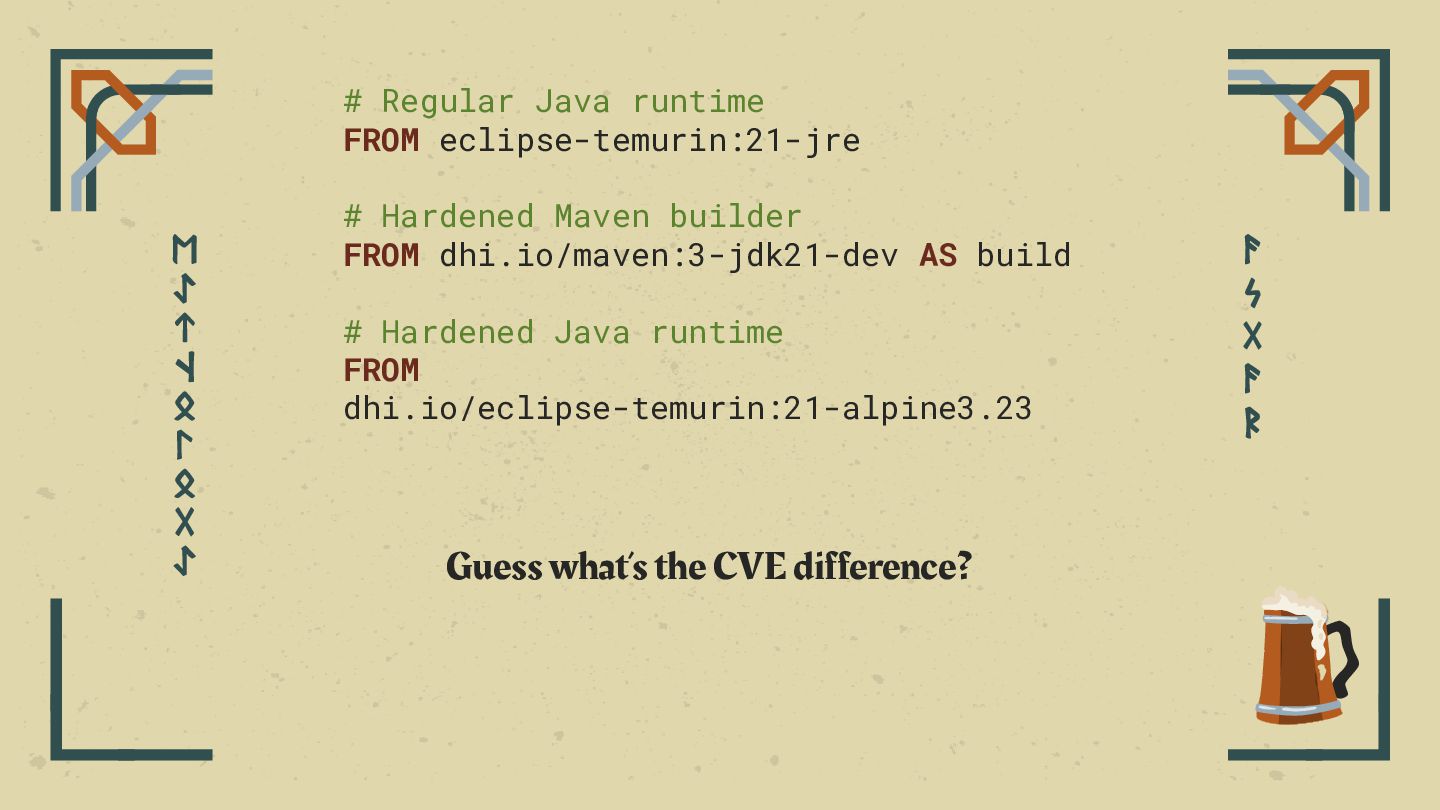
# Regular Java runtime FROM eclipse-temurin:21-jre # Hardened Maven builder
FROM dhi.io/maven:3-jdk21-dev AS build # Hardened Java runtime FROM dhi.io/eclipse-temurin:21-alpine3.23 Guess what’s the CVE difference?
# Regular Java runtime FROM eclipse-temurin:21-jre # Hardened Maven builder
FROM dhi.io/maven:3-jdk21-dev AS build # Hardened Java runtime FROM dhi.io/eclipse-temurin:21-alpine3.23 1→ 0 0 Critical/high CVEs Java image CVEs Temurin: 2 critical , 8 high DHI Maven: 1 medium (not affected), 1 low DHI Temurin: 0 CVEs
None
3 SBOM Attestations Passports for packages
None
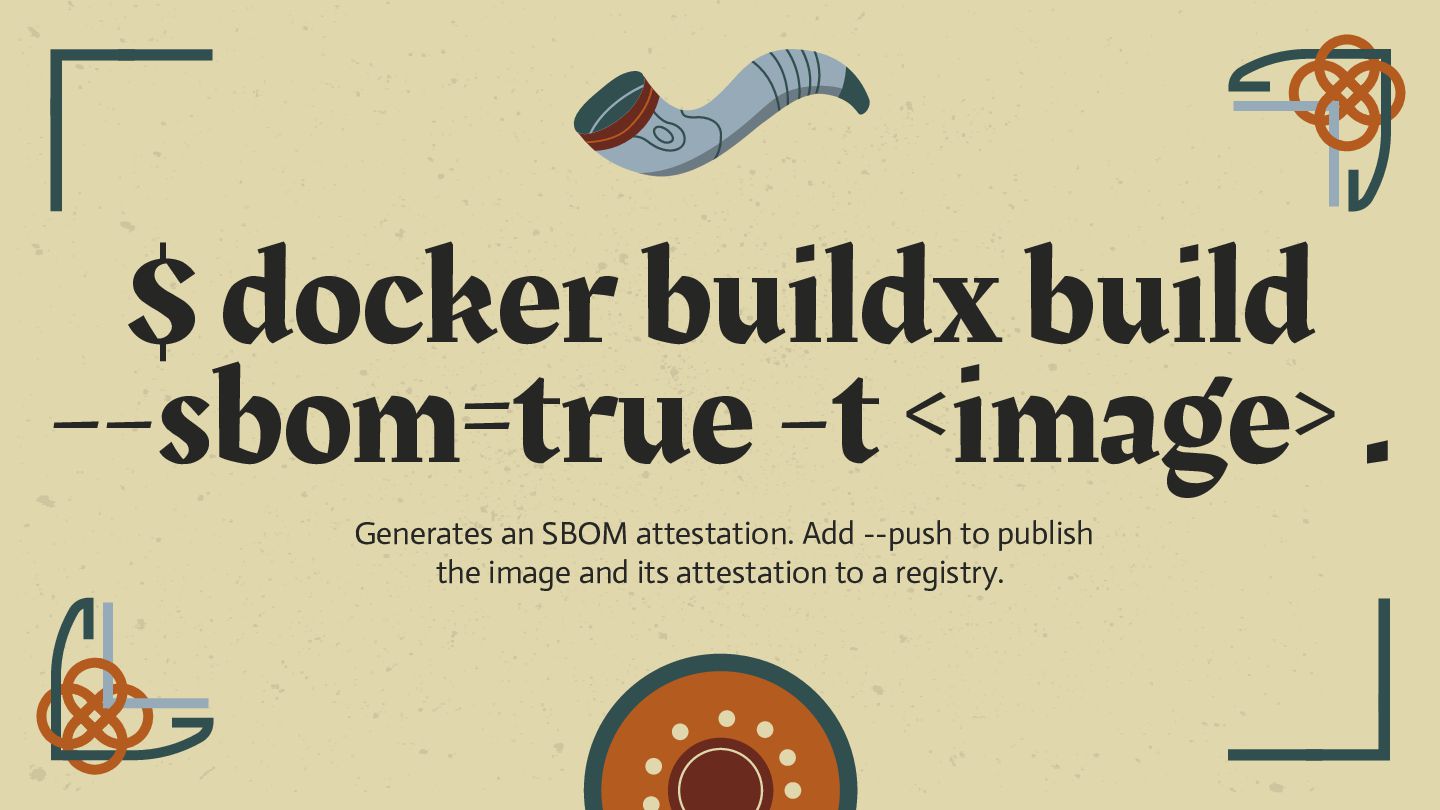
$ docker buildx build --sbom=true -t <image> . Generates an
SBOM attestation. Add --push to publish the image and its attestation to a registry.
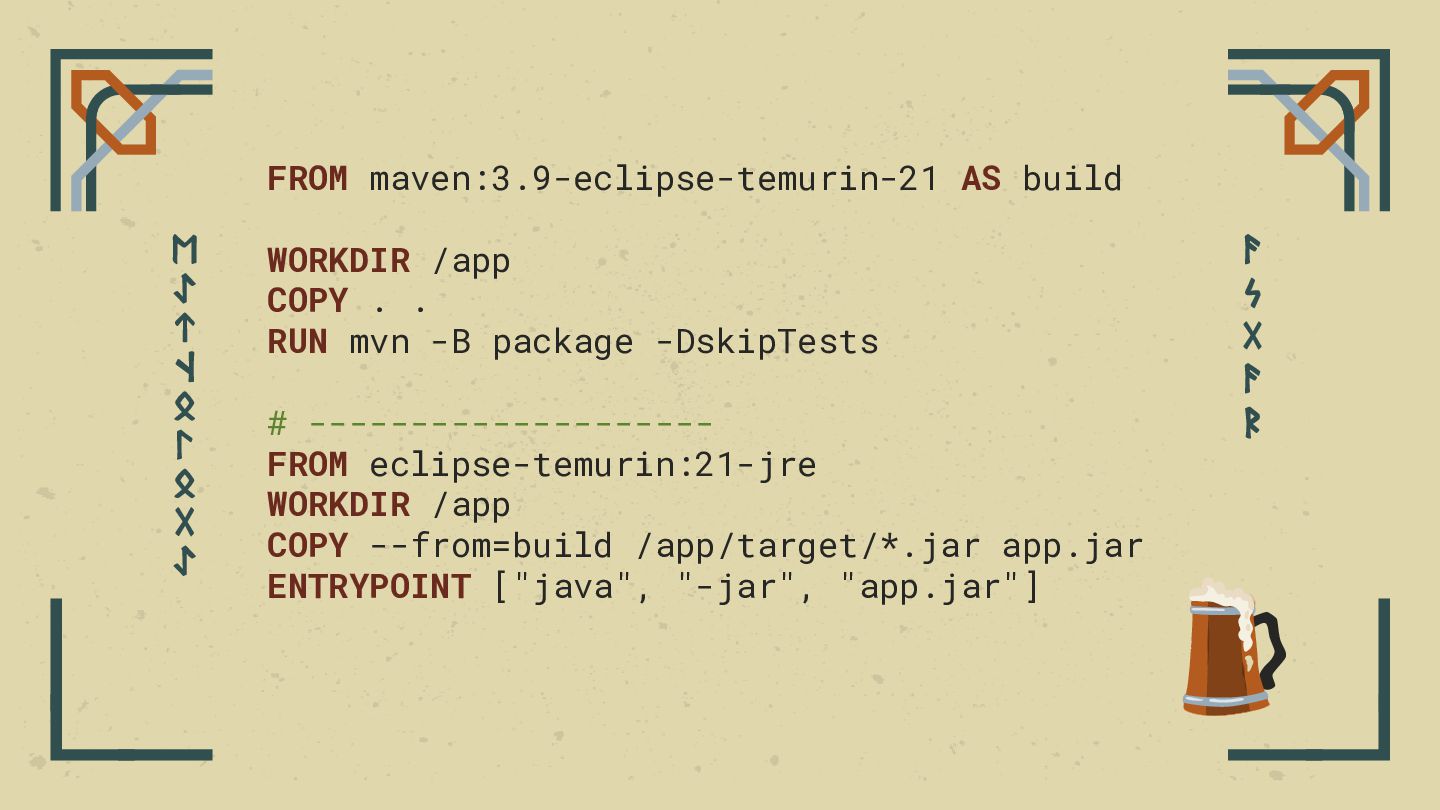
FROM maven:3.9-eclipse-temurin-21 AS build WORKDIR /app COPY . . RUN
mvn -B package -DskipTests # -------------------FROM eclipse-temurin:21-jre WORKDIR /app COPY --from=build /app/target/*.jar app.jar ENTRYPOINT ["java", "-jar", "app.jar"]
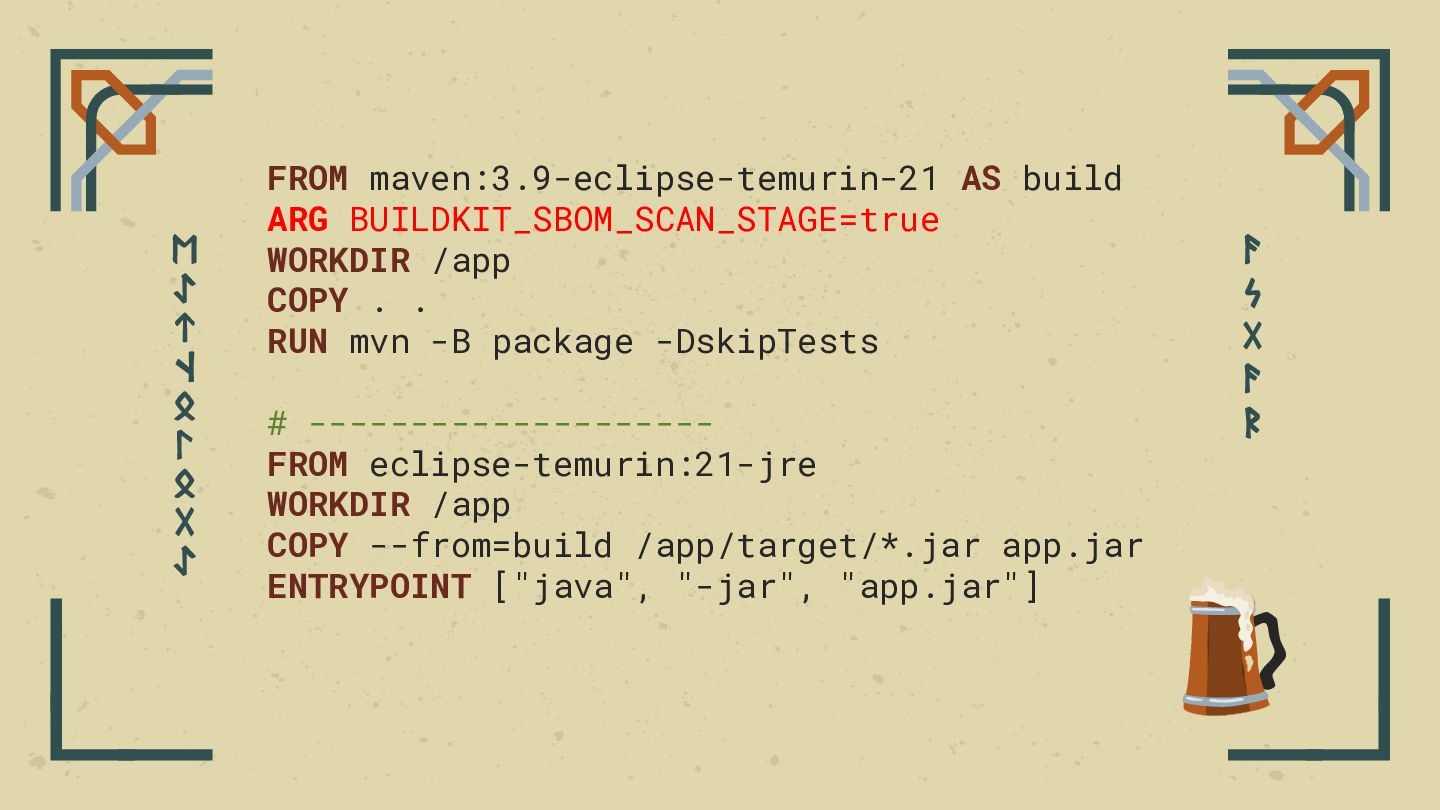
FROM maven:3.9-eclipse-temurin-21 AS build ARG BUILDKIT_SBOM_SCAN_STAGE=true WORKDIR /app COPY .
. RUN mvn -B package -DskipTests # -------------------FROM eclipse-temurin:21-jre WORKDIR /app COPY --from=build /app/target/*.jar app.jar ENTRYPOINT ["java", "-jar", "app.jar"]
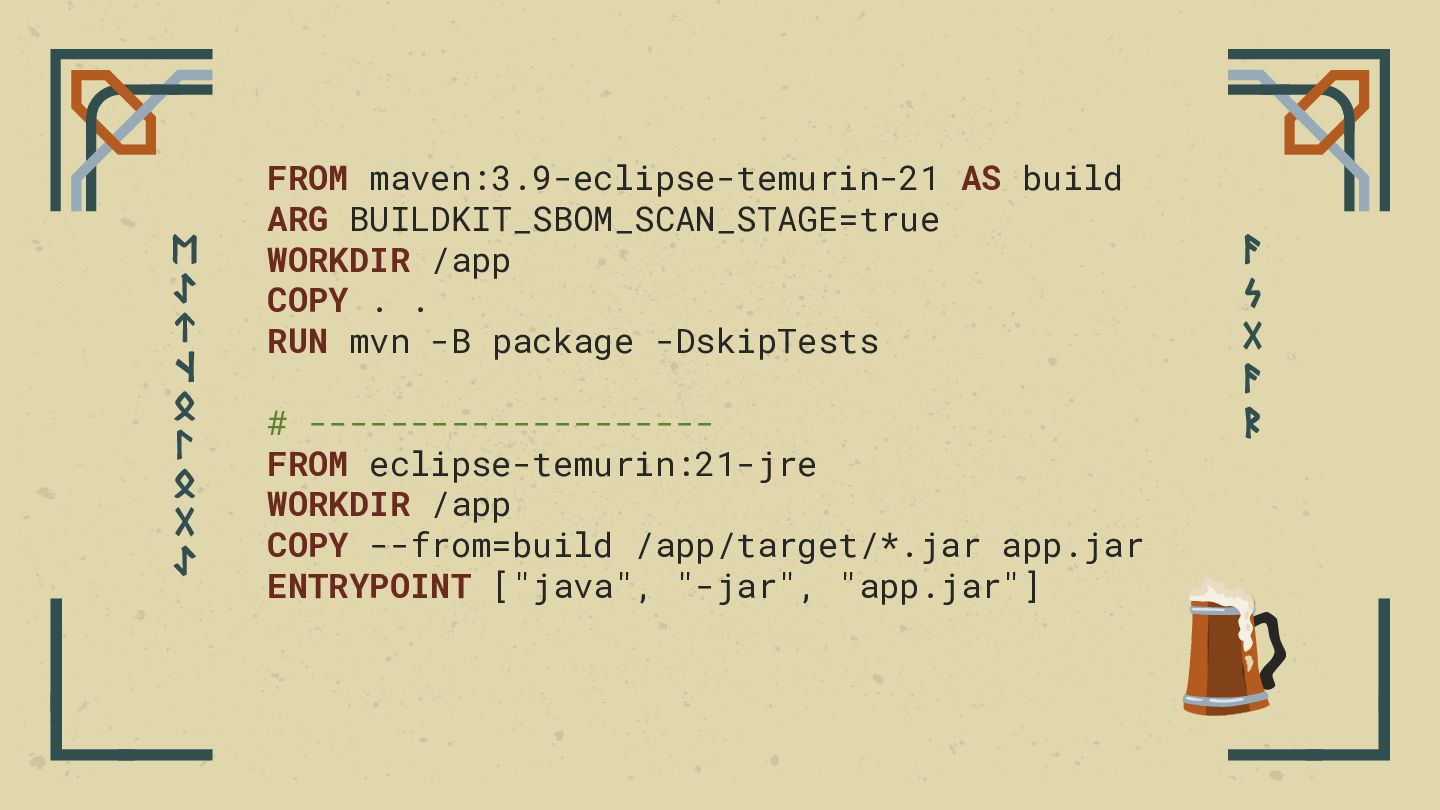
FROM maven:3.9-eclipse-temurin-21 AS build ARG BUILDKIT_SBOM_SCAN_STAGE=true WORKDIR /app COPY .
. RUN mvn -B package -DskipTests # -------------------FROM eclipse-temurin:21-jre WORKDIR /app COPY --from=build /app/target/*.jar app.jar ENTRYPOINT ["java", "-jar", "app.jar"]
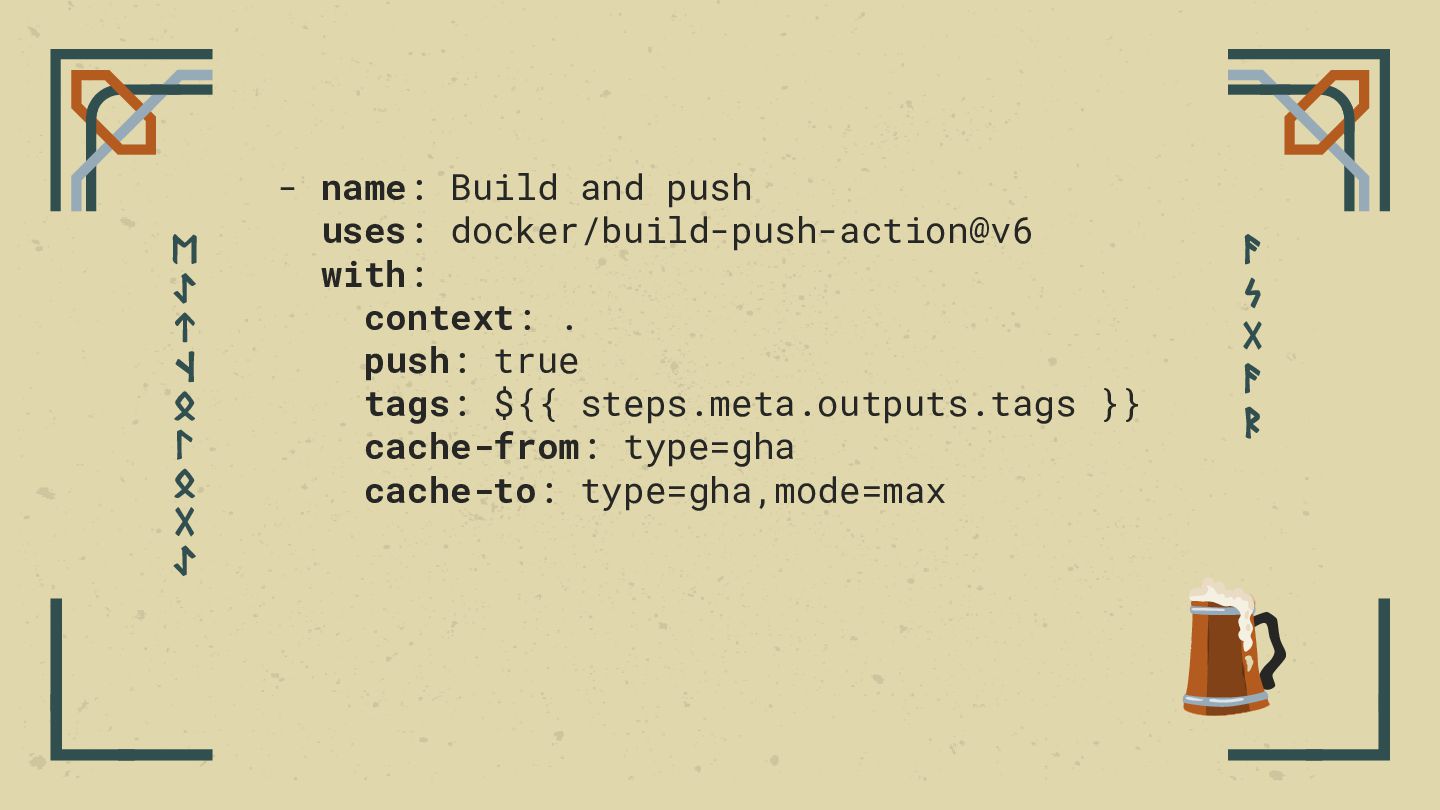
- name: Build and push uses: docker/build-push-action@v6 with: context: .
push: true tags: ${{ steps.meta.outputs.tags }} cache-from: type=gha cache-to: type=gha,mode=max
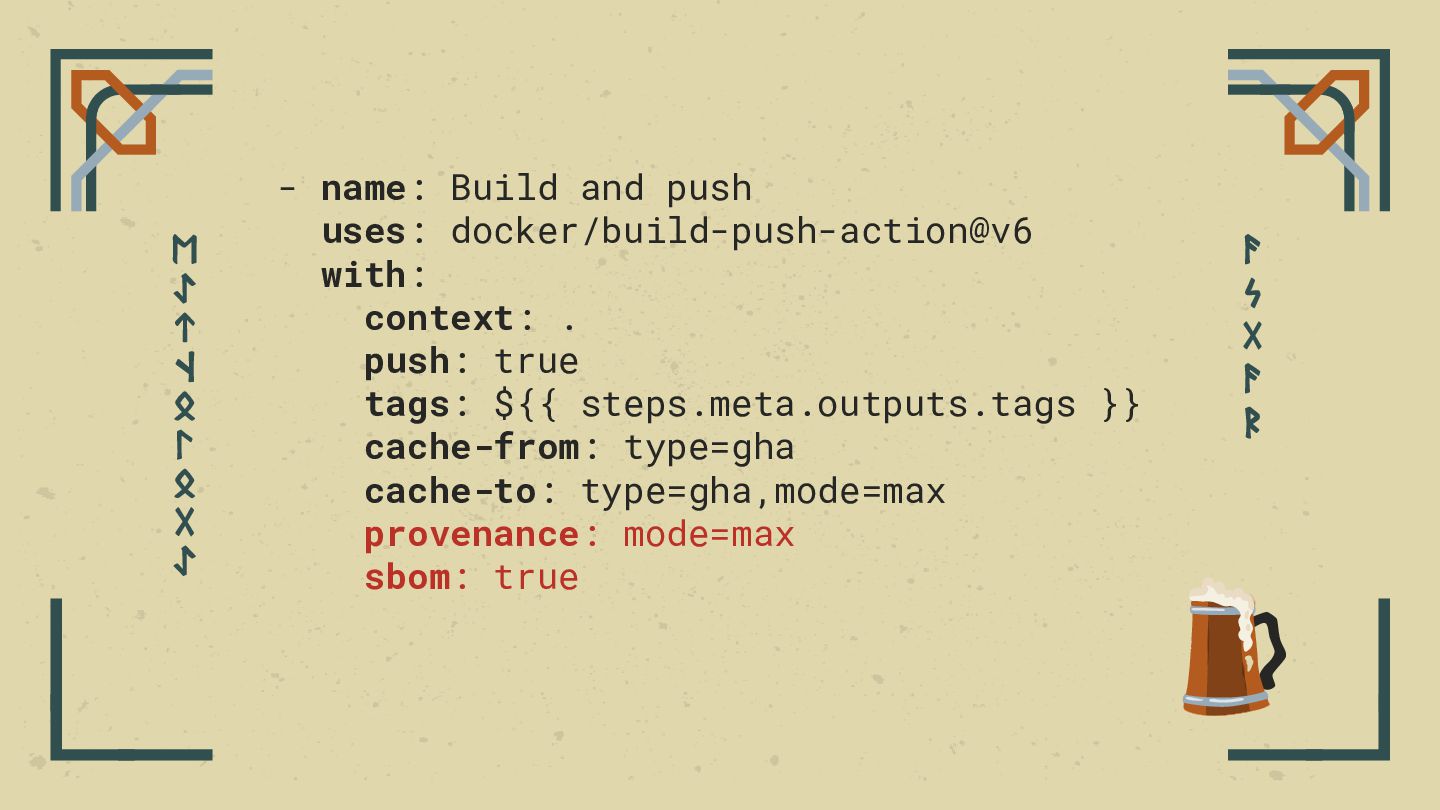
- name: Build and push uses: docker/build-push-action@v6 with: context: .
push: true tags: ${{ steps.meta.outputs.tags }} cache-from: type=gha cache-to: type=gha,mode=max provenance: mode=max sbom: true
Selfie Say CVE!
None
4 The Signature Here is Evie
None
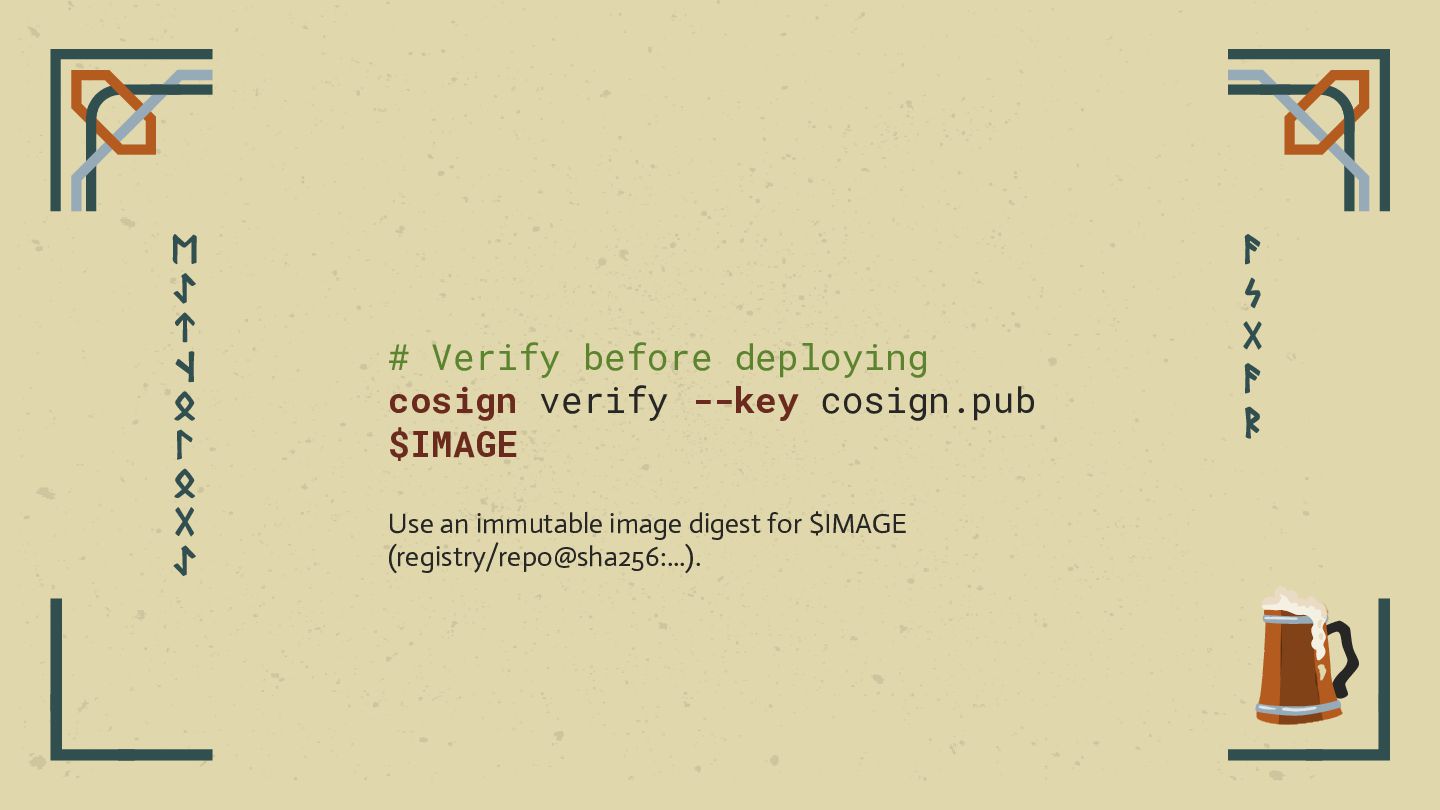
# Generate signing keys once cosign generate-key-pair # Sign a
pushed image by digest cosign sign --key cosign.key $IMAGE
# Verify before deploying cosign verify --key cosign.pub $IMAGE Use
an immutable image digest for $IMAGE (registry/repo@sha256:...).
Are we safe We have generated SBOM attestations, checked for
CVEs, used DHI, and signed the images.
None
Shai Hulud Shai-Hulud spread through compromised npm packages. Malicious npm
content has also crossed into Maven Central.
None
0 SIP it before you ship it Let’s have a
SIP of security
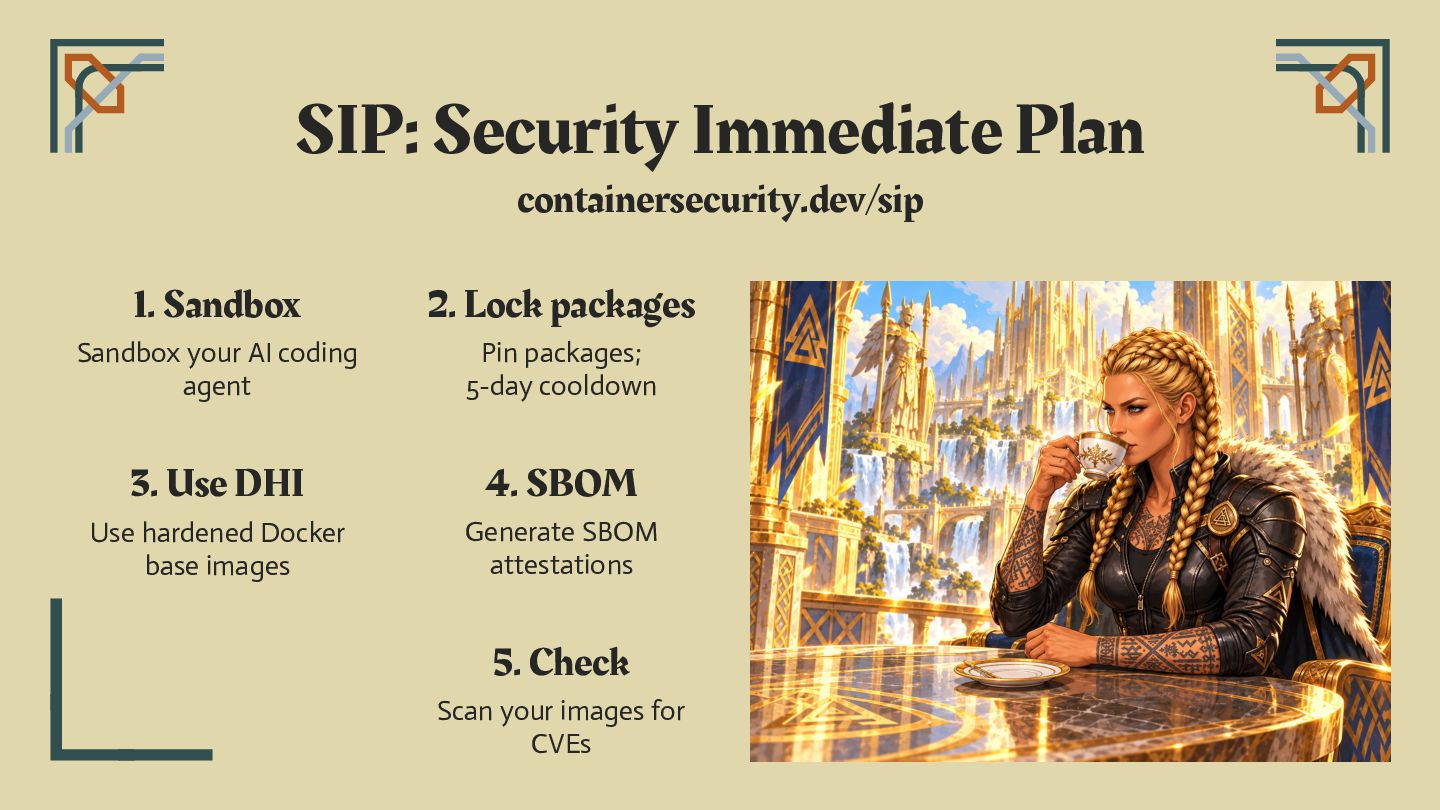
SIP: Security Immediate Plan containersecurity.dev/sip 1. Sandbox 2. Lock packages
Sandbox your AI coding agent Pin packages; 5-day cooldown 3. Use DHI 4. SBOM Use hardened Docker base images Generate SBOM attestations 5. Check Scan your images for CVEs
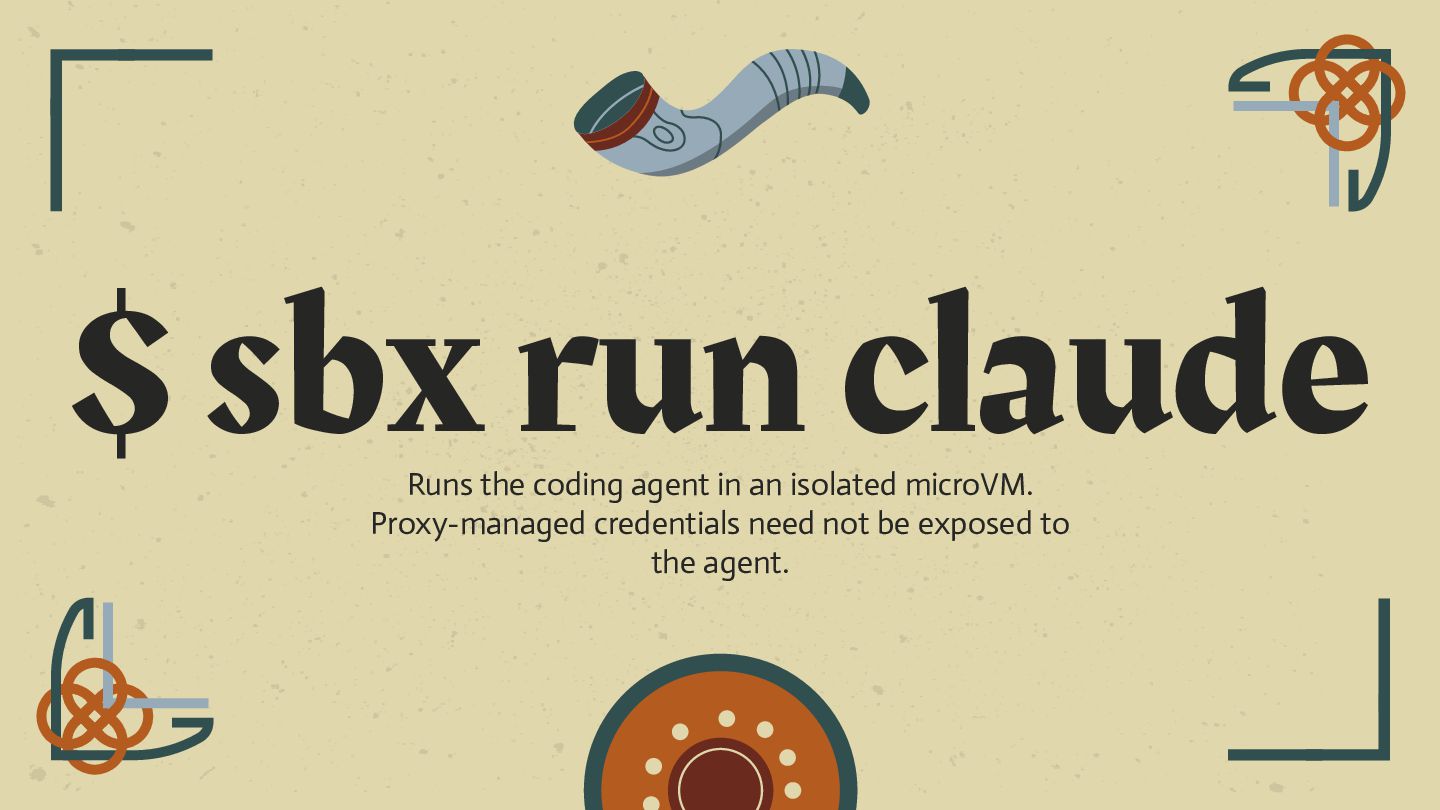
$ sbx run claude Runs the coding agent in an
isolated microVM. Proxy-managed credentials need not be exposed to the agent.
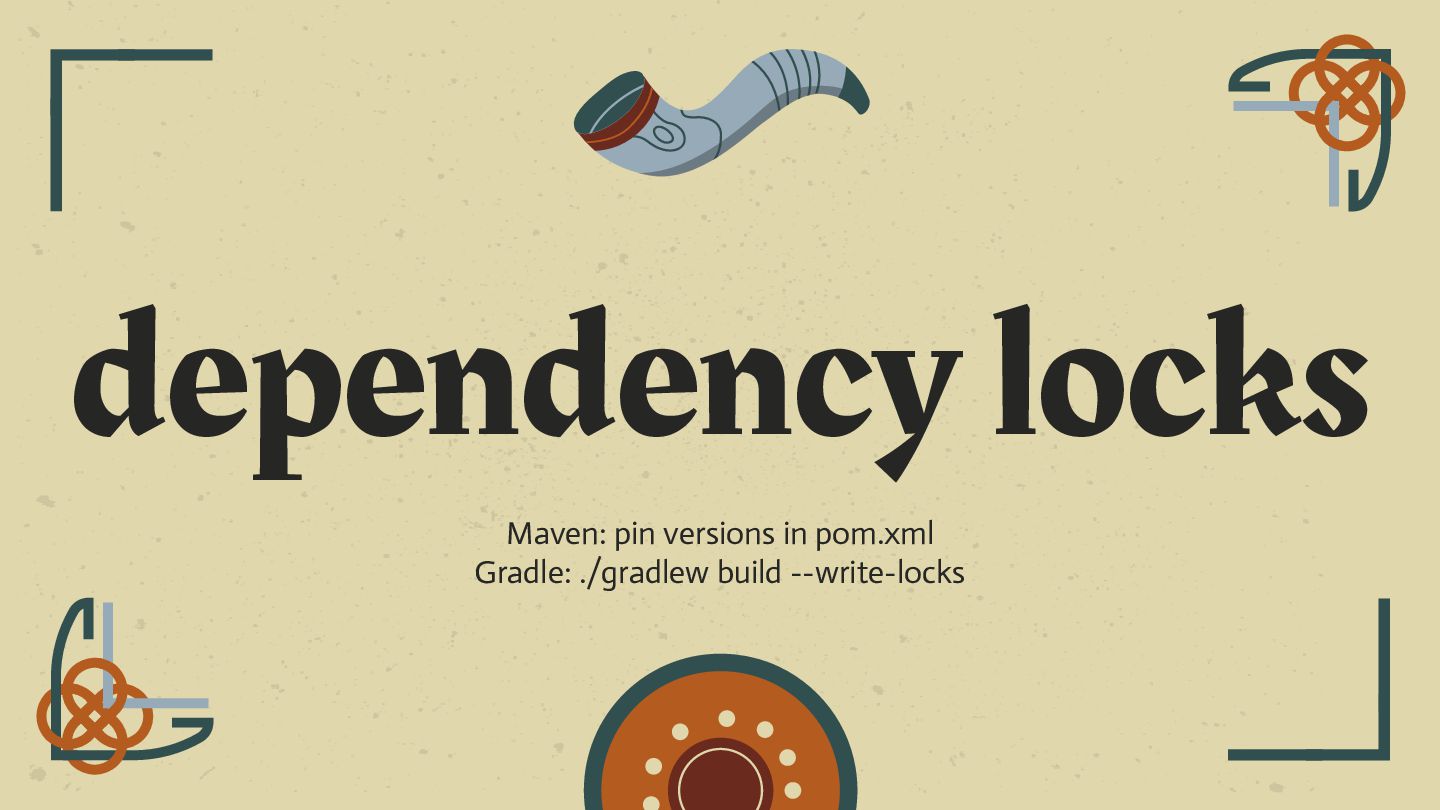
dependency locks Maven: pin versions in pom.xml Gradle: ./gradlew build
--write-locks
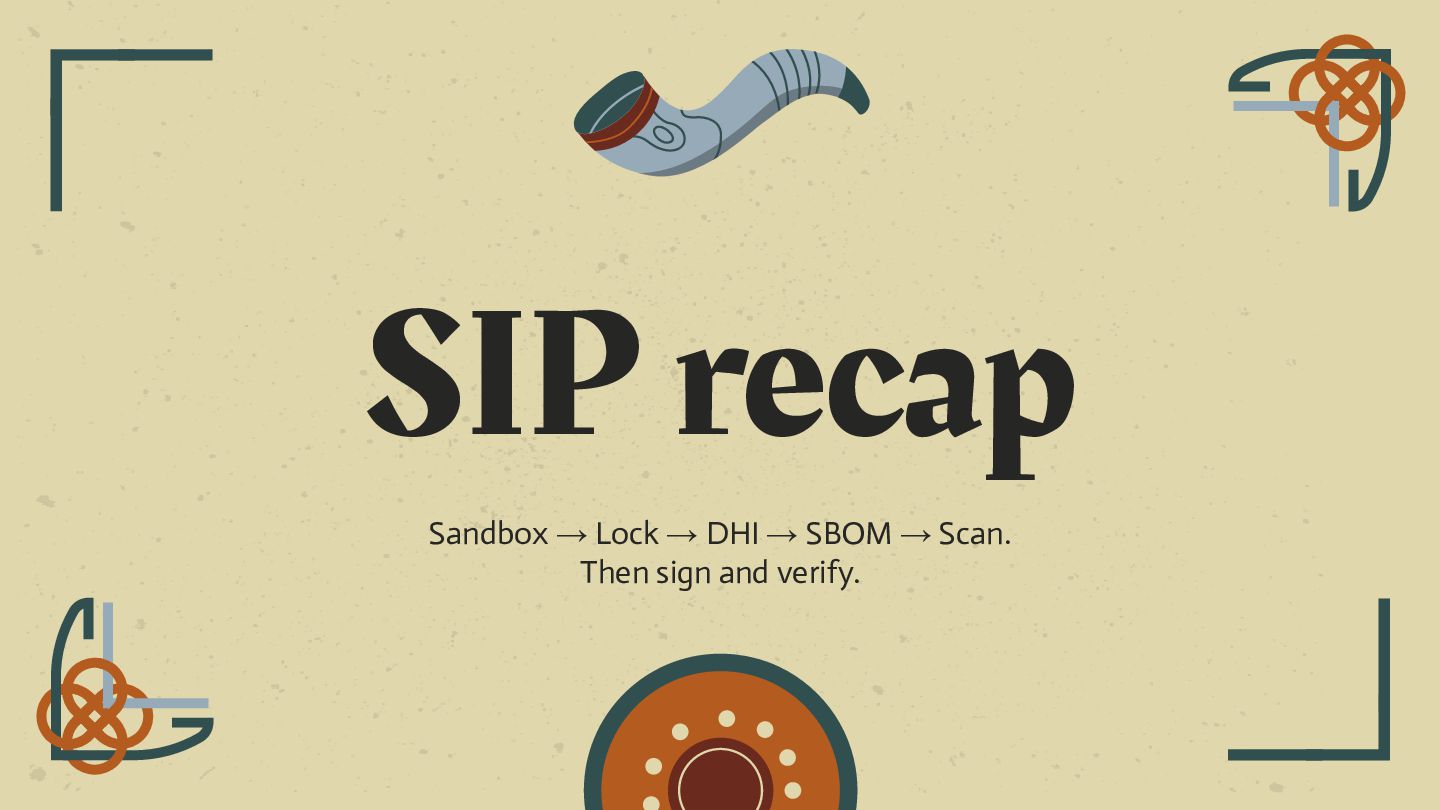
SIP recap Sandbox → Lock → DHI → SBOM →
Scan. Then sign and verify.
# Outro Get out! —Arnold Schwarzenegger
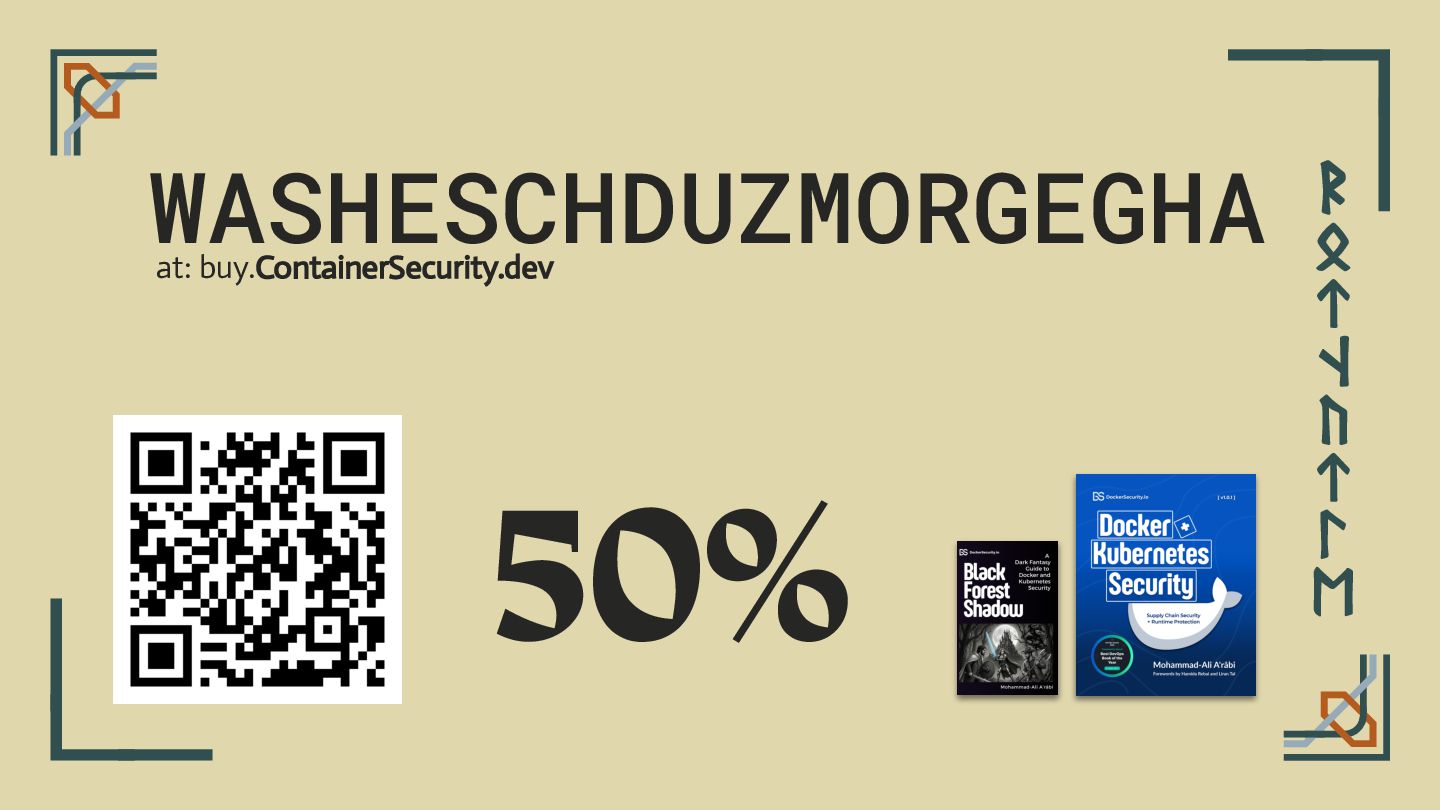
WASHESCHDUZMORGEGHA at: buy.ContainerSecurity.dev 50%
ContainerSecurity.dev Books Links Blog Games
Don’t forget to like and subscribe Disclaimer: BaselOne gave me
this QR code. If you got phished, it’s not me hacking you.
Thanks! Do you have any questions?
[email protected]
aerabi.com CREDITS: This
presentation template was created by Slidesgo , and includes icons by Flaticon , and infographics & images by Freepik
More Decks by Mohammad-Ali A'râbi
See All by Mohammad-Ali A'râbi
Beyond SBOMs: The Future of Container Supply Chain Security
aerabi
0
92
Featured
See All Featured
世界の人気アプリ100個を分析して見えたペイウォール設計の心得
akihiro_kokubo
PRO
74
43k
Un-Boring Meetings
codingconduct
0
500
Six Lessons from altMBA
skipperchong
29
4.6k
Learning to Love Humans: Emotional Interface Design
aarron
275
41k
Refactoring Trust on Your Teams (GOTO; Chicago 2020)
rmw
35
3.9k
Avoiding the “Bad Training, Faster” Trap in the Age of AI
tmiket
1
310
How Fast Is Fast Enough? [PerfNow 2025]
tammyeverts
3
980
Rebuilding a faster, lazier Slack
samanthasiow
85
9.8k
Odyssey Design
rkendrick25
PRO
3
950
Producing Creativity
orderedlist
PRO
348
41k
The Psychology of Web Performance [Beyond Tellerrand 2023]
tammyeverts
49
3.6k
Documentation Writing (for coders)
carmenintech
77
5.6k


 aerabi
 akihiro_kokubo
 codingconduct
 skipperchong
 aarron
 rmw
 tmiket
 tammyeverts
 samanthasiow
 rkendrick25
 orderedlist
 carmenintech