Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
Introduction to OAuth
Search
Sponsored
·
SiteGround - Reliable hosting with speed, security, and support you can count on.
→
Alex Bilbie
May 30, 2012
Technology
2.2k
6
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
Introduction to OAuth
Delivered at the Eduserv Federated Access Management conference 2011 on 9th November 2011
Alex Bilbie
May 30, 2012
More Decks by Alex Bilbie
See All by Alex Bilbie
12 Factor Laravel Apps
alexbilbie
1
630
The Joy of Open Data
alexbilbie
0
200
API Driven Development
alexbilbie
8
5.2k
Linkey Project
alexbilbie
0
1.8k
Linking You
alexbilbie
2
830
Introduction to HTML5 and CSS3
alexbilbie
3
1.6k
The @lncd toolchain
alexbilbie
2
1.5k
Introduction to MongoDB
alexbilbie
2
380
Other Decks in Technology
See All in Technology
AIに任せられるFlutterコードベースを作る 〜仕様をコードで表し、ハーネスで守る〜
myohei
1
290
CTO Night & Day Morning Session_AI-DLC:生成 AI 時代の開発プロセス変革
pikosan0000
0
110
You Have Agency(サンキュー、Ruby)
snoozer05
PRO
3
350
Deep Data Security 機能解説
oracle4engineer
PRO
3
950
Autonomous AI Lakehouse - Live AI Hubから始めるセキュアなAIデータ活用 -
oracle4engineer
PRO
2
160
200人の配信コメント、 全部Jevが仕分けます 〜 マサカリガードを作ってみた 〜
katayamatg
1
310
【データ横丁主催】AI エージェント時代のTranslytical Data Platform
shisyu_gaku
0
300
[FECONF-2026] 신대륙을 향한 카카오페이증권 프론트엔드 항해기 (이주승)
l1ghthouse
0
230
生成AI時代、PMは事業責任者に進化するともっと面白い〜PMだからこそ事業構造を動かせる時代に〜
kakehashi
PRO
1
910
クラウドエージェントの先駆け Devin。今も最先端を走る、他との違い
kinopeee
1
480
AI時代の開発はウォーターフォールに回帰する? / development-with-ai-back-to-wf
okamototakuyasr2
0
130
これだけは抑えておきたい!後悔しない re:Invent の過ごし方 / AWS re:Invent 2026 prestudy
kinunori
2
450
Featured
See All Featured
From Legacy to Launchpad: Building Startup-Ready Communities
dugsong
0
360
Bridging the Design Gap: How Collaborative Modelling removes blockers to flow between stakeholders and teams @FastFlow conf
baasie
0
740
Code Reviewing Like a Champion
maltzj
529
40k
Are puppies a ranking factor?
jonoalderson
2
4.1k
ラッコキーワード サービス紹介資料
rakko
5
5.5M
Building a Scalable Design System with Sketch
lauravandoore
464
34k
How To Speak Unicorn (iThemes Webinar)
marktimemedia
1
610
Documentation Writing (for coders)
carmenintech
77
5.6k
StorybookのUI Testing Handbookを読んだ
zakiyama
31
7k
個人開発の失敗を避けるイケてる考え方 / tips for indie hackers
panda_program
123
22k
How To Stay Up To Date on Web Technology
chriscoyier
790
250k
Making the Leap to Tech Lead
cromwellryan
135
10k
Transcript
Wednesday, 30 May 12
Alex Bilbie University of Lincoln @alexbilbie Wednesday, 30 May 12
Story time! Wednesday, 30 May 12
I’m a user of a web service Wednesday, 30 May
12
I own resources on the web service Wednesday, 30 May
12
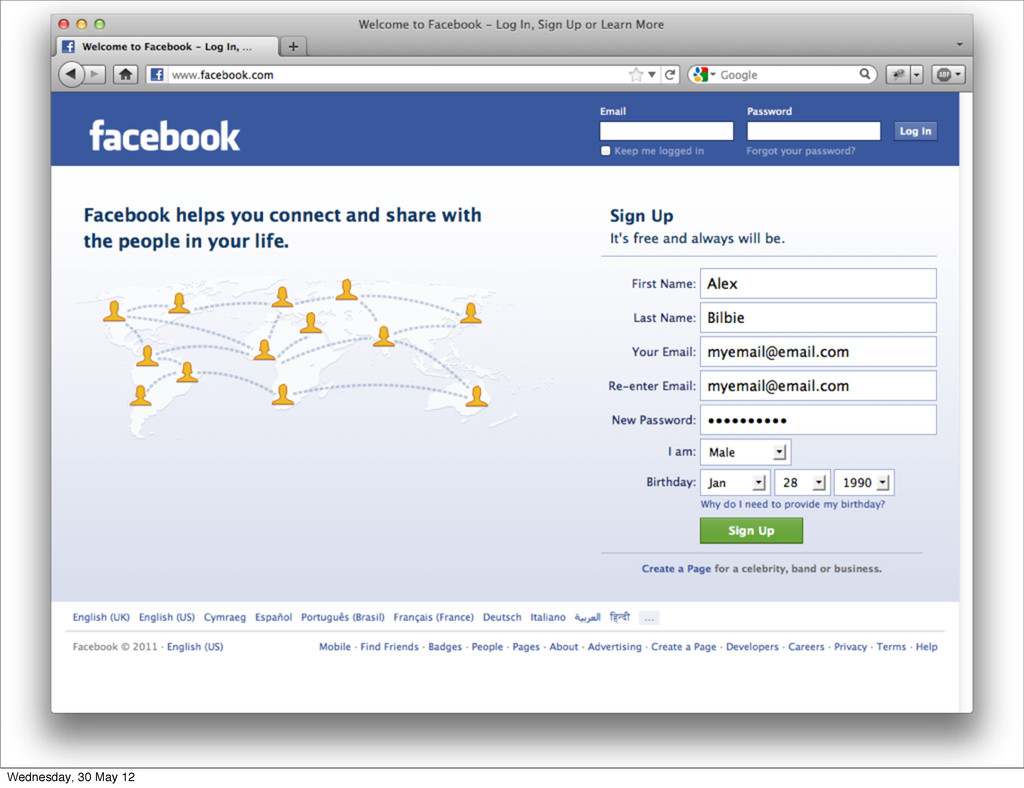
For example, personal details Wednesday, 30 May 12
Wednesday, 30 May 12
These resources1 are stored on a resource server 2 1.
personal details 2. facebook.com Wednesday, 30 May 12
The resource server exposes user resources over an API Wednesday,
30 May 12
I visit a 3rd party web application Wednesday, 30 May
12
The 3rd party web app is called a client Wednesday,
30 May 12
The client1 wants to use my resources2 1. 3rd party
web app 2. personal details Wednesday, 30 May 12
But the resource server’s API requires user authorisation Wednesday, 30
May 12
How? Wednesday, 30 May 12
Give the client my password Wednesday, 30 May 12
Give the client my password Wednesday, 30 May 12
So what then? Wednesday, 30 May 12
OAuth Wednesday, 30 May 12
“An open protocol to allow secure API authorisation in a
simple and standard method from desktop and web applications.” oauth.net Wednesday, 30 May 12
—˛ Wednesday, 30 May 12
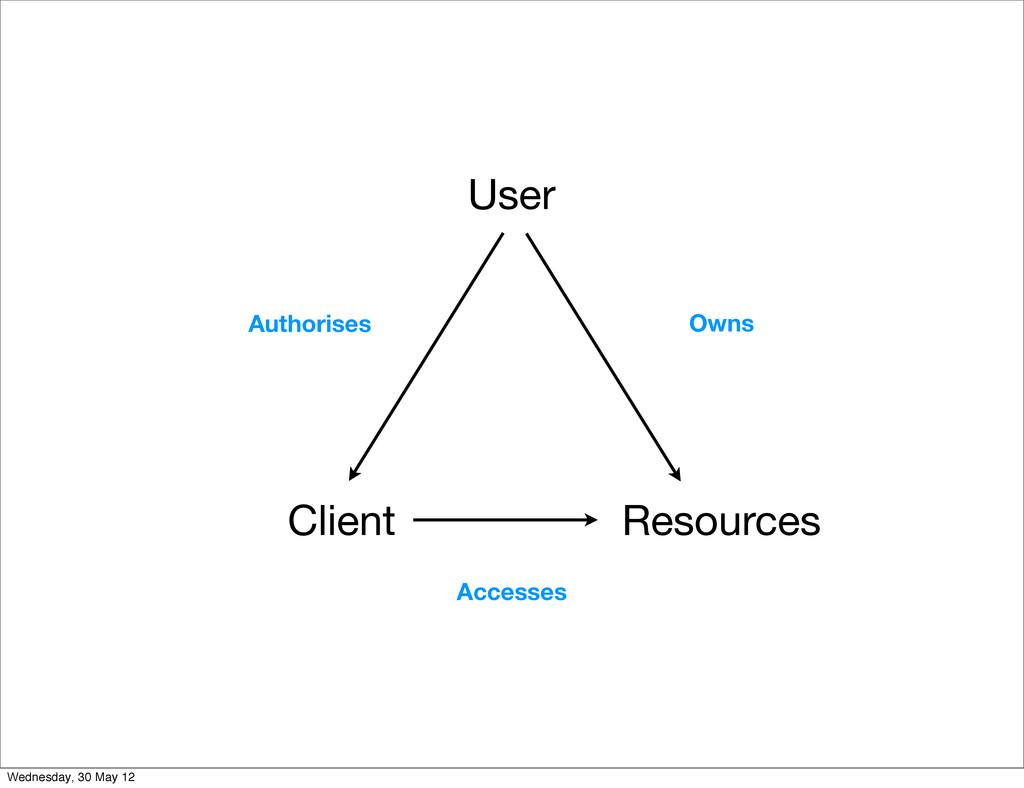
User Client Resources Owns Accesses OWNS OWNS S Authorises Wednesday,
30 May 12
The flow Wednesday, 30 May 12
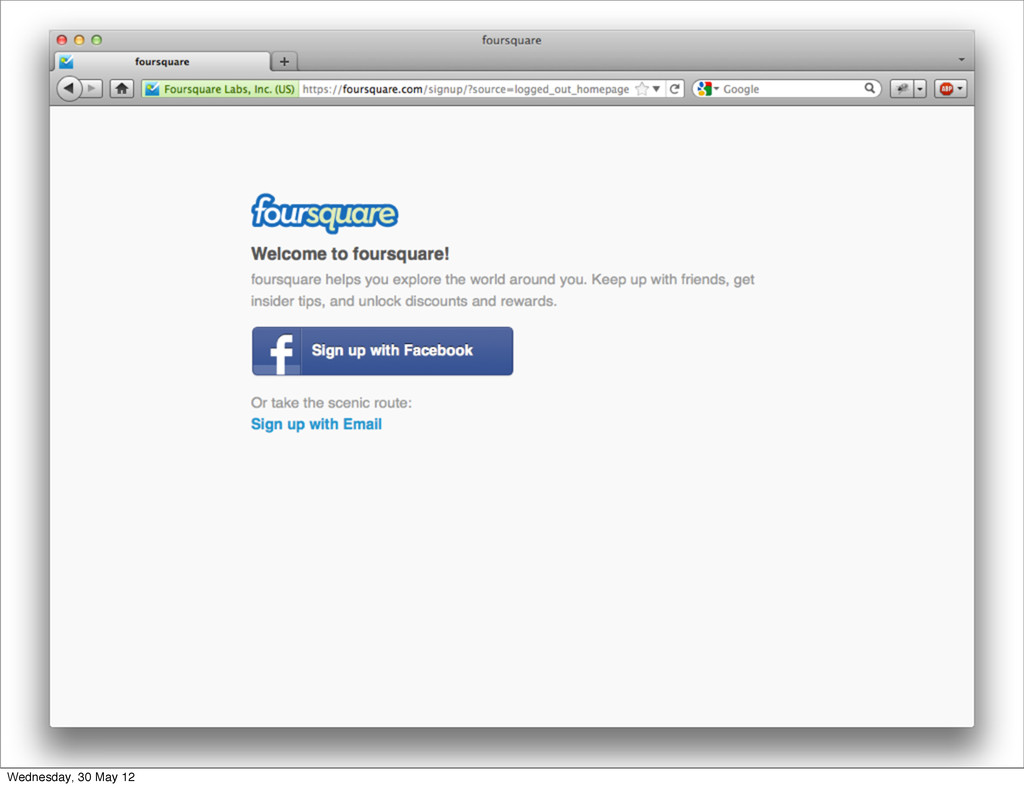
User clicks “sign in” in the client application Wednesday, 30
May 12
Wednesday, 30 May 12
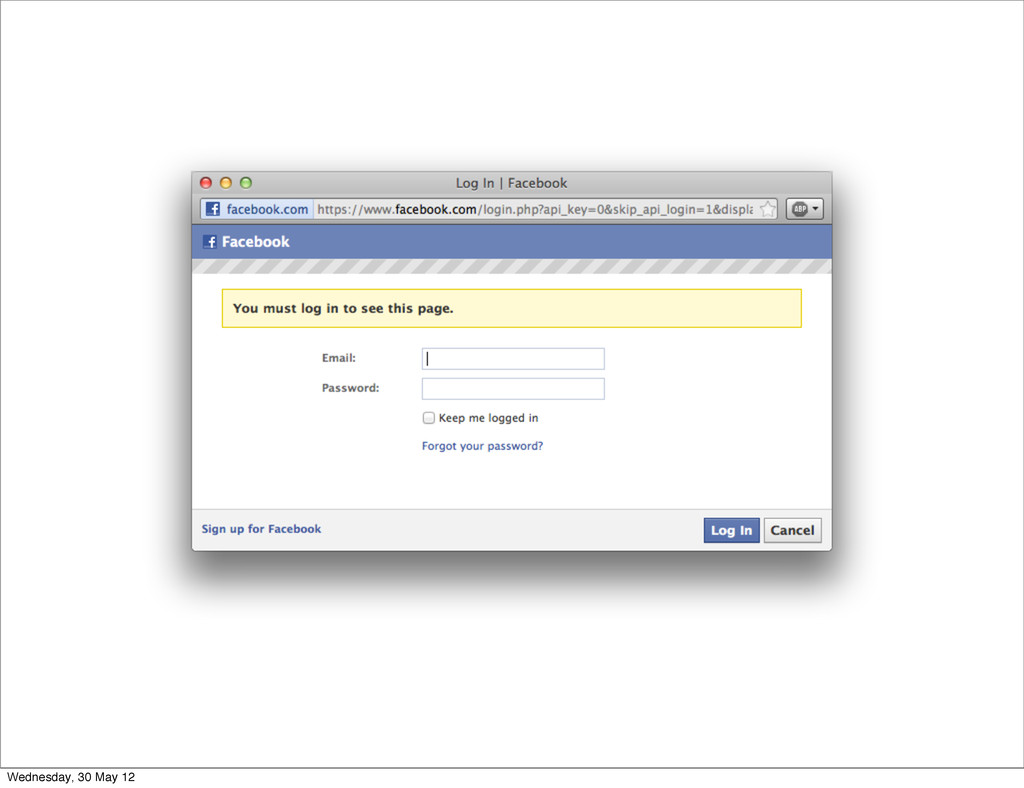
The user is redirected to the resource server and asked
to sign in Wednesday, 30 May 12
Wednesday, 30 May 12
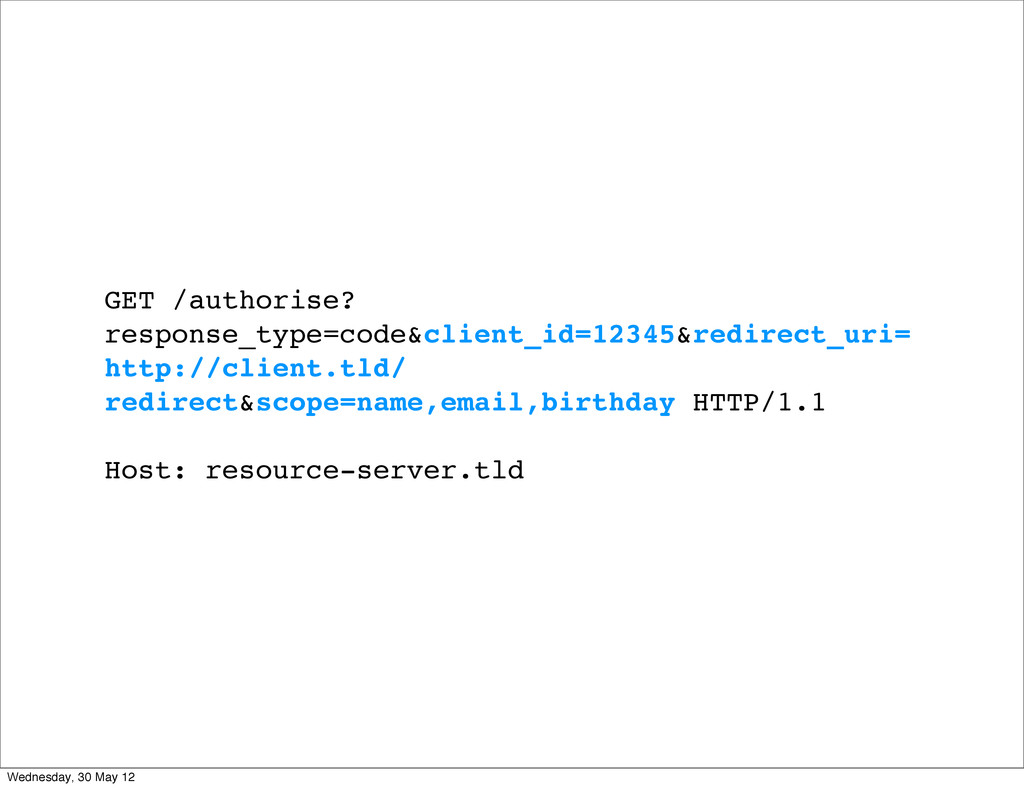
GET /authorise? response_type=code&client_id=12345&redirect_uri= http://client.tld/ redirect&scope=name,email,birthday HTTP/1.1 Host: resource-server.tld Wednesday, 30
May 12
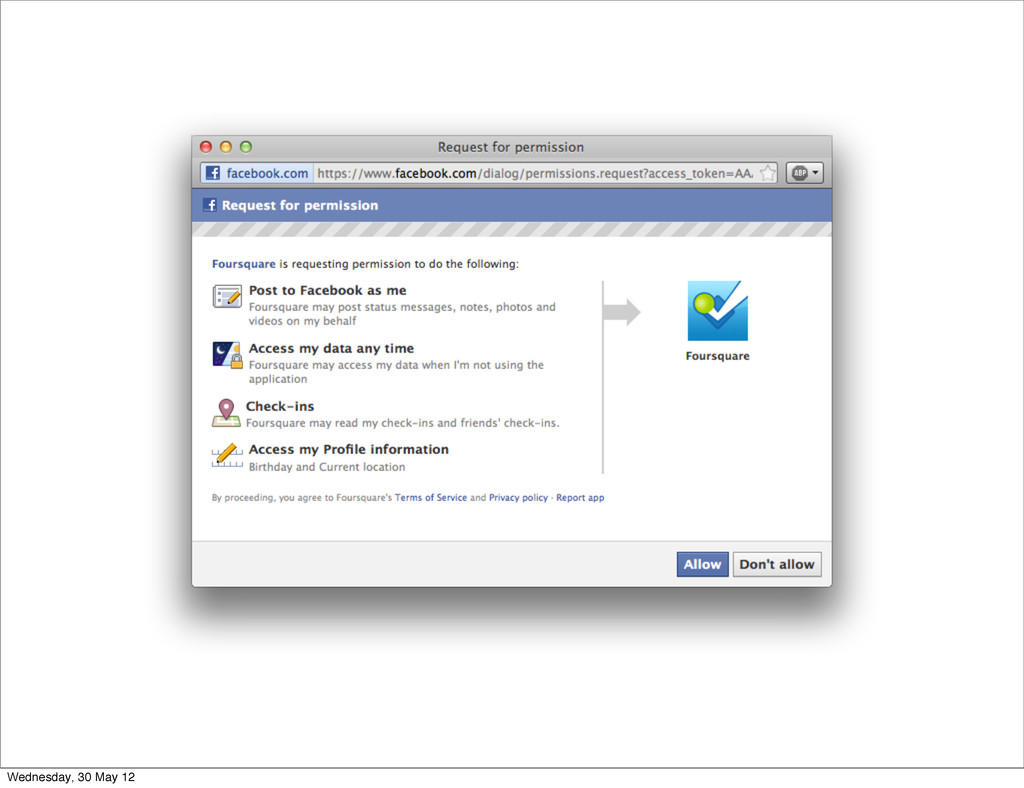
The resource server clearly tells the user the specific data
the client wants to access Wednesday, 30 May 12
Wednesday, 30 May 12
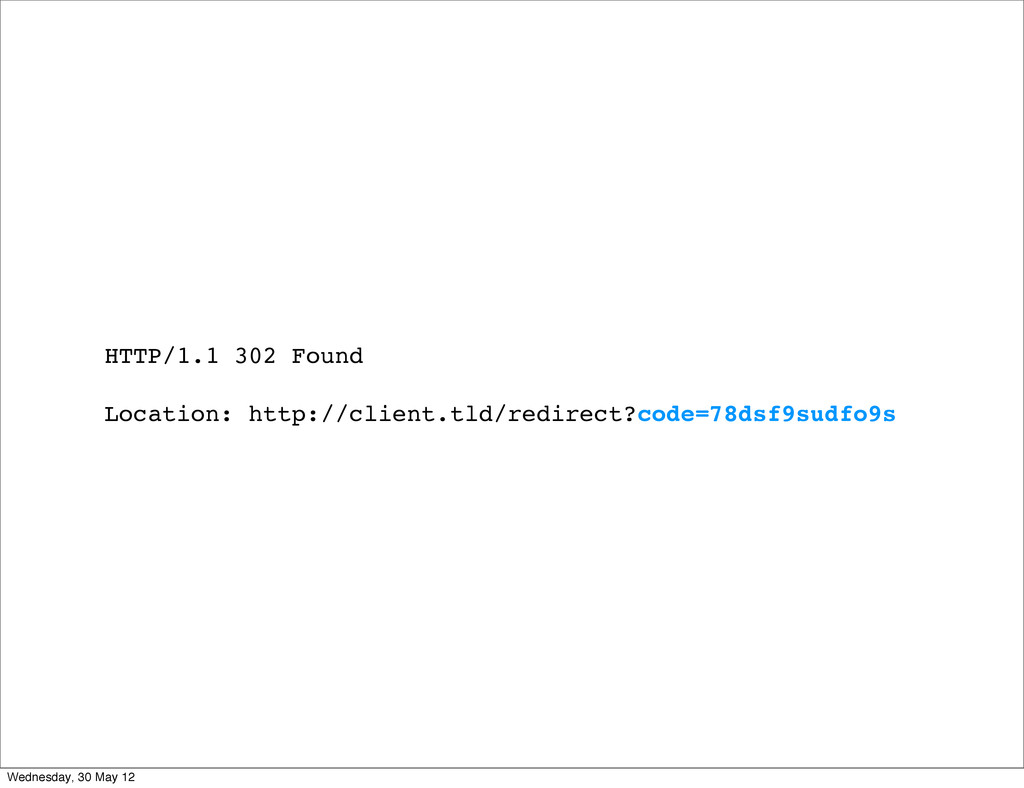
User authorises the application and is redirected back to client
with a authorisation code in the query string Wednesday, 30 May 12
HTTP/1.1 302 Found Location: http://client.tld/redirect?code=78dsf9sudfo9s Wednesday, 30 May 12
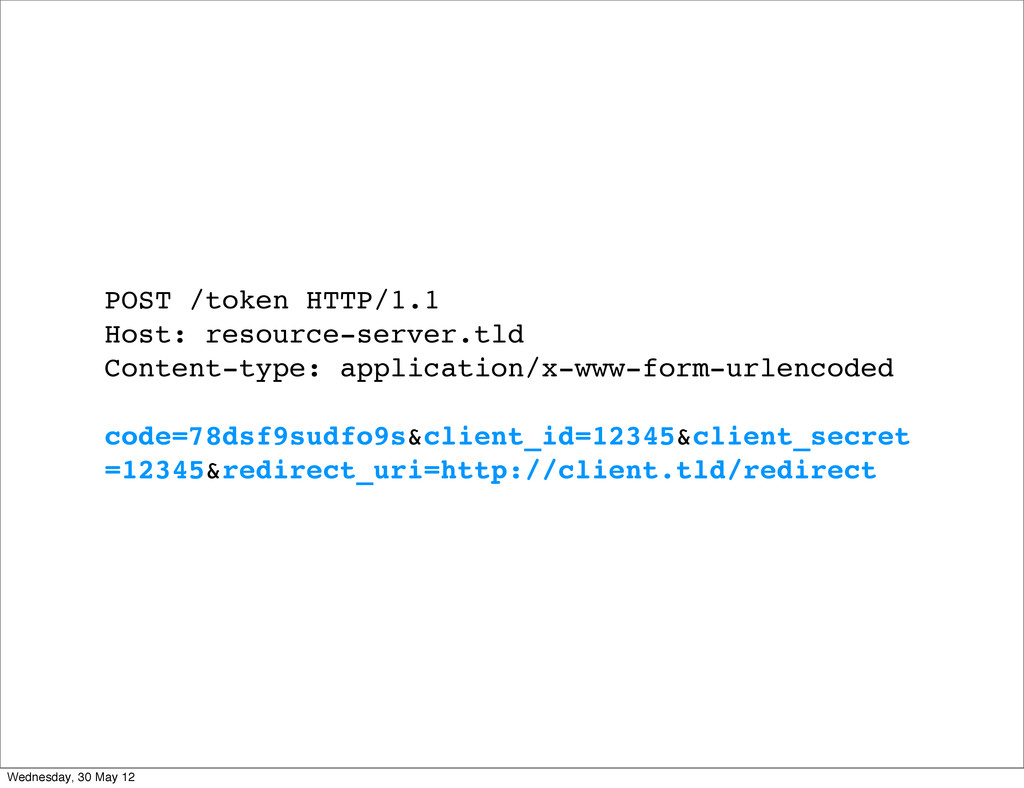
Client exchanges the authorisation code for an access token Wednesday,
30 May 12
POST /token HTTP/1.1 Host: resource-server.tld Content-type: application/x-www-form-urlencoded code=78dsf9sudfo9s&client_id=12345&client_secret =12345&redirect_uri=http://client.tld/redirect Wednesday,
30 May 12
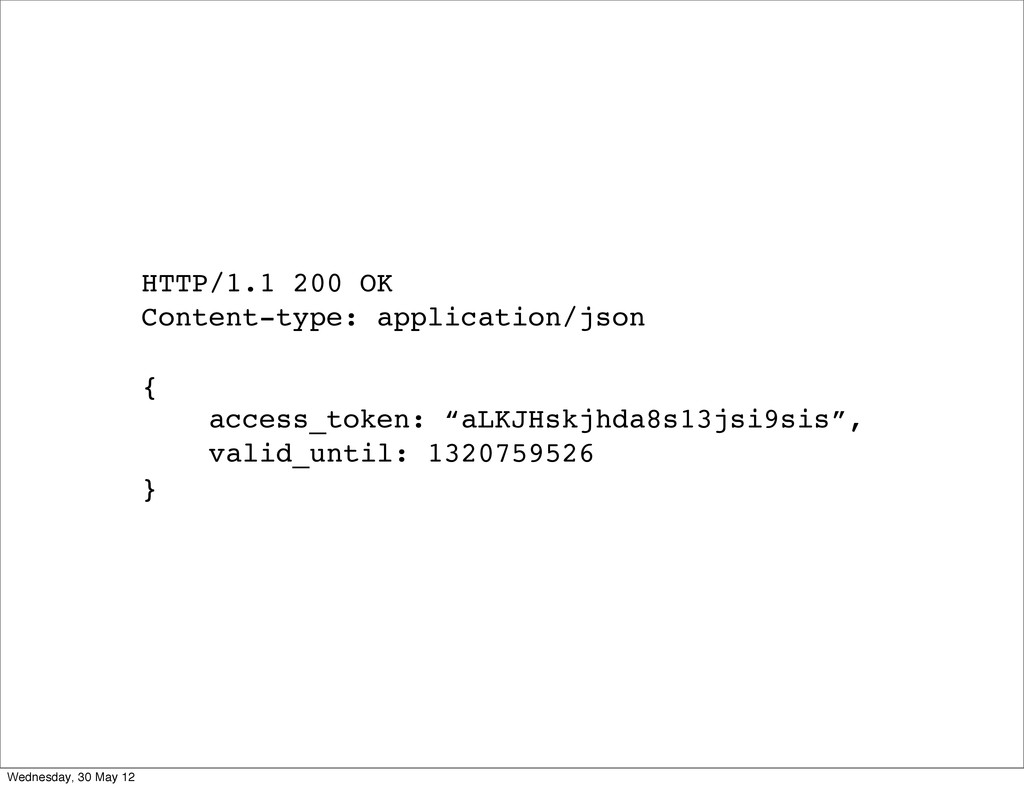
HTTP/1.1 200 OK Content-type: application/json { access_token: “aLKJHskjhda8s13jsi9sis”, valid_until: 1320759526
} Wednesday, 30 May 12
The access token can then be used as authorisation by
the client to access the specified resources for a specific length of time Wednesday, 30 May 12
Advantages Wednesday, 30 May 12
No password sharing <- Happy security conscious user Wednesday, 30
May 12
Developers just need to implement a redirect and a POST
request <- Happy developers Wednesday, 30 May 12
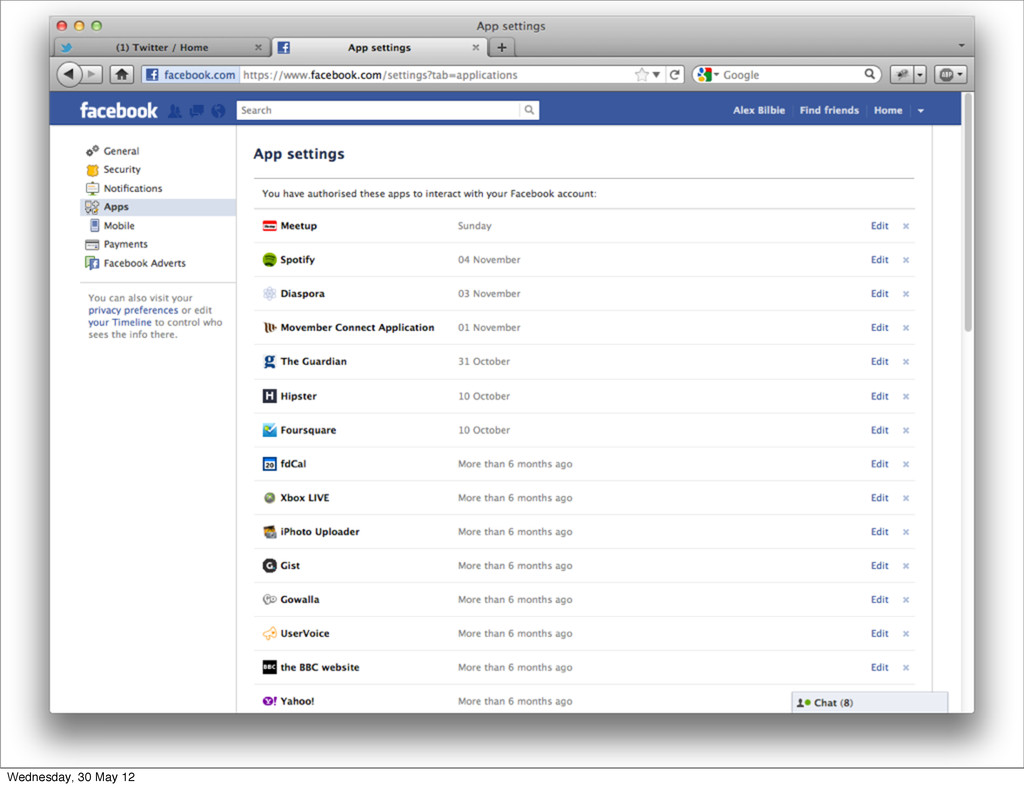
Users can revoke access tokens for specific clients Wednesday, 30
May 12
Wednesday, 30 May 12
Nefarious clients can have their credentials revoked and all associated
access tokens destroyed immediately Wednesday, 30 May 12
Wednesday, 30 May 12
Wednesday, 30 May 12
Currently version 1.0a lncn.eu/giy Wednesday, 30 May 12
Version 2.0 is almost finished lncn.eu/bkw Wednesday, 30 May 12
OAuth 2.0 •Simpler •Requires all communication over SSL •New flows
•Better UX Wednesday, 30 May 12
Who’s using OAuth? Wednesday, 30 May 12
Wednesday, 30 May 12
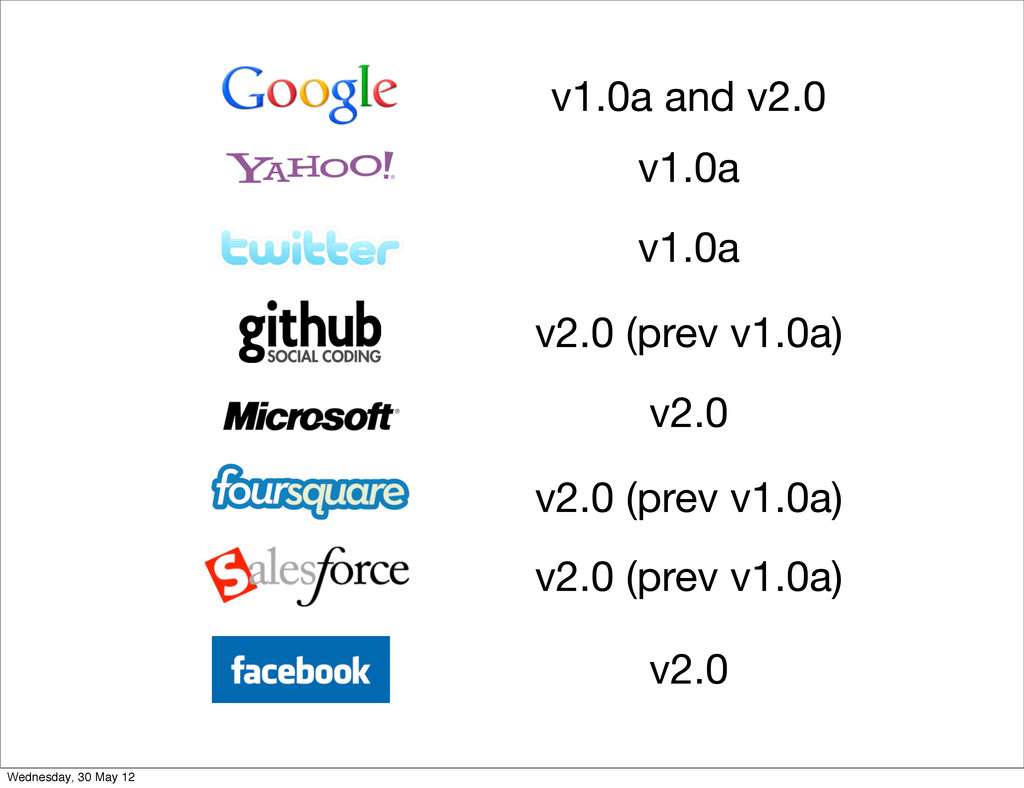
v1.0a and v2.0 v1.0a v1.0a v2.0 (prev v1.0a) v2.0 v2.0
(prev v1.0a) v2.0 (prev v1.0a) v2.0 Wednesday, 30 May 12
And in HE? Wednesday, 30 May 12
Wednesday, 30 May 12
Wednesday, 30 May 12
Wednesday, 30 May 12
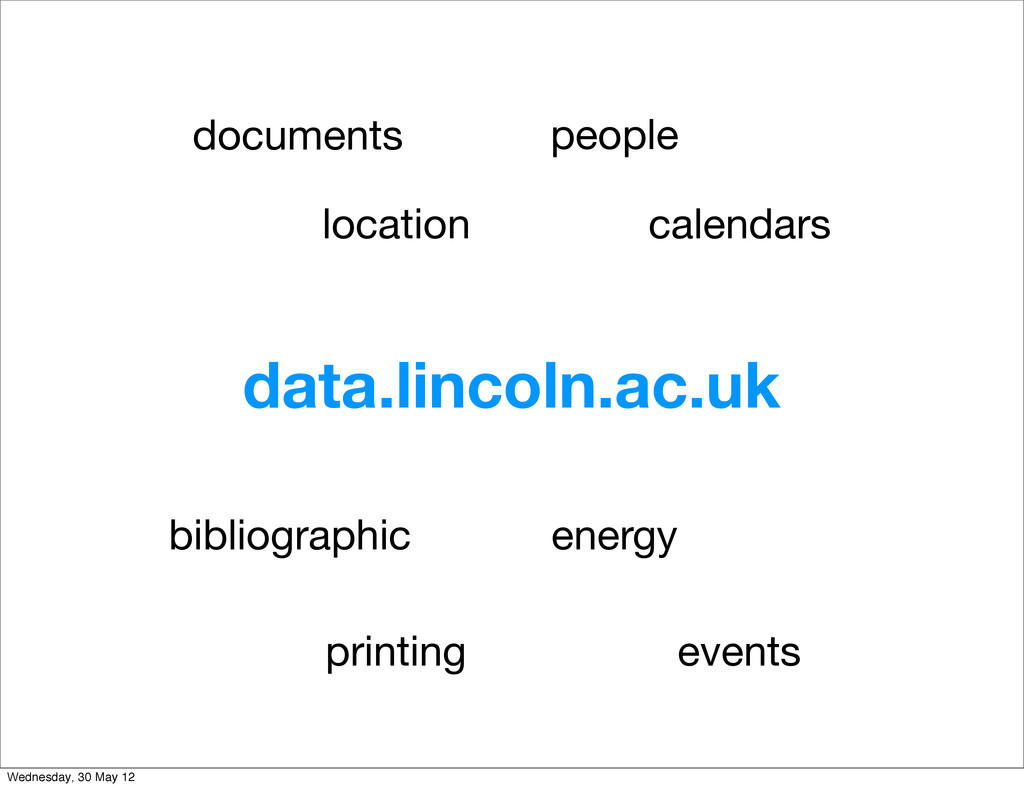
data.lincoln.ac.uk people energy location printing events calendars bibliographic documents Wednesday,
30 May 12
Internal and external authorisation Wednesday, 30 May 12
Single Sign-On Wednesday, 30 May 12
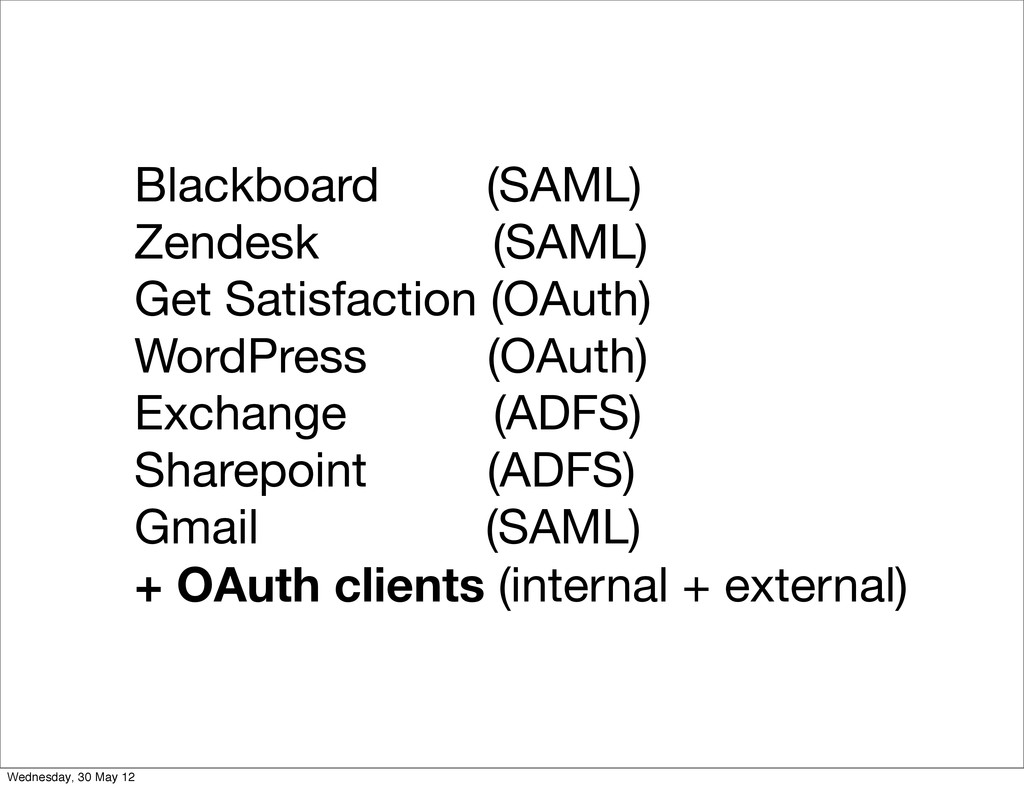
Blackboard (SAML) Zendesk (SAML) Get Satisfaction (OAuth) WordPress (OAuth) Exchange
(ADFS) Sharepoint (ADFS) Gmail (SAML) + OAuth clients (internal + external) Wednesday, 30 May 12
Open source 2.0 server lncn.eu/ar6 Wednesday, 30 May 12
Any questions? Wednesday, 30 May 12
Thank you @alexbilbie Wednesday, 30 May 12

 SiteGround - Reliable hosting with speed, security, and support you can count on.


 alexbilbie
 myohei
 pikosan0000
 snoozer05
 oracle4engineer
 katayamatg
 shisyu_gaku
 l1ghthouse
 kakehashi
 kinopeee
 okamototakuyasr2
 kinunori
 dugsong
 baasie
 maltzj
 jonoalderson
 rakko
 lauravandoore
 marktimemedia
 carmenintech
 zakiyama
 panda_program
 chriscoyier
 cromwellryan