Cryptosystems R.L. Rivest, A. Shamir, and L. Adleman – April 4, 1977 Public key, security and signatures Method Mathematical foundations Efficient implementation Security
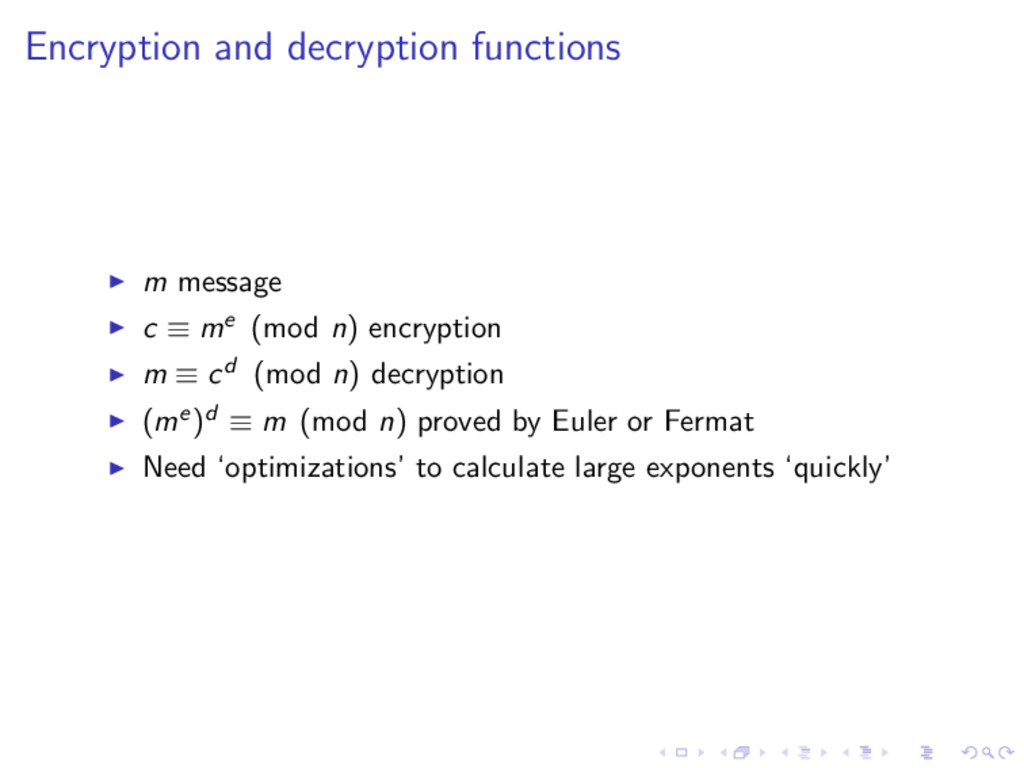
Theorem or Euler’s Theorem Large prime numbers are easy to find (and large composites are hard to decompose) Some optimizations . . . Much of this is number theory, which didn’t have practical uses before!
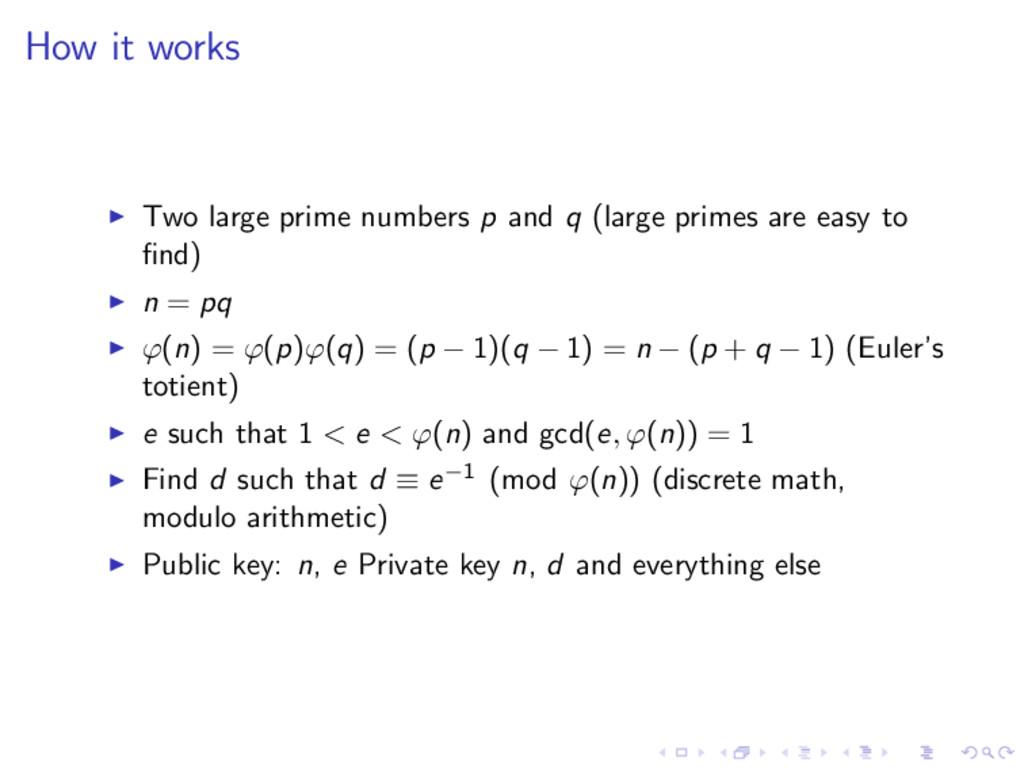
(large primes are easy to find) n = pq ϕ(n) = ϕ(p)ϕ(q) = (p − 1)(q − 1) = n − (p + q − 1) (Euler’s totient) e such that 1 < e < ϕ(n) and gcd(e, ϕ(n)) = 1 Find d such that d ≡ e−1 (mod ϕ(n)) (discrete math, modulo arithmetic) Public key: n, e Private key n, d and everything else
keep your private key private (obviously!) Anyone can encrypt a message with your public key, only you can decrypt it with your private key You can send out a message along with the message encoded with your private key. Anyone can decode the encoded message with your public key and verify it’s equal to the unencoded message
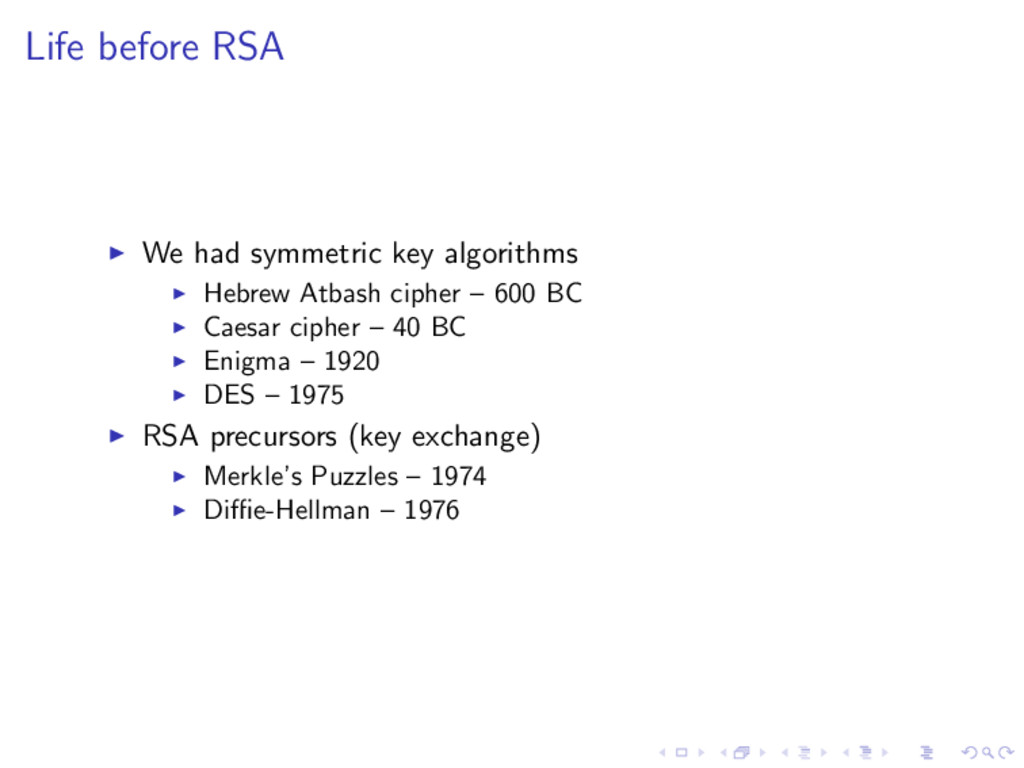
Signature didn’t even exist Symmetric is much faster than asymmetric, though! Hardy will be pissed: “No one has yet discovered any warlike purpose to be served by the theory of numbers or relativity, and it seems unlikely that anyone will do so for many years”
& CS2, Alan!) proves that asymmetric encryption is possible 1974 – Clifford Cocks, basically finds out the operations that work in Ellis’ paper and is equivalent to RSA (3 years before) 1976 – Malcolm Williamson invents Diffie-Helman (a few months before) RSA is just . . . intuitive? obvious? Everything fits together! 1Government Communications Headquarters 2Government Code and Cypher School


 xspa2012
 sshimizu2006
 tagtag
 trycycle
 tsoh
 konakalab
 expajp
 rmaruy
 gkazunii
 taka88
 hayashiyus884
 baggiponte
 nonsquared
 shpigford
 axbom
 davidcarrasco
 shlominoach
 baasie
 cassininazir
 paigeccino
 asonas
 tomoyanonymous
 inesmontani
 jdejongh