Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
Supply Chain Attack
Search
Sponsored
·
Your Podcast. Everywhere. Effortlessly.
Share. Educate. Inspire. Entertain. You do you. We'll handle the rest.
→
Andreas Mosti
May 03, 2021
90
0
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
Supply Chain Attack
Talk I gave for Bekk Trondheim principles and practices group for security, spring 2021.
Andreas Mosti
May 03, 2021
More Decks by Andreas Mosti
See All by Andreas Mosti
Deterministic Builds and where to find them
andmos
0
93
Correct Maps Are Useless: A guide to mental models
andmos
0
220
LEGO I Praksis
andmos
0
110
Supply Chain Attacks: Når den digitale forsyningslinja blir angrepsvektor
andmos
0
55
IoIT: Internet of Insecure Things
andmos
0
150
Containers'n stuff
andmos
0
78
IoT - Bevisstgjøring
andmos
0
72
GitOps in a nutshell
andmos
0
240
OpenFaaS: Serverless platform with no strings attached?
andmos
0
340
Featured
See All Featured
Neural Spatial Audio Processing for Sound Field Analysis and Control
skoyamalab
0
540
Designing Powerful Visuals for Engaging Learning
tmiket
1
590
Jamie Indigo - Trashchat’s Guide to Black Boxes: Technical SEO Tactics for LLMs
techseoconnect
PRO
0
690
Fantastic passwords and where to find them - at NoRuKo
philnash
52
4k
Sharpening the Axe: The Primacy of Toolmaking
bcantrill
46
3k
Google's AI Overviews - The New Search
badams
0
1.6k
Build your cross-platform service in a week with App Engine
jlugia
234
19k
How to build an LLM SEO readiness audit: a practical framework
nmsamuel
2
930
The untapped power of vector embeddings
frankvandijk
2
1.9k
What does AI have to do with Human Rights?
axbom
PRO
1
2.4k
Scaling GitHub
holman
464
140k
Taking LLMs out of the black box: A practical guide to human-in-the-loop distillation
inesmontani
PRO
3
2.4k
Transcript
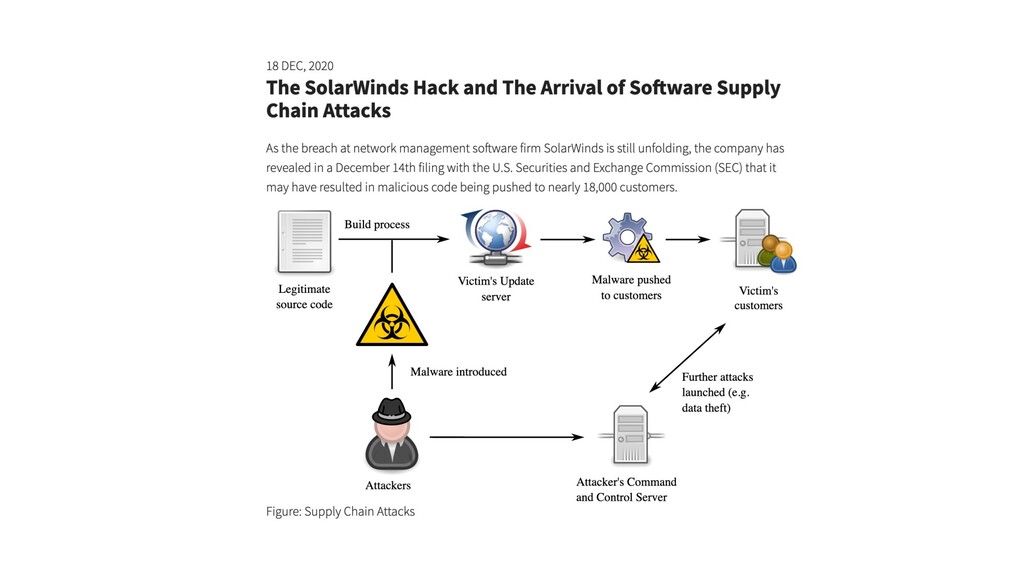
Supply Chain Attack
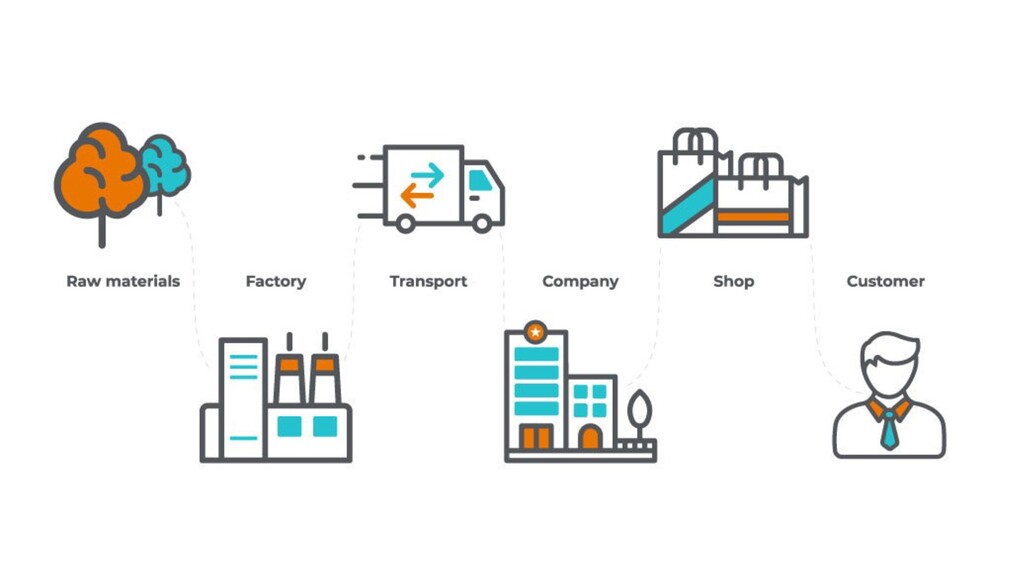
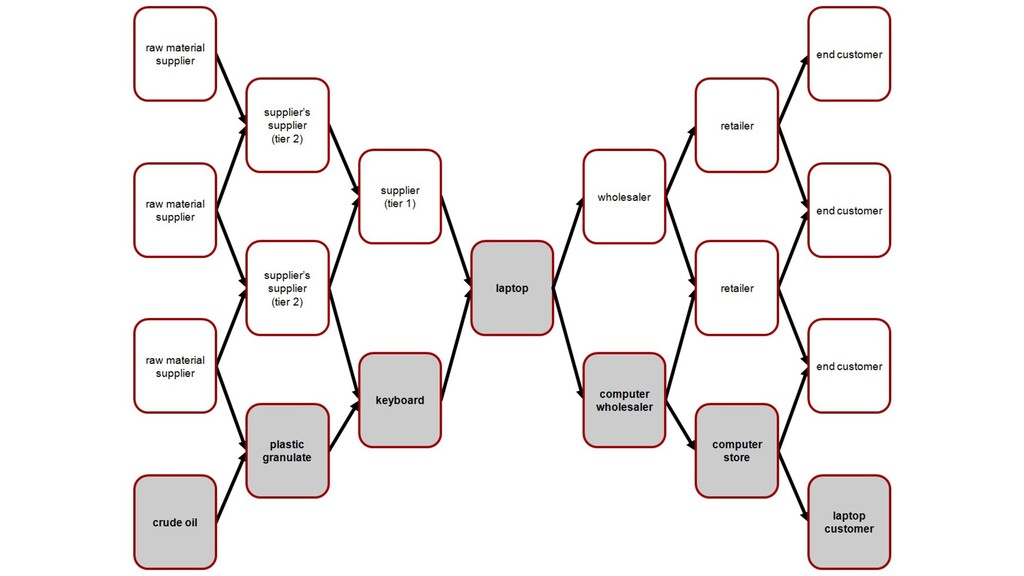
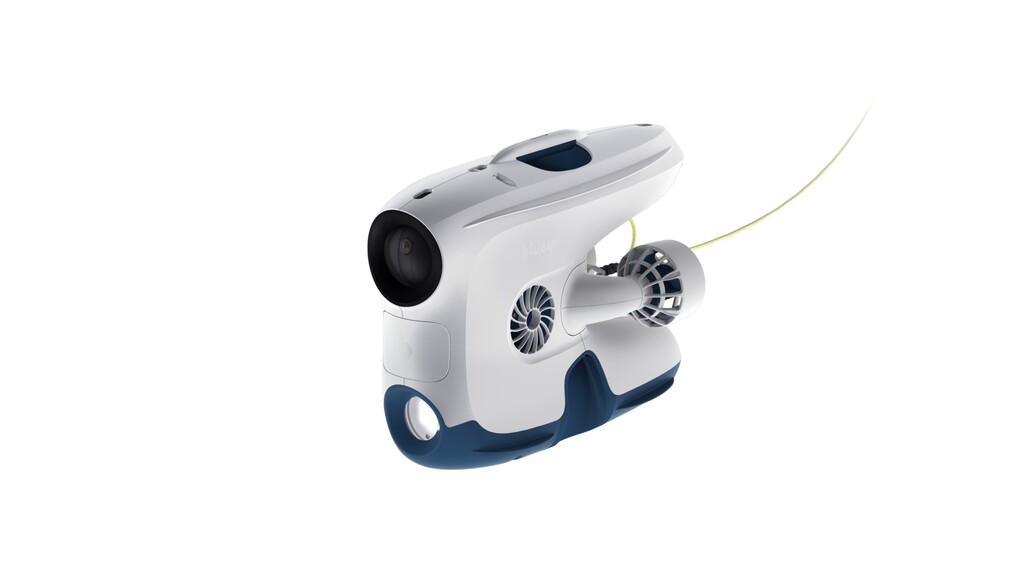
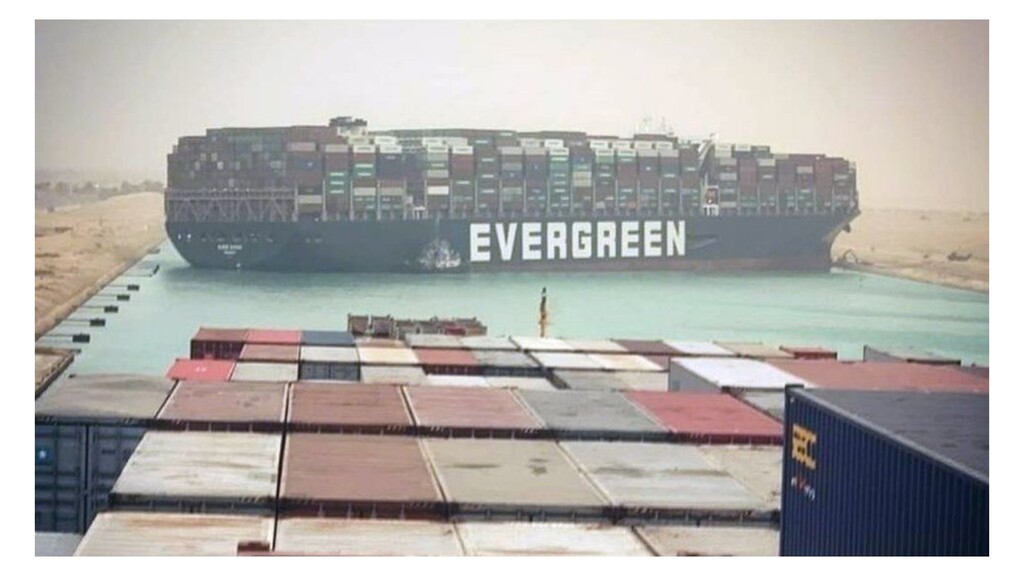
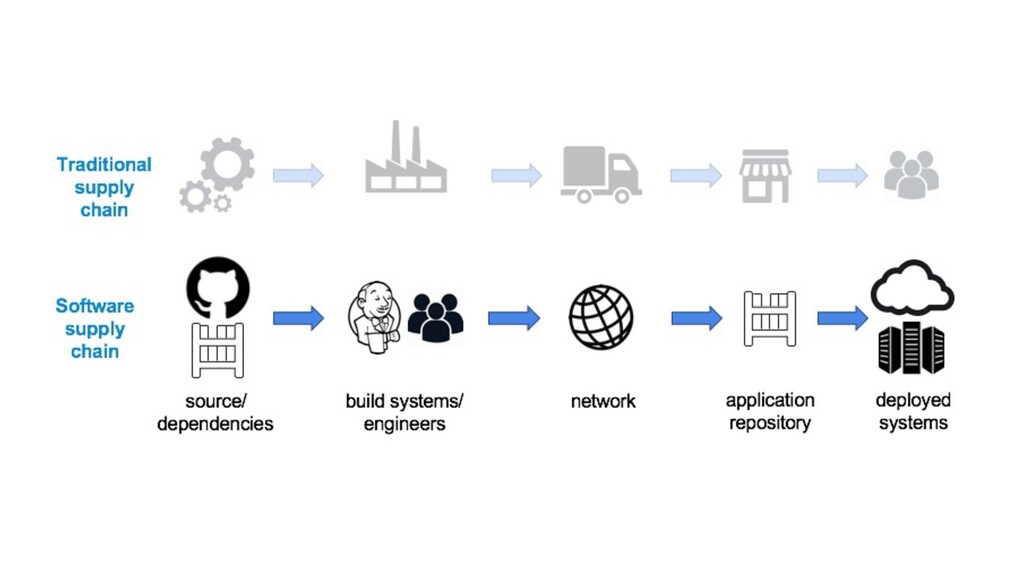
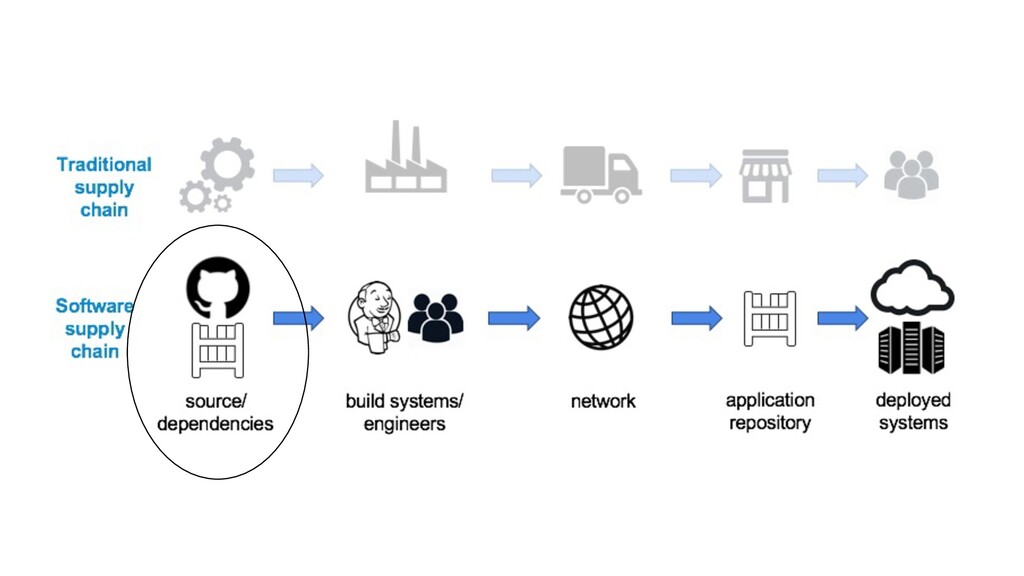
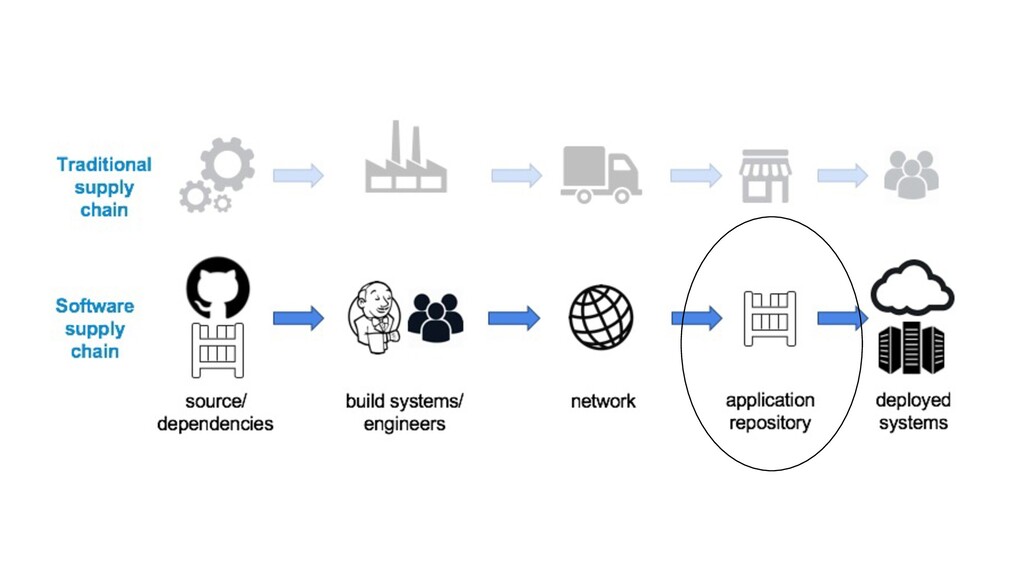
What’s a supply chain?
None
None
None
Ca. 1000 parts, most of them “passive”…
But 35 critical components, single-source dependencies
None
None
None
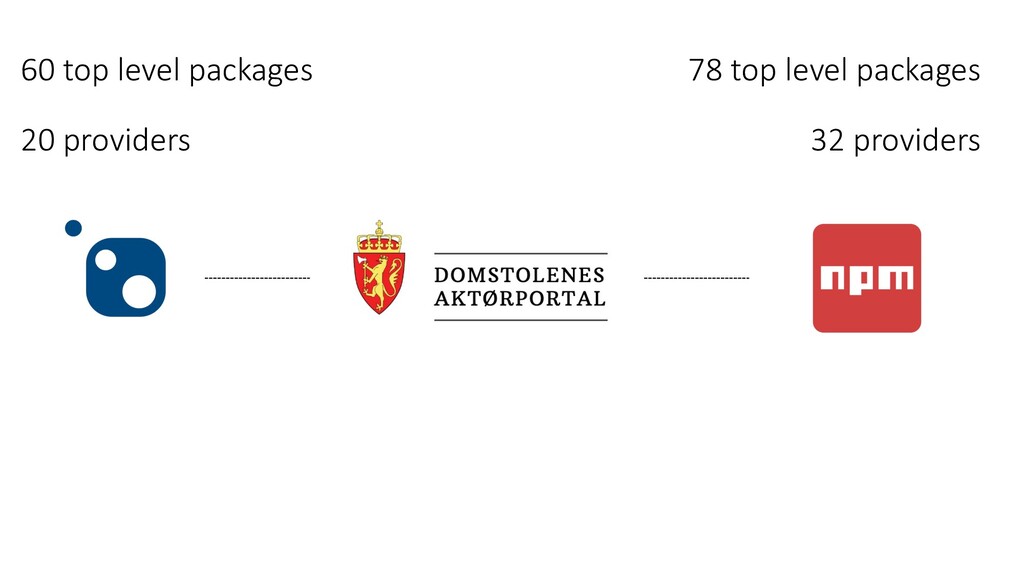
60 top level packages 20 providers 78 top level packages
32 providers
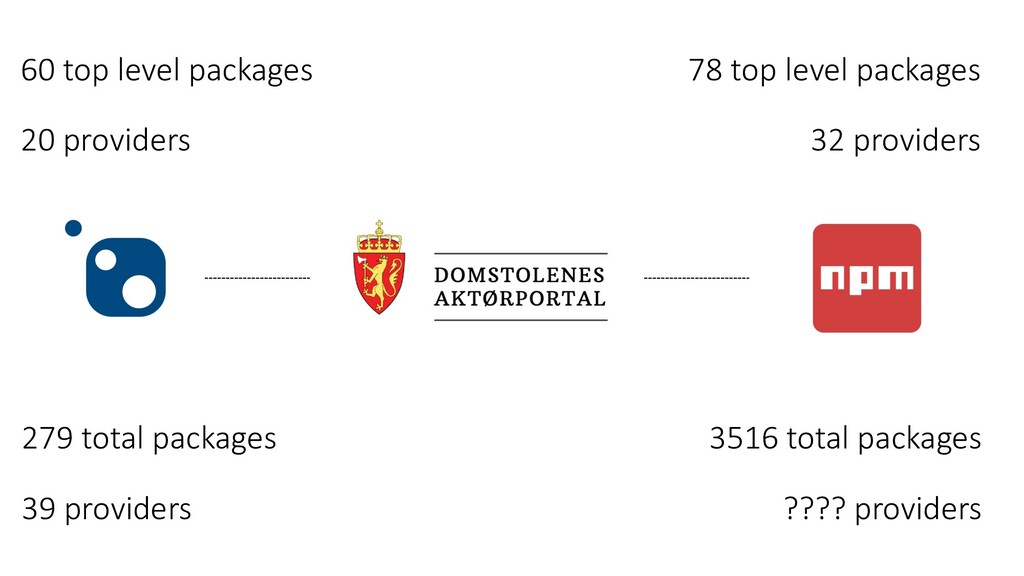
60 top level packages 20 providers 78 top level packages
32 providers 279 total packages 39 providers 3516 total packages ???? providers
None
None
None
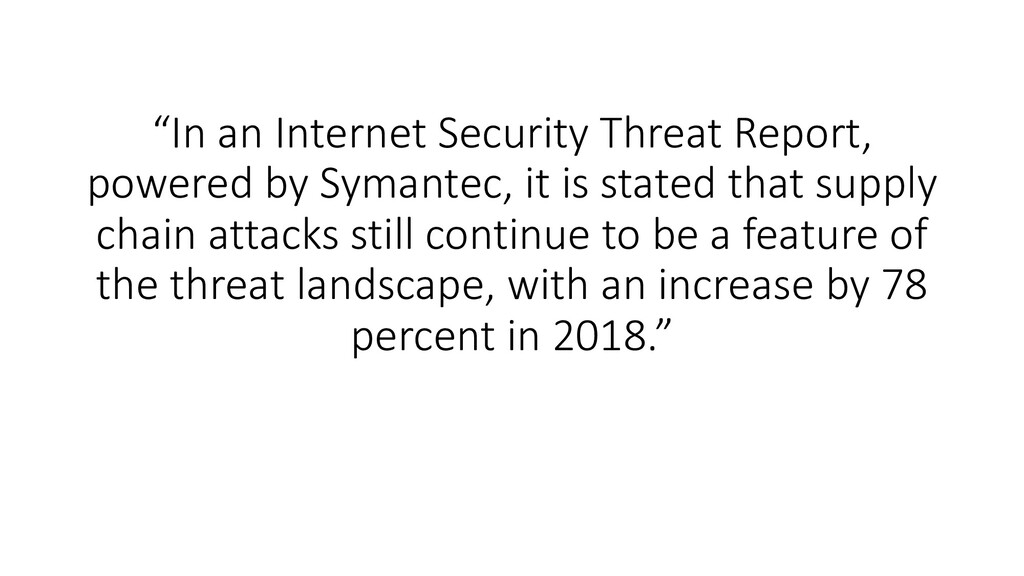
“In an Internet Security Threat Report, powered by Symantec, it
is stated that supply chain attacks still continue to be a feature of the threat landscape, with an increase by 78 percent in 2018.”
None
None
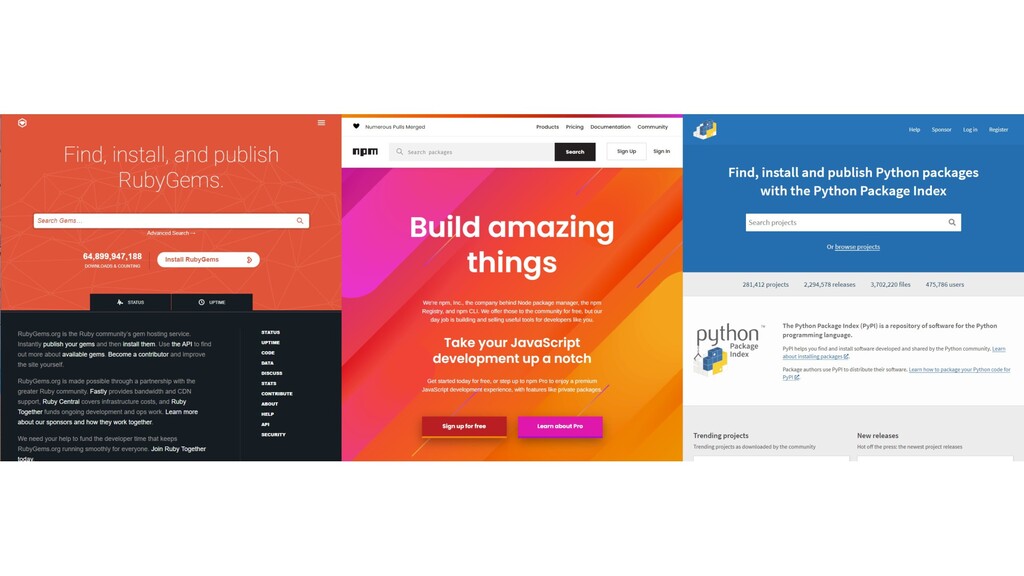
We go to the markedplace
None
“None of the package hosting services can ever guarantee that
all the code its users upload is malware-free”
None
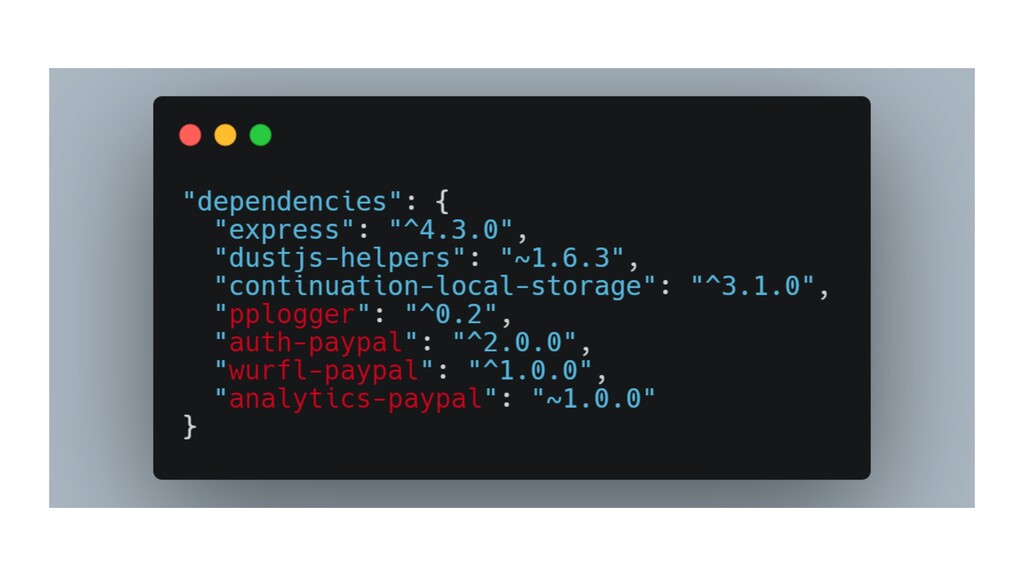
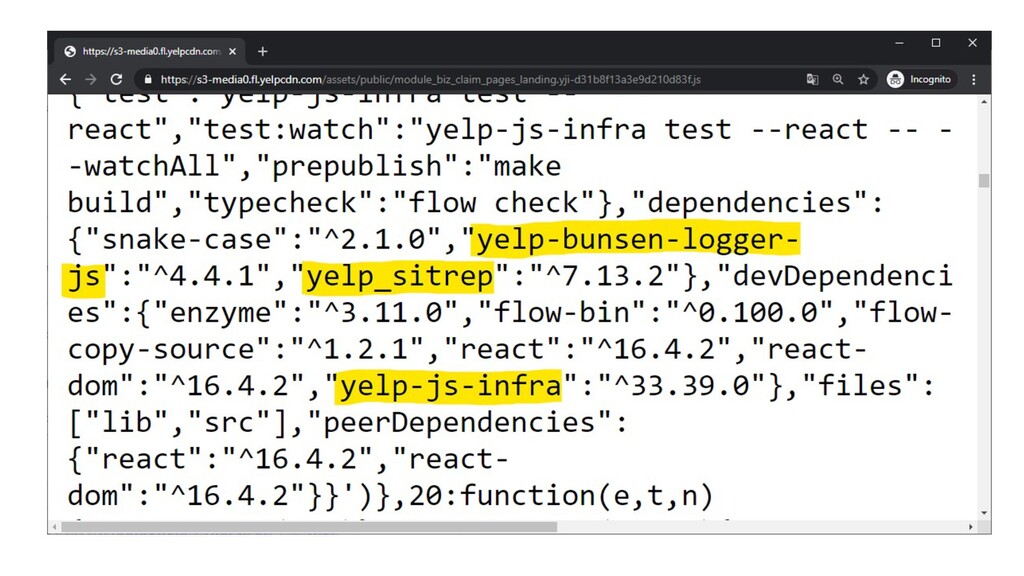
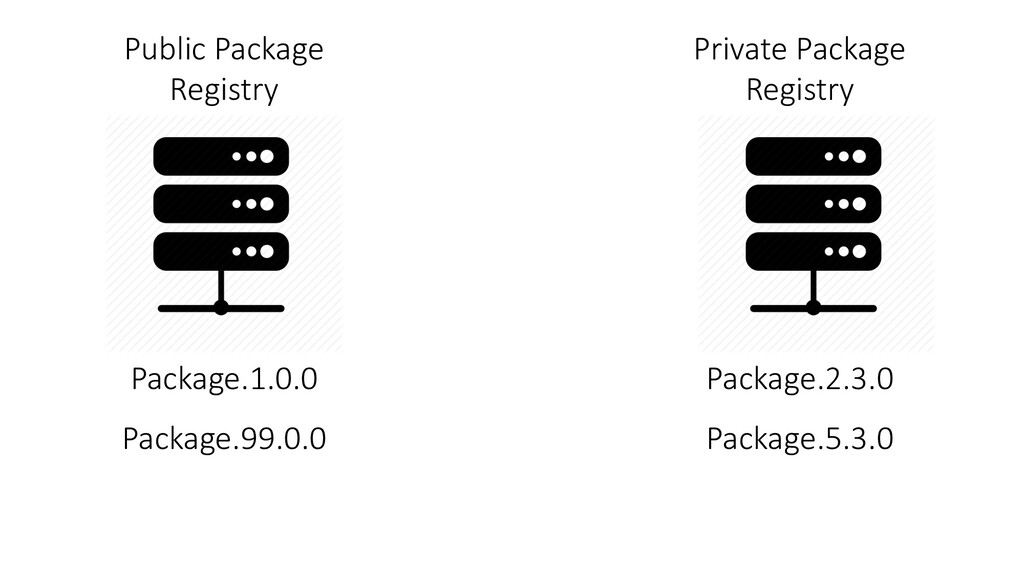
Dependency Confusion
None
None
None
None
Public Package Registry Private Package Registry Package.1.0.0 Package.2.3.0 Package.99.0.0 Package.5.3.0
None
None
None
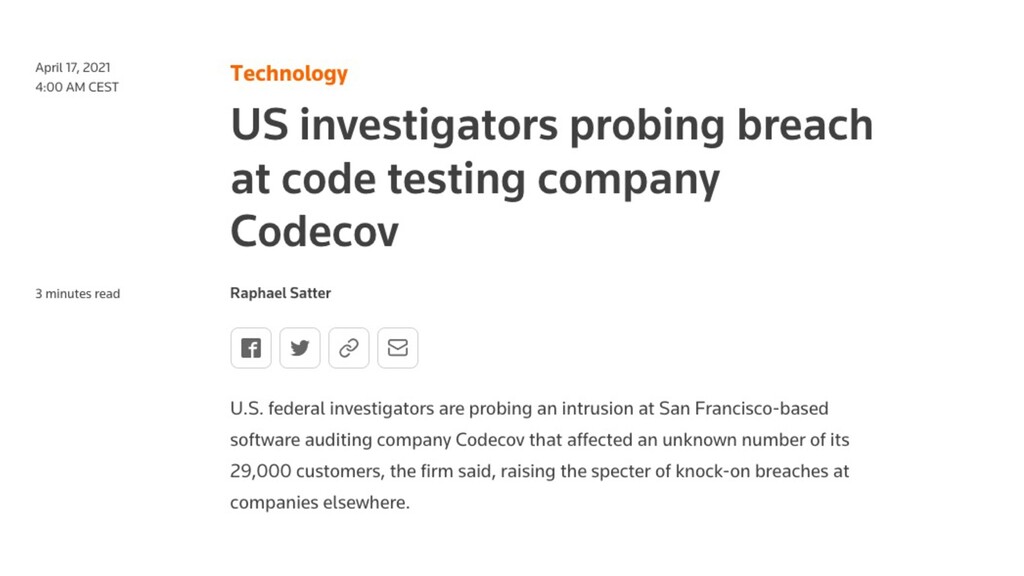
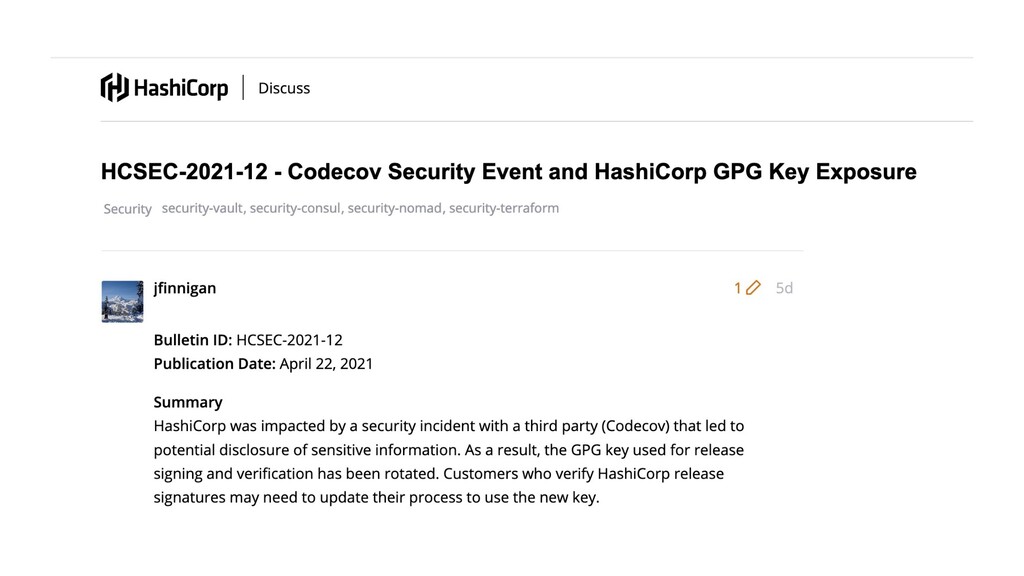
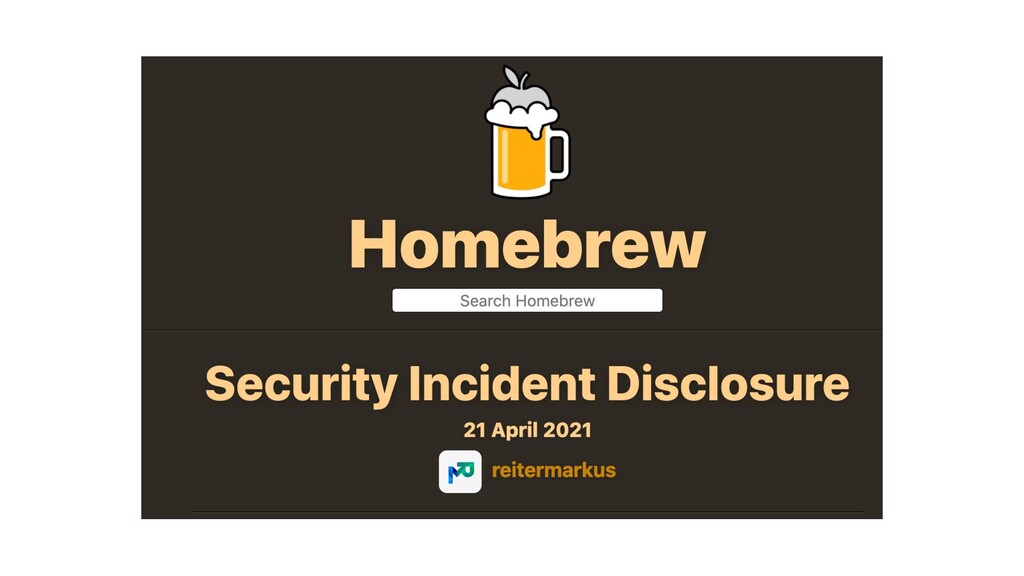
Service breaches
None
None
None
None
None
None
None
None
None
None
None
None
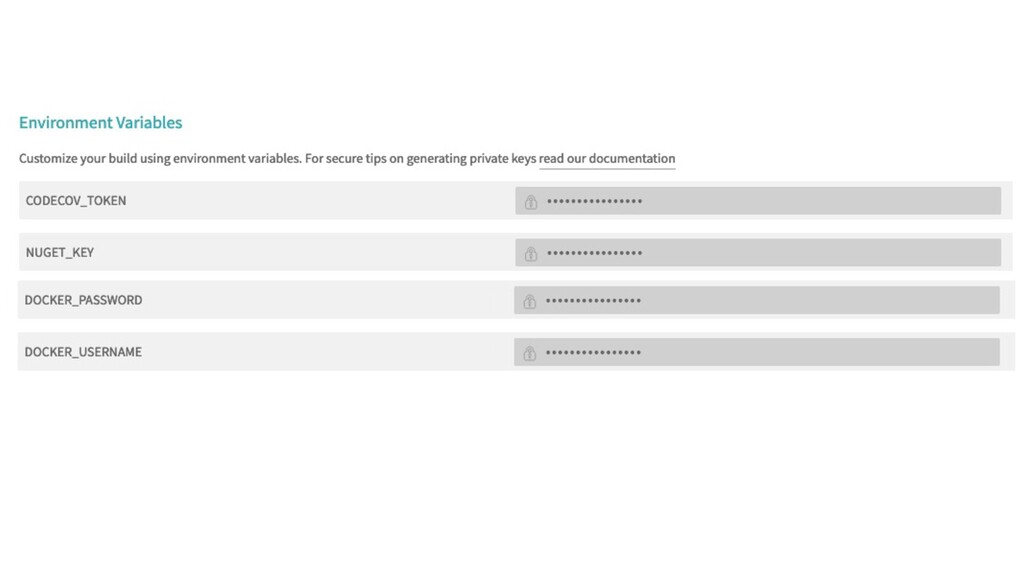
Worth mentioning: • Stolen signature key • Leaked API keys/passwords
• ????
How do we protect ourselves?


 andmos
 skoyamalab
 tmiket
 techseoconnect
 philnash
 bcantrill
 badams
 jlugia
 nmsamuel
 frankvandijk
 axbom
 holman
 inesmontani