Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
プレイブックの検証環境をdocker-composeで作った話/playbook tes...
Search
あんでぃー
February 12, 2020
Technology
930
5
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
プレイブックの検証環境をdocker-composeで作った話/playbook test environment by docker-compose
あんでぃー
February 12, 2020
Transcript
33 slides
ϓϨΠϒοΫͷݕূڥΛ docker-composeͰ࡞ͬͨ ͋ΜͰ͌ʔ @answer_d
ࣗݾհ • SIer • Πϯϑϥ͞Μ αʔόߏஙϚϯ • ʮAnsible͍ͬͯ͜͏Ͷʔʯͳ৬͚ͩͲීٴඍົ
͋ΔͷͰ͖͝ͱ
͋ΜͰ͌ʔ͘ΜAnsible Ͱ͖ΔΜͩΑͶʁ ͪΐͬͱͬͯΑʂ ͔͜͠·Γ
։ൃڥʁ ͳ͍ΑɺඞཁͩͬͨΒԿ͔ߟ͑ͯ
ΦϯϓϨҊ݅͋Δ͋Δ(͔ʁ)
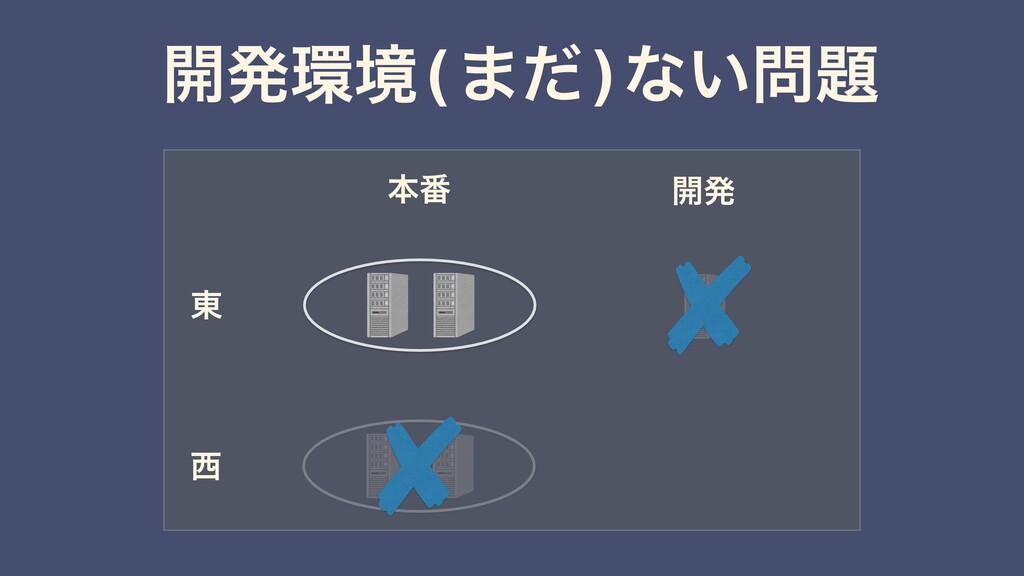
ຊ൪ ։ൃ ౦ ։ൃڥ(·ͩ)ͳ͍
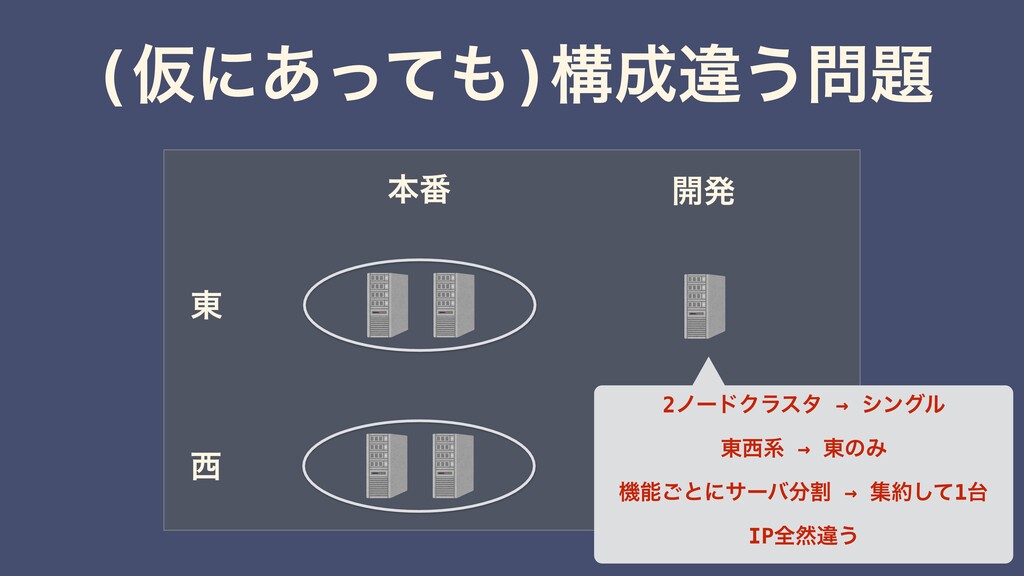
ຊ൪ ։ൃ ౦ (Ծʹ͋ͬͯ)ߏҧ͏ 2ϊʔυΫϥελ → γϯάϧ ౦ܥ →
౦ͷΈ ػೳ͝ͱʹαʔόׂ → ूͯ͠1 IPશવҧ͏
ϓϨΠϒοΫͷ࣭֬อ Ͳ͏͠Α͏ɾɾɾ
Ͱ͖Ε ຊ൪Ͱྲྀ͢ϓϨΠϒοΫΛ ͦͷ··ྲྀͯ͠ಈ࡞֬ೝ͍ͨ͠
DockerͰͰ͖ΔΜ͡ΌͶʁ
Γ·ͨ͠
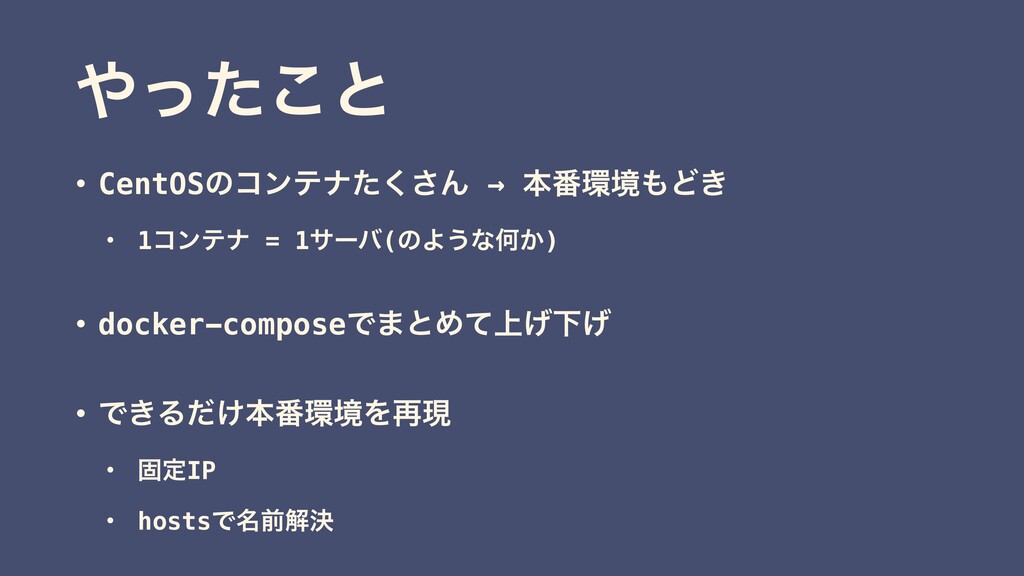
ͬͨ͜ͱ • CentOSͷίϯςφͨ͘͞Μ → ຊ൪ڥͲ͖ ɾ 1ίϯςφ = 1αʔό(ͷΑ͏ͳԿ͔) •
docker-composeͰ·ͱΊ্ͯ͛Լ͛ • Ͱ͖Δ͚ͩຊ൪ڥΛ࠶ݱ ɾ ݻఆIP ɾ hostsͰ໊લղܾ
͍ํΠϝʔδ
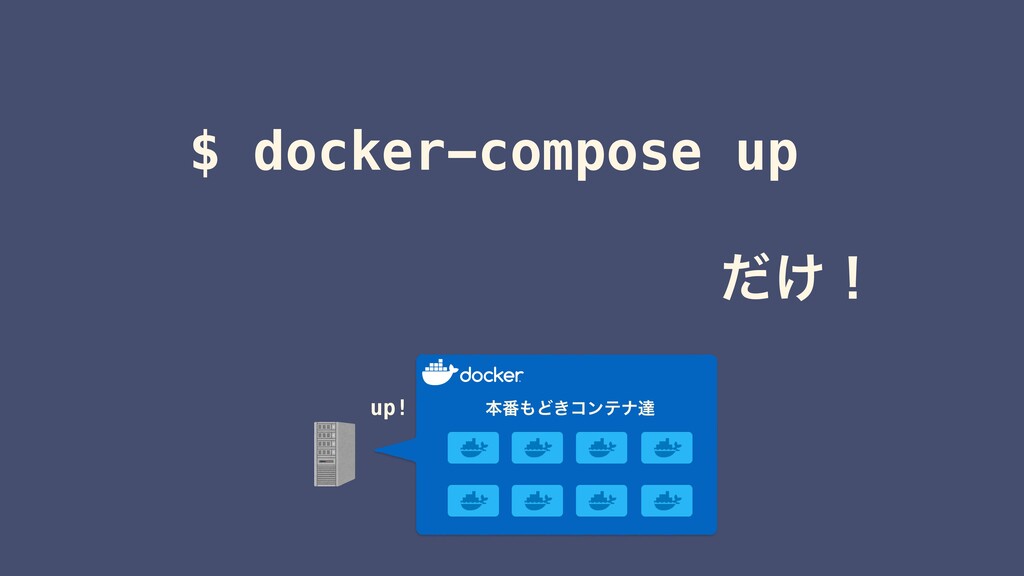
$ docker-compose up up! ͚ͩʂ ຊ൪Ͳ͖ίϯςφୡ
࡞ͬͨͭ
Dockerfile
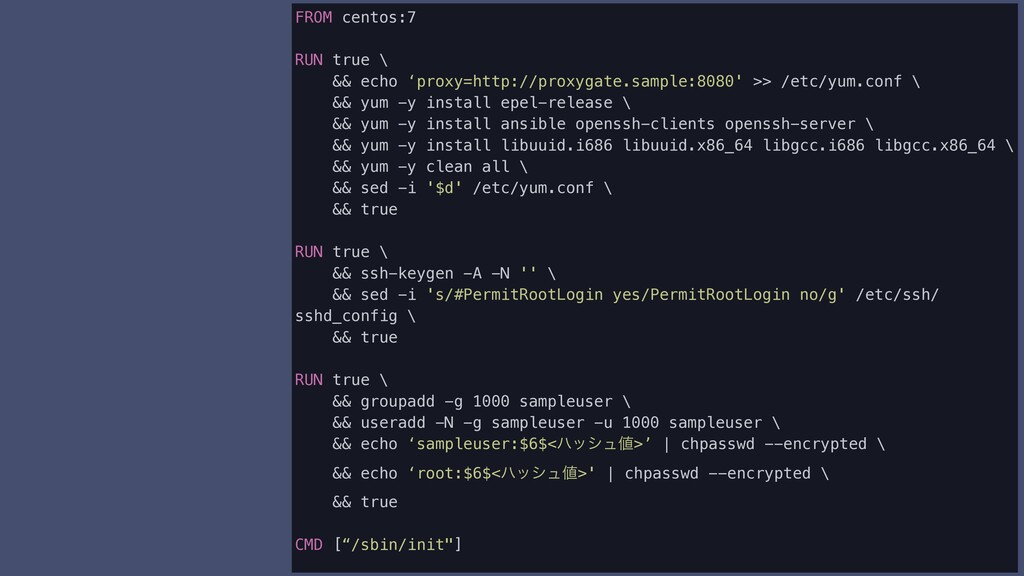
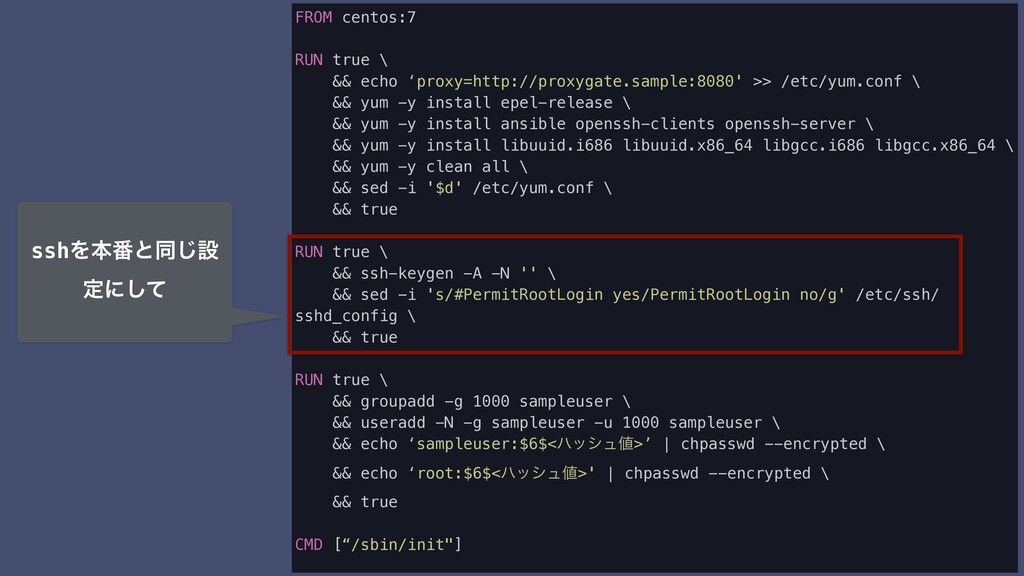
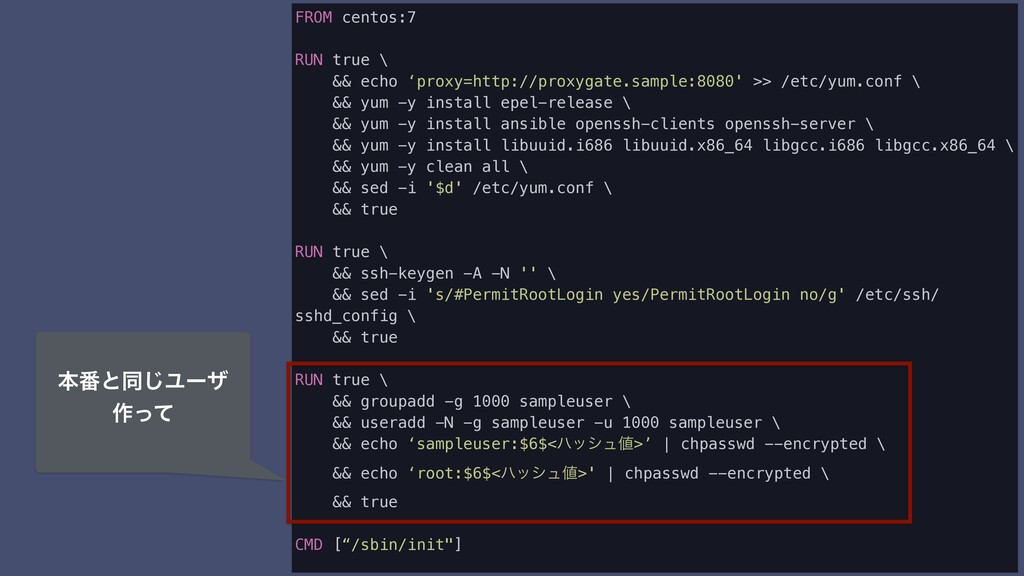
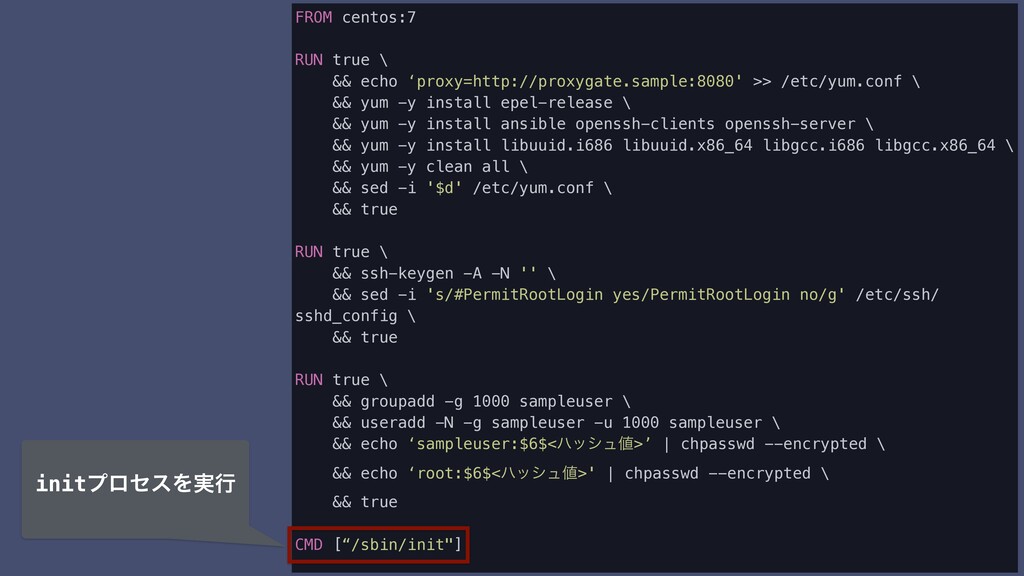
FROM centos:7 RUN true \ && echo ‘proxy=http://proxygate.sample:8080' >> /etc/yum.conf
\ && yum -y install epel-release \ && yum -y install ansible openssh-clients openssh-server \ && yum -y install libuuid.i686 libuuid.x86_64 libgcc.i686 libgcc.x86_64 \ && yum -y clean all \ && sed -i '$d' /etc/yum.conf \ && true RUN true \ && ssh-keygen -A -N '' \ && sed -i 's/#PermitRootLogin yes/PermitRootLogin no/g' /etc/ssh/ sshd_config \ && true RUN true \ && groupadd -g 1000 sampleuser \ && useradd -N -g sampleuser -u 1000 sampleuser \ && echo ‘sampleuser:$6$<ϋογϡ>’ | chpasswd --encrypted \ && echo ‘root:$6$<ϋογϡ>' | chpasswd --encrypted \ && true CMD [“/sbin/init"]
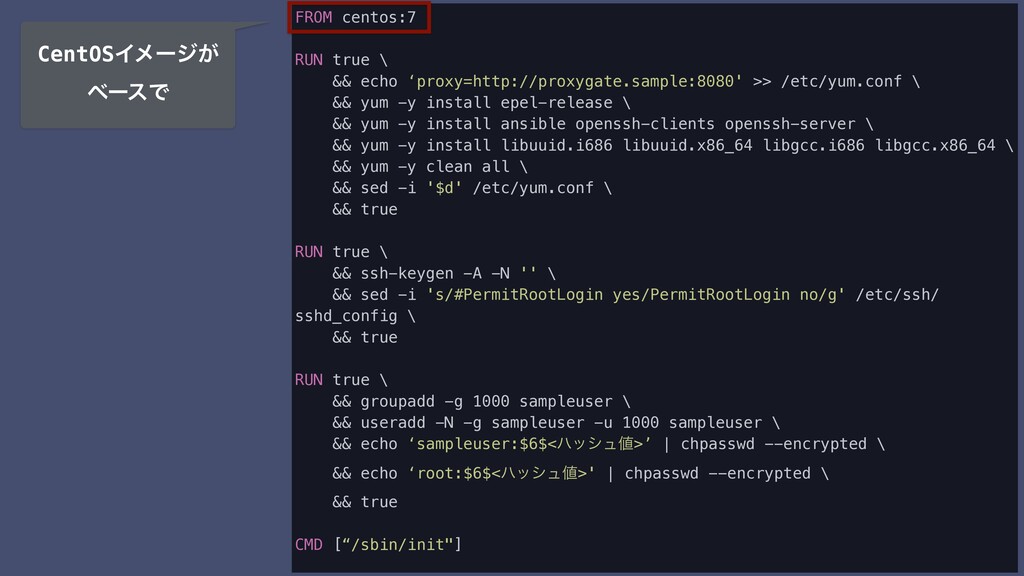
FROM centos:7 RUN true \ && echo ‘proxy=http://proxygate.sample:8080' >> /etc/yum.conf
\ && yum -y install epel-release \ && yum -y install ansible openssh-clients openssh-server \ && yum -y install libuuid.i686 libuuid.x86_64 libgcc.i686 libgcc.x86_64 \ && yum -y clean all \ && sed -i '$d' /etc/yum.conf \ && true RUN true \ && ssh-keygen -A -N '' \ && sed -i 's/#PermitRootLogin yes/PermitRootLogin no/g' /etc/ssh/ sshd_config \ && true RUN true \ && groupadd -g 1000 sampleuser \ && useradd -N -g sampleuser -u 1000 sampleuser \ && echo ‘sampleuser:$6$<ϋογϡ>’ | chpasswd --encrypted \ && echo ‘root:$6$<ϋογϡ>' | chpasswd --encrypted \ && true CMD [“/sbin/init"] CentOSΠϝʔδ͕ ϕʔεͰ
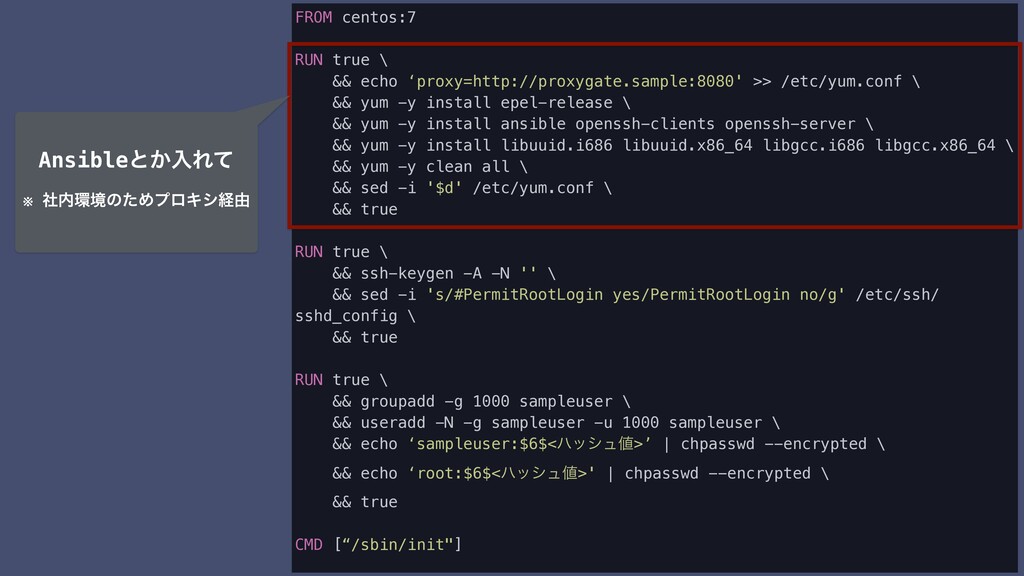
FROM centos:7 RUN true \ && echo ‘proxy=http://proxygate.sample:8080' >> /etc/yum.conf
\ && yum -y install epel-release \ && yum -y install ansible openssh-clients openssh-server \ && yum -y install libuuid.i686 libuuid.x86_64 libgcc.i686 libgcc.x86_64 \ && yum -y clean all \ && sed -i '$d' /etc/yum.conf \ && true RUN true \ && ssh-keygen -A -N '' \ && sed -i 's/#PermitRootLogin yes/PermitRootLogin no/g' /etc/ssh/ sshd_config \ && true RUN true \ && groupadd -g 1000 sampleuser \ && useradd -N -g sampleuser -u 1000 sampleuser \ && echo ‘sampleuser:$6$<ϋογϡ>’ | chpasswd --encrypted \ && echo ‘root:$6$<ϋογϡ>' | chpasswd --encrypted \ && true CMD [“/sbin/init"] Ansibleͱ͔ೖΕͯ ※ ࣾڥͷͨΊϓϩΩγܦ༝
FROM centos:7 RUN true \ && echo ‘proxy=http://proxygate.sample:8080' >> /etc/yum.conf
\ && yum -y install epel-release \ && yum -y install ansible openssh-clients openssh-server \ && yum -y install libuuid.i686 libuuid.x86_64 libgcc.i686 libgcc.x86_64 \ && yum -y clean all \ && sed -i '$d' /etc/yum.conf \ && true RUN true \ && ssh-keygen -A -N '' \ && sed -i 's/#PermitRootLogin yes/PermitRootLogin no/g' /etc/ssh/ sshd_config \ && true RUN true \ && groupadd -g 1000 sampleuser \ && useradd -N -g sampleuser -u 1000 sampleuser \ && echo ‘sampleuser:$6$<ϋογϡ>’ | chpasswd --encrypted \ && echo ‘root:$6$<ϋογϡ>' | chpasswd --encrypted \ && true CMD [“/sbin/init"] sshΛຊ൪ͱಉ͡ઃ ఆʹͯ͠
FROM centos:7 RUN true \ && echo ‘proxy=http://proxygate.sample:8080' >> /etc/yum.conf
\ && yum -y install epel-release \ && yum -y install ansible openssh-clients openssh-server \ && yum -y install libuuid.i686 libuuid.x86_64 libgcc.i686 libgcc.x86_64 \ && yum -y clean all \ && sed -i '$d' /etc/yum.conf \ && true RUN true \ && ssh-keygen -A -N '' \ && sed -i 's/#PermitRootLogin yes/PermitRootLogin no/g' /etc/ssh/ sshd_config \ && true RUN true \ && groupadd -g 1000 sampleuser \ && useradd -N -g sampleuser -u 1000 sampleuser \ && echo ‘sampleuser:$6$<ϋογϡ>’ | chpasswd --encrypted \ && echo ‘root:$6$<ϋογϡ>' | chpasswd --encrypted \ && true CMD [“/sbin/init"] ຊ൪ͱಉ͡Ϣʔβ ࡞ͬͯ
FROM centos:7 RUN true \ && echo ‘proxy=http://proxygate.sample:8080' >> /etc/yum.conf
\ && yum -y install epel-release \ && yum -y install ansible openssh-clients openssh-server \ && yum -y install libuuid.i686 libuuid.x86_64 libgcc.i686 libgcc.x86_64 \ && yum -y clean all \ && sed -i '$d' /etc/yum.conf \ && true RUN true \ && ssh-keygen -A -N '' \ && sed -i 's/#PermitRootLogin yes/PermitRootLogin no/g' /etc/ssh/ sshd_config \ && true RUN true \ && groupadd -g 1000 sampleuser \ && useradd -N -g sampleuser -u 1000 sampleuser \ && echo ‘sampleuser:$6$<ϋογϡ>’ | chpasswd --encrypted \ && echo ‘root:$6$<ϋογϡ>' | chpasswd --encrypted \ && true CMD [“/sbin/init"] initϓϩηεΛ࣮ߦ
docker-compose.yml
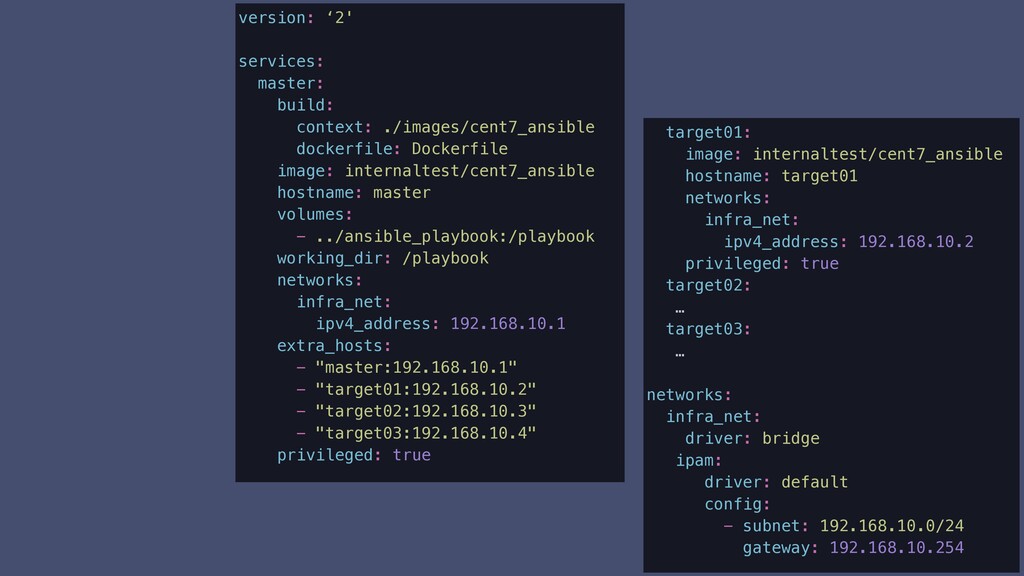
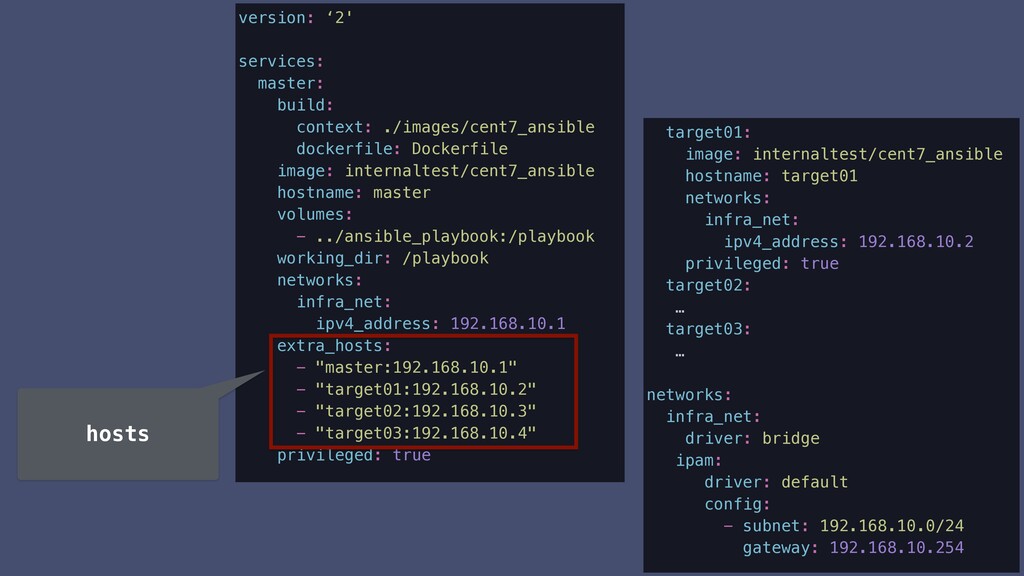
version: ‘2' services: master: build: context: ./images/cent7_ansible dockerfile: Dockerfile image:
internaltest/cent7_ansible hostname: master volumes: - ../ansible_playbook:/playbook working_dir: /playbook networks: infra_net: ipv4_address: 192.168.10.1 extra_hosts: - "master:192.168.10.1" - "target01:192.168.10.2" - "target02:192.168.10.3" - "target03:192.168.10.4" privileged: true target01: image: internaltest/cent7_ansible hostname: target01 networks: infra_net: ipv4_address: 192.168.10.2 privileged: true target02: … target03: … networks: infra_net: driver: bridge ipam: driver: default config: - subnet: 192.168.10.0/24 gateway: 192.168.10.254
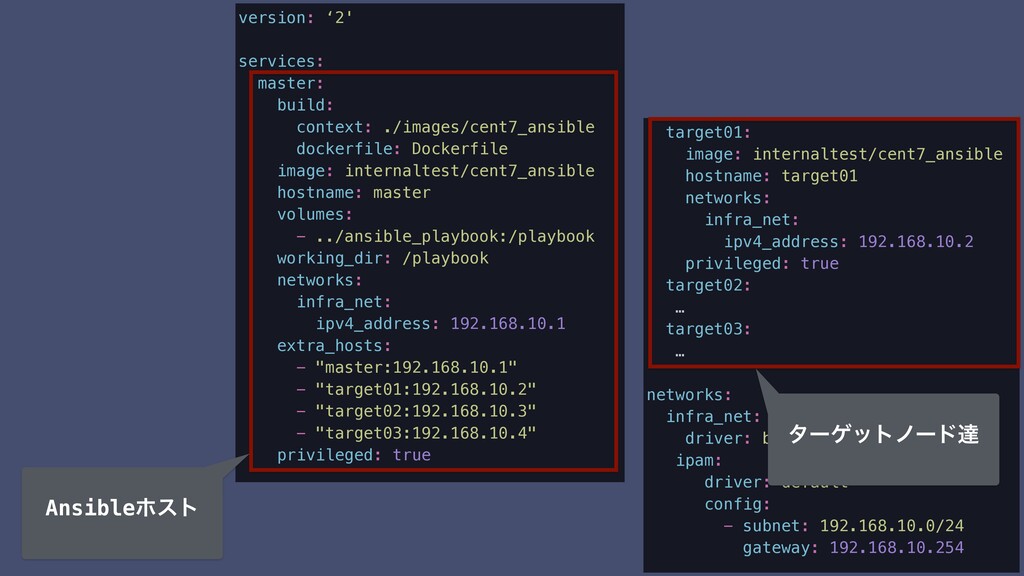
target01: image: internaltest/cent7_ansible hostname: target01 networks: infra_net: ipv4_address: 192.168.10.2 privileged:
true target02: … target03: … networks: infra_net: driver: bridge ipam: driver: default config: - subnet: 192.168.10.0/24 gateway: 192.168.10.254 version: ‘2' services: master: build: context: ./images/cent7_ansible dockerfile: Dockerfile image: internaltest/cent7_ansible hostname: master volumes: - ../ansible_playbook:/playbook working_dir: /playbook networks: infra_net: ipv4_address: 192.168.10.1 extra_hosts: - "master:192.168.10.1" - "target01:192.168.10.2" - "target02:192.168.10.3" - "target03:192.168.10.4" privileged: true Ansibleϗετ λʔήοτϊʔυୡ
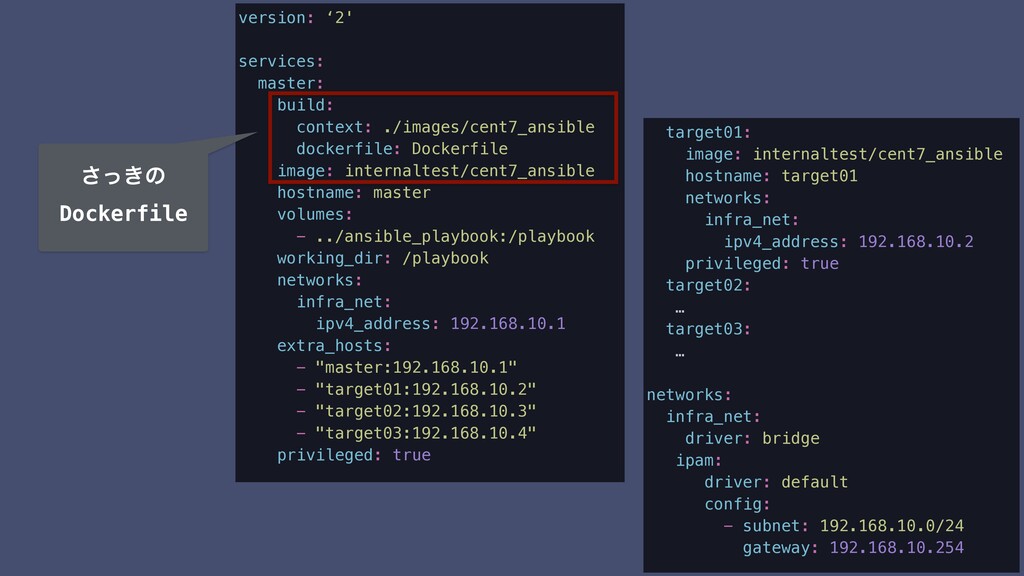
version: ‘2' services: master: build: context: ./images/cent7_ansible dockerfile: Dockerfile image:
internaltest/cent7_ansible hostname: master volumes: - ../ansible_playbook:/playbook working_dir: /playbook networks: infra_net: ipv4_address: 192.168.10.1 extra_hosts: - "master:192.168.10.1" - "target01:192.168.10.2" - "target02:192.168.10.3" - "target03:192.168.10.4" privileged: true ͖ͬ͞ͷ Dockerfile target01: image: internaltest/cent7_ansible hostname: target01 networks: infra_net: ipv4_address: 192.168.10.2 privileged: true target02: … target03: … networks: infra_net: driver: bridge ipam: driver: default config: - subnet: 192.168.10.0/24 gateway: 192.168.10.254
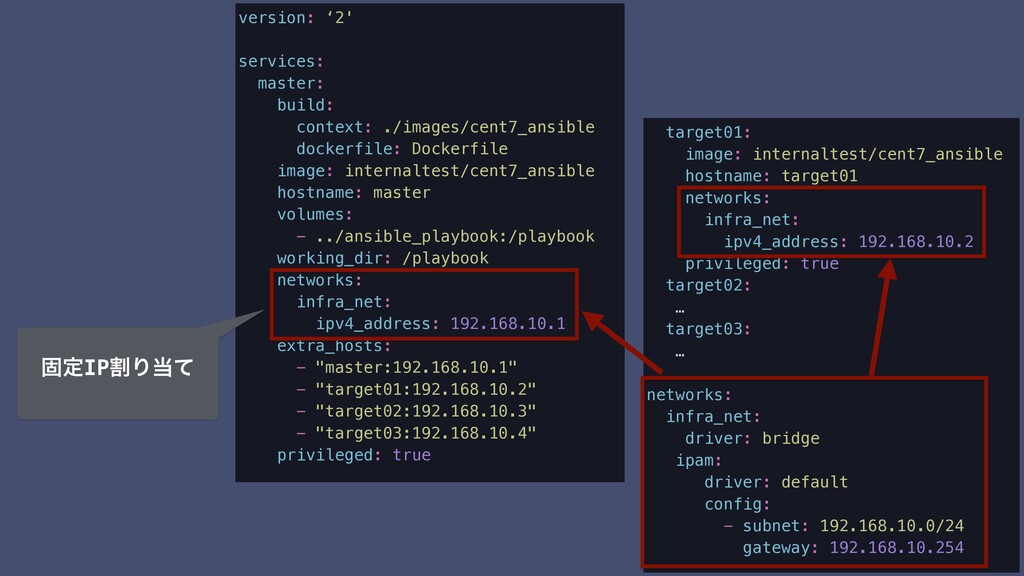
version: ‘2' services: master: build: context: ./images/cent7_ansible dockerfile: Dockerfile image:
internaltest/cent7_ansible hostname: master volumes: - ../ansible_playbook:/playbook working_dir: /playbook networks: infra_net: ipv4_address: 192.168.10.1 extra_hosts: - "master:192.168.10.1" - "target01:192.168.10.2" - "target02:192.168.10.3" - "target03:192.168.10.4" privileged: true target01: image: internaltest/cent7_ansible hostname: target01 networks: infra_net: ipv4_address: 192.168.10.2 privileged: true target02: … target03: … networks: infra_net: driver: bridge ipam: driver: default config: - subnet: 192.168.10.0/24 gateway: 192.168.10.254 ݻఆIPׂΓͯ
version: ‘2' services: master: build: context: ./images/cent7_ansible dockerfile: Dockerfile image:
internaltest/cent7_ansible hostname: master volumes: - ../ansible_playbook:/playbook working_dir: /playbook networks: infra_net: ipv4_address: 192.168.10.1 extra_hosts: - "master:192.168.10.1" - "target01:192.168.10.2" - "target02:192.168.10.3" - "target03:192.168.10.4" privileged: true hosts target01: image: internaltest/cent7_ansible hostname: target01 networks: infra_net: ipv4_address: 192.168.10.2 privileged: true target02: … target03: … networks: infra_net: driver: bridge ipam: driver: default config: - subnet: 192.168.10.0/24 gateway: 192.168.10.254
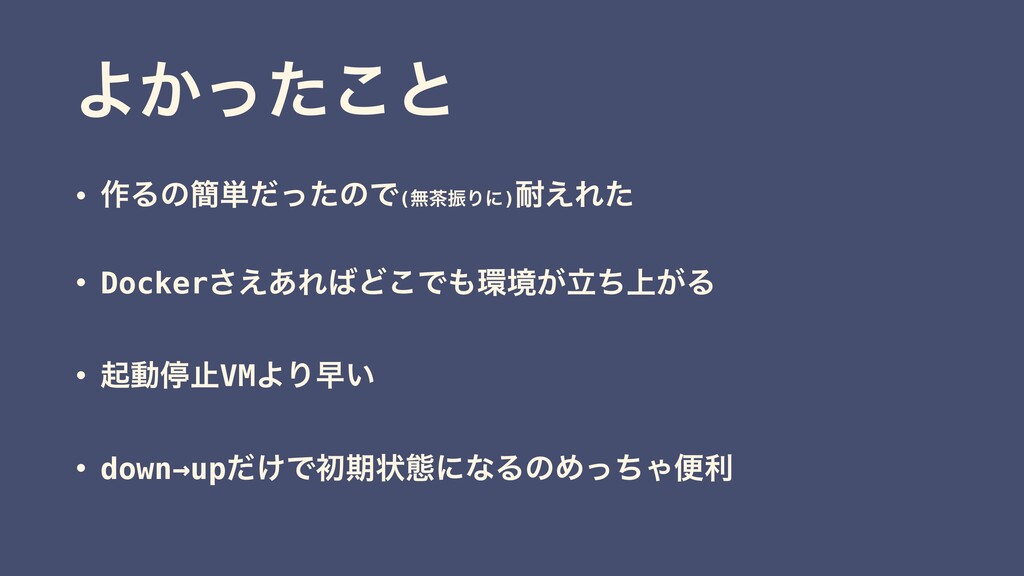
Α͔ͬͨ͜ͱ • ࡞Δͷ؆୯ͩͬͨͷͰ(ແৼΓʹ) ͑Εͨ • Docker͑͋͞ΕͲ͜Ͱڥ্ཱ͕͕ͪΔ • ىಈఀࢭVMΑΓૣ͍ • down→up͚ͩͰॳظঢ়ଶʹͳΔͷΊͬͪΌศར
·ͱΊ
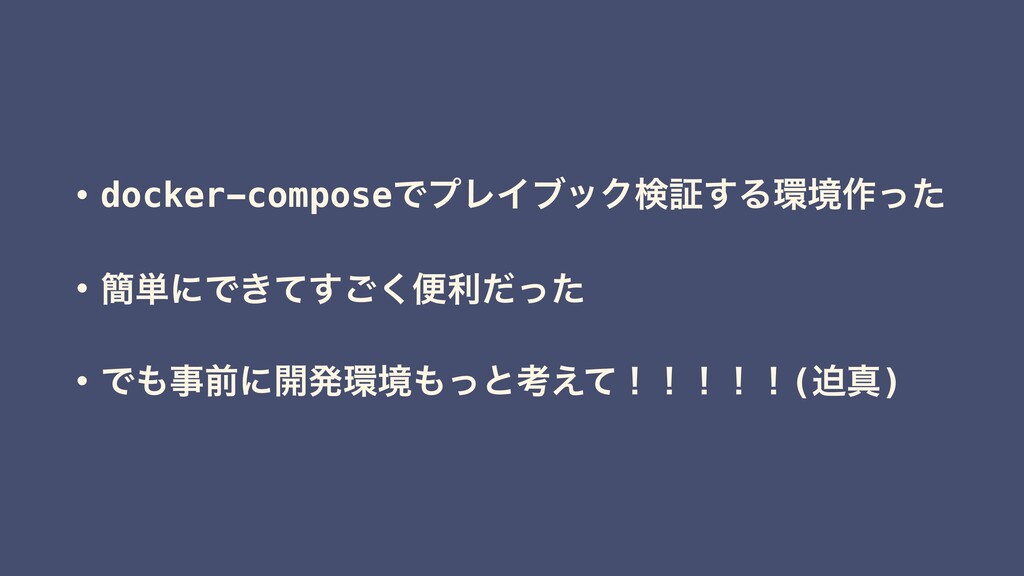
• docker-composeͰϓϨΠϒοΫݕূ͢Δڥ࡞ͬͨ • ؆୯ʹͰ͖ͯ͘͢͝ศརͩͬͨ • Ͱࣄલʹ։ൃڥͬͱߟ͑ͯʂʂʂʂʂ(ഭਅ)
͝ਗ਼ௌ͋Γ͕ͱ͏͍͟͝·ͨ͠ʂ
More Decks by あんでぃー
See All by あんでぃー
AnsibleでVSCode拡張を管理しちゃおう!/why dont you manage vscode extension with Ansible?
answerd
2
830
なぜSIerは自動化するのか/Why do SIers automate?
answerd
0
200
Other Decks in Technology
See All in Technology
メルカリの小規模チーム「Pod」で、 エンジニアがデータアナリストなしで、 AIを使ってデータ分析の自走を目指す取り組み
jackojacko_
0
100
少ない人手 限られた予算 それでも守る 消せない・見つける・戻れる オールハザード型BCP on AWS / 20261107 Mitsutoshi Matsuo
shift_evolve
PRO
0
410
変更差分を読むために環境を整備しよう
pipepasta
1
470
メール到達性を支える、リンク先URLのドメイン評価の扱い方
wind111
0
160
gradle-best-practices 使ってみた
mikanichinose
0
150
高品質と高スピードを支える品質のシフトレフトのアプローチ
goyoki
4
1.6k
WasmをRustにする技術
sansantech
PRO
1
120
「個社」ではなく「業界」の課題を解く AI 対話開発 ー 価値を広げる設計と、価値を守るエンジニアリング ー
ivry_presentationmaterials
3
660
常時稼働エージェントの作り方(Claude公式ブログを資料化)
minorun365
PRO
16
28k
Linuxネットワークスタック進化の軌跡: 過去10年の歩みと最新トレンド
orimanabu
4
750
PHPで家庭用ゲーム機の専用コントローラーをMIDIデバイスとして扱ってみる
wind111
0
150
HTTP通信に使おうとすると実はめんどくさいfile_get_contents
maguroalternative
0
220
Featured
See All Featured
How to Build an AI Search Optimization Roadmap - Criteria and Steps to Take #SEOIRL
aleyda
1
2.3k
ReactJS: Keep Simple. Everything can be a component!
pedronauck
666
130k
Pawsitive SEO: Lessons from My Dog (and Many Mistakes) on Thriving as a Consultant in the Age of AI
davidcarrasco
1
300
The SEO identity crisis: Don't let AI make you average
varn
0
630
Mind Mapping
helmedeiros
1
440
GraphQLとの向き合い方2022年版
quramy
50
15k
The Impact of AI in SEO - AI Overviews June 2024 Edition
aleyda
6
1.3k
Design and Strategy: How to Deal with People Who Don’t "Get" Design
morganepeng
133
20k
[Rails World 2023 - Day 1 Closing Keynote] - The Magic of Rails
eileencodes
38
3.1k
How to train your dragon (web standard)
notwaldorf
96
6.9k
[SF Ruby Conf 2025] Rails X
palkan
3
1.5k
RailsConf 2023
tenderlove
30
1.6k


 answerd
 jackojacko_
 shift_evolve
 pipepasta
 wind111
 mikanichinose
 goyoki
 sansantech
 ivry_presentationmaterials
 minorun365
 orimanabu
 maguroalternative
 aleyda
 pedronauck
 davidcarrasco
 varn
 helmedeiros
 quramy
 morganepeng
 eileencodes
 notwaldorf
 palkan
 tenderlove