Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
STARTTLS Everywhere
Search
Yan!
August 05, 2014
Programming
350
0
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
STARTTLS Everywhere
Yan Zhu and Jacob Hoffman-Andrews. PasswordsCon 2014.
Yan!
August 05, 2014
Other Decks in Programming
See All in Programming
複雑なUIコンポーネントとの ⻑い付き合い⽅:波及するバグからテスト戦略を経て、安全な再設計へ
mixplace
0
410
Everything will be SERVERLESS — 信じて運用した10年の経験値 / Everything Will be Serverless — Lessons Learned from 10 Years of Operational Experience
seike460
PRO
1
1.1k
月間100万人のサービス刷新で、 技術選定をHonoに振り切った話
yutobara
8
6.6k
C#の現在地 進化の歴史と、AI時代の.NET Everywhere
neuecc
5
5.2k
AmebaブログはKMPから卒業します
kmars0605
0
160
Apple Intelligence を用いた個人情報誤送信防止、及びユーザーリクエスト体験の改善について
yukiny
0
350
ActionController meets Protocol Buffers
sorah
0
450
IBM Bob Dojo #1 仕様駆動開発入門
oniak3ibm
PRO
0
390
Railsのためのパスキー実践入門 〜マルチテナントSaaSでの意思決定〜
utakaha
2
470
Workers Cache を知る
syumai
0
360
golang-bob.pdf
iwatsukayura
0
130
ジョジョの世界をXRで再現する
mofurune
0
160
Featured
See All Featured
[RailsConf 2023 Opening Keynote] The Magic of Rails
eileencodes
31
10k
Joys of Absence: A Defence of Solitary Play
codingconduct
1
550
Stop Working from a Prison Cell
hatefulcrawdad
274
21k
Easily Structure & Communicate Ideas using Wireframe
afnizarnur
194
17k
How STYLIGHT went responsive
nonsquared
100
6.3k
What’s in a name? Adding method to the madness
productmarketing
PRO
24
4.2k
Intergalactic Javascript Robots from Outer Space
tanoku
273
28k
ラッコキーワード サービス紹介資料
rakko
1
5.3M
Tell your own story through comics
letsgokoyo
1
1.1k
A Guide to Academic Writing Using Generative AI - A Workshop
ks91
PRO
1
520
16th Malabo Montpellier Forum Presentation
akademiya2063
PRO
0
410
StorybookのUI Testing Handbookを読んだ
zakiyama
31
7k
Transcript
STARTTLS Everywhere Peter Eckersley, Jacob Hoffman-Andrews, Yan Zhu Electronic Frontier
Foundation {pde, jsha,yan}@eff.org
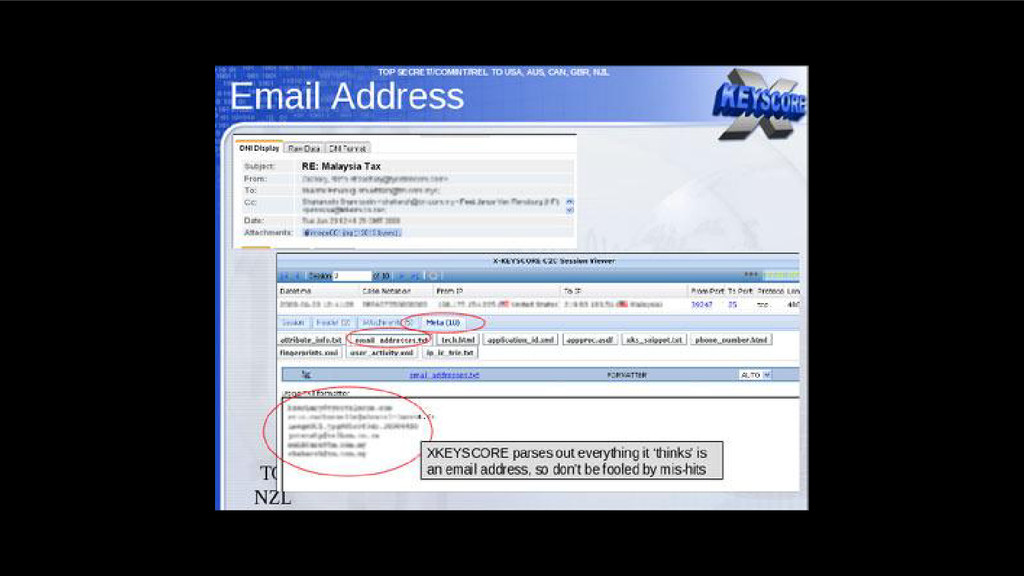
SMTP email transmission is mostly insecure
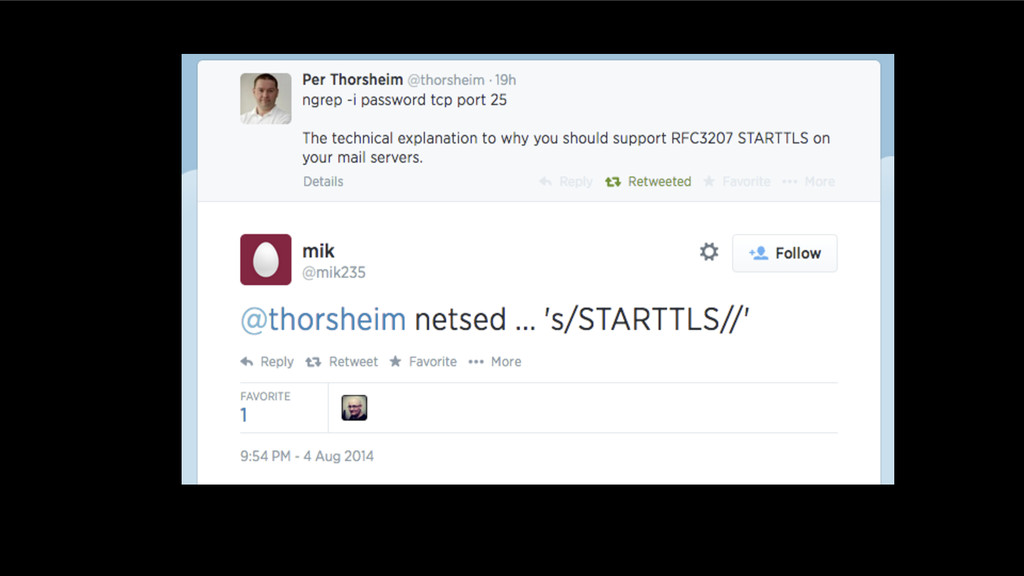
ngrep -i password tcp port 25
None
None
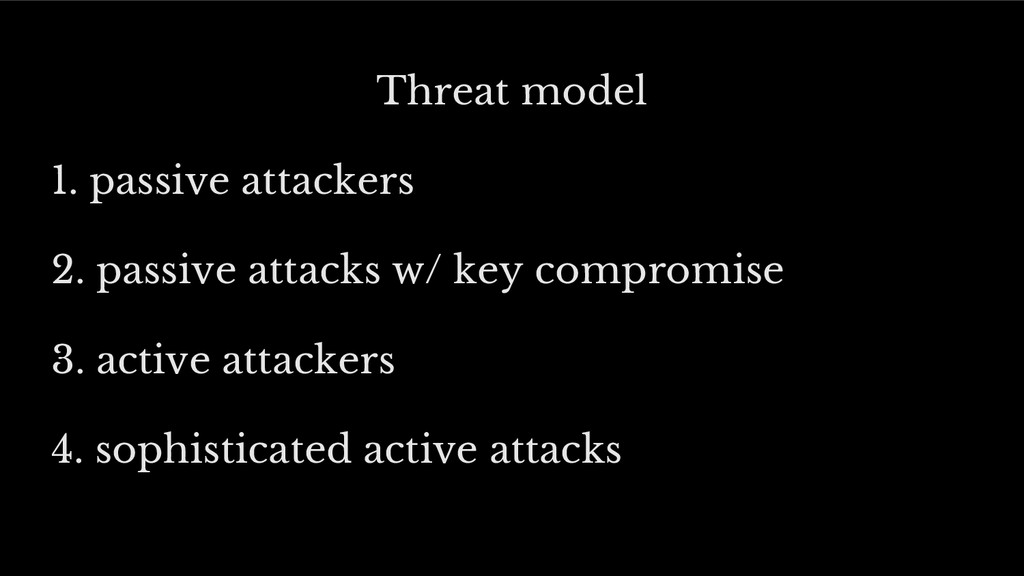
Threat model 1. passive attackers 2. passive attacks w/ key
compromise 3. active attackers 4. sophisticated active attacks
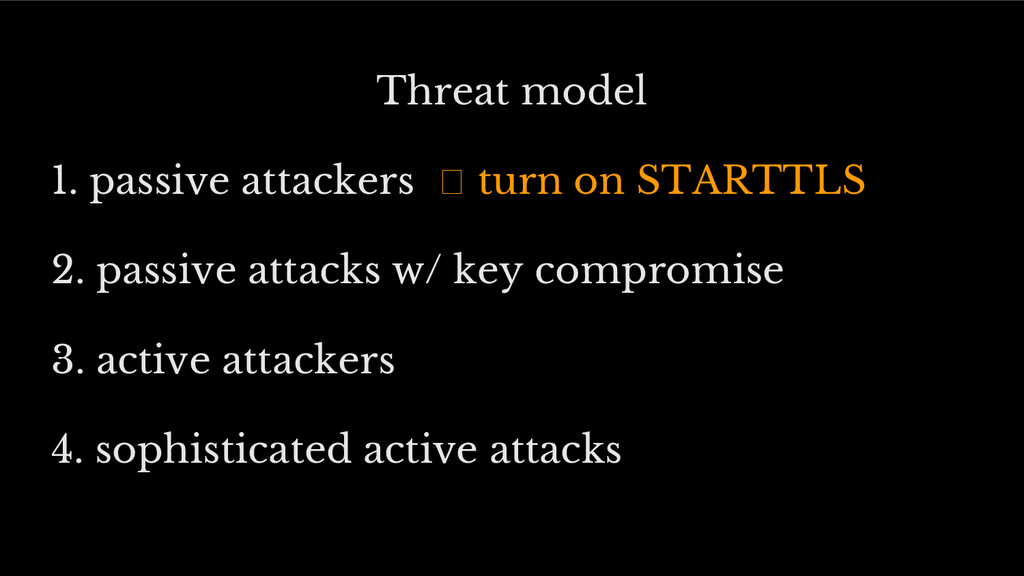
Threat model 1. passive attackers turn on STARTTLS 2. passive
attacks w/ key compromise 3. active attackers 4. sophisticated active attacks
None
None
None
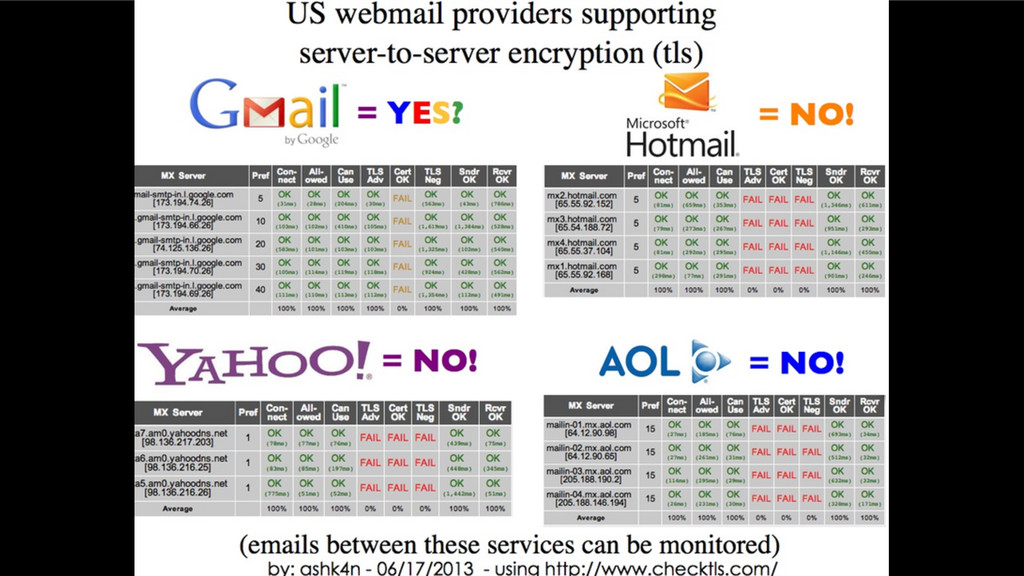
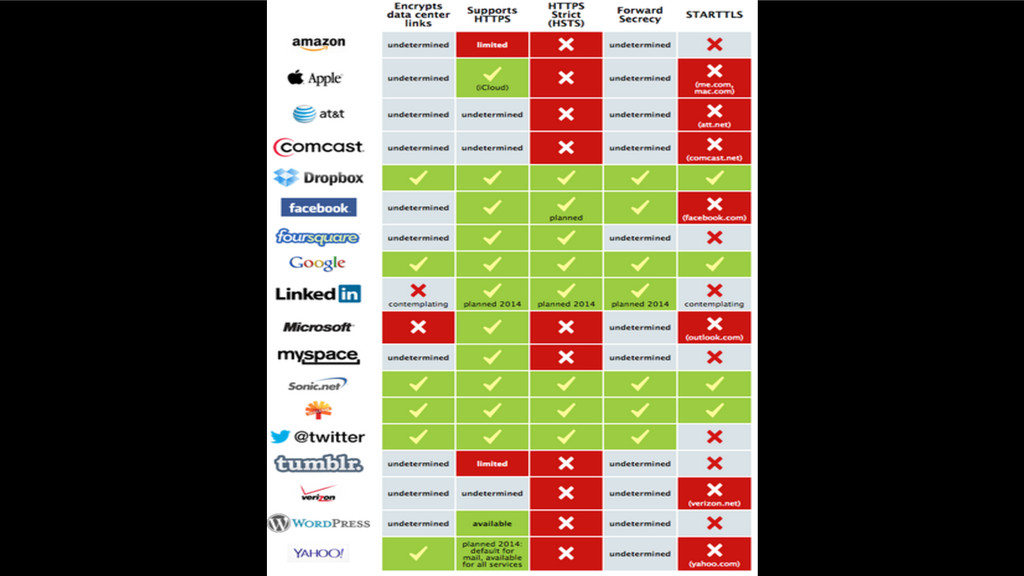
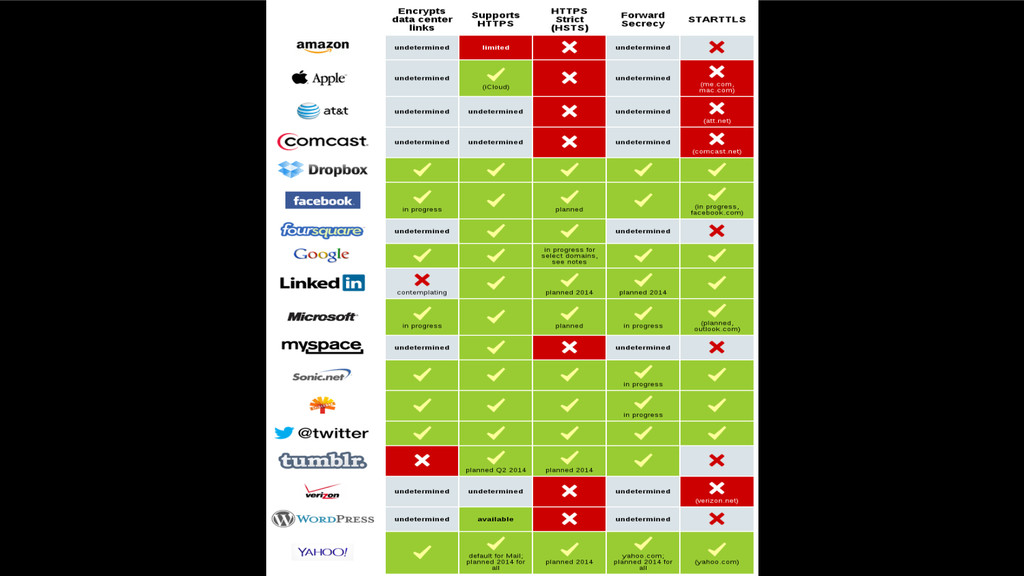
STARTTLS in/out of Gmail
It'd be nice to stretch that graph further back in
time https://github.com/EFForg/smtp-tls-history. git Email
[email protected]
if you'd like to run that on a large set of historical headers
2. passive attacks w/ sophisticated assistance (key theft)
What's the easiest way for eavesdroppers to read billions of
encrypted email transfers?
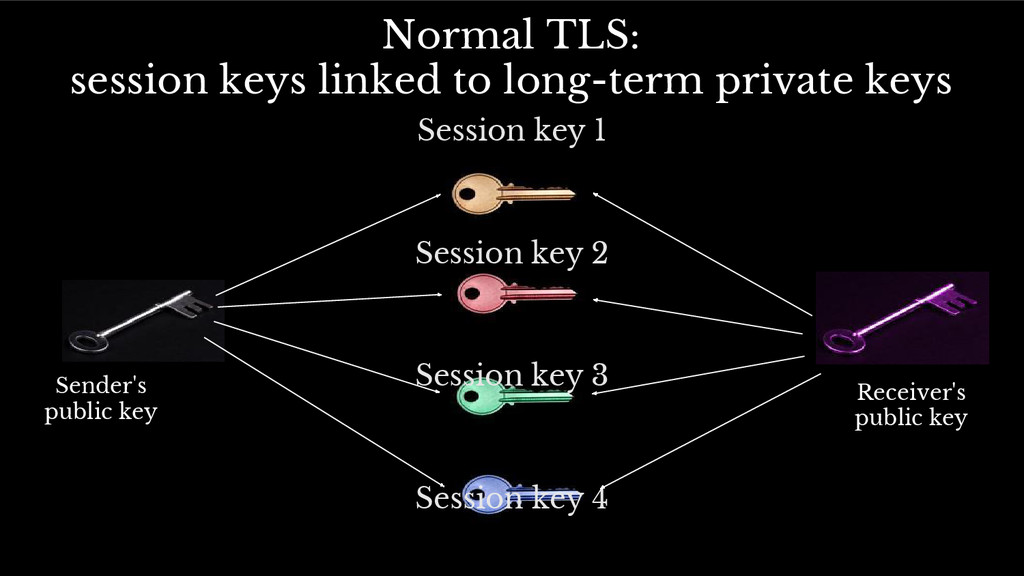
Session key 1 Session key 2 Session key 3 Session
key 4 Normal TLS: session keys linked to long-term private keys Sender's public key Receiver's public key
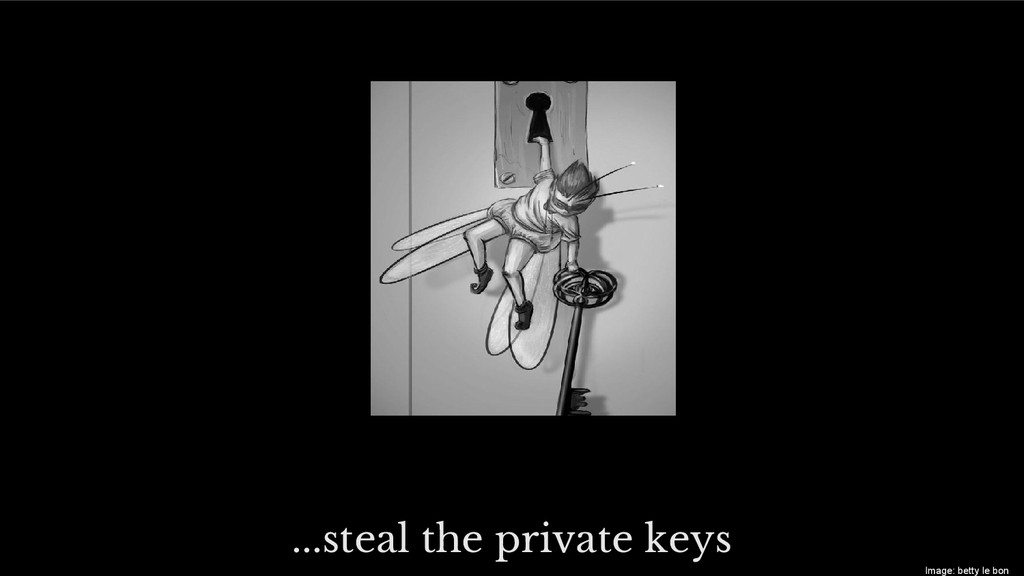
...steal the private keys Image: betty le bon
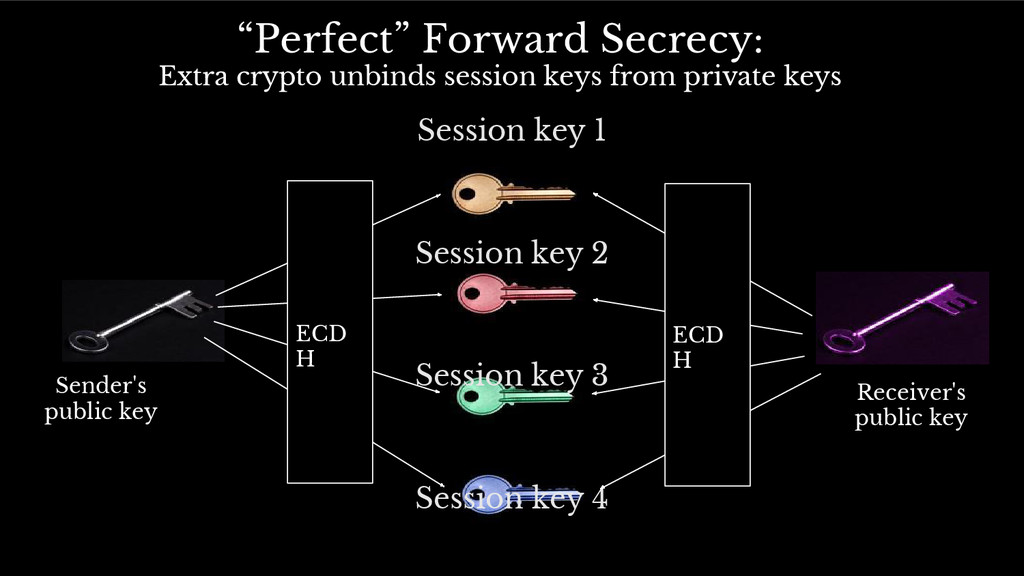
Session key 1 Session key 2 Session key 3 Session
key 4 “Perfect” Forward Secrecy: Extra crypto unbinds session keys from private keys Sender's public key Receiver's public key ECD H ECD H
How do we turn on Perfect Forward Secrecy correctly for
SMTP?
Simple answer: - support TLS v1.2 - protect against downgrade
attacks
Need a new policy mechanism to do that!
3. active network attacks
Unfortunately, active attacks are really easy...
How does SMTP-TLS work?
One side say “STARTTLS”, the other replies “STARTTLS”
None
The sender will fall back to insecure SMTP
Attackers can also “man in the middle”, speaking TLS themselves
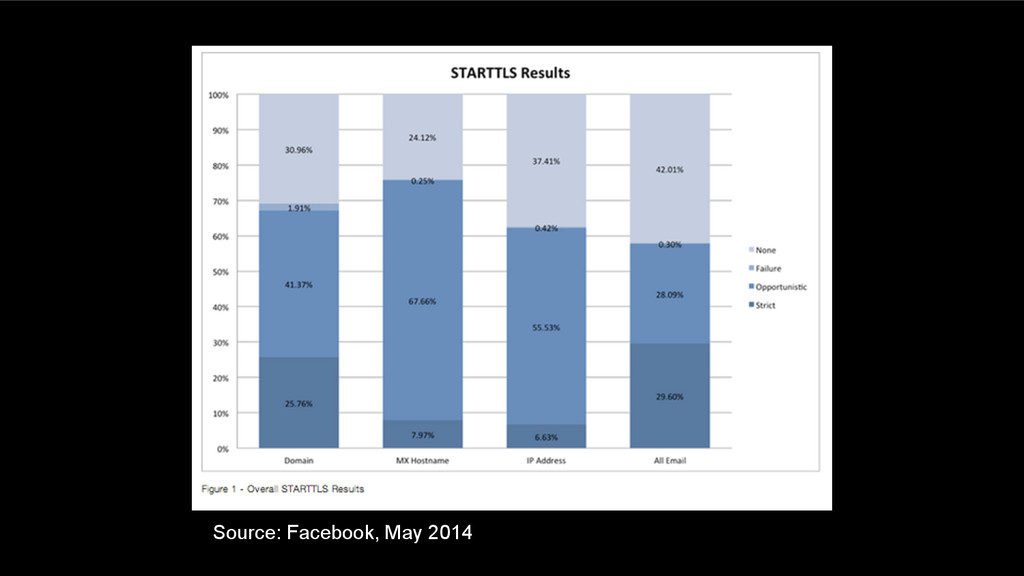
Source: Facebook, May 2014
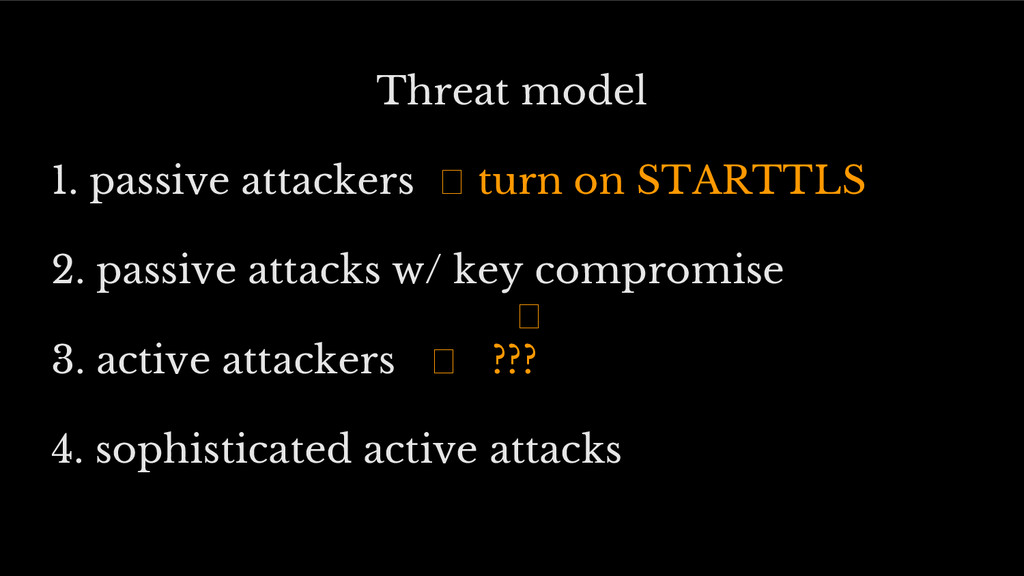
Threat model 1. passive attackers turn on STARTTLS 2. passive
attacks w/ key compromise 3. active attackers ??? 4. sophisticated active attacks
On the Web, we have the HSTS header for this
A quick pragmatic solution: STARTTLS Everywhere
git clone https://github.com/EFForg/starttls-everywhere.git
Main concepts: - Recipient security policy framework - Supports missing
functionality - Start with a centralized database - Multi-channel distribution
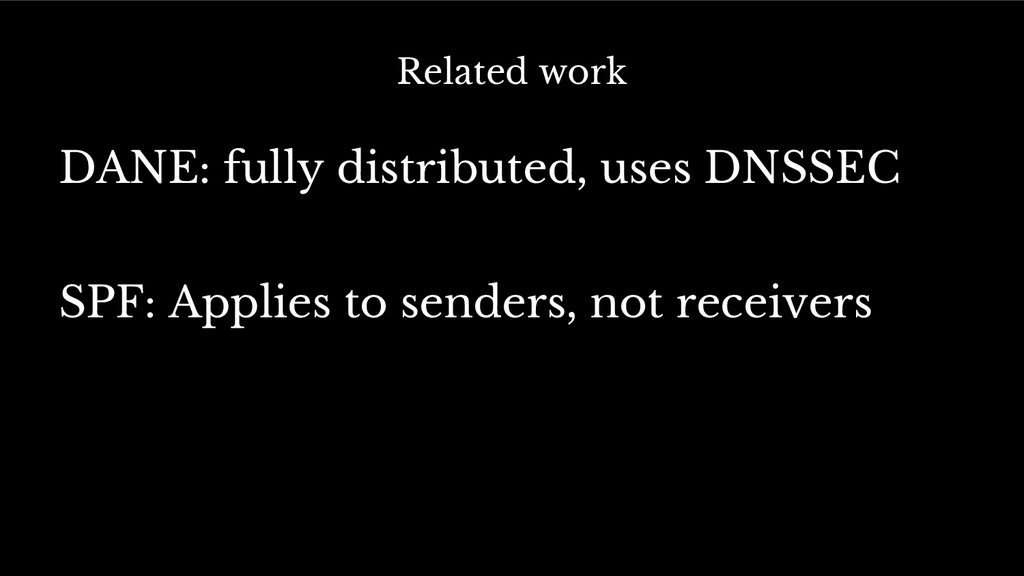
Related work DANE: fully distributed, uses DNSSEC SPF: Applies to
senders, not receivers
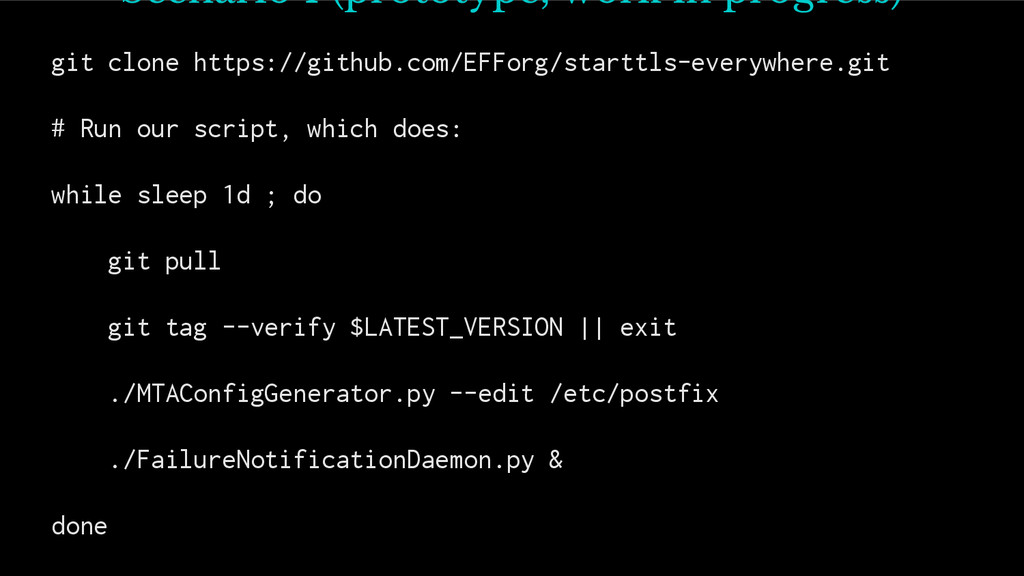
Scenario 1 (prototype, work in progress) git clone https://github.com/EFForg/starttls-everywhere.git #
Run our script, which does: while sleep 1d ; do git pull git tag --verify $LATEST_VERSION || exit ./MTAConfigGenerator.py --edit /etc/postfix ./FailureNotificationDaemon.py & done
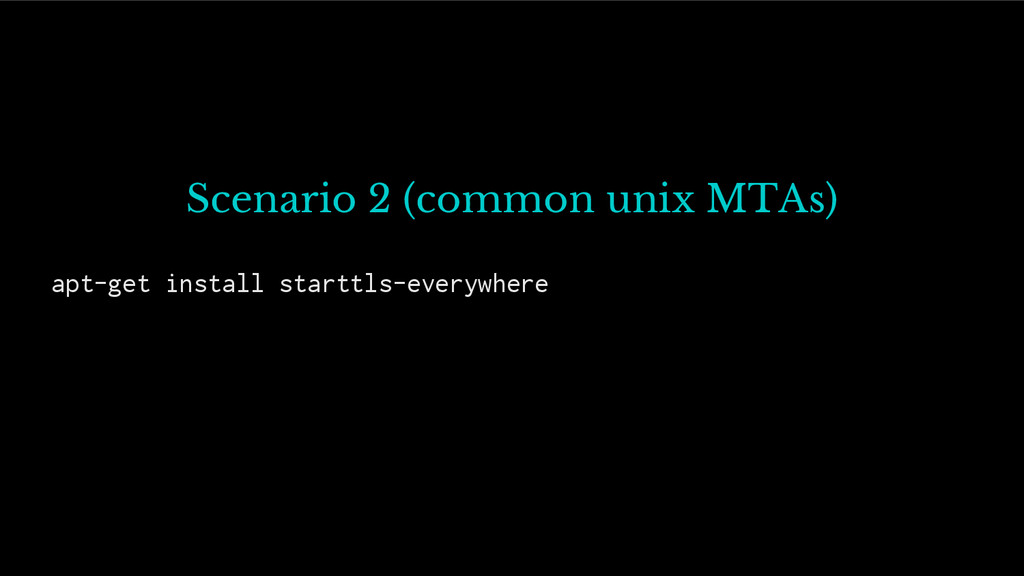
Scenario 2 (common unix MTAs) apt-get install starttls-everywhere
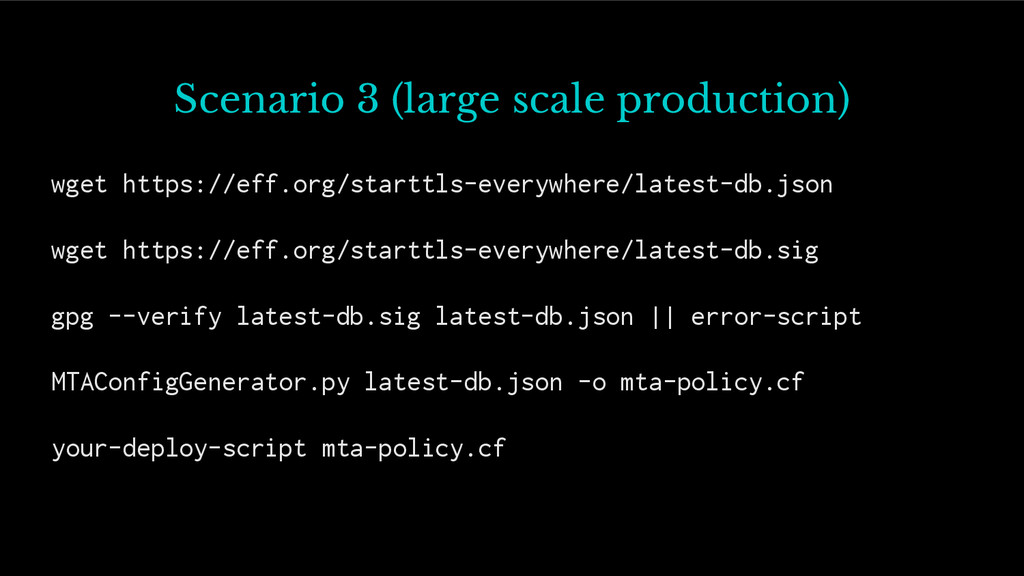
Scenario 3 (large scale production) wget https://eff.org/starttls-everywhere/latest-db.json wget https://eff.org/starttls-everywhere/latest-db.sig gpg
--verify latest-db.sig latest-db.json || error-script MTAConfigGenerator.py latest-db.json -o mta-policy.cf your-deploy-script mta-policy.cf
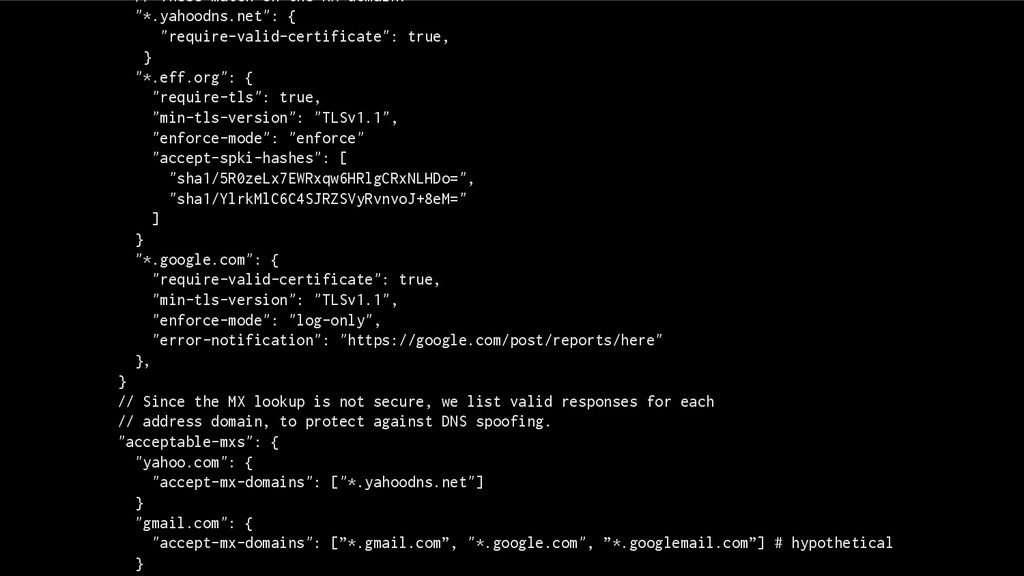
Policy database is a set of JSON blobs:
// These match on the MX domain. "*.yahoodns.net": { "require-valid-certificate":
true, } "*.eff.org": { "require-tls": true, "min-tls-version": "TLSv1.1", "enforce-mode": "enforce" "accept-spki-hashes": [ "sha1/5R0zeLx7EWRxqw6HRlgCRxNLHDo=", "sha1/YlrkMlC6C4SJRZSVyRvnvoJ+8eM=" ] } "*.google.com": { "require-valid-certificate": true, "min-tls-version": "TLSv1.1", "enforce-mode": "log-only", "error-notification": "https://google.com/post/reports/here" }, } // Since the MX lookup is not secure, we list valid responses for each // address domain, to protect against DNS spoofing. "acceptable-mxs": { "yahoo.com": { "accept-mx-domains": ["*.yahoodns.net"] } "gmail.com": { "accept-mx-domains": [”*.gmail.com”, "*.google.com", ”*.googlemail.com”] # hypothetical }
demo time! https://eff.org/starttls
https://eff.org/join https://eff.org/starttls EFF depends on your support!
None


 mixplace
 seike460
 yutobara
 neuecc
 kmars0605
 yukiny
 sorah
 oniak3ibm
 utakaha
 syumai
 iwatsukayura
 mofurune
 eileencodes
 codingconduct
 hatefulcrawdad
 afnizarnur
 nonsquared
 productmarketing
 tanoku
 rakko
 letsgokoyo
 ks91
 akademiya2063
 zakiyama