Share
Embed
セキュアエレメントによるWireGuardのセキュリティ強化
2023/9/26 SORACOM IoT-Tech Meetup 第5回

cyberomusubi
September 26, 2023
Transcript
39 slides
-
Agenda • 自己紹介 • IoTデバイスのリスク • 課題 • WireGuardとは •
セキュアエレメントについて • WireGuardのセキュリティ強化 • まとめ -
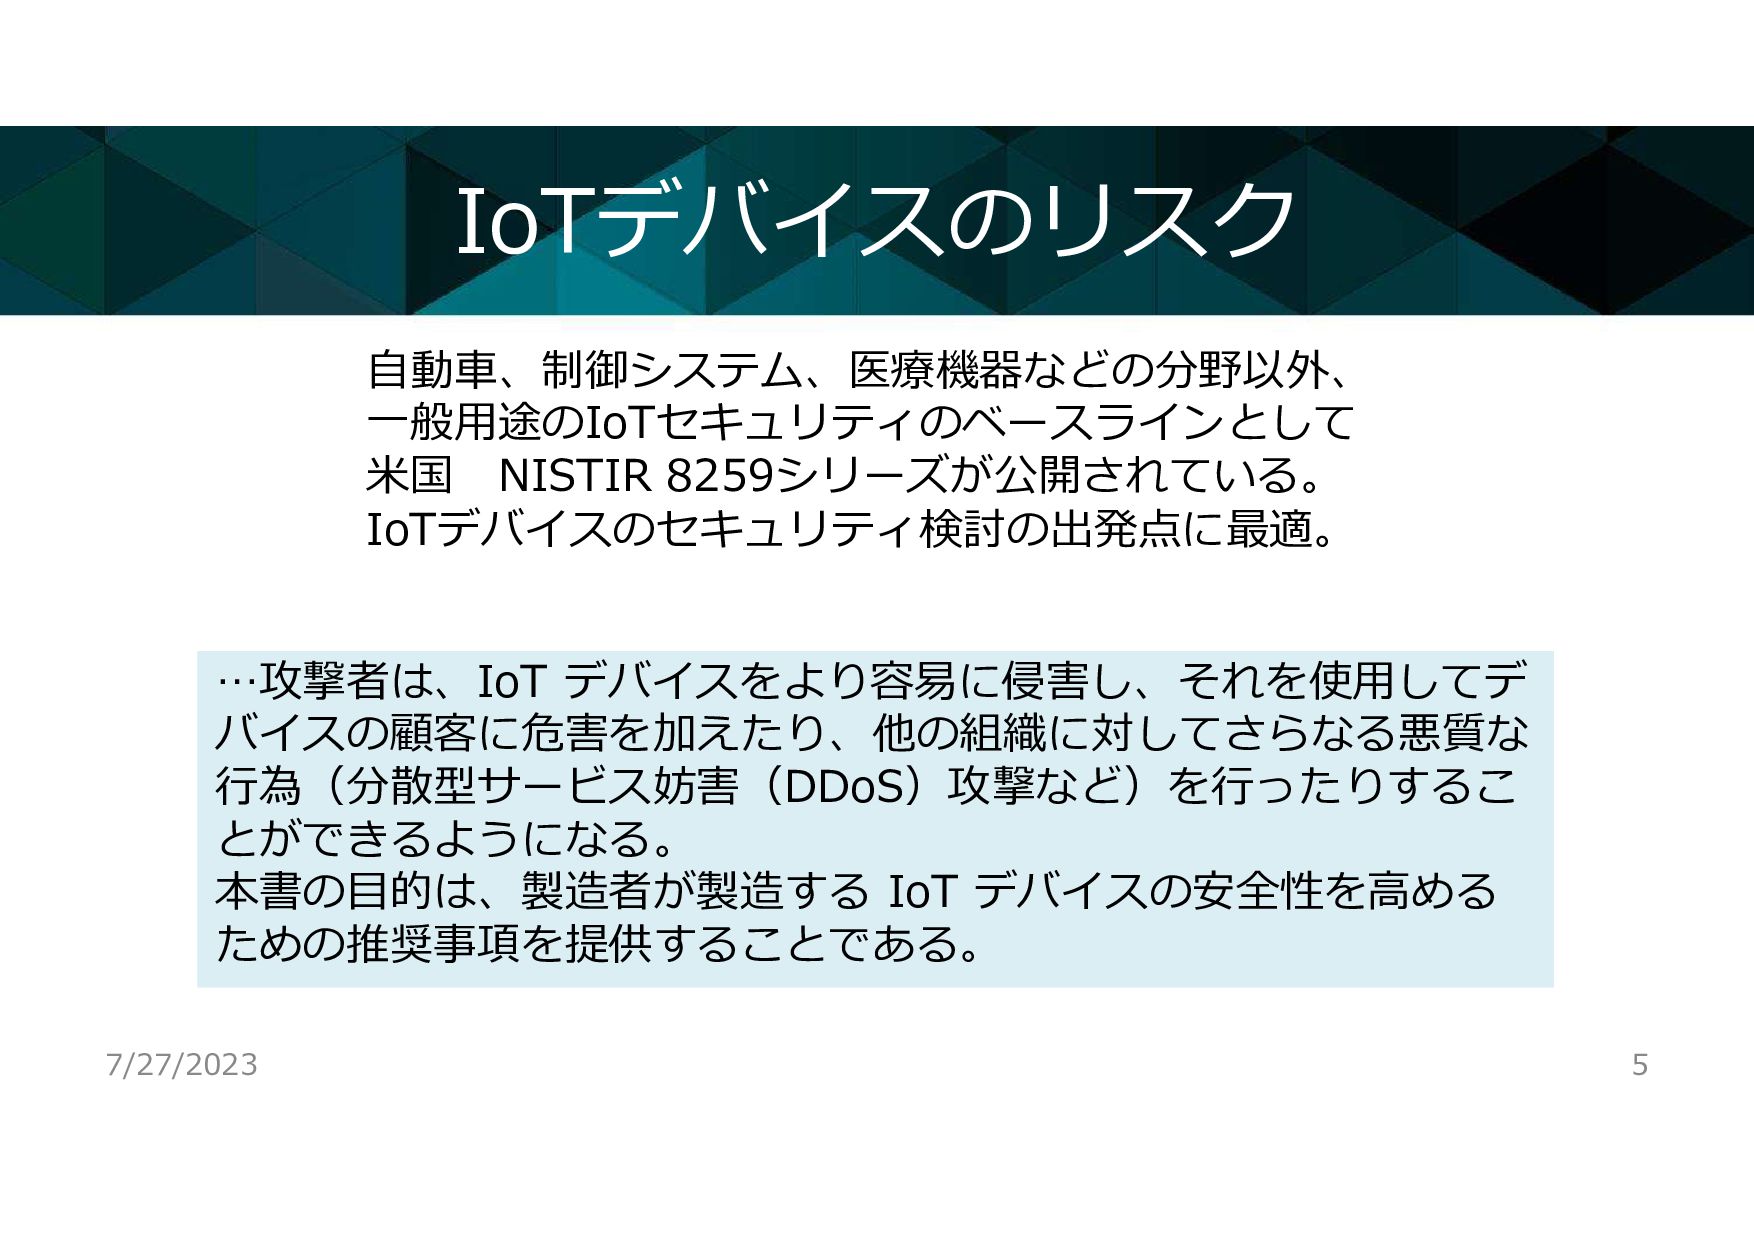
IoTデバイスのリスク 7/27/2023 5 自動車、制御システム、医療機器などの分野以外、 一般用途のIoTセキュリティのベースラインとして 米国 NISTIR 8259シリーズが公開されている。 IoTデバイスのセキュリティ検討の出発点に最適。 …攻撃者は、IoT
デバイスをより容易に侵害し、それを使用してデ バイスの顧客に危害を加えたり、他の組織に対してさらなる悪質な 行為(分散型サービス妨害(DDoS)攻撃など)を行ったりするこ とができるようになる。 本書の目的は、製造者が製造する IoT デバイスの安全性を高める ための推奨事項を提供することである。 -
IoTデバイスのリスク 7/28/2023 6 NISTIR 8259AはIoTデバイスが備えるべき機能のベースラインを記述。 項目 概要 デバイスの識別 IoTデバイスは、論理的にも物理的にも一意に識別できる デバイス構成
IoT デバイスのソフトウェア構成は変更できるが、そのような変更は許可されたエンティ ティのみが実行できる データ保護 保存、または転送されるデータを未承認のアクセスと変更から保護できる インターフェースへの論理アクセス ローカル・インターフェースおよびネットワーク・インターフェース、ならびにそれらの インターフェースで使用されるプロトコルおよびサービスへの論理アクセスを、許可され たエンティティのみに制限することができる ソフトウェア更新 IoT デバイスのソフトウェアは、安全で構成可能なメカニズムを使用して、承認されたエ ンティティのみが更新できる サイバーセキュリティ状態の認識 IoTデバイスは、そのサイバーセキュリティの状態を報告し、その情報を許可されたエン ティティのみがアクセスできるようにすることができる -
課題 7/28/2023 8 「セキュリティ・バイ・デザイン」の考え方からも、 事前にセキュリティ要件を考慮して、必要な構成を検討しておくことが重要。 WireGuardを用いてIoTプロジェクトのセキュリティのベストプラクティスを 検討してみたい。 IPA セキュリティ・バイ・デザイン 導入指南書
https://www.ipa.go.jp/jinzai/ics/core_human_resource/final_project/2022/ng i93u0000002kef-att/000100451.pdf -
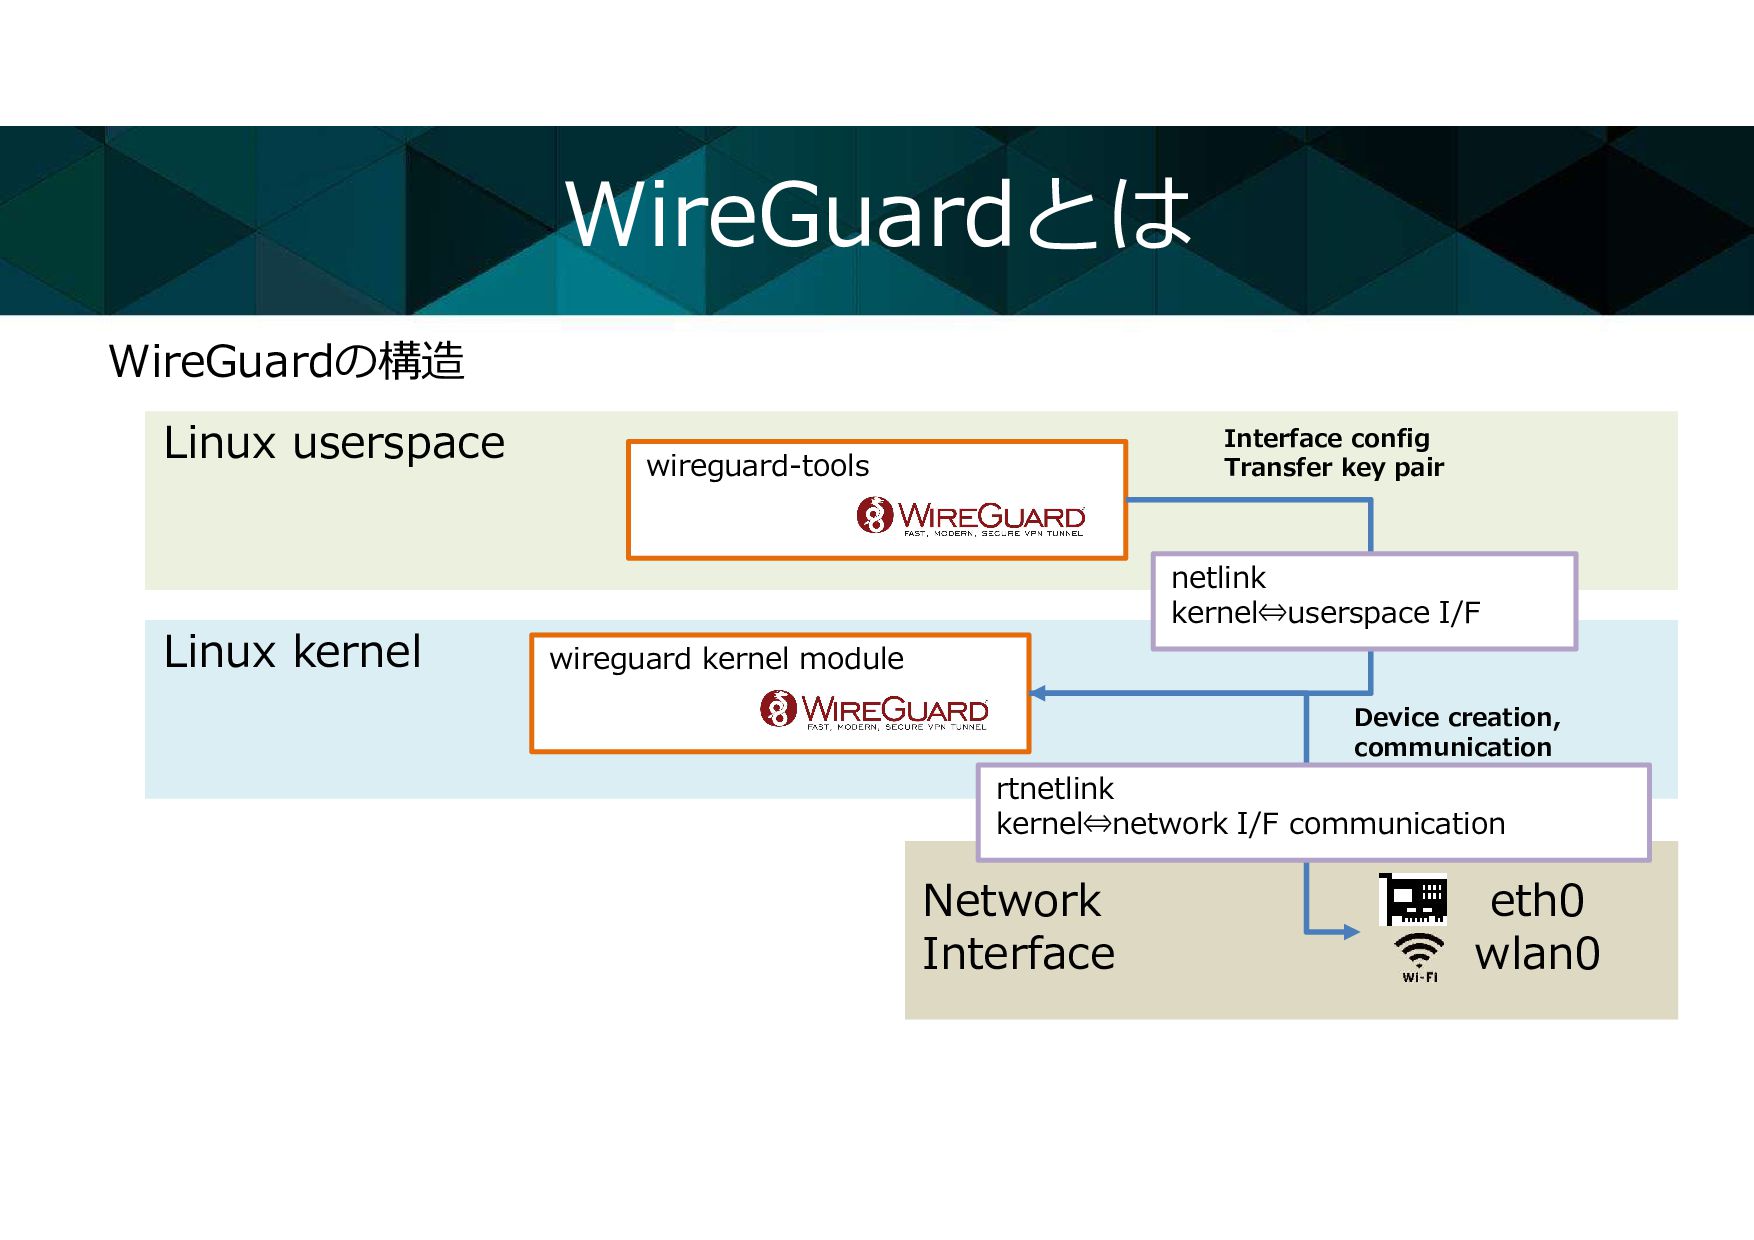
WireGuardの構造 Linux kernel Network Interface eth0 wlan0 wireguard kernel module
Linux userspace wireguard-tools rtnetlink kernel⇔network I/F communication netlink kernel⇔userspace I/F Interface config Transfer key pair Device creation, communication WireGuardとは -
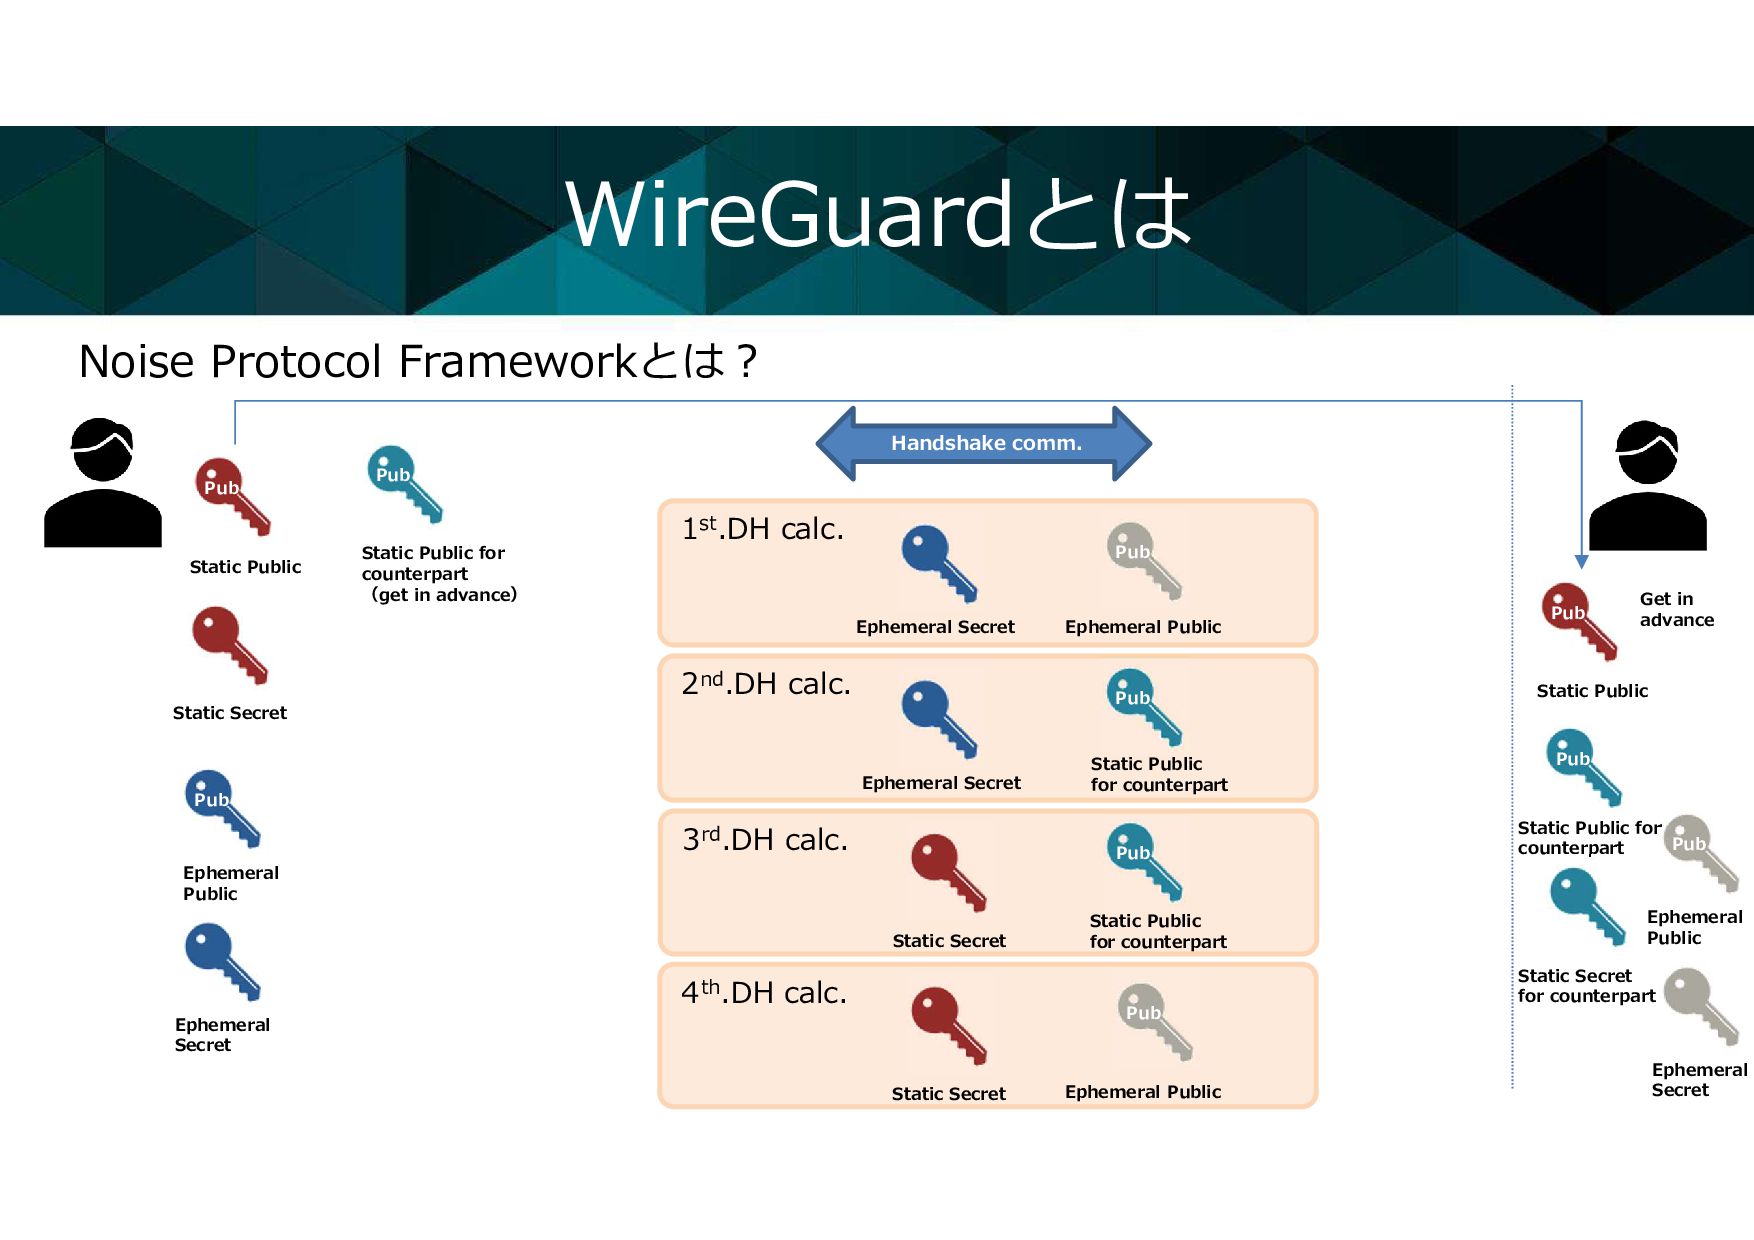
2nd.DH calc. Noise Protocol Frameworkとは? Static Secret Static Public Pub
Pub Ephemeral Public Ephemeral Secret Handshake comm. Static Public Pub Get in advance Static Public for counterpart Pub Static Public for counterpart (get in advance) Pub Static Public for counterpart Pub Ephemeral Secret 3rd.DH calc. Static Public for counterpart Pub Static Secret 4th.DH calc. Static Secret Pub Ephemeral Secret Static Secret for counterpart Ephemeral Public Pub Ephemeral Public 1st.DH calc. Ephemeral Secret Pub Ephemeral Public WireGuardとは -
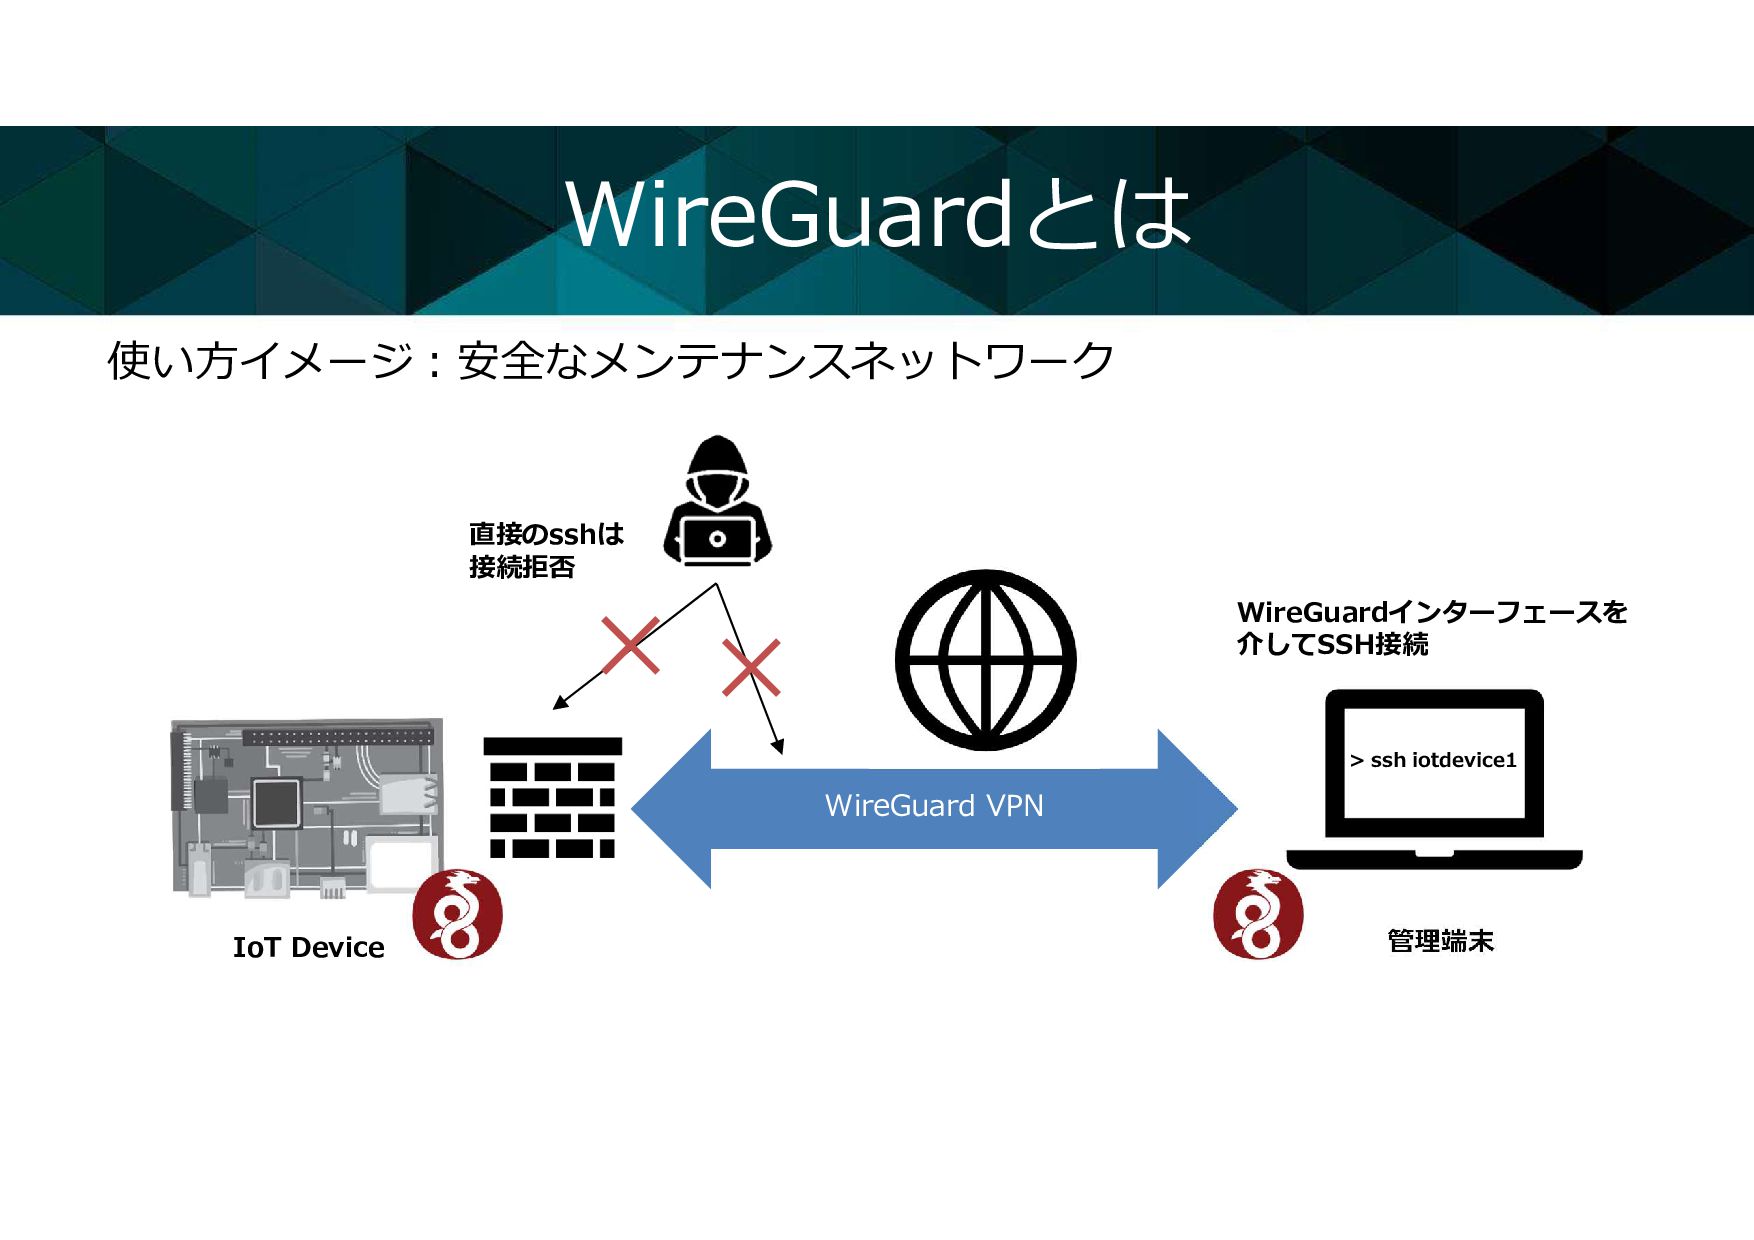
使い方イメージ:安全なメンテナンスネットワーク WireGuardとは IoT Device WireGuard VPN 直接のsshは 接続拒否 管理端末 WireGuardインターフェースを
介してSSH接続 > ssh iotdevice1 -
[Interface] PrivateKey = <Private Key> Address = 10.0.0.51 [Peer] PublicKey
= <Public Key> Endpoint = XXX.XXX.XXX.XXX:51820 AllowedIPs = 10.0.0.1/32 もし悪意のある第3者が脆弱性を利用してデバイスに侵入したら、WireGuardの 設定ファイルを入手する可能性がある WireGuardとは /etc/wireguard/wg0.conf 解析 このデバイスの秘密鍵 とIPアドレス 接続先の公開鍵と パブリックIPアドレス IPアドレスレンジ類推 -
[Interface] PrivateKey = <Private Key> Address = 10.0.0.51 [Peer] PublicKey
= <Public Key> Endpoint = XXX.XXX.XXX.XXX:51820 AllowedIPs = 10.0.0.0/24 なりすましを行い、接続を行ったり、ほかの接続先を探索し、 脆弱性を探すことができてしまう WireGuardとは /etc/wireguard/wg0.conf なりすまし なりすまし ネットワークレンジを 広げて探索 -
課題提起:静的秘密鍵の置き場所 これをセキュアエレメントで守れないか [Interface] PrivateKey = FA2qtPQO3XsjOSR06Sx9Eg/rR8pw2B5cSgdOXKpa8Gs= Address = 10.0.0.112/32 [Peer]
PublicKey = XXXXX= Endpoint = XXX.XXX.XXX.XXX:XXXXX Static Secret Static Public for counterpart (get in advance) Pub WireGuardとは -
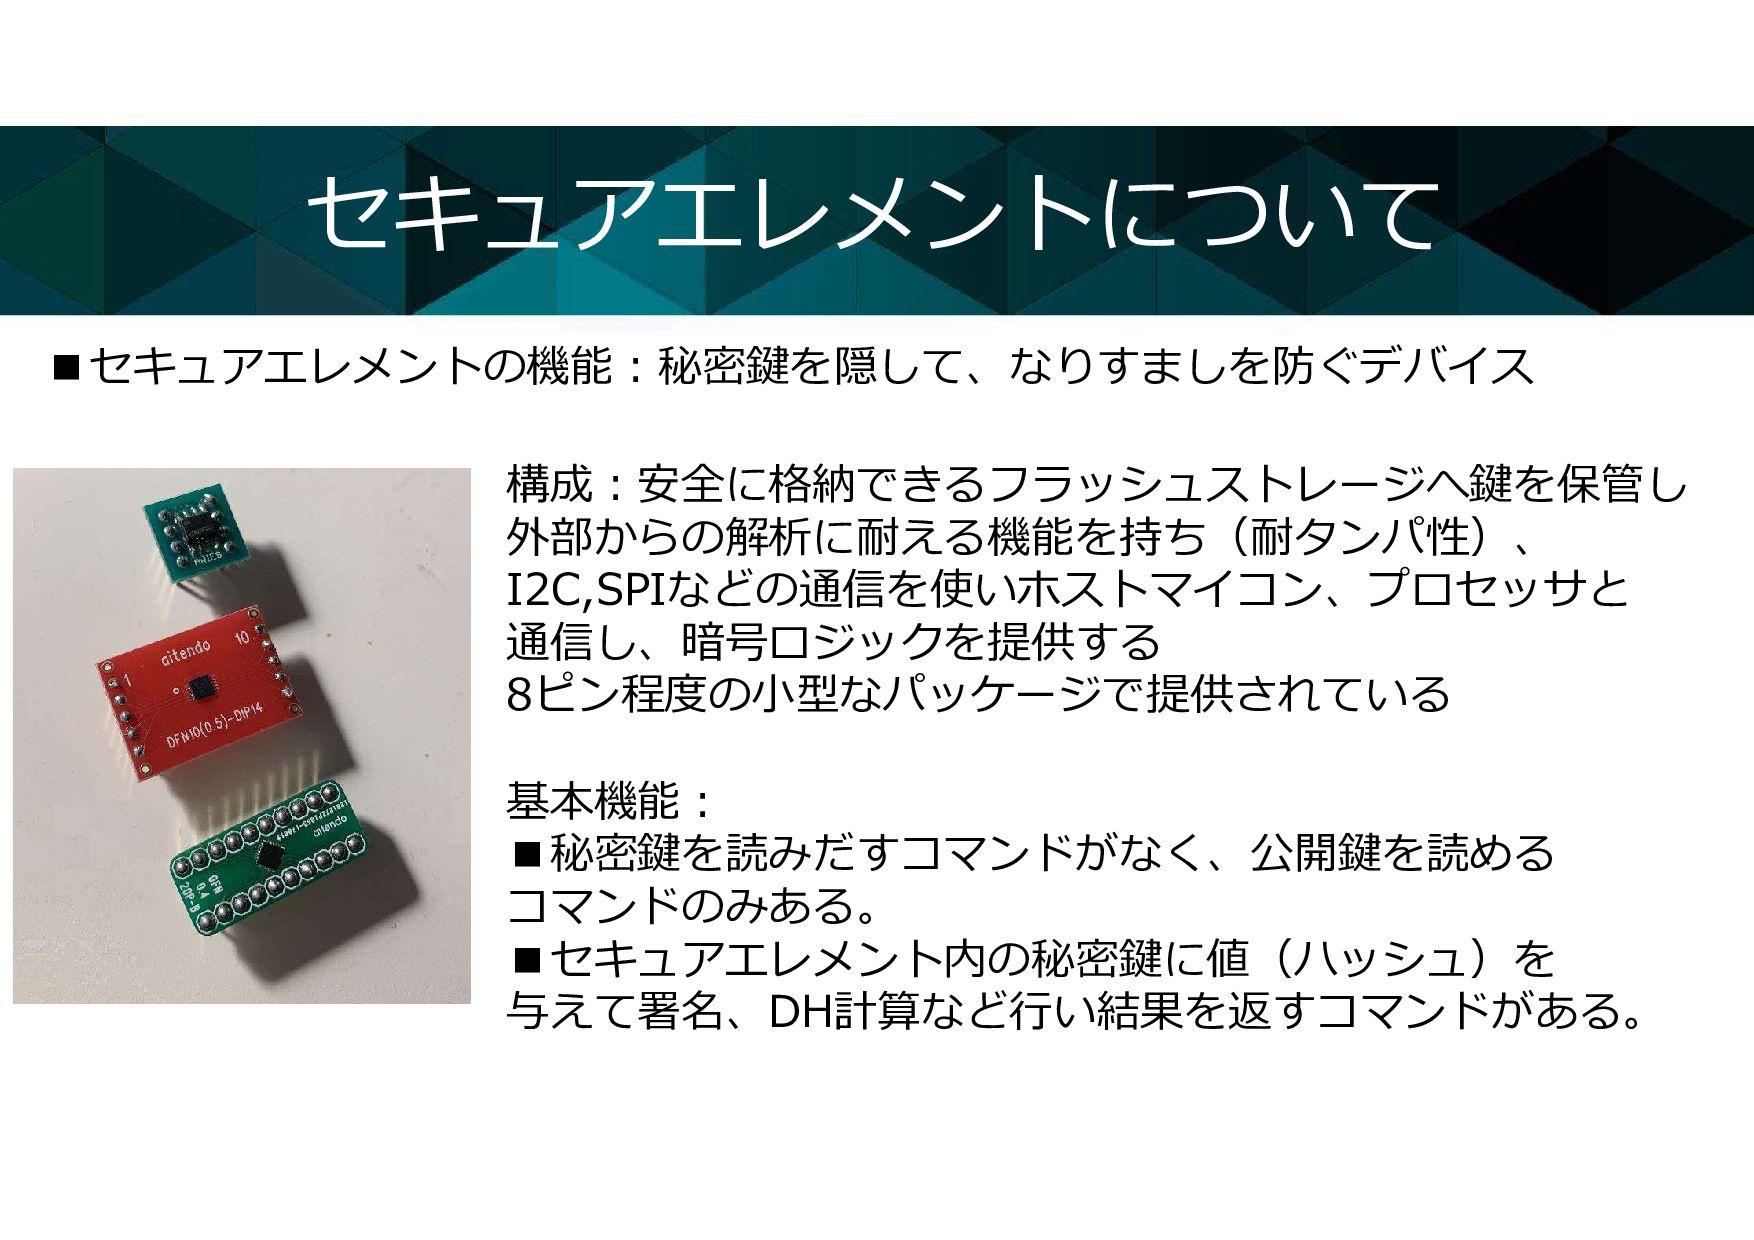
セキュアエレメントについて ▪セキュアエレメントの機能:秘密鍵を隠して、なりすましを防ぐデバイス 構成:安全に格納できるフラッシュストレージへ鍵を保管し 外部からの解析に耐える機能を持ち(耐タンパ性)、 I2C,SPIなどの通信を使いホストマイコン、プロセッサと 通信し、暗号ロジックを提供する 8ピン程度の小型なパッケージで提供されている 基本機能: ▪秘密鍵を読みだすコマンドがなく、公開鍵を読める コマンドのみある。
▪セキュアエレメント内の秘密鍵に値(ハッシュ)を 与えて署名、DH計算など行い結果を返すコマンドがある。 -
ATECC608A SE050(C) Optiga Trust M STSAFE-A110 メーカー Microchip NXP Infineon
STMicro インターフェース I2C 暗号演算 楕円暗号(ECC) 楕円暗号(ECC)、RSA 楕円暗号(ECC) 楕円暗号(ECC) 楕円暗号 NIST P-256 ECC NIST (192 to 521 bit) Brainpool (160 to 512 bit) Twisted Edwards Ed25519 Montgomery Curve25519 Koblitz (192 to 256 bit) Barreto-Naehrig Curve 256 bit NIST P-256, P-384 ECC NIST (256 to 384 bit) Brainpool (256 to 384 bit) RSA暗号 - up to 4096 bit - 共通鍵暗号 AES-128 AES 128, 192 and 256 bit and DES keys with single DES, 2K3DES and 3K3DES AES-128 AES-128 ハッシュ SHA-256 SHA-224/256/384/512 SHA-256 SHA-256/384 記憶領域 1.1KB 50KB 10KB 6KB 価格(1個当たり) ¥131 ¥755 ¥275 ¥467 パッケージ 8pin SOIC,DFN 20pin QFN 10pin DFN SO8N,UFDFPN8 製品ファミリ 限定機能のみの ATECC108Aなど 限定機能のみのSE050(A)、SE050(B) 温度環境対応品 SPL02,SPL03 採用実績 Google Coral SoM,Arduino MKR Wifi Amazon Dash Button 2nd gen.(ATECC108A) ZYMBIT security module NervesKey for NervesHub Adafruit ATECC608 Breakout Coldcard Bitcoin hardware wallet AWS IoT EduKit etc. Atmark Techmo Armadillo WithSecure USB Armory Arduino Nicla Vision Arduino Portenta H7 ー Starlink User Terminal 対応規格 ー CC EAL6+ (HW+JCOP) JavaCard version 3.0.5 GlobalPlatform specification version GP 3.0 CC EAL6+ CC EAL5+ AVA_VAN5 セキュアエレメントについて -
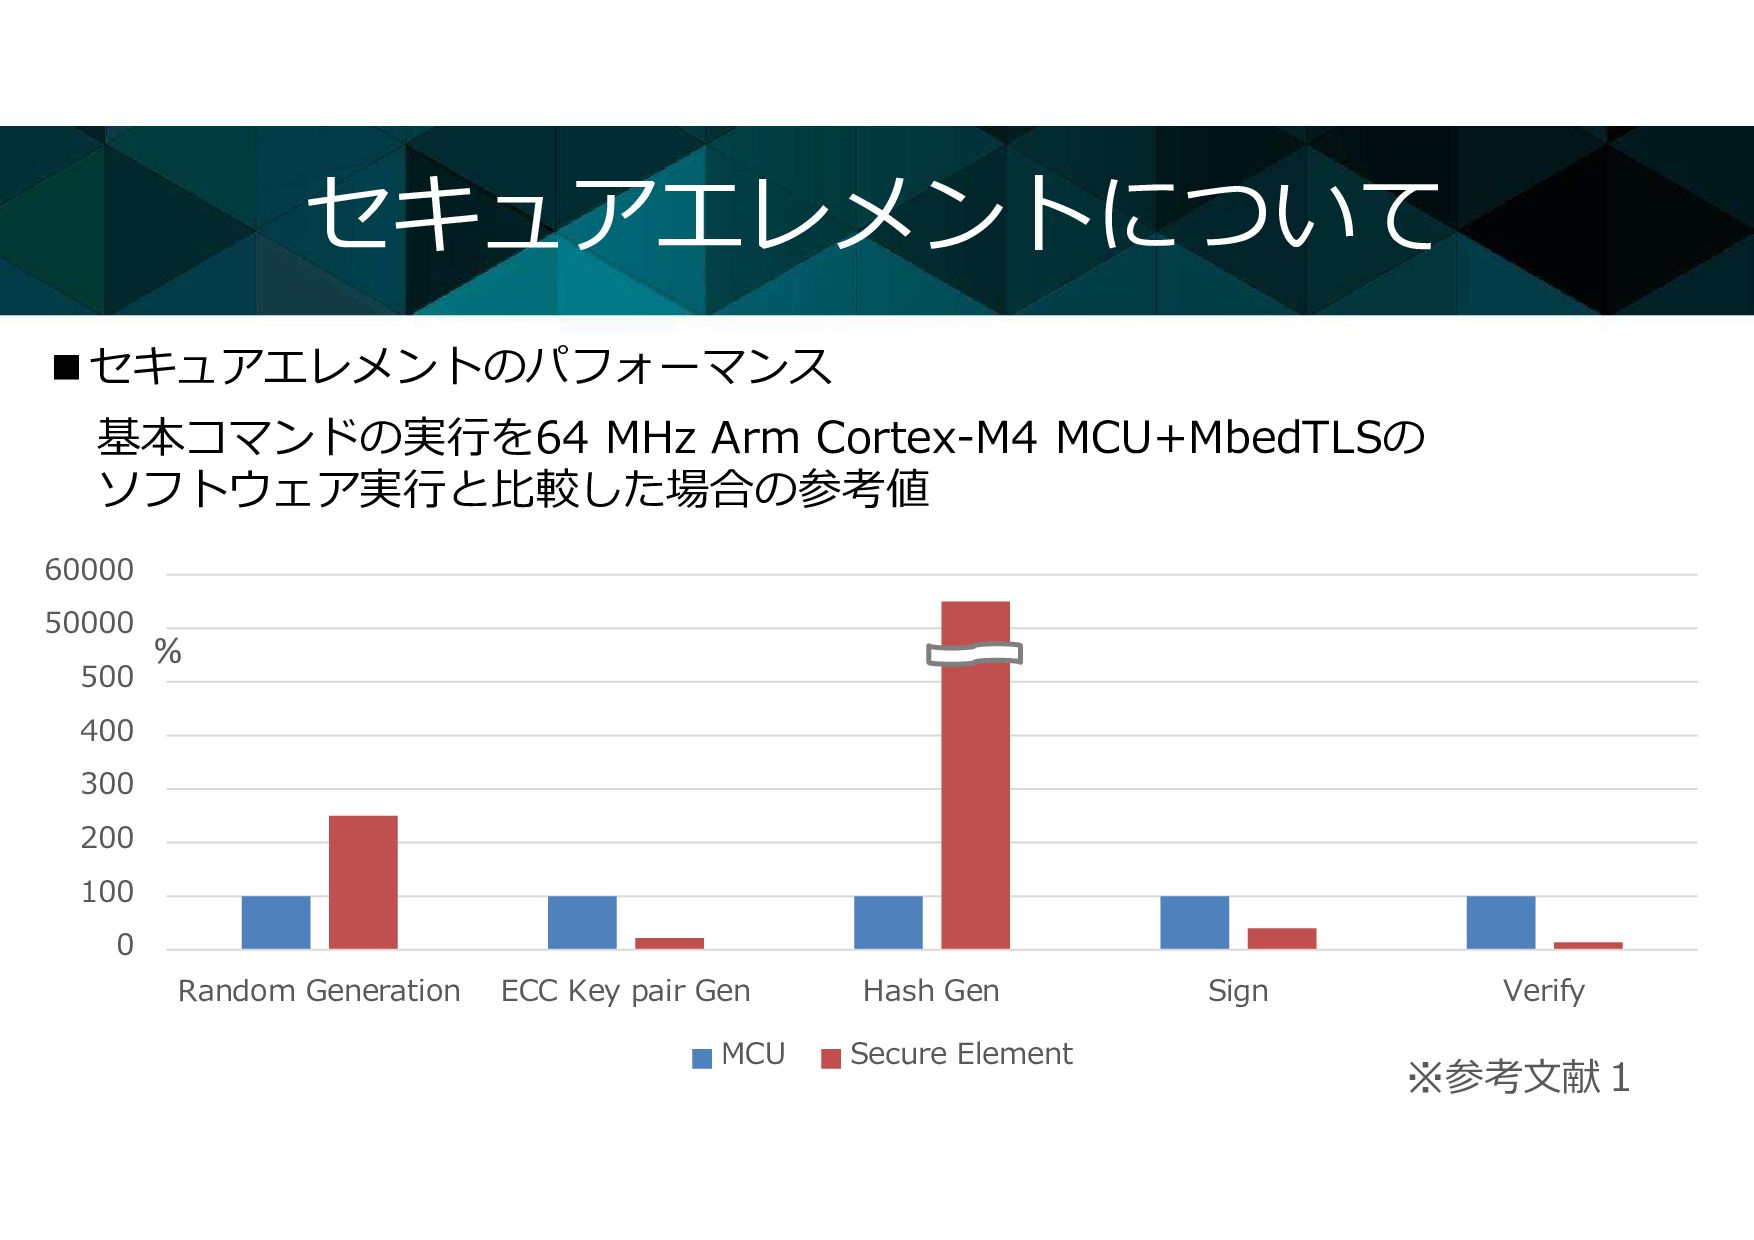
セキュアエレメントについて ▪セキュアエレメントのパフォーマンス 基本コマンドの実行を64 MHz Arm Cortex-M4 MCU+MbedTLSの ソフトウェア実行と比較した場合の参考値 0 100
200 300 400 500 50000 60000 Random Generation ECC Key pair Gen Hash Gen Sign Verify MCU Secure Element % ※参考文献1 -
▪Raspberry Pi 3b+ bullseye 環境を用意 NXP SE050 C1をI2C接続。 (市販品ではMIKROE Plug&Trust
clickが利用可能) $ sudo raspi-configでI2Cを有効 $ i2cdetect –y 1 コマンドで0x48認識を確認 WireGuardのセキュリティ強化 -
▪セキュアエレメントを組み込むイメージ WireGuardのセキュリティ強化 Give the public key to the secure element
to do DH calculation 2nd.DH calc. Static Secret Static Public Pub Pub Ephemeral Public Ephemeral Secret Handshake comm. Static Public Pub Get in advance Static Public for counterpart Pub Static Public for counterpart (get in advance) Pub Static Public for counterpart Pub Ephemeral Secret 3rd.DH calc. Static Public for counterpart Pub Static Secret 4th.DH calc. Static Secret Pub Ephemeral Secret Static Secret for counterpart Ephemeral Public Pub Ephemeral Public 1st.DH calc. Ephemeral Secret Pub Ephemeral Public -
WireGuardのセキュリティ強化 ▪実装のポイント Linux ユーザー空間 wireguard-tools •wg genkeyコマンド 出力される秘密鍵を隠すため、SE050の内部の鍵の保管番号である オブジェクトIDを代わりに出力する この値自体は漏れても問題ない
•wg pubkeyコマンド 上記オブジェクトIDを引数として、SE050から公開鍵を出力する。 -
WireGuardのセキュリティ強化 ▪実装のポイント •noise.c ハンドシェイクを行うコード内で、wg->static_identity.static_private 構造体の中身をSE050の内部の鍵の保管番号であるオブジェクトIDに 変更し、ECDH計算のためこれを呼び出す関数をSE050のAPIに置き換え る。 NXPのPlug&Trustミドルウェアはユーザー空間用なため、カーネル モジュール用にHAL(Hardware Abstraction
Layer)の作成が必要。 コードもカーネル空間用にリライトが必要。 Linux カーネル wireguard カーネルモジュール -
WireGuardのセキュリティ強化 /* Must hold peer->handshake.static_identity->lock */ void wg_noise_precompute_static_static(struct wg_peer *peer)
{ down_write(&peer->handshake.lock); #ifdef USE_SE if (ecdh_calc(peer->handshake.precomputed_static_static, peer->handshake.remote_static,peer->handshake.static_identity->static_private)) memset(peer->handshake.precomputed_static_static, 0, NOISE_PUBLIC_KEY_LEN); if (!peer->handshake.static_identity->has_identity || !crypto_memneq(peer->handshake.precomputed_static_static, curve25519_null_point, CURVE25519_KEY_SIZE)) memset(peer->handshake.precomputed_static_static, 0, NOISE_PUBLIC_KEY_LEN); #else if (!peer->handshake.static_identity->has_identity || !curve25519(peer->handshake.precomputed_static_static, peer->handshake.static_identity->static_private, peer->handshake.remote_static)) memset(peer->handshake.precomputed_static_static, 0, NOISE_PUBLIC_KEY_LEN); #endif up_write(&peer->handshake.lock); } noise.c変更点1 DH calculation 3rd.DH calc. Static Public for counterpart Pub Static Secret -
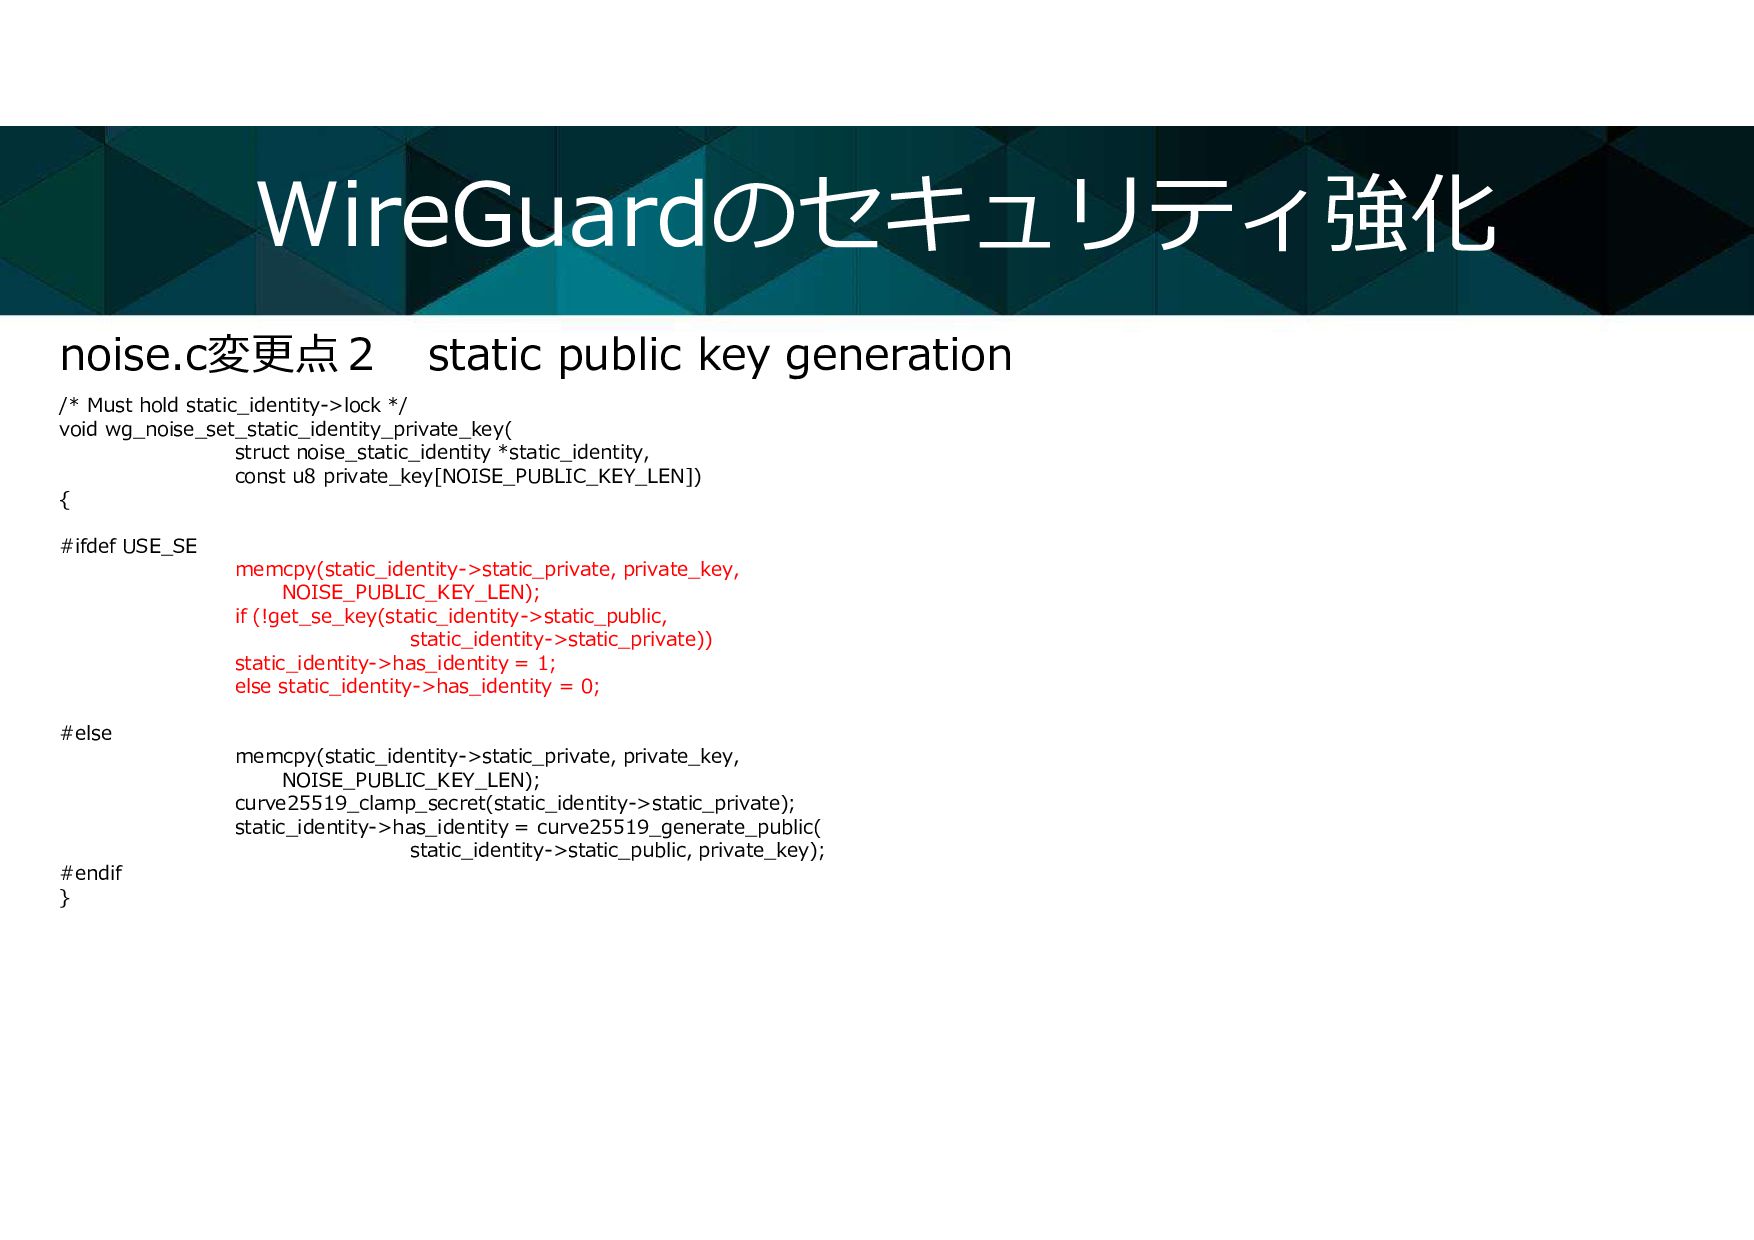
WireGuardのセキュリティ強化 /* Must hold static_identity->lock */ void wg_noise_set_static_identity_private_key( struct noise_static_identity
*static_identity, const u8 private_key[NOISE_PUBLIC_KEY_LEN]) { #ifdef USE_SE memcpy(static_identity->static_private, private_key, NOISE_PUBLIC_KEY_LEN); if (!get_se_key(static_identity->static_public, static_identity->static_private)) static_identity->has_identity = 1; else static_identity->has_identity = 0; #else memcpy(static_identity->static_private, private_key, NOISE_PUBLIC_KEY_LEN); curve25519_clamp_secret(static_identity->static_private); static_identity->has_identity = curve25519_generate_public( static_identity->static_public, private_key); #endif } noise.c変更点2 static public key generation -
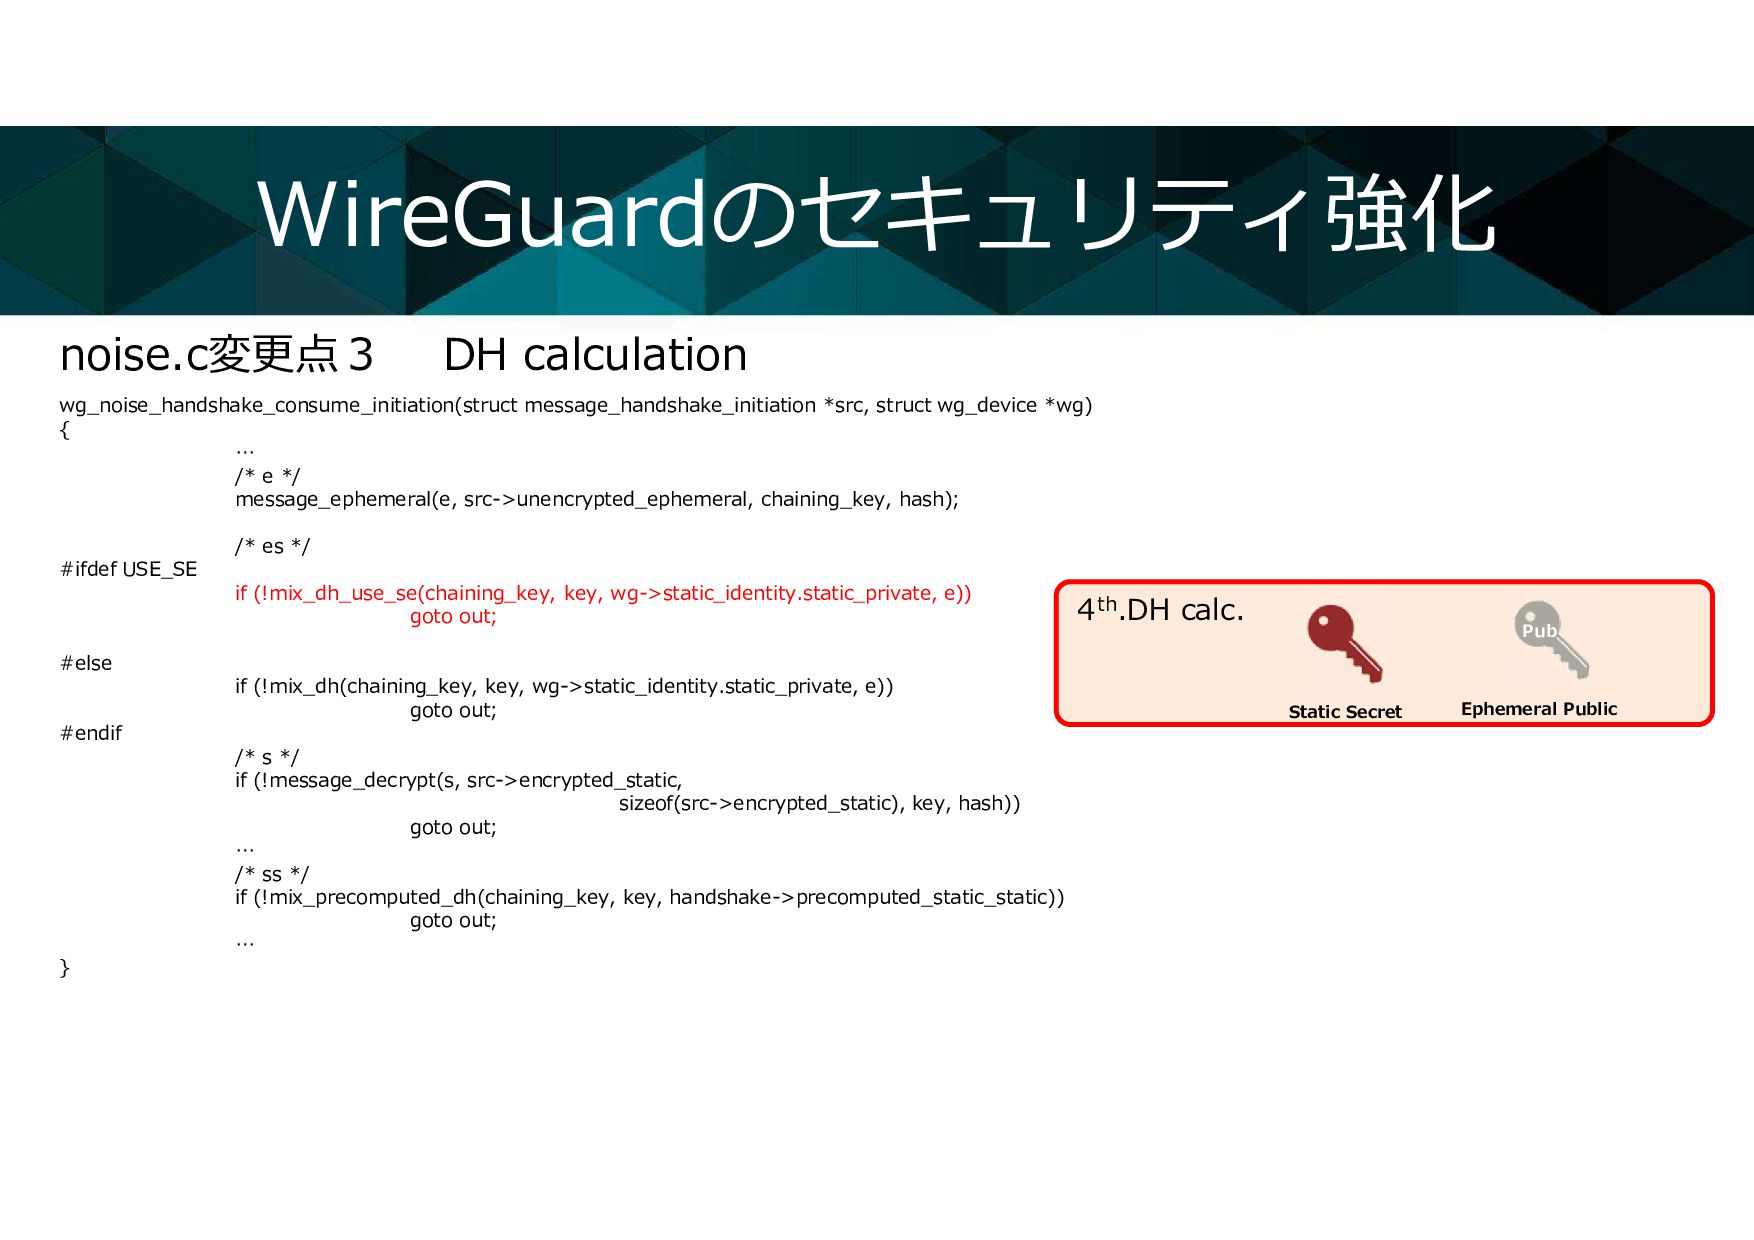
WireGuardのセキュリティ強化 wg_noise_handshake_consume_initiation(struct message_handshake_initiation *src, struct wg_device *wg) { … /*
e */ message_ephemeral(e, src->unencrypted_ephemeral, chaining_key, hash); /* es */ #ifdef USE_SE if (!mix_dh_use_se(chaining_key, key, wg->static_identity.static_private, e)) goto out; #else if (!mix_dh(chaining_key, key, wg->static_identity.static_private, e)) goto out; #endif /* s */ if (!message_decrypt(s, src->encrypted_static, sizeof(src->encrypted_static), key, hash)) goto out; … /* ss */ if (!mix_precomputed_dh(chaining_key, key, handshake->precomputed_static_static)) goto out; … } noise.c変更点3 DH calculation 4th.DH calc. Static Secret Pub Ephemeral Public -
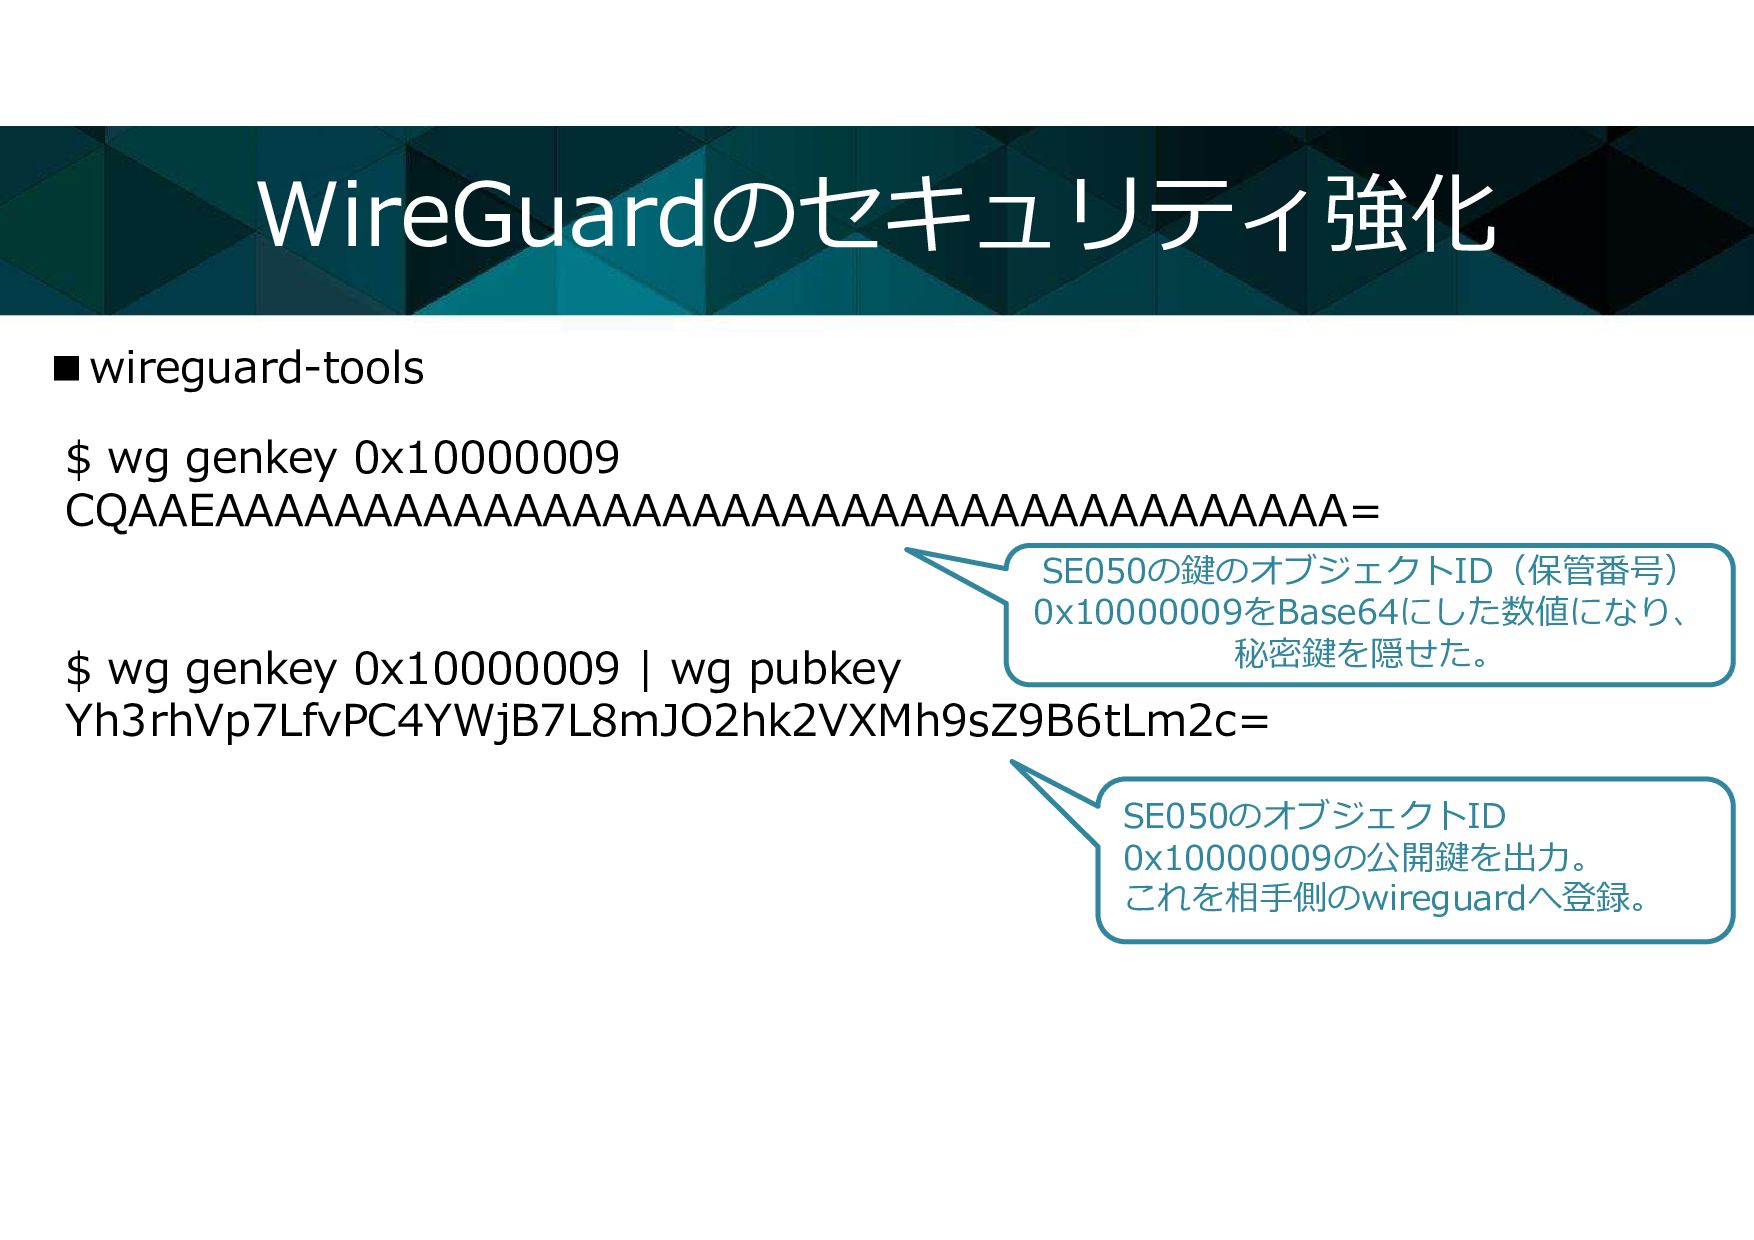
WireGuardのセキュリティ強化 ▪wireguard-tools $ wg genkey 0x10000009 CQAAEAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAA= $ wg genkey
0x10000009 | wg pubkey Yh3rhVp7LfvPC4YWjB7L8mJO2hk2VXMh9sZ9B6tLm2c= SE050の鍵のオブジェクトID(保管番号) 0x10000009をBase64にした数値になり、 秘密鍵を隠せた。 SE050のオブジェクトID 0x10000009の公開鍵を出力。 これを相手側のwireguardへ登録。 -
WireGuardのセキュリティ強化 ▪wireguard $ sudo cat /etc/wireguard/wg0.conf [Interface] PrivateKey = CQAAEAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAA=
Address = 10.0.0.110/32 [Peer] PublicKey = XXXXX= Endpoint = XXX.XXX.XXX.XXX:XXXXX 0x10000009をBase64にした数値を 秘密鍵として登録 相手側の公開鍵を登録 -
WireGuardのセキュリティ強化 ▪キーローテーションを試す。 クライアント側で新しいキー番号で秘密鍵 、公開鍵を作成する。 $ wg genkey 0x10000006 BgAAEAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAA= $
wg genkey 0x10000006 | wg pubkey 9oGFAiGUSMIzg2gzwwEBasjfKxkULebTwzOEjn7K4Rk= -
WireGuardのセキュリティ強化 ▪キーローテーションを試す。 サーバー側で: $ sudo wg set wg0 peer "9oGFAiGUSMIzg2gzwwEBasjfKxkULebTwzOEjn7K4Rk="
allowed-ips 10.0.0.111/32 これを実行したところで接続が切れる。 $ sudo wg set wg0 peer "ChgKBqwSnkov+rcC2KKUQKMgPH9pfrnWXzLpMzfKpg4=" remove IPは現在のIP 現在接続しているピアの公開鍵 -
WireGuardのセキュリティ強化 ▪キーローテーションを試す。 クライアント側で: $ sudo wg-quick down /etc/wireguard/wg0.conf $ sudo
vi /etc/wireguard/wg0.confで以下を変更 ``` [Interface] PrivateKey = BgAAEAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAA= Address = 10.0.0.111/32 ``` $ sudo wg-quick up /etc/wireguard/wg0.conf IPは現在のIP 新しい0x10000006の鍵を指定 -
まとめ セキュアエレメントを用いることで対応できるNISTIR 8259Aの項目 項目 概要 デバイスの識別 IoTデバイスは、論理的にも物理的にも一意に識別できる デバイス構成 IoT デバイスのソフトウェア構成は変更できるが、そのような変更は許可されたエンティ
ティのみが実行できる データ保護 保存、または転送されるデータを未承認のアクセスと変更から保護できる インターフェースへの論理アクセス ローカル・インターフェースおよびネットワーク・インターフェース、ならびにそれらの インターフェースで使用されるプロトコルおよびサービスへの論理アクセスを、許可され たエンティティのみに制限することができる ソフトウェア更新 IoT デバイスのソフトウェアは、安全で構成可能なメカニズムを使用して、承認されたエ ンティティのみが更新できる サイバーセキュリティ状態の認識 IoTデバイスは、そのサイバーセキュリティの状態を報告し、その情報を許可されたエン ティティのみがアクセスできるようにすることができる -
まとめ セキュアエレメントを用いることで対応できるNISTIR 8259Aの項目 項目 概要 データ保護 保存、または転送されるデータを未承認のアクセスと変更から保護できる 1. 標準化された暗号アルゴリズム (認証による暗号化、暗号
ハッシュ、デジタル署名の検証など) に対して明らかに安全な 暗号モジュールを使用して、デバイスの保存および送信データ の機密性と完全性が侵害されるのを防ぐ機能 セキュアエレメントにより、耐タンパ性による保護と、 RFC8410で定められたX25519共有鍵生成を行え、WireGuard VPN接続を行うための秘密鍵の保存、および送信データの機密 性と完全性が侵害されるのを防ぐ 2. 認可されたエンティティが、事前に認可されているかどうか にかかわらず、デバイス上のすべてのデータをすべてのエン ティティがアクセスできないようにする機能 (例: 内部スト レージのワイプ、暗号化されたデータの暗号キーの破壊など) ー 3. デバイス構成機能で使用する構成設定。これには、許可され たエンティティが暗号化の使用自体を構成する機能 (キーの⾧ さの選択など) が含まれますが、これに限定されません。 ー -
参考文献 1,https://www.mdpi.com/2624-831X/3/1/1 Mario Noseda 1,†, Lea Zimmerli 1,† , Tobias
Schläpfer 2,† and Andreas Rüst 1,∗,† 1, Institute of Embedded Systems, Zurich University of Applied Sciences, 8401 Winterthur, Switzerland; [email protected] (M.N.); [email protected] (L.Z.) 2, NatWest Group, NatWest Services (Switzerland) Ltd., 8045 Zuerich, Switzerland; [email protected] Correspondence: [email protected]; Tel.: +41-(0)-58-934-77-01 † These authors contributed equally to this work. CCライセンス 表示 4.0 国際(https://creativecommons.org/licenses/by/4.0/deed.ja)、データカタログサイト利用規約(http://www.data.go.jp) 2,作って理解するWireGuard https://speakerdeck.com/fadis/zuo-tuteli-jie-suruwireguard
 cyberomusubi
 knwoop
 staka121
 takaha4k
 ota1022
 amixedcolor
 _awache
 chmikata
 oracle4engineer
 manabuseki
 timakin
 carta_engineering
 dkduppf
 akademiya2063
 jonoalderson
 jct
 chikuwait
 tammielis
 rmw
 smashingmag
 chrisshort
 axbom
 eileencodes
 lindahogenes
 rasagy