Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
Secure your Web Application
Search
Dheeraj Joshi
July 16, 2016
Technology
6.8k
0
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
Secure your Web Application
Slides from my talk at JSChannel Conference 2016
Dheeraj Joshi
July 16, 2016
Transcript
27 slides
Let’s talk Security Secure your Web Application - Best Practices
Dheeraj Joshi @dheerajhere
• Front-End @ • Previously @ • Open Source (medium-cli)
• Ambidextrous TT Player About Me
More... I wear White Hat. Uber, CKEditor, Dropbox, MailChimp, Recruiterbox,
InVision, DigitalOcean, Intuit, Groupon, etc. What makes me happy?
Agenda • Why ? • Cross-site Scripting (XSS) • Cross-site
Request Forgery (CSRF) • Content Security Policy (CSP) • Useful Headers • Other Best Practices • Live Demo
Why should Startups Care about Security? Startups & SMEs are
known to cut corners. One of the first things they cut is ‘Security'.
None
Github Reused password attack
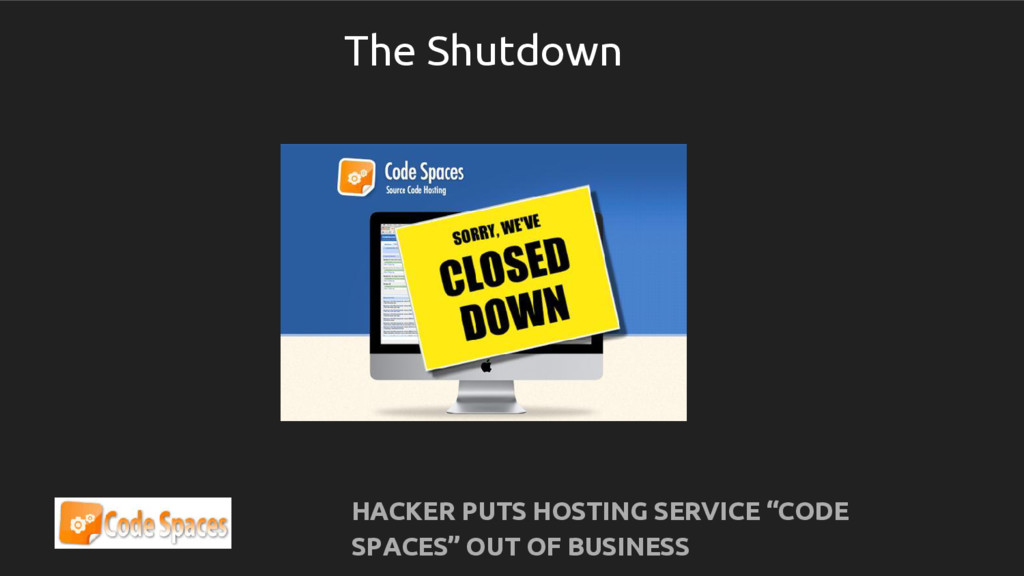
HACKER PUTS HOSTING SERVICE “CODE SPACES” OUT OF BUSINESS The
Shutdown
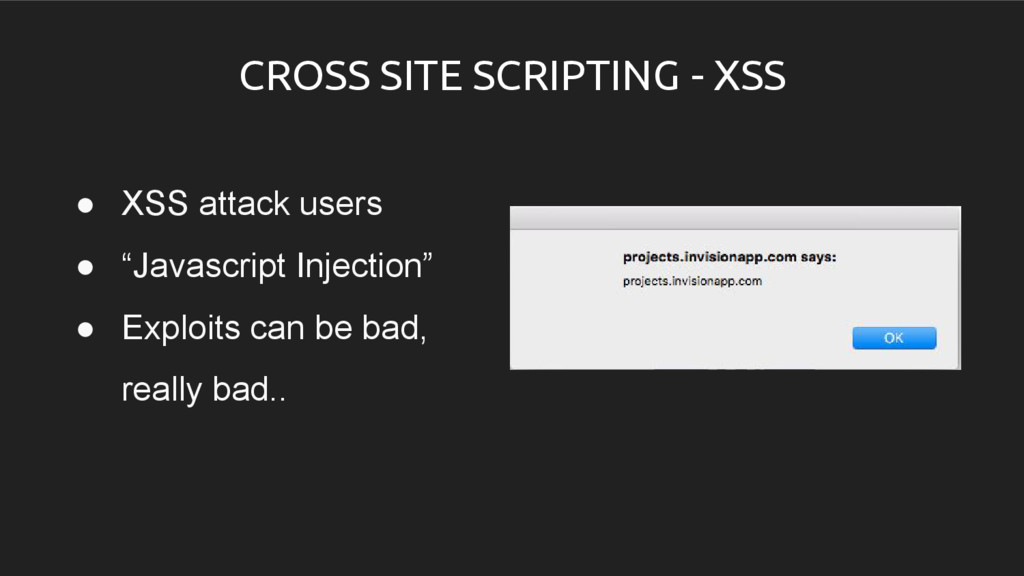
CROSS SITE SCRIPTING - XSS • XSS attack users •
“Javascript Injection” • Exploits can be bad, really bad..
What is XSS? Typical Reflected XSS
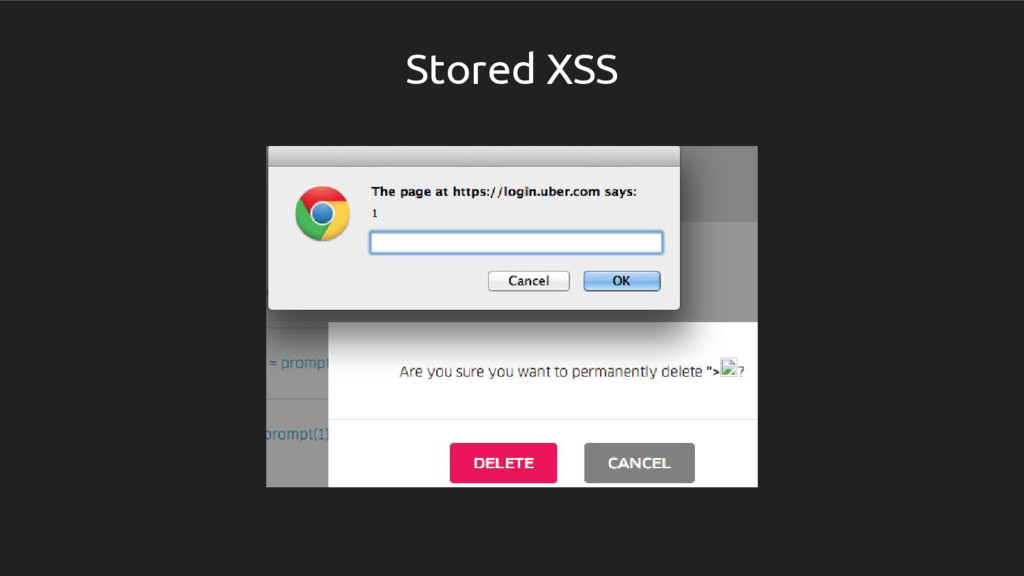
Stored XSS
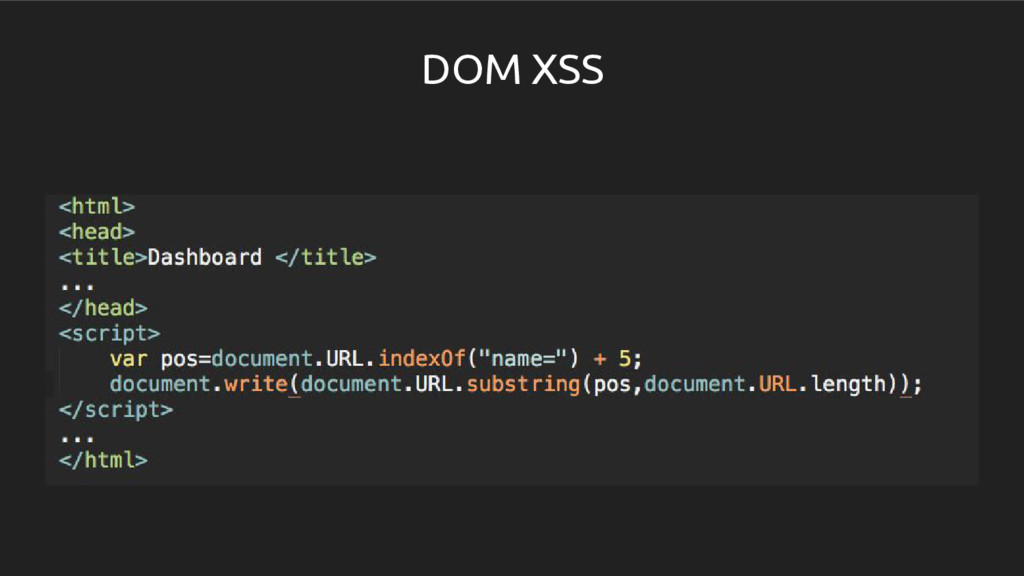
DOM XSS
Protect Yourself • Input Validation • Ensure that outputs are
HTML encoded • Don’t reinvent the wheel (Use proven sanitizers) • Analyze places where DOM elements are created
ngBind attribute $sanitize - service in module ngSanitize Sanitizes an
html string by stripping all potentially dangerous tokens.
• Add HTTPOnly, Secure attributes on Session Cookie
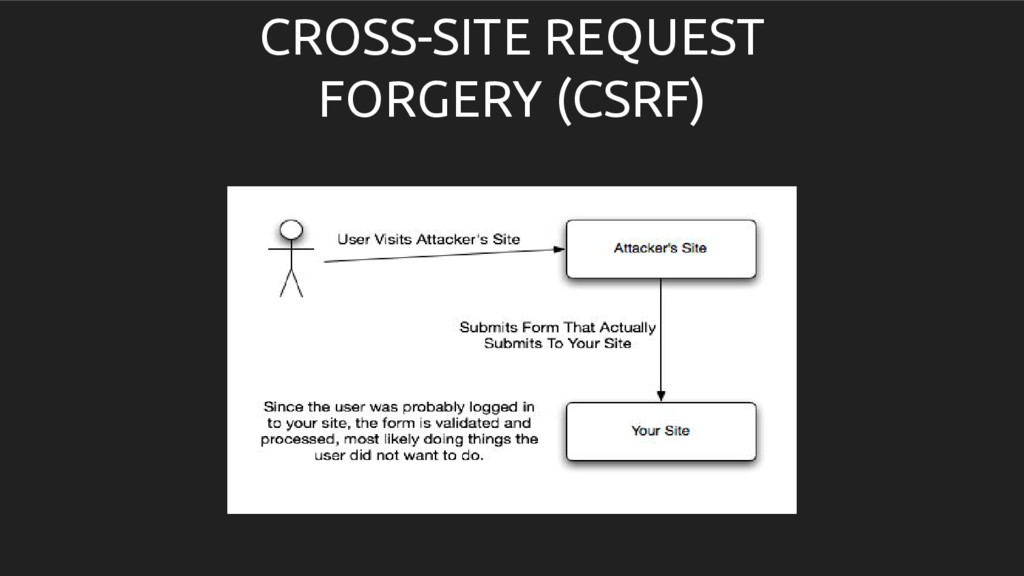
CROSS-SITE REQUEST FORGERY (CSRF)
Because the attack is carried out by the victim, CSRF
can bypass: • HTTP Auth • Session-based auth • Firewalls CSRF Attacks
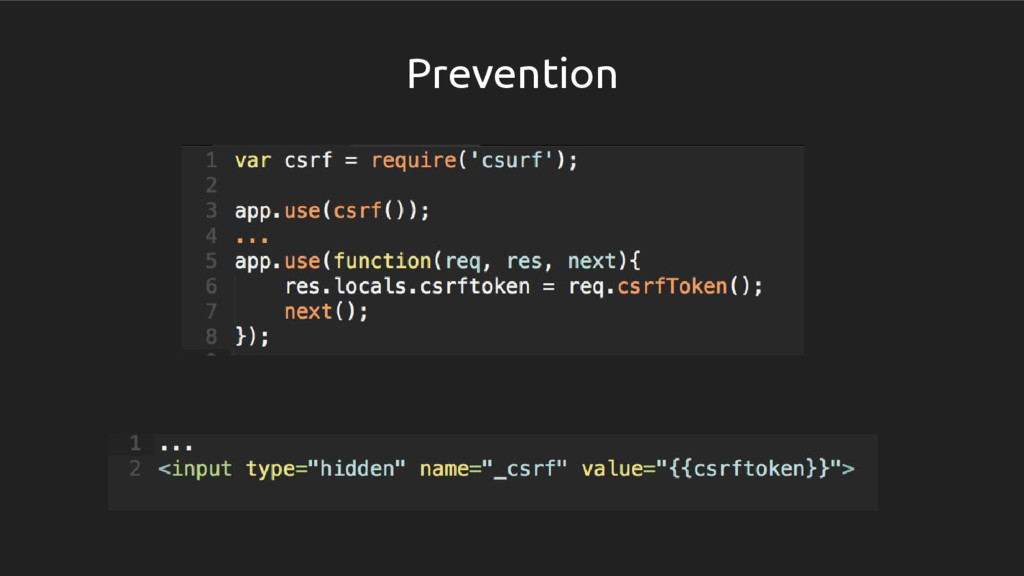
Prevention
• Only accepting POST requests • Referer Protection • Multi-Step
Transactions • URL Rewriting • application/json “CSRF Myths” Preventions that Won’t work
XSS + CSRF =
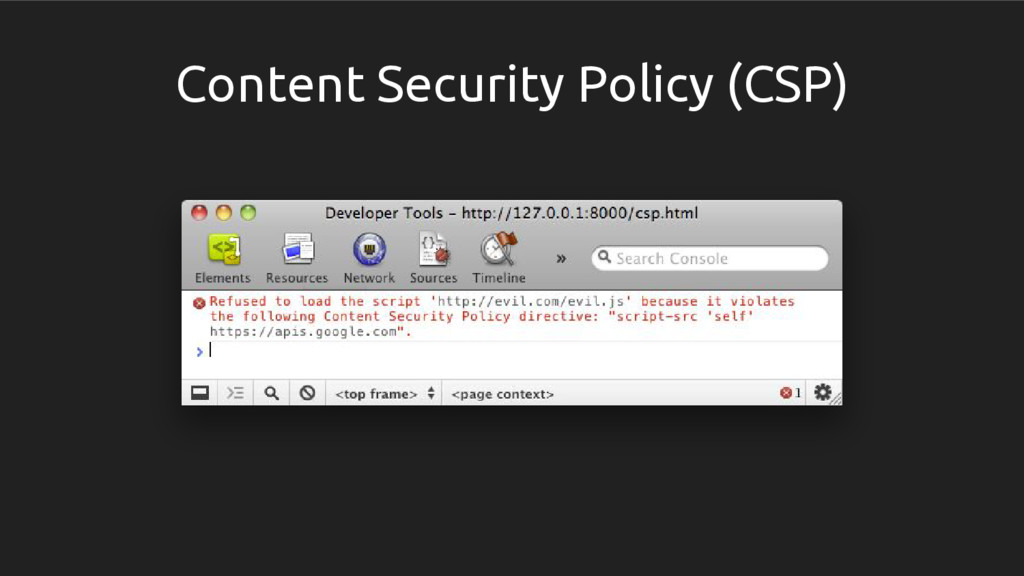
Content Security Policy (CSP)
List of useful HTTP headers • Strict-Transport-Security: max-age=16070400; includeSubDomains •
X-Frame-Options: deny • X-XSS-Protection: 1; mode=block
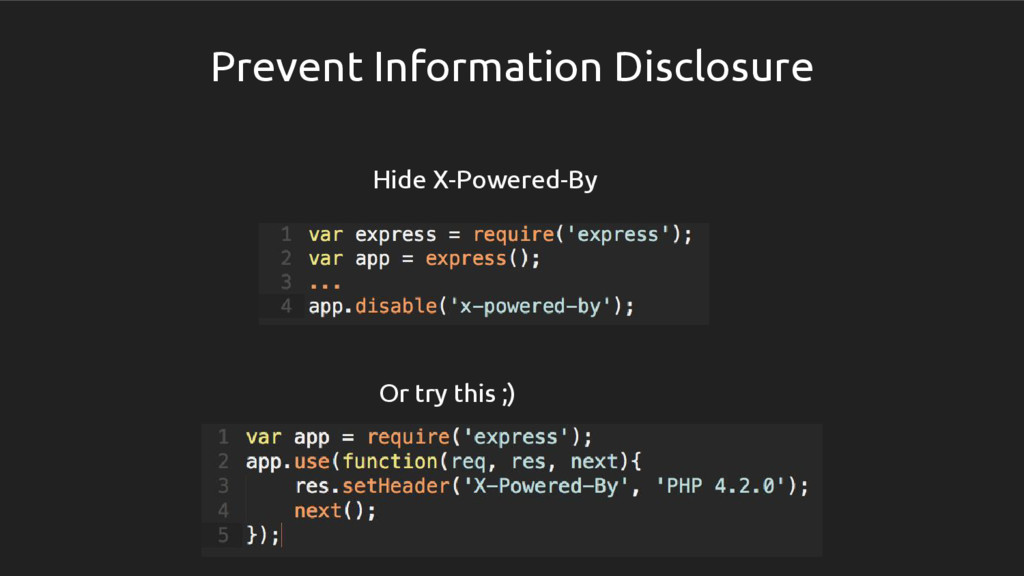
Prevent Information Disclosure Hide X-Powered-By Or try this ;)
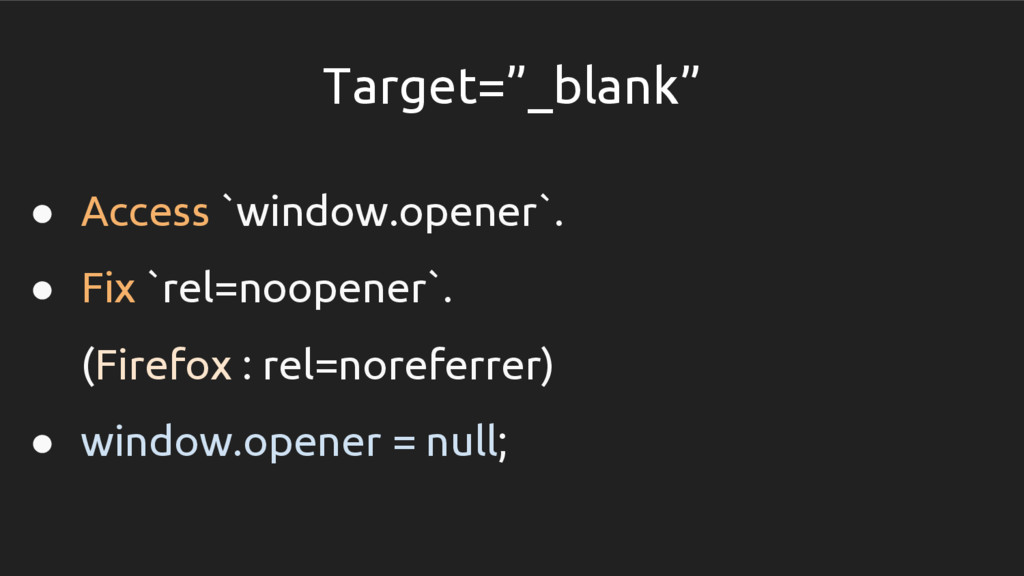
Target=”_blank” • Access `window.opener`. • Fix `rel=noopener`. (Firefox : rel=noreferrer)
• window.opener = null;
How to improve ? • SECURITY.md • Security audits •
Discuss Vulnerabilities
Show Time !
Thank you @dheerajhere @djadmin
More Decks by Dheeraj Joshi
See All by Dheeraj Joshi
Beyond Scanning
djadmin
0
520
Let's talk Security
djadmin
0
7.7k
Other Decks in Technology
See All in Technology
「AIチャットからもできないの?」と言われたら ~業務アプリをMCP対応するときの認証・認可の勘所
oidfj
0
340
Gov-JAWS#9 統合監視機能のマネージドサービス化+AIによる障害時自動調査
fj_yoshimura_kosuke
0
150
サボる子はいねぇがー!AgentCoreハーネスの脆弱性に学ぶ、エージェントの入力バリデーション
iwamot
PRO
5
350
AWS基盤改善を支える 私たちの理念と行動指針
kentosuzuki
0
230
Sonnetだけで業務はまわる?
kintotechdev
1
130
AWS Quick 入門 | 目指せ Quick マスター 01
inariku
PRO
2
350
Linuxネットワークスタック進化の軌跡: 過去10年の歩みと最新トレンド
orimanabu
4
710
高品質と高スピードを支える品質のシフトレフトのアプローチ
goyoki
4
1.3k
並列度を下げたら速くなった — go build の重複コンパイルを実測で見る
tomoaki25
2
1.3k
アラートを見直していたら営業組織への理解にちょっとだけ繋がった話
z63d
1
200
_マネジメントする人される人ナイト_2026__良いチームを作っていきたい_お気持ち_.pdf
xkxaxkx
0
570
属人化したISMS運用をGitHubとAIで仕組み化した1年間の記録
sioncojp
4
2.7k
Featured
See All Featured
Highjacked: Video Game Concept Design
rkendrick25
PRO
2
570
Design and Strategy: How to Deal with People Who Don’t "Get" Design
morganepeng
133
20k
The Curious Case for Waylosing
cassininazir
1
610
The Art of Delivering Value - GDevCon NA Keynote
reverentgeek
16
2.2k
Navigating Team Friction
lara
192
16k
How To Speak Unicorn (iThemes Webinar)
marktimemedia
1
640
Music & Morning Musume
bryan
48
7.5k
JavaScript: Past, Present, and Future - NDC Porto 2020
reverentgeek
52
6.2k
svc-hook: hooking system calls on ARM64 by binary rewriting
retrage
2
680
HTML-Aware ERB: The Path to Reactive Rendering @ RubyCon 2026, Rimini, Italy
marcoroth
6
930
How to Build an AI Search Optimization Roadmap - Criteria and Steps to Take #SEOIRL
aleyda
1
2.3k
AI in Enterprises - Java and Open Source to the Rescue
ivargrimstad
0
1.6k


 djadmin
 oidfj
 fj_yoshimura_kosuke
 iwamot
 kentosuzuki
 kintotechdev
 inariku
 orimanabu
 goyoki
 tomoaki25
 z63d
 xkxaxkx
 sioncojp
 rkendrick25
 morganepeng
 cassininazir
 reverentgeek
 lara
 marktimemedia
 bryan
 retrage
 marcoroth
 aleyda
 ivargrimstad