Share
Embed
Simple, Scalable, Secure networking for Kubernetes
Presented at the Kubernetes Cologne meetup, sponsored by Rewe Digital.
Ed Harrison
March 15, 2016
Transcript
44 slides
-
@projectcalico Project Calico is sponsored by Sponsored by SIMPLE, SCALABLE,
SECURE NETWORKING FOR KUBERNETES KUBERNETES COLOGNE MEETUP Ed Harrison @eepyaich 15th March 2016 -
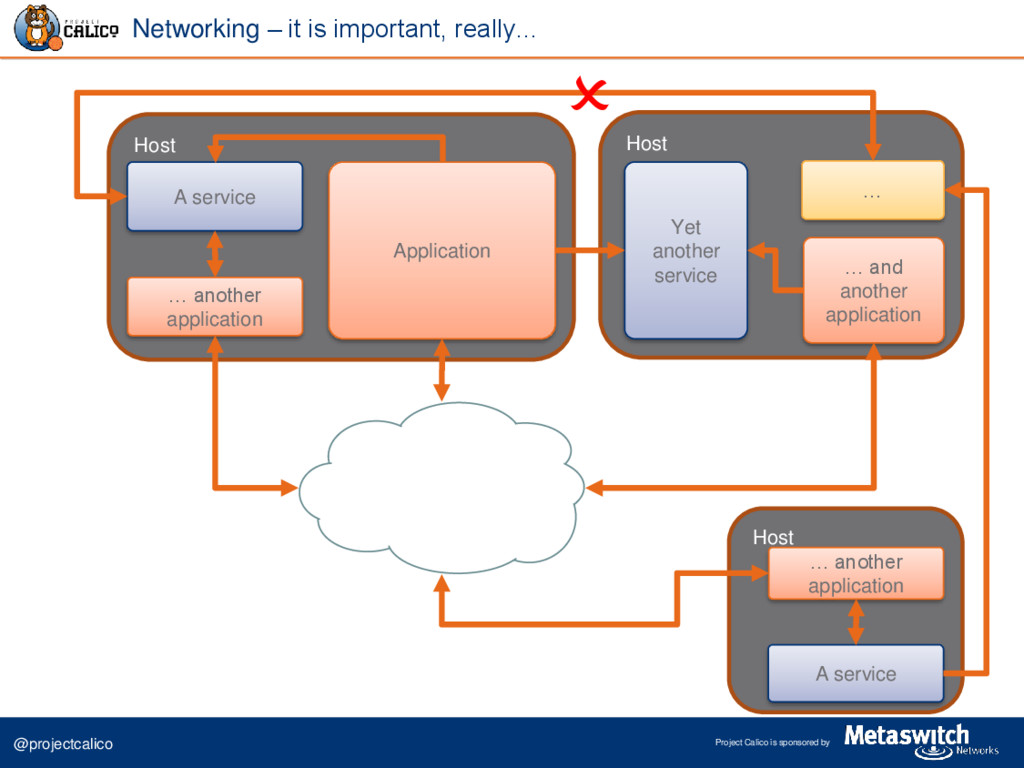
@projectcalico Project Calico is sponsored by Host Host Networking –
it is important, really… Application A service Host Yet another service … and another application … … another application A service … another application -
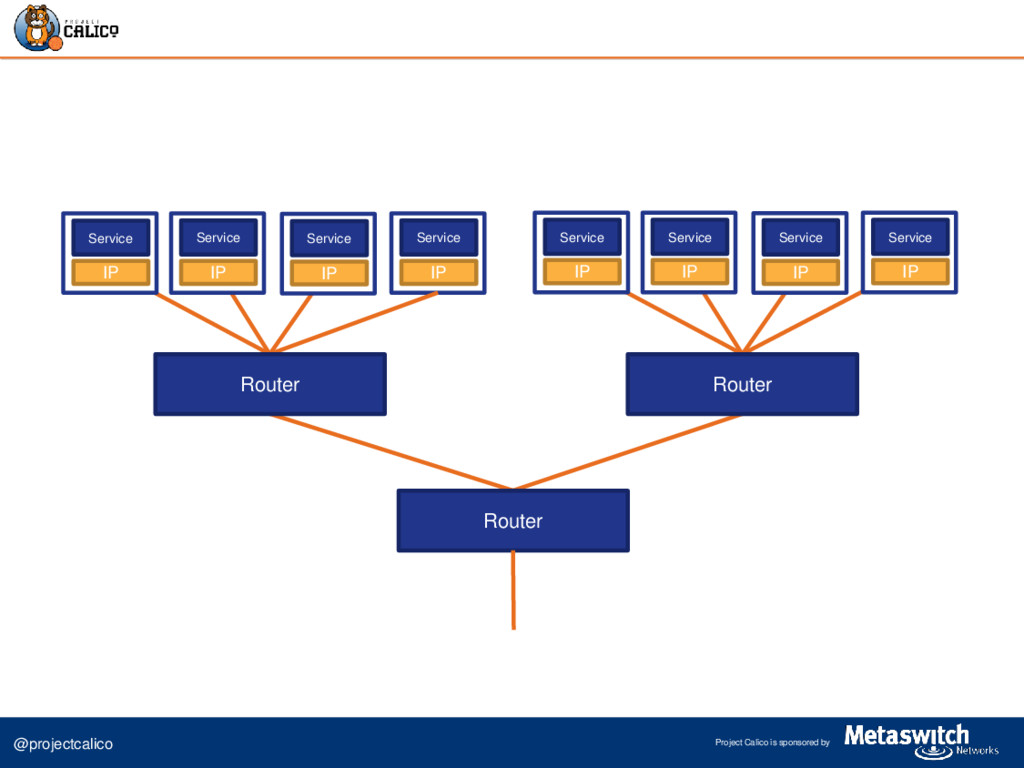
@projectcalico Project Calico is sponsored by IP Service Router Router
Router IP Service IP Service IP Service IP Service IP Service IP Service IP Service -
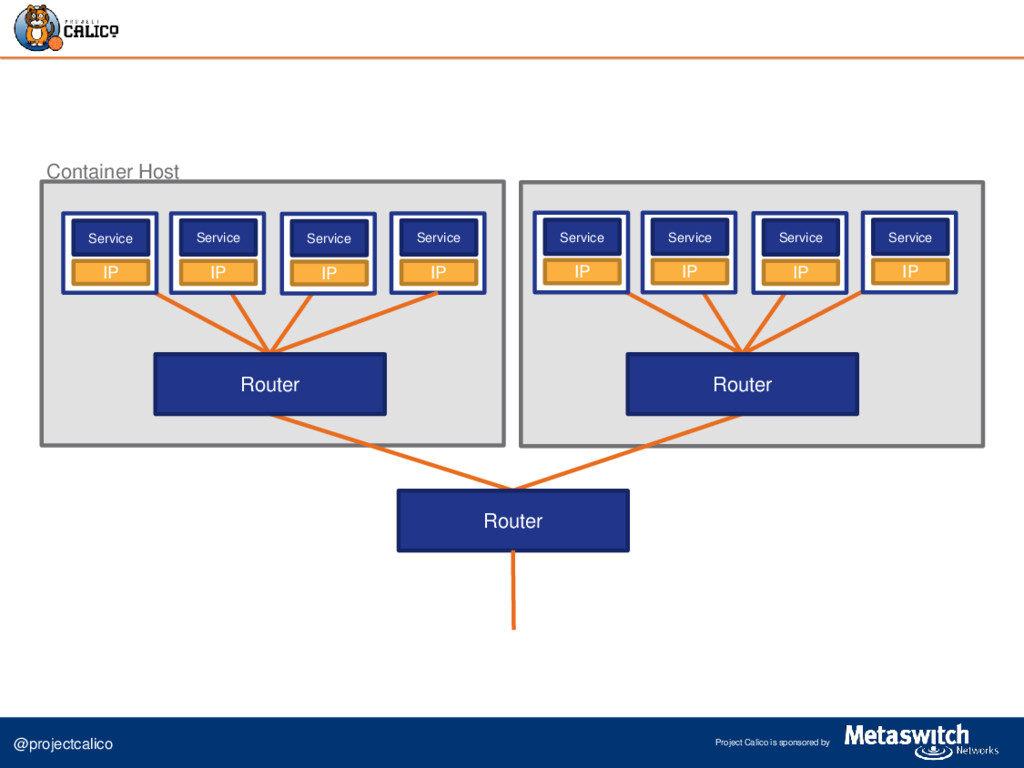
@projectcalico Project Calico is sponsored by IP Service Router Router
Router IP Service IP Service IP Service IP Service IP Service IP Service IP Service Container Host -
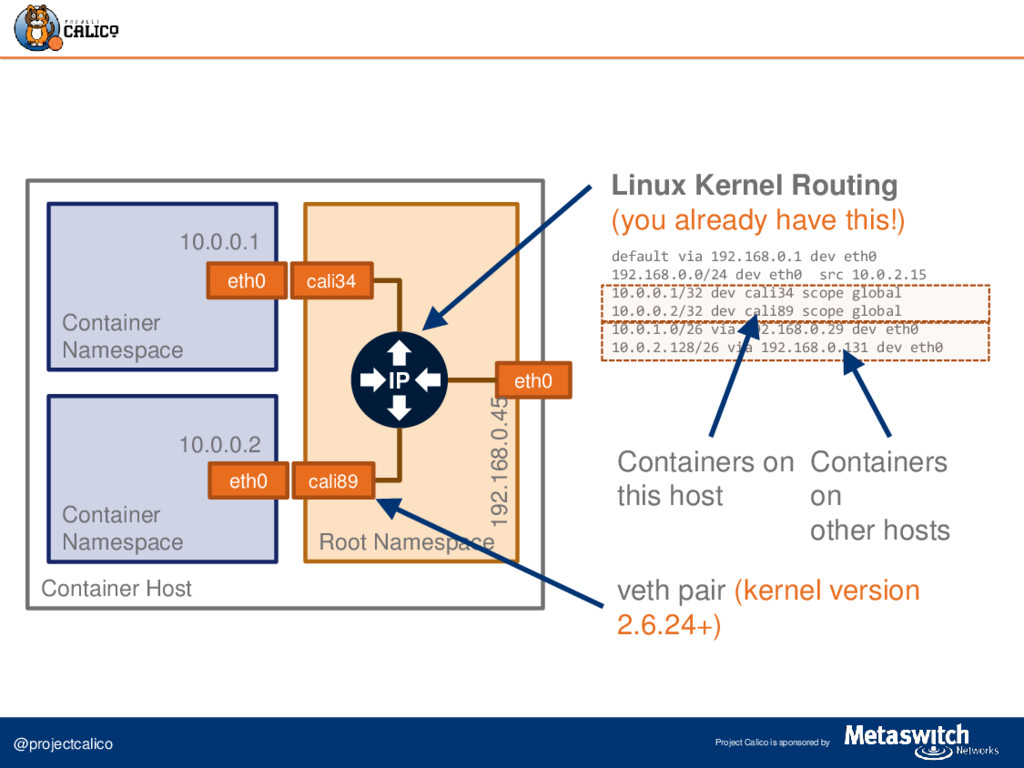
@projectcalico Project Calico is sponsored by Container Host Container Namespace
Root Namespace Container Namespace eth0 eth0 192.168.0.45 10.0.0.1 eth0 10.0.0.2 IP Linux Kernel Routing (you already have this!) default via 192.168.0.1 dev eth0 192.168.0.0/24 dev eth0 src 10.0.2.15 10.0.0.1/32 dev cali34 scope global 10.0.0.2/32 dev cali89 scope global 10.0.1.0/26 via 192.168.0.29 dev eth0 10.0.2.128/26 via 192.168.0.131 dev eth0 veth pair (kernel version 2.6.24+) Containers on other hosts Containers on this host cali34 cali89 -
@projectcalico Project Calico is sponsored by FBI director James Comey
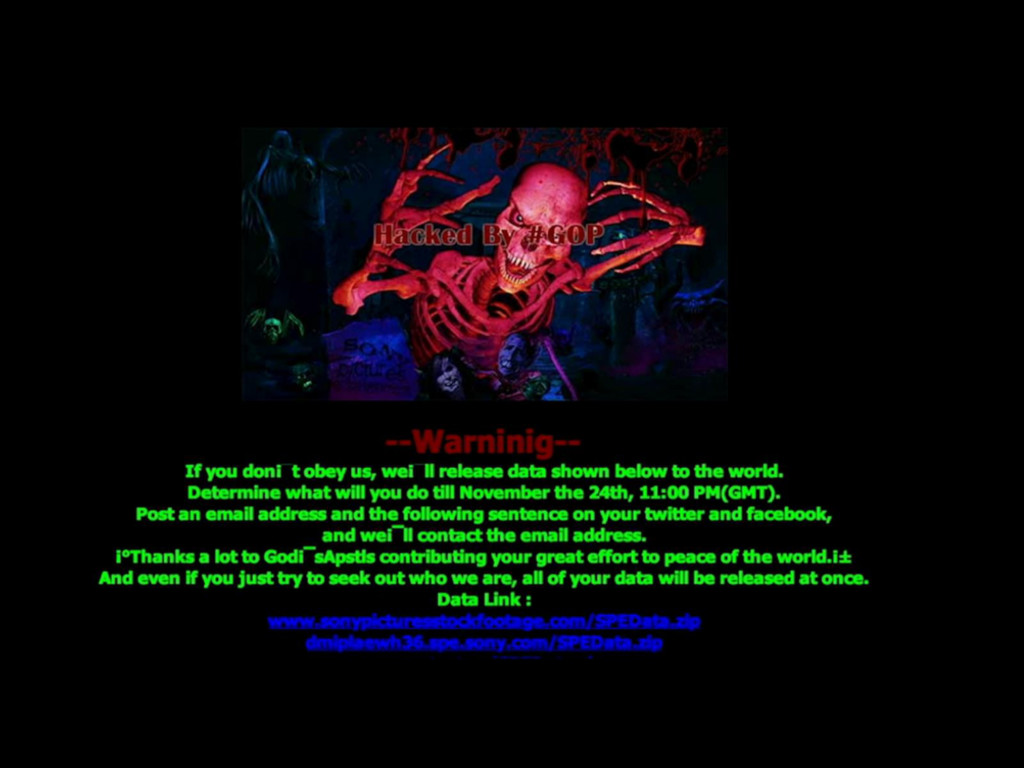
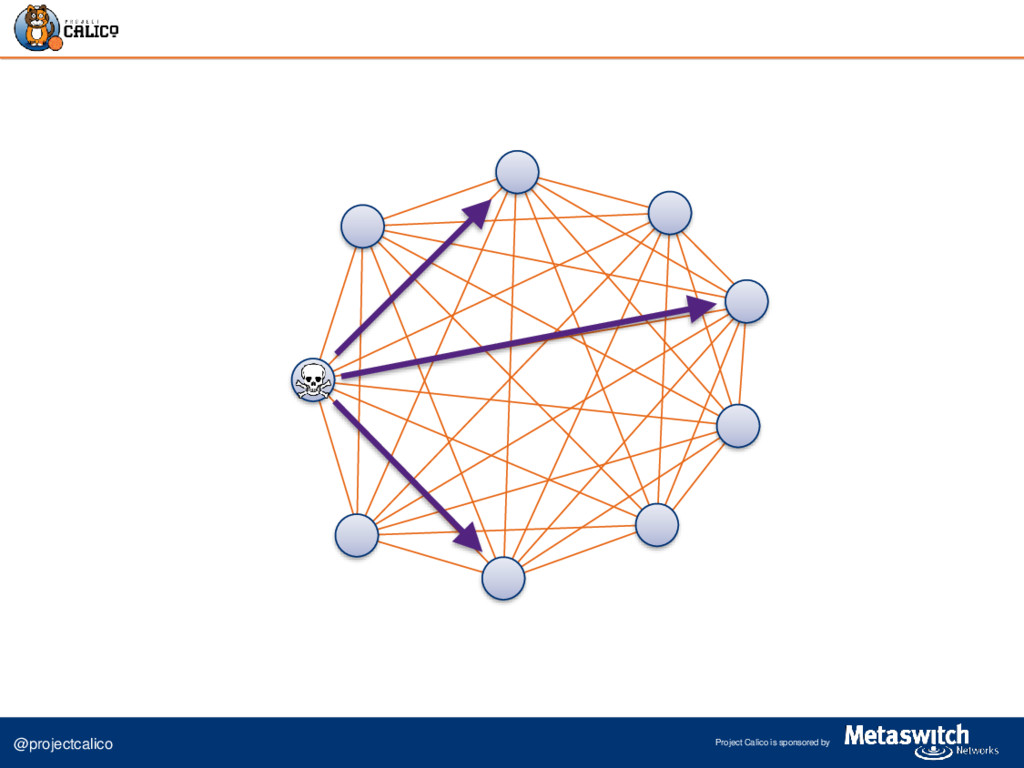
has said he believes Sony’s cyberattackers first breached the studio’s network in September, gaining access through a common tactic called “spear phishing”—duping an employee into clicking on an email attachment or a web link. …For more than two months Sony’s hackers roamed freely, identifying what they wanted to steal. This was possible because the studio, with few exceptions, didn’t segregate or provide extra security for even its most precious secrets. In effect, once the invaders made it past the network gates they could go anywhere they wanted because Sony hadn’t locked any doors. Inside the Hack of the Century by Peter Elkind, Fortune.com -
@projectcalico Project Calico is sponsored by Designing Policy for Kubernetes
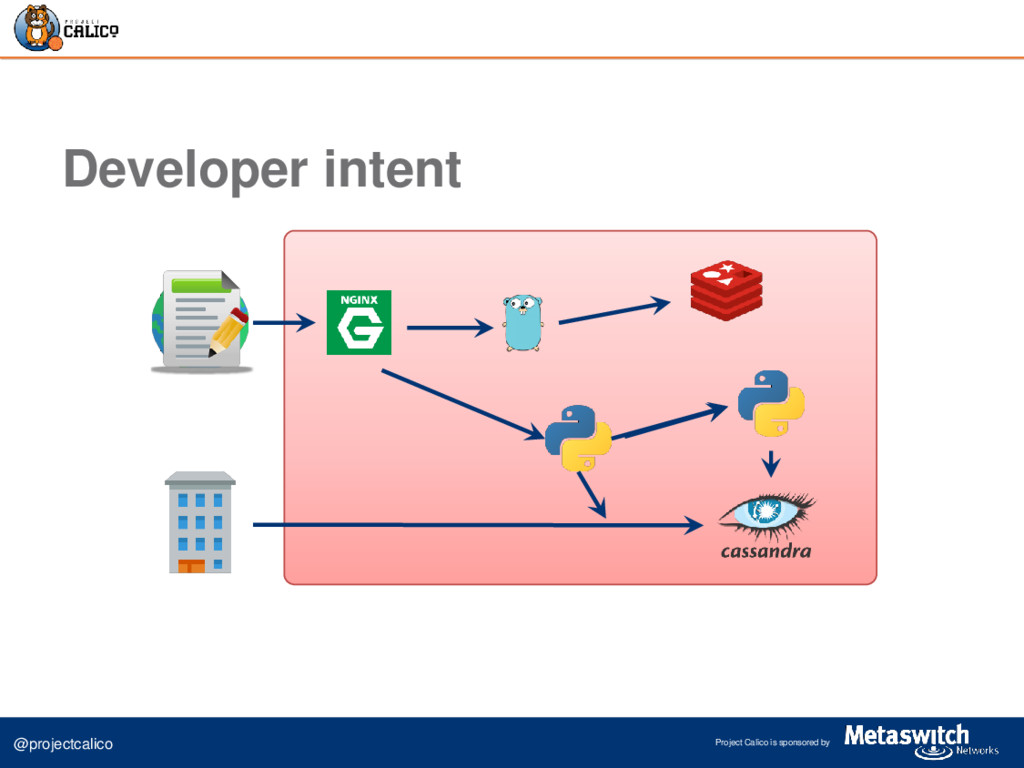
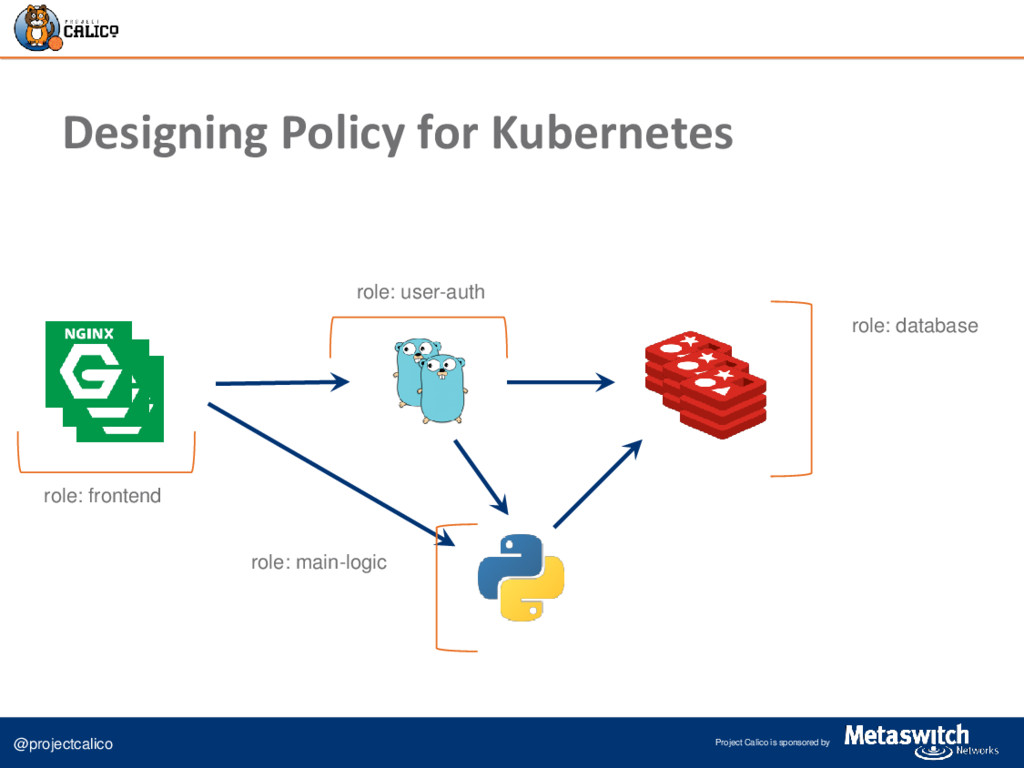
role: frontend role: user-auth role: main-logic role: database -
@projectcalico Project Calico is sponsored by Designing Policy for Kubernetes
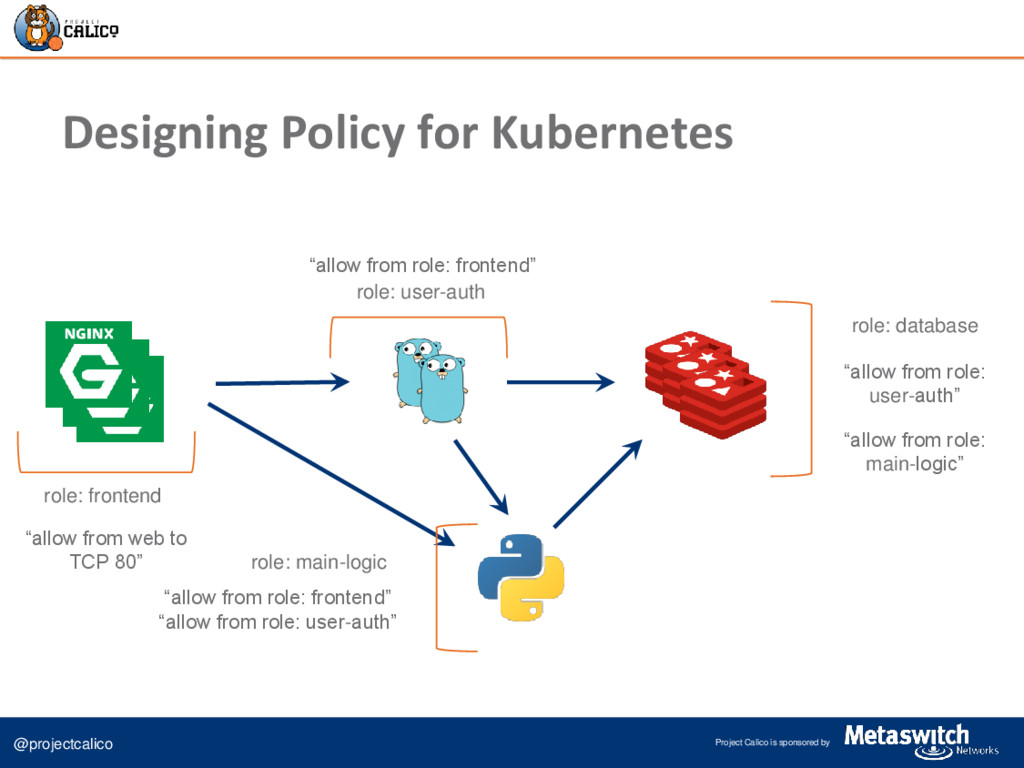
role: frontend role: user-auth role: main-logic role: database “allow from web to TCP 80” “allow from role: frontend” “allow from role: user-auth” “allow from role: user-auth” “allow from role: main-logic” “allow from role: frontend” -
@projectcalico Project Calico is sponsored by Designing Policy for Kubernetes
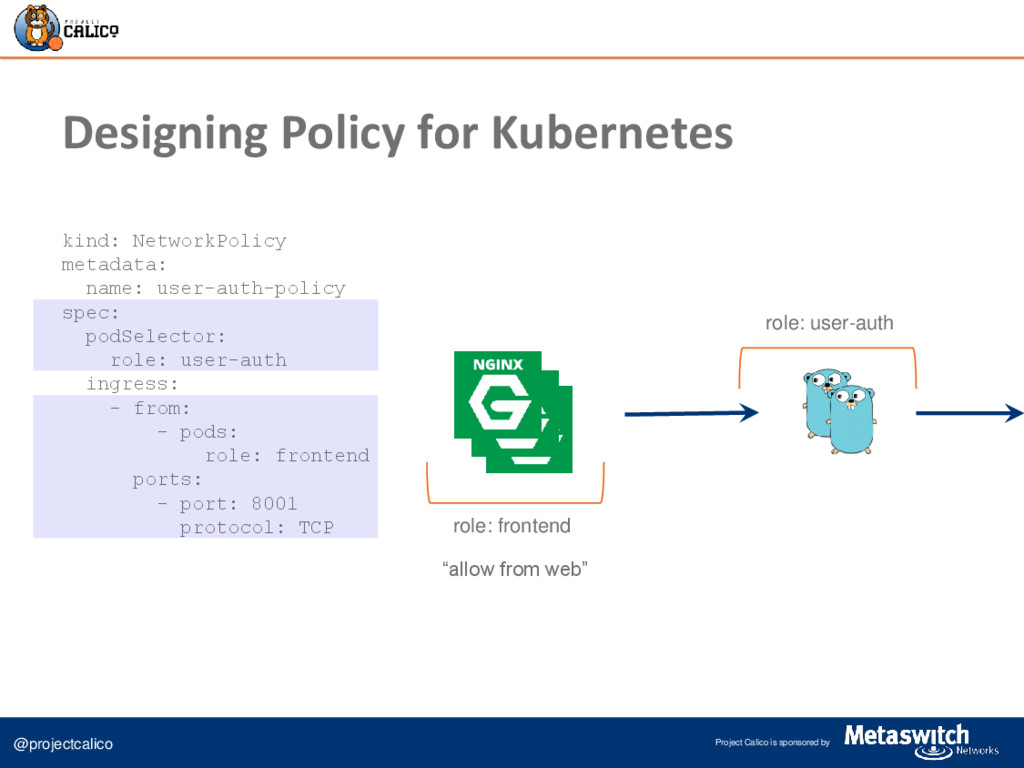
kind: NetworkPolicy metadata: name: user-auth-policy spec: podSelector: role: user-auth ingress: - from: - pods: role: frontend ports: - port: 8001 protocol: TCP role: frontend role: user-auth “allow from web” -
@projectcalico Project Calico is sponsored by Container Host Container Namespace
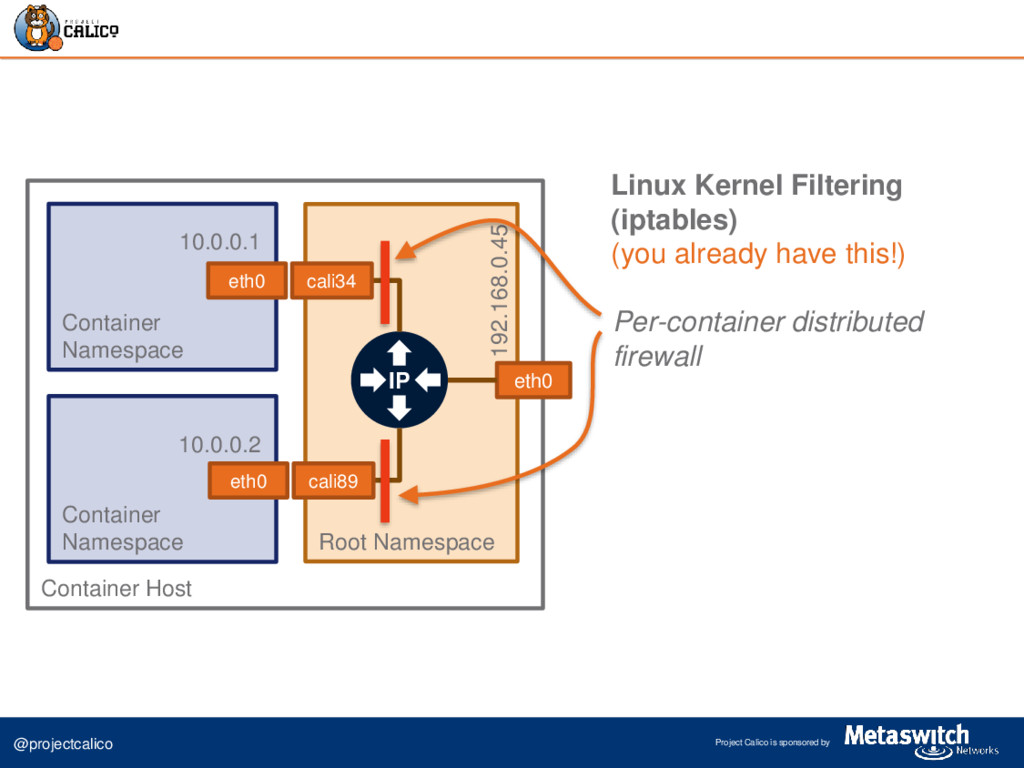
Root Namespace Container Namespace eth0 eth0 192.168.0.45 10.0.0.1 eth0 10.0.0.2 IP Linux Kernel Filtering (iptables) (you already have this!) Per-container distributed firewall cali34 cali89 -
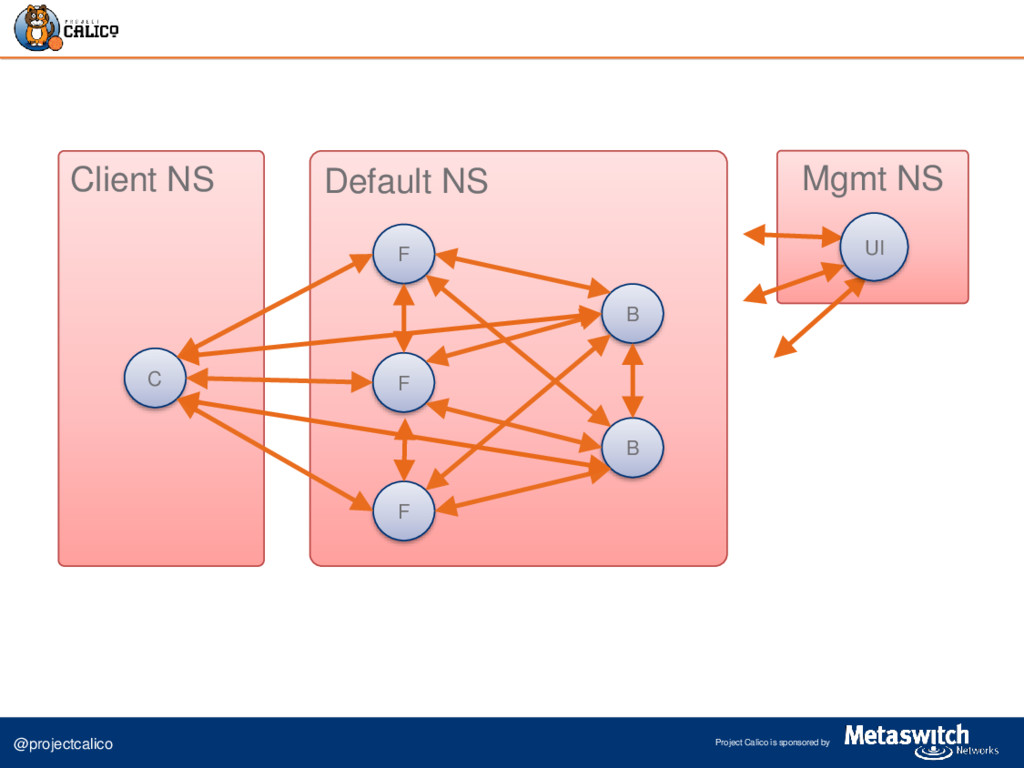
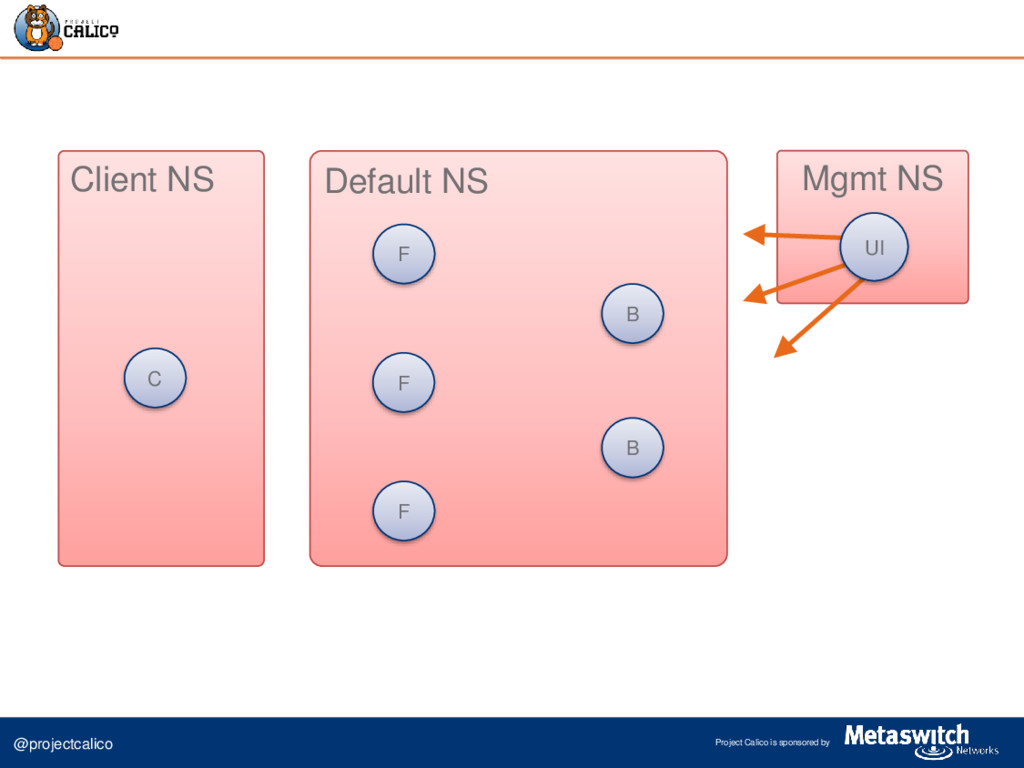
@projectcalico Project Calico is sponsored by Client NS Default NS
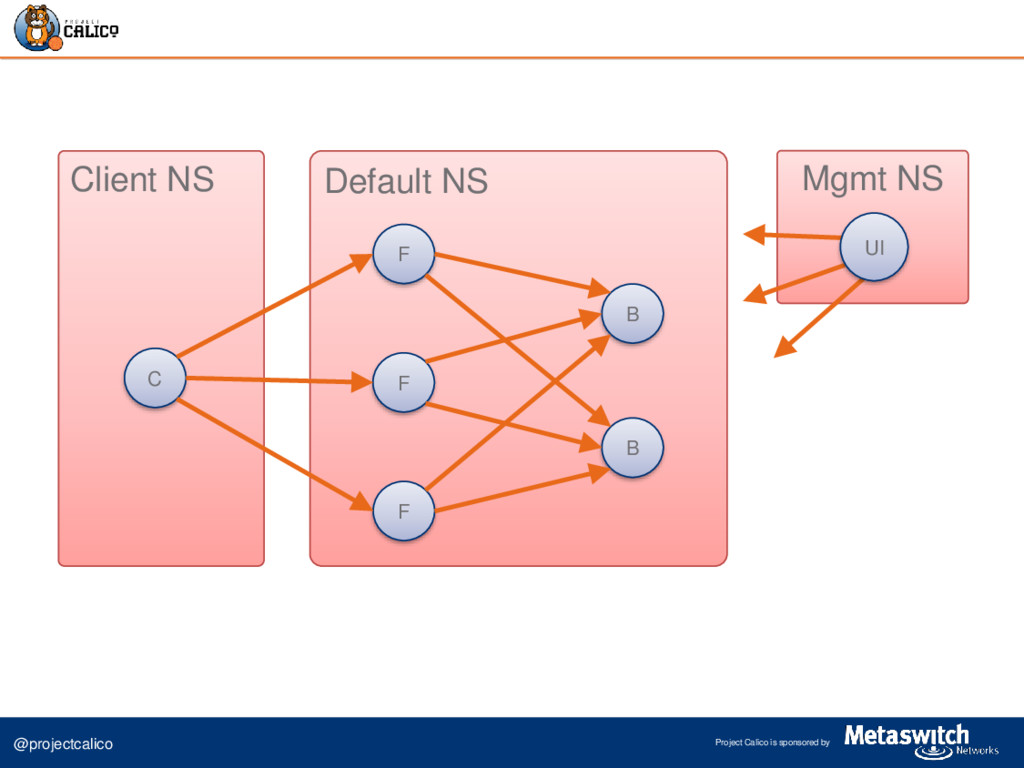
Mgmt NS F C B F B F UI -
@projectcalico Project Calico is sponsored by Client NS Default NS
Mgmt NS F C B F B F UI -
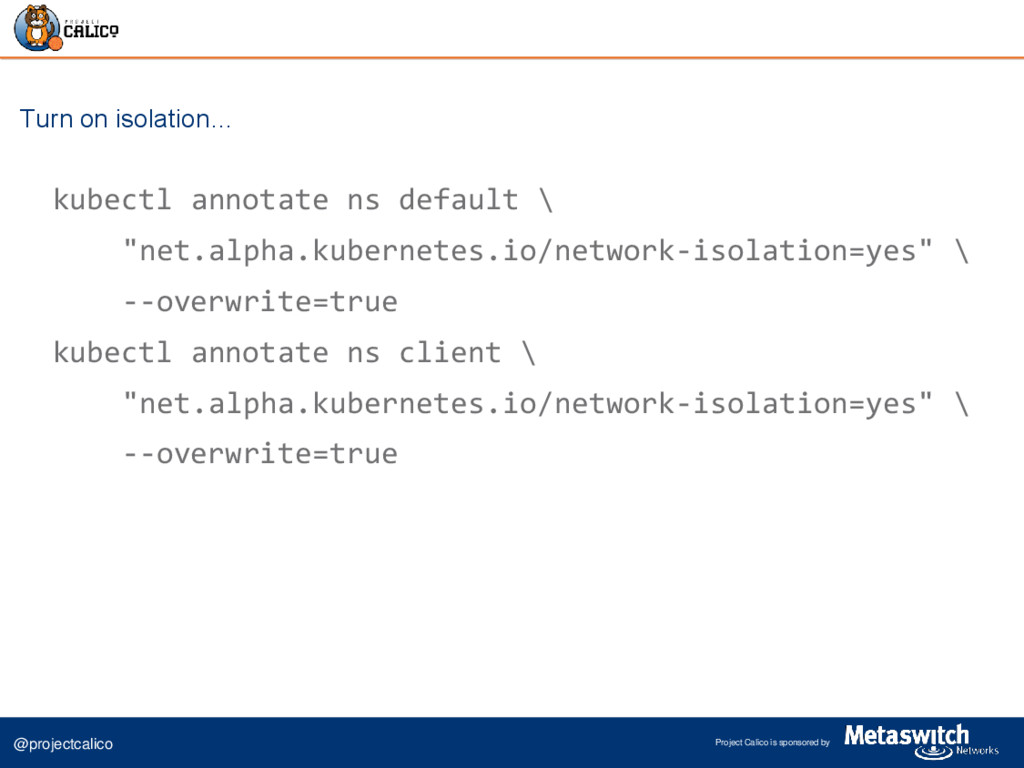
@projectcalico Project Calico is sponsored by kubectl annotate ns default
\ "net.alpha.kubernetes.io/network-isolation=yes" \ --overwrite=true kubectl annotate ns client \ "net.alpha.kubernetes.io/network-isolation=yes" \ --overwrite=true Turn on isolation… -
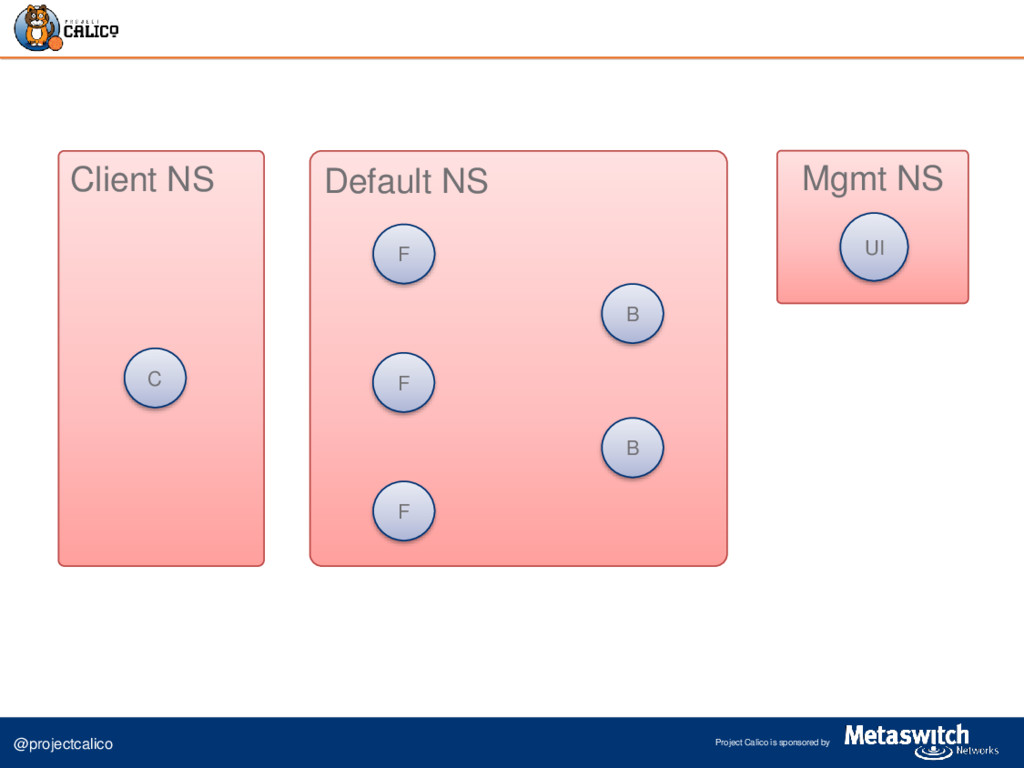
@projectcalico Project Calico is sponsored by Client NS Default NS
Mgmt NS F C B F B F UI -
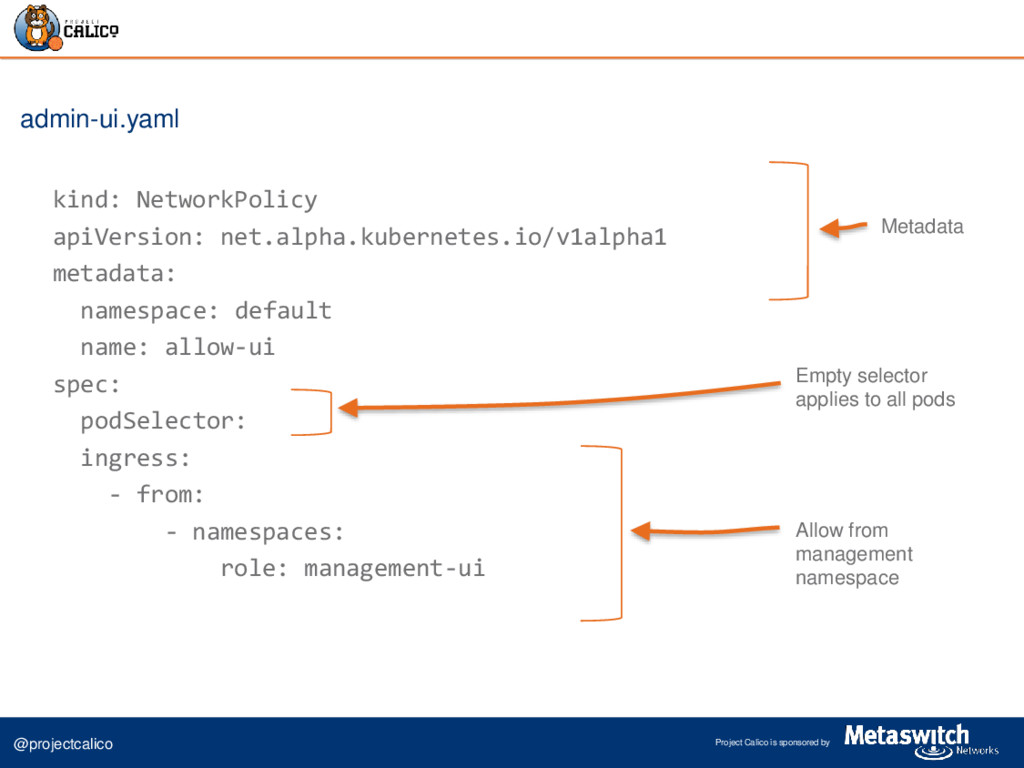
@projectcalico Project Calico is sponsored by kind: NetworkPolicy apiVersion: net.alpha.kubernetes.io/v1alpha1
metadata: namespace: default name: allow-ui spec: podSelector: ingress: - from: - namespaces: role: management-ui admin-ui.yaml Metadata Empty selector applies to all pods Allow from management namespace -
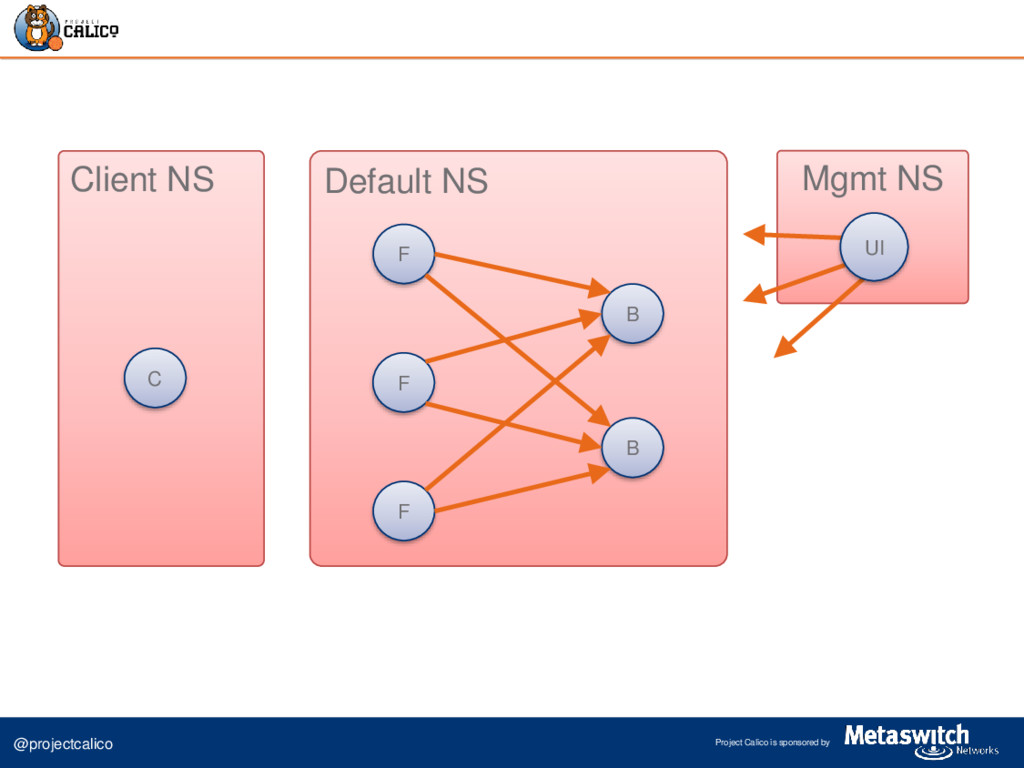
@projectcalico Project Calico is sponsored by Client NS Default NS
Mgmt NS F C B F B F UI -
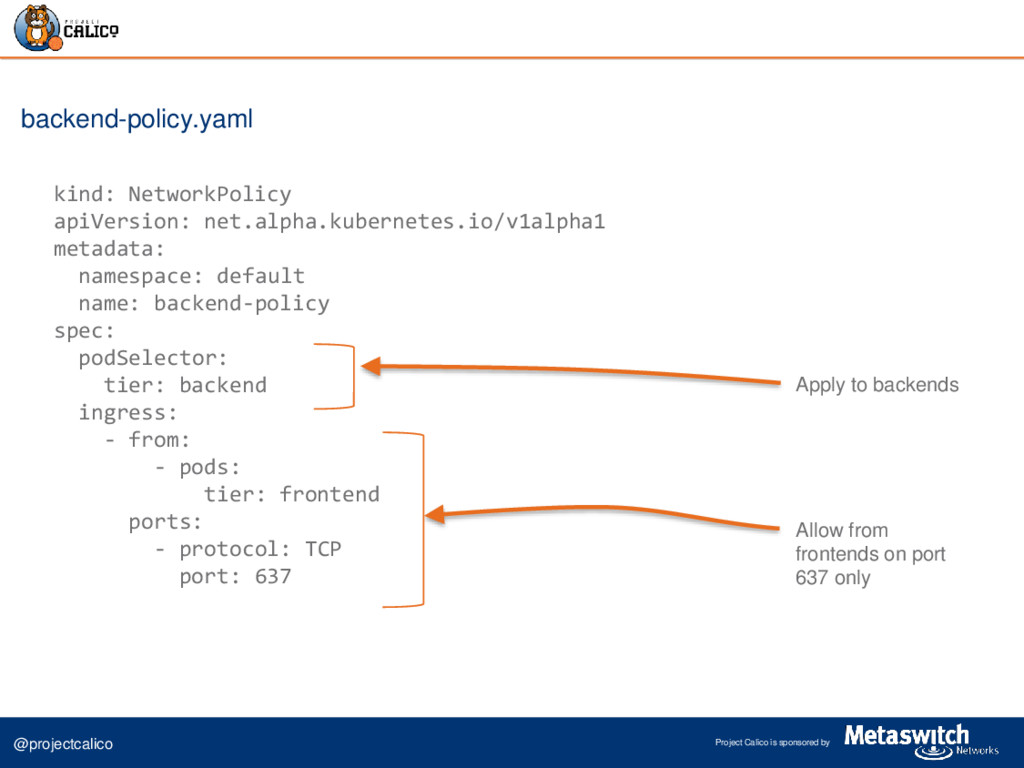
@projectcalico Project Calico is sponsored by kind: NetworkPolicy apiVersion: net.alpha.kubernetes.io/v1alpha1
metadata: namespace: default name: backend-policy spec: podSelector: tier: backend ingress: - from: - pods: tier: frontend ports: - protocol: TCP port: 637 backend-policy.yaml Allow from frontends on port 637 only Apply to backends -
@projectcalico Project Calico is sponsored by Client NS Default NS
Mgmt NS F C B F B F UI -
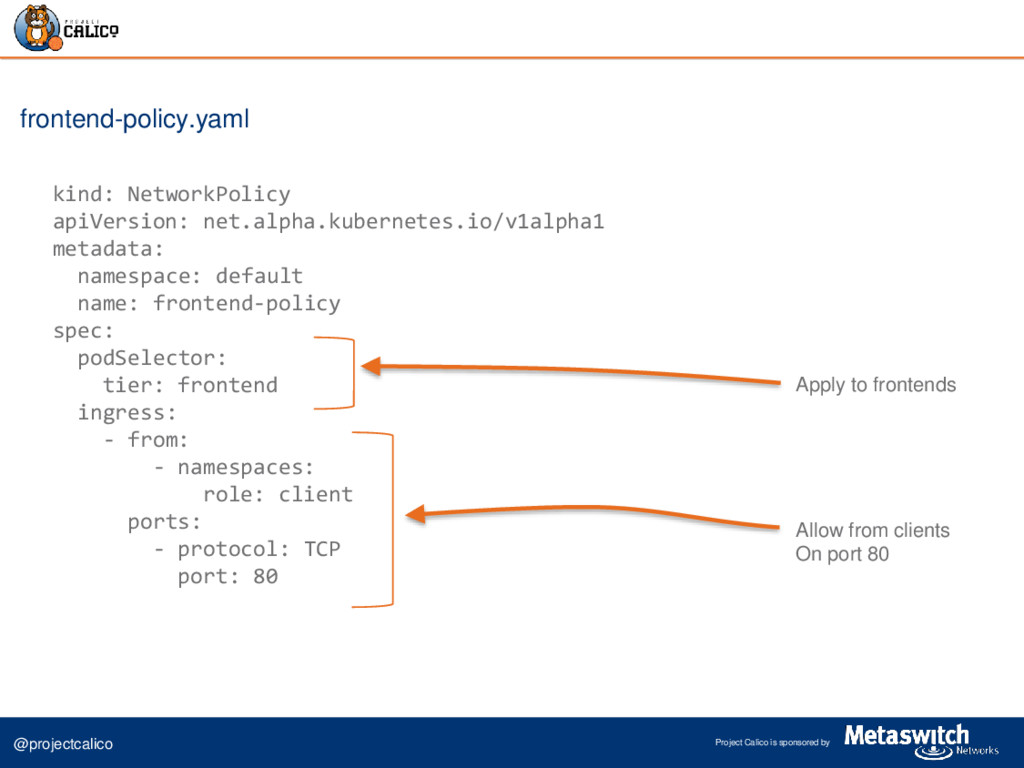
@projectcalico Project Calico is sponsored by kind: NetworkPolicy apiVersion: net.alpha.kubernetes.io/v1alpha1
metadata: namespace: default name: frontend-policy spec: podSelector: tier: frontend ingress: - from: - namespaces: role: client ports: - protocol: TCP port: 80 frontend-policy.yaml Apply to frontends Allow from clients On port 80 -
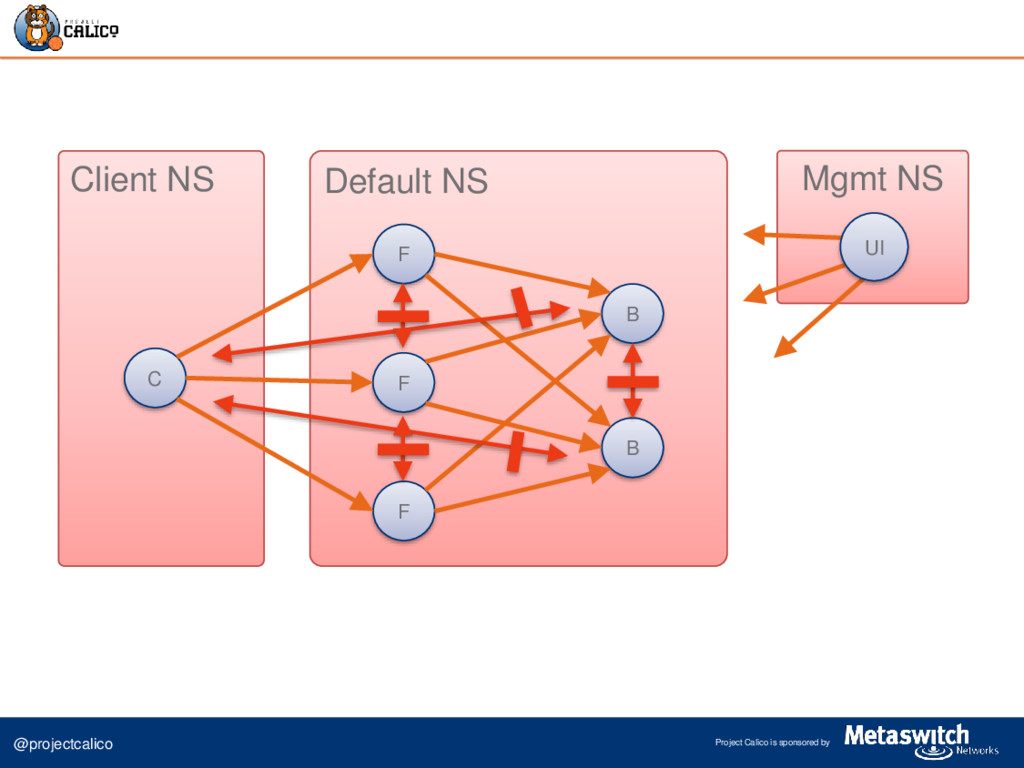
@projectcalico Project Calico is sponsored by Client NS Default NS
Mgmt NS F C B F B F UI -
@projectcalico Project Calico is sponsored by Main project website:
www.projectcalico.org CNI plugin for k8s: https://goo.gl/pyNsIf Try the demo: https://goo.gl/BYC97u Ansible playbooks from Kubespray https://docs.kubespray.io/ Public #slack https://calicousers-slackin.herokuapp.com/ Download & try it out We welcome your feedback and contributions Follow me @eepyaich Follow us @projectcalico