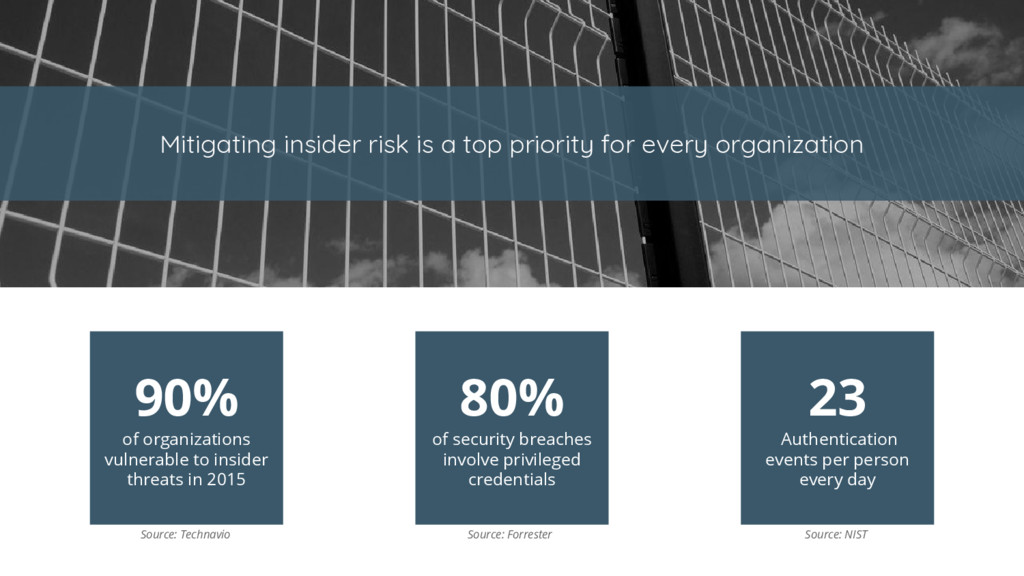
of security breaches involve privileged credentials 23 Authentication events per person every day Source: Forrester Source: Technavio Source: NIST Mitigating insider risk is a top priority for every organization
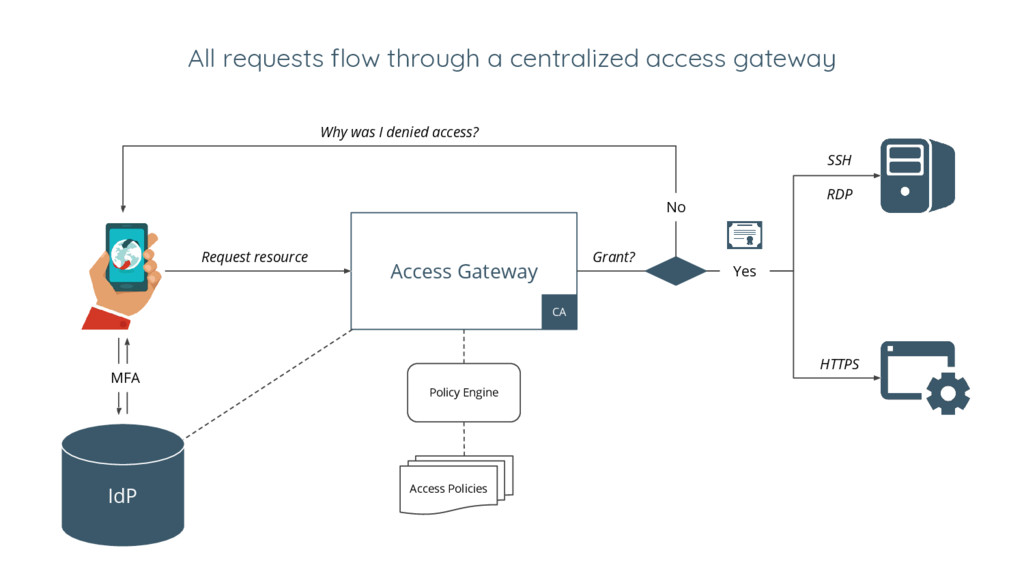
networks without use of a VPN 1. Connecting from a particular network must not determine which services you can access 2. Access to services is granted based on what we know about you and your device 3. All access to services must be authenticated, authorized, and encrypted Google really got it right with BeyondCorp
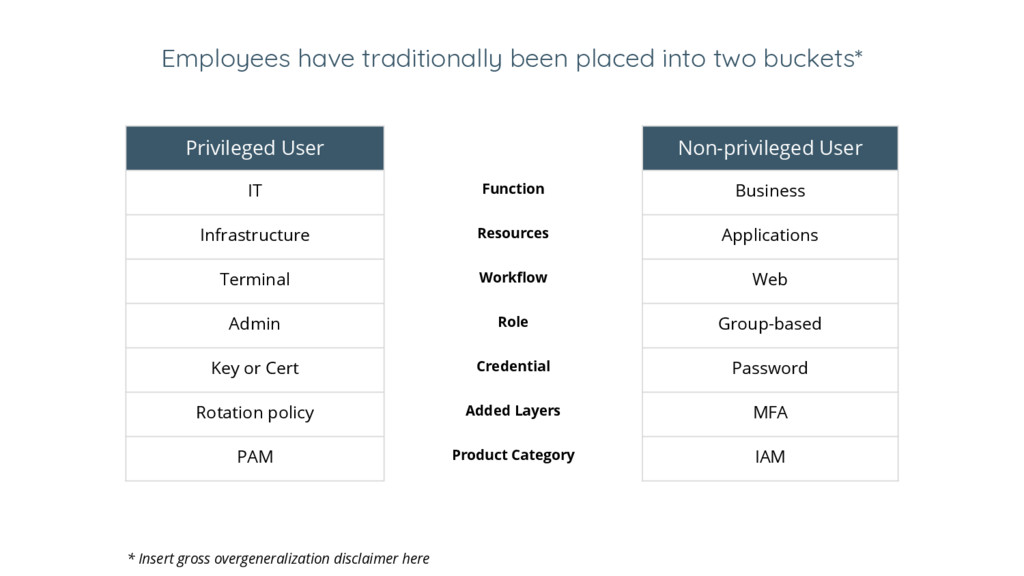
placed into two buckets* Privileged User Non-privileged User IT Function Business Infrastructure Resources Applications Terminal Workflow Web Admin Role Group-based Key or Cert Credential Password Rotation policy Added Layers MFA PAM Product Category IAM
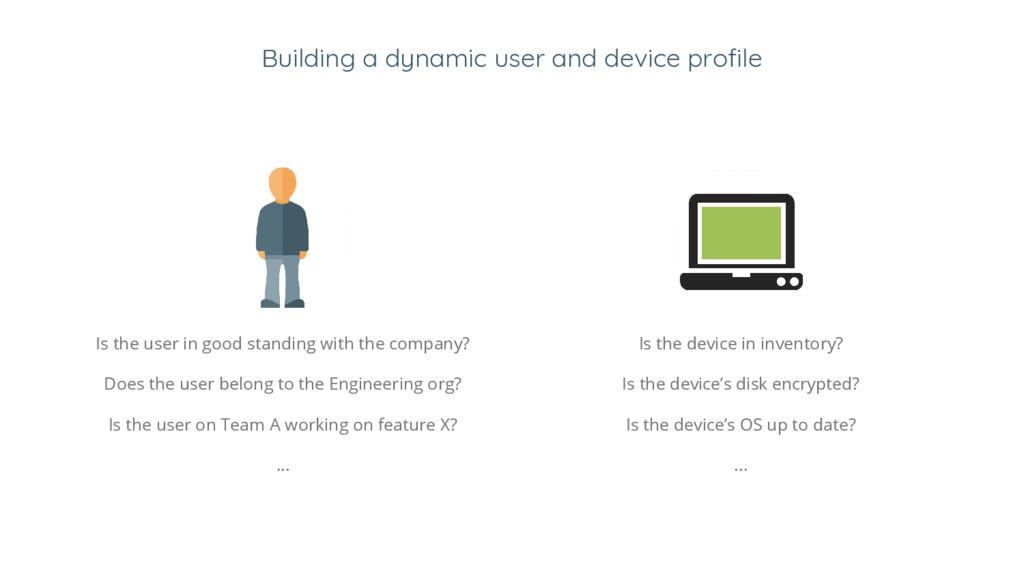
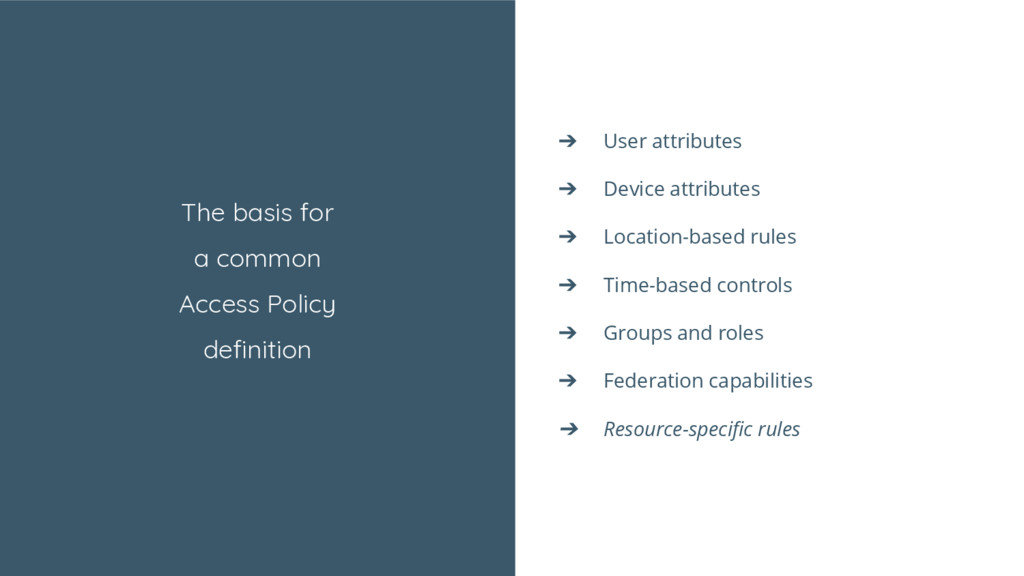
in good standing with the company? Does the user belong to the Engineering org? Is the user on Team A working on feature X? ... Is the device in inventory? Is the device’s disk encrypted? Is the device’s OS up to date? ...
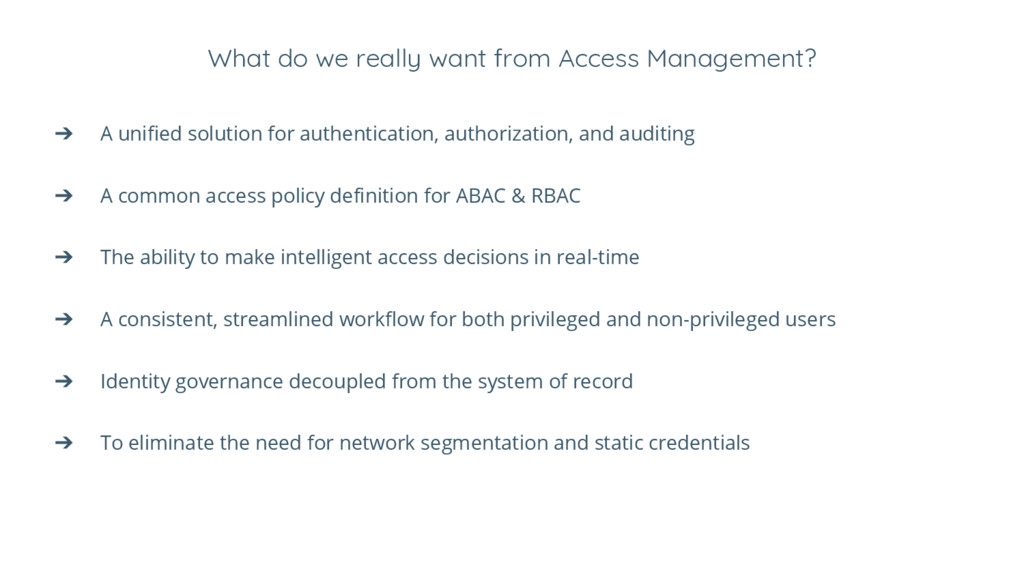
unified solution for authentication, authorization, and auditing ➔ A common access policy definition for ABAC & RBAC ➔ The ability to make intelligent access decisions in real-time ➔ A consistent, streamlined workflow for both privileged and non-privileged users ➔ Identity governance decoupled from the system of record ➔ To eliminate the need for network segmentation and static credentials
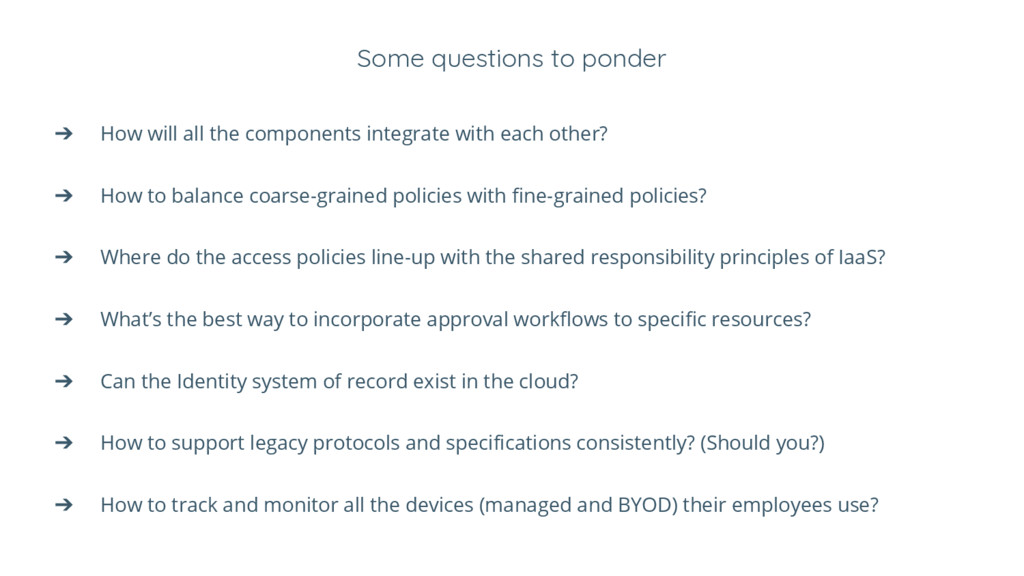
integrate with each other? ➔ How to balance coarse-grained policies with fine-grained policies? ➔ Where do the access policies line-up with the shared responsibility principles of IaaS? ➔ What’s the best way to incorporate approval workflows to specific resources? ➔ Can the Identity system of record exist in the cloud? ➔ How to support legacy protocols and specifications consistently? (Should you?) ➔ How to track and monitor all the devices (managed and BYOD) their employees use?
devices up-to-date with the latest software ➔ Maintain an inventory of employee devices ➔ Monitor all endpoints & log all traffic ➔ Only communicate over fully encrypted channels ➔ Incorporate multi-factor auth ➔ Eliminate static credentials
new category of Cloud Native solution providers are emerging that are disrupting the legacy security companies who focus primarily on strengthening perimeter security ➔ Defined market categories such as IAM and PAM will converge into a single Access Management category that works across privileged and nonprivileged users ➔ The Identity Provider space is about to heat up as cloud-based alternatives to Active Directory start to break through into the enterprise market ➔ The VPN market is going to be significantly impacted as more companies shift towards a Zero Trust model that places less (or no) emphasis on network protection as a security measure
leading Zero Trust Access Management provider Architecture Reviews Platform Implementations Community Efforts We work closely with you to design the right Zero Trust architecture for your organization The ScaleFT platform can be operated as a SaaS or as a dedicated deployment in any cloud environment We are leading the BeyondCorp movement, further educating the market about Zero Trust


 pfn
 kash1064
 nealle
 recruitengineers
 teamlab
 takuroabe
 shumei_ito
 codmoninc
 techtekt
 ezaki
 ueponx
 maimyyym
 tessaabrams
 ks91
 kimpetersen
 eileencodes
 brad_frost
 reverentgeek
 codingconduct
 elsirapls
 jonoalderson
 marktimemedia
 tonyrice
 mlcsv