! Security and embedded systems for US gov orgs ! Software engineer to startup founder/CEO ! Now VP/GM Mobile @ Rapid7 [email protected] @giri_sreenivas Cred 3
various embedded systems • Airborne Laser Program – Beam Control / Fire Control Systems • Wireless Sensor Networks - DARPA’s Network Embedded Sensor Technologies (NEST) • Trusted Computing – NSA High Assurance Platform • Mobile – platforms, applications, security ! IoT is more than just adding IP connectivity to embedded devices ! Key pillars required for exponential growth in usage and acceptance • Security • Trustworthiness Why I Care About Android and the Internet of Things 4
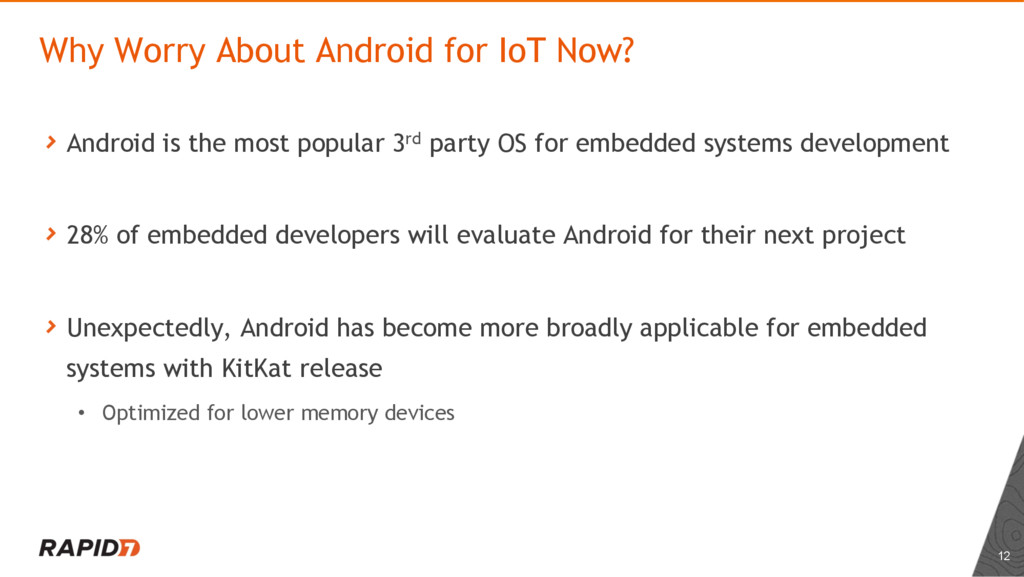
embedded systems development ! 28% of embedded developers will evaluate Android for their next project ! Unexpectedly, Android has become more broadly applicable for embedded systems with KitKat release • Optimized for lower memory devices Why Worry About Android for IoT Now? 12
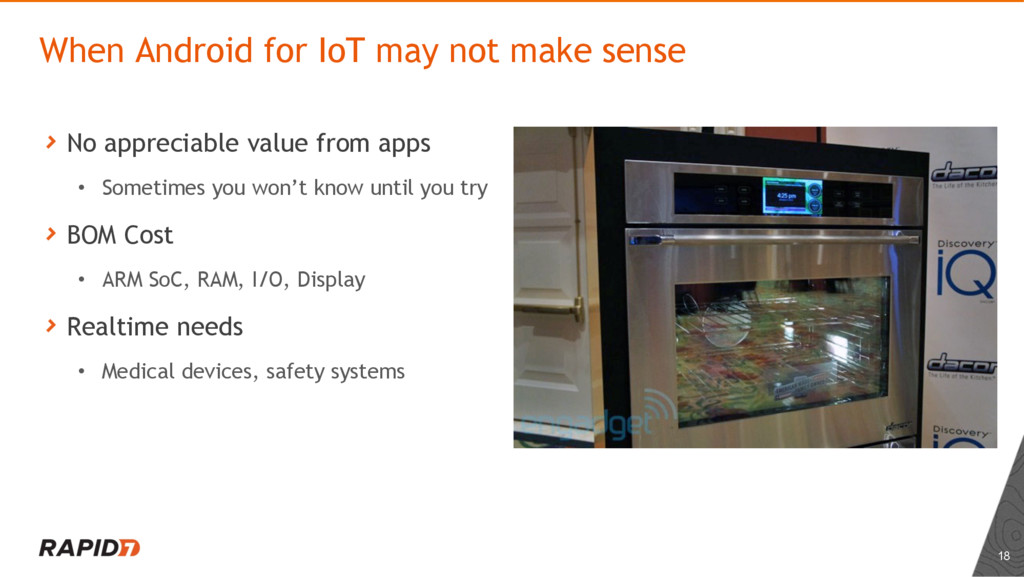
know until you try ! BOM Cost • ARM SoC, RAM, I/O, Display ! Realtime needs • Medical devices, safety systems When Android for IoT may not make sense 18
founder of Metasploit ! Uncovered numerous security issues in embedded systems that can help us from repeating history ! Project Sonar • http://miniurl.org/sonar Learning From The Past
! In 2010, HD scanned the Internet and found 250,000 vulnerable devices (310,000 in 2013) ! VxWorks Debug Service running on port 17185 ! Consequences • Disable login security • Read, write exec memory • Reboot devices • Scan memory for sensitive data ! Apple’s AirPort with an earlier firmware version was vulnerable VxWorks
UPnP discovery request for 5 months in 2012 and 81 million unique IPs responded ! 23 million were vulnerable to a single remote code execution flaw ! 1500+ vendors informed about 6900+ affected products ! 4 UPnP libraries responsible for 73% of devices ! Outdated/vulnerable libraries primarily responsible for security risk UPnP – Universal Plug and Play 22
Linux devices found vulnerable to simple credential login via telnet (e.g.: root:root, admin:admin, etc) ! 420,000 were used in a botnet to propagate scan ! Still think it’s a good idea to connect all devices to the Internet? Embedded Linux Botnets 23
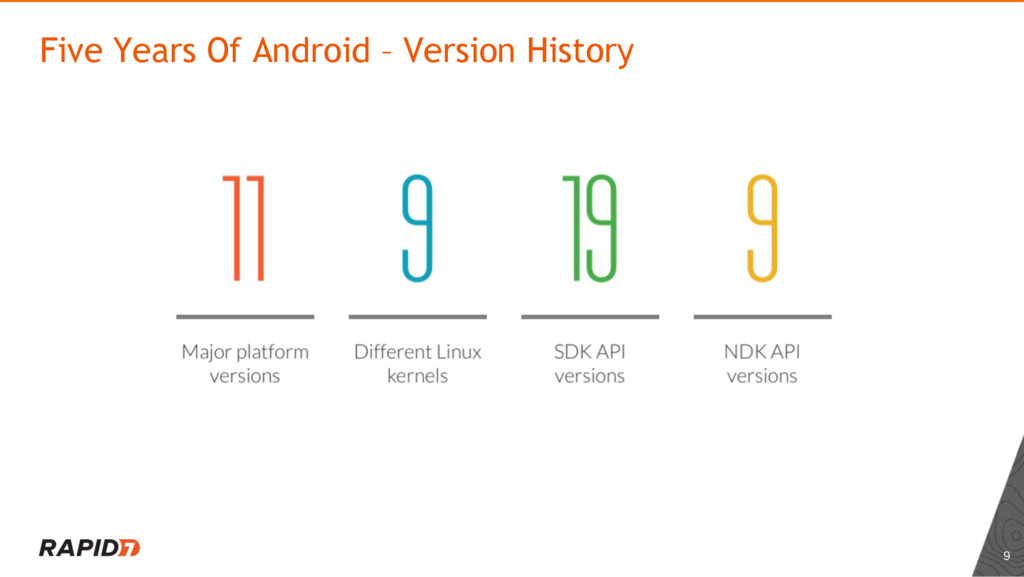
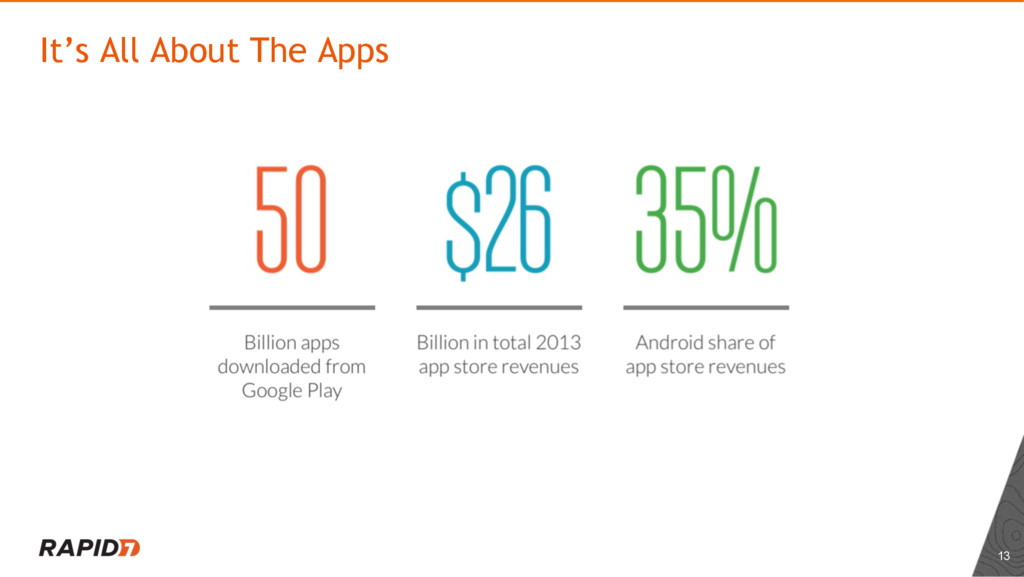
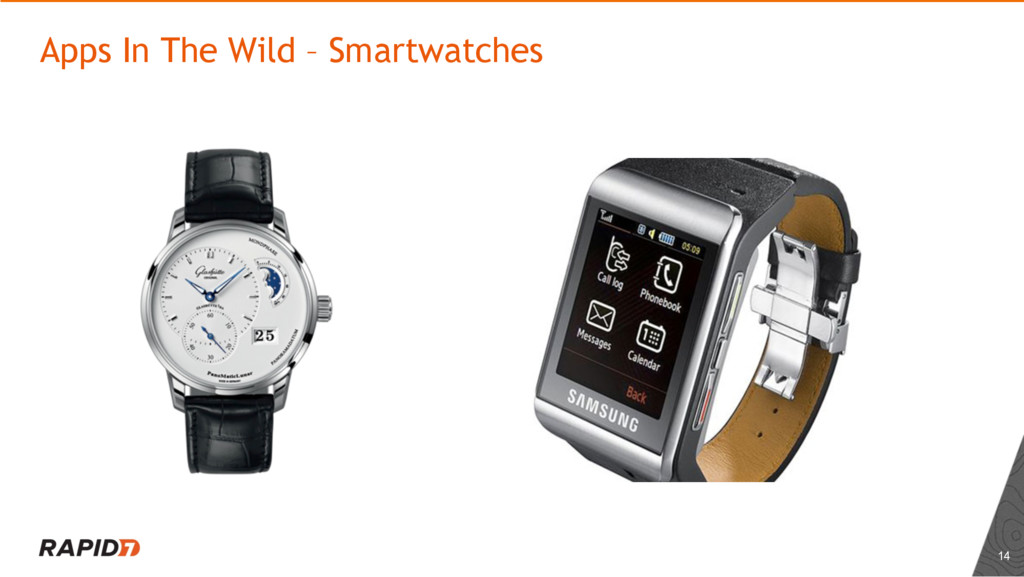
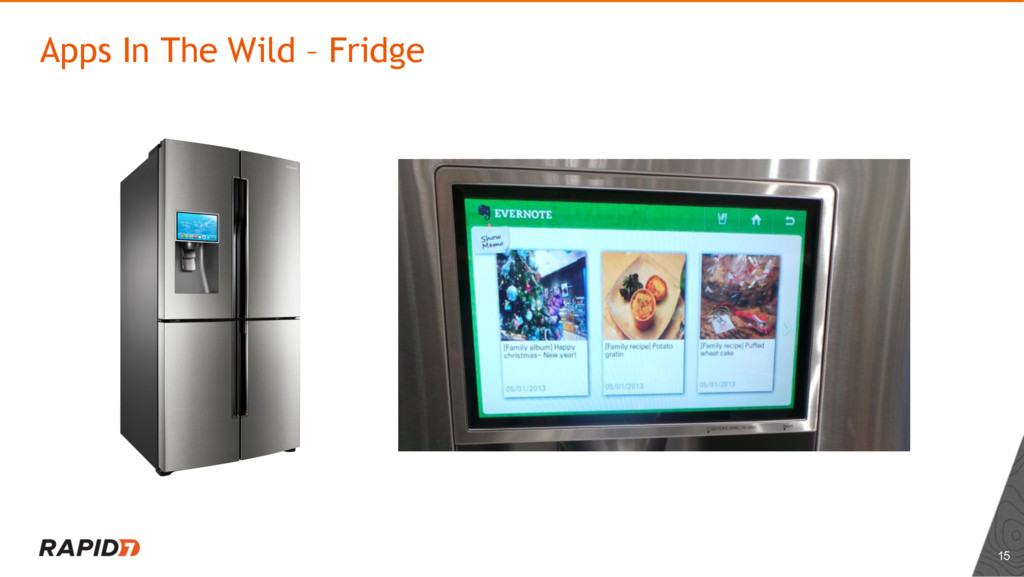
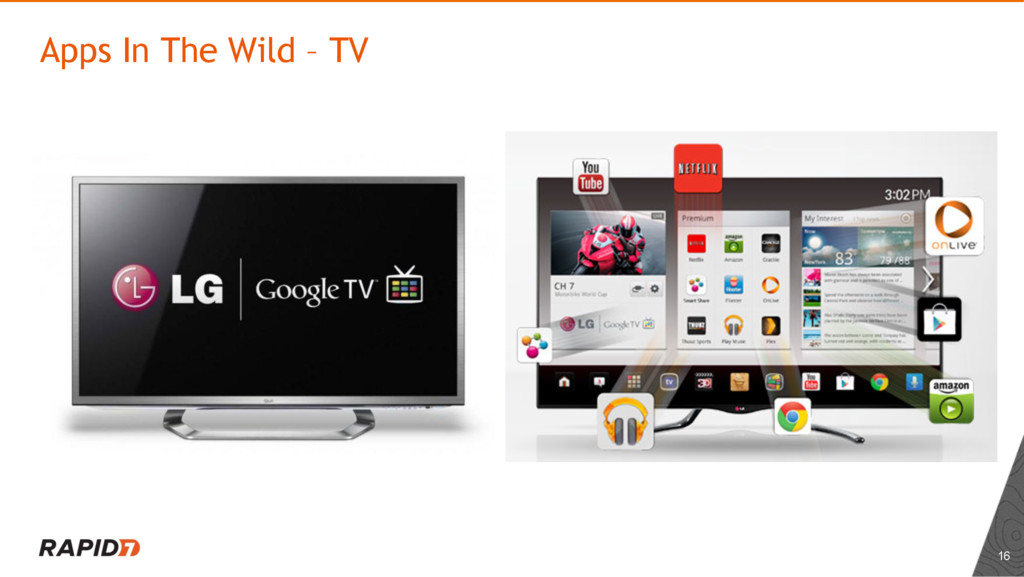
major platform for IoT ! Rapid pace of evolution in 5 years for Android ! Apps have played a critical role in bridging the last mile of UX and it is starting to take off for various embedded systems ! We’ve seen critical and widespread security mistakes with embedded systems on the WAN Intermediate Recap
Thousands of device models have been sold across hundreds of carriers ! The biggest carriers have rigorous testing processes that adds months to the release and update cycles This Can’t Be Happening With Android… Right? 26
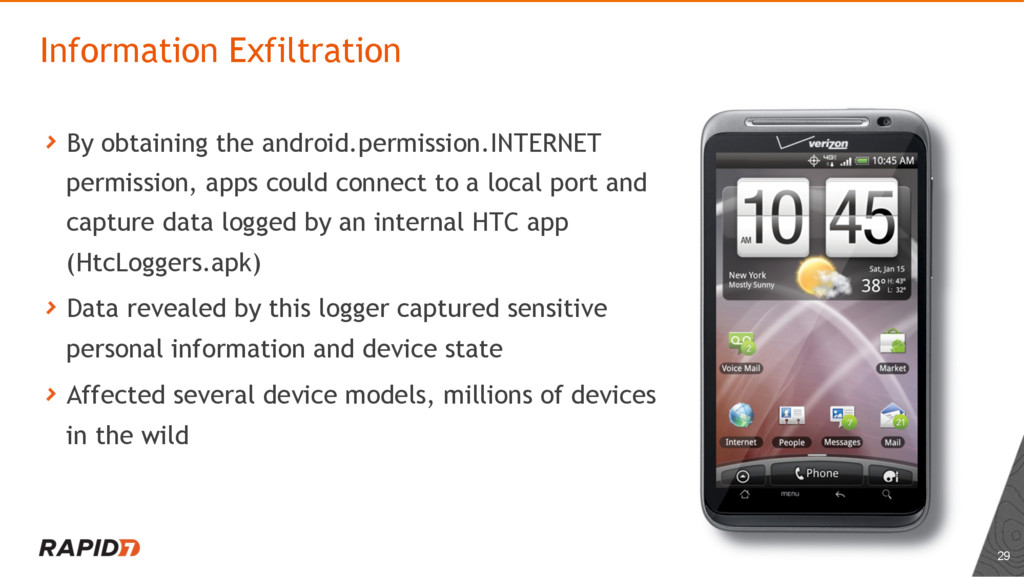
a local port and capture data logged by an internal HTC app (HtcLoggers.apk) ! Data revealed by this logger captured sensitive personal information and device state ! Affected several device models, millions of devices in the wild Information Exfiltration 29
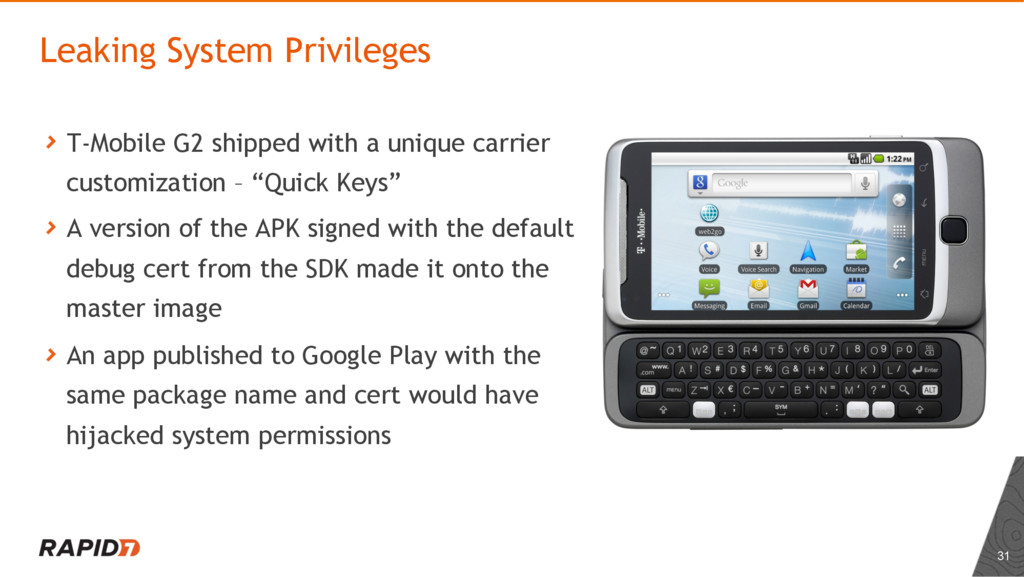
“Quick Keys” ! A version of the APK signed with the default debug cert from the SDK made it onto the master image ! An app published to Google Play with the same package name and cert would have hijacked system permissions Leaking System Privileges 31
insertion of malicious code into applications by bypassing application signing verification ! Numerous and inconsistent package verification implementations in the Android platform Master Key Vulnerability 32
software evolve quickly, in parallel ! Default/dummy configurations speed up dev/test/commercialization process but creep into the final product and create security holes ! Great paper by NCSU Android researcher Xuxian Jiang • The Impact of Vendor Customizations on Android Security • http://www.cs.ncsu.edu/faculty/jiang/pubs/CCS13.pdf ! Sometimes it’s ok to make mistakes if there’s an easy way to fix them Common Threads 34
in various healthcare situations with simple checklists ! Checklists to prevent past security mistakes ! Before enabling a device with Android for IoT, go beyond the business case • How do you patch when vulnerabilities are inevitably discovered? If you can’t patch it, you can’t secure it • What’s at stake? ! Before shipping • Pentest your devices! • Ship an update methodology you can follow through on The Power of Checklists


 girisreenivas
 gionn
 pfn
 raspython3
 takahashim
 takonda
 occhi
 tetsuya28
 shuta13
 ivry_presentationmaterials
 yut0naga1_fa
 4o1sobblue
 kentapapa
 skipperchong
 aleyda
 eileencodes
 eitanlees
 danielanewman
 aarron
 sstephenson
 livdayseo
 mkilby
 tonyrice
 427marketing
 jonyablonski