Upgrade to Pro — share decks privately, control downloads, hide ads and more …

Security Automation With OWASP ZAP - ZAPCon 2021

Avatar for Gowtham Gowtham
April 20, 2021

Security Automation With OWASP ZAP - ZAPCon 2021

Avatar for Gowtham

Gowtham

April 20, 2021

More Decks by Gowtham

Other Decks in Technology

Transcript

  1. Presented by Share this talk @ZAProxyCon 9 March 2021 Security

    Automation with OWASP ZAP Gowtham Sundar Security Engineer - Freshworks
  2. About Me • Senior Security Engineer @ Freshworks • ZAP

    Evangelist • Creator of Book of Bug Bounty Tips and Bug Hunter Handbook • Interested in Cloud and Container Security • Active Learner Contact: Linkedin - https://www.linkedin.com/in/gowtham-sundar-6669b380/ Twitter - https://twitter.com/gowsundar Blog - https://medium.com/@gowsundar
  3. Agenda • ZAP Introduction • Web Application Security Automation Using

    ZAP • Problem / Challenges Statement • Solving Problem - The ZAP Way ◦ ZAP + Jenkins ◦ ZEST Scripts • Demos • Resources and References
  4. OWASP ZAP (Zed Attack Proxy) - Introduction • Widely used

    Web Application Scanner • An OWASP Flagship Project • Free and Open Source • Well Maintained • Highly Flexible • New Automation Framework - To be Released
  5. Security Automation with ZAP ZAP is the most widely used

    free and open source scanner across the world. Check out - Is ZAP World's Most Popular Web Scanner ? Current Automation Options • Command Line • Jenkins Plugin • Packaged Scans • Github Actions • Daemon + API
  6. Problem / Challenge Statement - 1 Our Commercial Dynamic Application

    Security Testing (DAST) Tool’s • Scan Duration was “High” • Not Suitable for Continuous Integration (CI) ◦ Engineer’s had to trigger scan Manually • Not Flexible ◦ No Customization ◦ No Concurrent Scans ◦ Sharing of Credentials between Engineer’s Commercial DAST Tools RASP and other Solutions Commercial DAST Tools ZAP
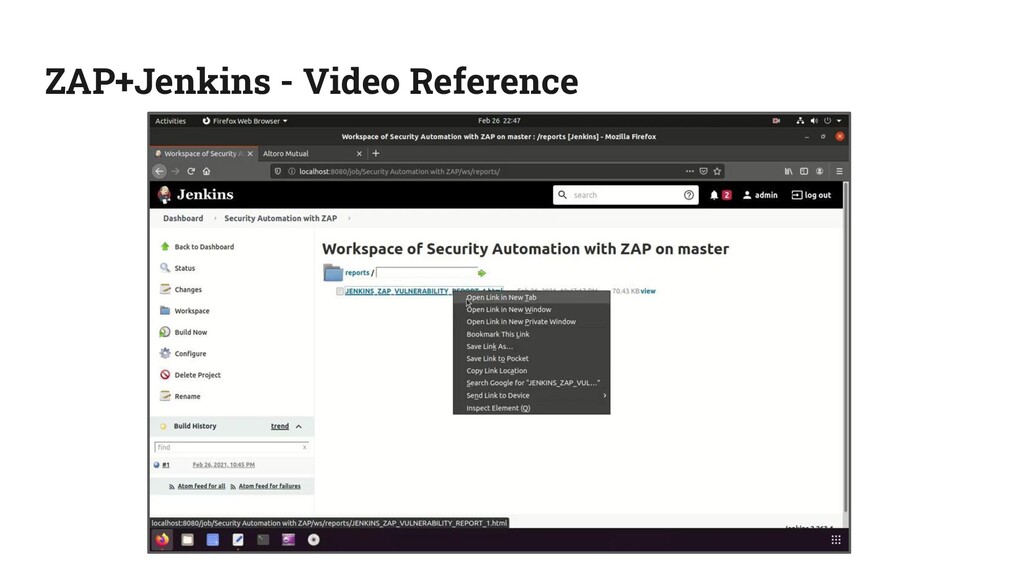
  7. Solution - The ZAP Way.. ZAP + Jenkins Integration (Plugin)

    • Key Highlights ◦ Completely Automated (CI Support) ◦ Highly Flexible / Configurable + =
  8. Problem / Challenge Statement - 2 Performing Authenticated Scans ??

    • Successful Scan using Form Based Authentication • Unable to handle Custom SSO Login ◦ Requires dynamic “callback_code” for authentication • Unable to perform authenticated scans ◦ Minimal Findings ◦ Less Application Coverage What type of AuthN Scheme You use? Custom SSO
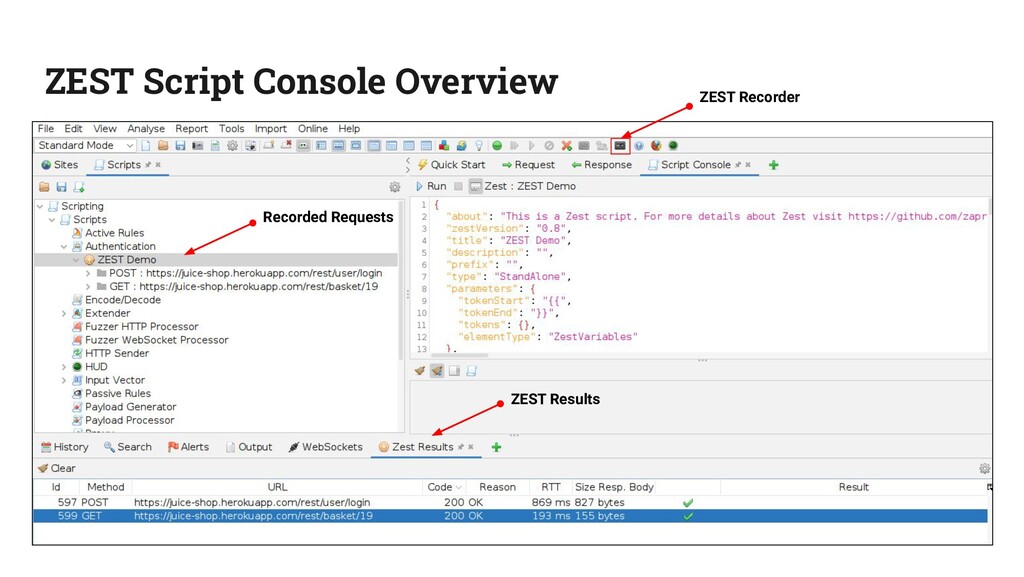
  9. Solution - The Z(AP)EST Way.. ZEST Scripts • What is

    ZEST ? ◦ An experimental scripting language initially developed by Mozilla ◦ Free and Open Source (included in ZAP by default) ◦ JSON Based ◦ Useful for creating custom scripts ◦ Multiple Features (Assignment, Assertion, Condition, Etc,.) • Other Supported Scripts ◦ ECMAScript / JavaScript ◦ Groovy ◦ Python ◦ Ruby ZEST Recorder
  10. Demo Time Scenario: • Consider an Application requires “dynamic token”

    during Login. Steps: • Record the Application Login Flow using via ZEST Recorder • Assign the “dynamic token” to a variable using ZEST Assignment Option • Modify the Login request to include the assigned variable • Successful Login !!
  11. ZEST Script - Recording Login Flow / Assignment Assigning Dynamic

    Token to a variable using ZEST Assignment.
  12. ZEST Script - Modifying Login Request Modifying Login Request to

    include the Dynamic Token from the “assigned” variable. Successful Login Flow
  13. References / Resources • Security Automation With ZAP - Jenkins

    [Blog] • OWASP ZAP Advanced Features [Video] • Semi - Automated Security Testing with ZAP [Blog] • ZAP in Ten [Video Series] • ZAP Automation in CI / CD [Video] • ZAP Homepage
  14. Presented by Share this talk @ZAProxyCon Thank You Please join

    us on the ZAProxyCon Discord Server! https://discord.gg/8ejQWfbb6p