Upgrade to Pro — share decks privately, control downloads, hide ads and more …

More Power to ZAP

Avatar for Gowtham Gowtham
March 09, 2022

More Power to ZAP

Avatar for Gowtham

Gowtham

March 09, 2022

More Decks by Gowtham

Other Decks in Technology

Transcript

  1. About Me! Lead Security Engineer @ Freshworks • ZAP Evangelist

    • Interested in Offensive Security • Blogger and active Learner Blog - medium.com/@gowsundar 2
  2. Session Agenda • ZAP - Introduction • Explore ZAP Features

    • ZAP Power Up’s ◦ ZAP Marketplace - Overview ◦ Demystifying Add-ons ◦ Quick Demo’s 3
  3. Takeaways • Know / Understand ZAP features • Utilize ZAP

    addons for effective coverage / pen-test • Importance of contribution to open-source • Identify bugs for $$$ free using ZAP !!! 4
  4. OWASP ZAP - Introduction • Widely used Web Application Proxy

    • An OWASP Flagship Project • Free and Open Source • Well Maintained • Highly Flexible • Powerful Automation Framework 6
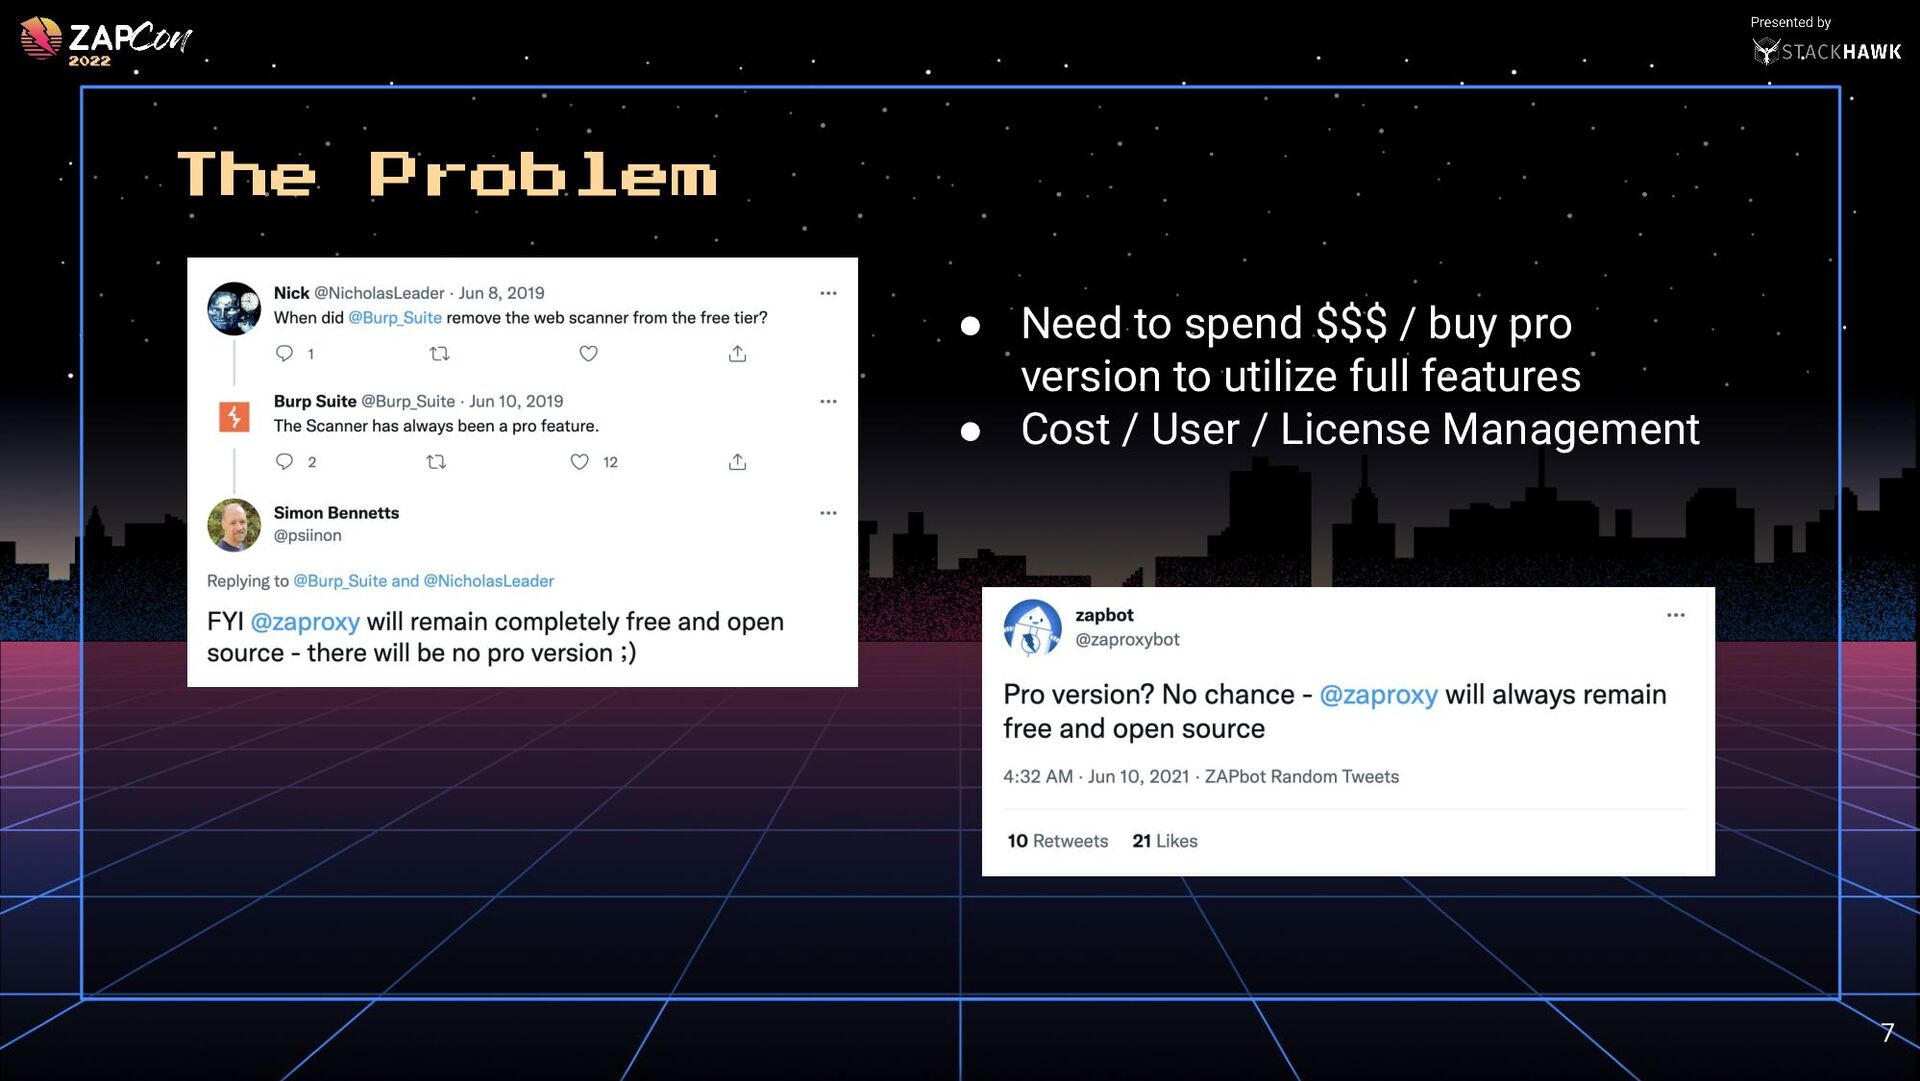
  5. The Problem • Need to spend $$$ / buy pro

    version to utilize full features • Cost / User / License Management 7
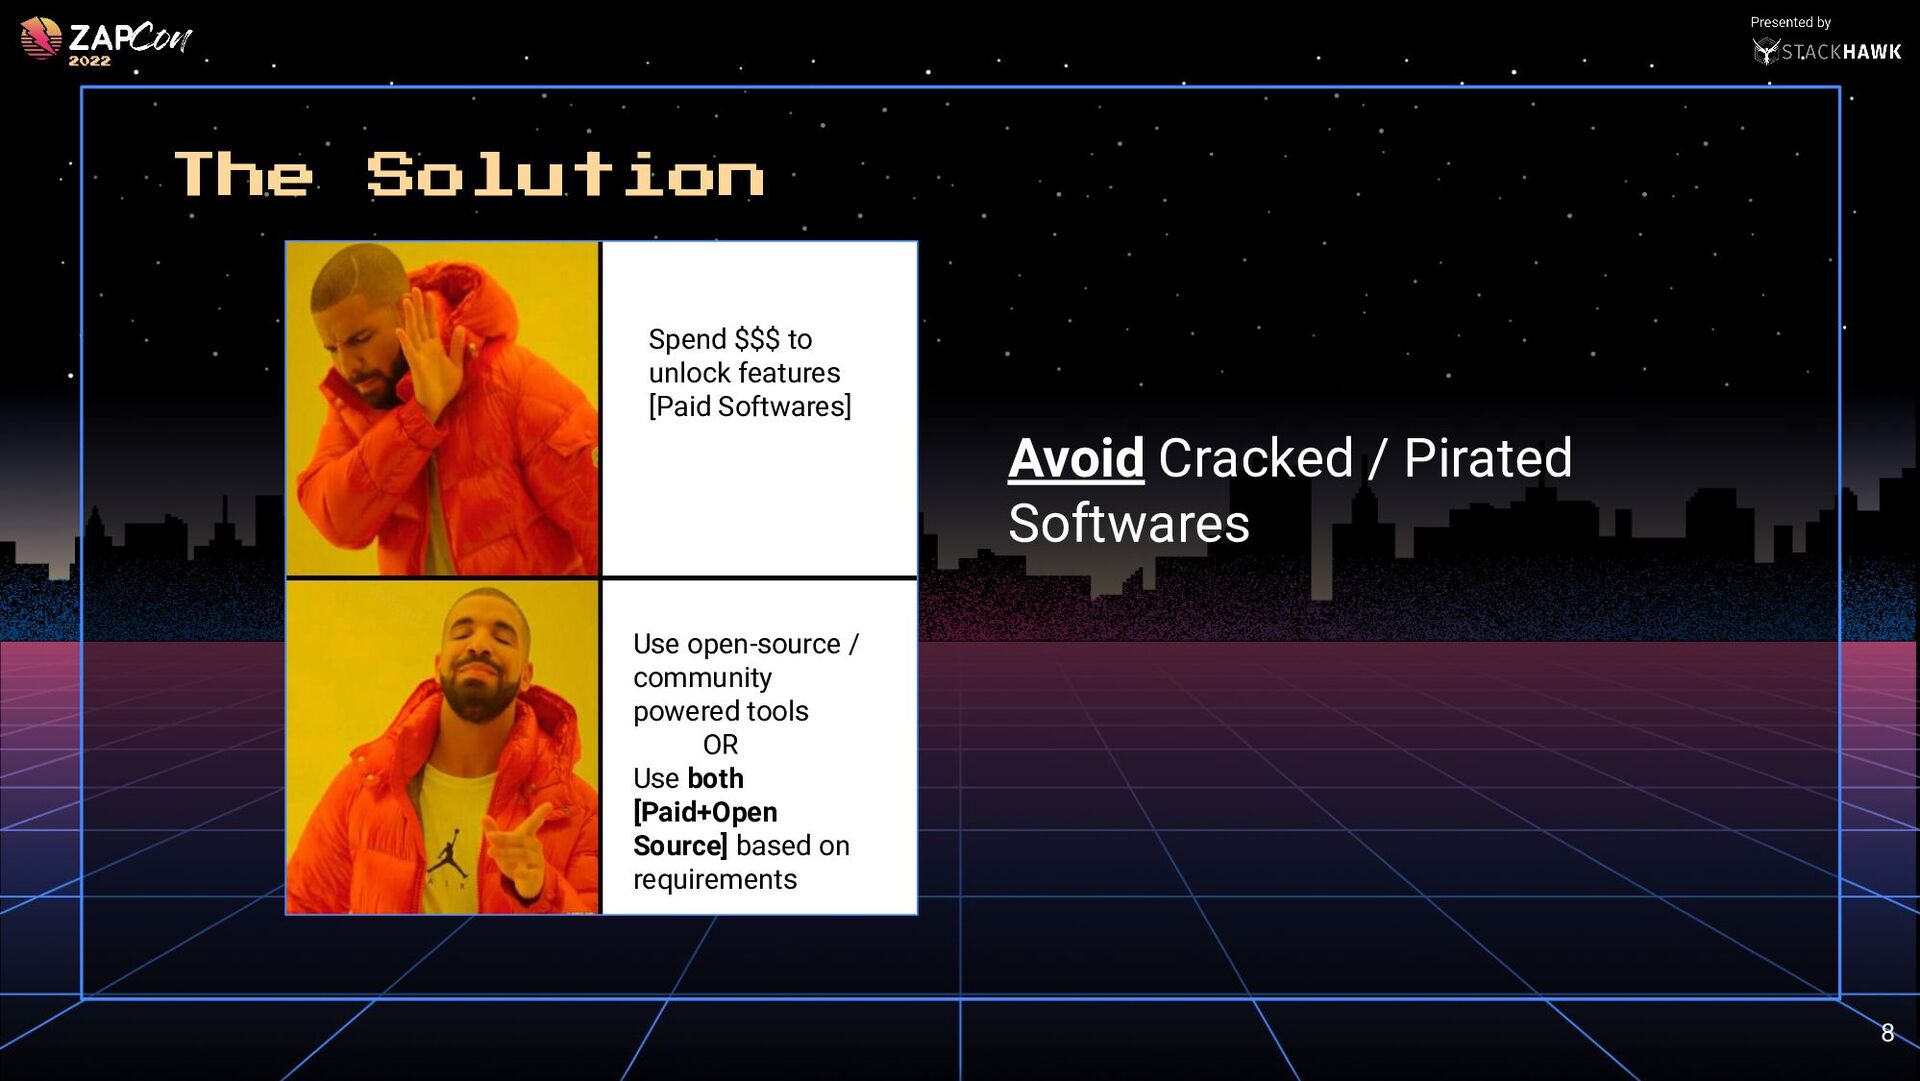
  6. The Solution Avoid Cracked / Pirated Softwares Spend $$$ to

    unlock features [Paid Softwares] Use open-source / community powered tools OR Use both [Paid+Open Source] based on requirements 8
  7. Before We Begin!! Credits: - Simon Bennetts (@psiinon) - ZAP

    Dev / Core Team Members - ZAP Contributors 9
  8. • Active Scan ◦ Attack Mode ◦ Disabled by default

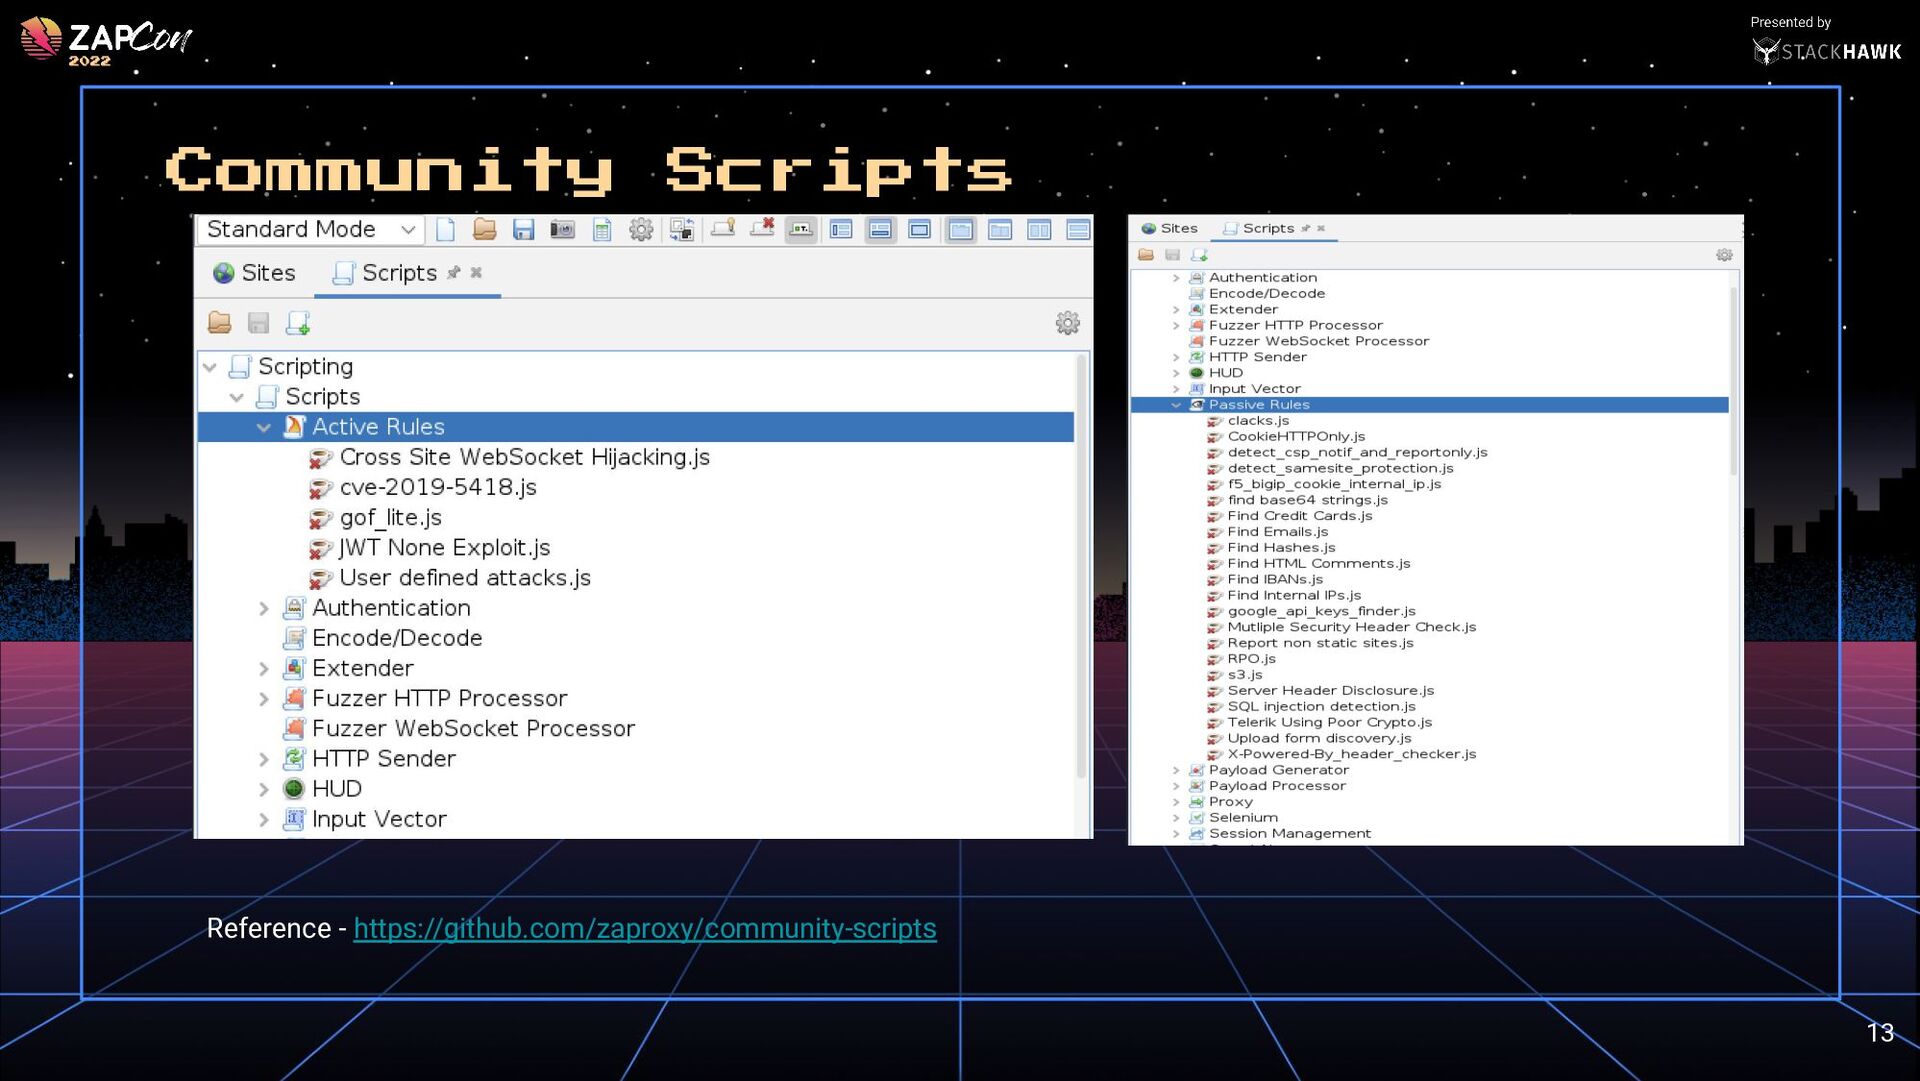
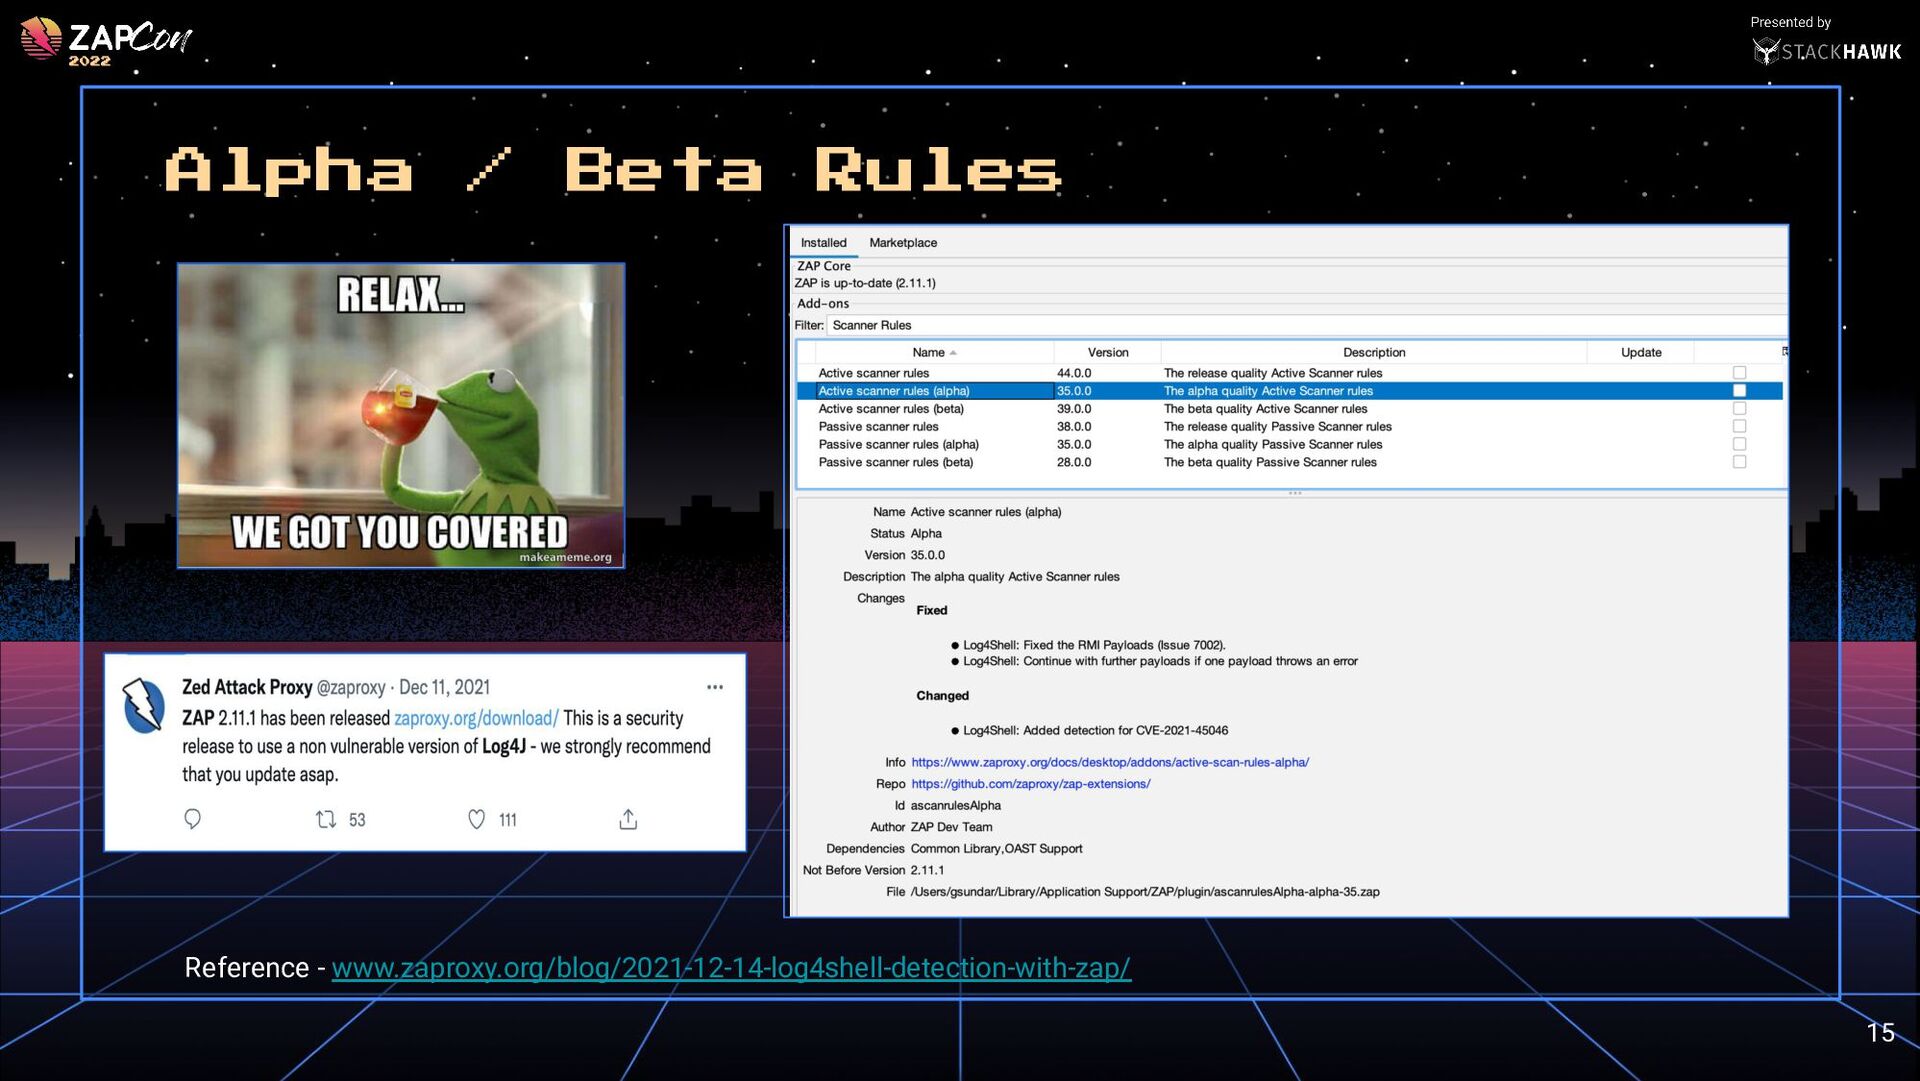
    ◦ Multi-threading support • Passive Scan ◦ Non-Intrusive ◦ Enabled by default ◦ Custom rules via scripts • Customized scan Policies • Alpha / Beta rules via add-ons 1.Automated Scanner 10
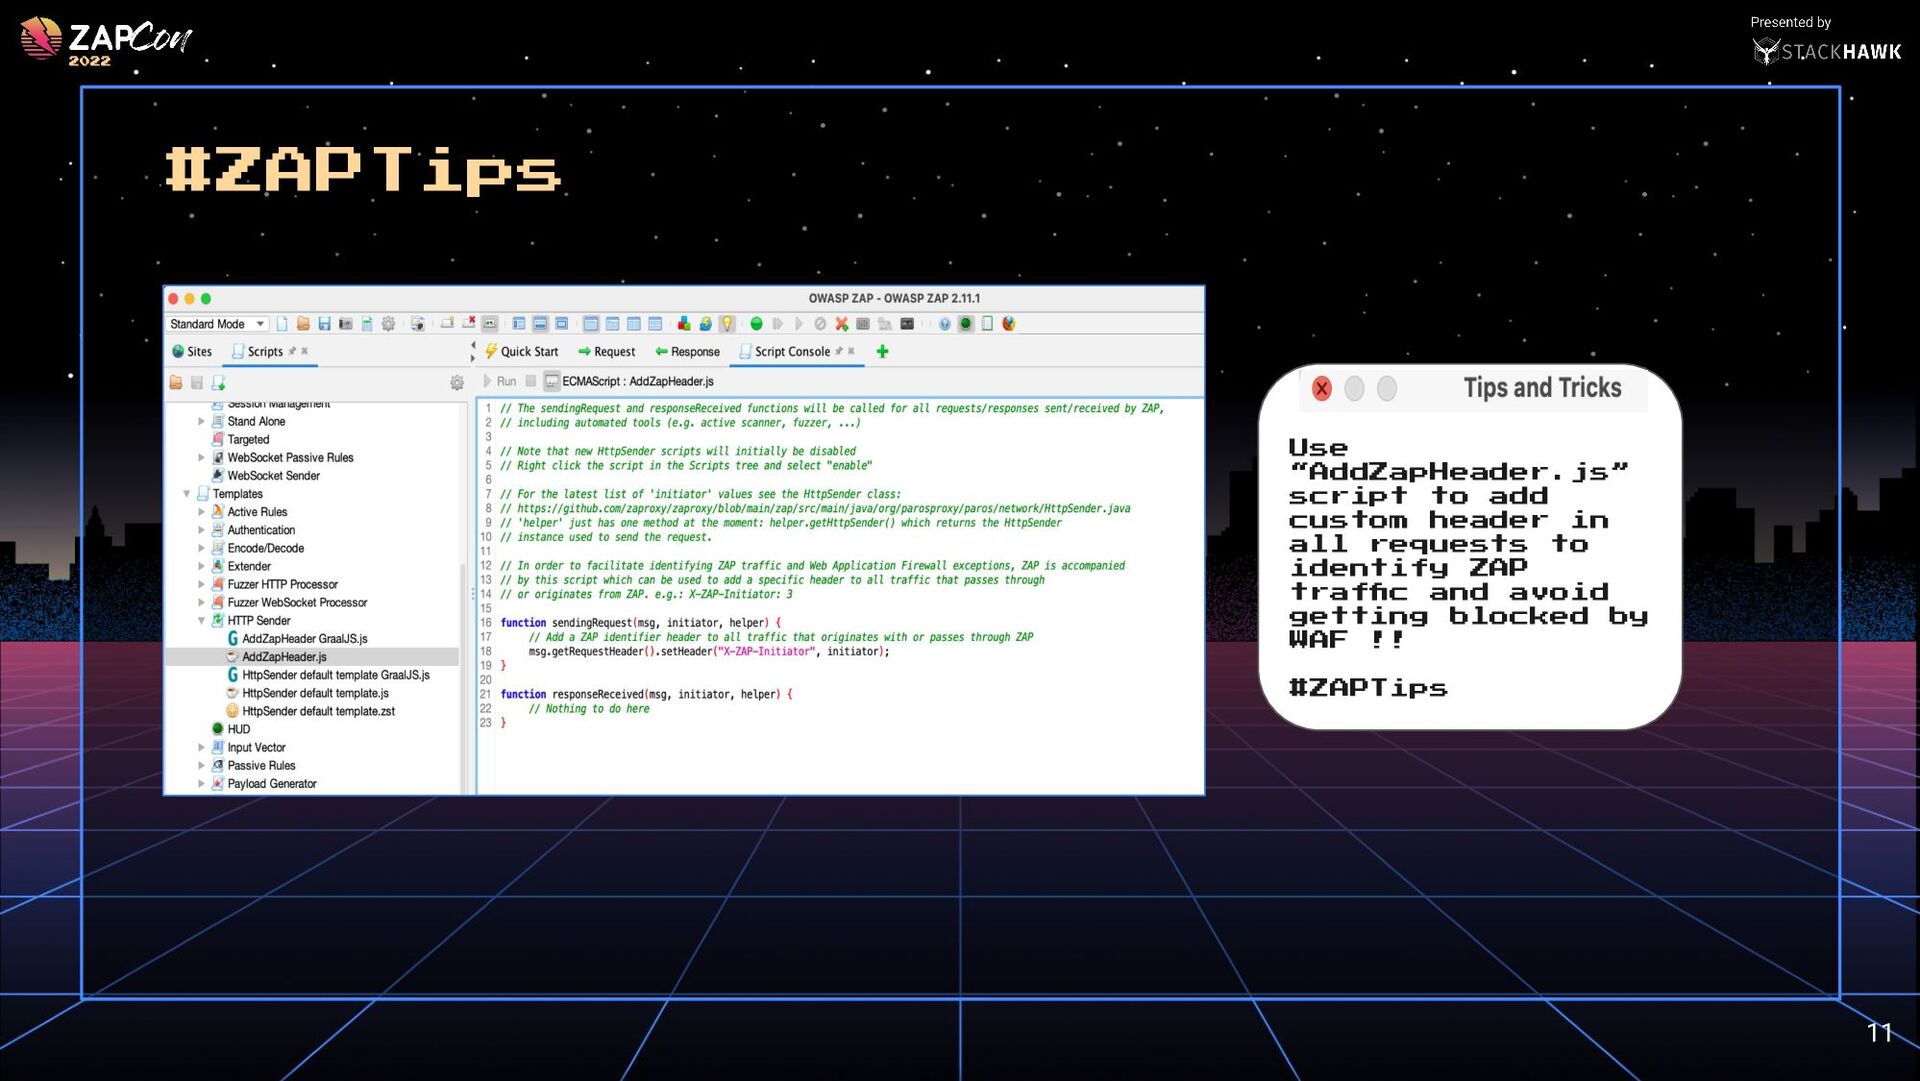
  9. #ZAPTips Use “AddZapHeader.js” script to add custom header in all

    requests to identify ZAP traffic and avoid getting blocked by WAF !! #ZAPTips 11
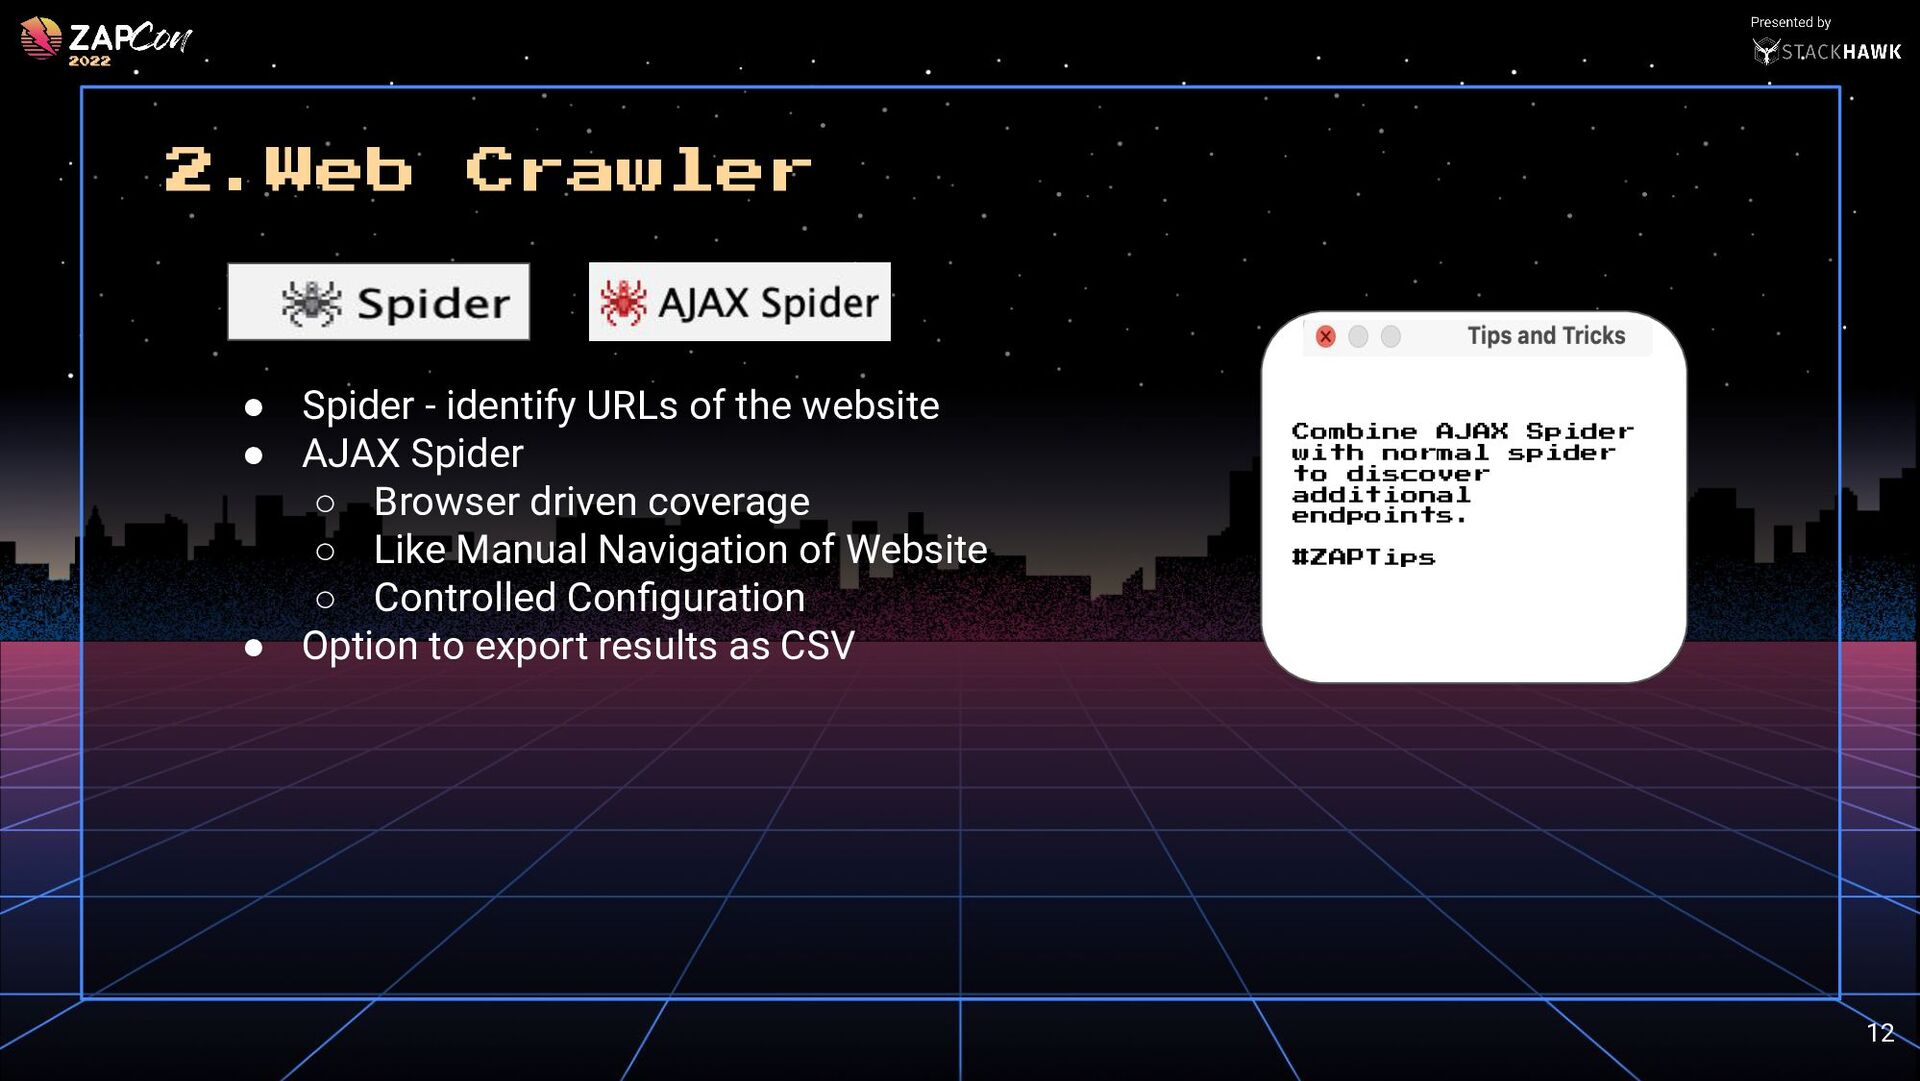
  10. • Spider - identify URLs of the website • AJAX

    Spider ◦ Browser driven coverage ◦ Like Manual Navigation of Website ◦ Controlled Configuration • Option to export results as CSV 2.Web Crawler Combine AJAX Spider with normal spider to discover additional endpoints. #ZAPTips 12
  11. Fuzzer - Random data / payloads - “Manual” fuzzing -

    Payload / Message processors - FuzzDB / FuzzDB Offensive / SVN Digger Files [Add-on] Content Discovery - Files / Directories - Force browse - OWASP DirBuster fork - Actively maintained 2.Fuzzing / Content Discovery 16
  12. - Race Conditions - Cross Site Scripting (XSS) - SQL

    Injection - Brute Force Attacks - Many others with custom payloads / scripts Vulnerability Coverage 17
  13. Quick Demo - Race Condition Application Credits - OWASP TimeGap

    Theory Project by Abhi M Balakrishnan 19
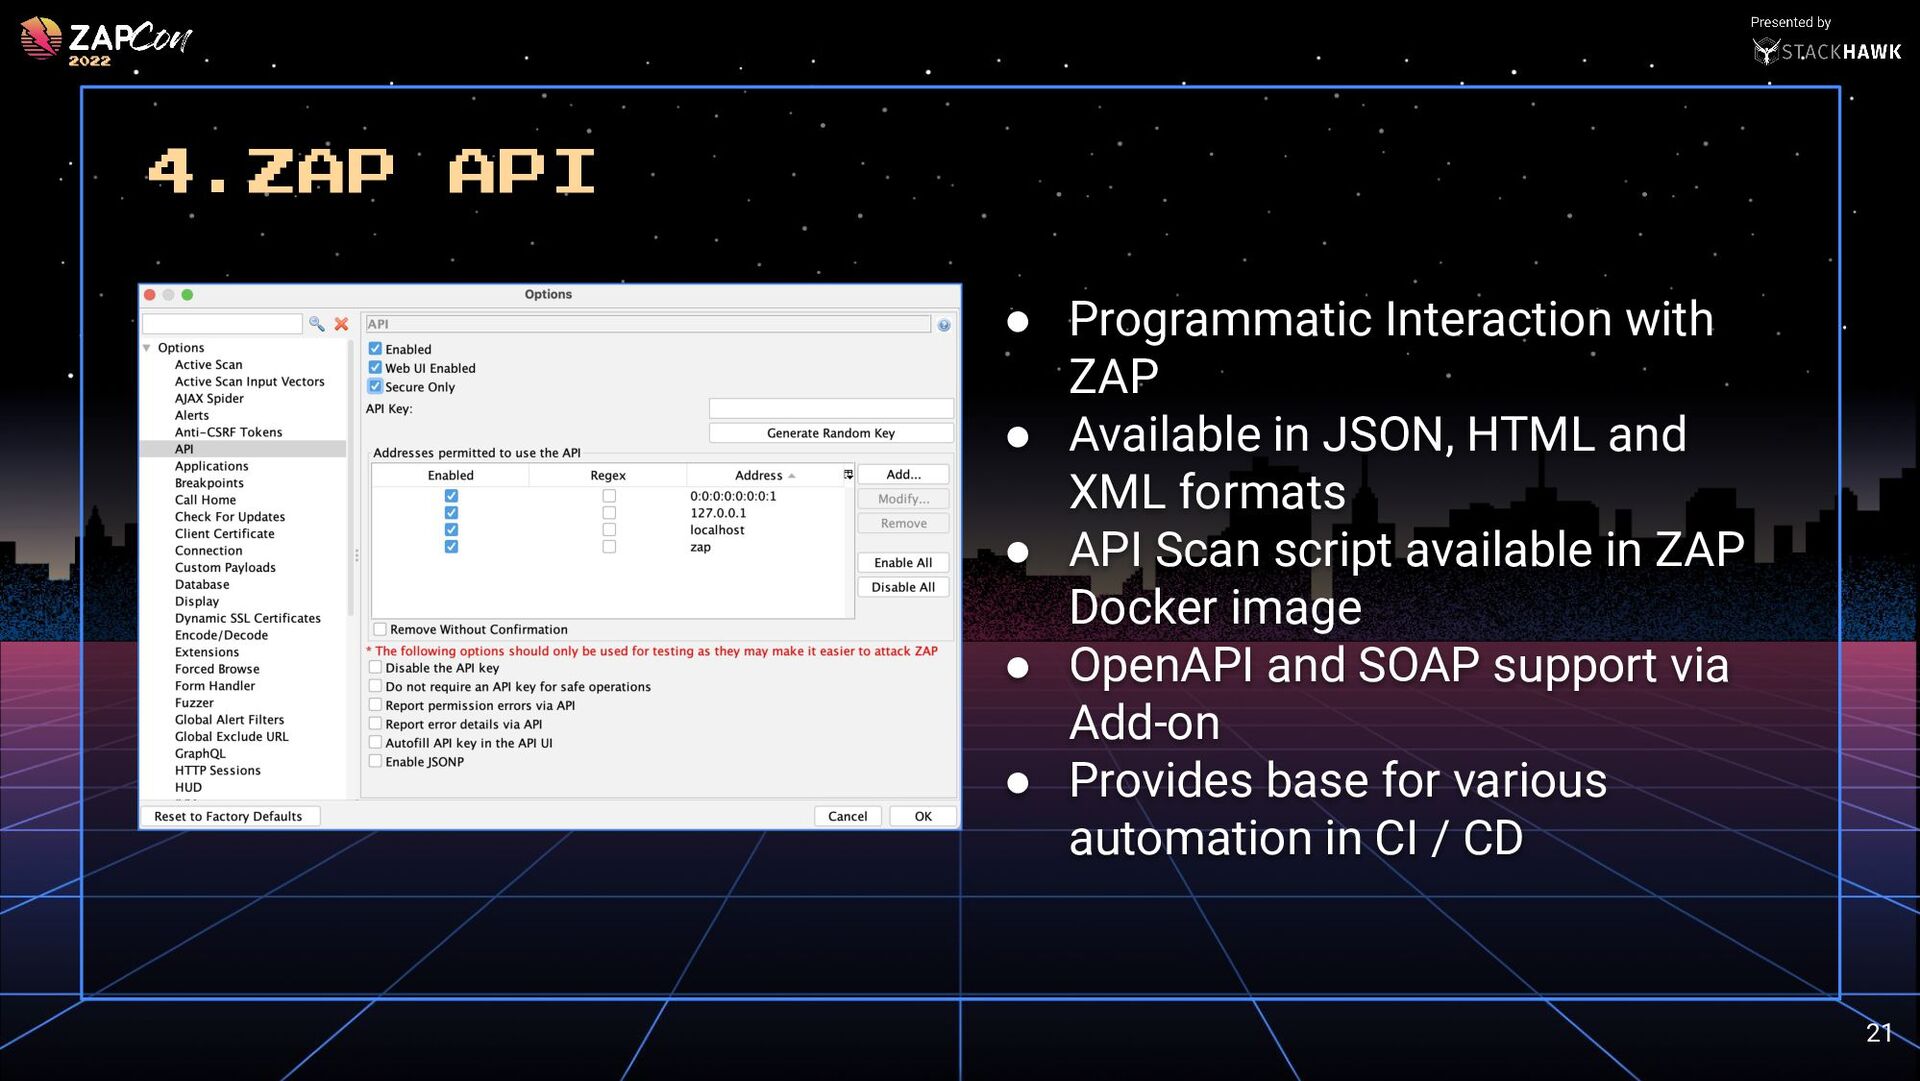
  14. 4.ZAP API • Programmatic Interaction with ZAP • Available in

    JSON, HTML and XML formats • API Scan script available in ZAP Docker image • OpenAPI and SOAP support via Add-on • Provides base for various automation in CI / CD 21
  15. ZAP Add-ons - Explained • Provides additional support • Full

    access of ZAP internals • Add-on statuses - Alpha -> Under development - Beta -> To be tested - Release -> High quality / ready to use • Custom Add-on support You can add/remove add-ons from ZAP UI with “no restart” required. #ZAPTips 25
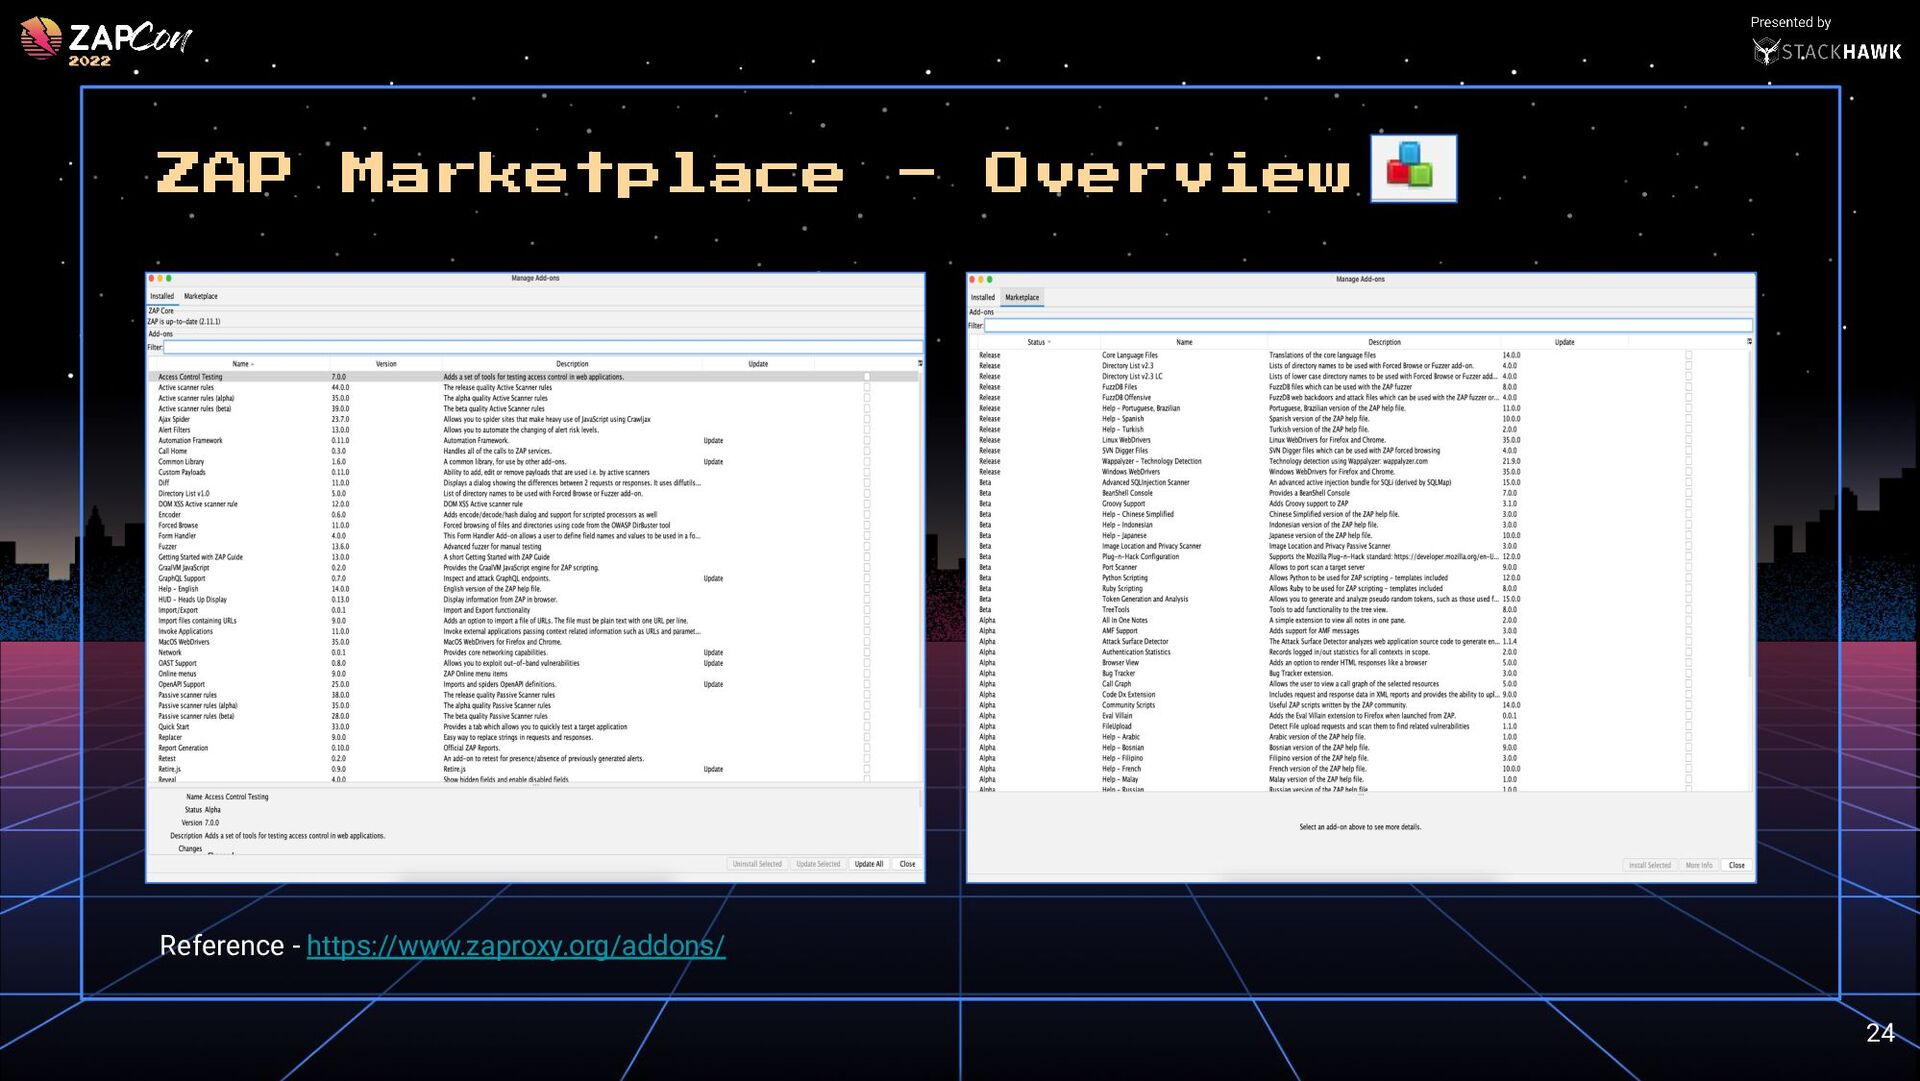
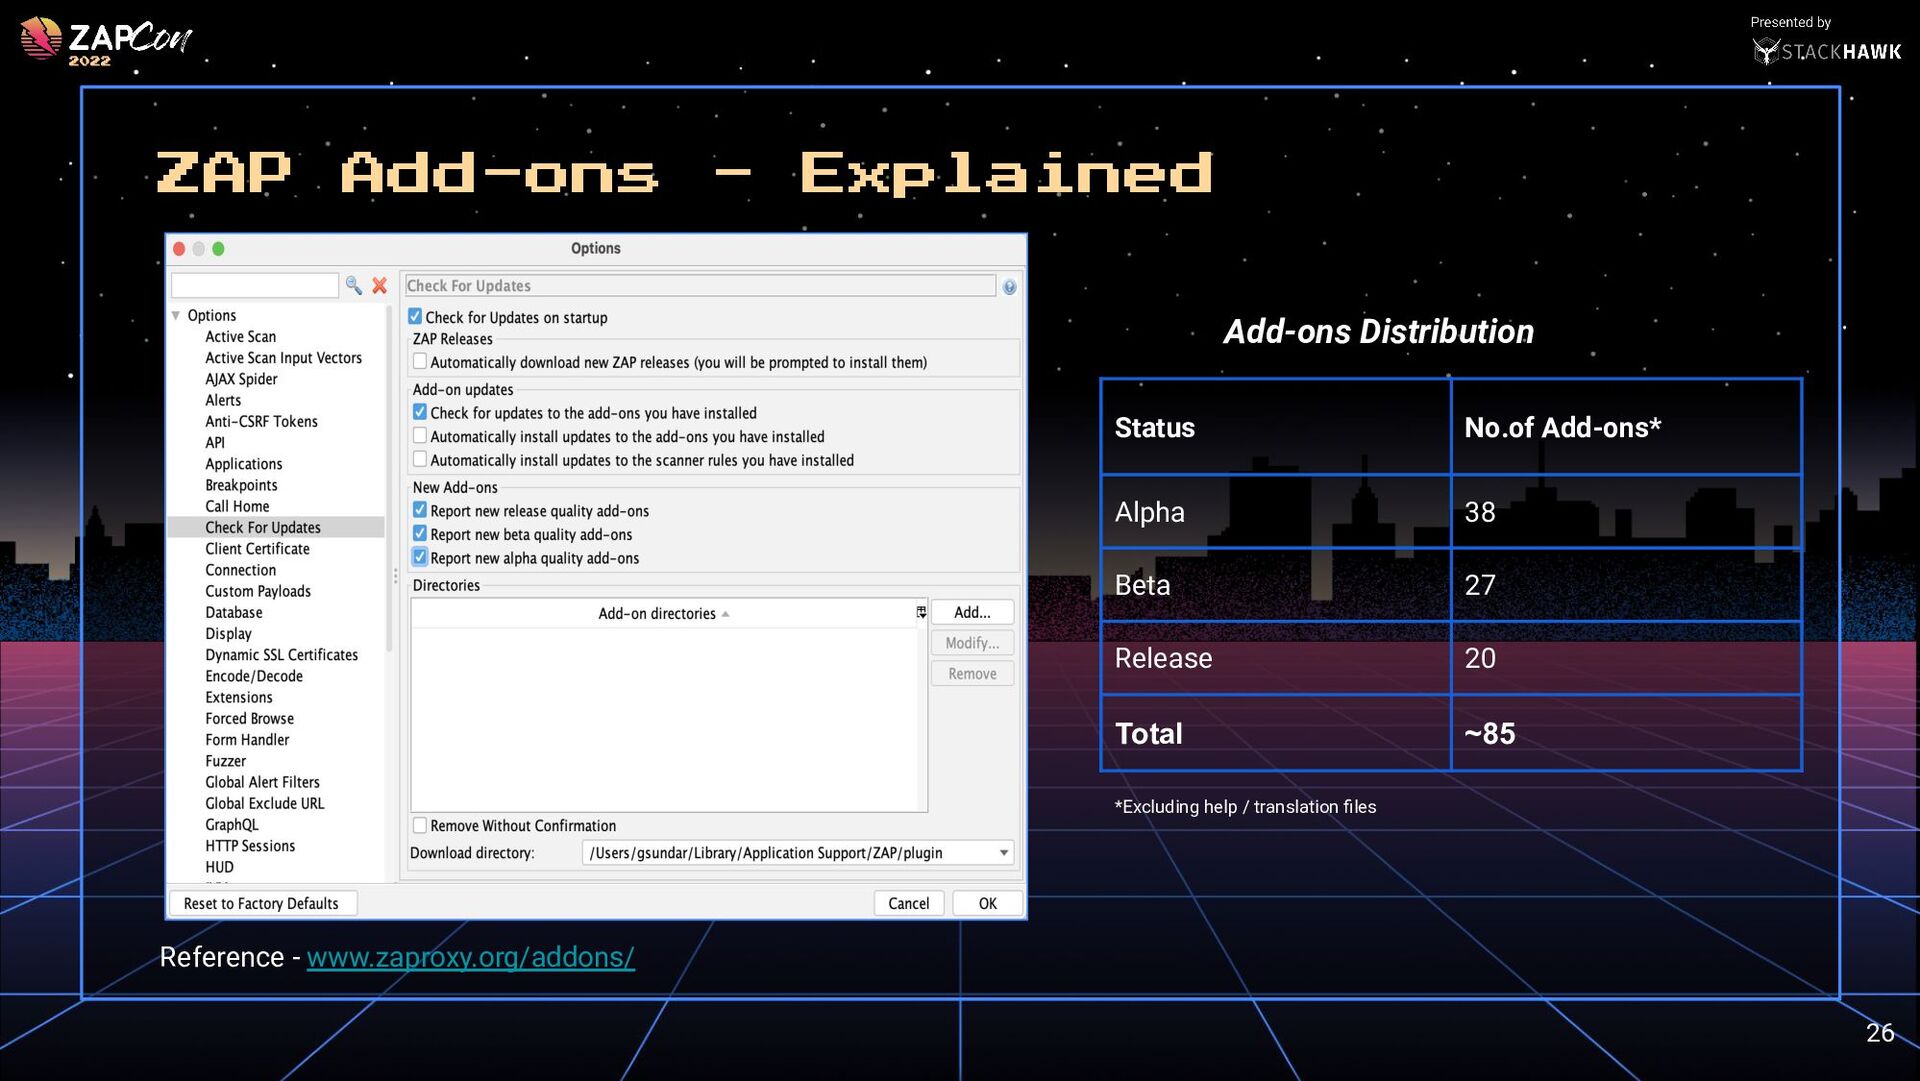
  16. ZAP Add-ons - Explained Add-ons Distribution Status No.of Add-ons* Alpha

    38 Beta 27 Release 20 Total ~85 *Excluding help / translation files Reference - www.zaproxy.org/addons/ 26
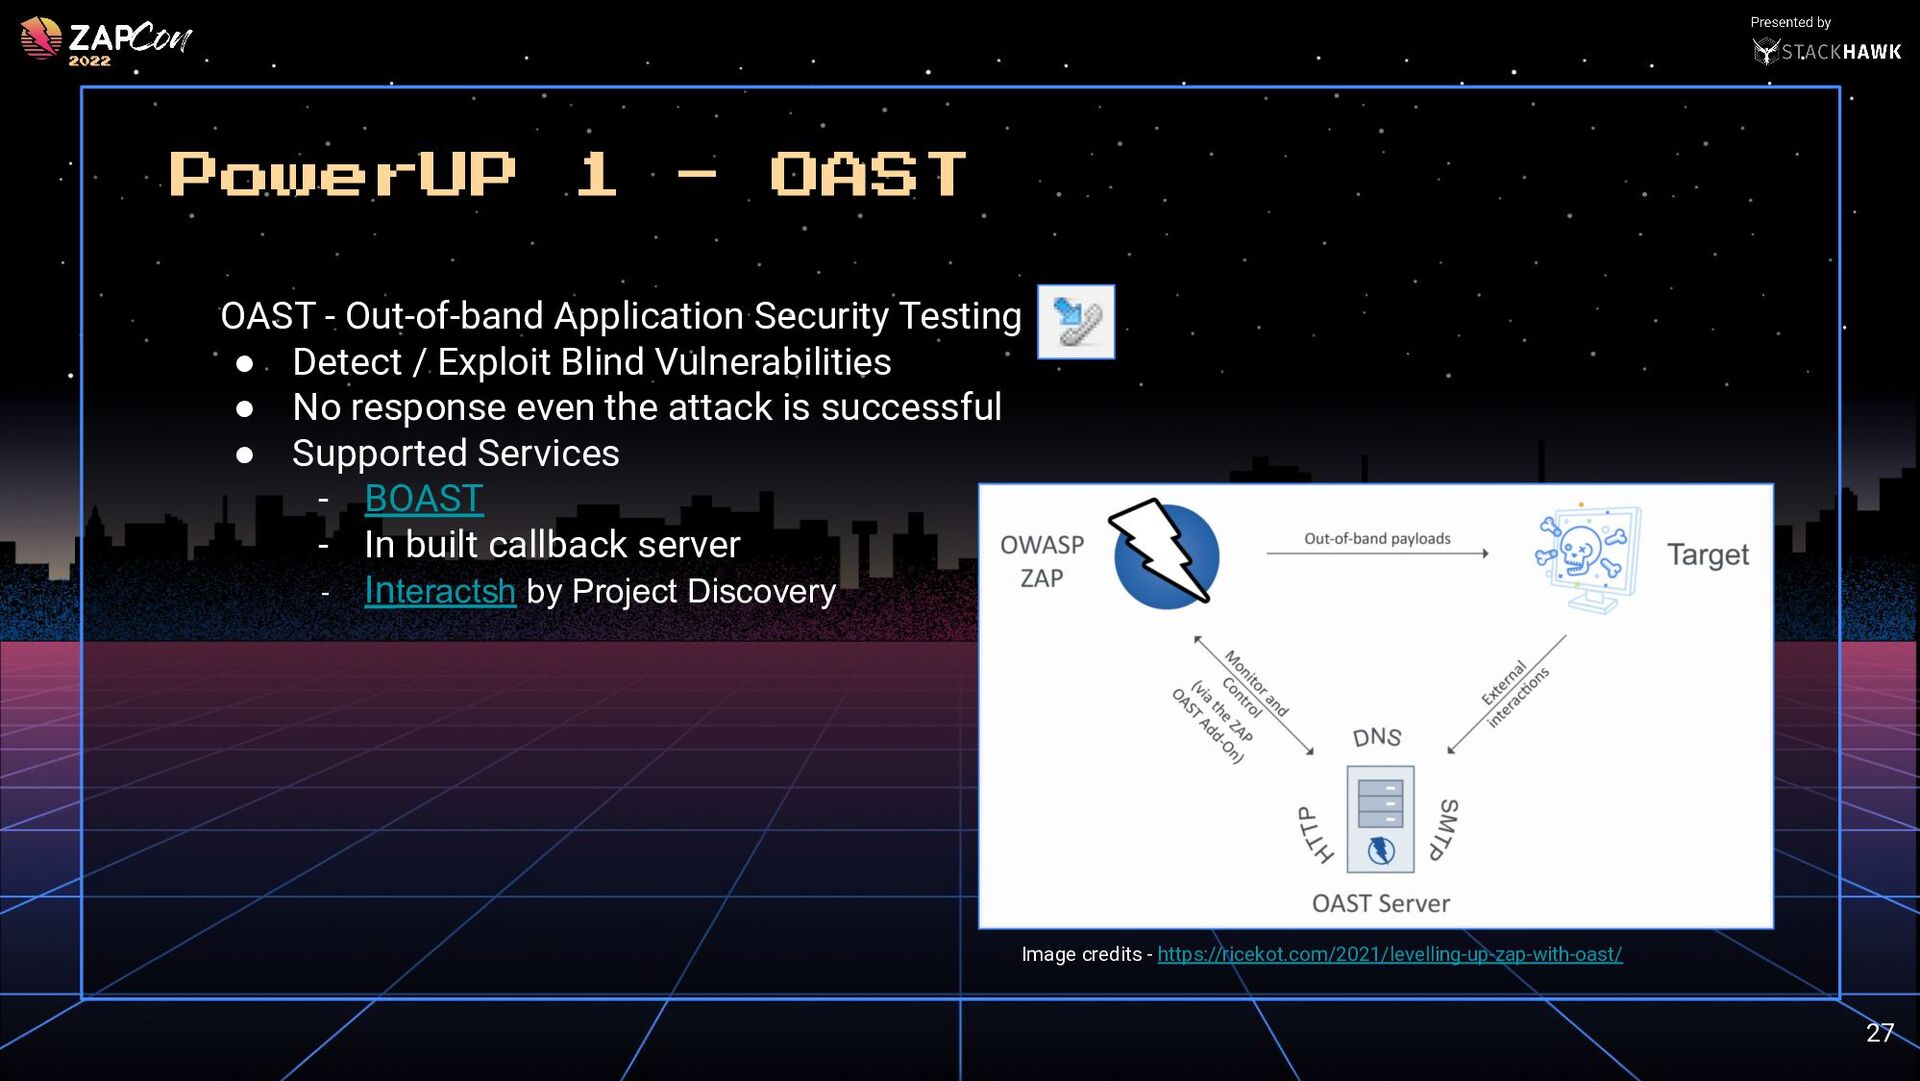
  17. PowerUP 1 - OAST OAST - Out-of-band Application Security Testing

    • Detect / Exploit Blind Vulnerabilities • No response even the attack is successful • Supported Services - BOAST - In built callback server - Interactsh by Project Discovery Image credits - https://ricekot.com/2021/levelling-up-zap-with-oast/ 27
  18. Vulnerability Coverage - Server Side Request Forgery (SSRF) - Out-of-band

    (OOB) XML-External -Entity Injection(XXE) - Blind Cross Site Scripting - Bling SQL Injection - Other External Service Interactions 28
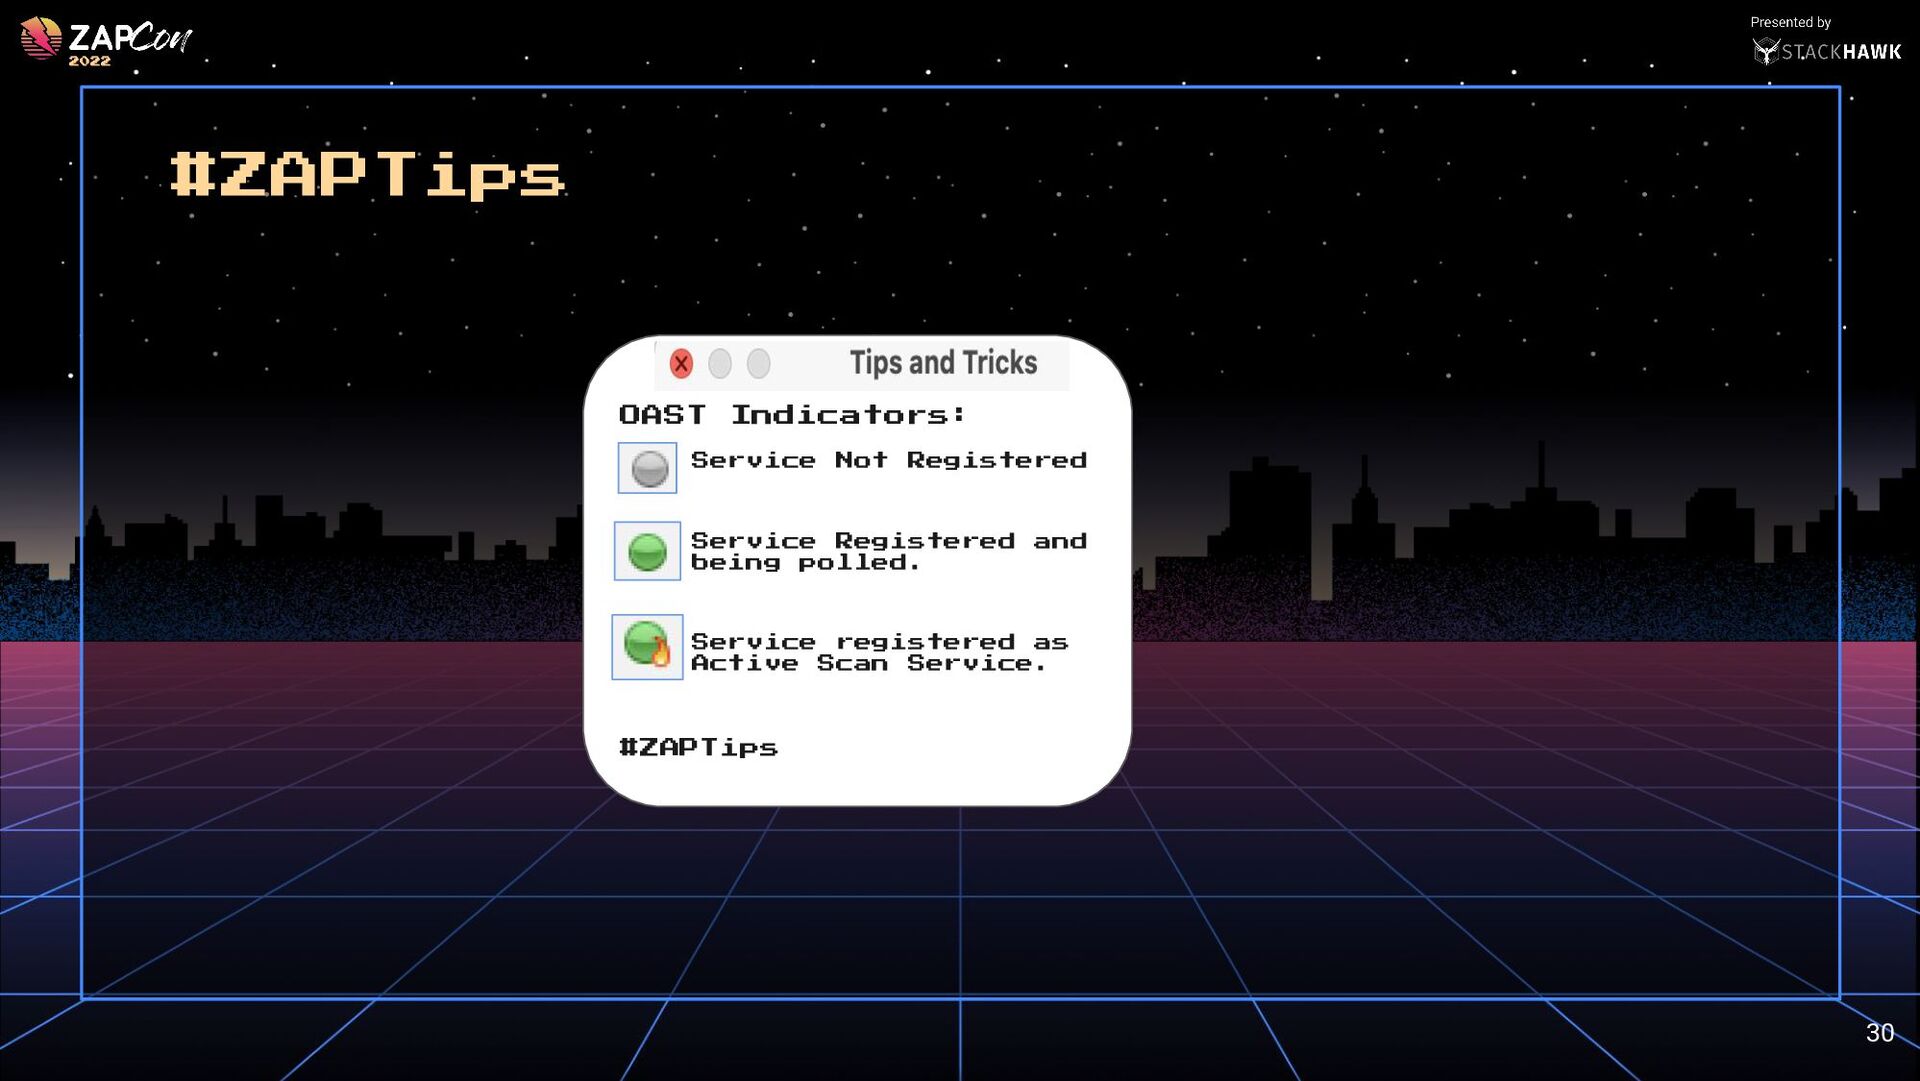
  19. #ZAPTips 30 OAST Indicators: Service Not Registered Service Registered and

    being polled. Service registered as Active Scan Service. #ZAPTips
  20. PowerUP 2 - Automation Framework Automation Framework • Replacement for

    Command Line / Packaged Scan options • Easy and flexible Automation • Controlled via Single YAML File • Customized • Job based actions 31
  21. Quick Demo - Automation Framework 32 The automation framework supports

    all type of authentication supported by ZAP. #ZAPTips
  22. PowerUP 3 - Websockets WebSockets - • Intercept / Fuzz

    WebSocket messages • Breakpoints on specific types of WebSocket messages • Scan WebSockets Passively • Custom Scripts for websockets 33
  23. Quick Demo - Websockets 34 Use the Cross Site Website

    Hijacking.js script rule to detect/validate XSWH attacks. #ZAPTips
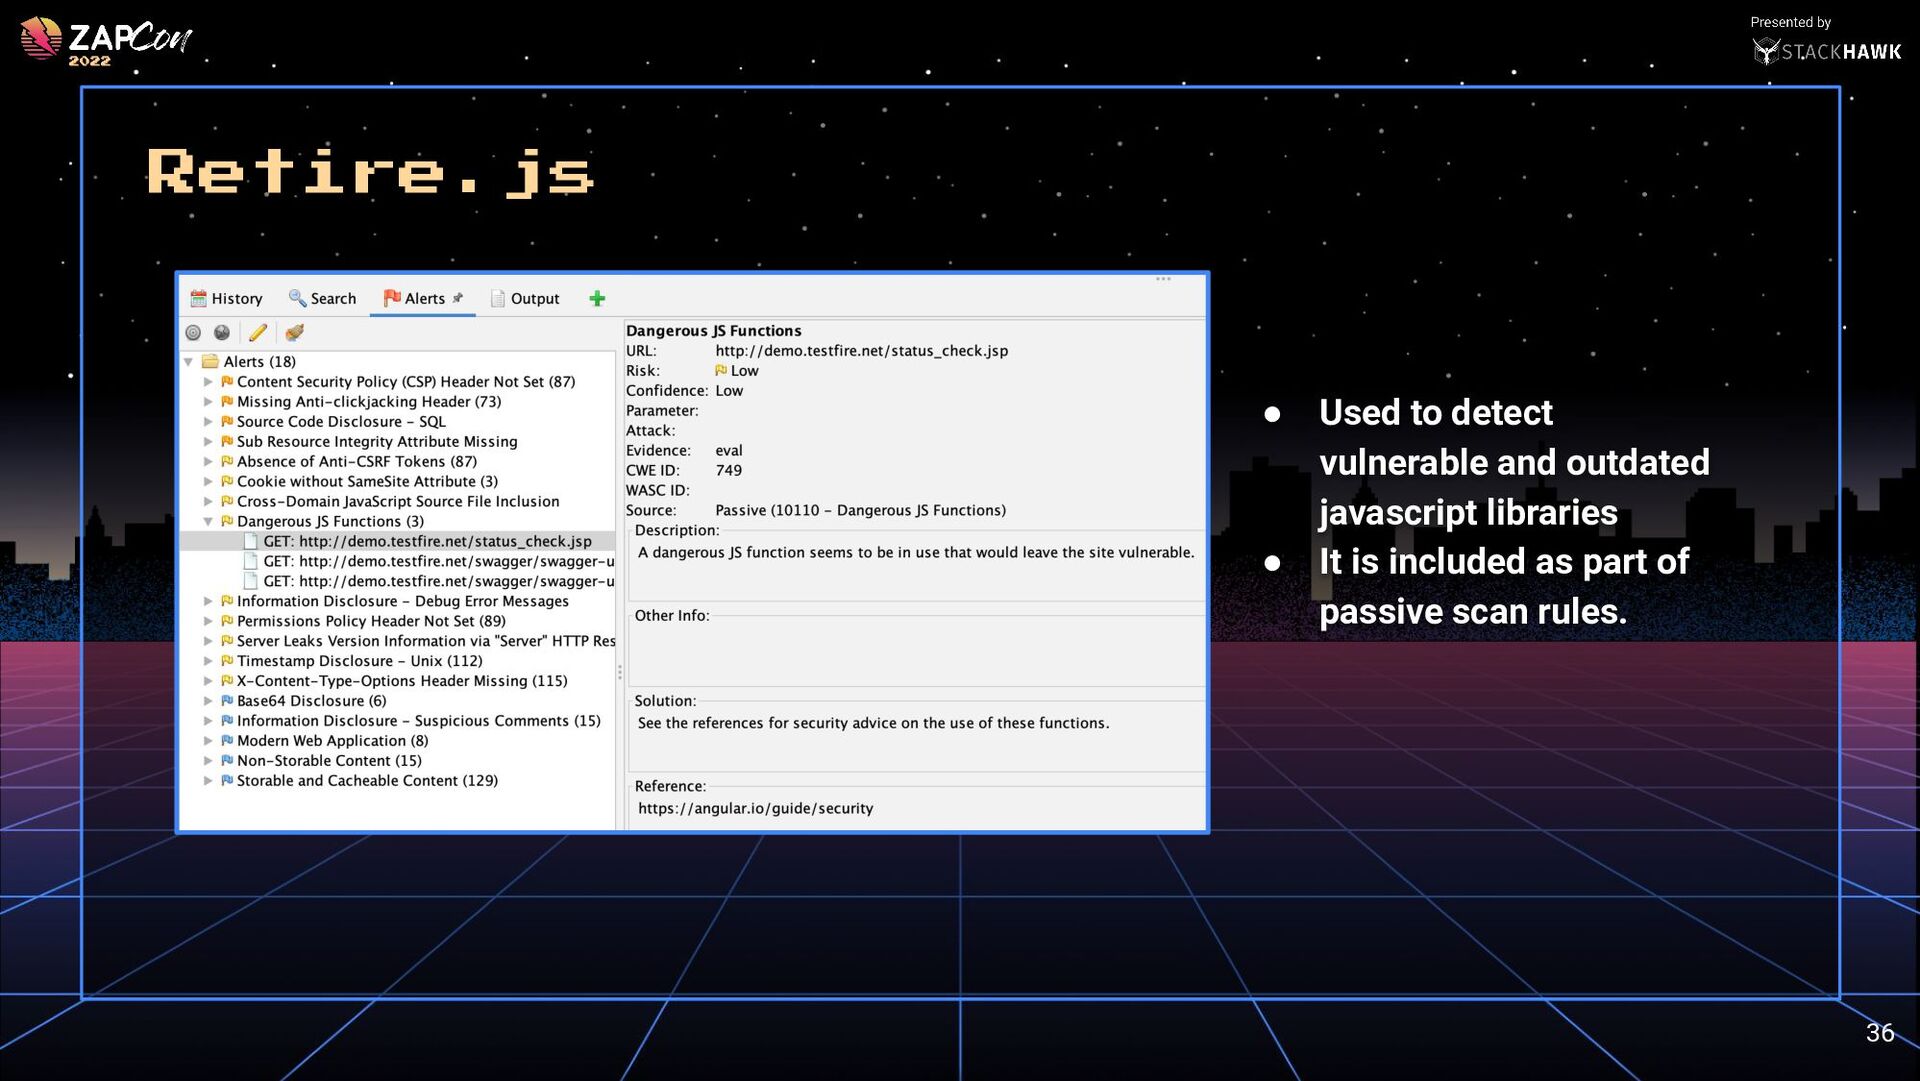
  24. Retire.js • Used to detect vulnerable and outdated javascript libraries
    • It is included as part of passive scan rules. 36
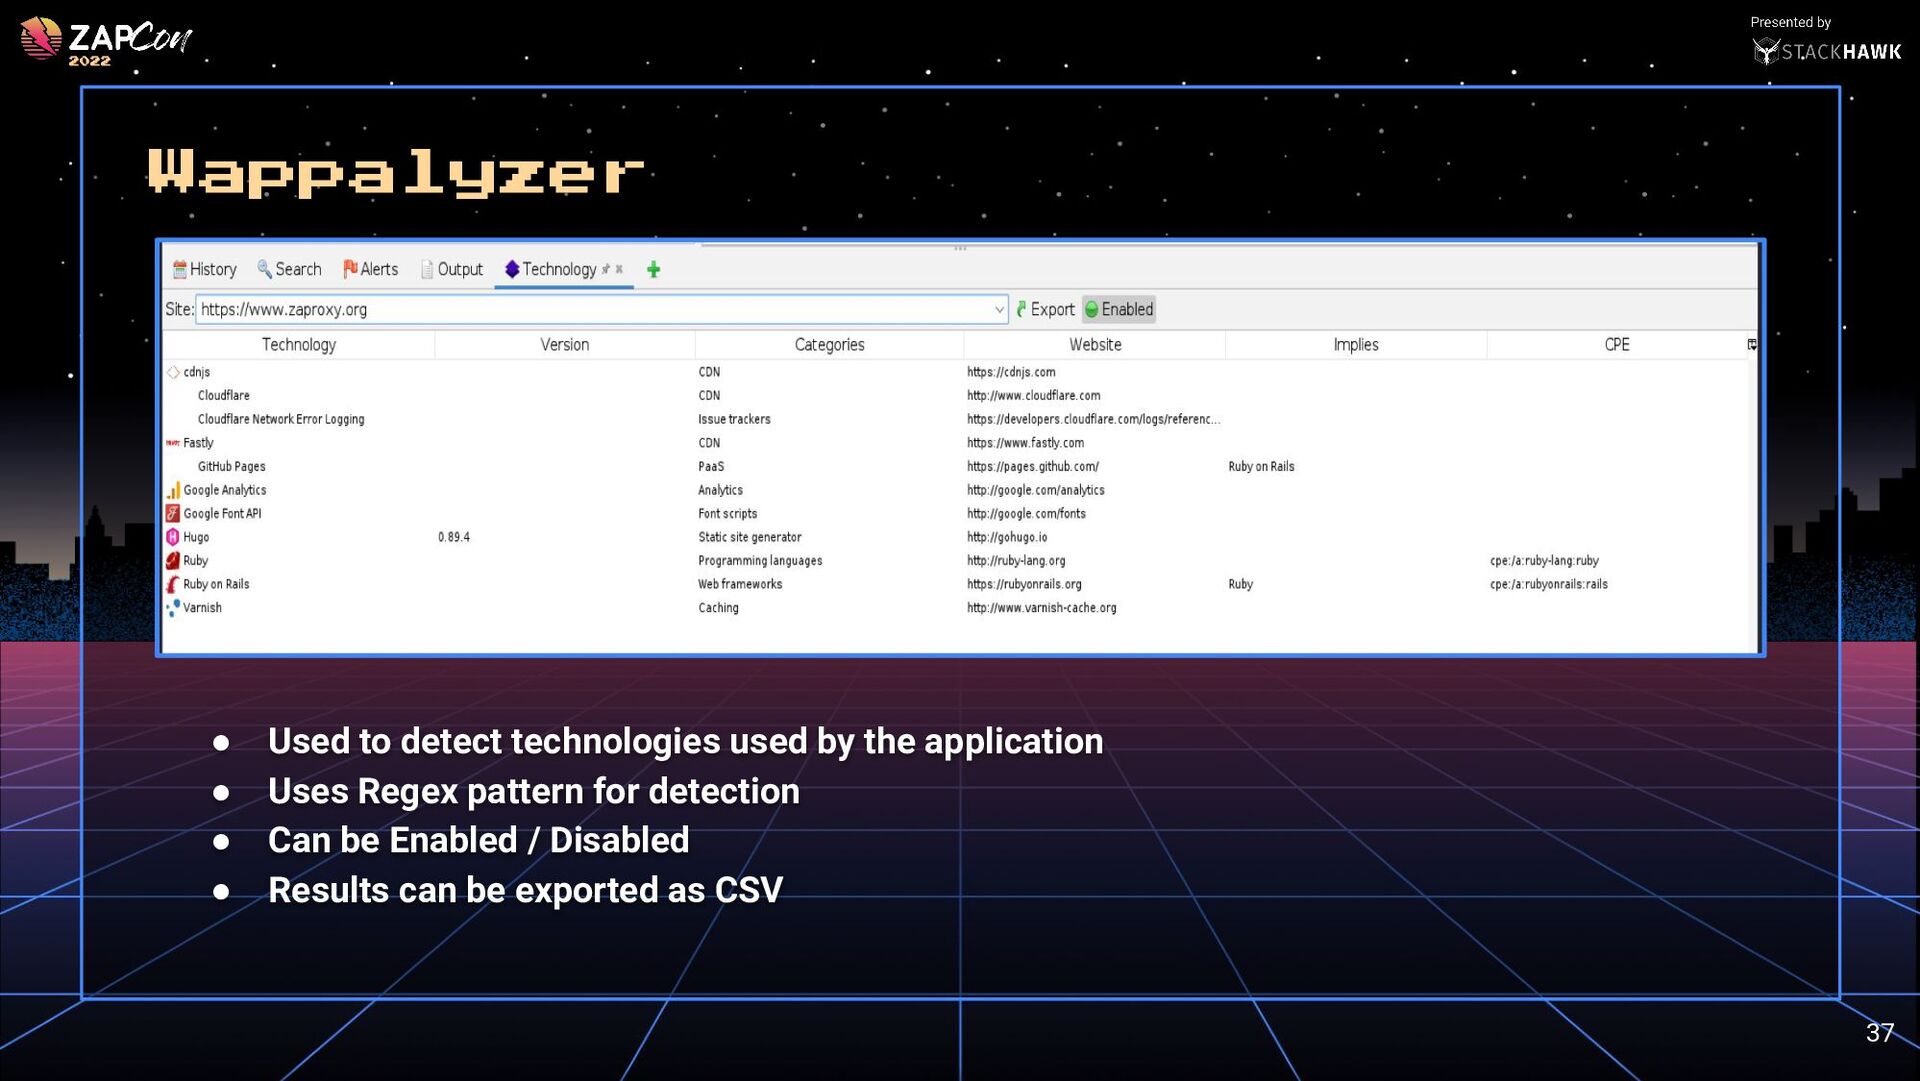
  25. Wappalyzer • Used to detect technologies used by the application
    • Uses Regex pattern for detection • Can be Enabled / Disabled • Results can be exported as CSV 37
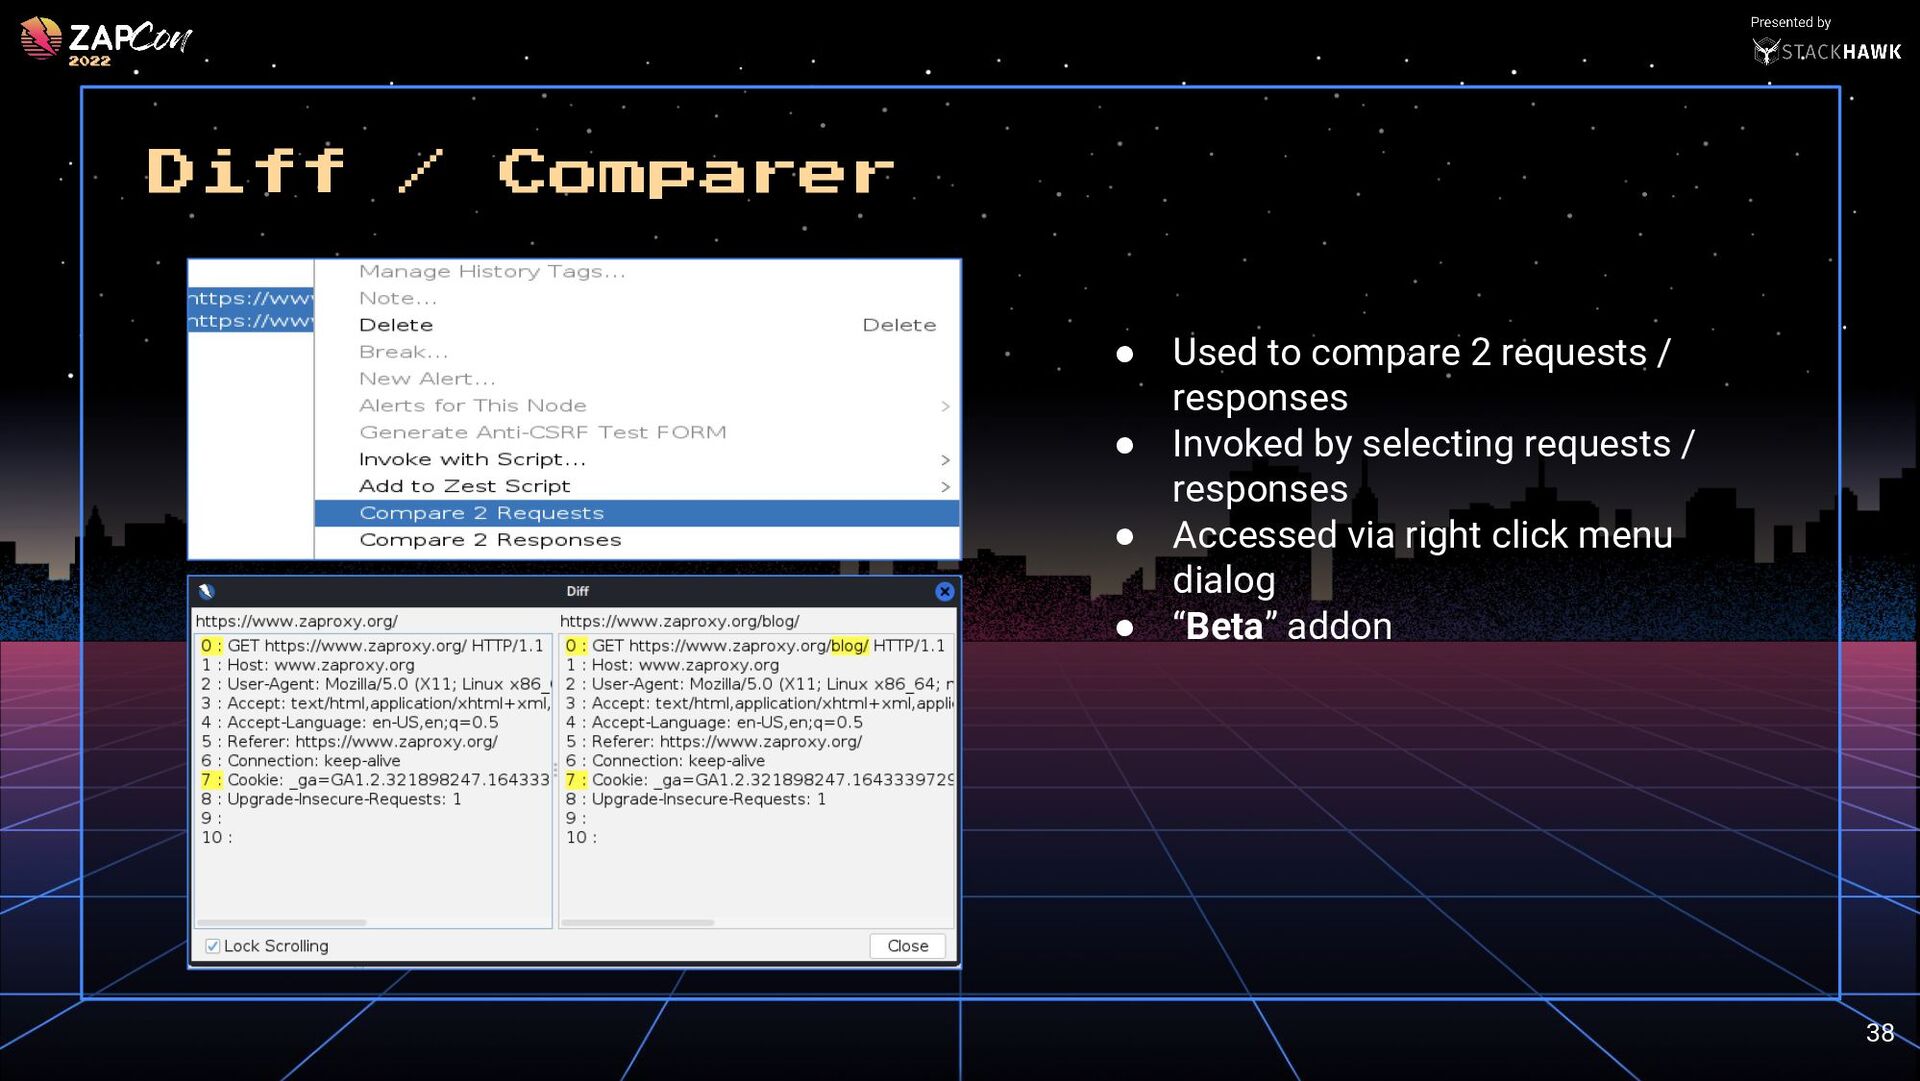
  26. Diff / Comparer • Used to compare 2 requests /

    responses • Invoked by selecting requests / responses • Accessed via right click menu dialog • “Beta” addon 38
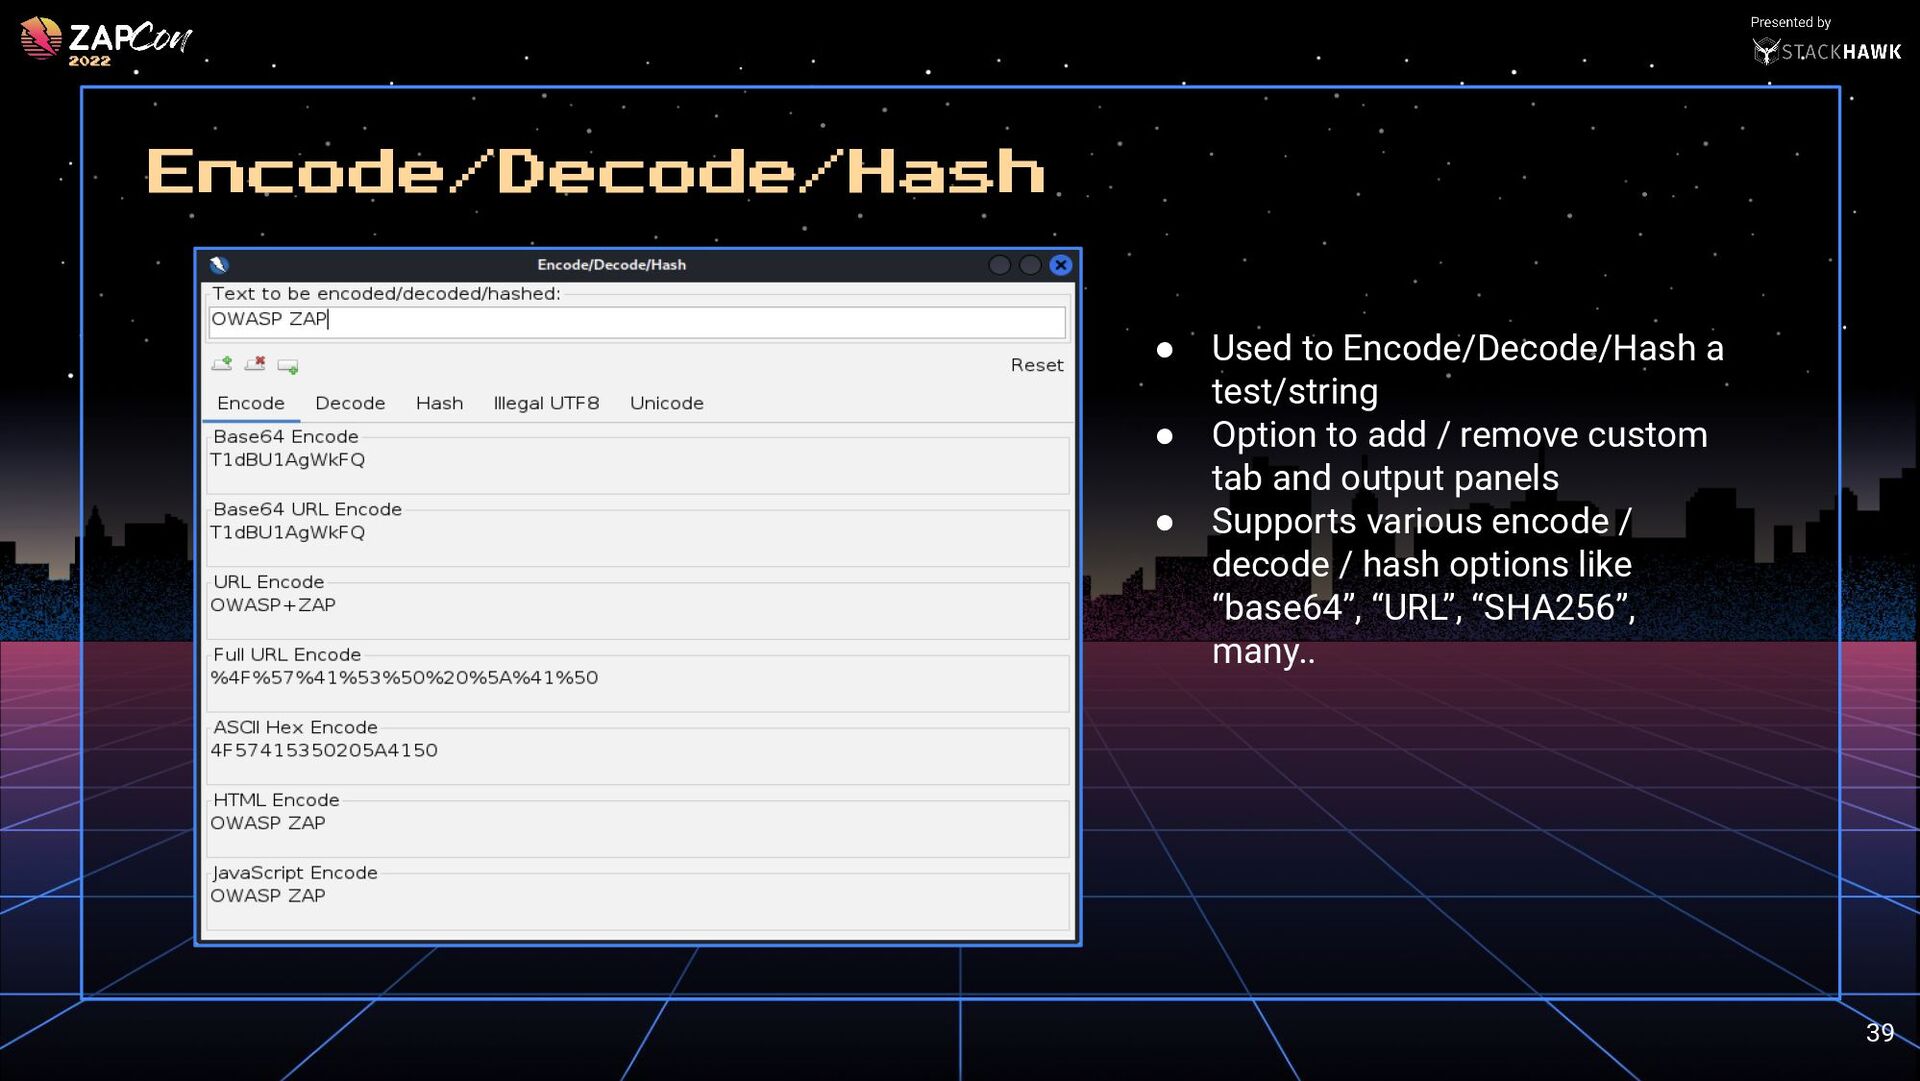
  27. Encode/Decode/Hash • Used to Encode/Decode/Hash a test/string • Option to

    add / remove custom tab and output panels • Supports various encode / decode / hash options like “base64”, “URL”, “SHA256”, many.. 39
  28. Generate CSRF Test Form • Used for testing Cross Site

    Request Forgery Vulnerabilities • Create easy CSRF PoC file 40
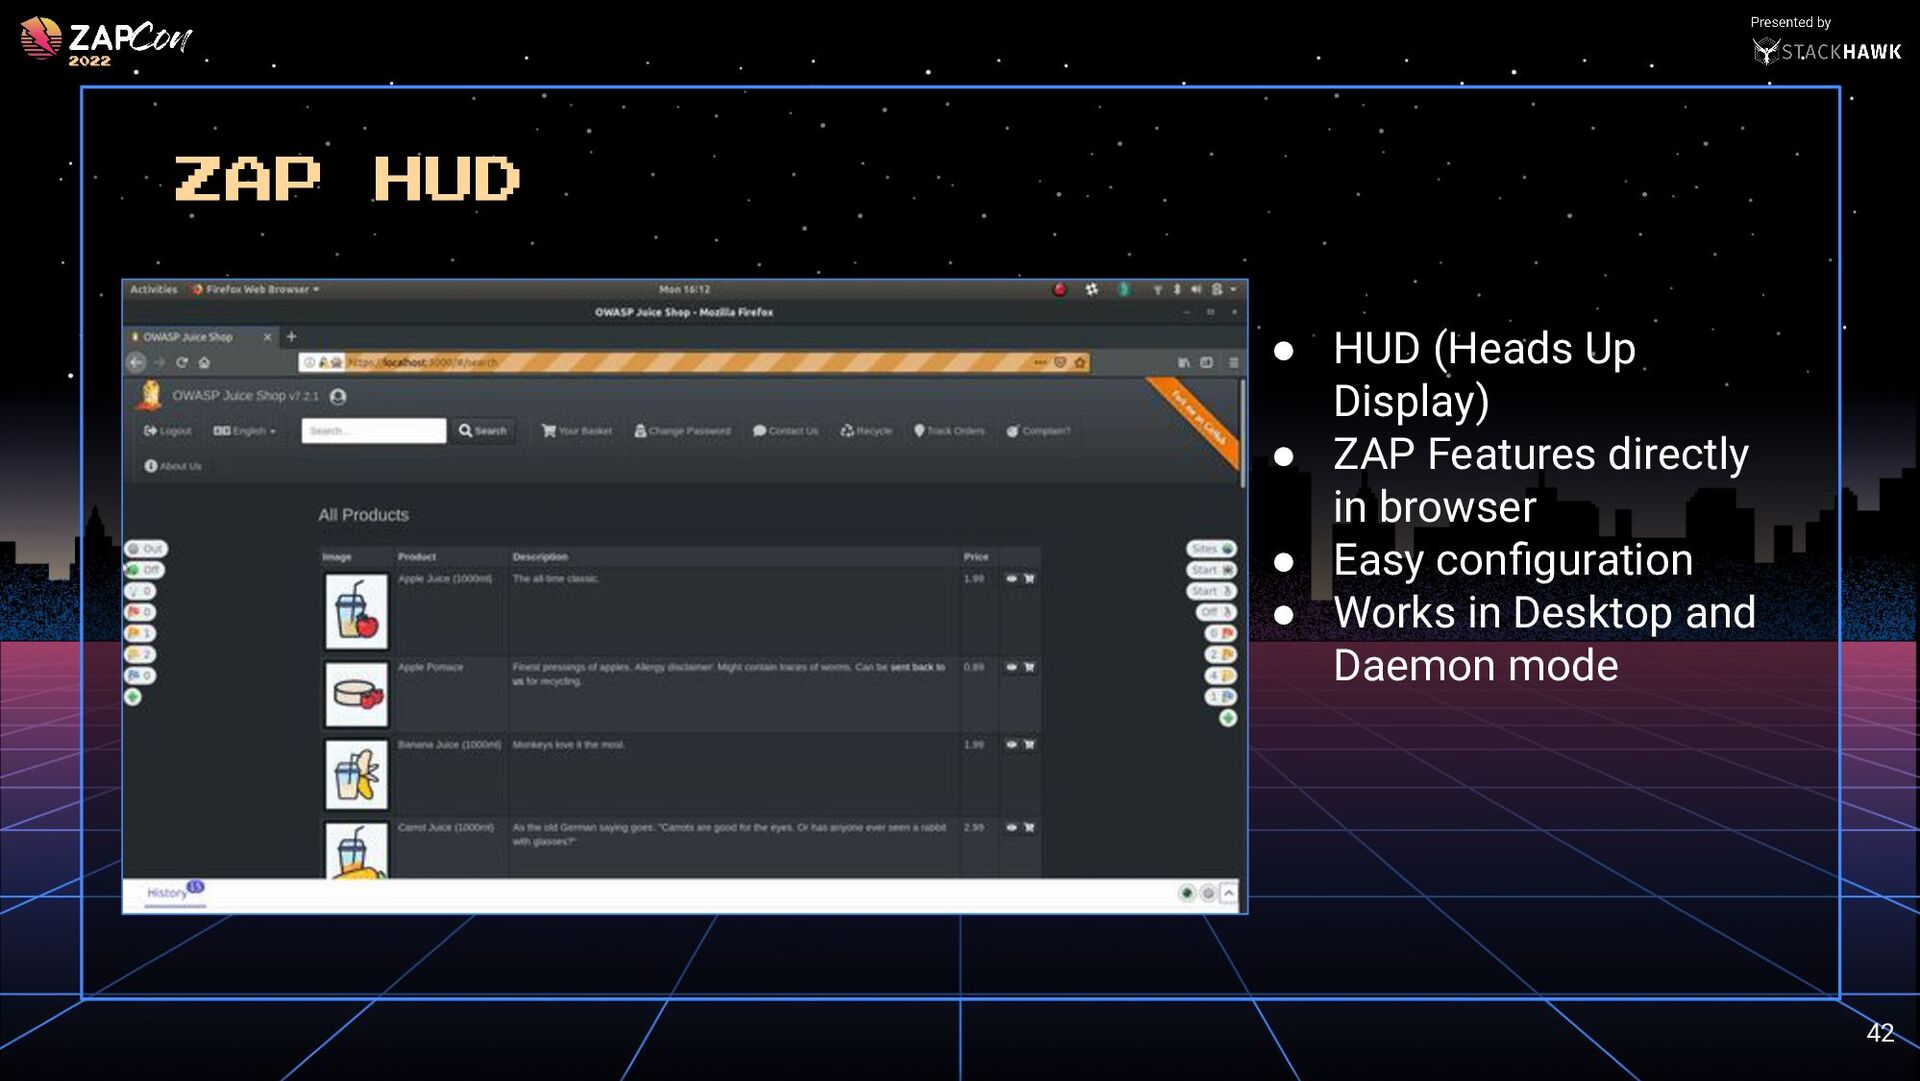
  29. ZAP HUD 42 • HUD (Heads Up Display) • ZAP

    Features directly in browser • Easy configuration • Works in Desktop and Daemon mode
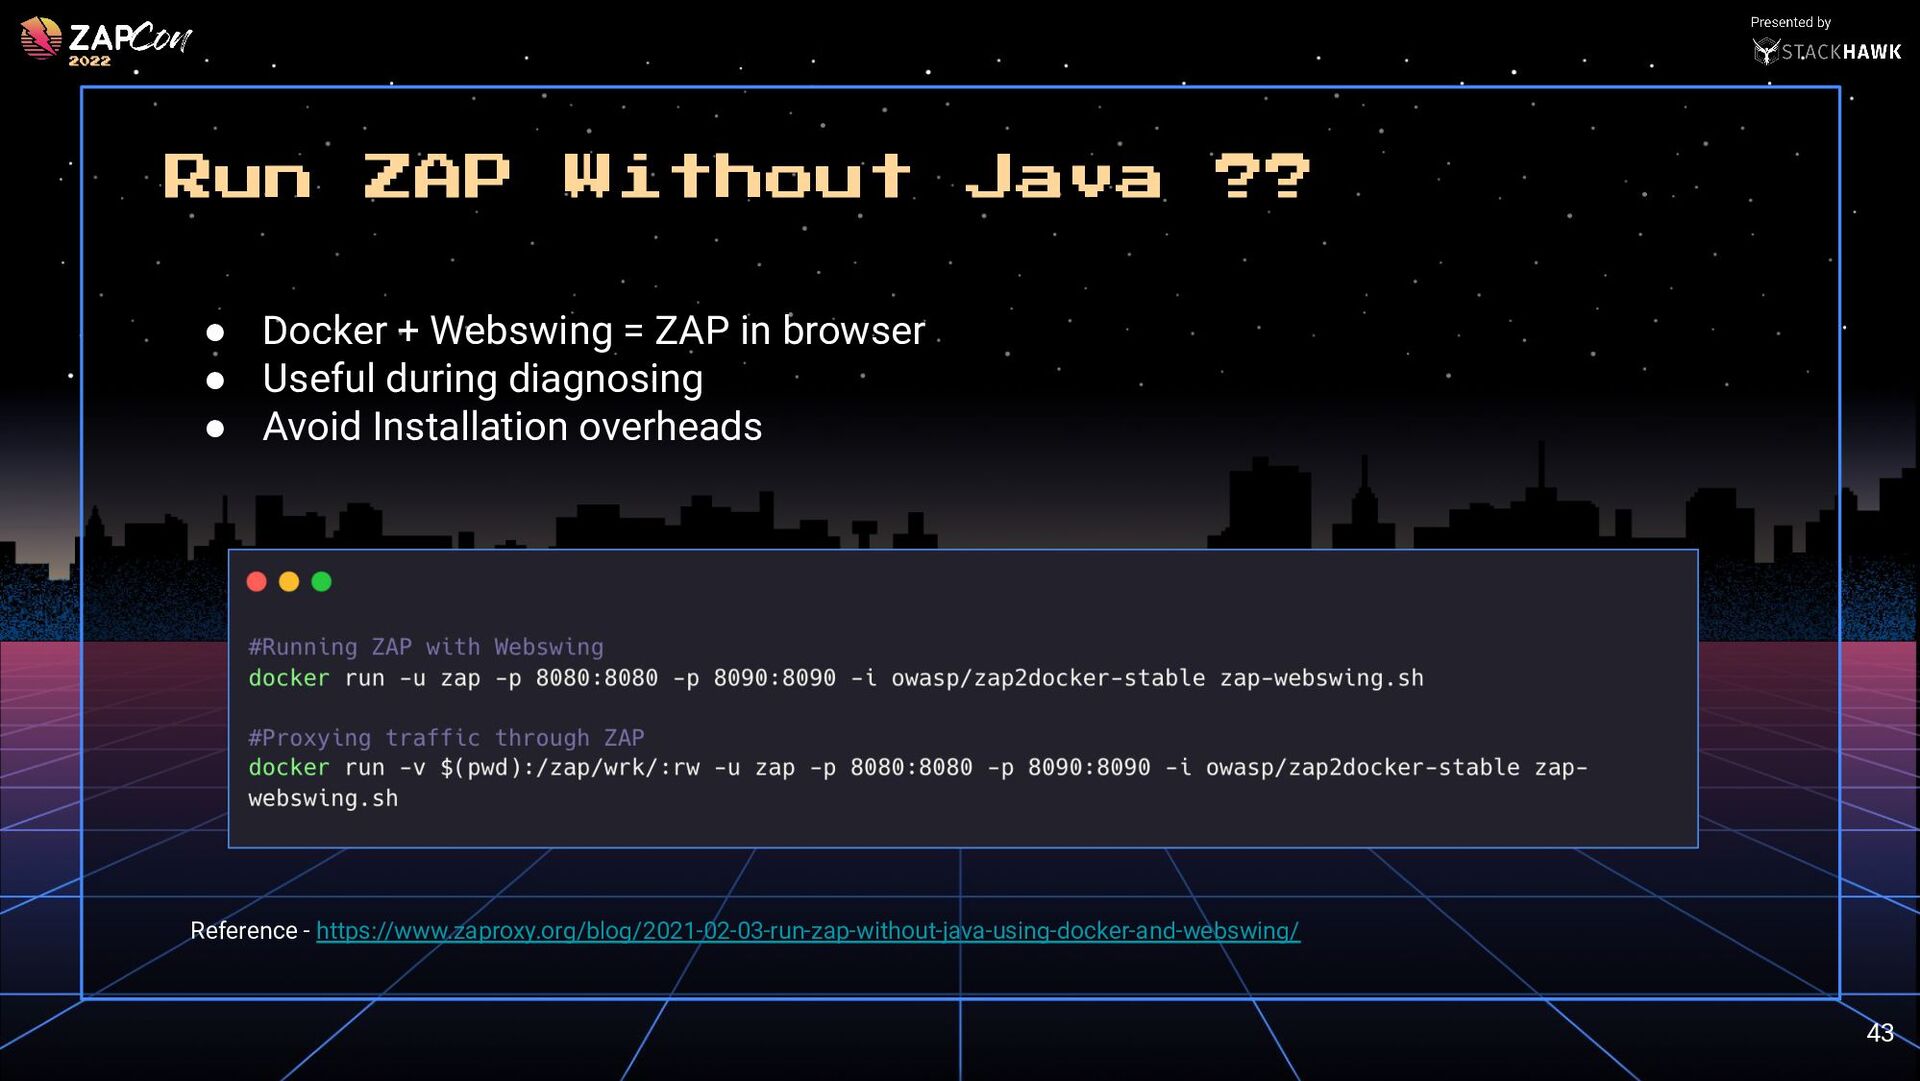
  30. Run ZAP Without Java ?? 43 • Docker + Webswing

    = ZAP in browser • Useful during diagnosing • Avoid Installation overheads Reference - https://www.zaproxy.org/blog/2021-02-03-run-zap-without-java-using-docker-and-webswing/
  31. References / Resources 46 • Extensive Documentation - https://www.zaproxy.org/docs/ •

    https://www.zaproxy.org/docs/guides/zapping-the-top-10-2021/ • https://www.zaproxy.org/addons/ • https://manosmagnus.github.io/posts/websocket-passive-scan-using-scripts- with-zap/ • https://github.com/zaproxy/community-scripts • https://www.zaproxy.org/videos/