Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
dev_server_proxyのススメ
Search
hirasa
December 06, 2021
Technology
180
0
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
dev_server_proxyのススメ
dev_server_proxyのススメ
hirasa
December 06, 2021
More Decks by hirasa
See All by hirasa
redux使うのやめました
hirasa
1
630
eslintのプラグインを作成した話
hirasa
1
140
Other Decks in Technology
See All in Technology
Context Ontology Accelerator 入門 (業務データの意味を、AI エージェントに渡す)
inariku
PRO
3
510
企画からFlutter実装まで、1つの機能を一貫して開発したプロセスと成果物
khiroyuki1003
1
160
GCASアップデート(202607-202610)
techniczna
1
220
【dbts2026】AIエージェントの 判断と探索を変える、 データベース エンジニアリング― 既存DBの処理と依存関係から作る、オペレーショナルオントロジー ―
shisyu_gaku
0
230
新米を「売り越さない」、Aurora DSQLで作る在庫ゼロ死守の限定ドロップEC
yama3133
0
190
会社説明資料_最新版
demaecan
0
32k
生成AI時代のIAMのマニアックな話
takuros
6
2.7k
AI時代の組織作り:チーム開発から「個人×AI」への移行と、持続可能な「開発資本」の築き方
ham0215
2
300
少ない人手 限られた予算 それでも守る 消せない・見つける・戻れる オールハザード型BCP on AWS / 20261107 Mitsutoshi Matsuo
shift_evolve
PRO
0
210
FinOpsを導入してマルチプロダクトのコスト最適化を実現する
kworkdev
PRO
0
140
Sinatra on PicoRuby ローカルでセルフホスト
bash0c7
0
110
AIコーディングはじめました
miso
0
150
Featured
See All Featured
Groundhog Day: Seeking Process in Gaming for Health
codingconduct
0
470
Side Projects
sachag
456
43k
"I'm Feeling Lucky" - Building Great Search Experiences for Today's Users (#IAC19)
danielanewman
230
23k
GraphQLとの向き合い方2022年版
quramy
50
15k
Keith and Marios Guide to Fast Websites
keithpitt
413
23k
Money Talks: Using Revenue to Get Sh*t Done
nikkihalliwell
0
550
JavaScript: Past, Present, and Future - NDC Porto 2020
reverentgeek
52
6.2k
How to build a perfect <img>
jonoalderson
1
6.2k
The Psychology of Web Performance [Beyond Tellerrand 2023]
tammyeverts
49
3.6k
Building Experiences: Design Systems, User Experience, and Full Site Editing
marktimemedia
1
660
A brief & incomplete history of UX Design for the World Wide Web: 1989–2019
jct
2
560
B2B Lead Gen: Tactics, Traps & Triumph
marketingsoph
1
300
Transcript
Dev server – proxyのススメ 平崎 葵(ひらさき まもる) 2021/12/06
自己紹介 平崎 葵 (ひらさき まもる) クーガー株式会社 所属 https://couger.co.jp/ ◦フロントエンド、サーバサイドエンジニア ◦バーチャルヒューマンエージェントの開発
趣味:音楽、ドラム、作曲
発表内容 Dev serverのproxy機能を使用して、 効率よくcors対策をしよう。
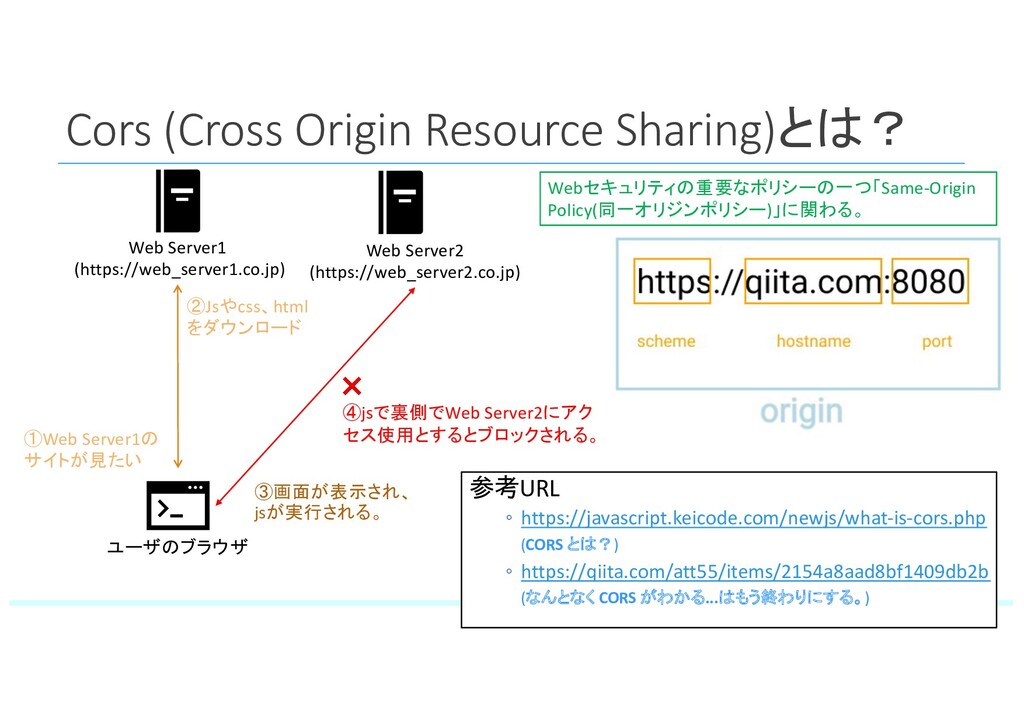
Cors (Cross Origin Resource Sharing)とは? Web Server1 (https://web_server1.co.jp) Web Server2
(https://web_server2.co.jp) ユーザのブラウザ ②Jsやcss、html をダウンロード ①Web Server1の サイトが見たい ③画面が表示され、 jsが実行される。 ❌ ④jsで裏側でWeb Server2にアク セス使用とするとブロックされる。 Webセキュリティの重要なポリシーの一つ「Same-Origin Policy(同一オリジンポリシー)」に関わる。 参考URL ◦ https://javascript.keicode.com/newjs/what-is-cors.php (CORS とは?) ◦ https://qiita.com/att55/items/2154a8aad8bf1409db2b (なんとなく CORS がわかる...はもう終わりにする。)
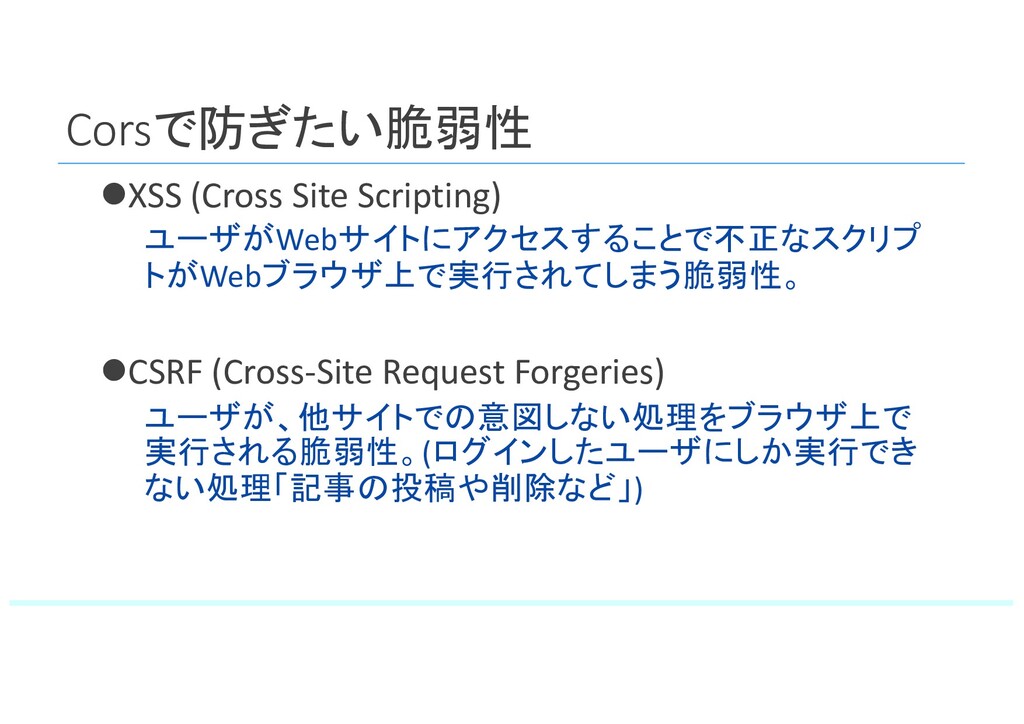
Corsで防ぎたい脆弱性 lXSS (Cross Site Scripting) ユーザがWebサイトにアクセスすることで不正なスクリプ トがWebブラウザ上で実行されてしまう脆弱性。 lCSRF (Cross-Site Request
Forgeries) ユーザが、他サイトでの意図しない処理をブラウザ上で 実行される脆弱性。(ログインしたユーザにしか実行でき ない処理「記事の投稿や削除など」)
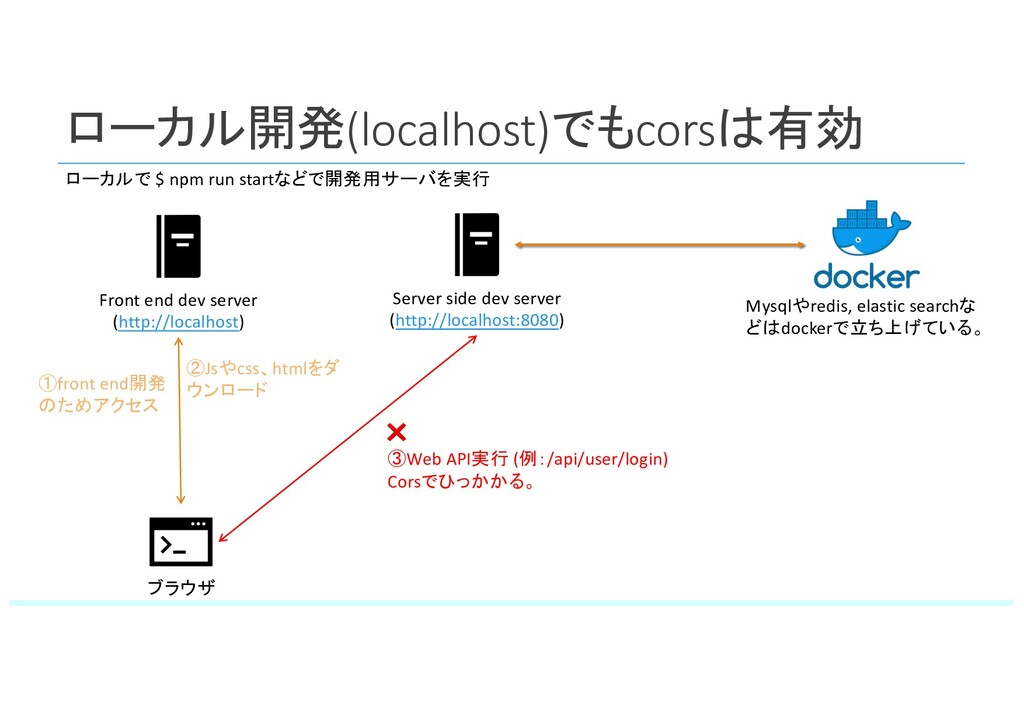
ローカル開発(localhost)でもcorsは有効 Front end dev server (http://localhost) Server side dev server
(http://localhost:8080) ローカルで $ npm run startなどで開発用サーバを実行 Mysqlやredis, elastic searchな どはdockerで立ち上げている。 ブラウザ ②Jsやcss、htmlをダ ウンロード ①front end開発 のためアクセス ❌ ③Web API実行 (例:/api/user/login) Corsでひっかかる。
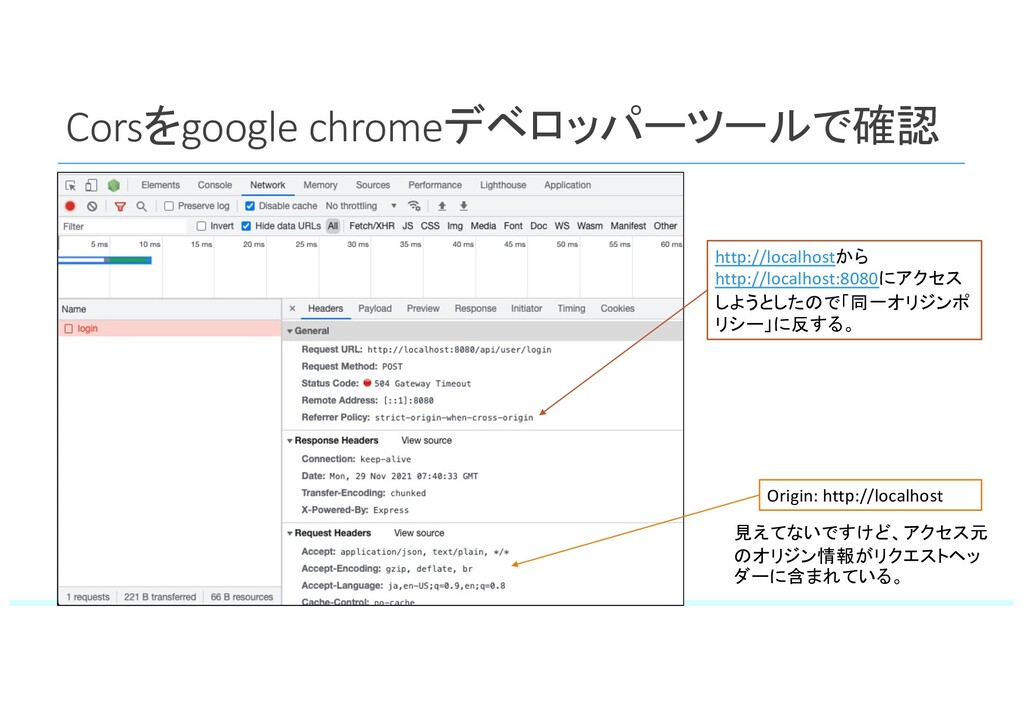
Corsをgoogle chromeデベロッパーツールで確認 http://localhostから http://localhost:8080にアクセス しようとしたので「同一オリジンポ リシー」に反する。 Origin: http://localhost 見えてないですけど、アクセス元 のオリジン情報がリクエストヘッ
ダーに含まれている。
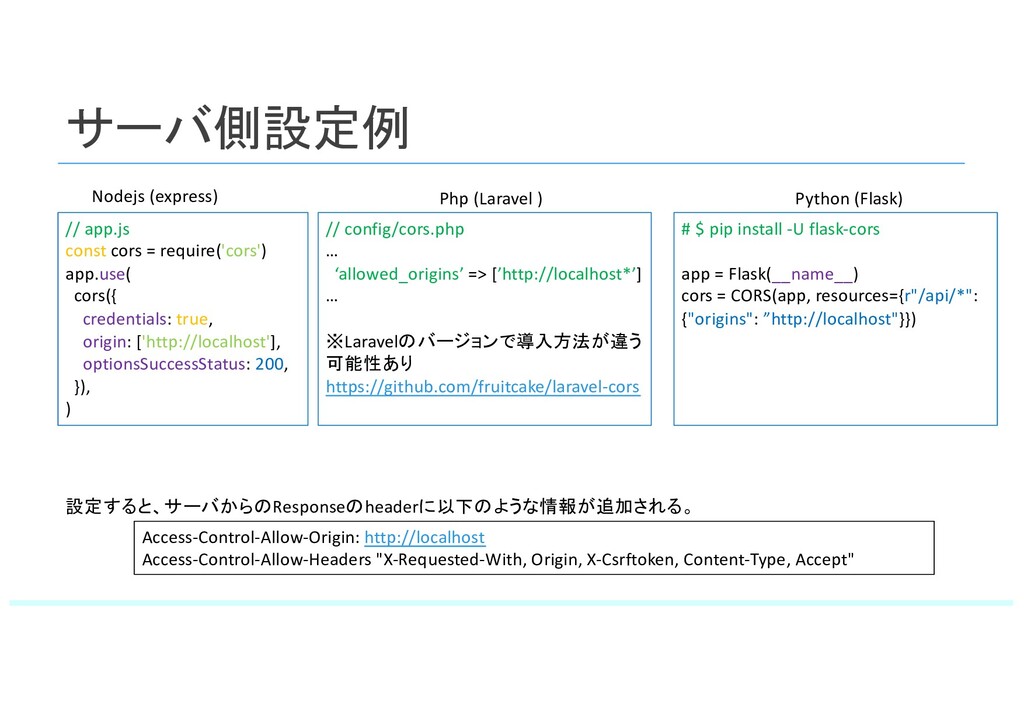
Corsはサーバ側で許可することで回避できる。 l Laravelの場合 https://qiita.com/kyo-san/items/a507aa0b46037df1b139 (LaravelでのCORS対策とmiddlewareへの理解) https://github.com/fruitcake/laravel-cors l Nodejs (express)の場合 https://expressjs.com/en/resources/middleware/cors.ht
ml l Python (flask)の場合 https://flask-cors.readthedocs.io/en/latest/
サーバ側設定例 // app.js const cors = require('cors') app.use( cors({ credentials:
true, origin: ['http://localhost'], optionsSuccessStatus: 200, }), ) Nodejs (express) Php (Laravel ) // config/cors.php … ‘allowed_origins’ => [’http://localhost*’] … ※Laravelのバージョンで導入方法が違う 可能性あり https://github.com/fruitcake/laravel-cors Python (Flask) # $ pip install -U flask-cors app = Flask(__name__) cors = CORS(app, resources={r"/api/*": {"origins": ”http://localhost"}}) Access-Control-Allow-Origin: http://localhost Access-Control-Allow-Headers "X-Requested-With, Origin, X-Csrftoken, Content-Type, Accept" 設定すると、サーバからのResponseのheaderに以下のような情報が追加される。
サーバサイドにcors対策を入れて解決はできた。 しかし、フロントのdev serverのproxyの機能を使えば、 サーバサイドに手を入れることなくcors対策ができる。
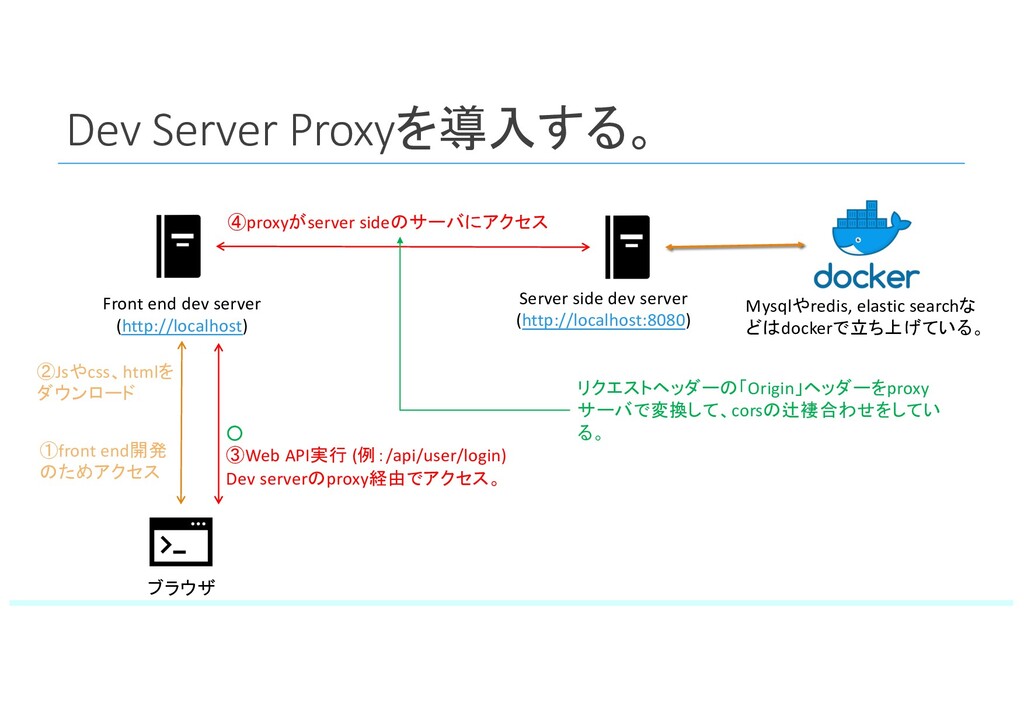
Dev Server Proxyを導入する。 Front end dev server (http://localhost) Server side
dev server (http://localhost:8080) Mysqlやredis, elastic searchな どはdockerで立ち上げている。 ブラウザ ②Jsやcss、htmlを ダウンロード ①front end開発 のためアクセス ◦ ③Web API実行 (例:/api/user/login) Dev serverのproxy経由でアクセス。 ④proxyがserver sideのサーバにアクセス リクエストヘッダーの「Origin」ヘッダーをproxy サーバで変換して、corsの辻褄合わせをしてい る。
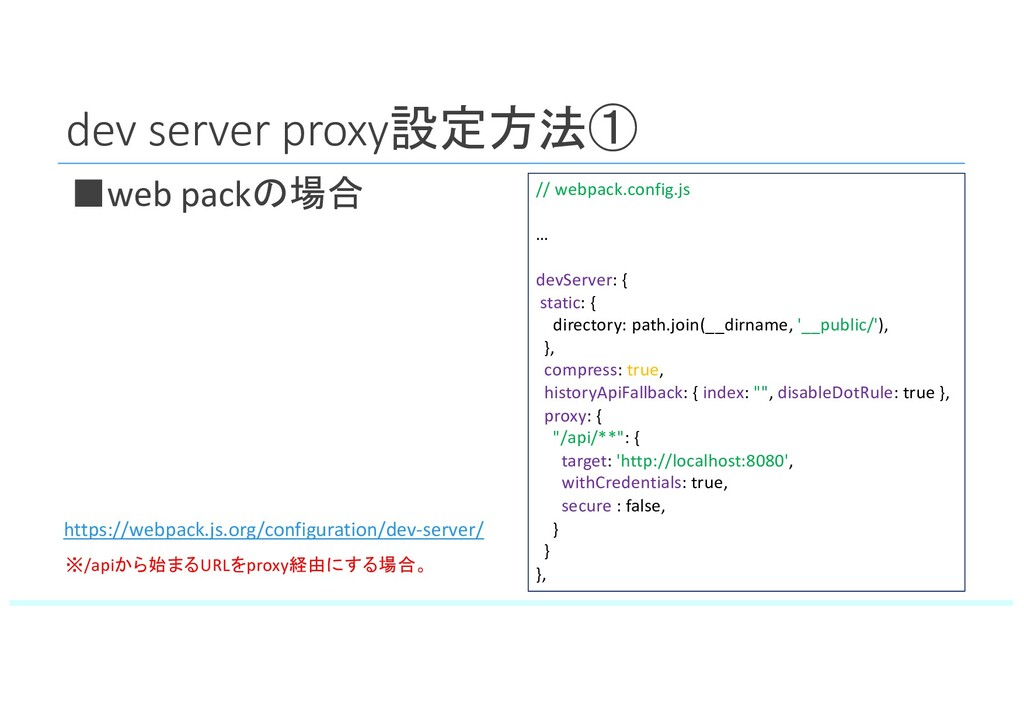
dev server proxy設定方法① ▪web packの場合 // webpack.config.js … devServer: {
static: { directory: path.join(__dirname, '__public/'), }, compress: true, historyApiFallback: { index: "", disableDotRule: true }, proxy: { "/api/**": { target: 'http://localhost:8080', withCredentials: true, secure : false, } } }, ※/apiから始まるURLをproxy経由にする場合。 https://webpack.js.org/configuration/dev-server/
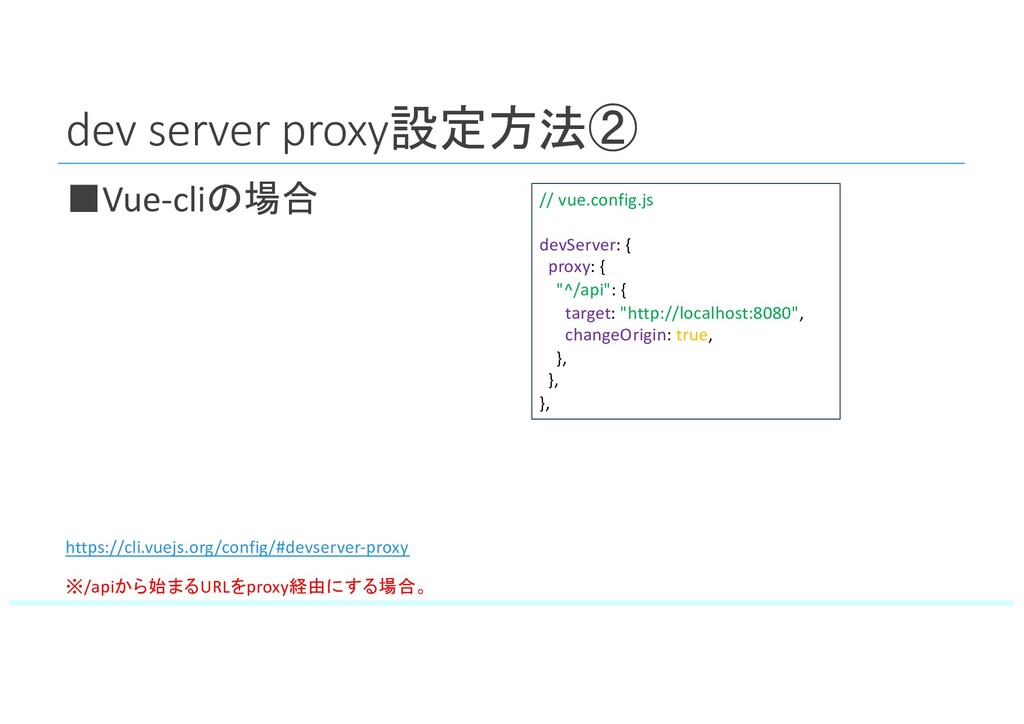
dev server proxy設定方法② ▪Vue-cliの場合 // vue.config.js devServer: { proxy: {
"^/api": { target: "http://localhost:8080", changeOrigin: true, }, }, }, ※/apiから始まるURLをproxy経由にする場合。 https://cli.vuejs.org/config/#devserver-proxy
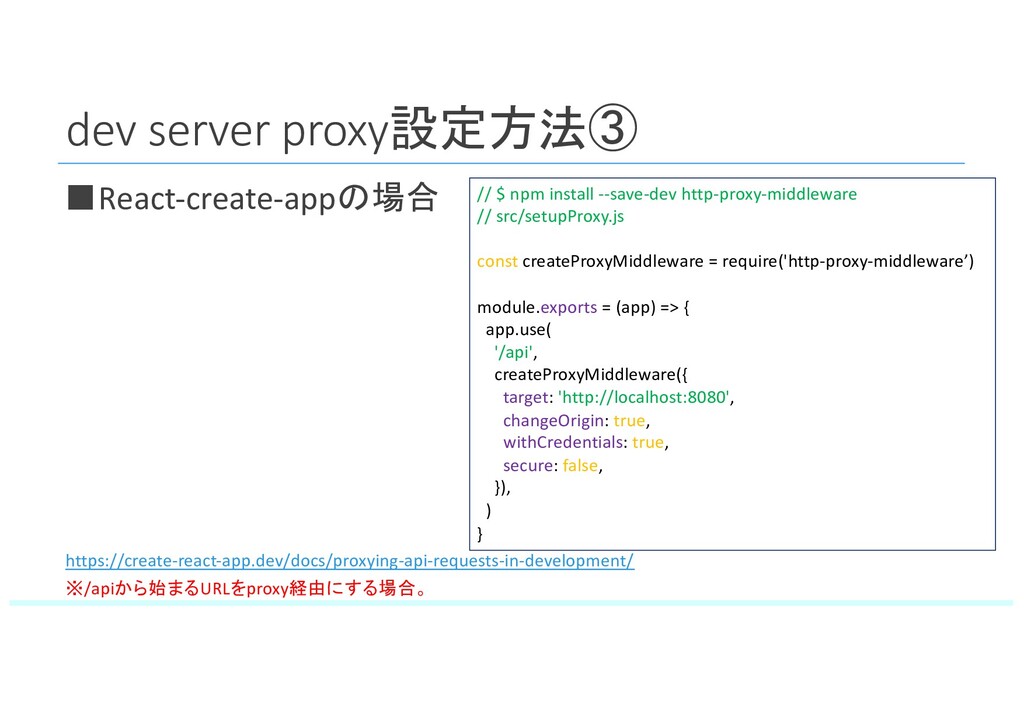
dev server proxy設定方法③ ▪React-create-appの場合 ※/apiから始まるURLをproxy経由にする場合。 https://create-react-app.dev/docs/proxying-api-requests-in-development/ // $ npm install
--save-dev http-proxy-middleware // src/setupProxy.js const createProxyMiddleware = require('http-proxy-middleware’) module.exports = (app) => { app.use( '/api', createProxyMiddleware({ target: 'http://localhost:8080', changeOrigin: true, withCredentials: true, secure: false, }), ) }
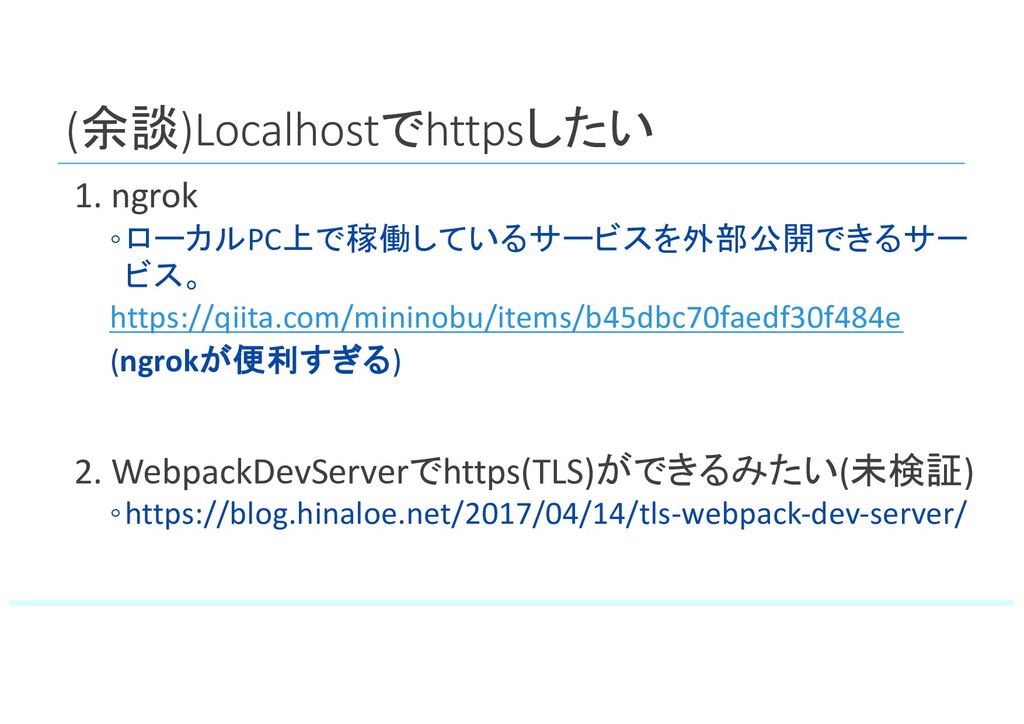
(余談)Localhostでhttpsしたい 1. ngrok ◦ローカルPC上で稼働しているサービスを外部公開できるサー ビス。 https://qiita.com/mininobu/items/b45dbc70faedf30f484e (ngrokが便利すぎる) 2. WebpackDevServerでhttps(TLS)ができるみたい(未検証) ◦https://blog.hinaloe.net/2017/04/14/tls-webpack-dev-server/
エンジニア募集中 https://couger.co.jp/news/career/ カジュアル面談実施中! lフロントエンドエンジニア lDevOpsエンジニア lAI/機械学習エンジニア lサーバアプリケーションエンジニア


 hirasa
 inariku
 khiroyuki1003
 techniczna
 shisyu_gaku
 yama3133
 demaecan
 takuros
 ham0215
 shift_evolve
 kworkdev
 bash0c7
 miso
 codingconduct
 sachag
 danielanewman
 quramy
 keithpitt
 nikkihalliwell
 reverentgeek
 jonoalderson
 tammyeverts
 marktimemedia
 jct
 marketingsoph