Upgrade to Pro — share decks privately, control downloads, hide ads and more …

istio_traffic.pdf

Avatar for Hiroto Osuga Hiroto Osuga
August 30, 2024
73

 istio_traffic.pdf

Avatar for Hiroto Osuga

Hiroto Osuga

August 30, 2024

Transcript

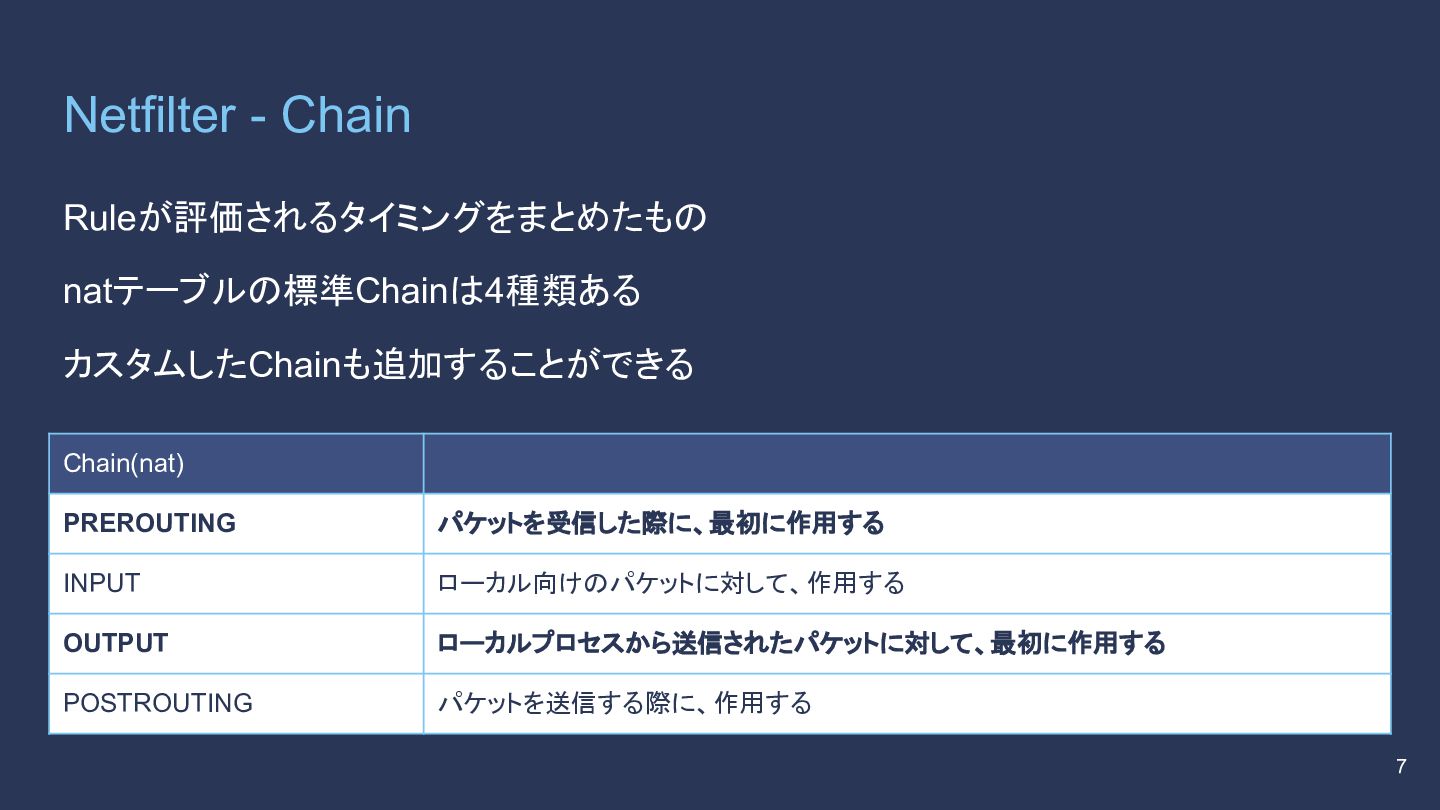
  1. Netfilter - Chain Ruleが評価されるタイミングをまとめたもの natテーブルの標準Chainは4種類ある カスタムしたChainも追加することができる 7 Chain(nat) PREROUTING パケットを受信した際に、最初に作用する

    INPUT ローカル向けのパケットに対して、作用する OUTPUT ローカルプロセスから送信されたパケットに対して、最初に作用する POSTROUTING パケットを送信する際に、作用する
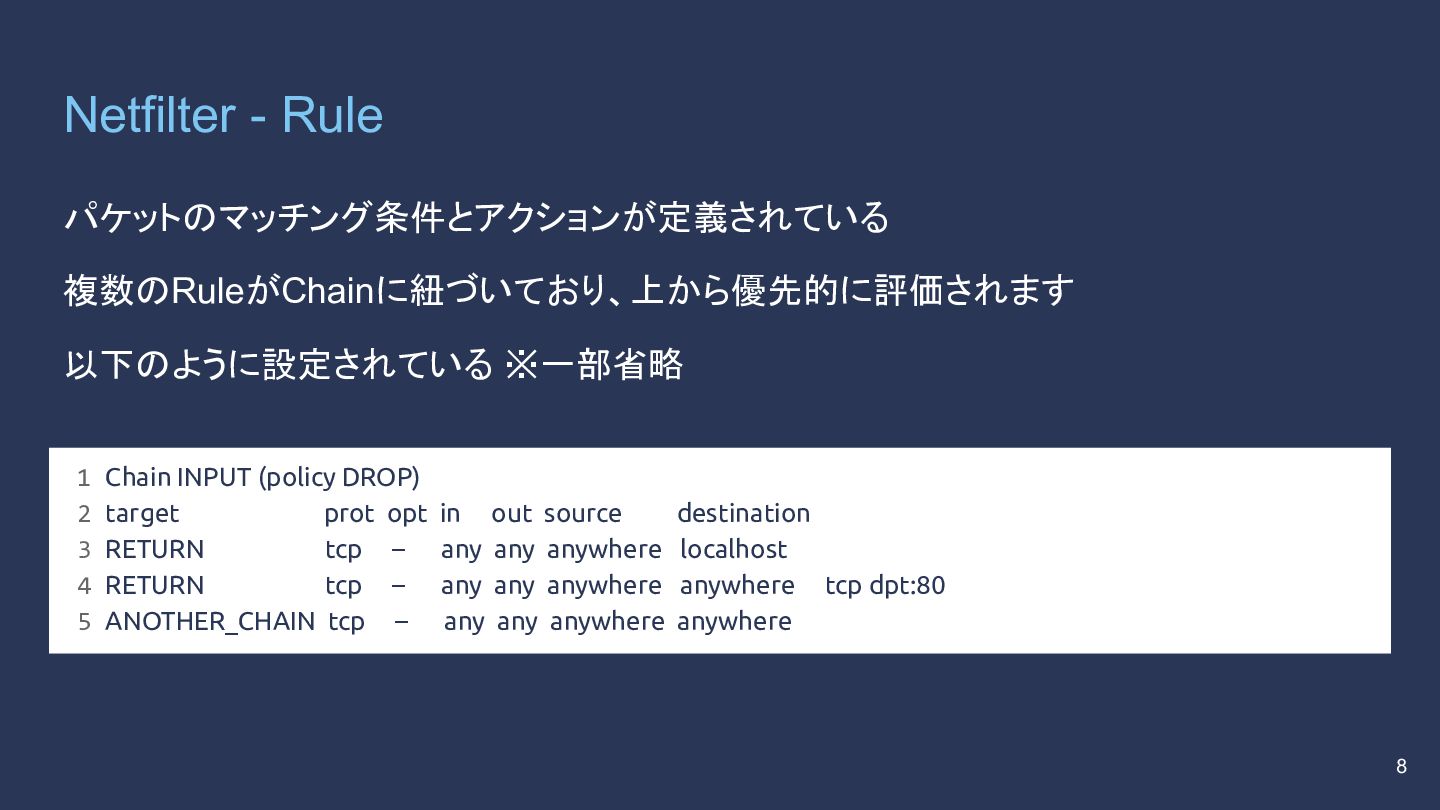
  2. Netfilter - Rule パケットのマッチング条件とアクションが定義されている 複数のRuleがChainに紐づいており、上から優先的に評価されます 以下のように設定されている ※一部省略 8 1 Chain

    INPUT (policy DROP) 2 target prot opt in out source destination 3 RETURN tcp – any any anywhere localhost 4 RETURN tcp – any any anywhere anywhere tcp dpt:80 5 ANOTHER_CHAIN tcp – any any anywhere anywhere
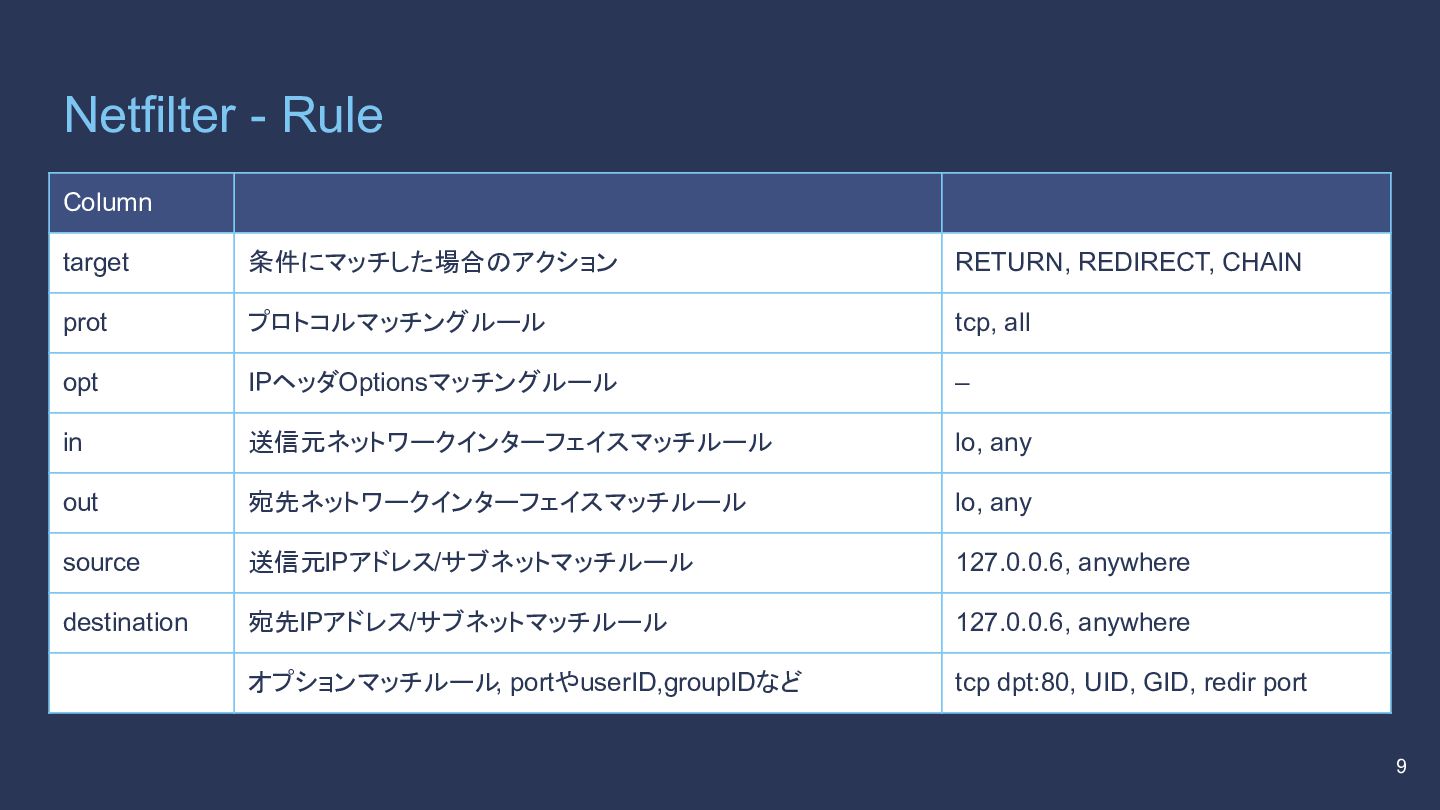
  3. Netfilter - Rule 9 Column target 条件にマッチした場合のアクション RETURN, REDIRECT, CHAIN

    prot プロトコルマッチングルール tcp, all opt IPヘッダOptionsマッチングルール – in 送信元ネットワークインターフェイスマッチルール lo, any out 宛先ネットワークインターフェイスマッチルール lo, any source 送信元IPアドレス/サブネットマッチルール 127.0.0.6, anywhere destination 宛先IPアドレス/サブネットマッチルール 127.0.0.6, anywhere オプションマッチルール, portやuserID,groupIDなど tcp dpt:80, UID, GID, redir port
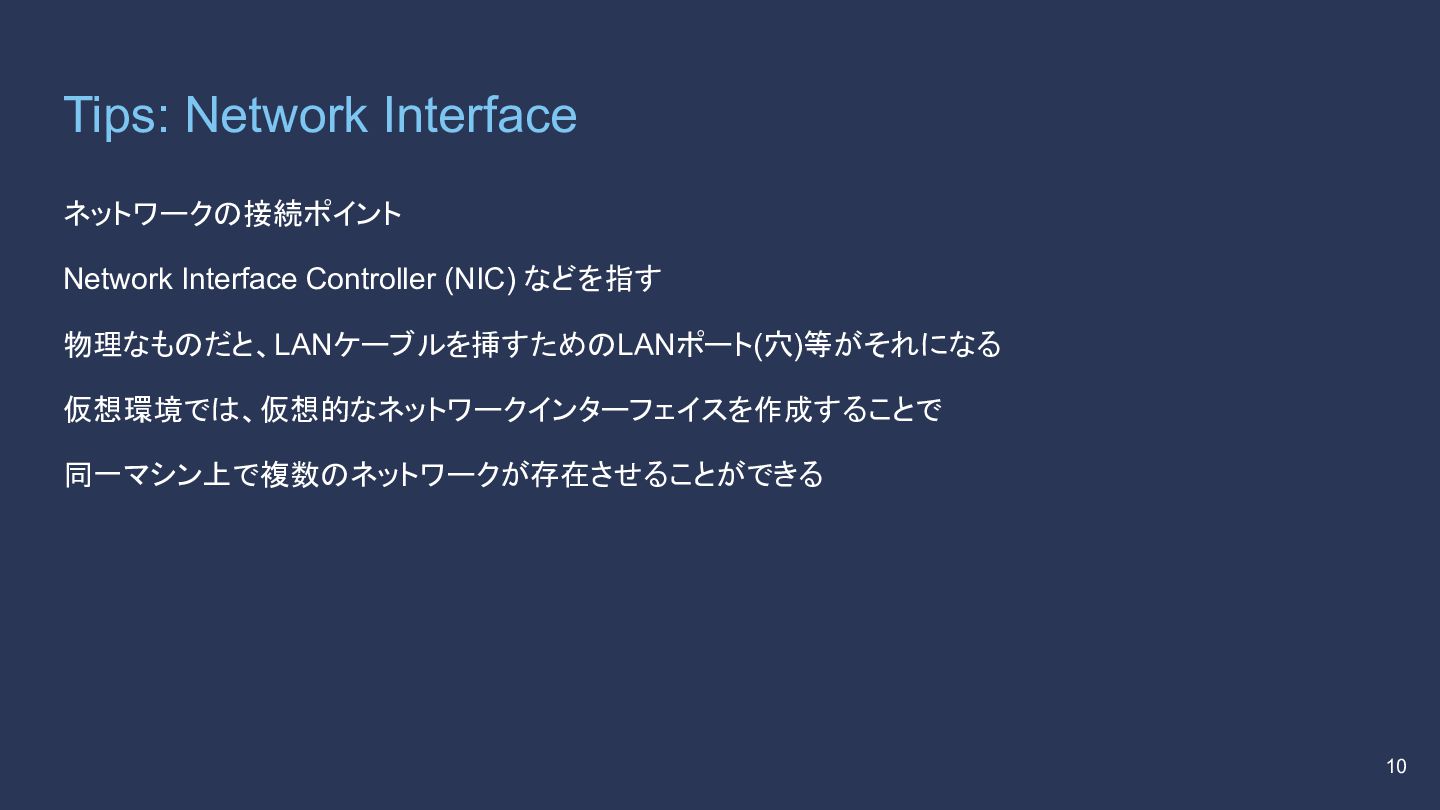
  4. Tips: Network Interface ネットワークの接続ポイント Network Interface Controller (NIC) などを指す 物理なものだと、LANケーブルを挿すためのLANポート(穴)等がそれになる

    仮想環境では、仮想的なネットワークインターフェイスを作成することで 同一マシン上で複数のネットワークが存在させることができる 10
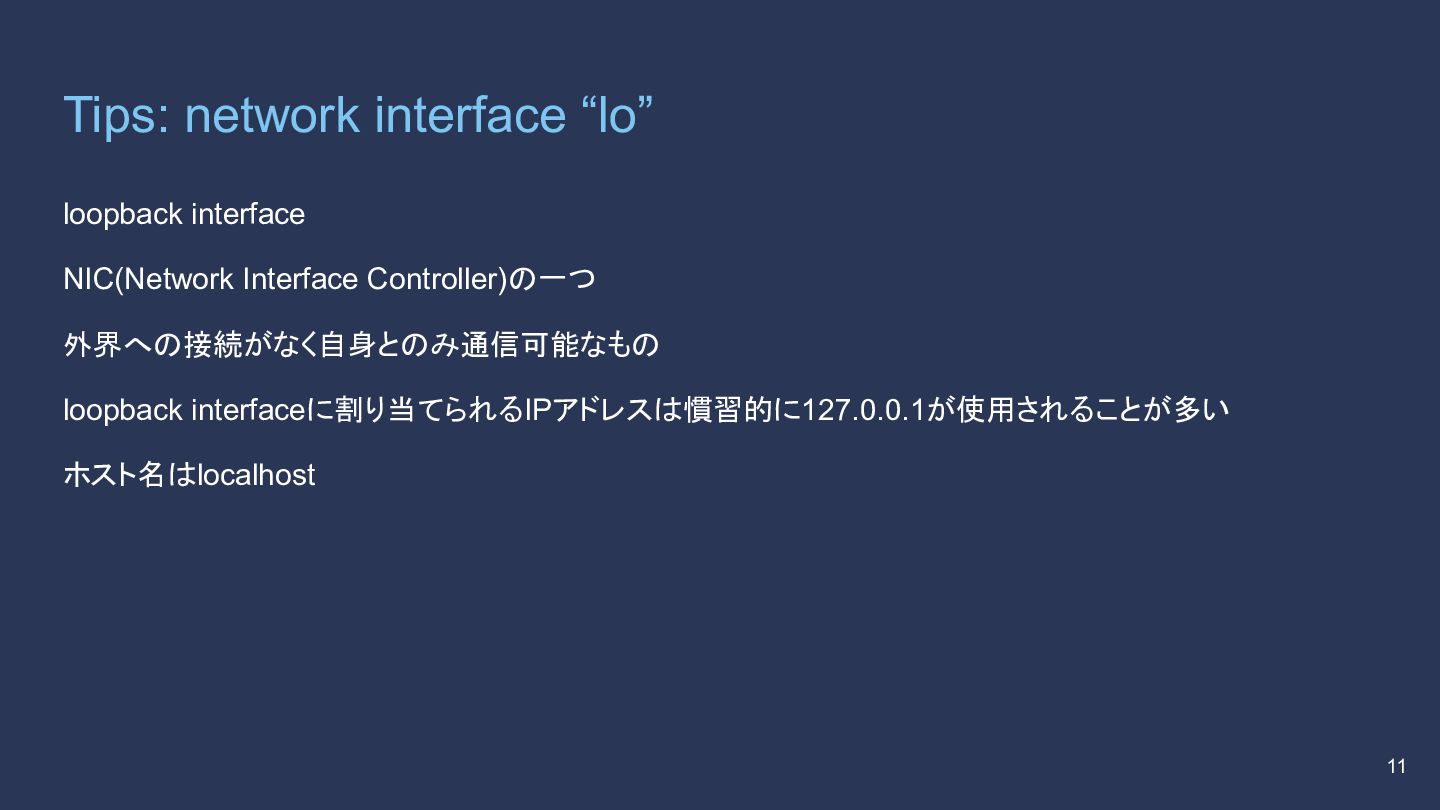
  5. Tips: network interface “lo” loopback interface NIC(Network Interface Controller)の一つ 外界への接続がなく自身とのみ通信可能なもの

    loopback interfaceに割り当てられるIPアドレスは慣習的に127.0.0.1が使用されることが多い ホスト名はlocalhost 11
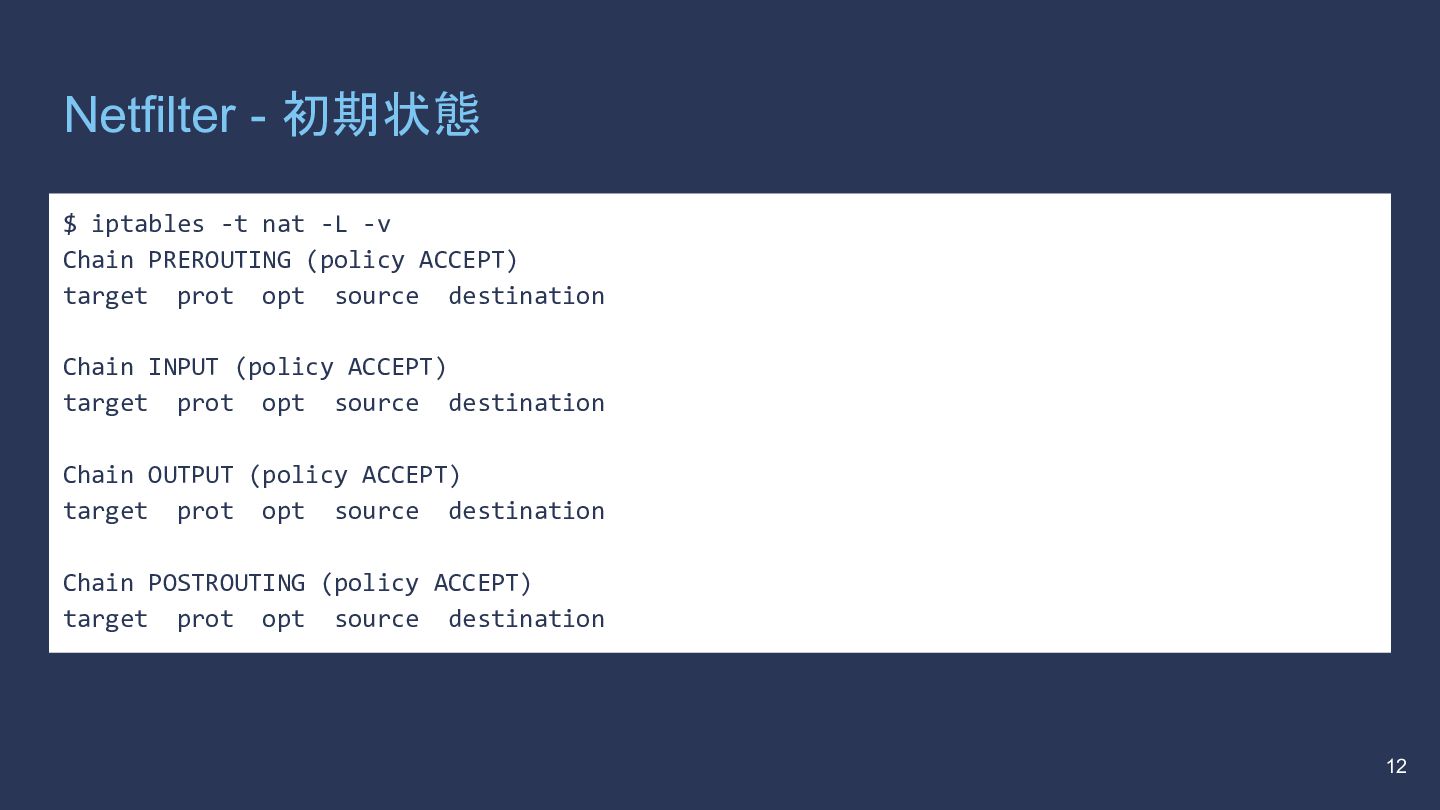
  6. Netfilter - 初期状態 12 $ iptables -t nat -L -v

    Chain PREROUTING (policy ACCEPT) target prot opt source destination Chain INPUT (policy ACCEPT) target prot opt source destination Chain OUTPUT (policy ACCEPT) target prot opt source destination Chain POSTROUTING (policy ACCEPT) target prot opt source destination
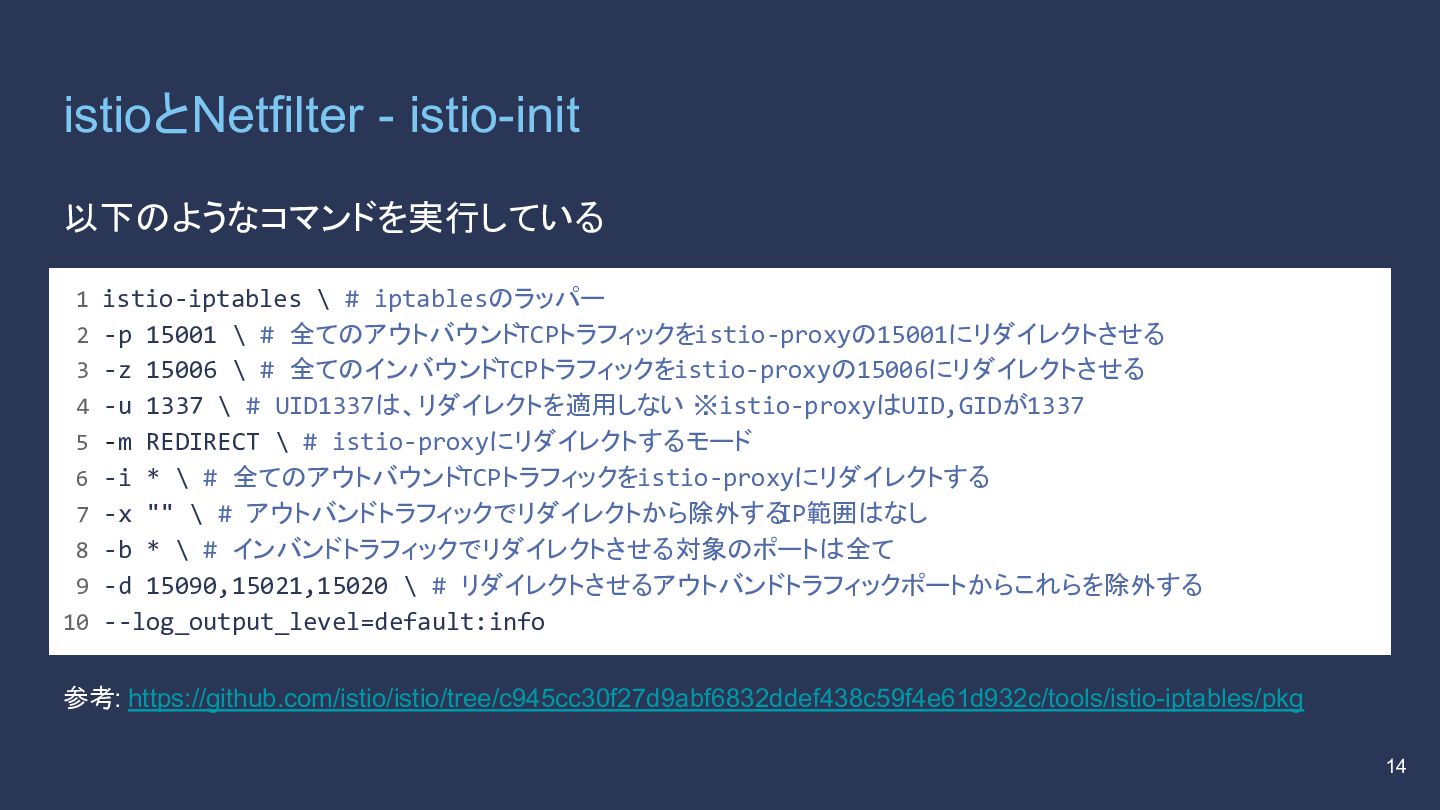
  7. istioとNetfilter - istio-init 以下のようなコマンドを実行している 14 参考: https://github.com/istio/istio/tree/c945cc30f27d9abf6832ddef438c59f4e61d932c/tools/istio-iptables/pkg 1 istio-iptables \

    # iptablesのラッパー 2 -p 15001 \ # 全てのアウトバウンドTCPトラフィックをistio-proxyの15001にリダイレクトさせる 3 -z 15006 \ # 全てのインバウンドTCPトラフィックをistio-proxyの15006にリダイレクトさせる 4 -u 1337 \ # UID1337は、リダイレクトを適用しない ※istio-proxyはUID,GIDが1337 5 -m REDIRECT \ # istio-proxyにリダイレクトするモード 6 -i * \ # 全てのアウトバウンドTCPトラフィックをistio-proxyにリダイレクトする 7 -x "" \ # アウトバンドトラフィックでリダイレクトから除外する IP範囲はなし 8 -b * \ # インバンドトラフィックでリダイレクトさせる対象のポートは全て 9 -d 15090,15021,15020 \ # リダイレクトさせるアウトバンドトラフィックポートからこれらを除外する 10 --log_output_level=default:info
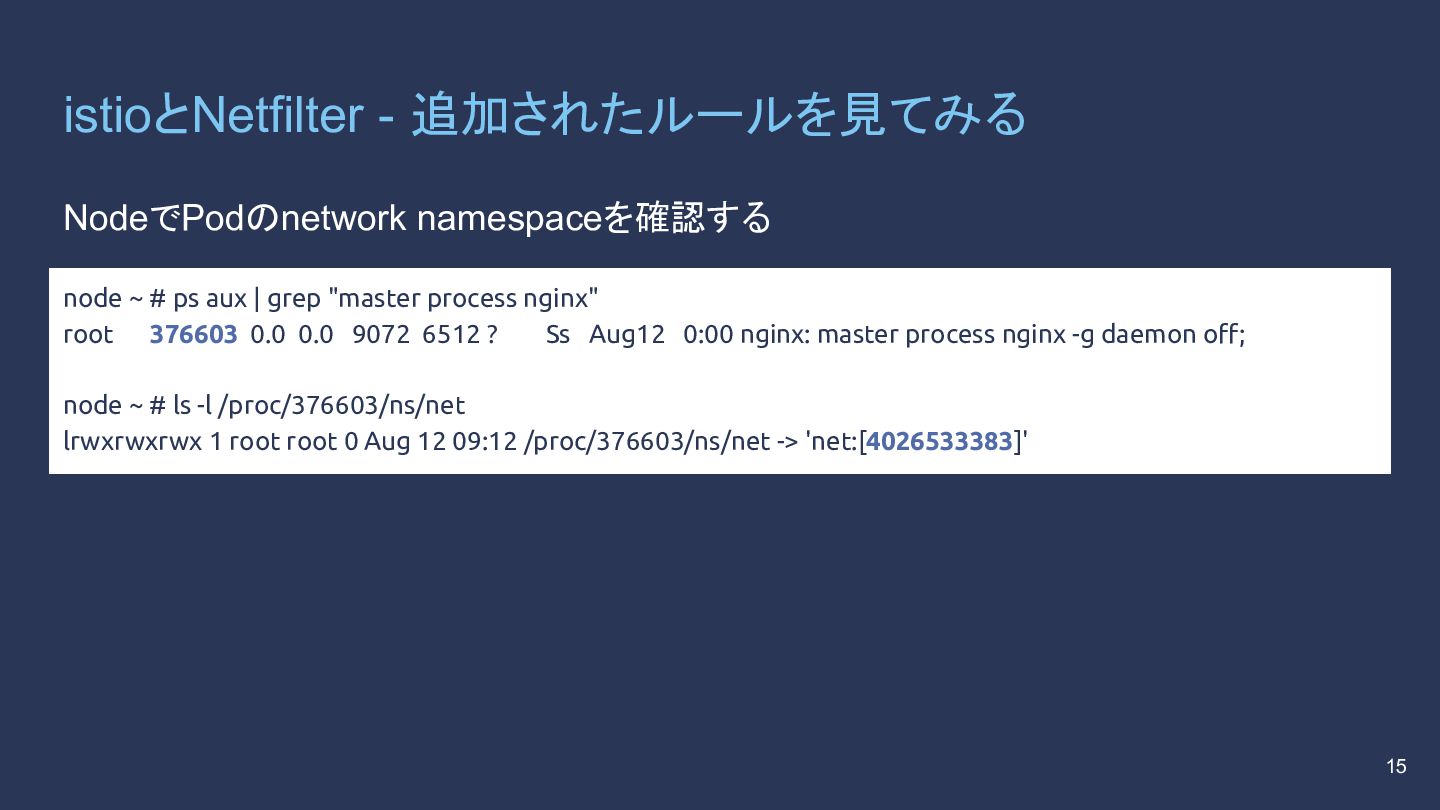
  8. istioとNetfilter - 追加されたルールを見てみる NodeでPodのnetwork namespaceを確認する 15 node ~ # ps

    aux | grep "master process nginx" root 376603 0.0 0.0 9072 6512 ? Ss Aug12 0:00 nginx: master process nginx -g daemon off; node ~ # ls -l /proc/376603/ns/net lrwxrwxrwx 1 root root 0 Aug 12 09:12 /proc/376603/ns/net -> 'net:[4026533383]'
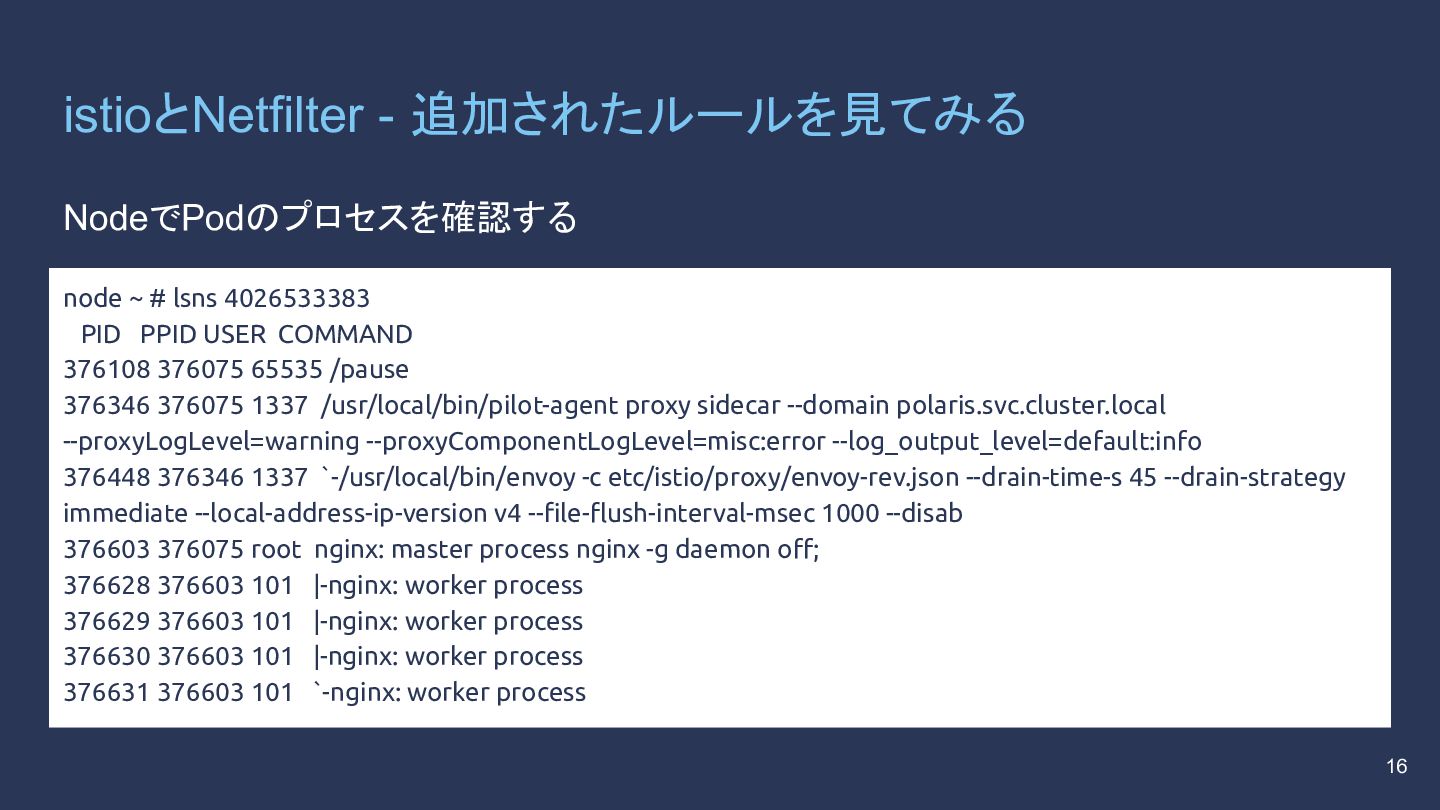
  9. istioとNetfilter - 追加されたルールを見てみる NodeでPodのプロセスを確認する 16 node ~ # lsns 4026533383

    PID PPID USER COMMAND 376108 376075 65535 /pause 376346 376075 1337 /usr/local/bin/pilot-agent proxy sidecar --domain polaris.svc.cluster.local --proxyLogLevel=warning --proxyComponentLogLevel=misc:error --log_output_level=default:info 376448 376346 1337 `-/usr/local/bin/envoy -c etc/istio/proxy/envoy-rev.json --drain-time-s 45 --drain-strategy immediate --local-address-ip-version v4 --file-flush-interval-msec 1000 --disab 376603 376075 root nginx: master process nginx -g daemon off; 376628 376603 101 |-nginx: worker process 376629 376603 101 |-nginx: worker process 376630 376603 101 |-nginx: worker process 376631 376603 101 `-nginx: worker process
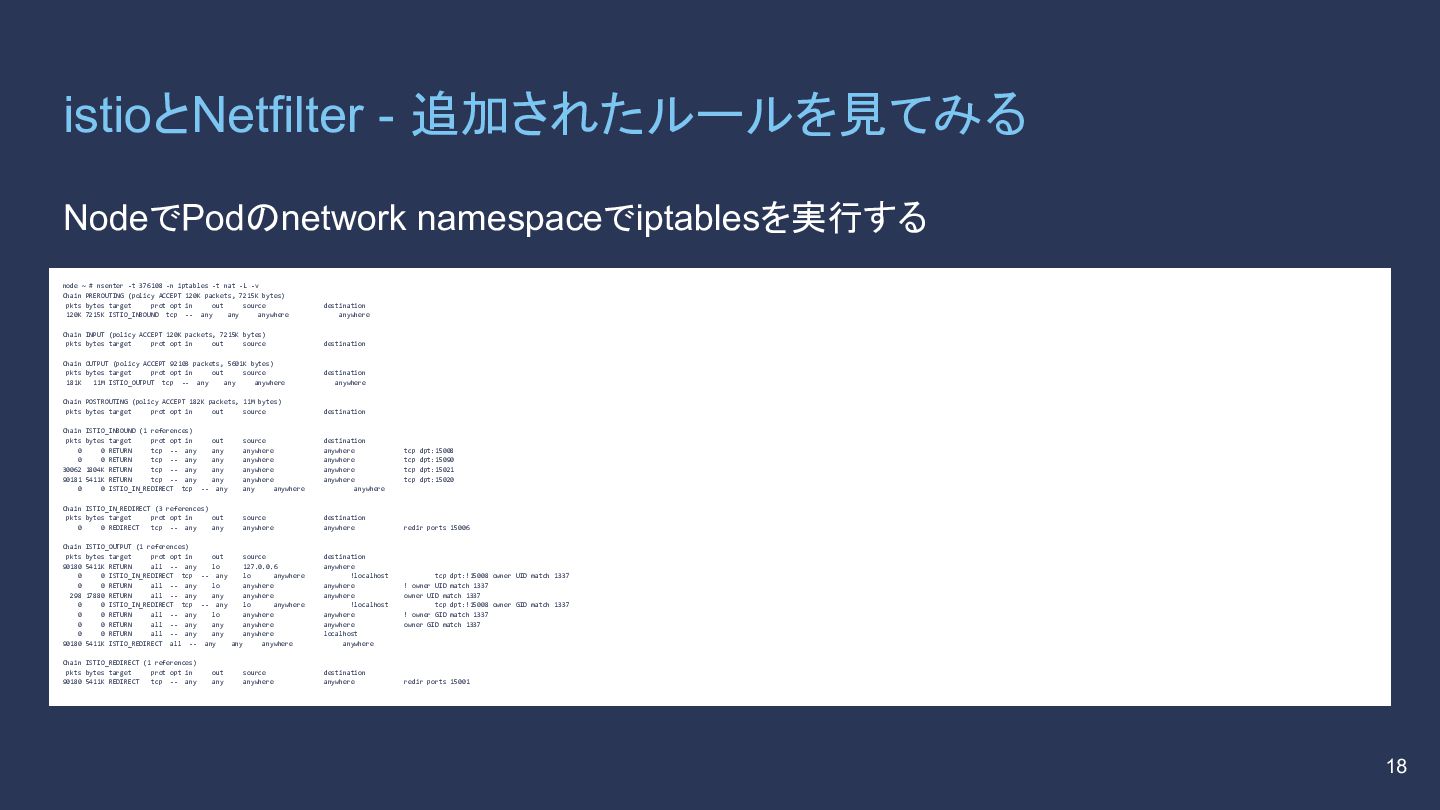
  10. istioとNetfilter - 追加されたルールを見てみる NodeでPodのnetwork namespaceでiptablesを実行する 18 node ~ # nsenter

    -t 376108 -n iptables -t nat -L -v Chain PREROUTING (policy ACCEPT 120K packets, 7215K bytes) pkts bytes target prot opt in out source destination 120K 7215K ISTIO_INBOUND tcp -- any any anywhere anywhere Chain INPUT (policy ACCEPT 120K packets, 7215K bytes) pkts bytes target prot opt in out source destination Chain OUTPUT (policy ACCEPT 92103 packets, 5601K bytes) pkts bytes target prot opt in out source destination 181K 11M ISTIO_OUTPUT tcp -- any any anywhere anywhere Chain POSTROUTING (policy ACCEPT 182K packets, 11M bytes) pkts bytes target prot opt in out source destination Chain ISTIO_INBOUND (1 references) pkts bytes target prot opt in out source destination 0 0 RETURN tcp -- any any anywhere anywhere tcp dpt:15008 0 0 RETURN tcp -- any any anywhere anywhere tcp dpt:15090 30062 1804K RETURN tcp -- any any anywhere anywhere tcp dpt:15021 90181 5411K RETURN tcp -- any any anywhere anywhere tcp dpt:15020 0 0 ISTIO_IN_REDIRECT tcp -- any any anywhere anywhere Chain ISTIO_IN_REDIRECT (3 references) pkts bytes target prot opt in out source destination 0 0 REDIRECT tcp -- any any anywhere anywhere redir ports 15006 Chain ISTIO_OUTPUT (1 references) pkts bytes target prot opt in out source destination 90180 5411K RETURN all -- any lo 127.0.0.6 anywhere 0 0 ISTIO_IN_REDIRECT tcp -- any lo anywhere !localhost tcp dpt:!15008 owner UID match 1337 0 0 RETURN all -- any lo anywhere anywhere ! owner UID match 1337 298 17880 RETURN all -- any any anywhere anywhere owner UID match 1337 0 0 ISTIO_IN_REDIRECT tcp -- any lo anywhere !localhost tcp dpt:!15008 owner GID match 1337 0 0 RETURN all -- any lo anywhere anywhere ! owner GID match 1337 0 0 RETURN all -- any any anywhere anywhere owner GID match 1337 0 0 RETURN all -- any any anywhere localhost 90180 5411K ISTIO_REDIRECT all -- any any anywhere anywhere Chain ISTIO_REDIRECT (1 references) pkts bytes target prot opt in out source destination 90180 5411K REDIRECT tcp -- any any anywhere anywhere redir ports 15001
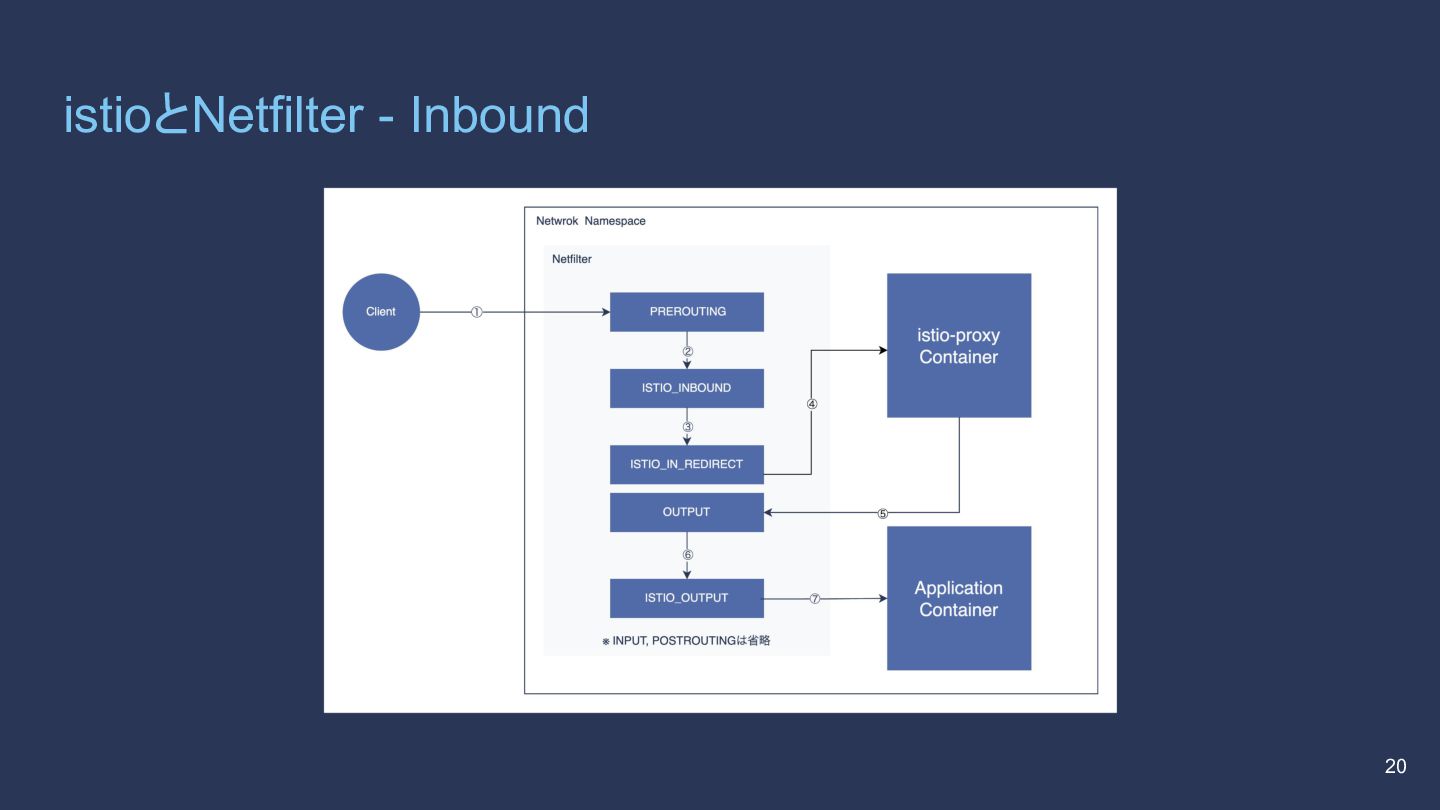
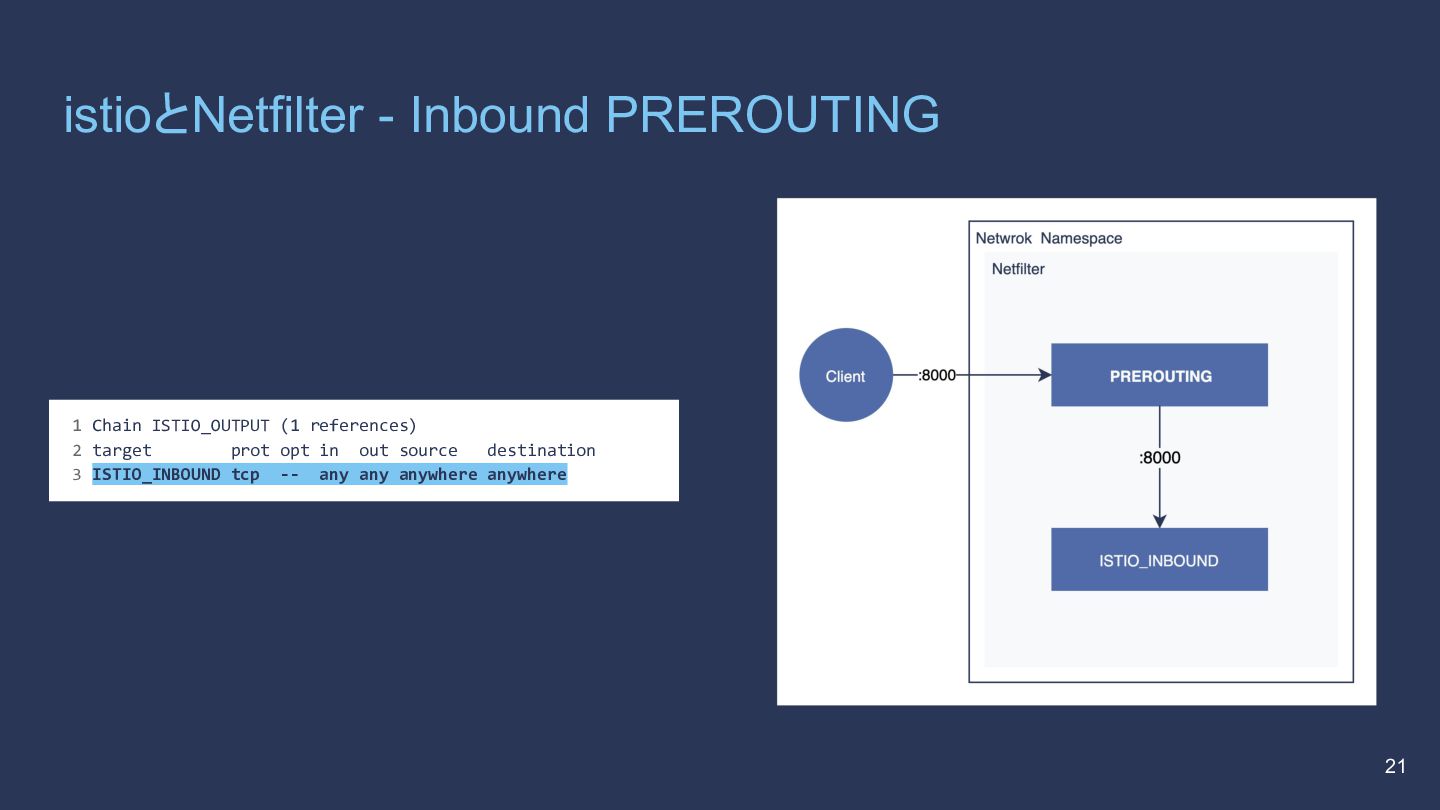
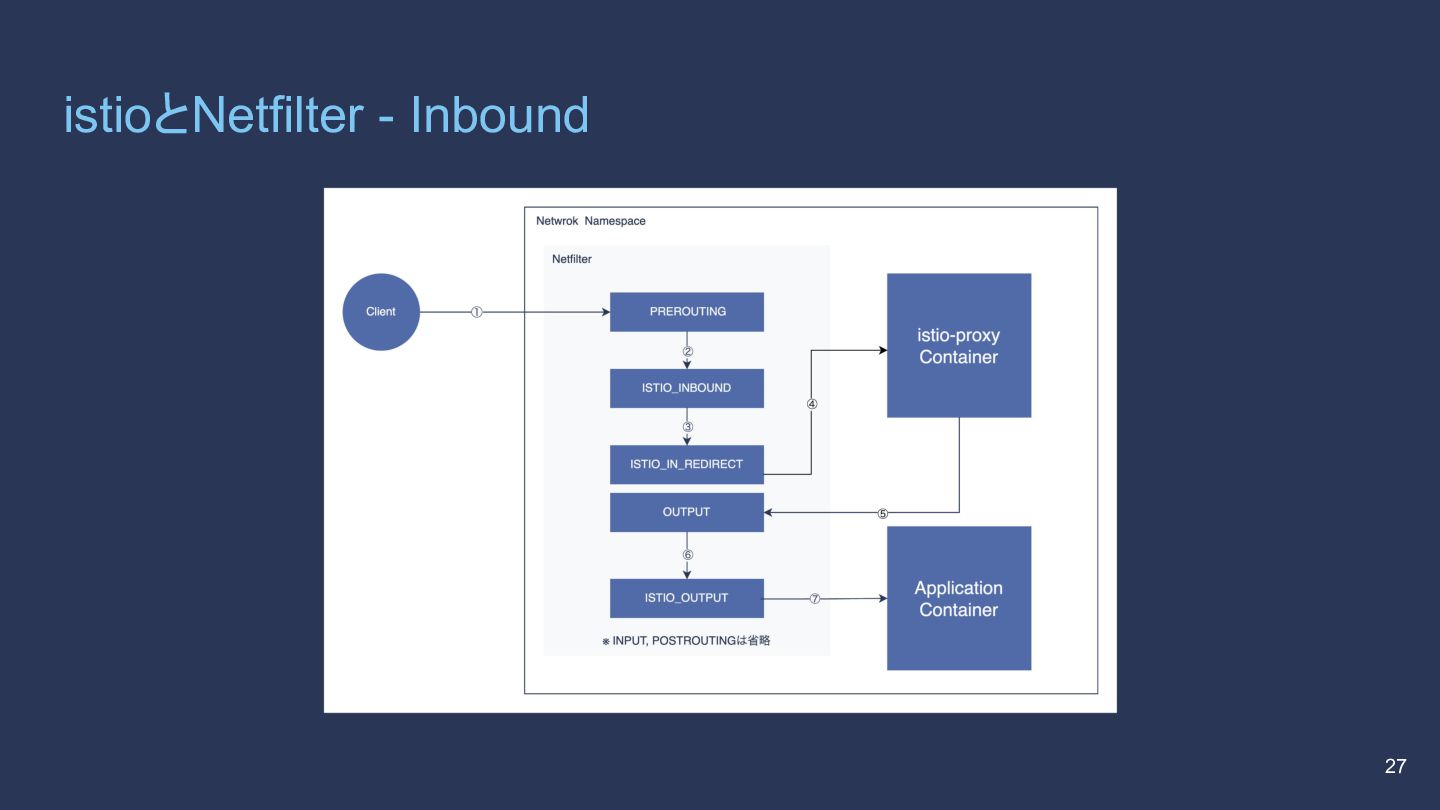
  11. istioとNetfilter - Inbound PREROUTING 21 1 Chain ISTIO_OUTPUT (1 references)

    2 target prot opt in out source destination 3 ISTIO_INBOUND tcp -- any any anywhere anywhere
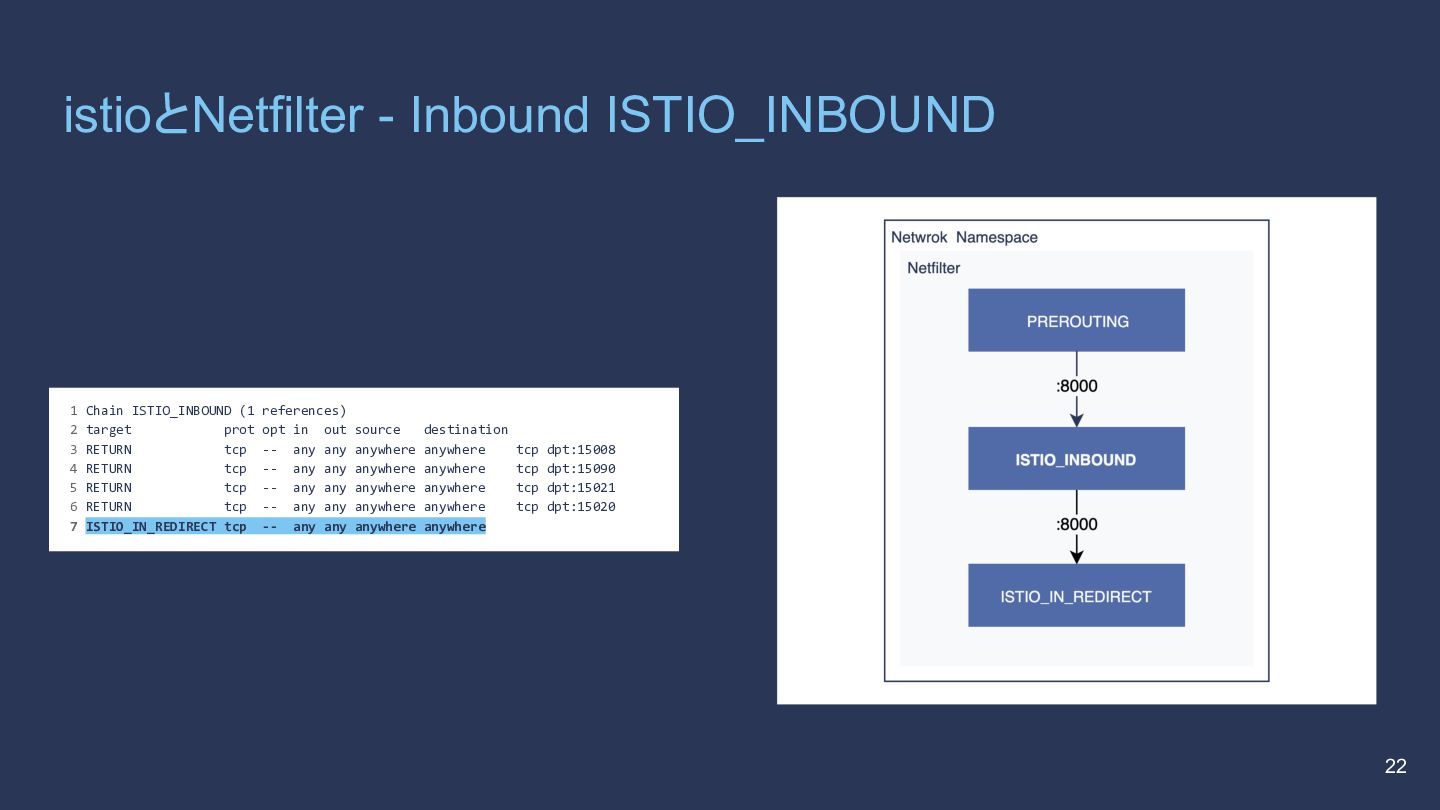
  12. istioとNetfilter - Inbound ISTIO_INBOUND 22 1 Chain ISTIO_INBOUND (1 references)

    2 target prot opt in out source destination 3 RETURN tcp -- any any anywhere anywhere tcp dpt:15008 4 RETURN tcp -- any any anywhere anywhere tcp dpt:15090 5 RETURN tcp -- any any anywhere anywhere tcp dpt:15021 6 RETURN tcp -- any any anywhere anywhere tcp dpt:15020 7 ISTIO_IN_REDIRECT tcp -- any any anywhere anywhere
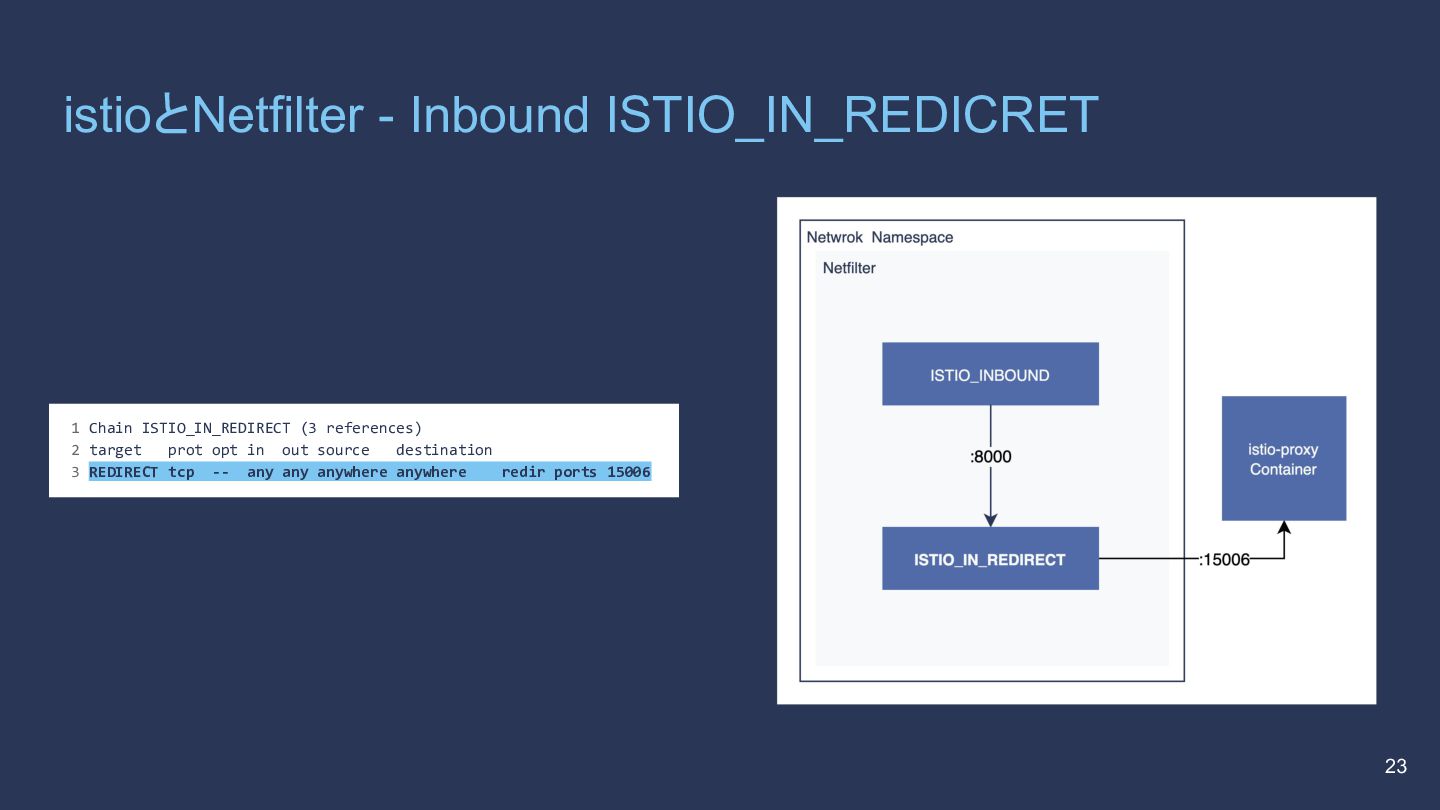
  13. istioとNetfilter - Inbound ISTIO_IN_REDICRET 23 1 Chain ISTIO_IN_REDIRECT (3 references)

    2 target prot opt in out source destination 3 REDIRECT tcp -- any any anywhere anywhere redir ports 15006
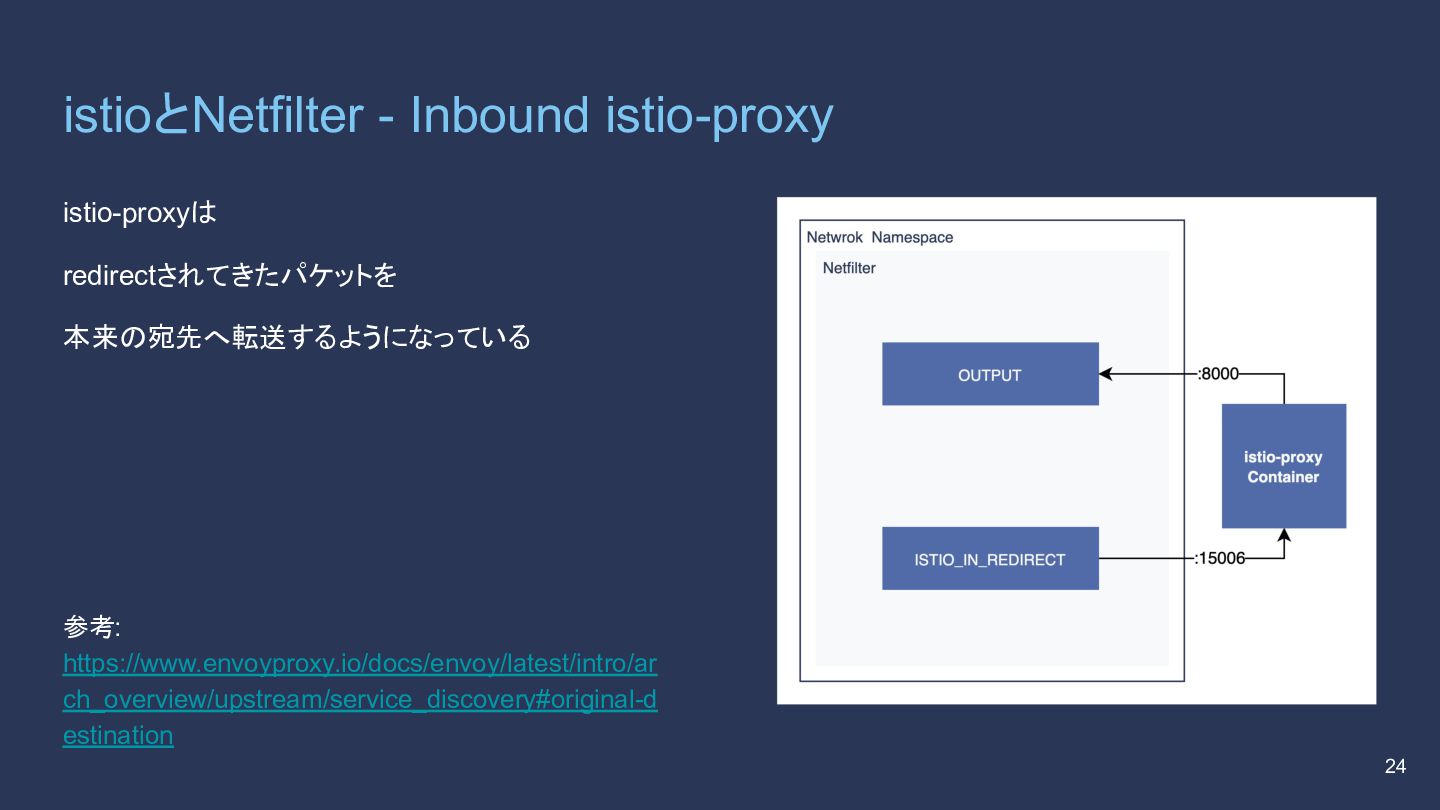
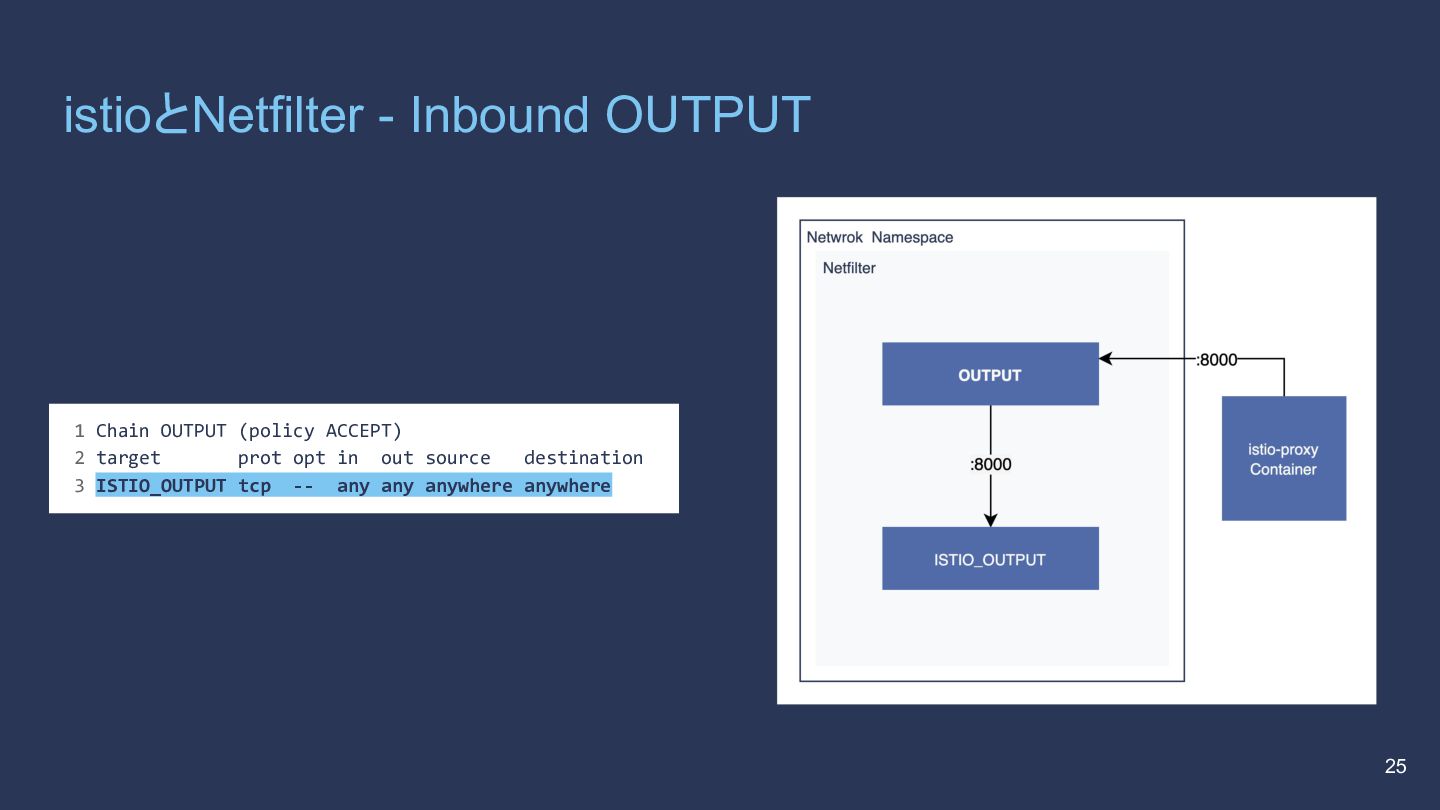
  14. istioとNetfilter - Inbound OUTPUT 25 1 Chain OUTPUT (policy ACCEPT)

    2 target prot opt in out source destination 3 ISTIO_OUTPUT tcp -- any any anywhere anywhere
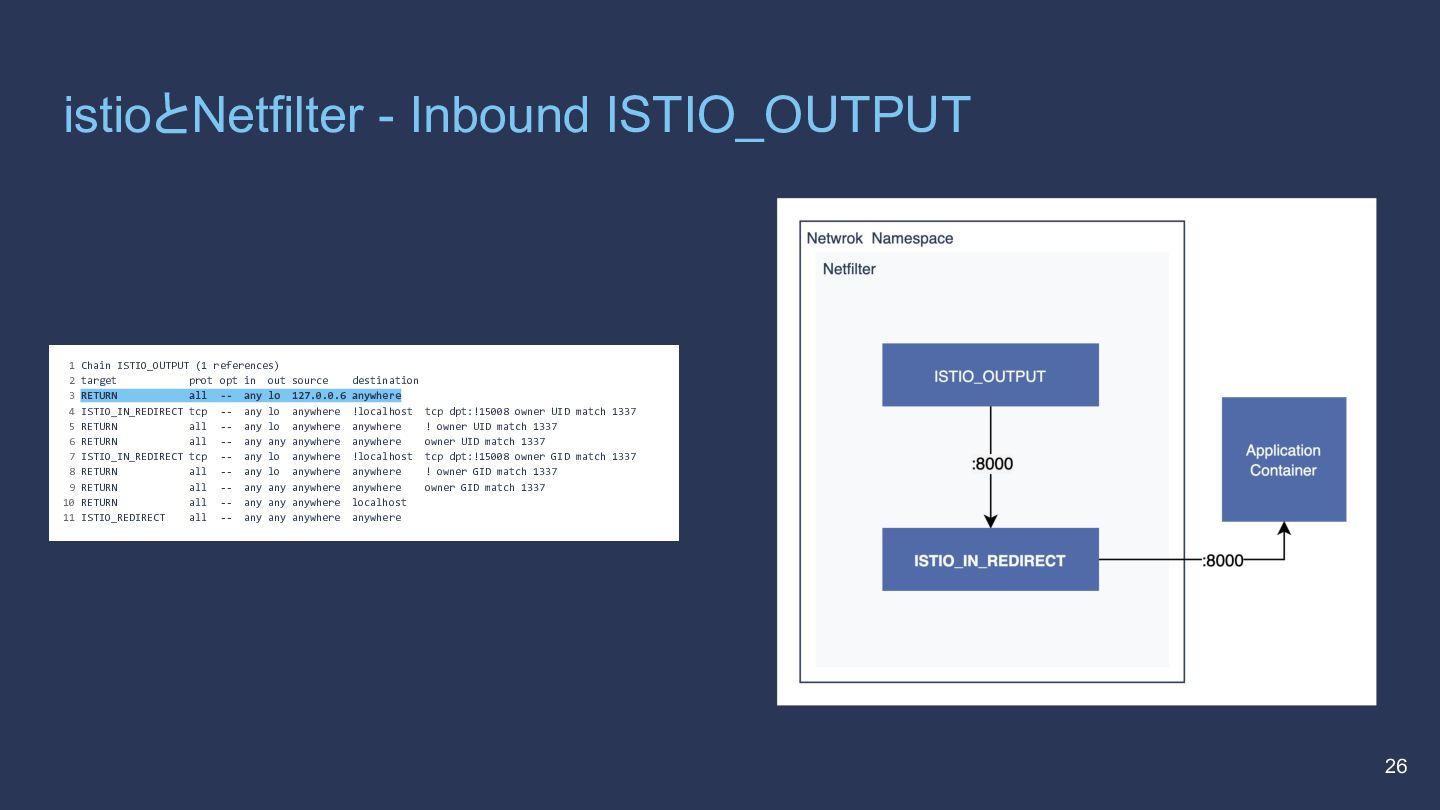
  15. istioとNetfilter - Inbound ISTIO_OUTPUT 26 1 Chain ISTIO_OUTPUT (1 references)

    2 target prot opt in out source destination 3 RETURN all -- any lo 127.0.0.6 anywhere 4 ISTIO_IN_REDIRECT tcp -- any lo anywhere !localhost tcp dpt:!15008 owner UID match 1337 5 RETURN all -- any lo anywhere anywhere ! owner UID match 1337 6 RETURN all -- any any anywhere anywhere owner UID match 1337 7 ISTIO_IN_REDIRECT tcp -- any lo anywhere !localhost tcp dpt:!15008 owner GID match 1337 8 RETURN all -- any lo anywhere anywhere ! owner GID match 1337 9 RETURN all -- any any anywhere anywhere owner GID match 1337 10 RETURN all -- any any anywhere localhost 11 ISTIO_REDIRECT all -- any any anywhere anywhere
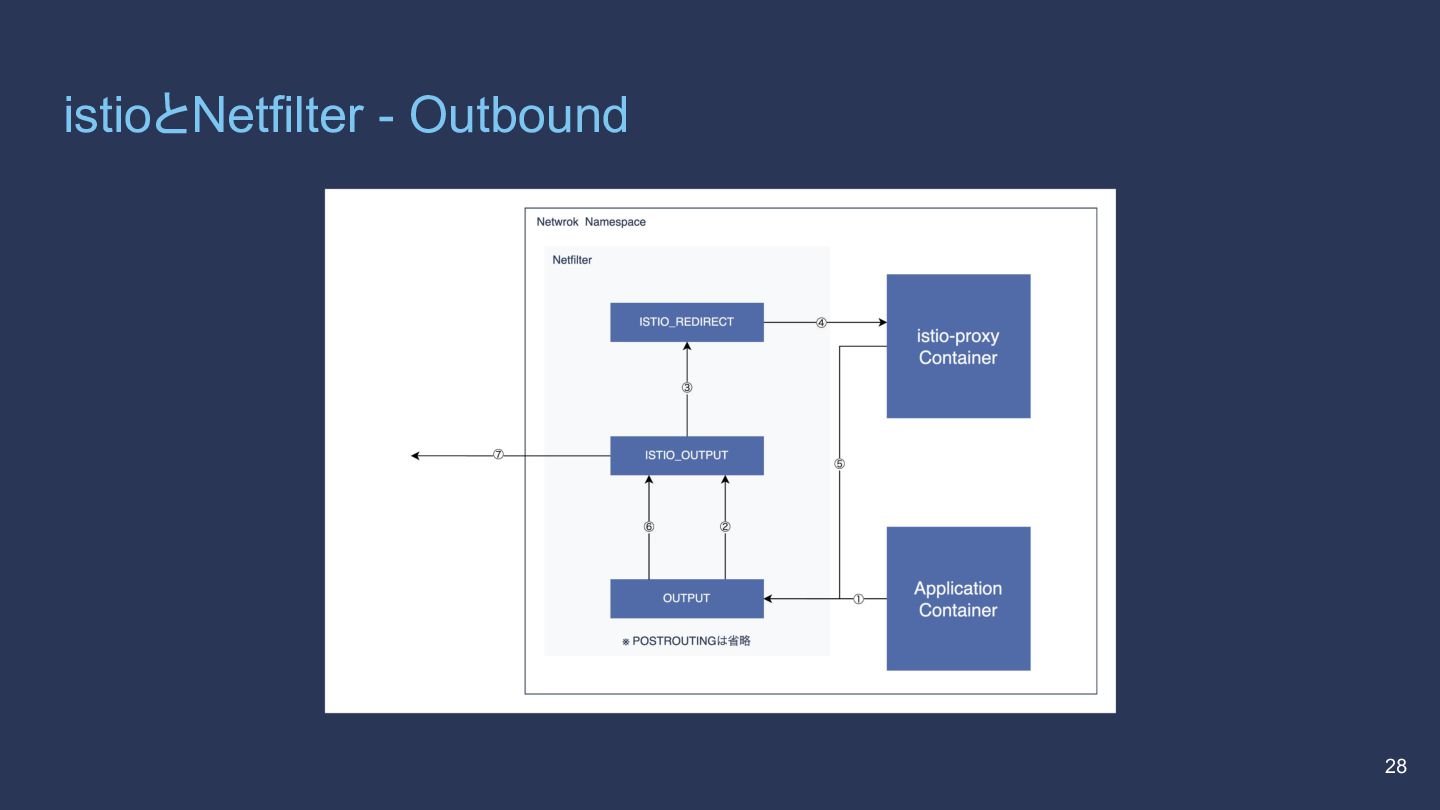
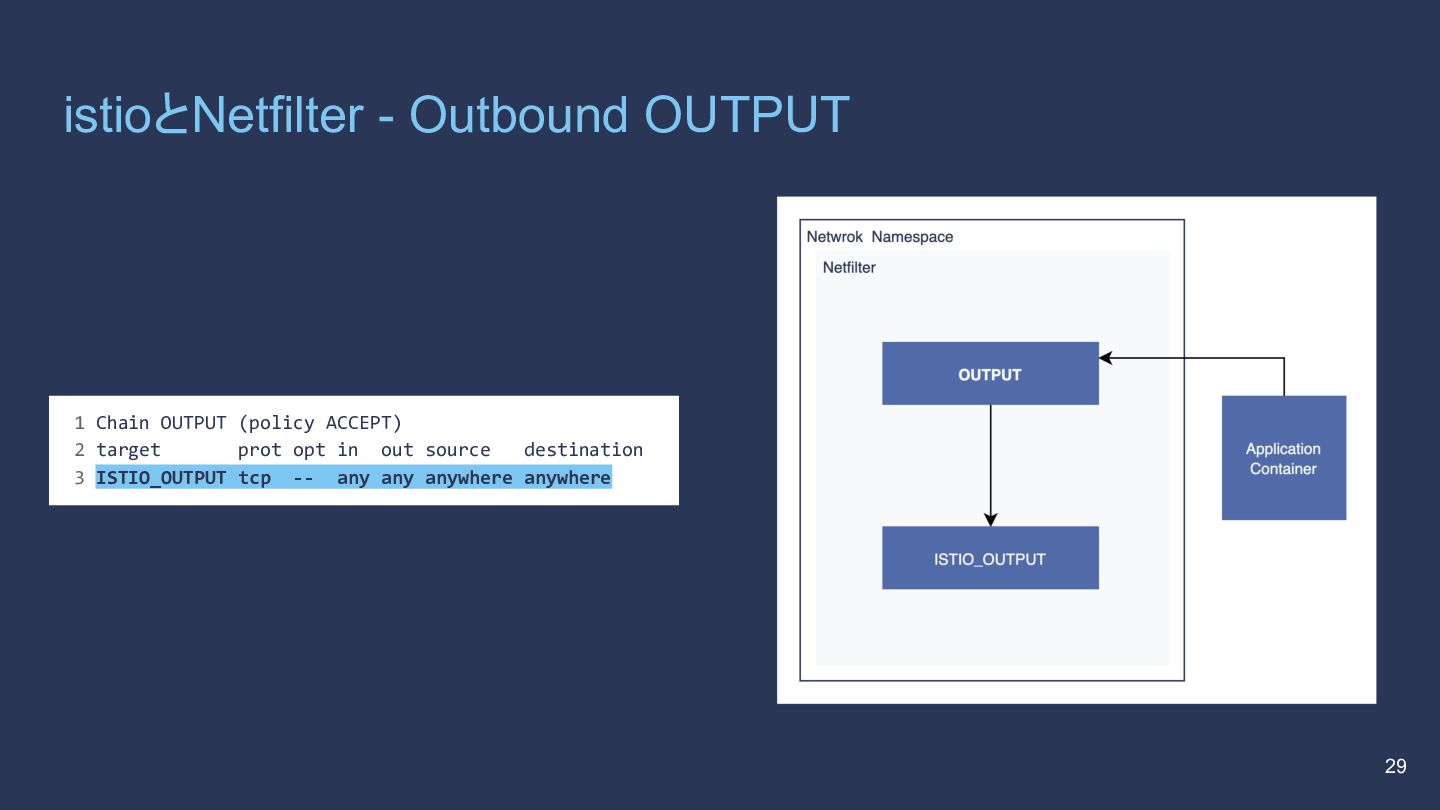
  16. istioとNetfilter - Outbound OUTPUT 29 1 Chain OUTPUT (policy ACCEPT)

    2 target prot opt in out source destination 3 ISTIO_OUTPUT tcp -- any any anywhere anywhere
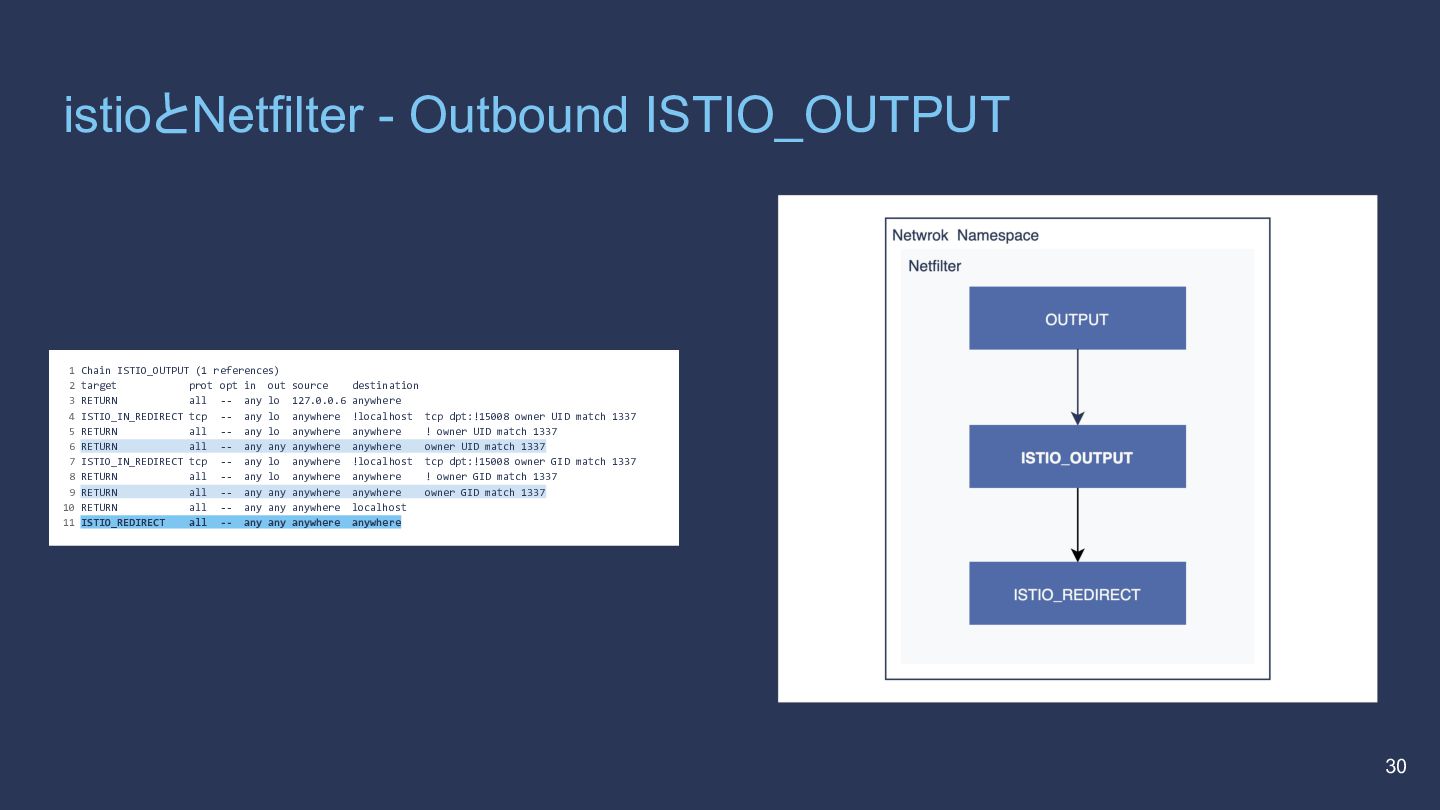
  17. istioとNetfilter - Outbound ISTIO_OUTPUT 30 1 Chain ISTIO_OUTPUT (1 references)

    2 target prot opt in out source destination 3 RETURN all -- any lo 127.0.0.6 anywhere 4 ISTIO_IN_REDIRECT tcp -- any lo anywhere !localhost tcp dpt:!15008 owner UID match 1337 5 RETURN all -- any lo anywhere anywhere ! owner UID match 1337 6 RETURN all -- any any anywhere anywhere owner UID match 1337 7 ISTIO_IN_REDIRECT tcp -- any lo anywhere !localhost tcp dpt:!15008 owner GID match 1337 8 RETURN all -- any lo anywhere anywhere ! owner GID match 1337 9 RETURN all -- any any anywhere anywhere owner GID match 1337 10 RETURN all -- any any anywhere localhost 11 ISTIO_REDIRECT all -- any any anywhere anywhere
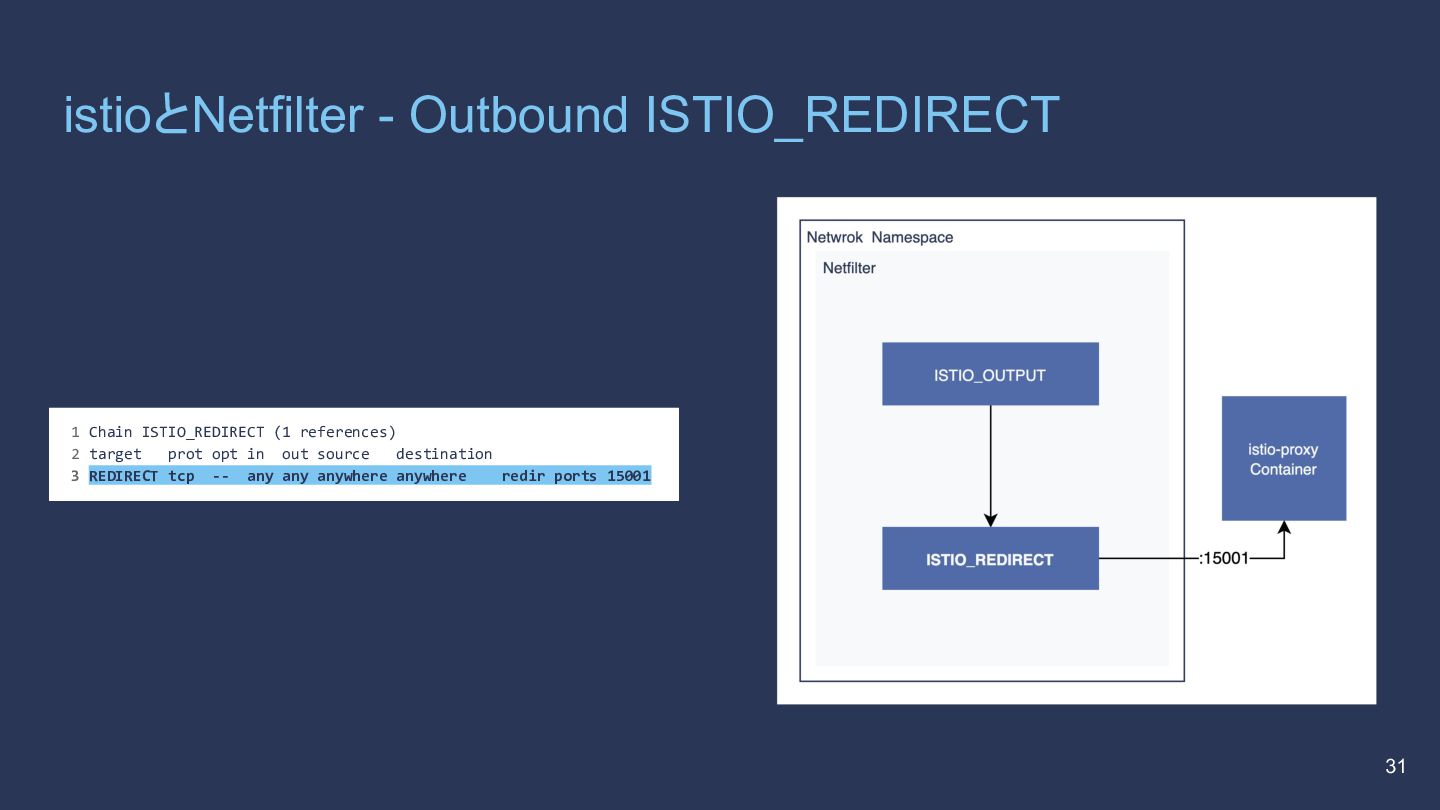
  18. istioとNetfilter - Outbound ISTIO_REDIRECT 31 1 Chain ISTIO_REDIRECT (1 references)

    2 target prot opt in out source destination 3 REDIRECT tcp -- any any anywhere anywhere redir ports 15001
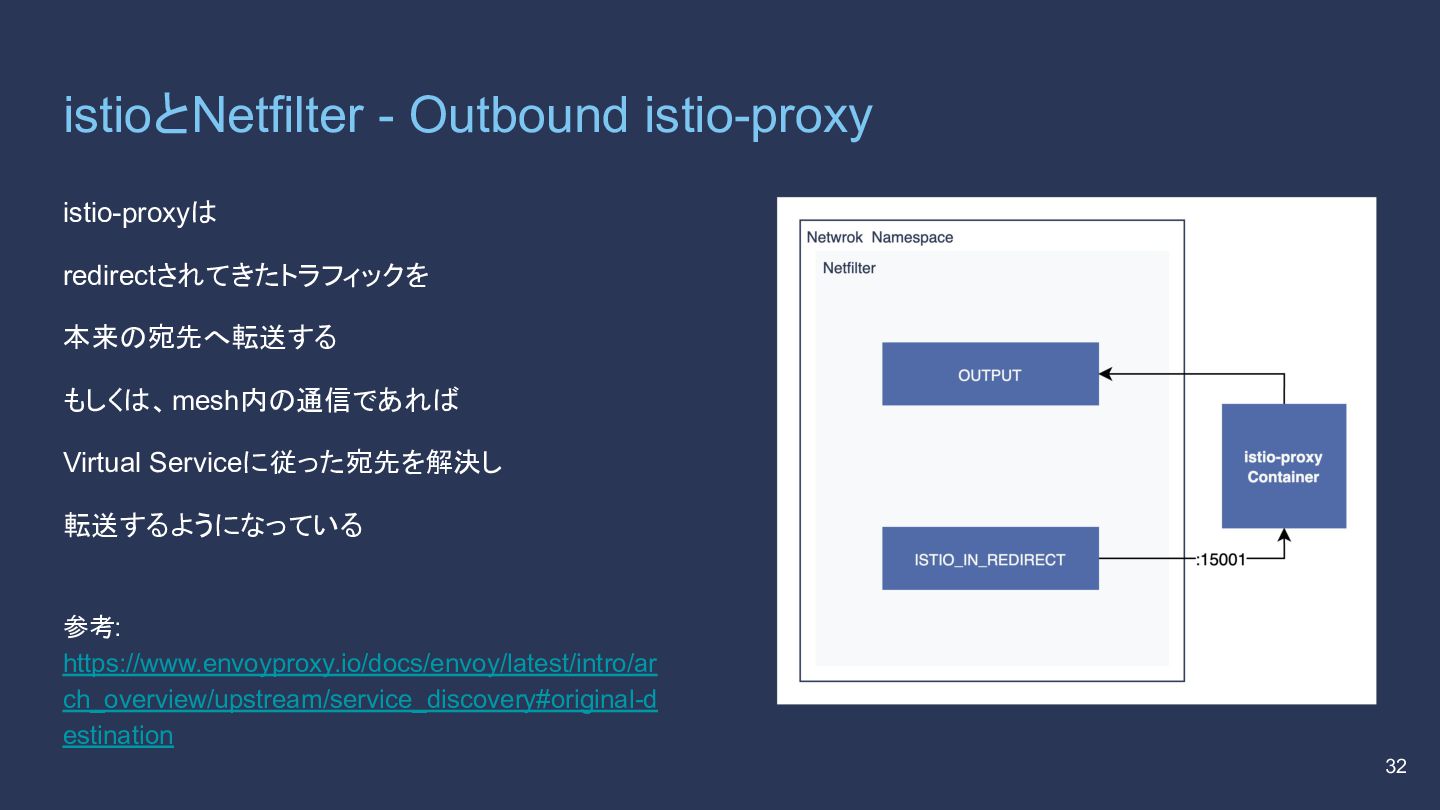
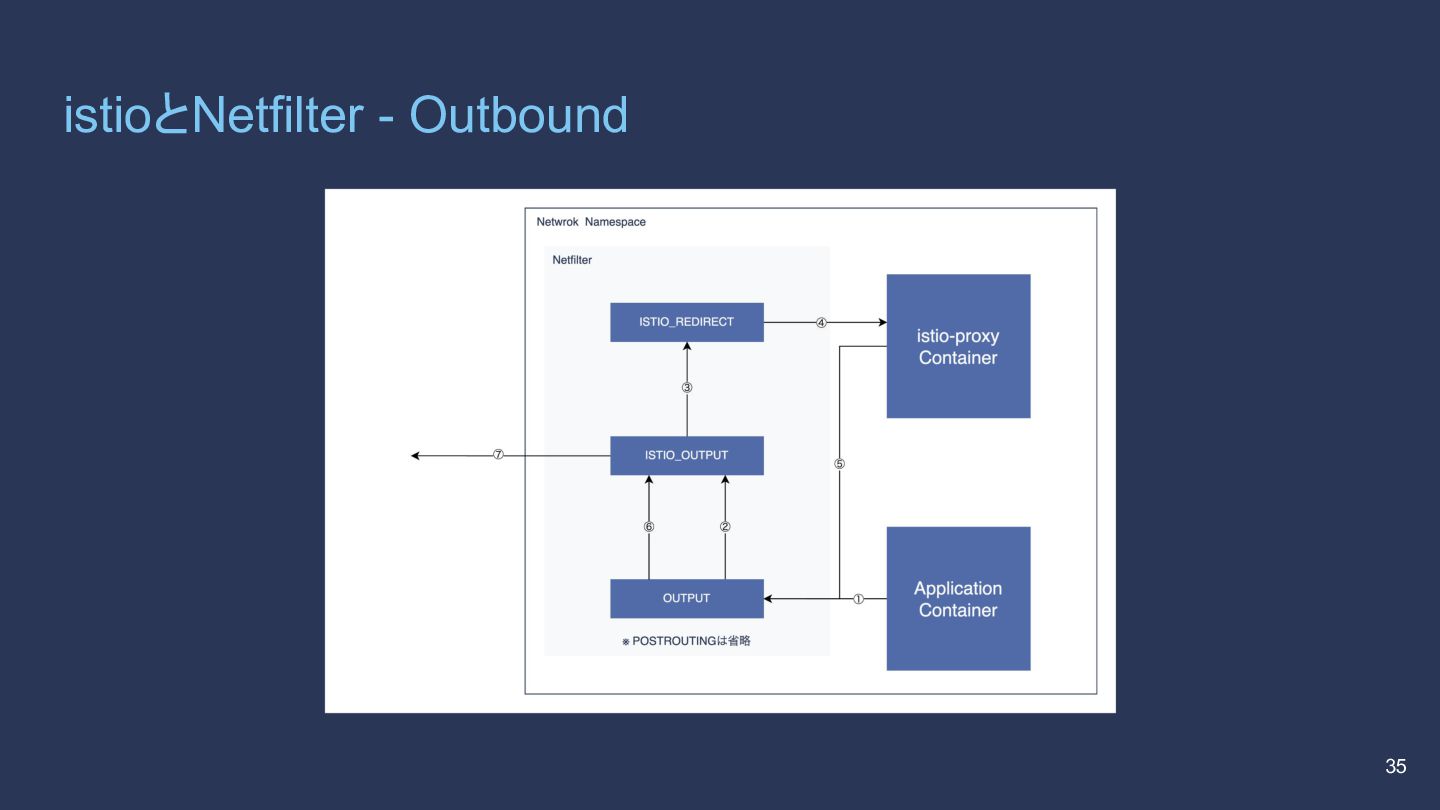
  19. istioとNetfilter - Outbound istio-proxy 32 istio-proxyは redirectされてきたトラフィックを 本来の宛先へ転送する もしくは、mesh内の通信であれば Virtual

    Serviceに従った宛先を解決し 転送するようになっている 参考: https://www.envoyproxy.io/docs/envoy/latest/intro/ar ch_overview/upstream/service_discovery#original-d estination
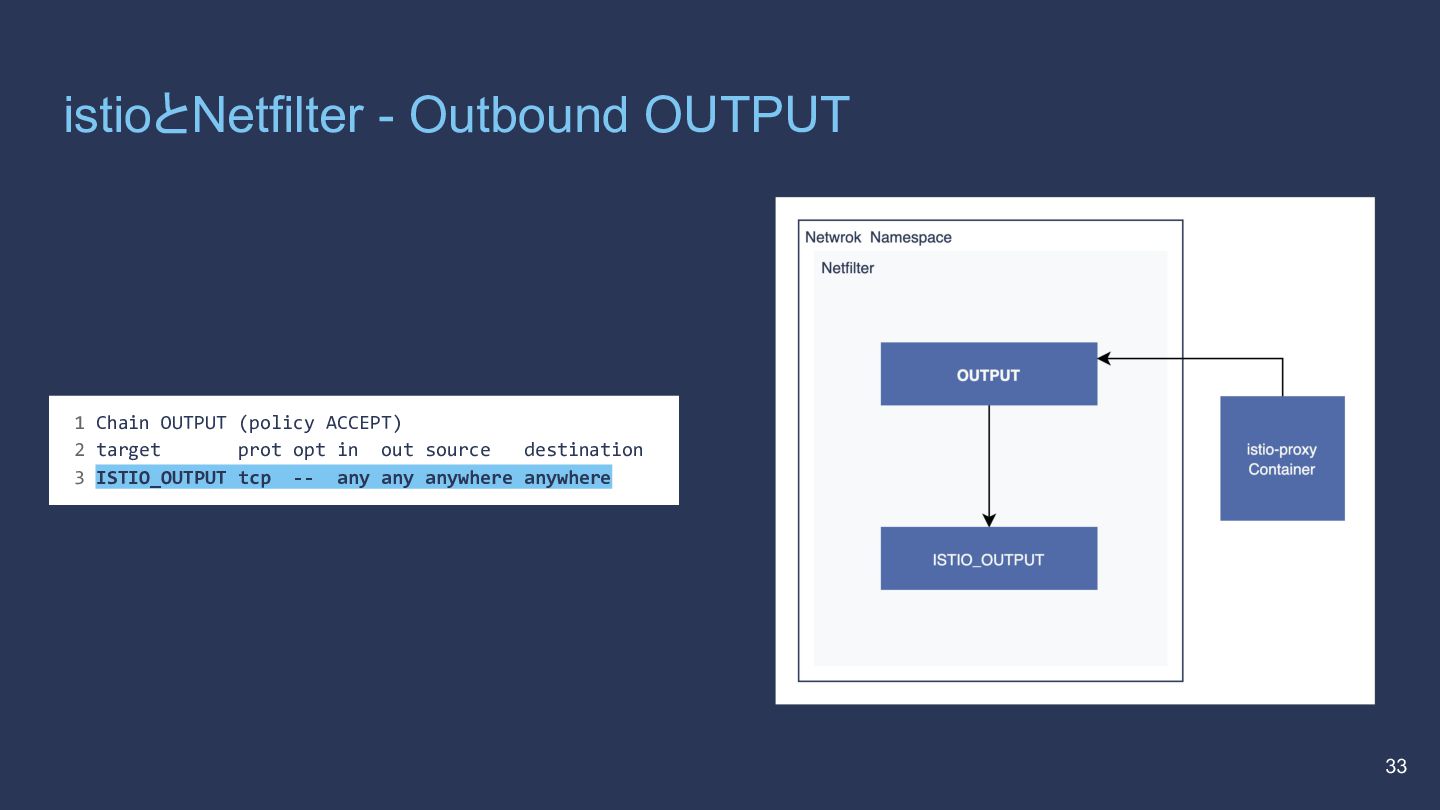
  20. istioとNetfilter - Outbound OUTPUT 33 1 Chain OUTPUT (policy ACCEPT)

    2 target prot opt in out source destination 3 ISTIO_OUTPUT tcp -- any any anywhere anywhere
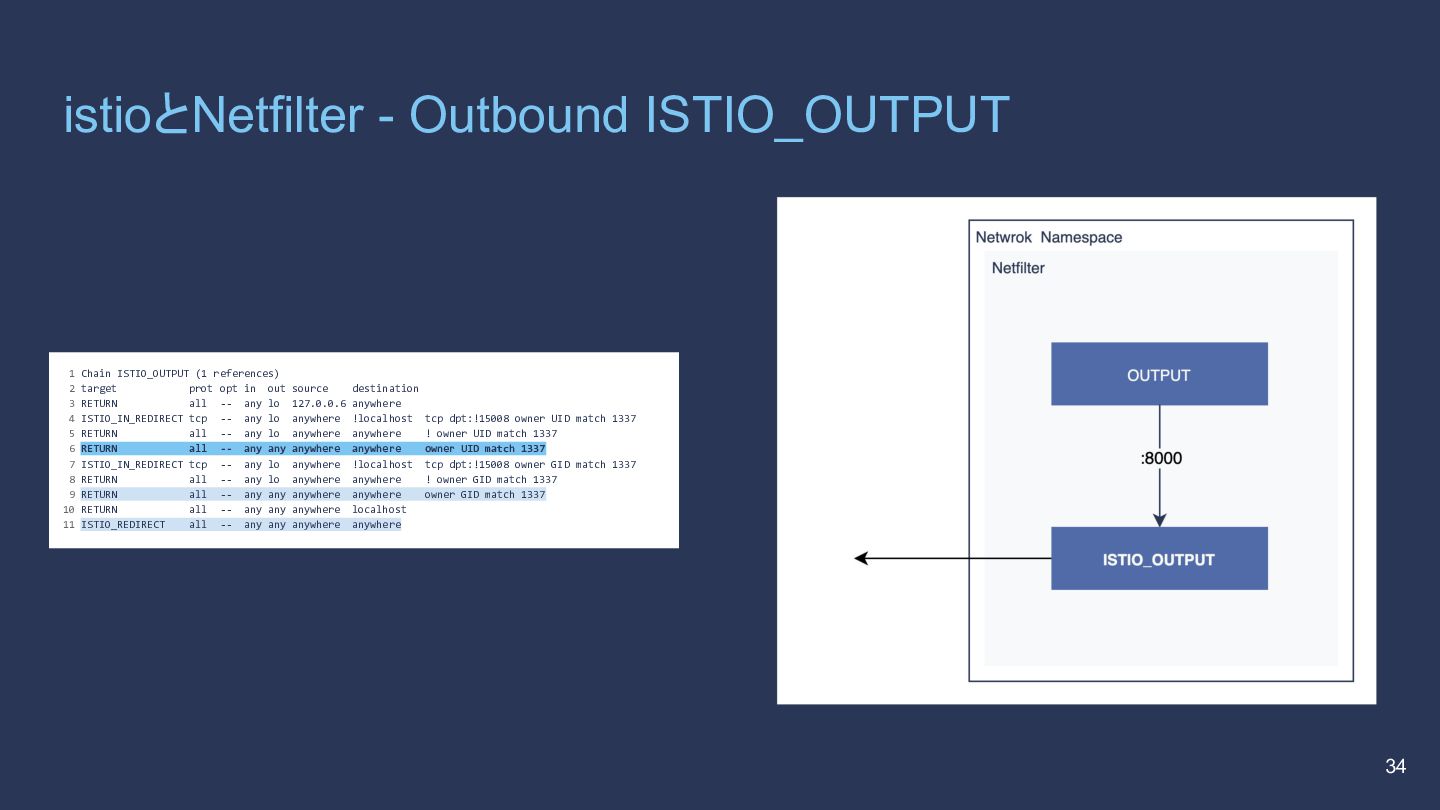
  21. istioとNetfilter - Outbound ISTIO_OUTPUT 34 1 Chain ISTIO_OUTPUT (1 references)

    2 target prot opt in out source destination 3 RETURN all -- any lo 127.0.0.6 anywhere 4 ISTIO_IN_REDIRECT tcp -- any lo anywhere !localhost tcp dpt:!15008 owner UID match 1337 5 RETURN all -- any lo anywhere anywhere ! owner UID match 1337 6 RETURN all -- any any anywhere anywhere owner UID match 1337 7 ISTIO_IN_REDIRECT tcp -- any lo anywhere !localhost tcp dpt:!15008 owner GID match 1337 8 RETURN all -- any lo anywhere anywhere ! owner GID match 1337 9 RETURN all -- any any anywhere anywhere owner GID match 1337 10 RETURN all -- any any anywhere localhost 11 ISTIO_REDIRECT all -- any any anywhere anywhere