Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
Web Security
Search
Hooopo
November 29, 2012
Programming
240
4
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
Web Security
Web Security
Hooopo
November 29, 2012
Transcript
29 slides
Web Security
Same Origin Policy 同源策略
同源 • 协议相同 • 域名相同 • 端口相同
同源策略的内容 限制来自不同源的“document”或脚本, 对当前“document”读取或设置某些属 性
浏览器沙箱 • XMLHttpRequest和CURL发起请求有 什么不同? • 同源策略保护当前域还是被请求域? • SRC属性加载外部资源违背同源策略 么? •
第三方Cookie和会话Cookie
如何绕过同源策略 • document.domain = "csdn.net" • Flash的crossdomain.xml • JSONP解决跨域发送请求,带来的问 题?
• P3P解决跨域共享Cookie,带来的问 题?
Cross Site Scriping 跨站脚本攻击
XSS的分类 • 反射型 • 持久型
XSS攻击方式 • Cookie劫持 • XSS钓鱼(诱骗密码) • XSS蠕虫
对抗XSS • HTTP Only Cookie • IE8 XSS Filter •
Firefox的CSP(Content Security Policy) • IE8的X-Content-Type-Options: nosniff
IE8 XSS Filter • X-XSS-Protection: 1; mode=block
Firefox CSP • X-Content-Security-Policy: allow 'self' *.mydomain.com • X-Content-Security-Policy: allow
'self' img-src *;media-src medial. com script-src script.com
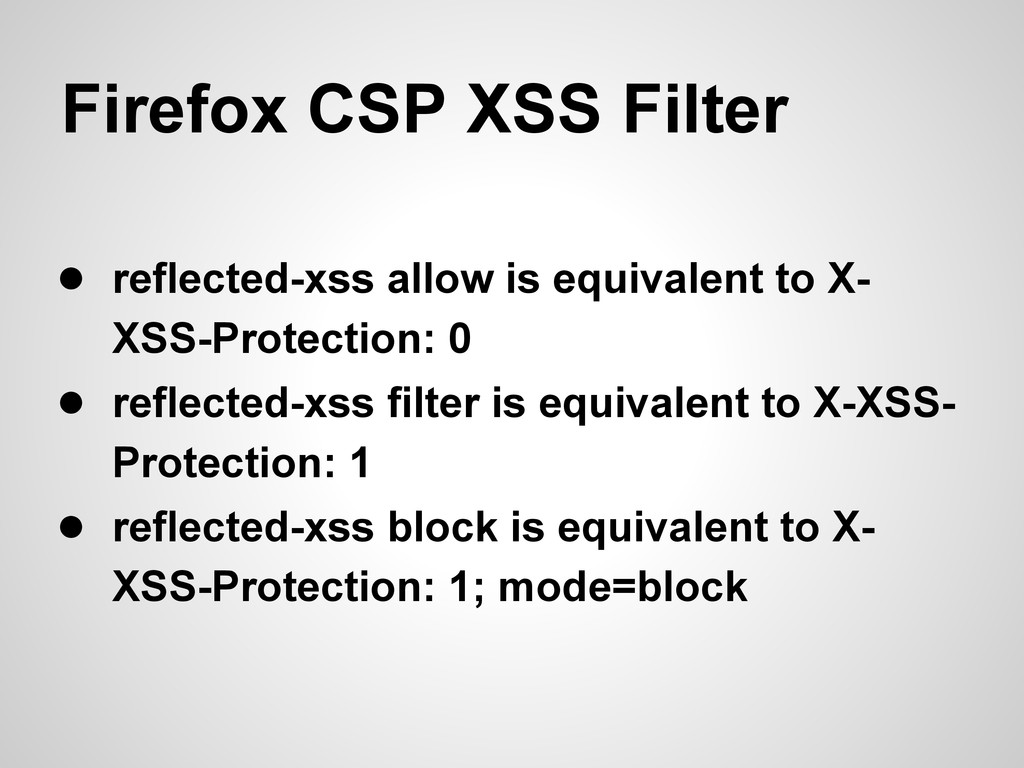
Firefox CSP XSS Filter • reflected-xss allow is equivalent to
X- XSS-Protection: 0 • reflected-xss filter is equivalent to X-XSS- Protection: 1 • reflected-xss block is equivalent to X- XSS-Protection: 1; mode=block
Auto HTML Escape能否彻底防御XSS?
Cross Site Request Forgery 跨站伪造请求
CSRF的原理 • 以用户的身份(Cookie)伪造请求
CSRF的危害 • 伪造普通用户的请求 • 伪造管理员的请求 • CSRF蠕虫
使用Post请求能否彻底防御 CSRF?
Referer检测能否正确防御 CSRF? • Flash某些版本可以自定义referer • 页面从HTTPS跳转到HTTP(RFC-2616) • Firefox中有相应参数可以设置是否发送HTTP Referer
CSRF的本质 • 所有请求参数都可以被攻击者猜到
正确的防御CSRF方法 • 不可预测原则 • one csrf token per session •
one csrf token per user
JSONP Hijacking JSONP 劫持
JSONP劫持本质是CSRF
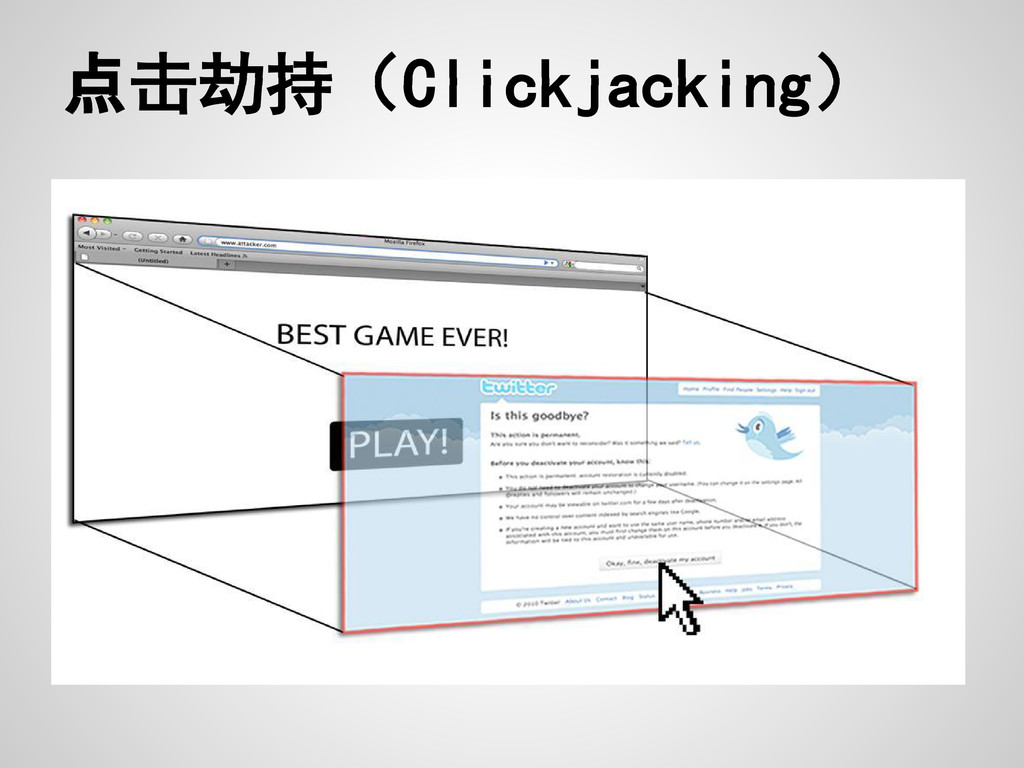
点击劫持(Clickjacking)
点击劫持的防御 • FrameBusting:HTML5 iframe sandbox属性 和IE iframe security属性 • IE8+的
X-Frame-Options: DENY/SAMEORIGIN/Allow-From • Firefox的CSP
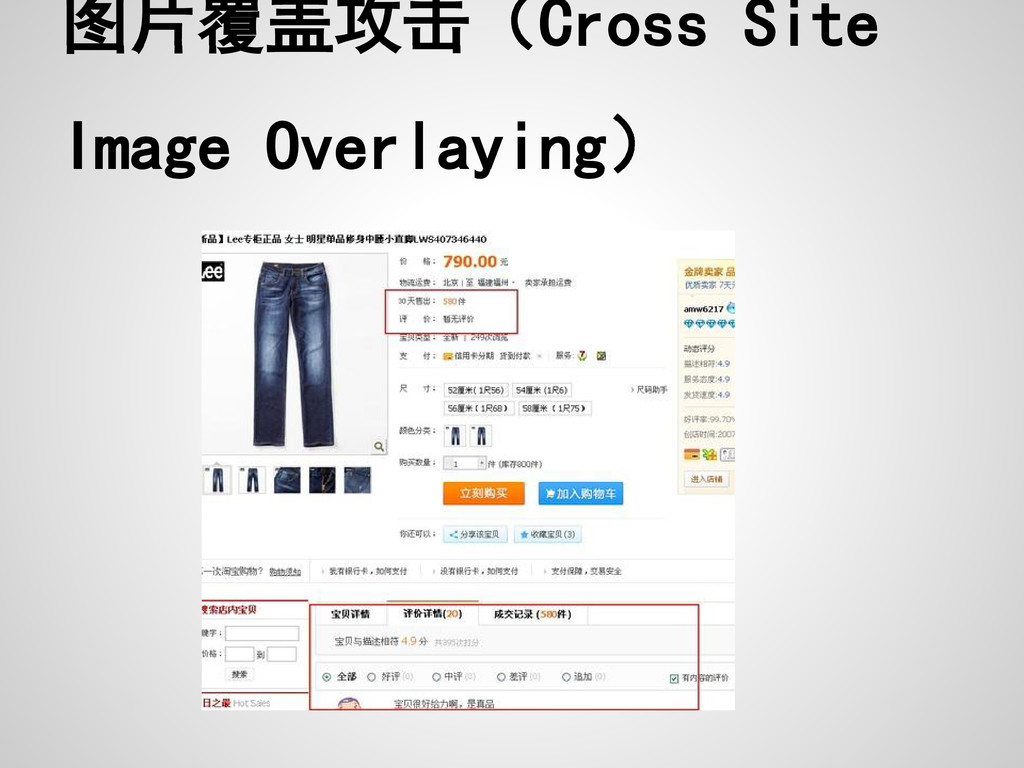
图片覆盖攻击(Cross Site Image Overlaying)
P3P头的副作用 IE默认禁止img,iframe,script,link等 标签发送第三方cookie,开启P3P之后会 允许发送第三方cookie
开源软件和CVE • Semantic Versioning
Refs • http://recxltd.blogspot.co.uk/2012/03/seven-web-server-http-headers-that.html • https://blog.whitehatsec.com/x-frame-options/ • http://blogs.msdn.com/b/ie/archive/2008/07/02/ie8-security-part-iv-the-xss-filter.aspx • http://homakov.blogspot.com/2012/06/saferweb-with-new-features-come-new.html •
http://msdn.microsoft.com/en-us/library/ie/gg622941(v=vs.85).aspx • https://www.owasp.org/index.php/HttpOnly • http://guides.rubyonrails.org/security.html#session-hijacking • http://en.wikipedia.org/wiki/HTTP_cookie#Secure_and_HttpOnly • http://rubylution.herokuapp.com/topics/32 • https://www.owasp.org/index.php/Clickjacking • http://blogs.msdn.com/b/ie/archive/2010/10/26/mime-handling-changes-in-internet- explorer.aspx • http://hi.baidu.com/aullik5/item/da5f5fec1a78c9d5ea34c9f8 • http://seclab.stanford.edu/websec/framebusting/framebust.pdf • http://book.douban.com/subject/10546925/ • http://hi.baidu.com/sysdog/item/4b44b7dd892d9655d63aaeb5 • http://semver.org/
More Decks by Hooopo
See All by Hooopo
test
hooopo
2
130
Other Decks in Programming
See All in Programming
プロジェクトコードをキレイキレイしよう!暗黙的な参照を読み解く静的解析
ostk0069
0
220
Augmenting AI with the Power of Jakarta EE
ivargrimstad
0
390
小さなアプリを作って公開するまで
onozaty
0
210
クラウドゲーミングのパフォーマンス最適化に挑む / Cloud Gaming Performance Tuning
vivion
0
360
AI駆動開発4年目の現在地(『あなたはFDEになるべきか?』イベント資料)
kumaiu
0
670
Kotlin Fest 2026: Kotlin コンパイラに Contribute してみよう! - Kotlin/Wasm で深い再帰を書けるようにした話
ternbusty
1
390
Debian JP Projectのサーバー構成
uwabami
1
150
Materialが消えた日 〜真っ白なFlutterキャンバスにRenderObjectで絵を描く〜
umigishiaoi
0
170
仕様駆動開発入門 (何を作るかを先に決めて渡す) | 目指せ Kiro マスター 05
inariku
PRO
3
210
学びを記事・スライド・Xへ高速展開する― AI-assisted Learning Loopで回すコンテンツ生成術
ochtum
0
220
LLM 101
dalinaum
0
520
Vapor Mode でアクセシビリティは 壊れないか検証した話
fuqda
1
350
Featured
See All Featured
How to Align SEO within the Product Triangle To Get Buy-In & Support - #RIMC
aleyda
2
1.9k
Code Reviewing Like a Champion
maltzj
529
40k
Money Talks: Using Revenue to Get Sh*t Done
nikkihalliwell
0
570
Are puppies a ranking factor?
jonoalderson
2
4.2k
The Curious Case for Waylosing
cassininazir
1
620
AI Search: Where Are We & What Can We Do About It?
aleyda
0
8.2k
The Invisible Side of Design
smashingmag
301
52k
Testing 201, or: Great Expectations
jmmastey
46
8.4k
The Cult of Friendly URLs
andyhume
79
7.1k
How to Ace a Technical Interview
jacobian
280
24k
sira's awesome portfolio website redesign presentation
elsirapls
0
520
Imperfection Machines: The Place of Print at Facebook
scottboms
270
14k


 hooopo
 ostk0069
 ivargrimstad
 onozaty
 vivion
 kumaiu
 ternbusty
 uwabami
 umigishiaoi
 inariku
 ochtum
 dalinaum
 fuqda
 aleyda
 maltzj
 nikkihalliwell
 jonoalderson
 cassininazir
 smashingmag
 jmmastey
 andyhume
 jacobian
 elsirapls
 scottboms